
Cybersecurity Compliance Consulting for Audit-Ready Businesses
Clarify which requirements apply, what an auditor or customer will expect, where the gaps are, and who owns the work to close them — HIPAA, PCI DSS, SOC 2, NIST, ISO 27001.
Evidence a customer or auditor will accept
Control mapping, policy packages, evidence checklists and technical validation — not paperwork-only templates.
Renewal, questionnaire or tax-preparer obligation driving the deadline?
Cyber-insurance readiness, IRS WISP compliance and board-level risk documentation, with a focused plan built around the requirement.
Choose the compliance path that matches your audit, customer or regulatory pressure.
Move from a broad compliance concern to the right readiness review, evidence plan, control-gap assessment or executive next step.
I need HIPAA or healthcare cybersecurity readiness.
HIPAA Security Rule readiness, safeguards review, risk analysis support and practical evidence planning for clinics and dental offices.
I need PCI DSS scope, evidence or audit readiness.
Cardholder data, payment systems, segmentation, firewall rules, access controls and PCI DSS documentation.
I need SOC 2 readiness or help with customer security reviews.
Prospects, enterprise customers or partners are asking for security evidence, policies, risk management and control documentation.
I need NIST or ISO 27001 readiness.
Control mapping, maturity planning, policy direction, evidence checklists and prioritized remediation against formal frameworks.
I need IRS WISP, cyber insurance or risk documentation.
Insurance renewal, tax-preparer obligations, board risk visibility or written security documentation are driving the project.
I need a trusted starting point before choosing a framework.
Use a free readiness tool or schedule a consultation to decide whether the next step is compliance, an audit, vCISO guidance or remediation.
Compliance frameworks exist because the controls they require stop real losses.
One security partner for multiple compliance paths.
Each framework has different evidence expectations, but the goal is the same: reduce legal, operational, financial and reputational exposure while building stronger controls.
HIPAA compliance consulting
Security risk assessments, gap analysis, ePHI safeguard review, policies, remediation planning and audit or investigation readiness.
HIPAA support →
PCI DSS compliance consulting
Readiness assessments, cardholder-data scoping, firewall and network review, MFA, vulnerability management and remediation roadmap.
PCI DSS support →
SOC 2 readiness consulting
Trust Services Criteria mapping, control gap analysis, evidence preparation, vendor risk and Type 1 / Type 2 audit readiness.
SOC 2 readiness →
ISO 27001 and ISO/IEC 27000
ISMS planning, risk treatment plans, Statement of Applicability, internal audit readiness and management review.
ISO consulting →
NIST Cybersecurity Framework
NIST CSF implementation, NIST 800-171 readiness, NIST 800-53 control assessment and a continuous-improvement roadmap.
NIST support →
Cyber insurance readiness
Application evidence, control gaps (MFA, EDR, backups, email security) and renewal priorities so coverage is not denied or delayed.
Cyber insurance readiness →From discovery to audit readiness.
A structured process that helps your organization understand its obligations, identify gaps, fix weaknesses and prepare for audits or customer reviews.
Read-only access. OC Security Audit reviews and reports; it does not change your configuration. Every finding comes with an owner, a priority and evidence you can hand to leadership, an auditor or an insurer.
Compliance discovery
Which requirements apply, based on your industry, data types, customers, contracts, systems and risk exposure.
Gap assessment
Current controls, documentation, policies and processes compared against the applicable framework.
Risk assessment
Sensitive data, access control, network, cloud, endpoints, vendors, backups, incident response and continuity.
Remediation roadmap
A prioritized plan that explains what to fix, why it matters and how to address each issue.
Policies, documentation & technical validation
Policy packages, risk registers, IR and DR plans, plus technical checks of MFA, firewalls, endpoints, logging and Microsoft 365.
Audit readiness support
Evidence organized, stakeholders prepared, auditor requests answered — and re-audit support if a control failed.
Compliance consulting deliverables.
From uncertainty to readiness: discovery, assessment, risk reduction, documentation, technical validation and audit support.
| Deliverable | What it contains | Who uses it |
|---|---|---|
| Compliance gap assessment report | Control-by-control status against the applicable framework with evidence notes | Compliance lead, leadership |
| Executive summary | Business-level view of exposure, priorities and the decisions leadership must make | Owners, executives, board |
| Risk register & remediation roadmap | Scored risks with owners, sequencing and realistic timelines | IT team, MSP, compliance |
| Security policy package | Policies and procedures customized to your operations and auditor-ready | Compliance, HR, IT |
| Control mapping worksheet & evidence checklist | What each control needs, who owns it and what evidence proves it | Compliance, auditors |
| Technical findings & follow-up review | Validation of MFA, firewalls, endpoints, backups, logging and cloud security; re-check after fixes | IT team, MSP |
Compliance and cybersecurity support for organizations with real exposure.
Different industries need different controls, evidence and priorities. We connect the requirement to the security risk that matters most for your business.
Healthcare clinics & dental
HIPAA readiness, ePHI safeguards, Microsoft 365 security, access control and audit evidence.
Healthcare cybersecurity →CPA firms & tax preparers
IRS WISP planning, client data protection, email security and compliance readiness.
CPA firm cybersecurity →Law firms
Confidential files, email accounts, client portals, case data and vendor access.
Law firm cybersecurity →
Manufacturing
Firewall security, segmentation, vulnerability management, incident response and downtime reduction.
Manufacturing cybersecurity →Connect compliance readiness to policy authority and executive oversight
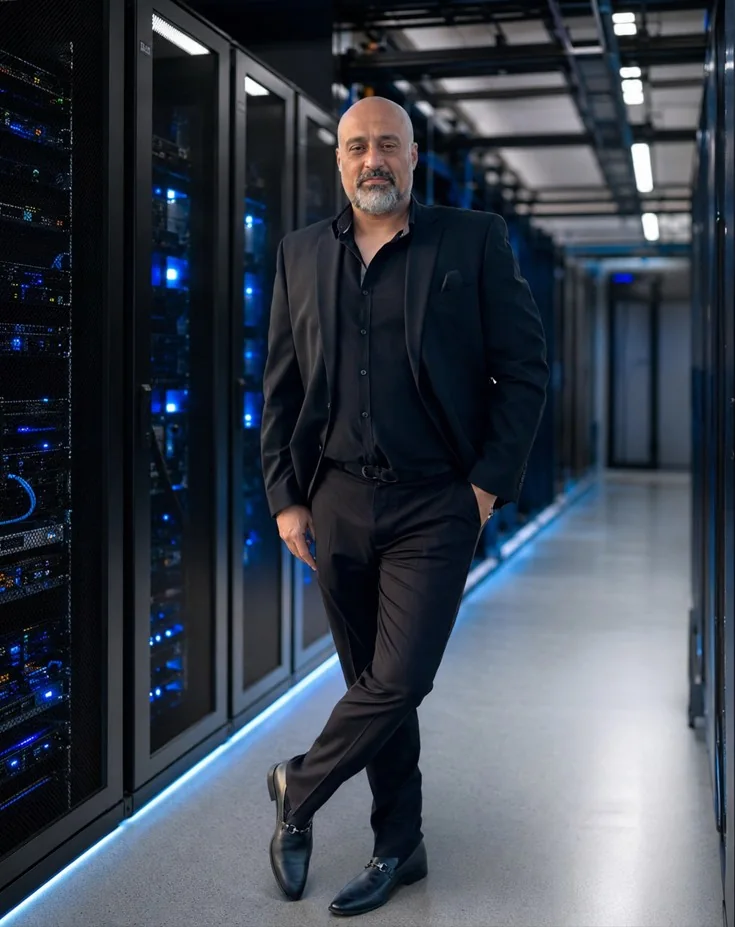
Led by Ali Hassani, Certified CISO (C|CISO) and CISSP
Compliance guidance from a hands-on cybersecurity and IT leader: engagements are practical, technical and business-focused, with transparent deliverables — executive summaries, control gaps, evidence checklists and remediation plans — not generic templates.
Ali holds the CISSP and C|CISO certifications plus dozens of Microsoft and Cisco credentials (CCNP, CCNA, MCSE, MCITP, MCSA Security). He works on-site across Orange County, Los Angeles and Southern California, and remotely for organizations nationwide.
Start with a free self-assessment before the audit pressure arrives.
These tools give initial guidance only; they do not replace a professional audit, compliance assessment, penetration test or legal review.
Questions business owners and IT managers ask
Clear answers on scope, deliverables, pricing logic and how we work with your IT team or MSP.
What compliance consulting services do you offer?
End-to-end readiness for HIPAA, PCI DSS, SOC 2, ISO 27001, NIST 800-53, NIST 800-171, IRS WISP and cyber-insurance programs: gap assessments, remediation roadmaps, documentation, technical validation and audit support.
Can you help determine which compliance requirements apply to us?
Yes. During the initial consultation we identify the frameworks that apply based on your industry, data types, customers, contracts and regulatory exposure.
What technical items do you check during a compliance assessment?
Network security, firewall configurations, endpoint protection, patch management, identity and access, MFA, least privilege, Microsoft 365 and cloud controls, logging and monitoring, backup, disaster recovery and ransomware readiness.
Can you help if we failed a compliance audit?
Yes. We help close audit findings, remediate failed controls, prepare supporting documentation and get your organization ready for re-audit.
Do you provide compliance documentation and policies?
Yes: security policies and procedures, risk assessments, incident response plans, business continuity and disaster recovery plans, and vendor risk documentation — customized and auditor-ready.
Can you work with our MSP or IT provider?
Yes. We frequently partner with MSPs and internal IT teams so controls are implemented efficiently while OC Security Audit stays independent.
How long does it take to become compliant?
Timelines depend on your current posture, size, documentation maturity and framework. After the assessment you receive a roadmap with realistic timelines and prioritized next steps.
Are your services on-site or remote?
On-site compliance consulting across Orange County and Southern California; remote compliance consulting nationwide.
Implementation partner
OC Security Audit stays independent and read-only. If you want hands-on administration, IT Perfection can implement the fixes and support ongoing operations.
On-site across Orange County and Southern California — remote nationwide
Based in Irvine, OC Security Audit works on-site with businesses across Orange County and Los Angeles County, and remotely with organizations anywhere in the United States.
Need help getting audit-ready?
Identify compliance gaps, validate security controls, prepare documentation and build a practical roadmap toward audit readiness — with a CISO-led partner, not a template.