
Executive Cyber Risk Scorecard Assessment
Use this executive cyber risk scorecard to identify gaps across business risk and accountability, governance and policy, and control evidence. Treat the result as initial guidance and validate material findings through a professional review.
CISO-led guidance from Ali Hassani, backed by 25+ years of IT, cybersecurity, compliance, and infrastructure experience.
FROM FIRST CHECK TO NEXT STEP
Can Executives See the Decisions Behind the Score?
Use the scorecard questions to review how your organization explains cyber exposure and readiness. Turn uncertain answers into specific management follow-up.
- Connect results with accountable risk decisions.
- Identify evidence needed for a useful executive briefing.
Initial guidance only, not a professional audit or compliance certification. Do not enter confidential information.

A focused video briefing for leaders and IT teams working through this page.
Virtual CISO Leadership Series · Episode 08
Executive and Board Cybersecurity Reporting
Use this concise briefing alongside the guidance on this page to connect executive cybersecurity reporting with clear evidence, accountable ownership, and a practical next action.
Executive Cyber Risk Scorecard Assessment
Executive cyber risk reporting helps boards, business owners, and leadership teams understand risk without getting buried in technical detail. This free scorecard-style assessment helps determine whether your reporting covers the essentials: top risks, incident readiness, resilience, compliance exposure, and remediation priorities.
You will get a readiness score around reporting quality, decision support, resilience visibility, and how effectively security is communicated to executive stakeholders.

Practical guidance for business owners, IT managers, CISOs, and compliance leaders
OC Security Audit designed this tool to help leadership teams find important cybersecurity gaps without collecting personal information or sending data anywhere.
The assessment runs entirely in the browser and produces an immediate visual score, category breakdown, and recommendation summary that can support planning discussions before a deeper review.


Work with Ali Hassani, CISO
Ali Hassani brings 25+ years of cybersecurity, network security, Microsoft 365 security, compliance readiness, audit support, identity and access management, backup resilience, and executive security reporting experience.
For this topic, Ali helps organizations translate security requirements into practical controls, documentation, leadership reporting, and remediation priorities that reflect their real business environment. Relevant certifications and background include CISSP, CCISO, CCNP, MCSE, MCSA Security, MCITP, MCP, and hands-on consulting experience across cloud, audit, compliance, risk management, and security operations.
Choose the areas you want to assess
No personal information is collected. Yes / Implemented = 2 points. Partially / In progress = 1 point. No / Not sure = 0 points.
0 selected
What the report shows
Overall readiness score
An immediate snapshot of how mature your current responses appear across the selected categories.
Key strengths and gaps
A focused view of what looks stronger and where important governance, control, or documentation gaps remain.
Priority recommendations
Practical next steps you can use to guide roadmap planning or a deeper OC Security Audit engagement.
Helpful resources
Need help reviewing your CISO readiness?
OC Security Audit can help you move from a self-score into a deeper cybersecurity assessment, roadmap, compliance readiness review, or vCISO engagement.
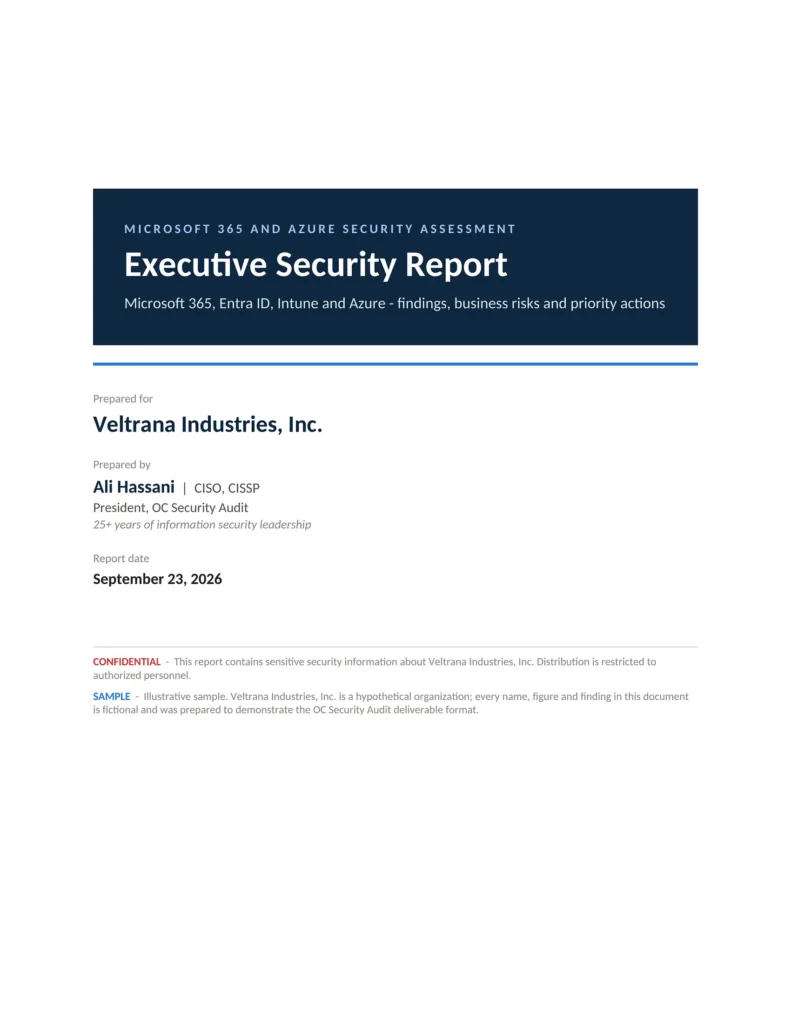
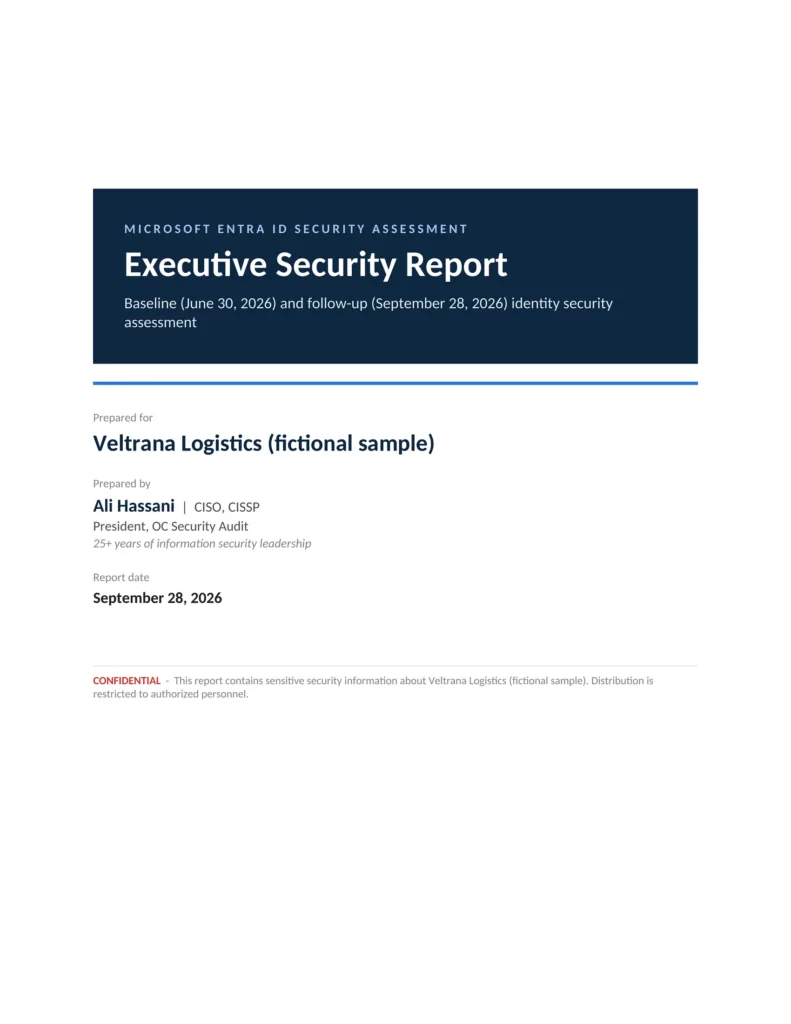
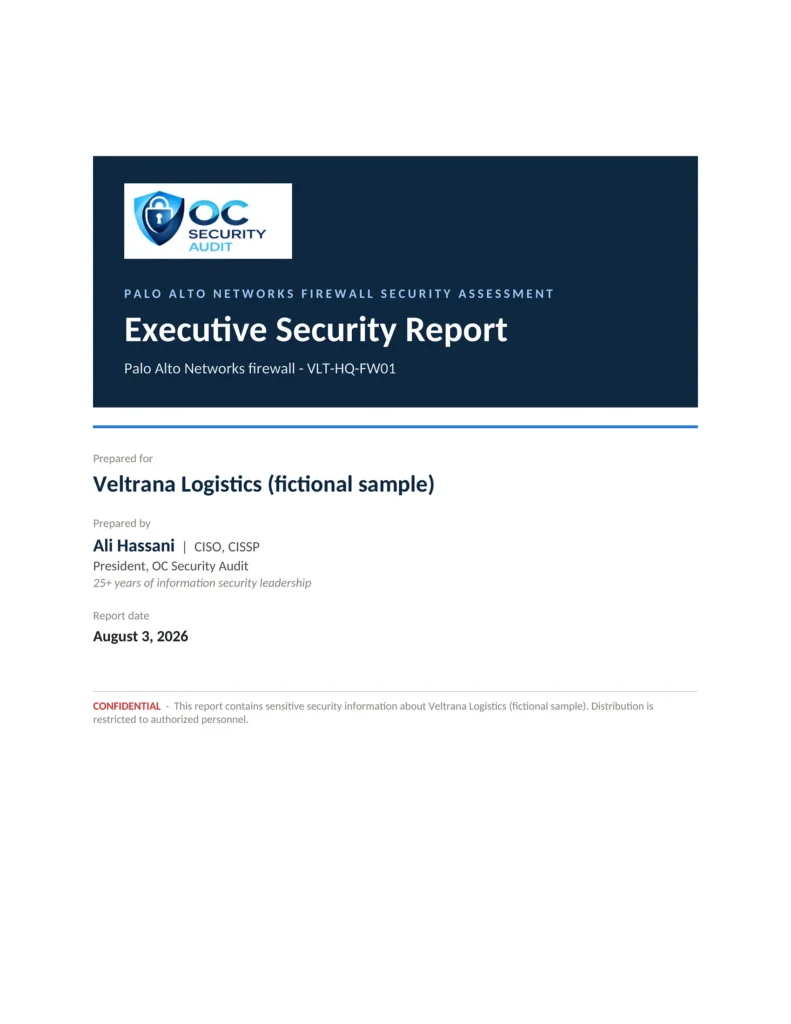
Sample reports
This tool is a quick check. A full audit goes further.
See what a full security audit delivers: real pages from our executive and technical reports, risk registers, roadmaps and workbooks, for fictional companies.