
IT engineer with a laptop in a server room
Sample reports · Showcases

Sample Security Audit Reports

See real pages from the reports we deliver: executive and technical reports, risk registers, roadmaps and Excel workbooks. Fictional companies, illustrative data.

Security executive in a server room reviewing audit results
Written for leadership

Every audit starts with a report owners can read

The executive report gives the score, the top risks and the decisions leadership needs to make, in plain business language.

IT engineer reviewing audit findings on a laptop in a server room
Built for your IT team

Evidence your administrators can act on

Technical reports and workbooks show each finding with the evidence, the risk and the fix, ready to assign and track.

25+ yearsIT & cybersecurity experience
Certified CISOC|CISO · CISSP · Microsoft · Cisco
Southern CaliforniaLocal and on-site, based in Irvine
NationwideRemote audits & advisory
Why we publish samples

See the sample security audit report before you book

Most businesses buy a security audit without ever seeing what they will get. We think you should know before you book. This page collects every sample security audit report we have published, so you can open the exact pages your owners, managers and IT team would receive.

Each sample was prepared for a fictional company with illustrative data, using the same templates, rating model and report structure we use for clients. Thirteen of them are full showcases: every page of every deliverable, shown one slide at a time. The rest show the structure and sample findings for each service.

When you find the audit that fits your business, the service page explains the scope, the process and the price, and you can schedule a consultation from there.

Two professionals reviewing a security audit report on a laptop
What every audit delivers

One audit, one consistent report pack

Whichever audit you choose, the results arrive in the same set of documents, so leadership and IT work from one set of facts. Some audits add specialist reports, such as a sign-in analysis, a rulebase review or a log review.

01

Executive Security Report

The score, the top risks and the decisions to make, written for owners and managers.

02

Technical Security Report

Every finding with the evidence, the risk it creates and the steps to fix it.

03

Risk Register

Each risk scored by likelihood and impact, with an owner and a treatment.

04

Security Roadmap

What to fix first, next and later, sorted into a practical timeline.

05

Findings Workbook

An Excel workbook your IT team can filter, assign and track to closure.

Full showcases

Sample report showcases, page by page

These showcases show every page of every deliverable from one audit, with a short note on what each page tells you. Open one, use the arrows to move through the report, and click any page to enlarge it.

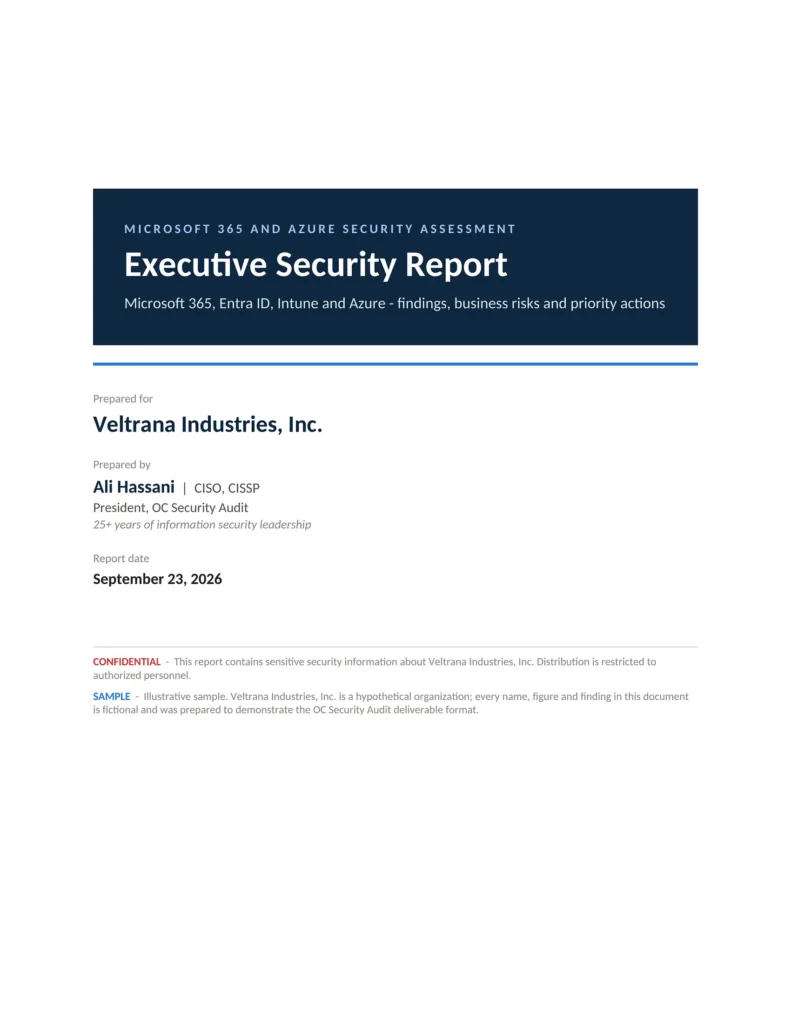
Cover of the Microsoft 365 Security Audit sample executive report (fictional company, illustrative data)
5 deliverables

Microsoft 365 Security Audit

Tenant-wide review of identity, admin access, Exchange and Defender, email authentication, SharePoint, OneDrive and Teams, Purview, logging and devices.

  1. Executive Security Report
  2. Technical Security Report
  3. Risk Register
  4. Next Steps & Security Roadmap
  5. Technical Findings Workbook (Excel)
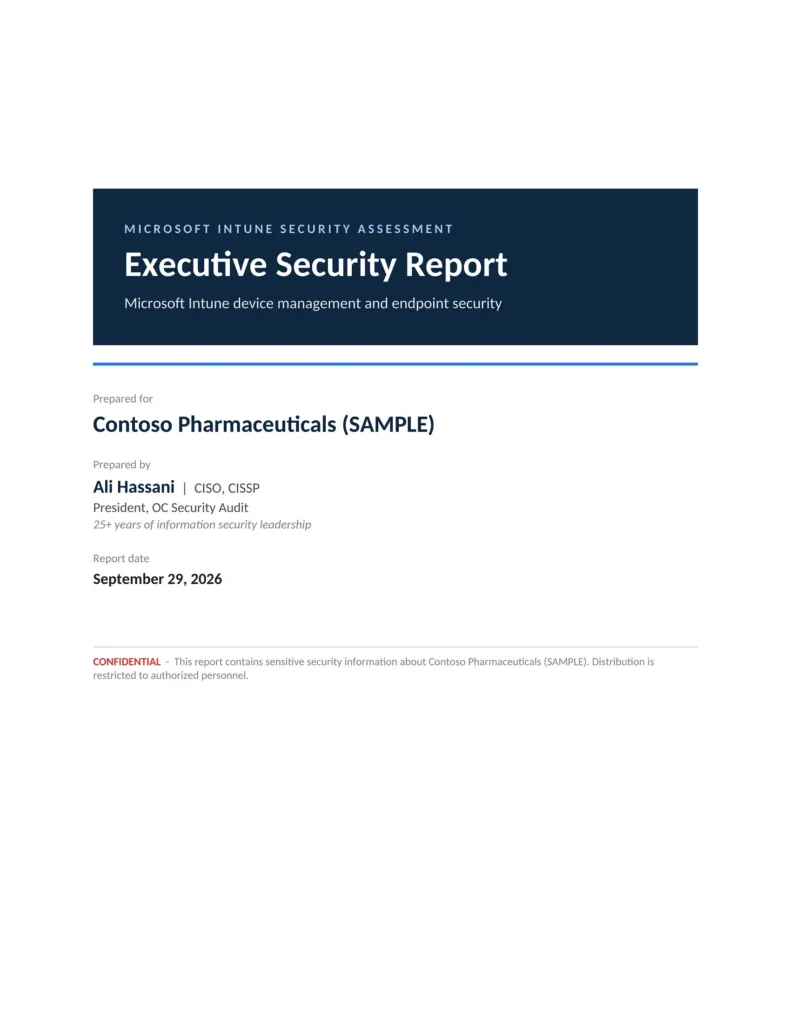
Cover of the Microsoft Intune Security Audit sample executive report (fictional company, illustrative data)
5 deliverables

Microsoft Intune Security Audit

Device management review: enrollment, compliance and configuration policies, endpoint security, app protection and the devices that fall through the gaps.

  1. Executive Security Report
  2. Technical Security Report
  3. Risk Register
  4. Next Steps & Security Roadmap
  5. Technical Findings Workbook (Excel)
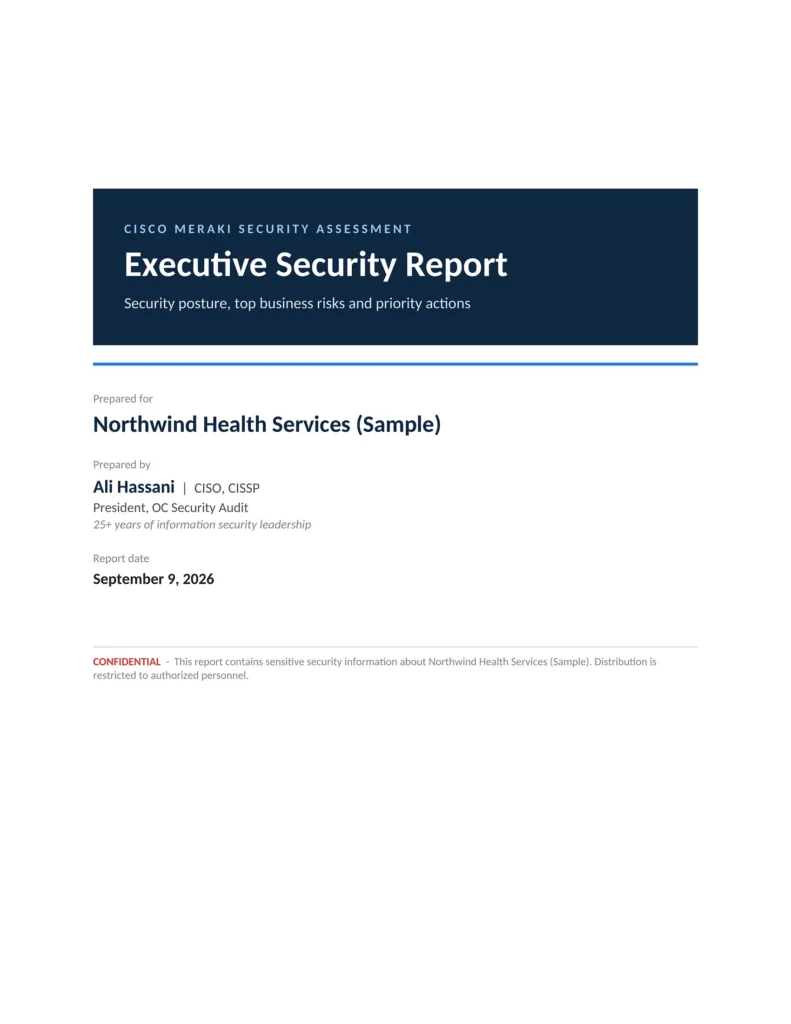
Cover of the Cisco Meraki Security Audit sample executive report (fictional company, illustrative data)
5 deliverables

Cisco Meraki Security Audit

Read-only review of MX firewalls, site-to-site and client VPN, MR wireless, MS switches and Dashboard administration.

  1. Executive Security Report
  2. Technical Security Report
  3. Risk Register
  4. Next Steps & Security Roadmap
  5. Technical Findings Workbook (Excel)
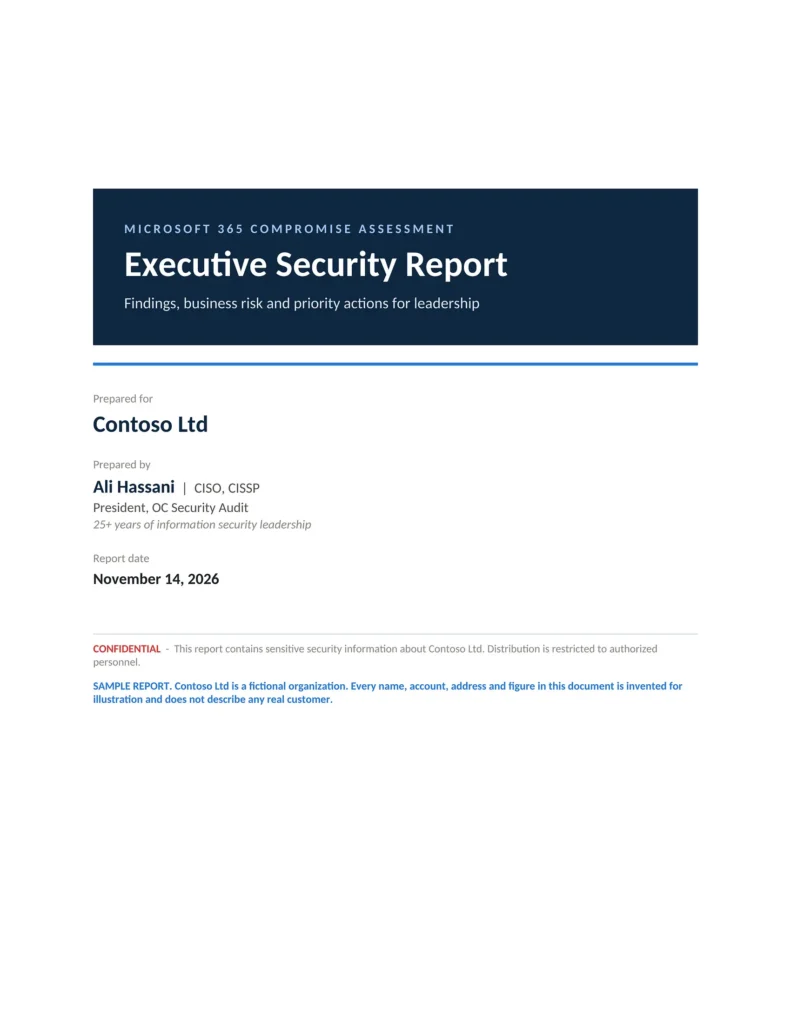
Cover of the Microsoft 365 and Azure Compromise Investigation sample executive report (fictional company, illustrative data)
5 deliverables

Microsoft 365 & Azure Compromise Investigation

A compromise assessment across Microsoft 365, Entra ID and Azure: what the records show happened, what is still exposed and what to close first.

  1. Executive Report
  2. Technical Report
  3. Risk Register
  4. Roadmap
  5. Technical Findings Workbook (Excel)
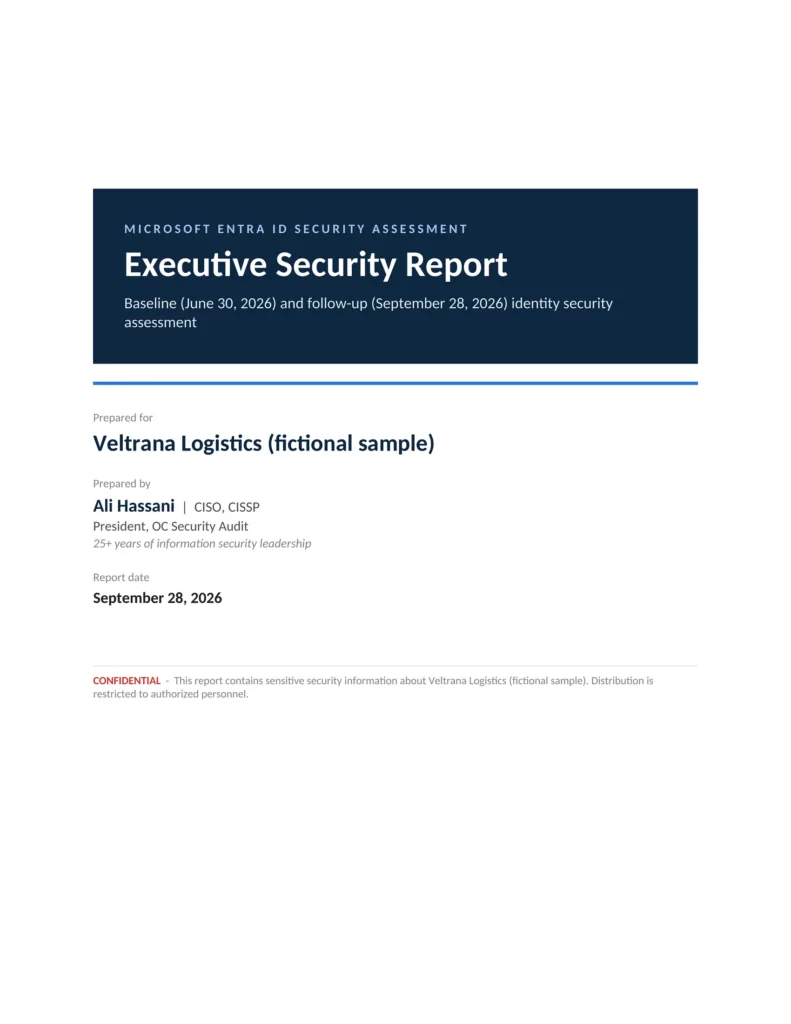
Cover of the Microsoft Entra ID Security Audit sample executive report (fictional company, illustrative data)
7 deliverables

Microsoft Entra ID Security Audit

Identity-focused review of sign-ins, Conditional Access, privileged roles and PIM, app consent and guest access, with a follow-up progress report.

  1. Executive Security Report
  2. Technical Security Report
  3. Identity Threat & Sign-in Analysis
  4. Risk Register
  5. Next Steps & Security Roadmap
  6. Technical Findings Workbook (Excel)
  7. Remediation Progress Report (follow-up audit)
Cover of the Palo Alto Firewall Security Audit sample executive report (fictional company, illustrative data)
7 deliverables

Palo Alto Firewall Security Audit

141 controls in 13 areas: management access, PAN-OS lifecycle, security policy, threat prevention, decryption, GlobalProtect, logging and HA.

  1. Executive Security Report
  2. Technical Security Report
  3. Firewall Rulebase Review
  4. Log Review & Threat Activity
  5. Risk Register
  6. Next Steps & Security Roadmap
  7. Technical Findings Workbook (Excel)
Cover of the HIPAA Compliance Assessment sample executive report (fictional company, illustrative data)
5 deliverables

HIPAA Compliance Assessment

HIPAA Security Rule assessment of a fictional two-location clinic: 145 controls in 14 areas, 41 HIPAA standards rated, administrative, physical and technical safeguards across Microsoft 365, identity, devices, firewalls, network and backup.

  1. Executive Security Report
  2. Technical Security Report
  3. Risk Register
  4. Next Steps & Security Roadmap
  5. HIPAA Findings Workbook (Excel)
Cover of the PCI DSS Readiness Assessment sample executive report (fictional company, illustrative data)
5 deliverables

PCI DSS Readiness Assessment

PCI DSS v4.0.1 readiness assessment of a fictional retailer with store POS terminals and an online store: 200 controls across all 12 requirements, from stored card data and payment page scripts to CDE access, encryption keys, logging and testing.

  1. Executive Security Report
  2. Technical Security Report
  3. Risk Register
  4. Next Steps & Security Roadmap
  5. Technical Findings Workbook (Excel)
Cover of the Microsoft Azure Security Audit sample executive report (fictional company, illustrative data)
5 deliverables

Microsoft Azure Security Audit

Read-only review of a four-subscription Azure estate: governance and policy, Entra ID access, network exposure, VMs, storage and SQL, logging, Defender for Cloud and backup.

  1. Executive Security Report
  2. Technical Security Report
  3. Risk Register
  4. Next Steps & Security Roadmap
  5. Technical Findings Workbook (Excel)
Cover of the NIST 800-53 Assessment sample executive report (fictional company, illustrative data)
5 deliverables

NIST SP 800-53 Assessment

NIST SP 800-53 Rev. 5 assessment of a fictional cloud platform provider at FIPS 199 Moderate: 35 controls in nine families, from access control and authentication to contingency planning, incident response and supply chain.

  1. Executive Security Report
  2. Technical Security Report
  3. Risk Register
  4. Next Steps & Security Roadmap
  5. Technical Findings Workbook (Excel)
Cover of the Cisco Network Security Audit sample executive report (fictional company, illustrative data)
8 deliverables

Cisco Network Security Audit

Read-only review of IOS and IOS XE routers and switches, ASA and Secure Firewall, and wireless controllers, with a topology diagram, redacted configuration backups and a follow-up comparison.

  1. Executive Security Report
  2. Technical Security Report
  3. Risk Register
  4. Next Steps & Security Roadmap
  5. Technical Findings Workbook (Excel)
  6. Interactive Assessment Dashboard (HTML)
  7. Network Topology & Configuration Backups
  8. Follow-up Comparison Report (follow-up audit)
Cover of the MSP Security Audit sample executive report (fictional company, illustrative data)
9 deliverables

MSP and MSSP Security Audit

Read-only audit of a managed service provider’s own security, procedures and tools: the RMM, the client credential vault, delegated admin access and the help desk, shown across a three-audit cycle.

  1. Executive Security Report
  2. Technical Security Report
  3. Risk Register
  4. Next Steps & Security Roadmap
  5. MSP Security Scorecard
  6. Client Exposure Analysis
  7. Certification Readiness
  8. Technical Findings Workbook (Excel)

  9. Remediation History (re-audits)
Cover of the Windows Server and Active Directory Security Audit sample executive report (fictional company, illustrative data)
6 deliverables

Windows Server & Active Directory Security Audit

140 controls in 13 areas: Active Directory health, privileged access, accounts, Kerberos and certificates, Group Policy, DNS, DHCP, domain controllers, server patching, file shares, Hyper-V, backup and remote access.

  1. Executive Security Report
  2. Technical Security & Configuration Report
  3. Identity & Access Inventory
  4. Risk Register
  5. Next Steps & Security Roadmap
  6. Technical Findings Workbook (Excel)
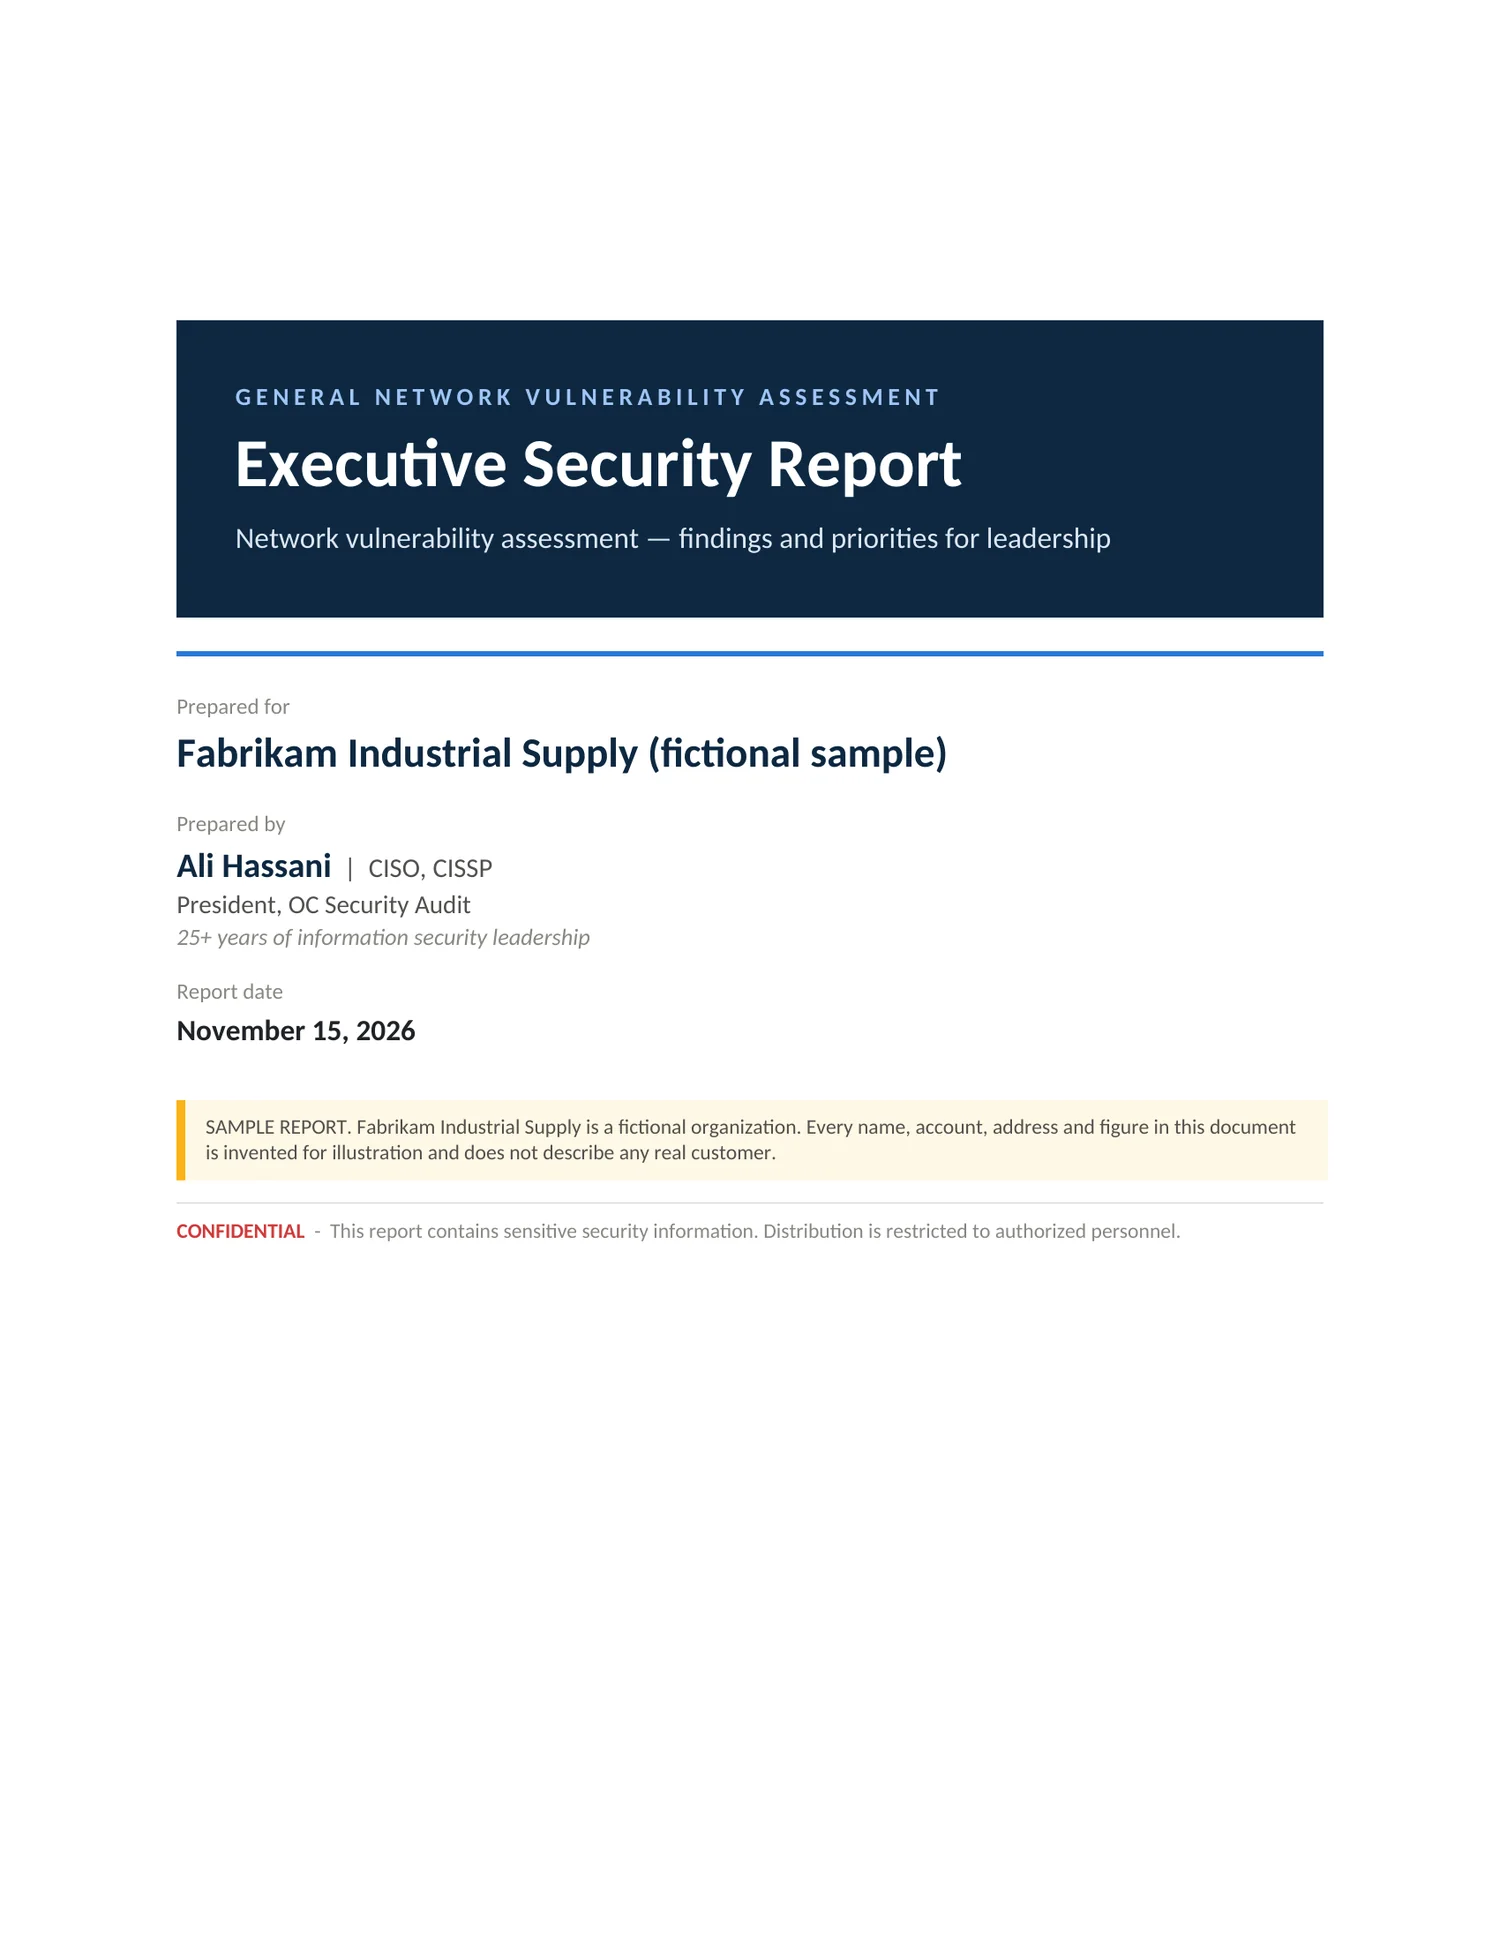
Cover of the Network Vulnerability Assessment sample executive report (fictional company, illustrative data)
5 deliverables

Network Vulnerability Assessment

Internal and external vulnerability scanning with a configuration review across 315 controls in fourteen areas, turned into prioritized business risks, a phased remediation roadmap and a working Excel findings workbook.

  1. Executive Security Report
  2. Technical Security Report
  3. Risk Register
  4. Next Steps & Security Roadmap
  5. Technical Findings Workbook (Excel)
More sample reports

Sample reports for every service

Each of these pages shows the structure of the report for that service, with sample scores, findings, risks and a roadmap for a fictional company.

Network, firewall and server audits

Fortinet FortiGate Security AuditScore by area, SSL VPN and FortiOS findings, a risk register and a roadmap.
SonicWall Firewall Security AuditScore by area, SSL VPN and firmware findings, a risk register and a roadmap.
WatchGuard Firebox Security AuditScore by area, IKEv2 VPN and Fireware findings, a risk register and a roadmap.

Cloud, AI and internal audits

AI Security AuditExposure score, results in eight domains, top findings and a 30/60/90-day roadmap.
Internal Security AuditRatings by area, findings written as condition, criteria, cause and evidence, a risk register and a 30/60/90 roadmap.

Resilience and recovery

Backup & Disaster Recovery AuditScores by domain, risk-rated findings, business risks and a 90-day roadmap.
Incident Response ReadinessReadiness scores, findings, risks and a 90-day roadmap.

Risk, governance and compliance

Cybersecurity Risk AssessmentA scored risk register, an executive summary and a risk treatment plan.
GRC AssessmentExecutive summary, risk register, compliance gap map and roadmap.
Cyber Insurance Readiness AssessmentApplication answers checked against evidence, the gaps found and a renewal roadmap.
How to read a sample

Four things to check in any security audit report

Use these checks on our samples, and on any report you receive from another provider.

Start with the executive report

Read the score, the top risks and the recommended decisions. If an owner can understand the business risk in five minutes, the report is doing its job.

Open one technical finding

Pick any finding and check that it shows the setting reviewed, the evidence, why it matters and the exact steps to fix it.

Check the risk register

See how each risk is scored, who owns it and how it will be treated, so nothing depends on memory or email threads.

Look at the roadmap and workbook

The roadmap tells you what to fix first; the workbook lets your IT team filter, assign and track every item to closure.

Confidentiality

Fictional data, real report structure

Your data stays yours. The samples prove the format without exposing anyone.

  • Every company, person, domain and figure in the samples is fictional and illustrative
  • No client name, client data or page from a real client report is ever published
  • Client reports are delivered privately to the people you name
  • Our audits use read-only access; your team or a partner you choose makes the changes

Want to see a report walked through?

Schedule a consultation and we will go through a sample report with you, explain how each finding is rated, and confirm which audit fits your environment and what it costs before any work begins.

Ali Hassani, CISO and founder of OC Security Audit
Who prepares your report

Prepared under the direction of Ali Hassani

Every OC Security Audit report is prepared under the direction of Ali Hassani, a Certified CISO (C|CISO) and CISSP with more than 25 years in IT and cybersecurity and dozens of Microsoft and Cisco certifications.

We are based in Irvine, work on-site across Orange County and Southern California, and deliver audits remotely nationwide. The samples on this page use the same templates, rating model and review process as the reports we deliver to clients.

Questions

Questions about our sample reports

Are these real client reports?

No. Every sample on this page was prepared for a fictional company, and every name, account, address and figure in it is illustrative. We never publish client names, client data or pages from a real client report.

Will my report look like the sample?

It will have the same structure and the same deliverables. The scores, findings, risks and roadmap are written from the evidence in your own environment, so the content is specific to your business.

Which sample should I look at first?

Start with the platform you use most. If your business runs on Microsoft 365, open the Microsoft 365 sample first; if you are worried about a firewall, open the sample for your firewall brand. If you are not sure, schedule a consultation and we will point you to the right one.

Can you walk me through a sample report?

Yes. Schedule a consultation and we will go through a sample report with you on the call, explain how each finding is rated and show what your team would receive.

Do you make changes to our systems during an audit?

No. Our audits use read-only access. We review settings and evidence, then hand you the reports and the roadmap; your IT team or a partner you choose makes the changes.

Do you work outside Southern California?

Yes. We are based in Irvine and work on-site across Orange County and Southern California, and we deliver audits remotely to businesses nationwide.

Security consultant reviewing an audit plan on a tablet with a business client

Get this report for your own business

Tell us what you run, and we will recommend the audit that fits and confirm the scope and price in writing before work begins.

Irvine, Orange County and Southern California on-site; remote nationwide.