

Attackers don’t break in anymore. They sign in.
Is your Entra ID set up to stop an account takeover?
Microsoft Entra ID (formerly Azure AD) decides who can sign in to your email, files, Teams and every connected app. Over the years admins are added, exceptions pile up, apps are approved with a click and guests are never removed.
The Microsoft Entra ID security audit reviews your whole identity configuration against 72 best-practice checks, reads 30 days of sign-in and audit logs for attacks, and turns what we find into business risks, a prioritized roadmap and plain-English reports.
72 checks across the 8 areas of your Entra ID tenant
Pick an area to see example checks. Every check has a severity, the evidence behind it, a fix and a NIST CSF 2.0, ISO 27001 and CIS mapping.
Identity & Authentication
Who can sign in, and how hard it is to steal that sign-in.
Privileged Access
How much standing admin power exists, and who holds it.
Conditional Access
Whether your policies actually reach every user, app and risk.
Applications & Consent
Which apps can read your mail and files, and who let them in.
External Collaboration
Guests and partner tenants that can reach your data.
Devices
The identity side of devices: registration and join settings.
Monitoring & Threat Protection
Whether attacks would be seen and acted on.
Directory & Domains
Tenant-wide settings, domains and directory sync.
We read 30 days of sign-ins for attacks already underway
Settings tell you what should happen. Logs tell you what did. The audit reviews interactive, non-interactive and app sign-ins plus directory audit logs, and flags:
Exactly what your administrator will see
The audit reads your configuration and logs; it never changes them. Here is everything that happens on your side, so there are no surprises.
Fixes are made by your IT team, your MSP or IT Perfection, never by the audit itself.
| Item | What happens |
|---|---|
| Access needed | A Global Reader account. Your Global Administrator approves our read-only audit app once, with one link. No write permission is ever requested. |
| Requests made | Microsoft Graph read requests only. The tool cannot create, change or delete anything, and every request is logged. |
| What your admin sees | One consent screen listing the read-only permissions. The app “OCSA Entra ID Read-Only Audit” appears under Enterprise applications until you delete it; we suggest deleting it after the engagement. |
| What your security team may see | Our sign-ins in your logs and possibly an automated alert. We tell them the audit date and our sign-in details in advance. |
| What users see | Nothing. No e-mail, prompt, notification or install for any employee or device. |
What an Entra ID audit typically uncovers
From the sample report for Veltrana Logistics, a fictional company. Real client findings are confidential and never published.
| Finding (SAMPLE) | Severity | Business risk |
|---|---|---|
| Seven permanent Global Administrators; two without MFA | Critical | Full tenant takeover |
| No Conditional Access policy requires MFA for all users | Critical | Account takeover |
| Two accounts signed in from a password-spraying source | Critical | Active compromise |
| Legacy authentication still allowed | High | MFA bypass |
| Any user can consent to third-party apps | High | Mail and file access by rogue apps |
Sample score: 54 / 100 · 41 findings · 12 business risks.
| Observation | 7 permanent Global Administrators (target 2–4, eligible through PIM). 2 of them have never registered an MFA method. |
| Impact | One stolen password on these accounts gives full control of mail, files, users and billing. |
| Recommendation | Reduce to 2–4, make the rest eligible in PIM, require phishing-resistant MFA for all admin roles. |
| Affected | 7 accounts (listed in the workbook) |
| Frameworks | NIST CSF 2.0 PR.AA · ISO 27001:2022 A.5.15, A.8.2 · CIS M365 |
What the Entra ID audit does for your business
Close account-takeover paths
MFA gaps, legacy sign-ins and weak methods found account by account.
Shrink the admin blast radius
Standing Global Admins cut to the few you need, the rest just-in-time.
Know which apps hold the keys
Every app with access to mail and files, who approved it and whether it is still needed.
Catch attacks already happening
Spray, brute force and MFA fatigue found in your own logs, not in theory.
Evidence for insurers and auditors
MFA, admin and logging evidence mapped to NIST CSF, ISO 27001, HIPAA and cyber-insurance questions.
A plan leadership can fund
Business risks with owners, dates and a 180-day roadmap instead of a list of settings.
A report pack leadership and IT can both use
Every deliverable is reviewed by the assessor and written in plain English. See every page of the sample report →
Report date June 30, 2026
Prepared by Ali Hassani, C|CISO, CISSP
Report date June 30, 2026
Prepared by Ali Hassani, C|CISO, CISSP
Report date June 30, 2026
Prepared by Ali Hassani, C|CISO, CISSP
Report date June 30, 2026
Prepared by Ali Hassani, C|CISO, CISSP
Report date June 30, 2026
Prepared by Ali Hassani, C|CISO, CISSP
| Deliverable | What it contains | Who uses it |
|---|---|---|
| Executive Security Report | Score, top business risks, what is working, priority decisions for leadership | Owners, executives |
| Technical Security Configuration Report | Every finding with evidence, impact, fix steps and NIST / ISO / CIS mapping | IT team, MSP |
| Identity Threat & Sign-in Analysis | 30 days of sign-in and audit logs reviewed for attacks, with charts and an attack chain | IT, security, leadership |
| Risk Register | Business risks scored likelihood × impact, heat maps, owners and target dates | Leadership, compliance |
| Next Steps & Security Roadmap | Phased actions and projects from 0–7 days to 180 days | IT team, leadership |
| Technical Findings Workbook (Excel) | Findings tracker with formulas, drop-downs and charts | IT team, MSP |
| Remediation Progress Report (follow-up audit) | Before-and-after score, resolved, still-open and new findings | Leadership, insurers |
Every report comes as Word and PDF. The Remediation Progress Report comes with a follow-up audit.
Five steps from scoping call to readout
Remote-friendly; your administrator spends a few minutes on one approval.
Scoping call
Tenant size, compliance drivers (HIPAA, IRS WISP, insurance) and your concerns. We agree the audit date with your security team.
One read-only approval
Your Global Administrator approves our read-only audit app once, with one link; we sign in with a Global Reader account.
Review against 72 checks
Users, admins, Conditional Access, apps, guests, devices and 30 days of sign-in and audit logs.
Assessor review
Ali reviews every finding, adjusts severity for your context and writes the business impact.
Readout and report pack
A walk-through with leadership and IT, the full report pack and a prioritized 180-day roadmap.
Built for businesses that run on Microsoft 365
Healthcare & dental
MFA, admin access and audit logs for HIPAA access-control safeguards.
Healthcare cybersecurity →
CPA & tax firms
The MFA and access controls your IRS WISP relies on, checked account by account.
CPA firm cybersecurity →
Law & professional services
Guest access, app consent and sign-in attacks against client-confidential mail.
Law firm cybersecurity →
MSP clients & partners
Independent validation of the tenant your MSP manages.
Security audit for MSP clients →Findings mapped to the frameworks your auditors and insurers use
Each check maps to NIST CSF 2.0, ISO/IEC 27001:2022 Annex A and the CIS Microsoft 365 Foundations Benchmark.
Three audits, one Microsoft cloud
Microsoft 365 security audit
Identity, email and Defender, SPF/DKIM/DMARC, SharePoint and Teams sharing, Purview and logging: the whole tenant, 200 checks.
Microsoft Entra ID security audit
Identity in depth: 72 checks on sign-in, admins, Conditional Access, apps and guests, plus 30 days of sign-in logs read for attacks.
Microsoft Intune security audit
Devices in depth: 127 checks on compliance, encryption, Defender, updates, apps and app protection.
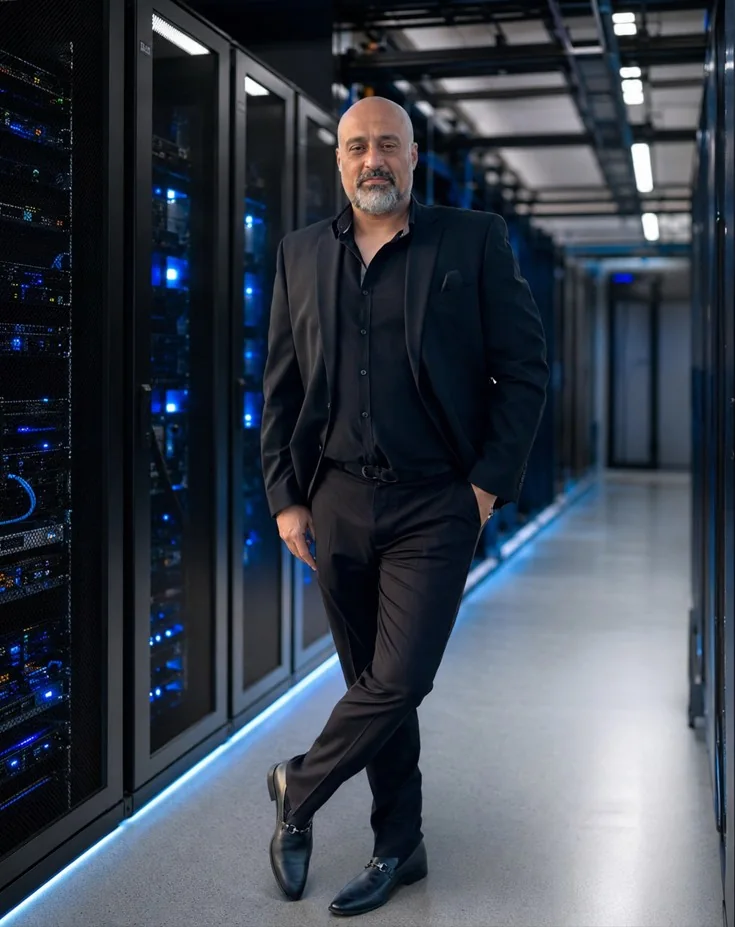
Every Entra ID audit is led by Ali Hassani, CISO
Certified CISO (C|CISO) and CISSP with 25+ years in IT, cybersecurity, compliance and infrastructure. Ali personally reviews every finding before it reaches your desk, and walks your leadership and IT team through the results.
He holds dozens of Microsoft and Cisco credentials (CCNP, CCNA, MCSE, MCITP, MCSA Security) and works on-site across Orange County, Los Angeles and Southern California, and remotely for organizations nationwide.
Not ready to talk? Get a first read for free.
Free tools give initial guidance only; they do not replace a professional audit.
Questions about the Entra ID audit
Scope, access, what your team will see and how it fits with our other Microsoft audits.
Will the audit change anything in our tenant?
What access do you need?
What will our administrators and users see?
Why read our sign-in logs?
Do we need Entra ID P1 or P2?
How is this different from the Microsoft 365 audit?
How is it different from Microsoft Secure Score?
How much does the Entra ID audit cost?
Implementation partner
OC Security Audit stays independent and read-only. If you want hands-on administration, IT Perfection can implement the fixes and support ongoing operations.