
MSP security audit sample report
MSP Security Audit Sample Report
Every report from a full audit cycle for a fictional managed service provider, page by page: from the first audit to the third.
Our deliverables
Nine deliverables from a full MSP audit cycle
An MSP security audit has to serve three audiences at once: the owners who decide, the engineers who fix, and the clients and insurers who want proof. Each deliverable below is shown page by page in a slideshow, with a caption that explains what the page contains.
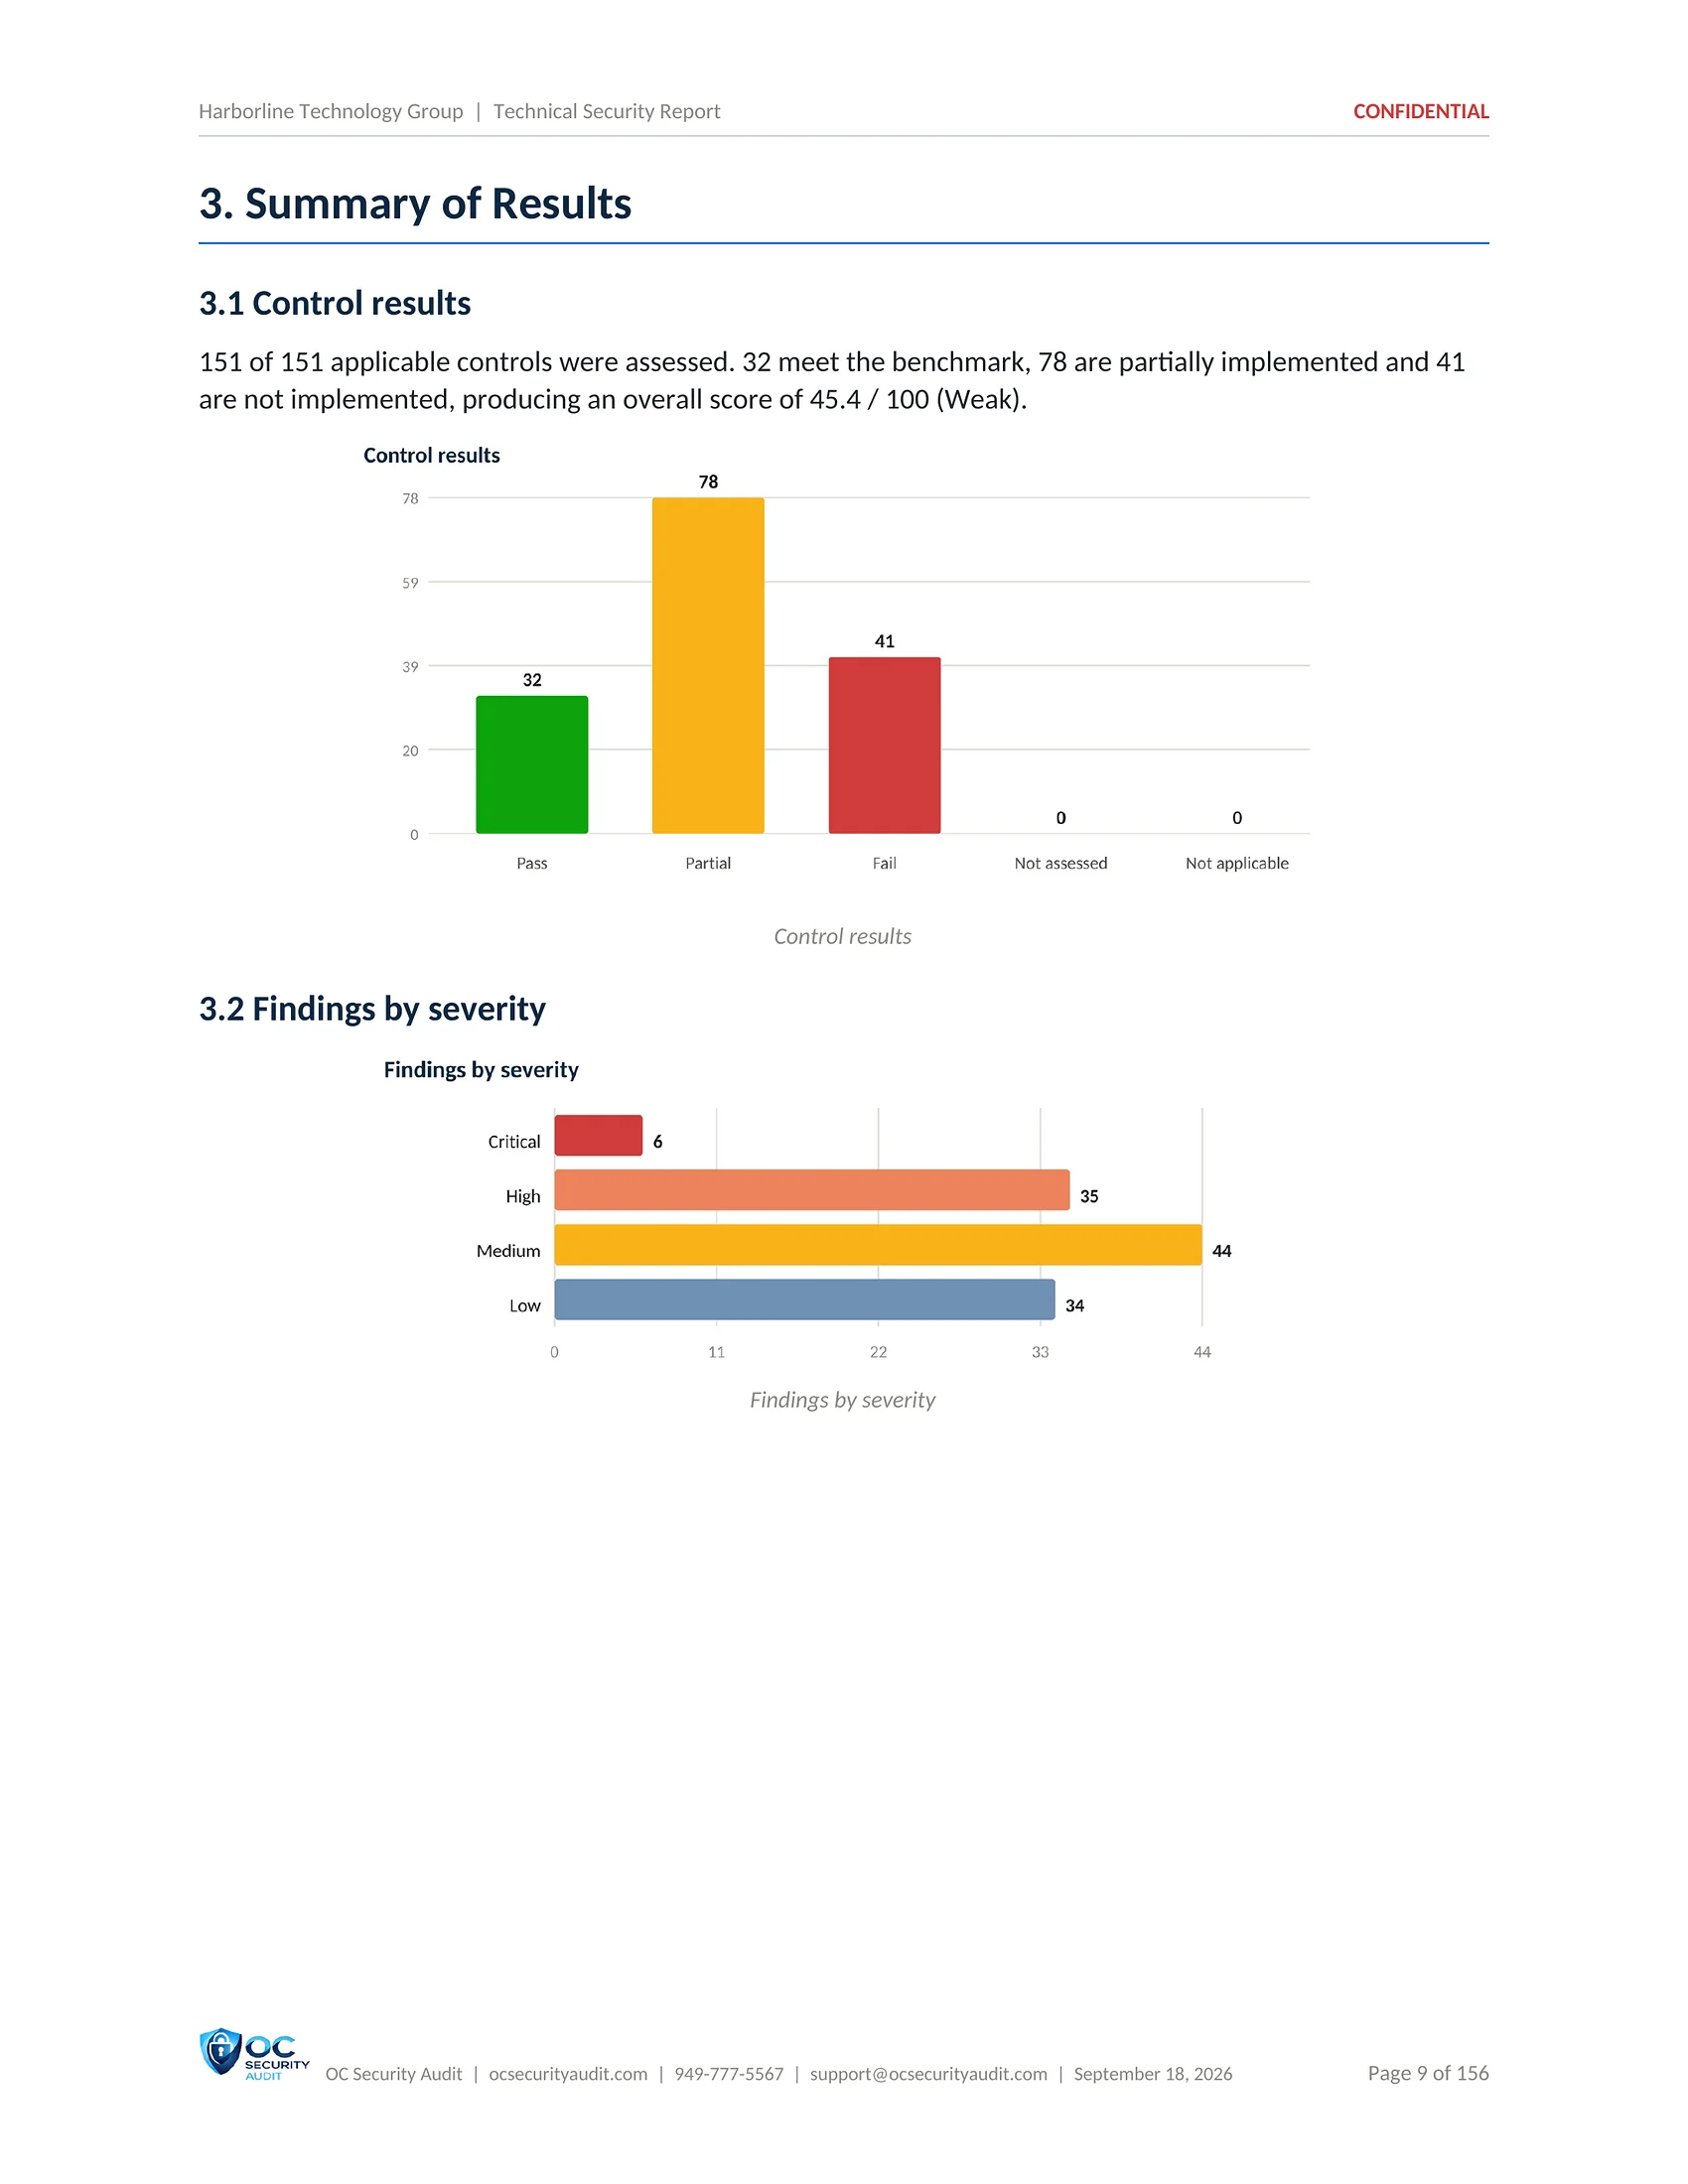
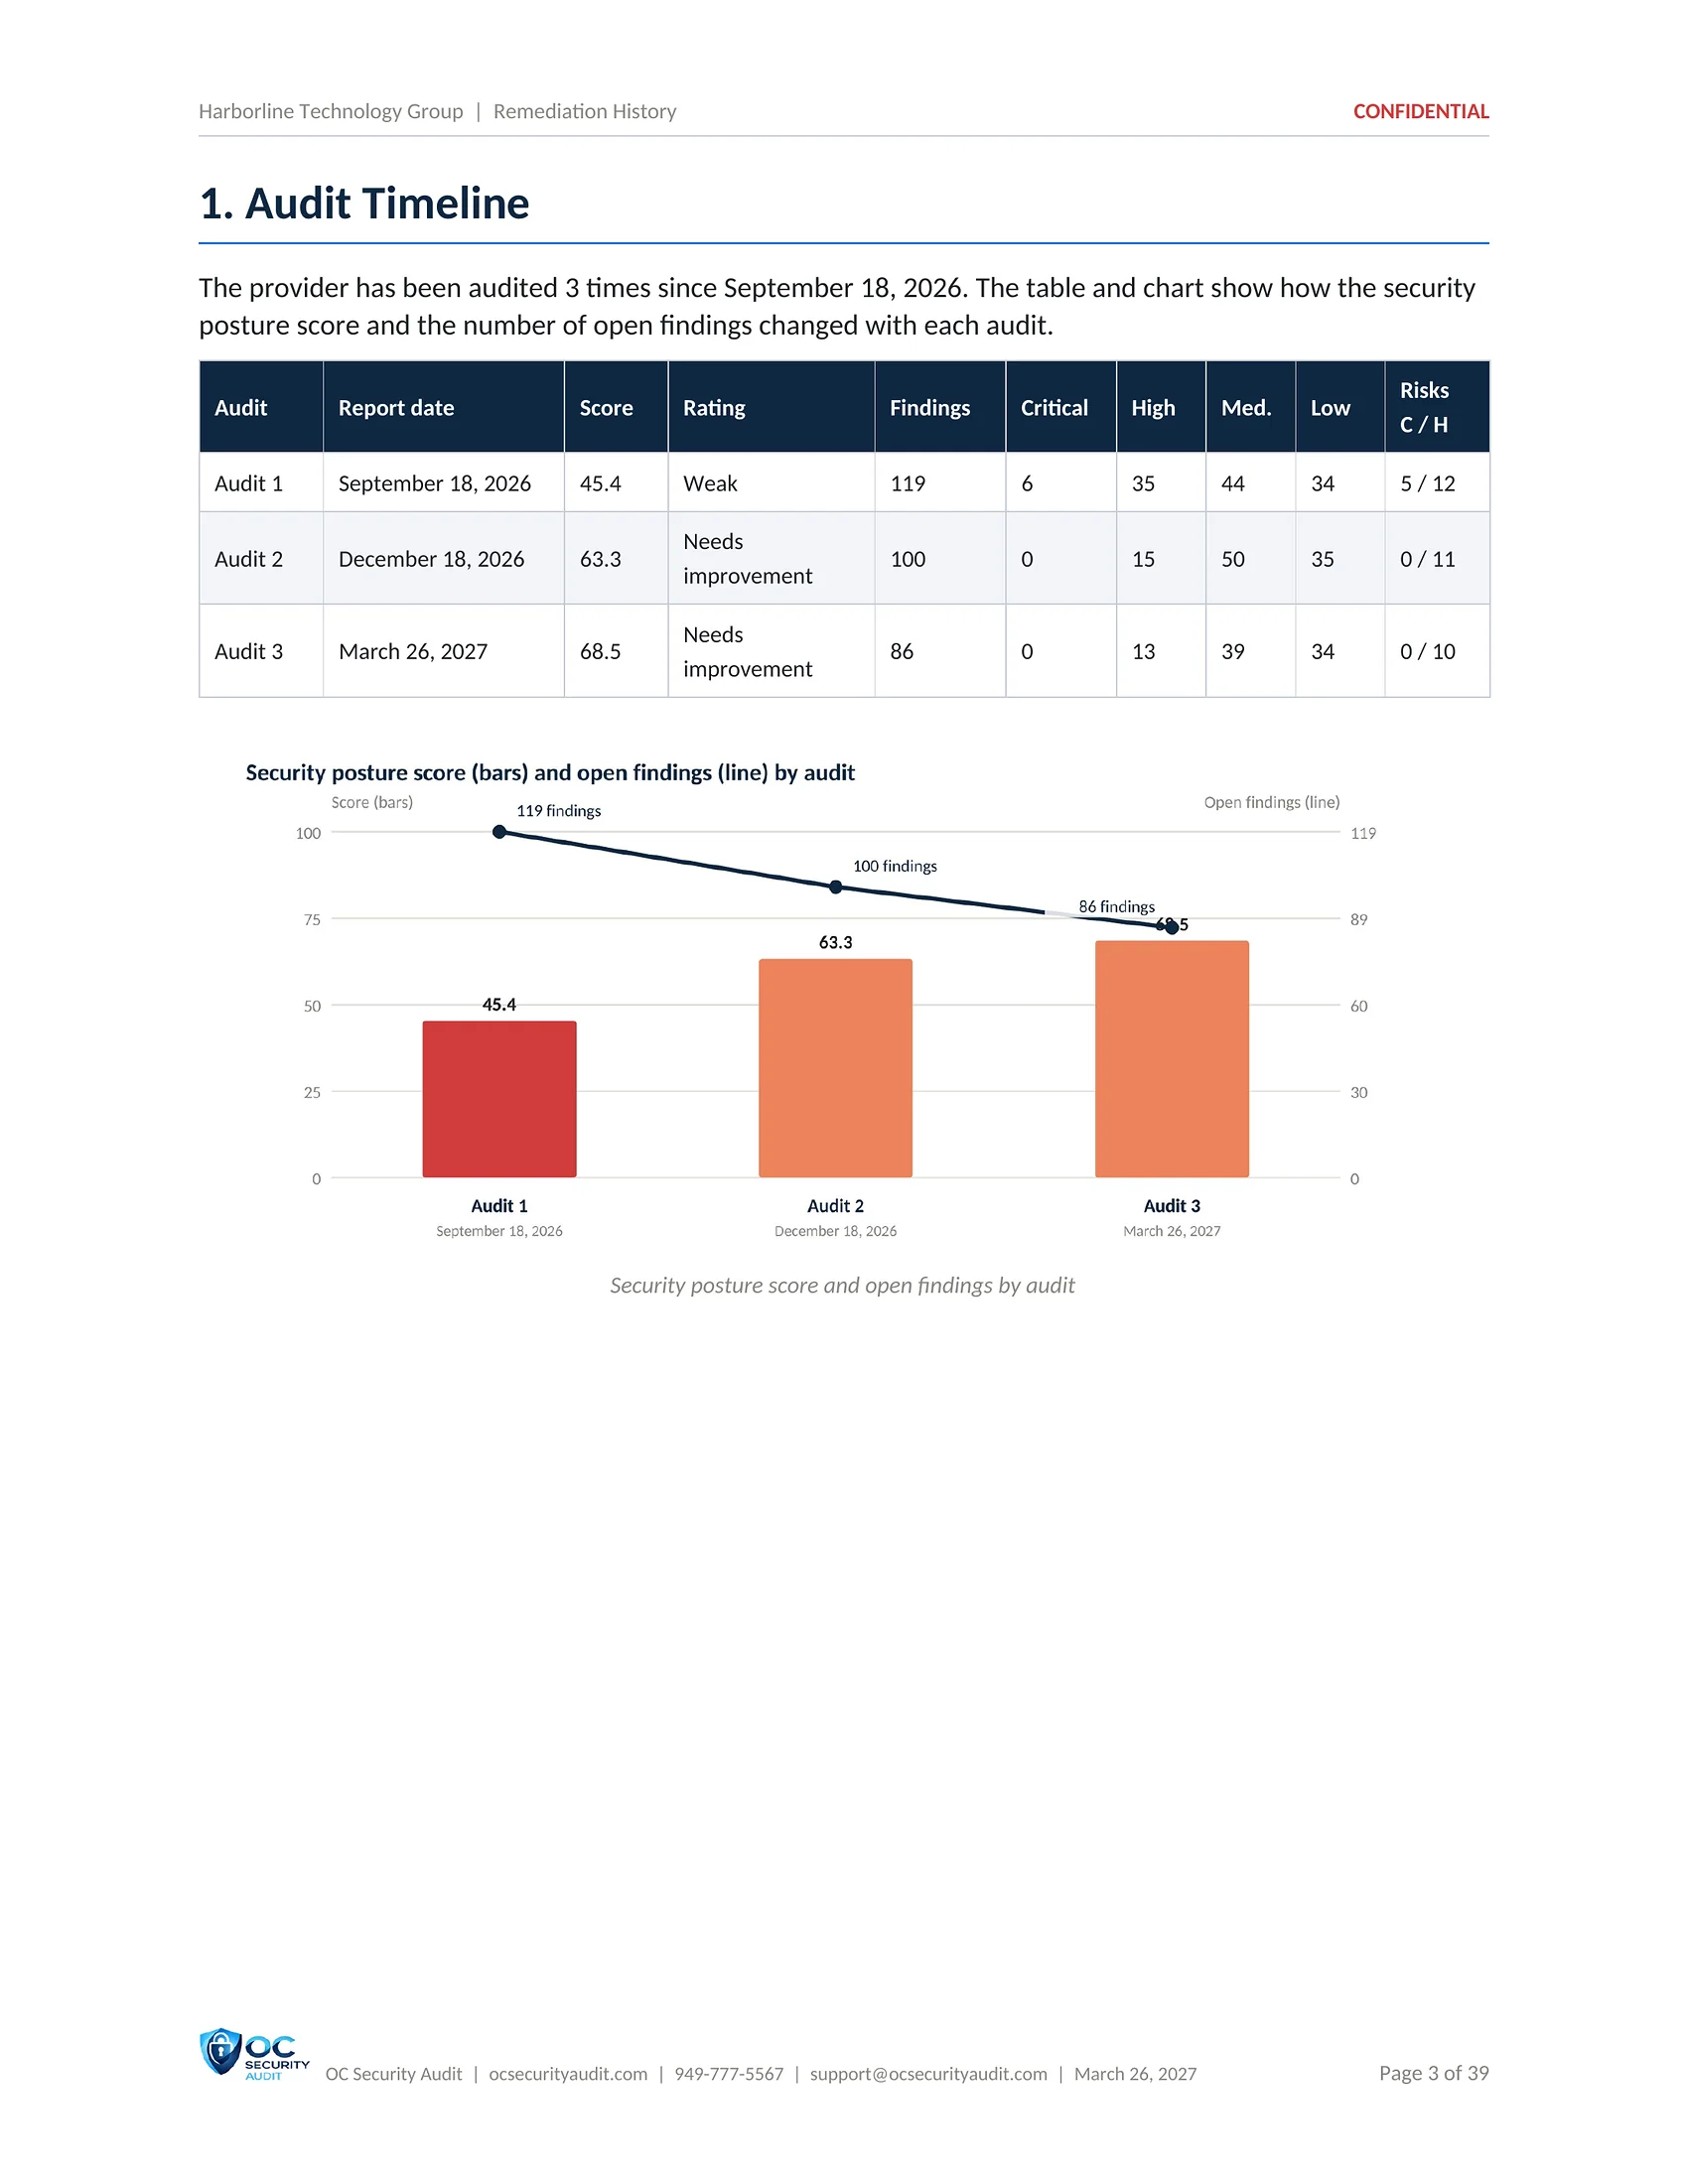
The sample follows one provider through three audits. The first audit found 119 findings and a posture score of 45.4 out of 100; after two rounds of remediation the third audit recorded 86 open findings and a score of 68.5. Most slides come from the first audit; the scorecard and the Remediation History show the later audits.
Sample data. These reports were produced for Harborline Technology Group, a fictional managed service provider with 64 clients, about 3,900 endpoints and 19 technical staff. All names, figures and observations are illustrative, and the three audits are shown on a sample timeline.
PDF and Word · 14 pages
Executive Security Report
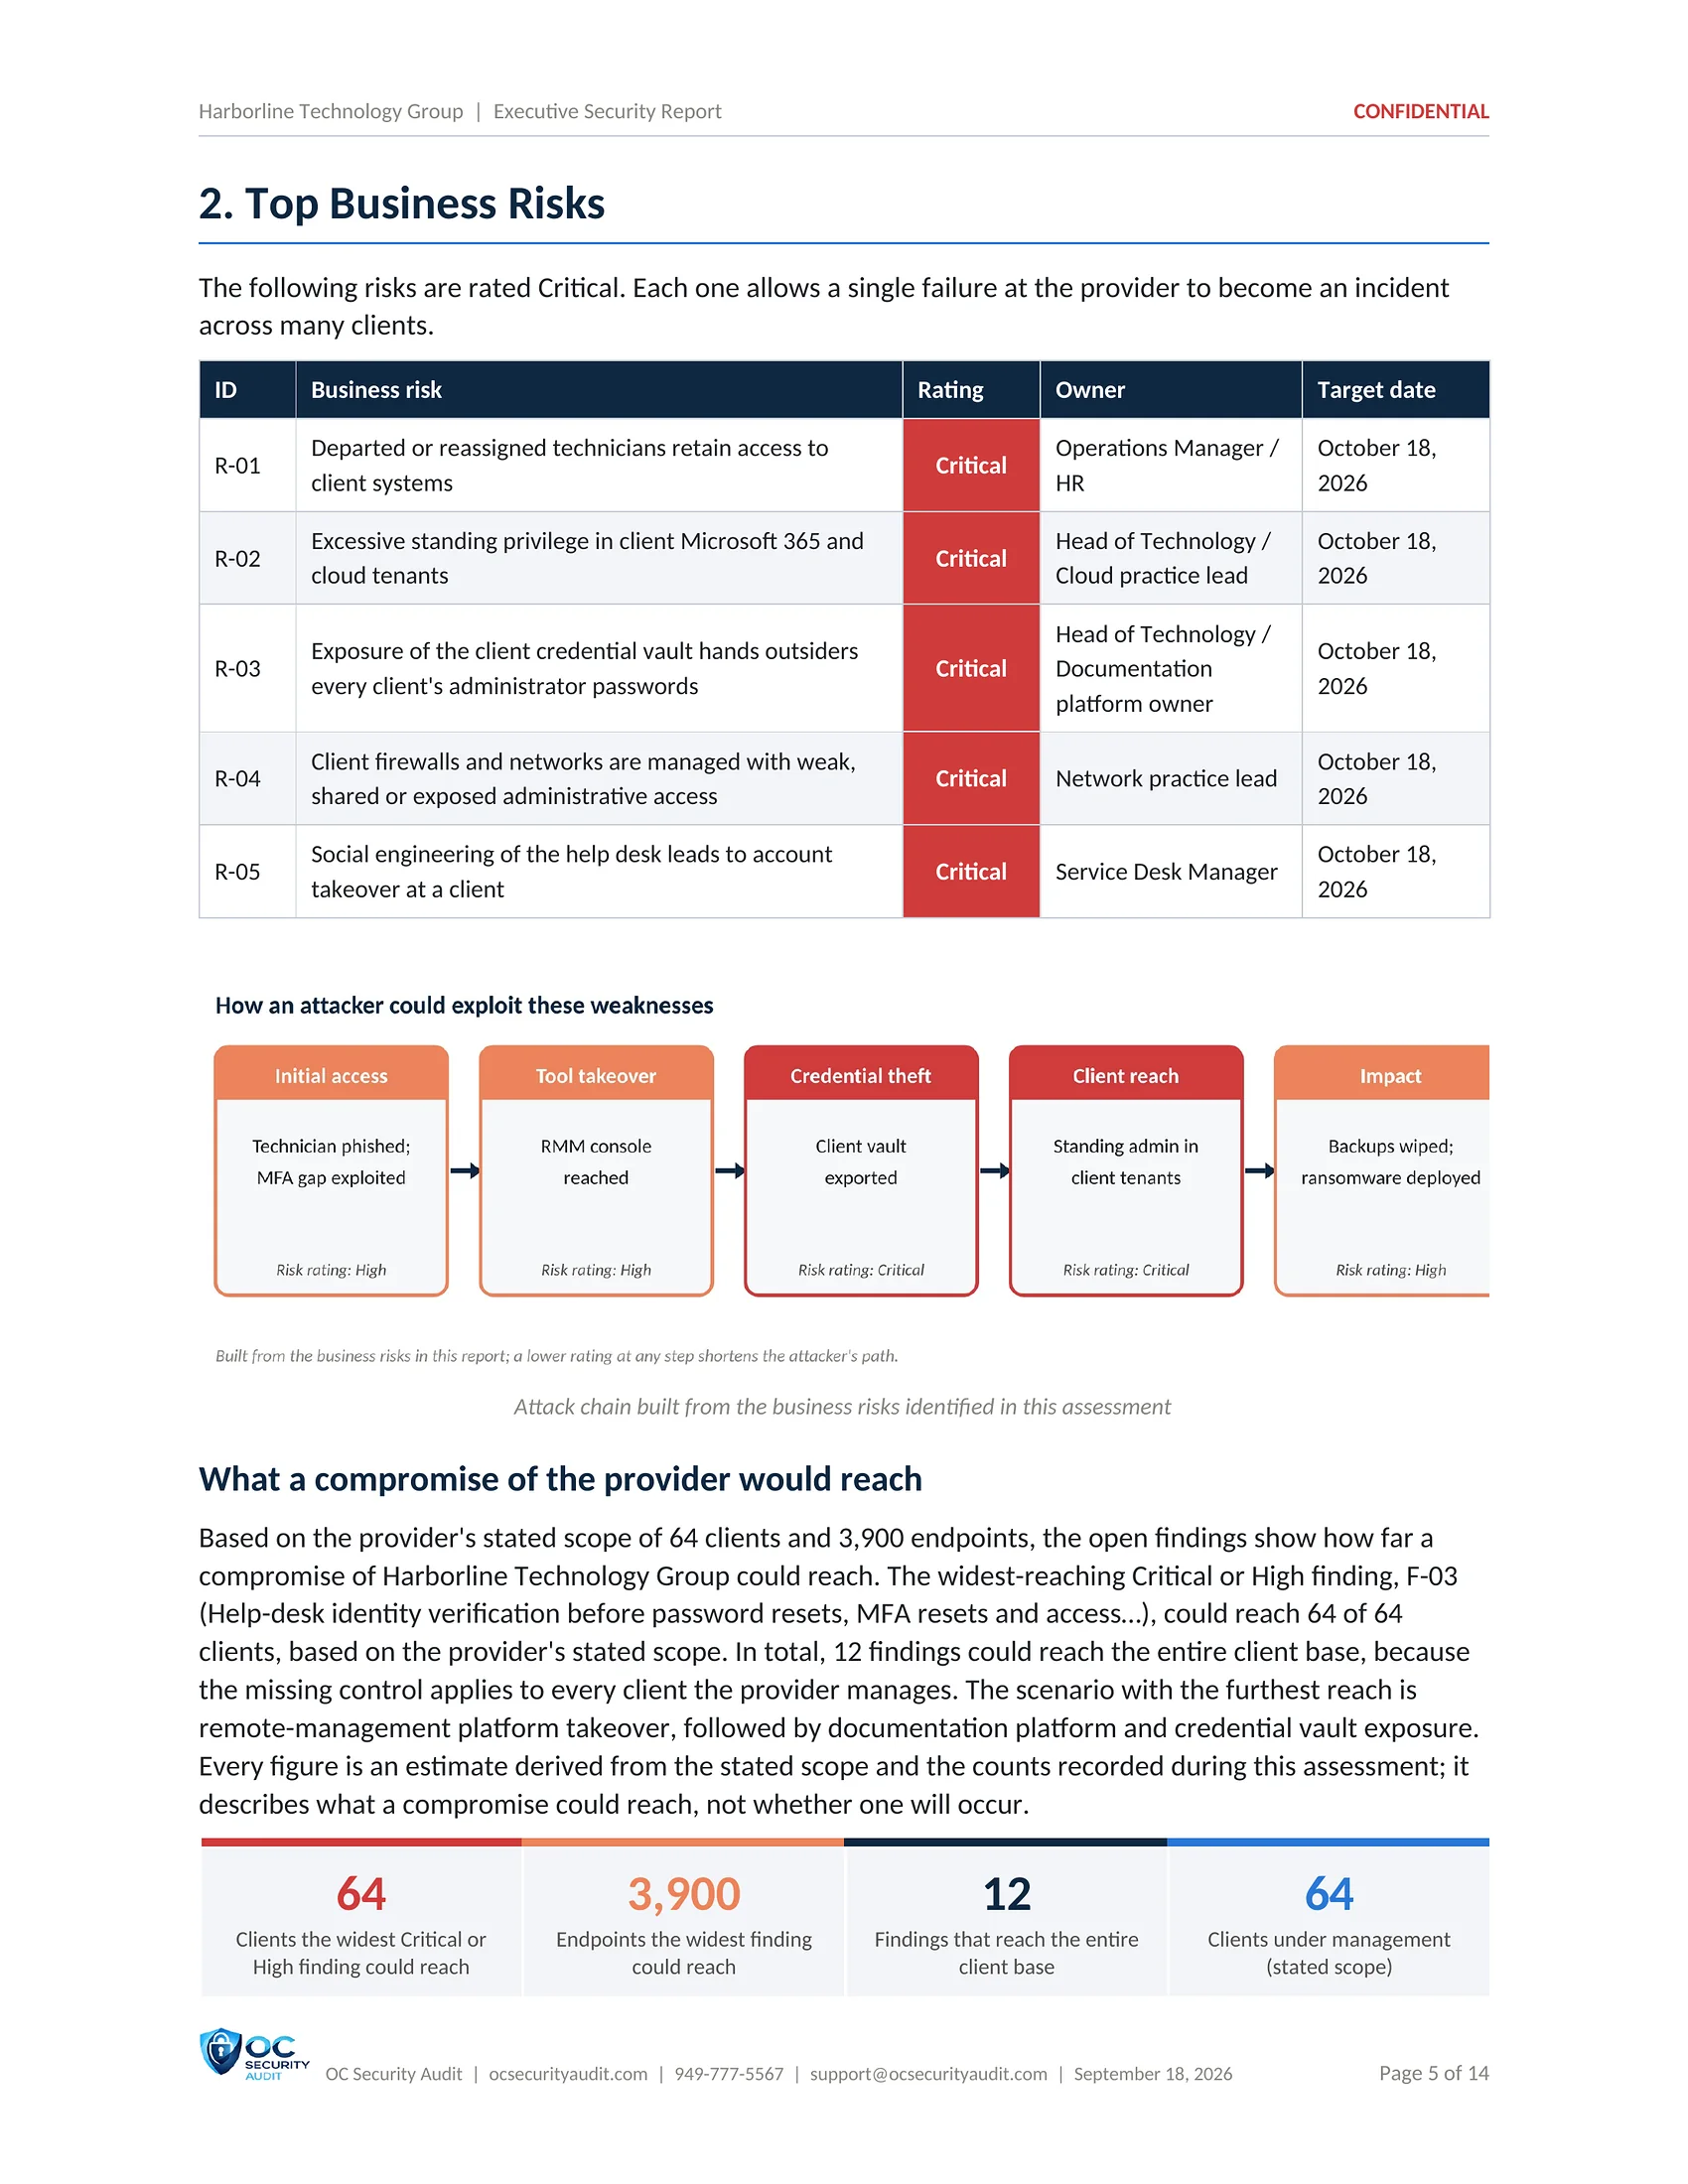
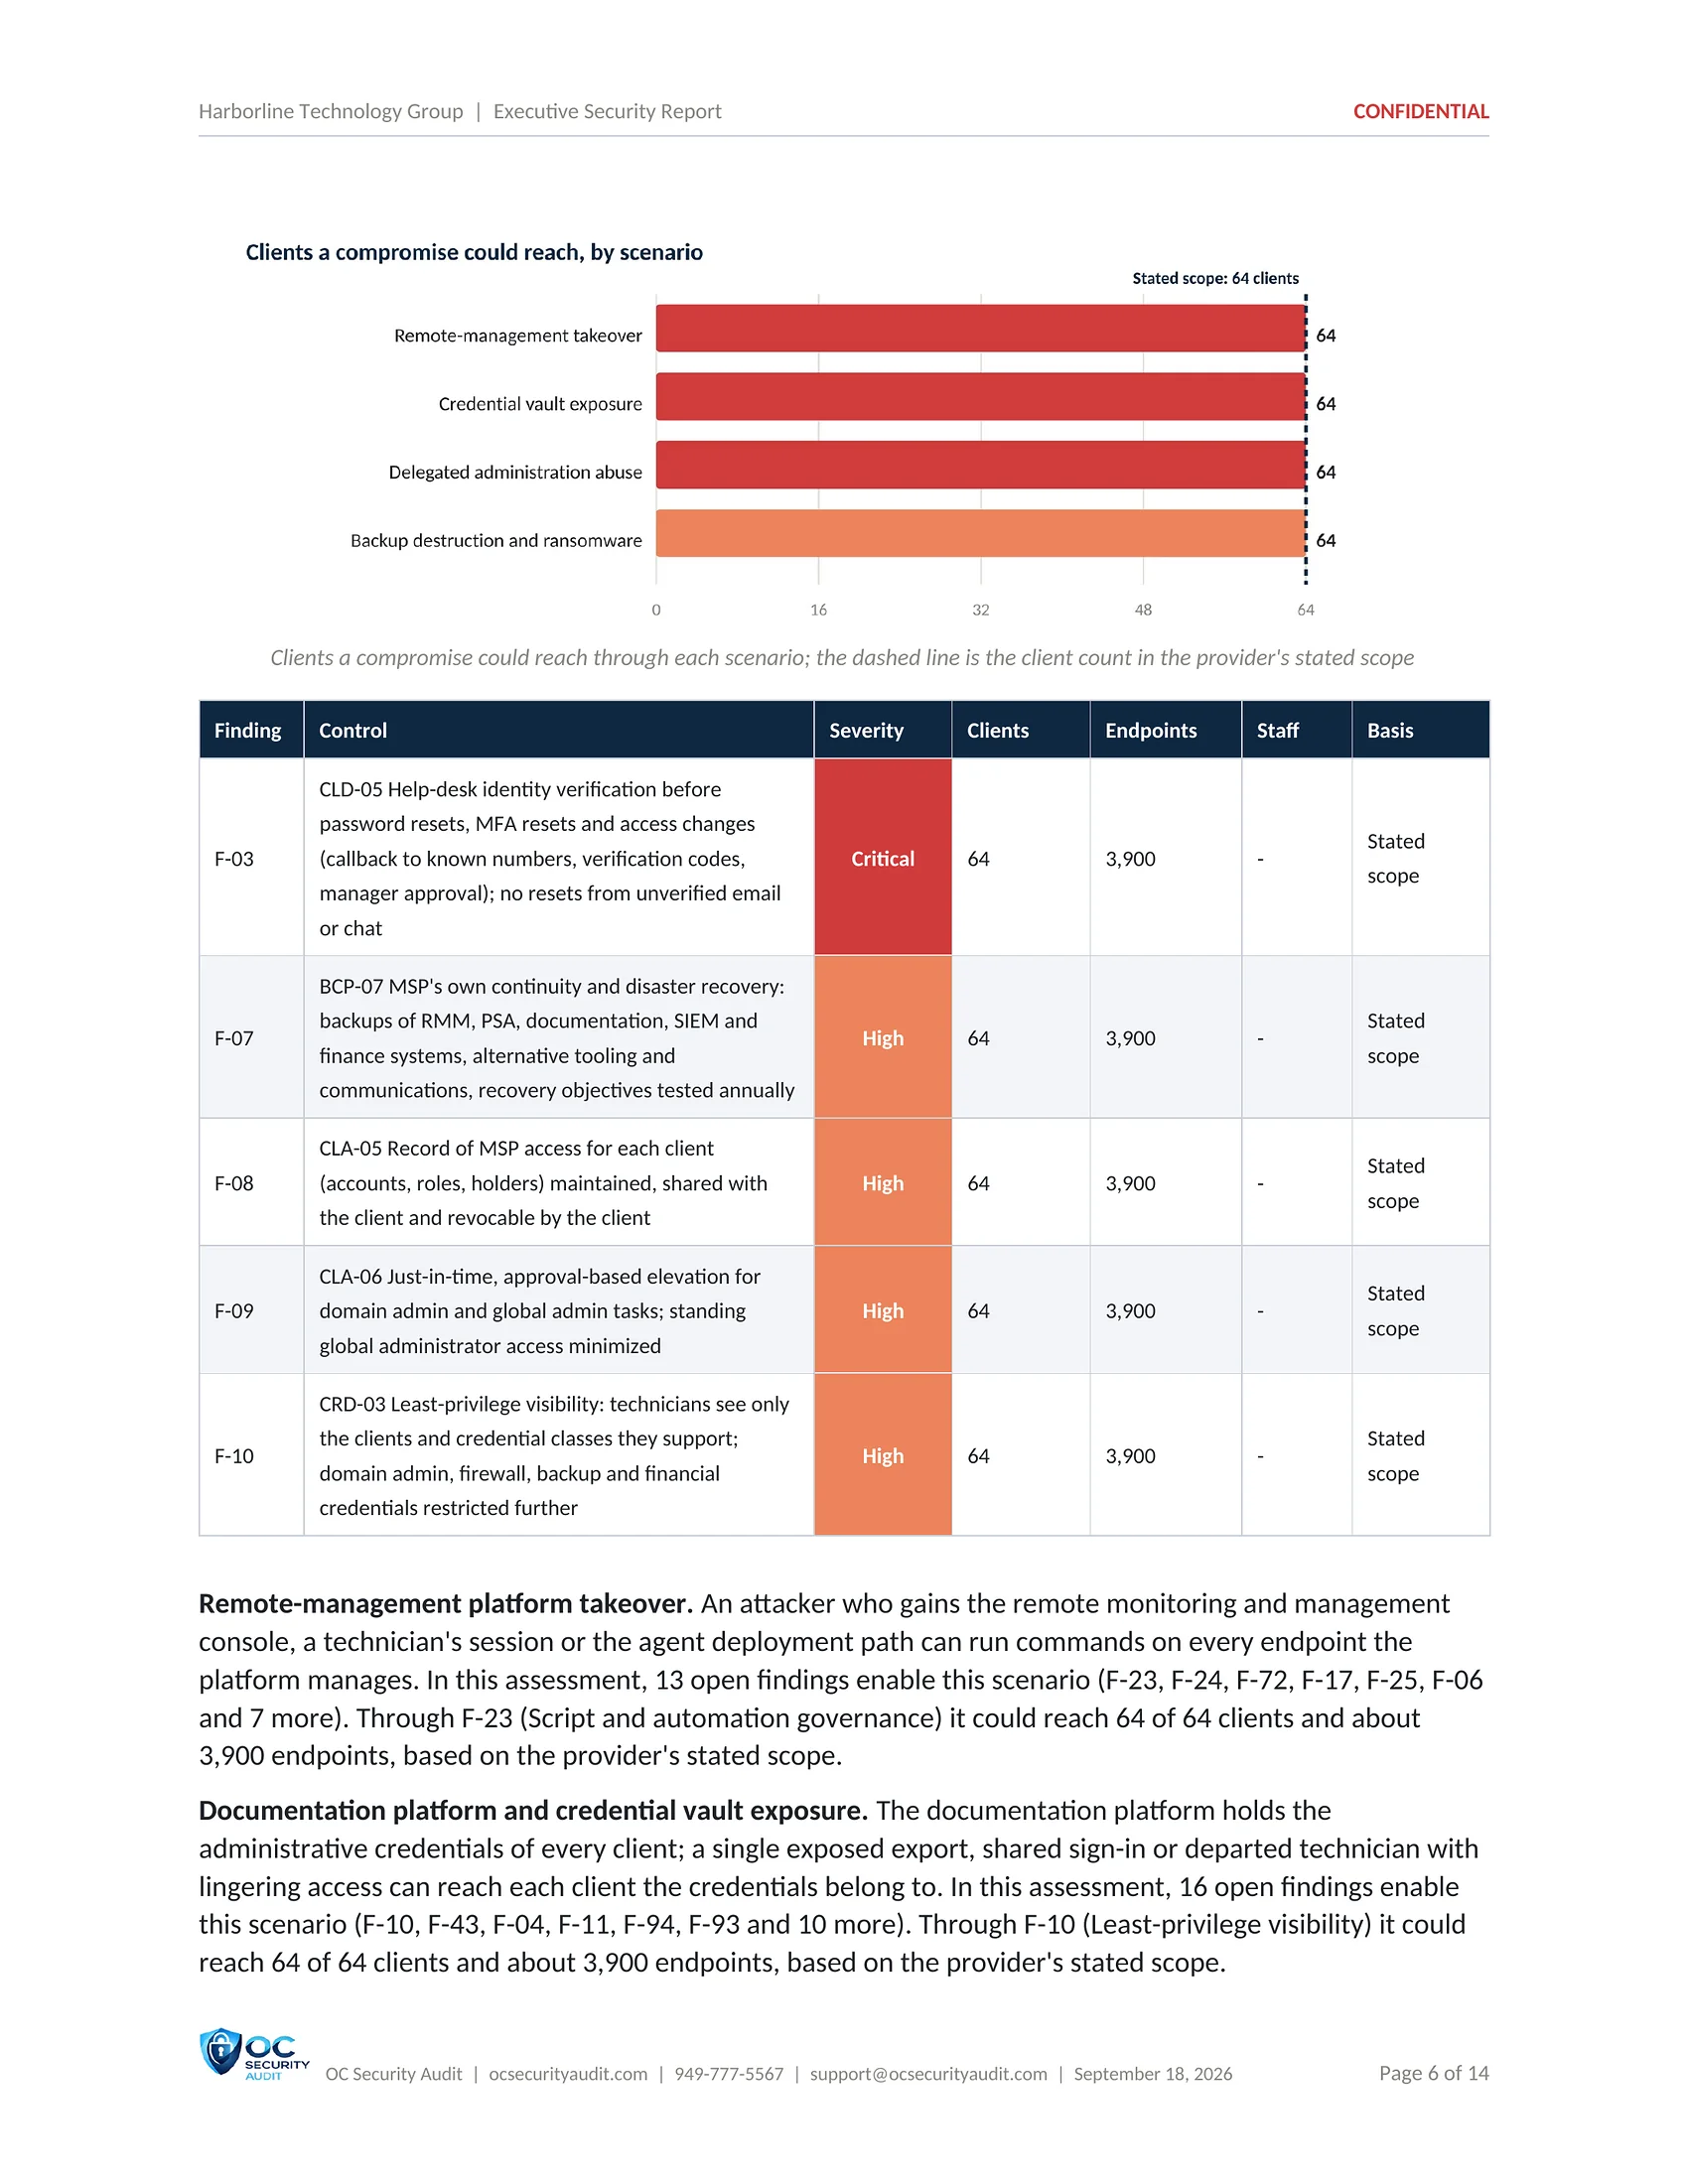
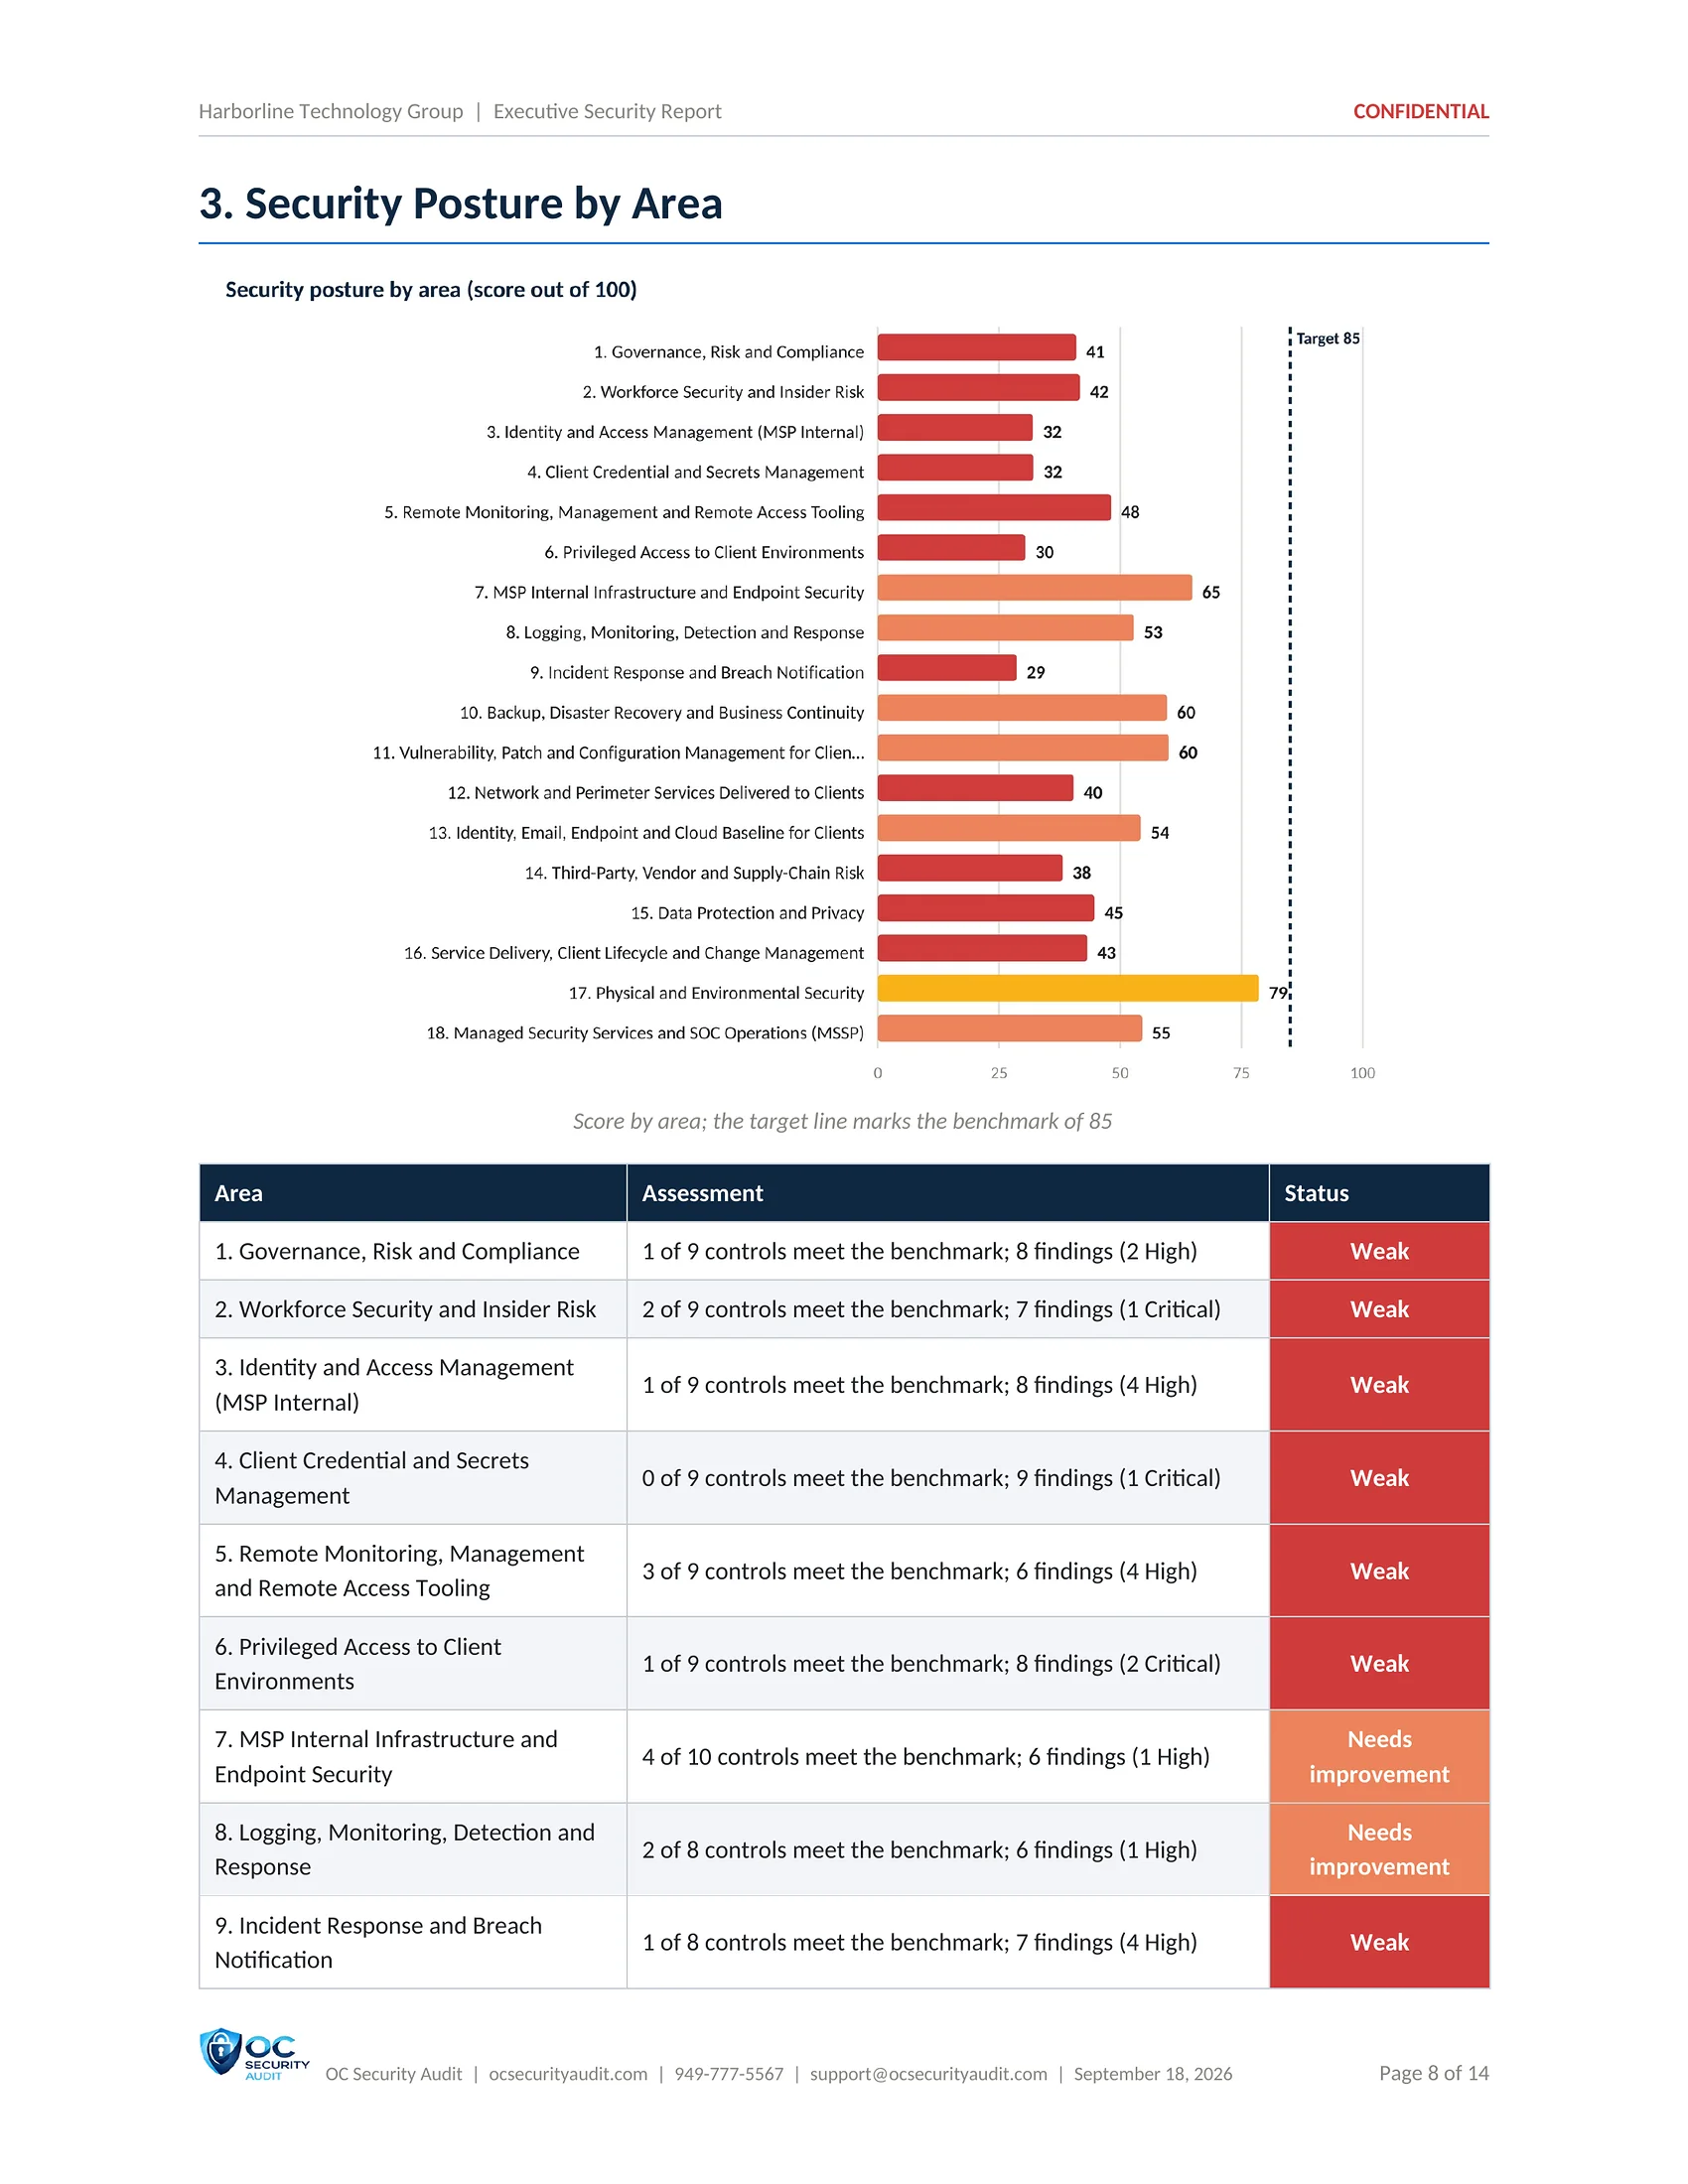
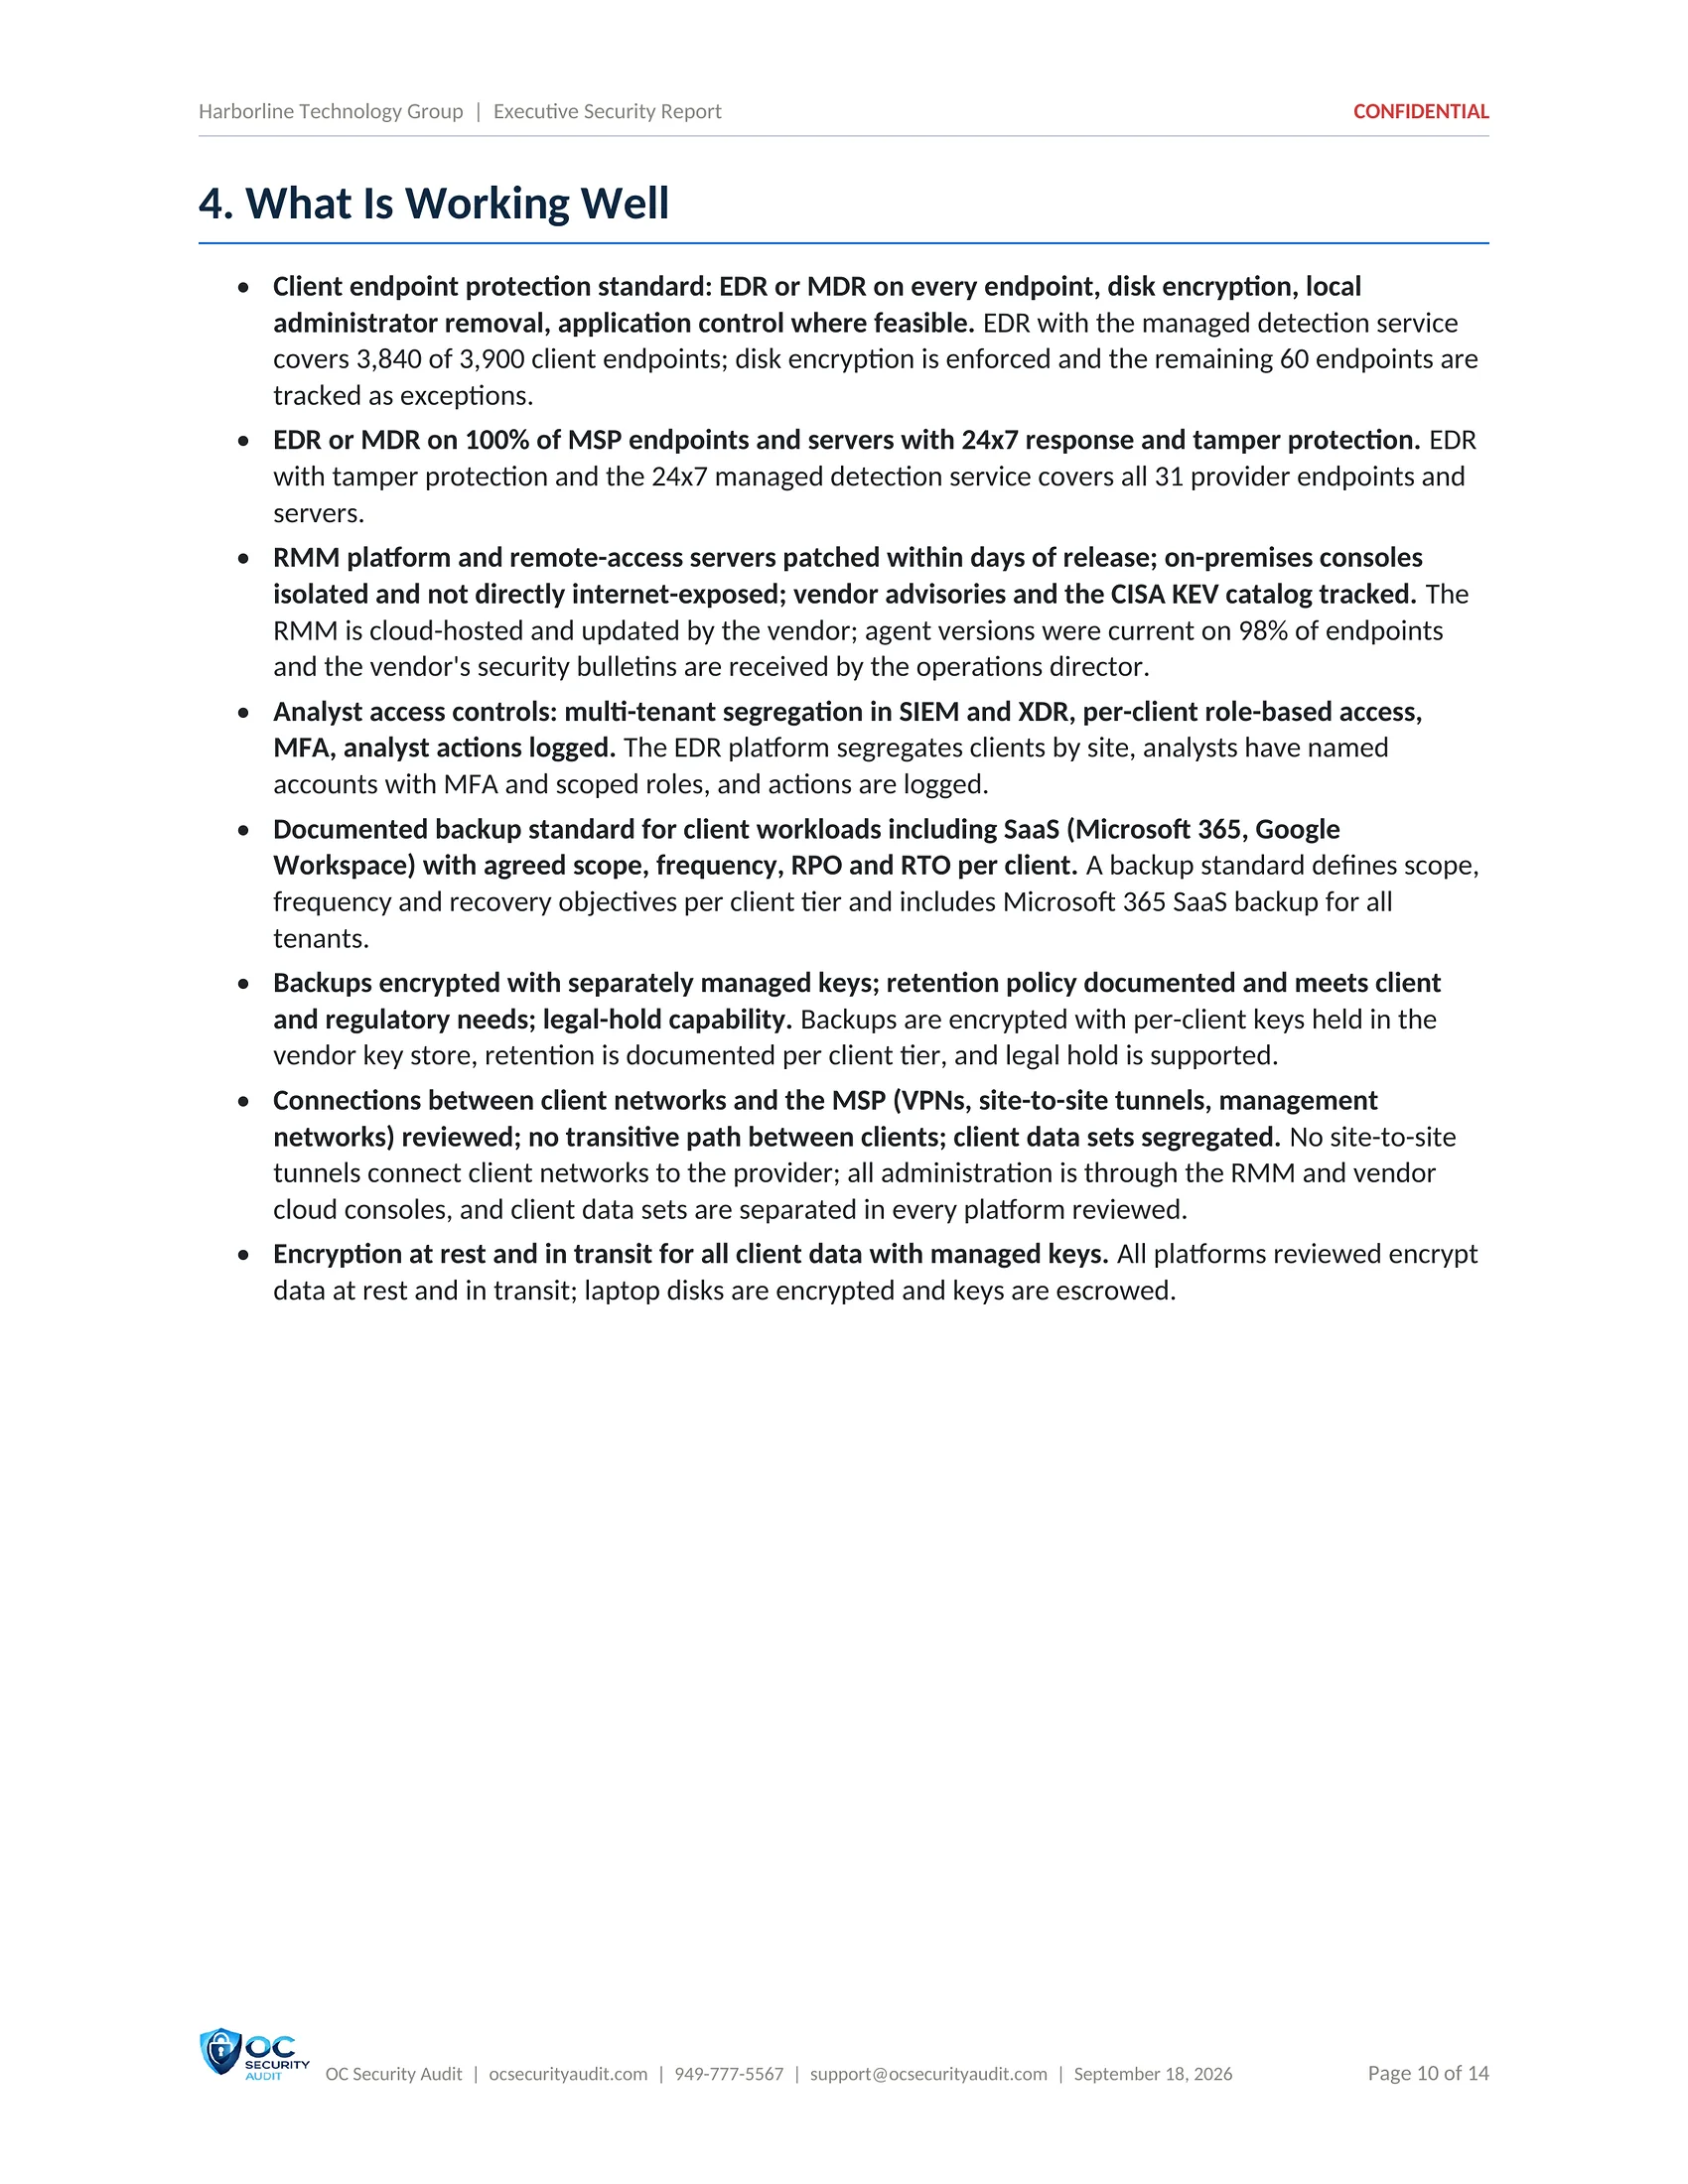
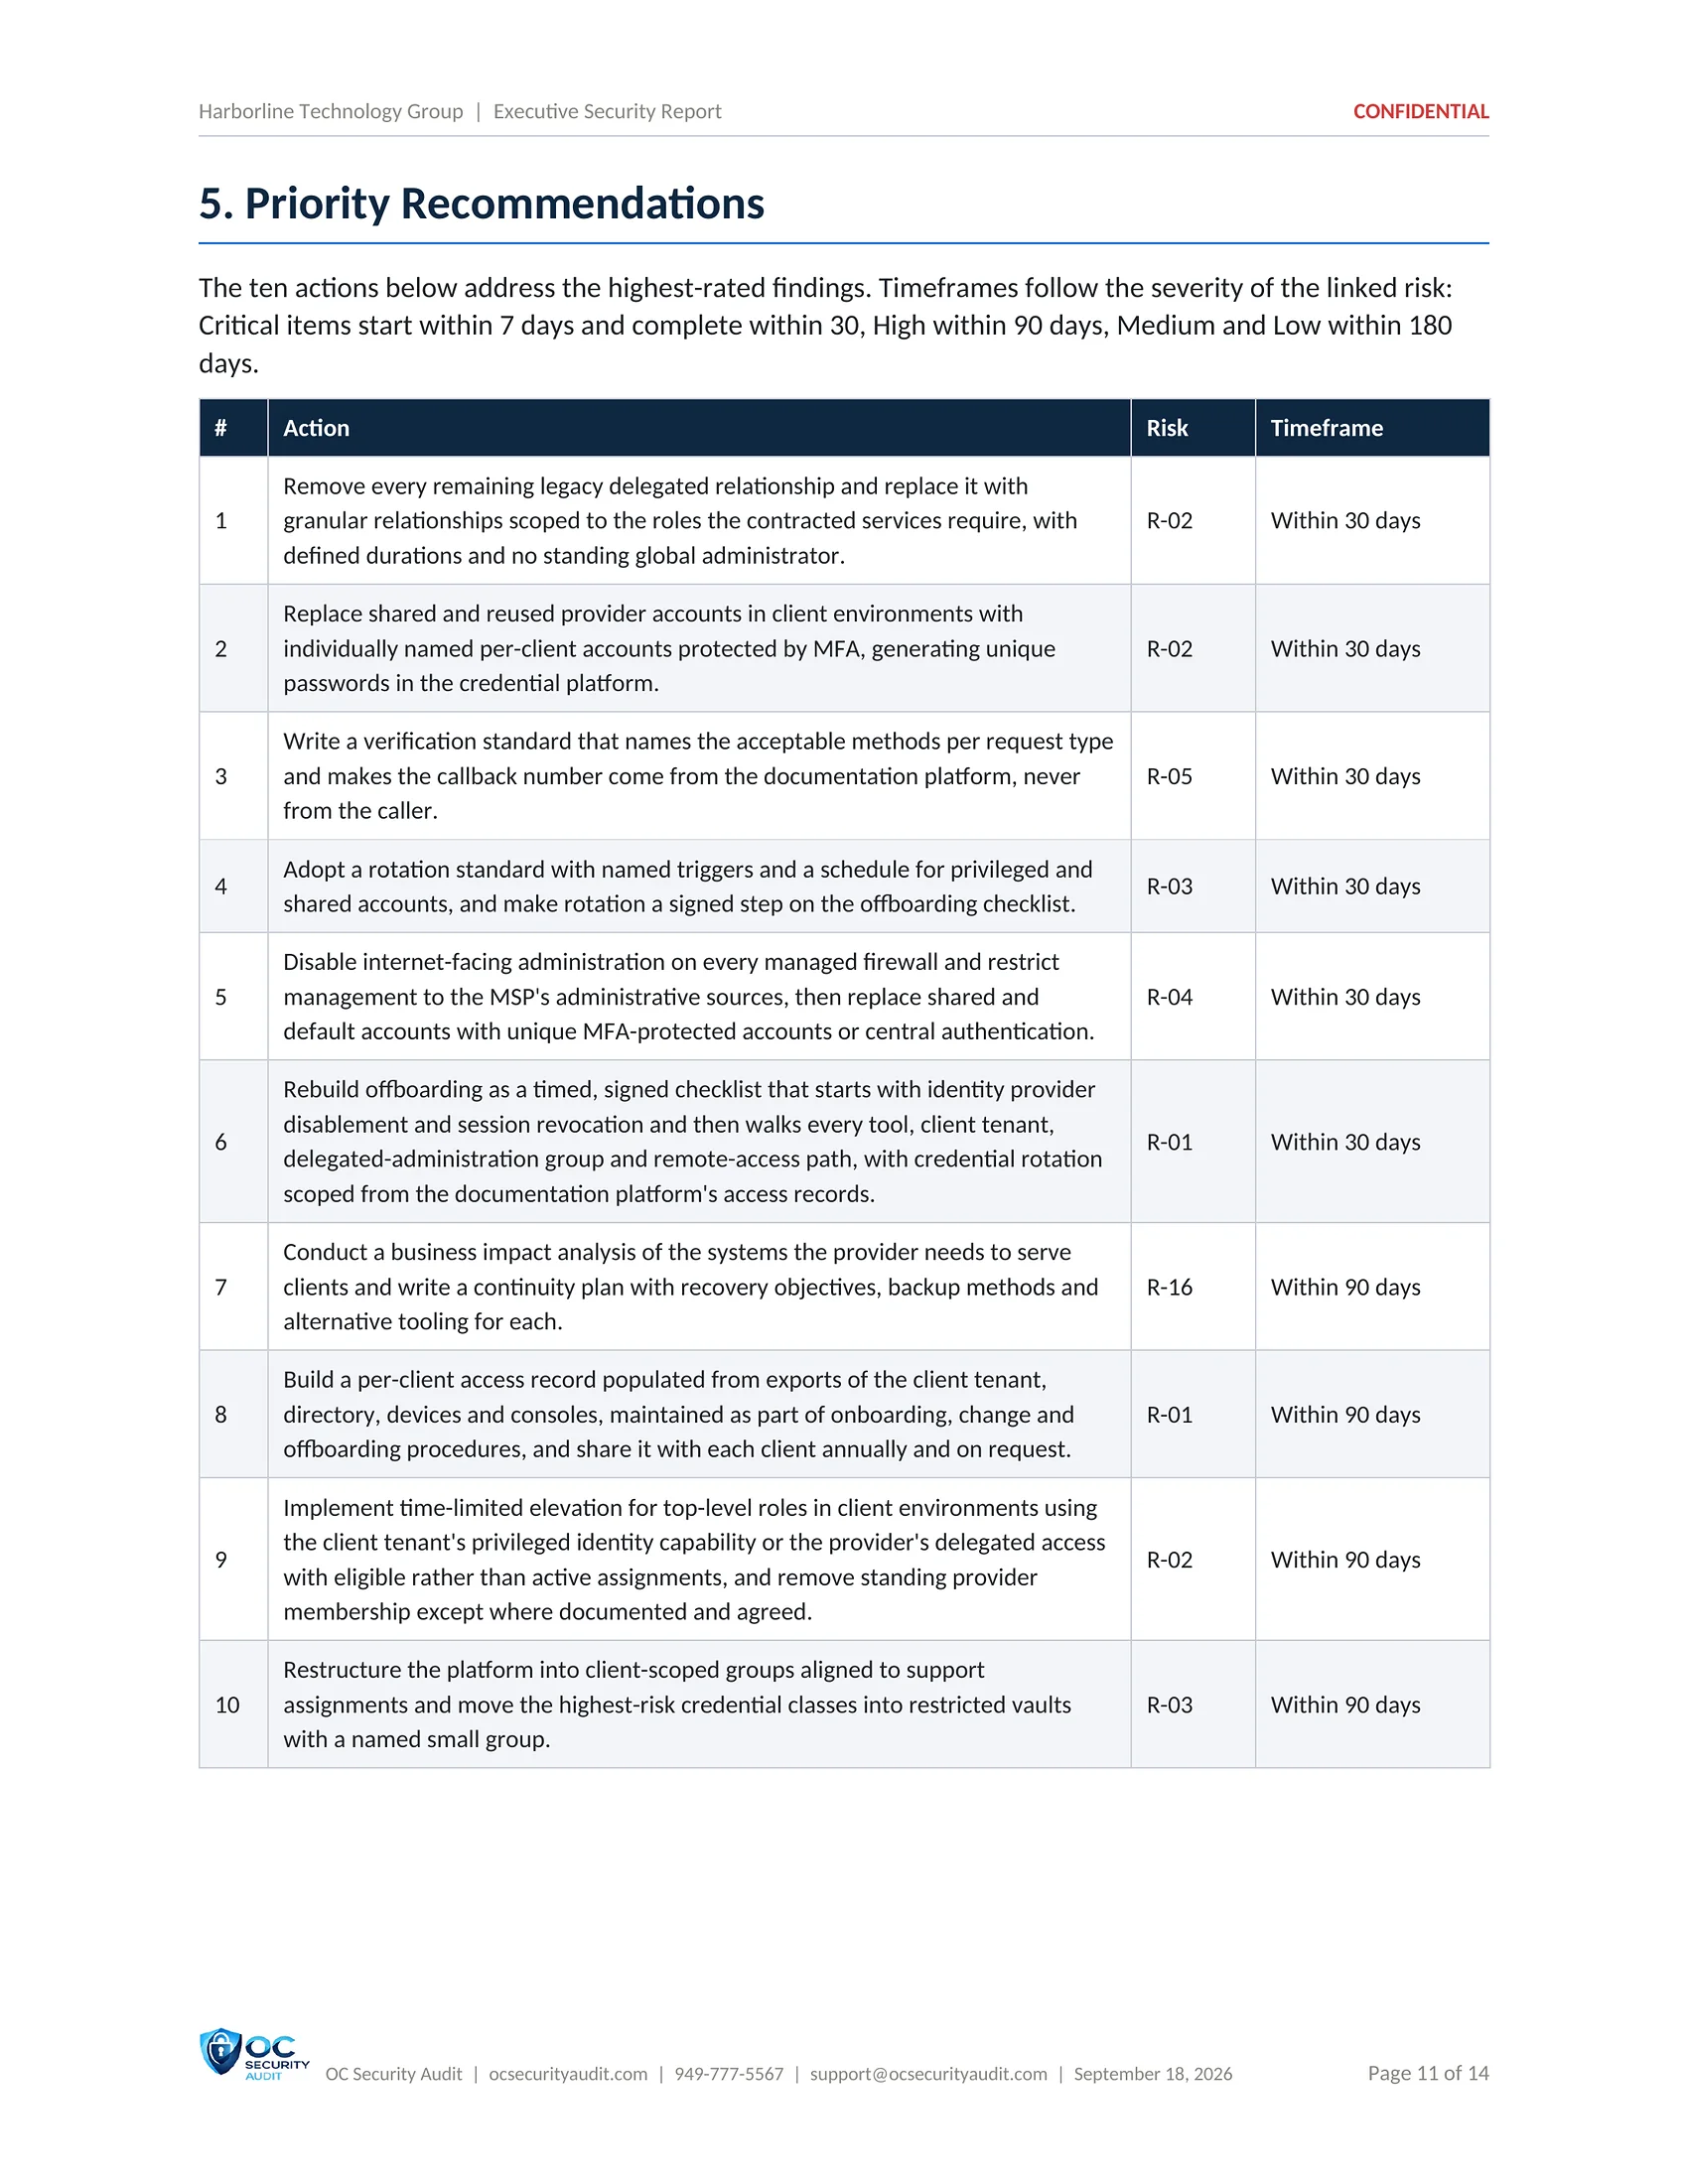
The decision document for the owners of the provider. It states the posture score and rating, the business risks that matter most, what a compromise of the provider could reach across its clients, what is already working and the decisions only leadership can make. It is written in plain language, without tool names or jargon.
Owners, partners and leadership; also the basis for conversations with insurers and large clients.
What is included
- Executive summary and posture score
- Top business risks with owners and dates
- Reach of a provider compromise
- Score for each of the 18 areas
- What is working well
- Ten priority recommendations
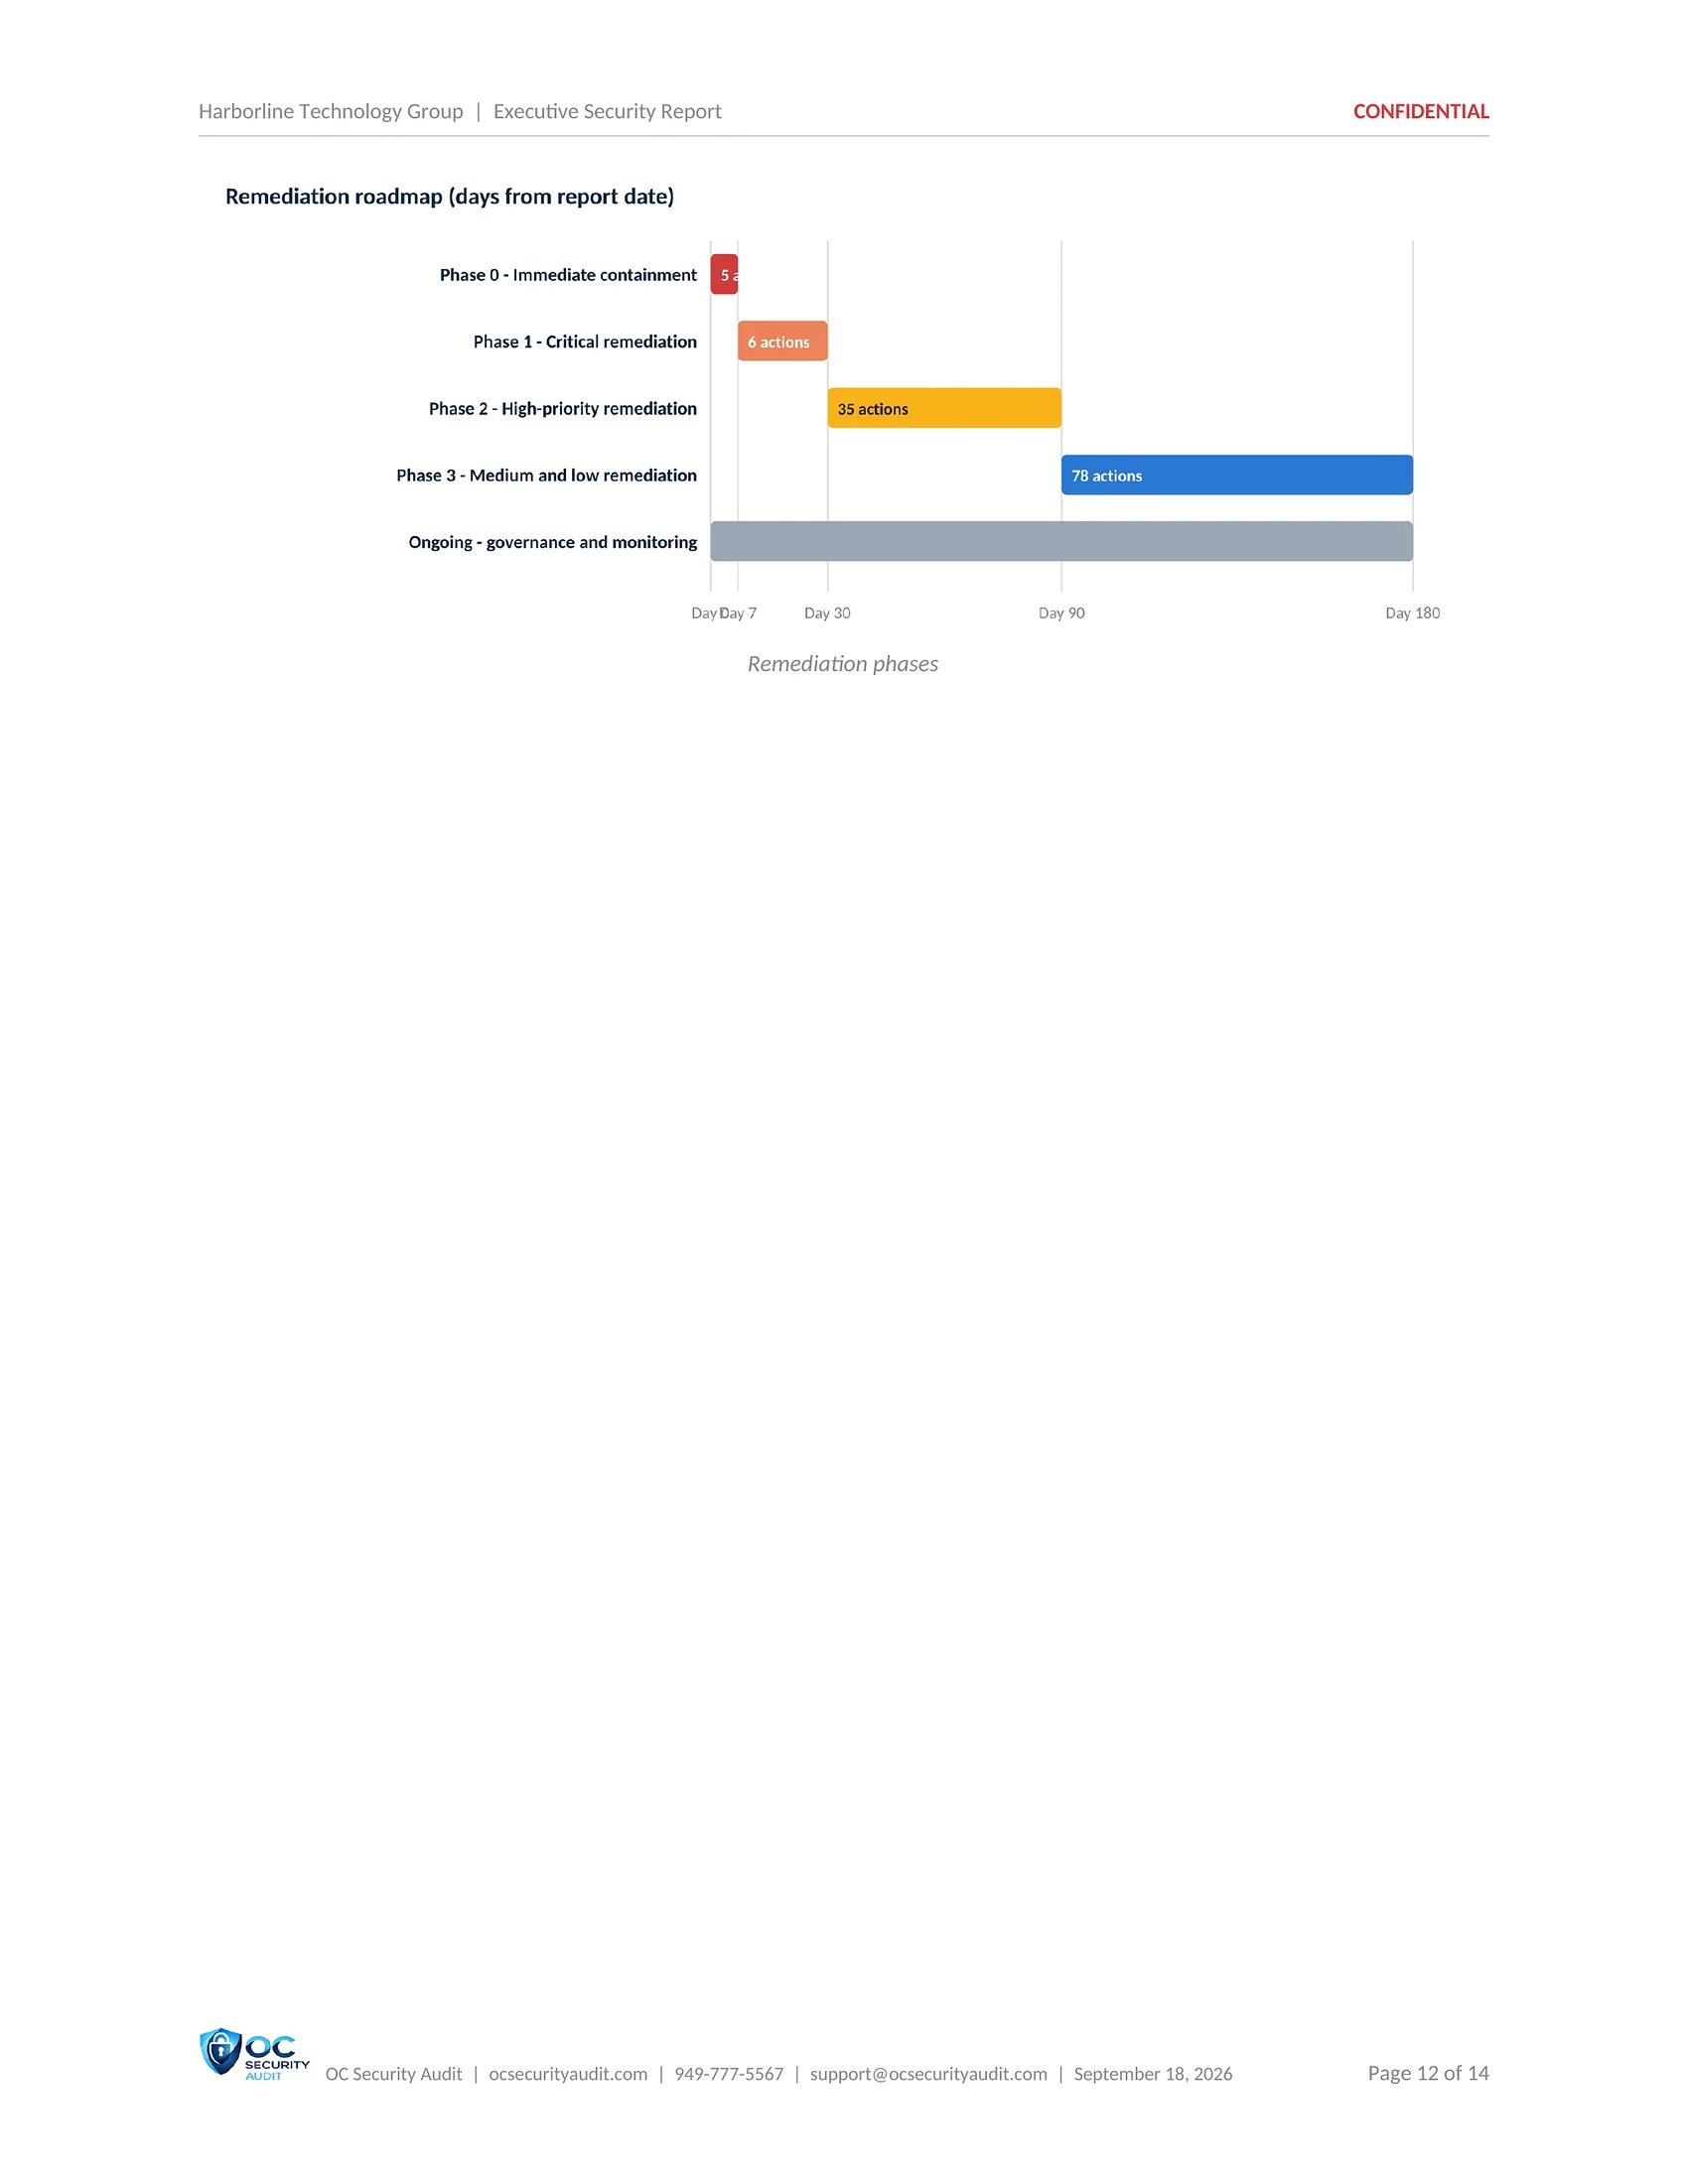
- Remediation phases
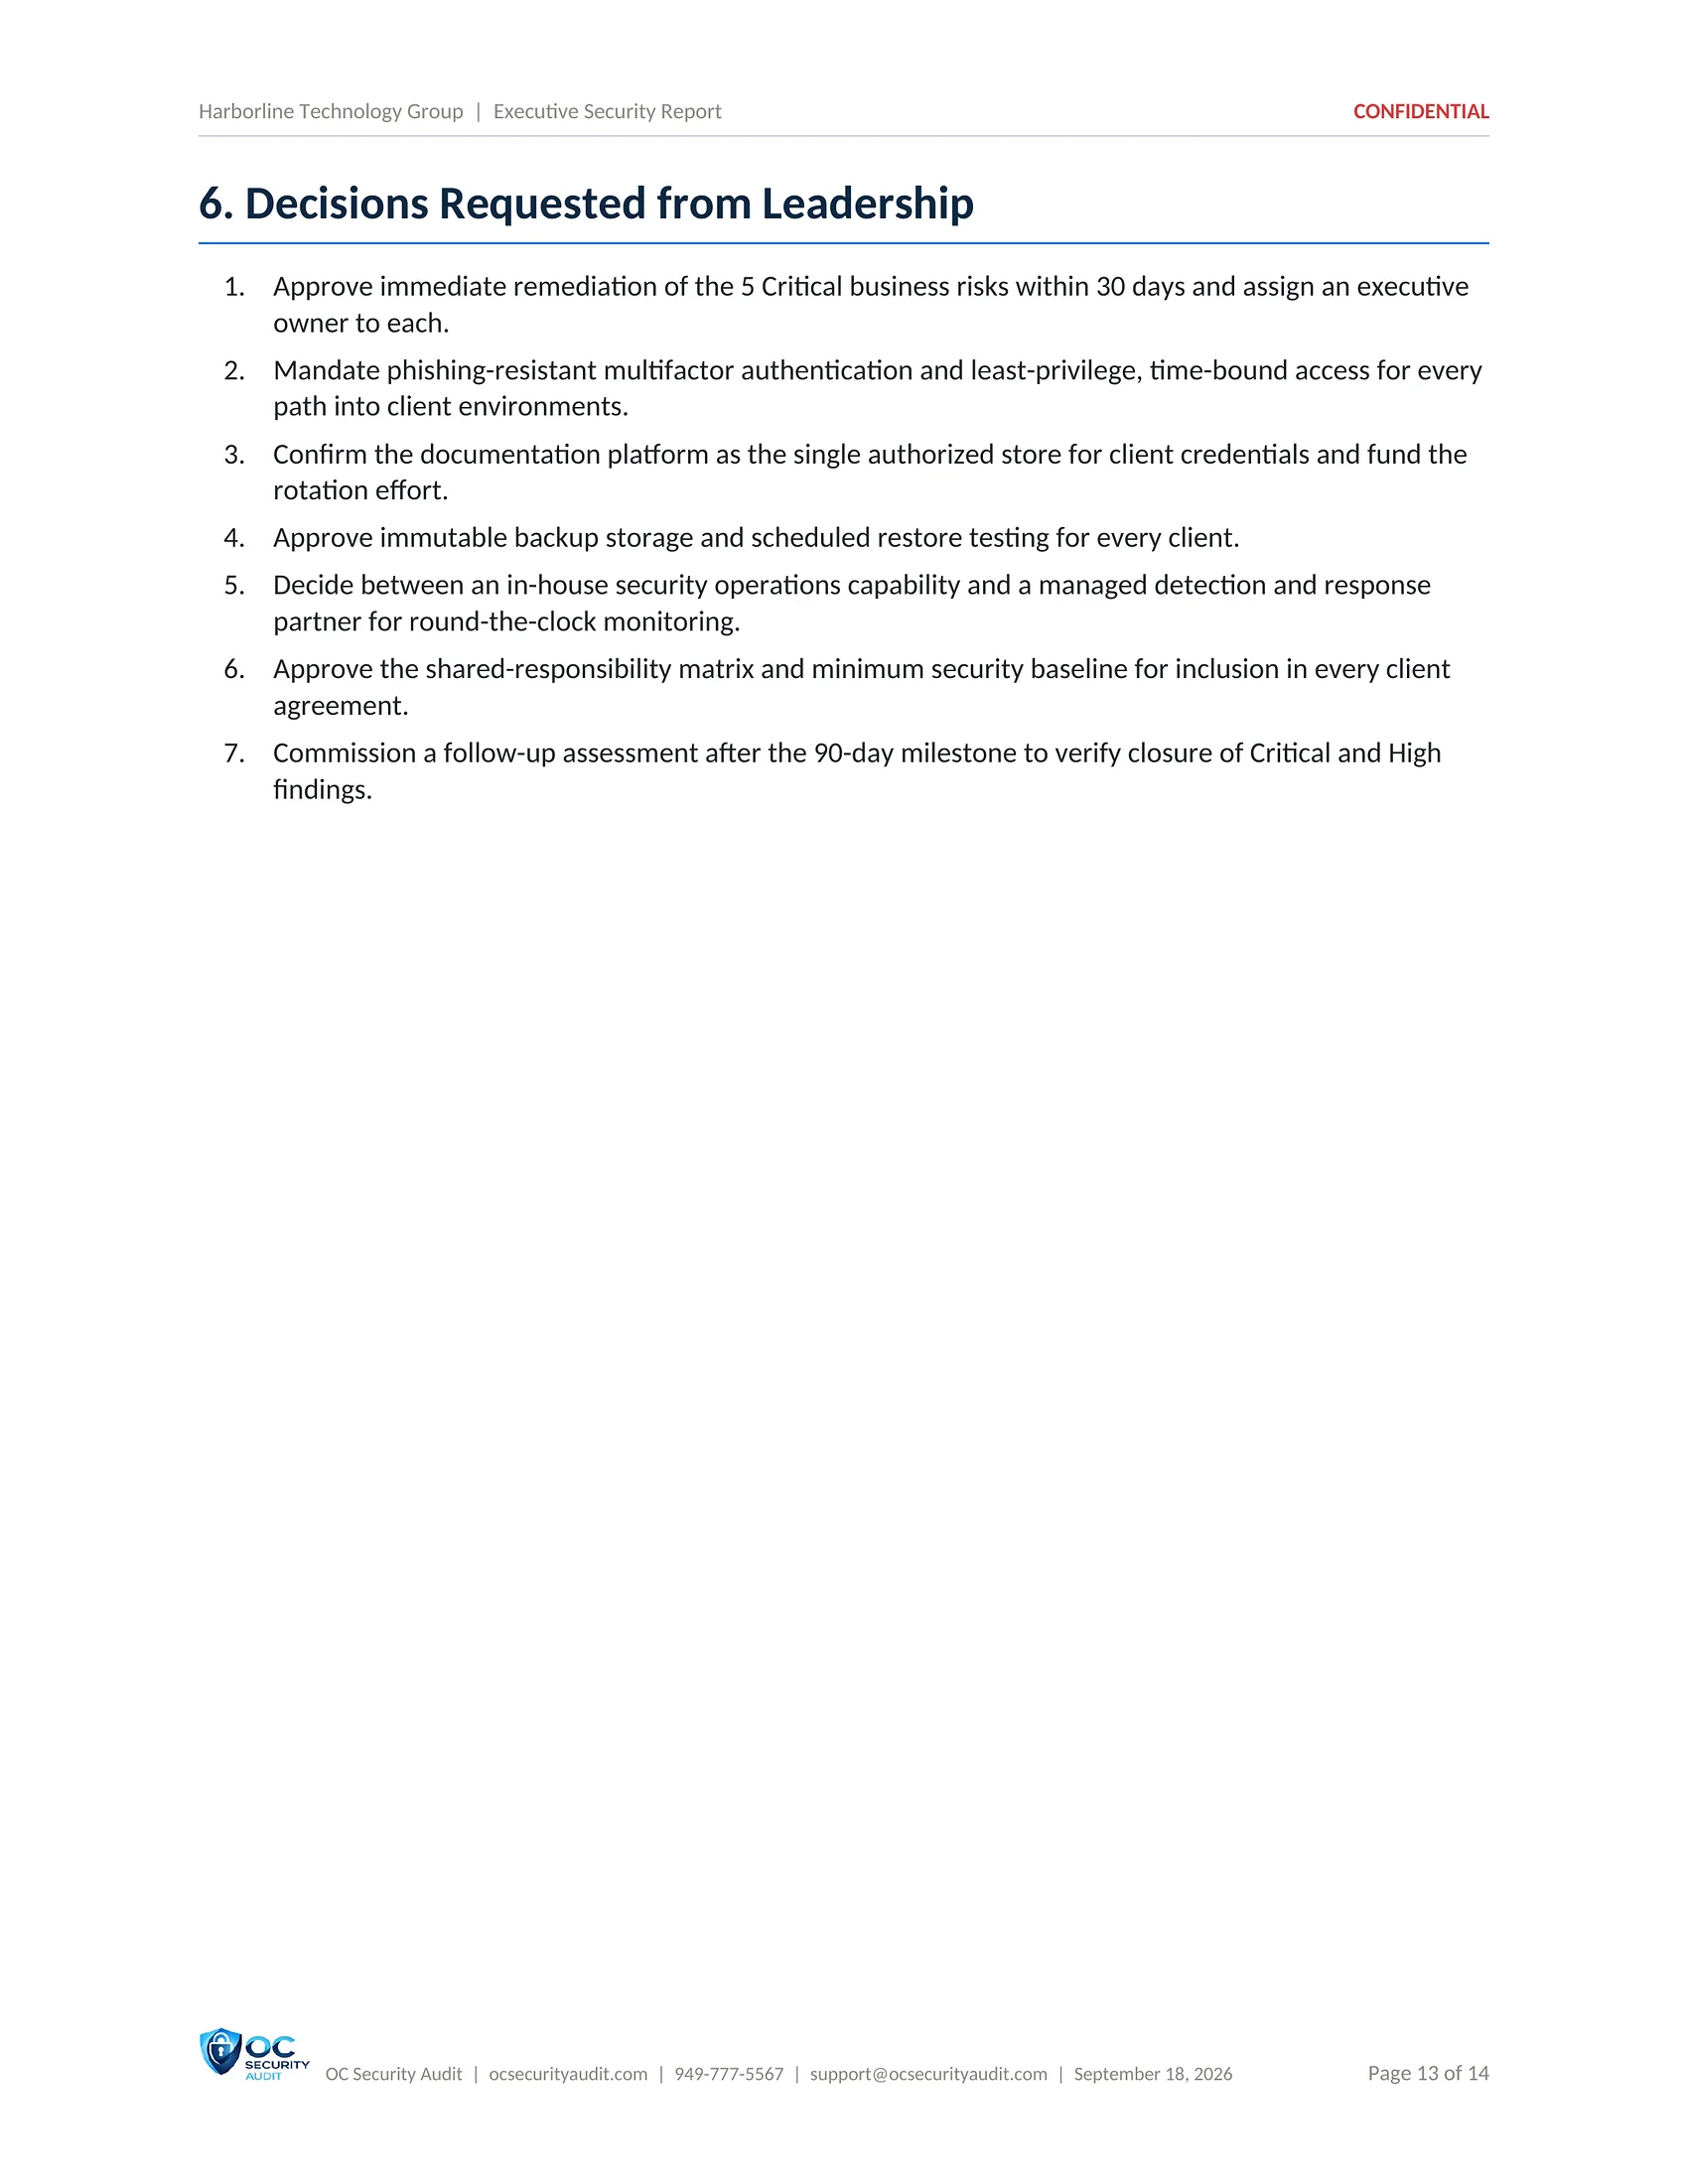
- Decisions requested from leadership
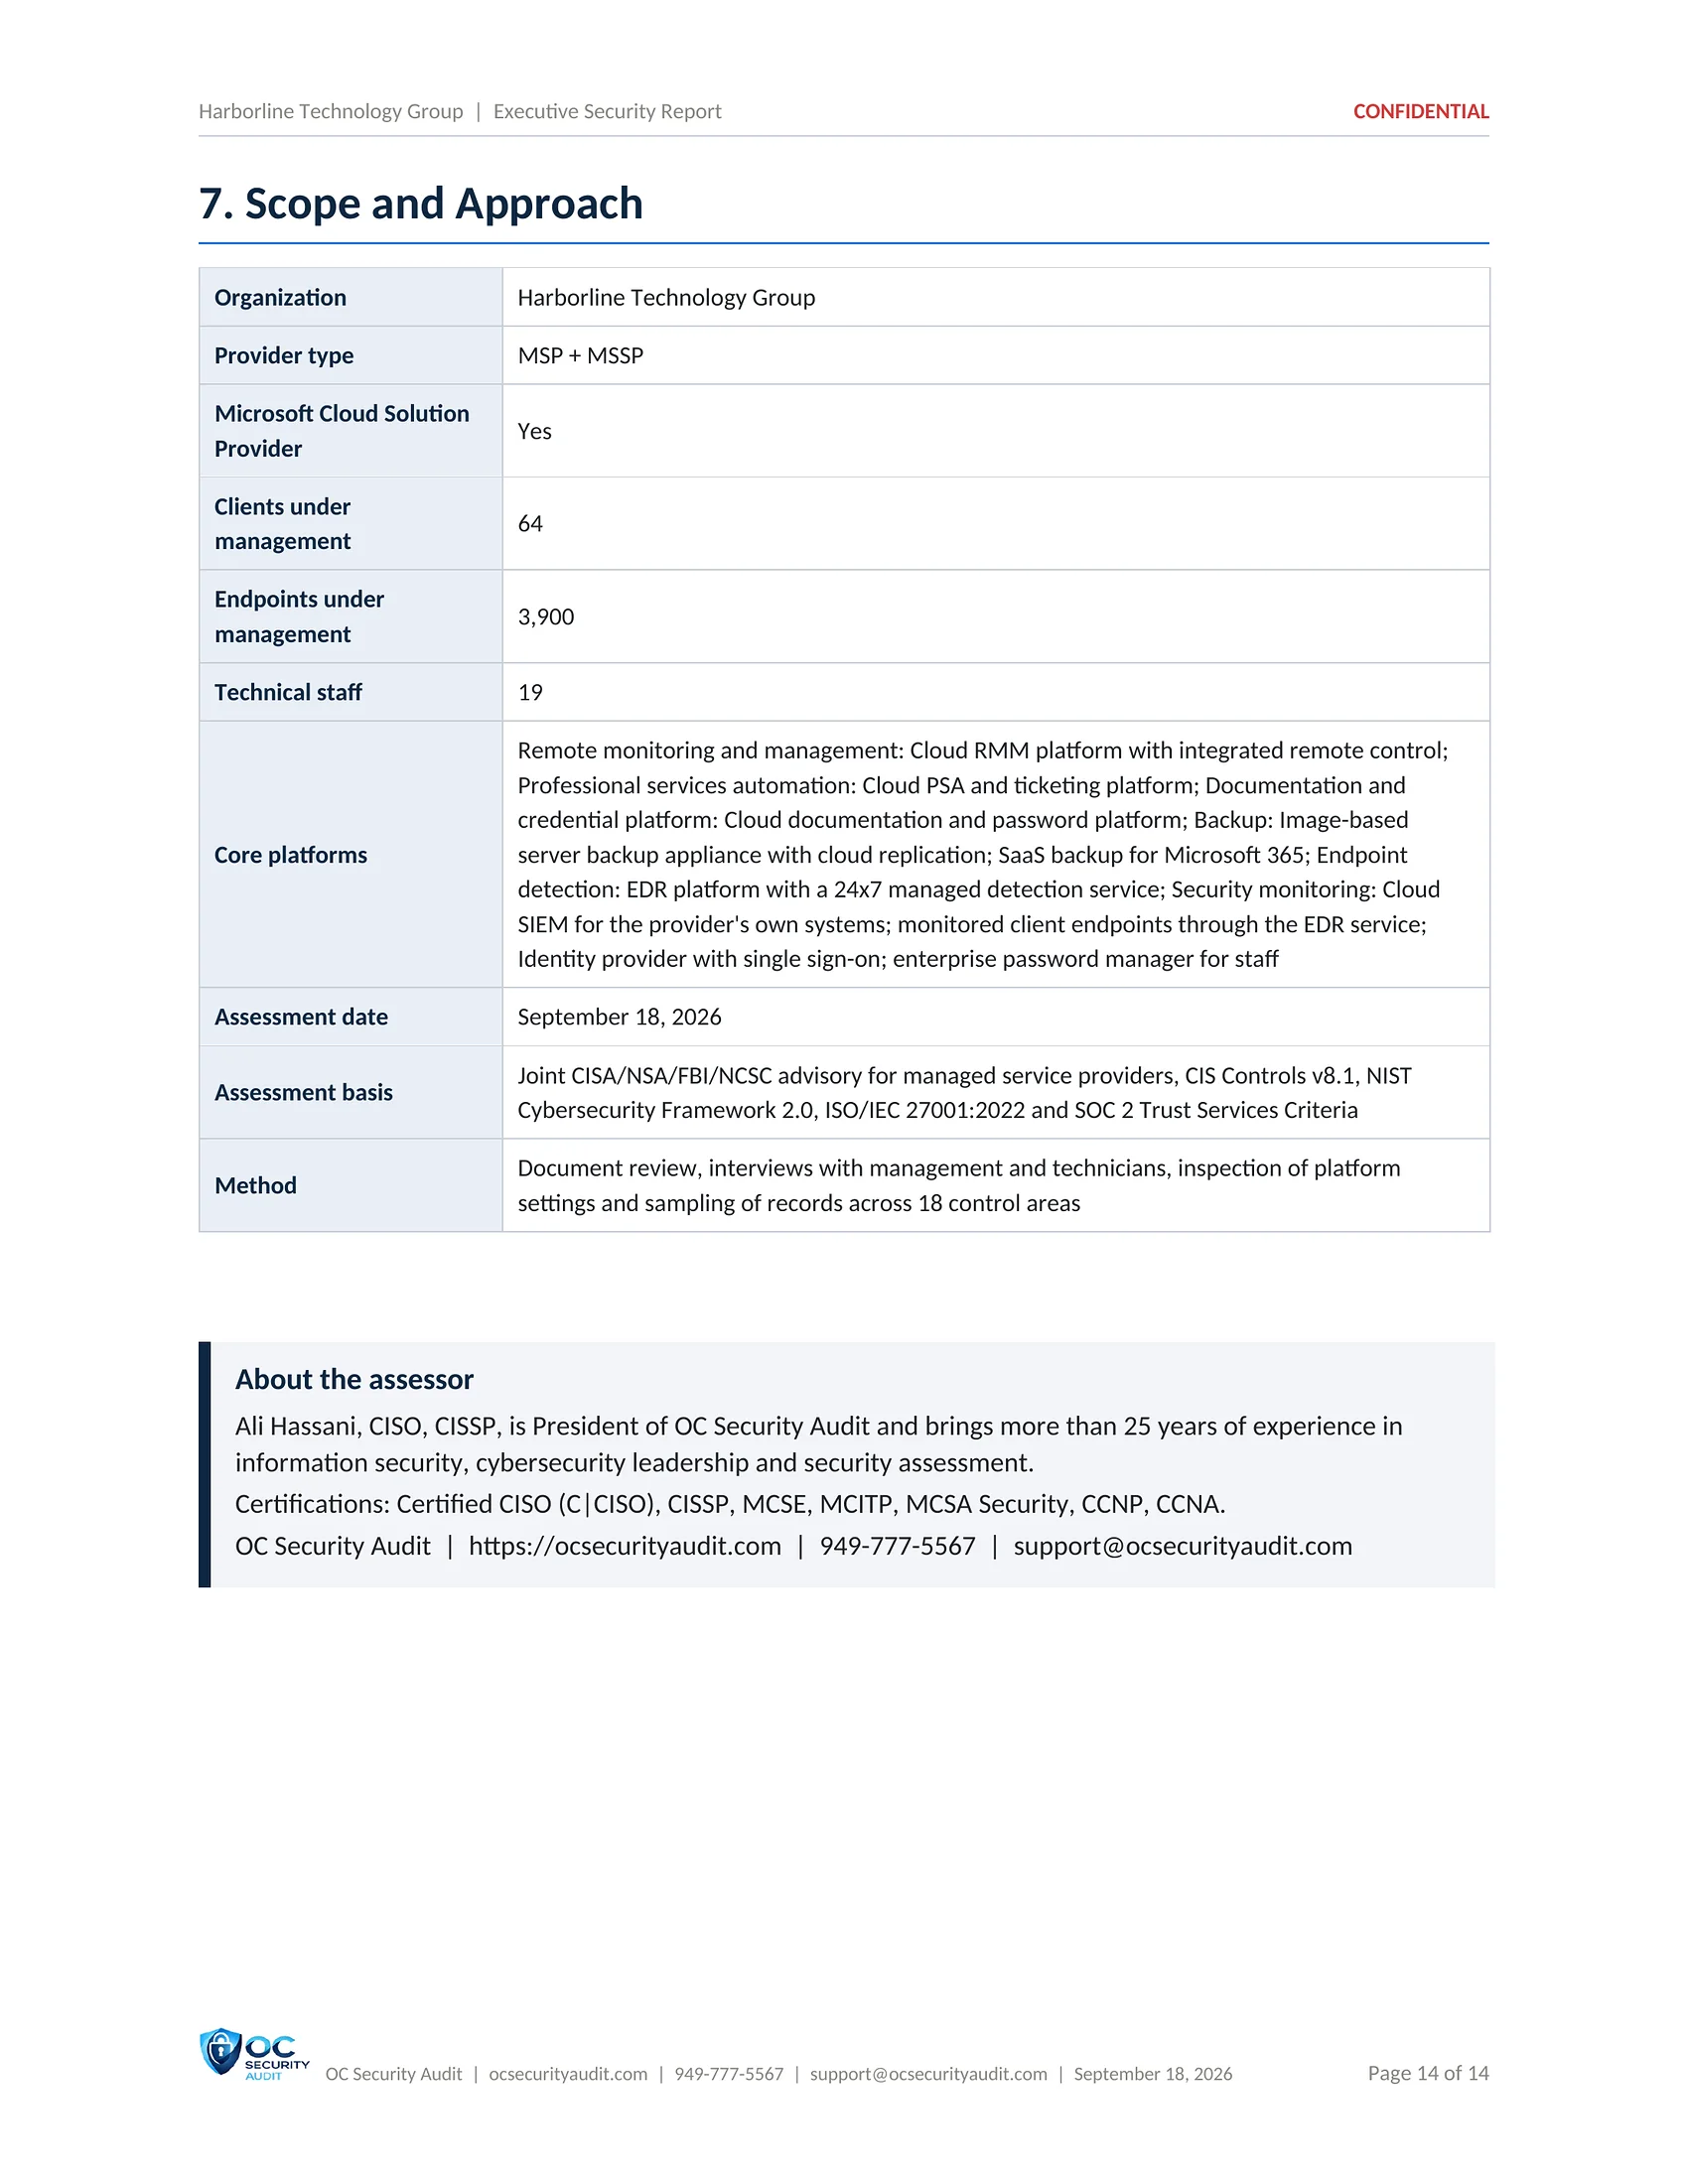
- Scope and approach
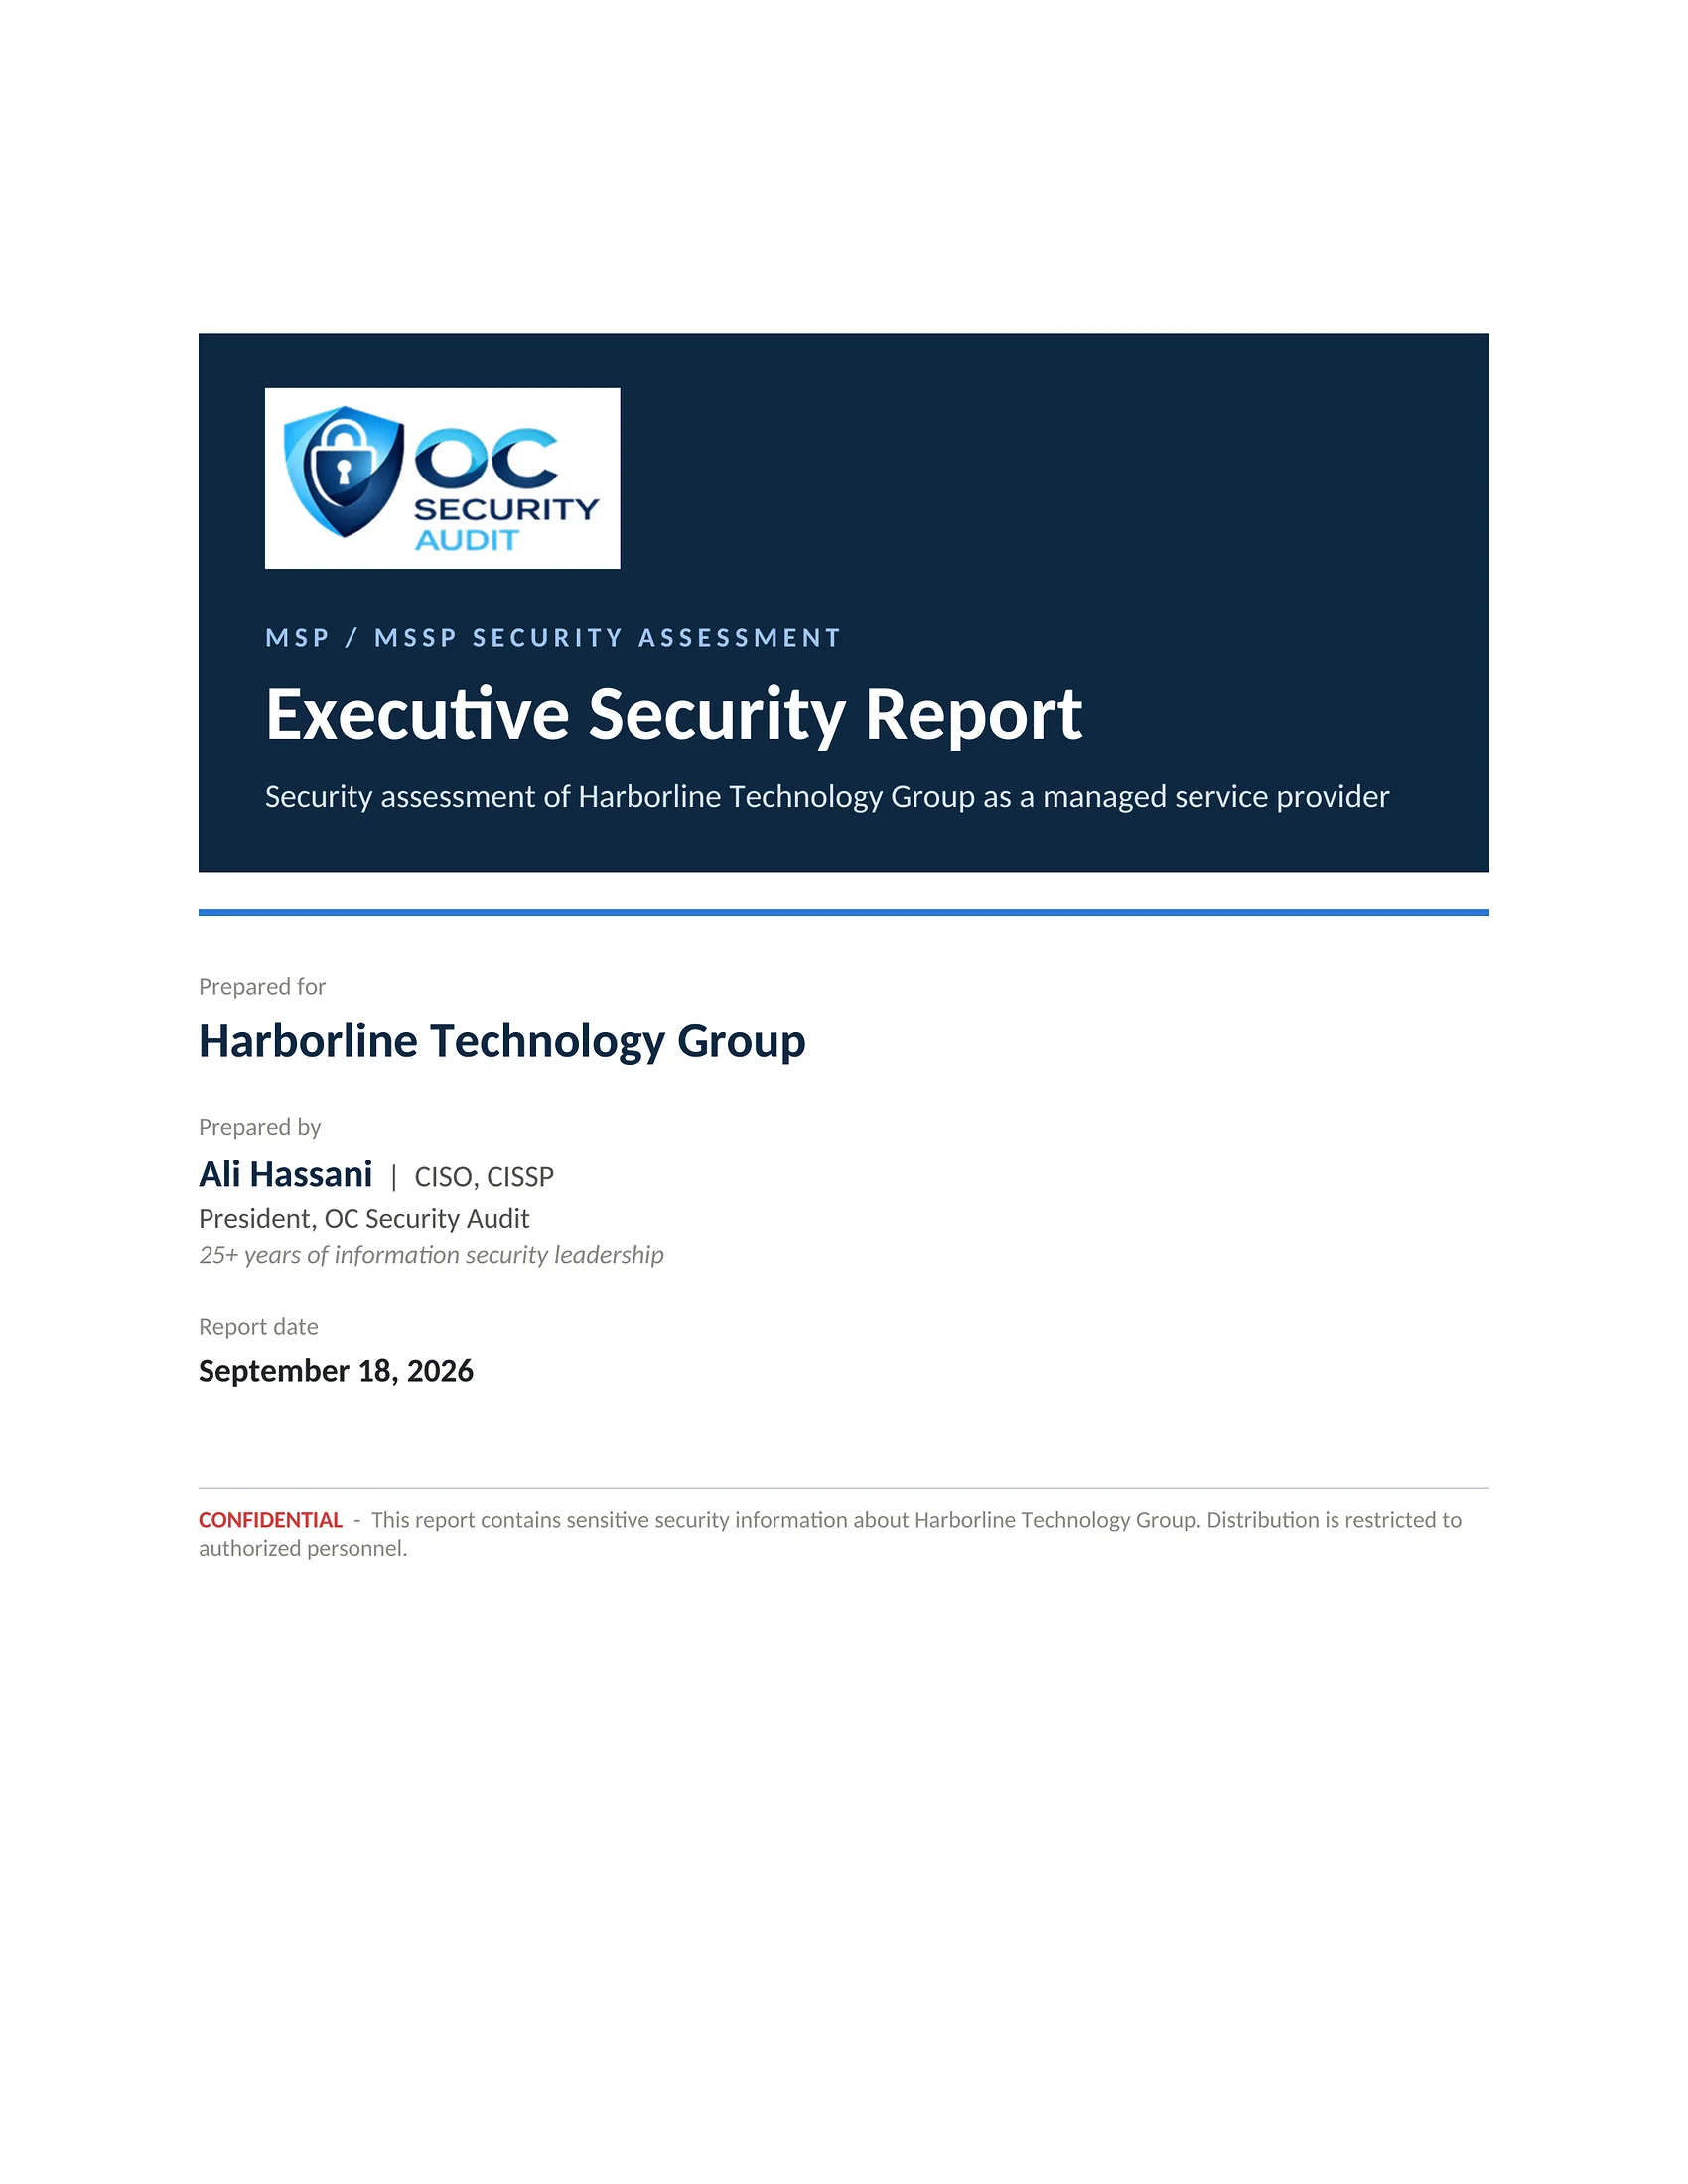
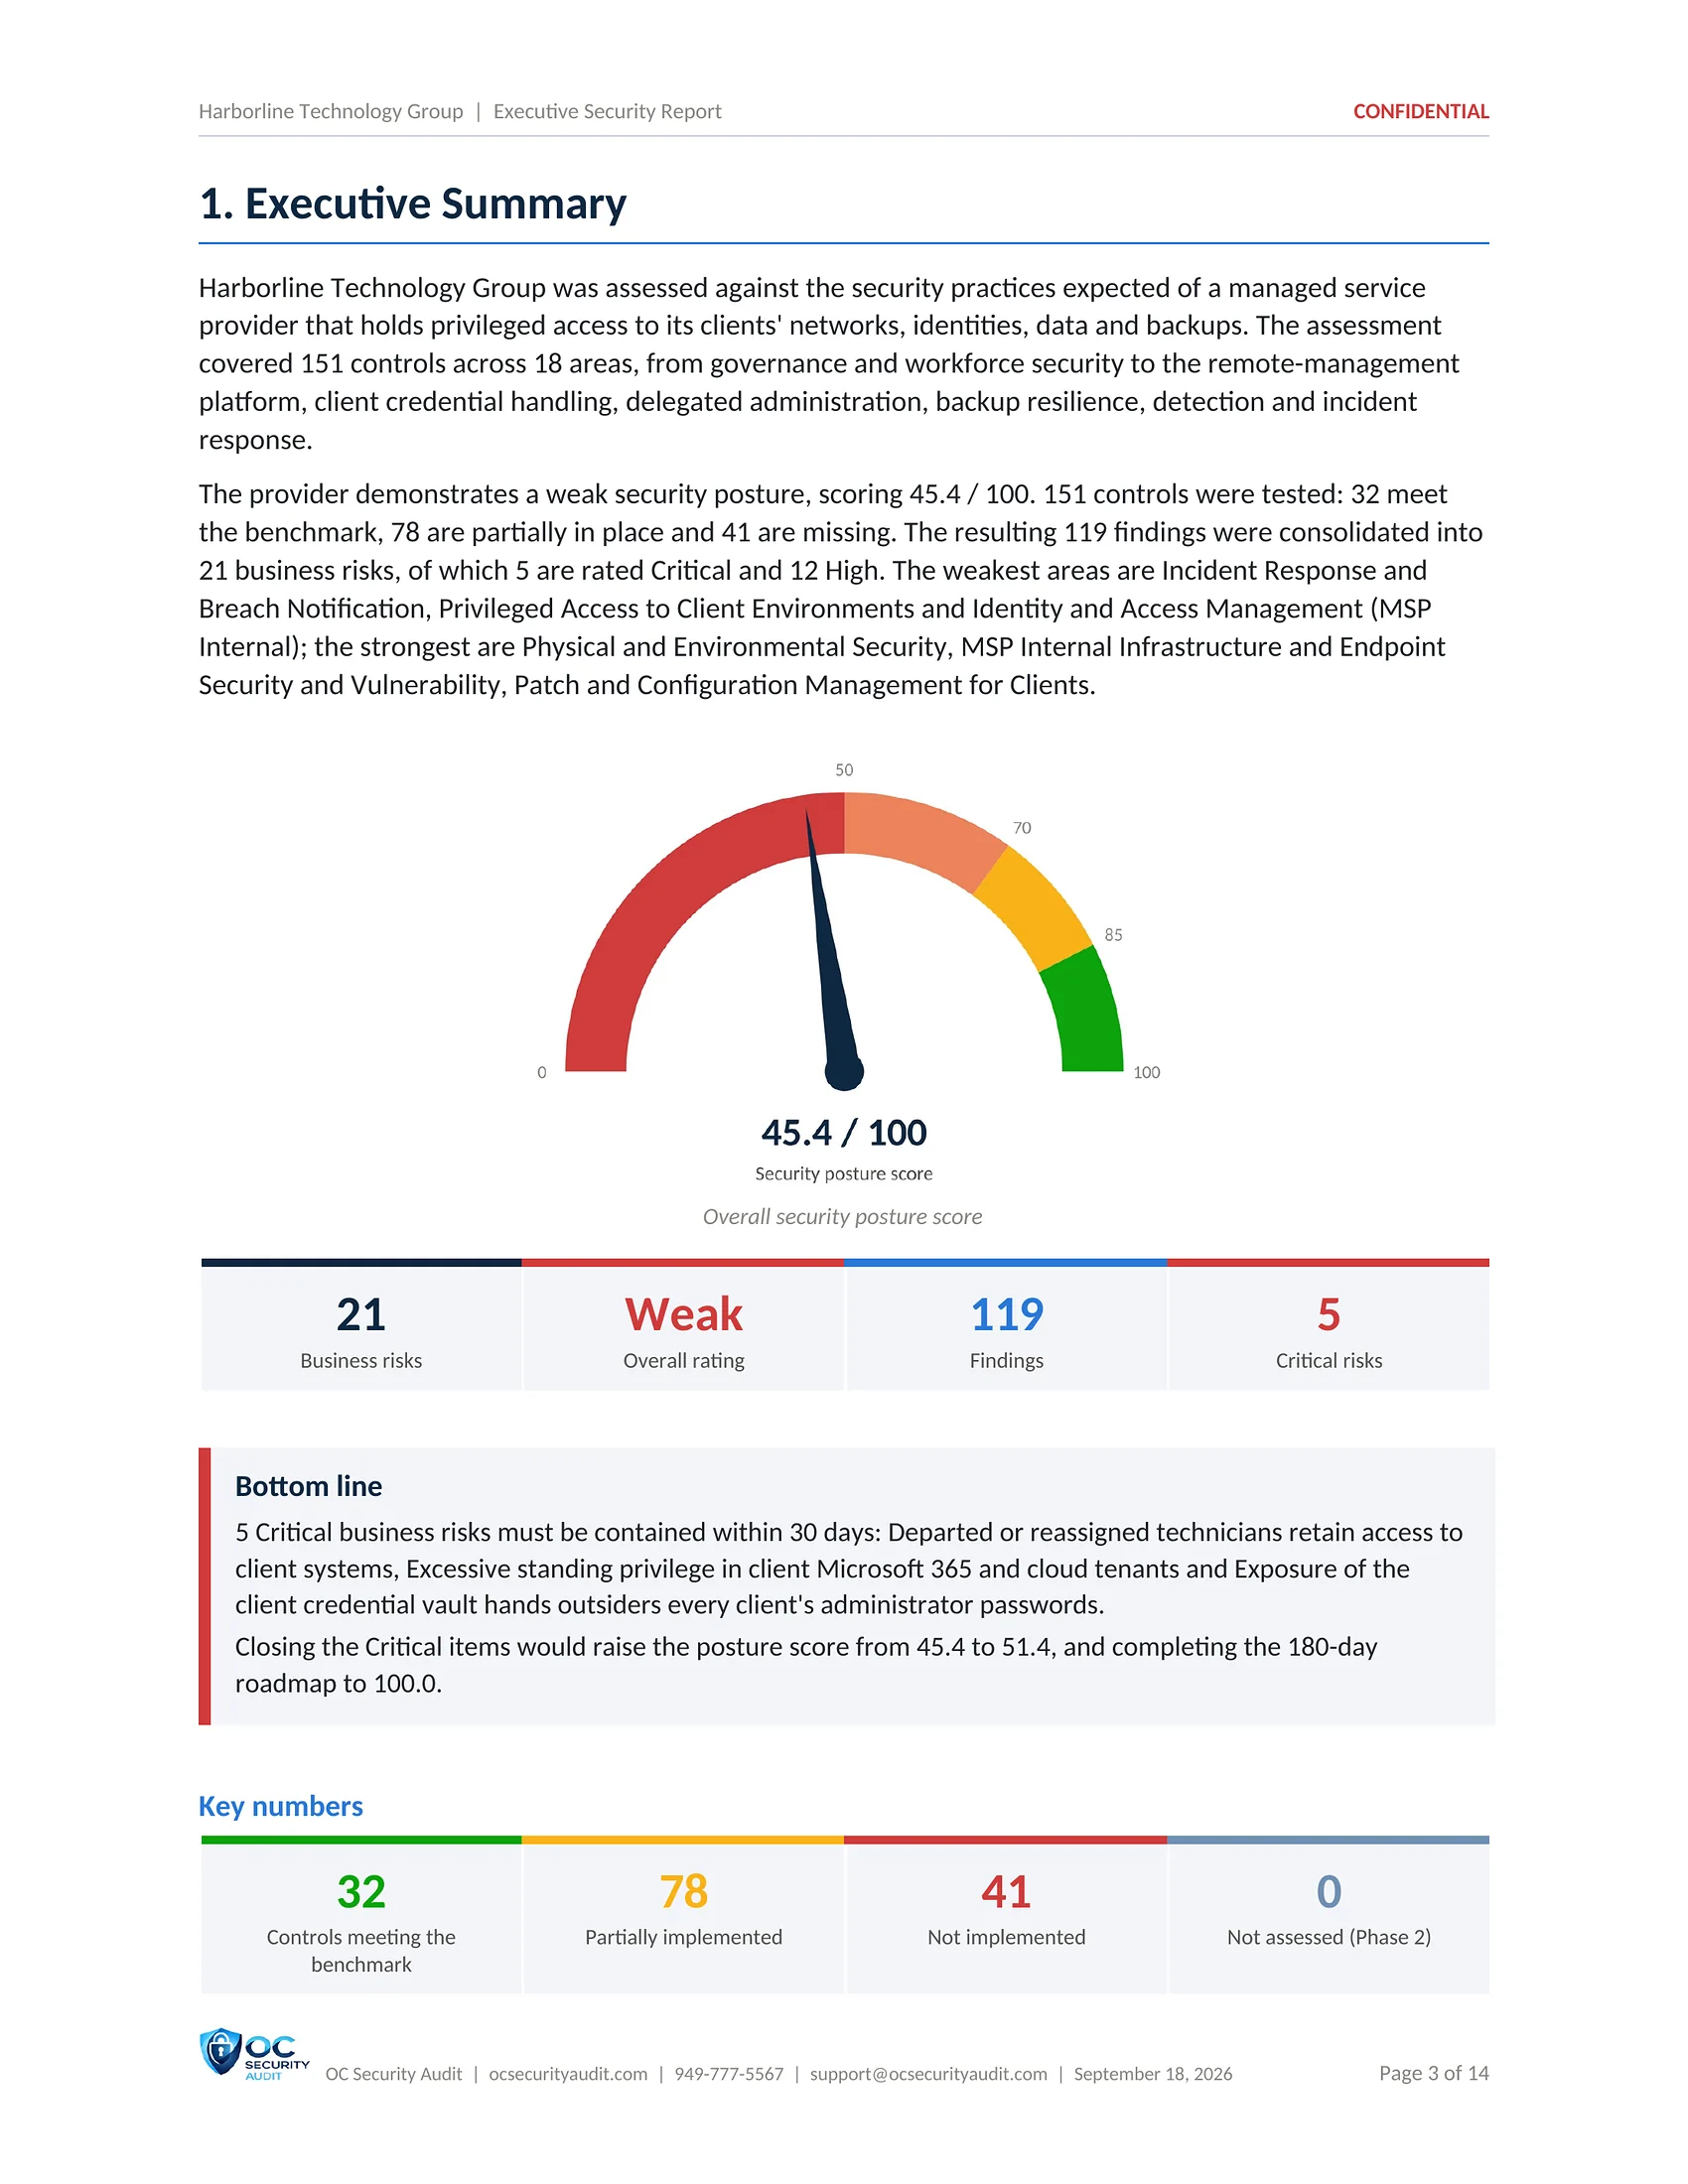
Click the centre page to open it full size and zoom in.
PDF and Word · 156 pages
Technical Security Report
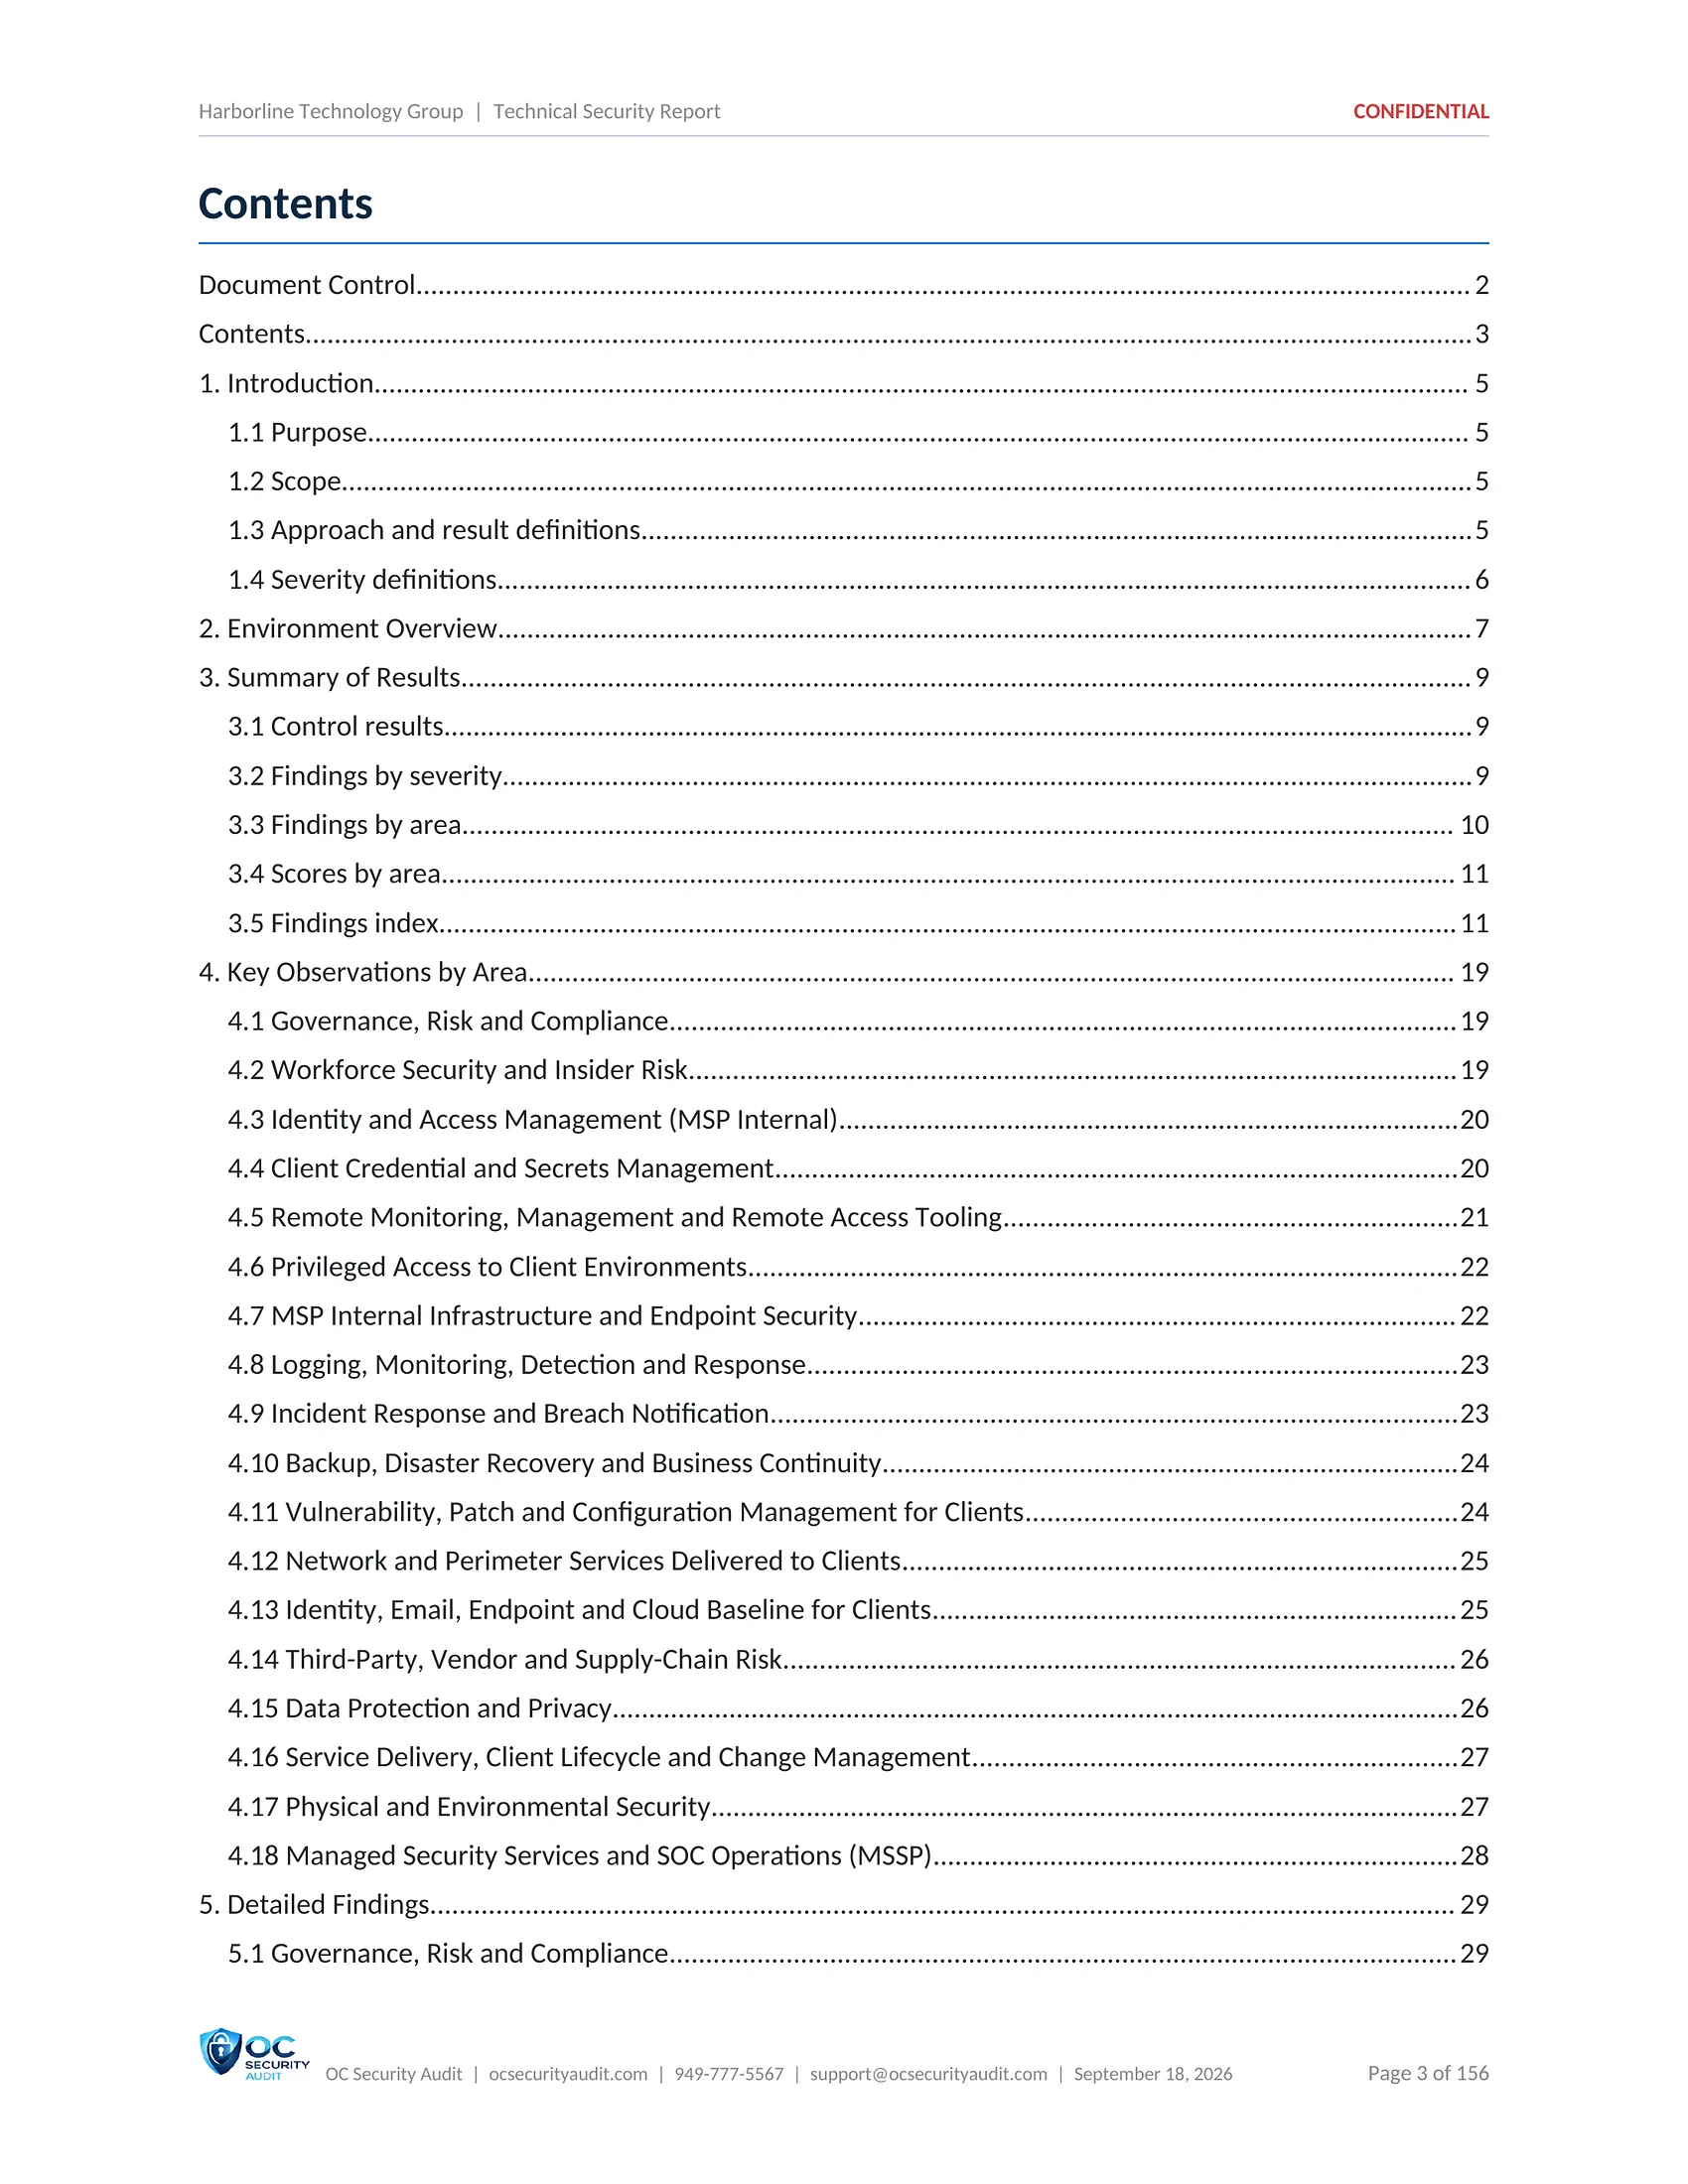
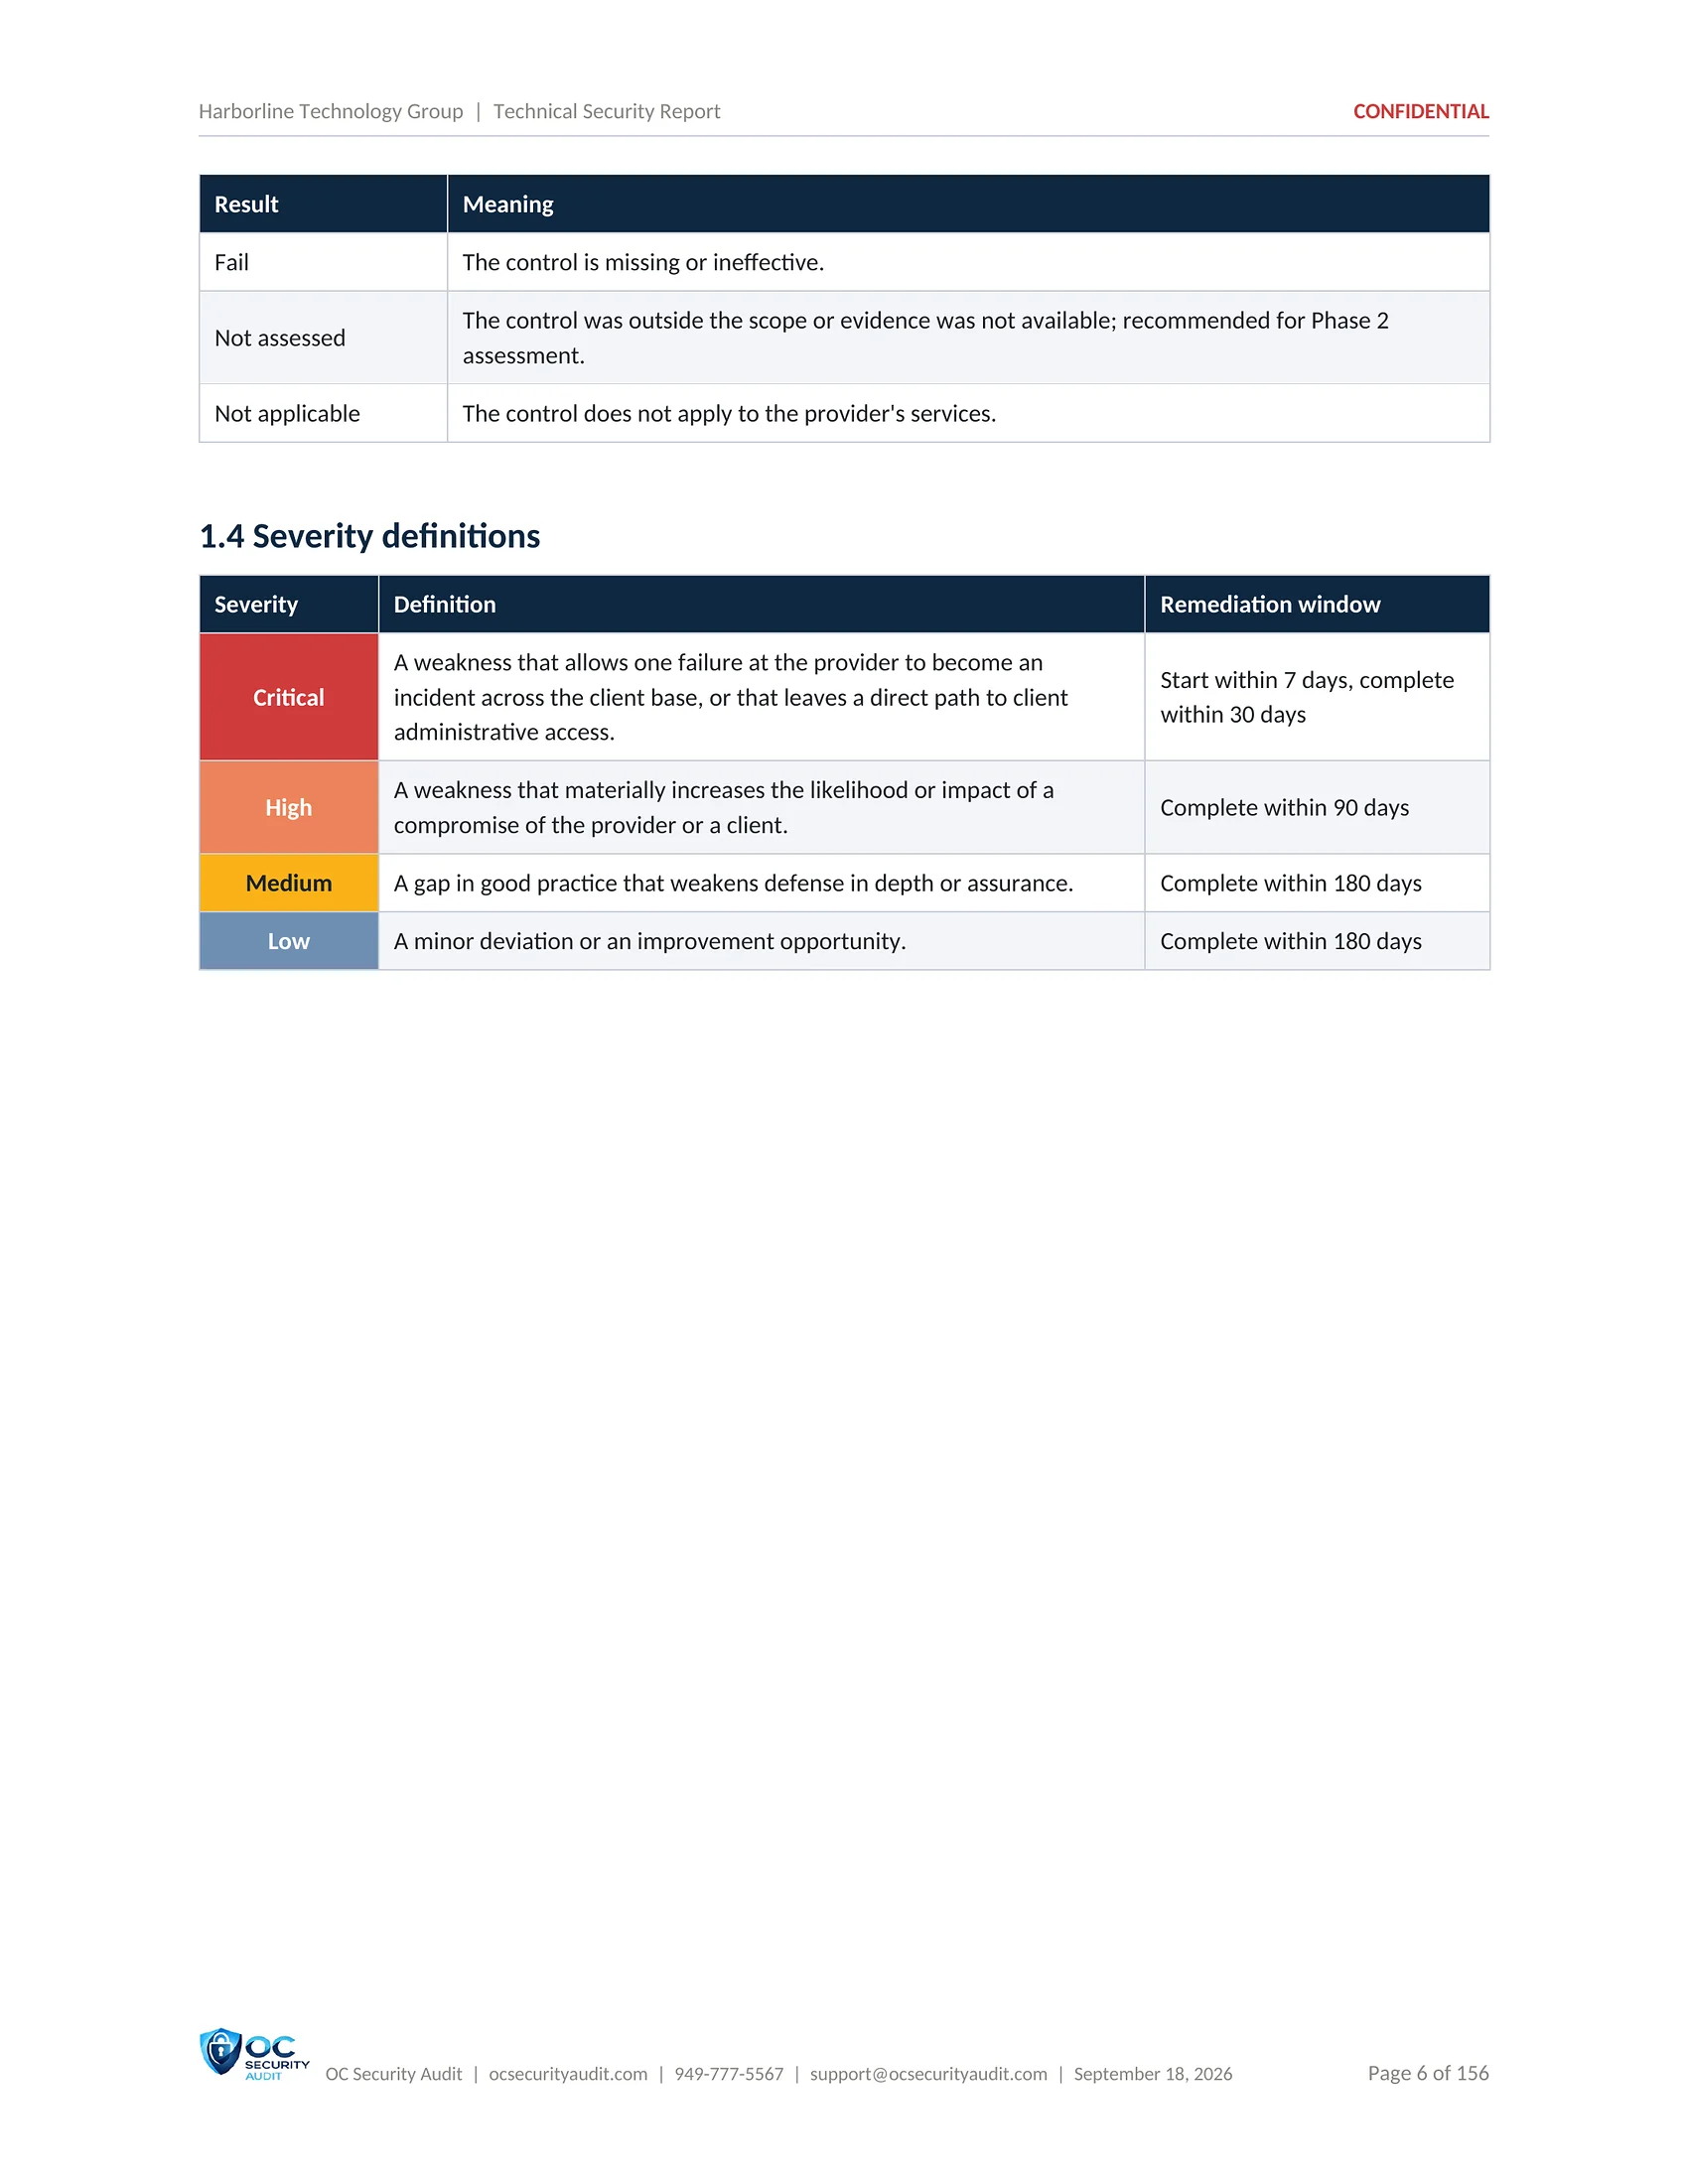
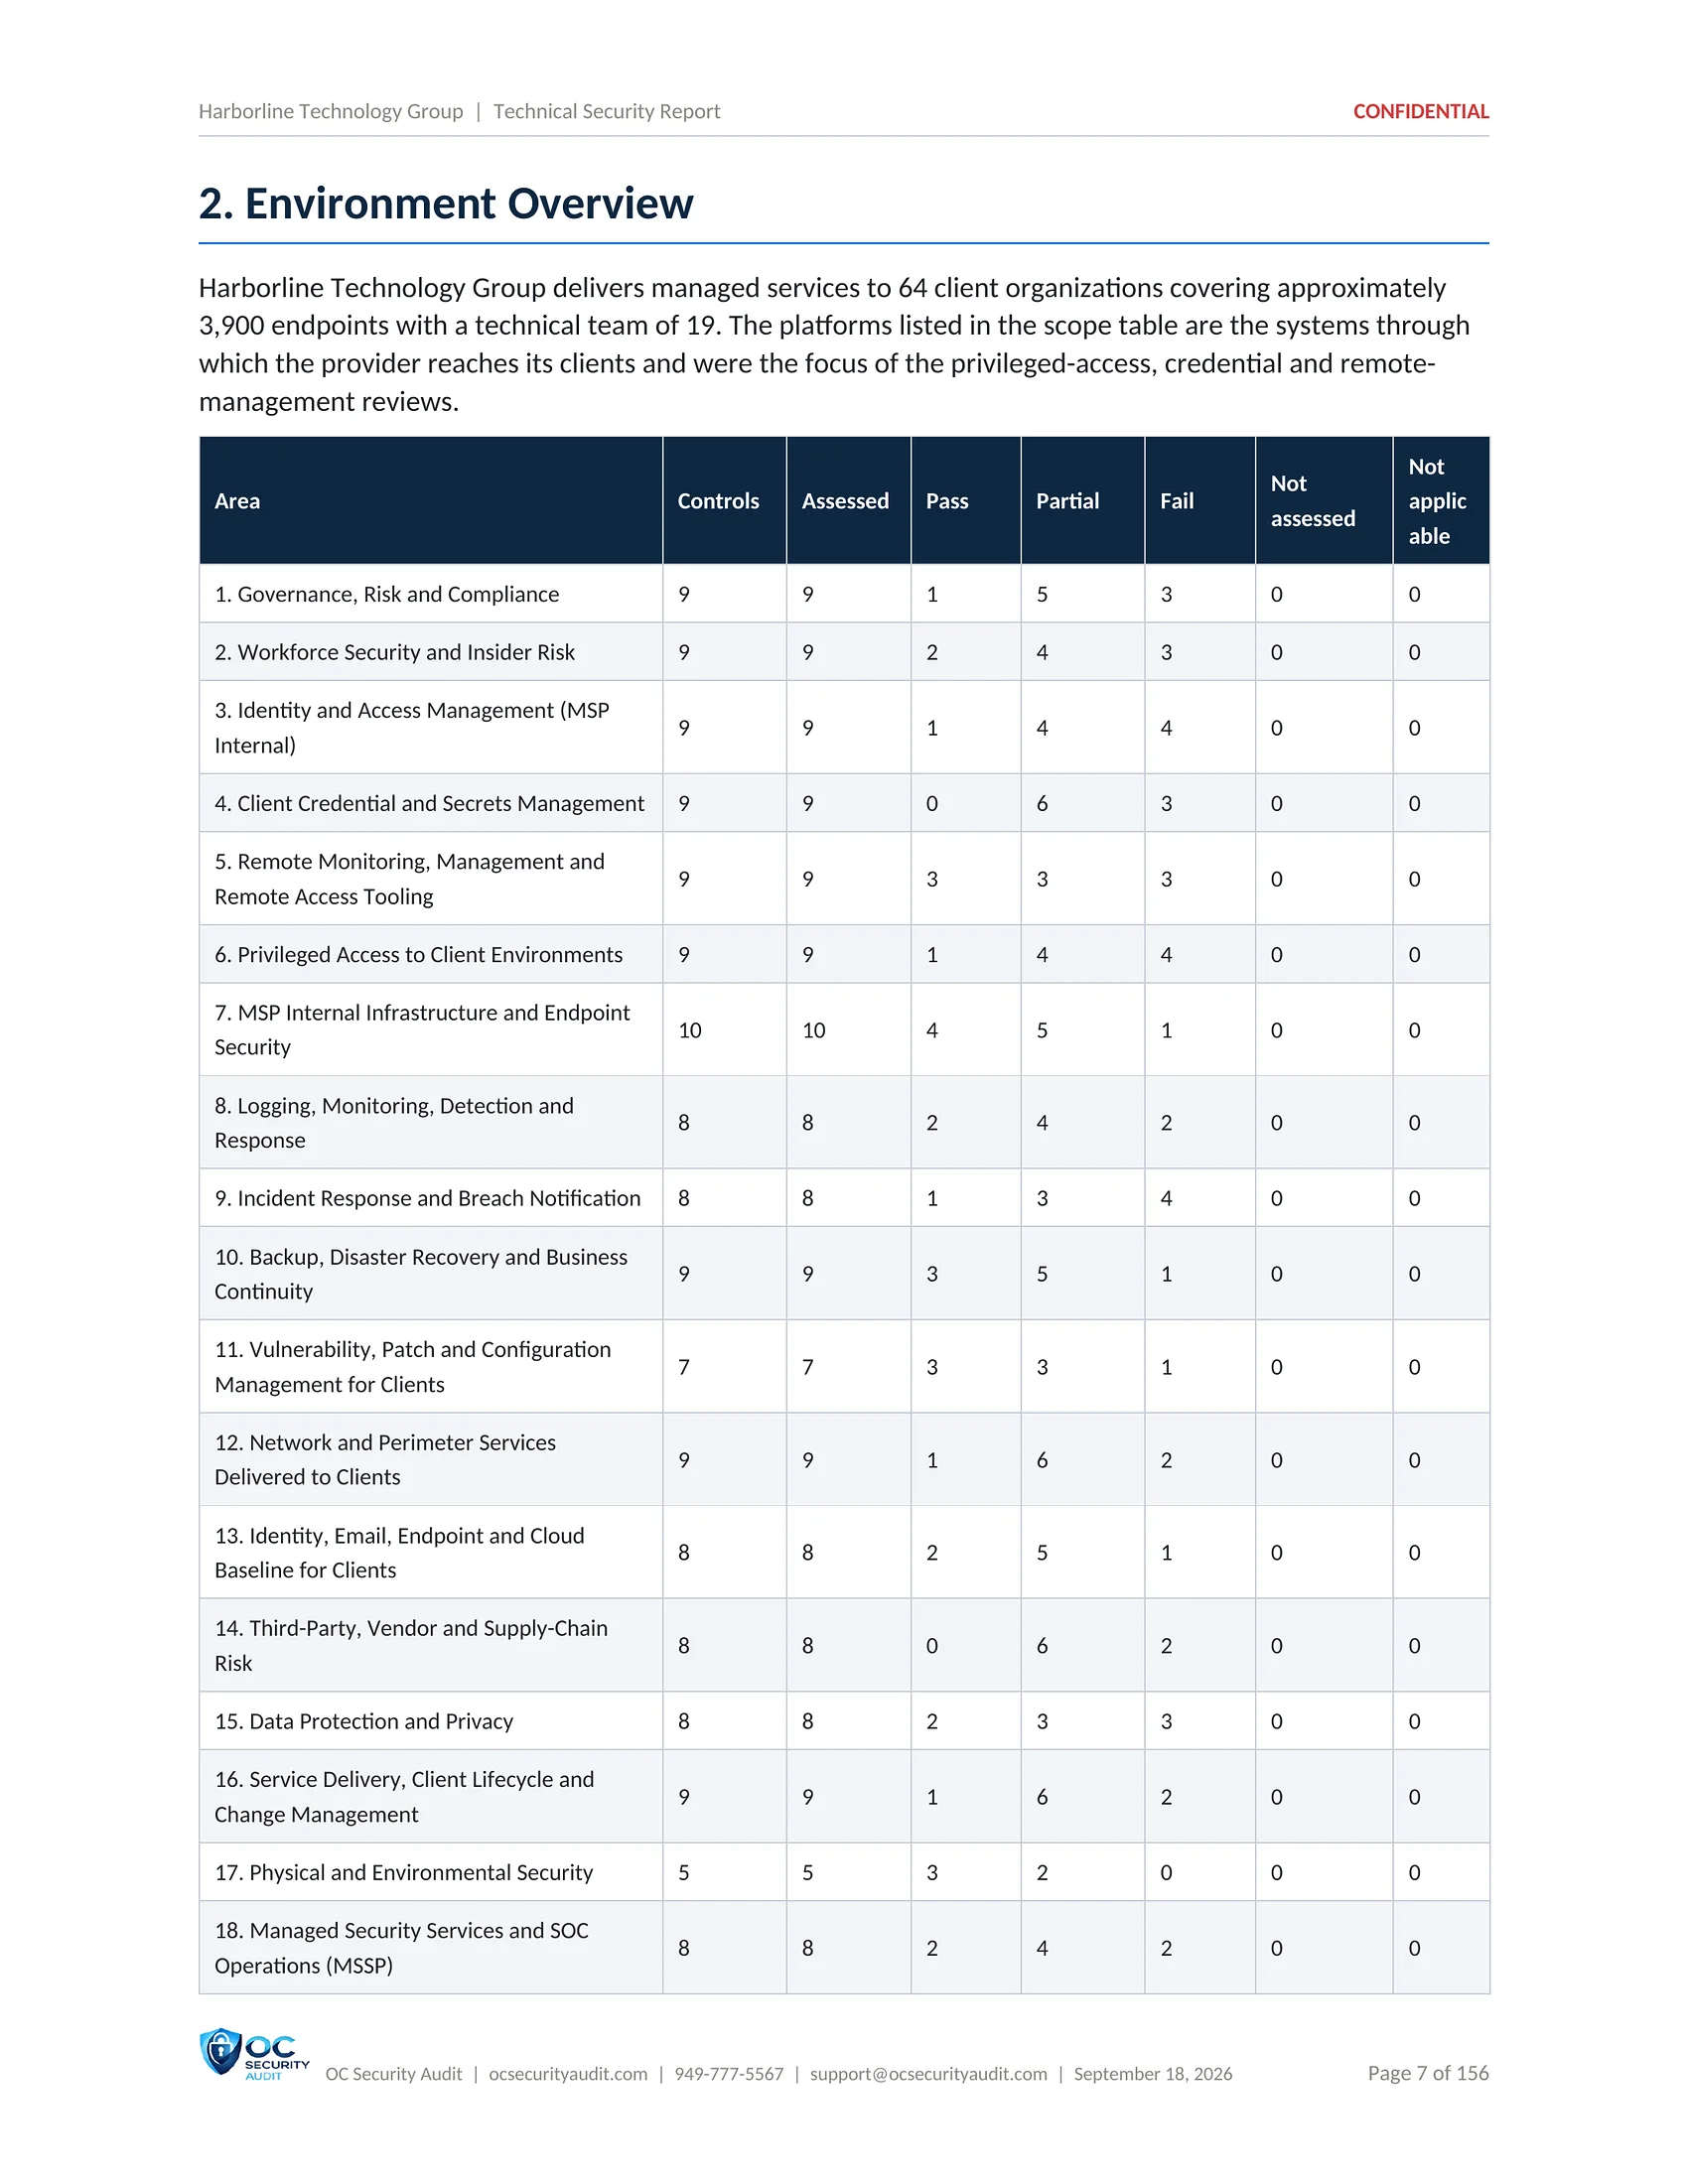
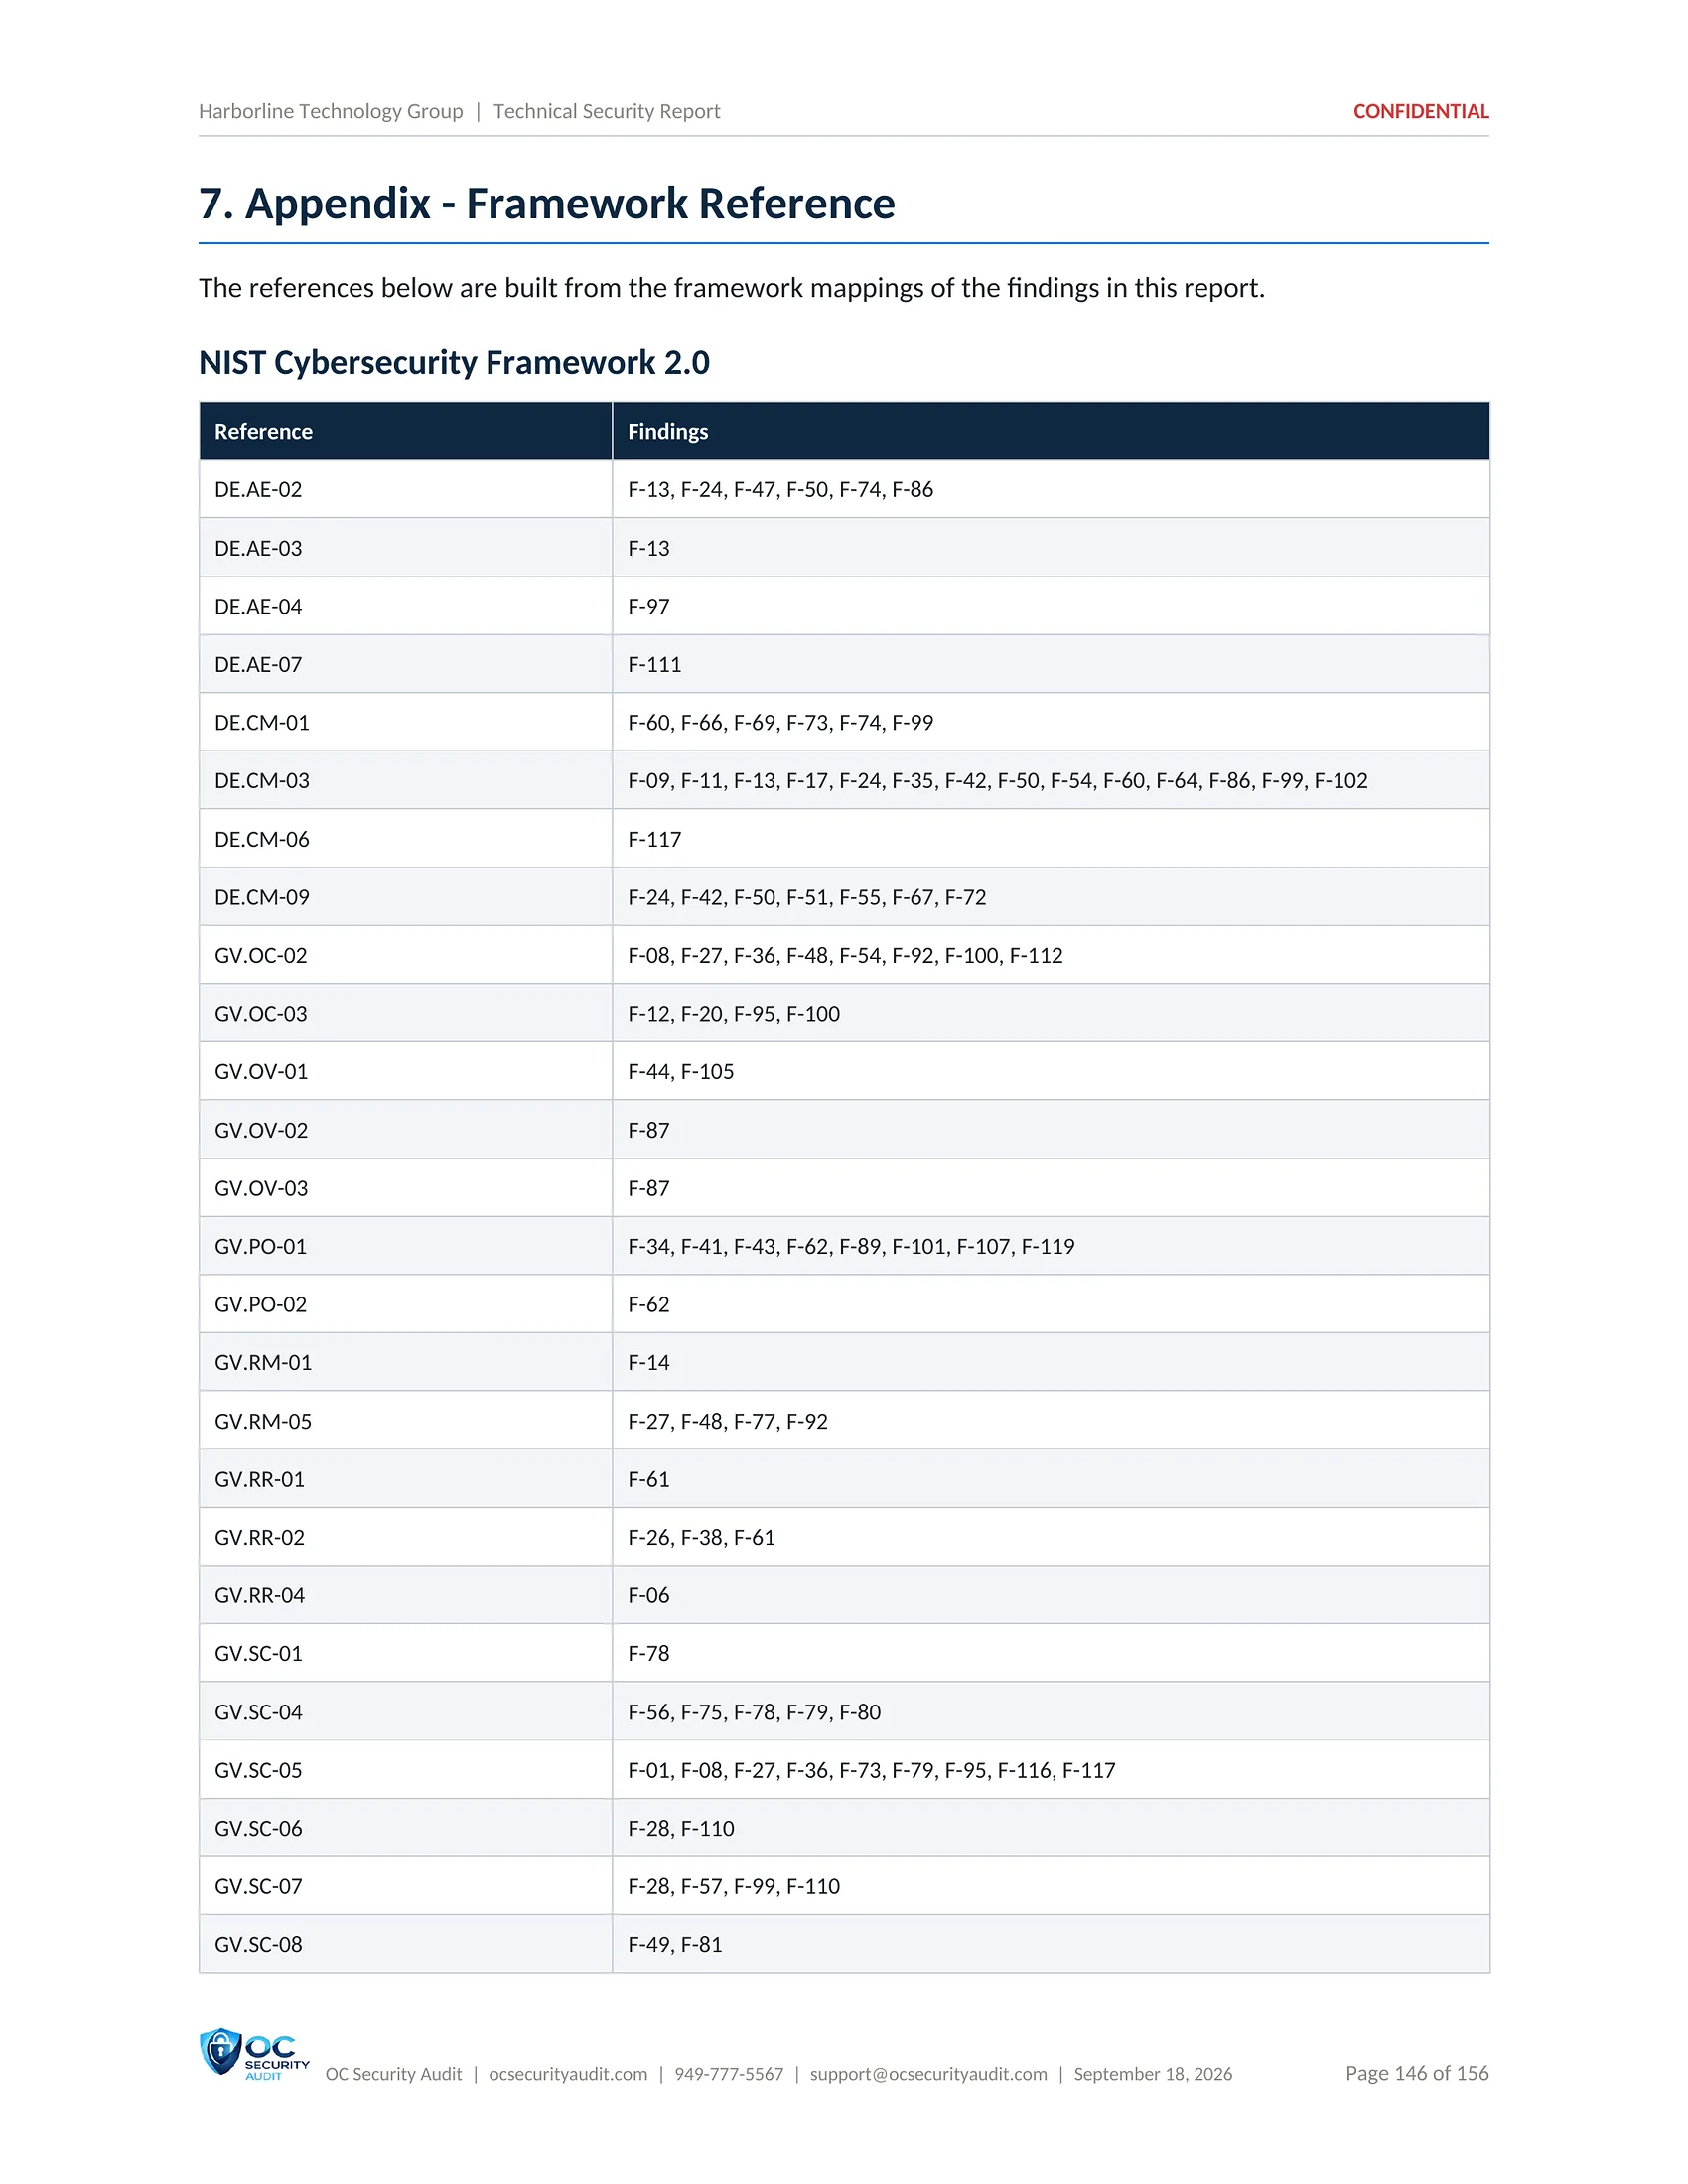
The full record of the audit for the people who will fix it. Every control result is listed, and every finding has its own page with the observation, the evidence reviewed, the business impact, the recommendation and how to confirm the fix, grouped by the 18 areas and mapped to frameworks.
Head of technology, engineers, security staff and the auditors of a later certification.
What is included
- Result and severity definitions
- Environment and platforms in scope
- Summary of results and charts
- Scores by area and findings index
- Key observations for each area
- A detail page for every finding
- Controls that meet the benchmark
- Framework reference appendix
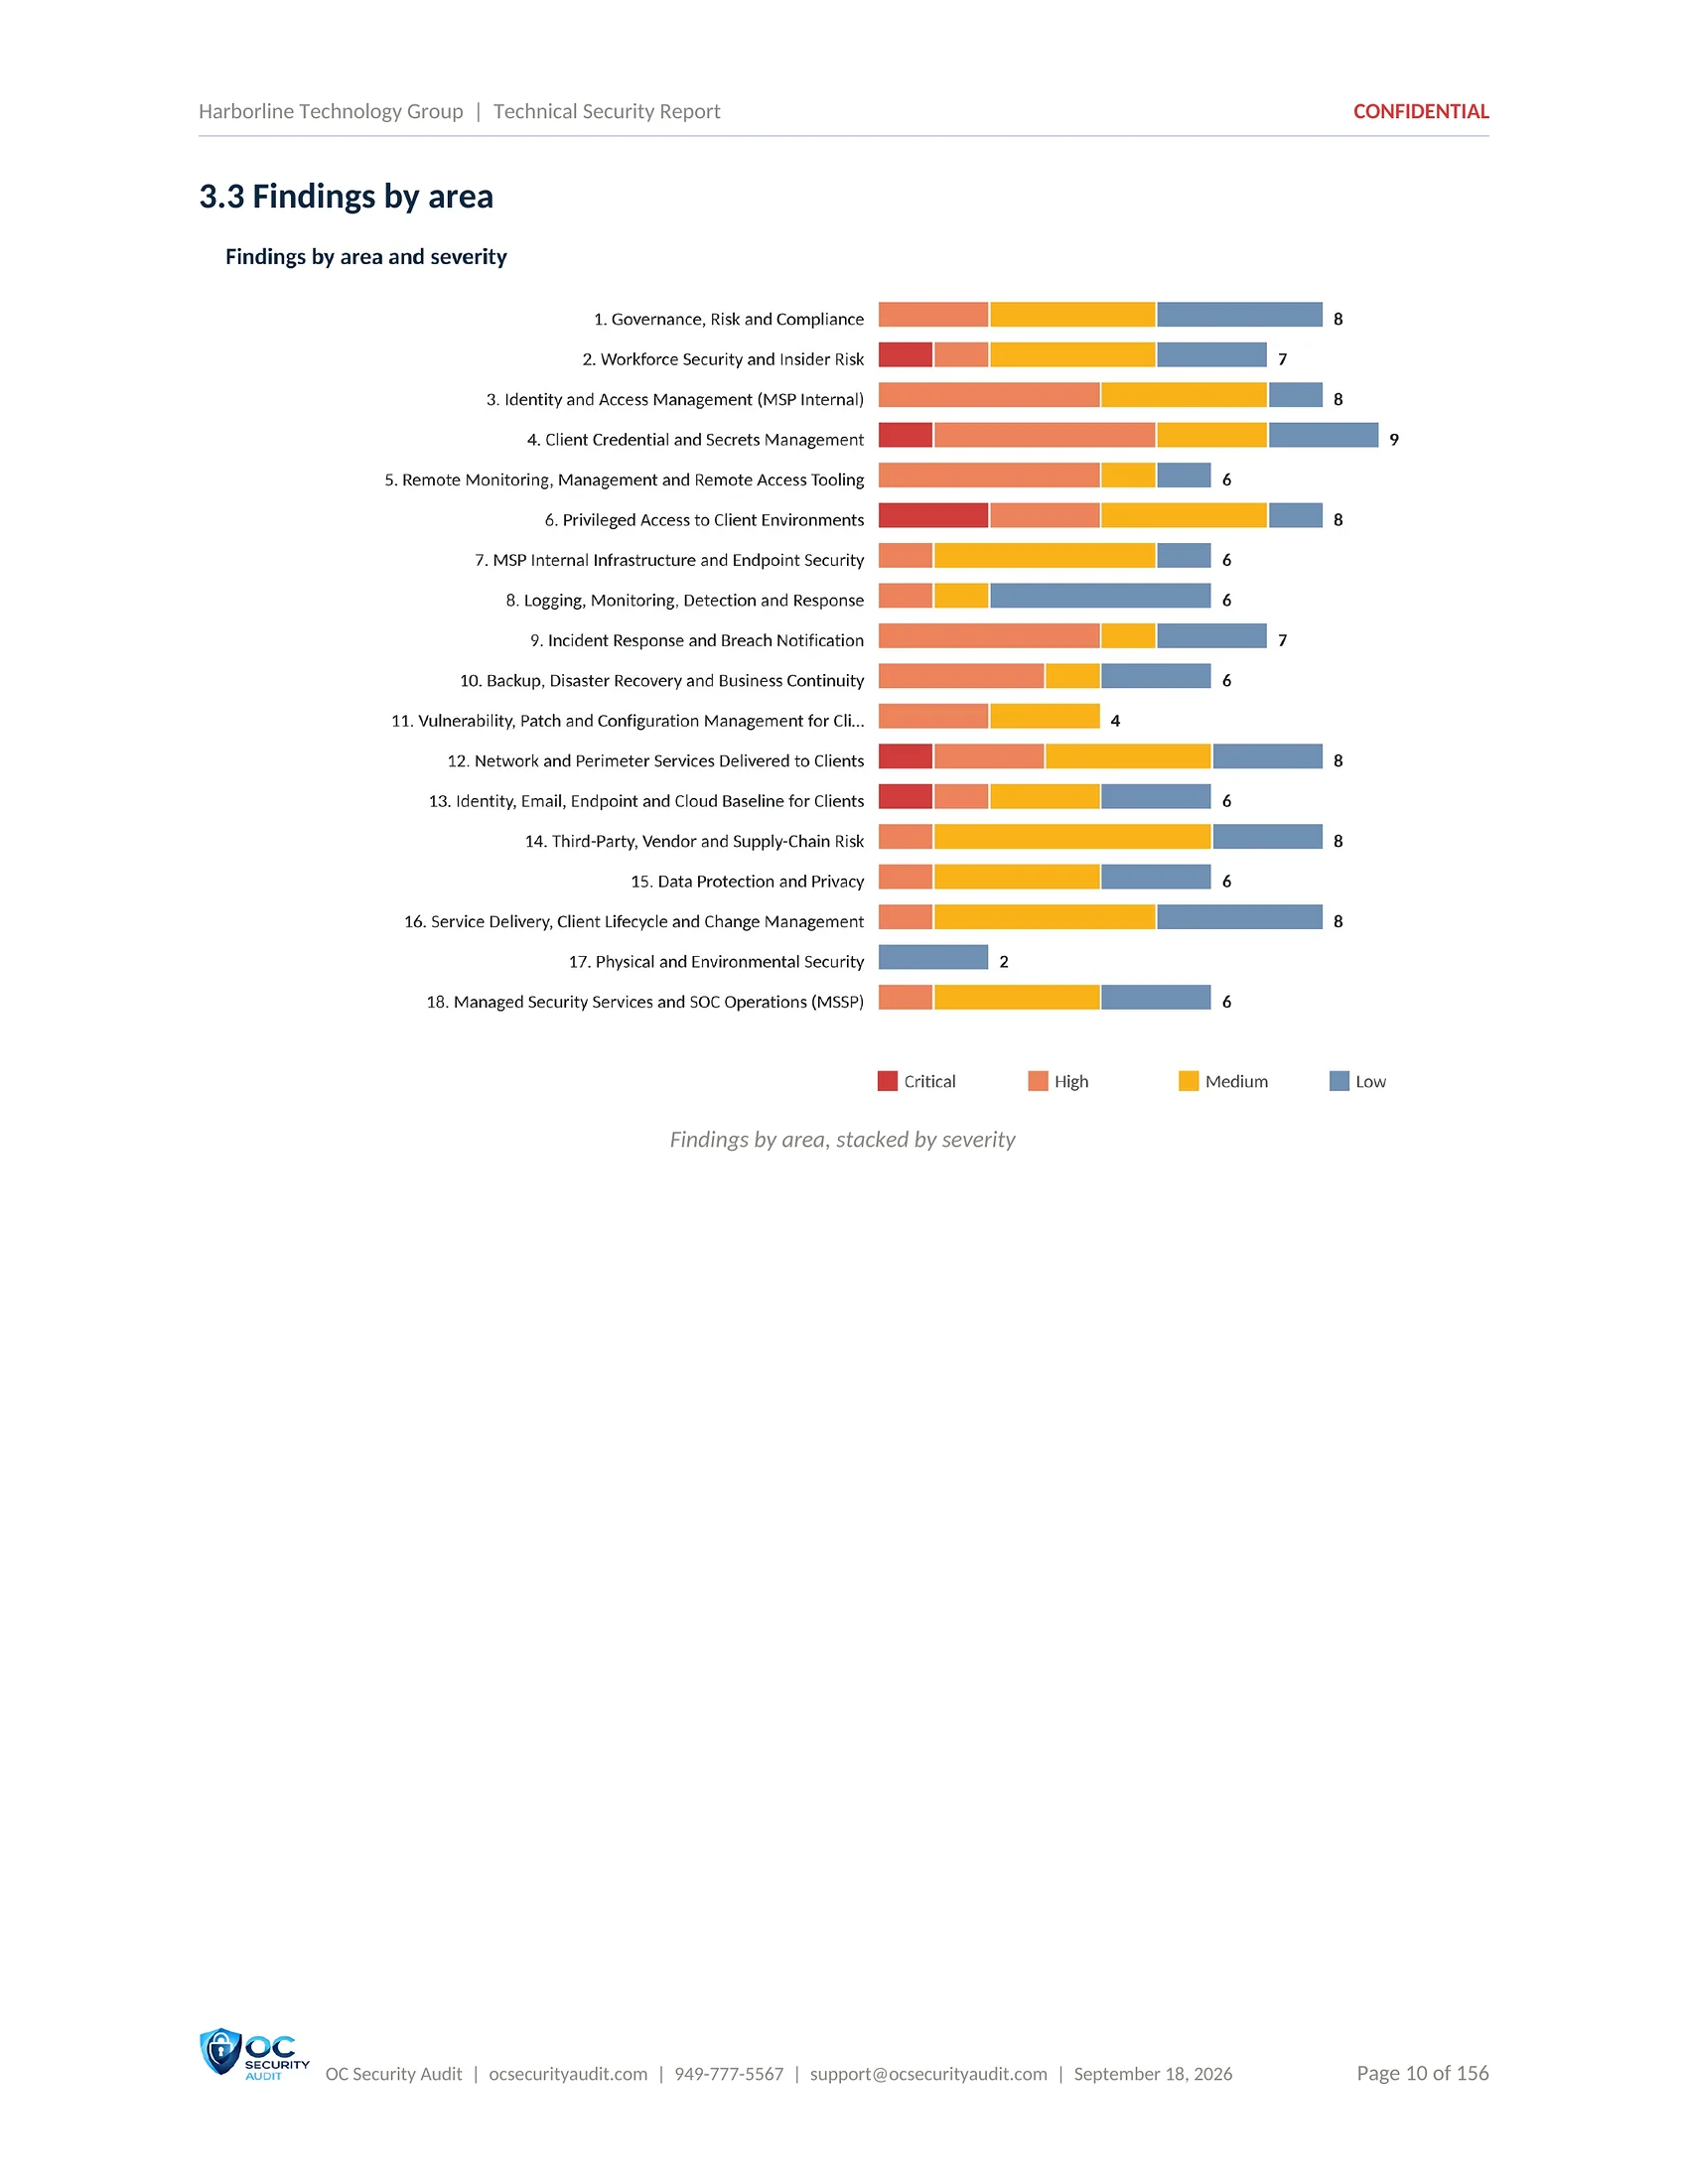
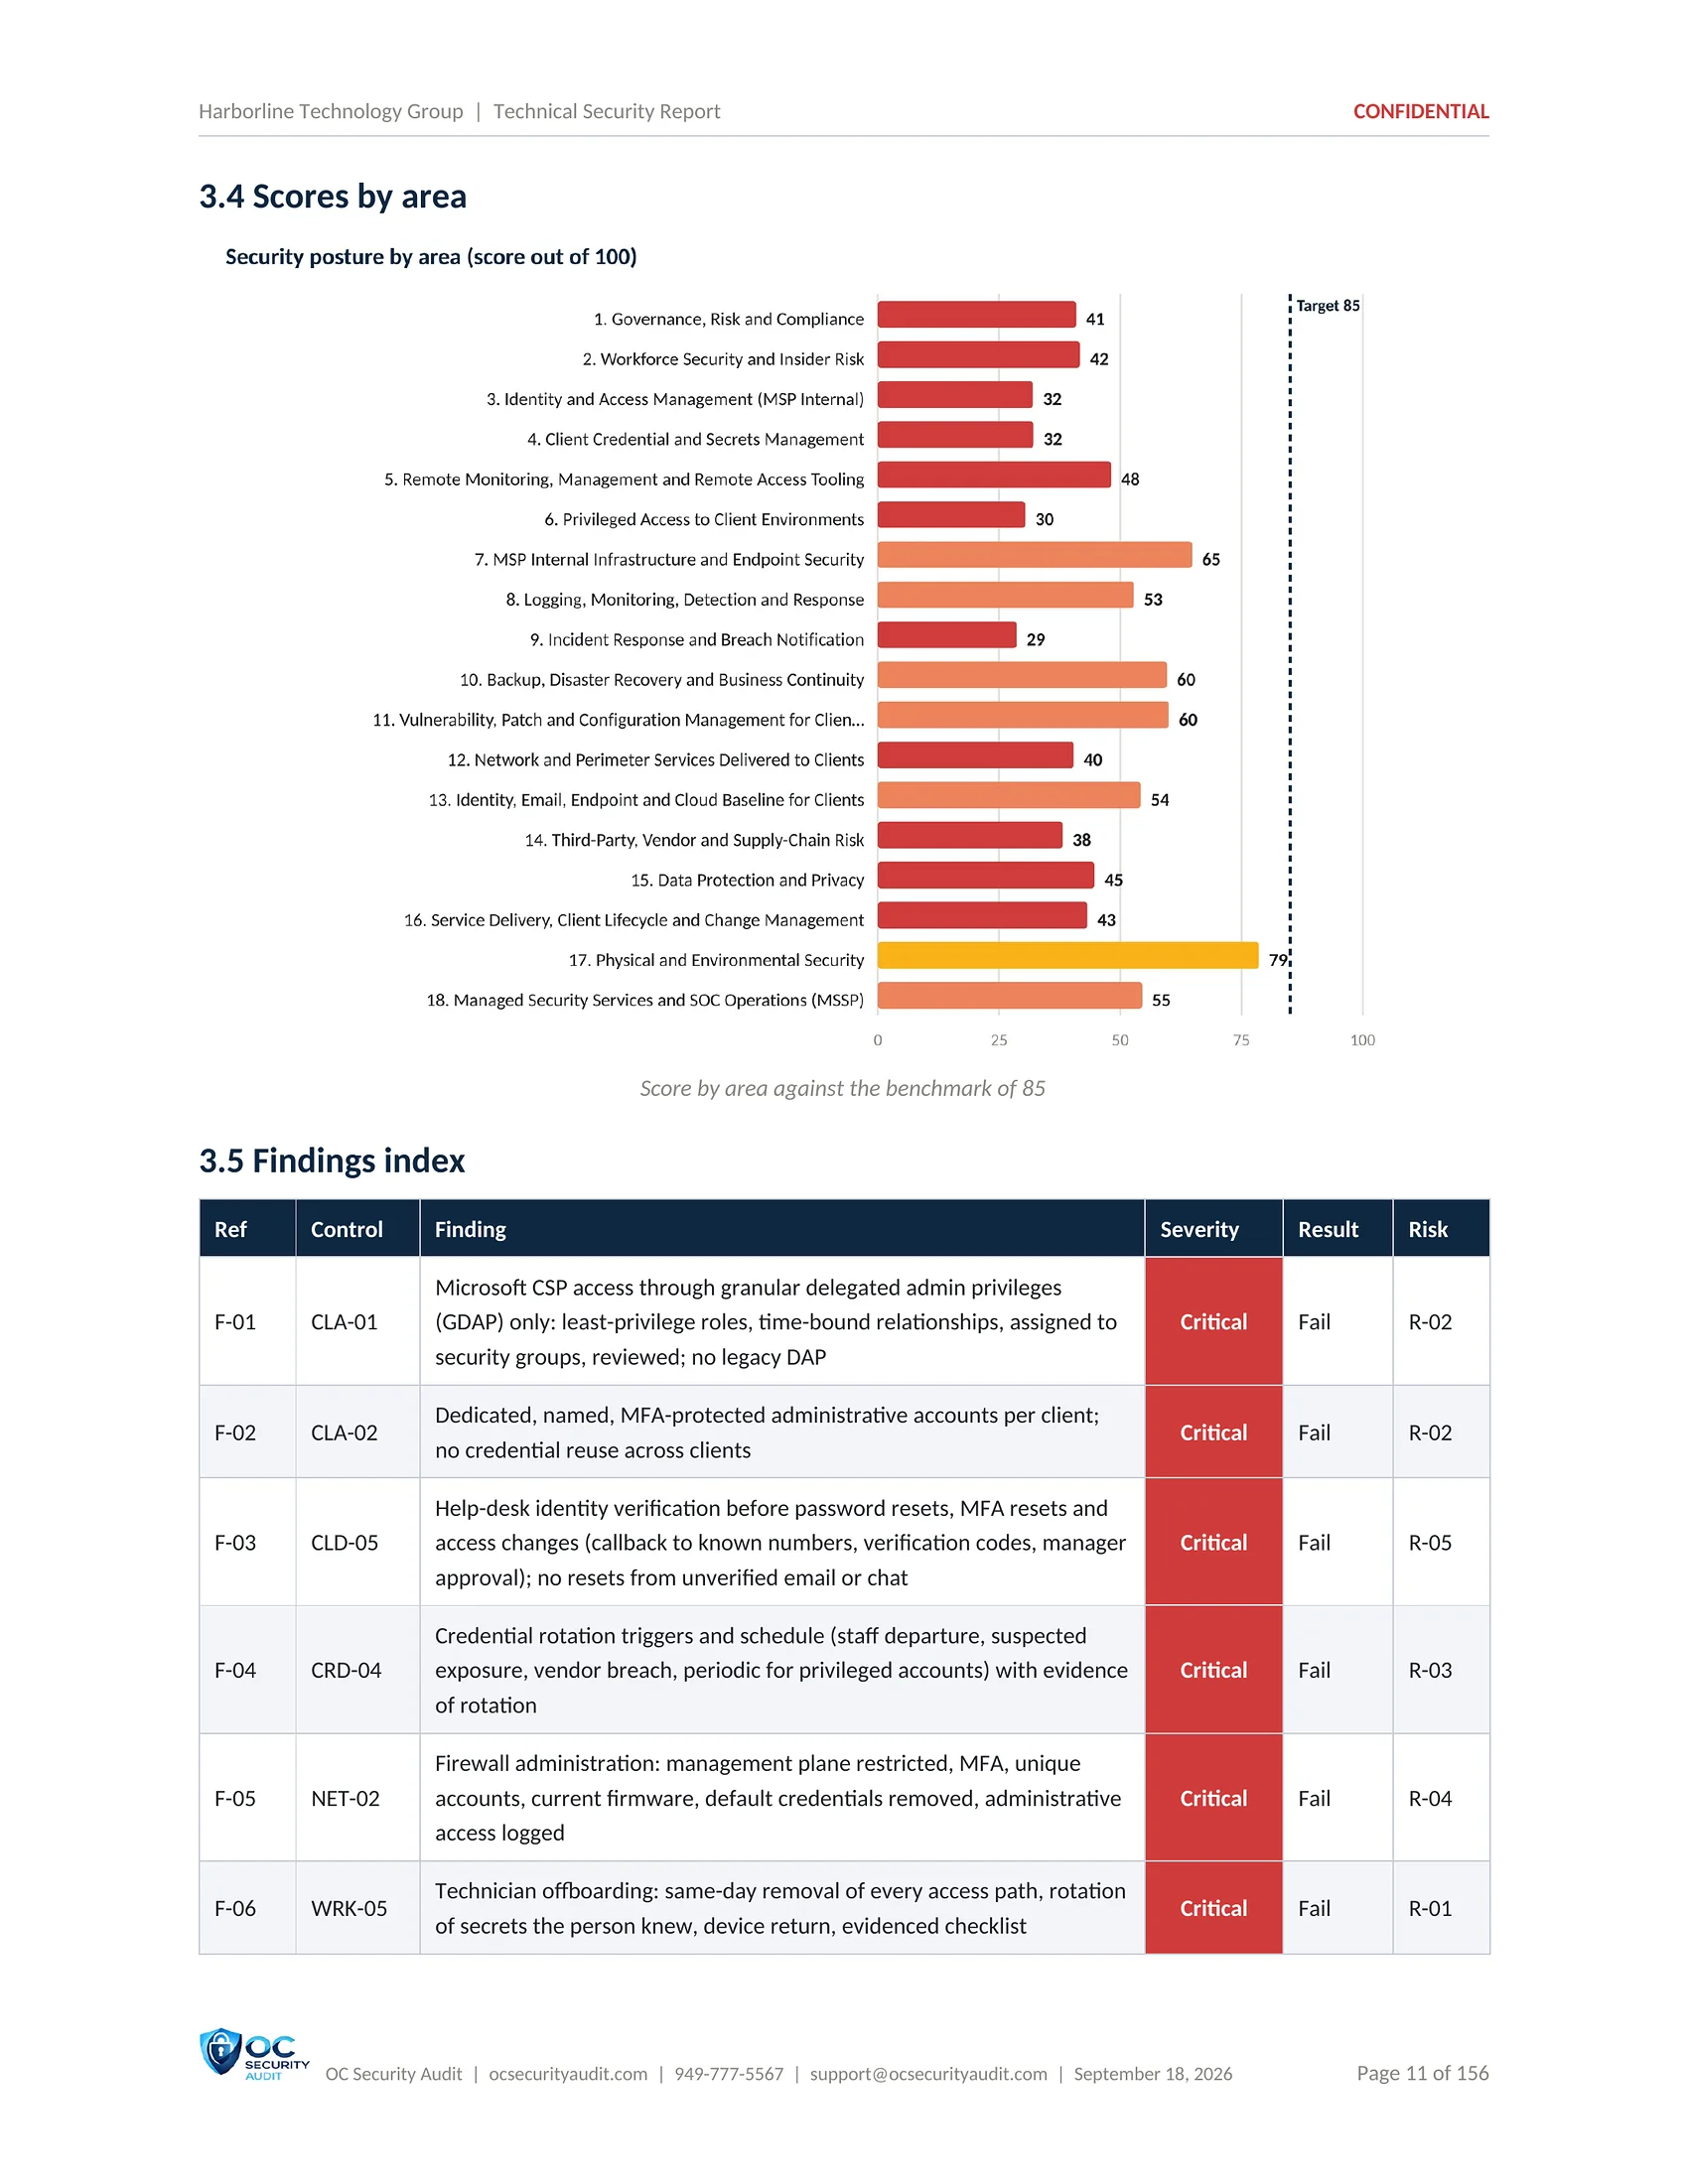
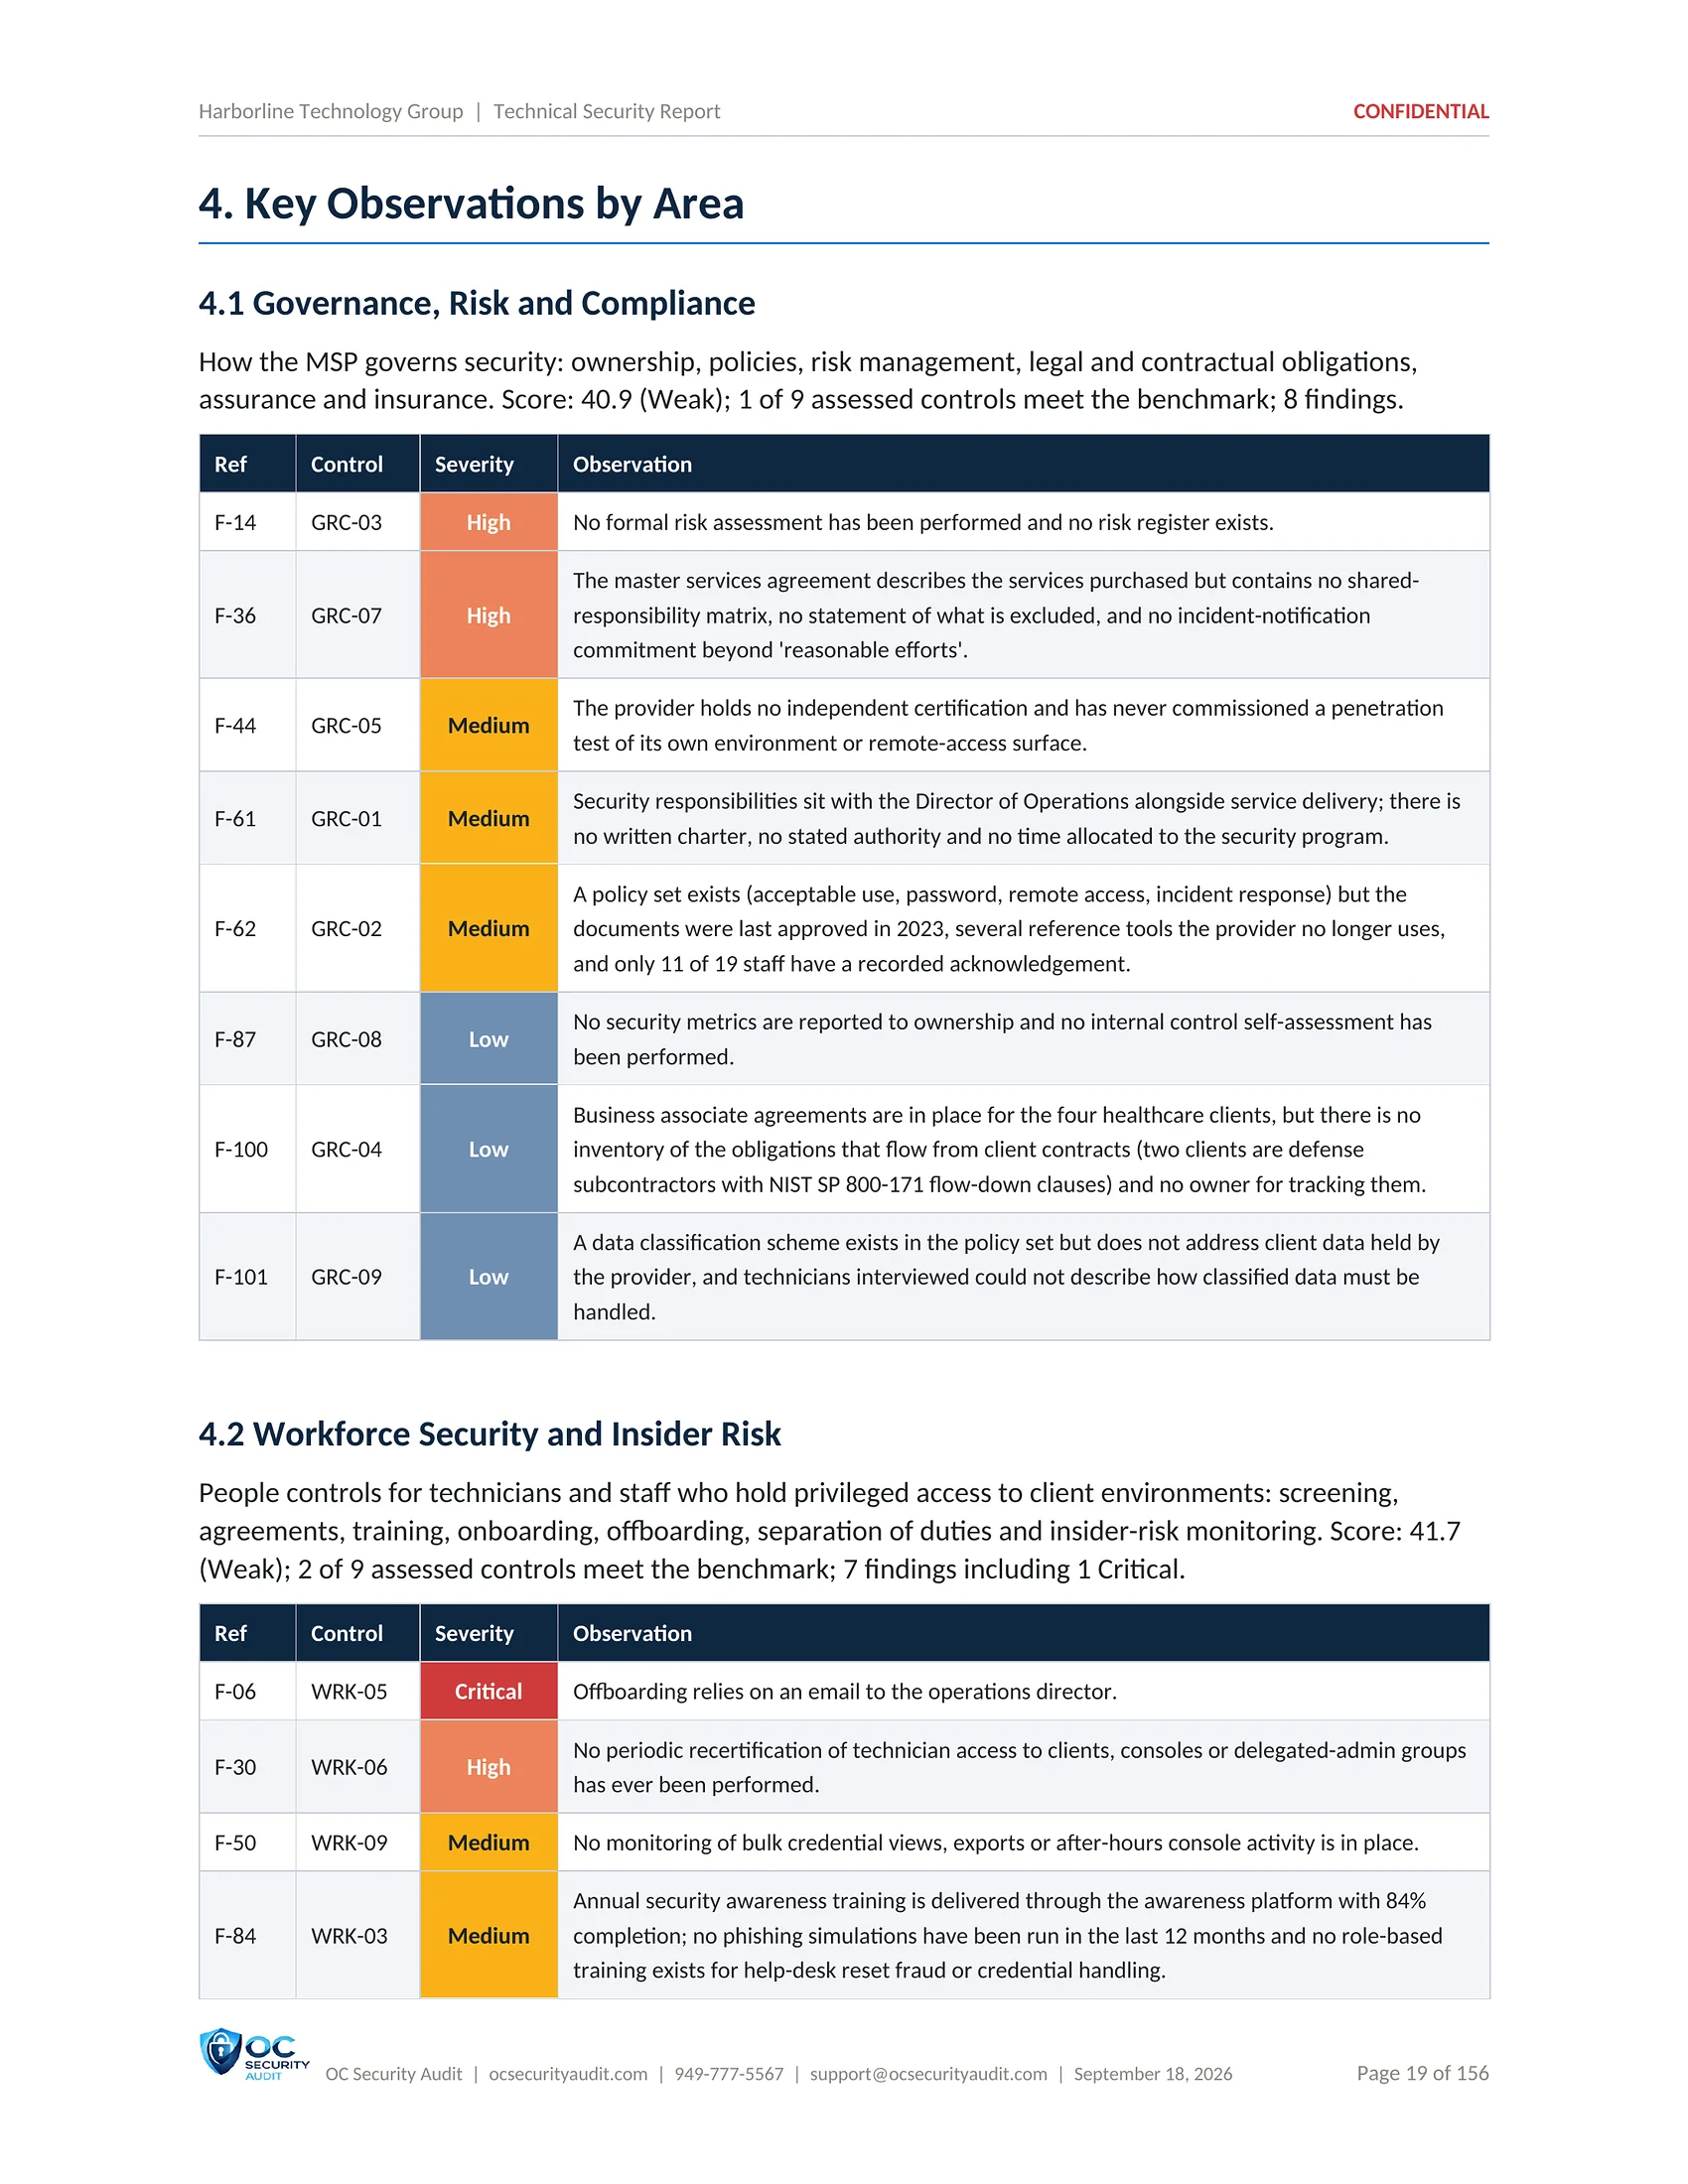
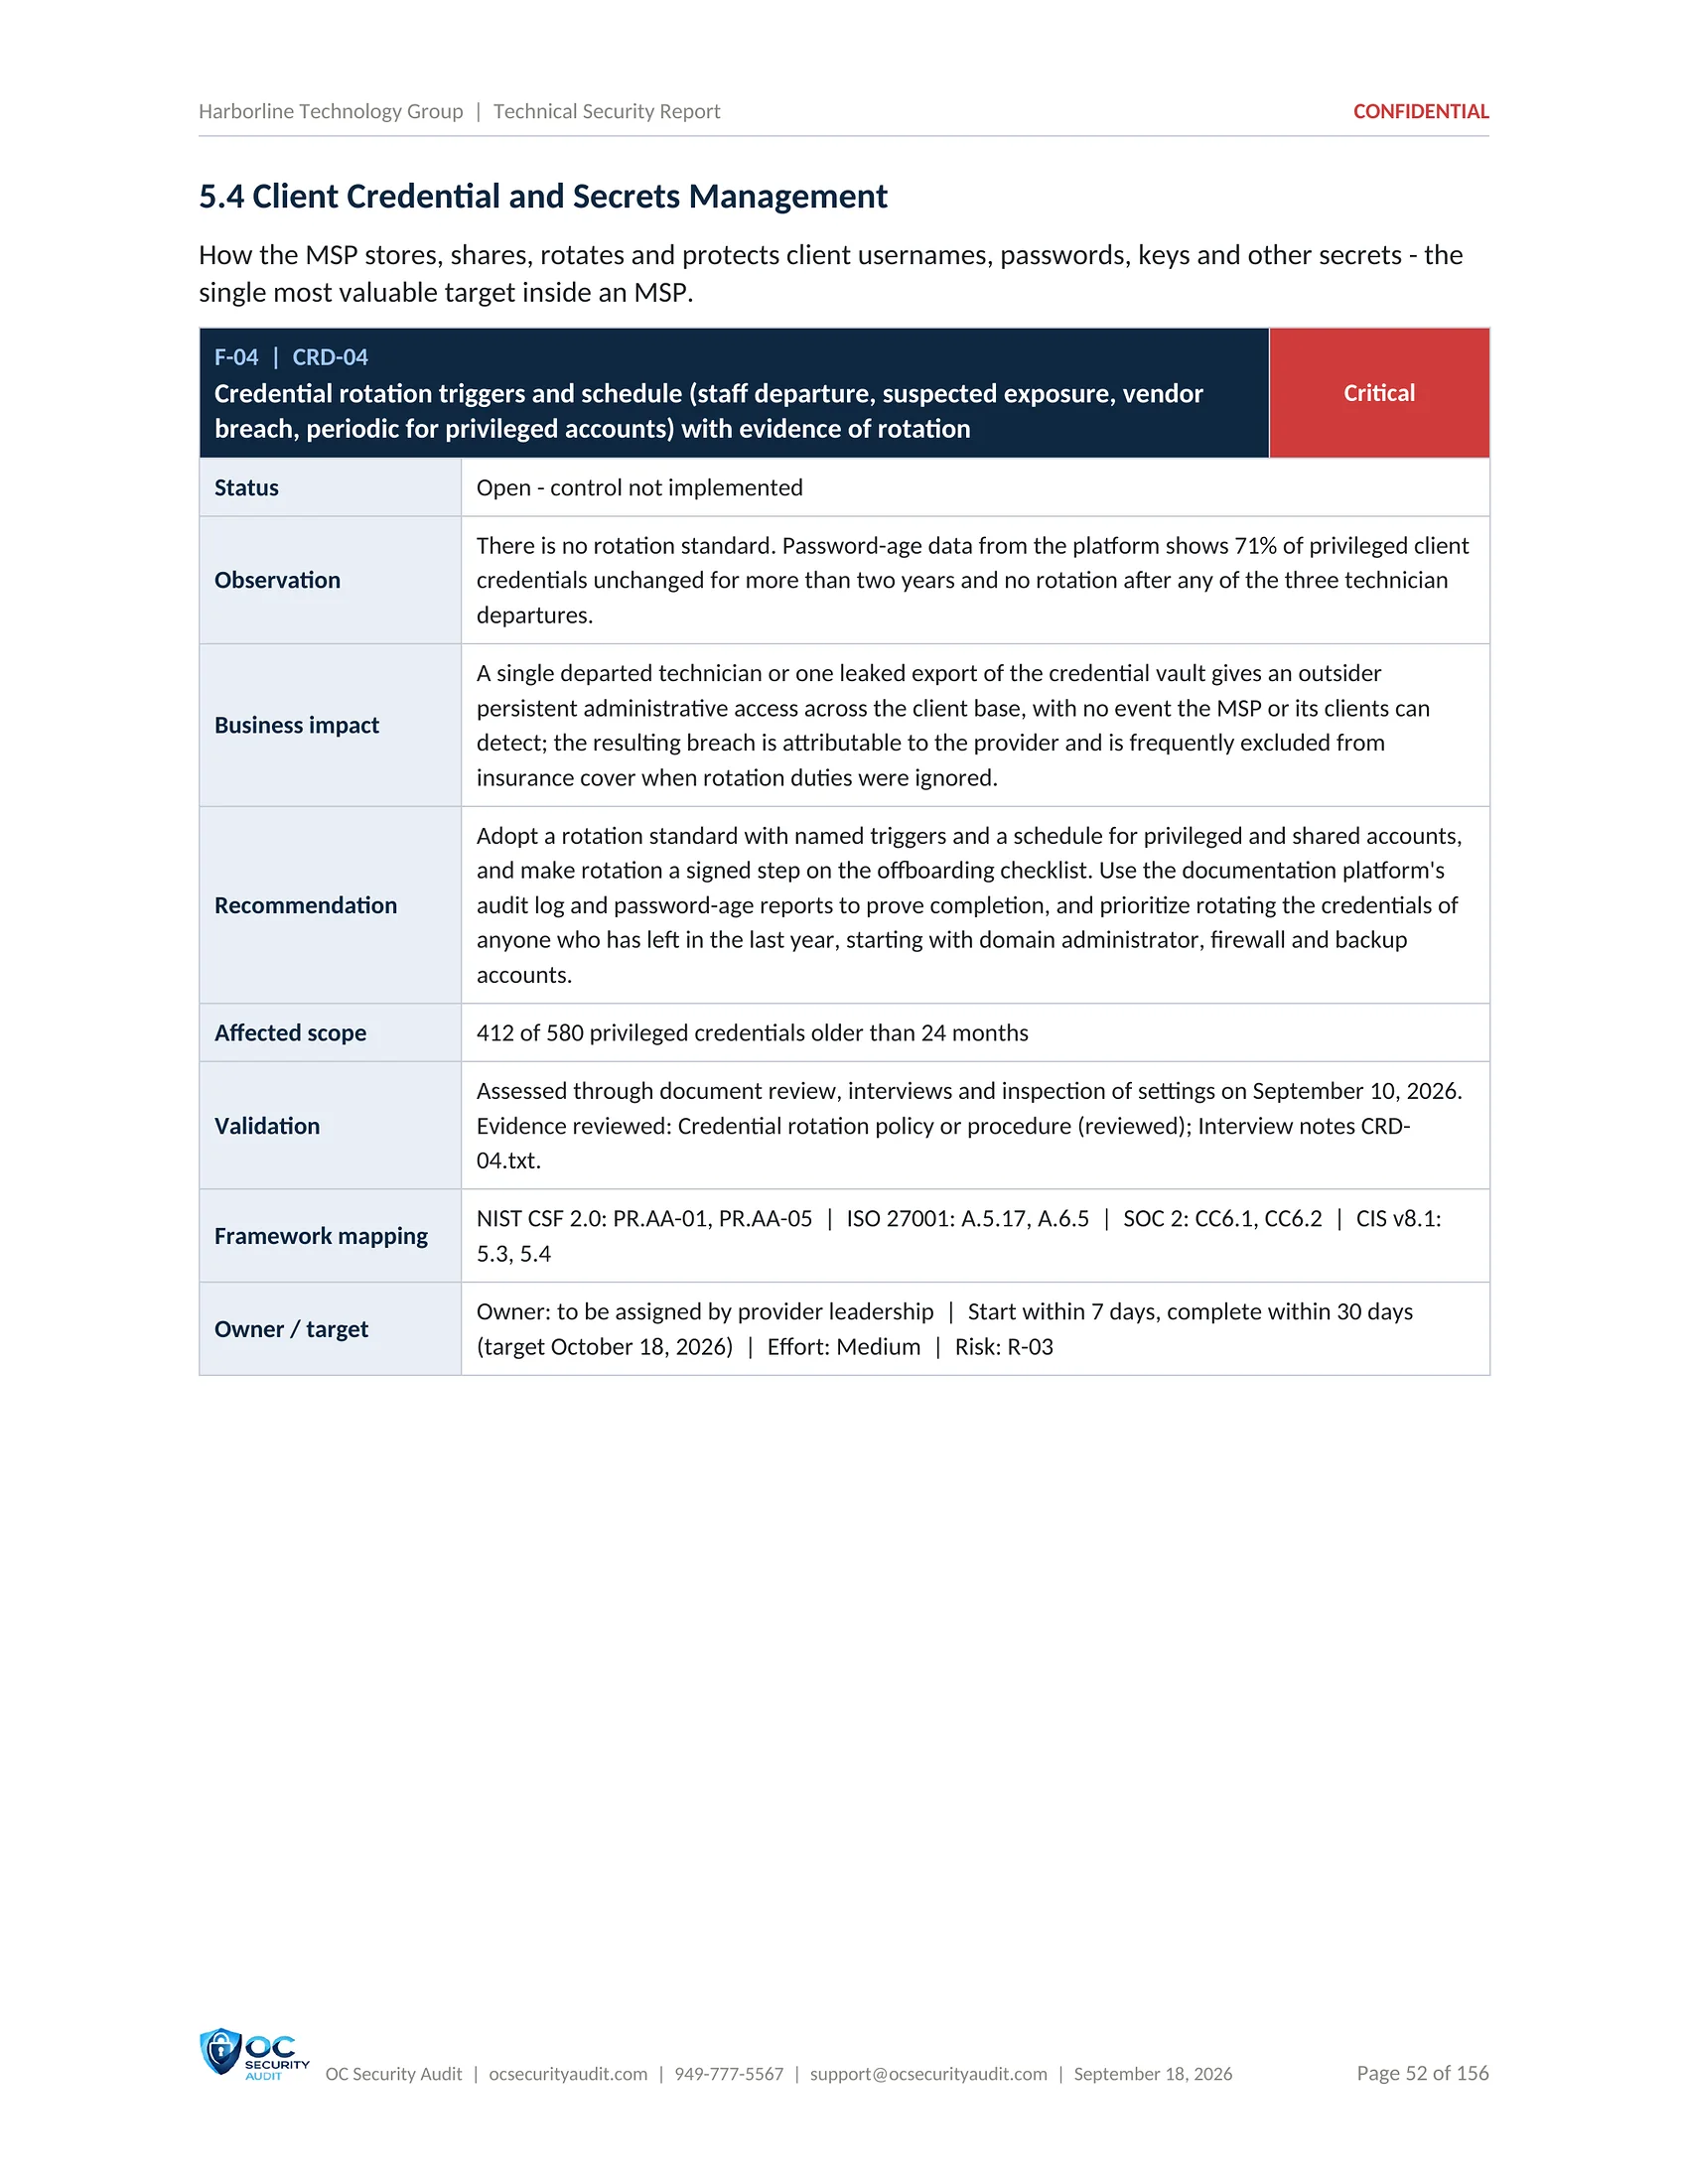
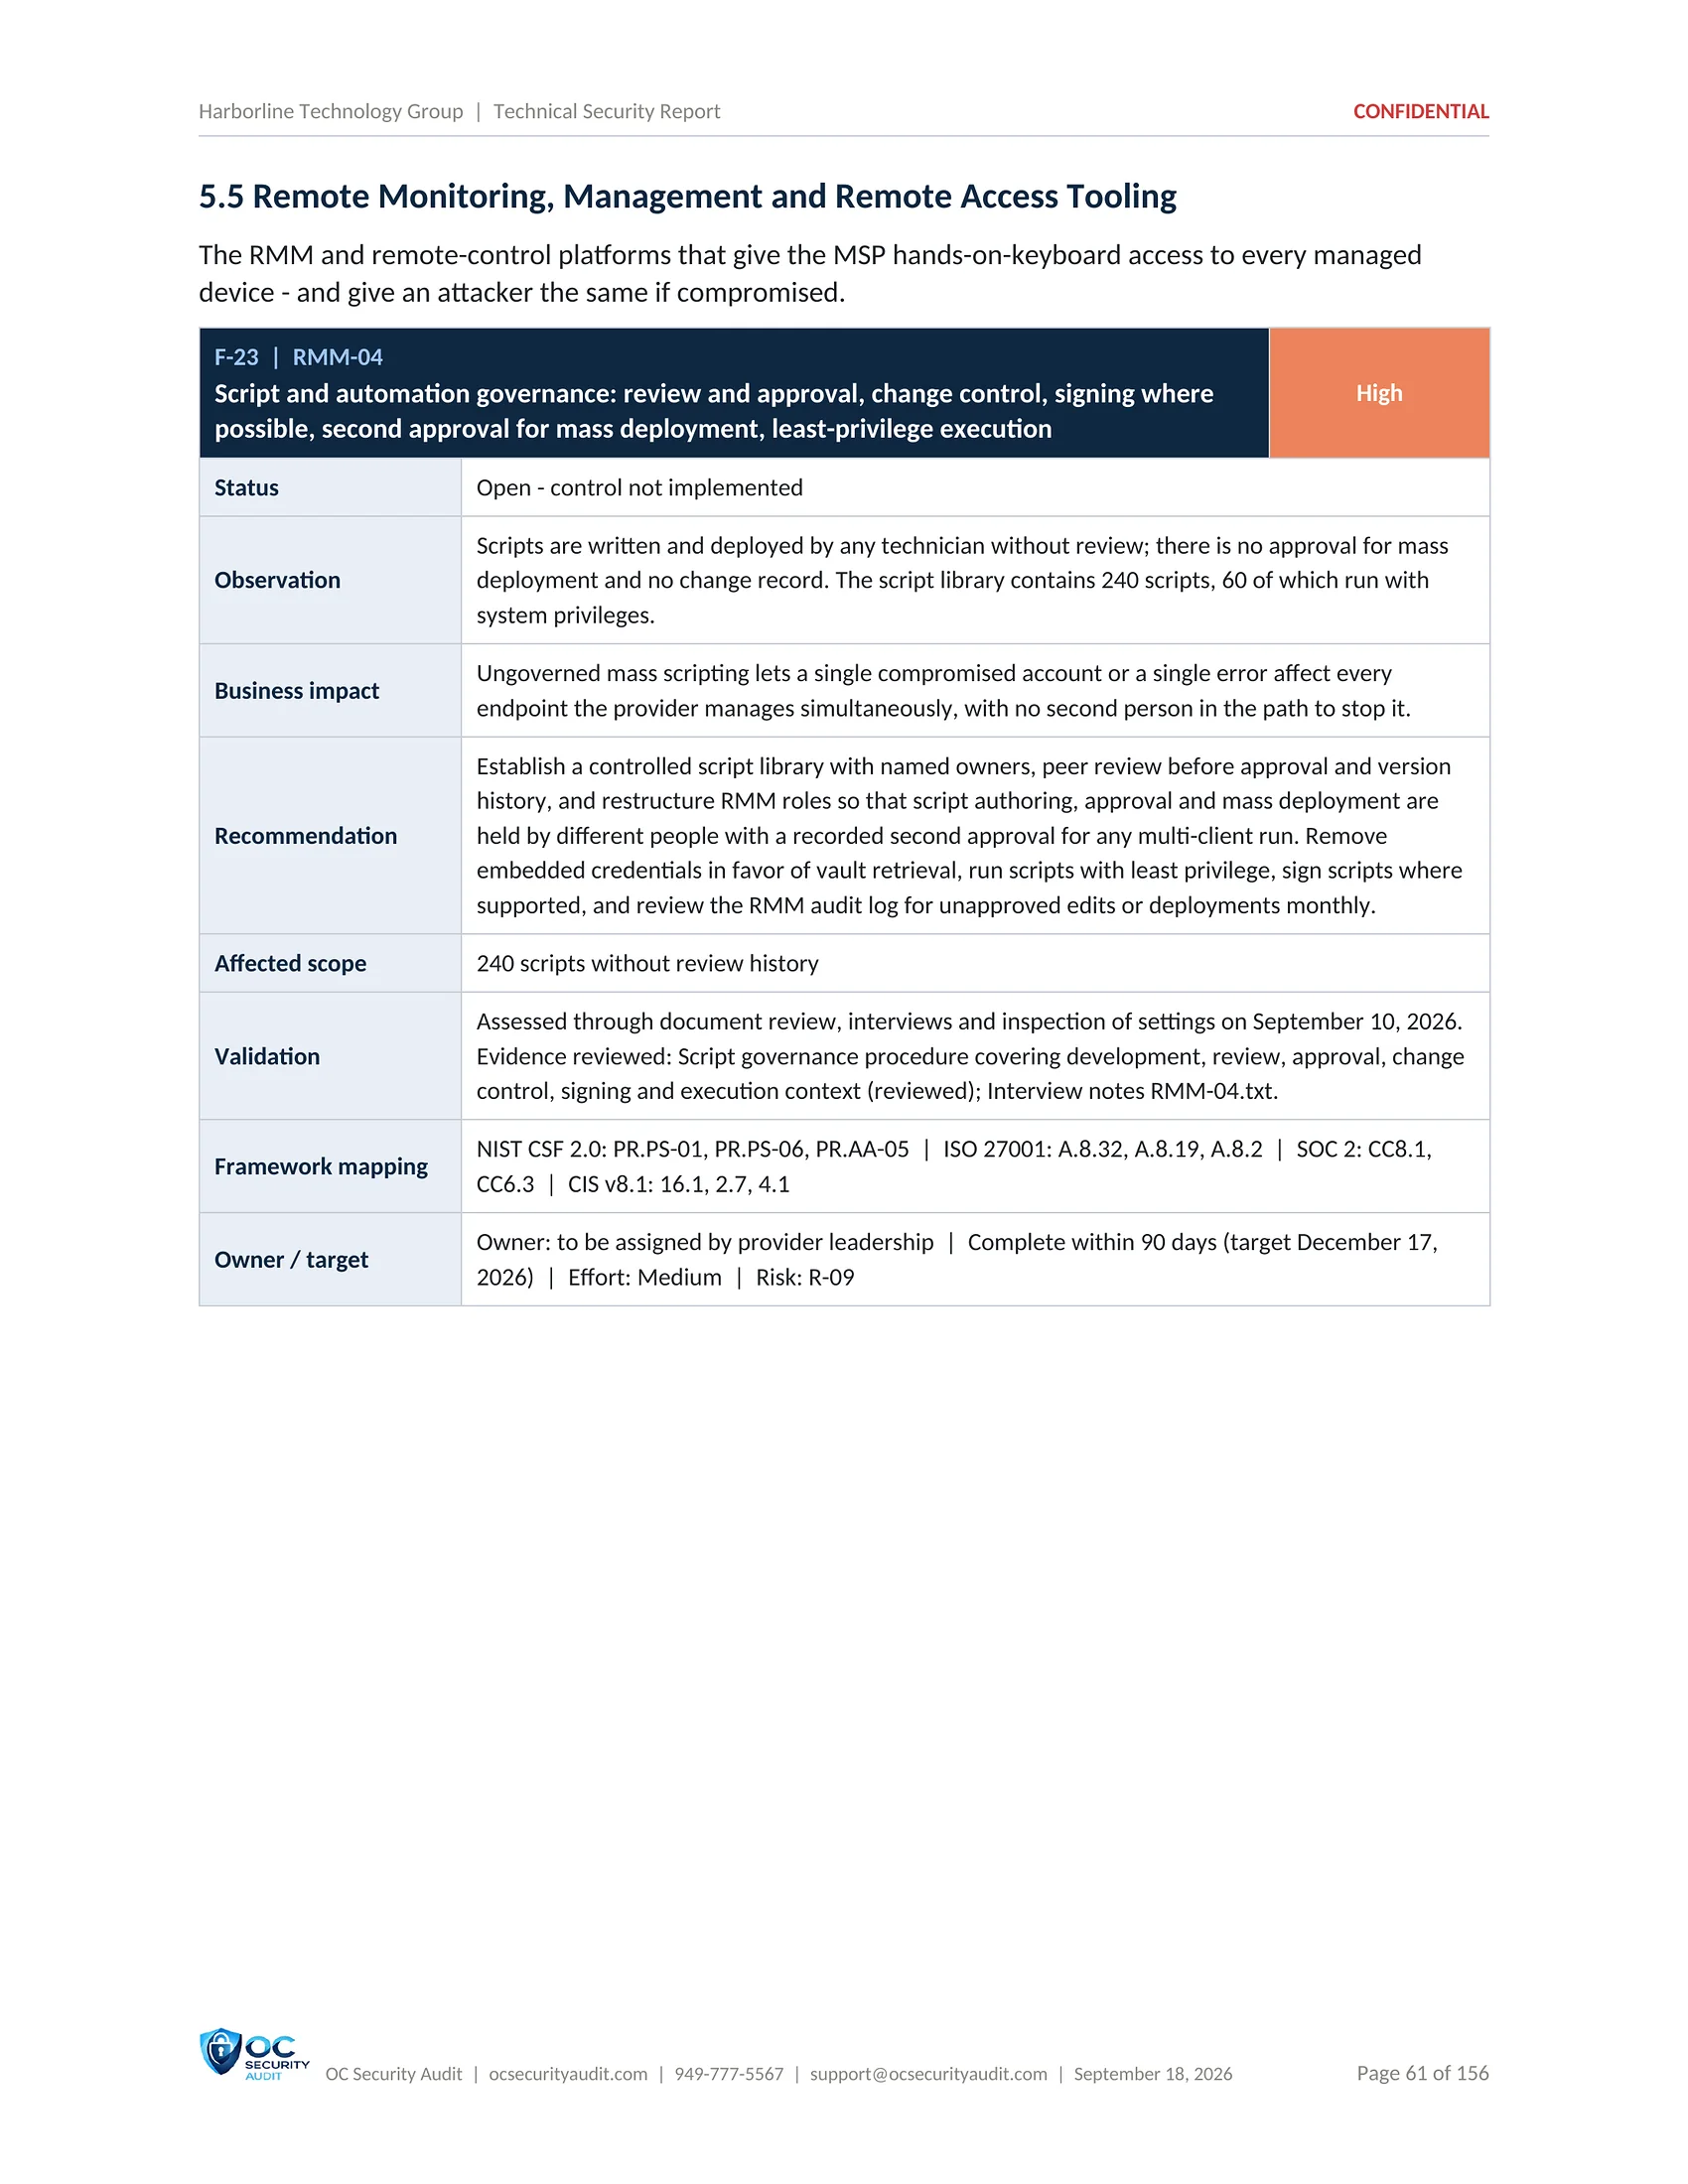
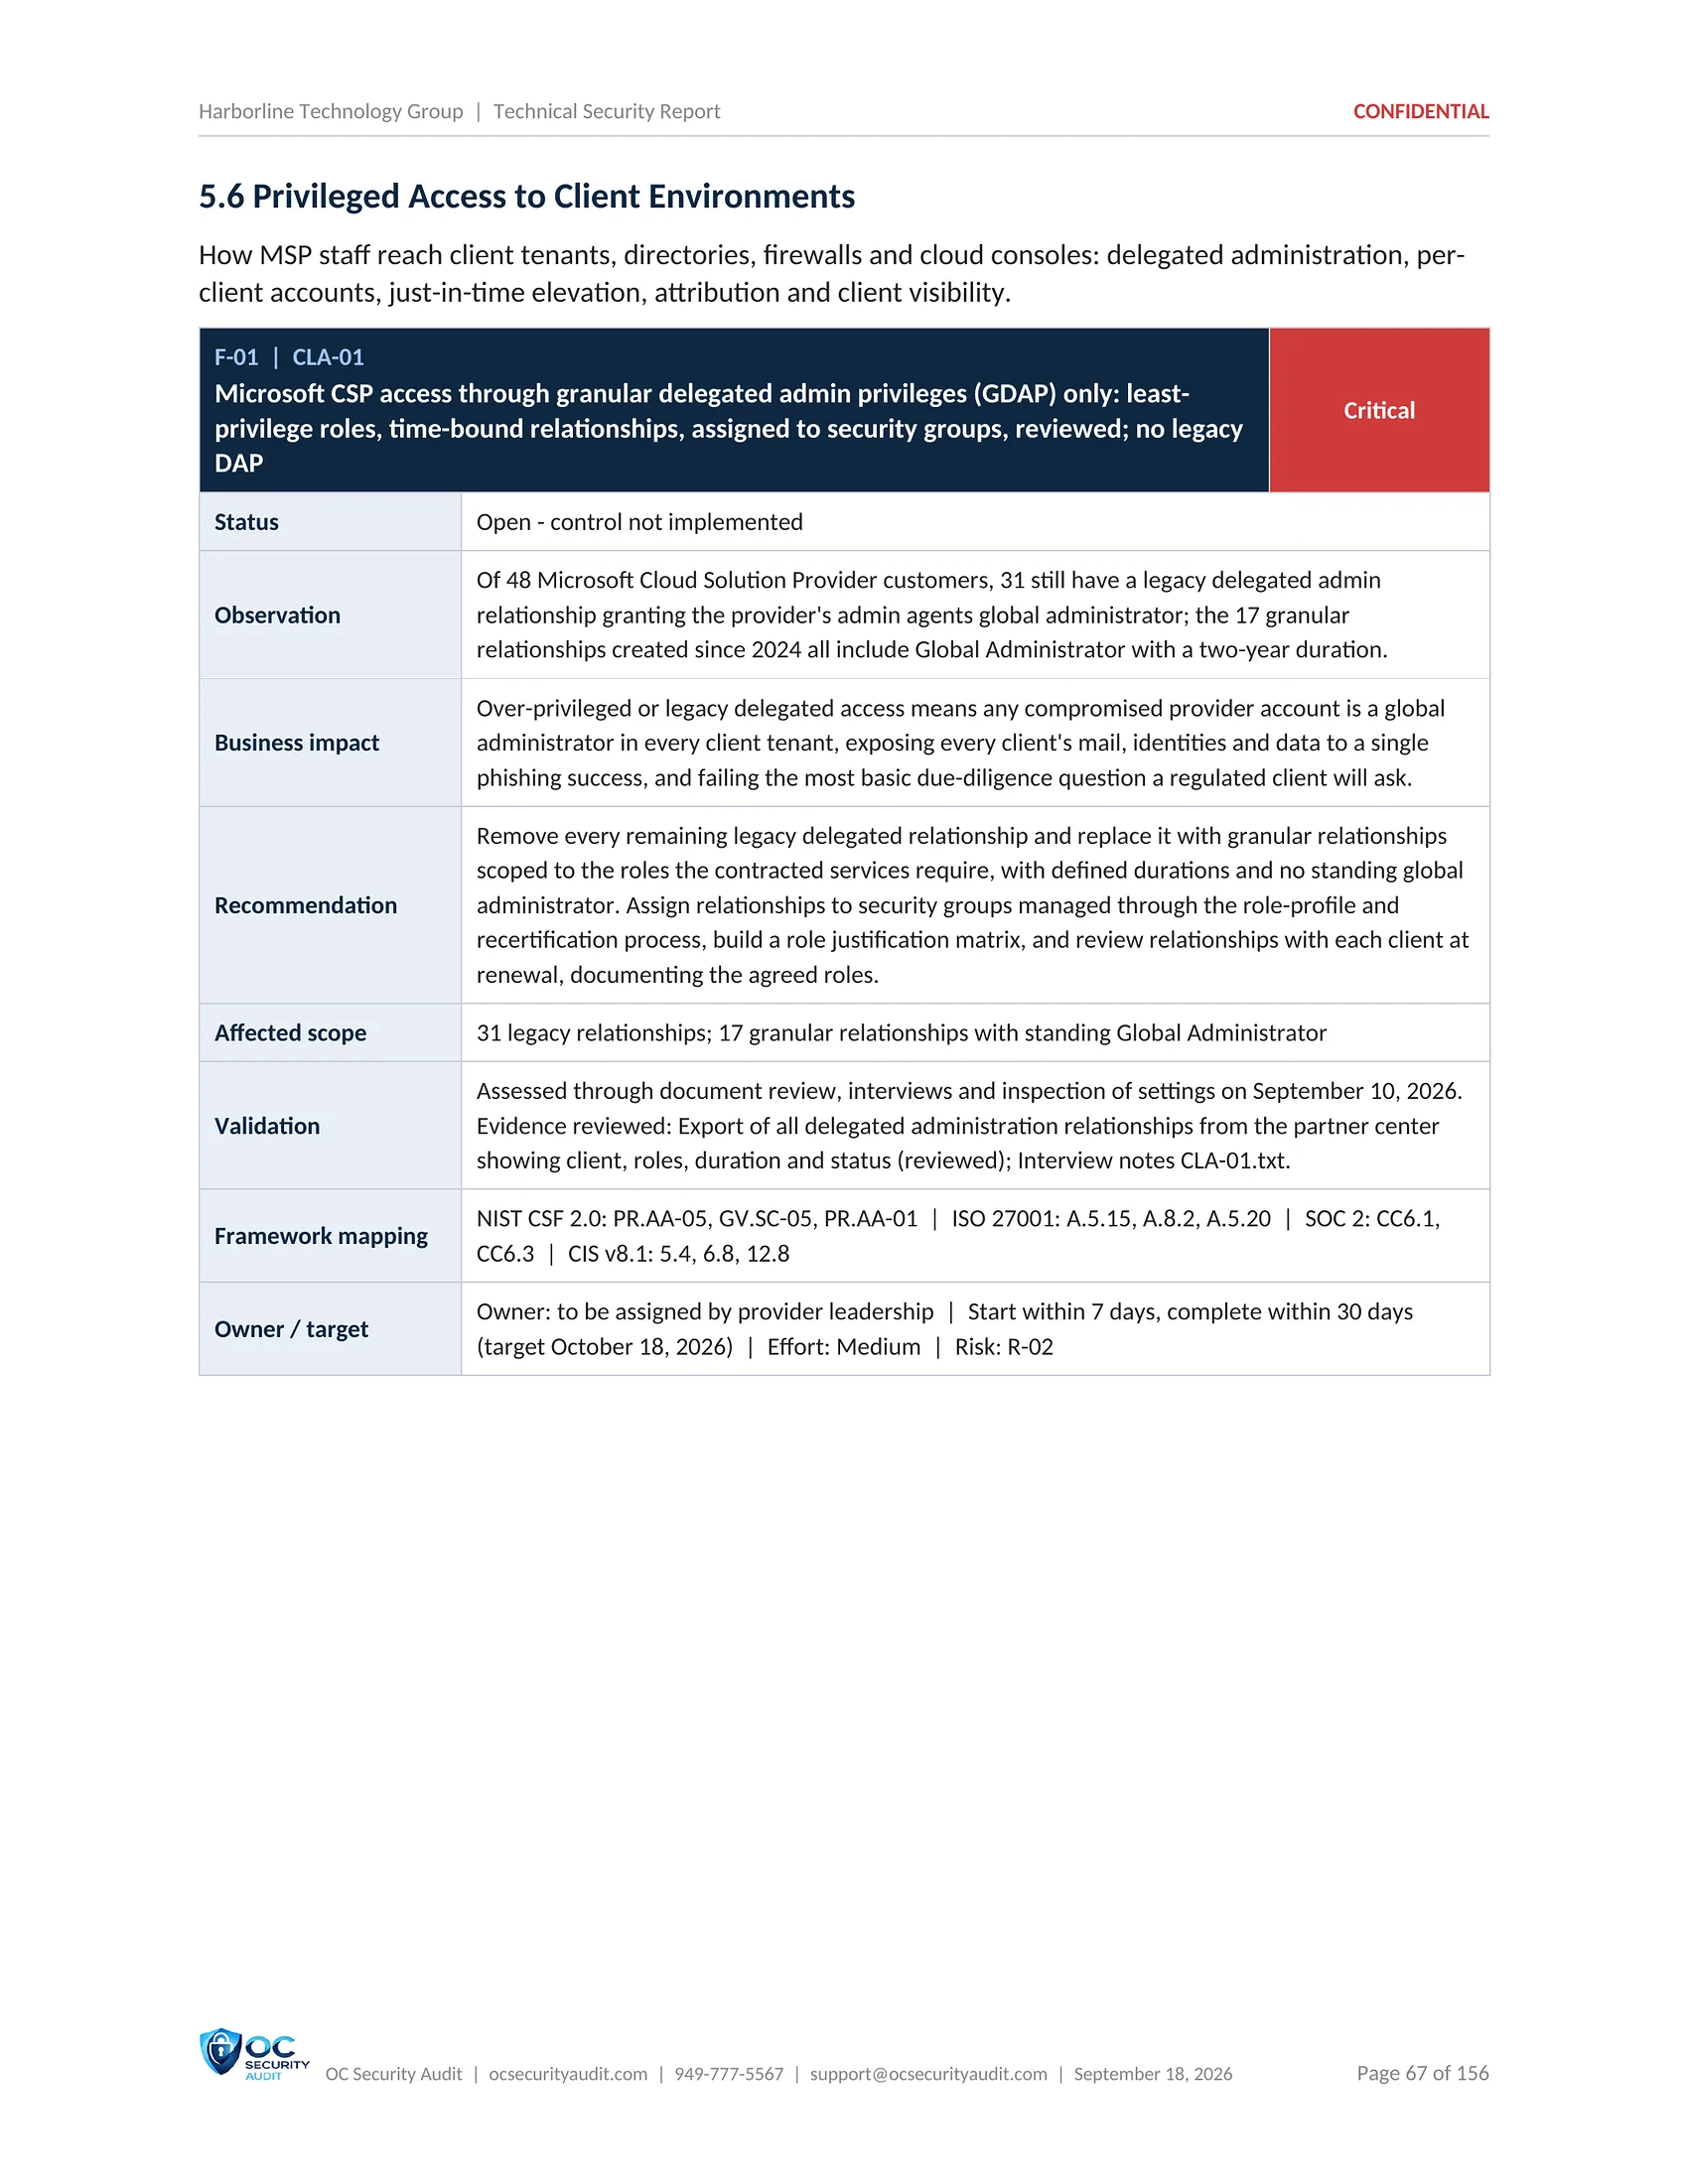
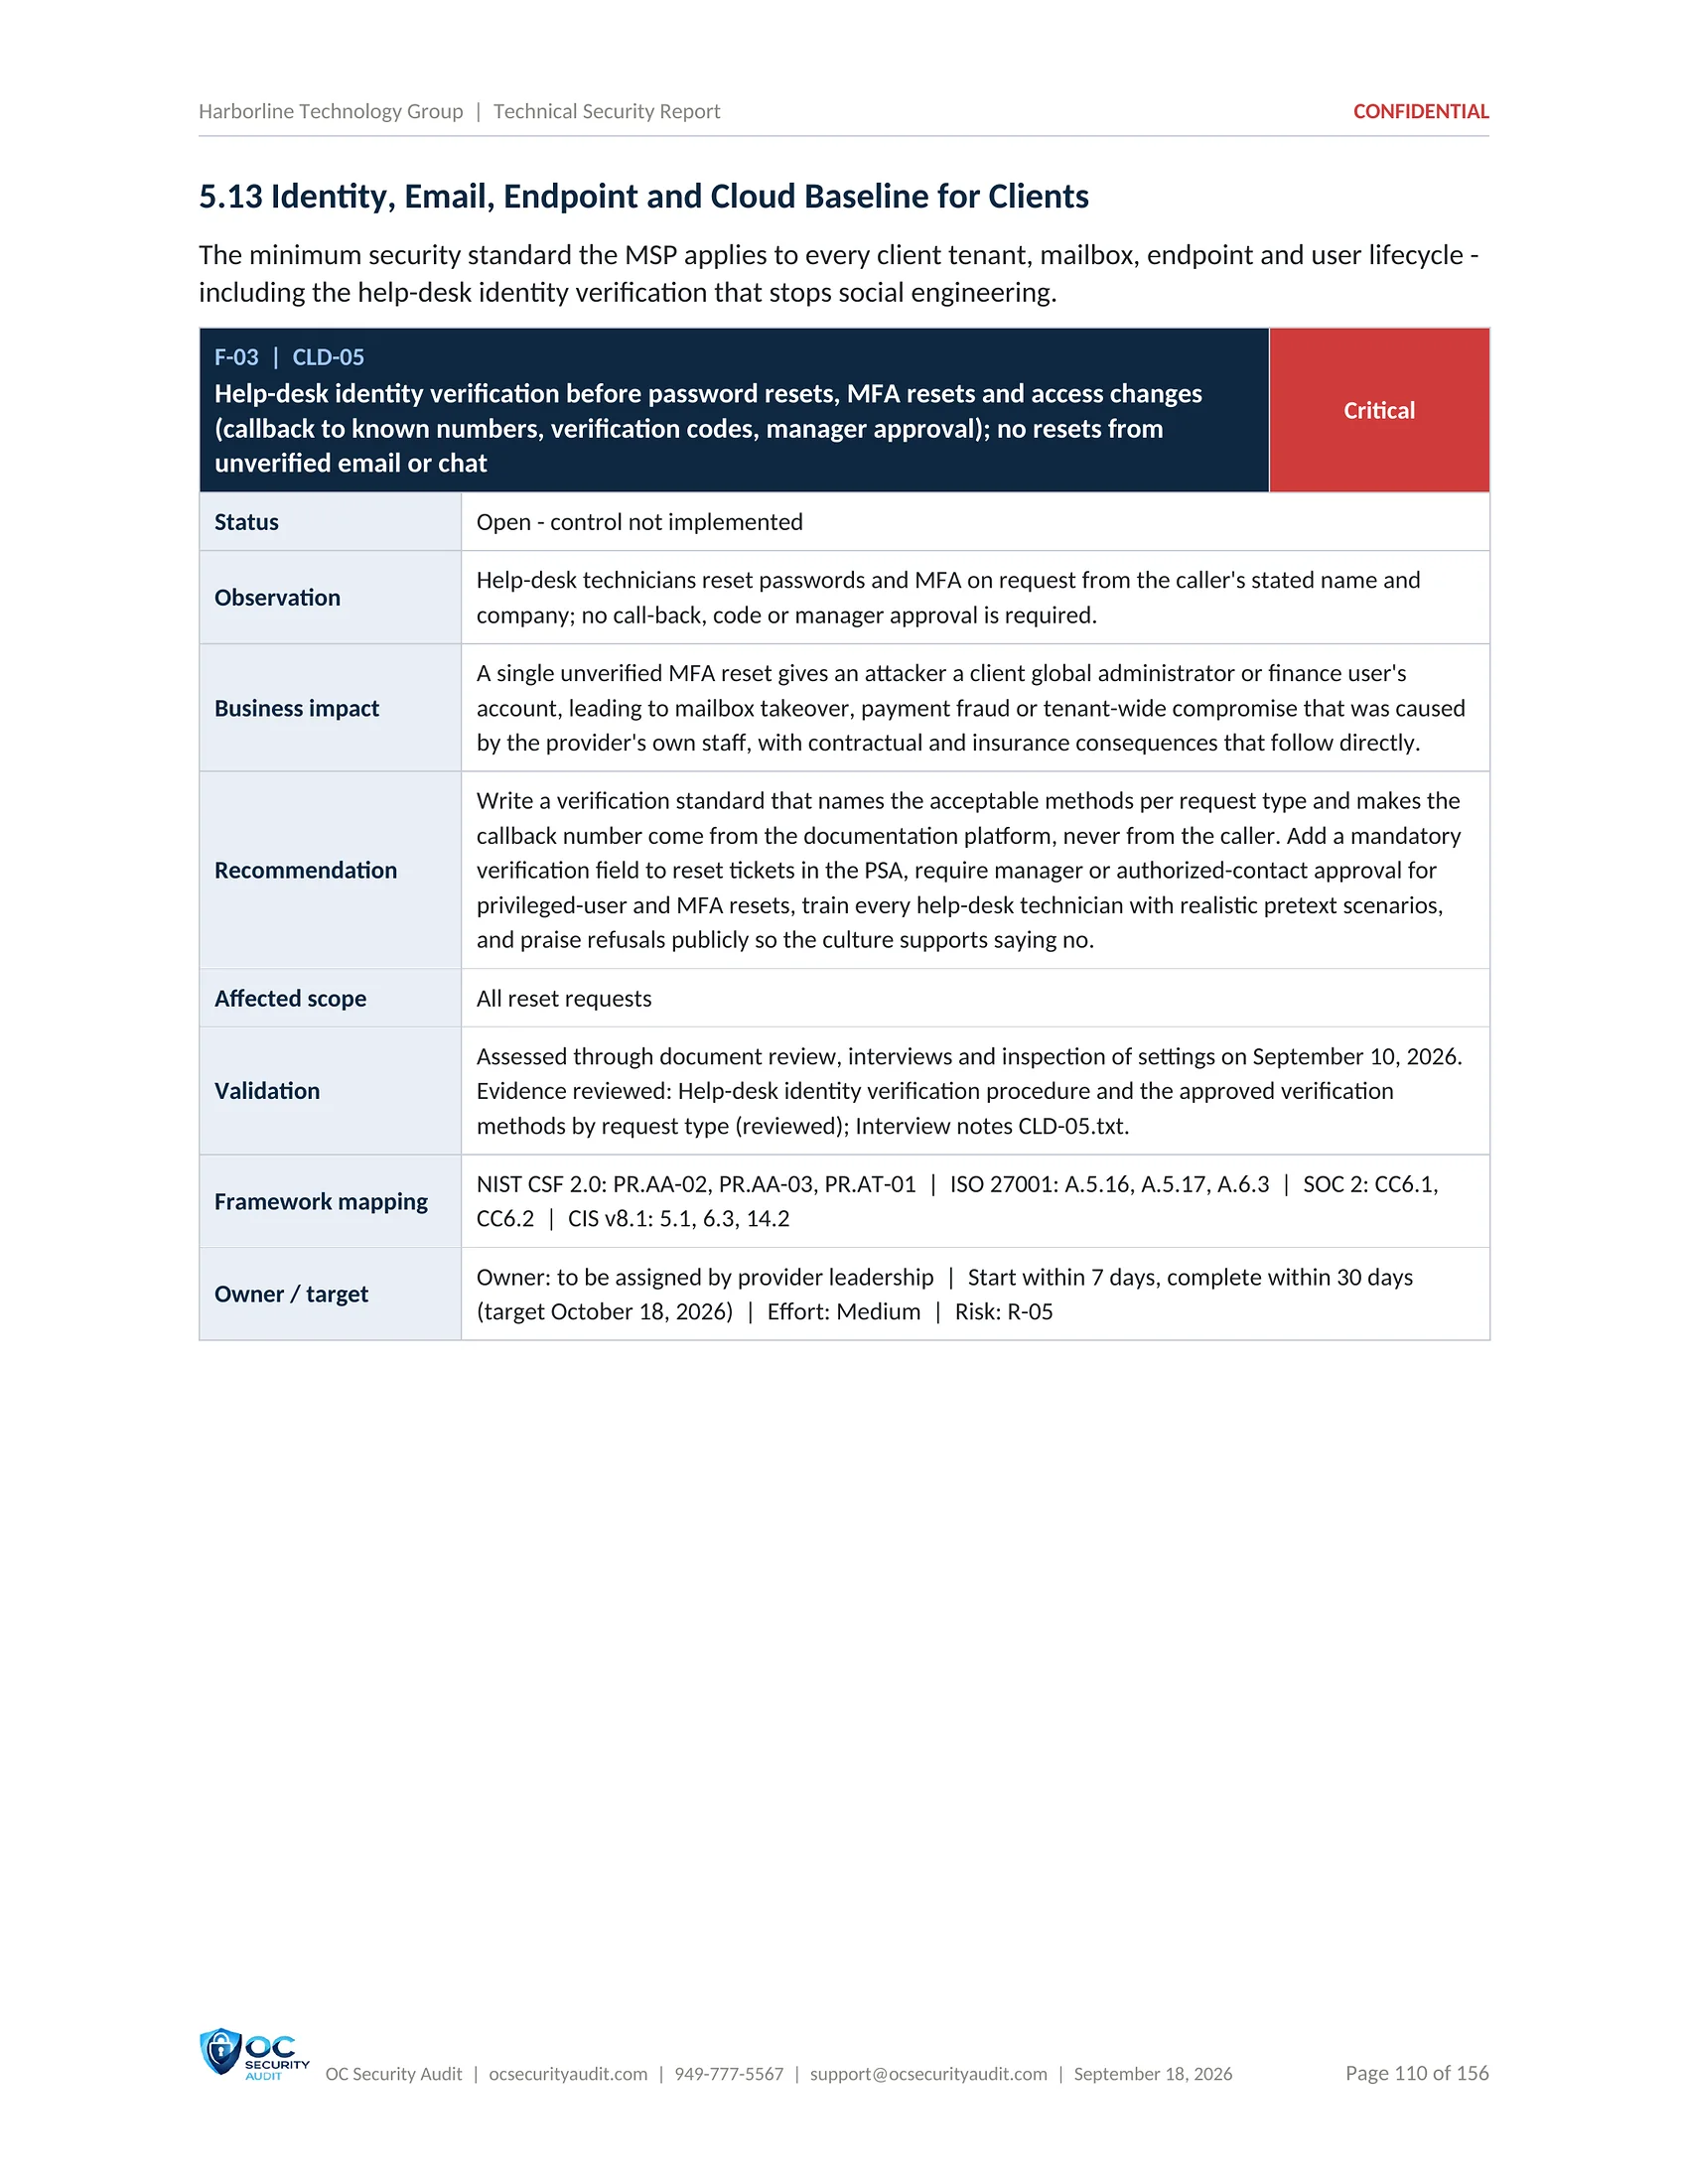
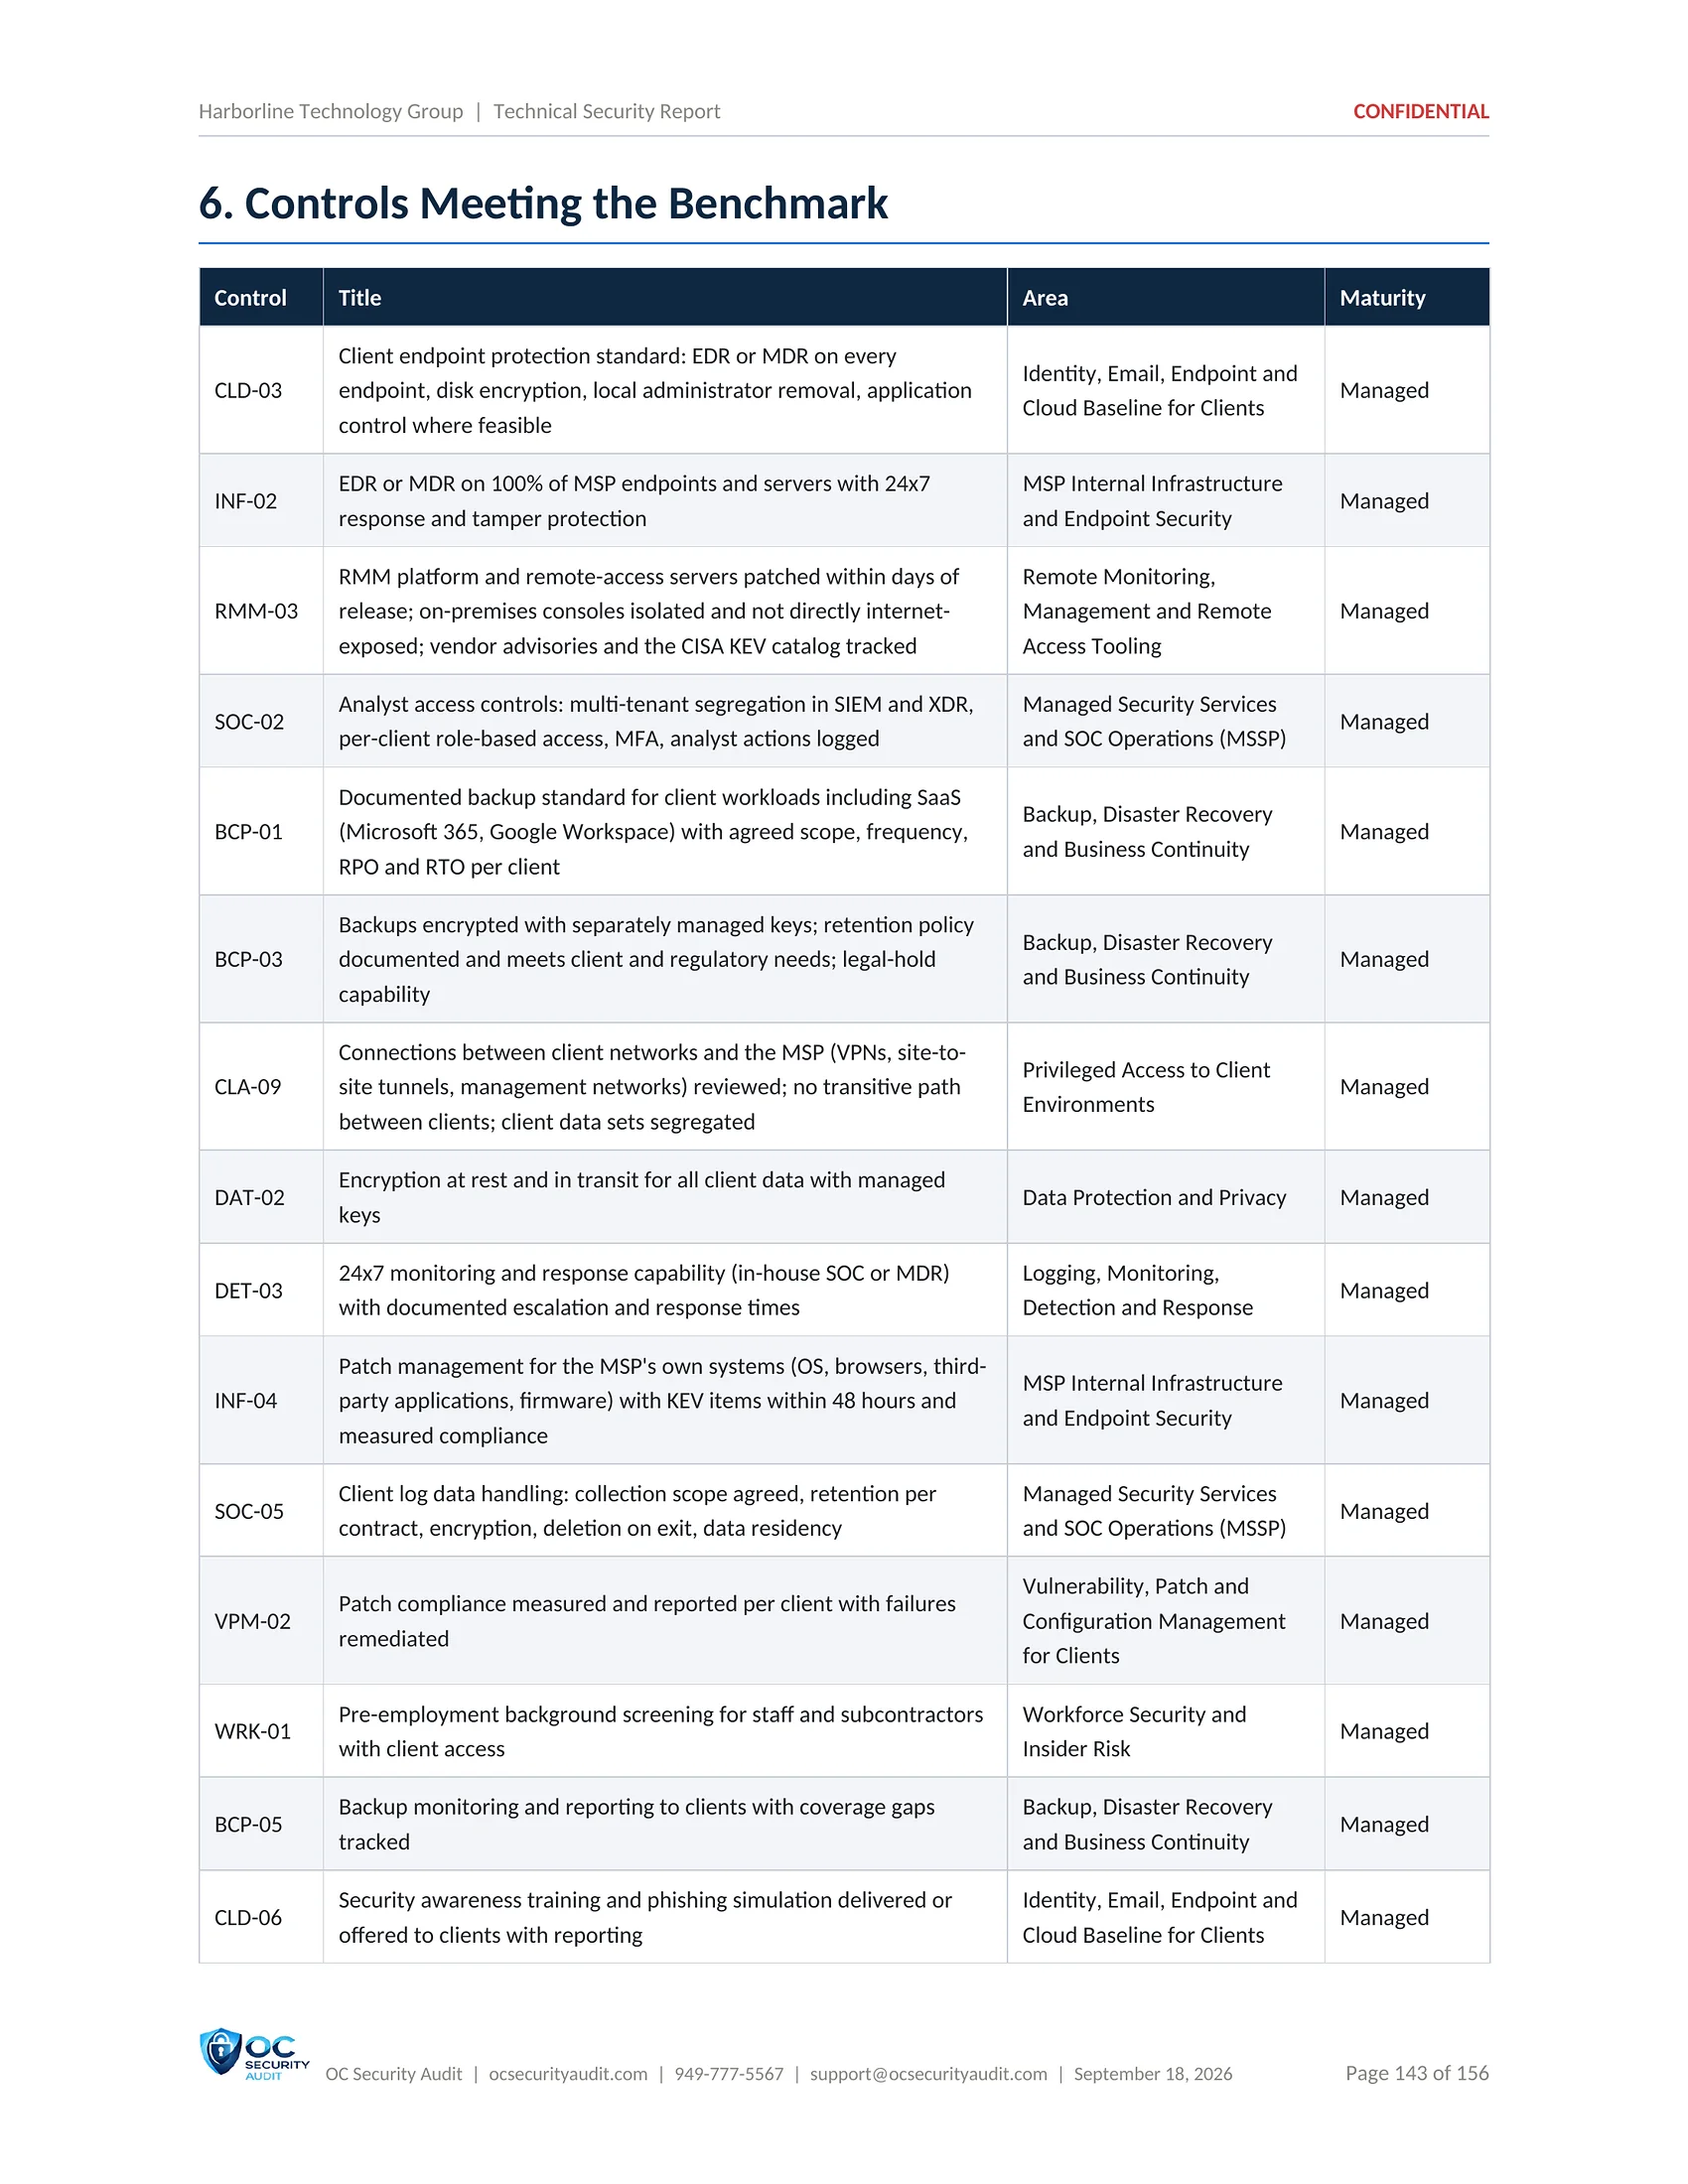
Click the centre page to open it full size and zoom in.
PDF and Word · 26 pages, landscape
Risk Register
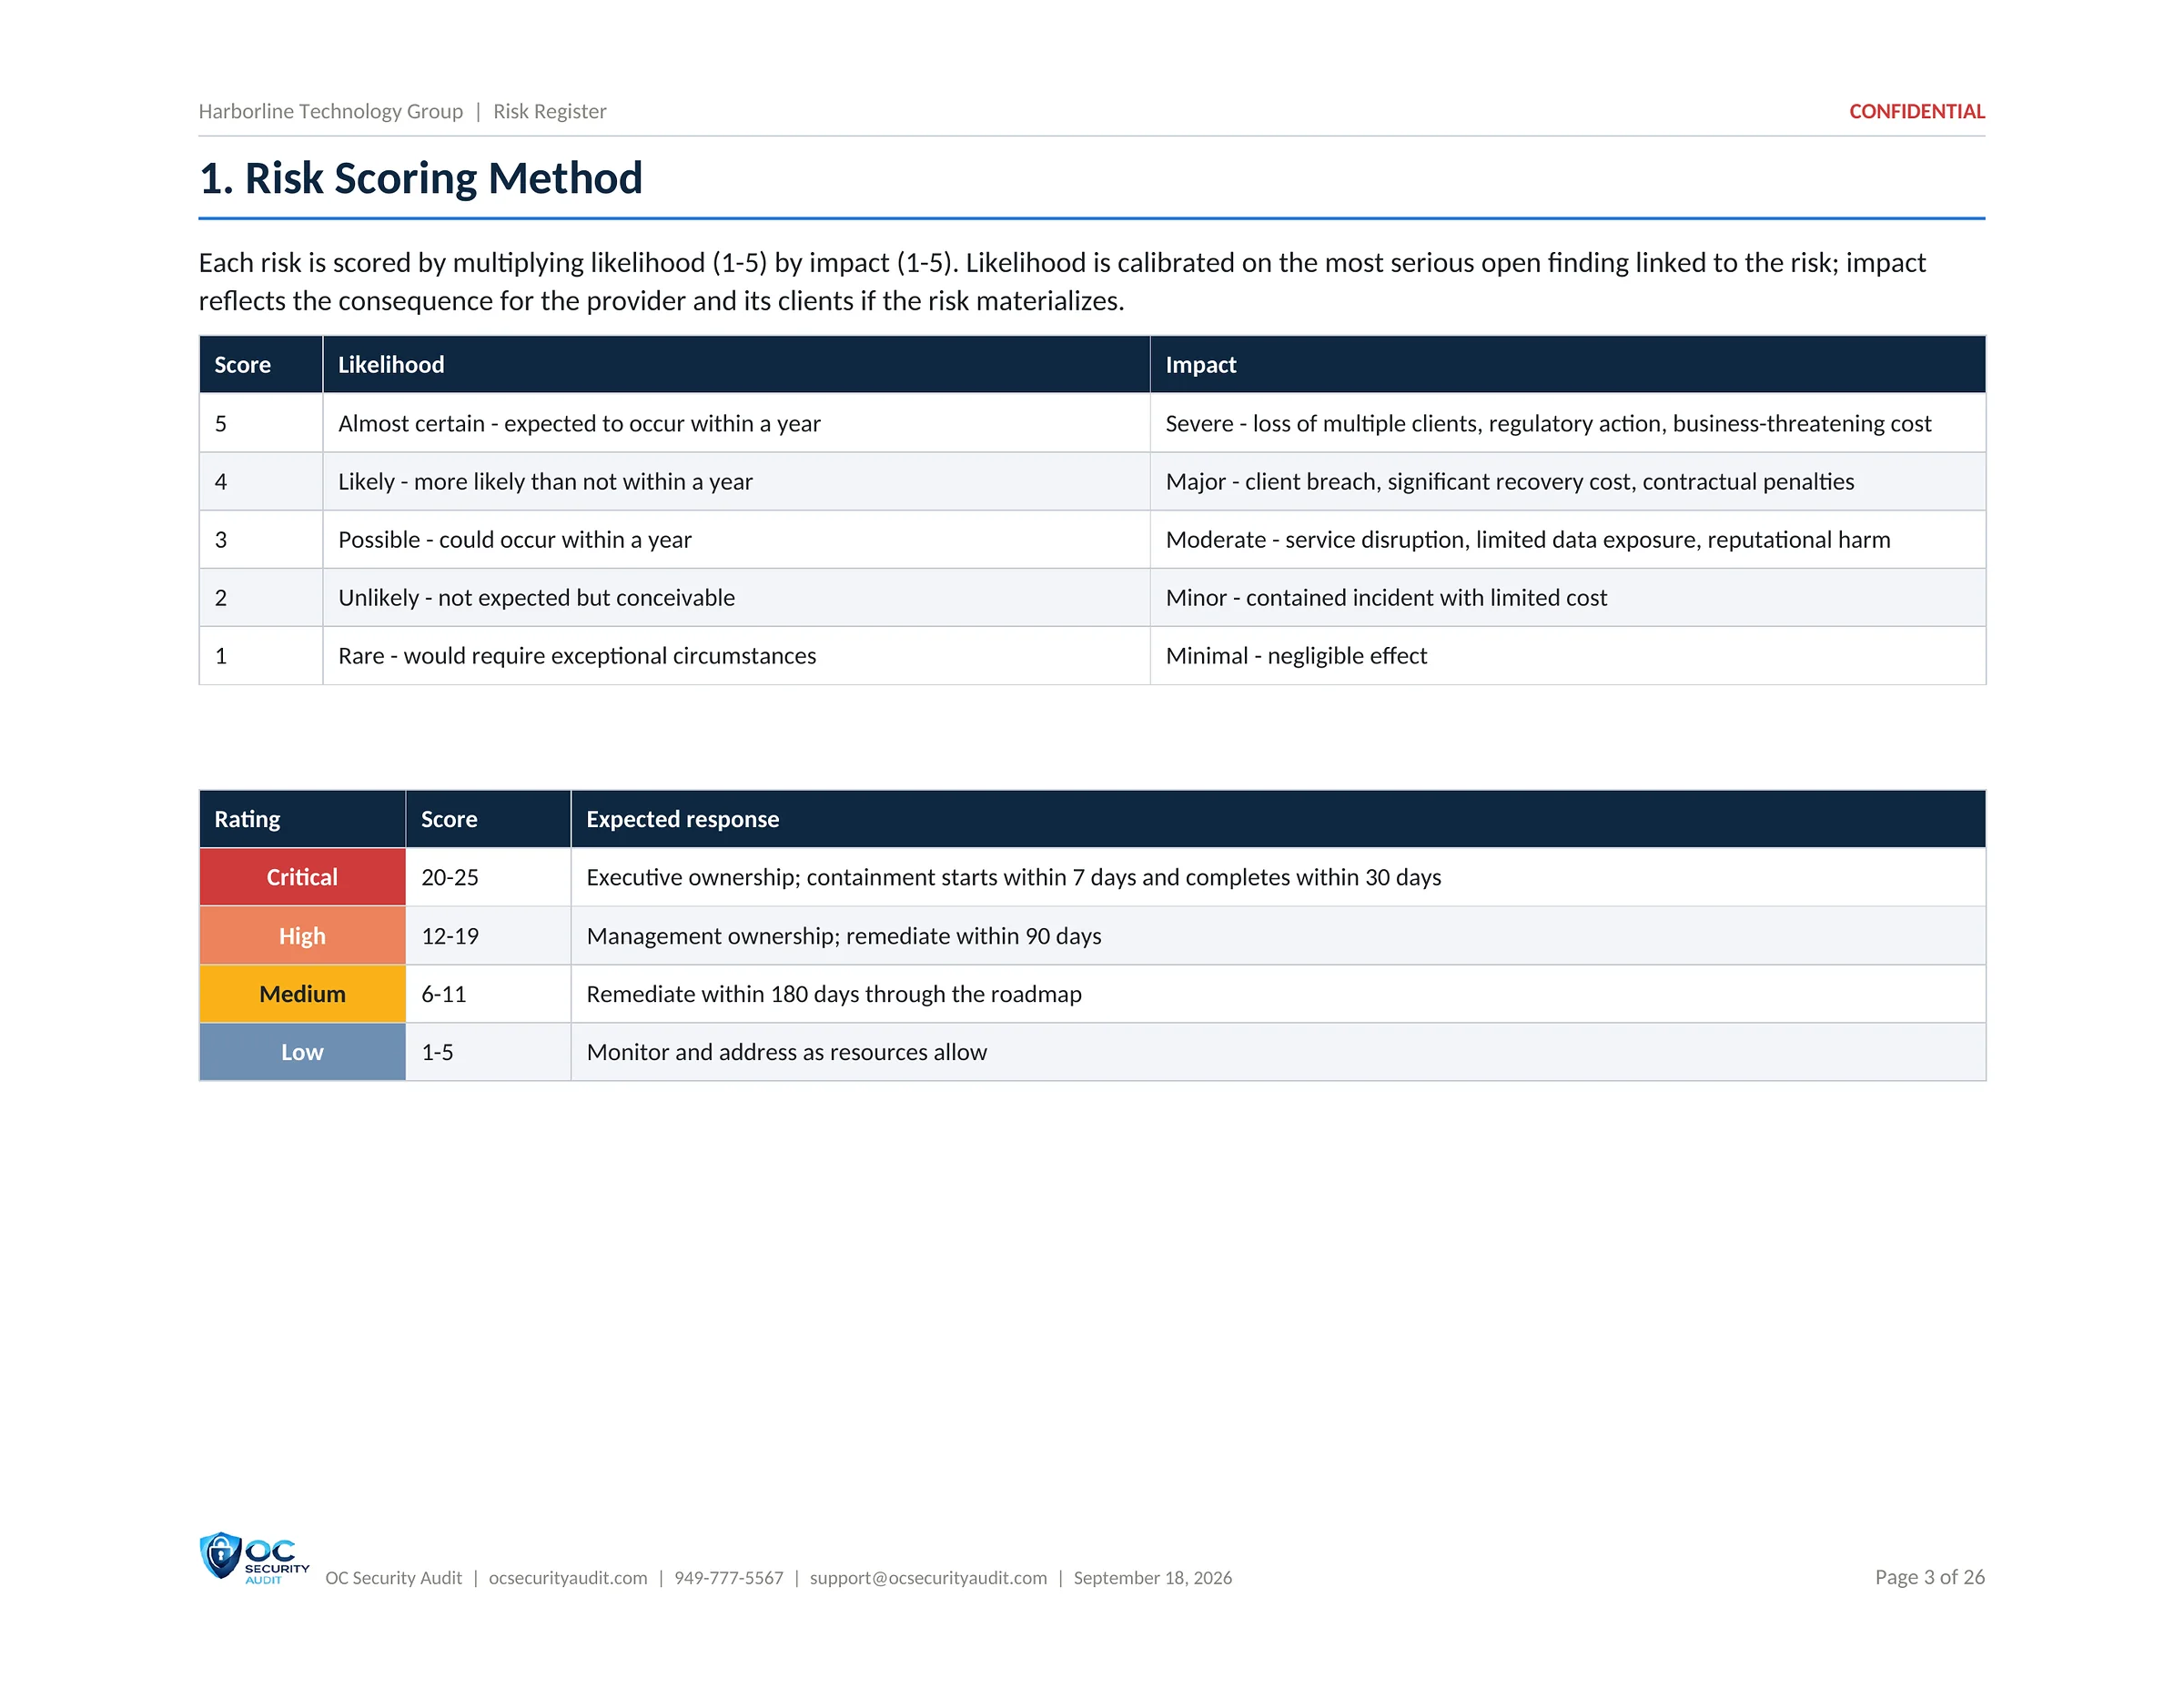
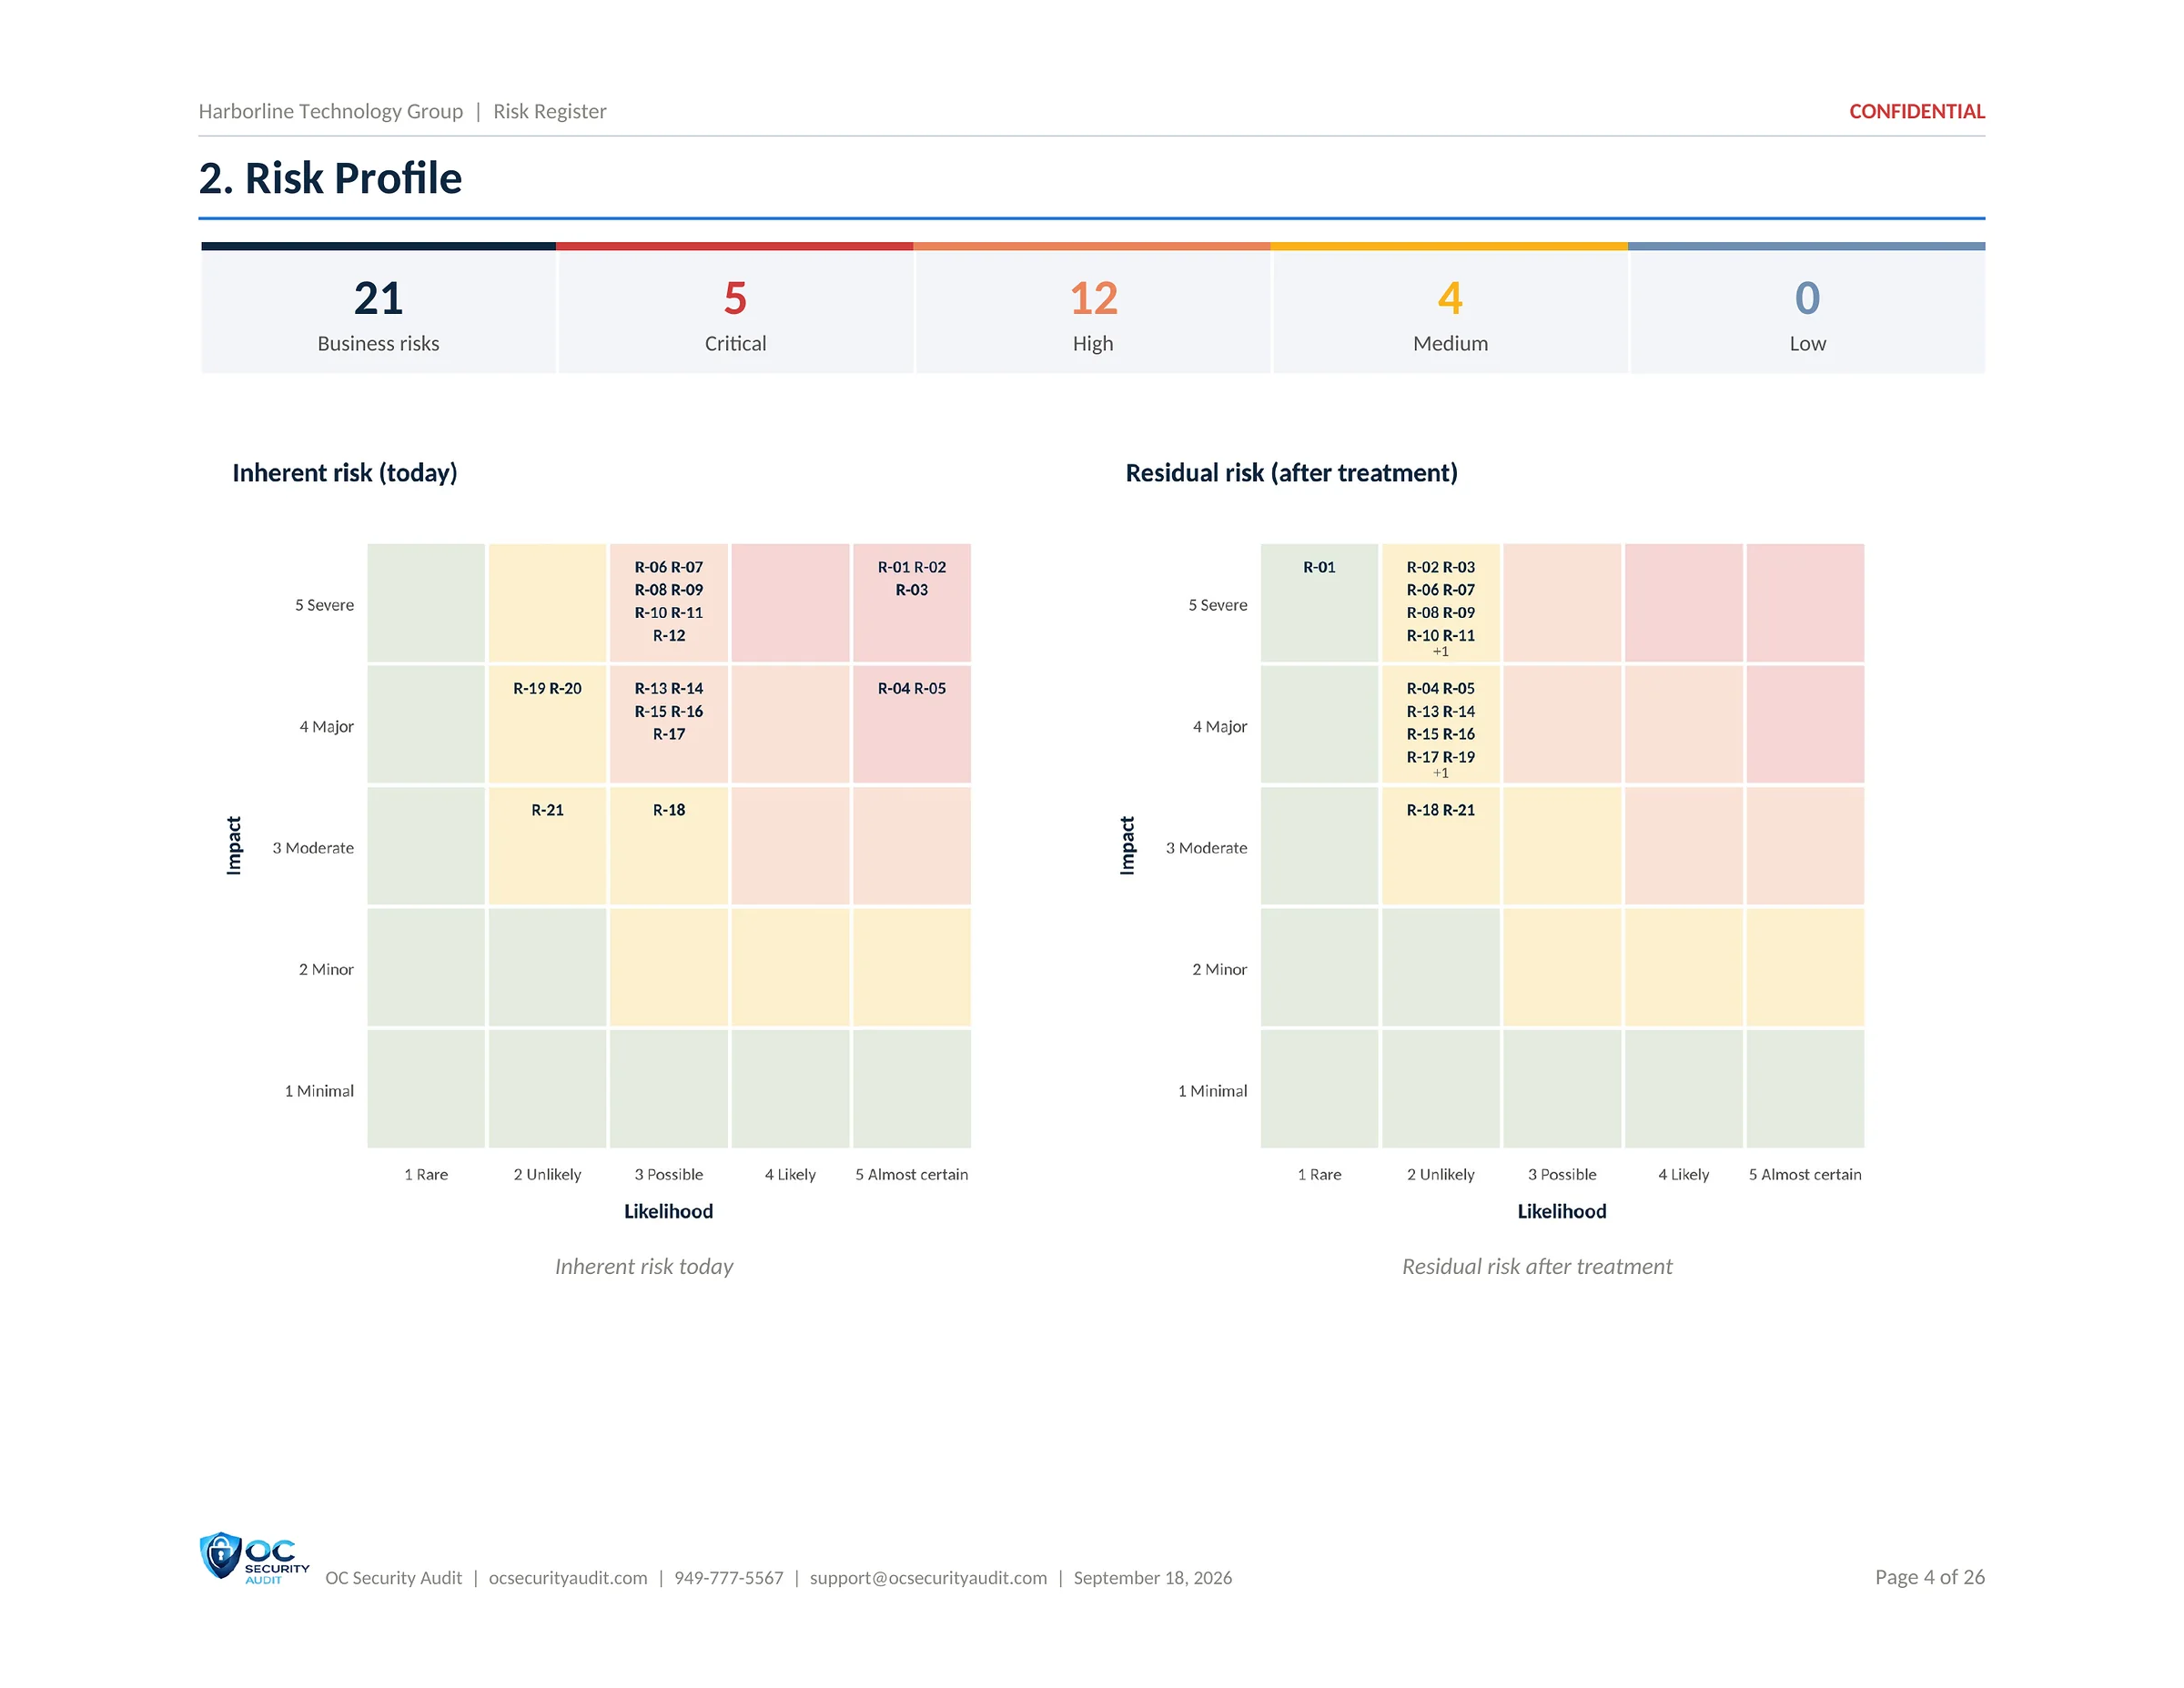
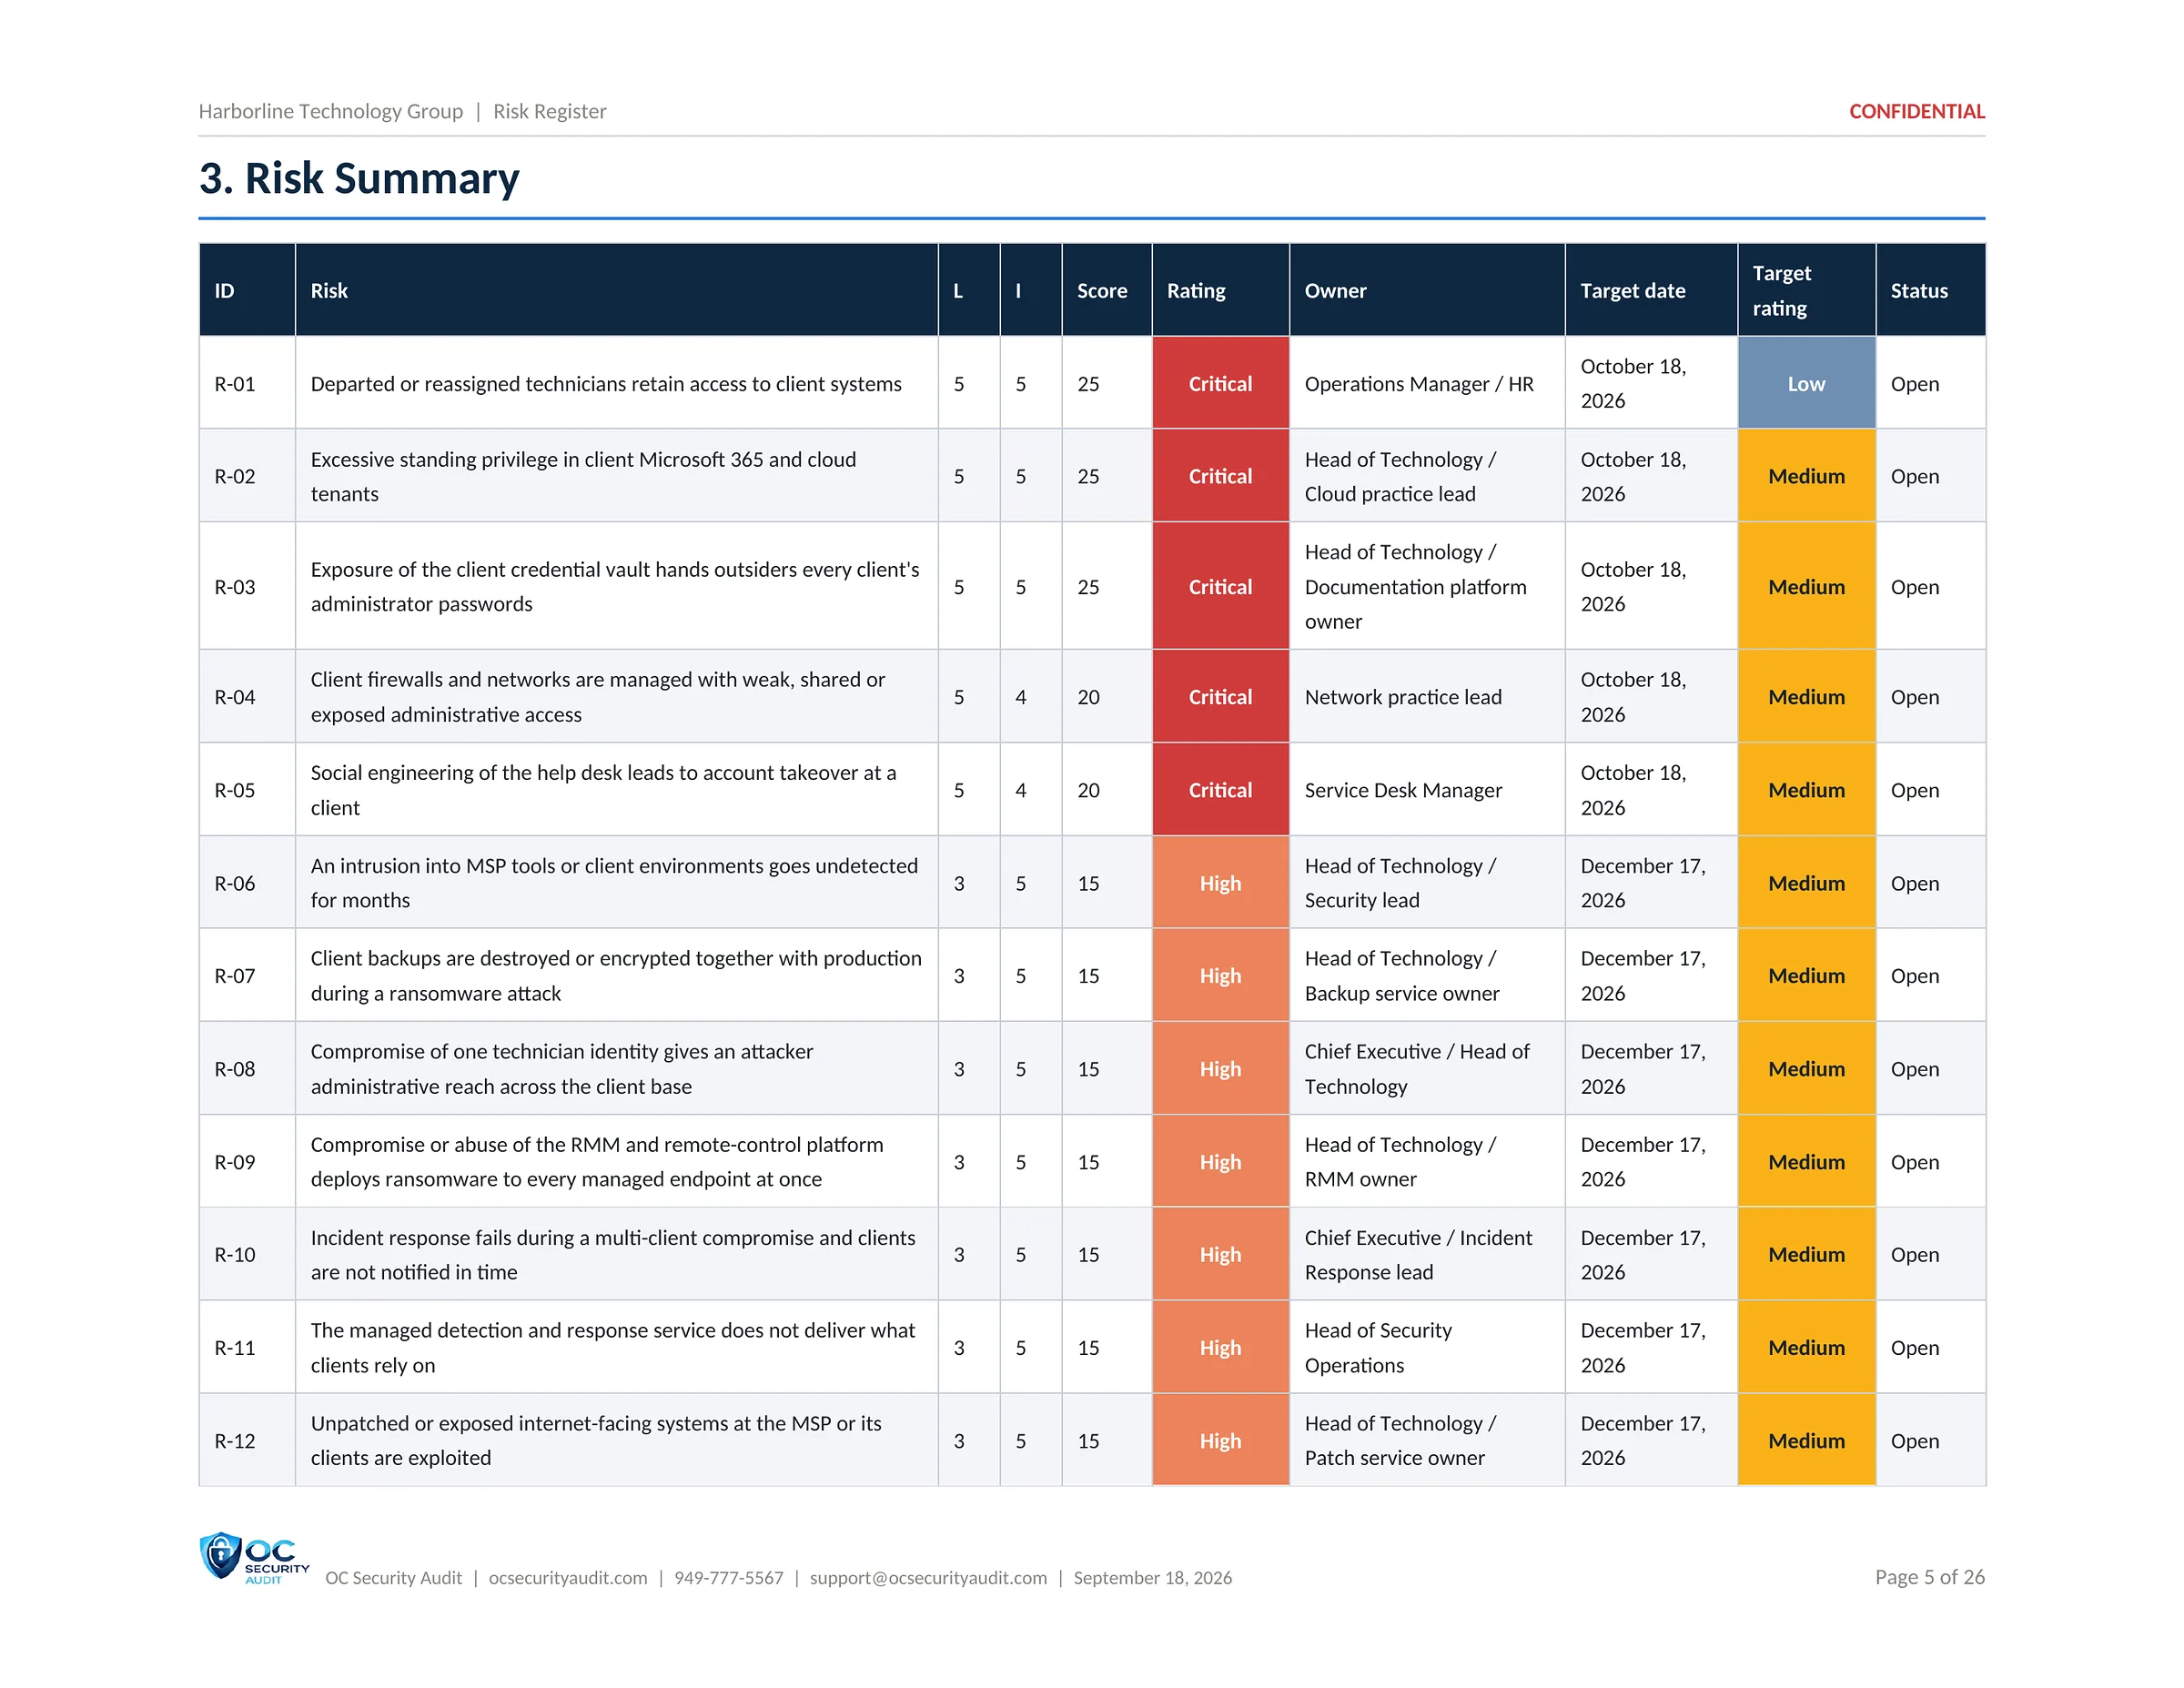
The register that turns findings into business risks a leadership team can own. Each risk has a likelihood, an impact, a score, a rating, an owner, a target date and a treatment plan, and every finding is traced to the risk it feeds.
Leadership and risk owners; also useful for insurers, auditors and enterprise clients.
What is included
- Risk scoring method
- Risk profile and heat maps
- Risk summary with owners and dates
- Current versus residual risk
- A detail page for each risk
- Finding-to-risk traceability
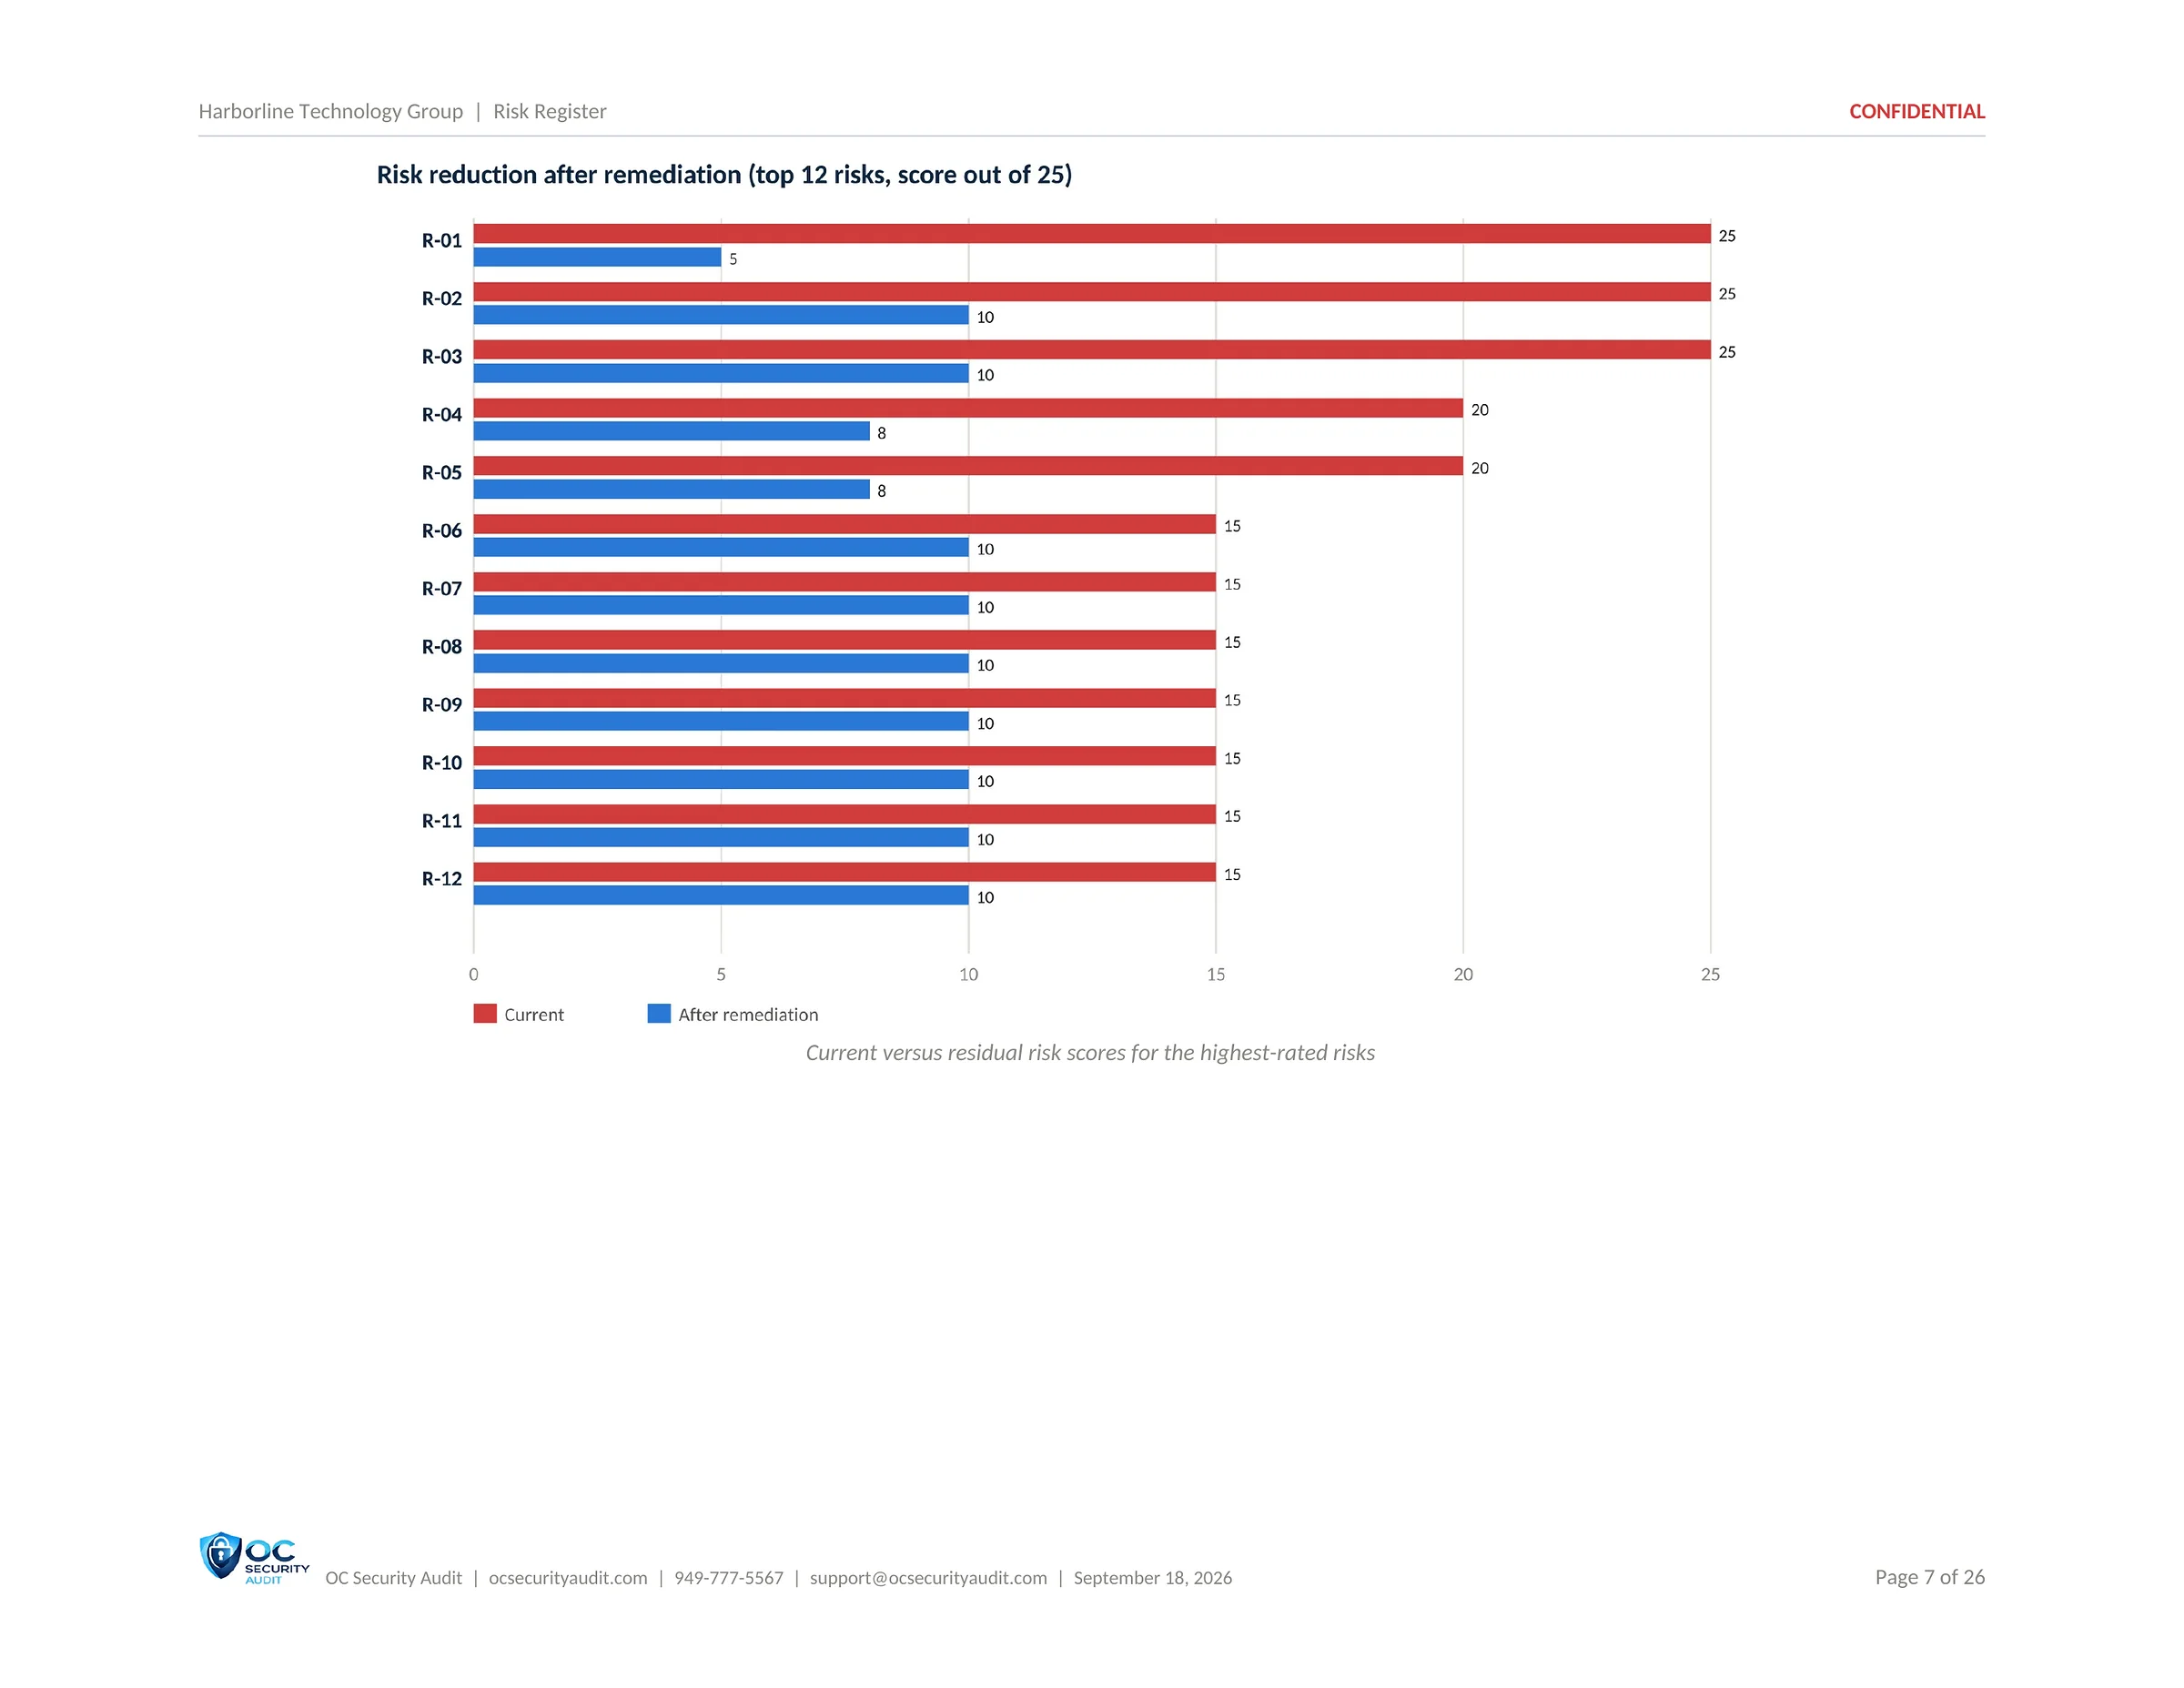
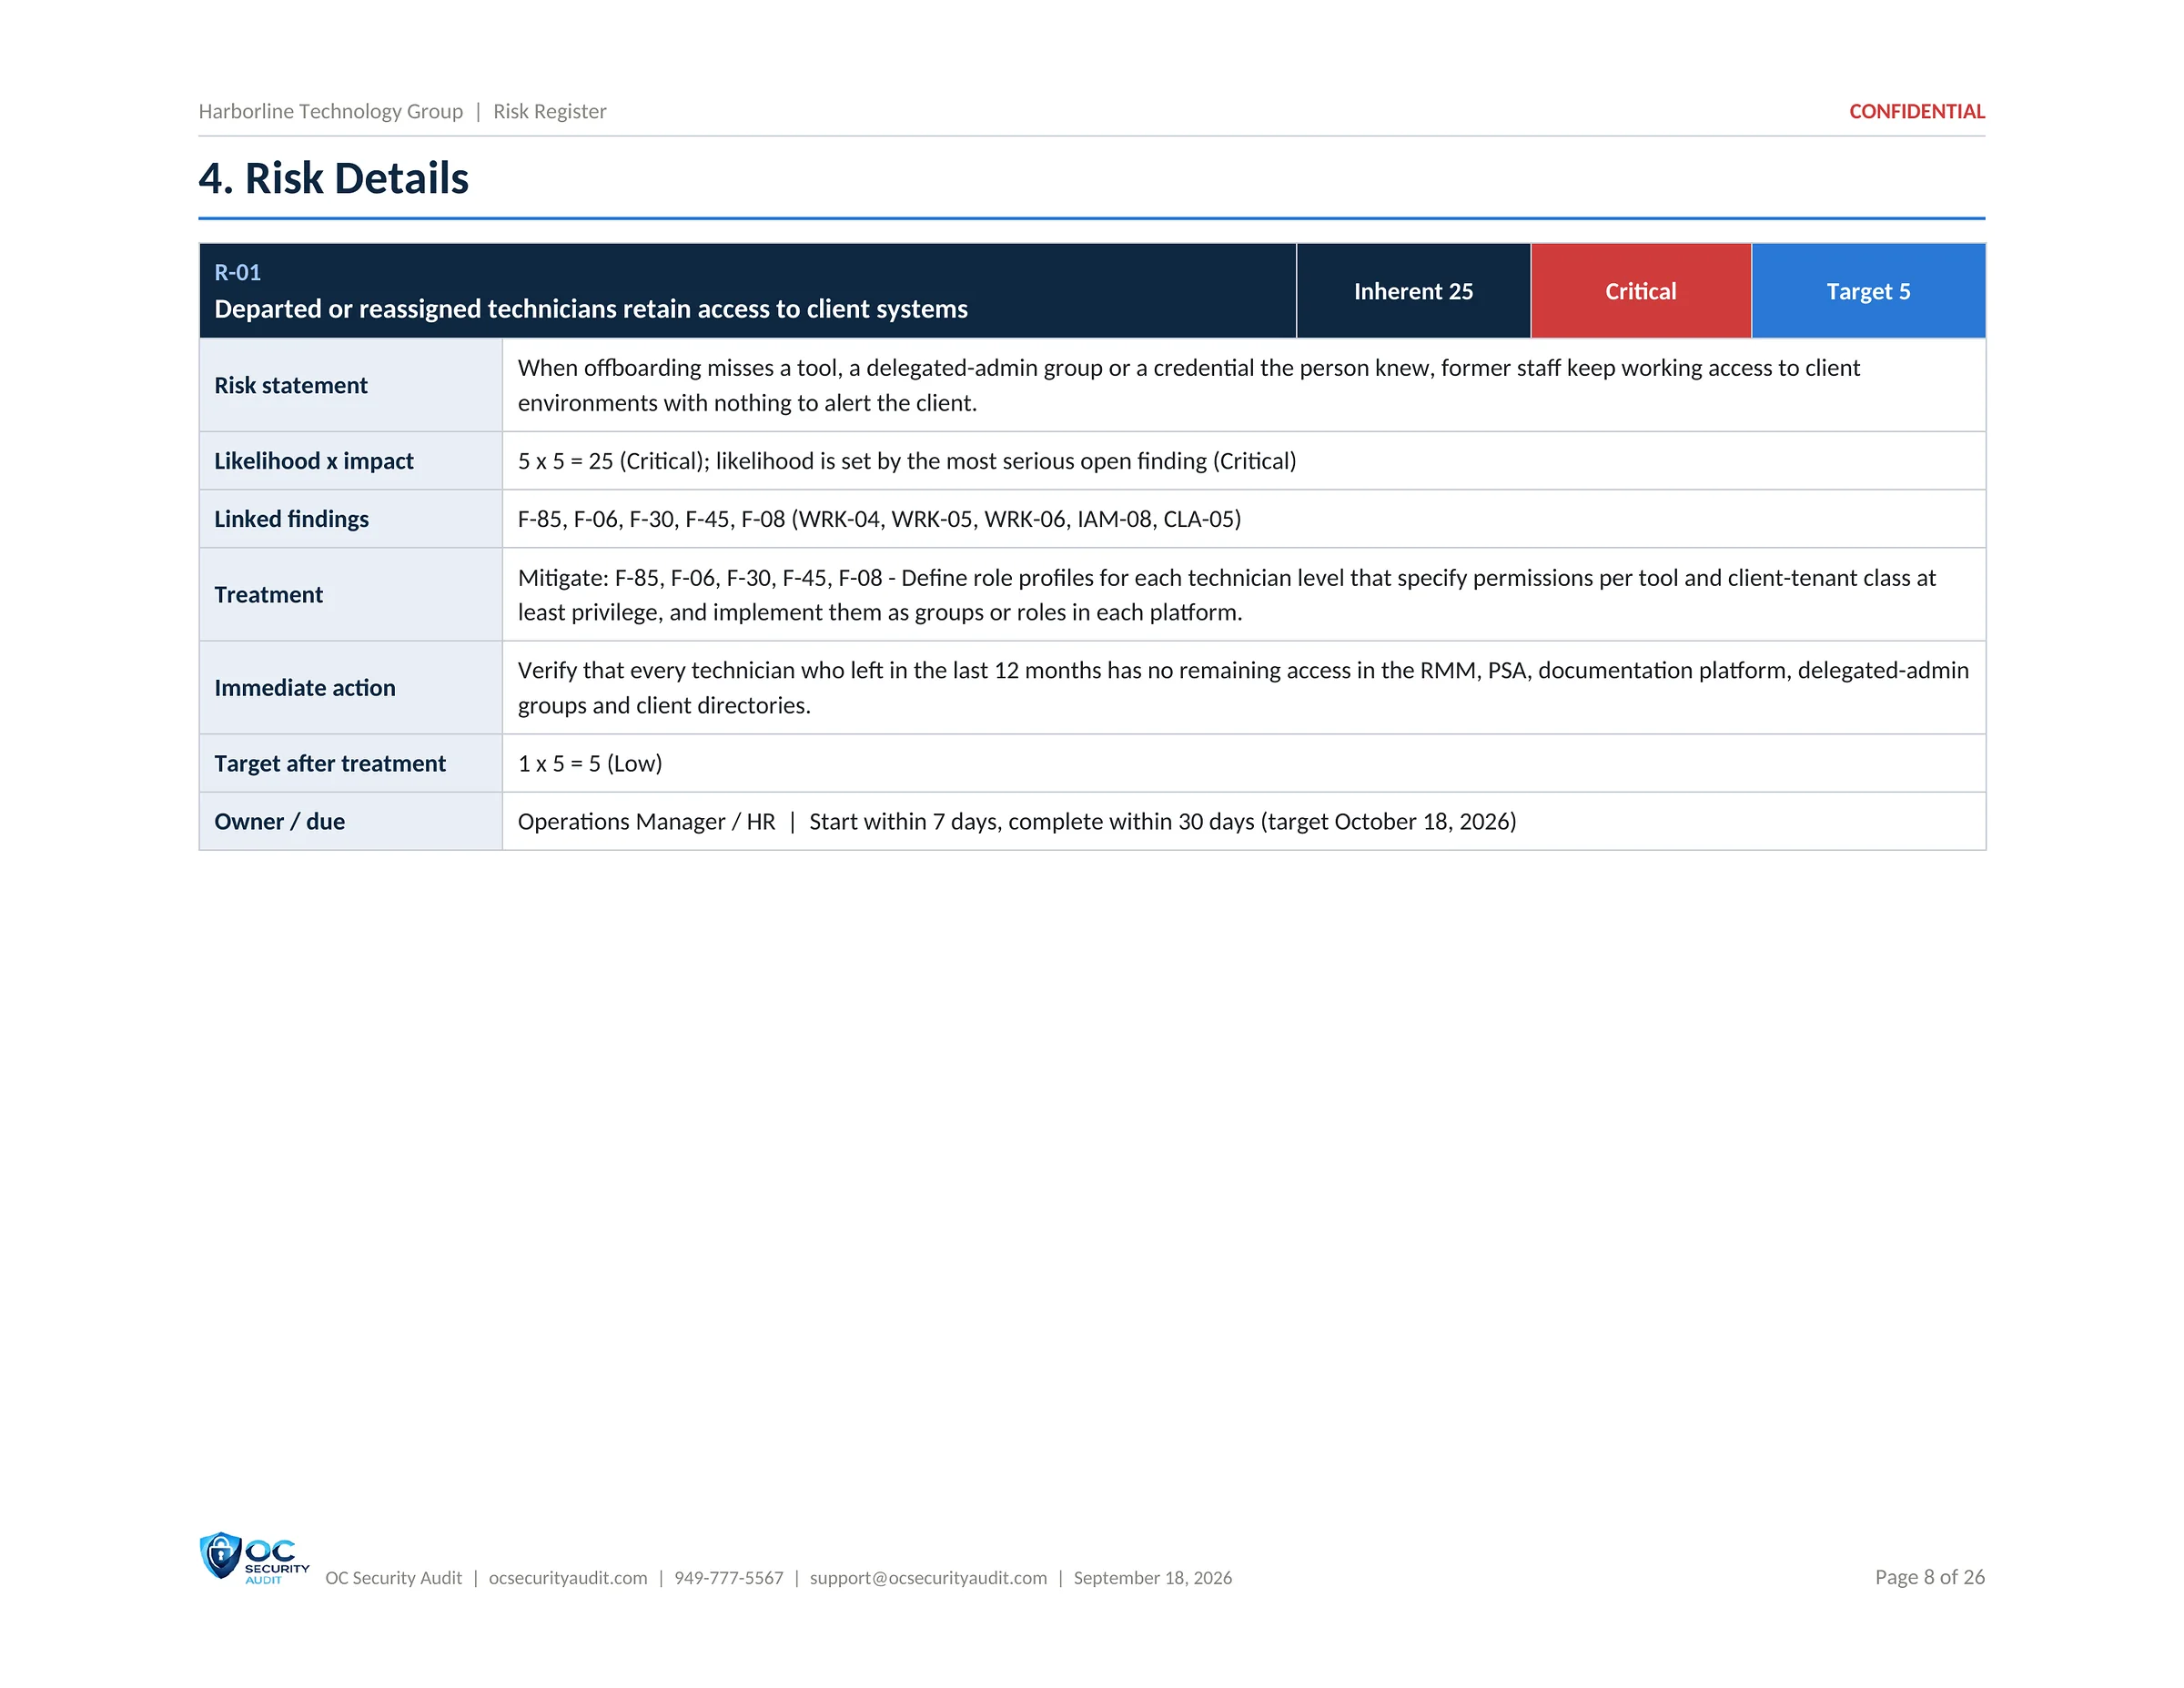
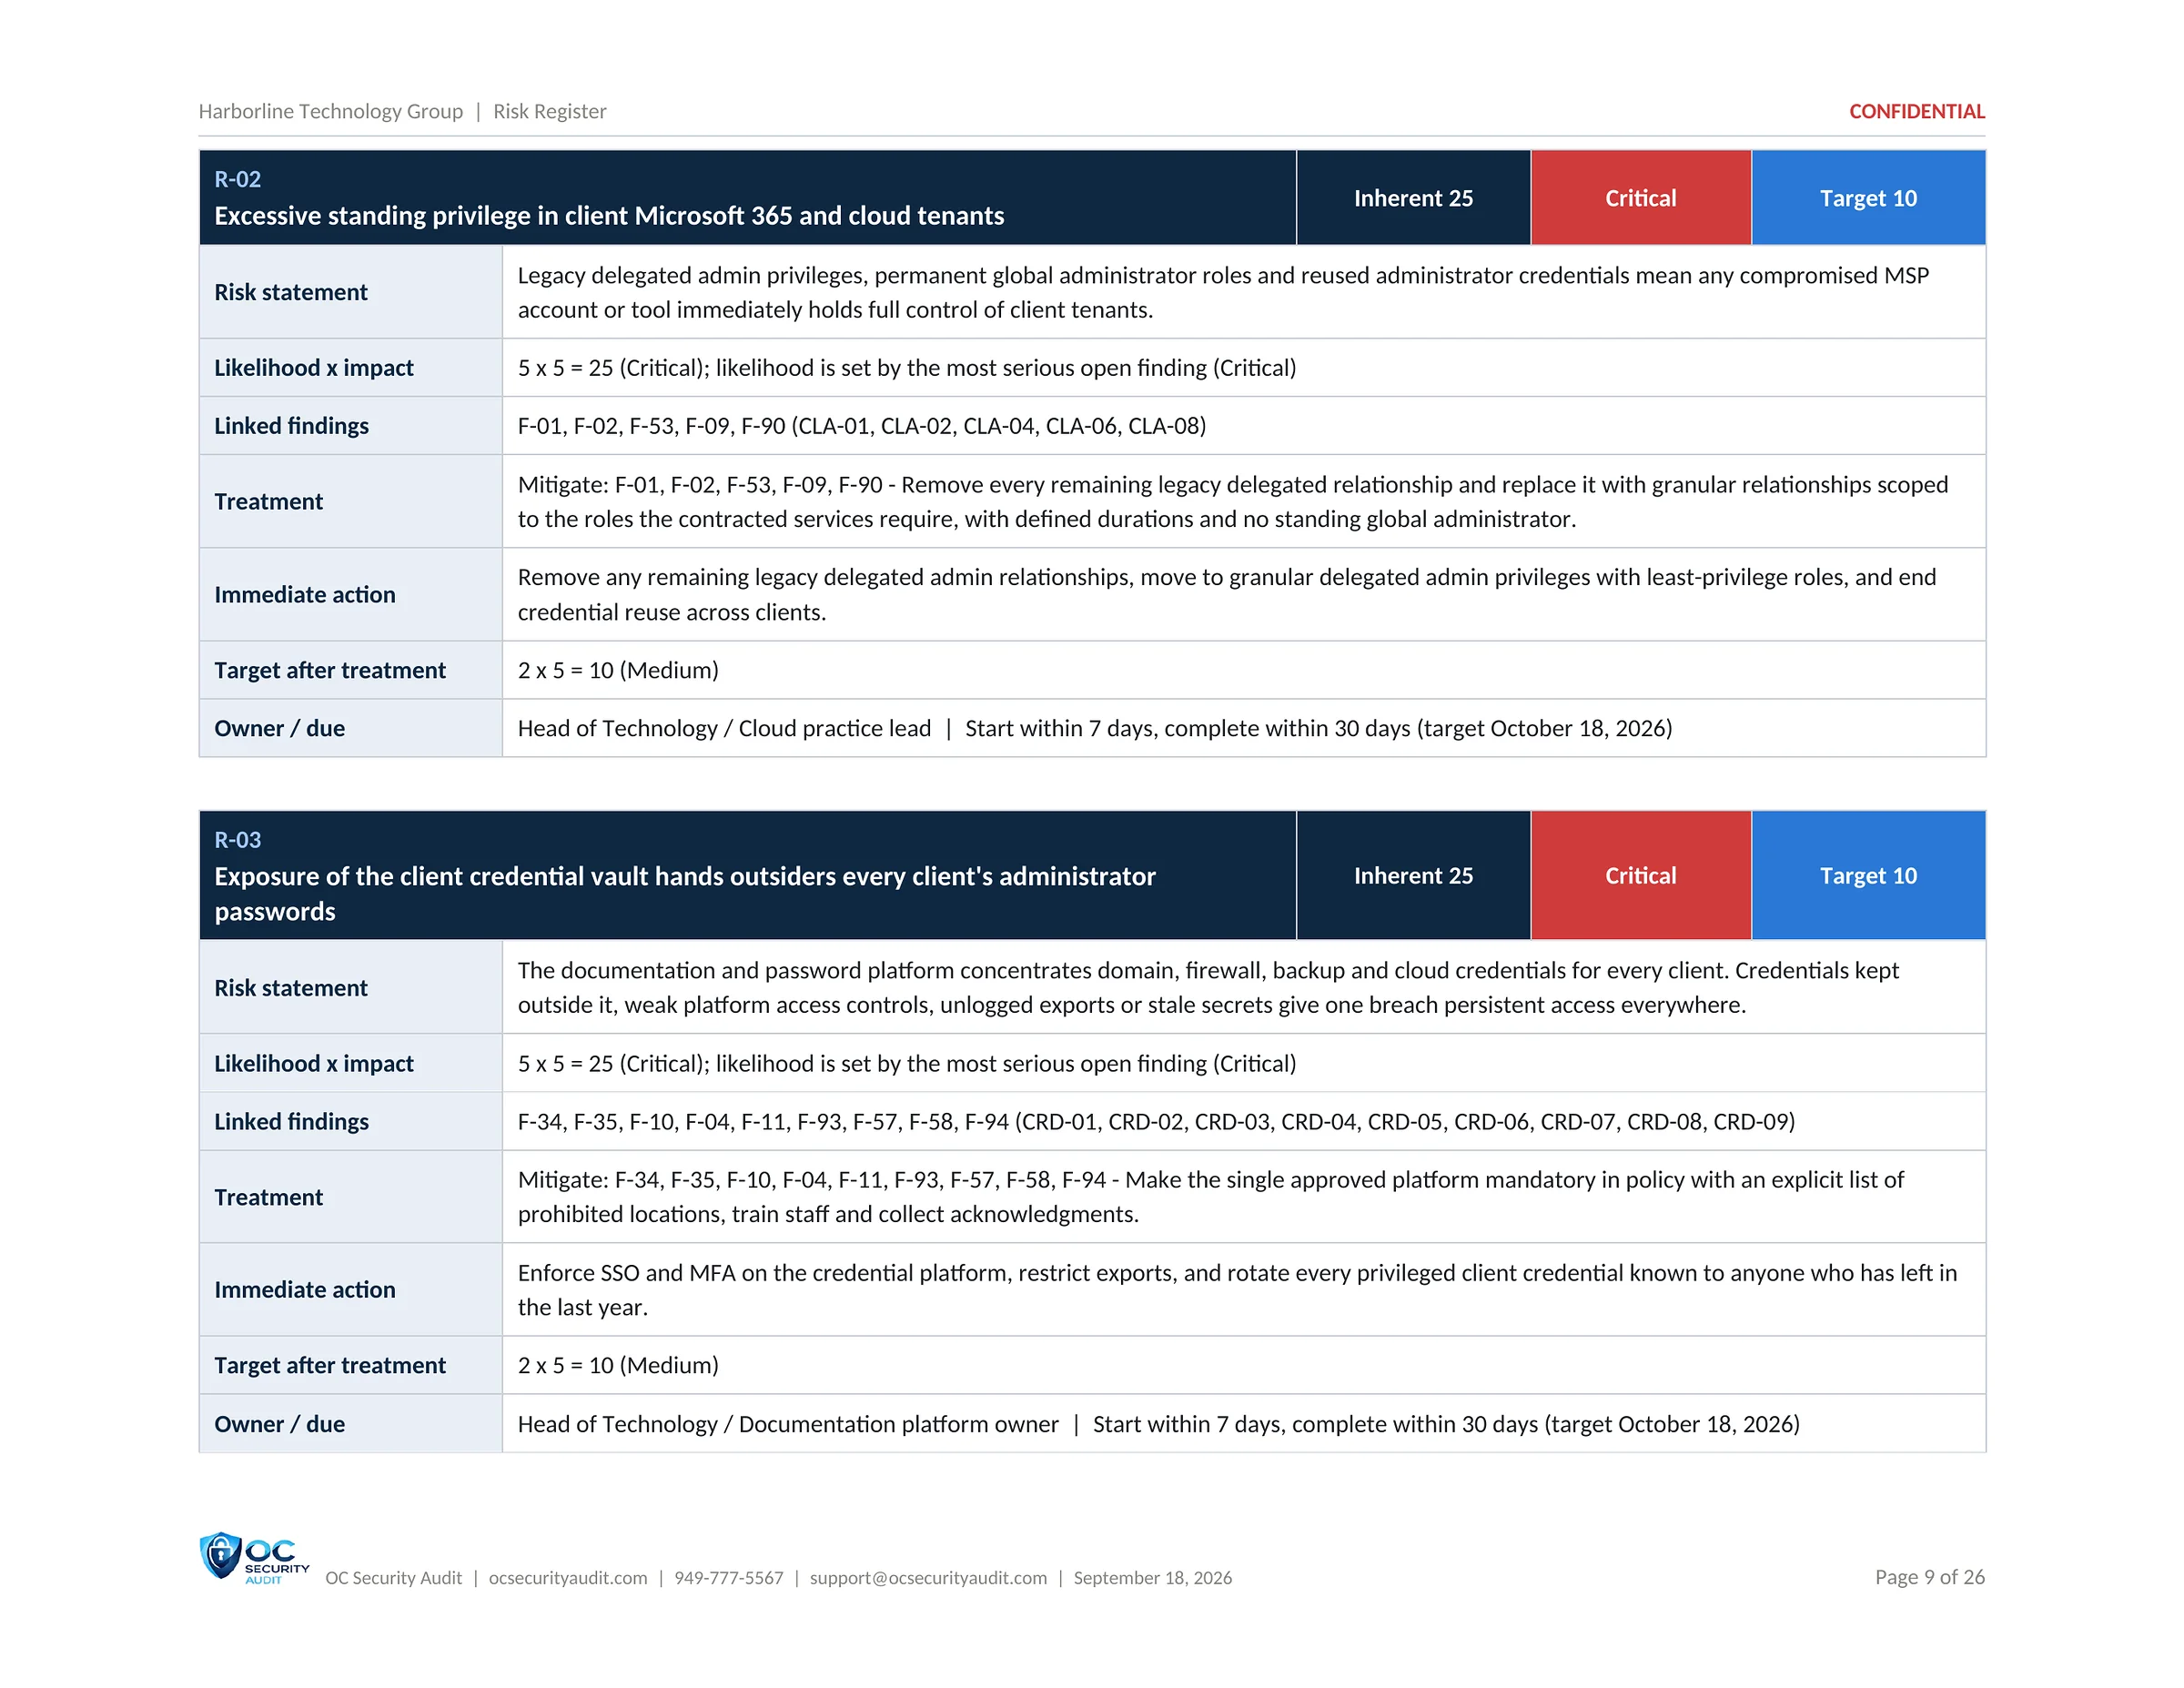
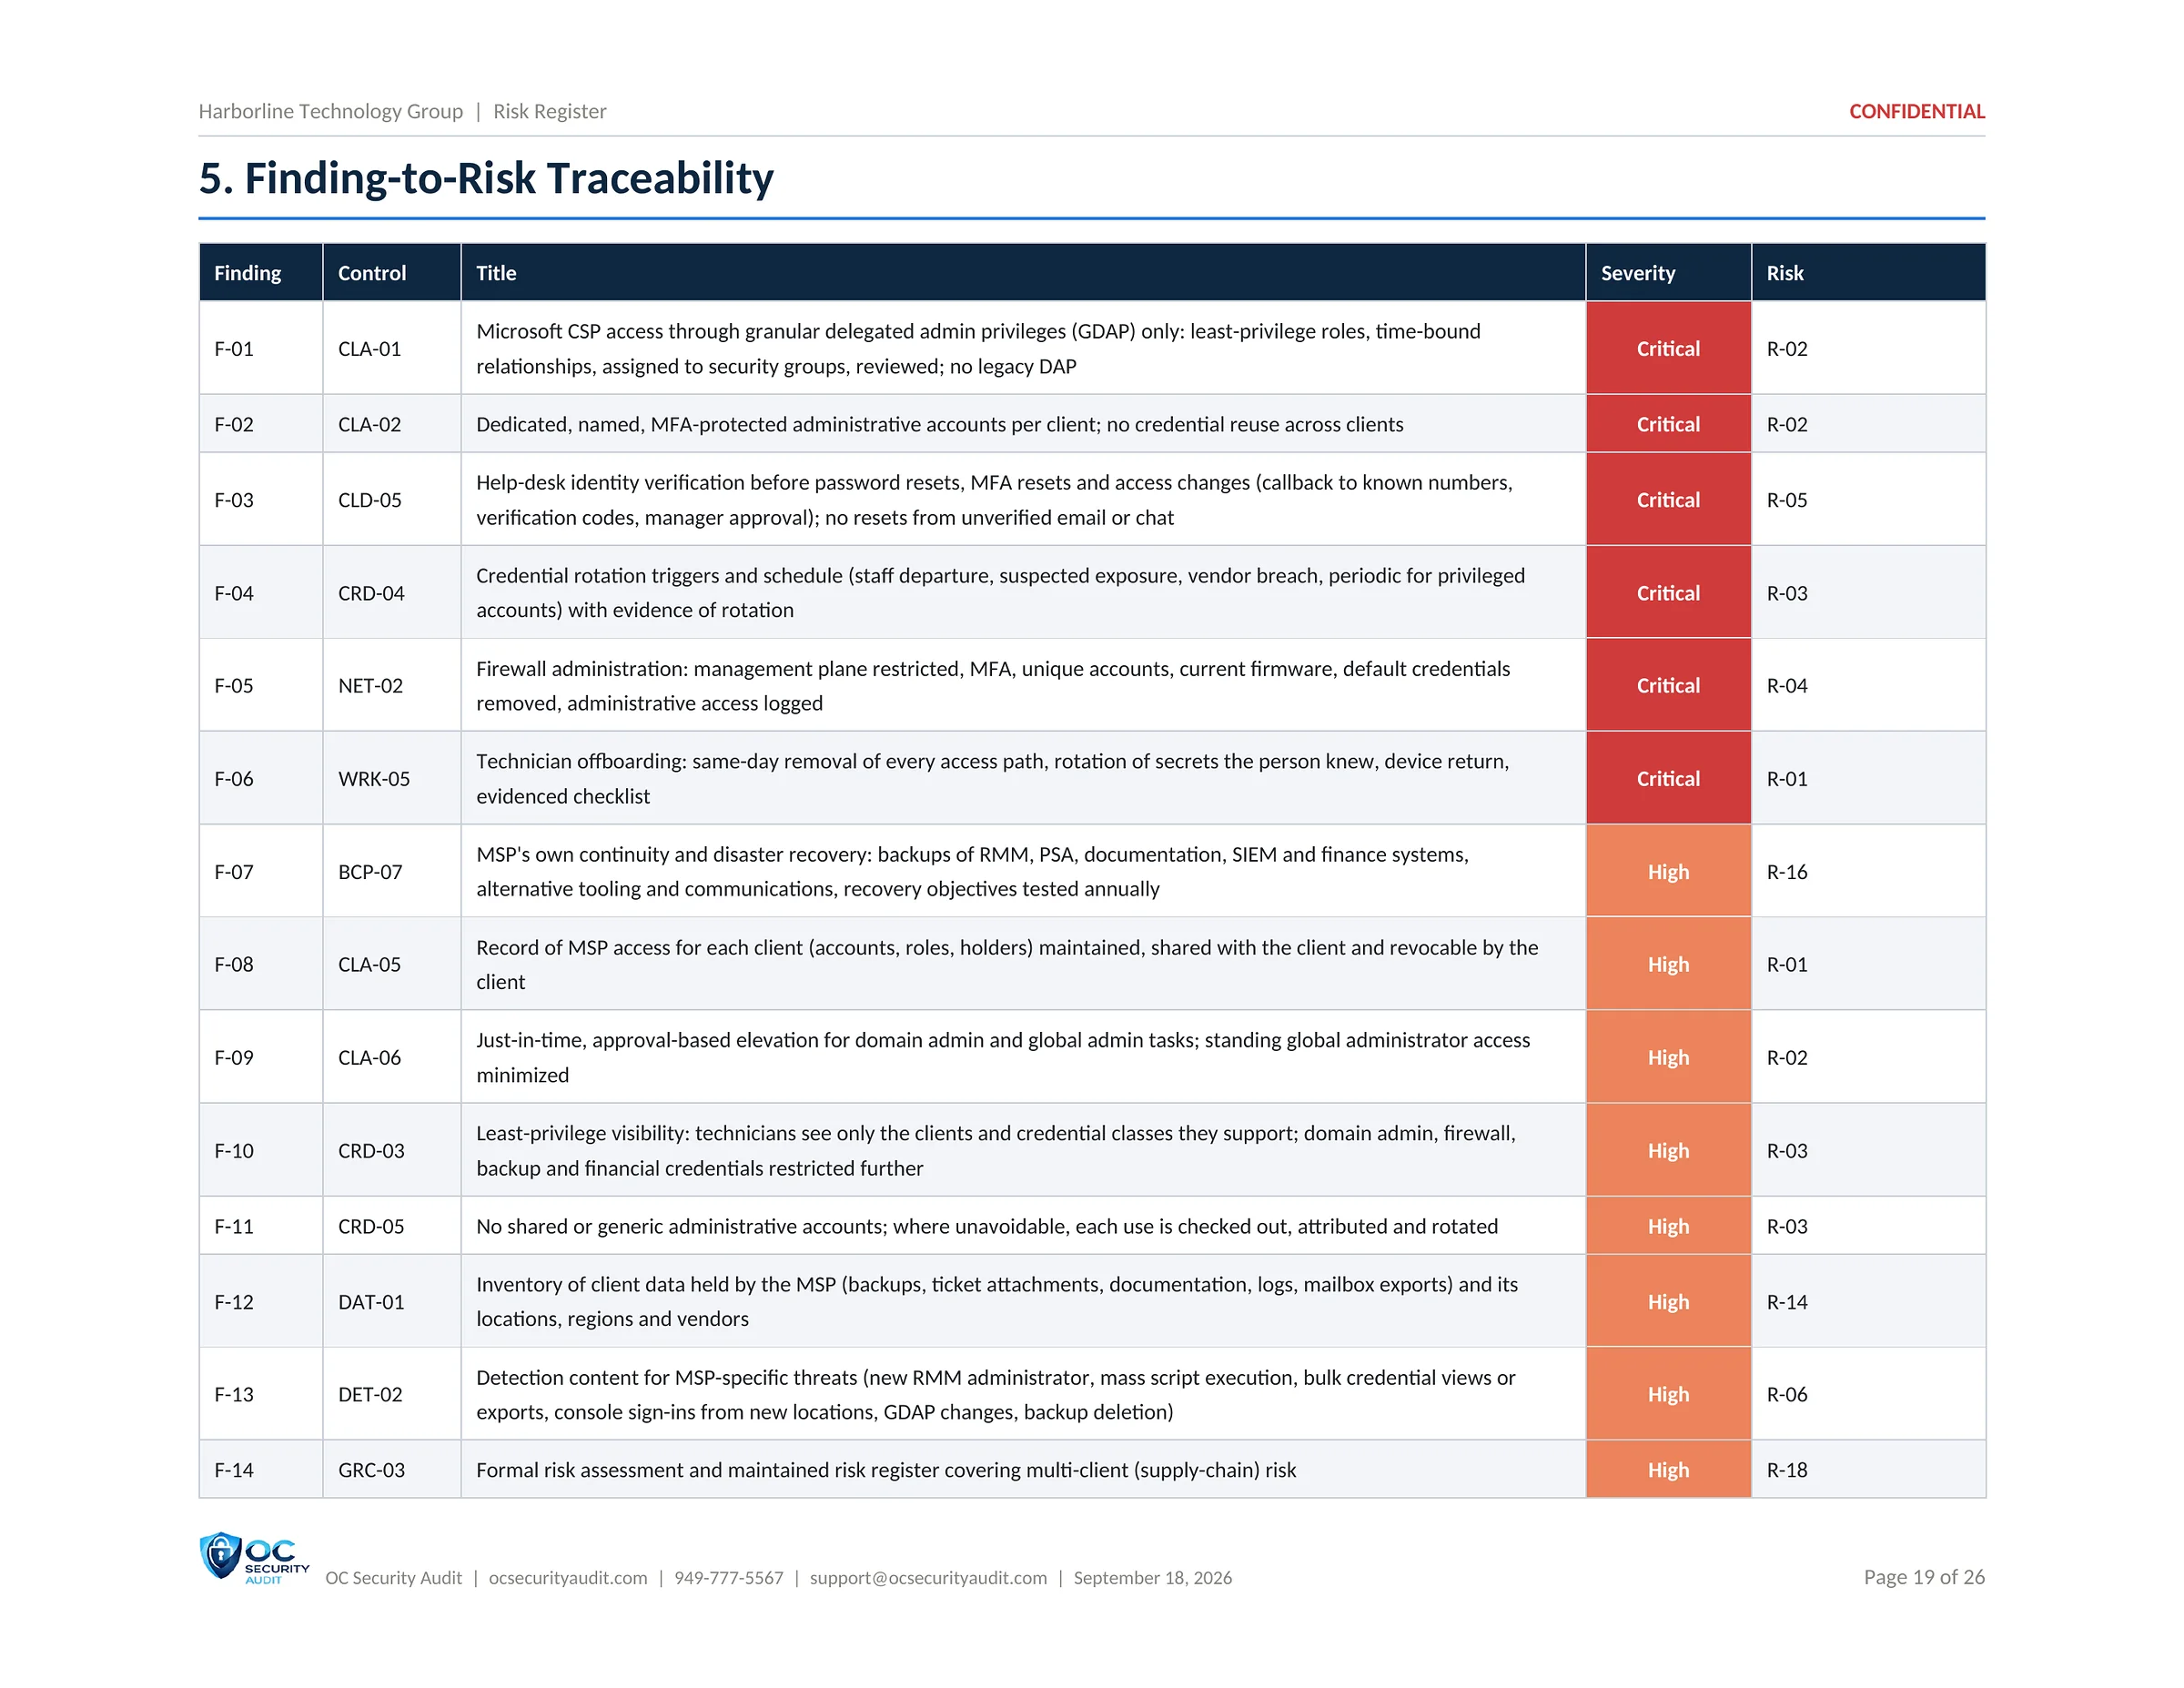
Click the centre page to open it full size and zoom in.
PDF and Word · 22 pages
Next Steps and Security Roadmap
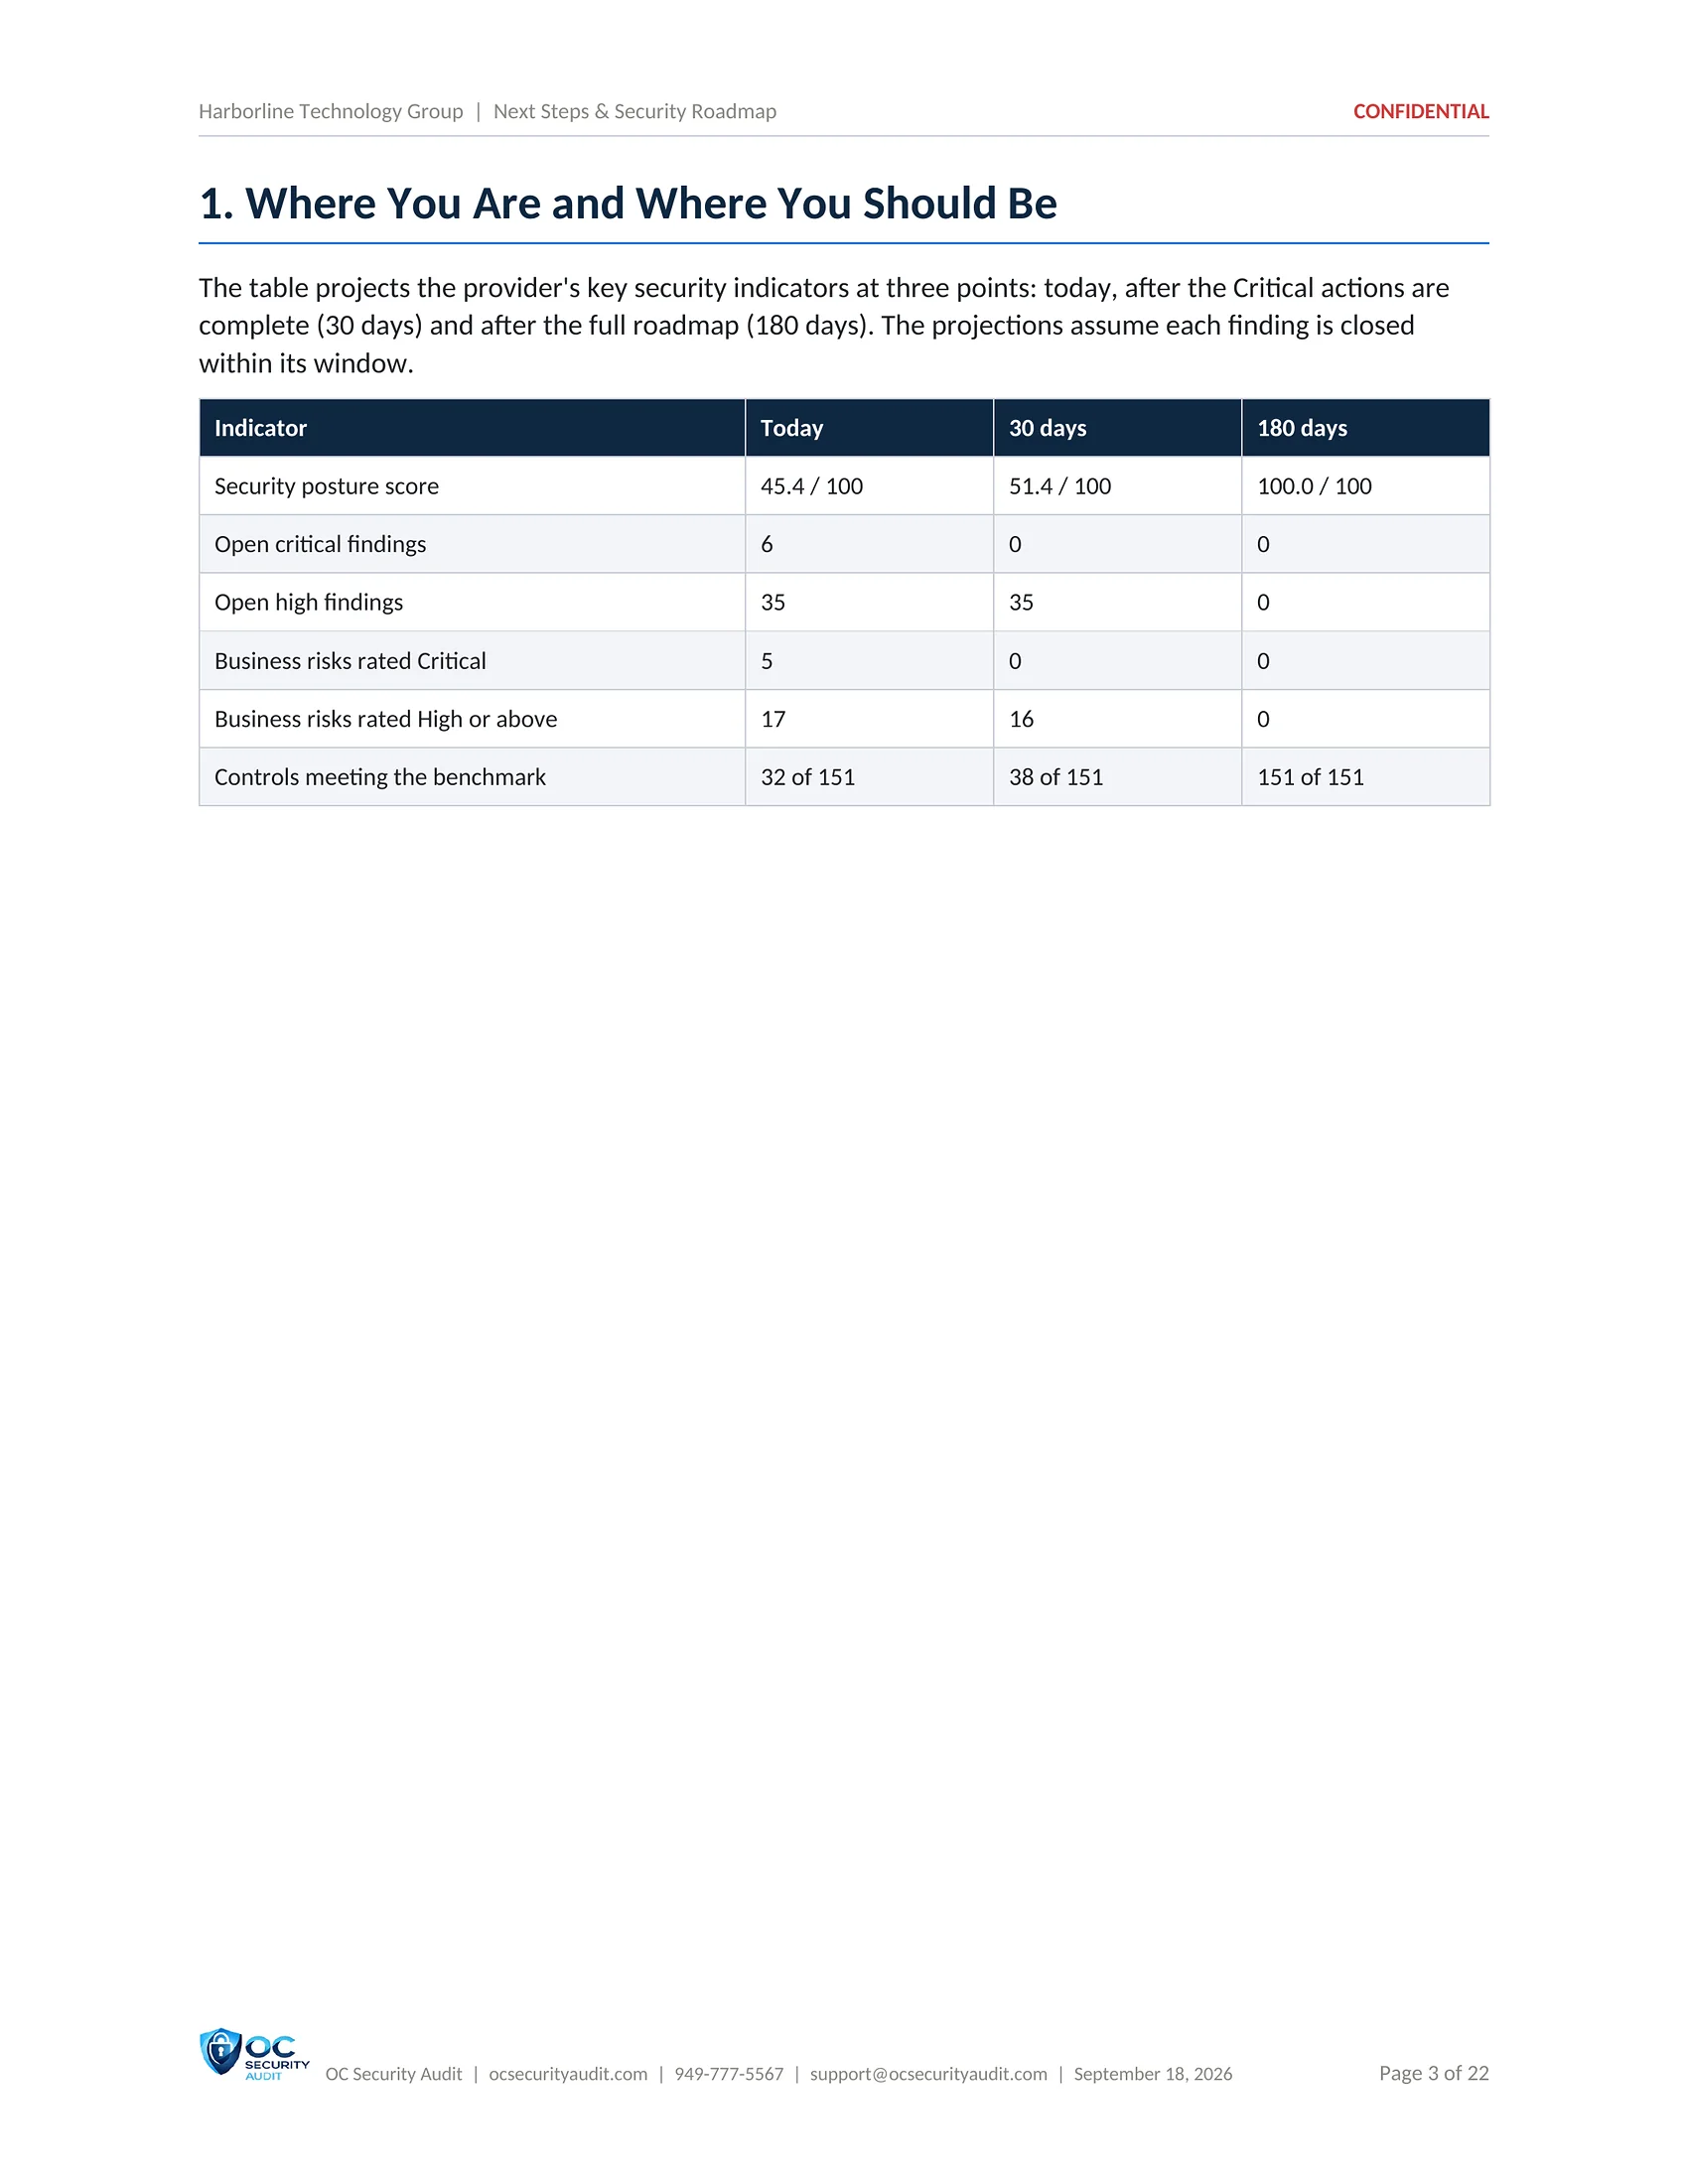
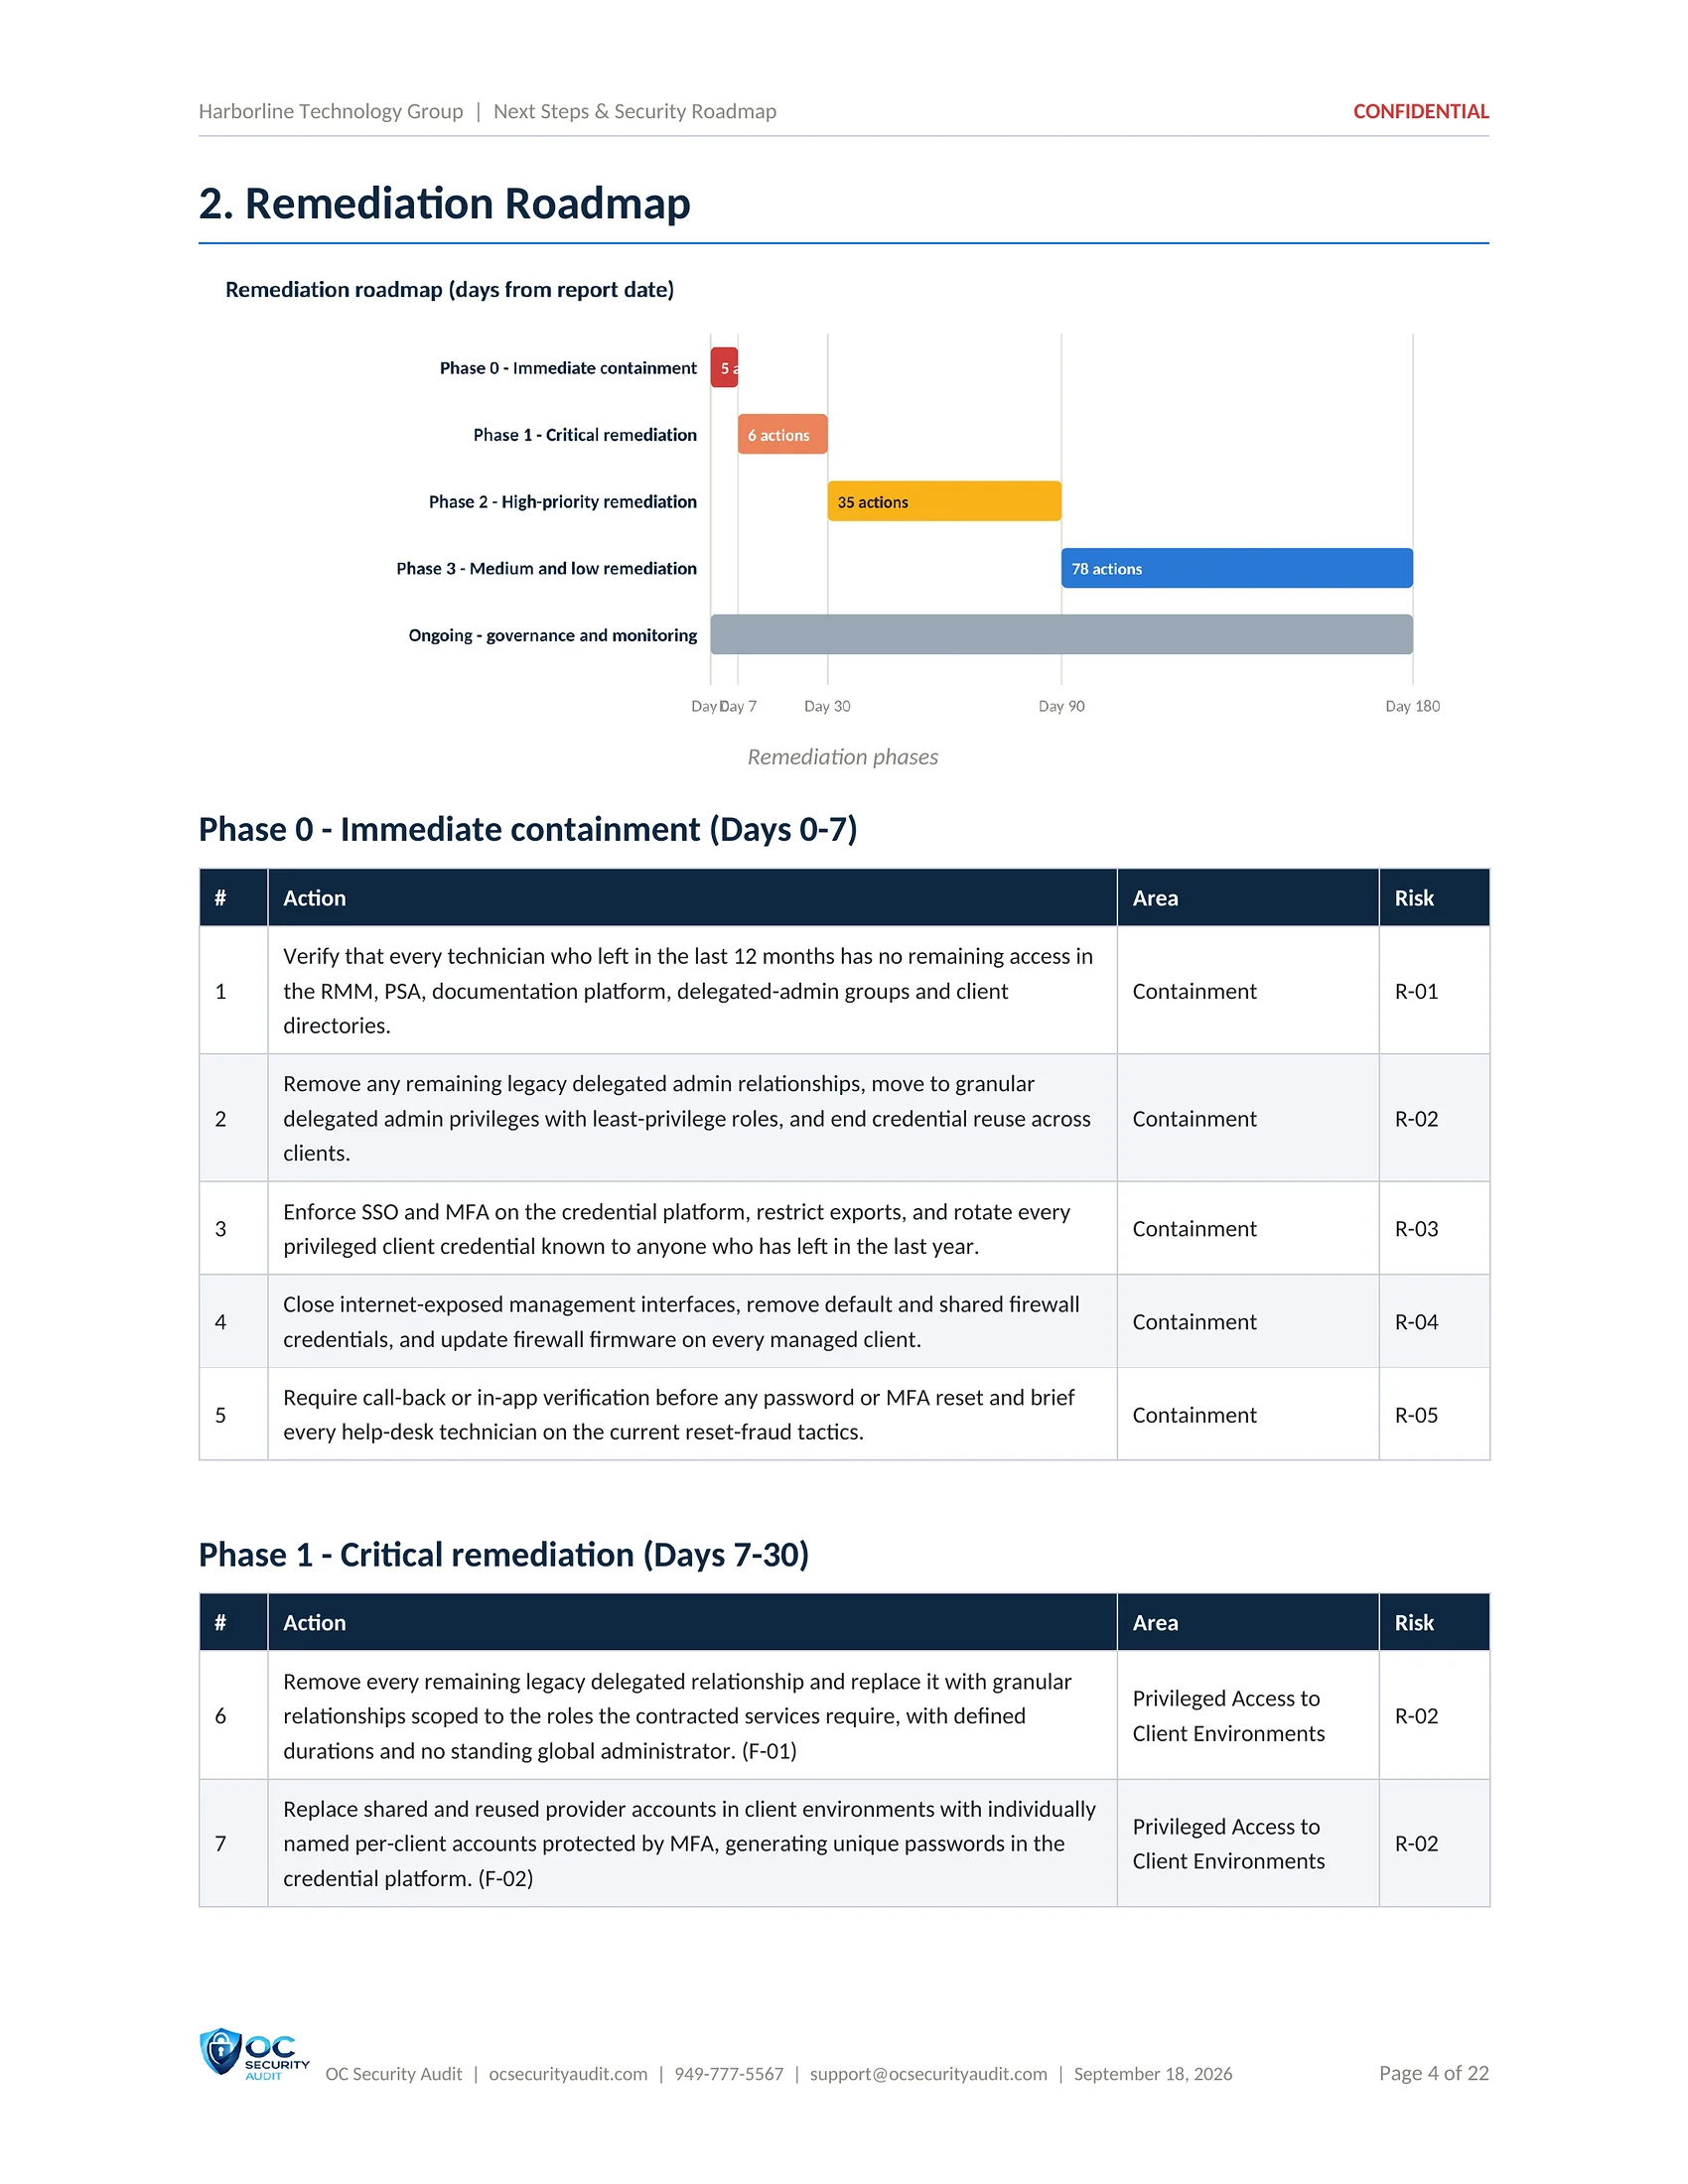
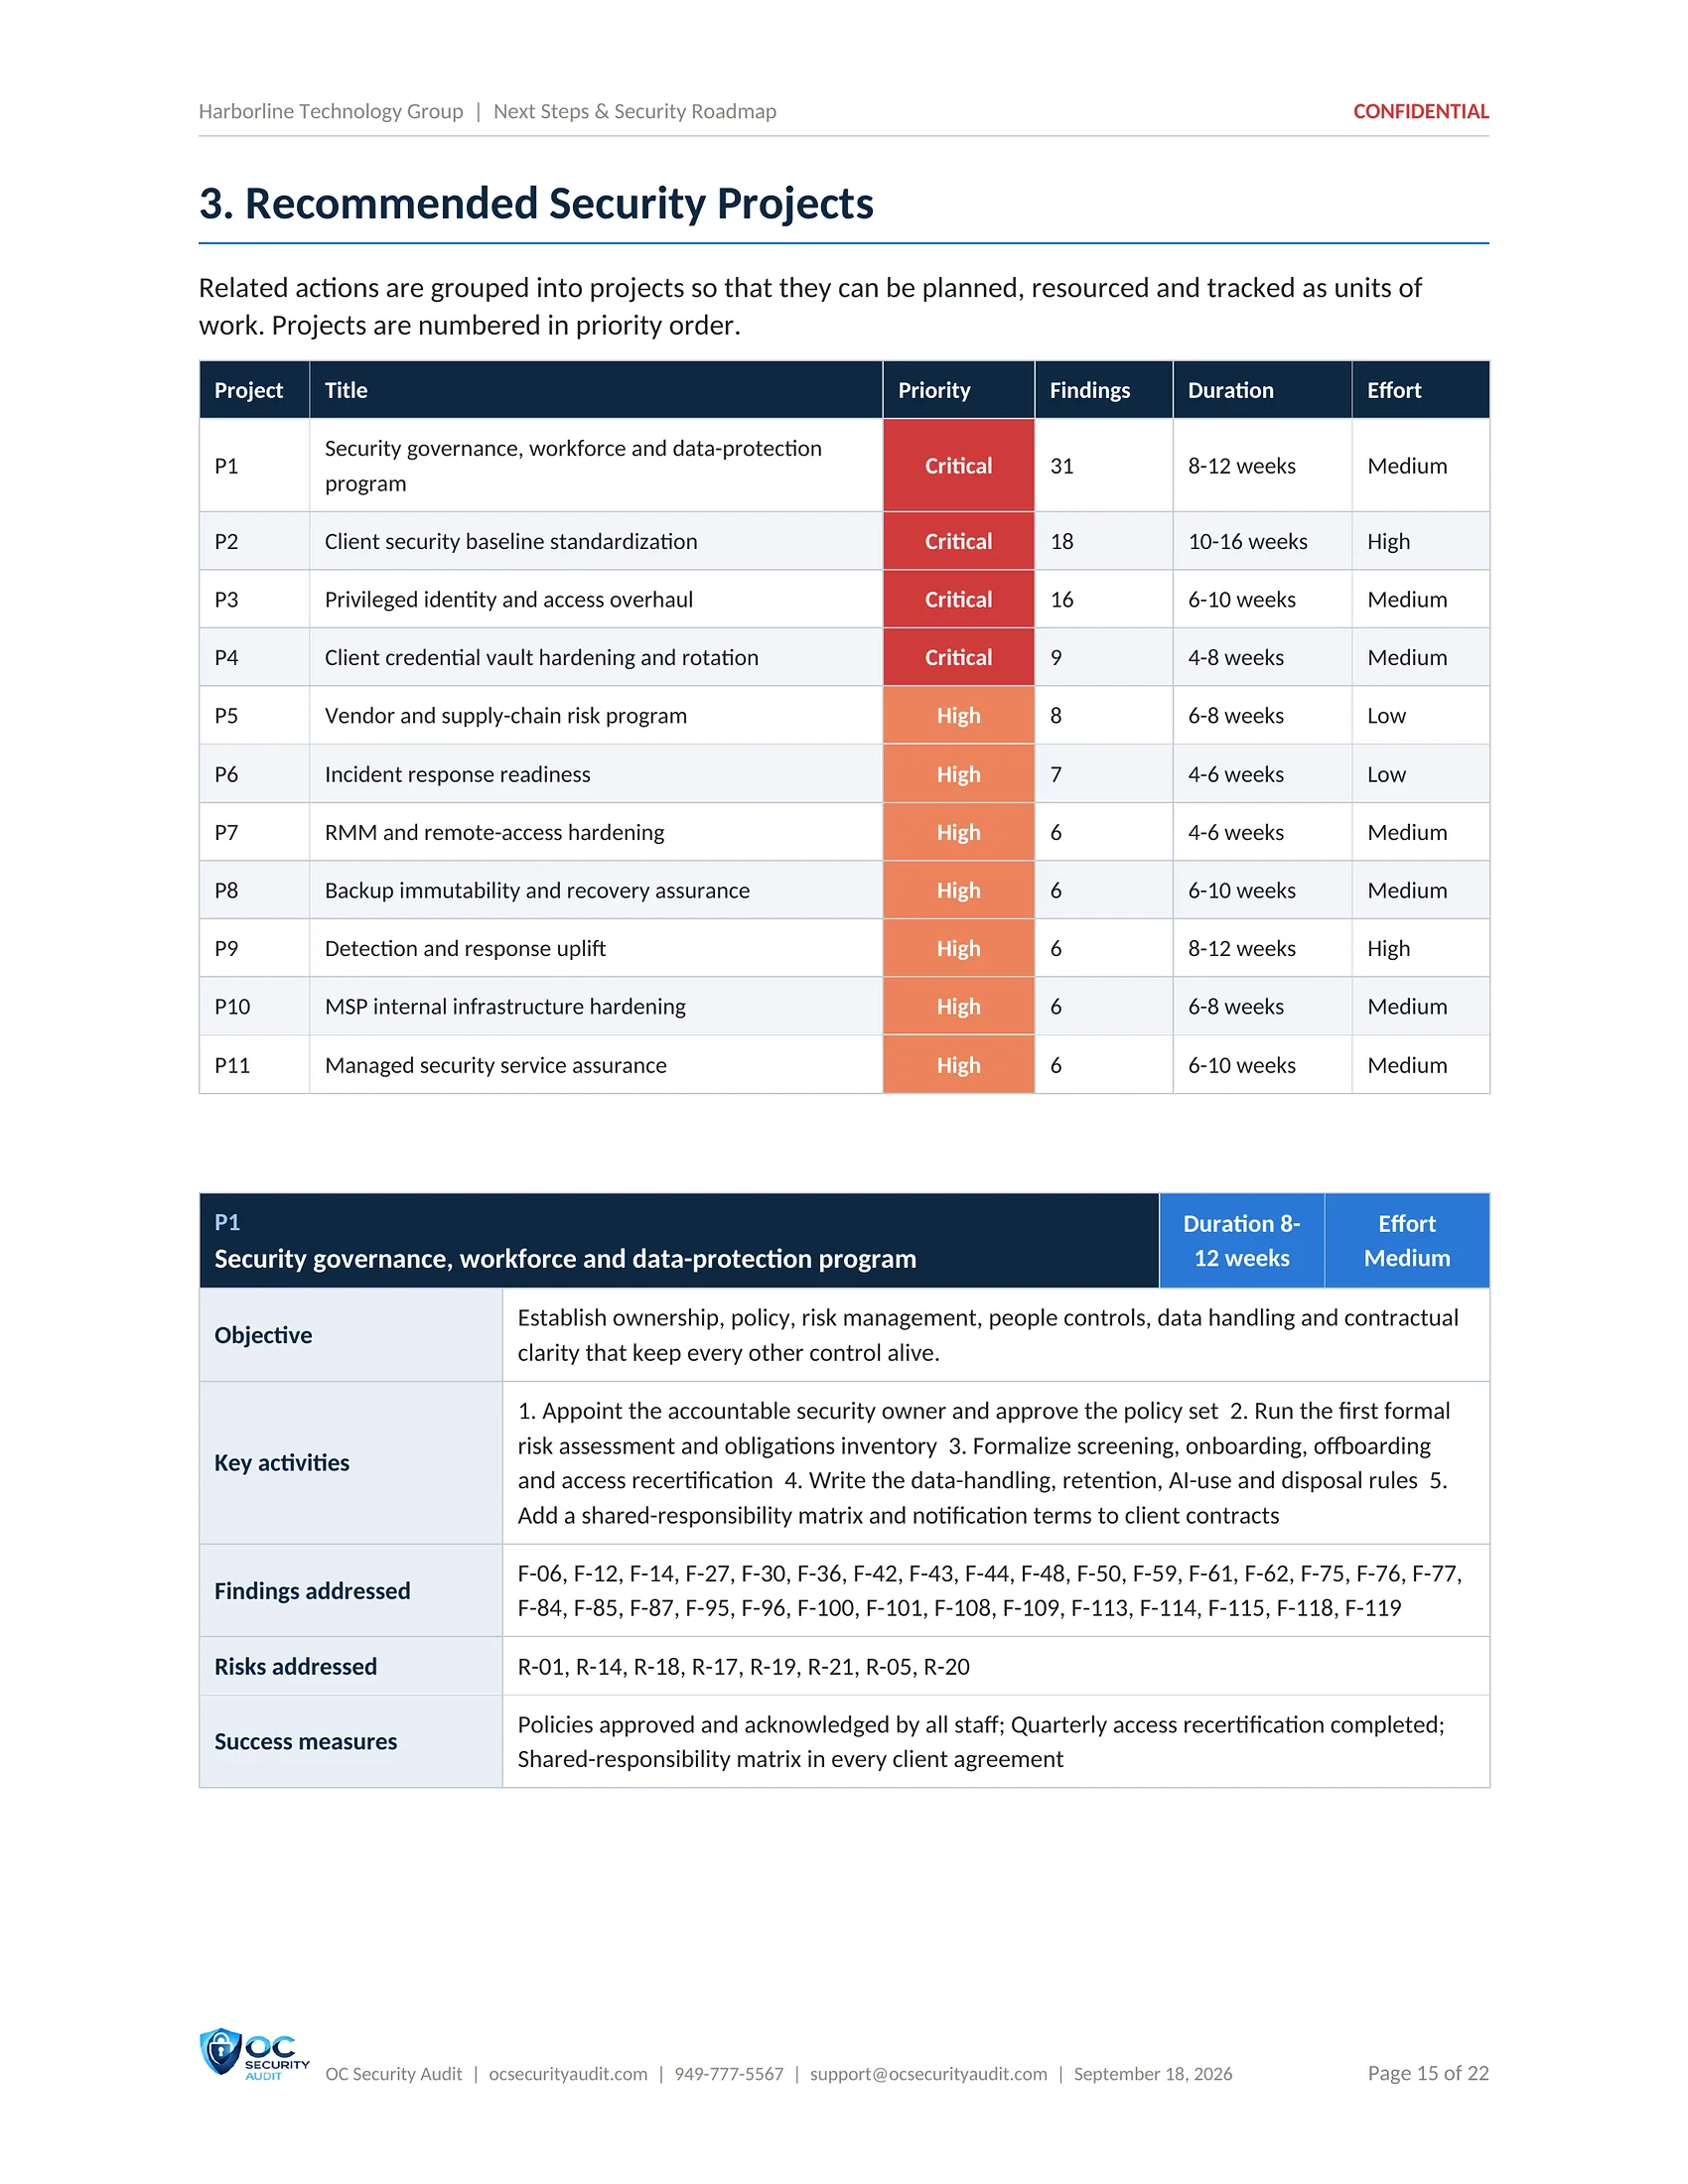
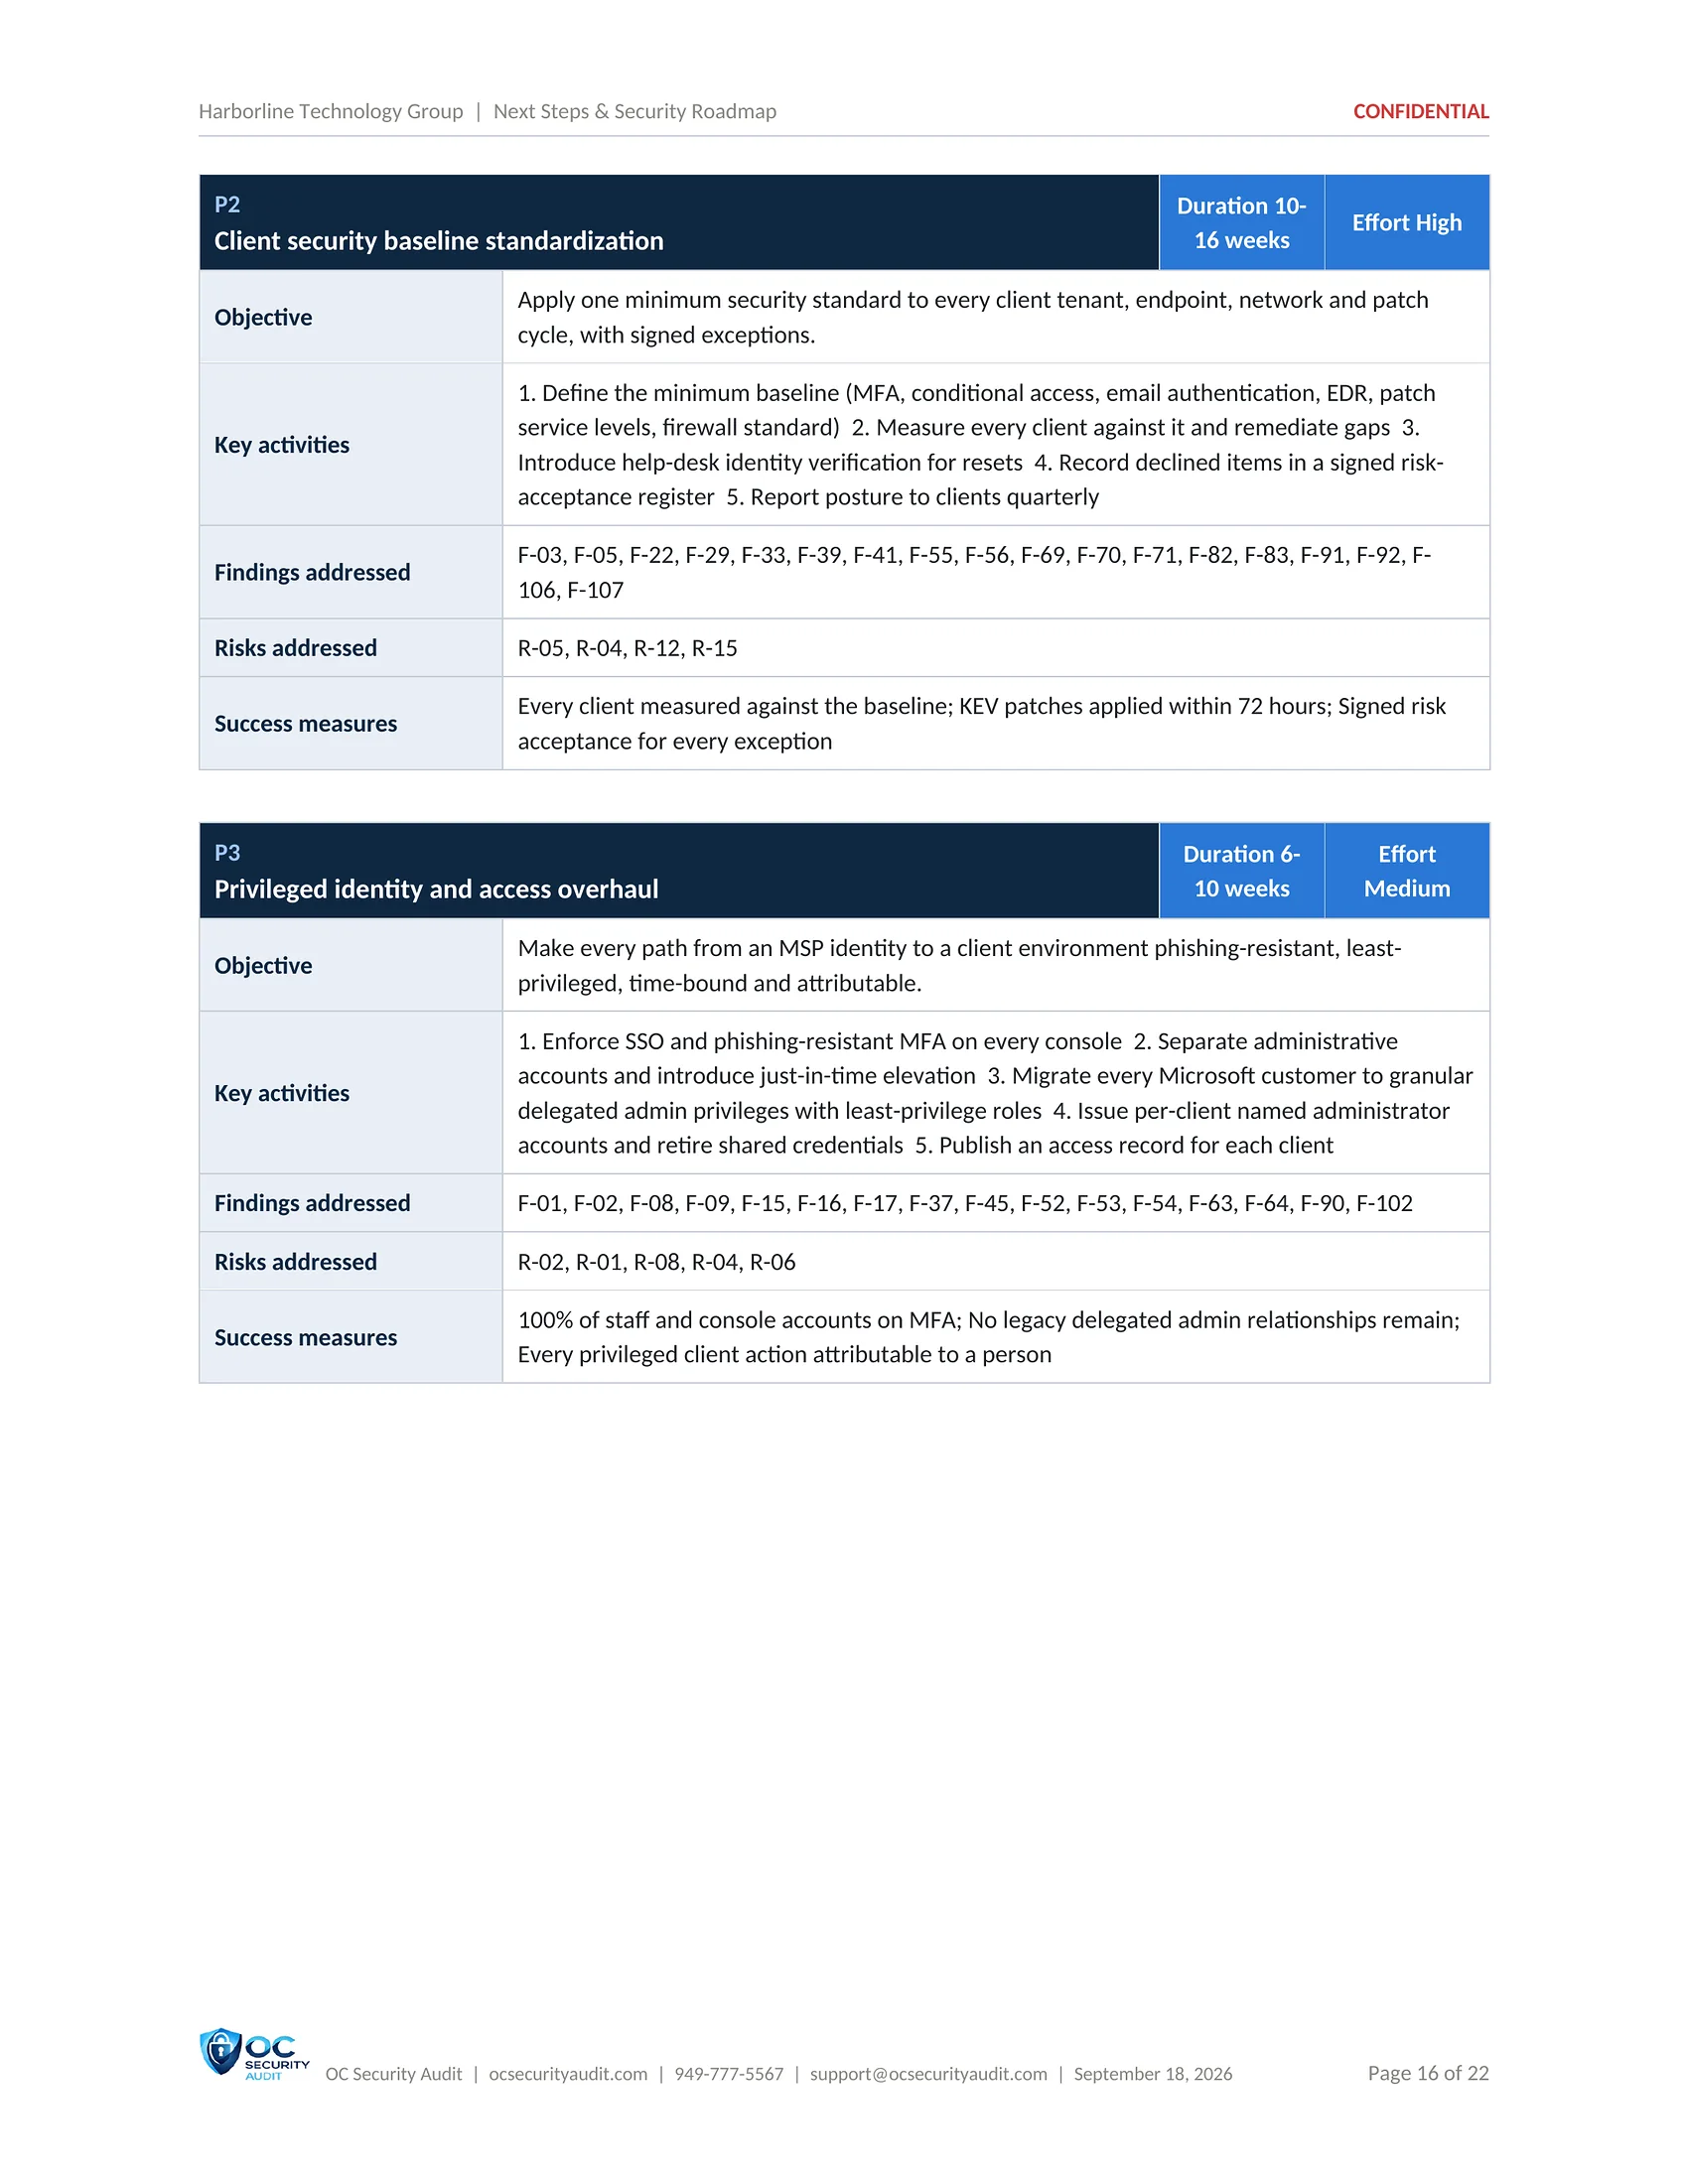
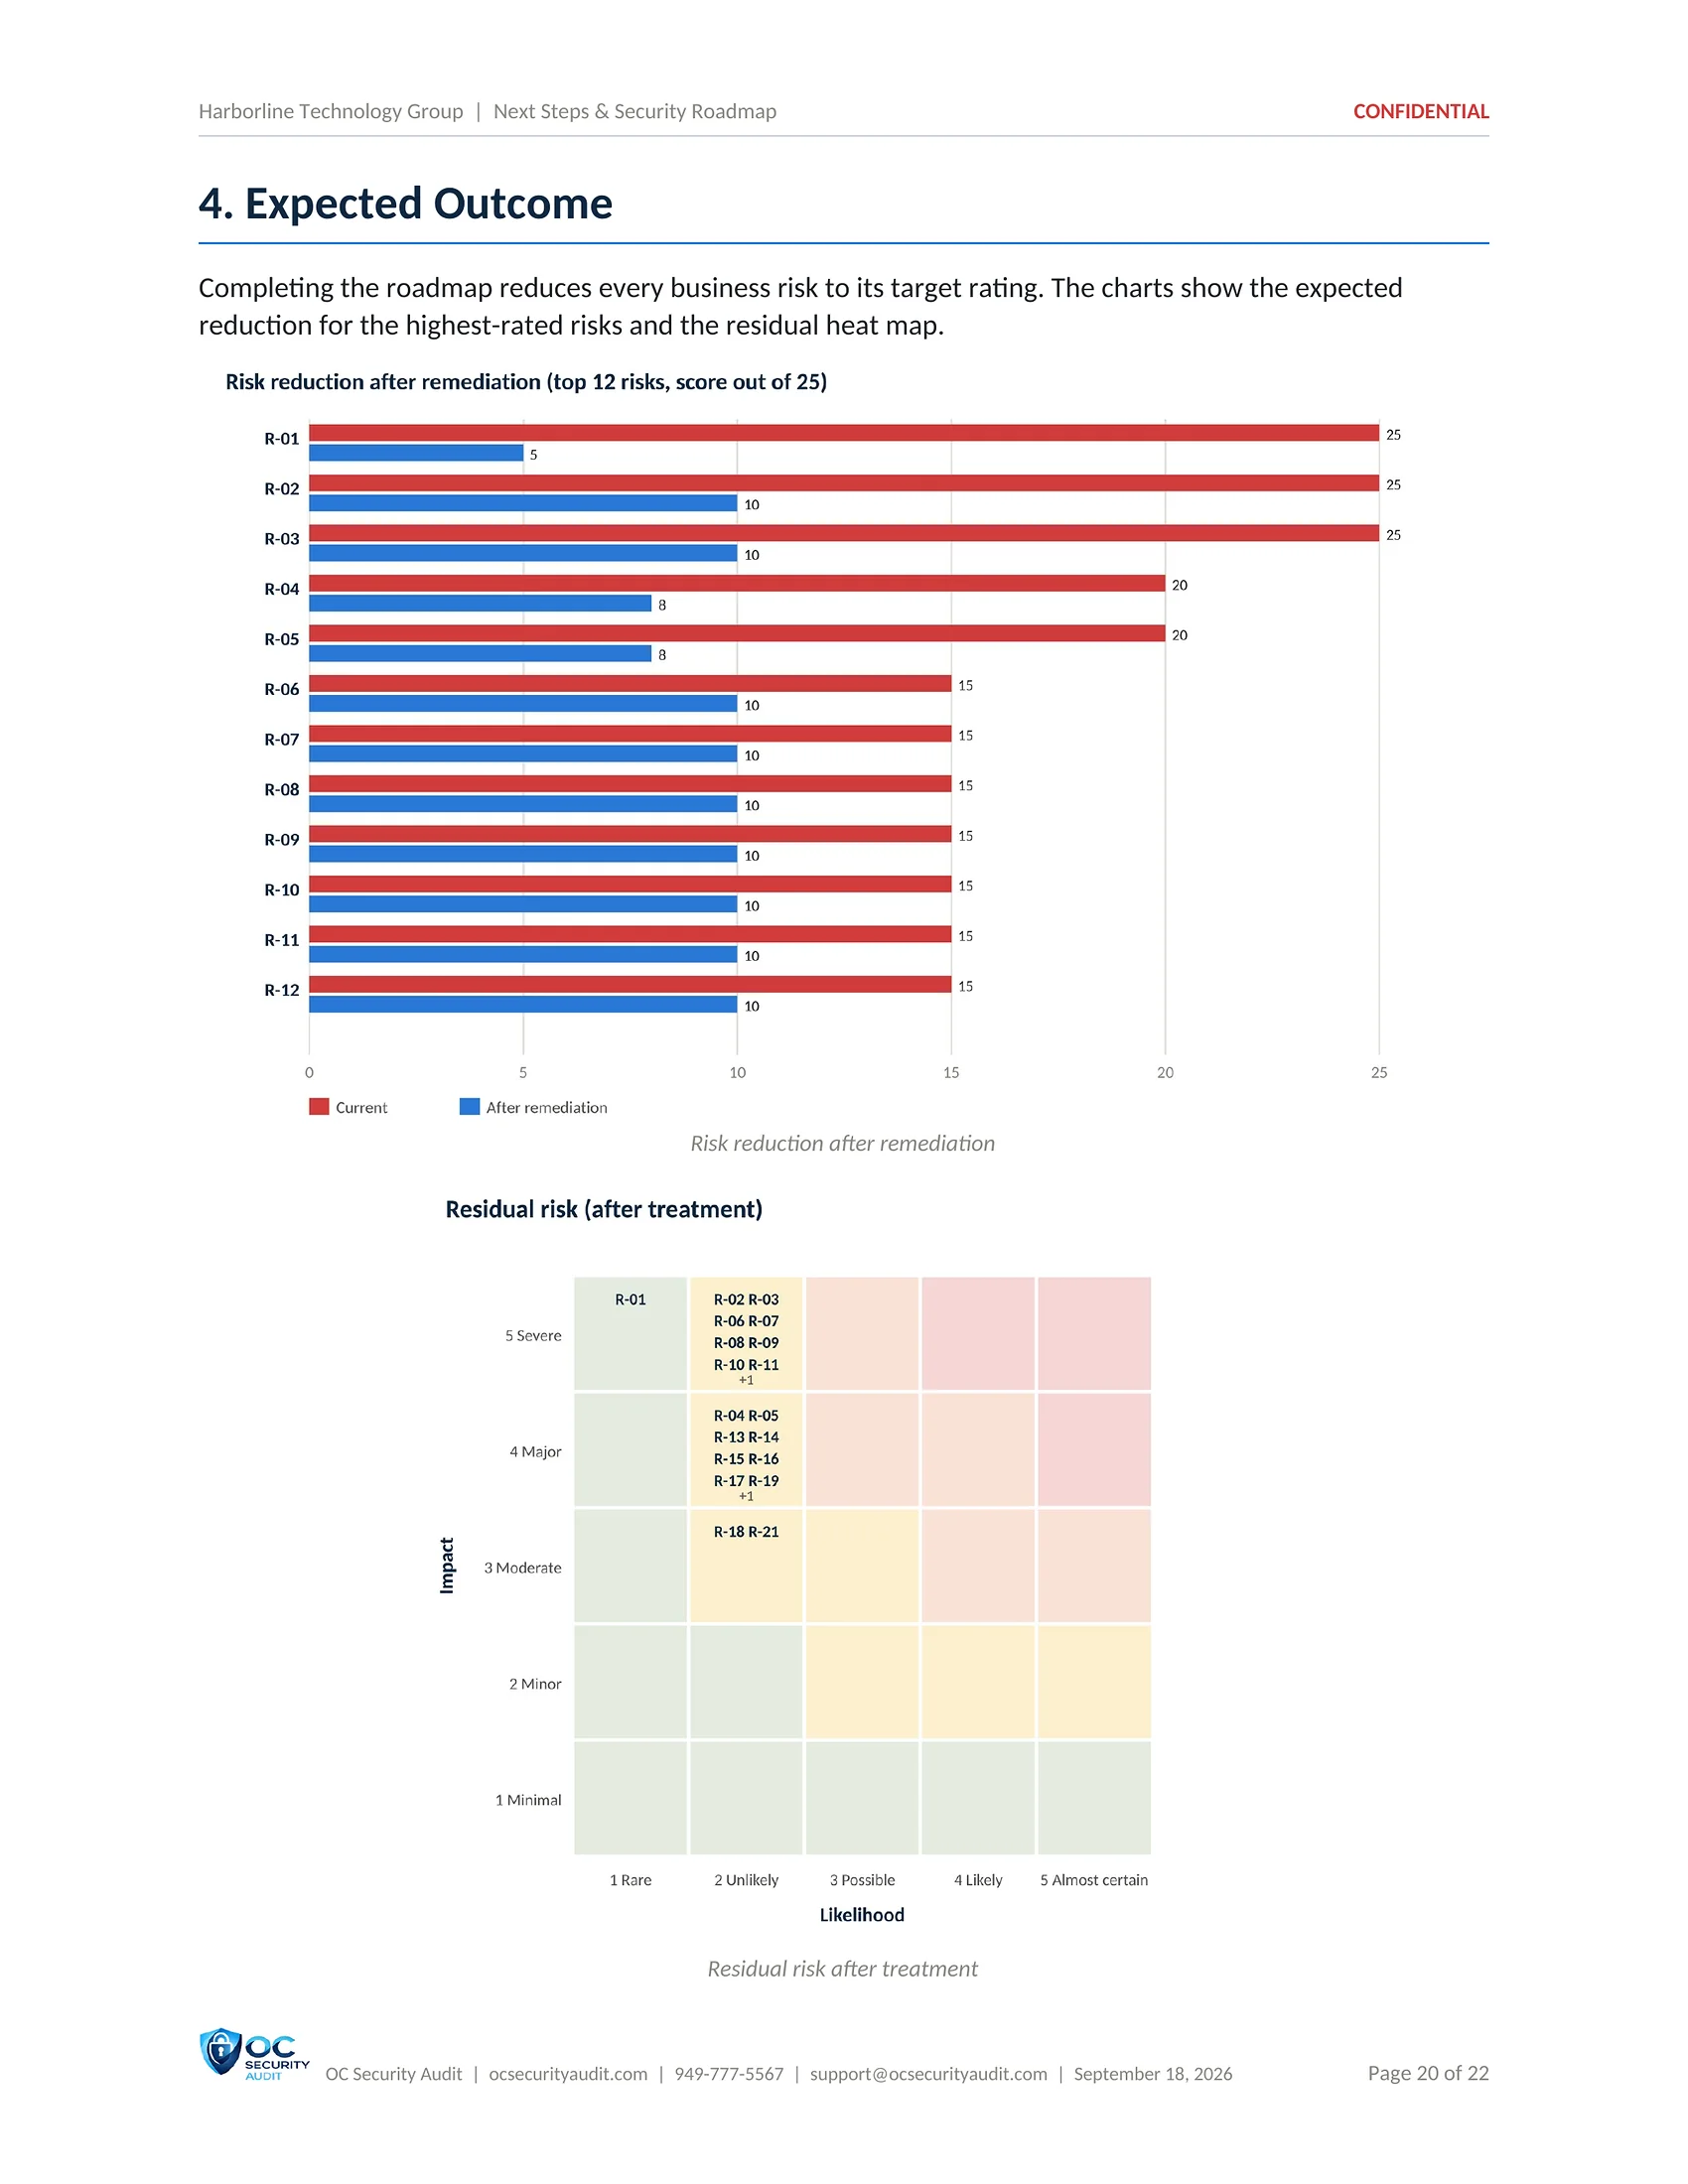
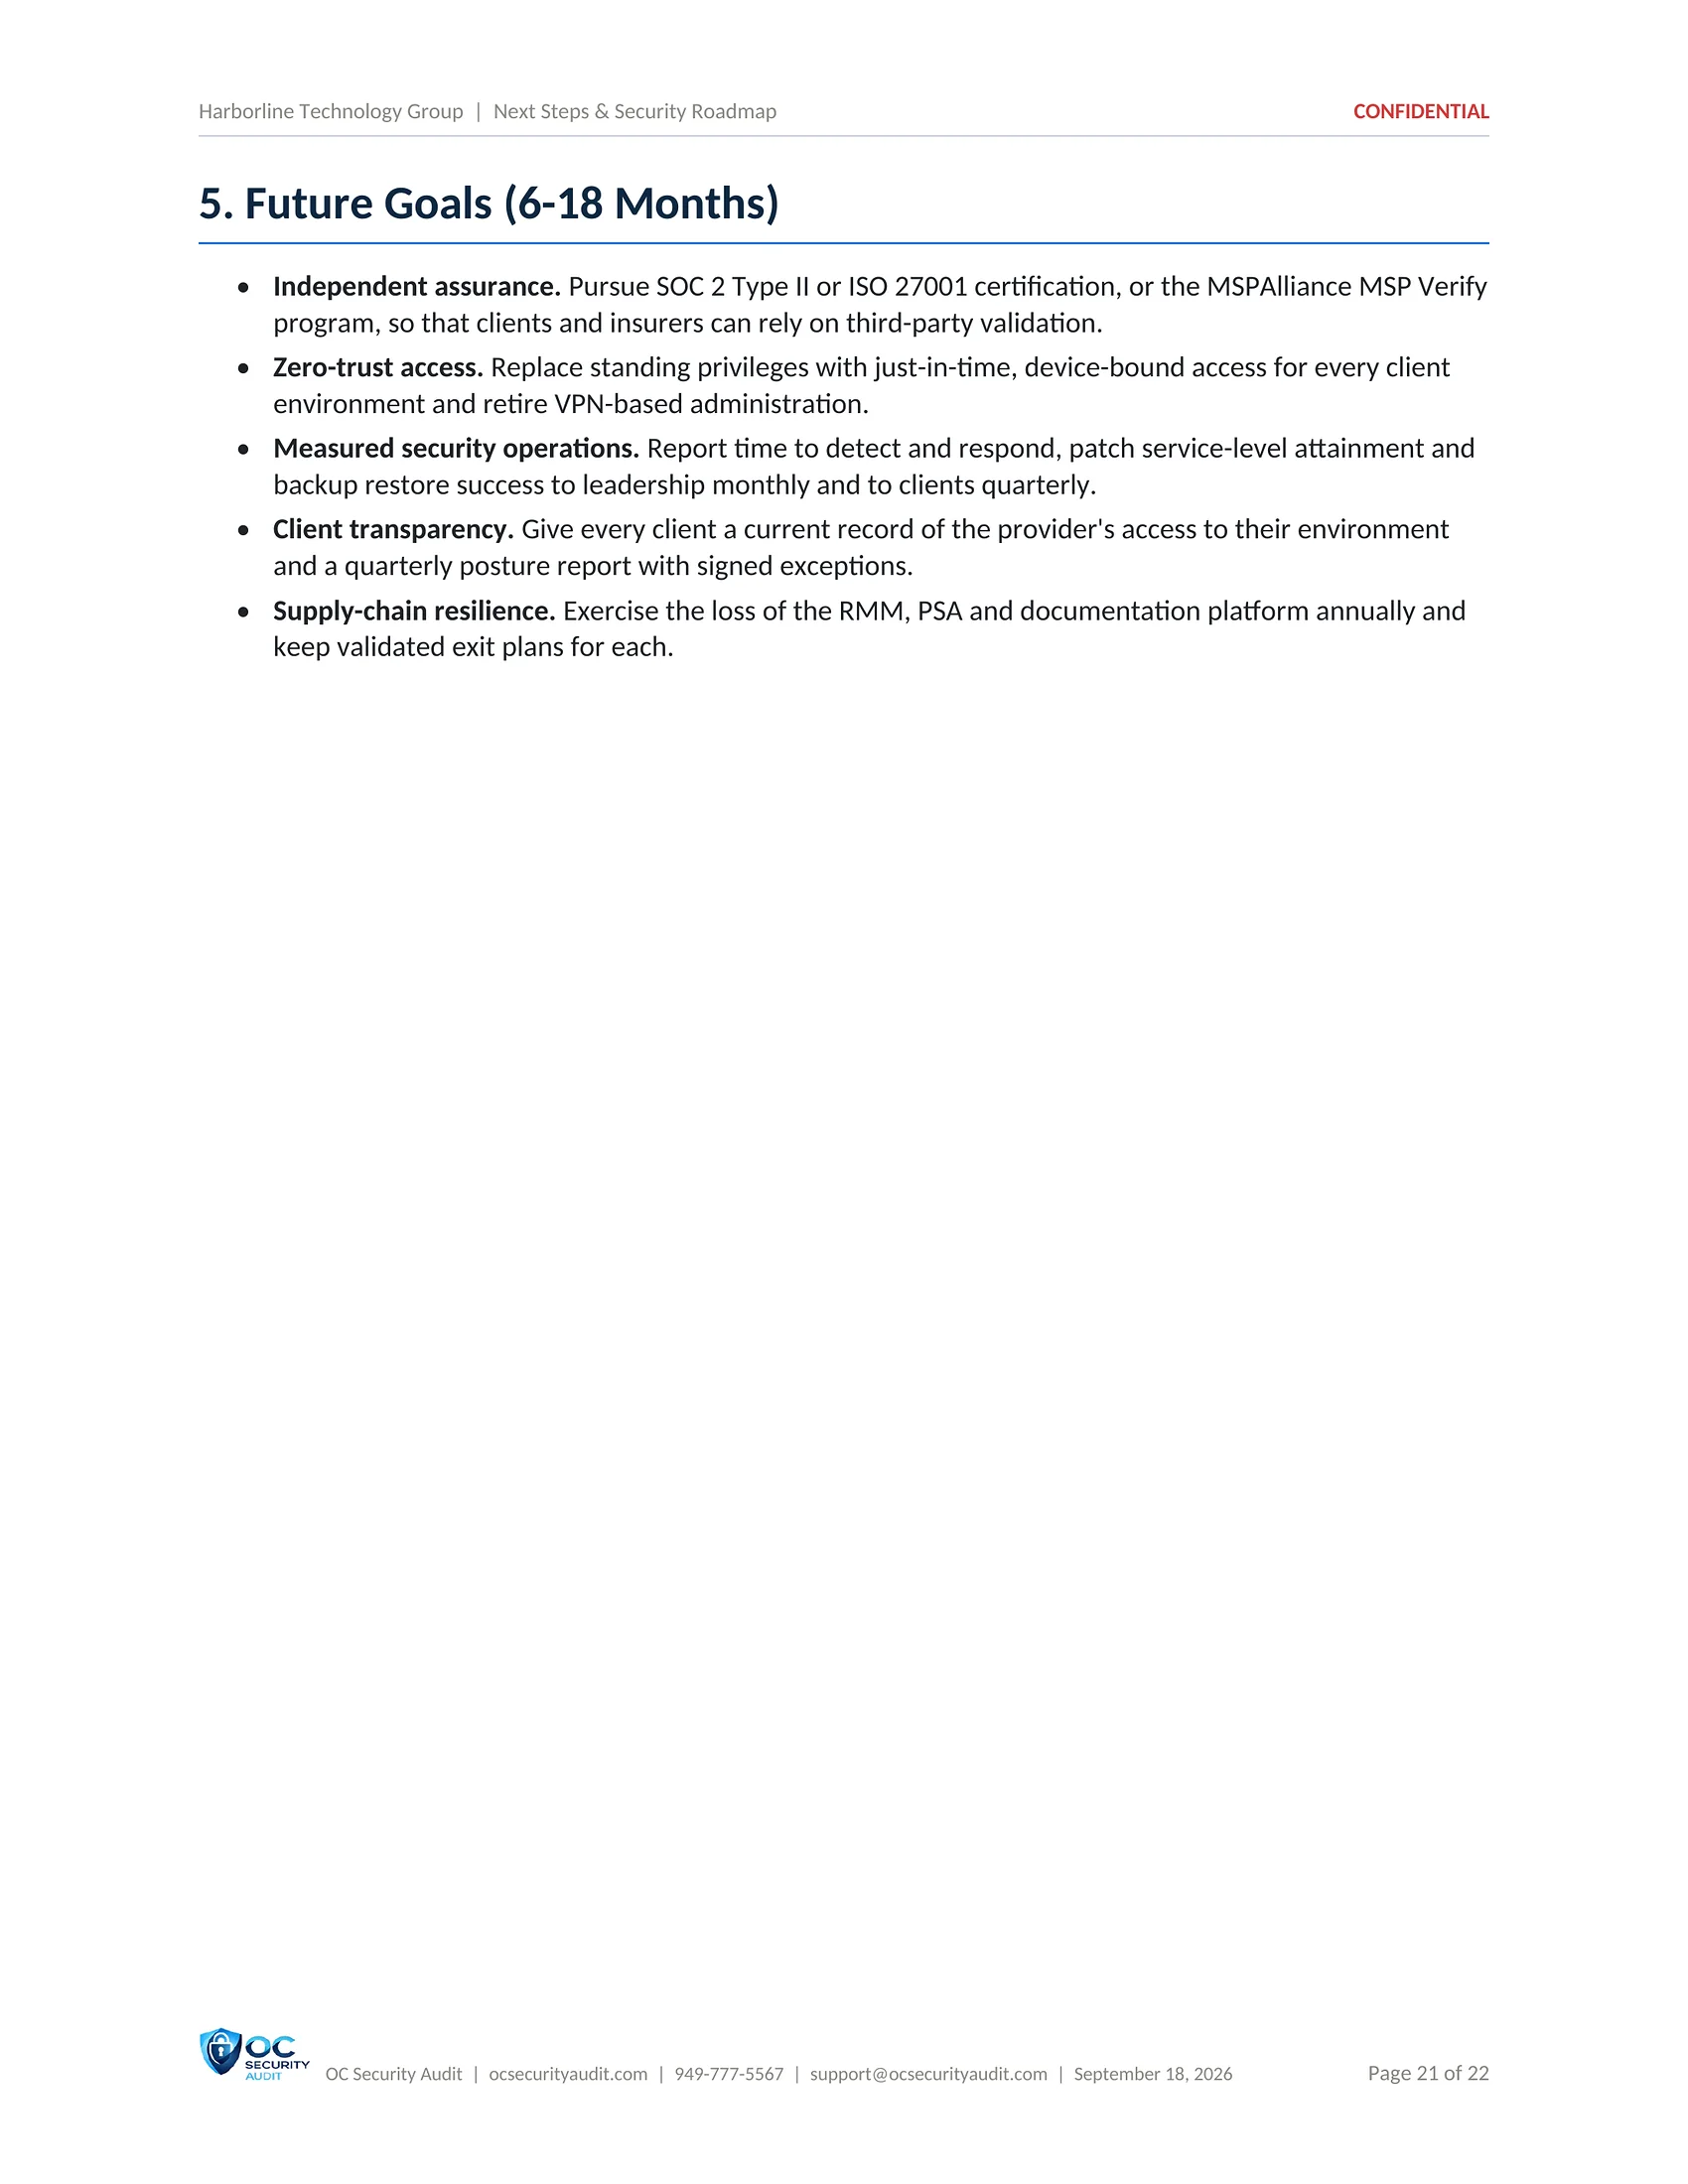
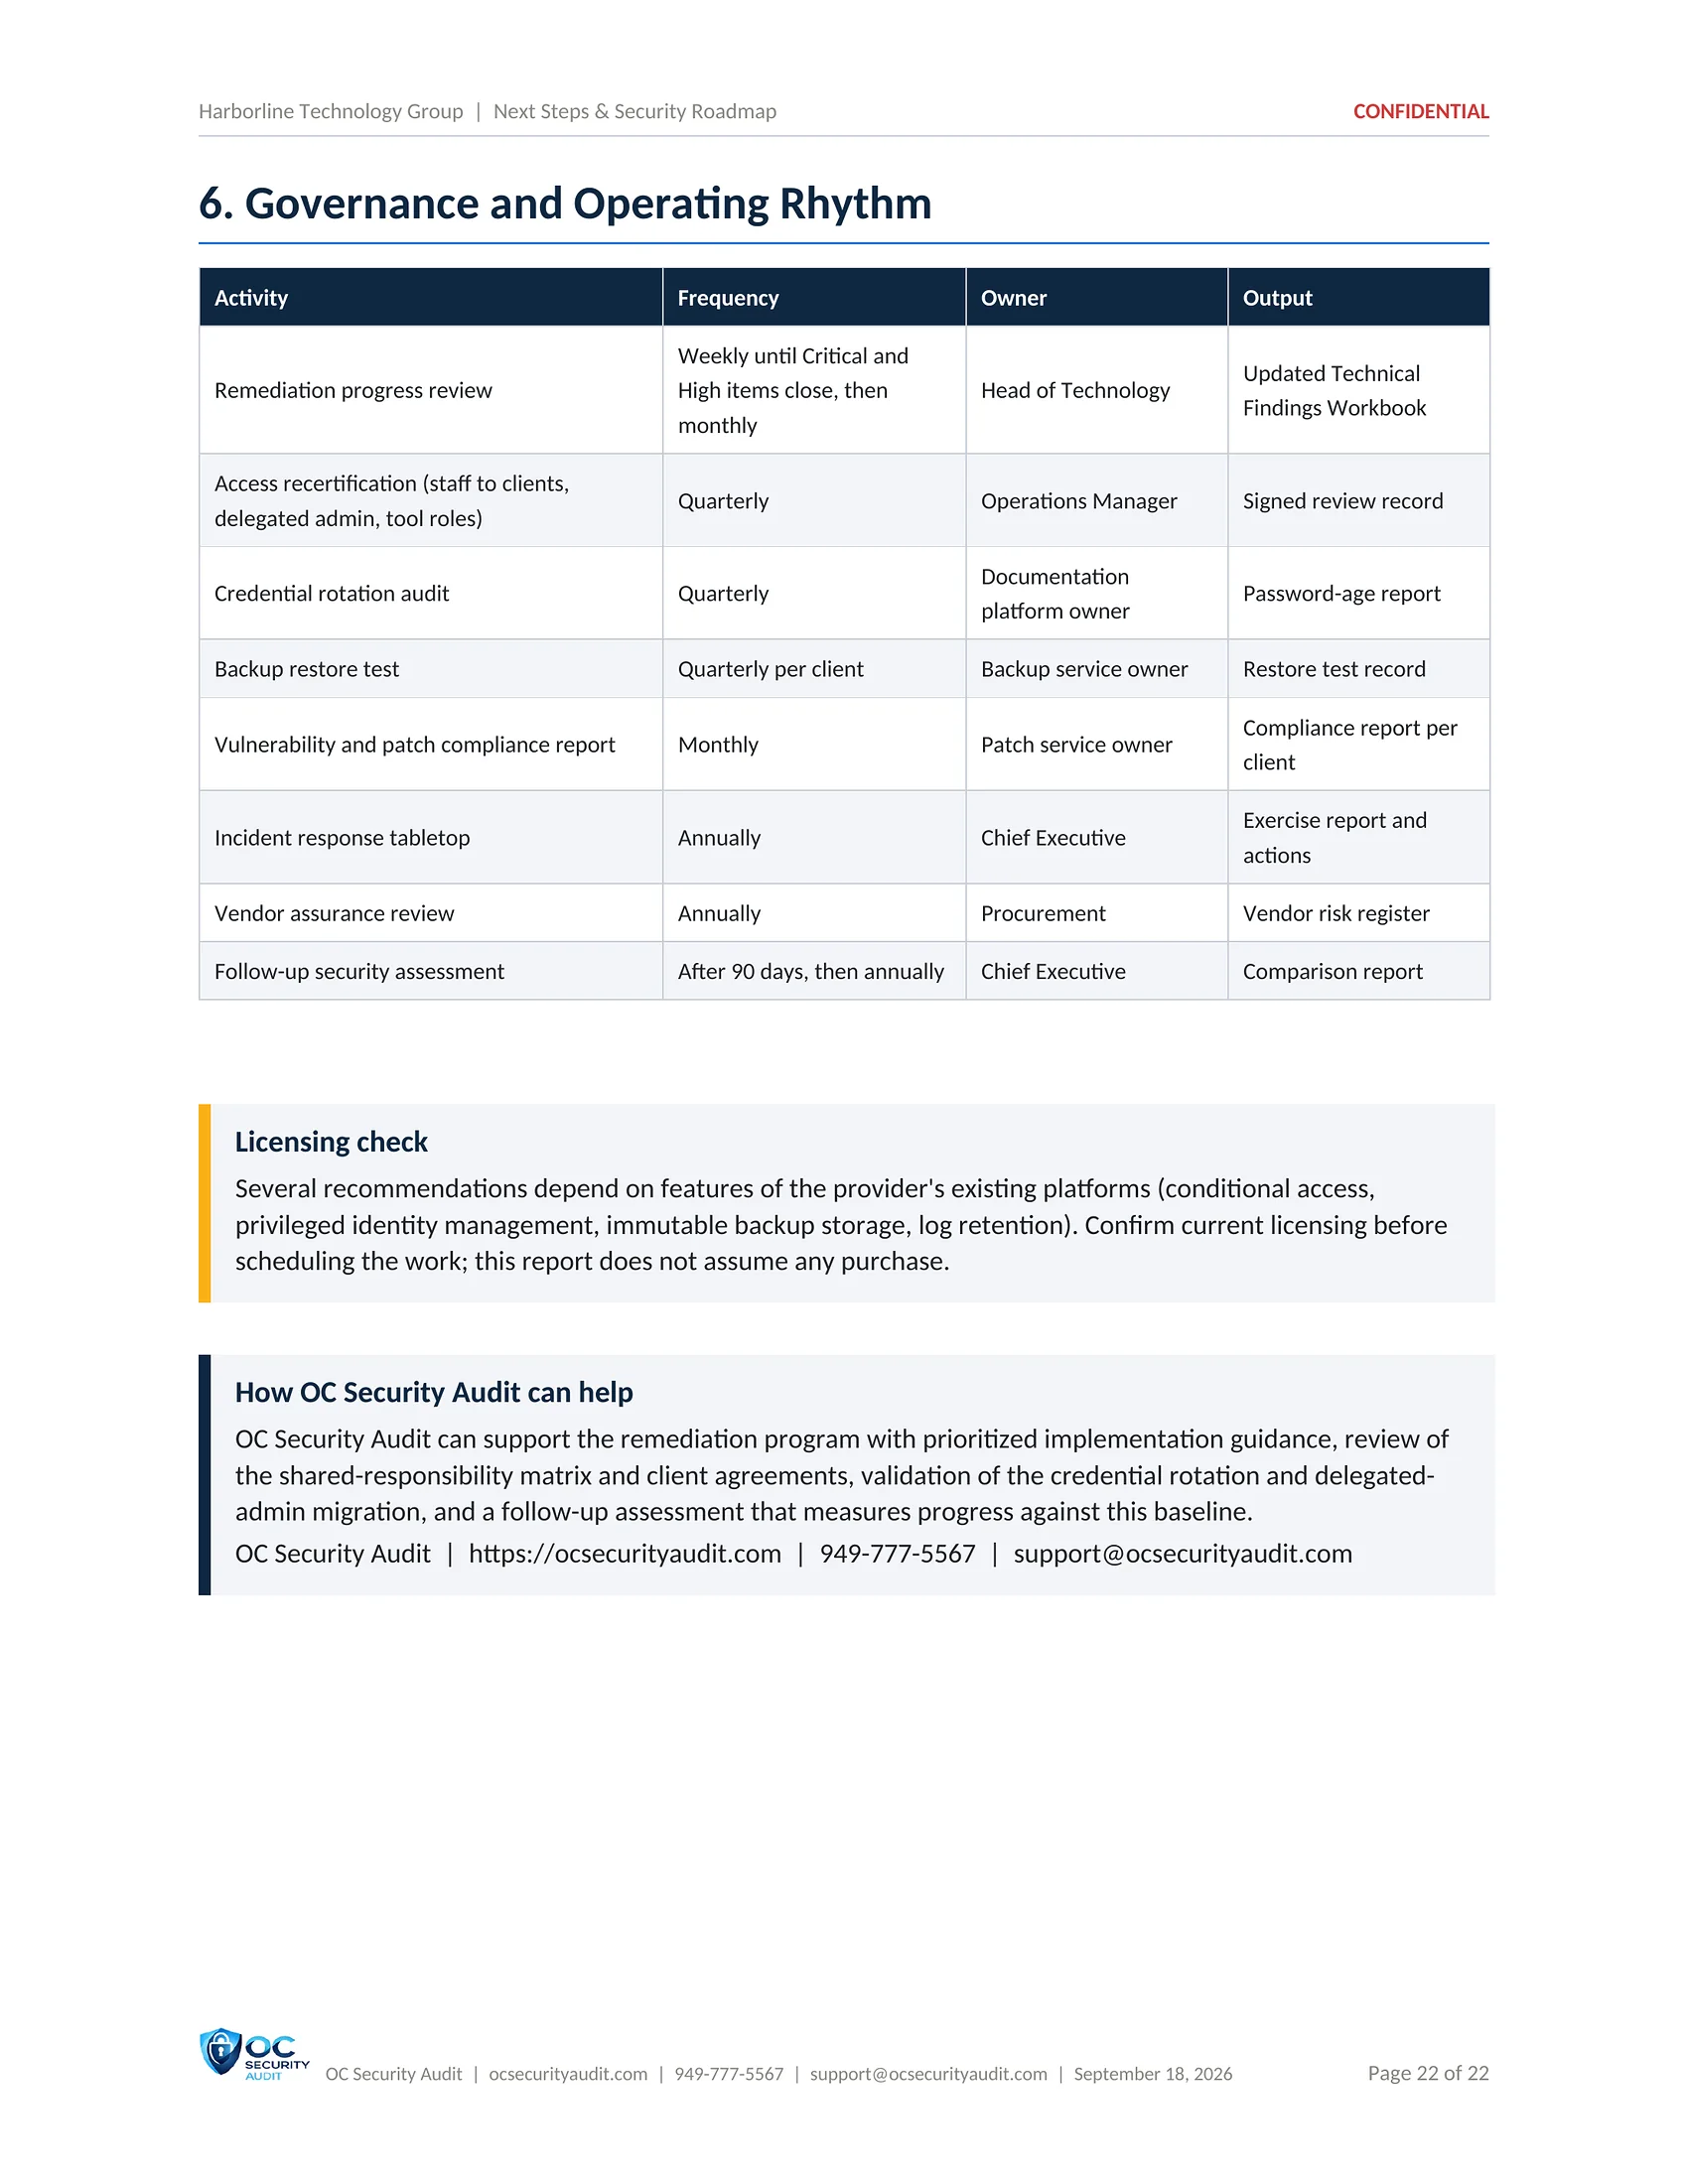
The plan that turns the audit into work. It starts with containment in the first seven days, then sets out what to complete within 30, 90 and 180 days, grouped into projects with priority, effort and duration, and the governance rhythm to keep it on track.
Operations, project leads and the head of technology who will run the remediation.
What is included
- Today, 30 days and 180 days compared
- Phase 0 containment, days 0 to 7
- Critical, High and Medium phases
- Numbered security projects
- Expected outcome and residual risk
- Future goals for 6 to 18 months
- Governance and operating rhythm
Click the centre page to open it full size and zoom in.
PDF and Word · 2 pages per audit
MSP Security Scorecard
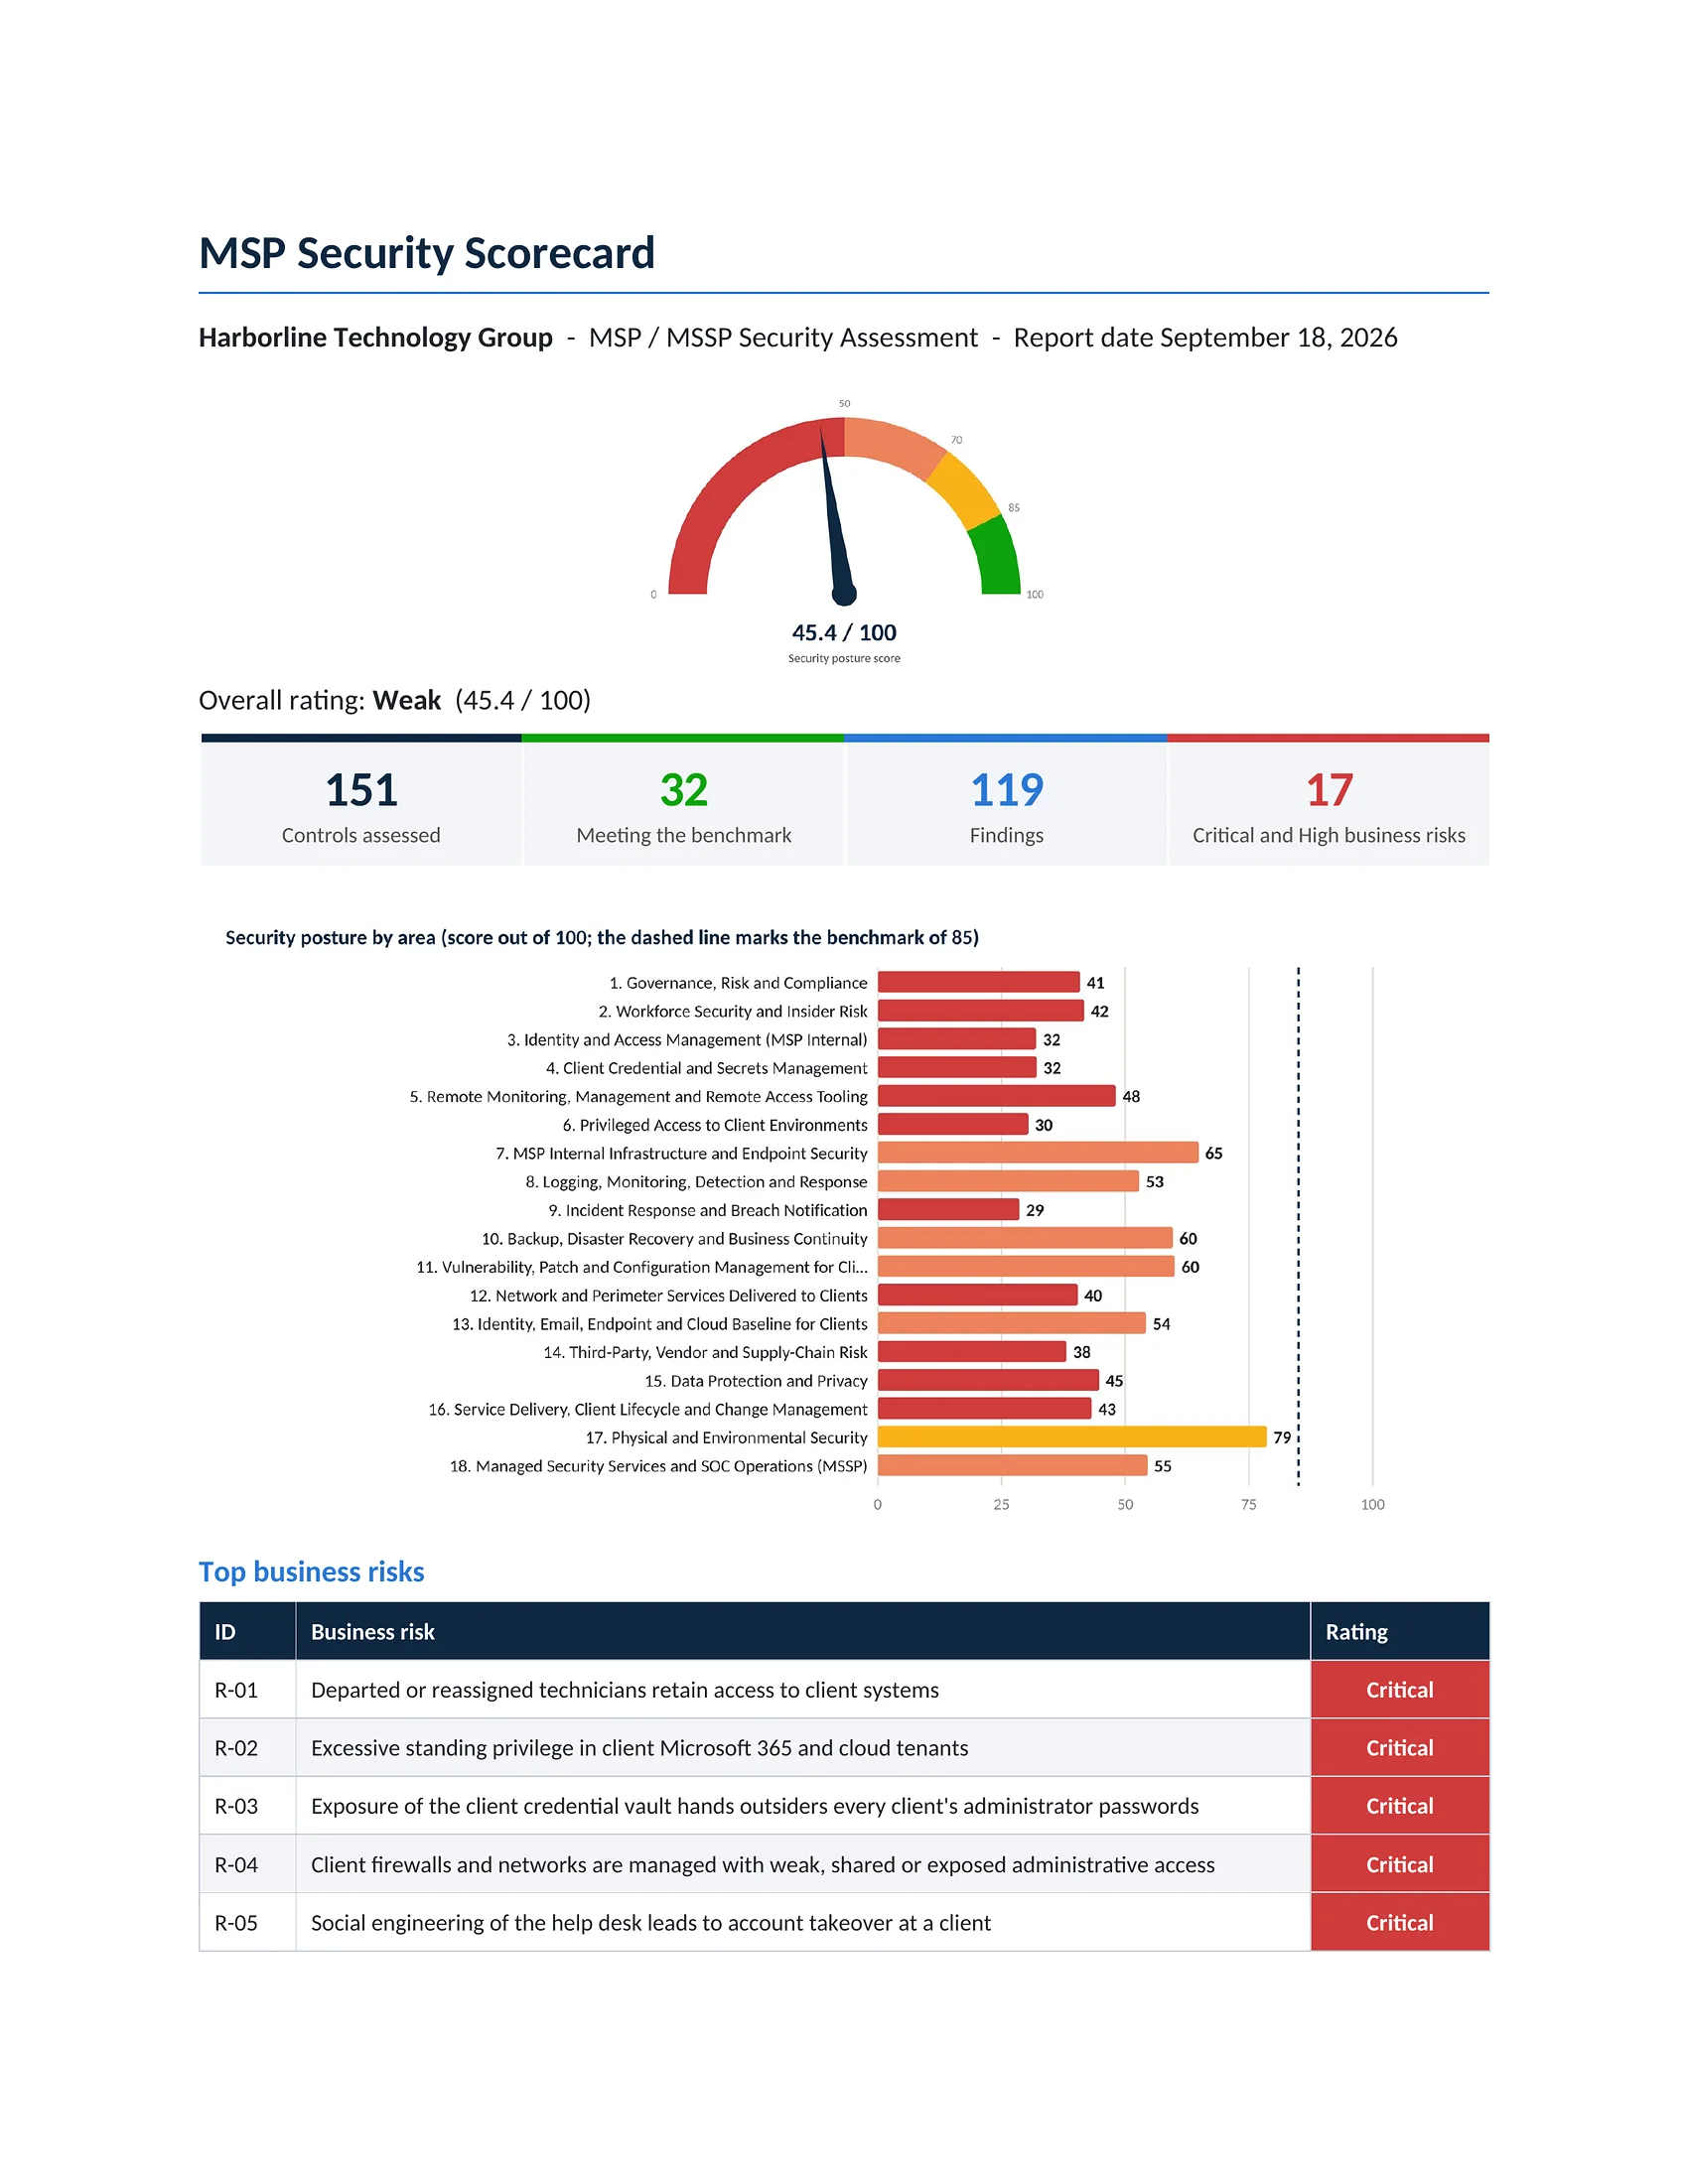
A two-page summary that a provider can share. It shows the overall rating, the key numbers, the score of each area, the top business risks and the strongest areas, in a form owners, sales teams and clients can read in minutes. A new scorecard is issued after every audit.
Owners, account managers, client reviews and insurance renewals.
What is included
- Overall rating and score
- Controls, findings and business risks
- Score by area
- Top business risks
- Strongest areas
- What the result means
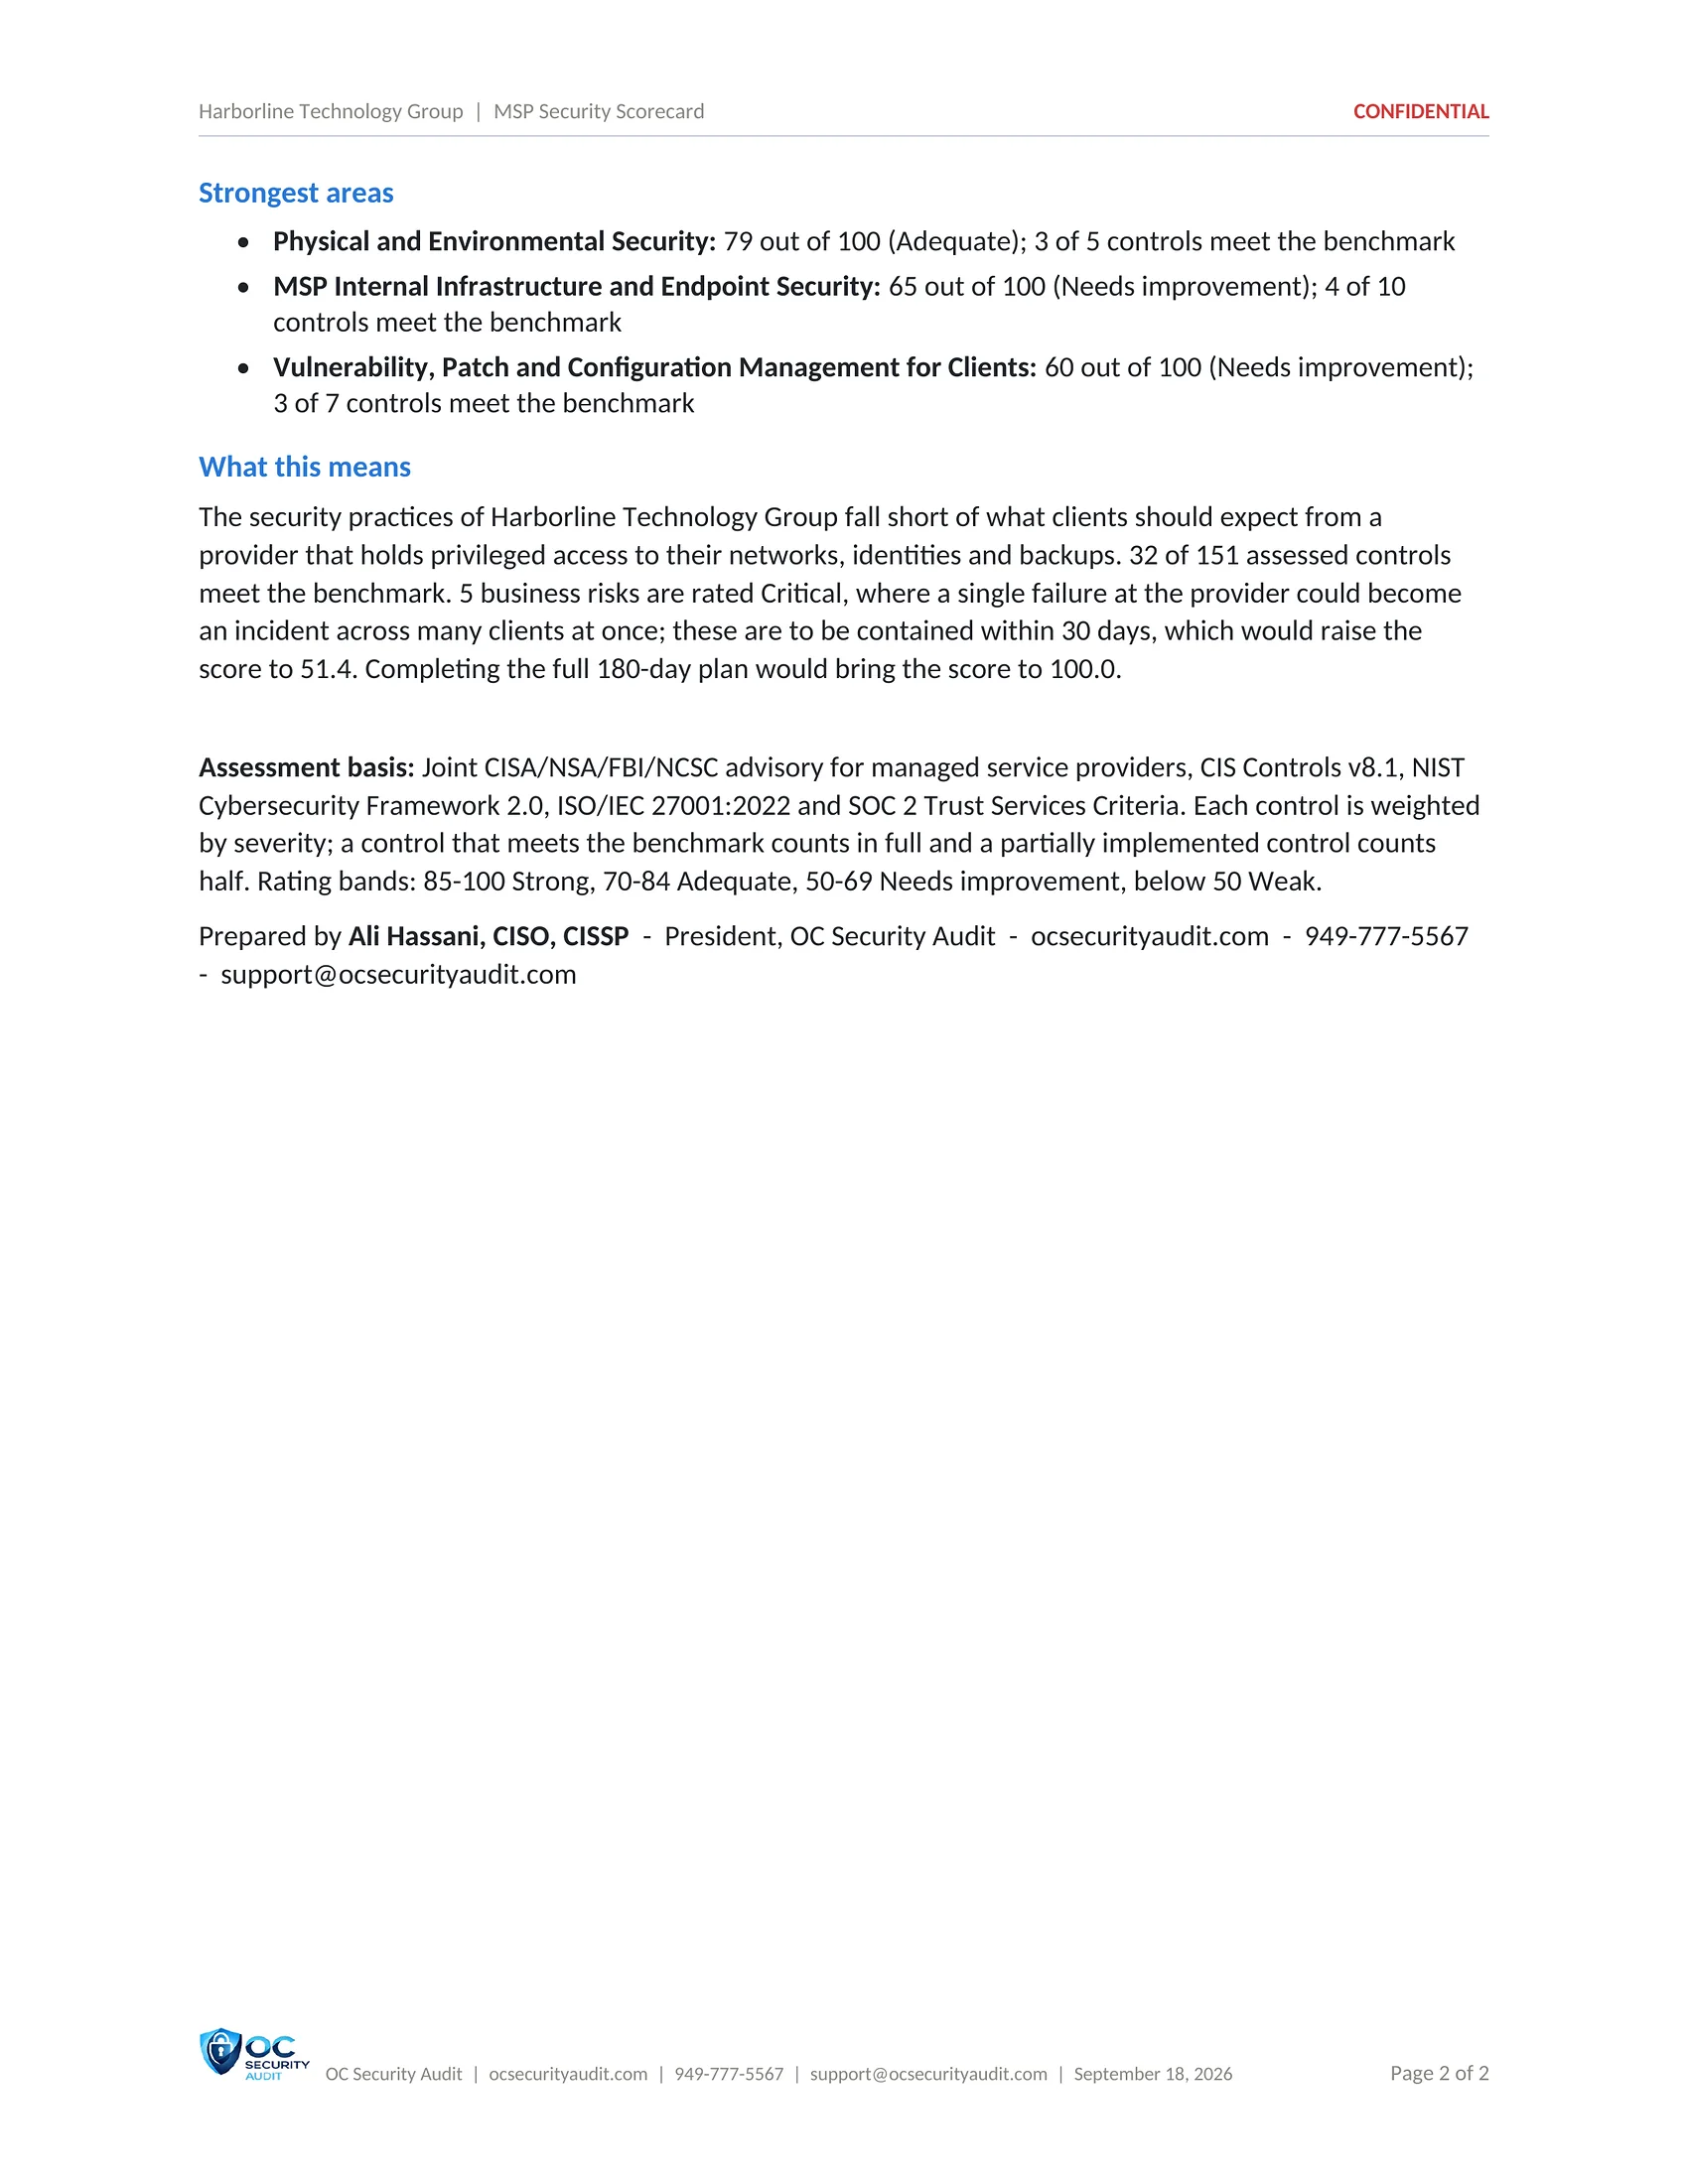
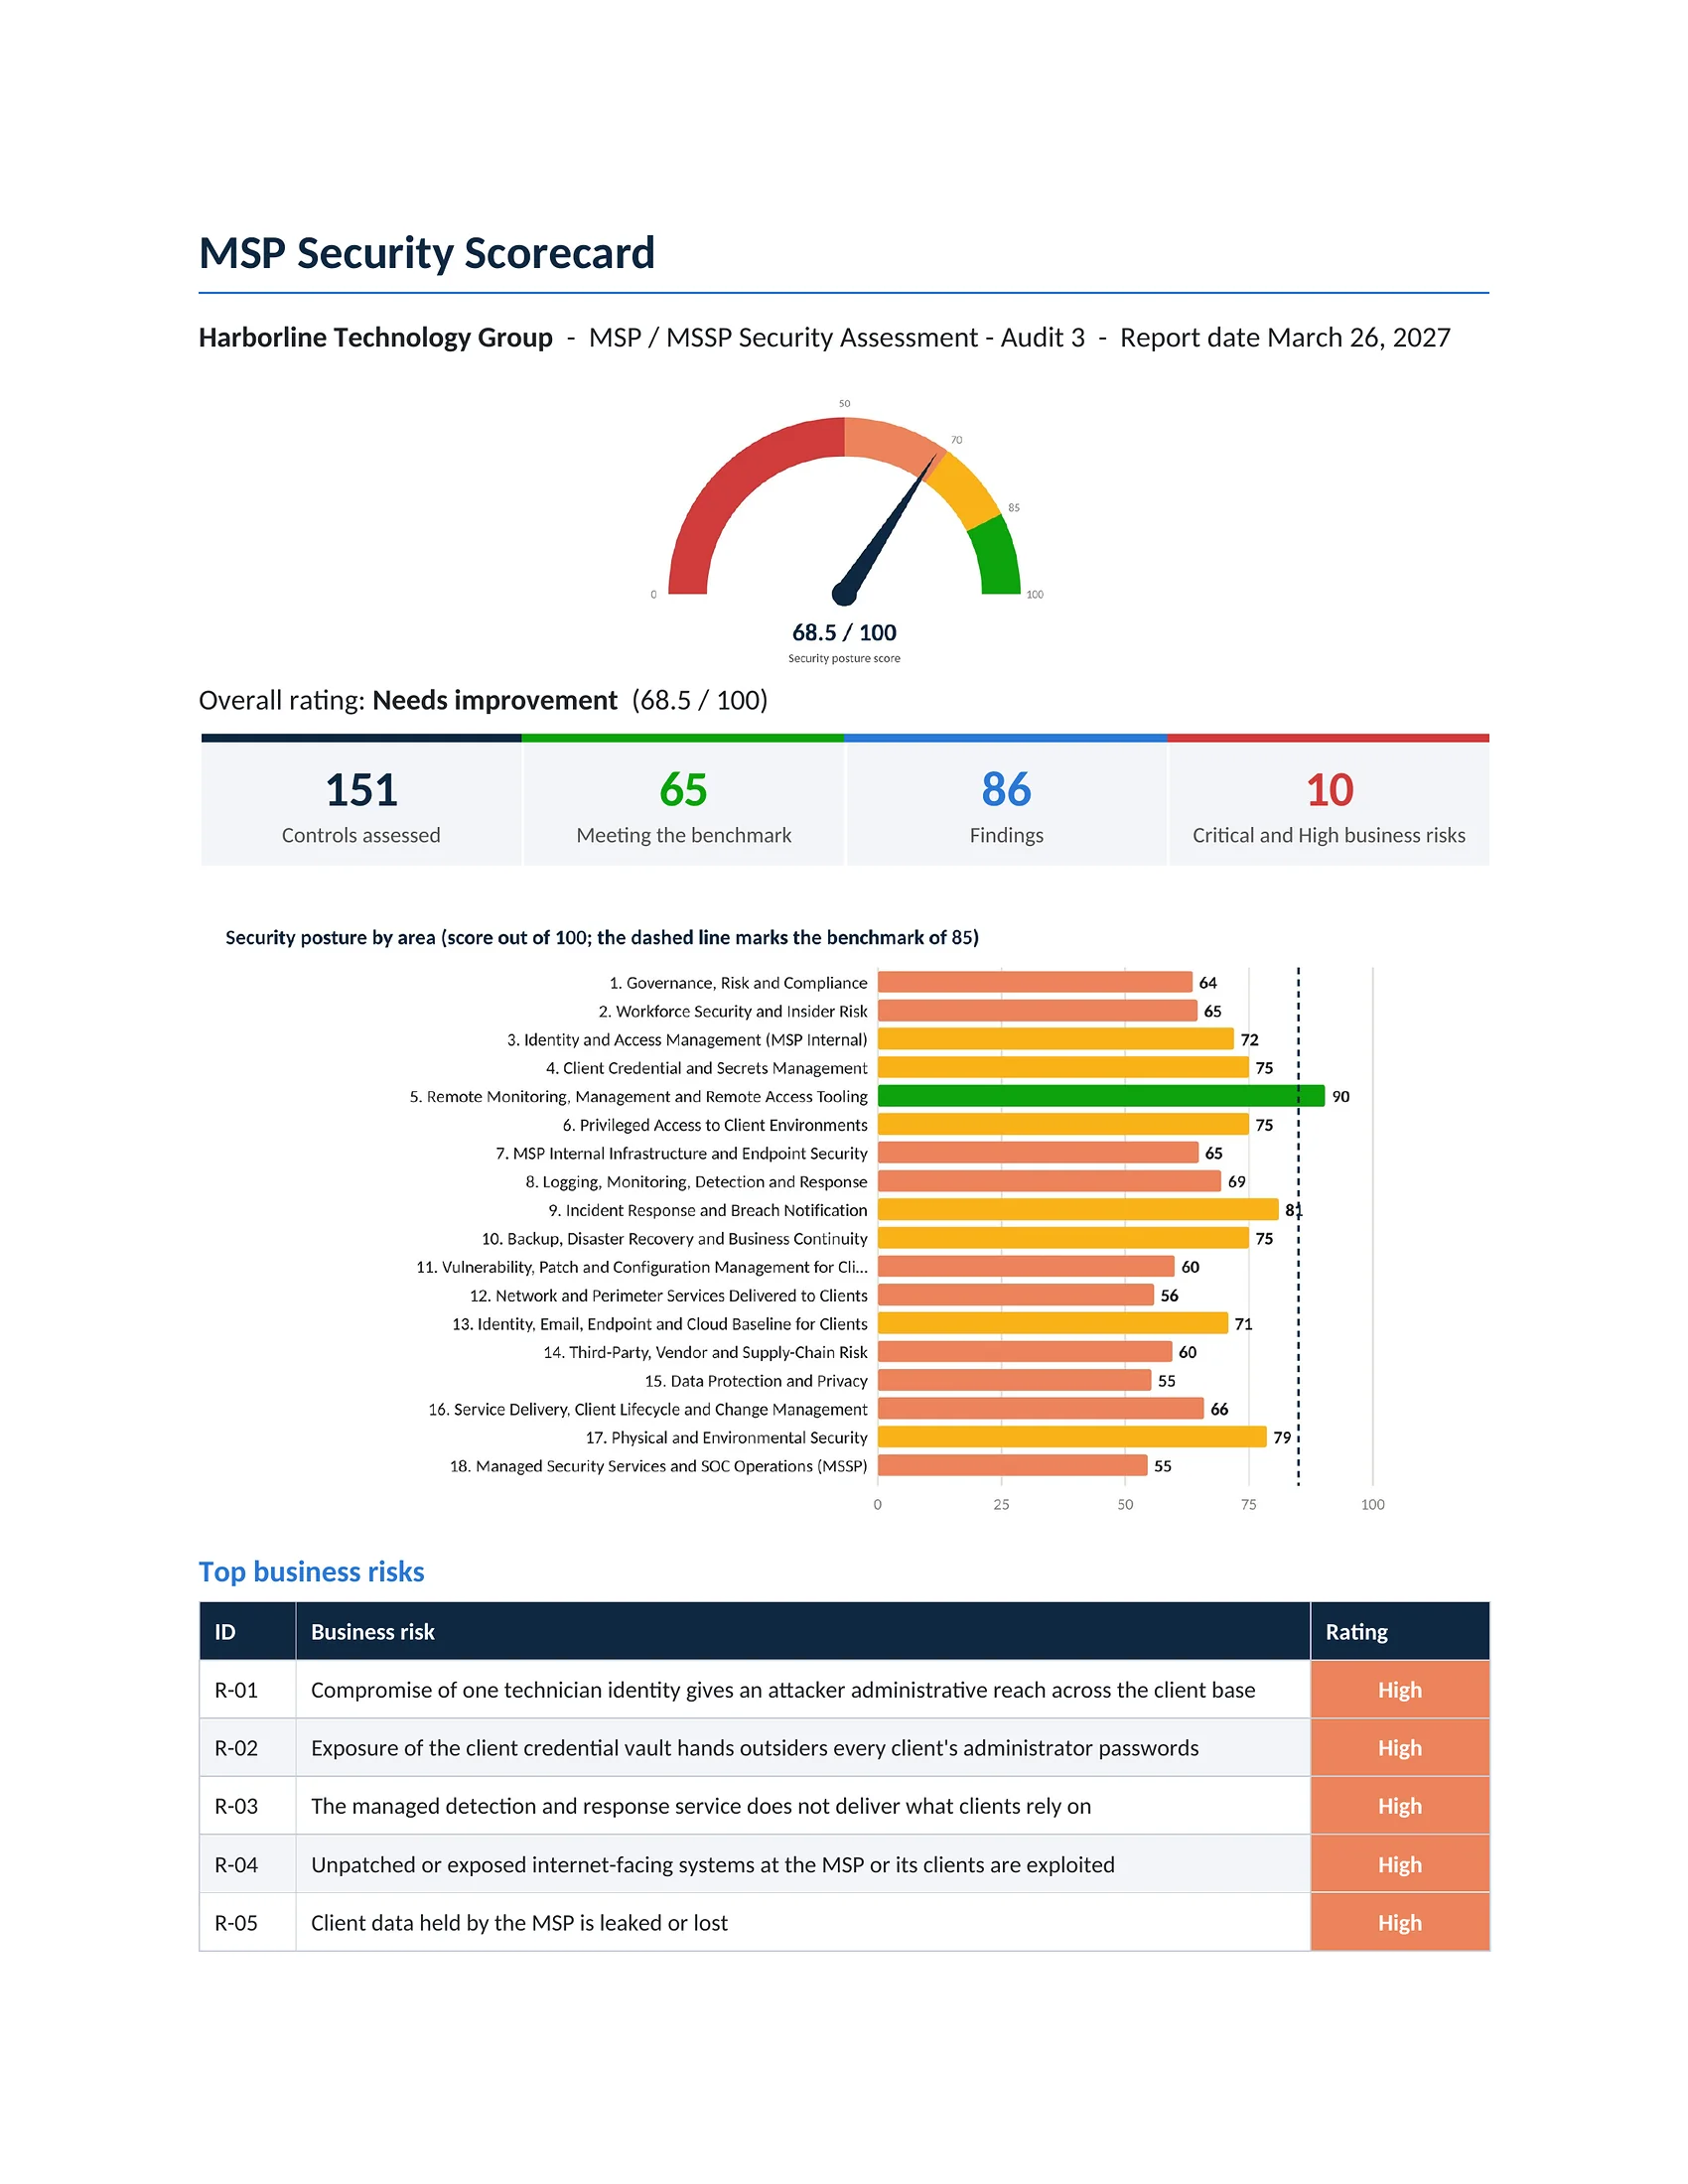
Click the centre page to open it full size and zoom in.
PDF and Word · 26 pages
Client Exposure Analysis
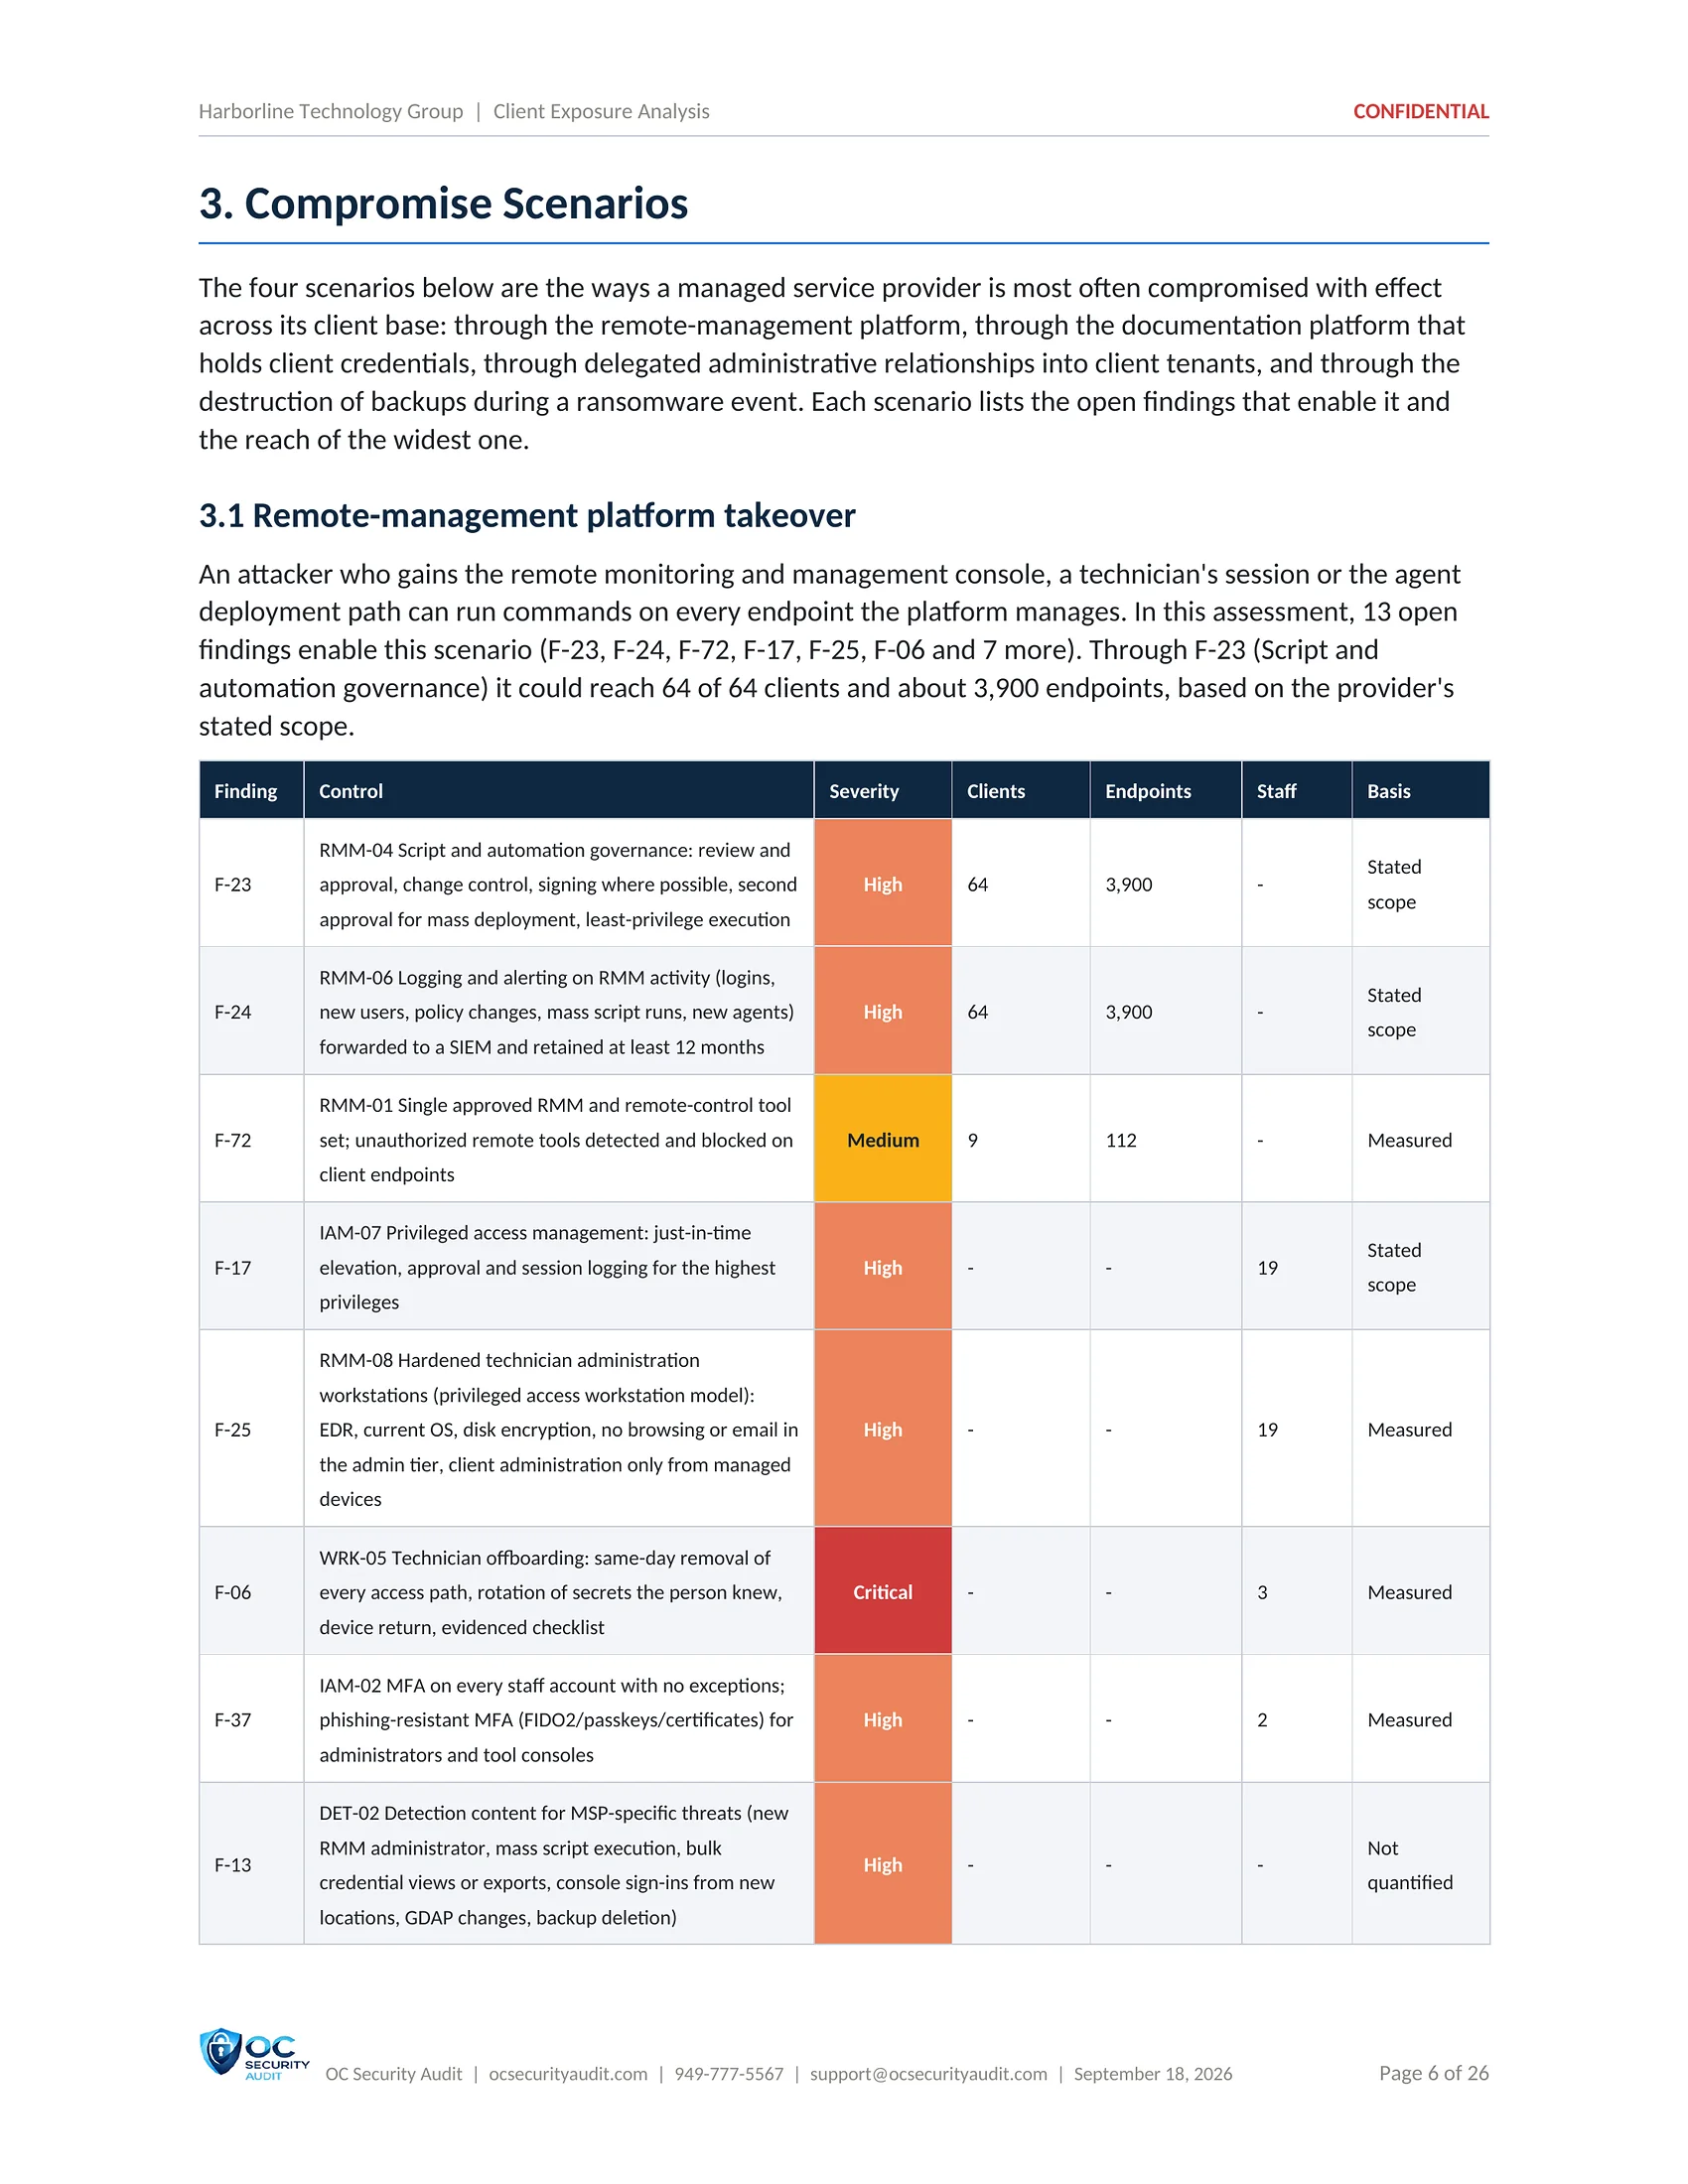
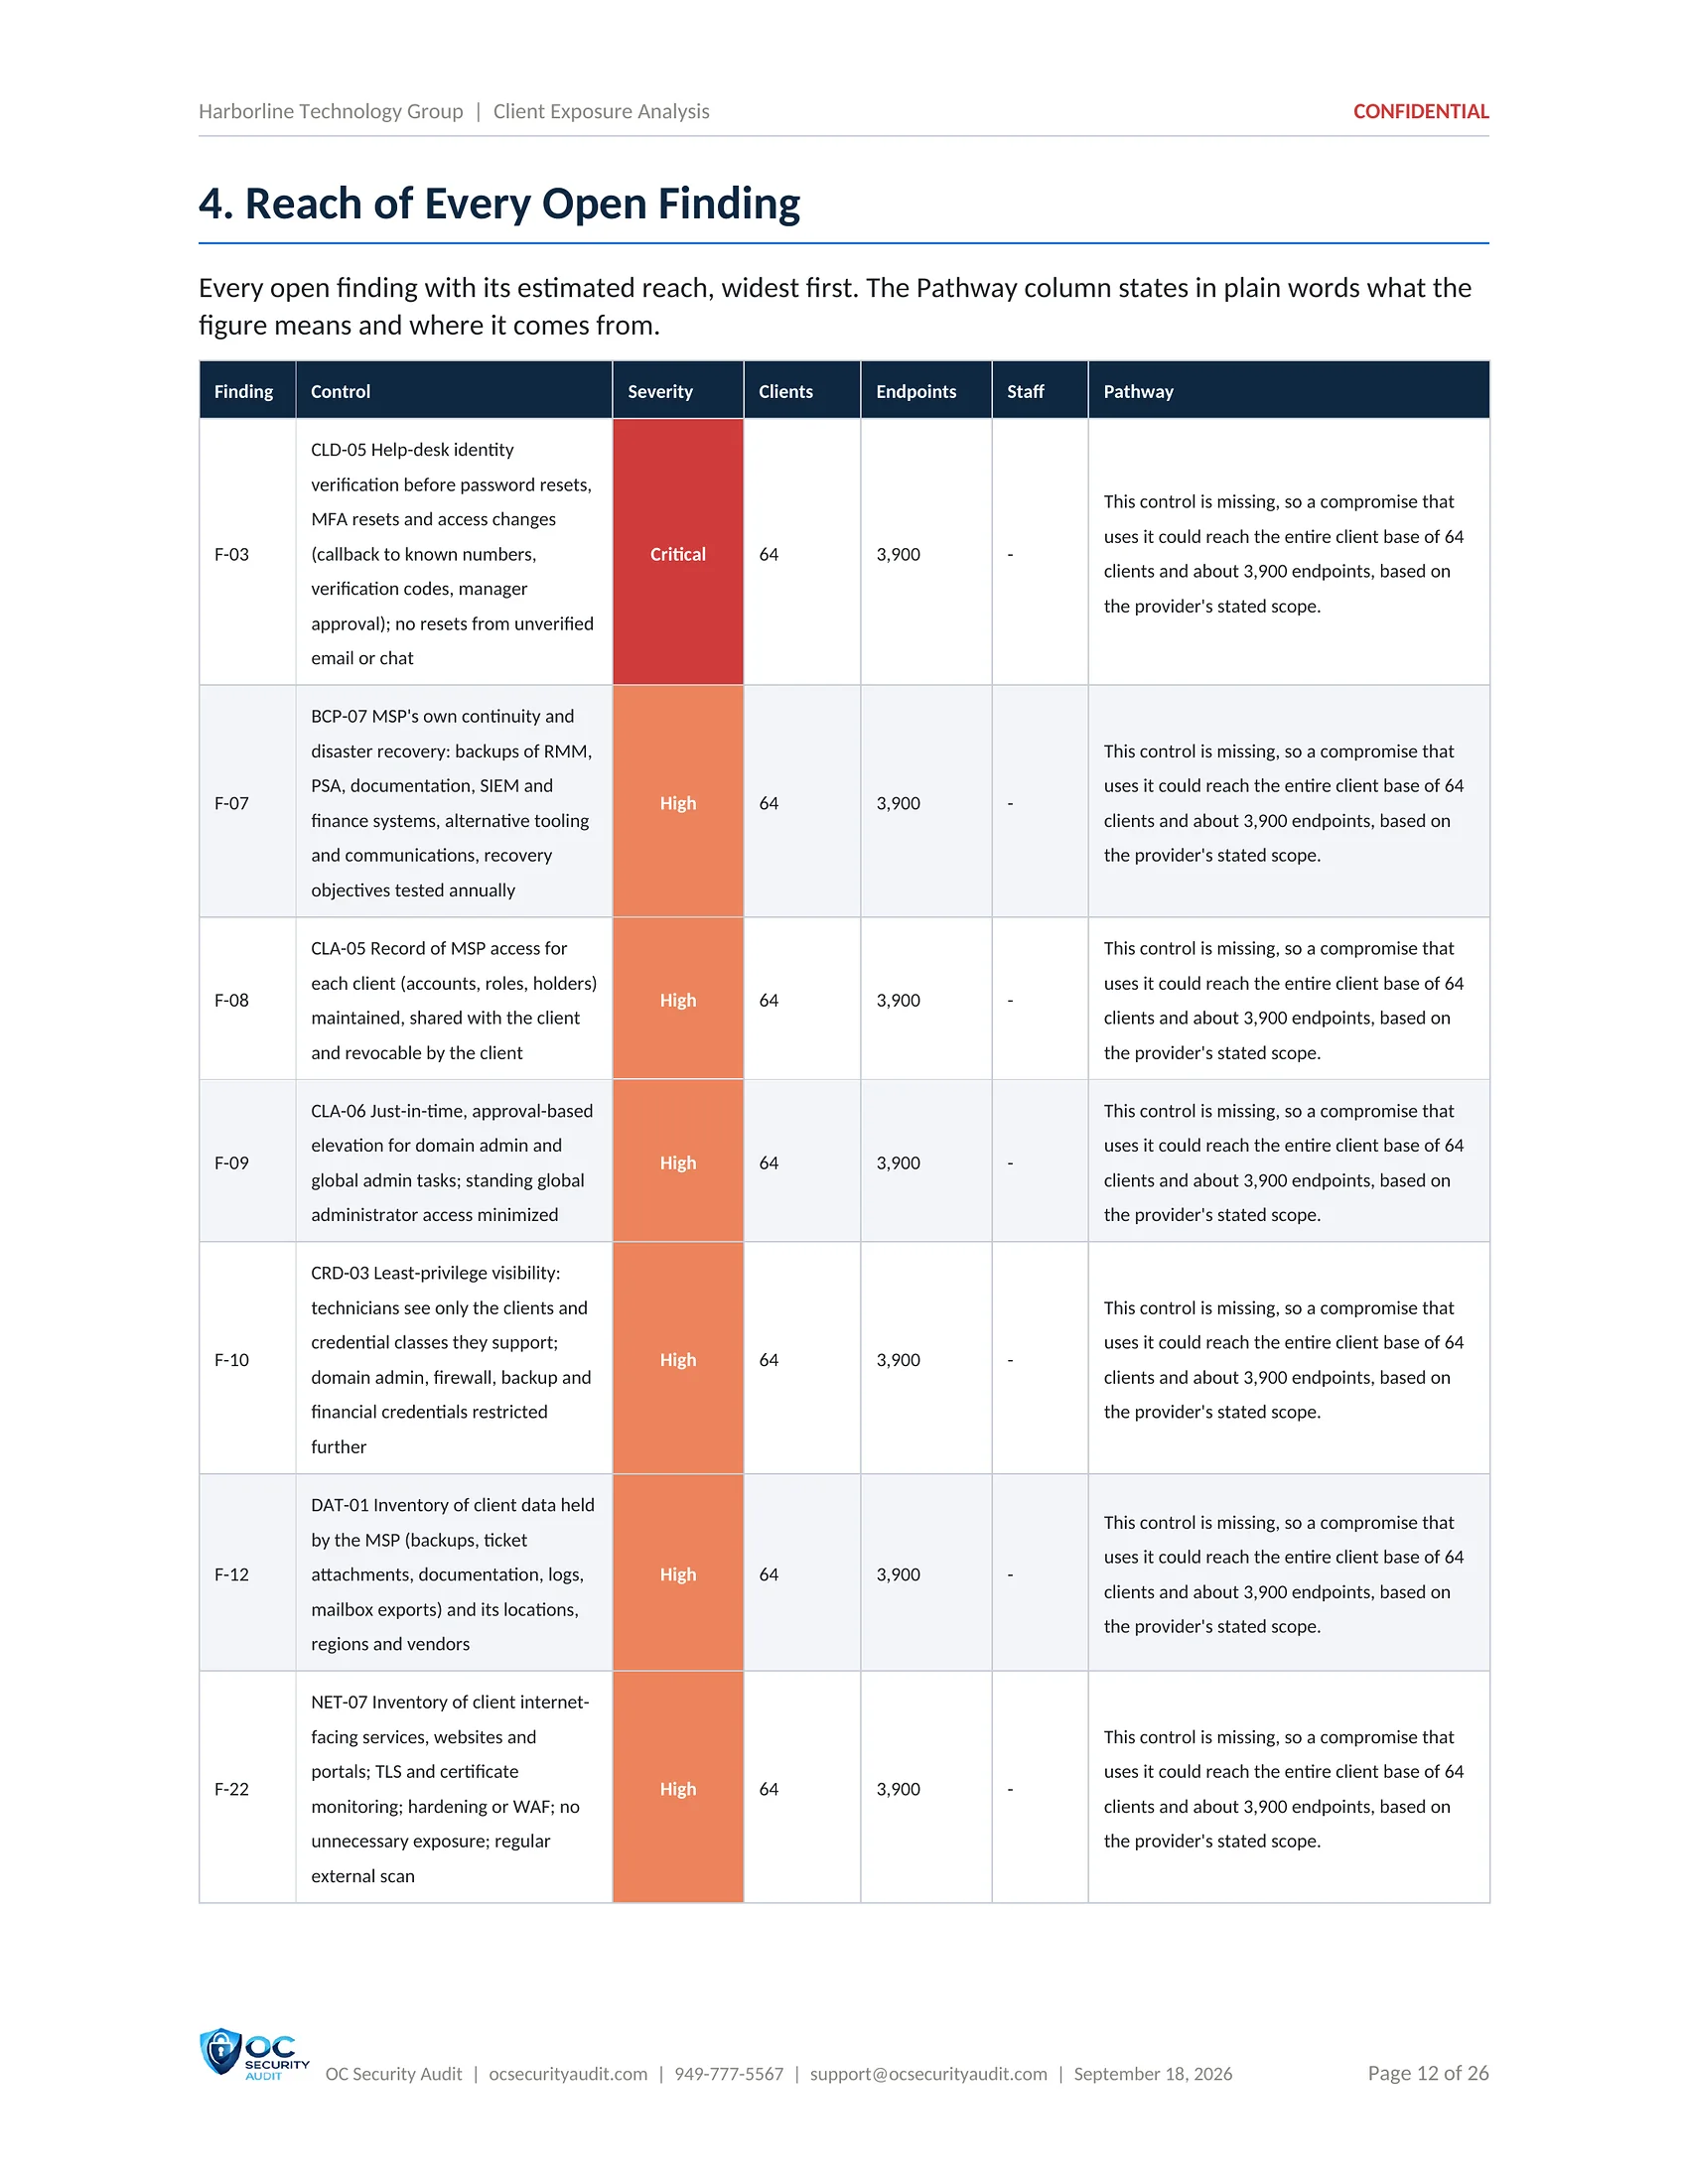
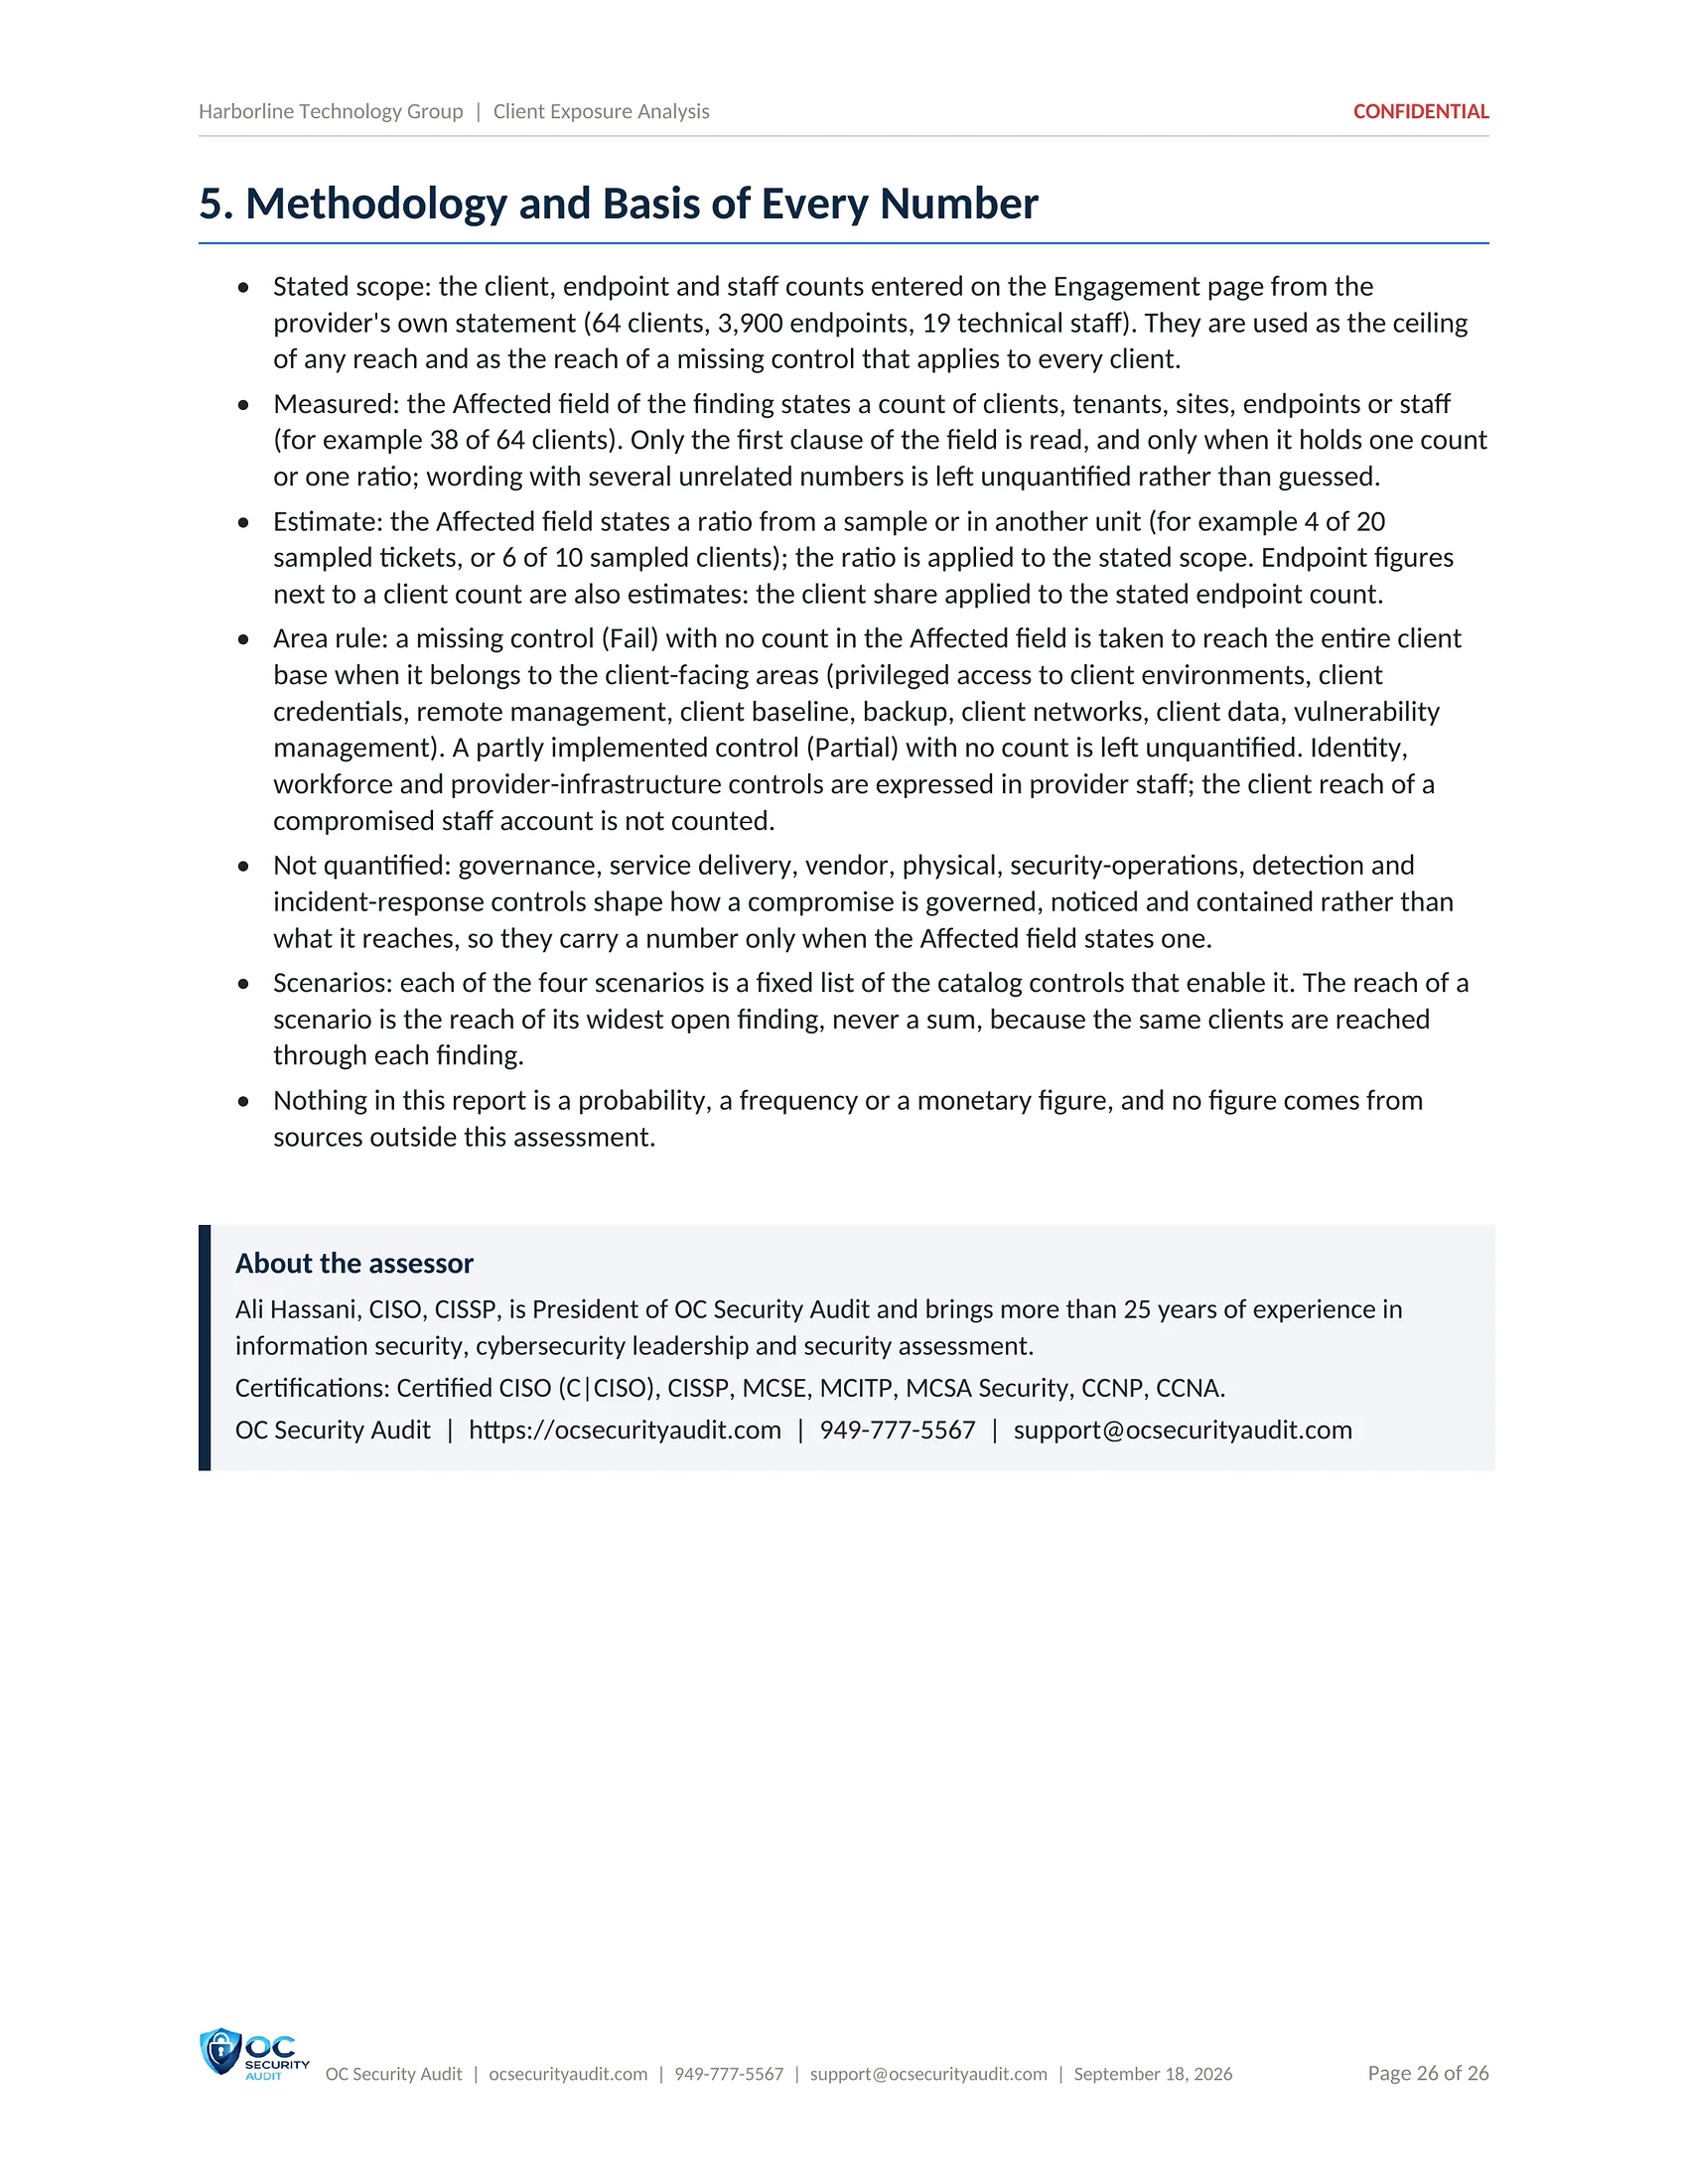
The report that is specific to auditing a provider. It answers one question for leadership: if a weakness found in the audit were used by an attacker, how far could it reach? Each open finding is expressed in clients, endpoints and staff, with the basis of every number stated.
Leadership, insurers and large clients who want to understand concentration risk.
What is included
- Purpose and method
- Summary of the widest-reaching findings
- Four MSP compromise scenarios
- Reach of every open finding
- Methodology and basis of every number
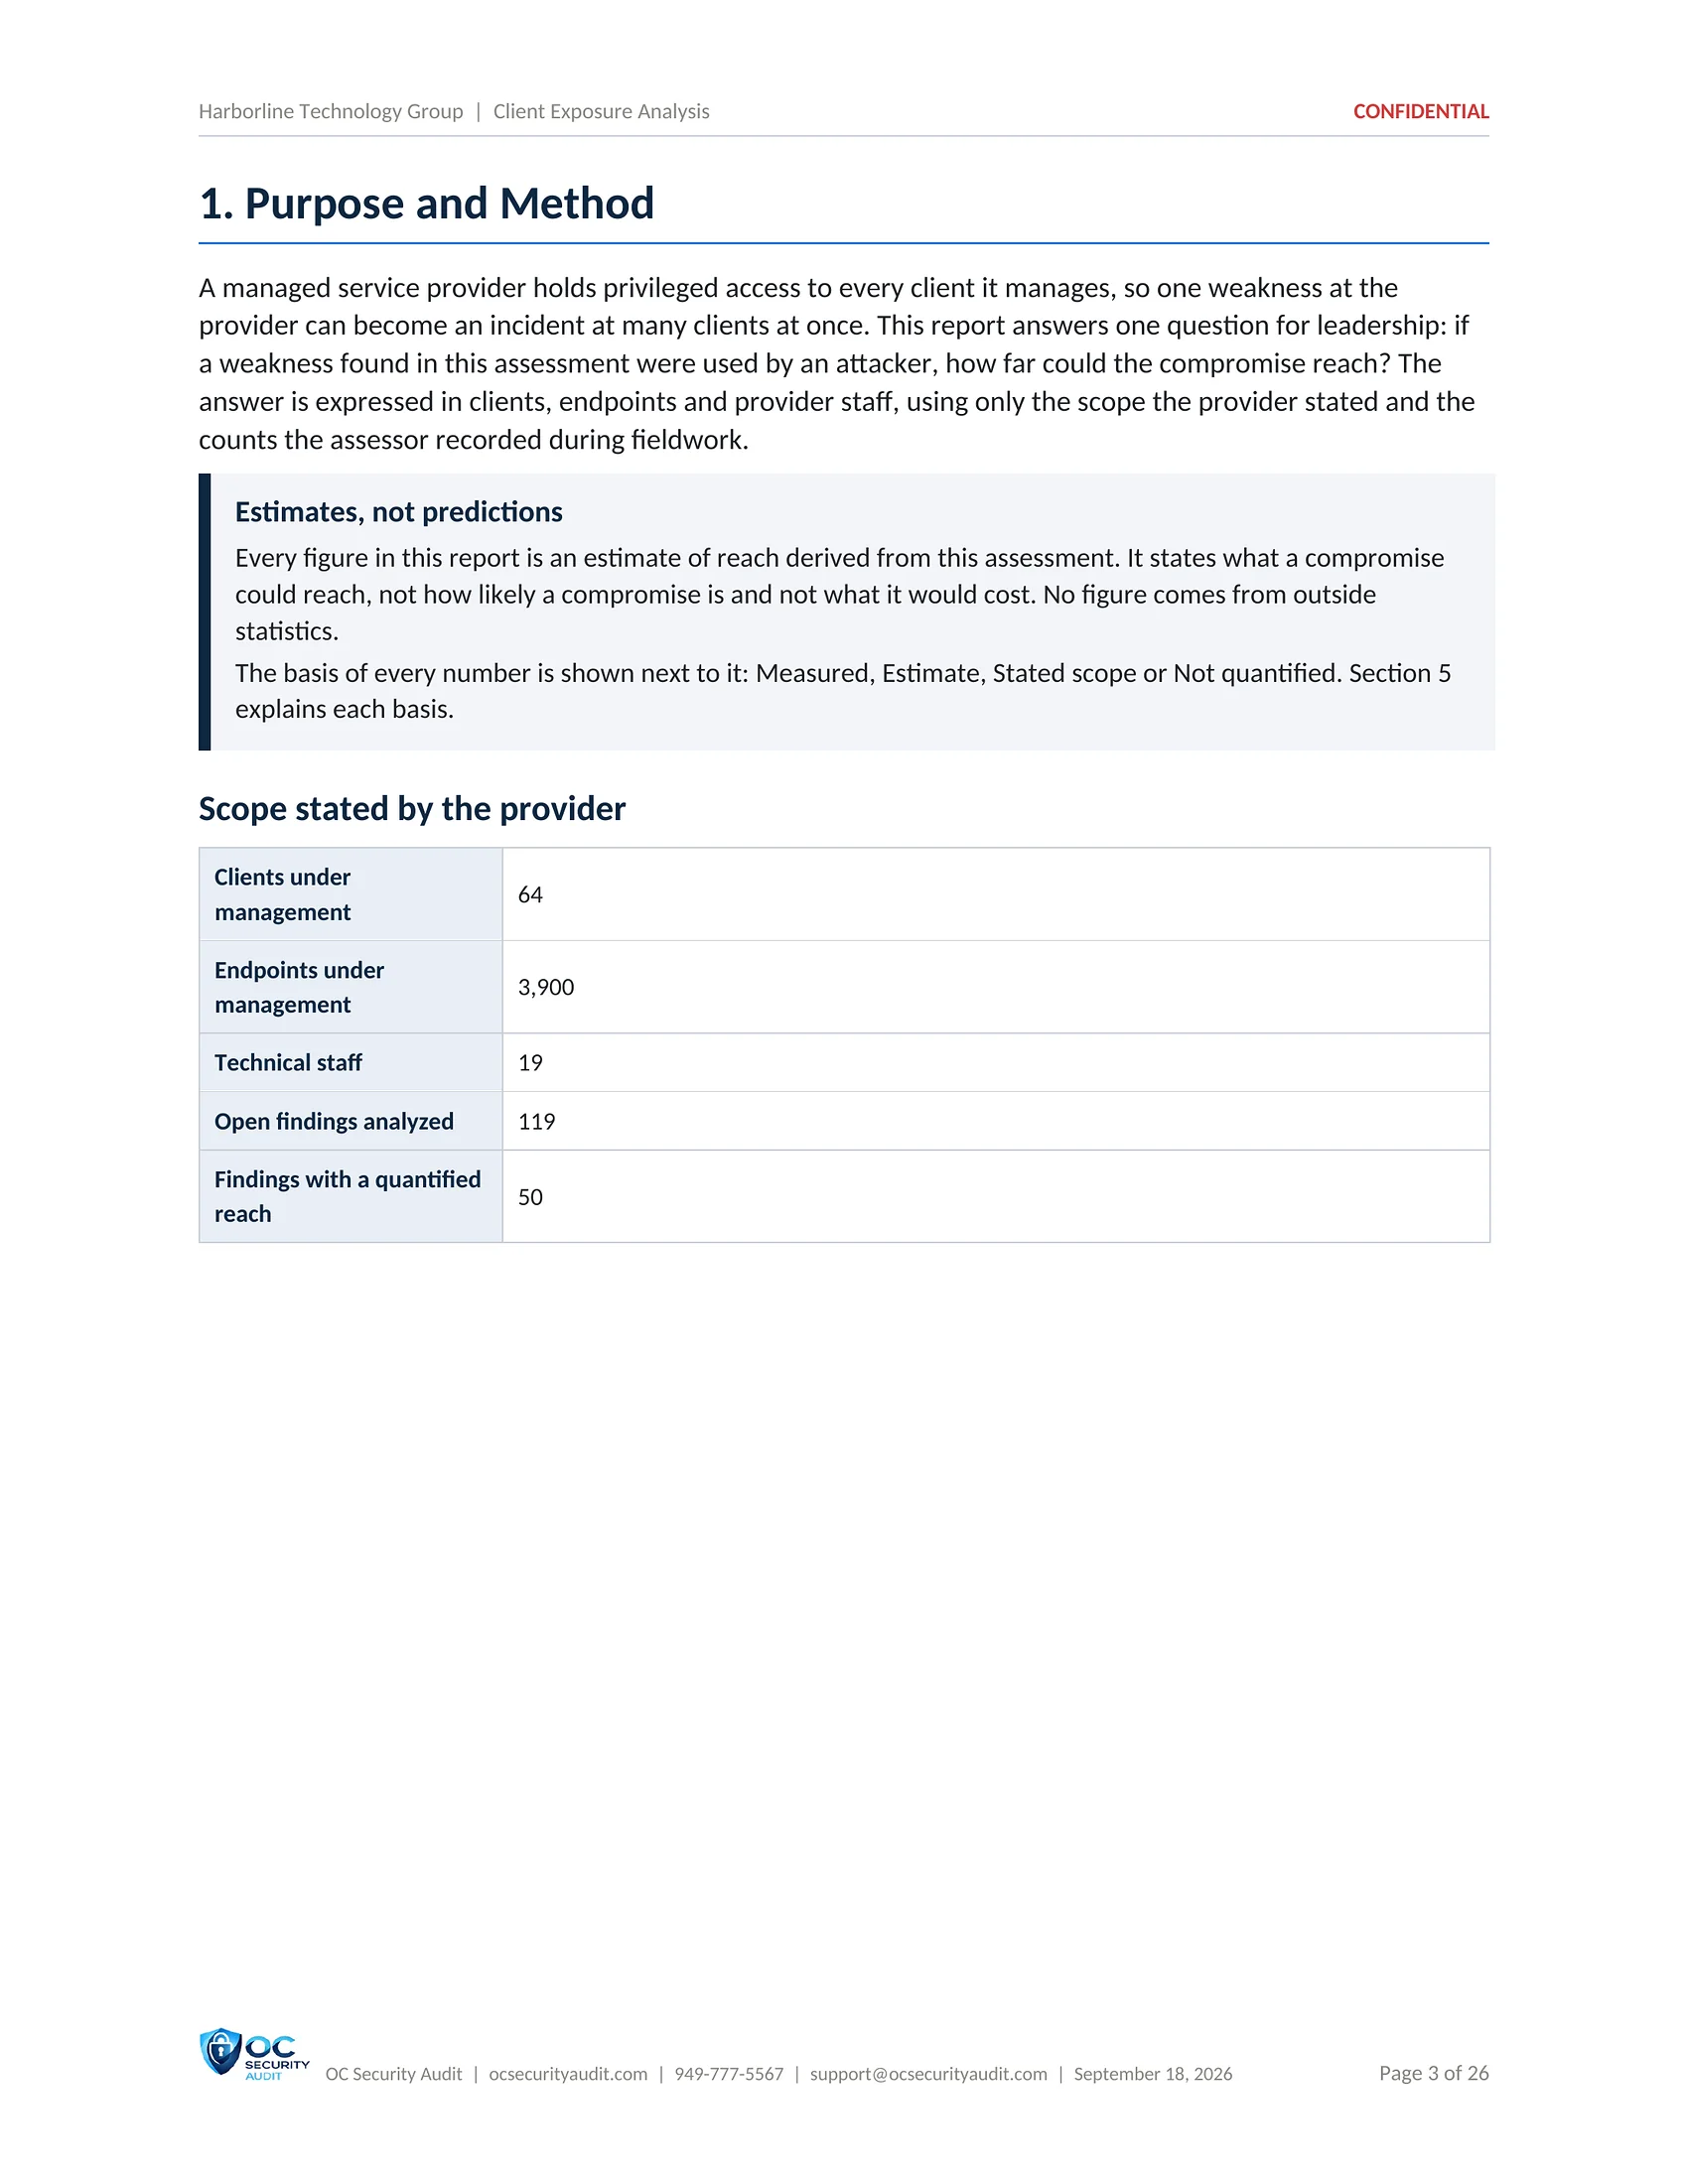
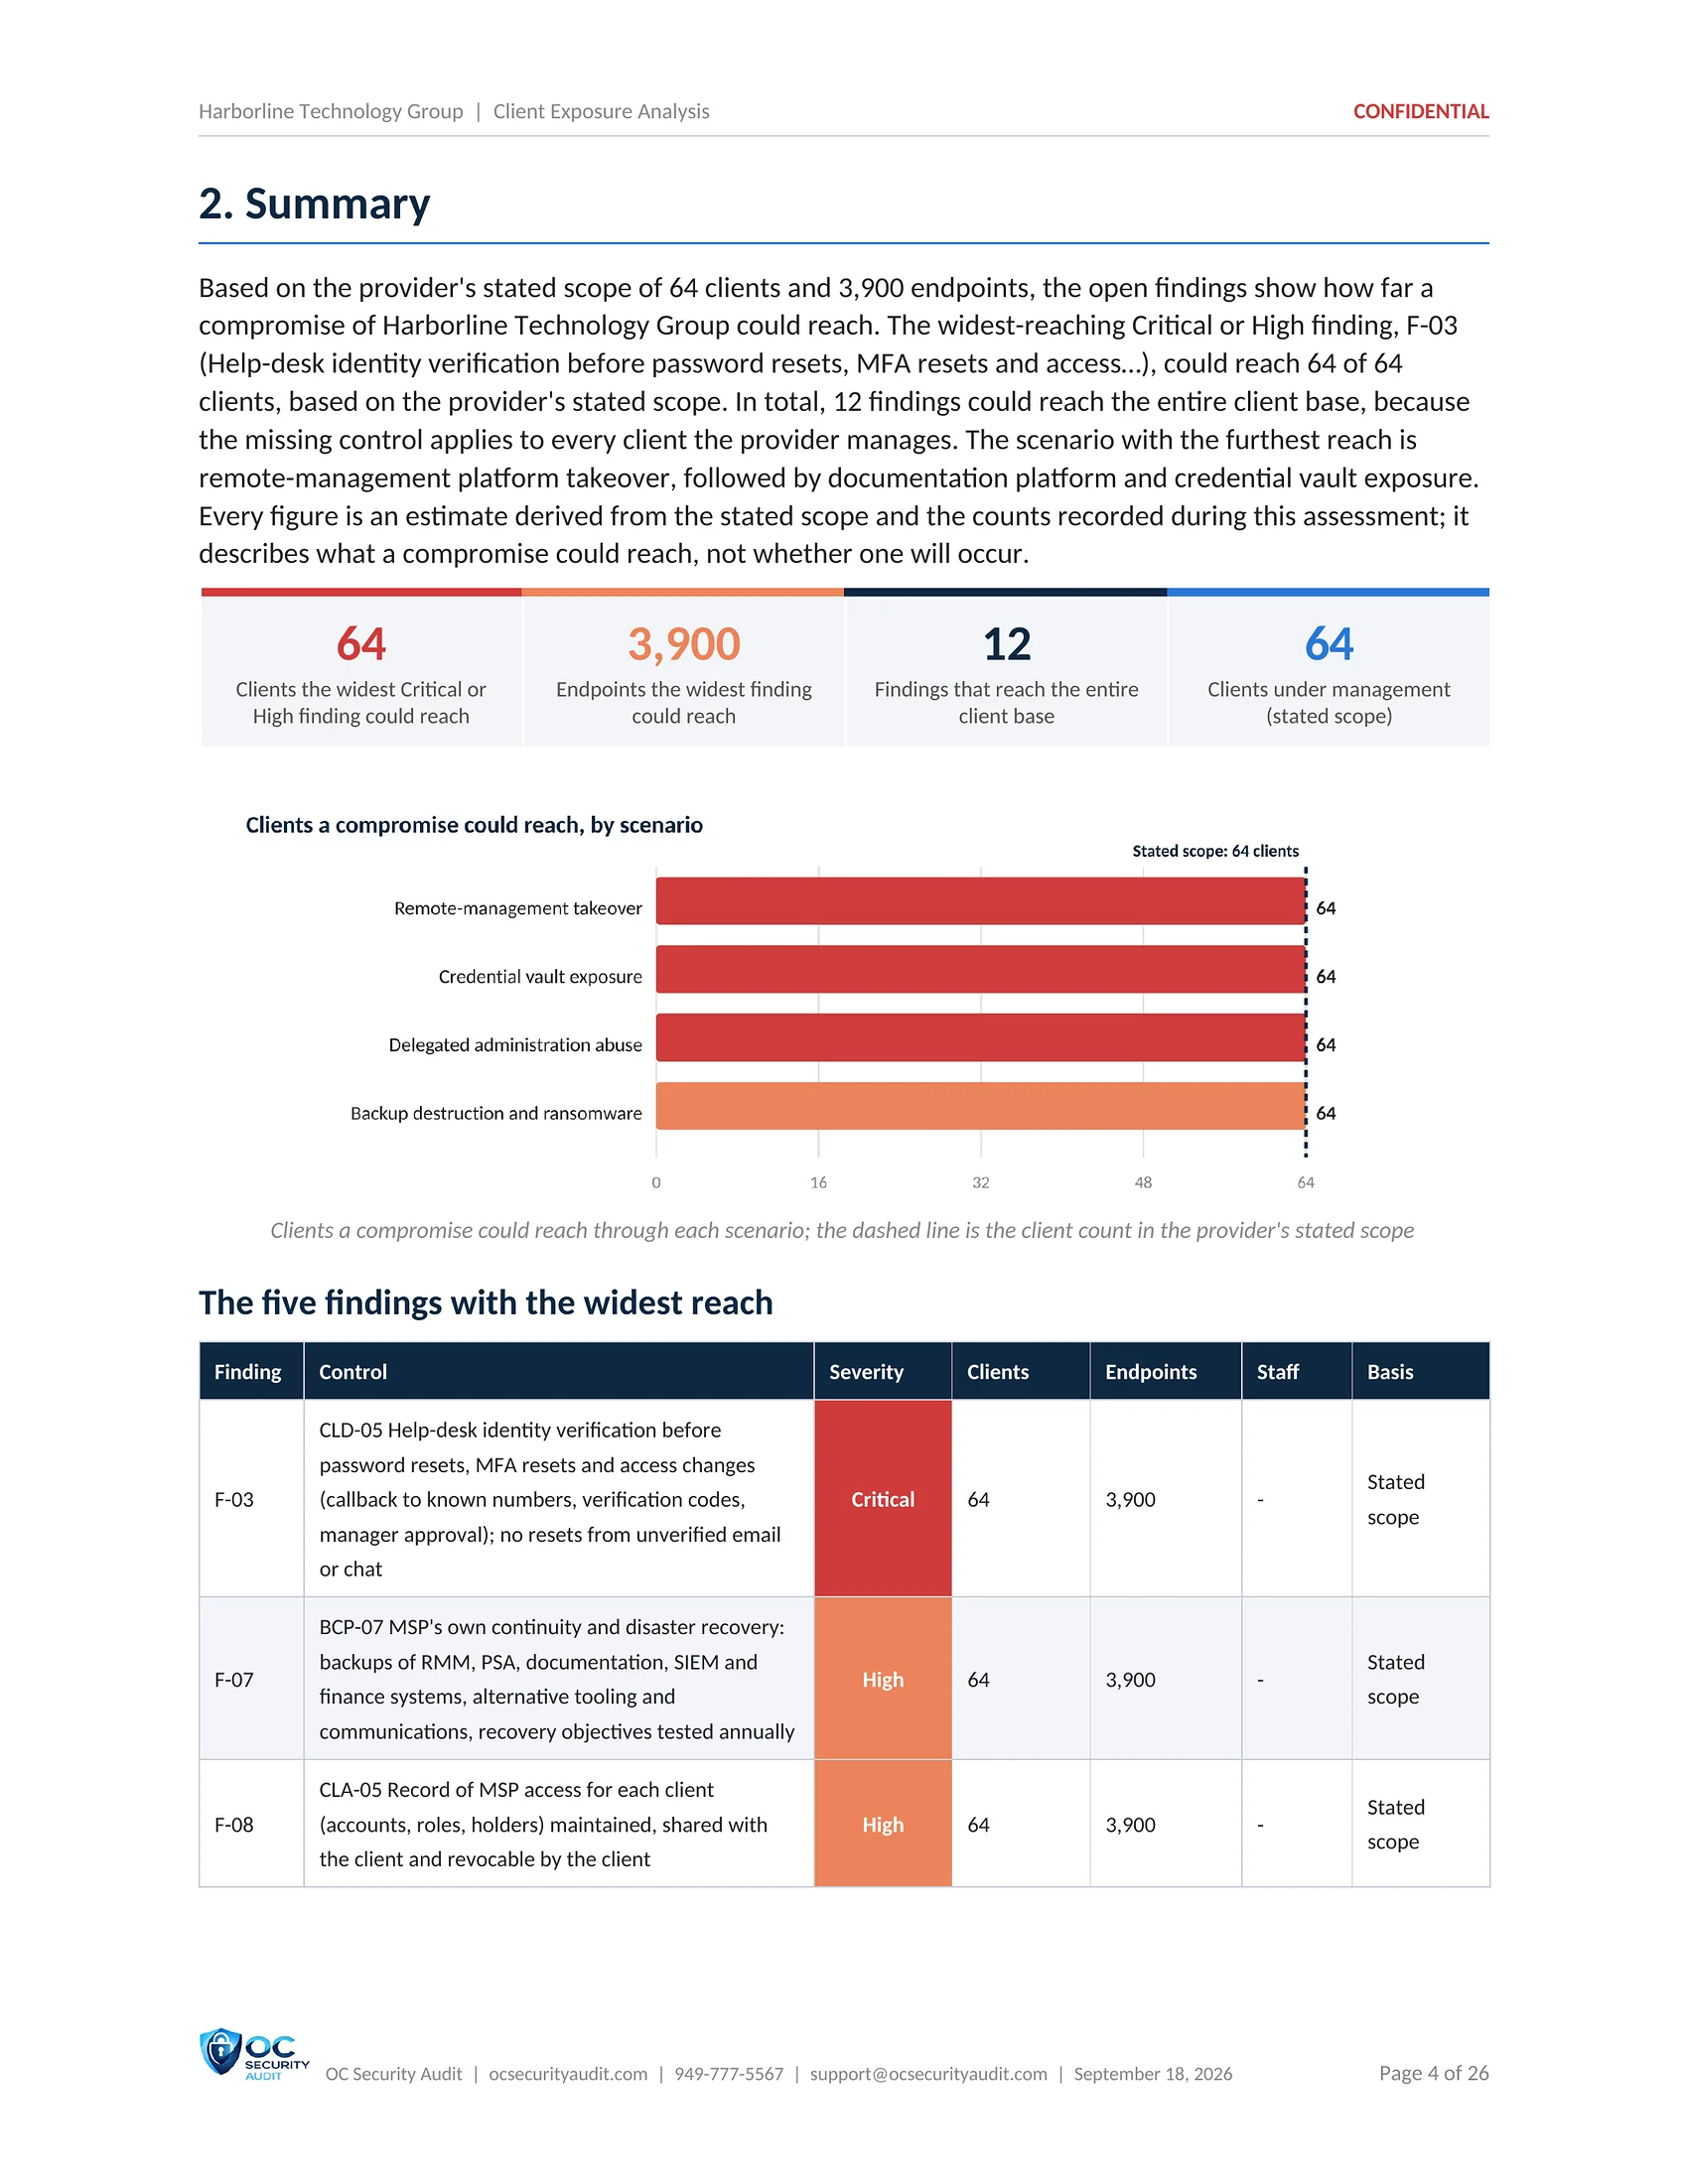
Click the centre page to open it full size and zoom in.
PDF and Word · 32 pages
Certification Readiness
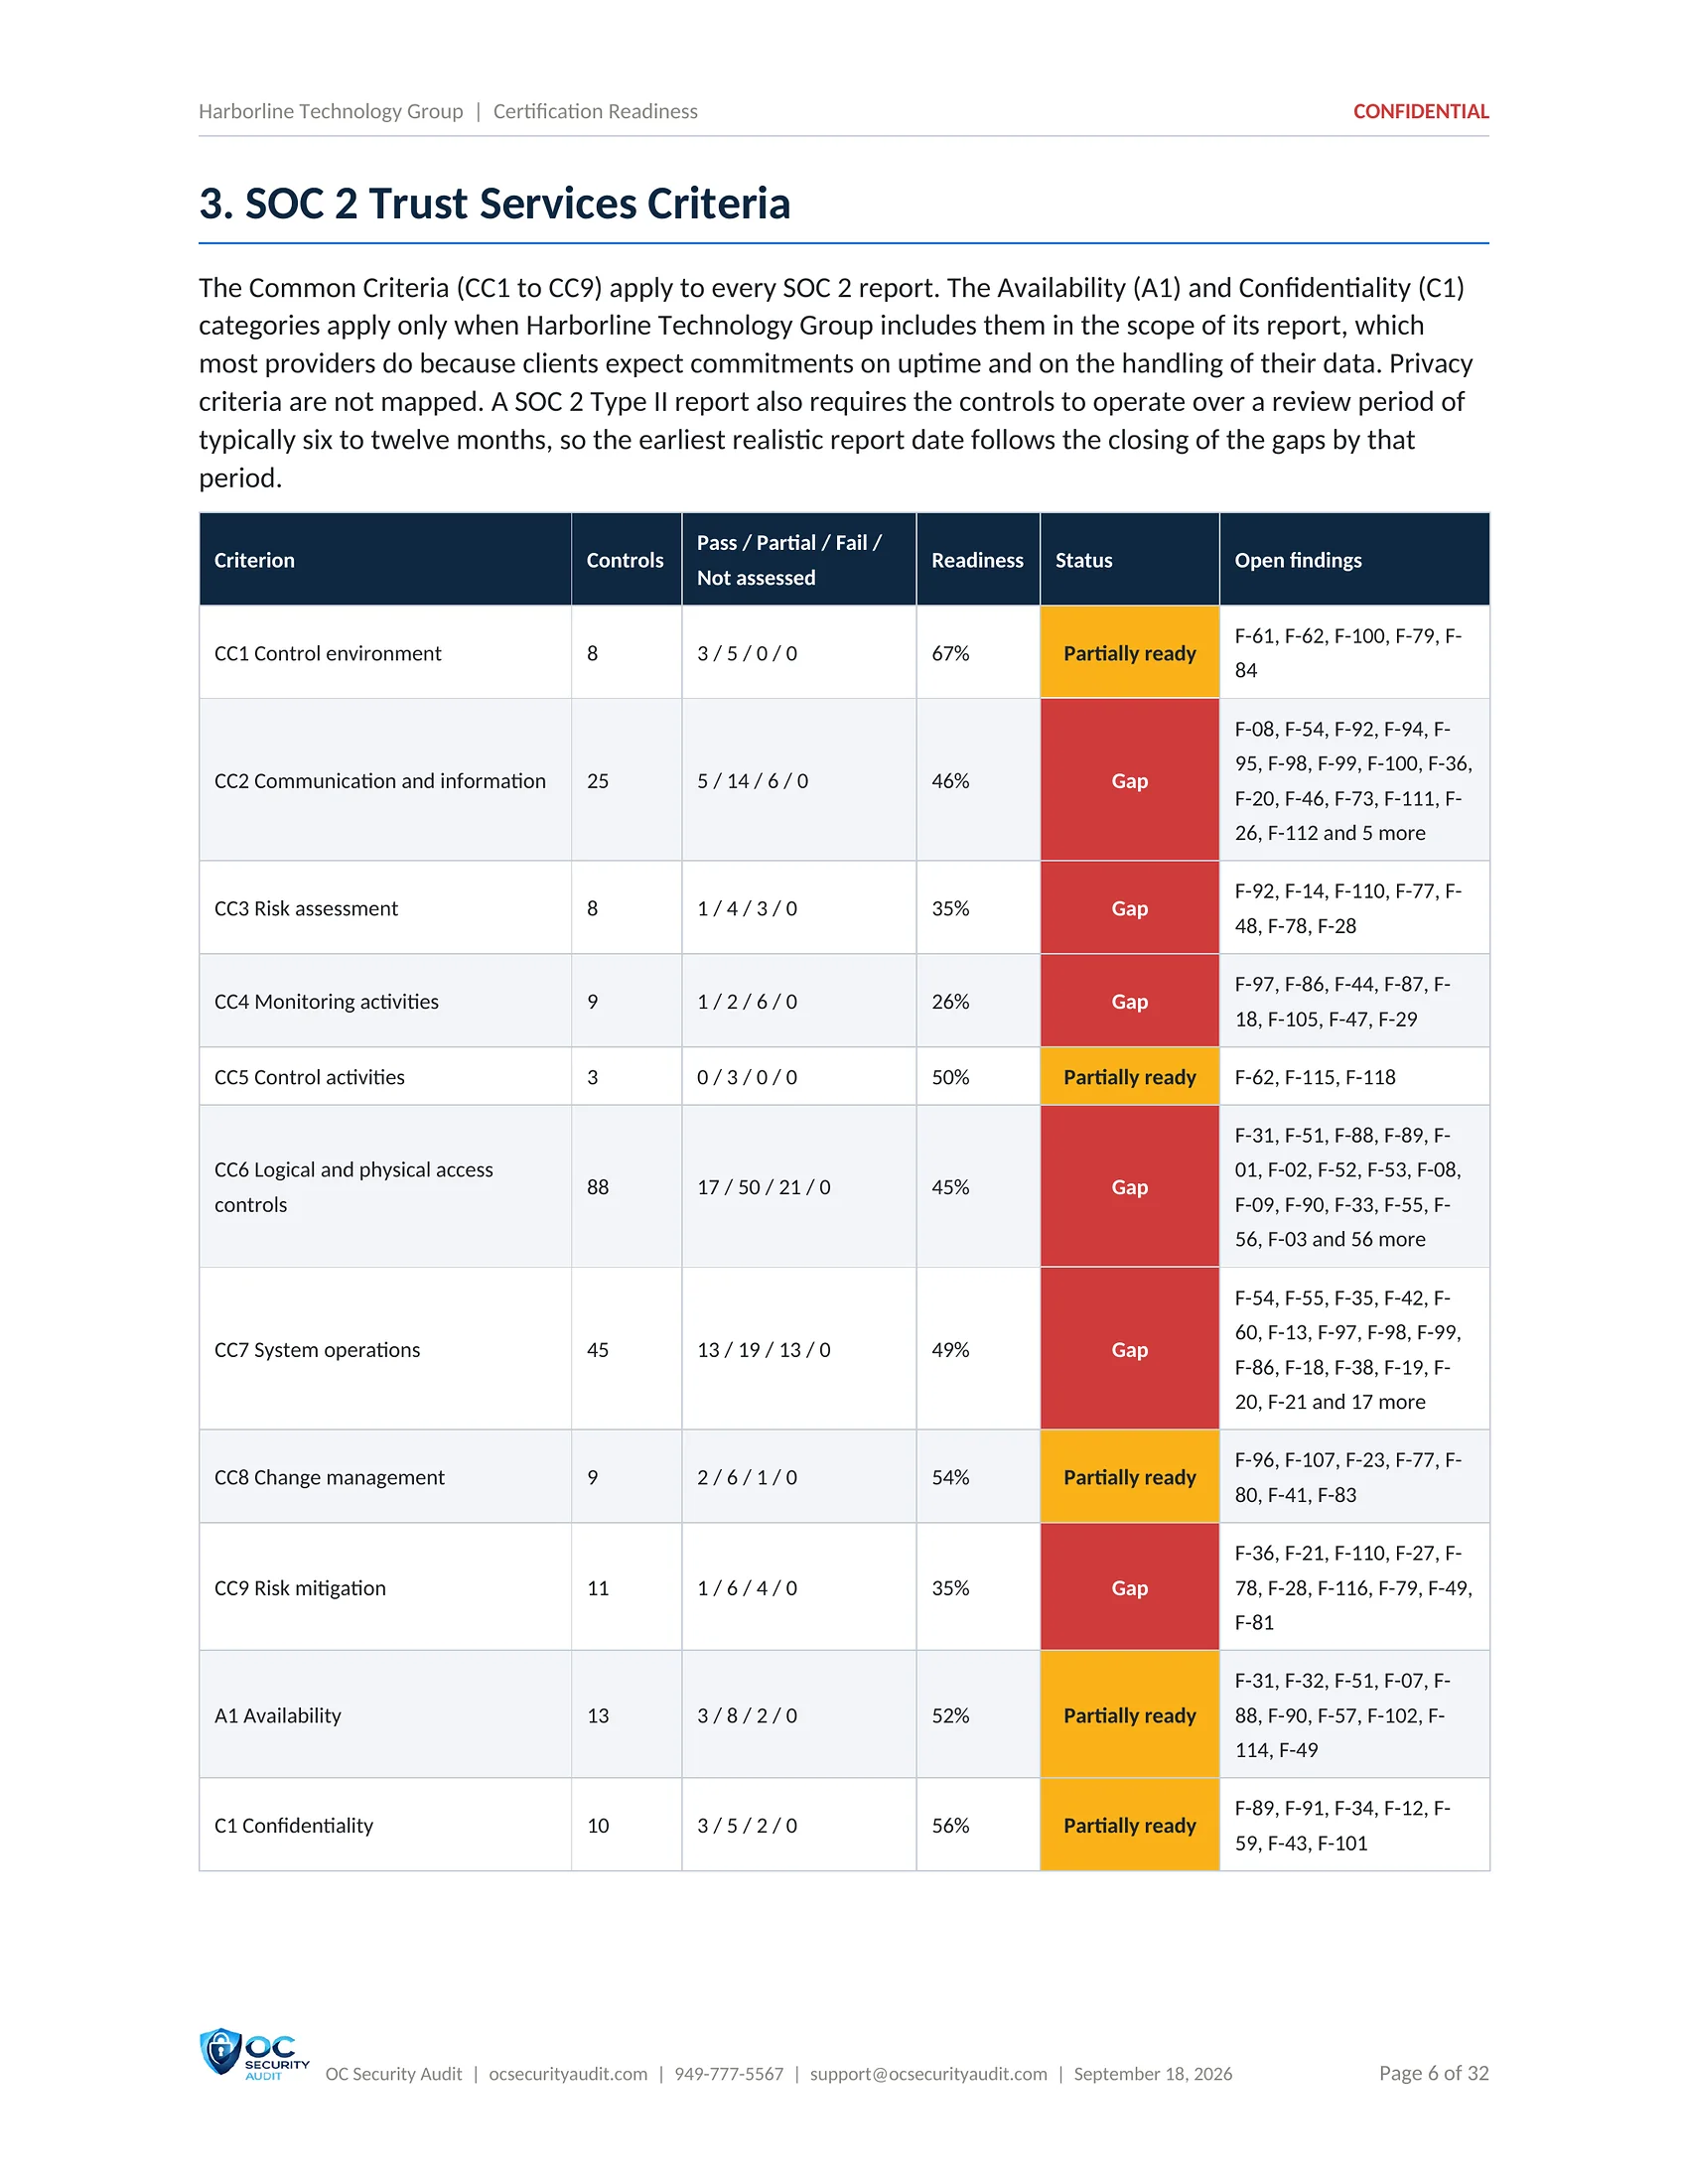
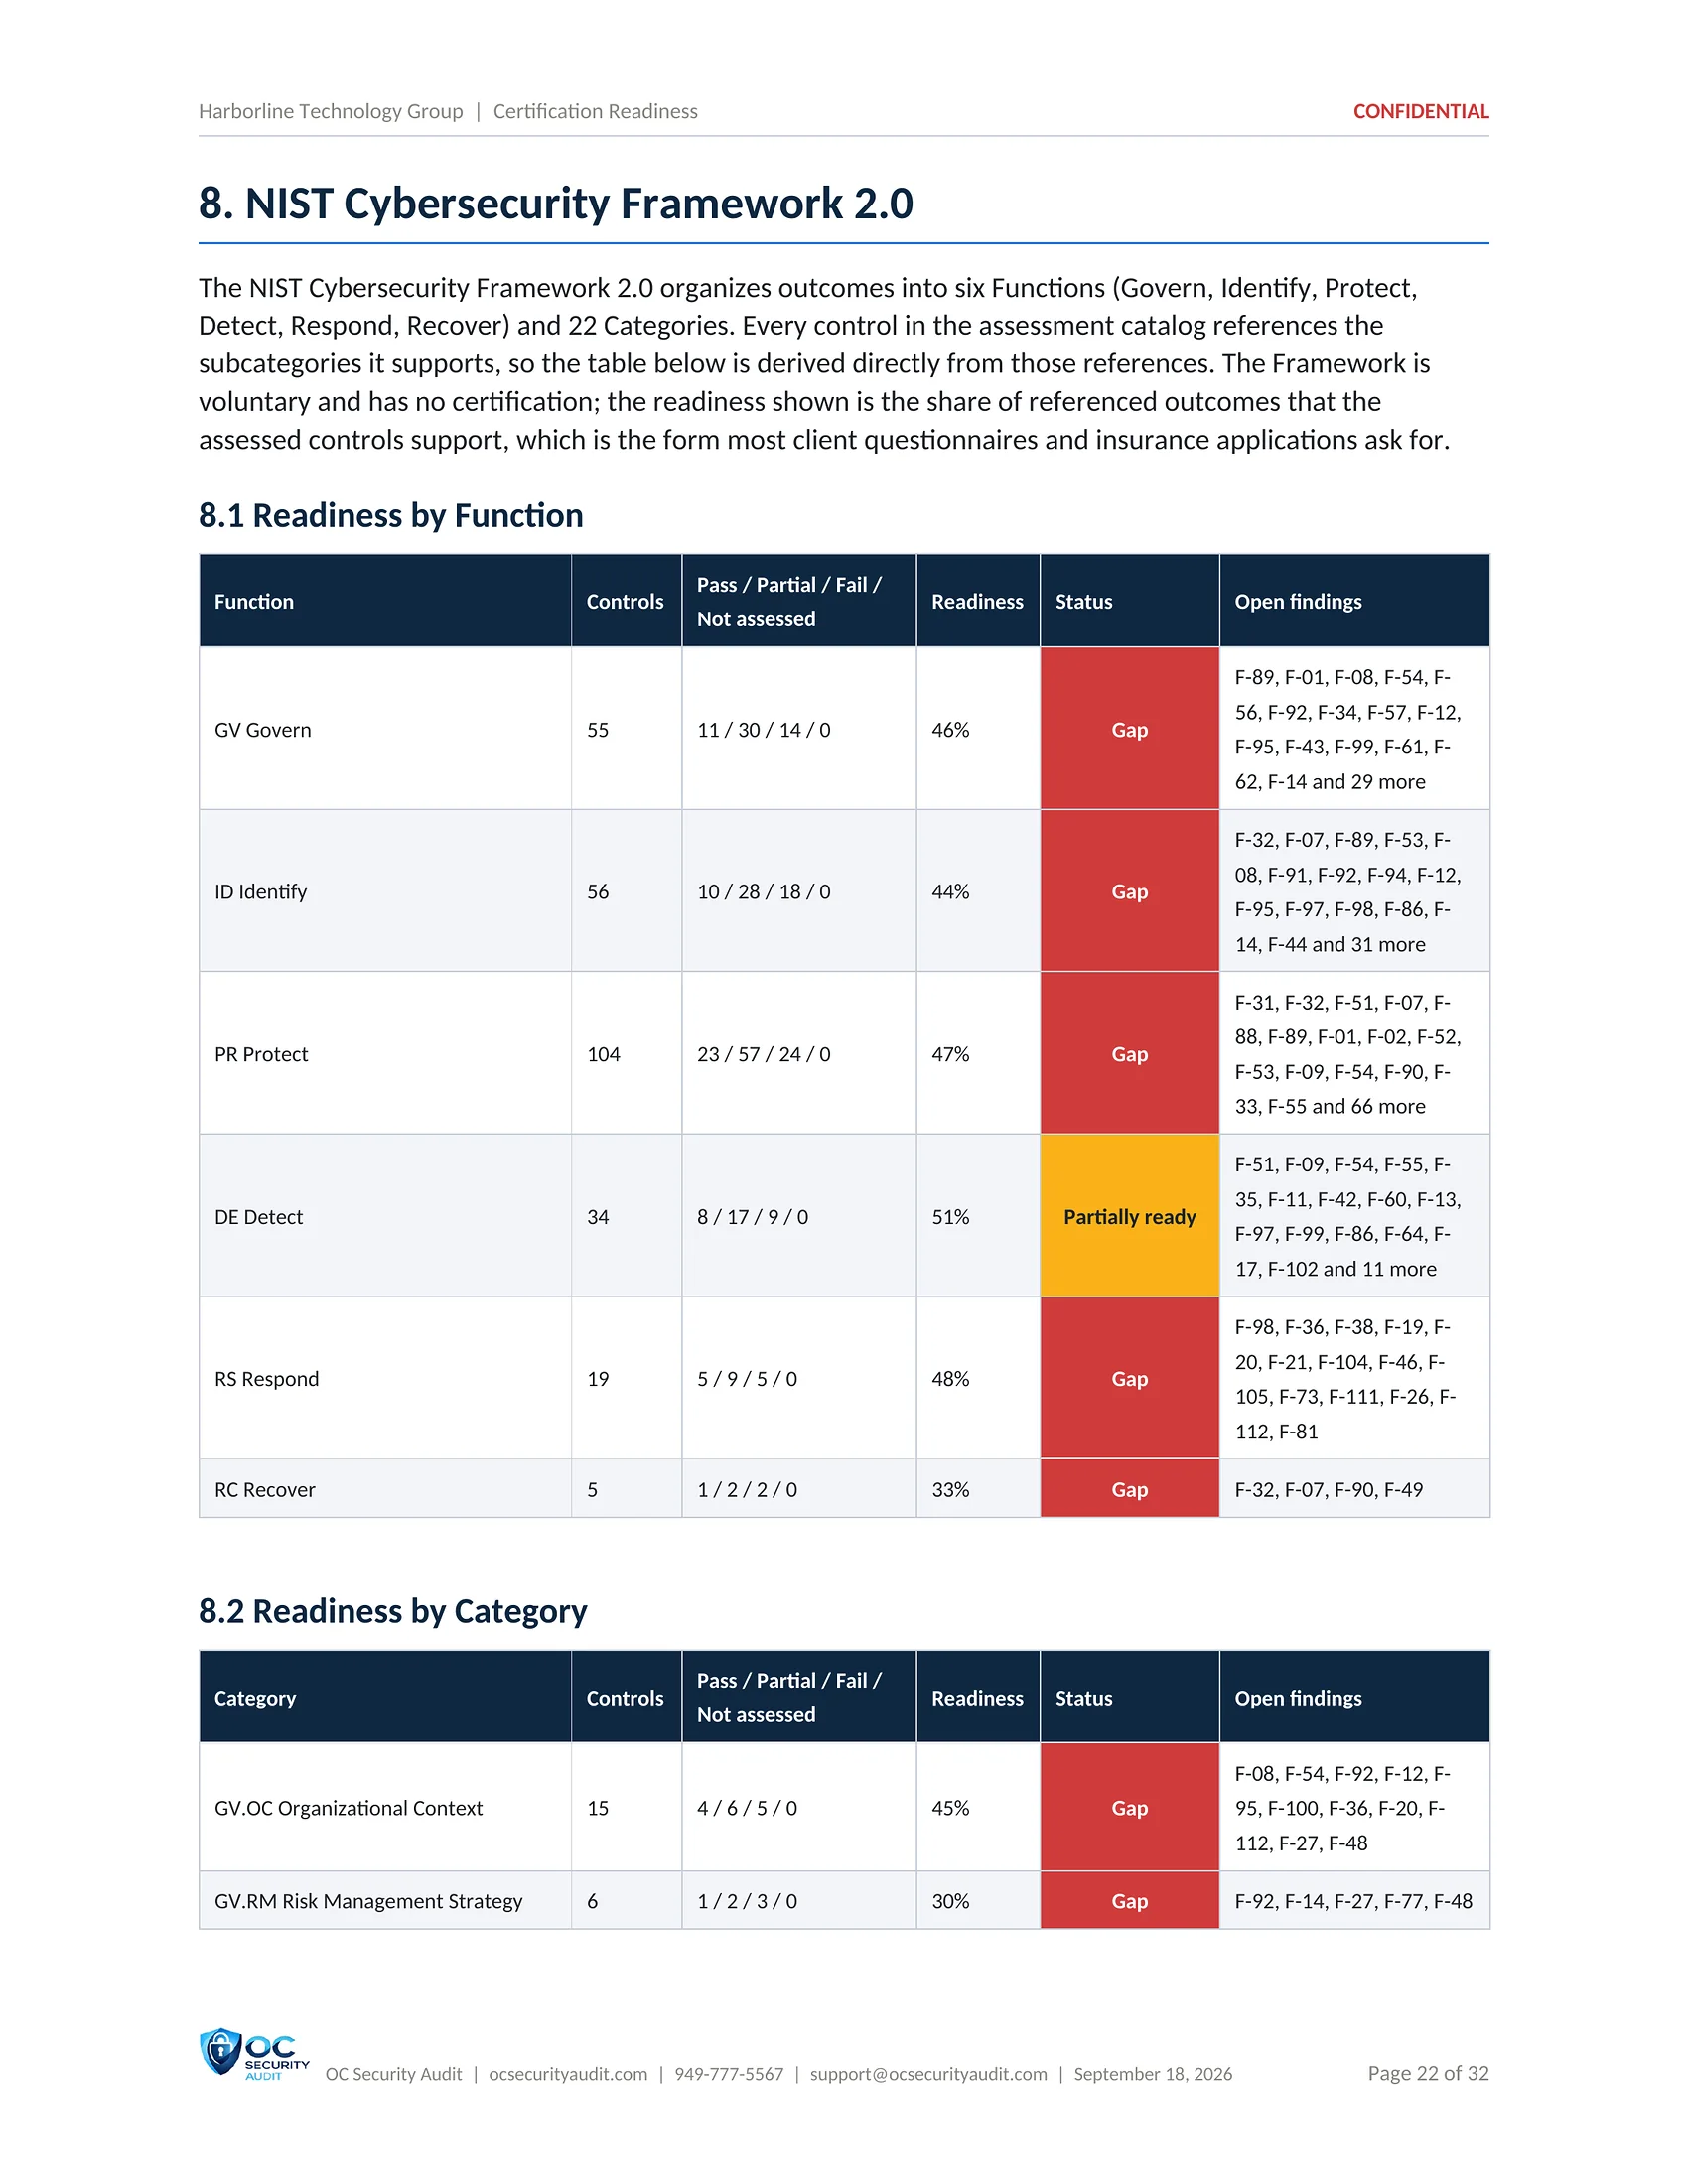
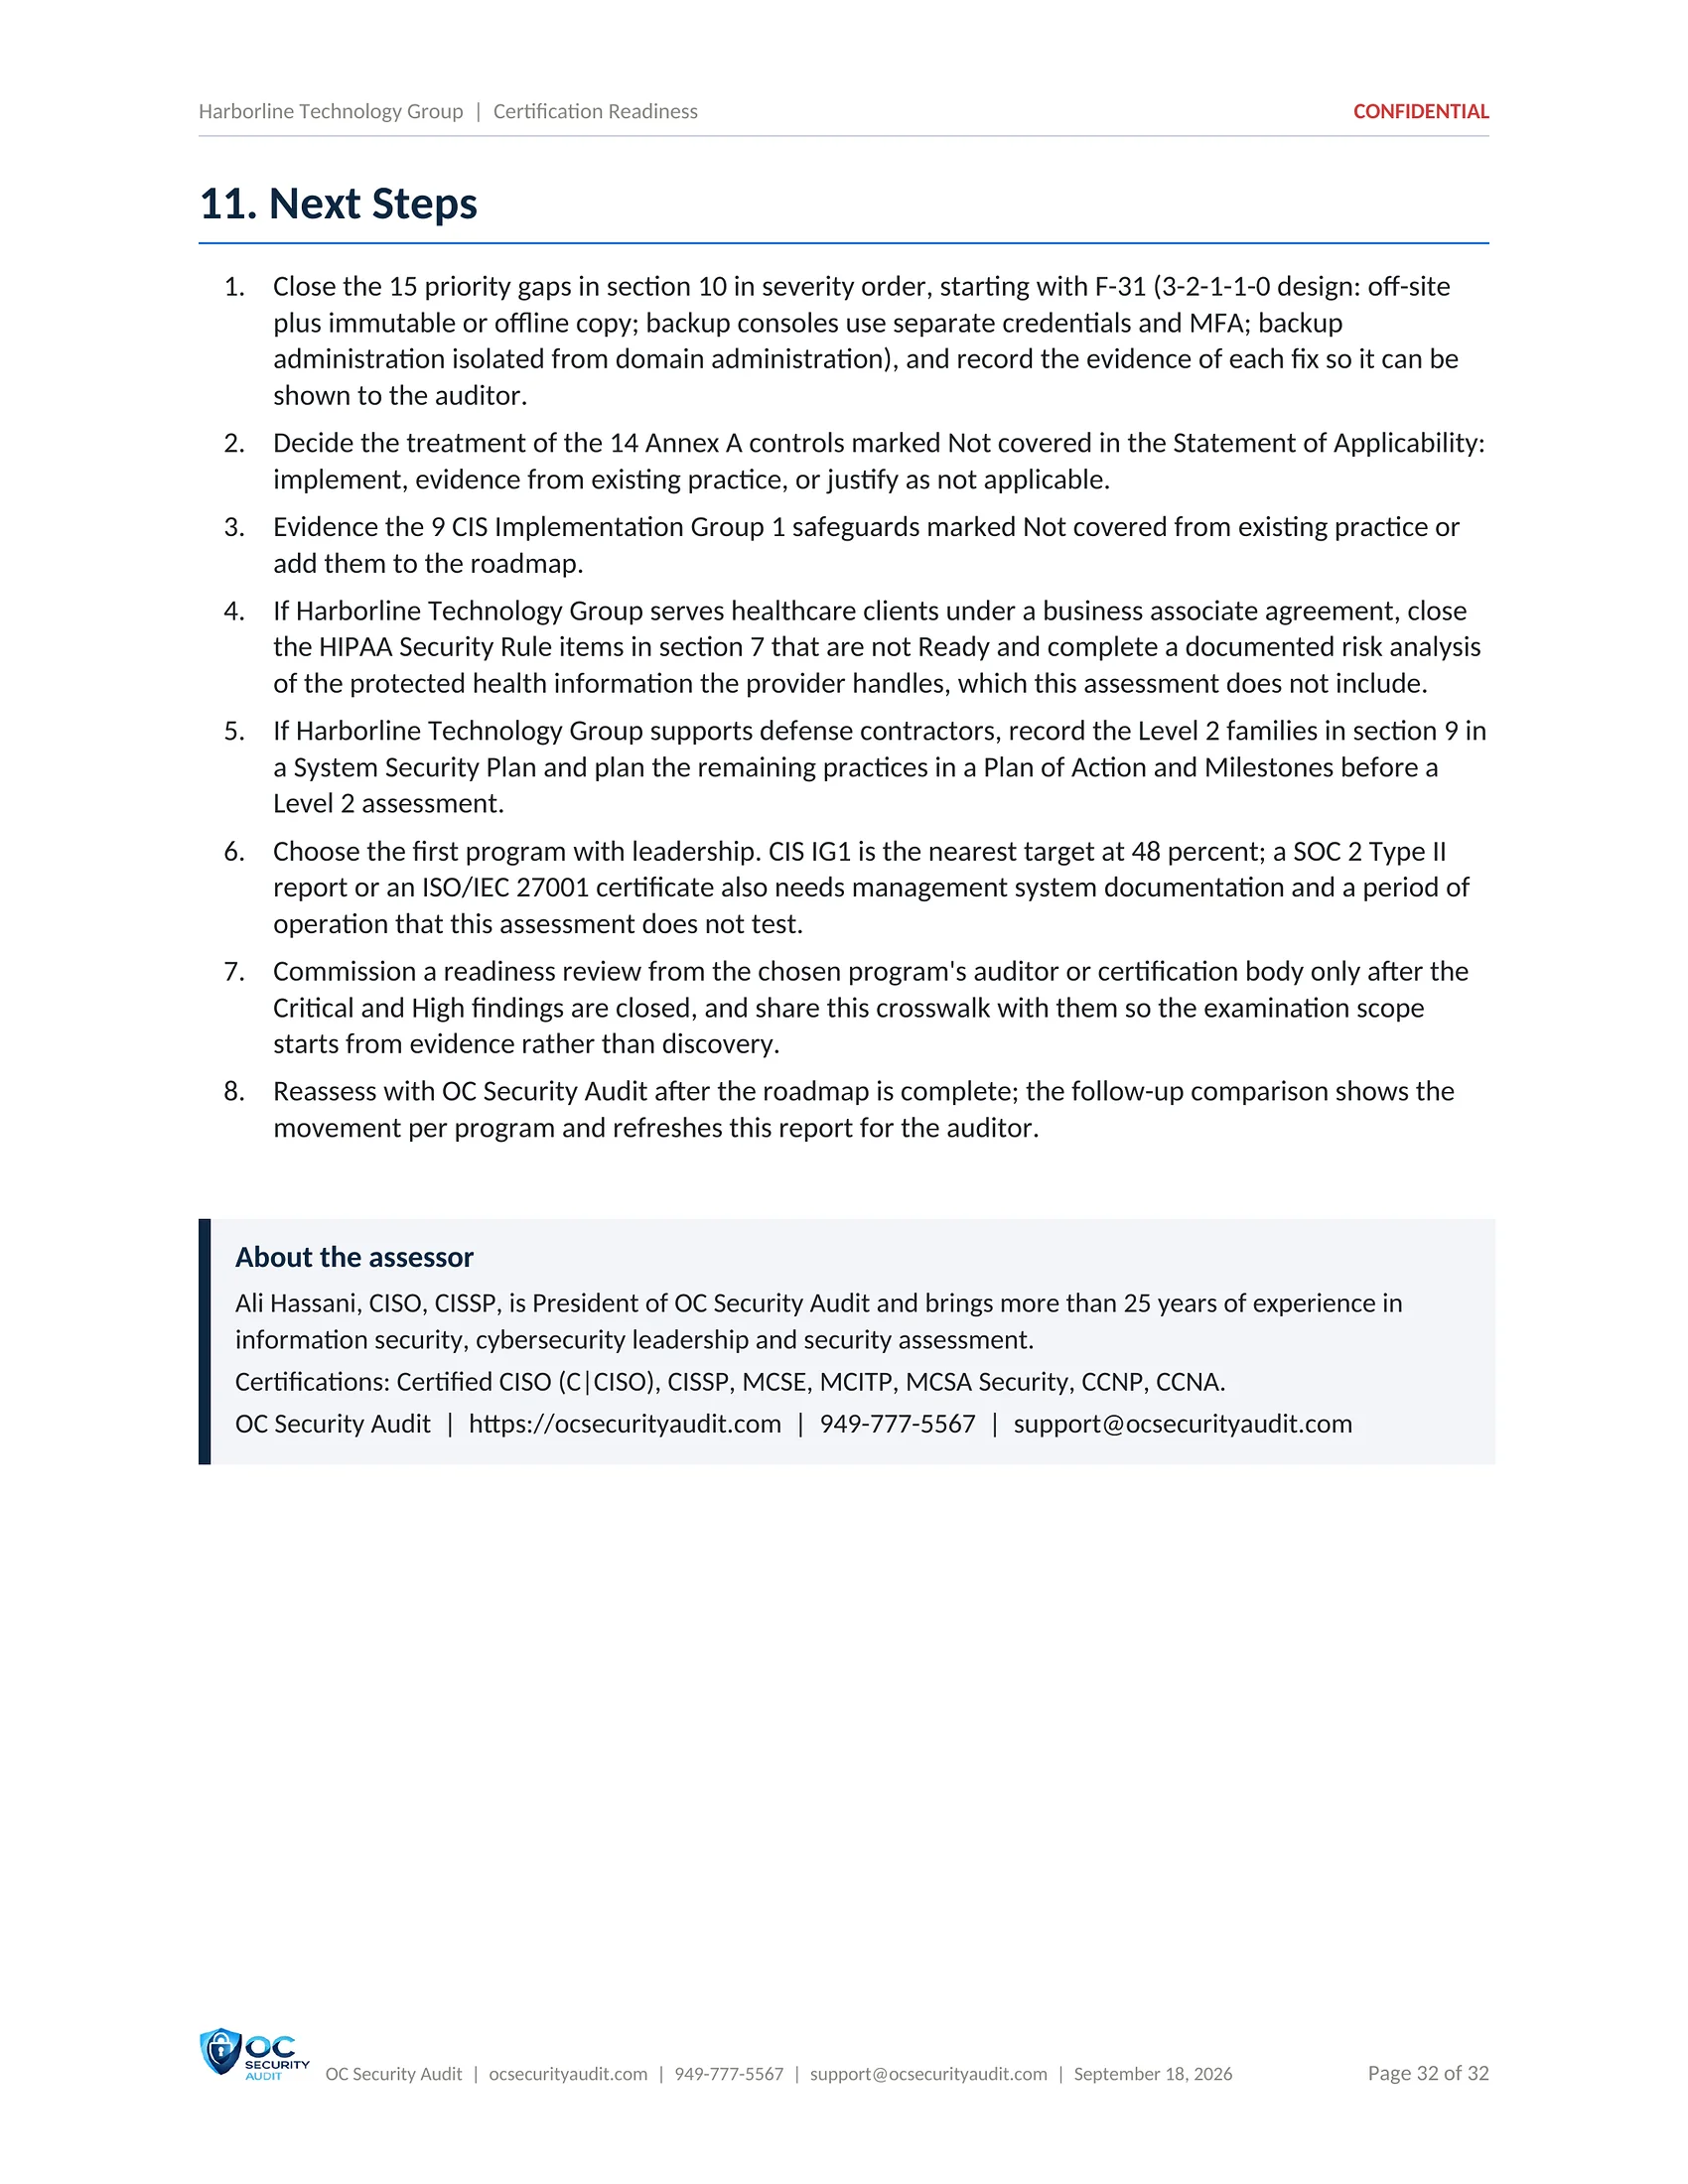
A readiness indicator for the assurance programs clients ask providers about, calculated from the same control results. It shows readiness by program, by theme and by item, lists the priority gaps and recommends what to close before engaging an auditor. It is not a certification opinion.
Leadership and the compliance lead planning SOC 2, ISO/IEC 27001 or MSP Verify.
What is included
- SOC 2 Trust Services Criteria
- ISO/IEC 27001:2022 Annex A
- MSPAlliance MSP Verify
- CIS Controls v8.1 IG1
- HIPAA Security Rule
- NIST CSF 2.0
- Priority gaps and next steps
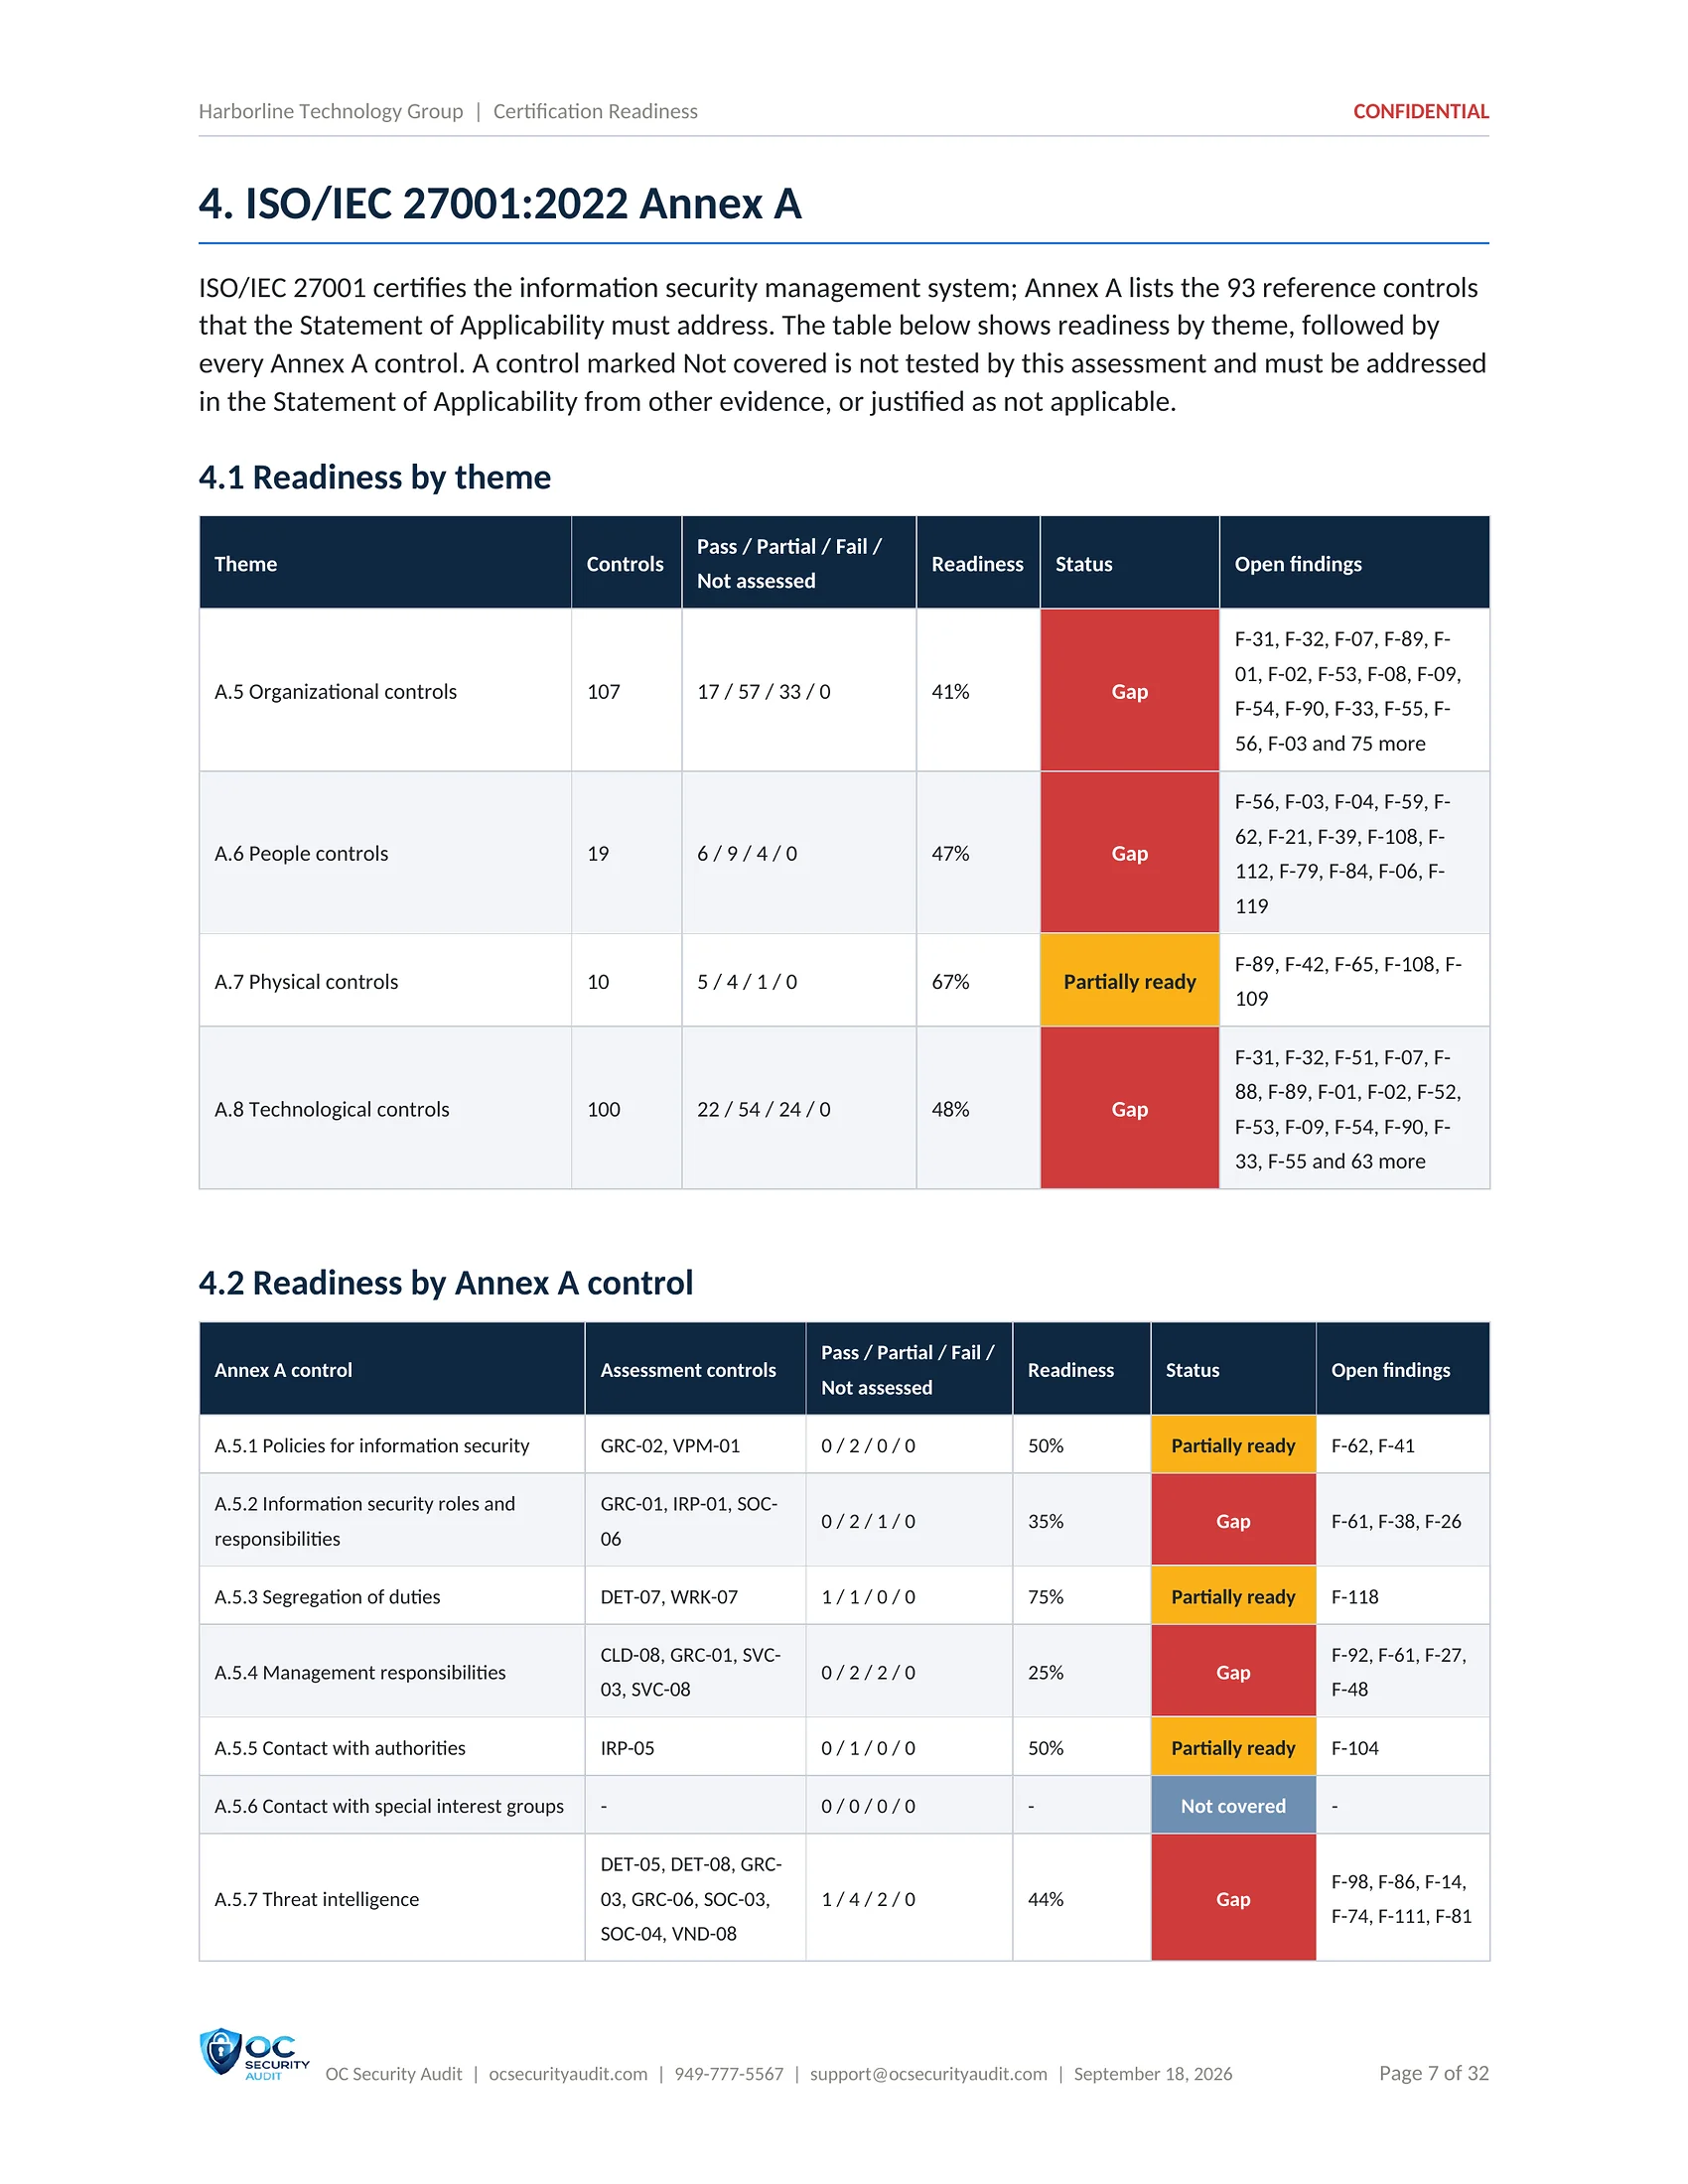
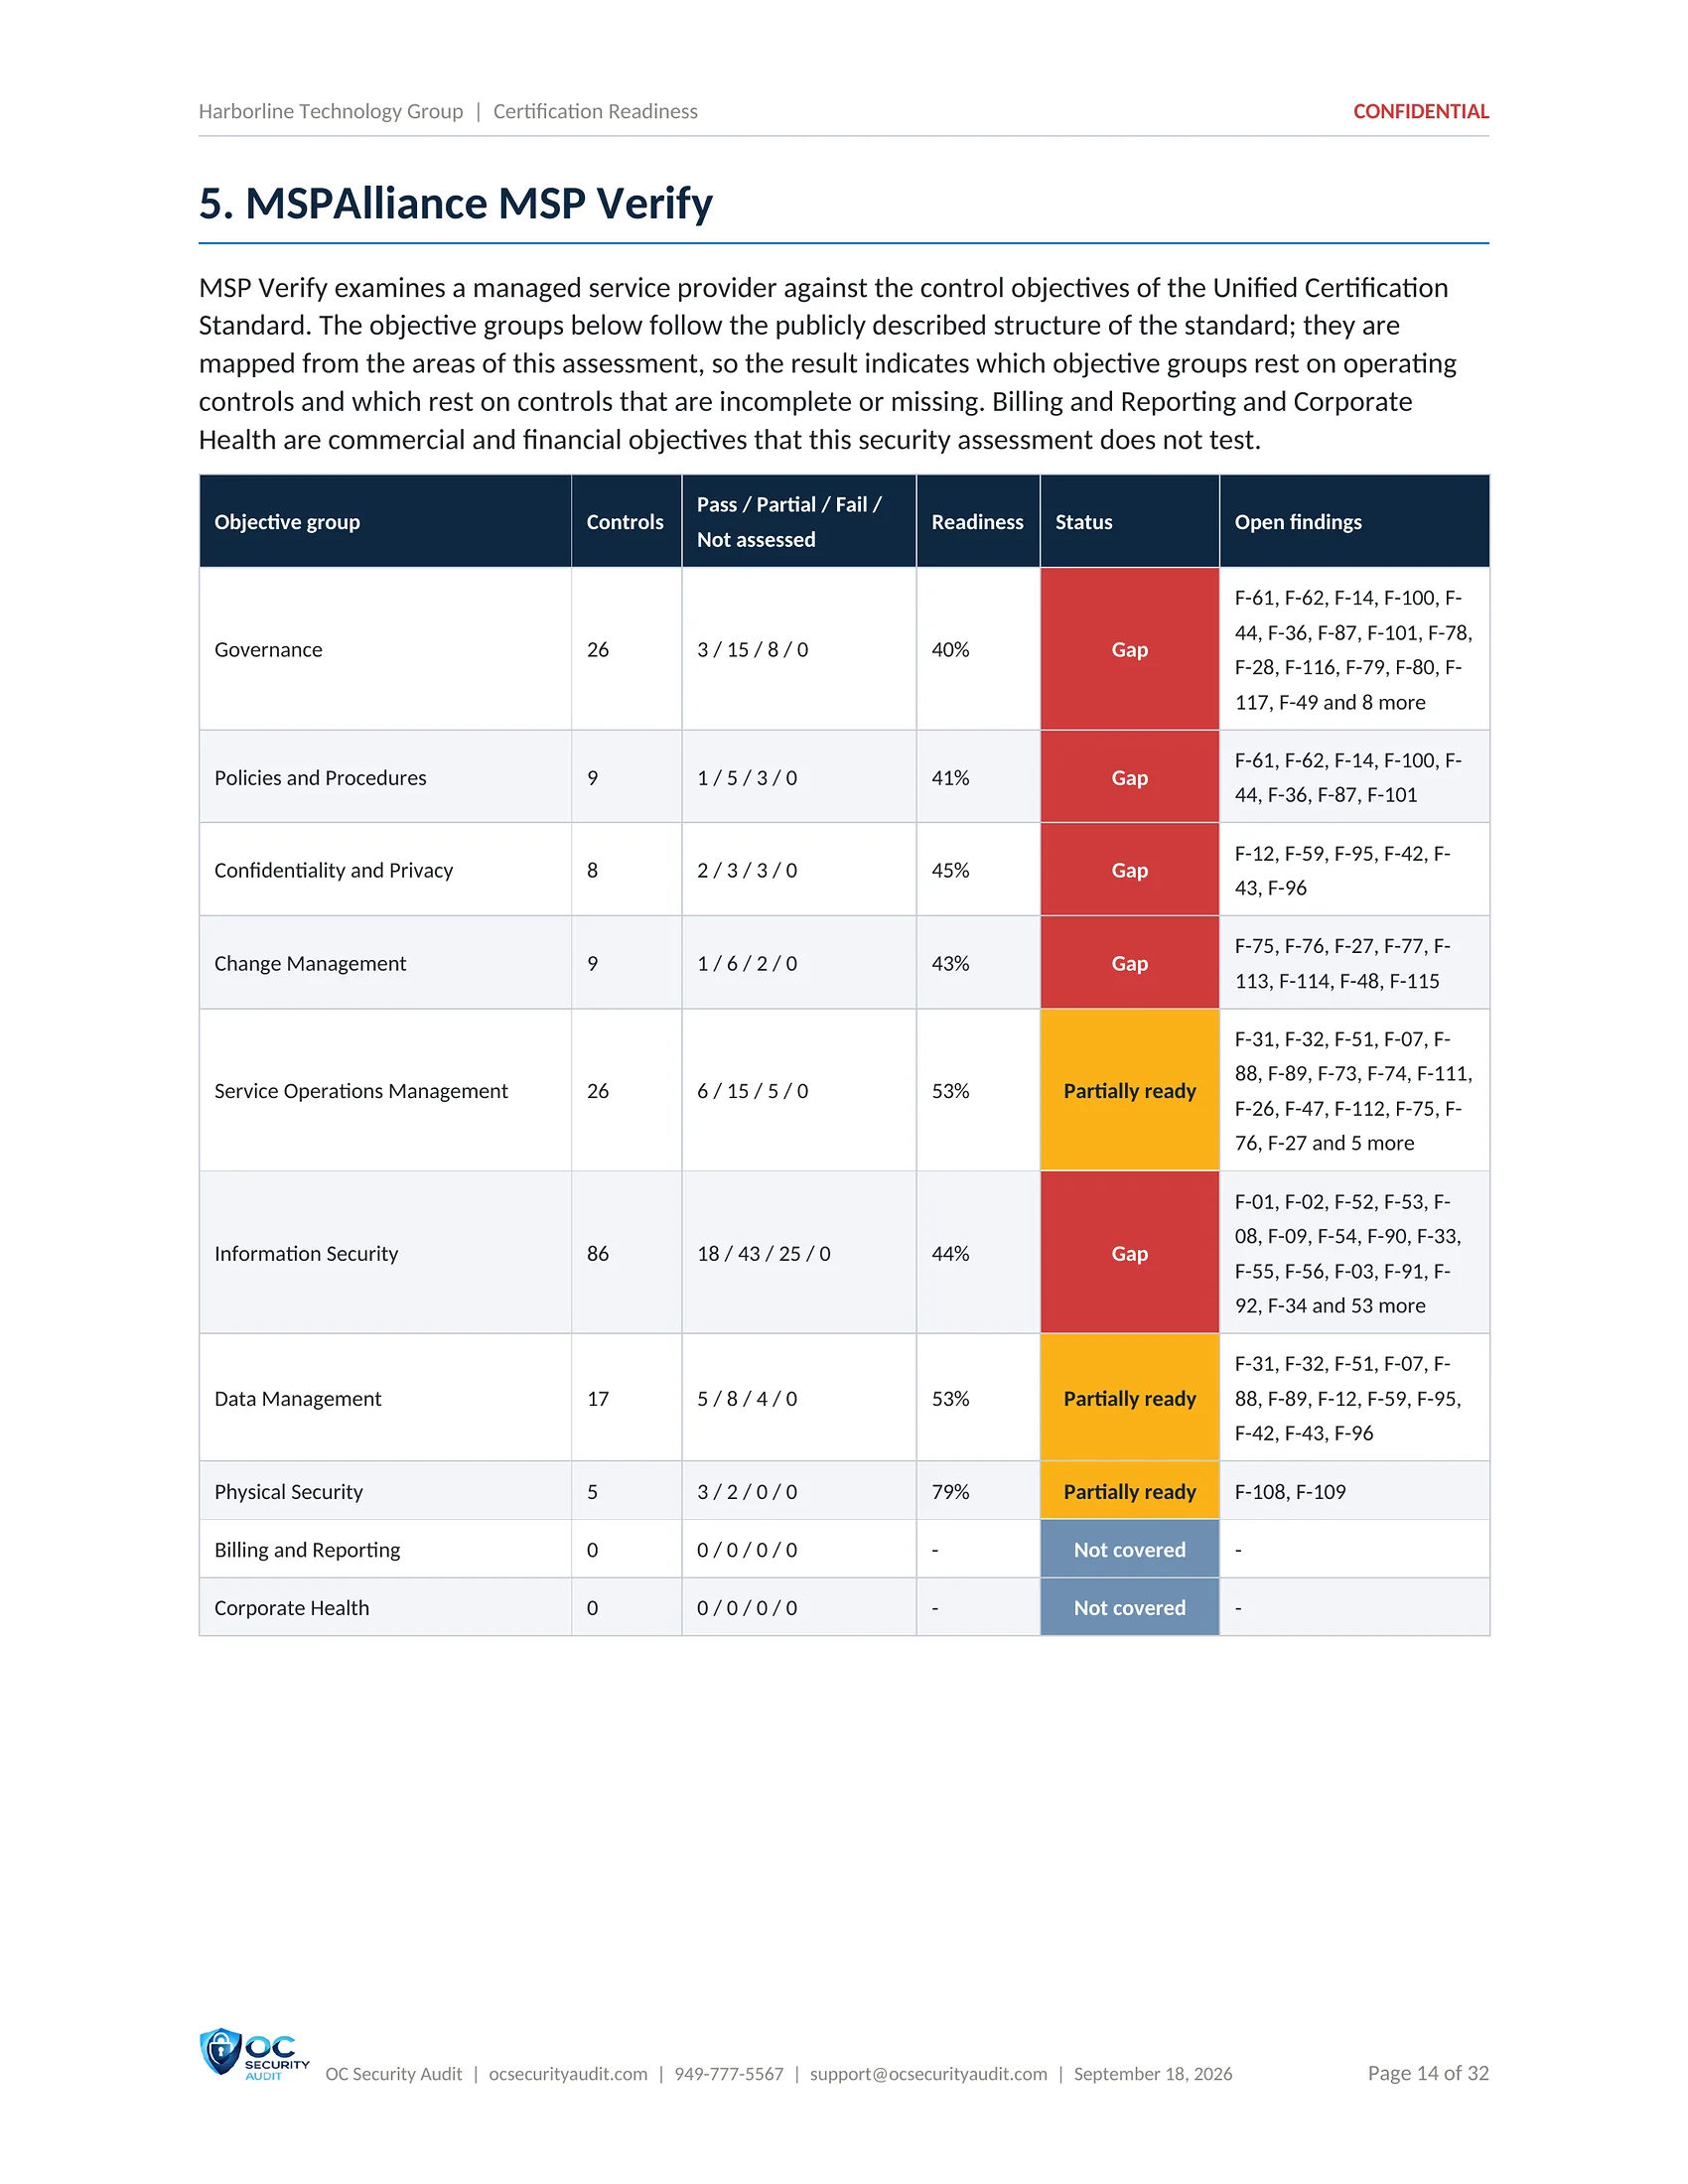
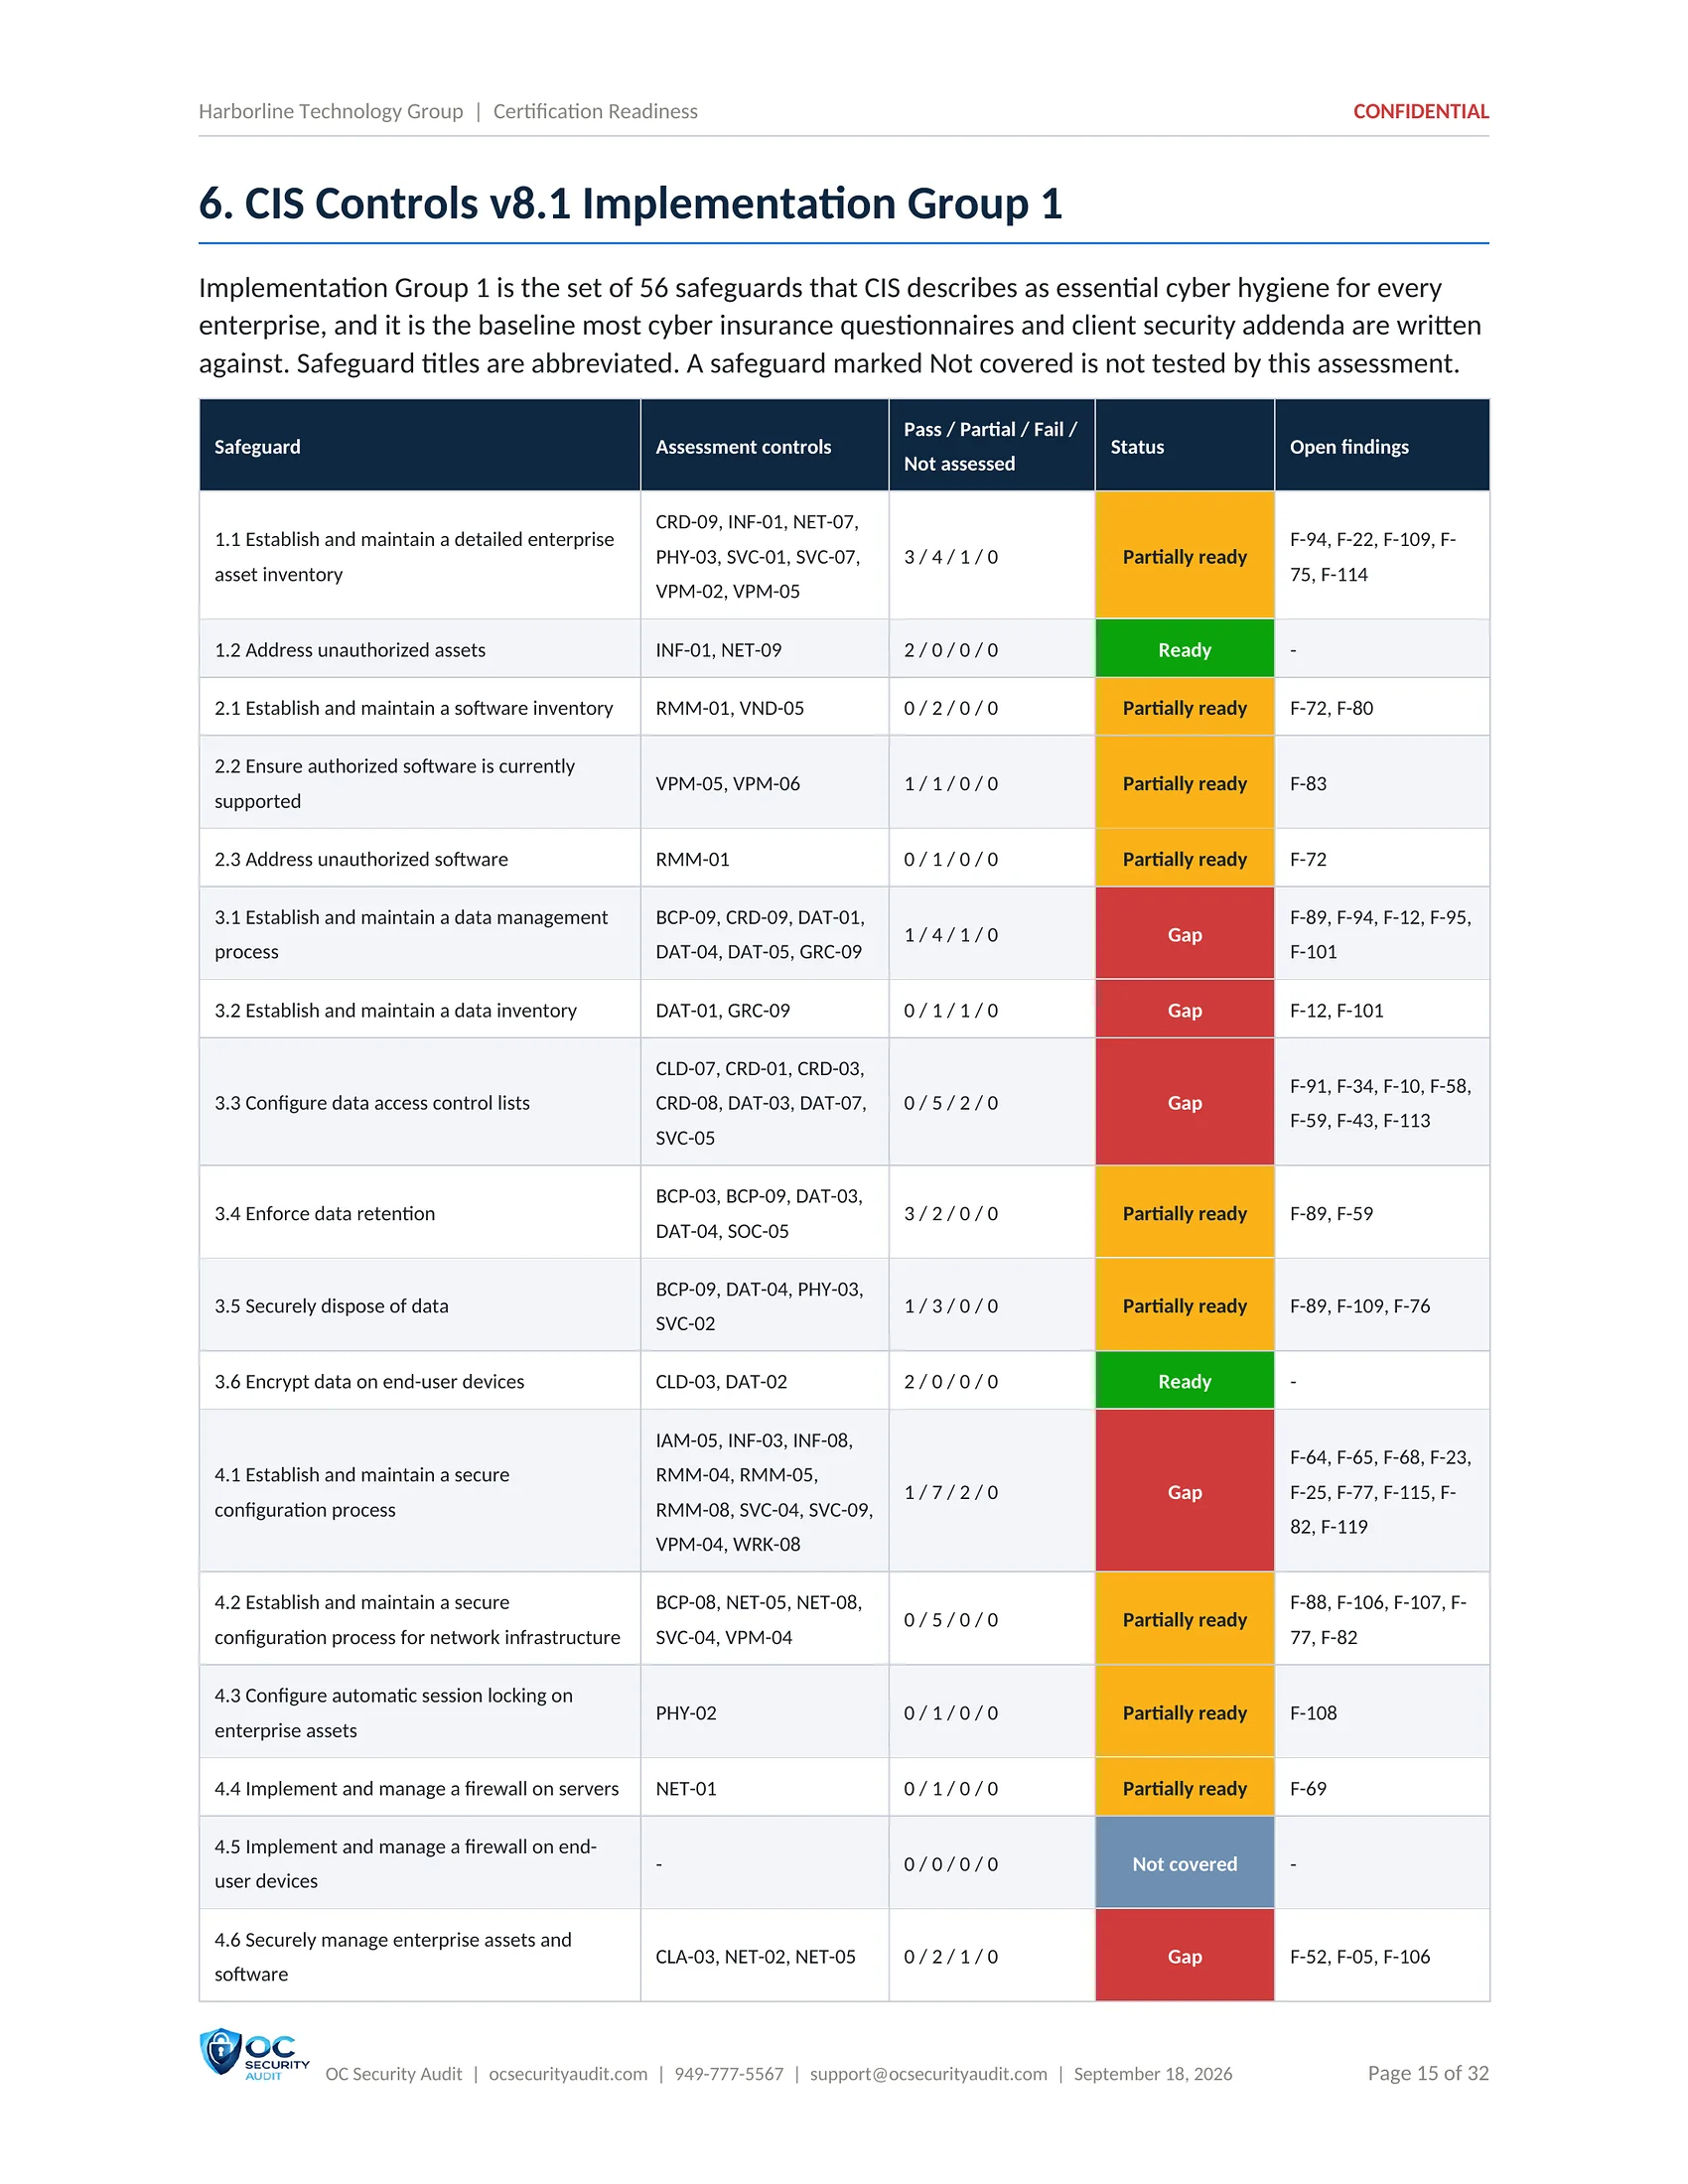
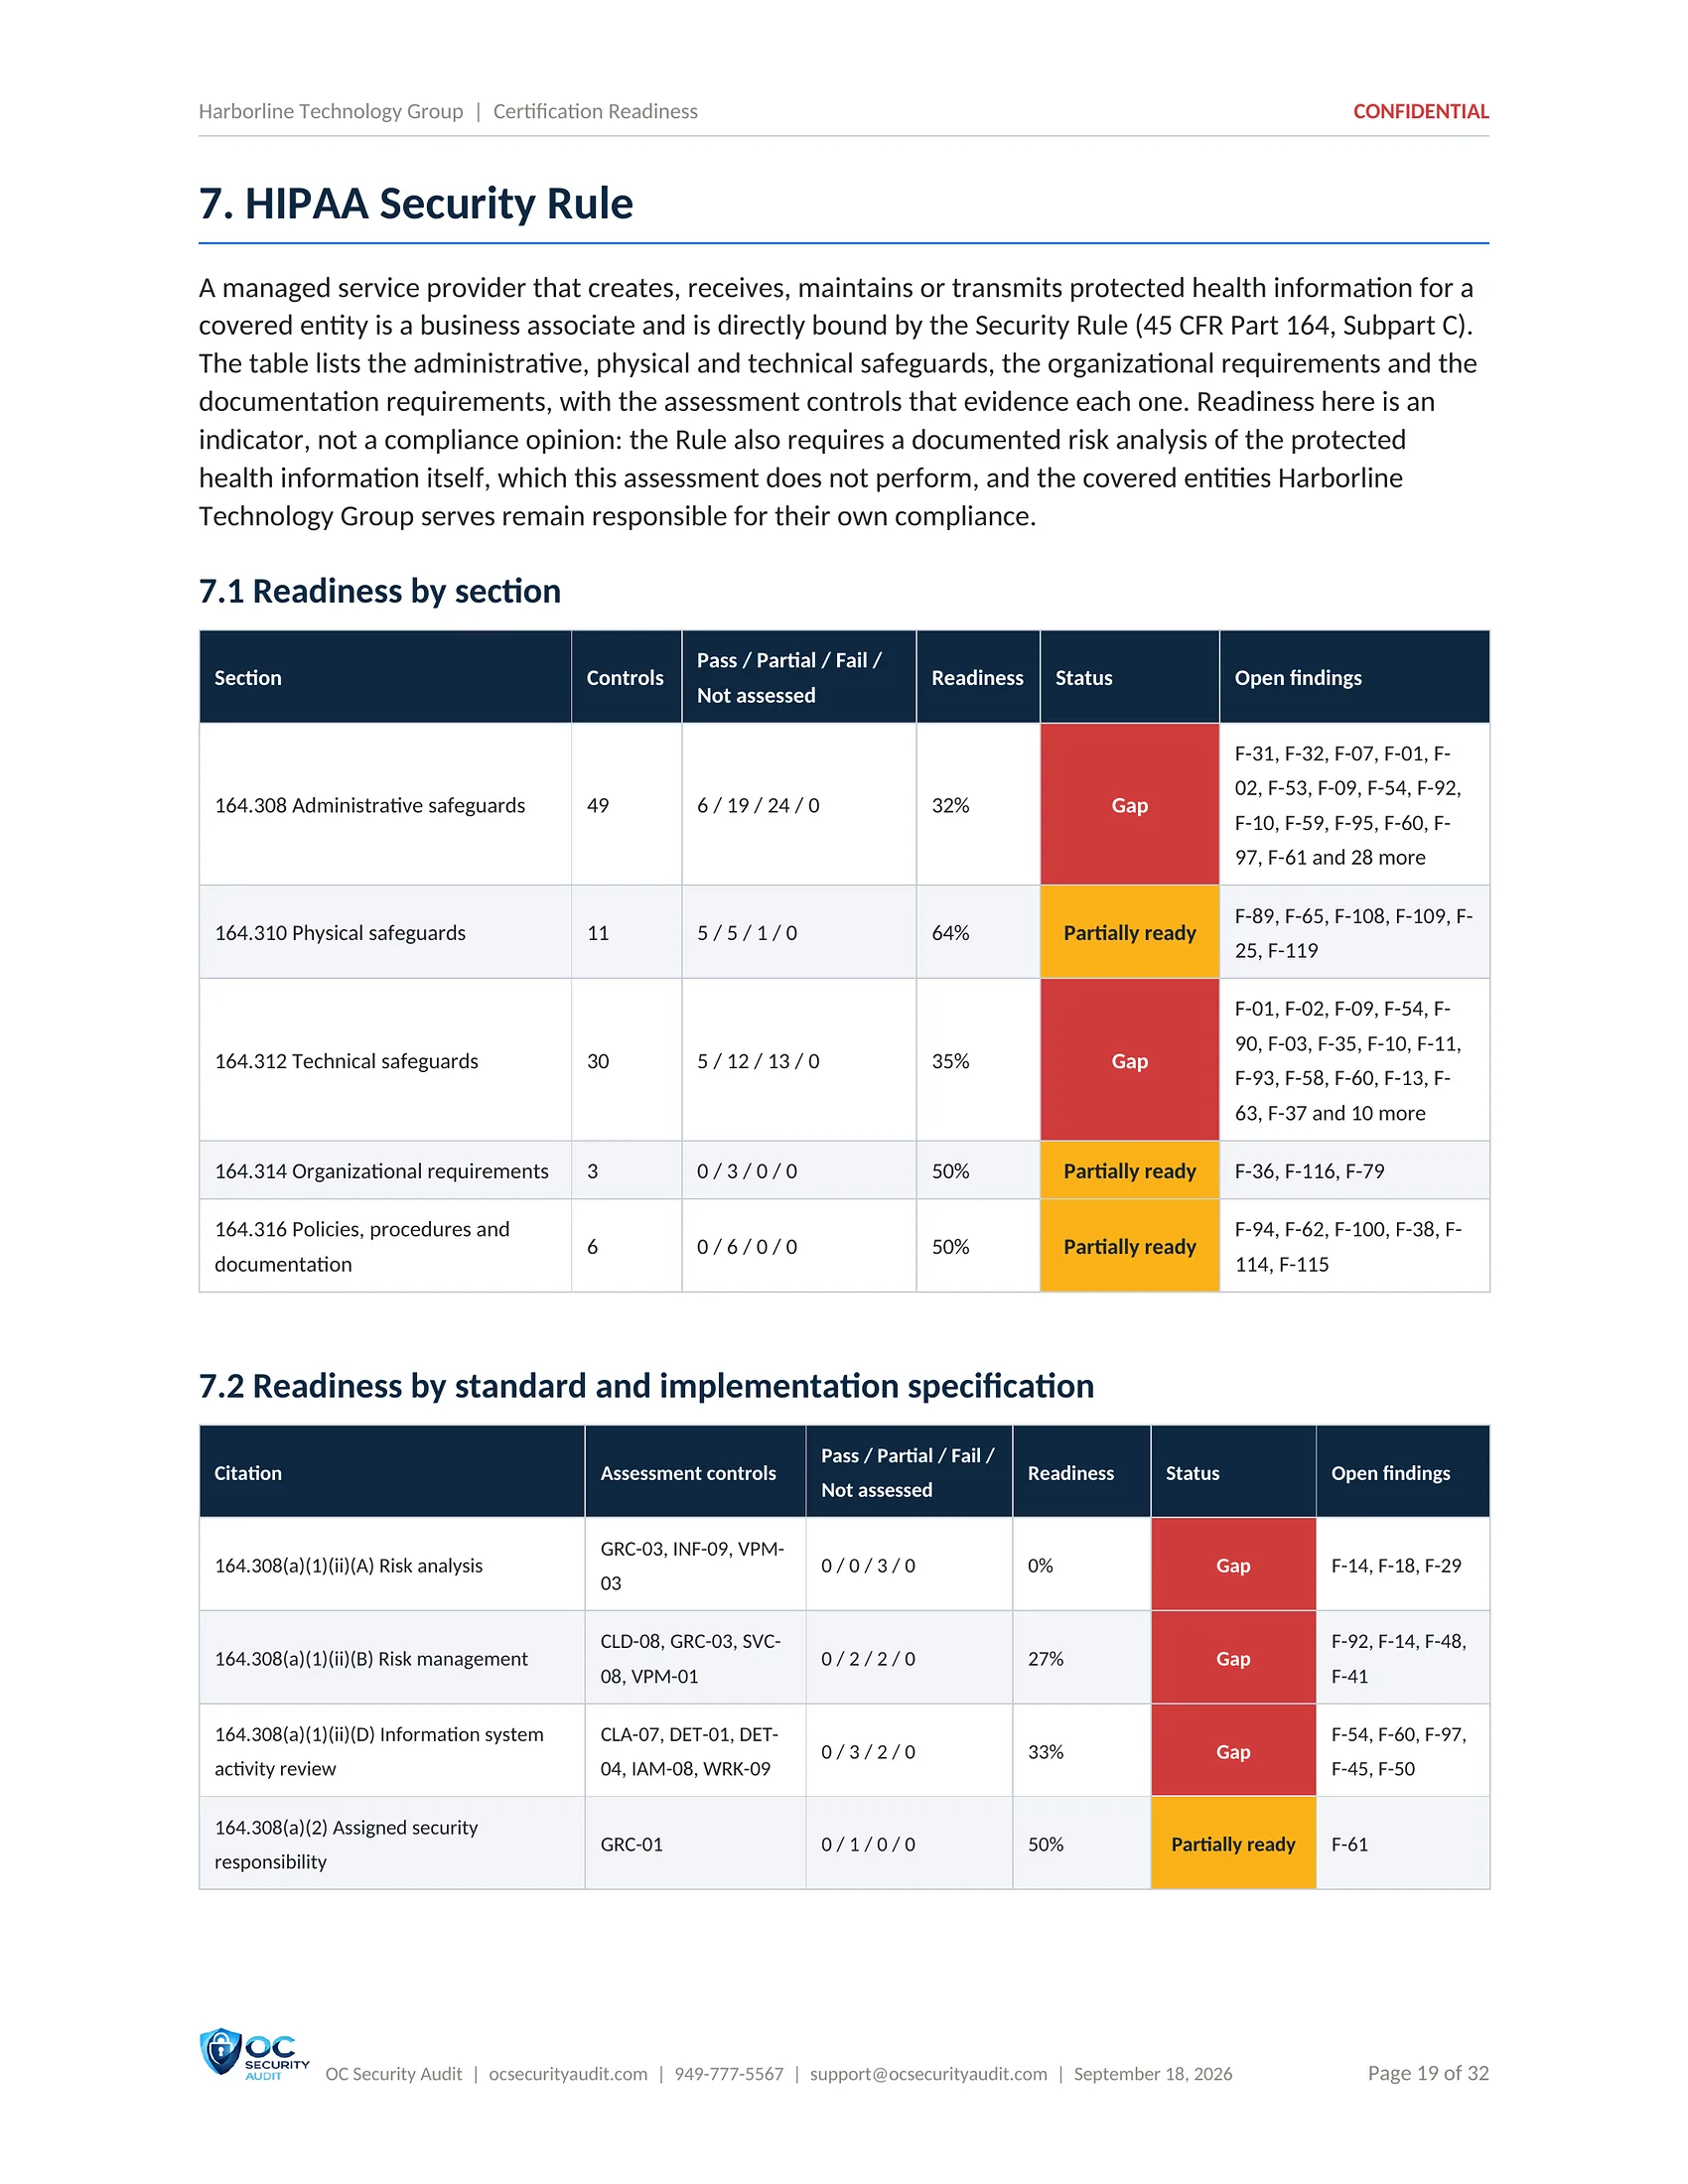
Click the centre page to open it full size and zoom in.
PDF and Word · 39 pages, from the third audit
Remediation History (re-audits)
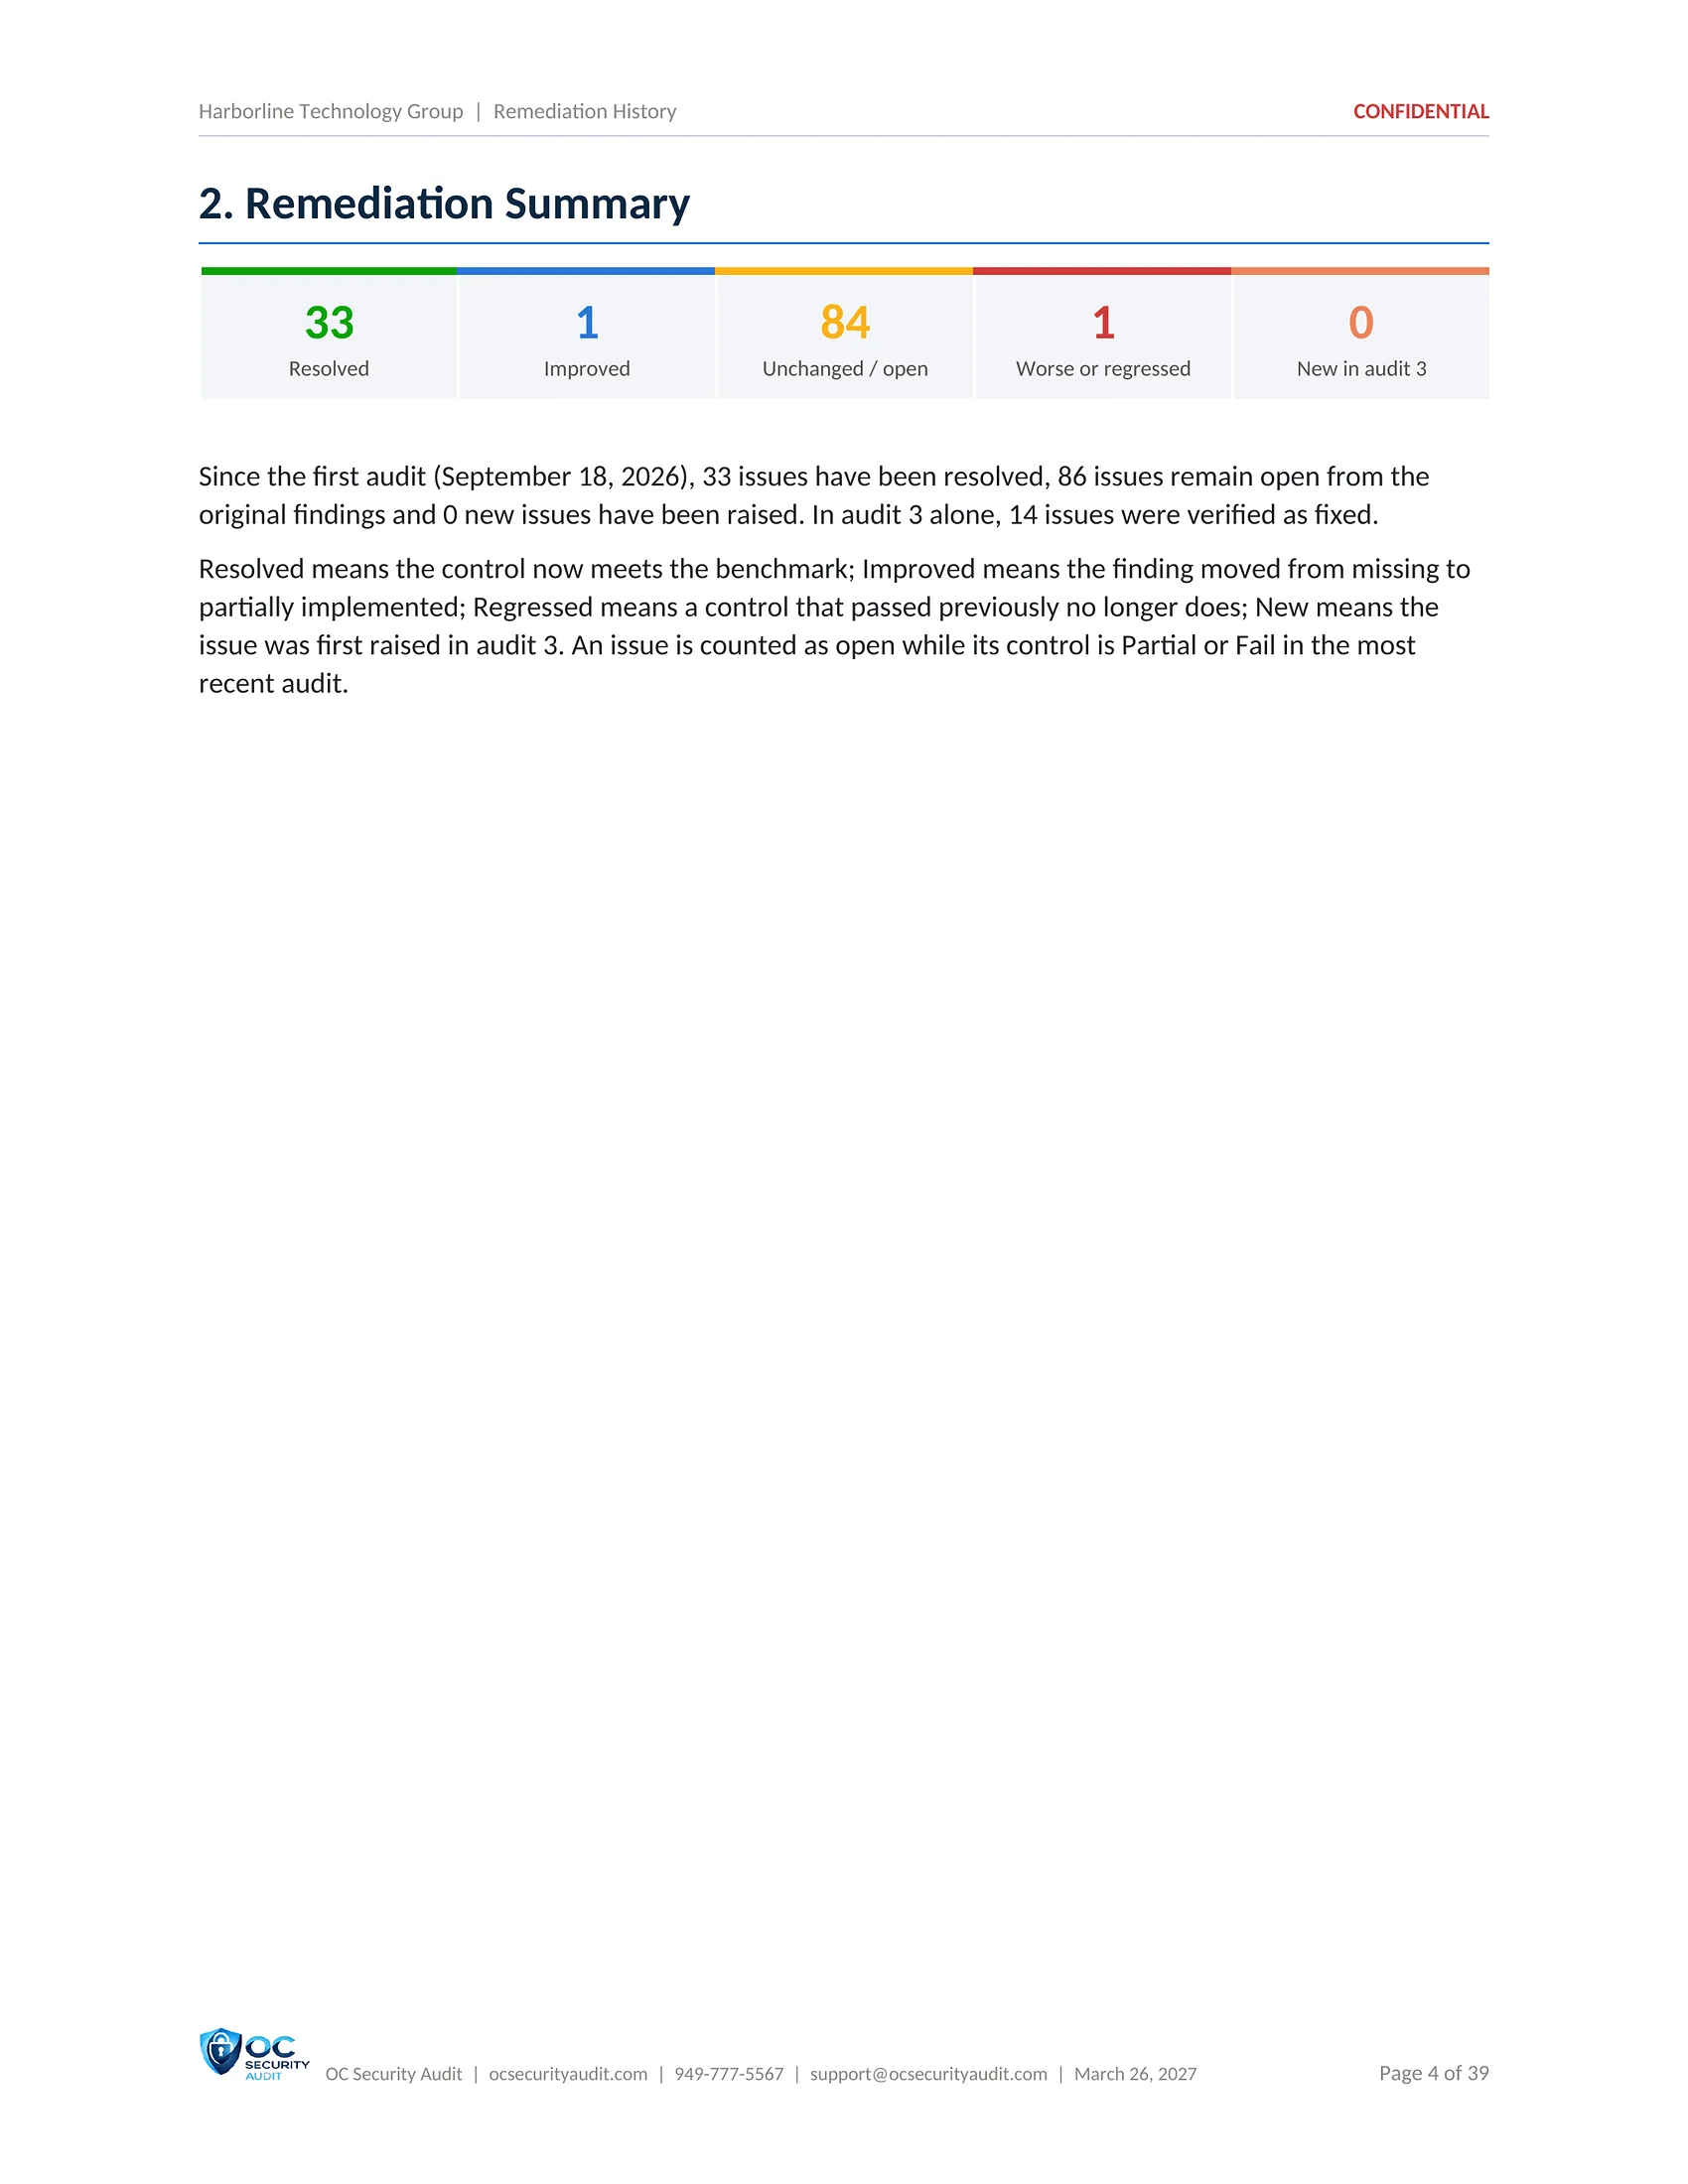
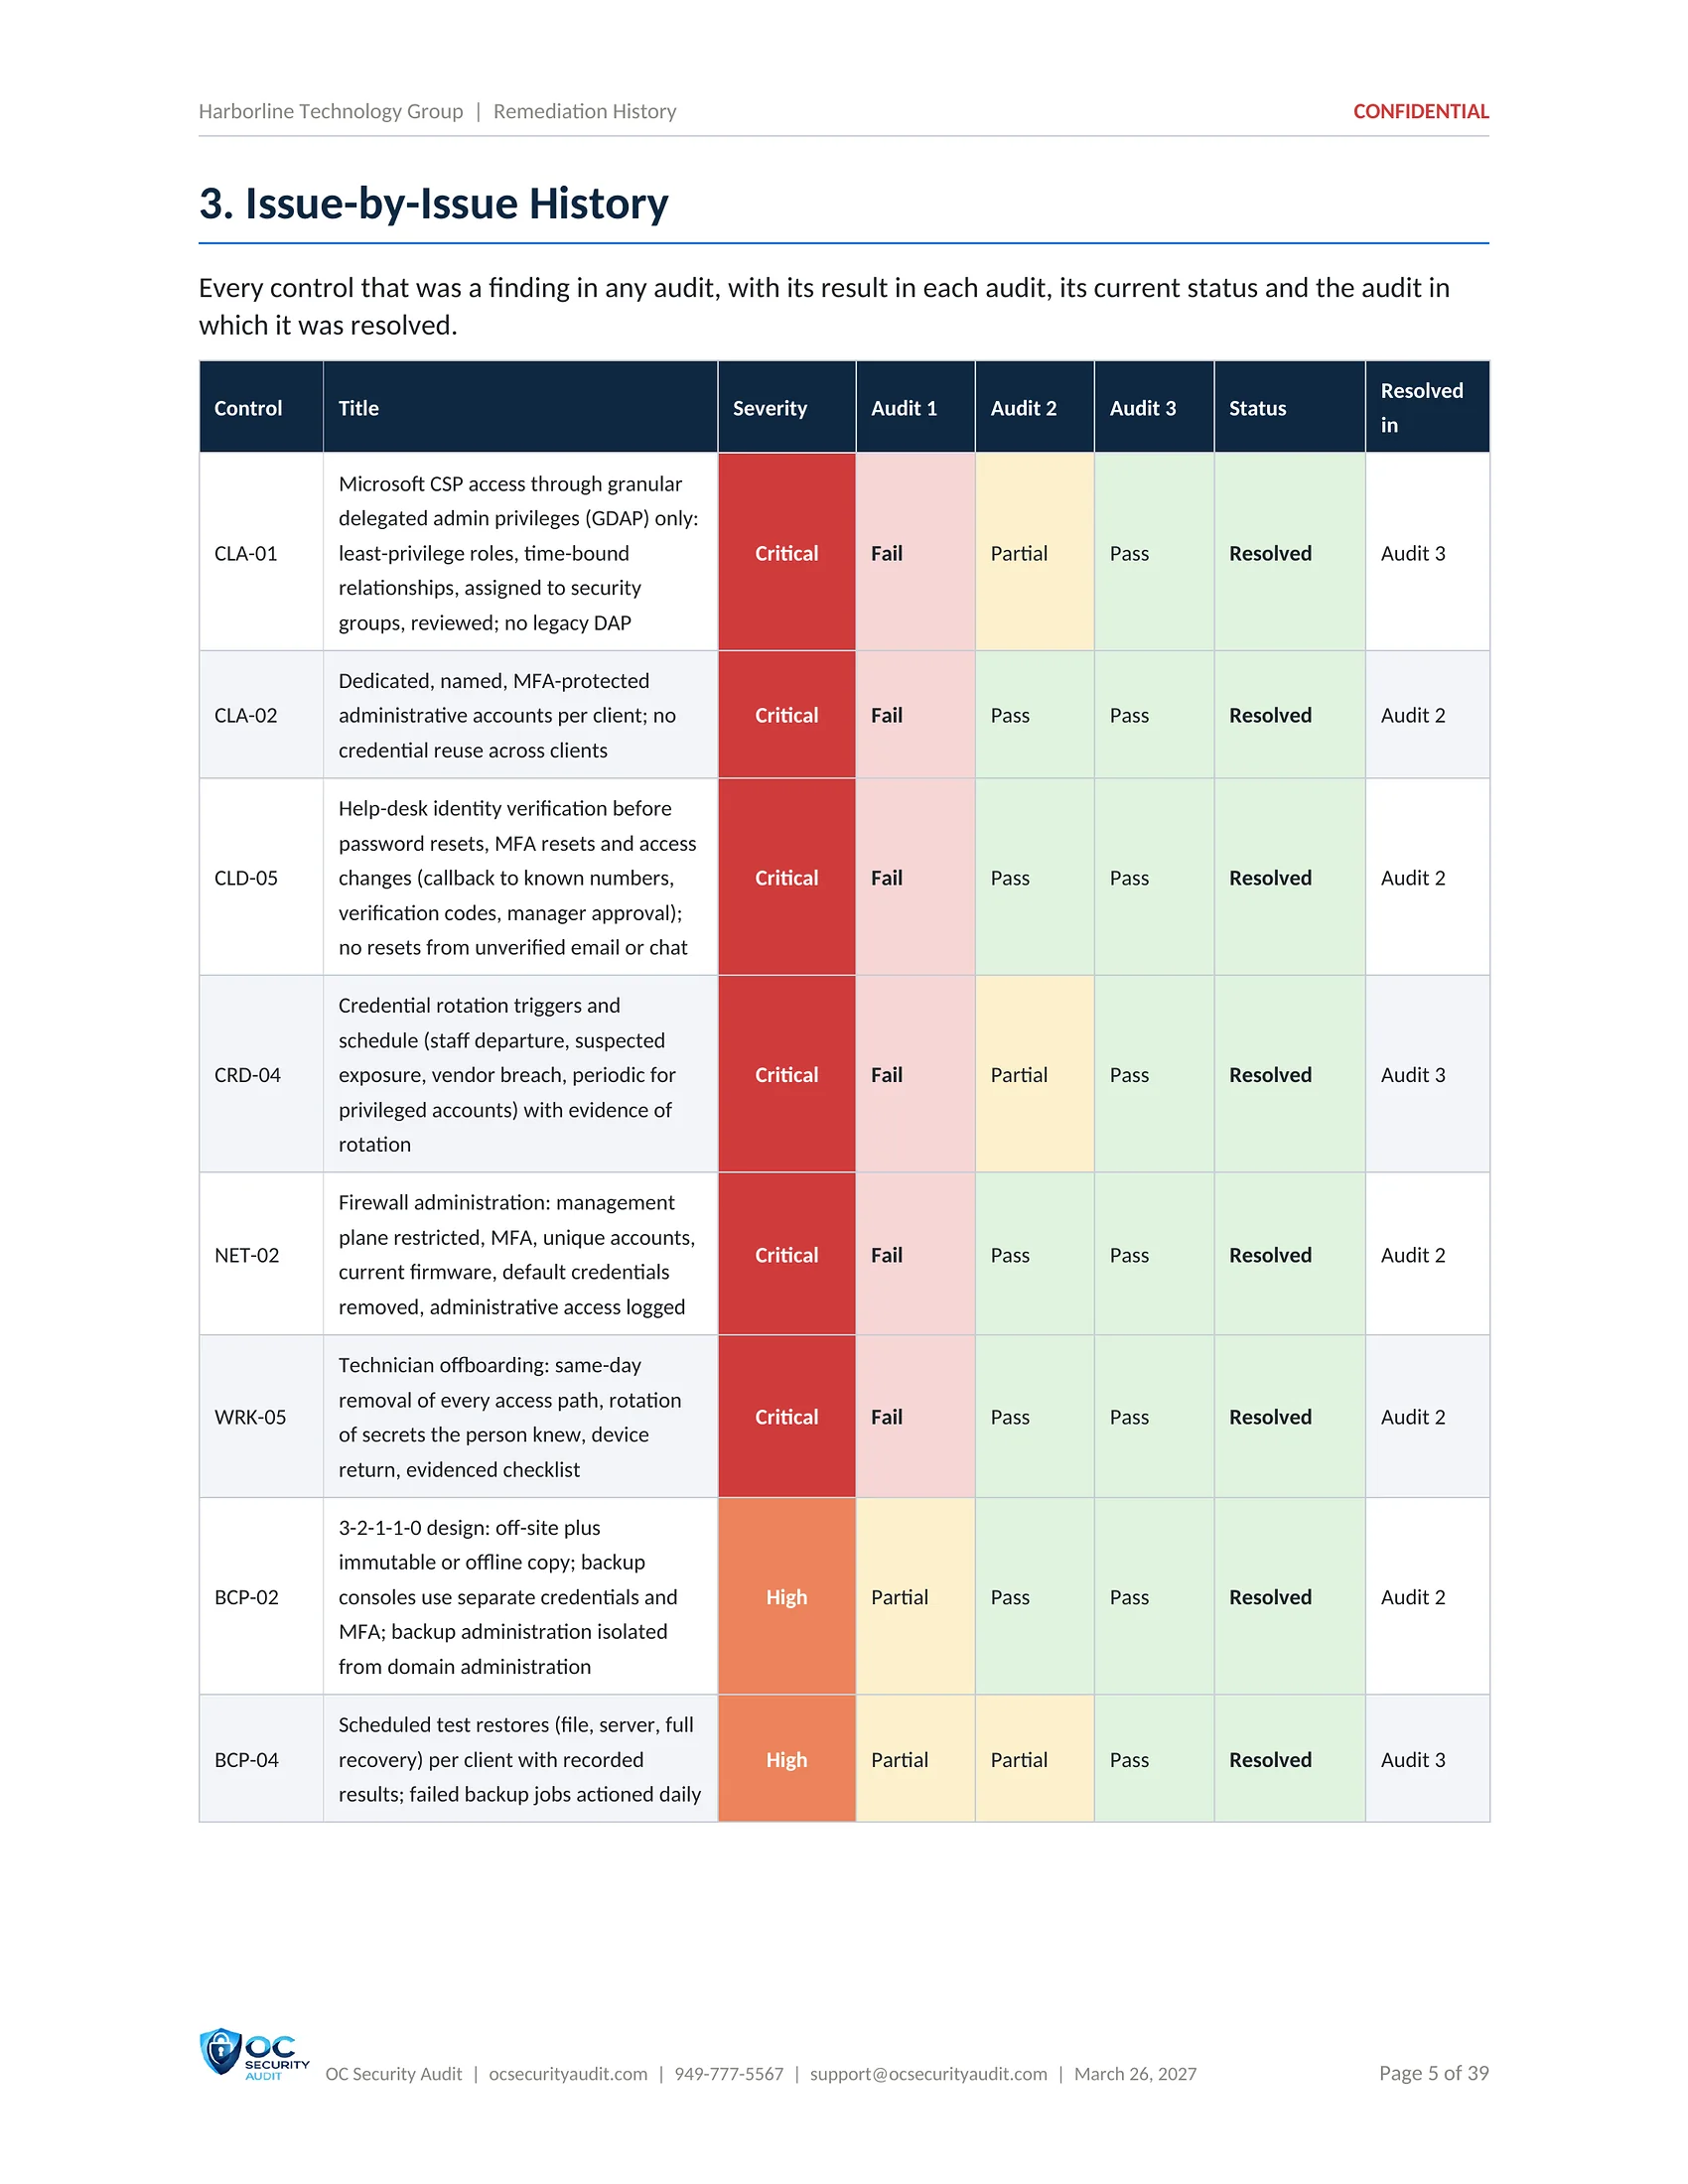
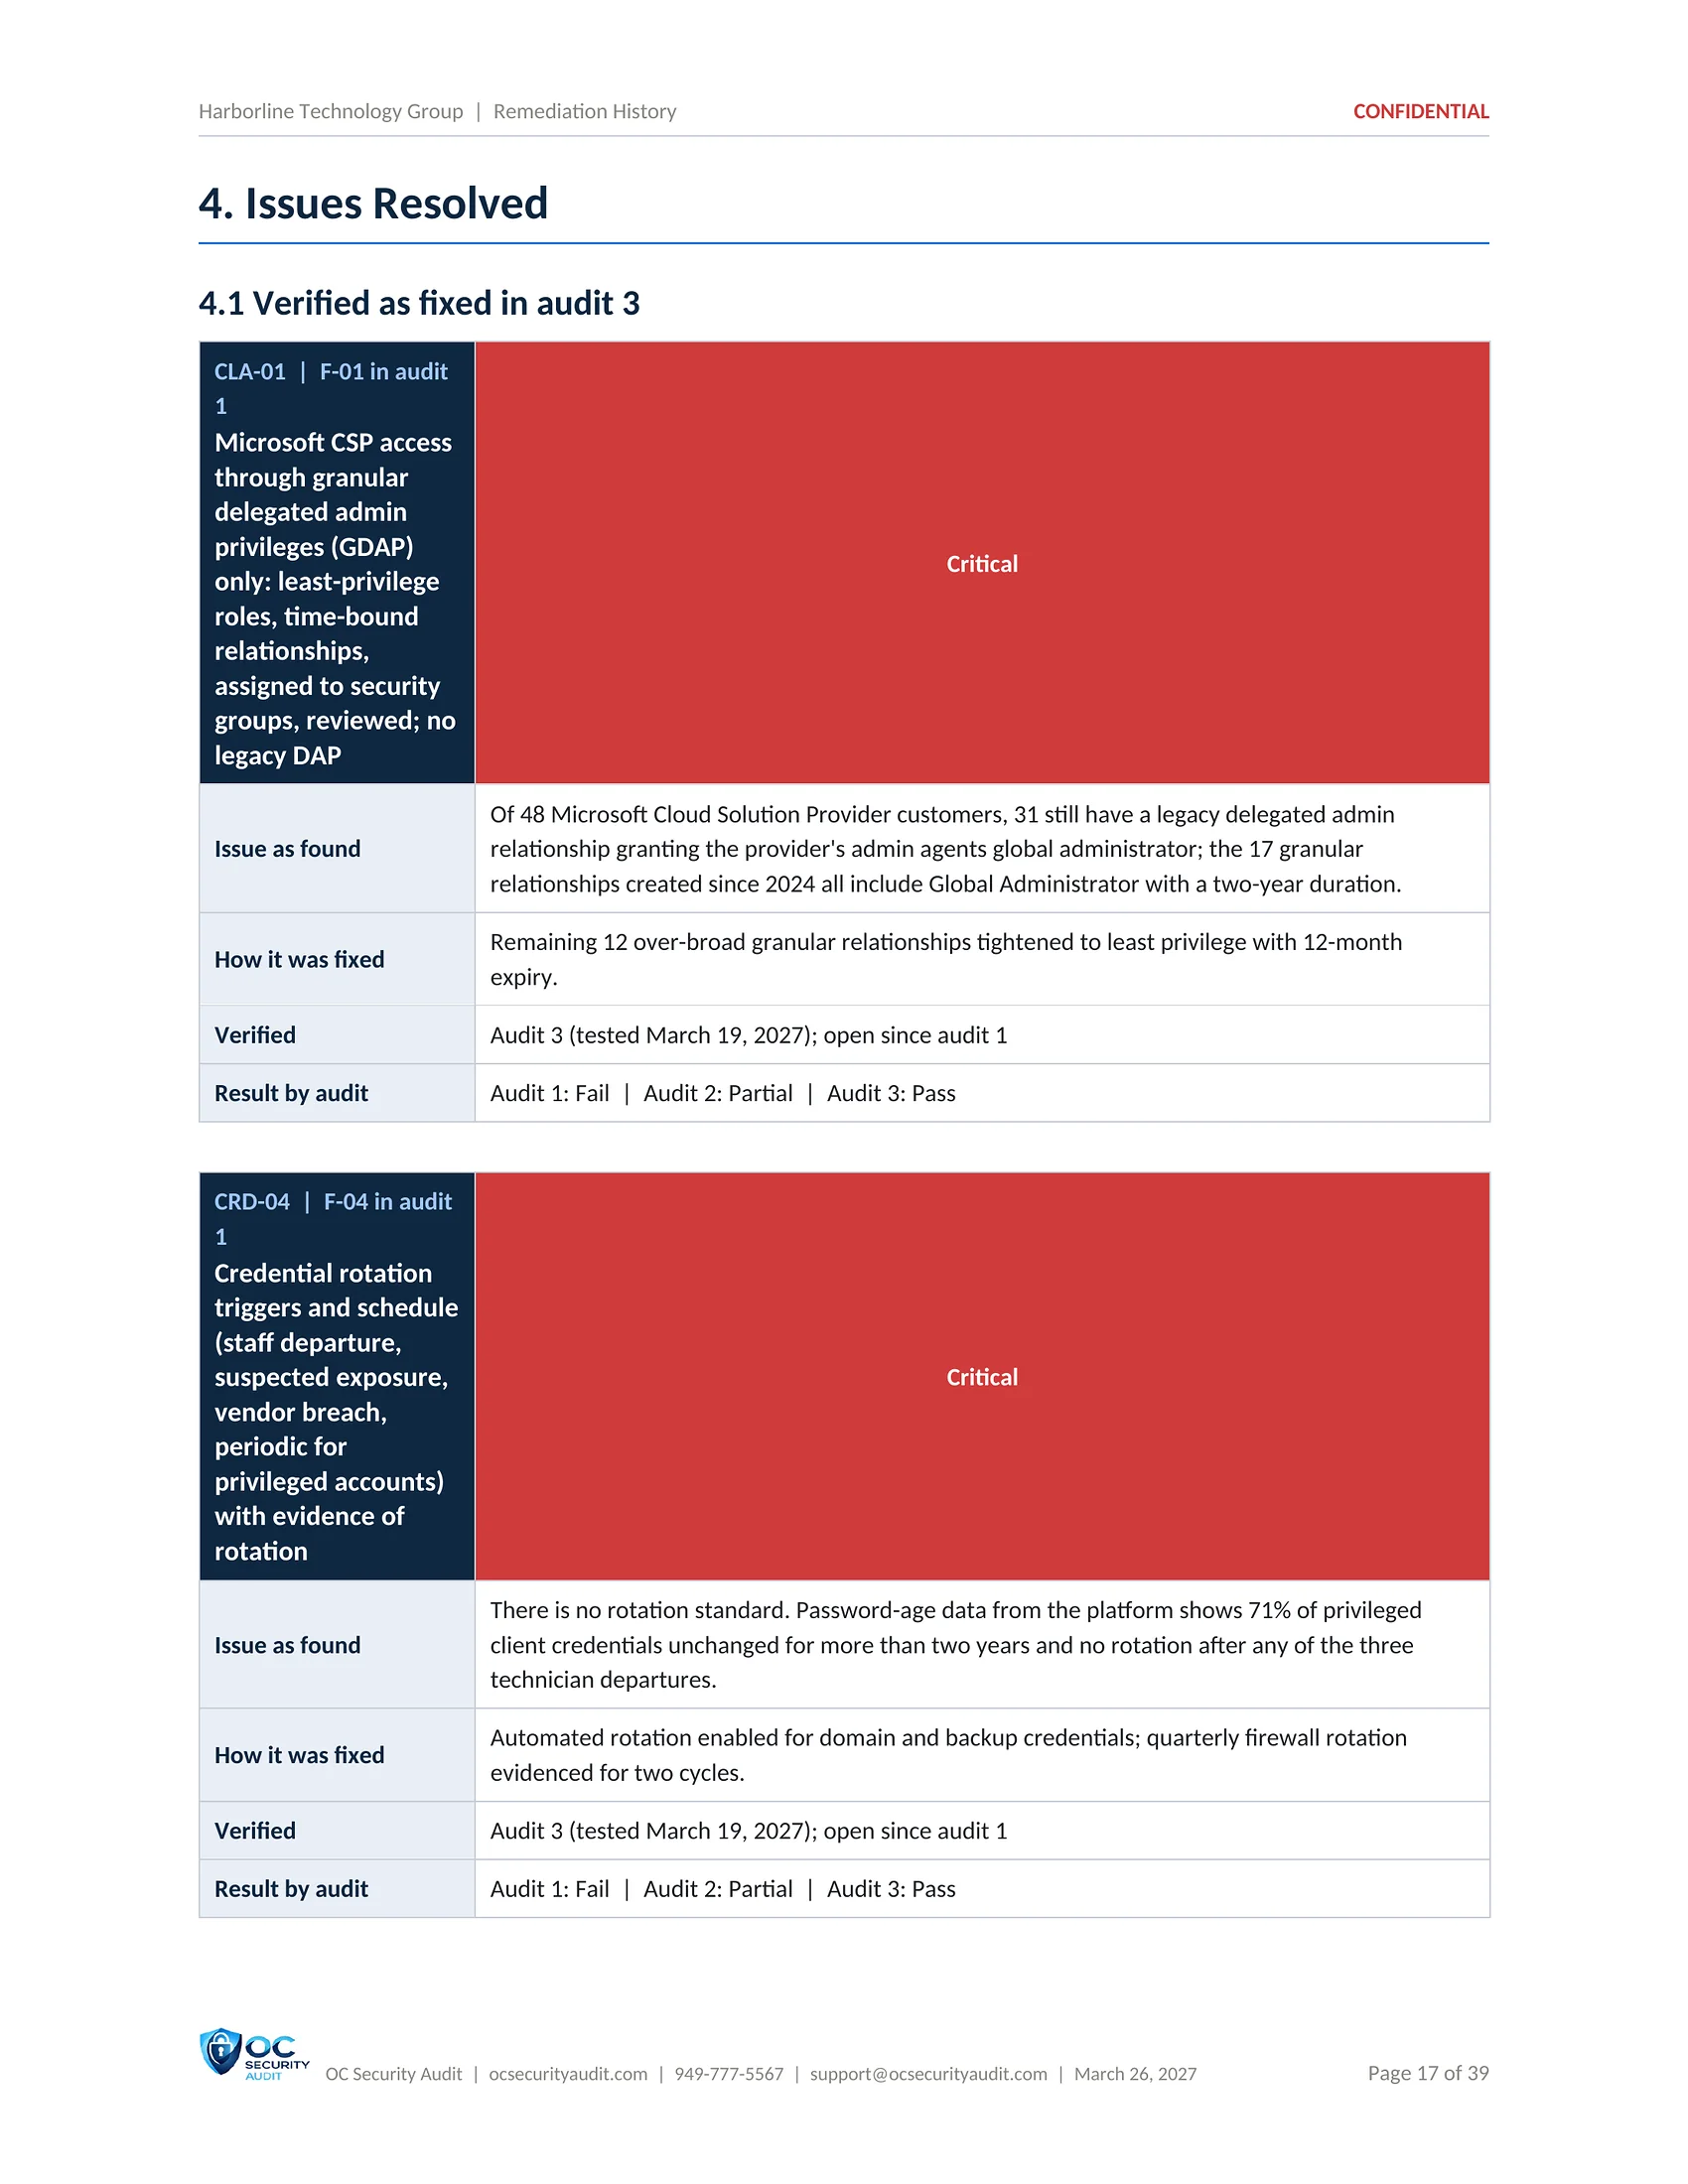
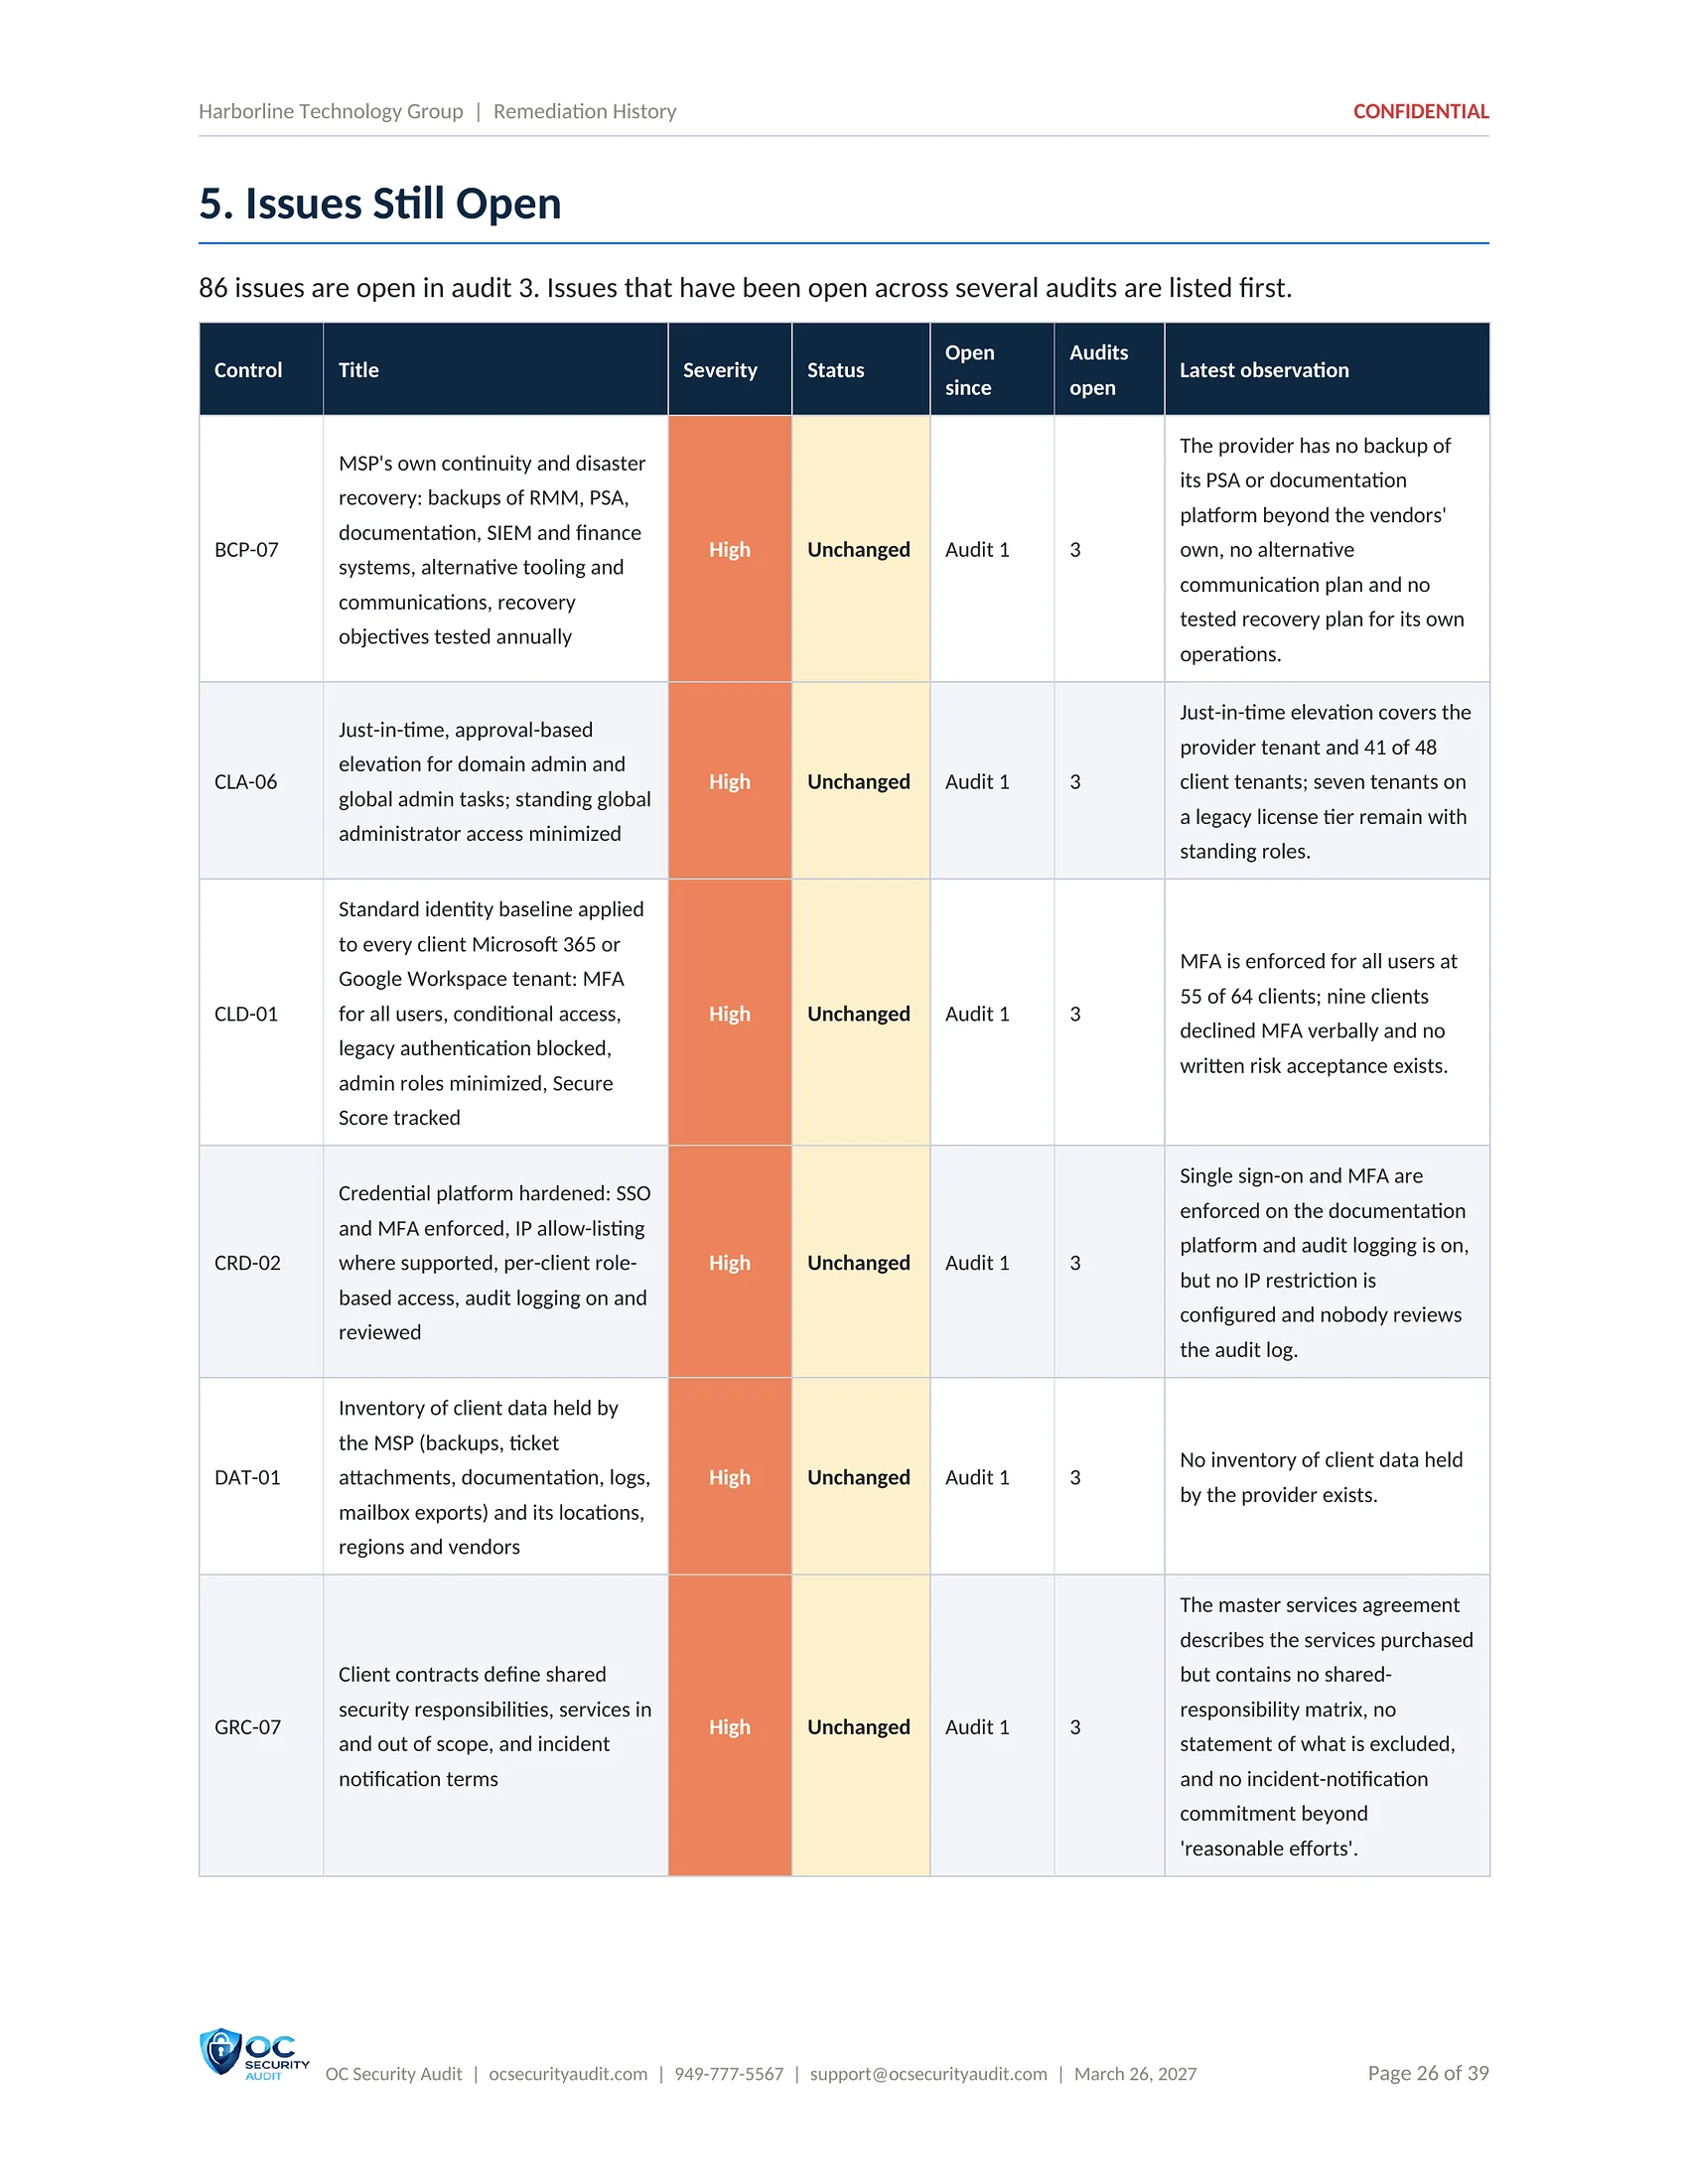
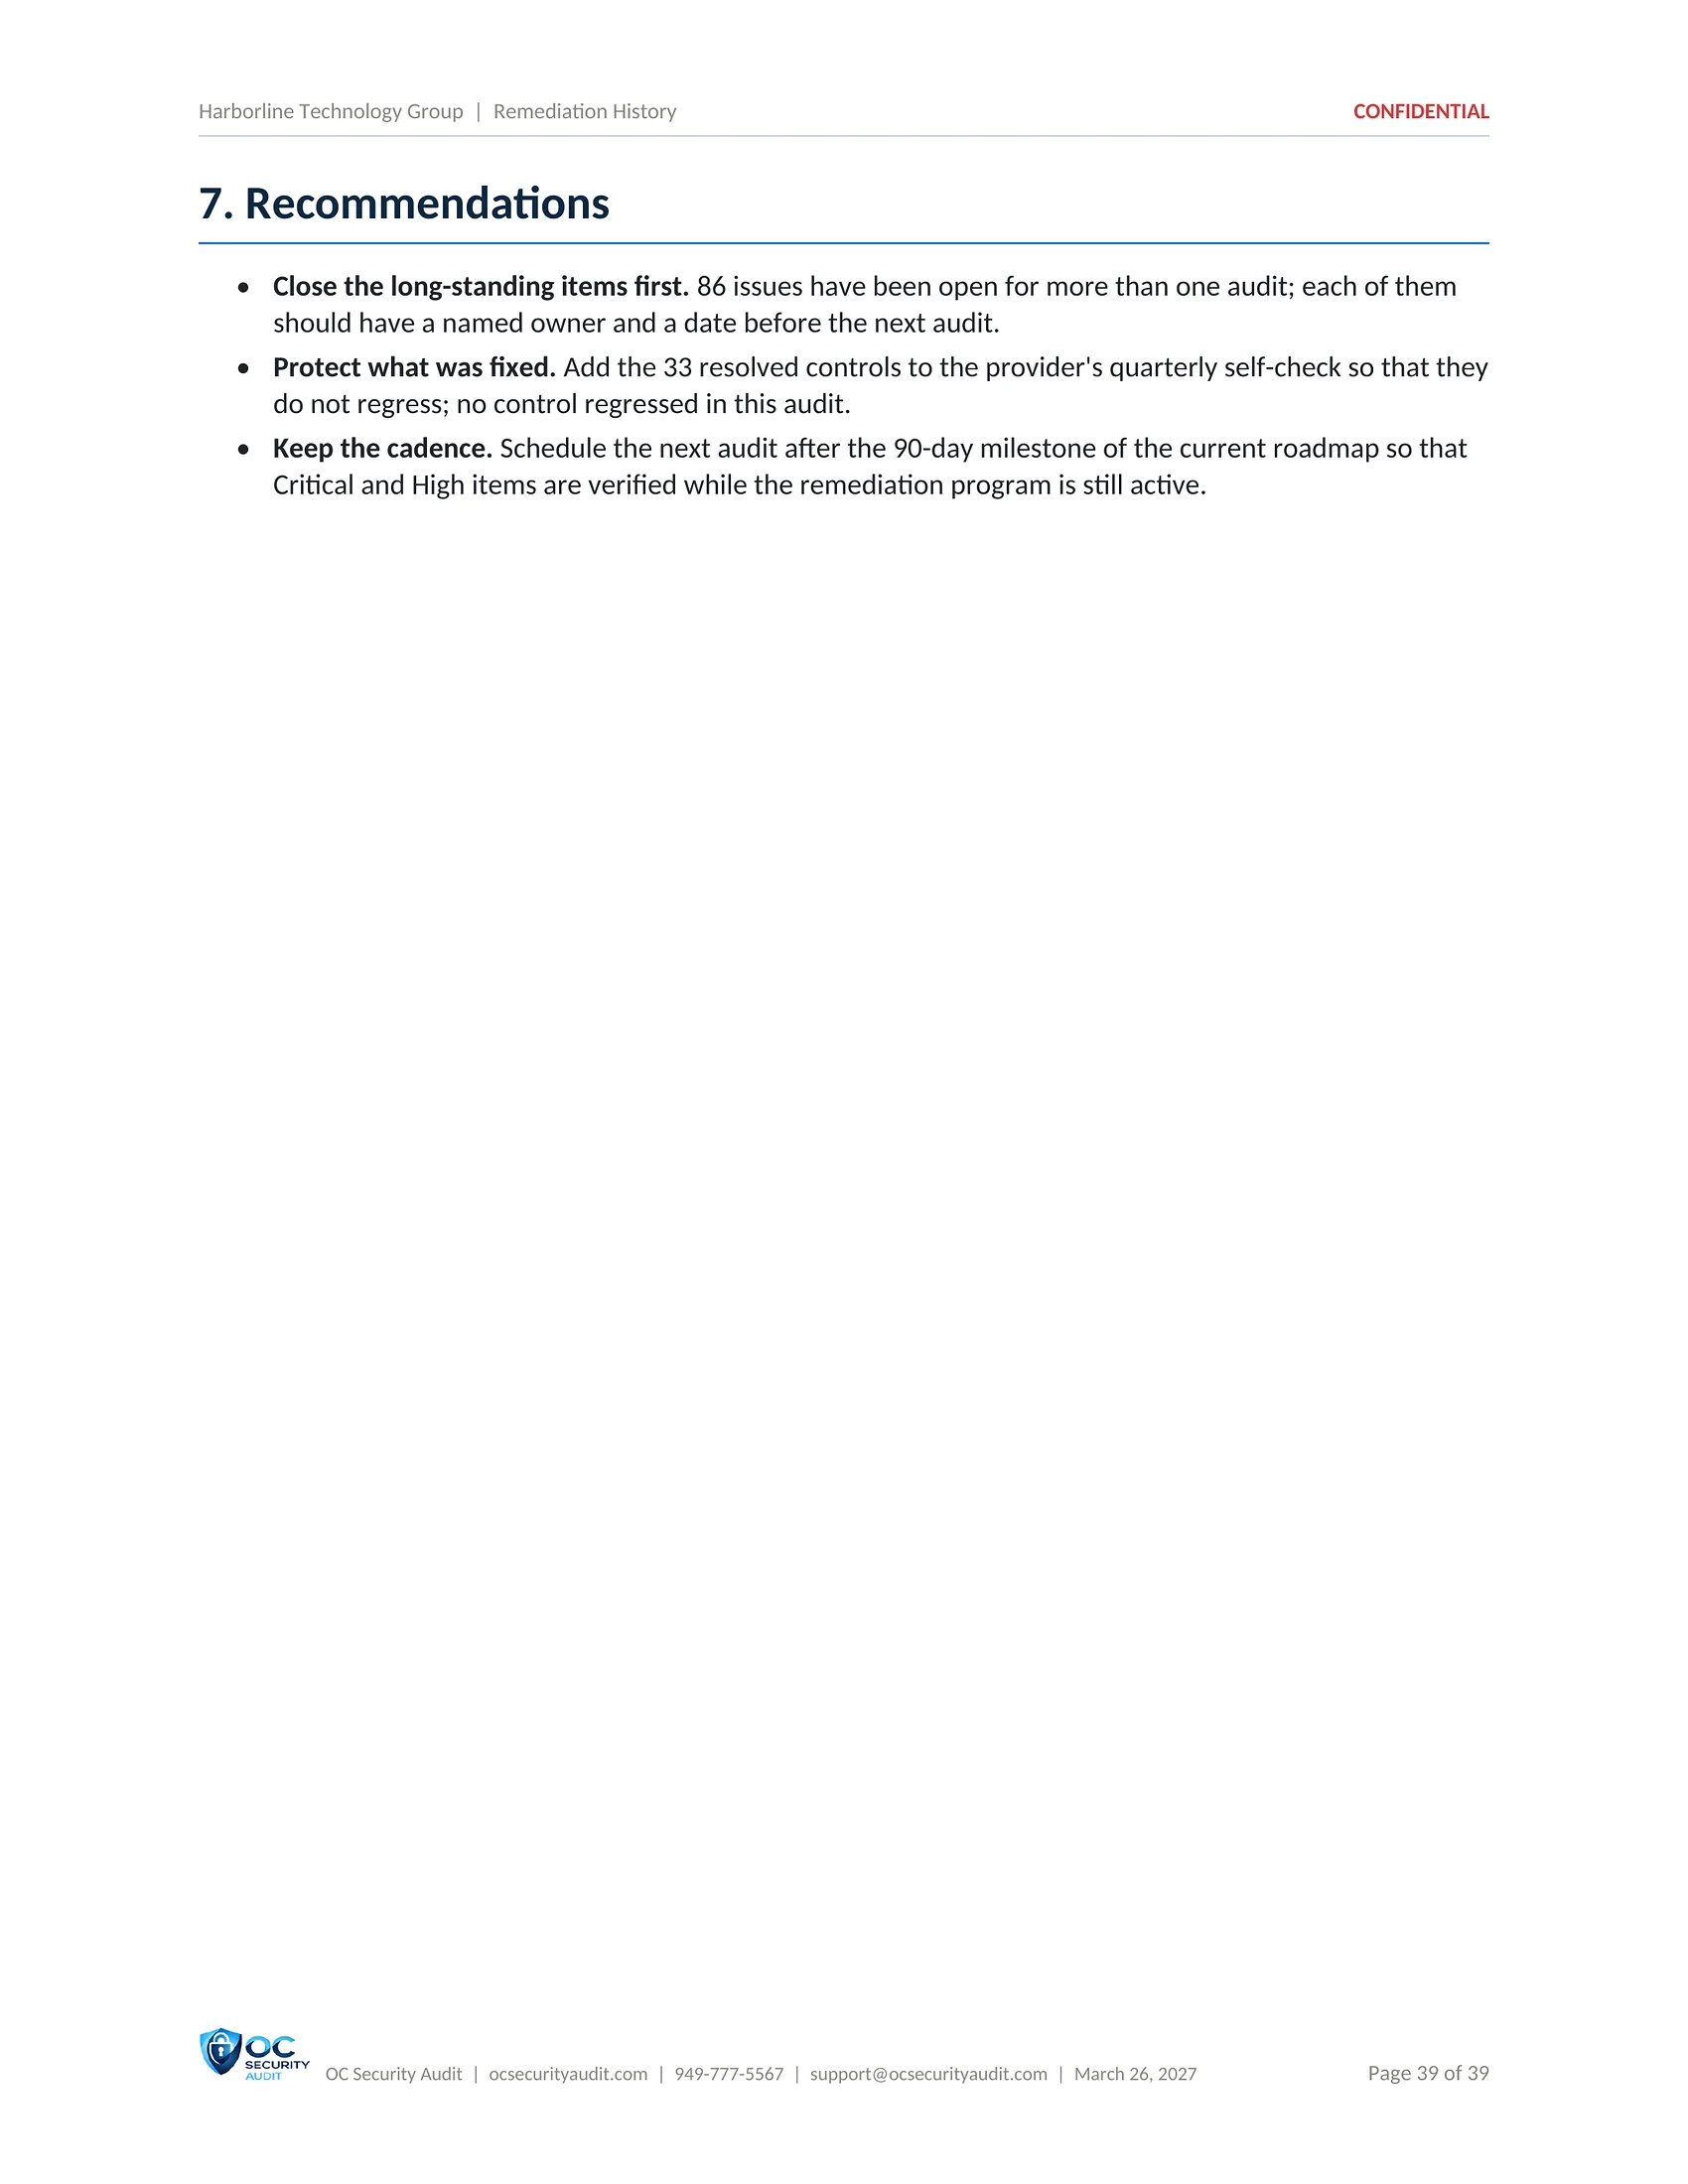
Issued from the second audit on. It compares every control with every earlier audit and shows what was fixed and verified, what is still open and for how long, and what is new or has regressed, so leadership, clients and insurers can see progress over the audit cycle.
Leadership, clients and insurers who want proof of progress between audits.
What is included
- Audit timeline and score trend
- Remediation summary
- Issue-by-issue history
- Issues verified as fixed
- Issues still open
- Recommendations
- Audit History sheet in the workbook
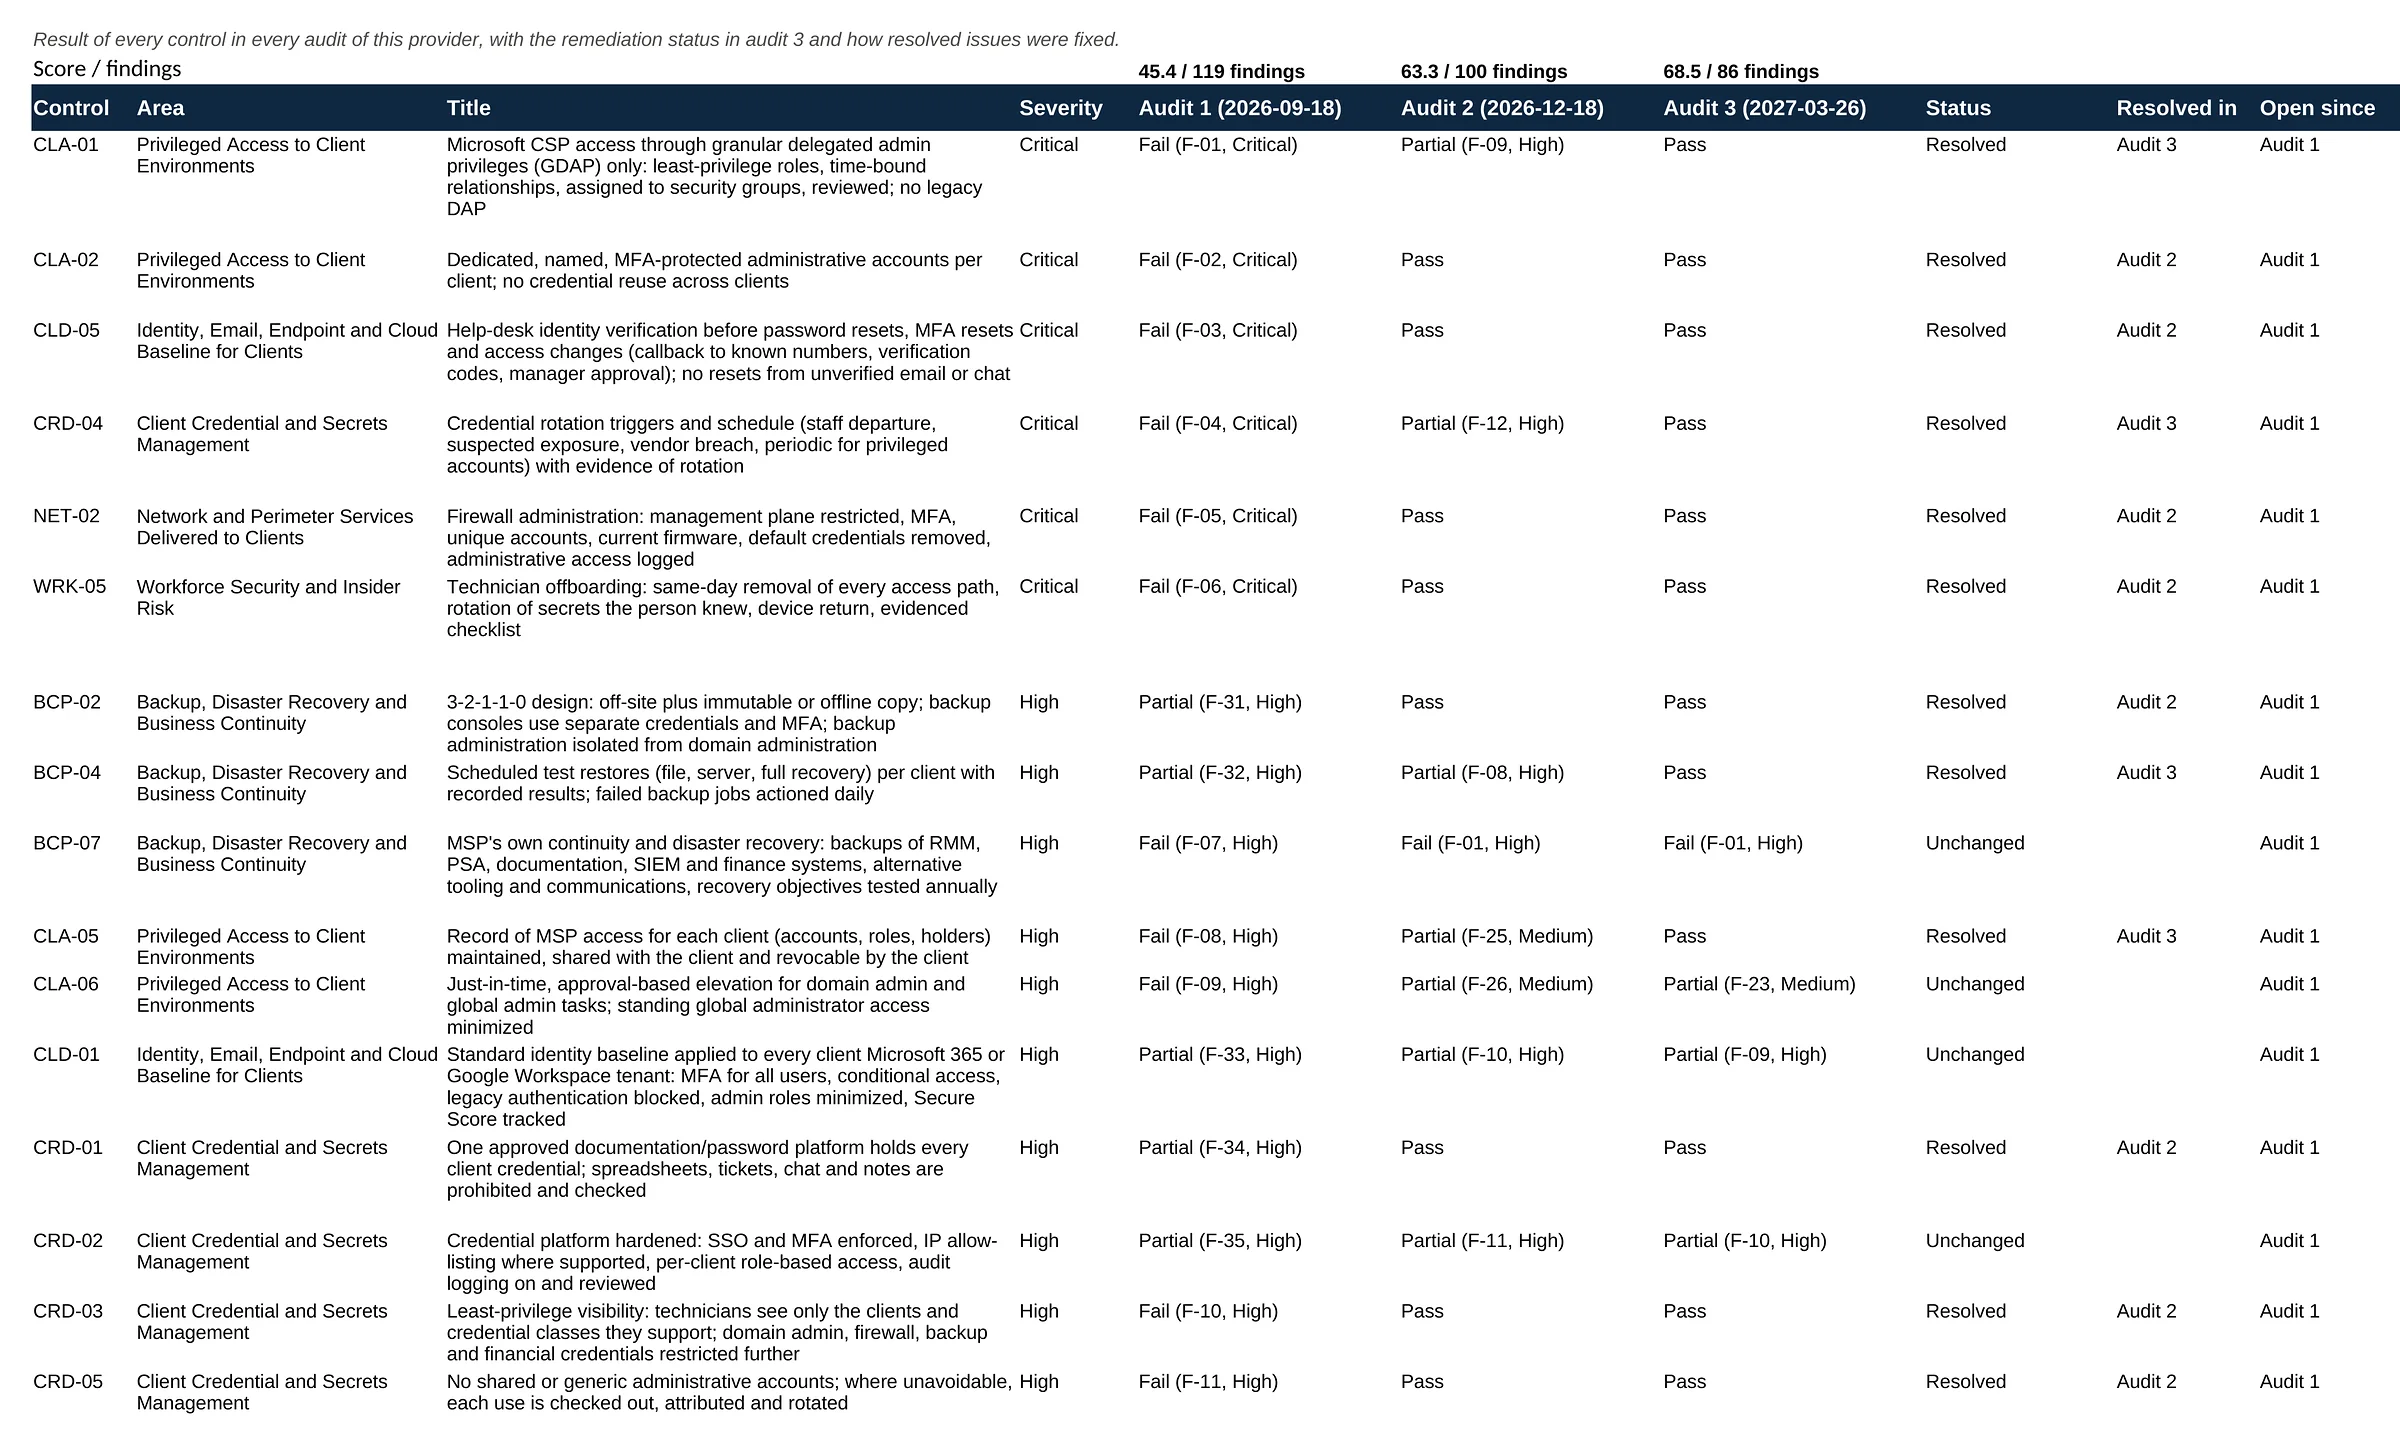
Click the centre page to open it full size and zoom in.
Excel · 8 working sheets, plus Audit History in re-audits
Technical Findings Workbook
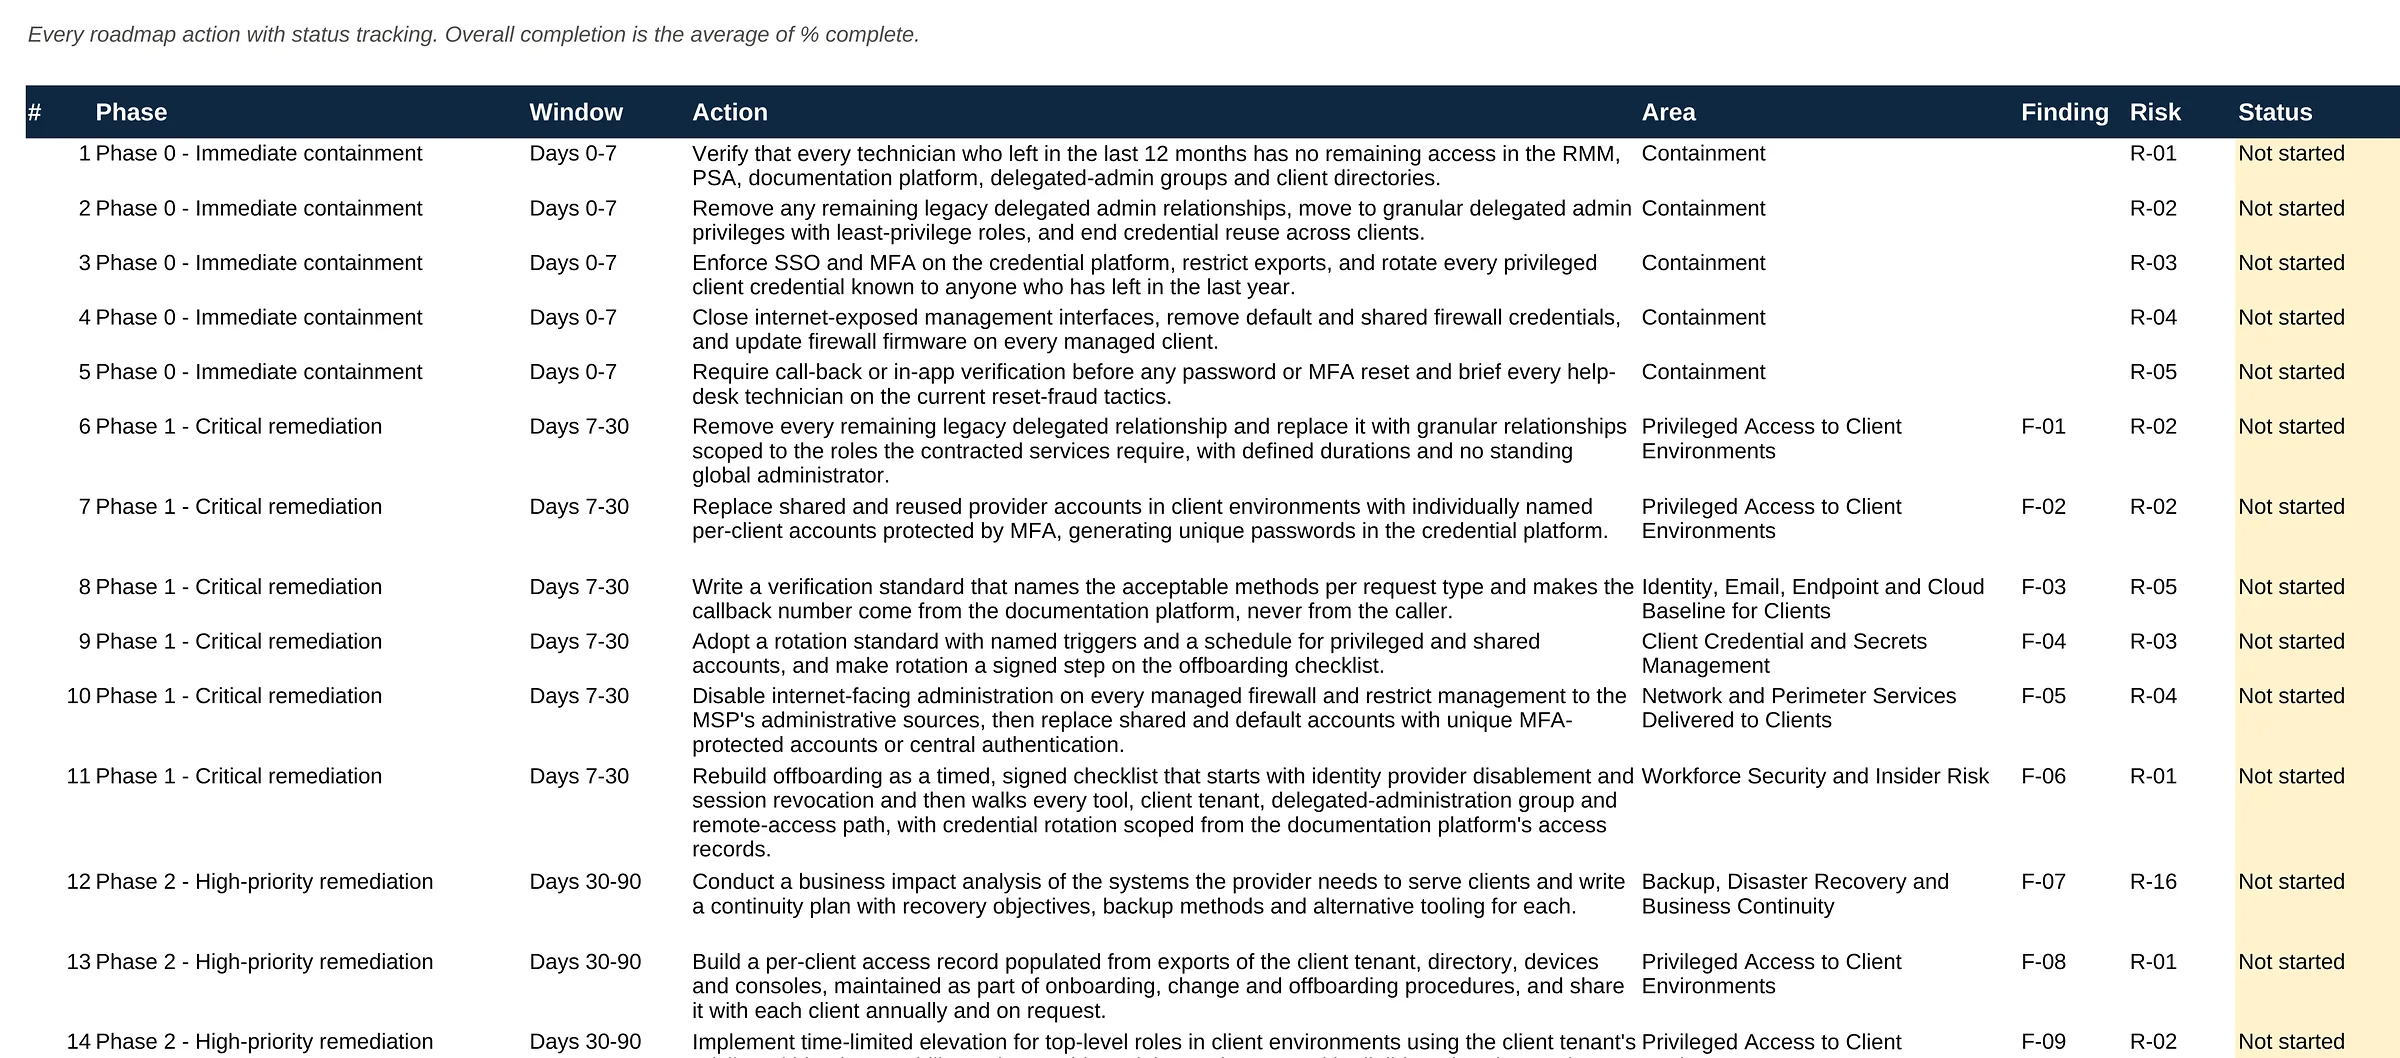
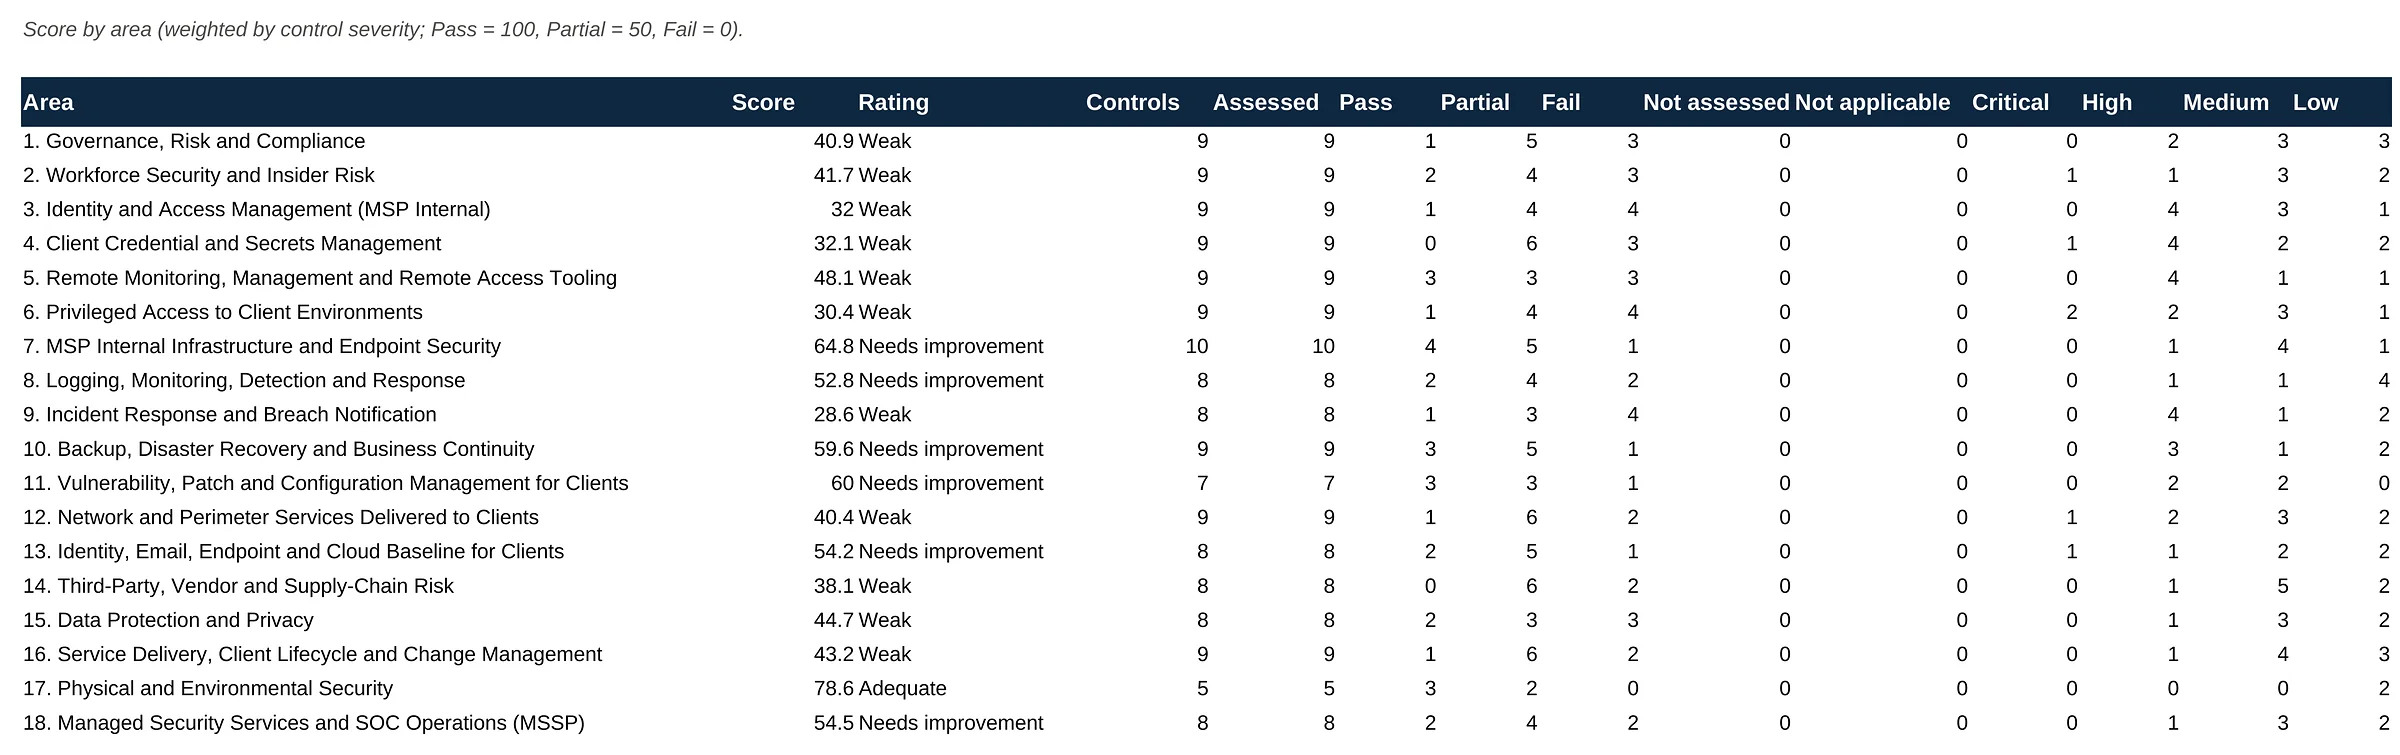
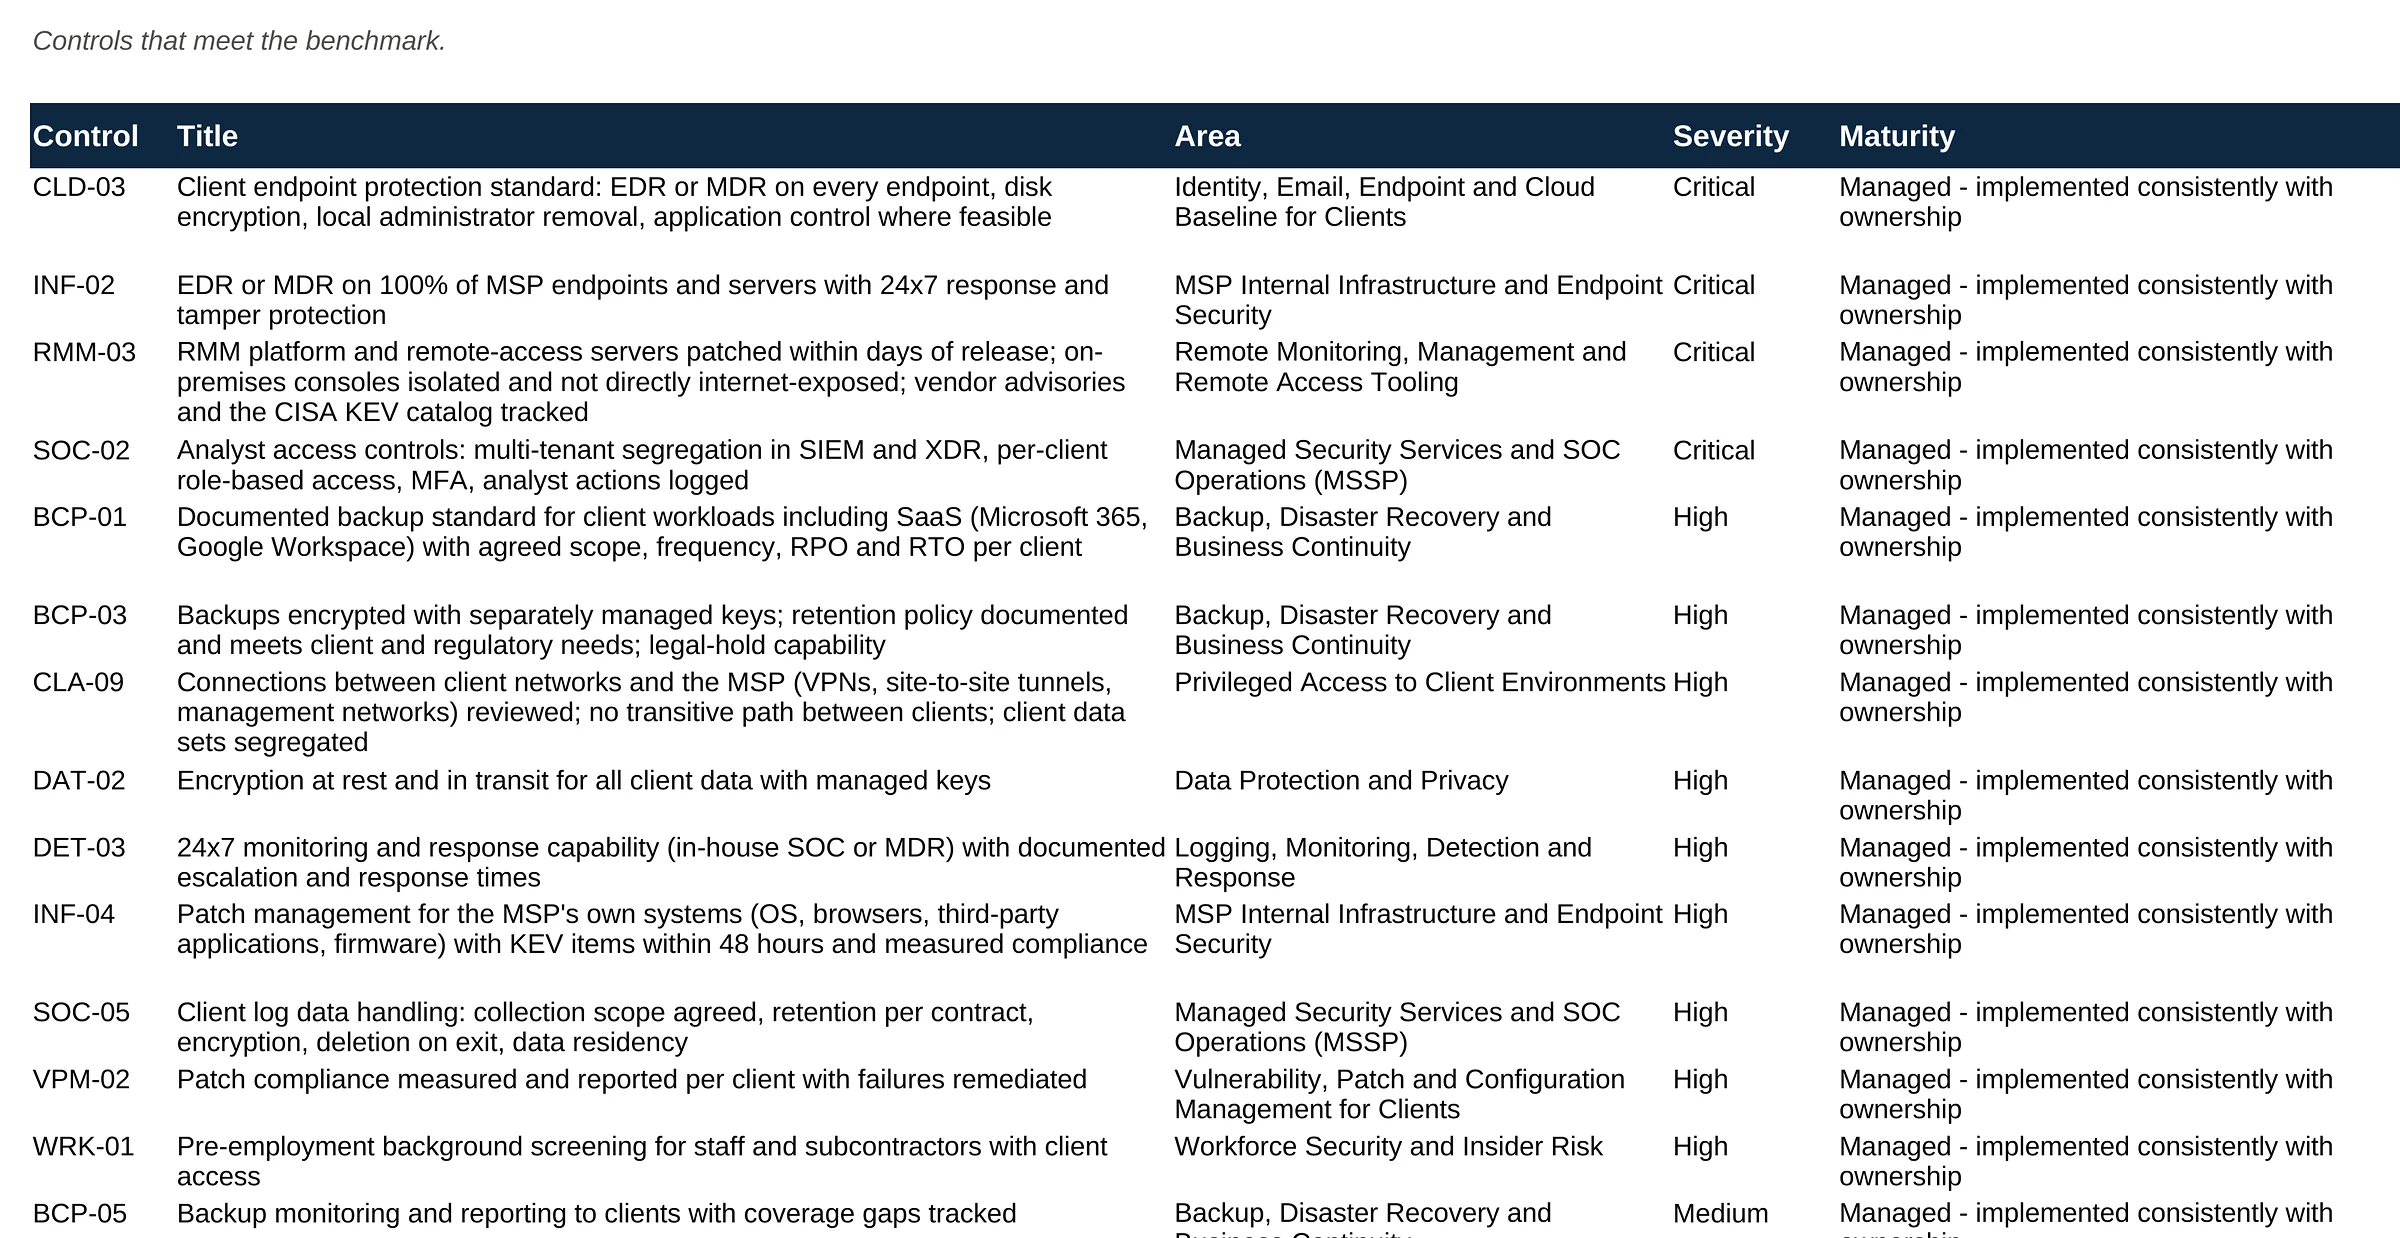
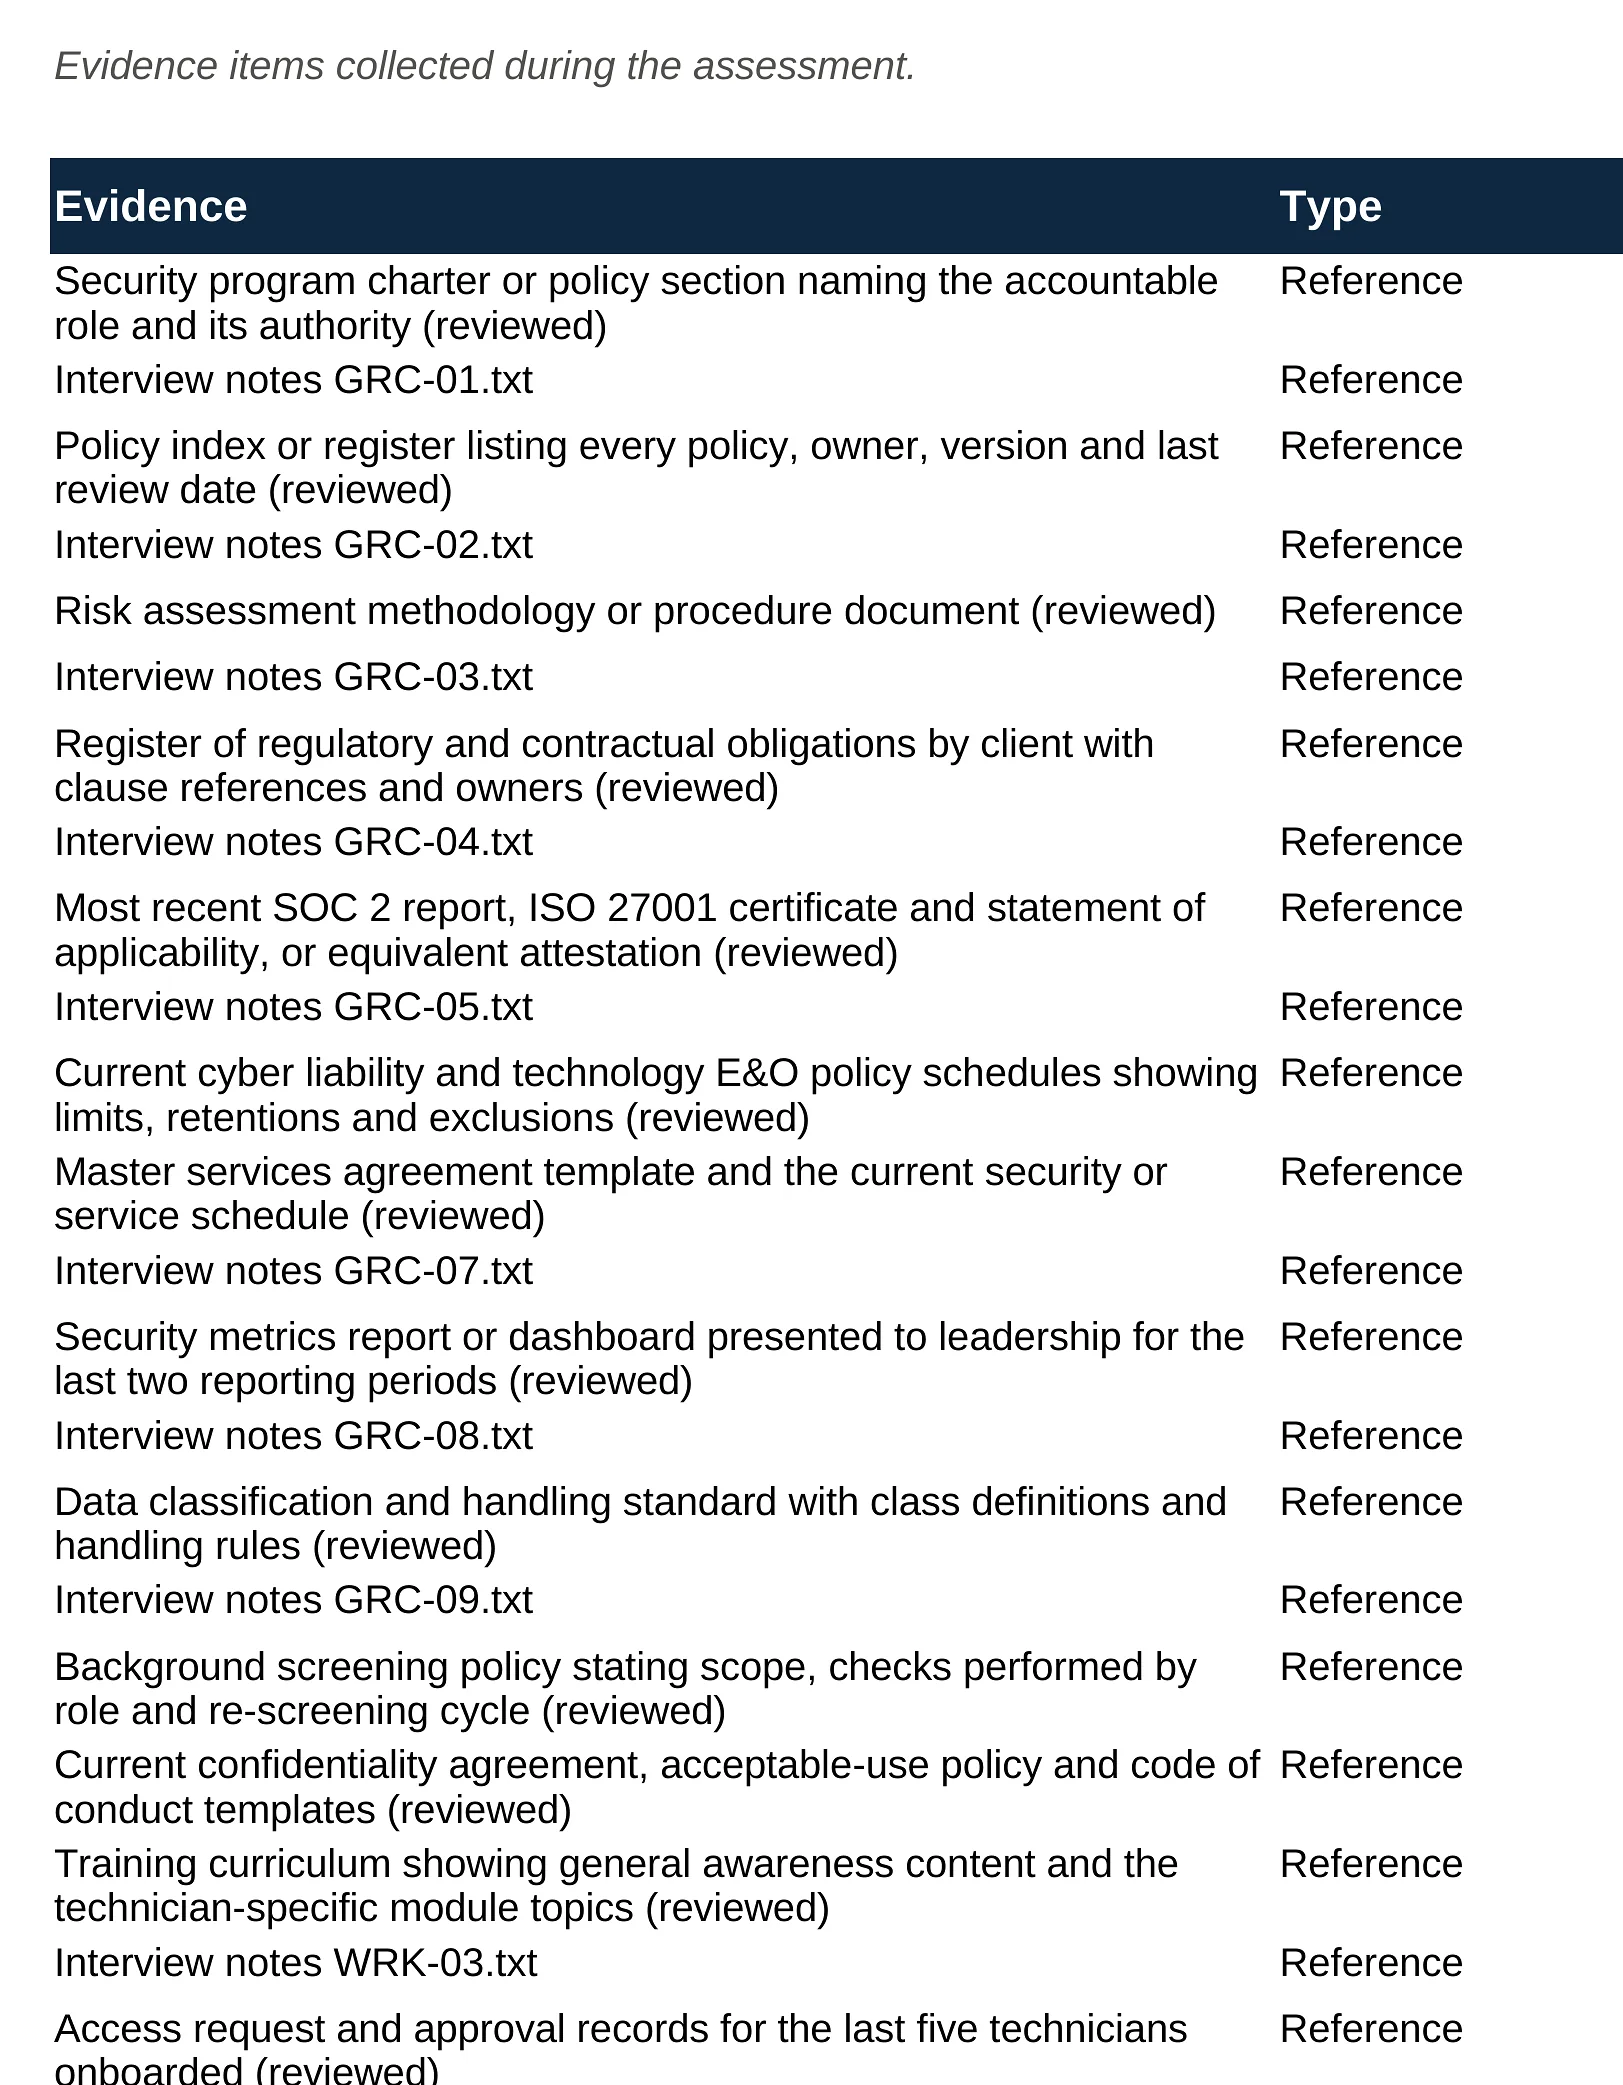
The working file for the remediation. It holds every finding, risk, roadmap action, area score, strength and evidence item in sortable sheets, with yellow input columns for status, owner and due date and summary counts that update as the provider closes items.
Engineers and project managers tracking the fixes week by week.
What is included
- Summary that updates automatically
- Findings ordered by severity
- Risk register with live scoring
- Remediation plan with status
- Domain scores
- Strengths
- Evidence register
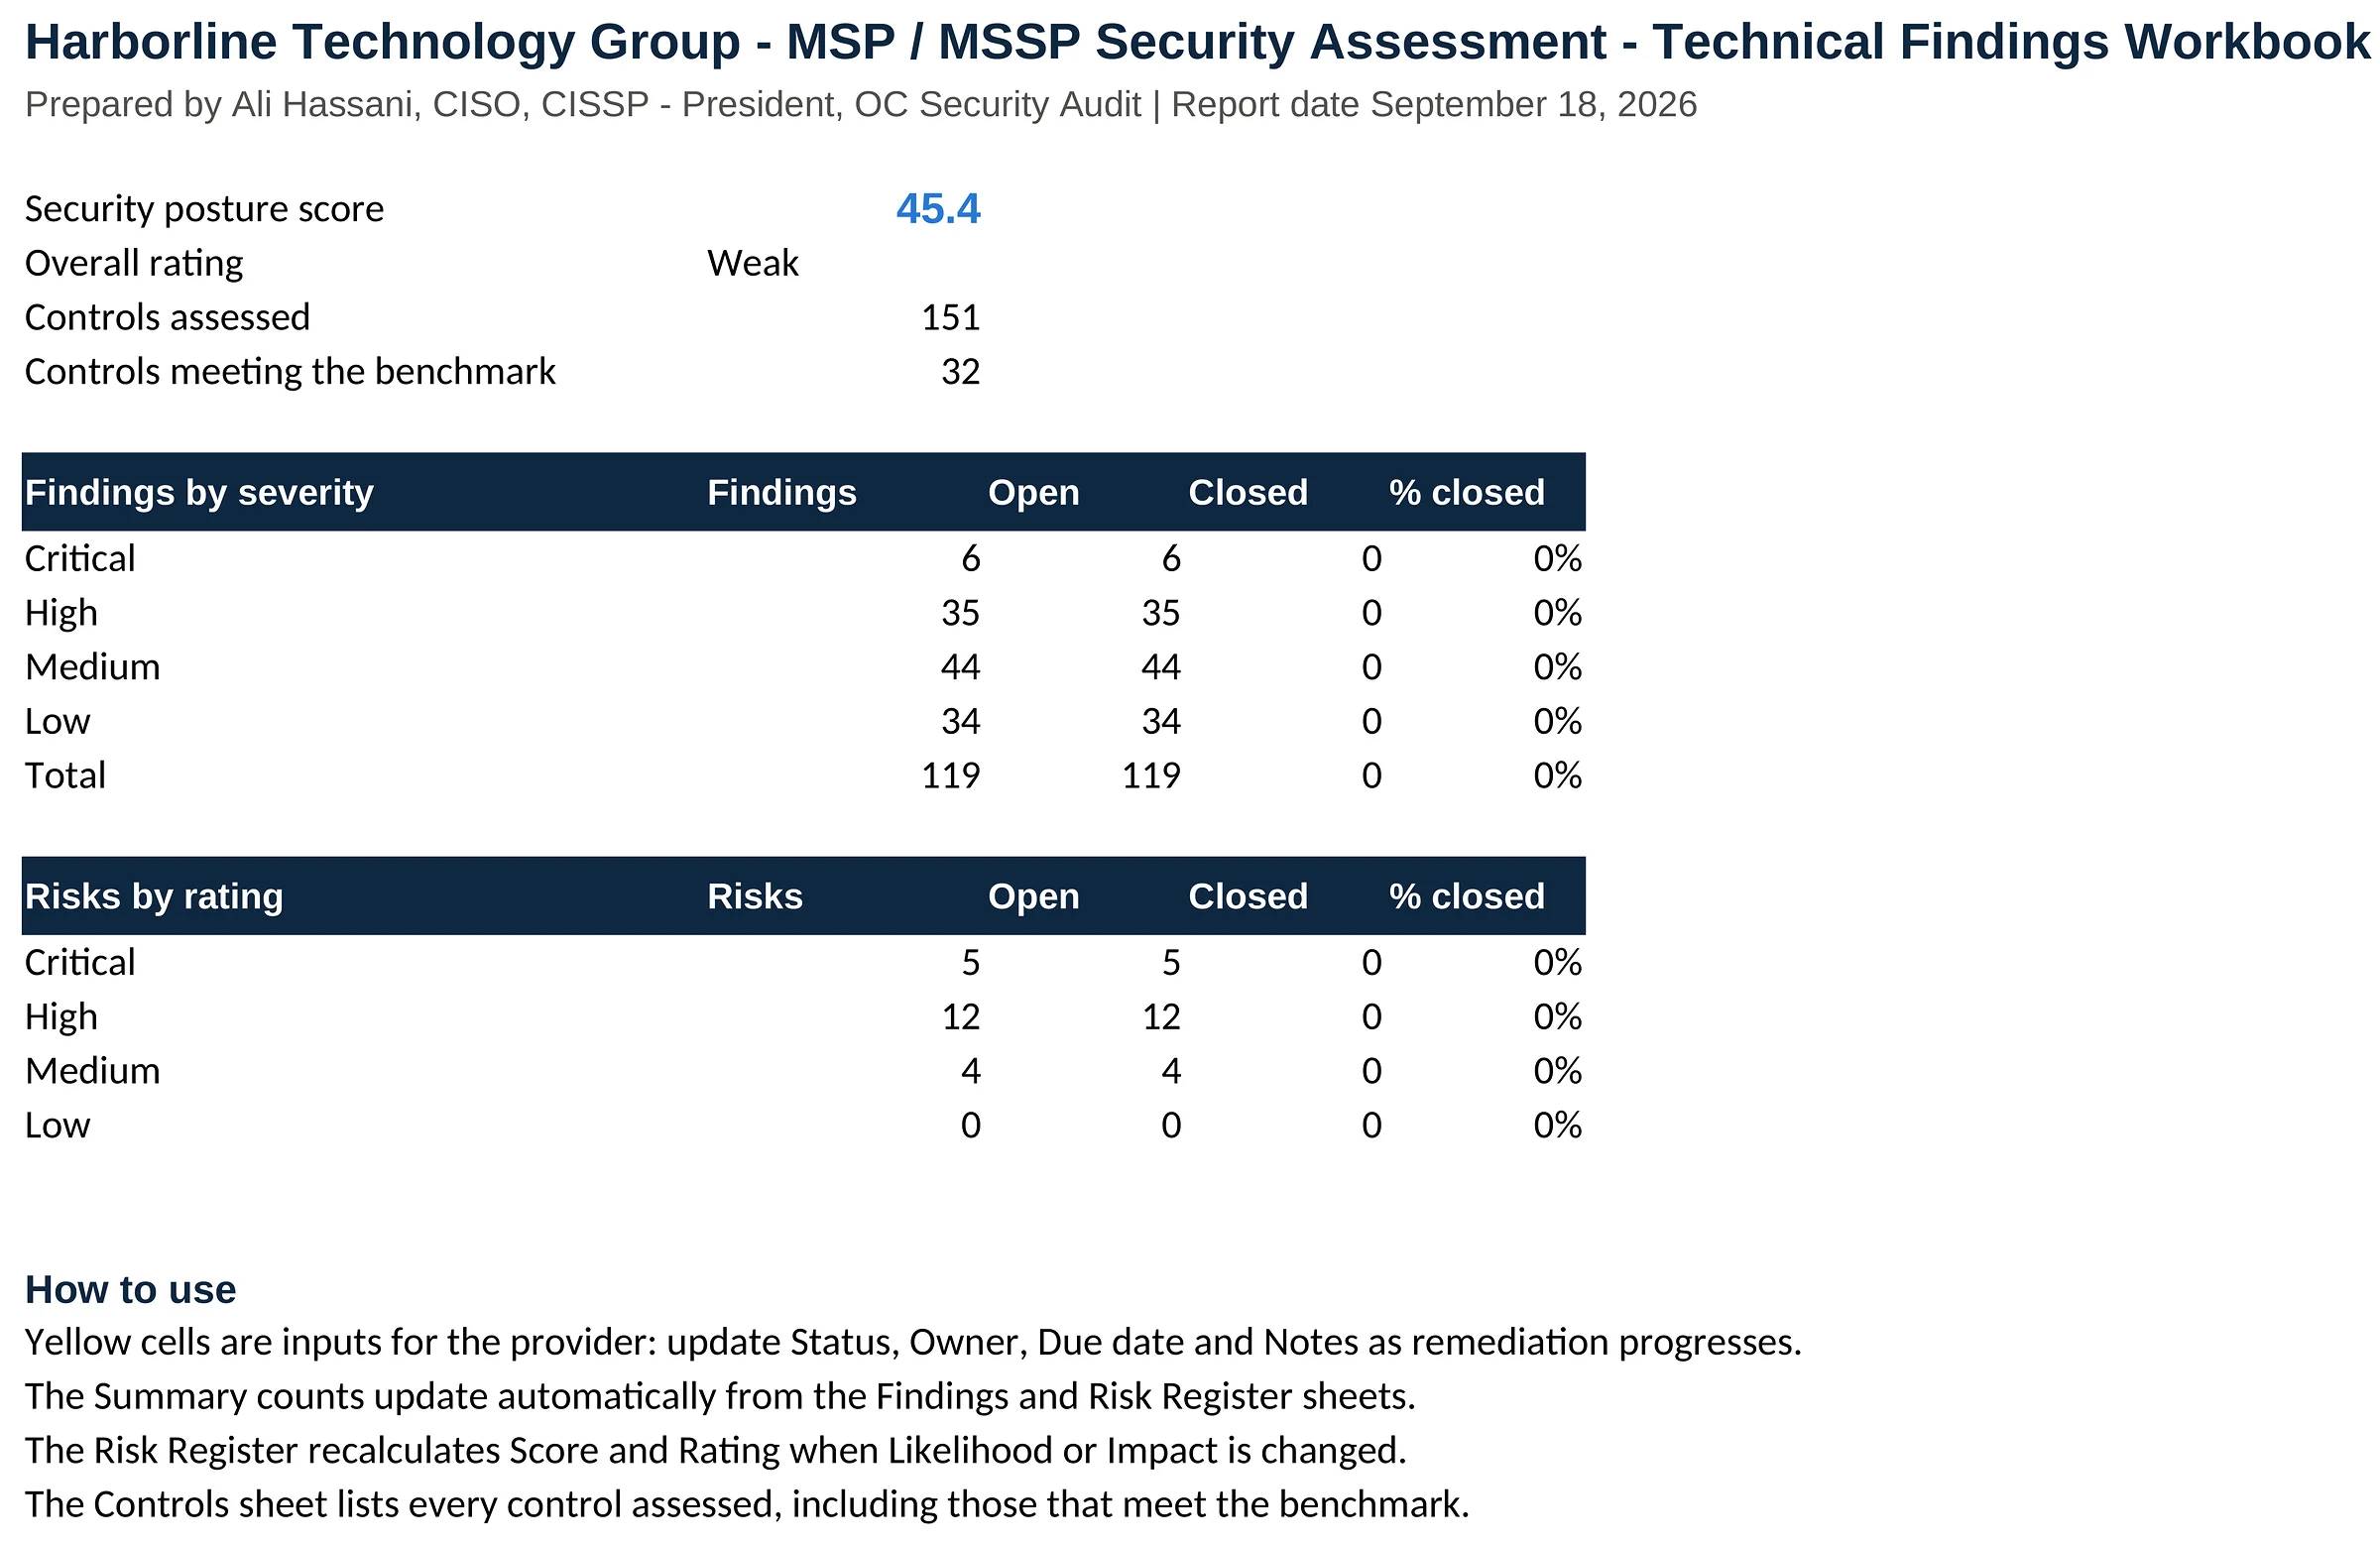
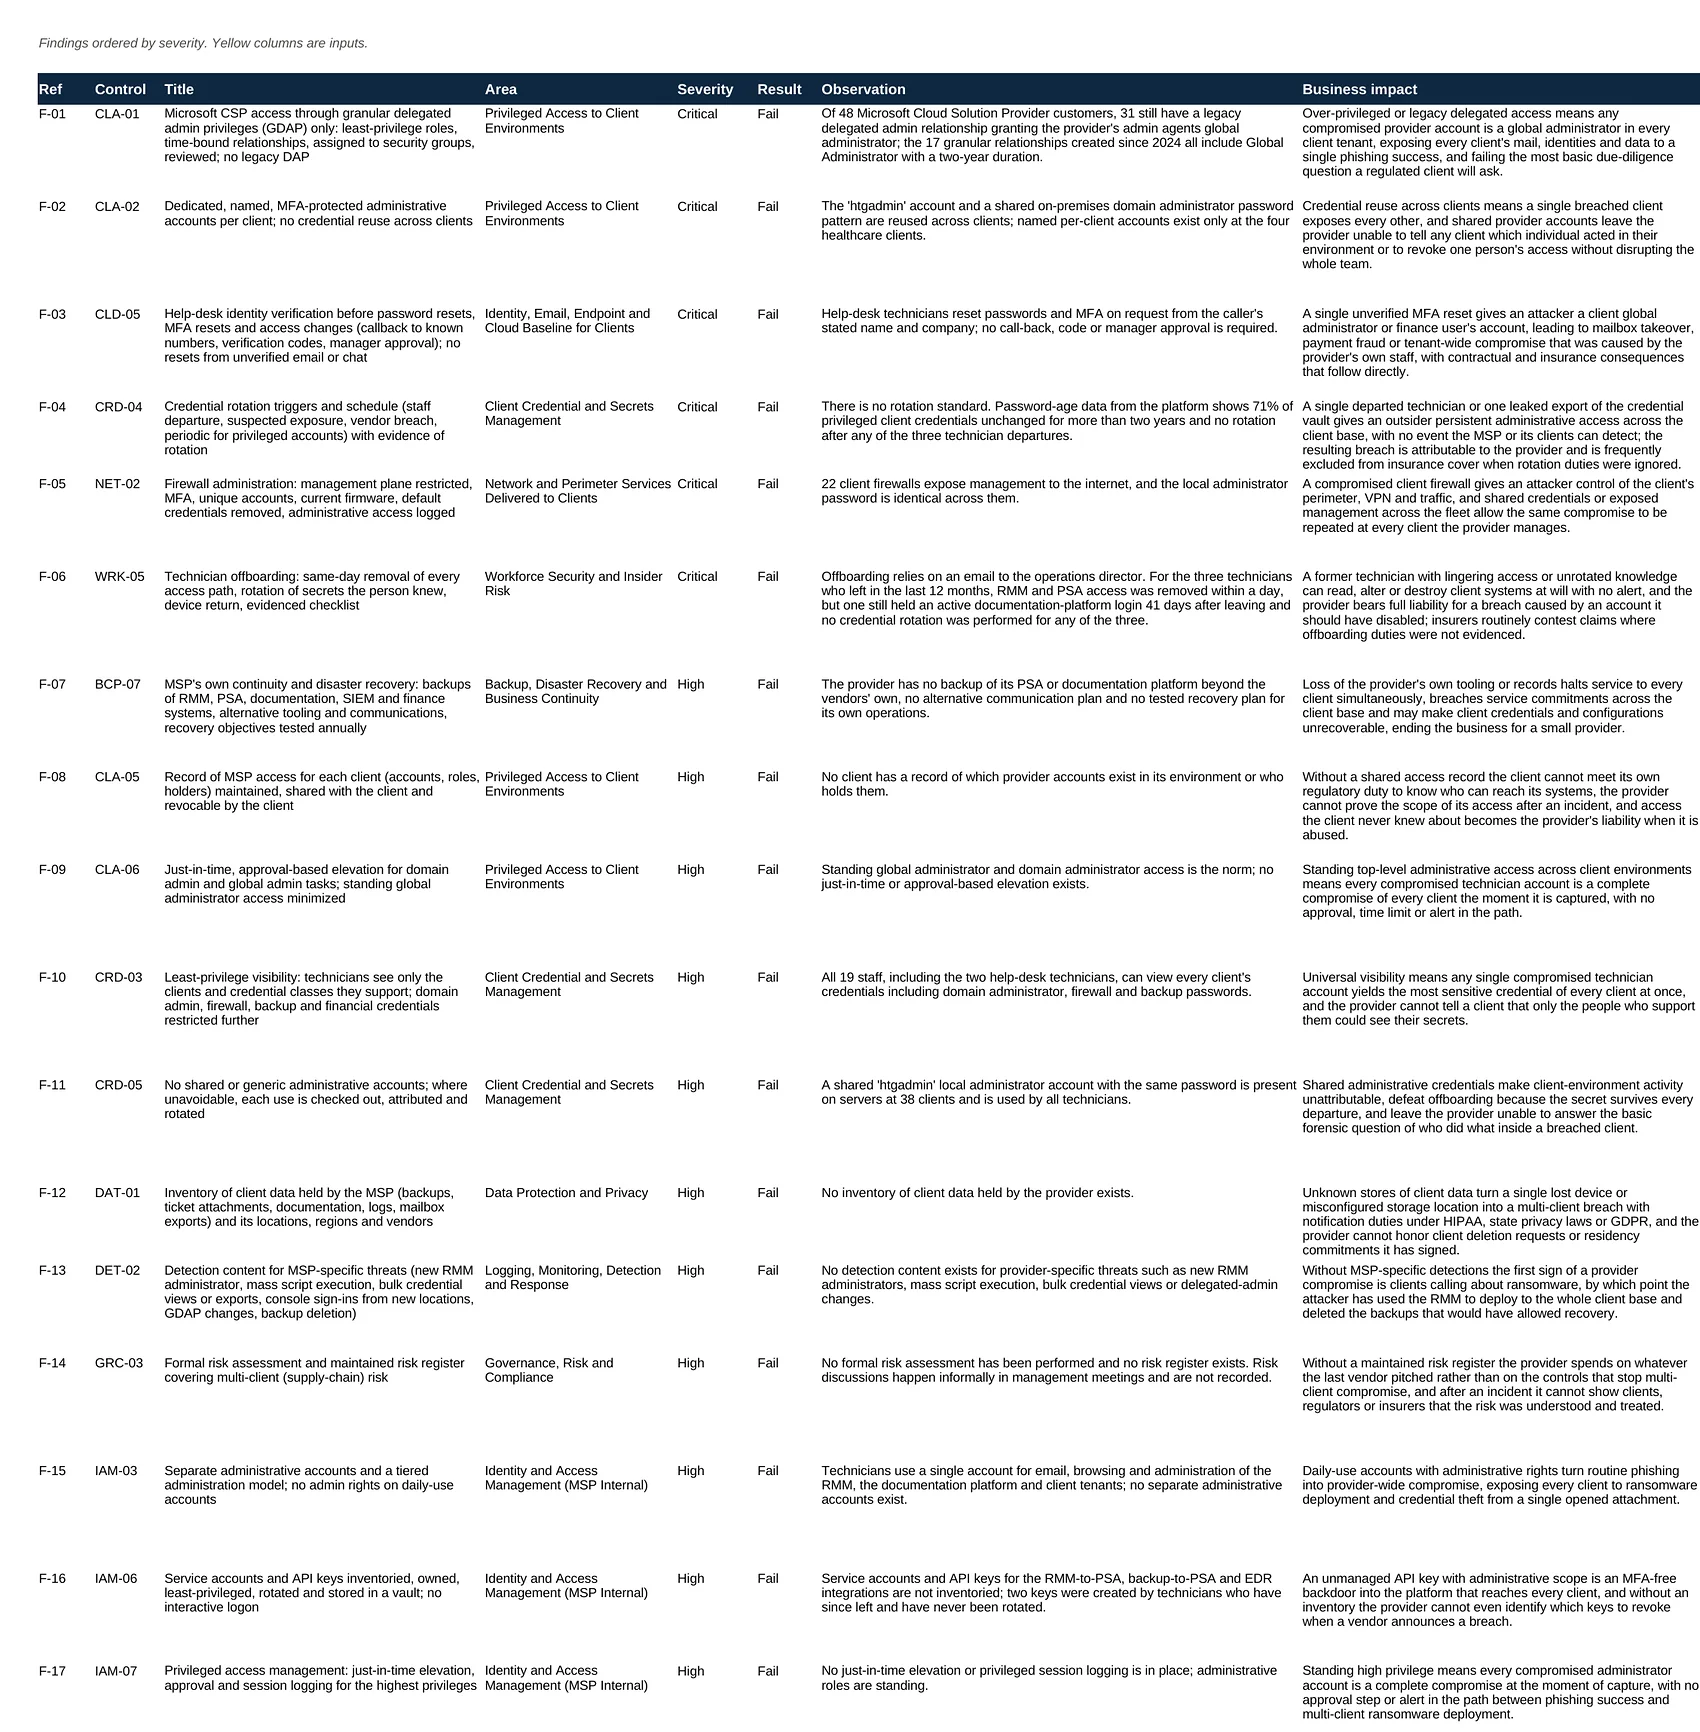
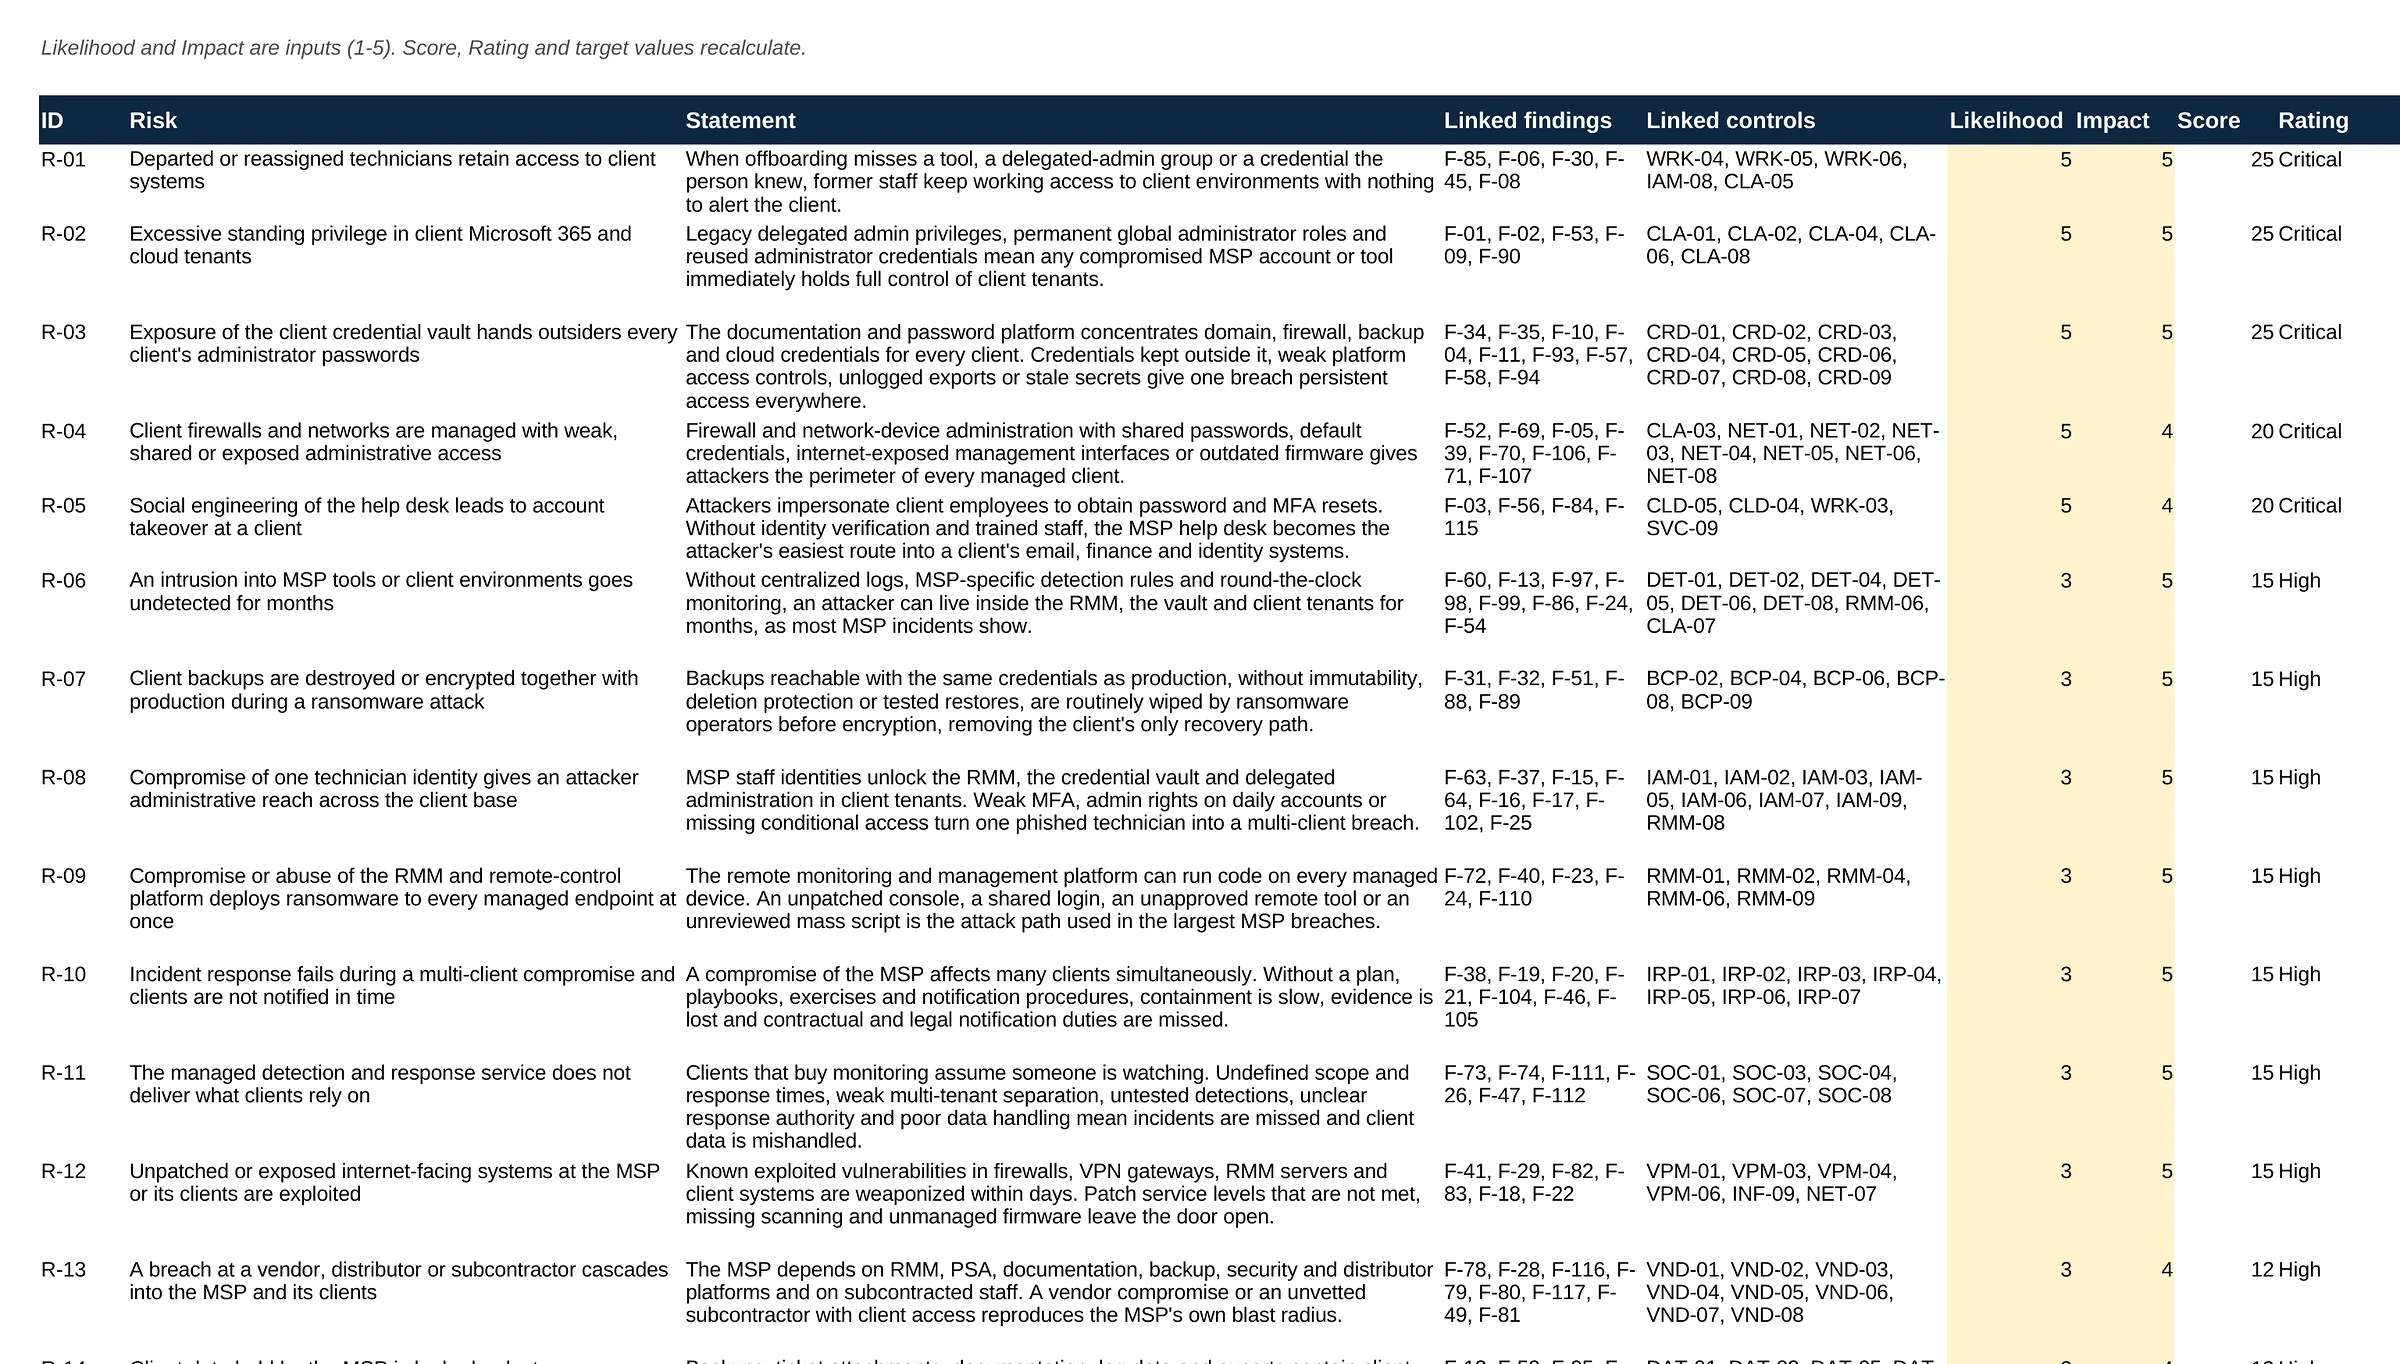
Click the centre page to open it full size and zoom in.
Your own audit
Get these reports for your provider
The MSP Security Audit is CISO-led and read-only, starts at $3,500 for one provider and includes every deliverable above.
Related pages
Continue through the MSP audit
The service
MSP Security Audit
What we audit at a managed service provider, how the work runs and what you receive.
See the audit →
Tooling
RMM and privileged access review
Remote management, the credential vault and delegated admin access into every client tenant.
See the review →
Pricing
Starting at $3,500
One CISO-led audit of the provider, all 18 areas, every deliverable included, priced before work starts.
See pricing →
Who leads the audit
Led by Ali Hassani, CISO
Certified CISO (C|CISO) and CISSP with 25+ years in IT, cybersecurity, compliance and infrastructure, and dozens of Microsoft and Cisco certifications, including MCSE, MCITP, MCSA Security, CCNP and CCNA.
Every MSP security audit is planned, performed and signed by Ali, not handed to a junior analyst. We stay independent: we assess and advise, and your team carries out the fixes, with our help if you want it.
Questions and answers
MSP sample report questions
Is this a real provider’s audit report?
No. Harborline Technology Group is a fictional managed service provider, and every name, figure and observation in the sample is invented. We never publish client data. The structure, depth and format are the same as the reports our clients receive.
Why are there three audits in the sample?
To show a full audit cycle. The first audit sets the baseline, and each re-audit compares every control with the earlier results. The scorecards and the Remediation History show how the score moved from 45.4 to 63.3 and then 68.5 as findings were fixed.
Which deliverables come with every MSP security audit?
The Executive Security Report, Technical Security Report, Risk Register, Next Steps and Security Roadmap, MSP Security Scorecard, Client Exposure Analysis, Certification Readiness report and the Technical Findings Workbook in Excel. The Remediation History is added from the second audit on.
Do we receive Word files or only PDFs?
Both. Reports come as Word and PDF files, and the findings workbook is an Excel file with input columns your team can update as items are closed.
Does the Certification Readiness report mean we are certified?
No. It is a readiness indicator calculated from the audit results. Certification and attestation decisions are made by the programs’ own auditors, such as a CPA firm for SOC 2 or an accredited body for ISO/IEC 27001.
How much does the audit that produces these reports cost?
The MSP Security Audit starts at $3,500 for one provider and includes every deliverable shown on this page for that audit.
See what your own reports would say
Book a short call to confirm your scope and price in writing before any work starts.
Or call 949-777-5567