
SAMPLENIST 800-53 assessment sample report
NIST 800-53 assessment sample report
Every deliverable of a real NIST SP 800-53 assessment, built for a fictional company, page by page.
Our deliverables
Five deliverables from one NIST 800-53 assessment
This is what a NIST 800-53 assessment from OC Security Audit produces. The sample was built for a fictional organization that runs a case-management platform for state and county agencies on Microsoft Azure, categorized FIPS 199 Moderate. This NIST 800-53 sample report lets you step through every key page below; open any page full size and zoom in to read it.
Sample report. Fabrikam Civic Systems is a fictional organization. Every name, account, address and figure in these pages is invented for illustration and does not describe any real customer.
PDF and Word · 9 pages
Executive Security Report
The decision document for leadership. It gives the overall implementation score and rating, the business risks that matter most, how an attacker could chain the weaknesses, posture by control family, what already works, the ten priority actions and the decisions only leadership can make. It is written in plain language for people who will not read the technical detail.
Owners, executives and the board; also what you share with a government customer that asks for a summary.
What is included
- Executive summary and implementation score
- Top business risks with scores
- Attack chain built from real findings
- Posture by control family
- What is working well
- Ten priority recommendations
- 180-day roadmap at a glance
- Decisions requested from leadership
- Scope, method and limits
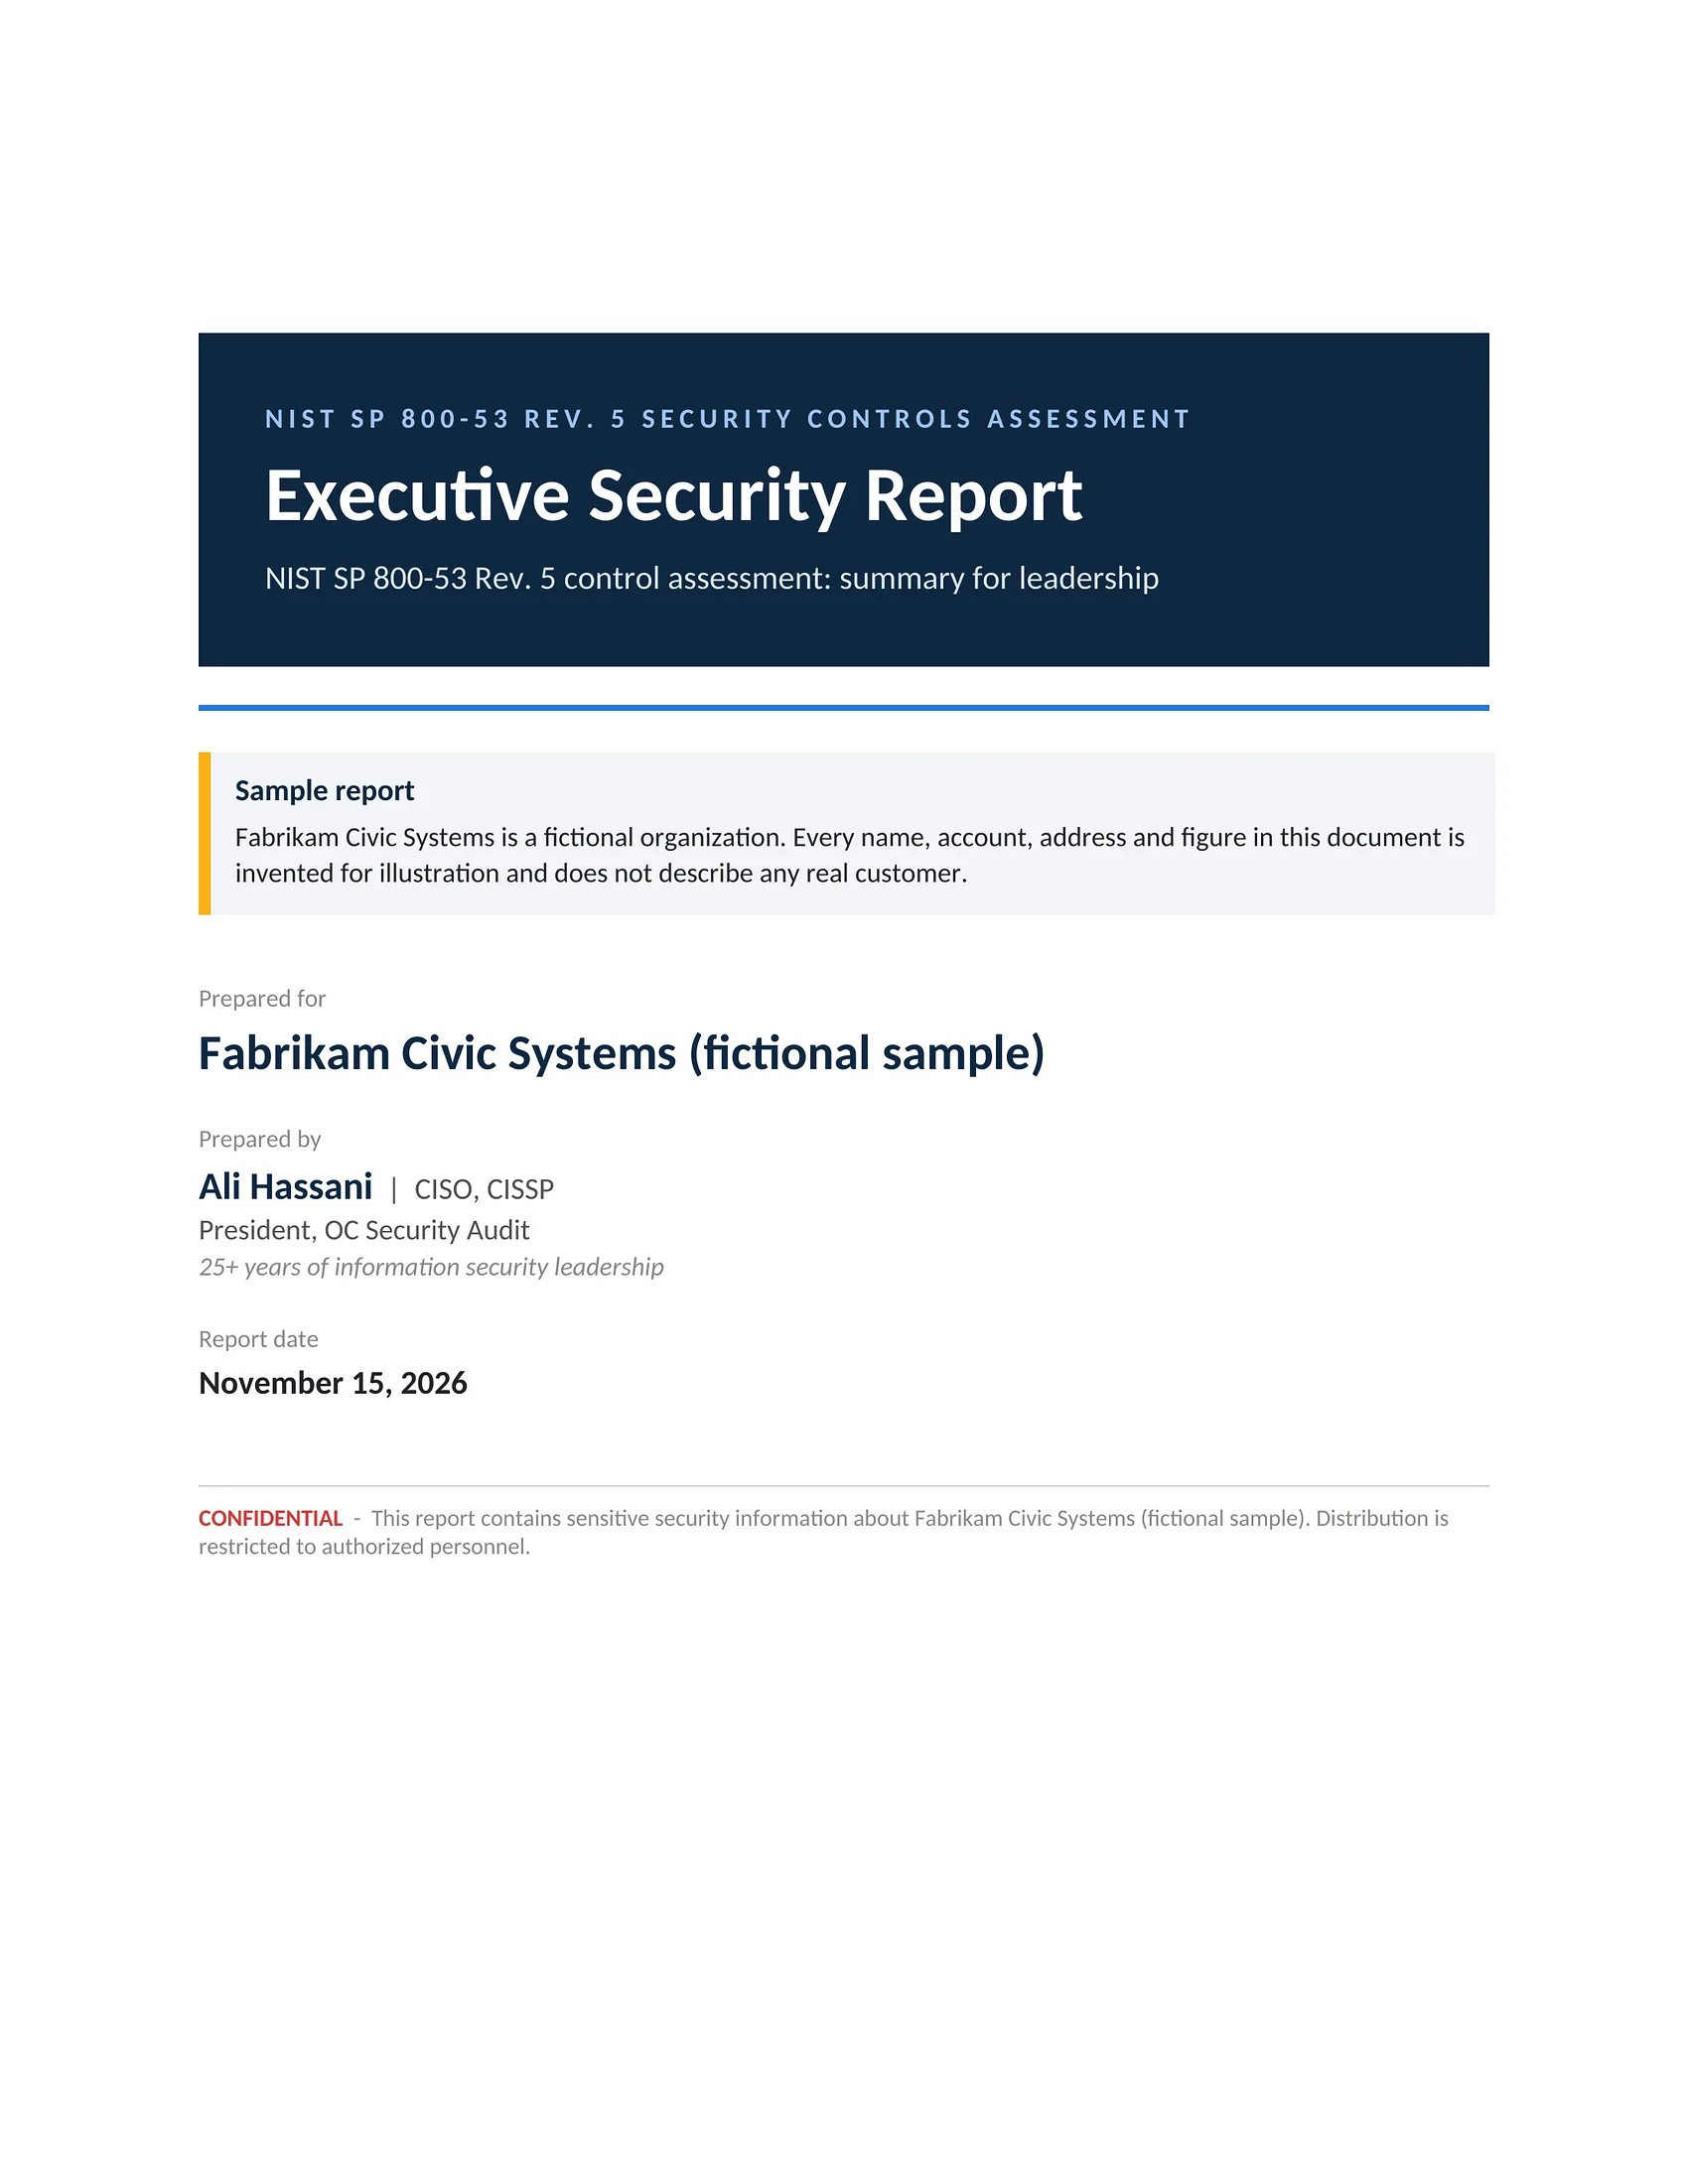
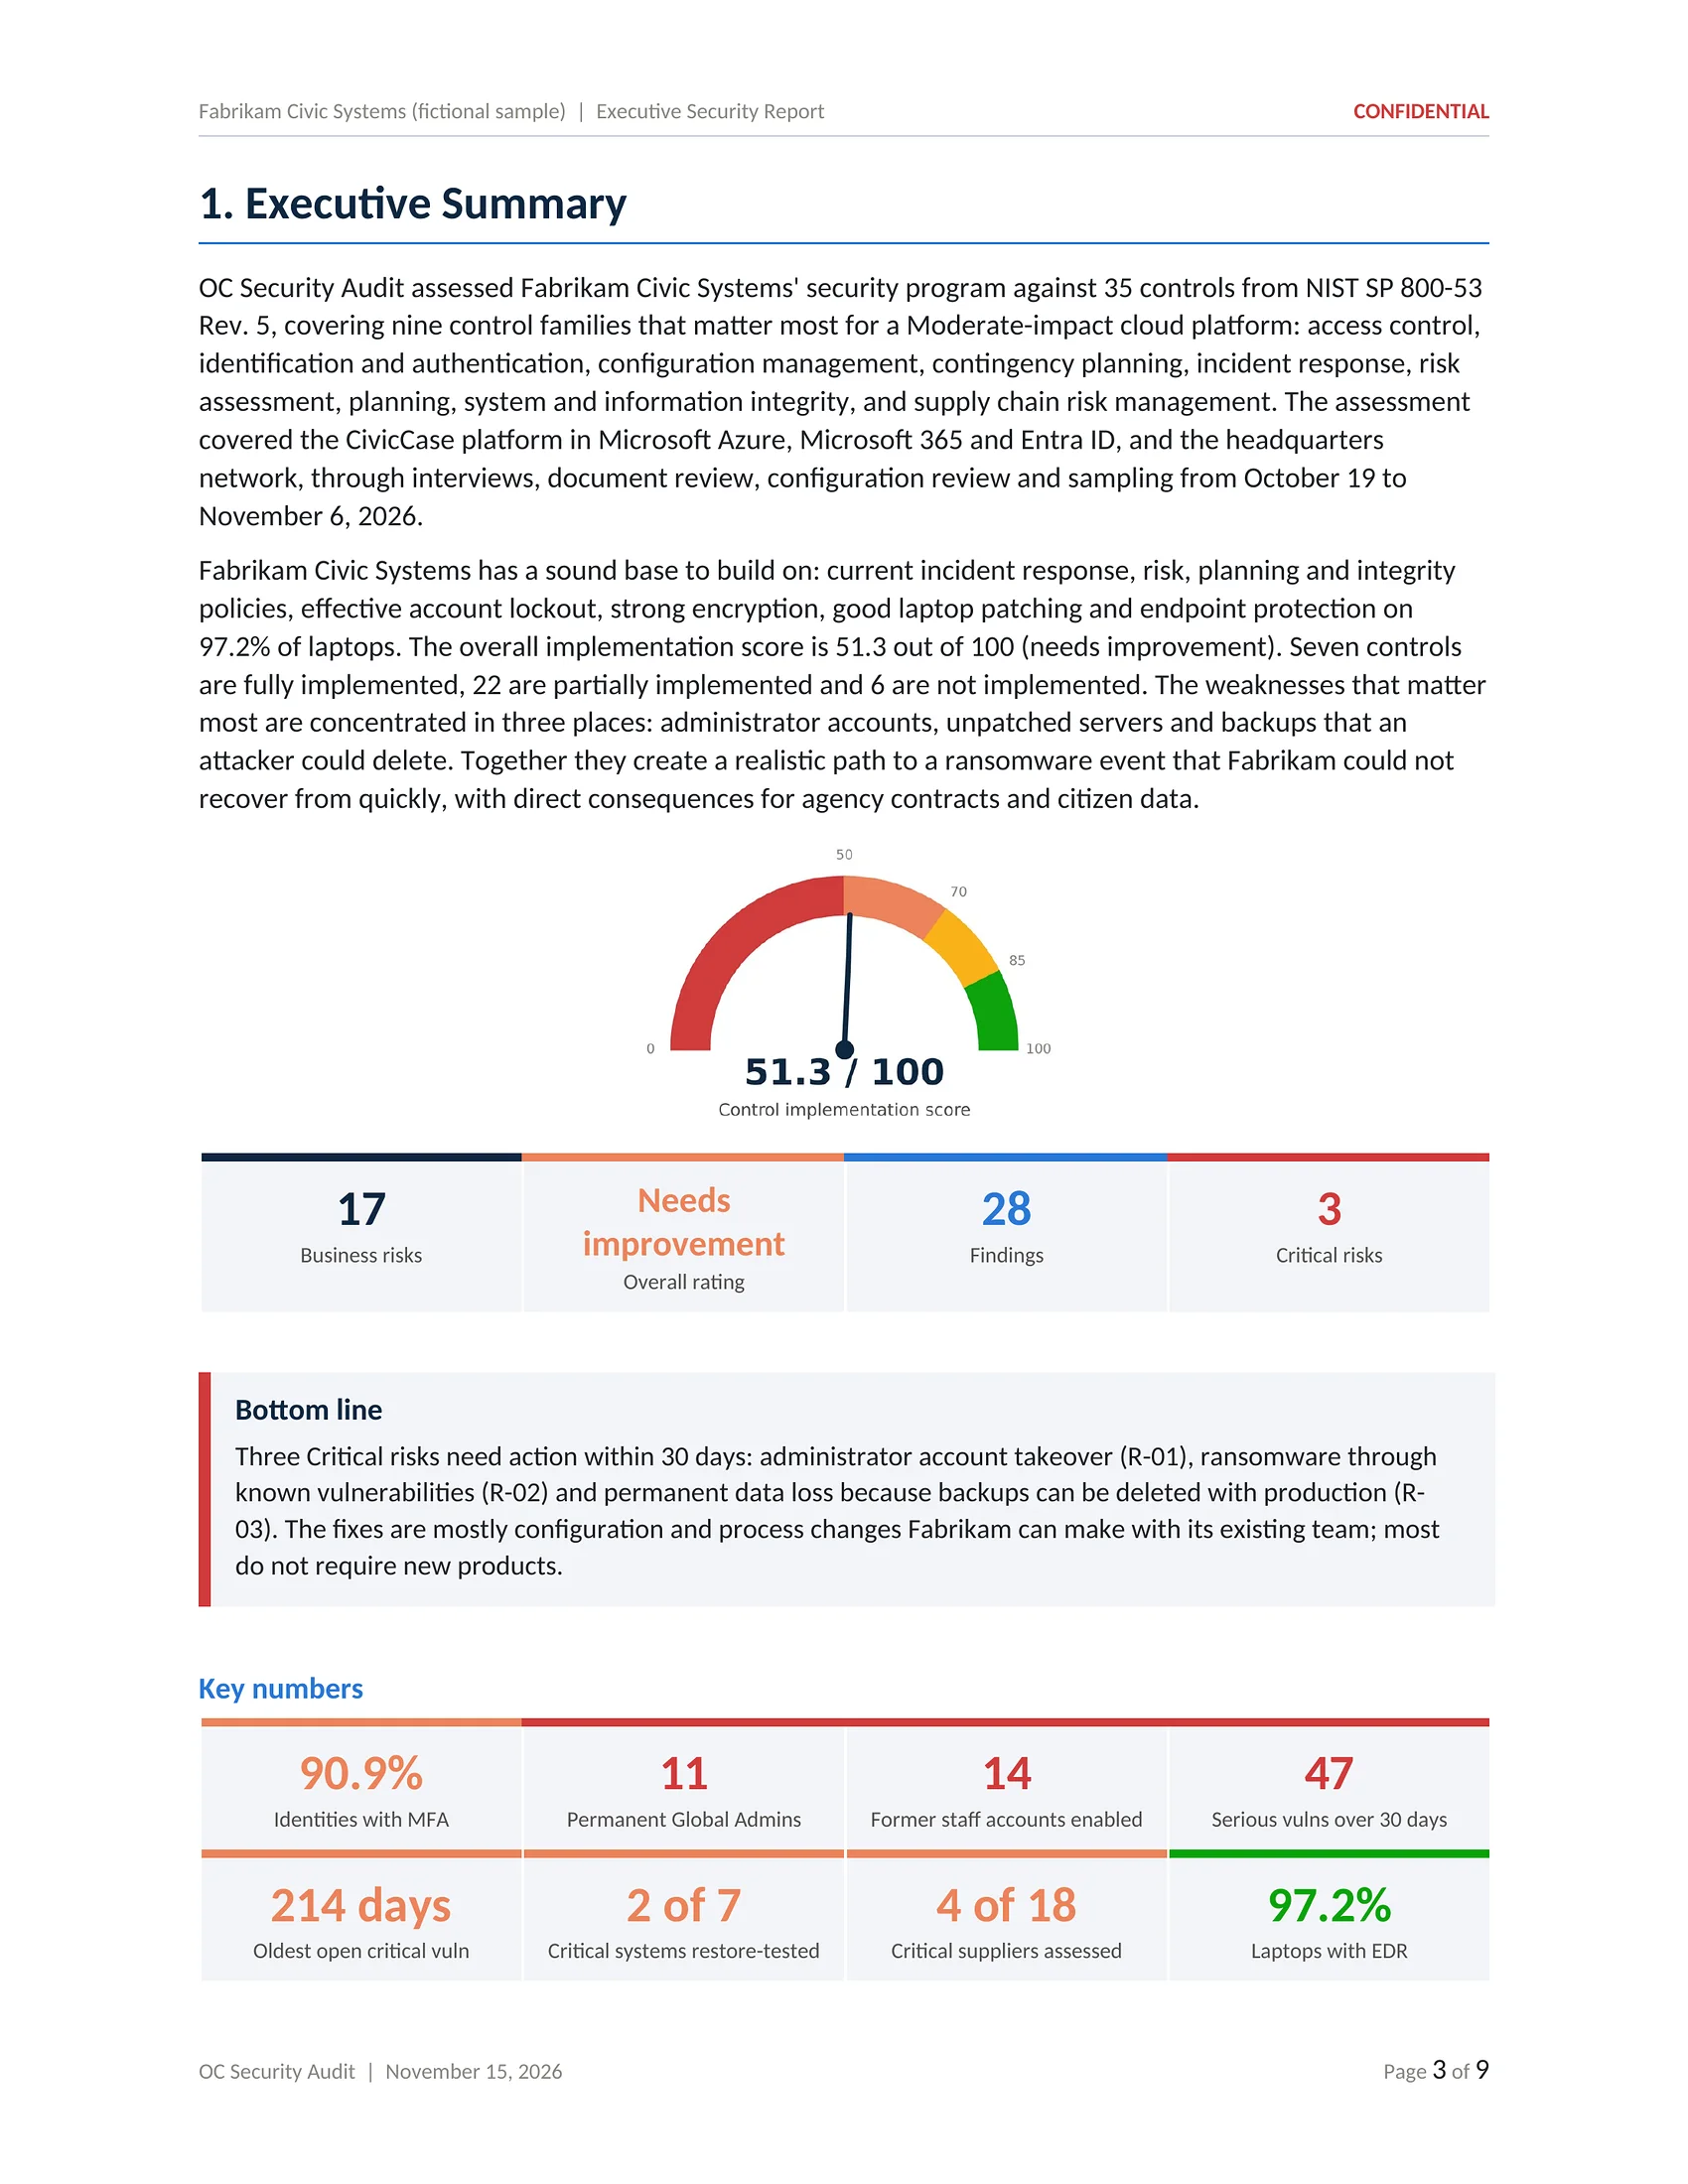
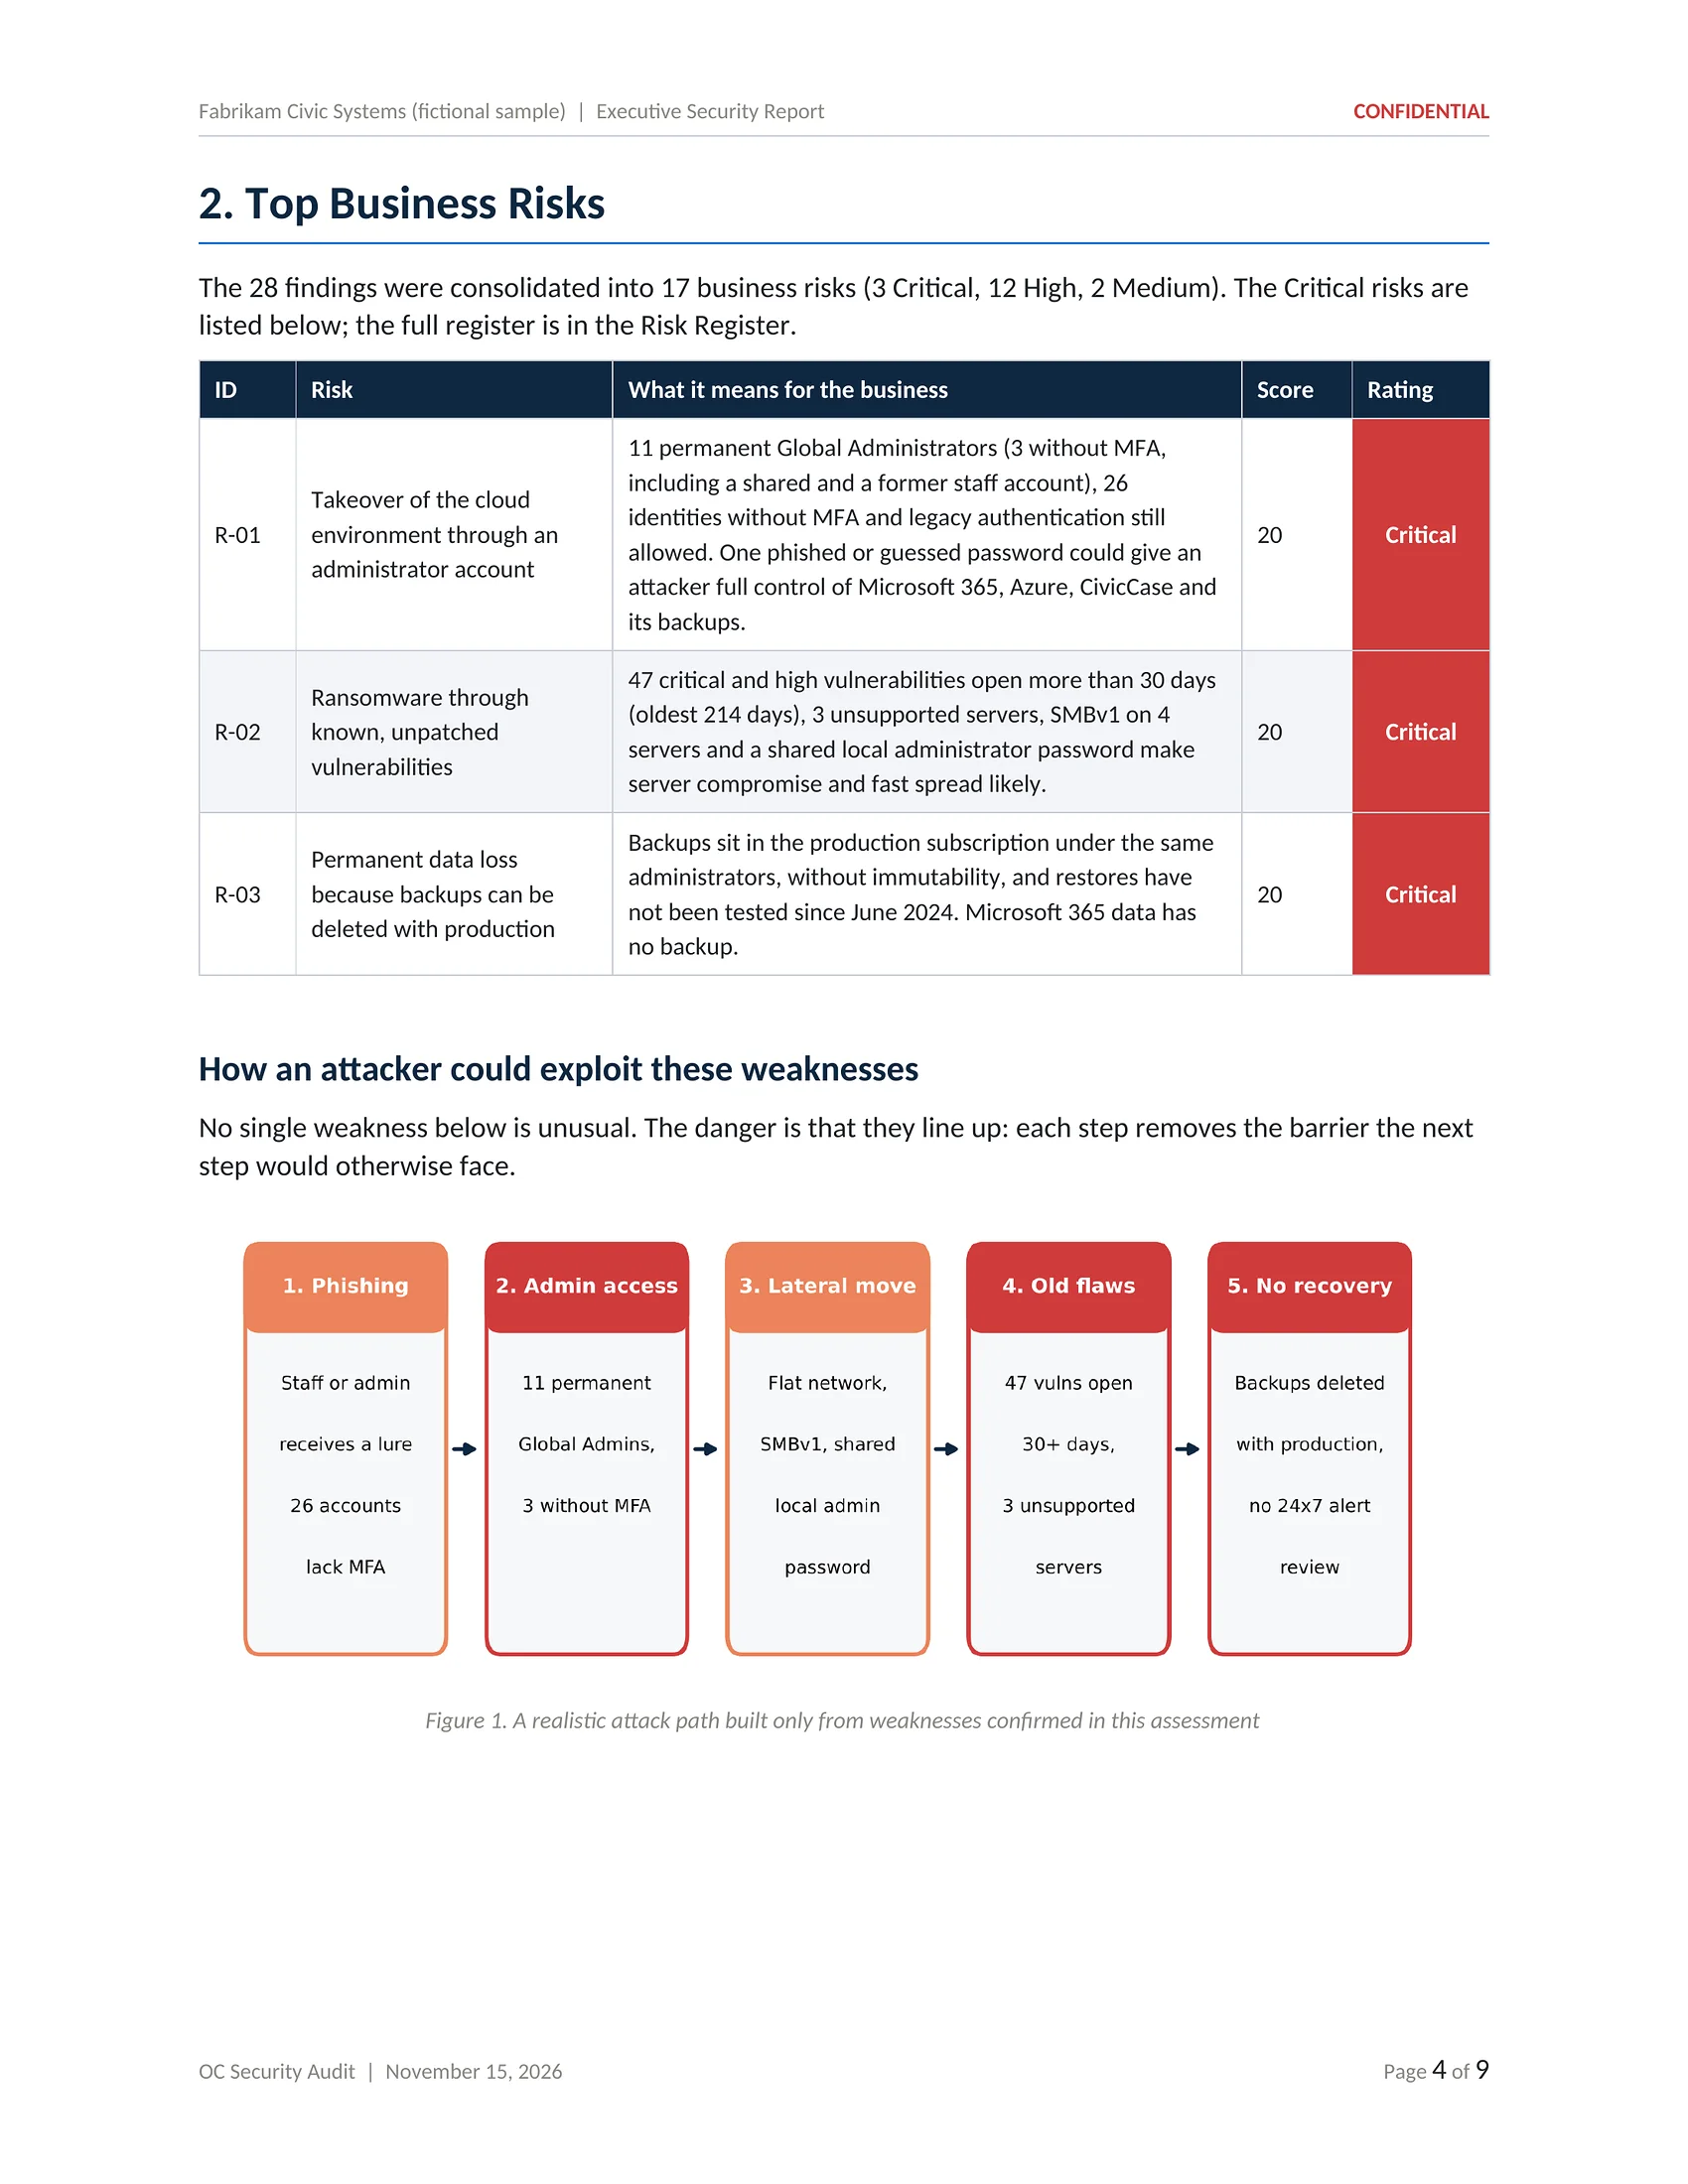
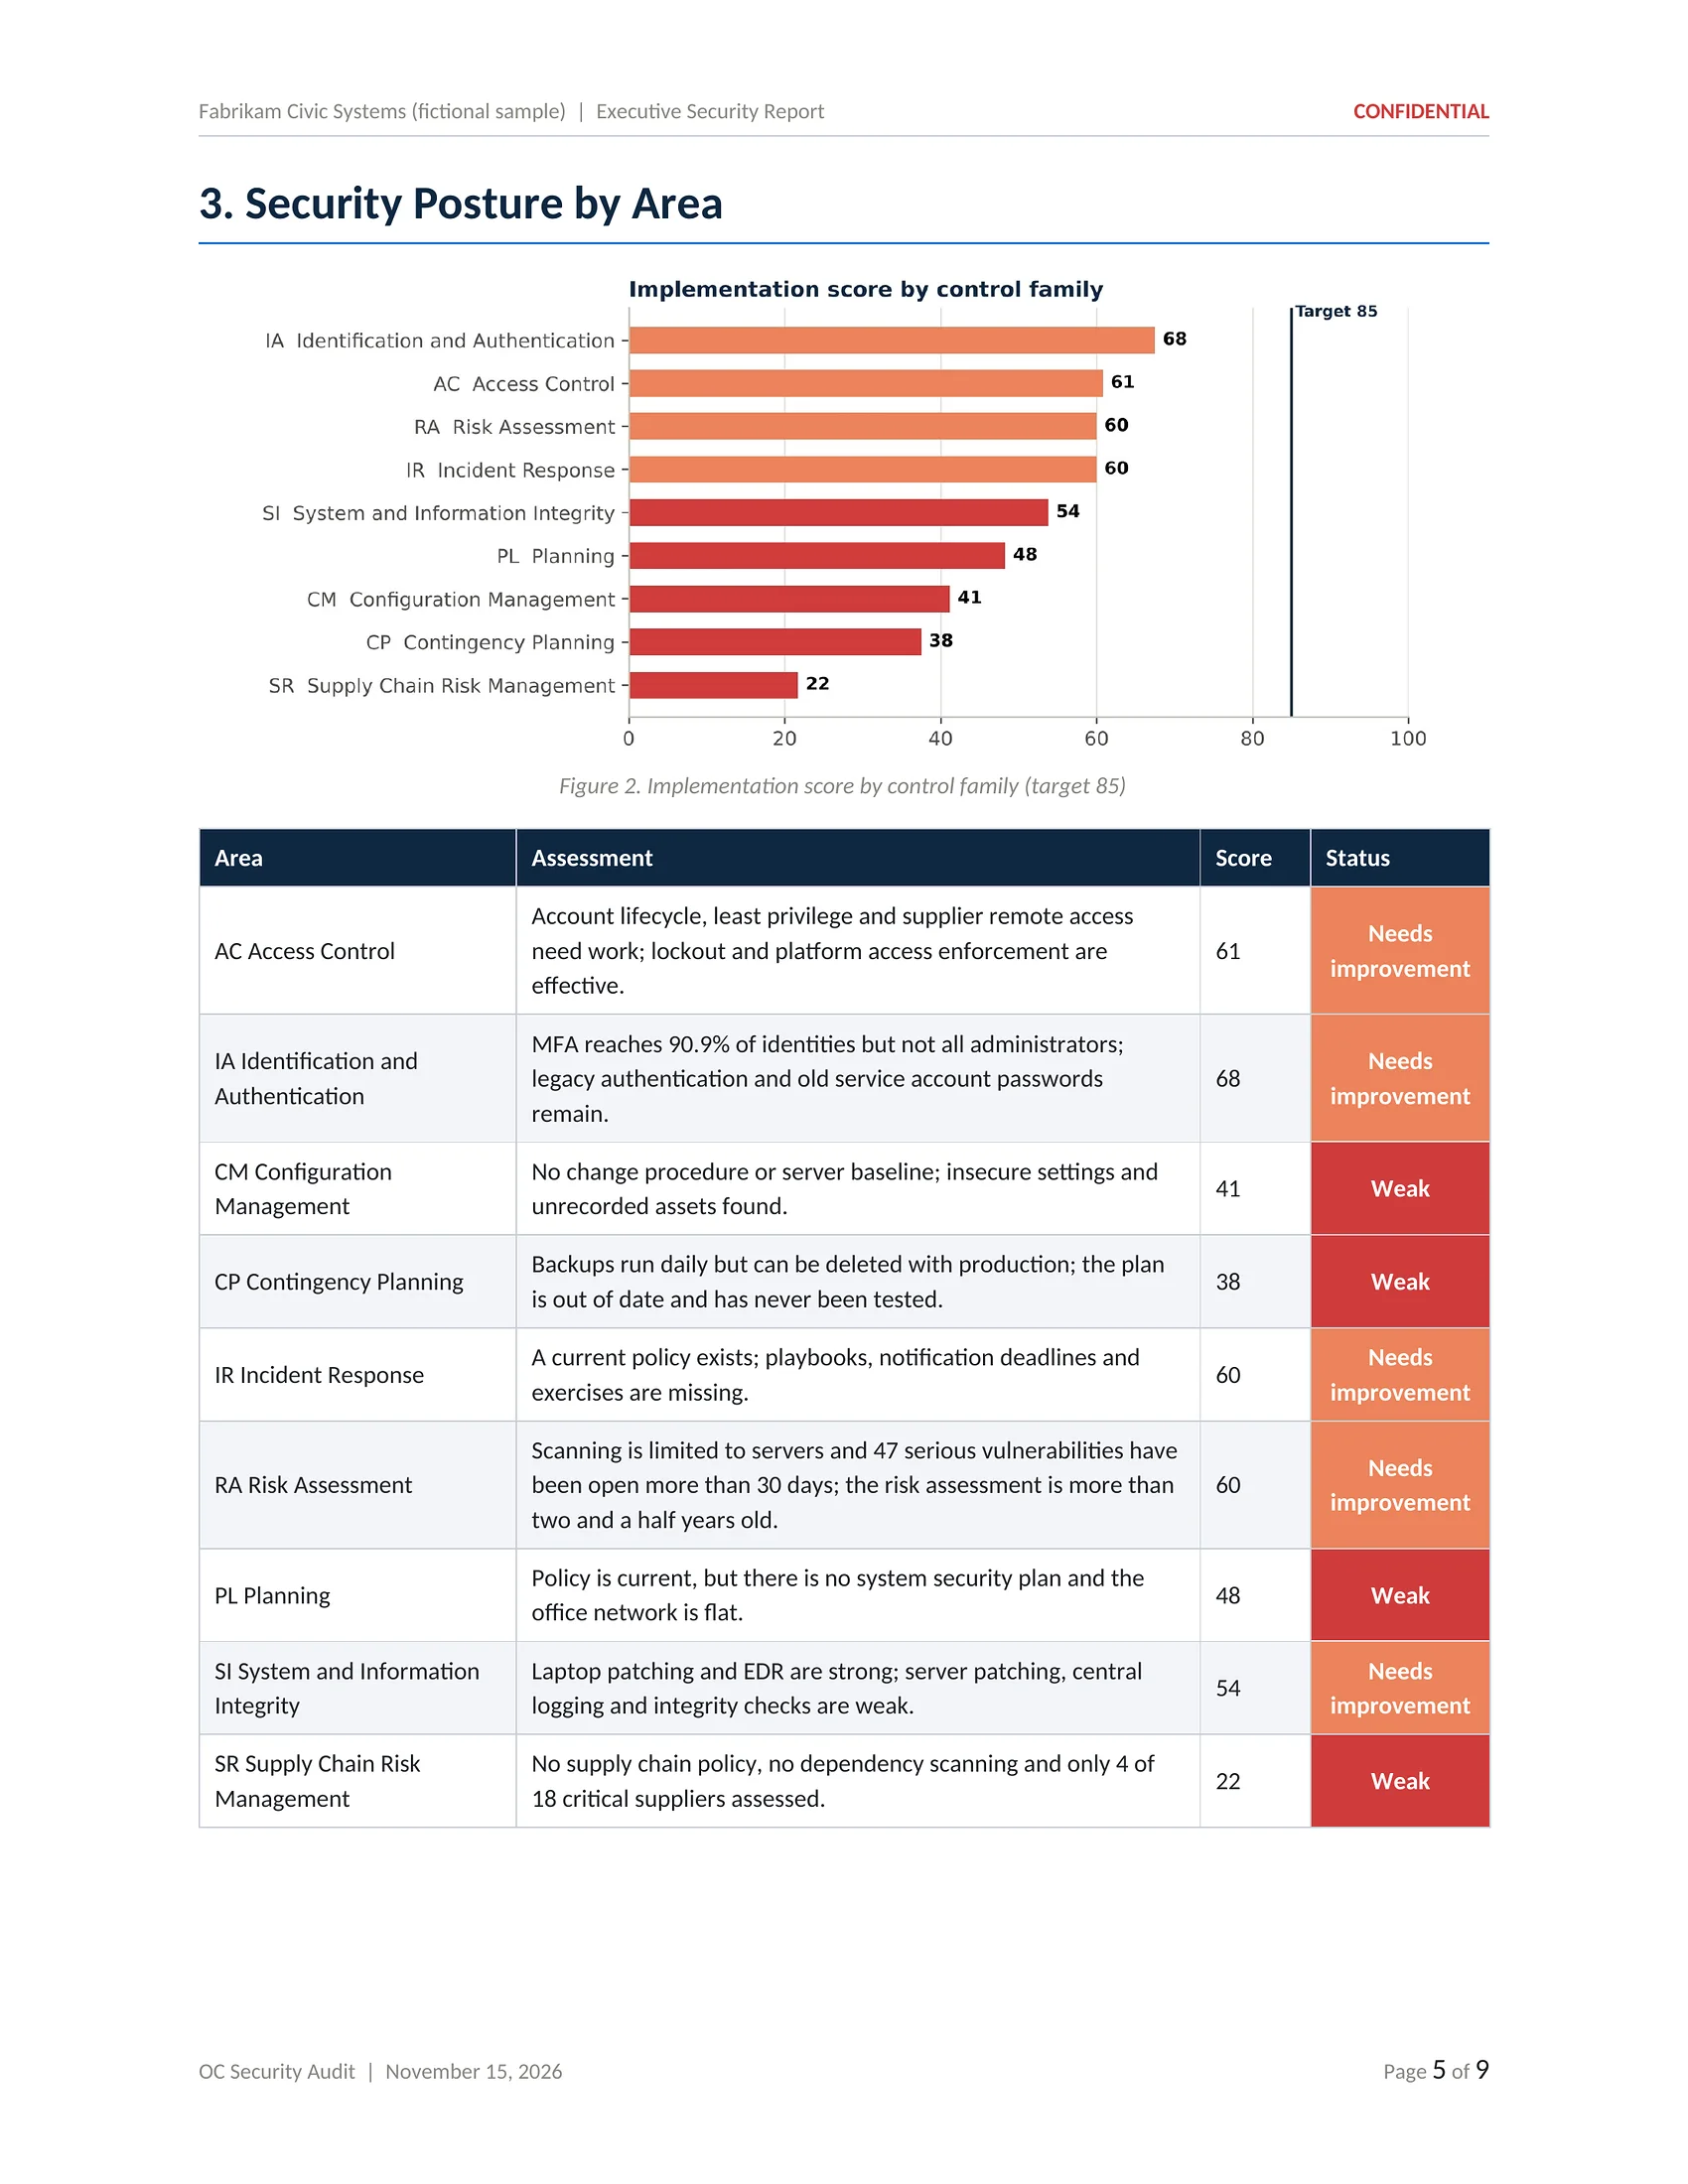
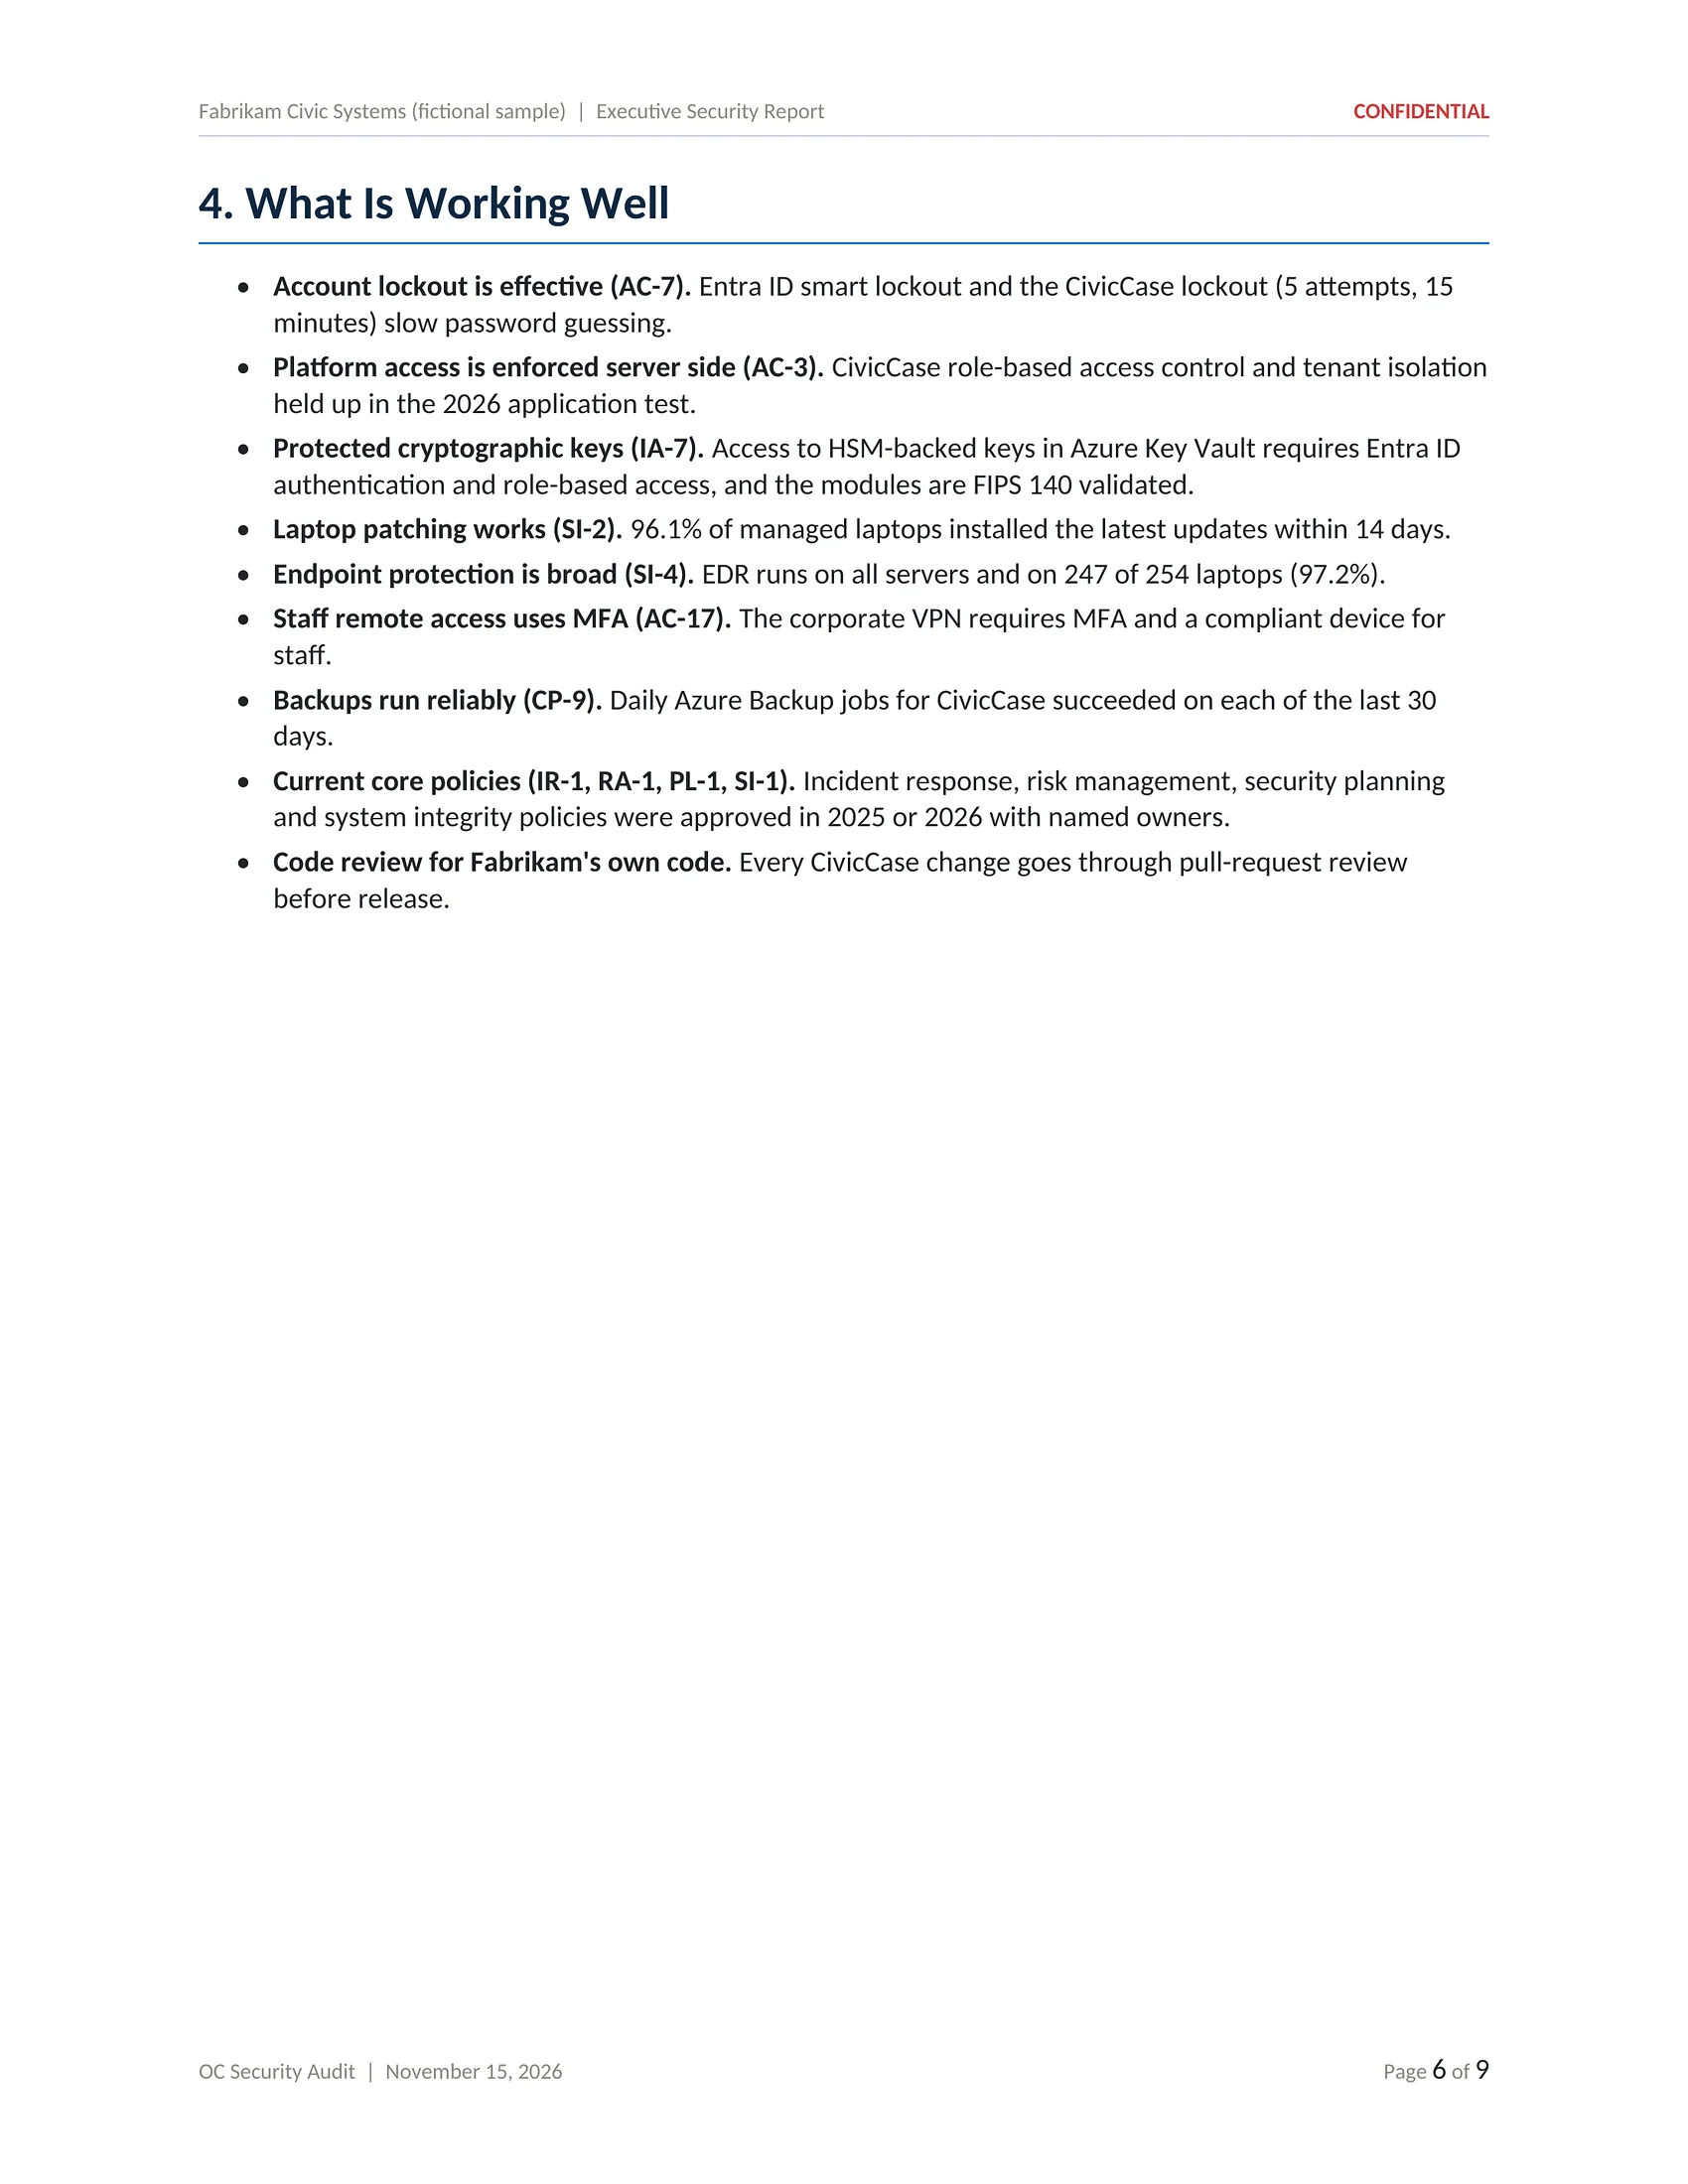
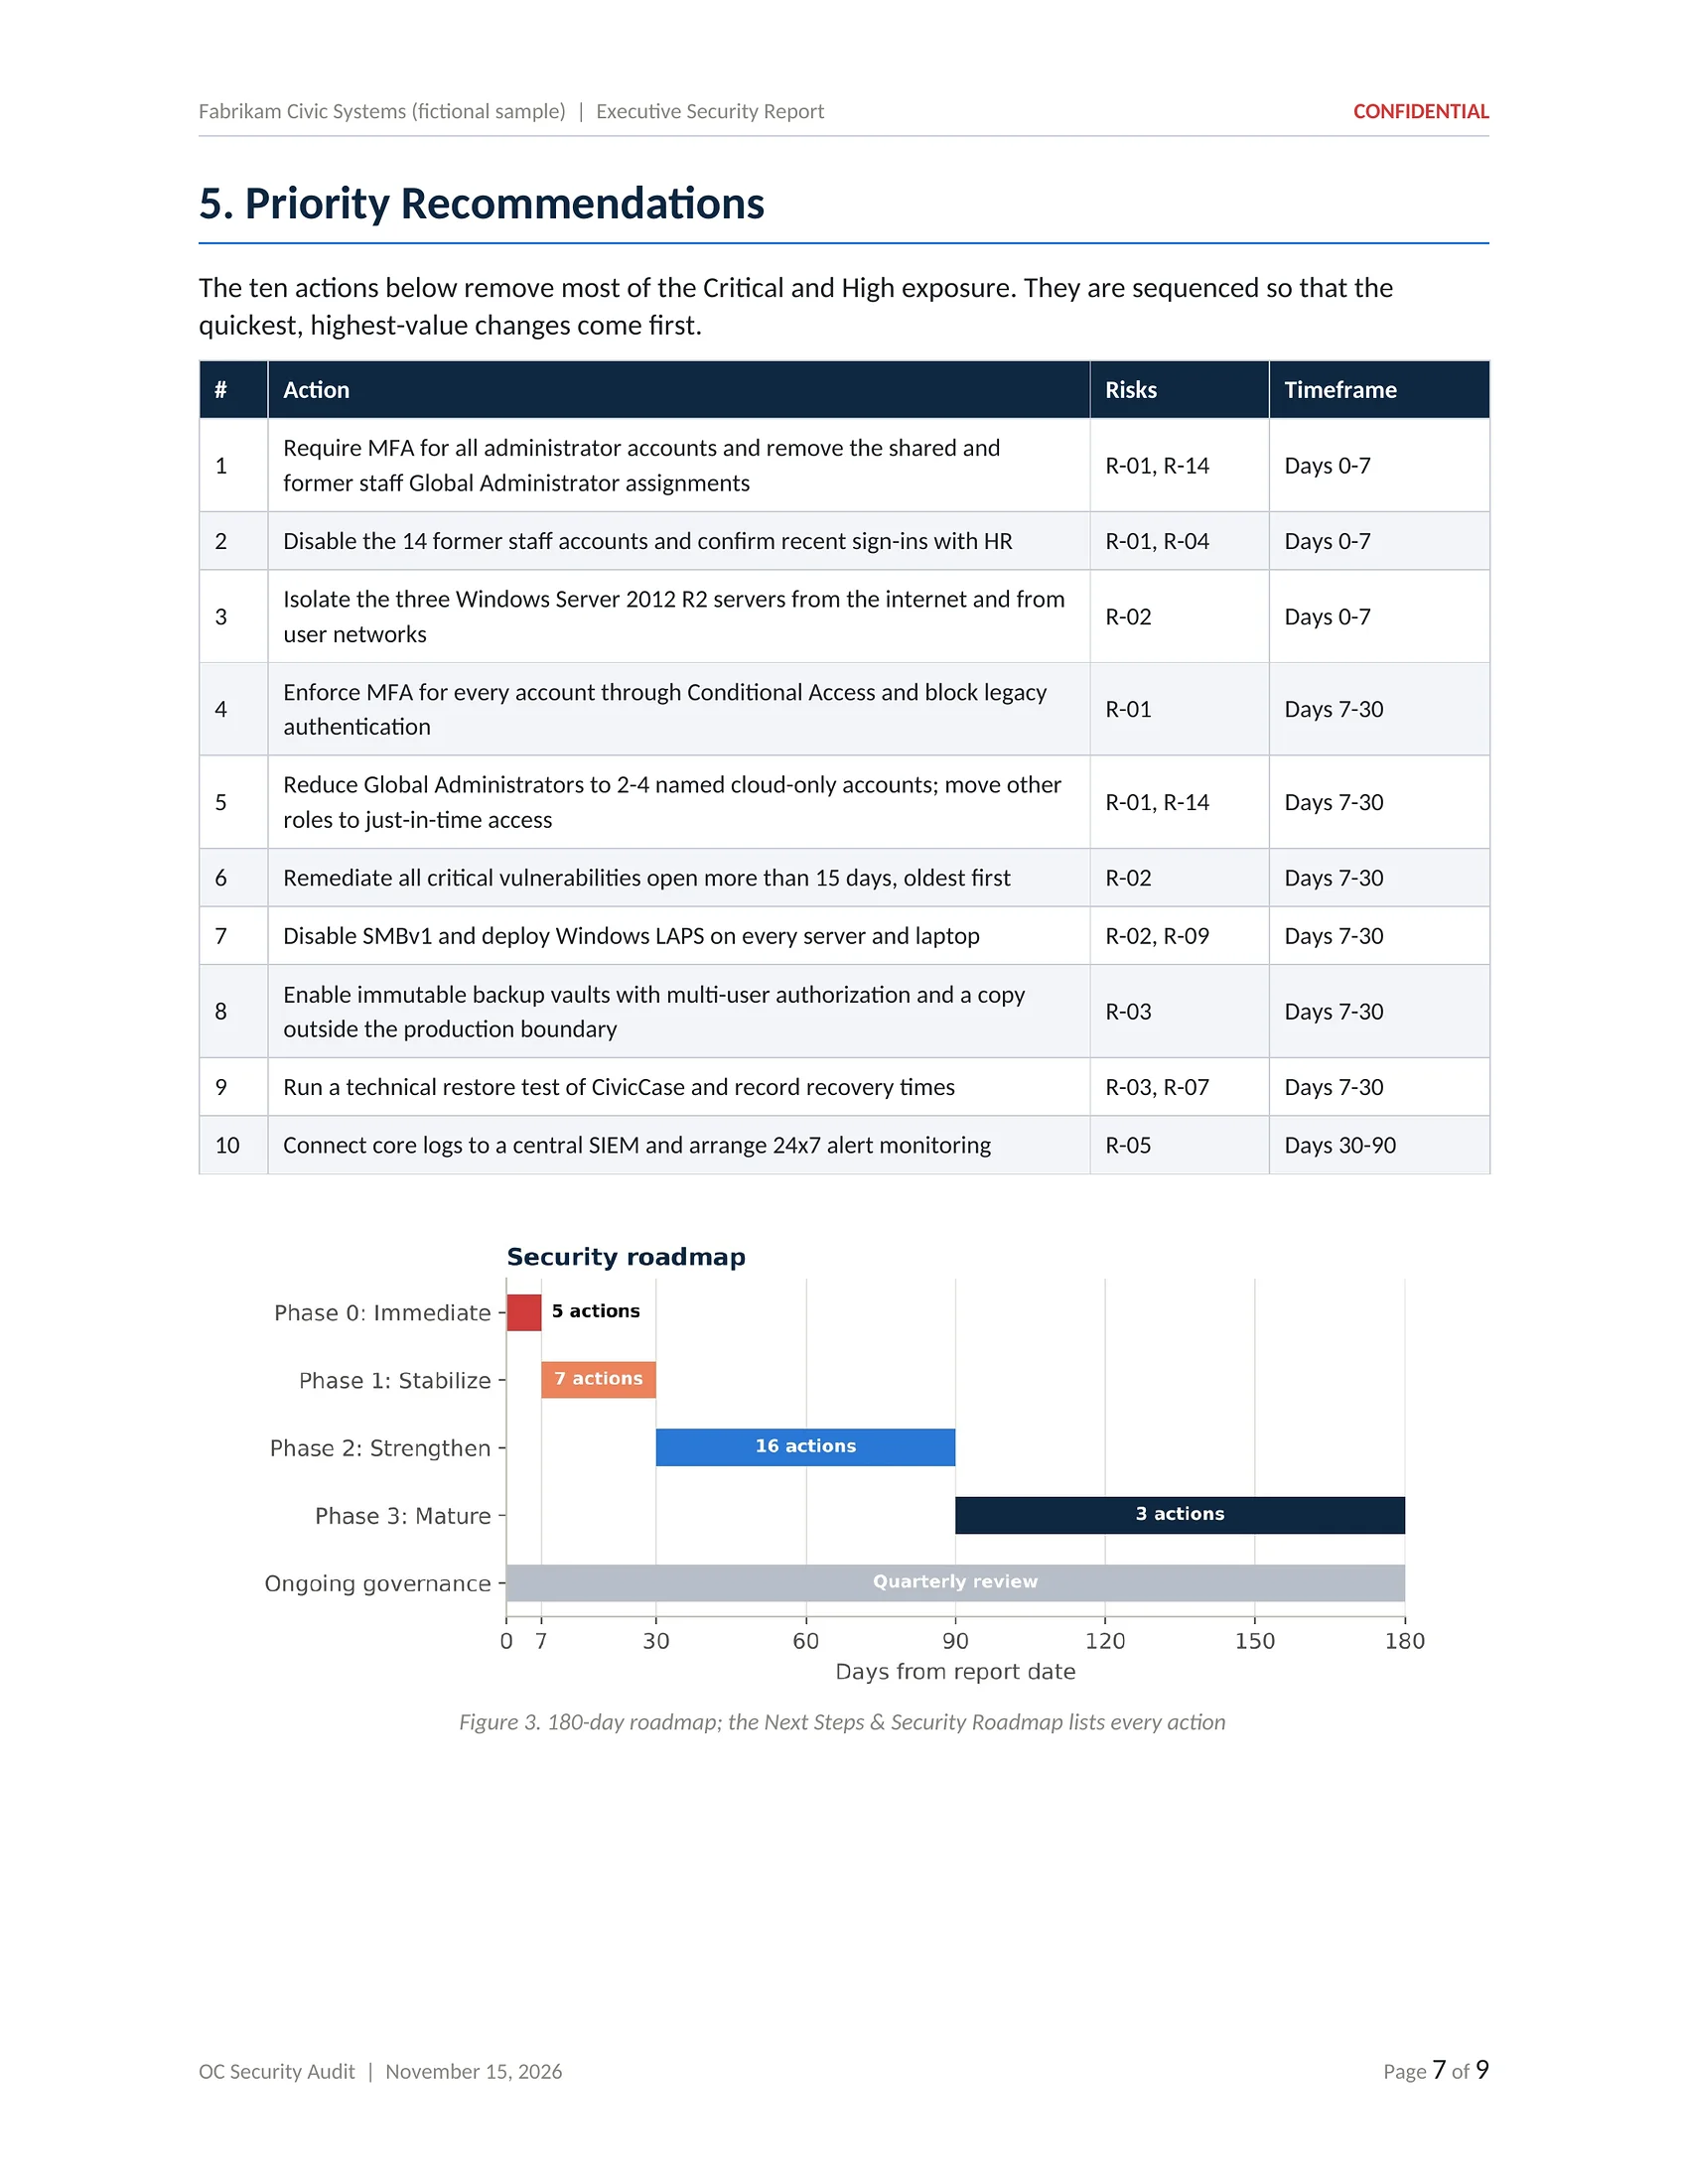
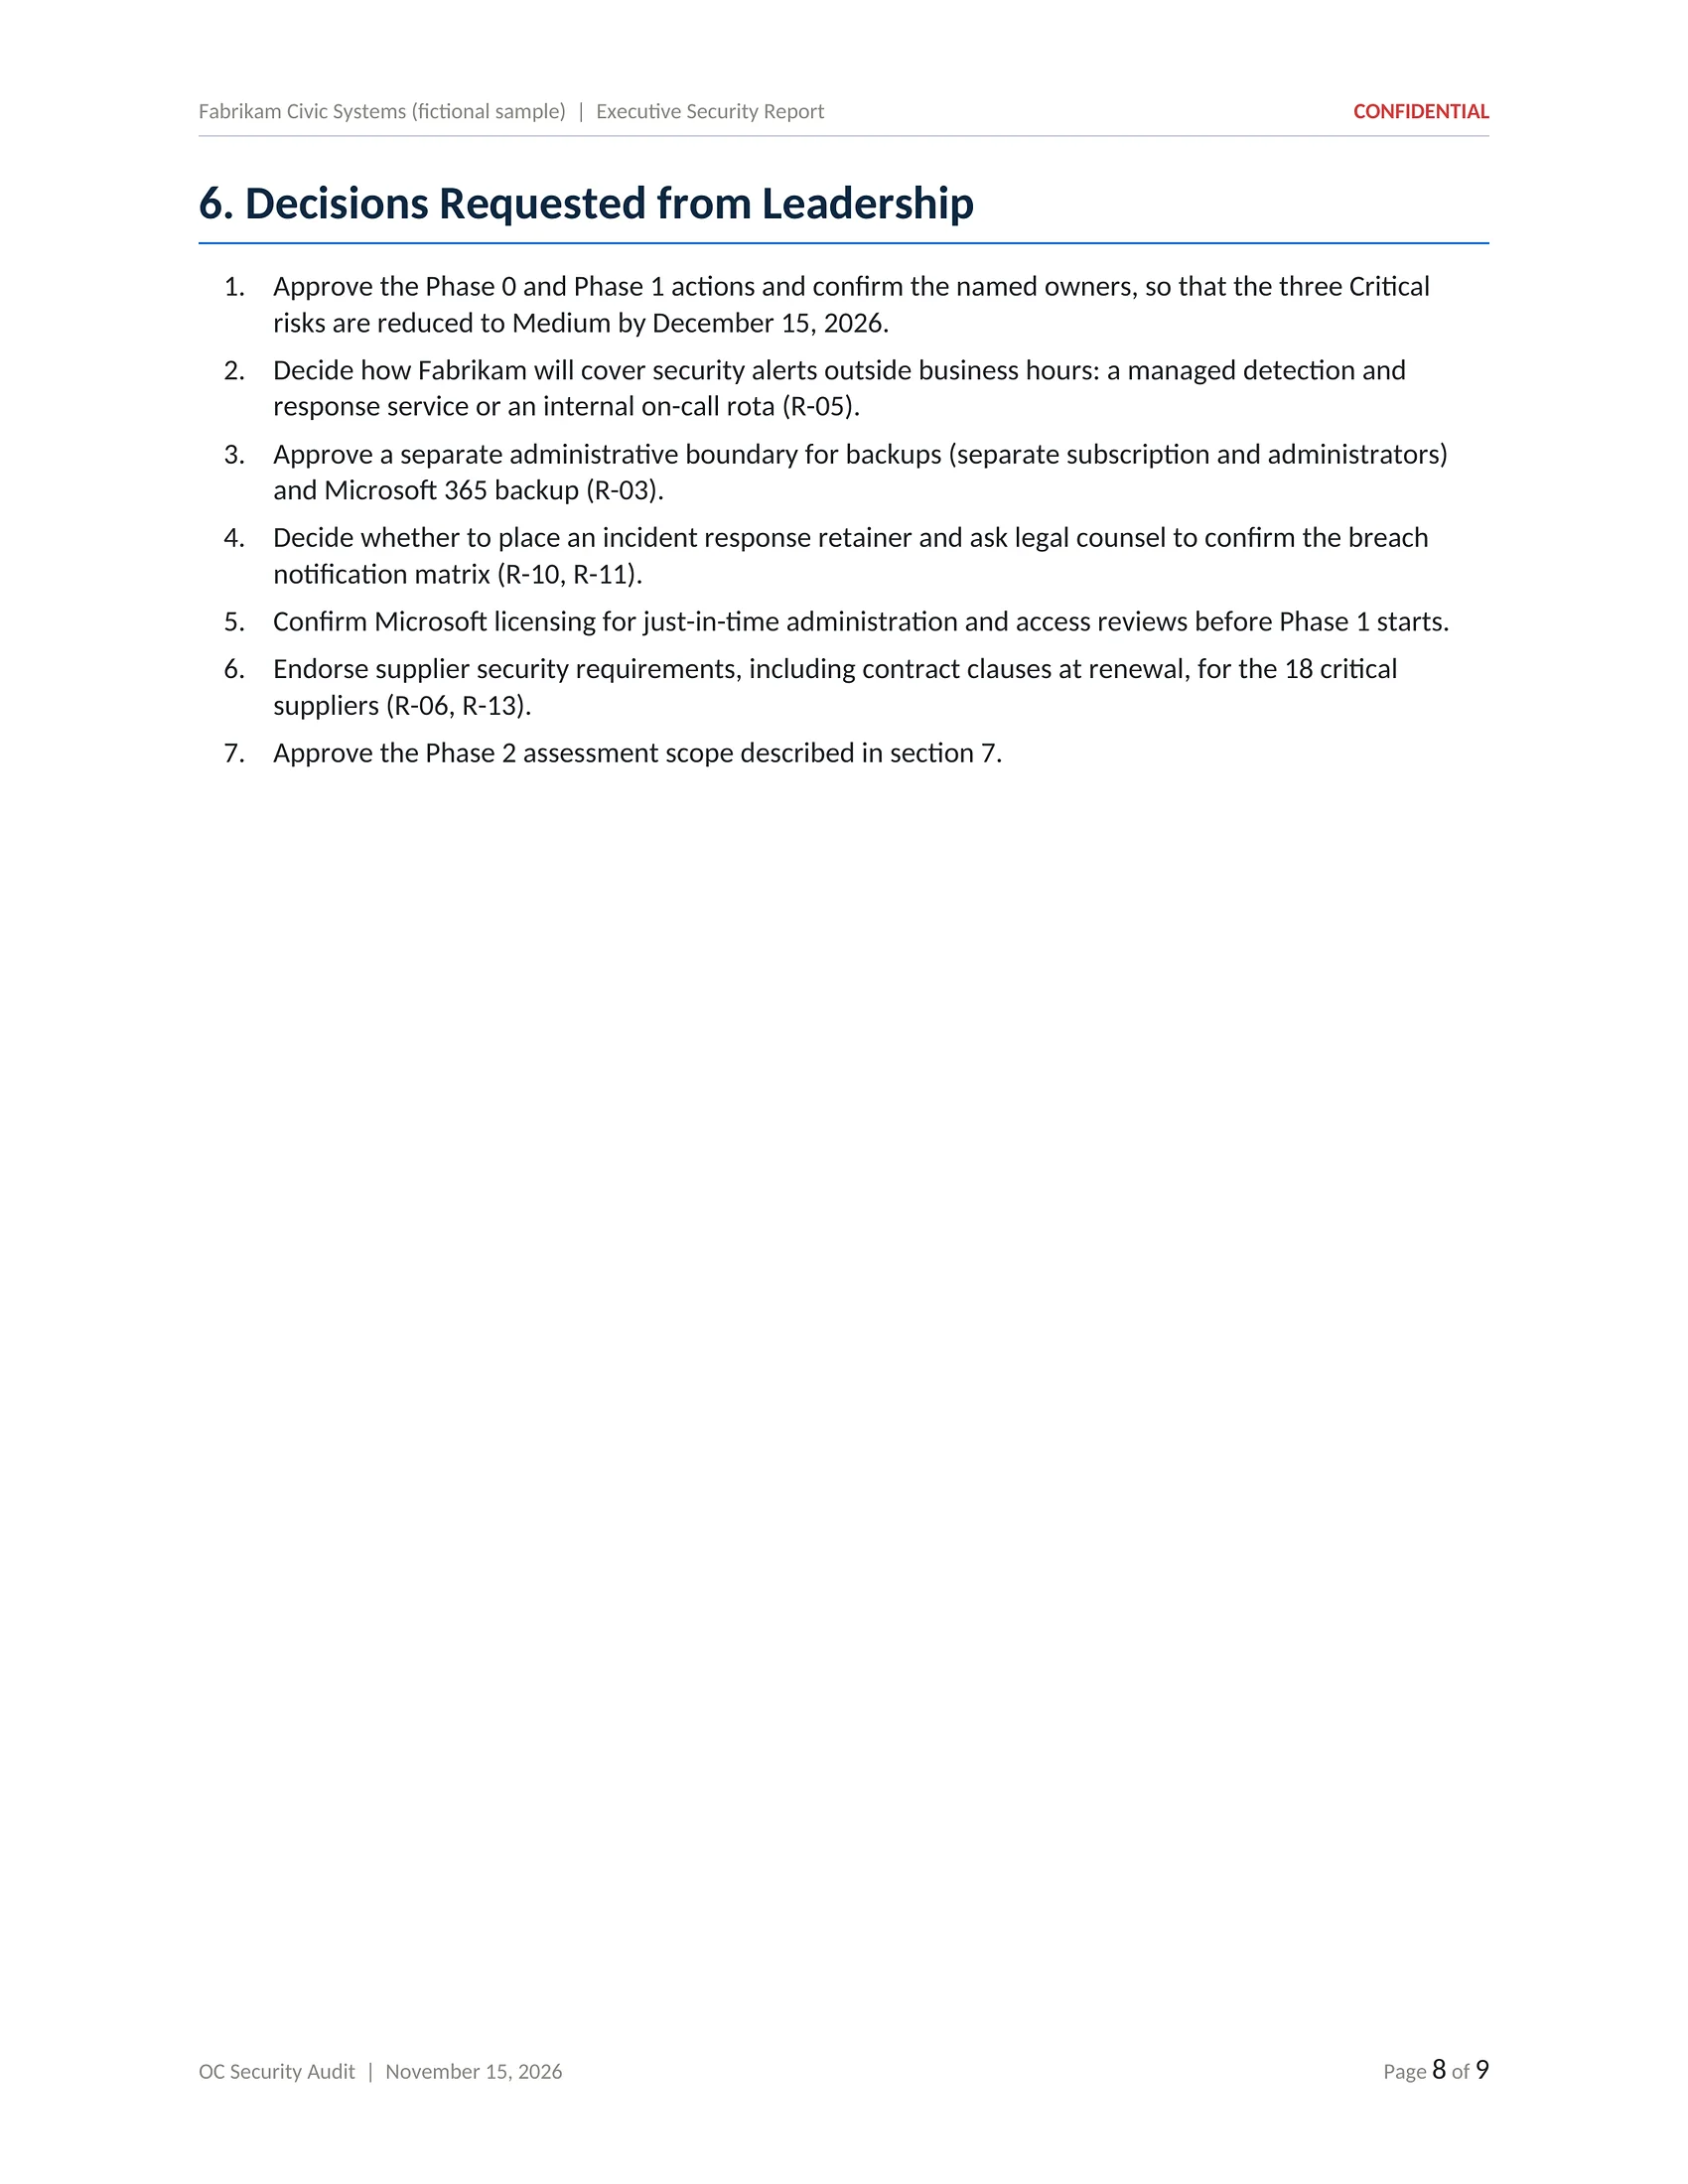
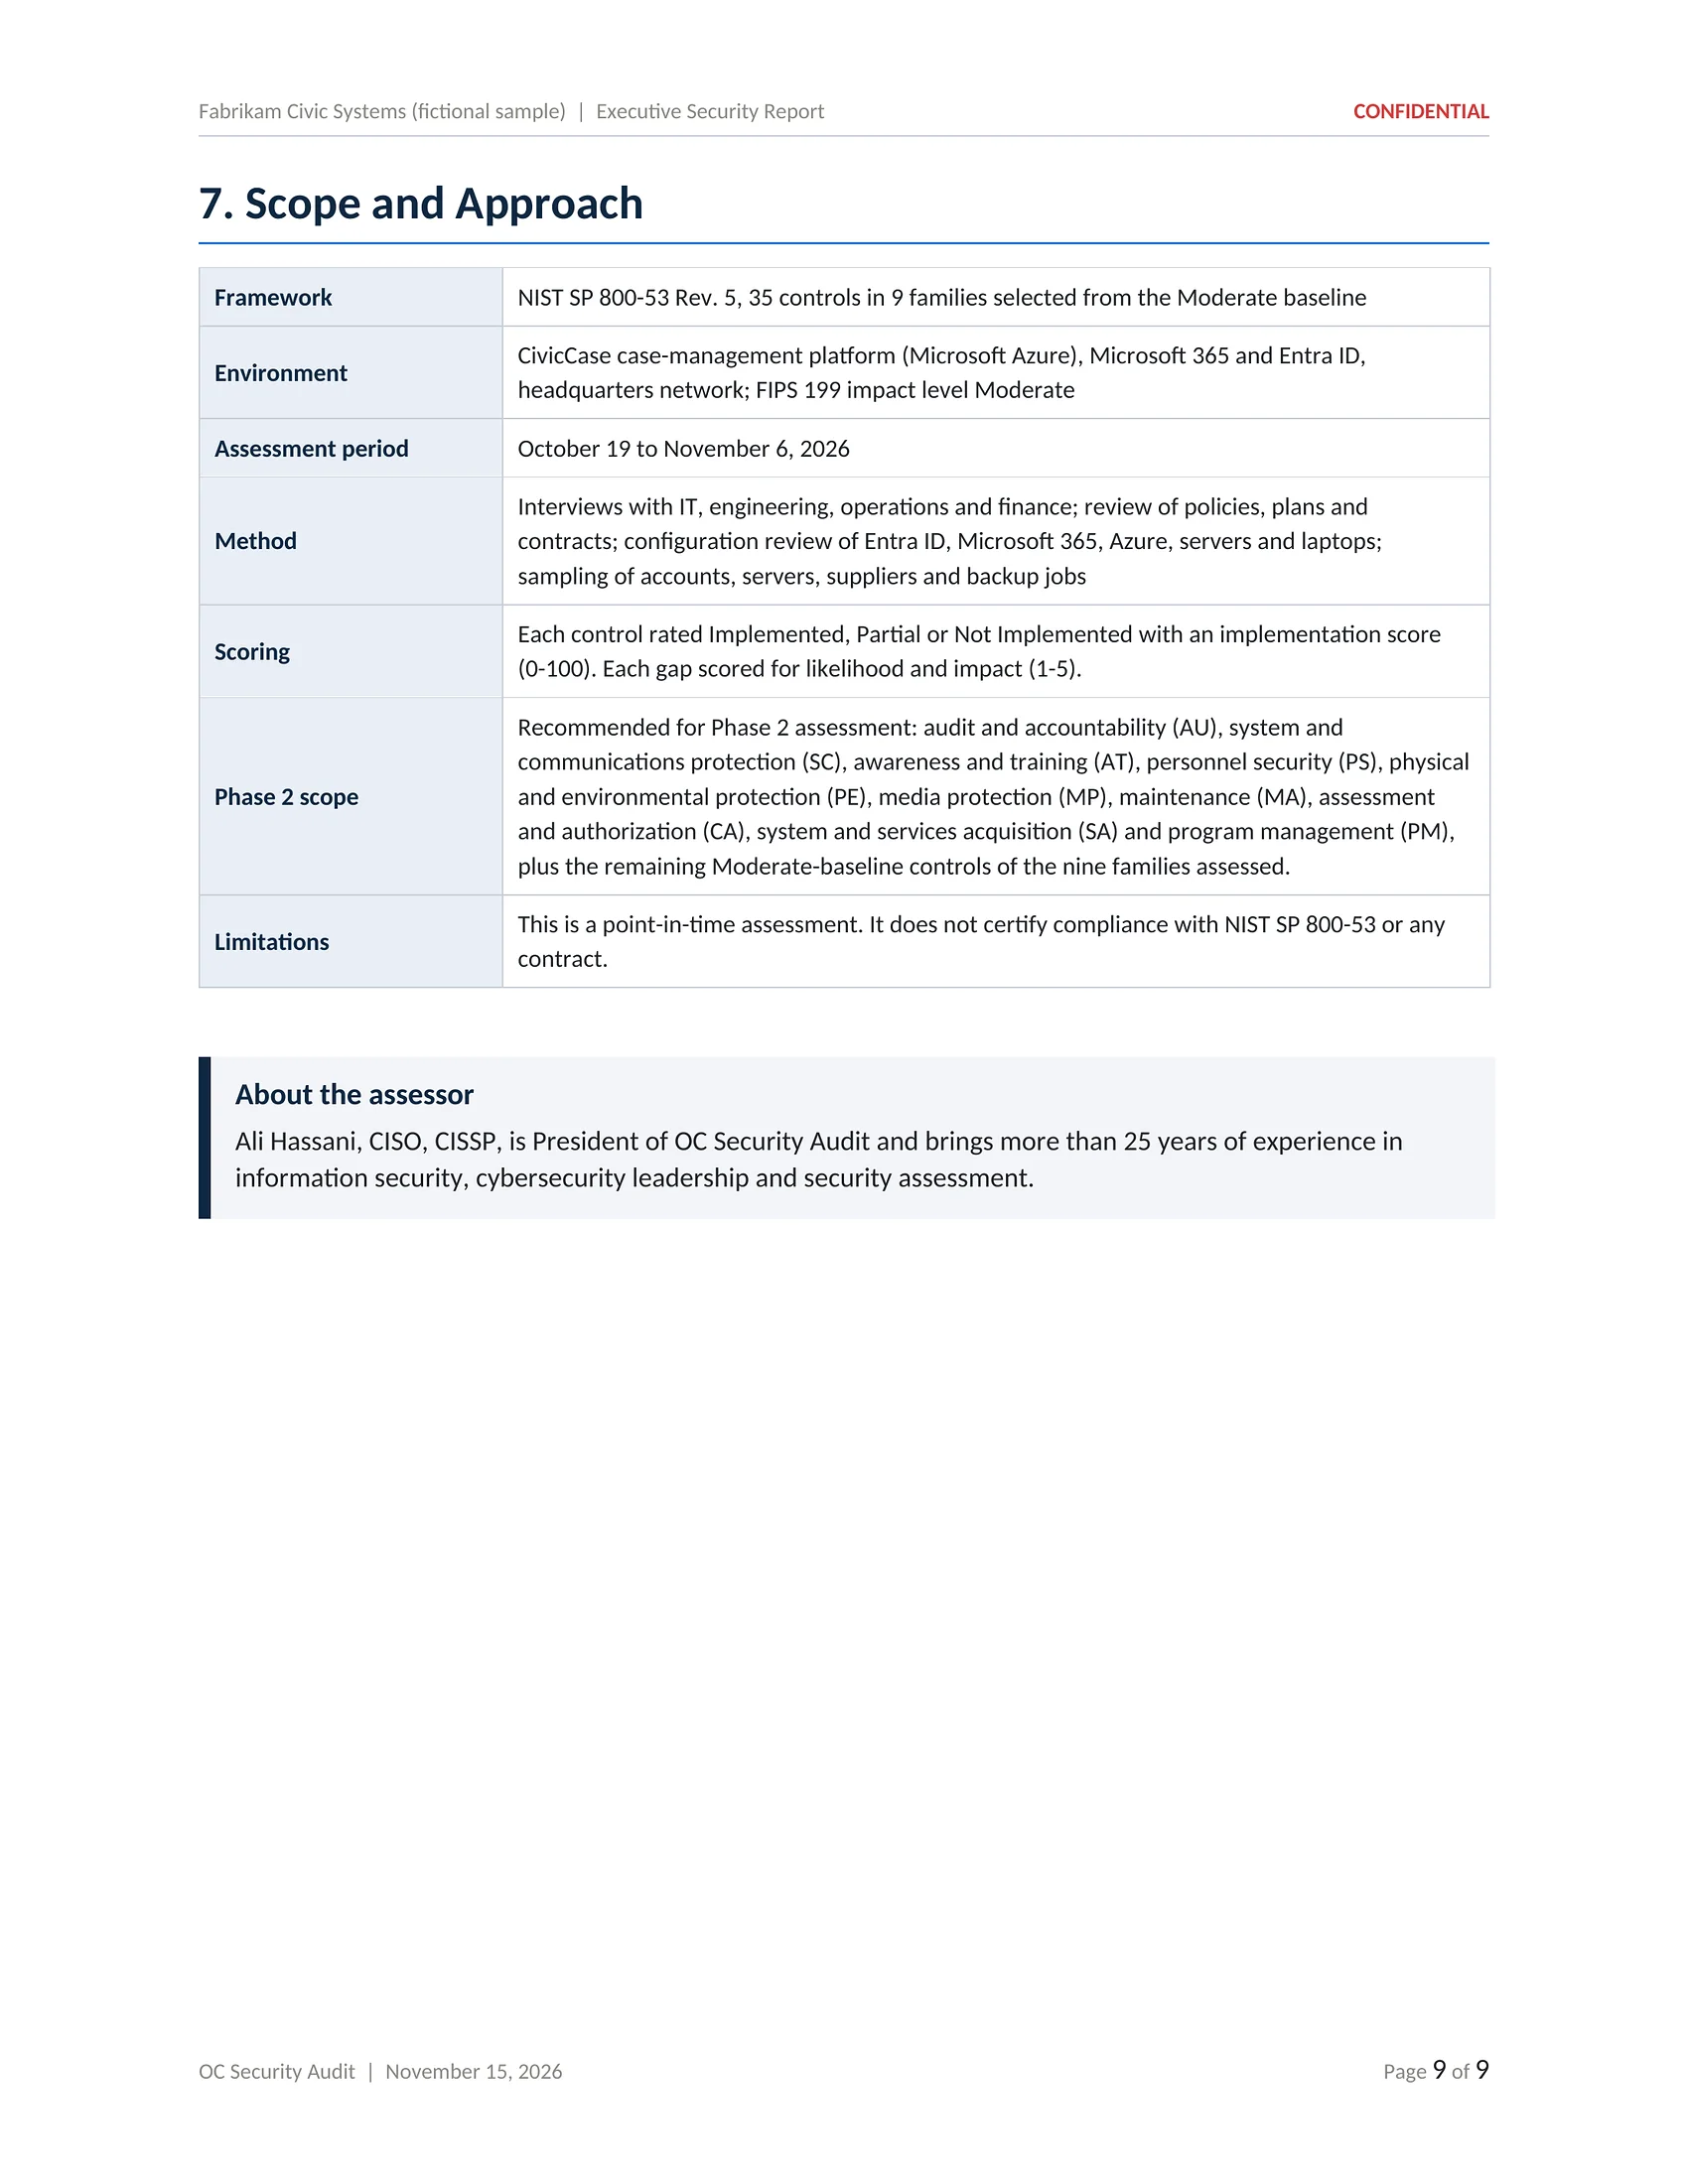
Click the page in the centre to open it full size, then zoom in to read every line.
PDF and Word · 36 pages
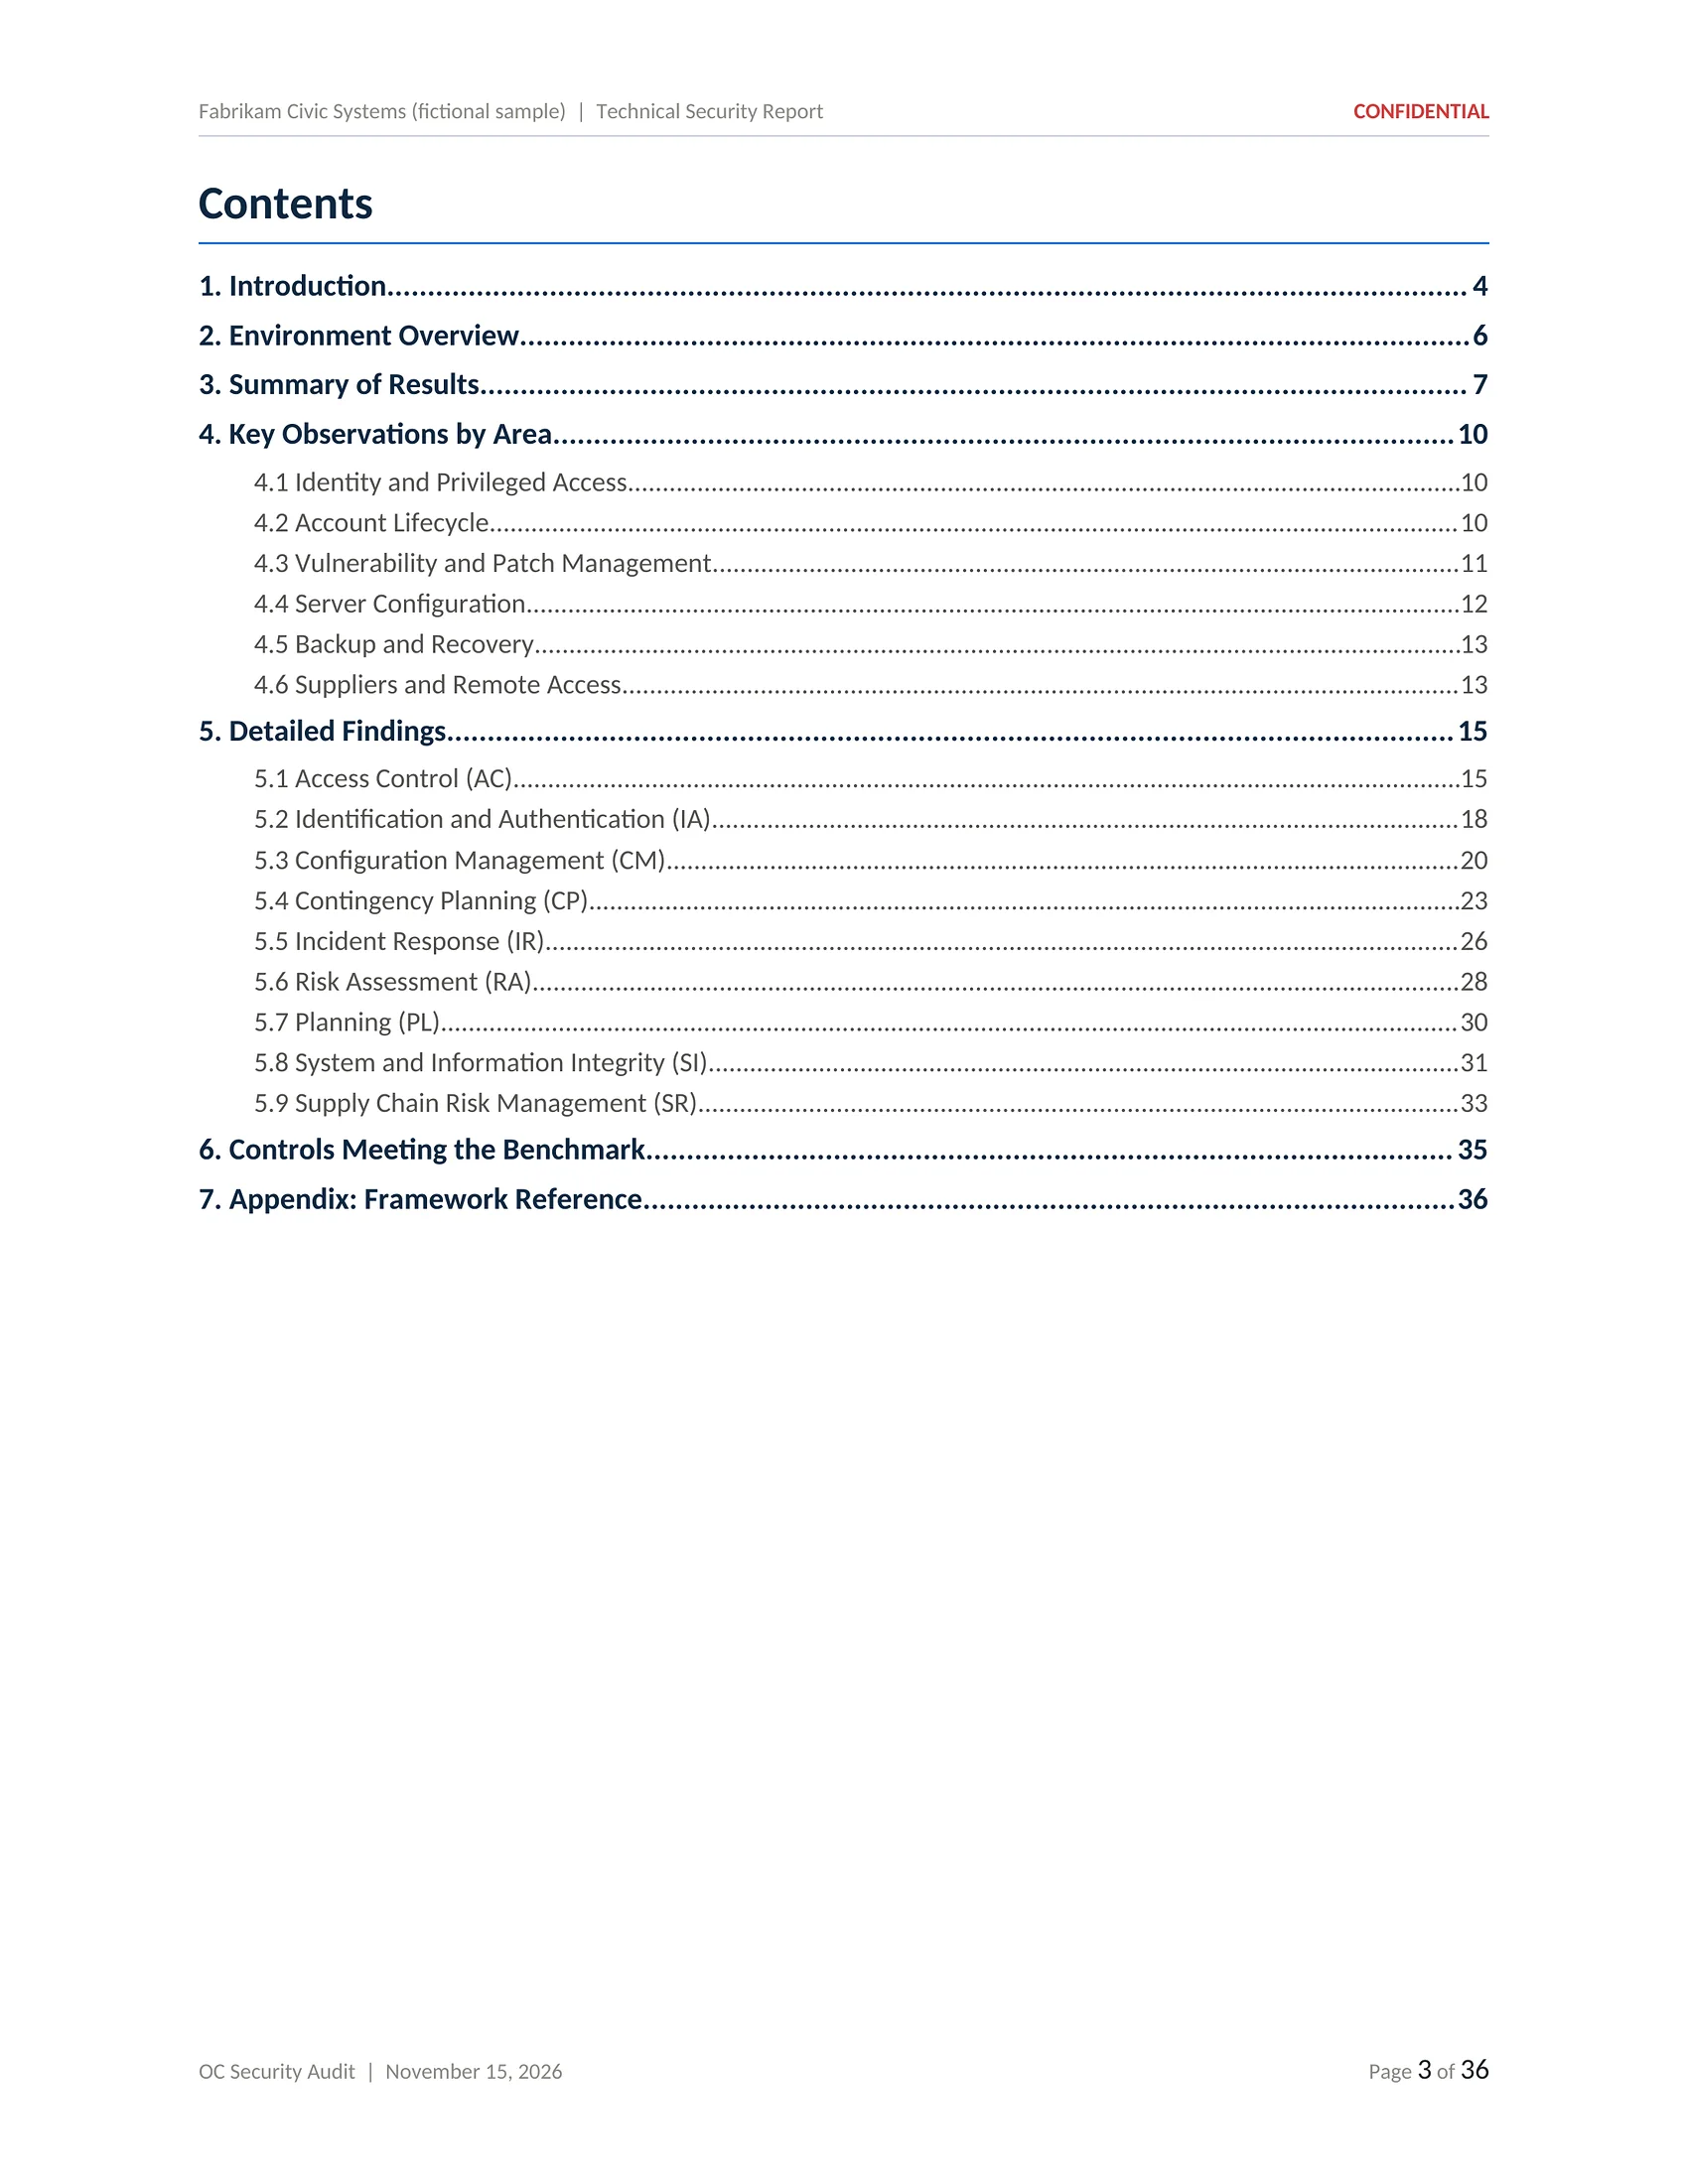
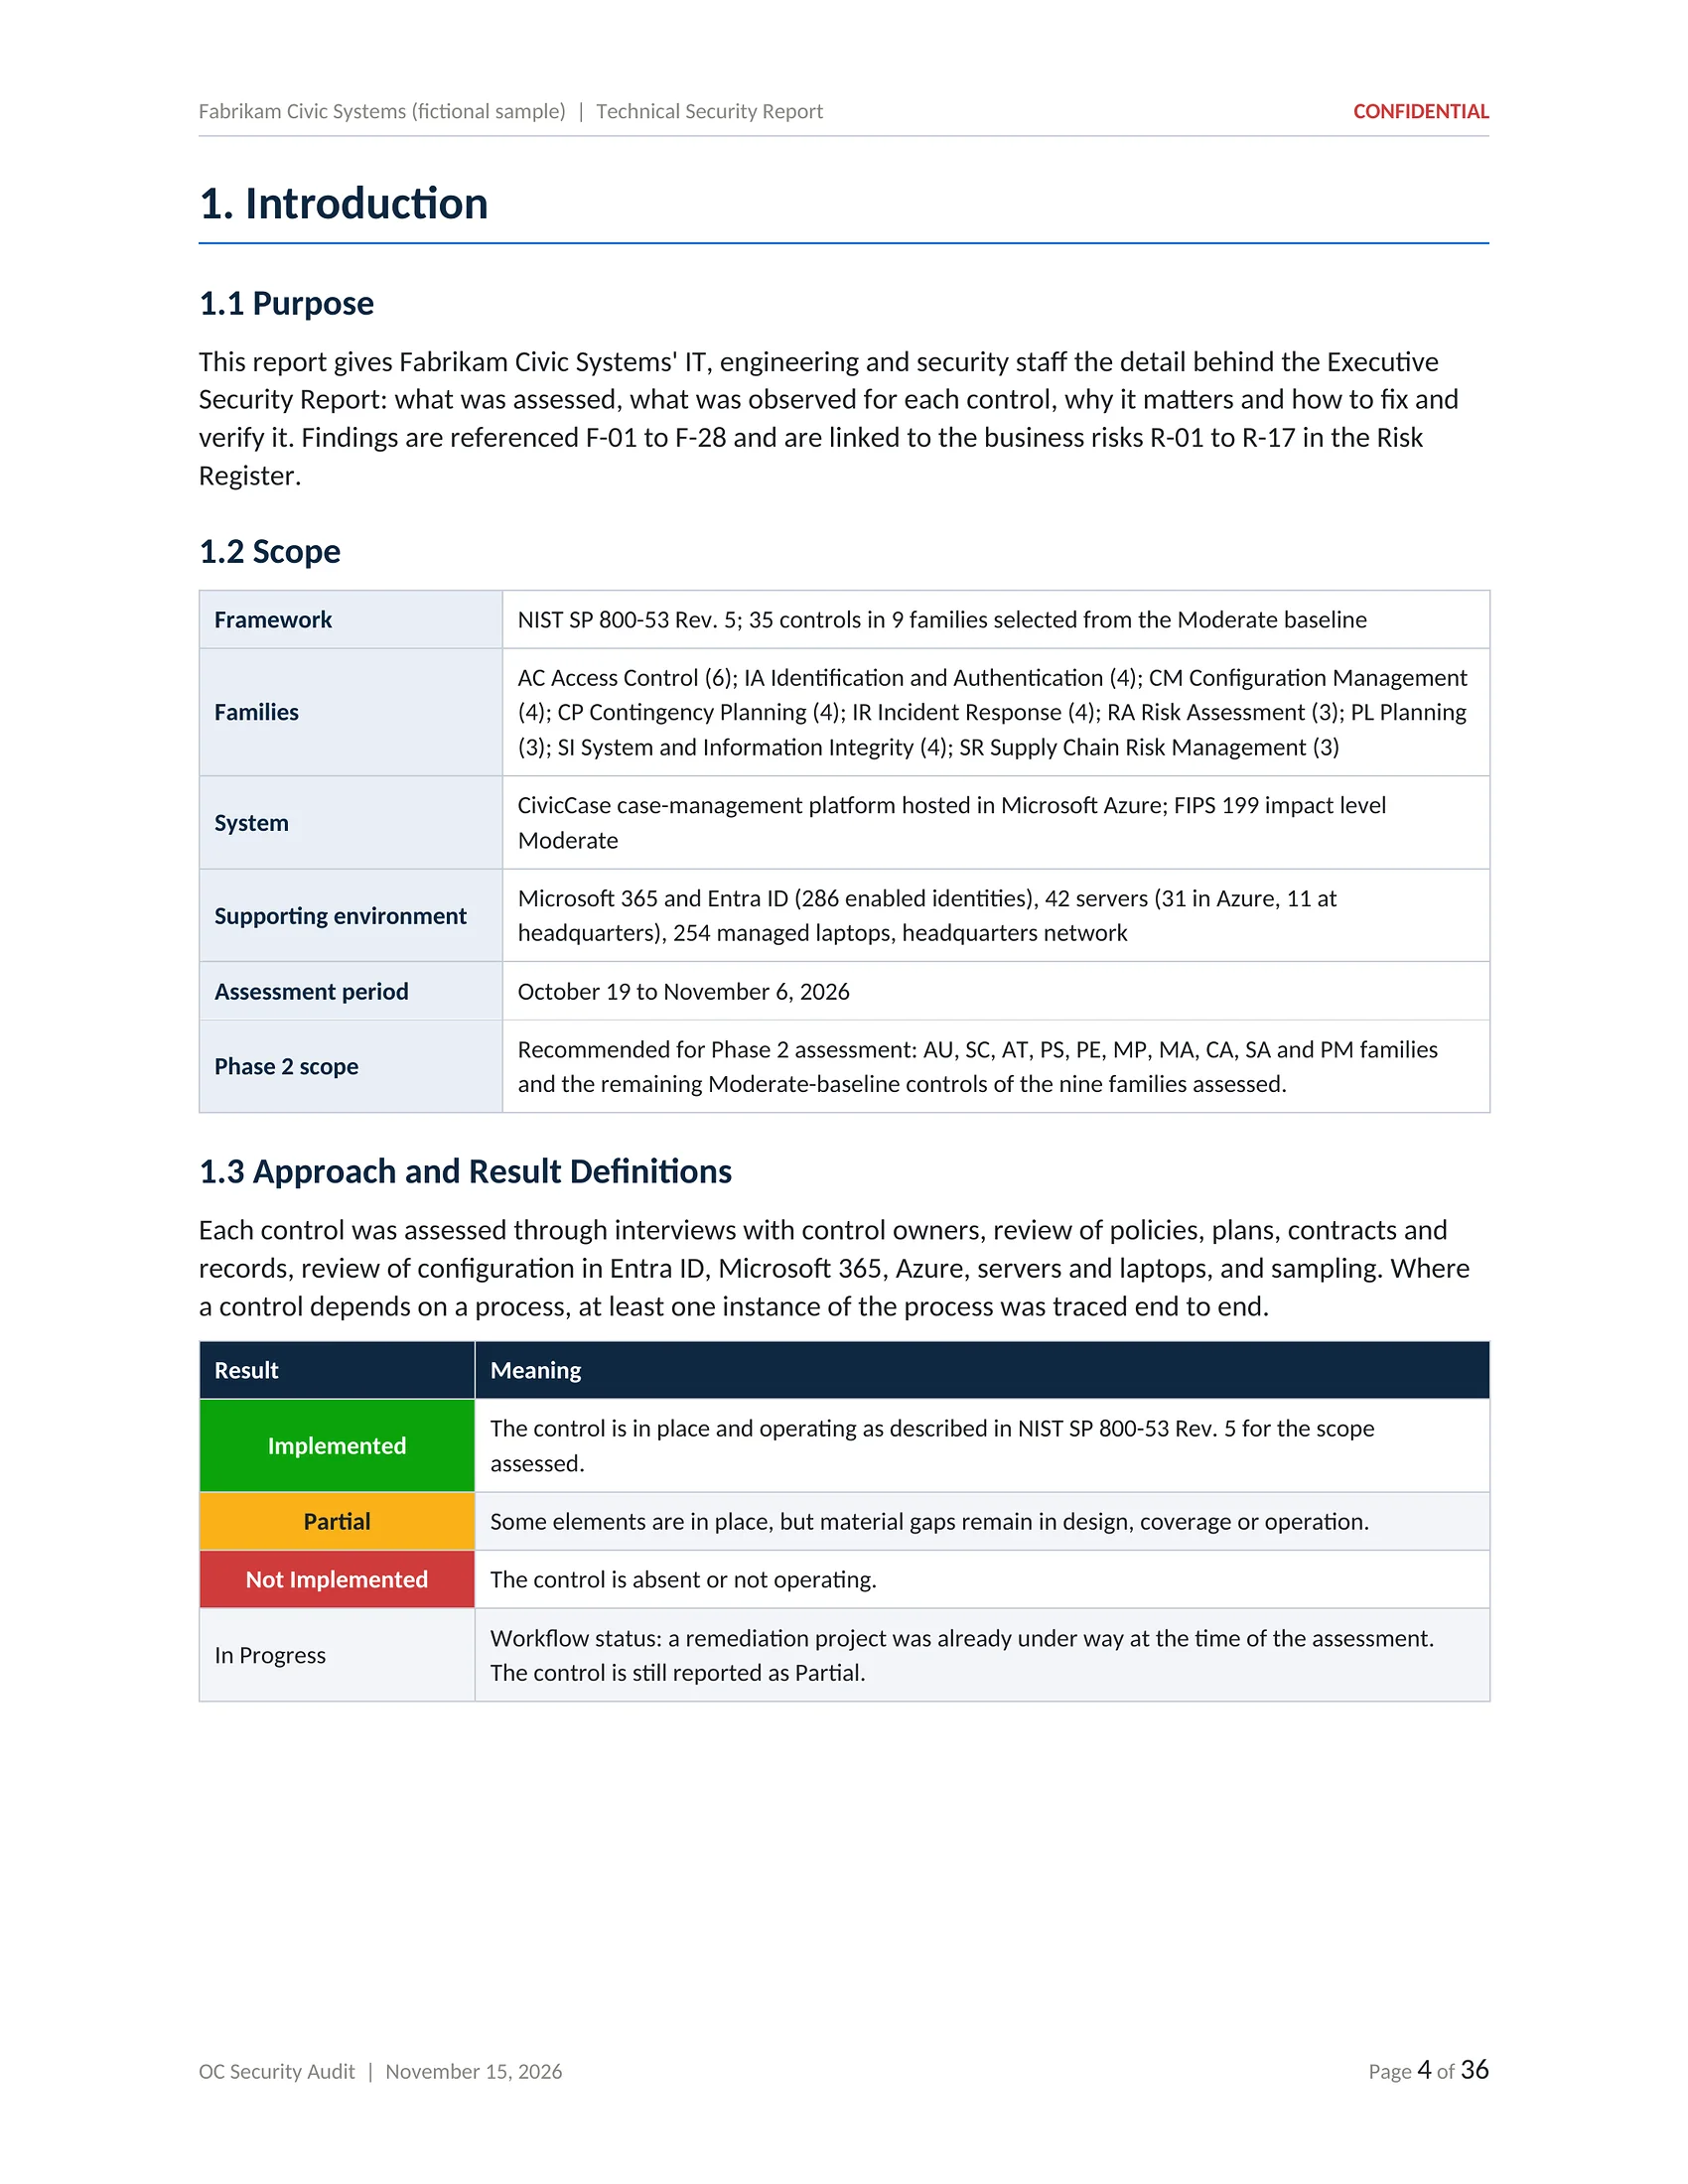
Technical Security Report
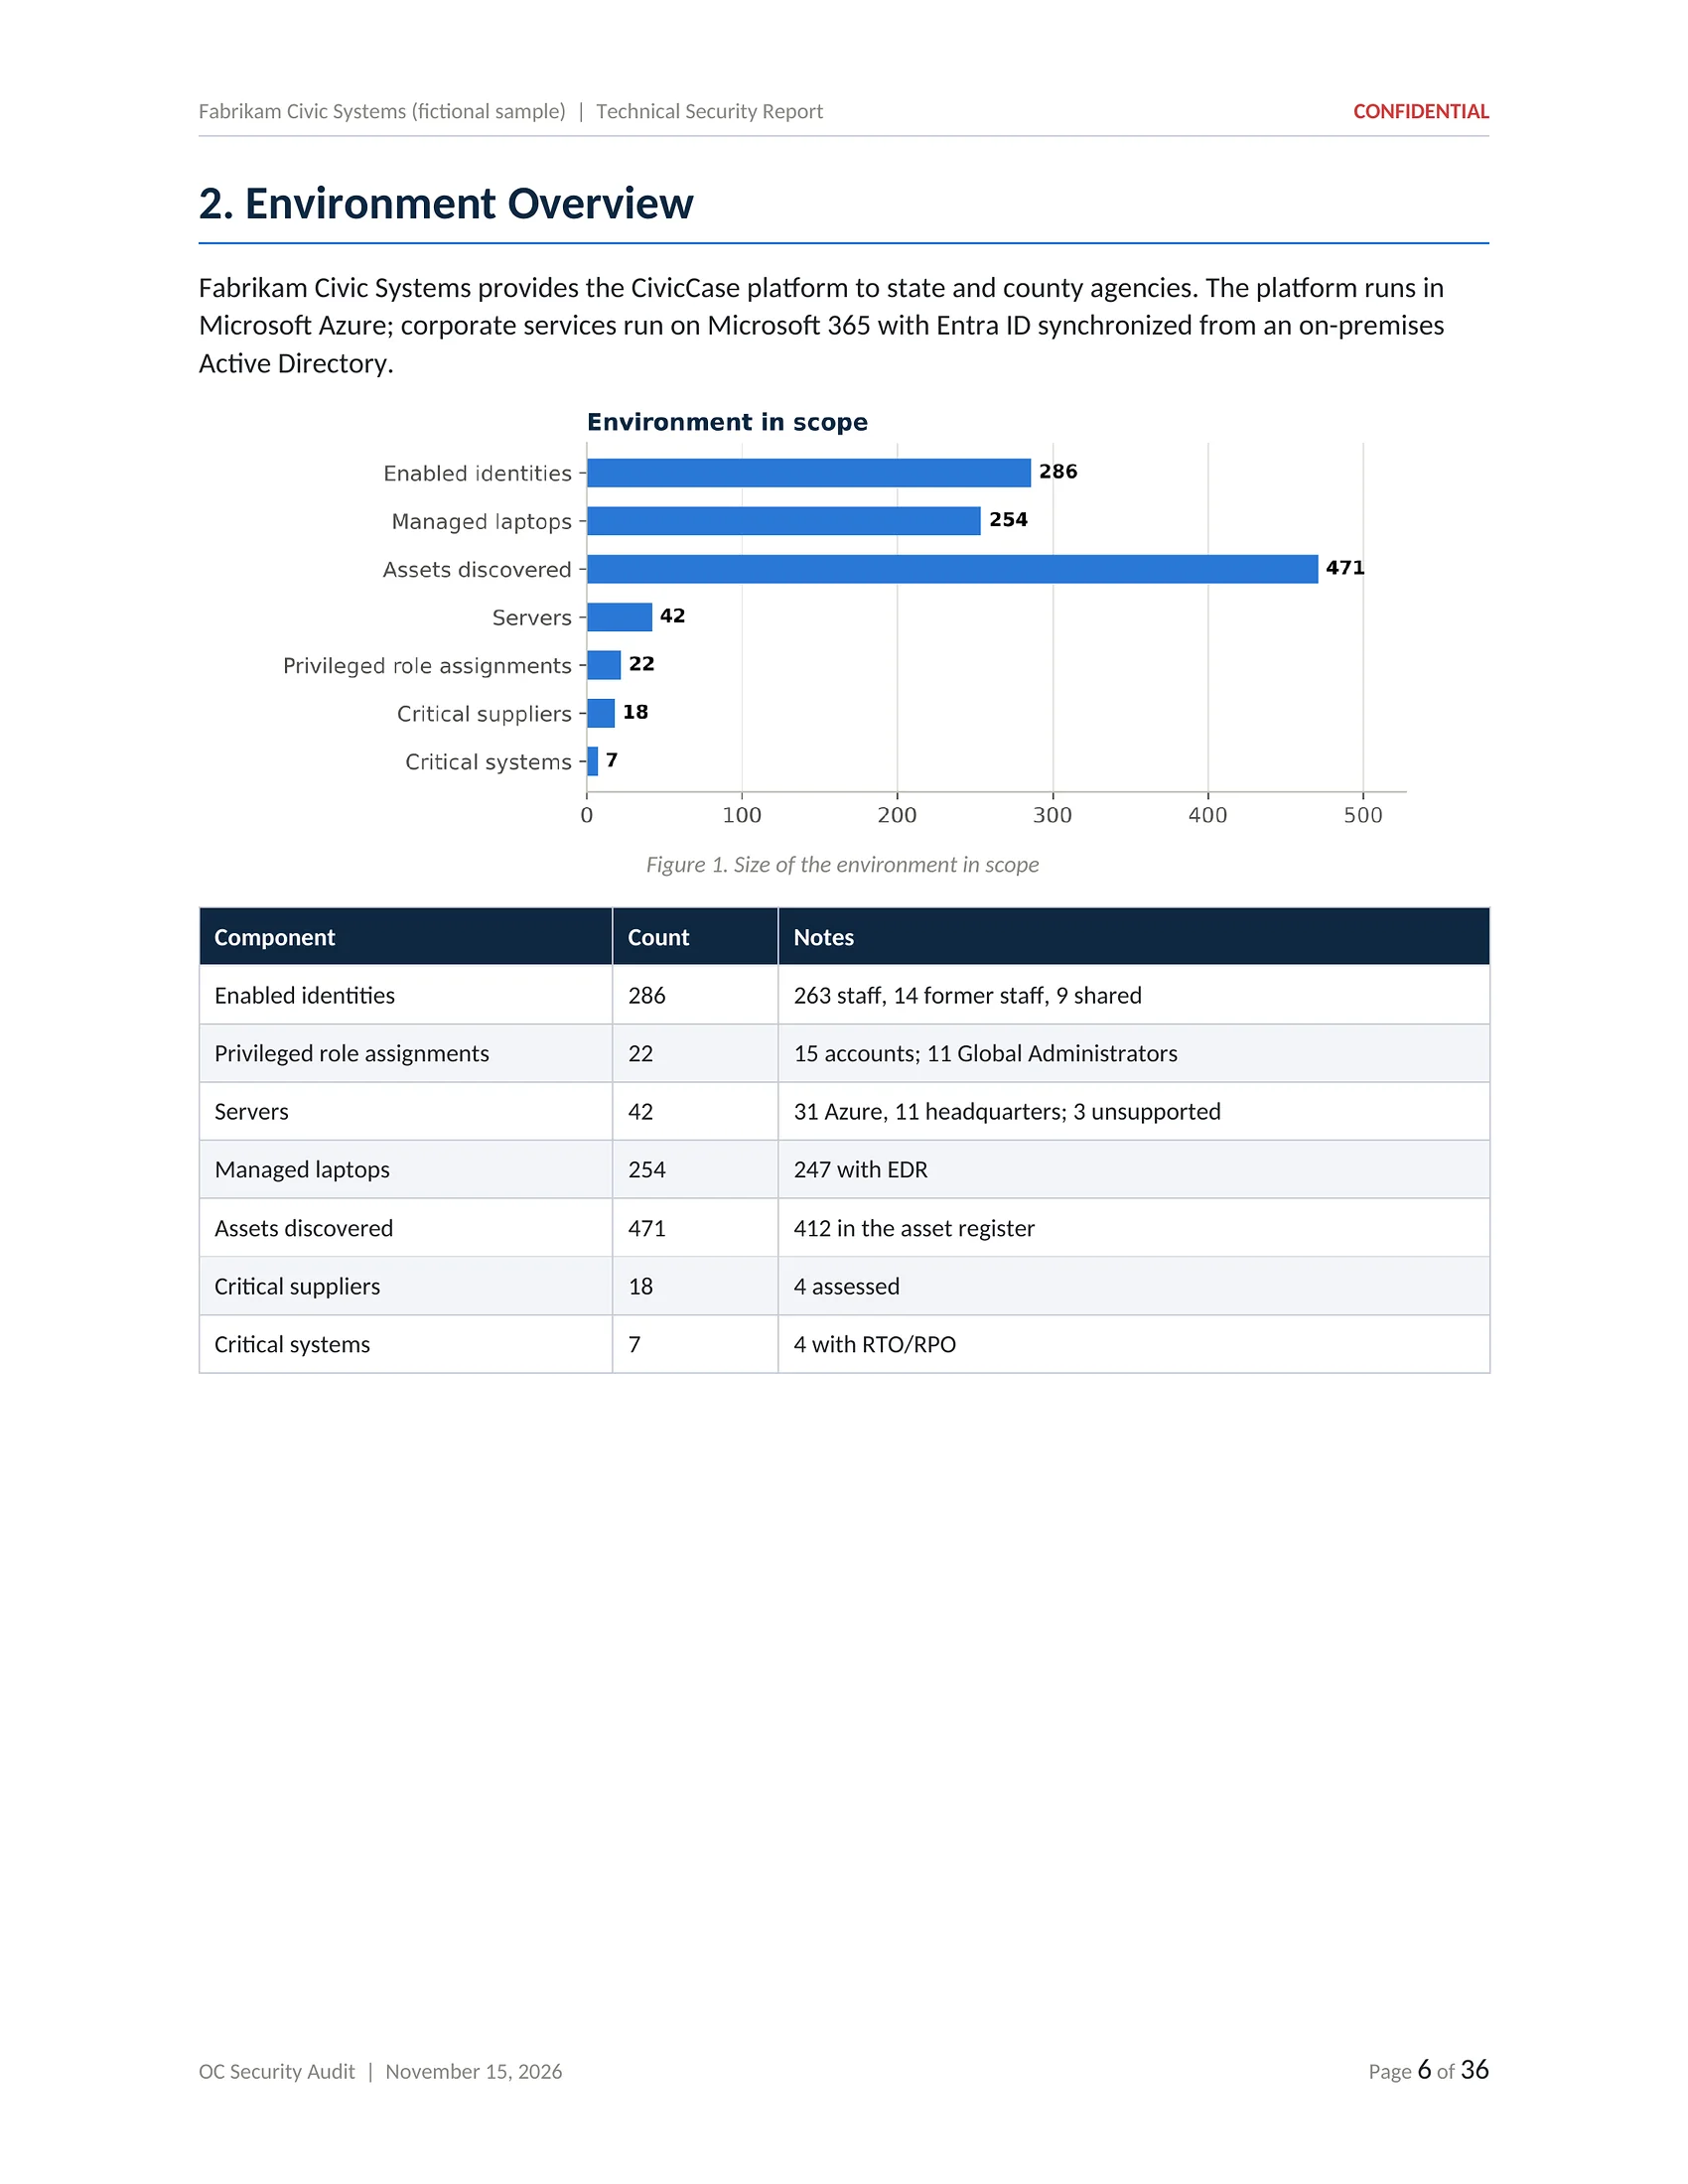
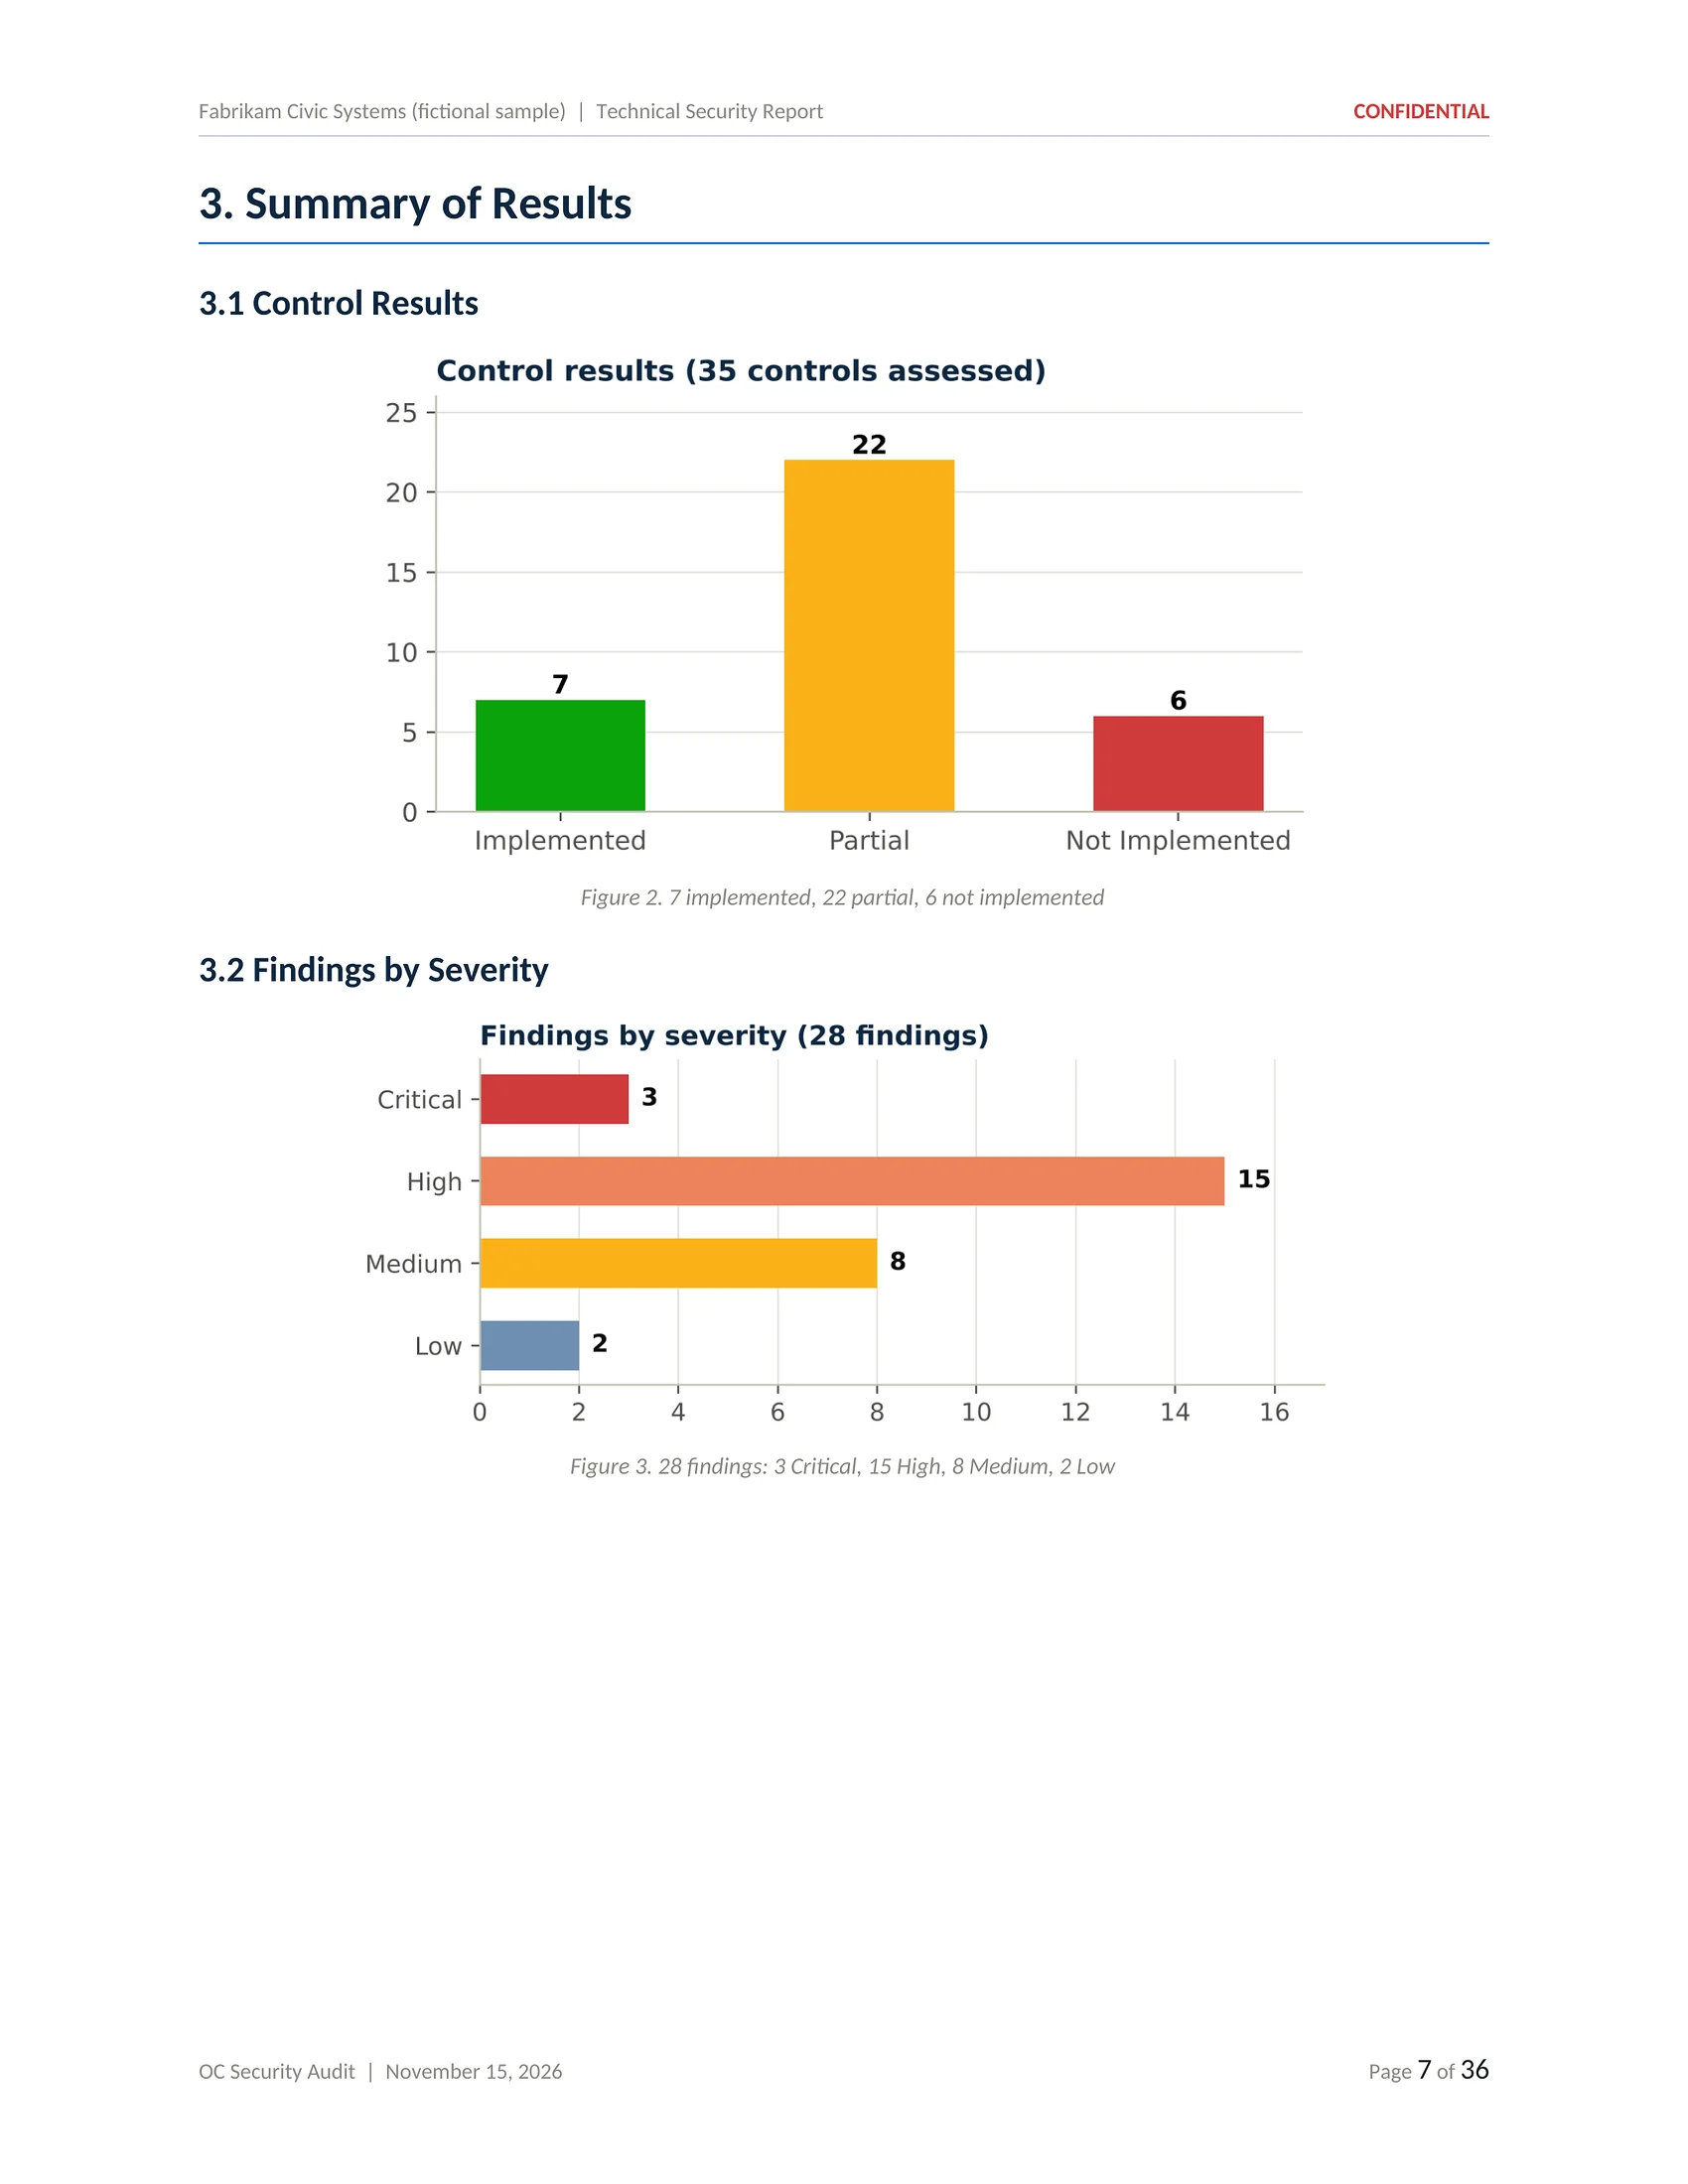
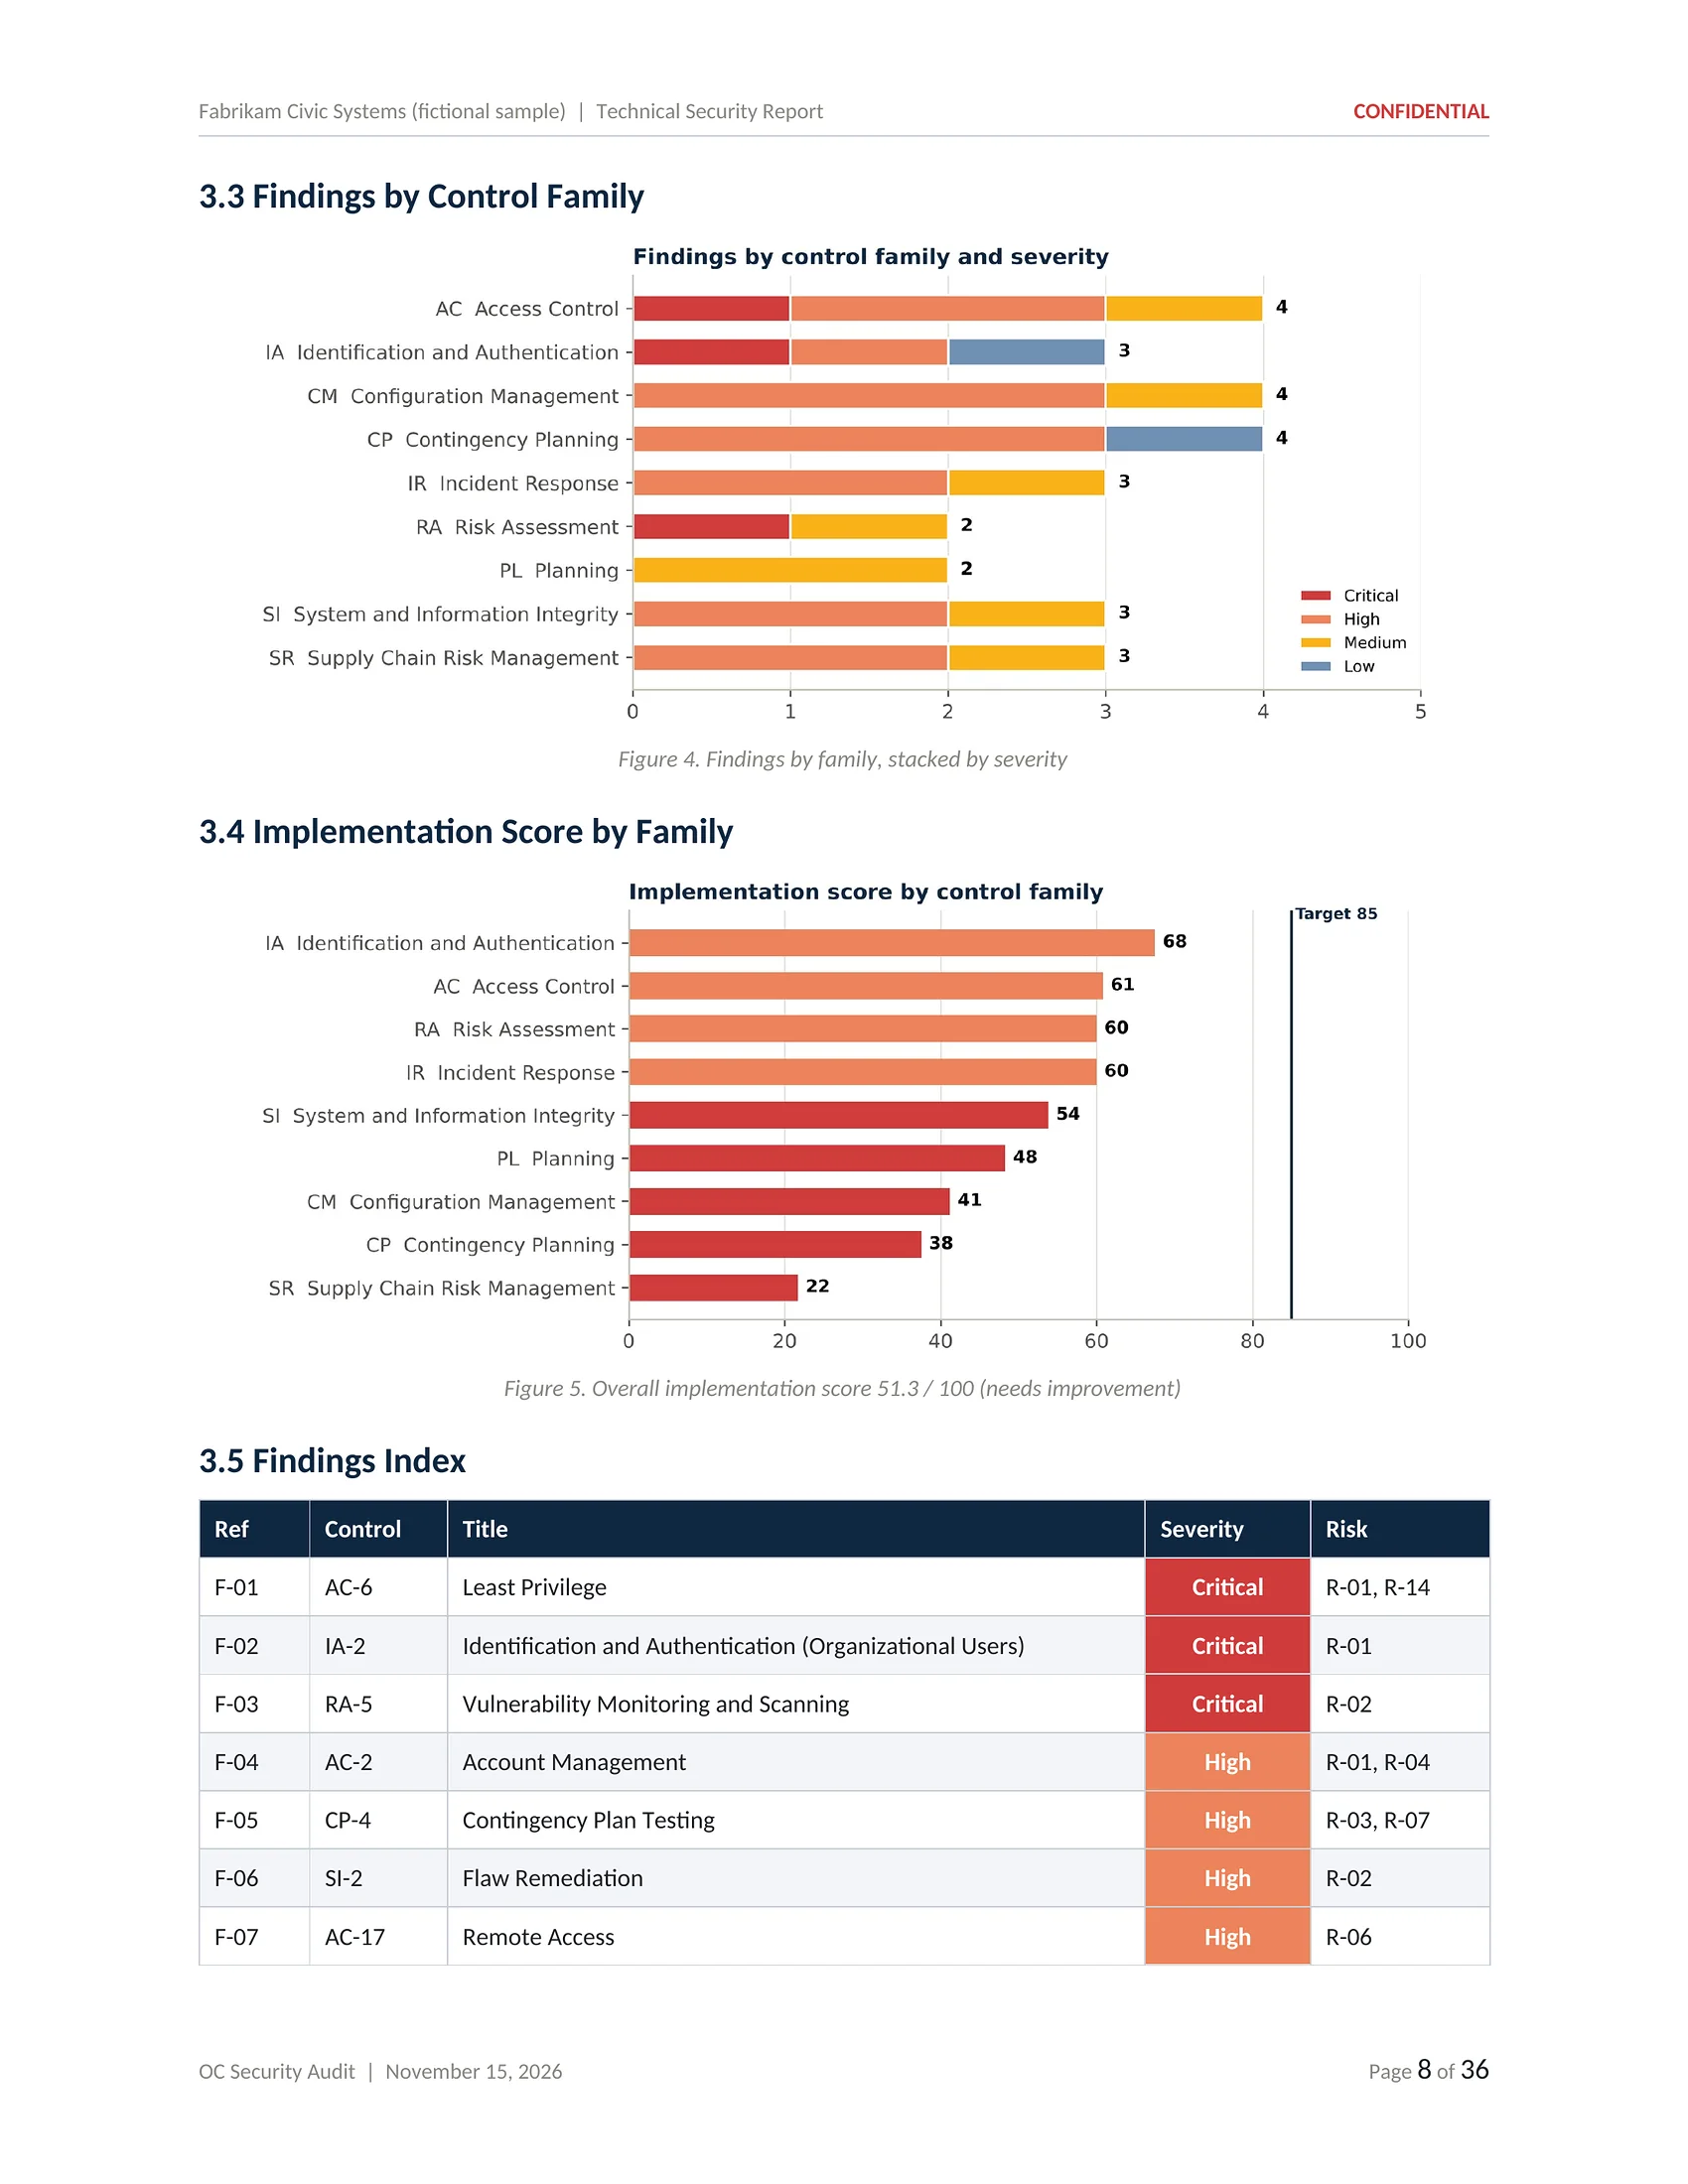
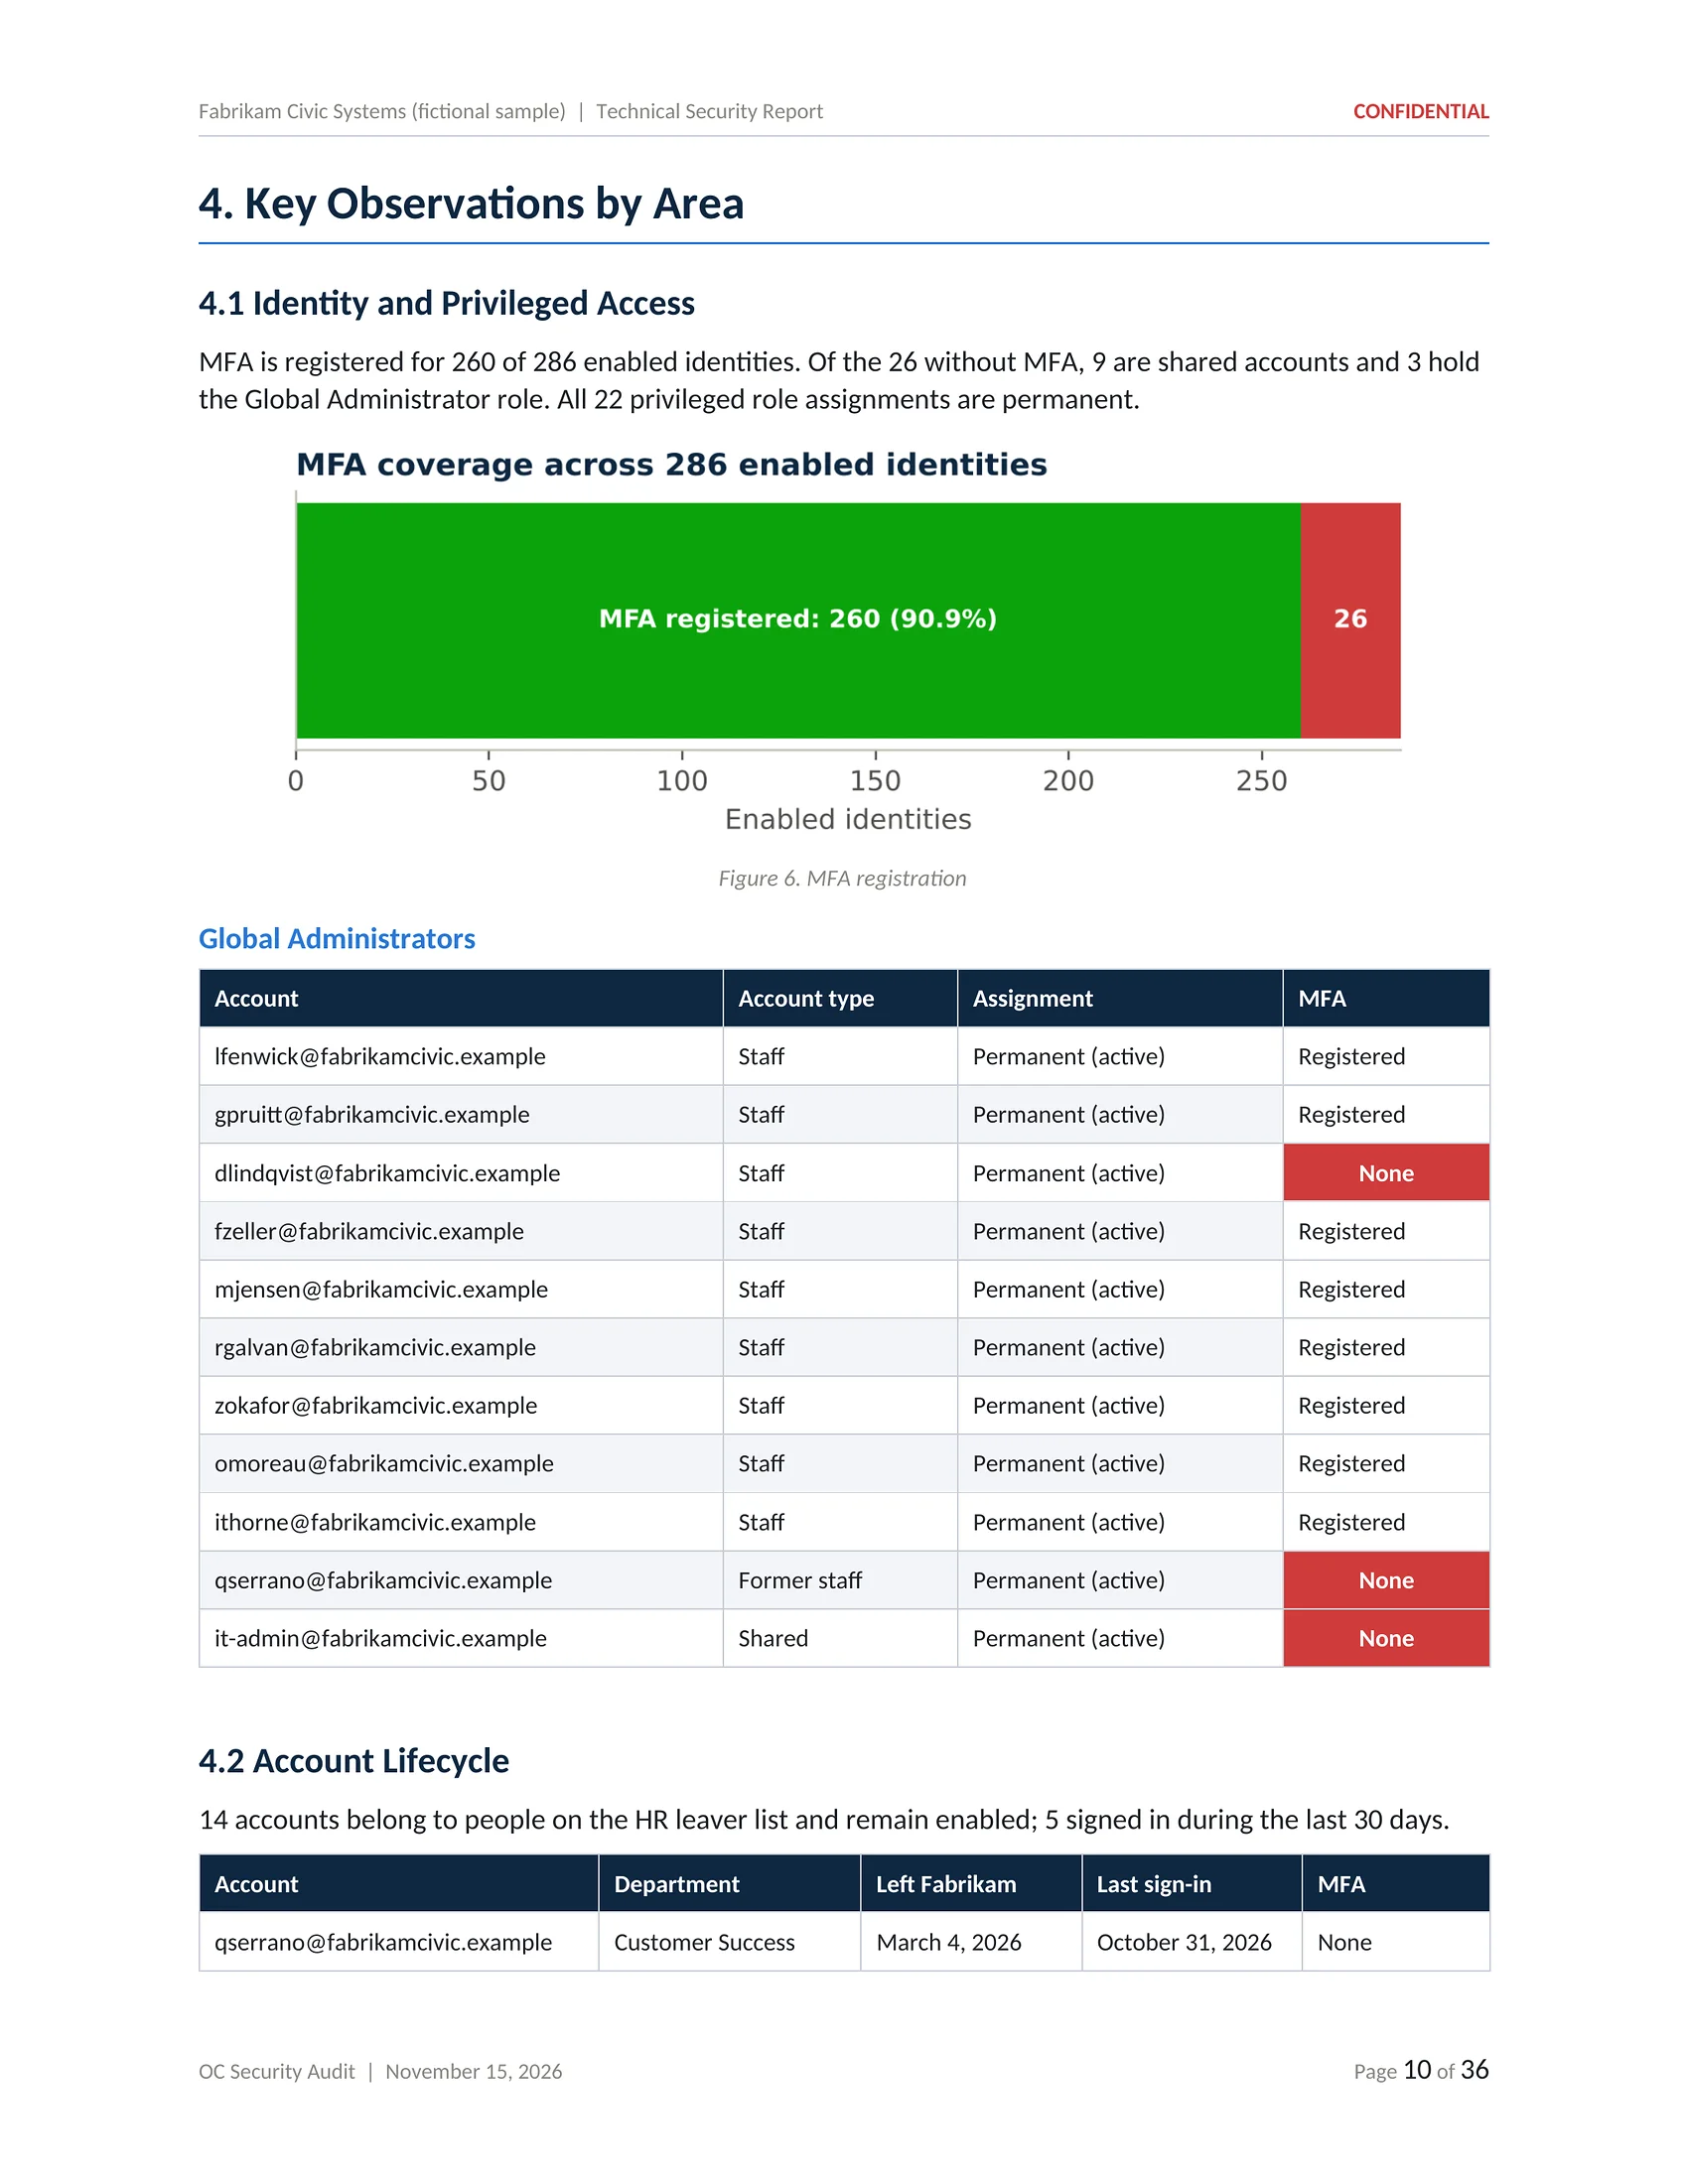
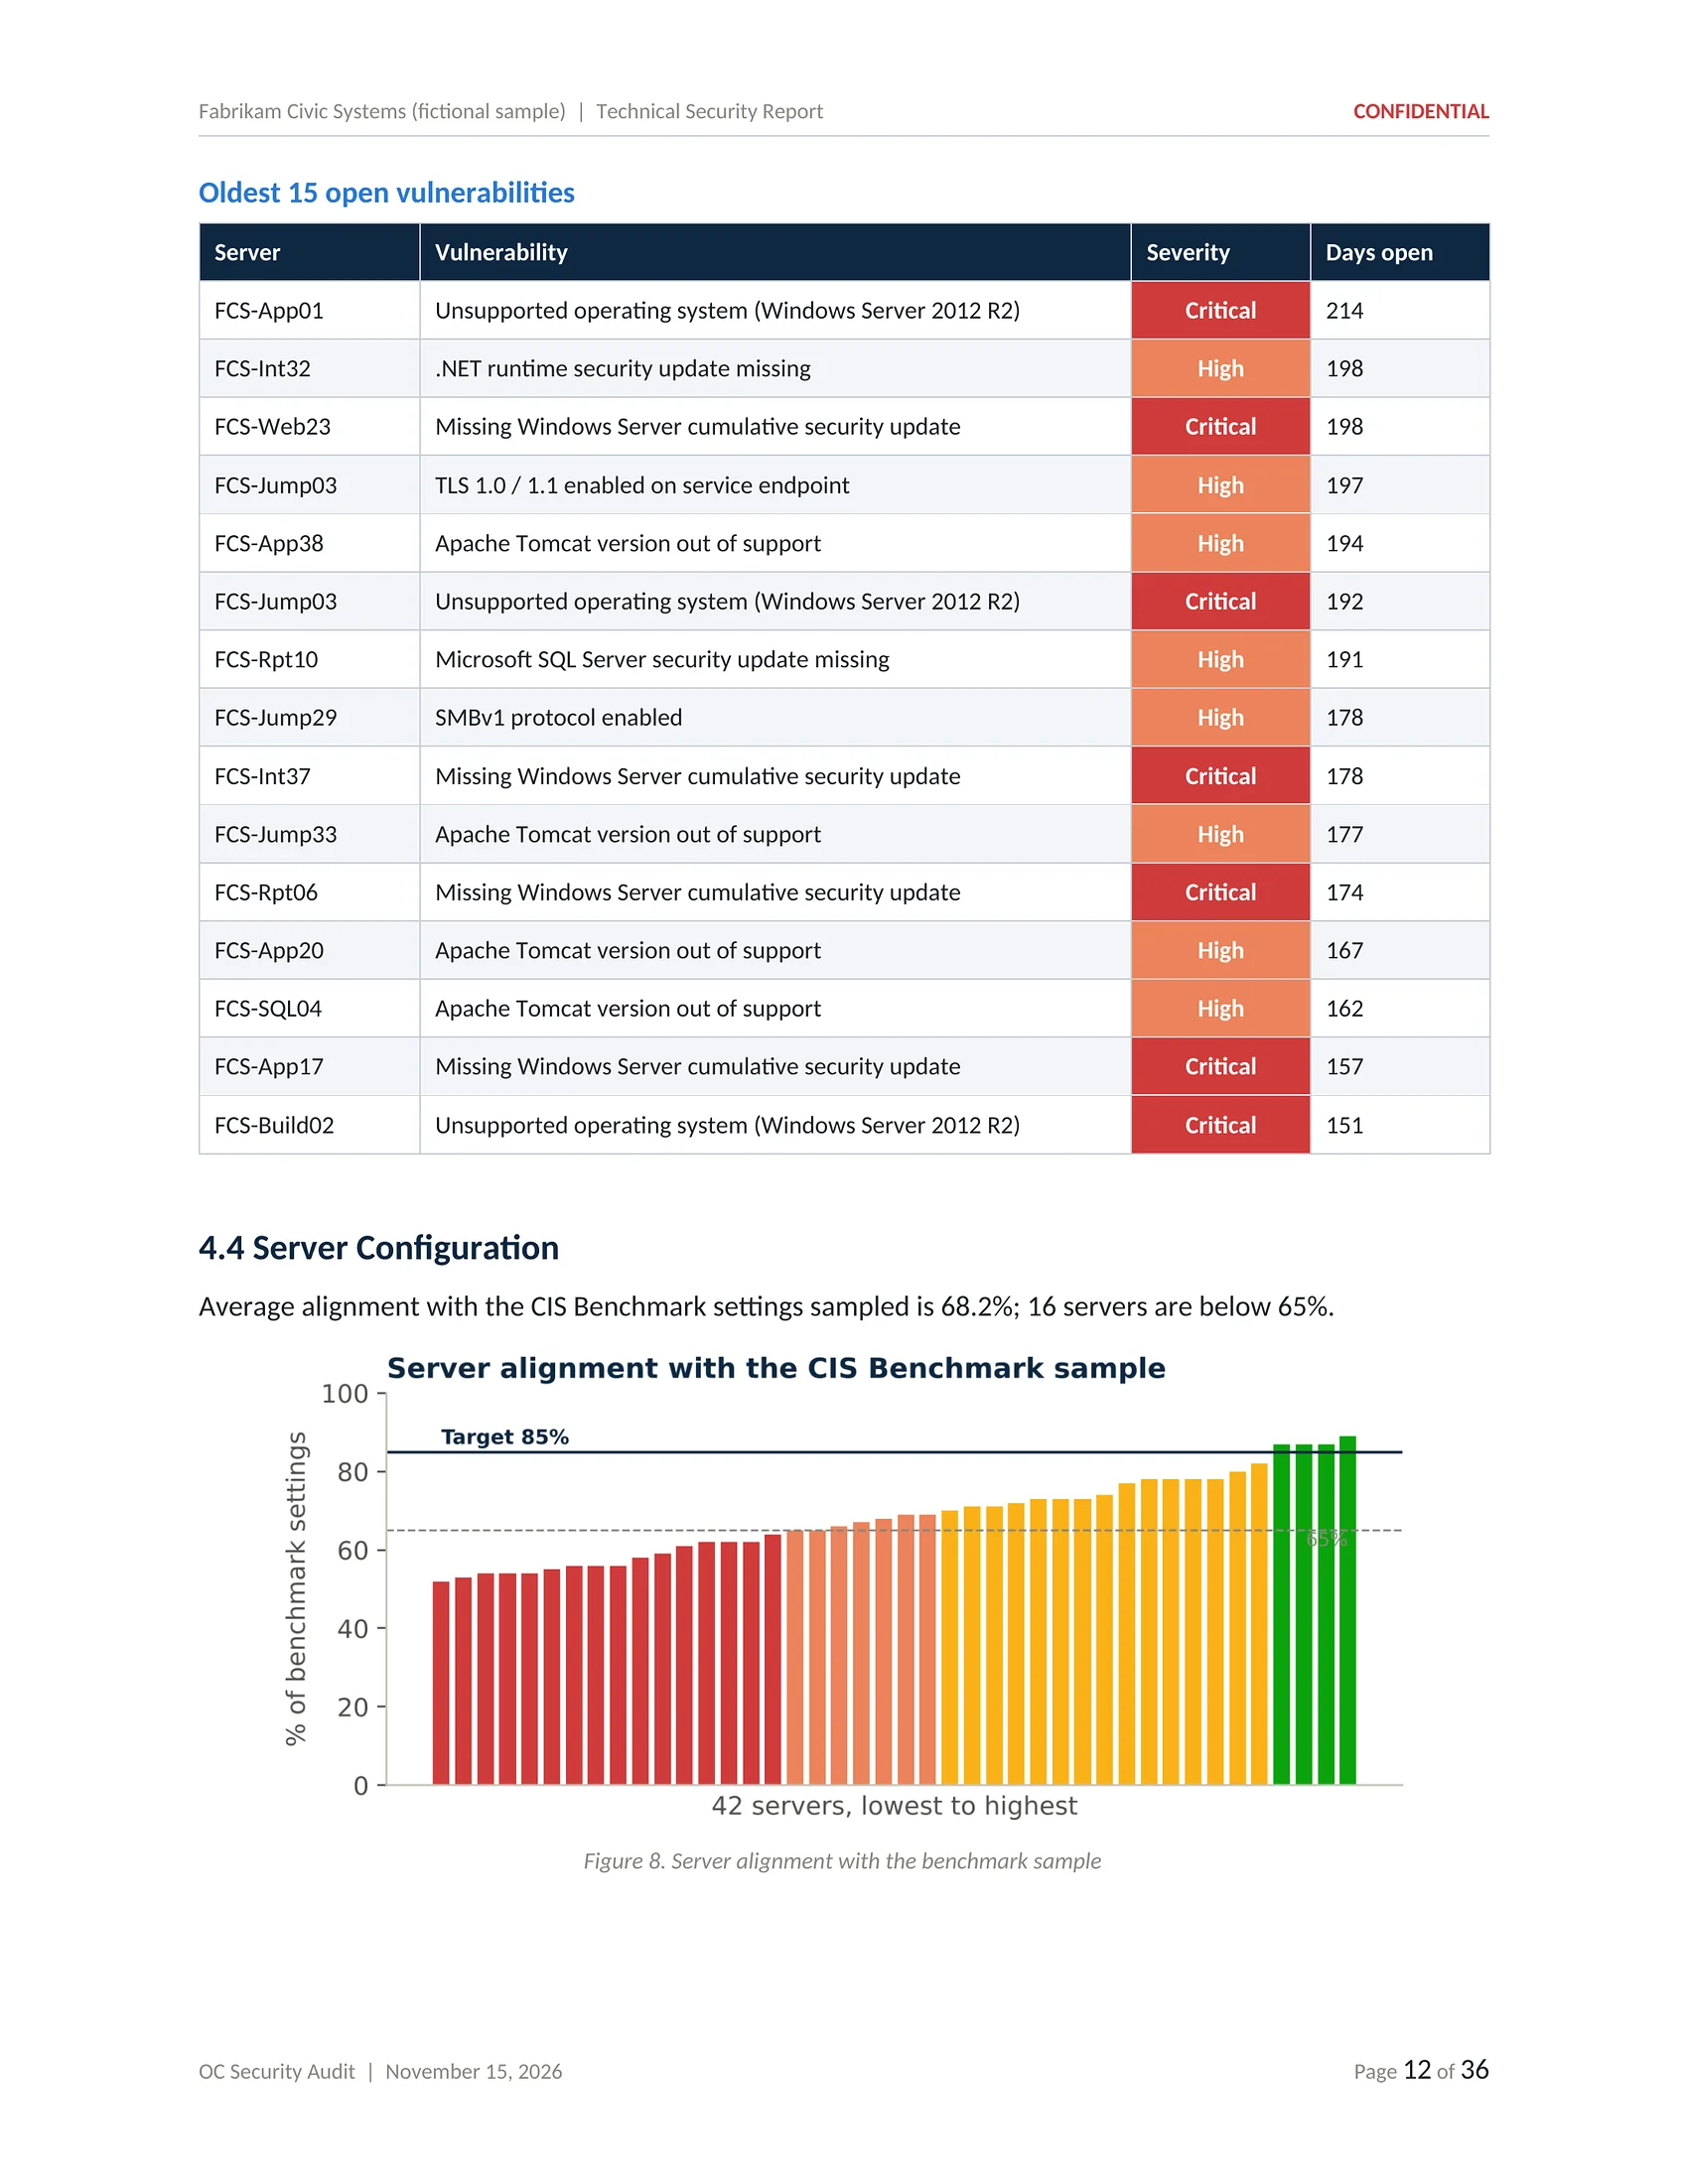
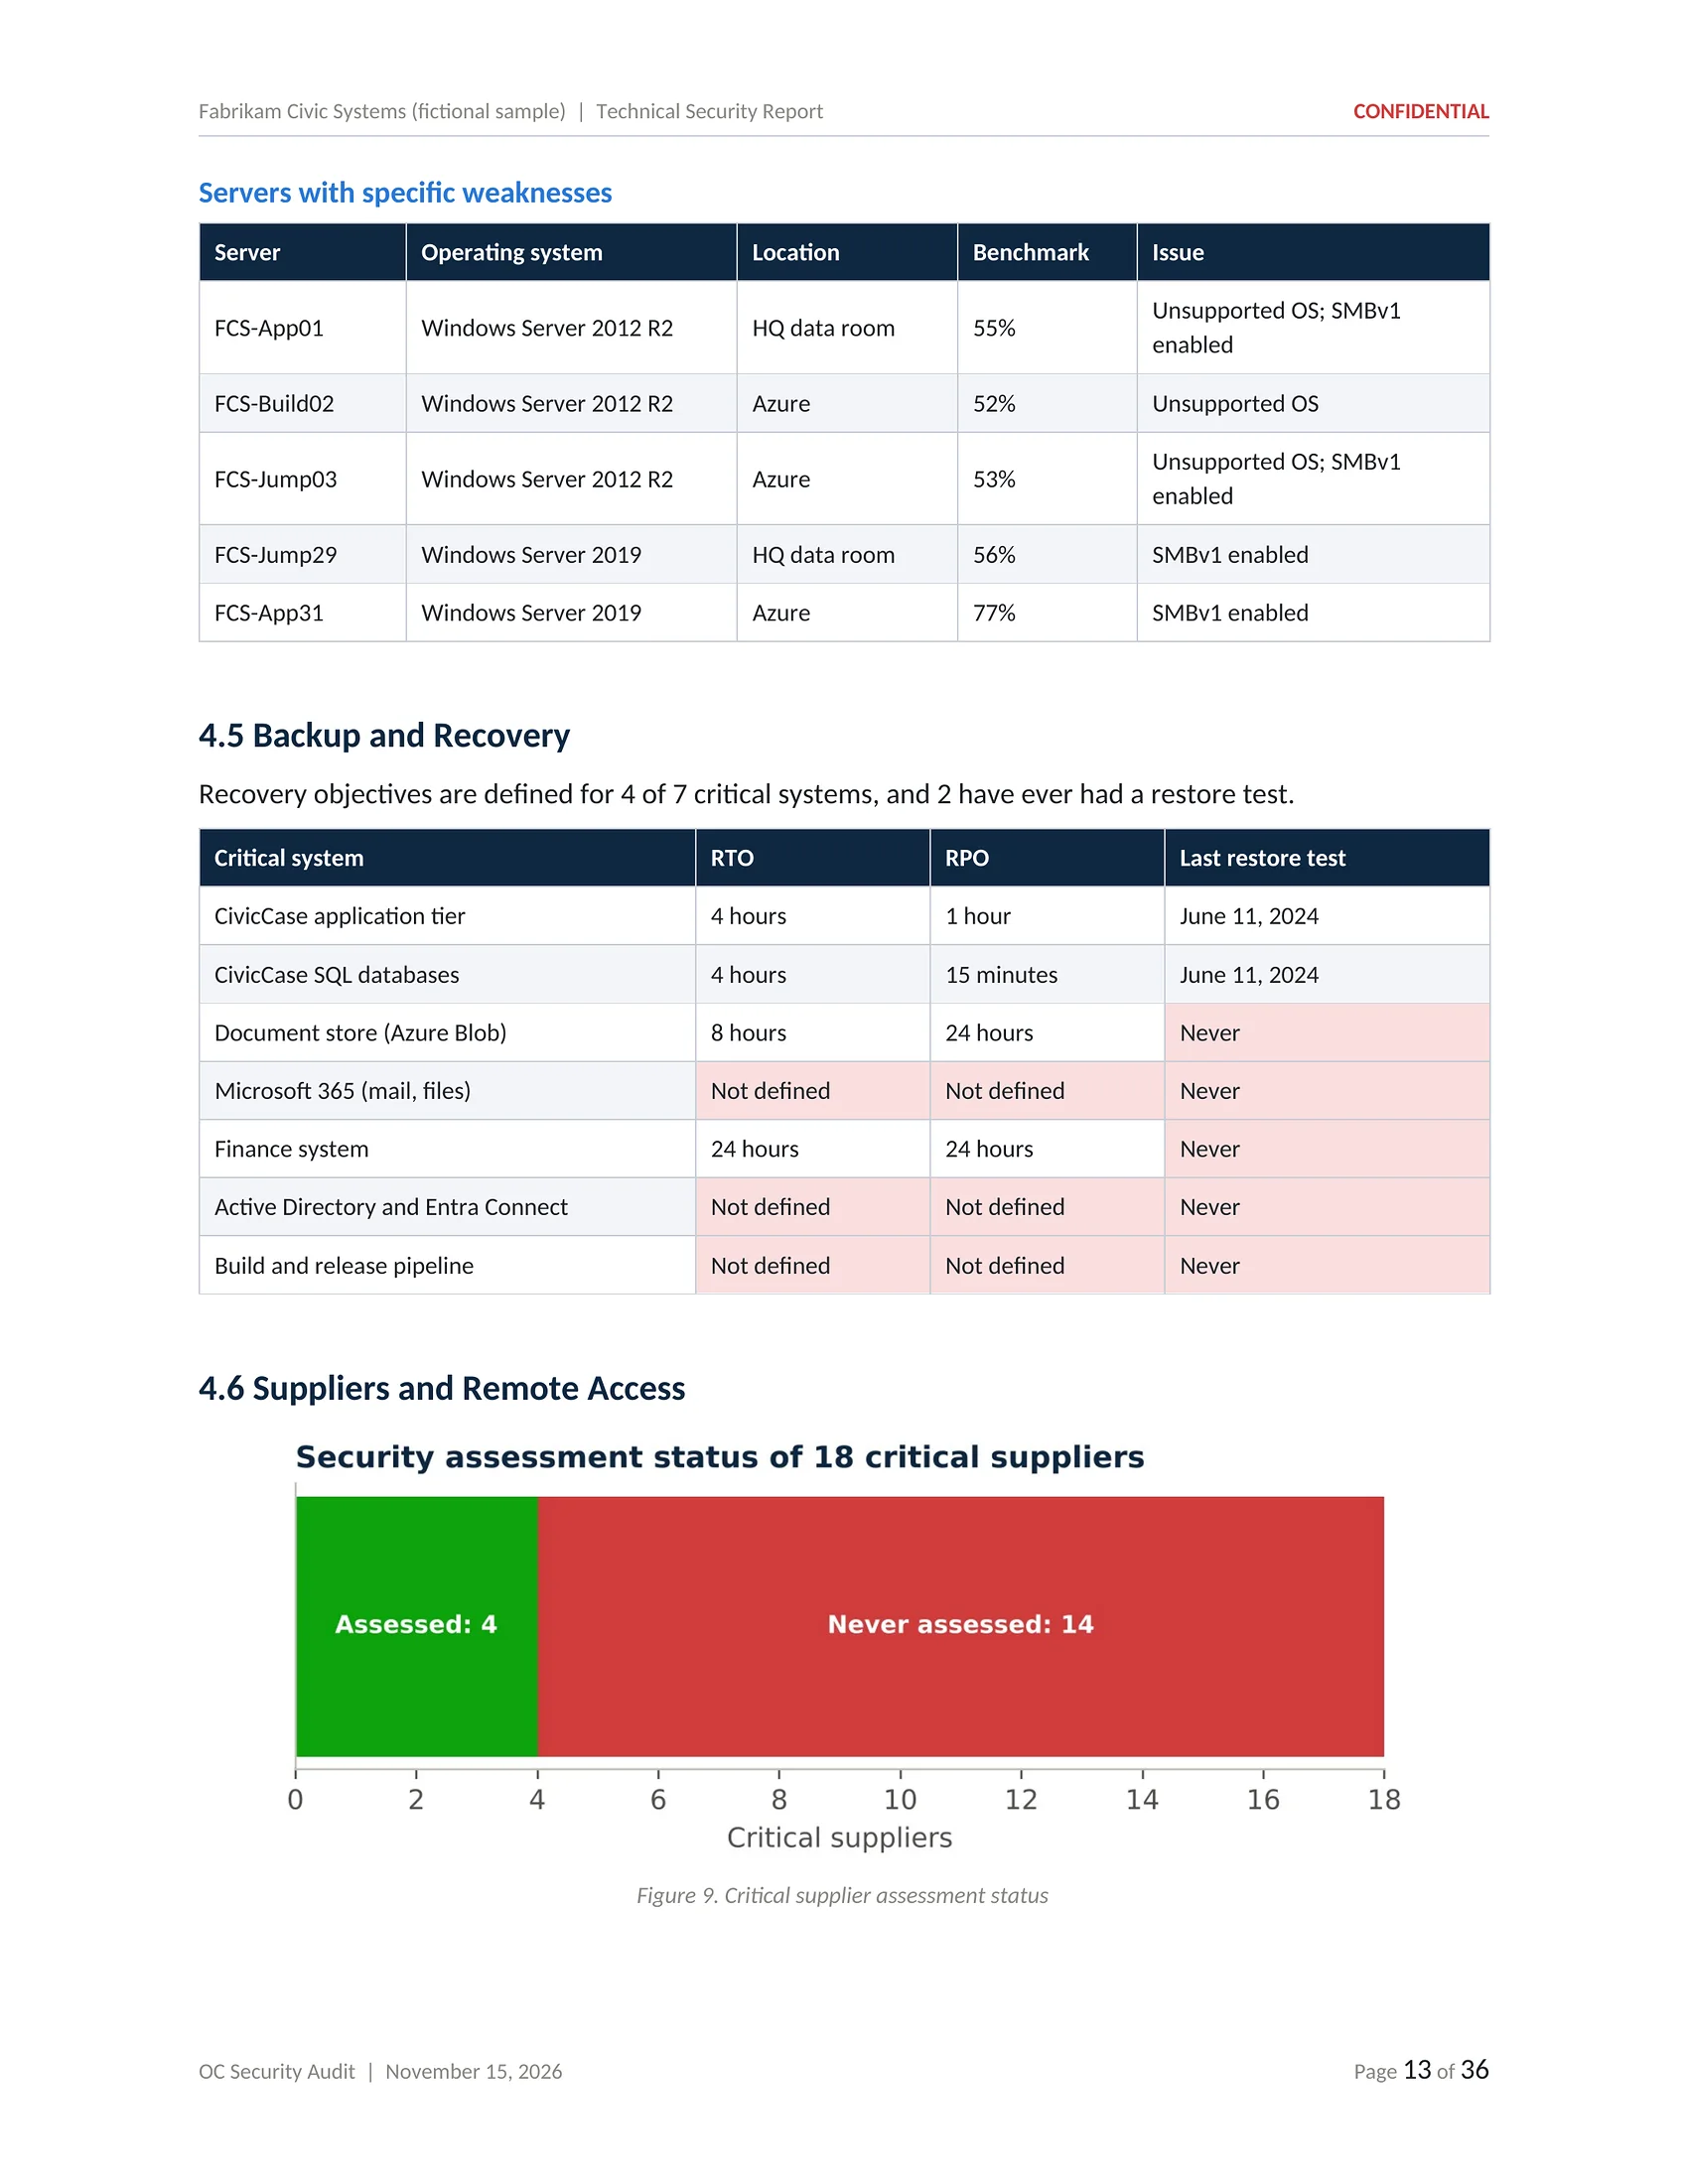
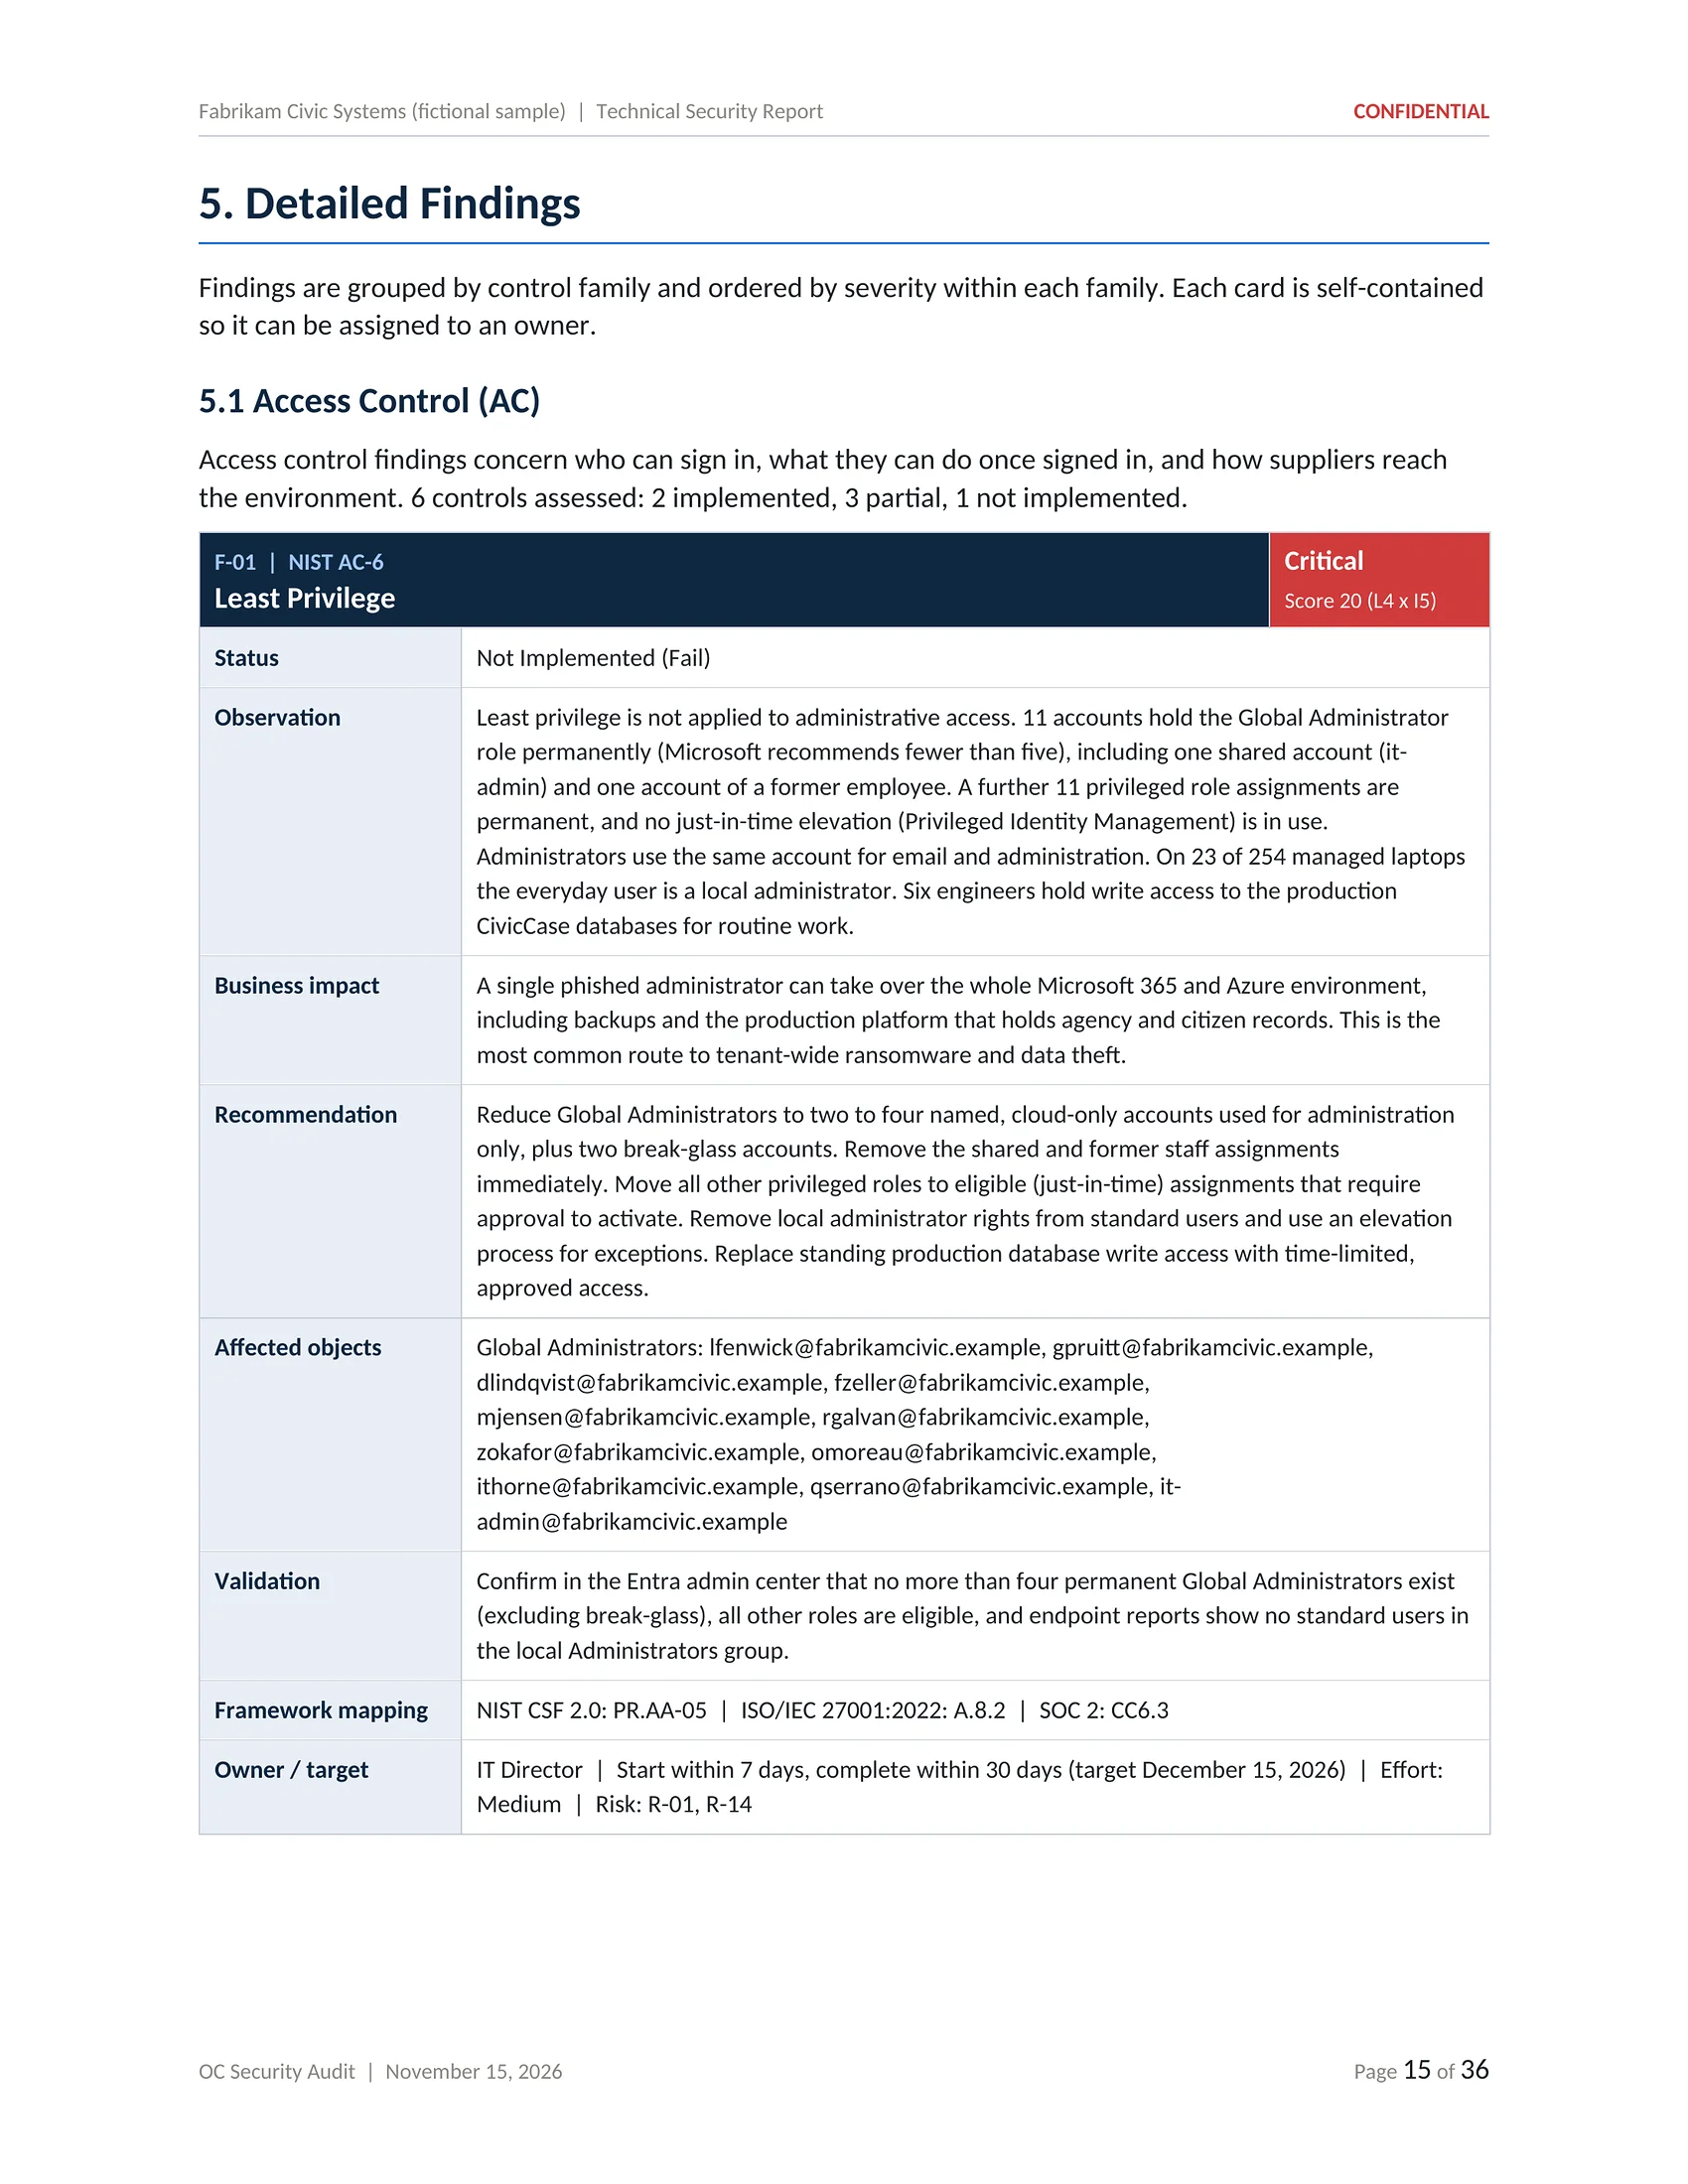
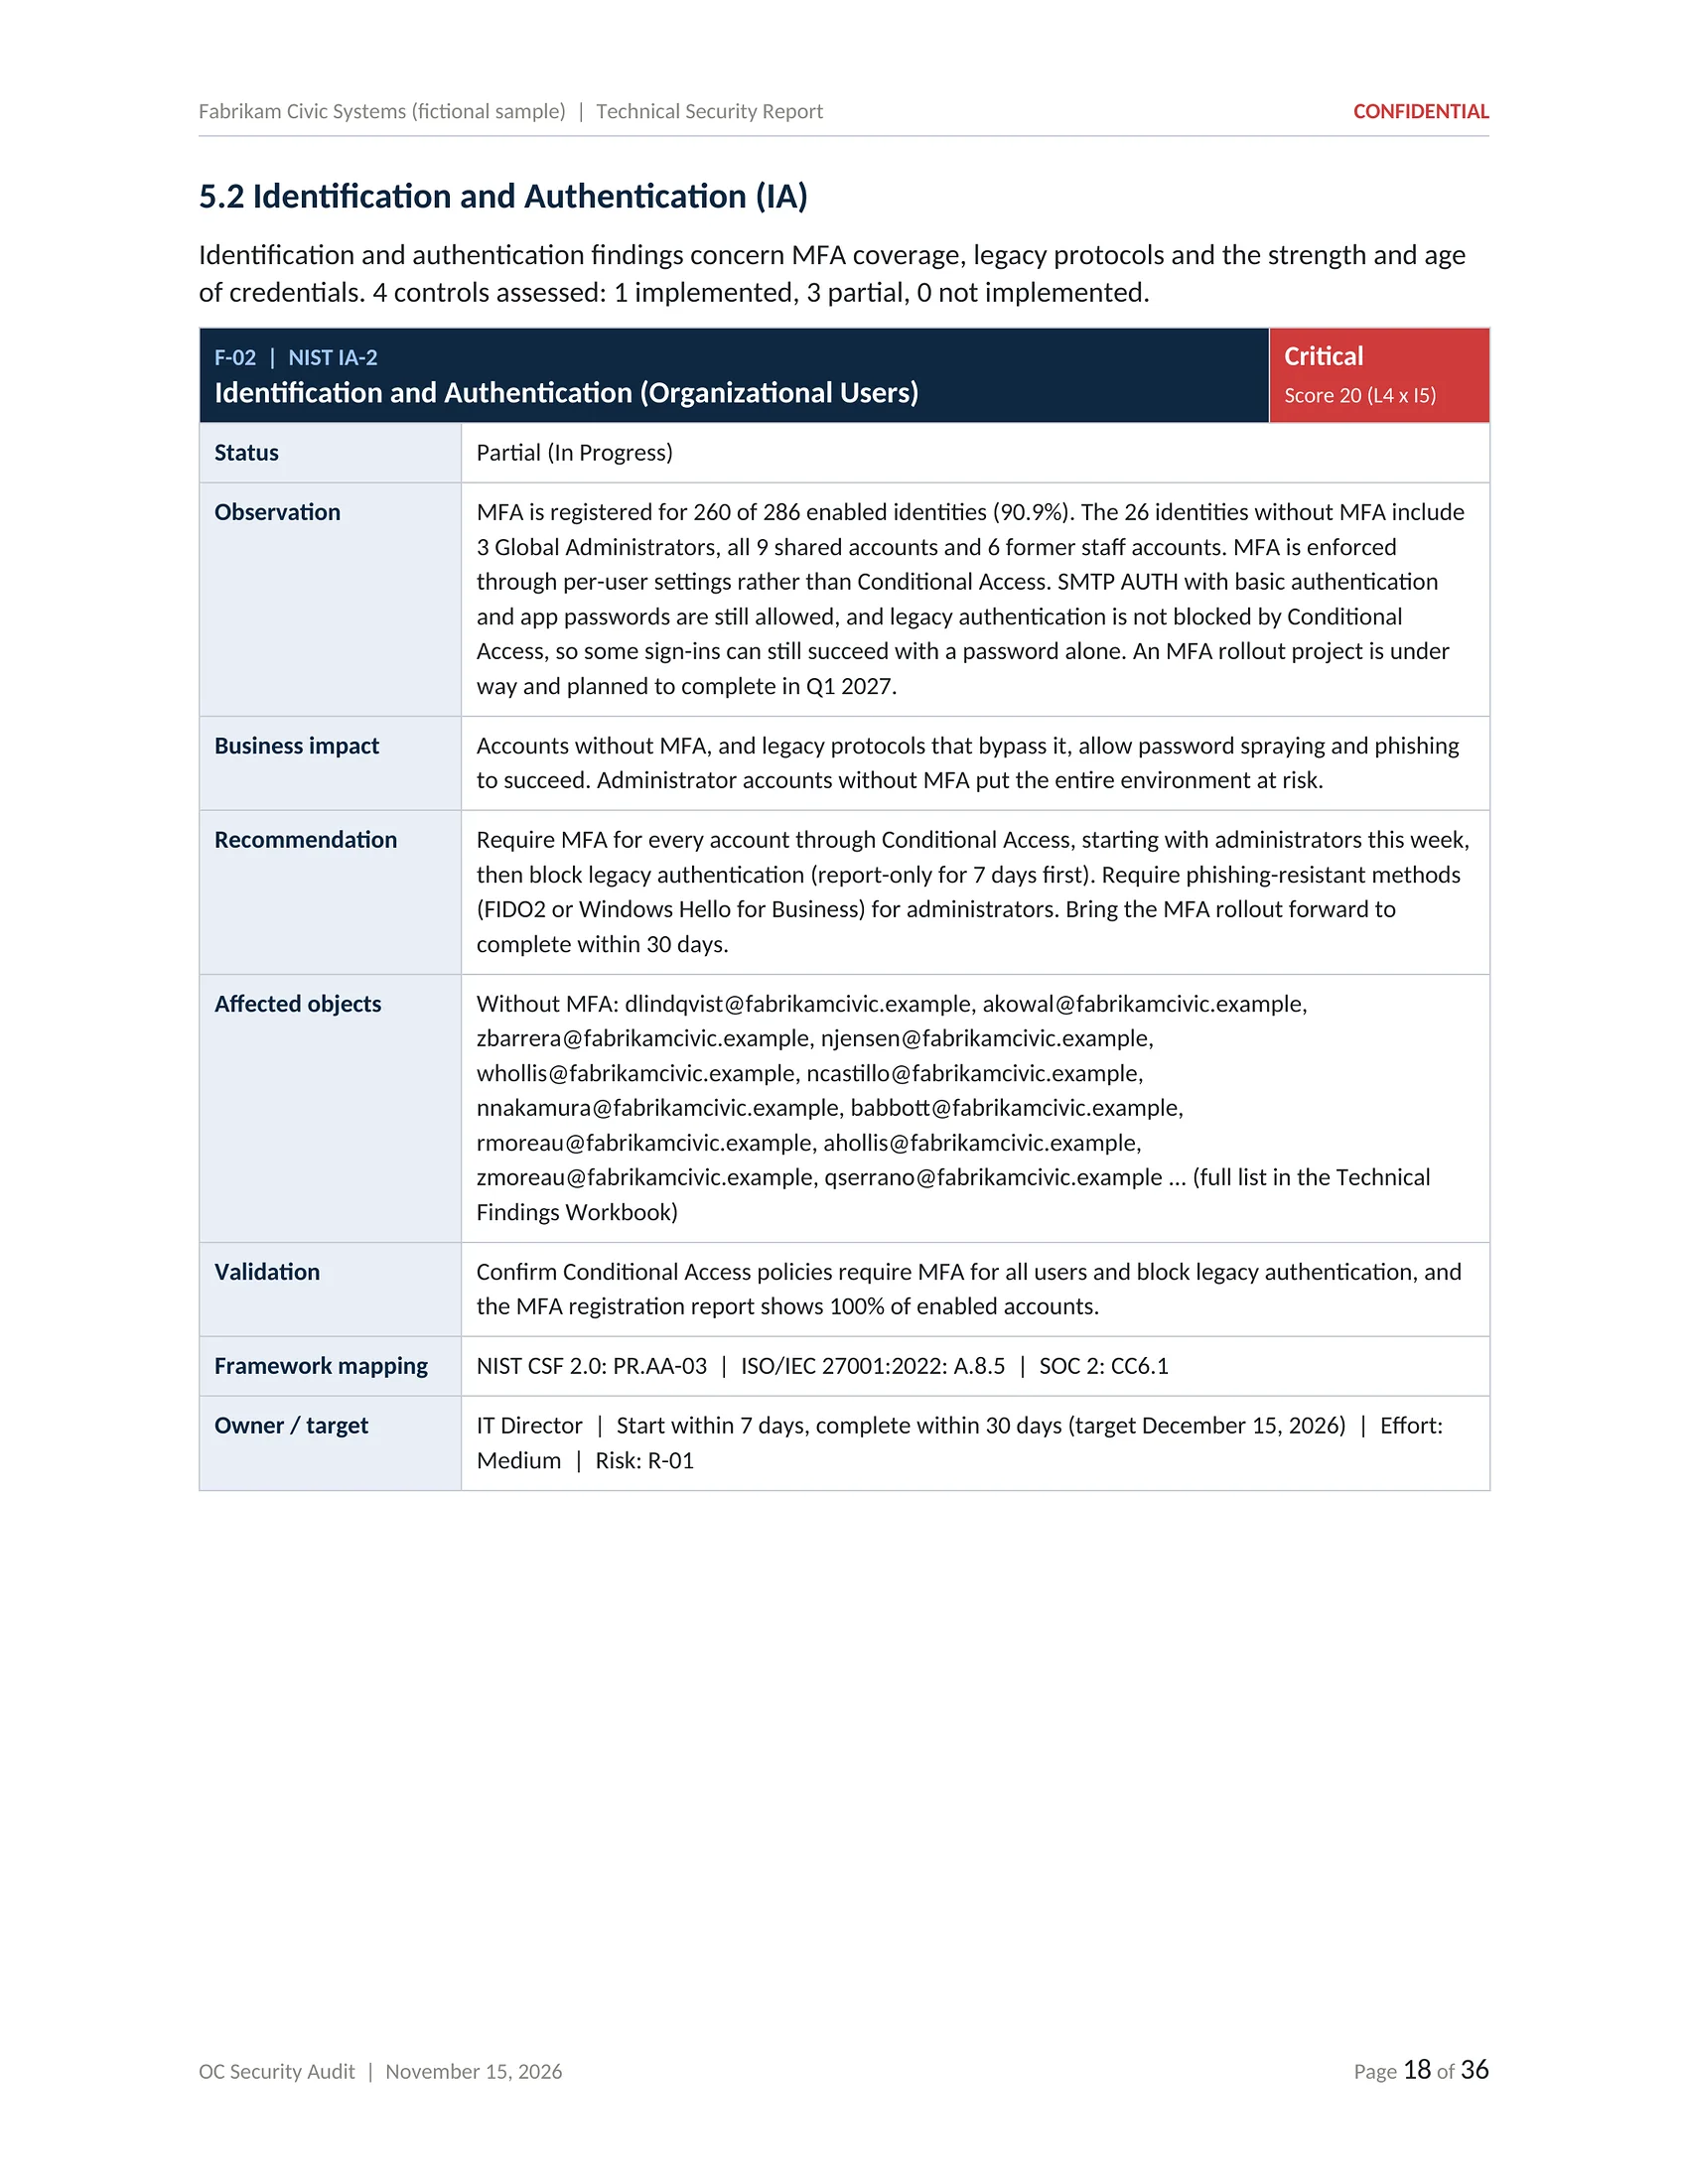
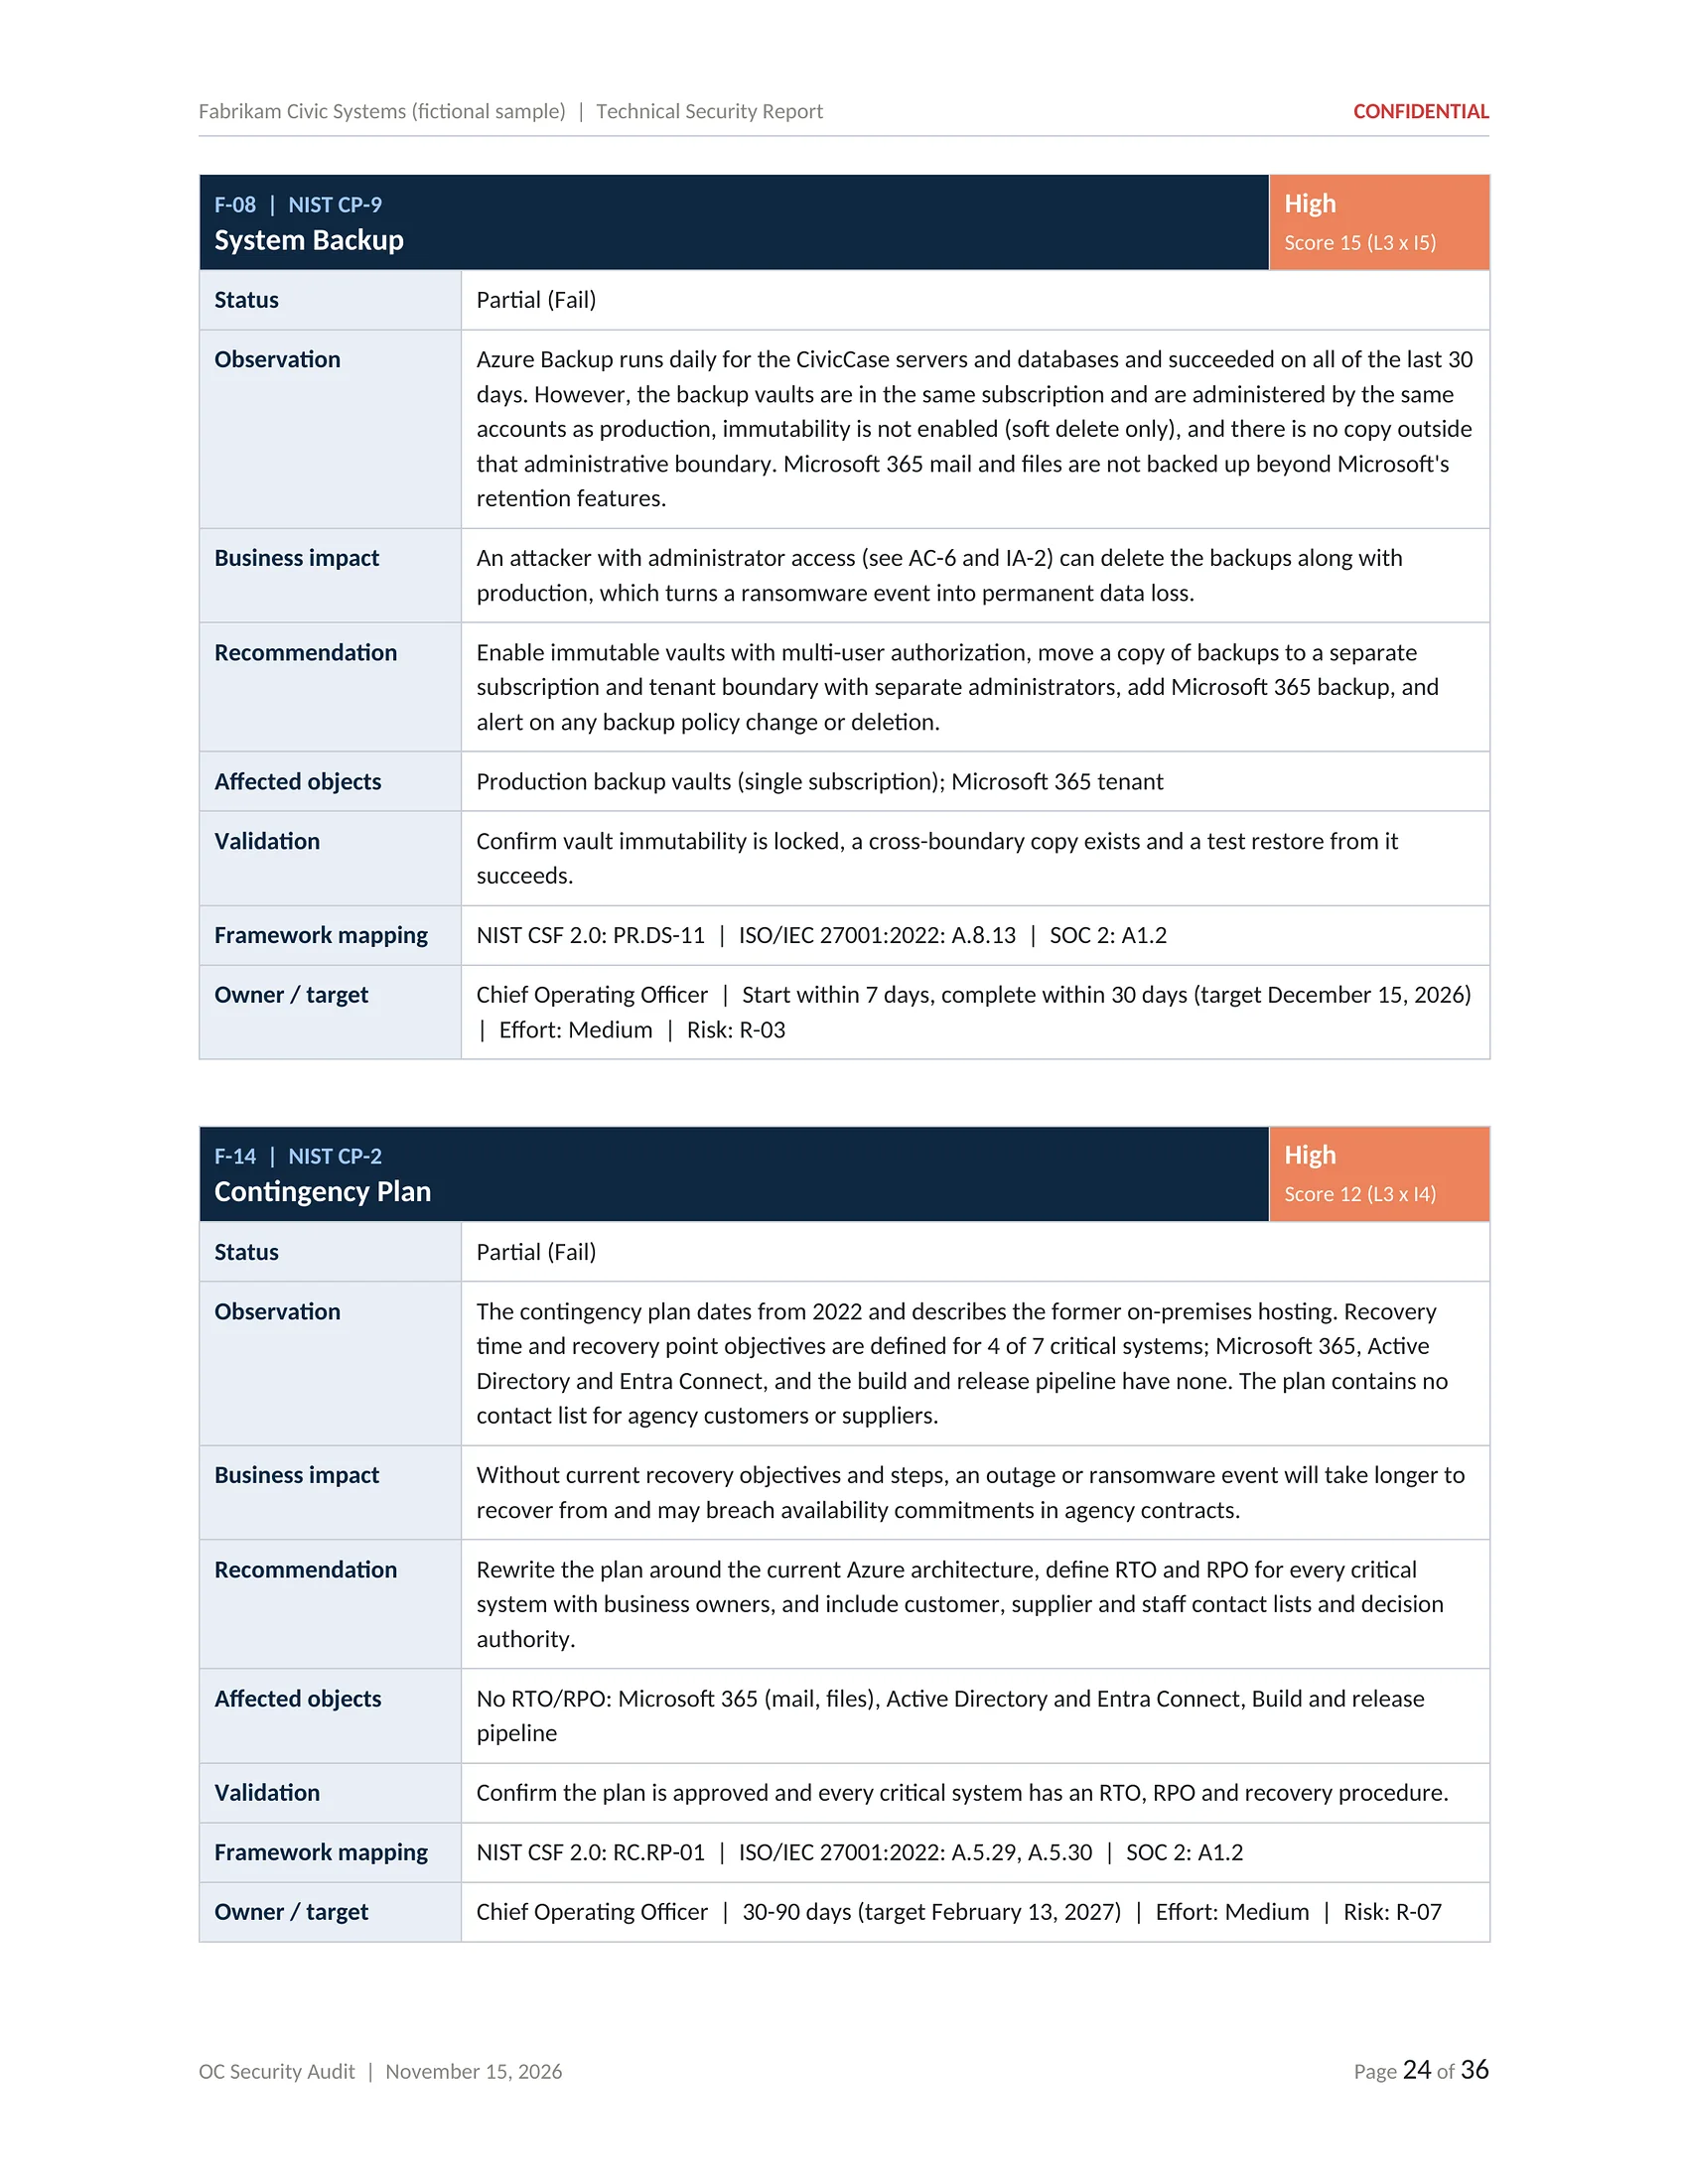
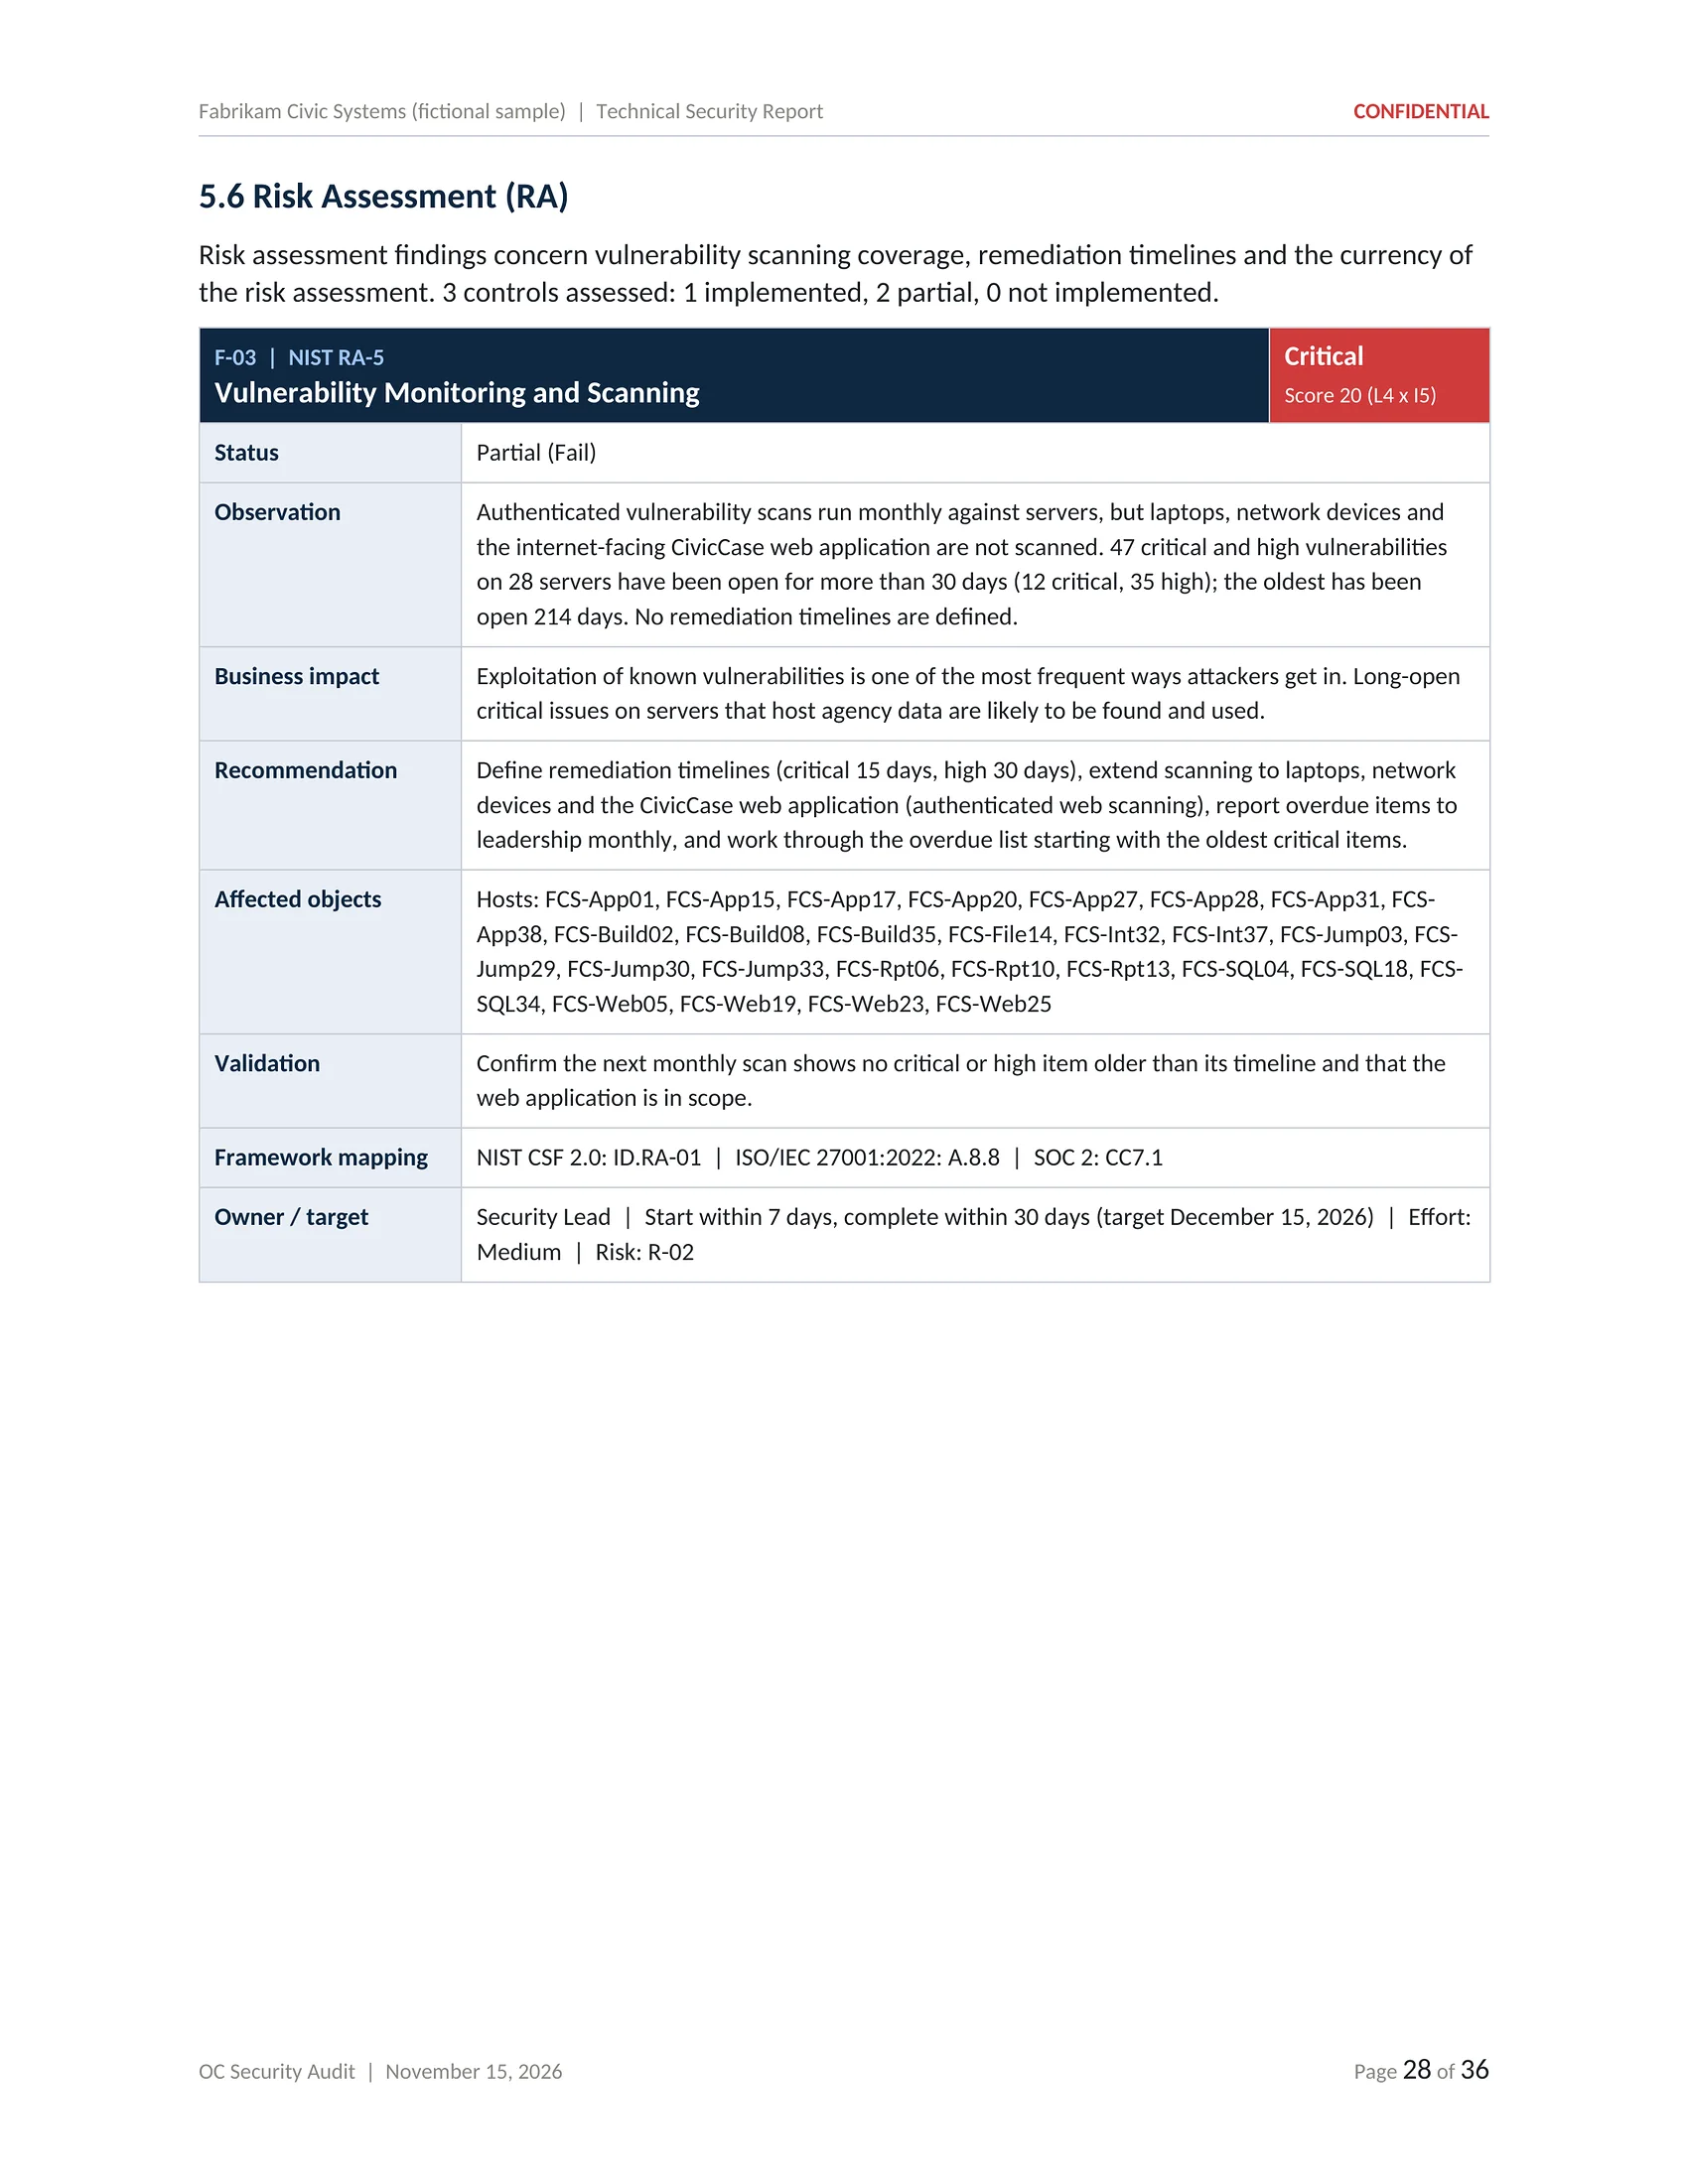
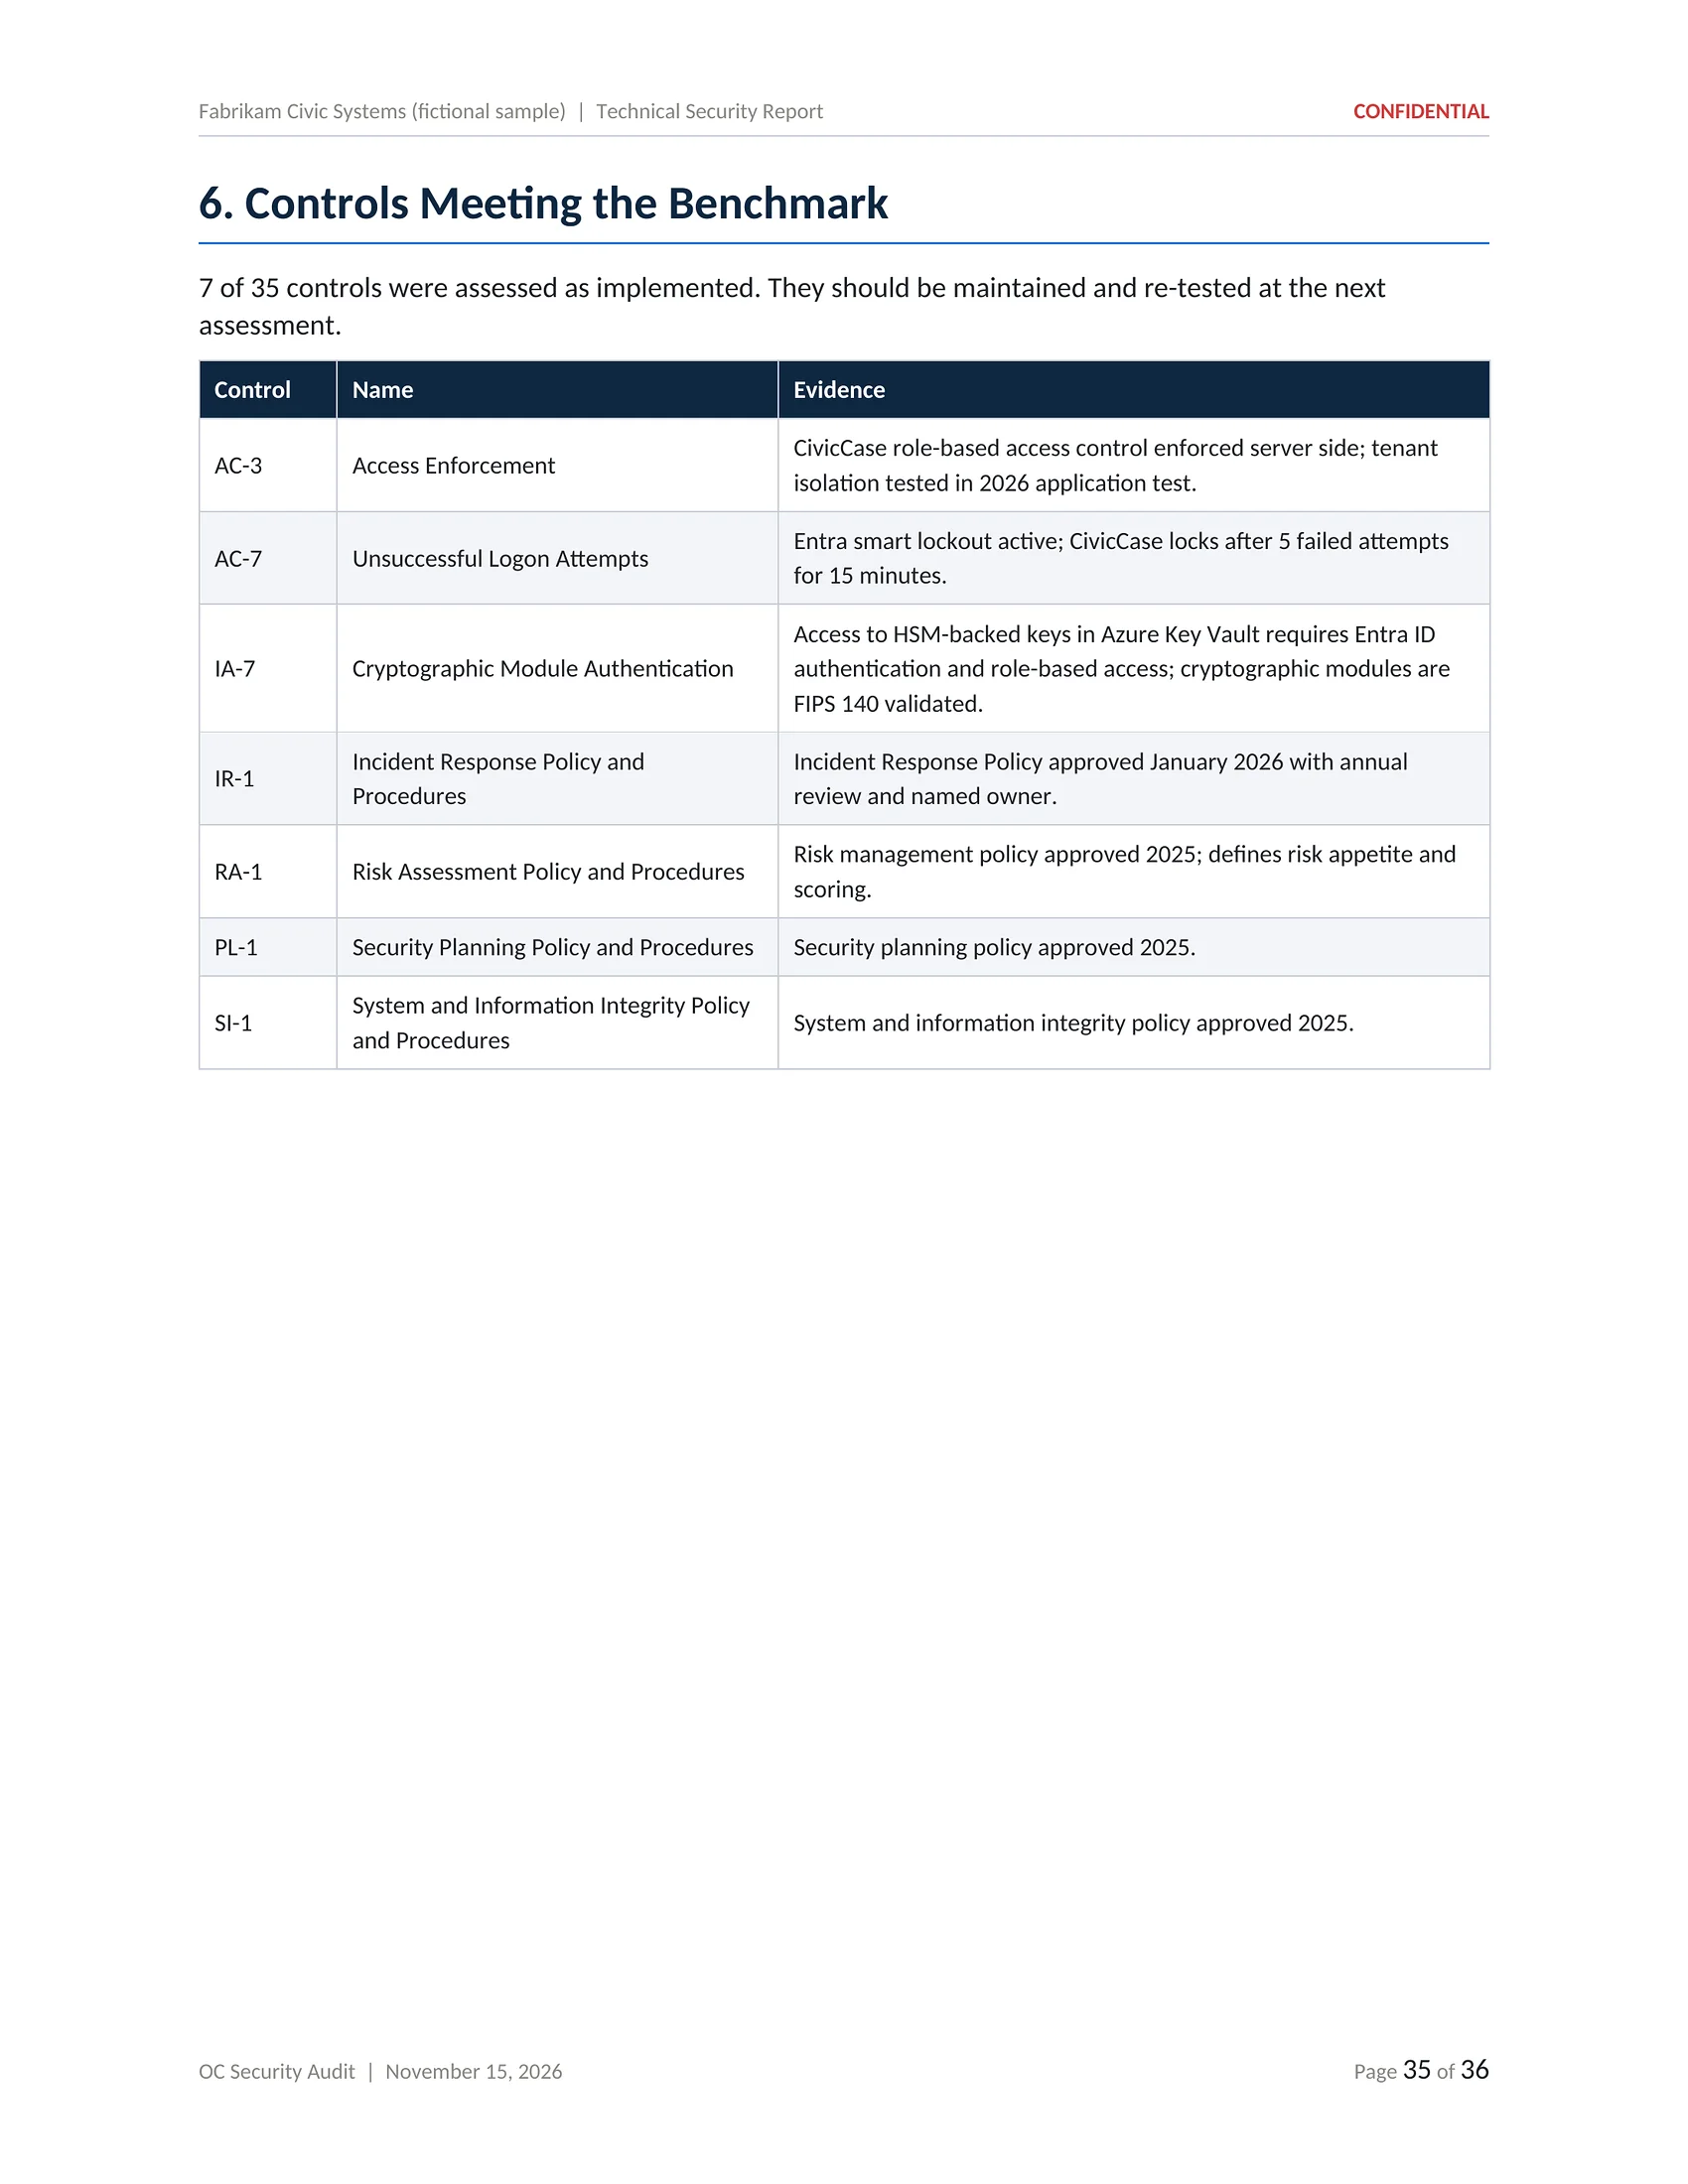
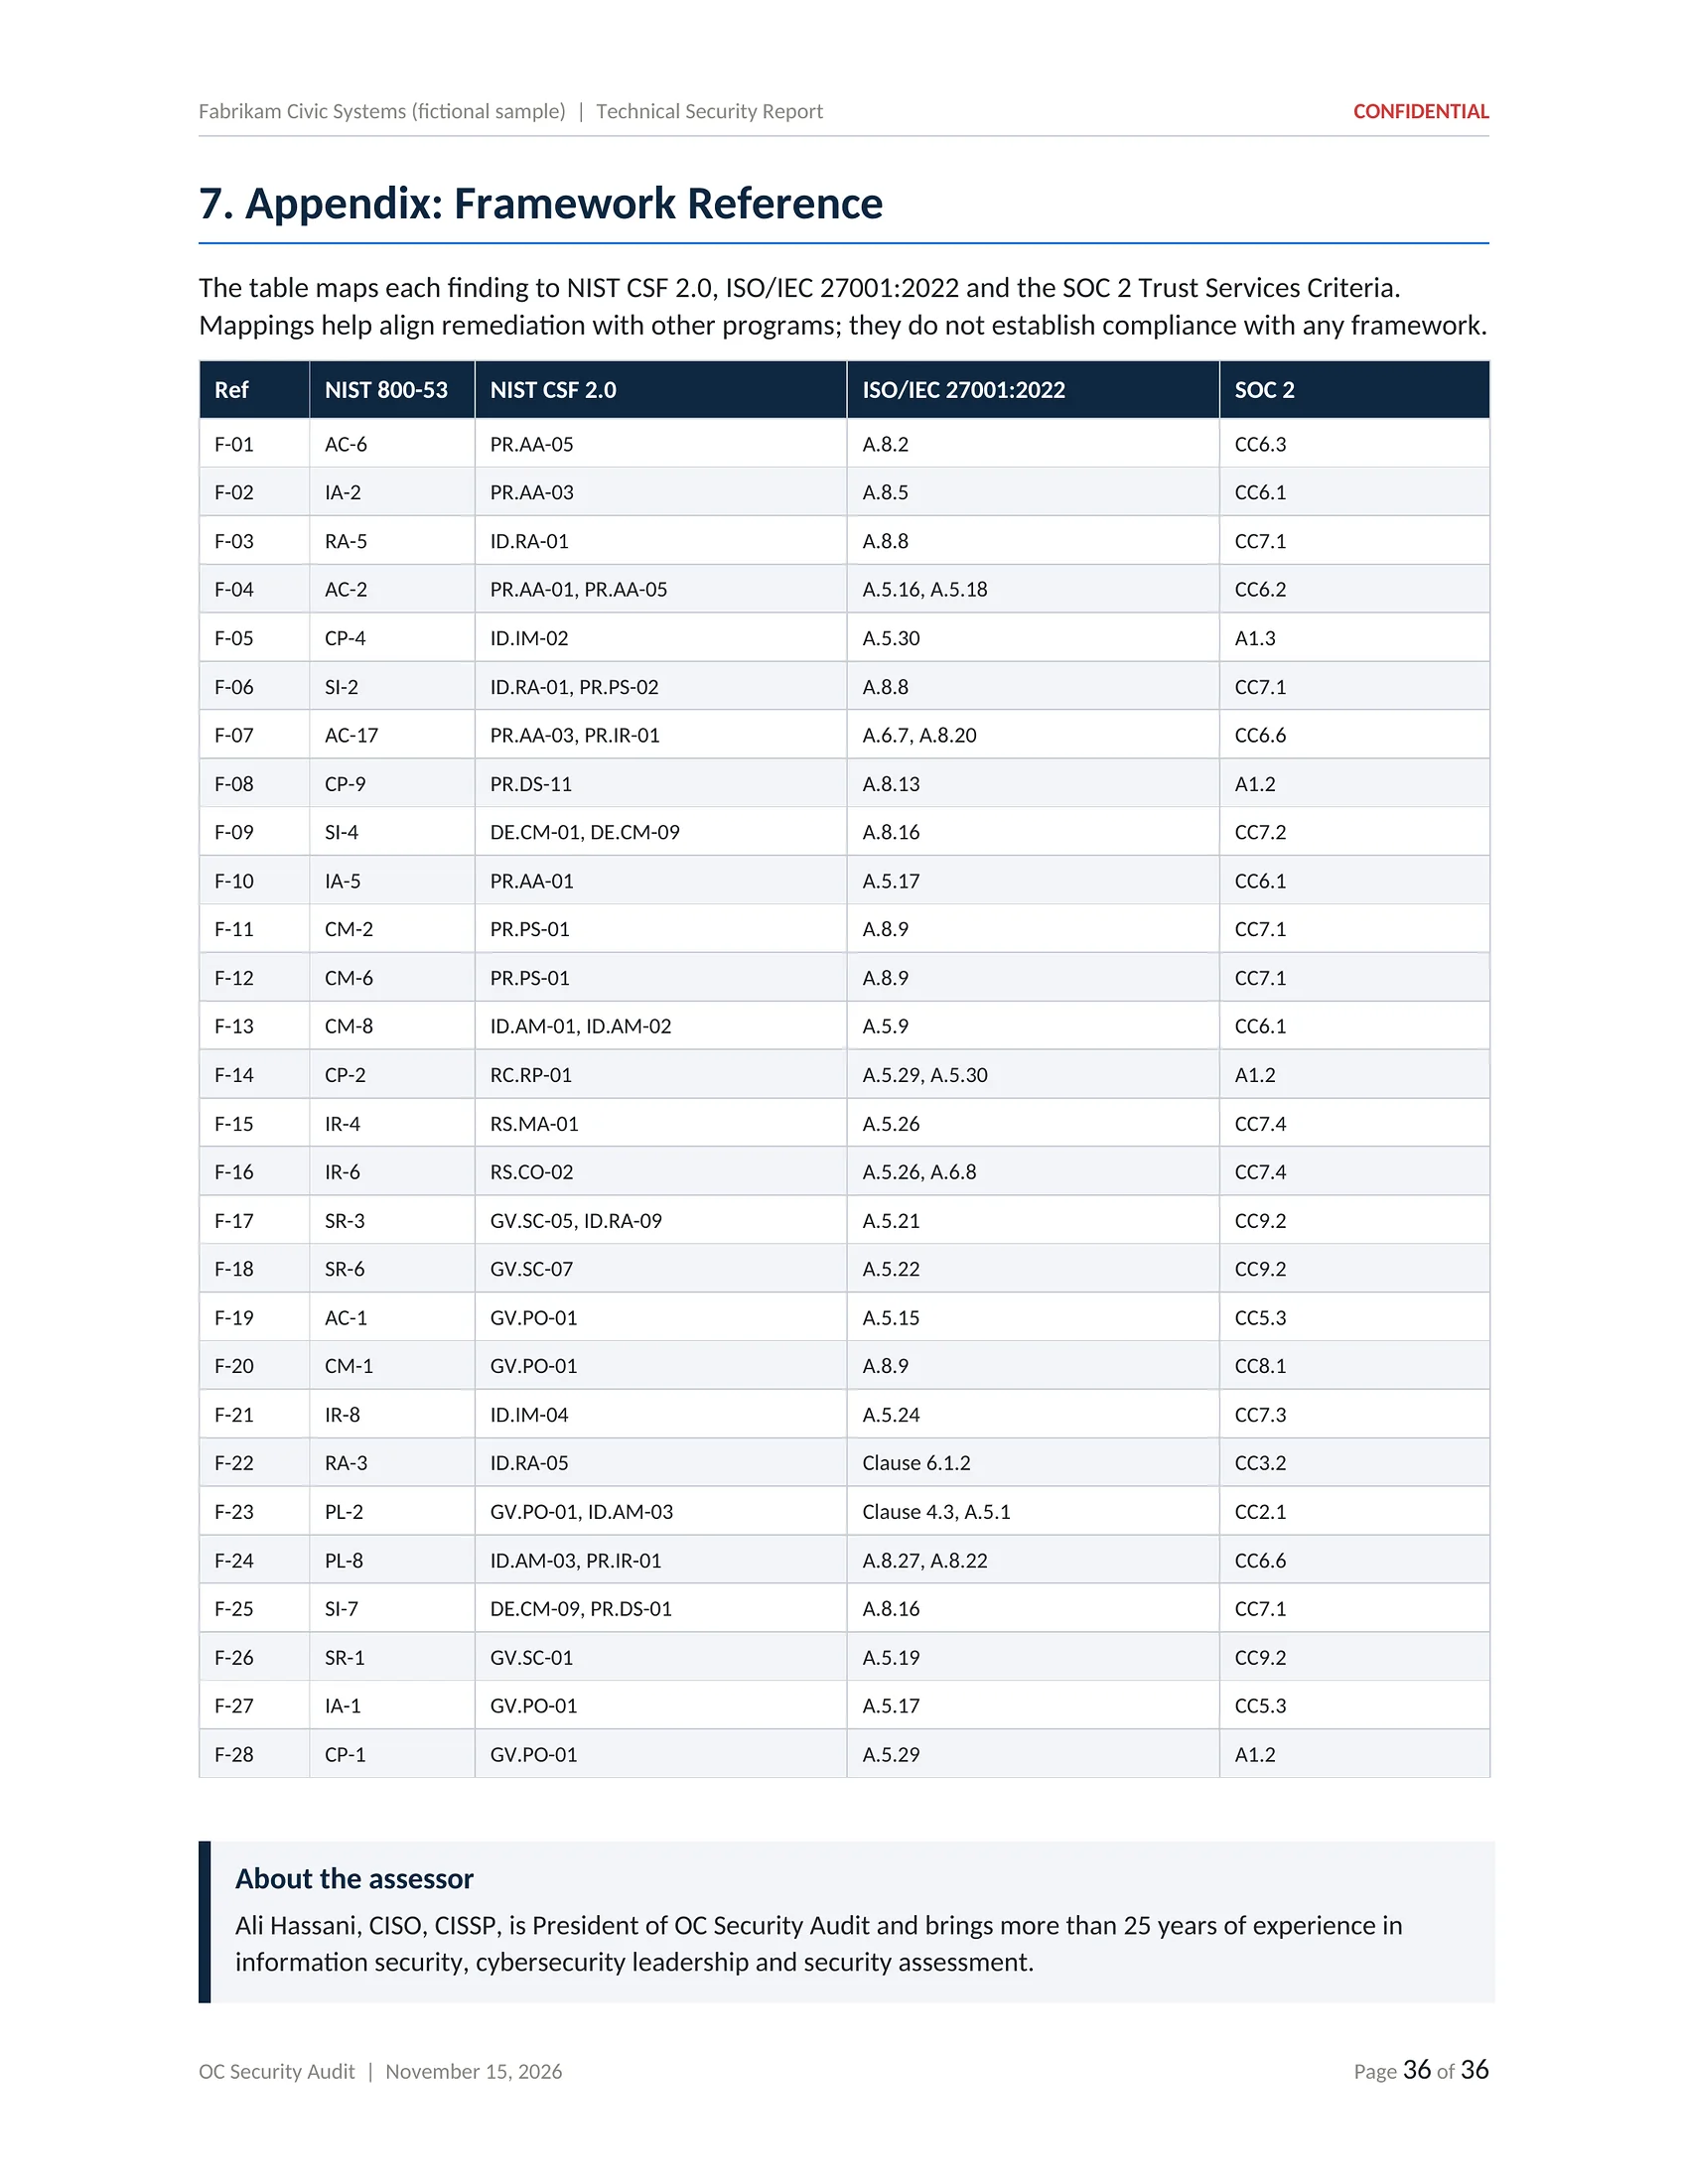
The working document for IT, security and engineering. After the scope, result definitions and environment overview, it summarizes the results, shows the evidence behind the key observations and gives one finding card per control gap: what we observed, the business impact, the recommendation, how to validate the fix, framework mappings, owner and target date.
IT director, security lead, engineers and the people who will close each finding.
What is included
- Scope, method and result definitions
- Environment overview
- Results by severity and family
- Key observations with evidence tables
- One finding card per control gap
- Validation steps for every fix
- Owner, window and target date
- Controls meeting the benchmark
- NIST CSF 2.0, ISO 27001 and SOC 2 mapping
Click the page in the centre to open it full size, then zoom in to read every line.
PDF and Word · 17 pages, landscape
Risk Register
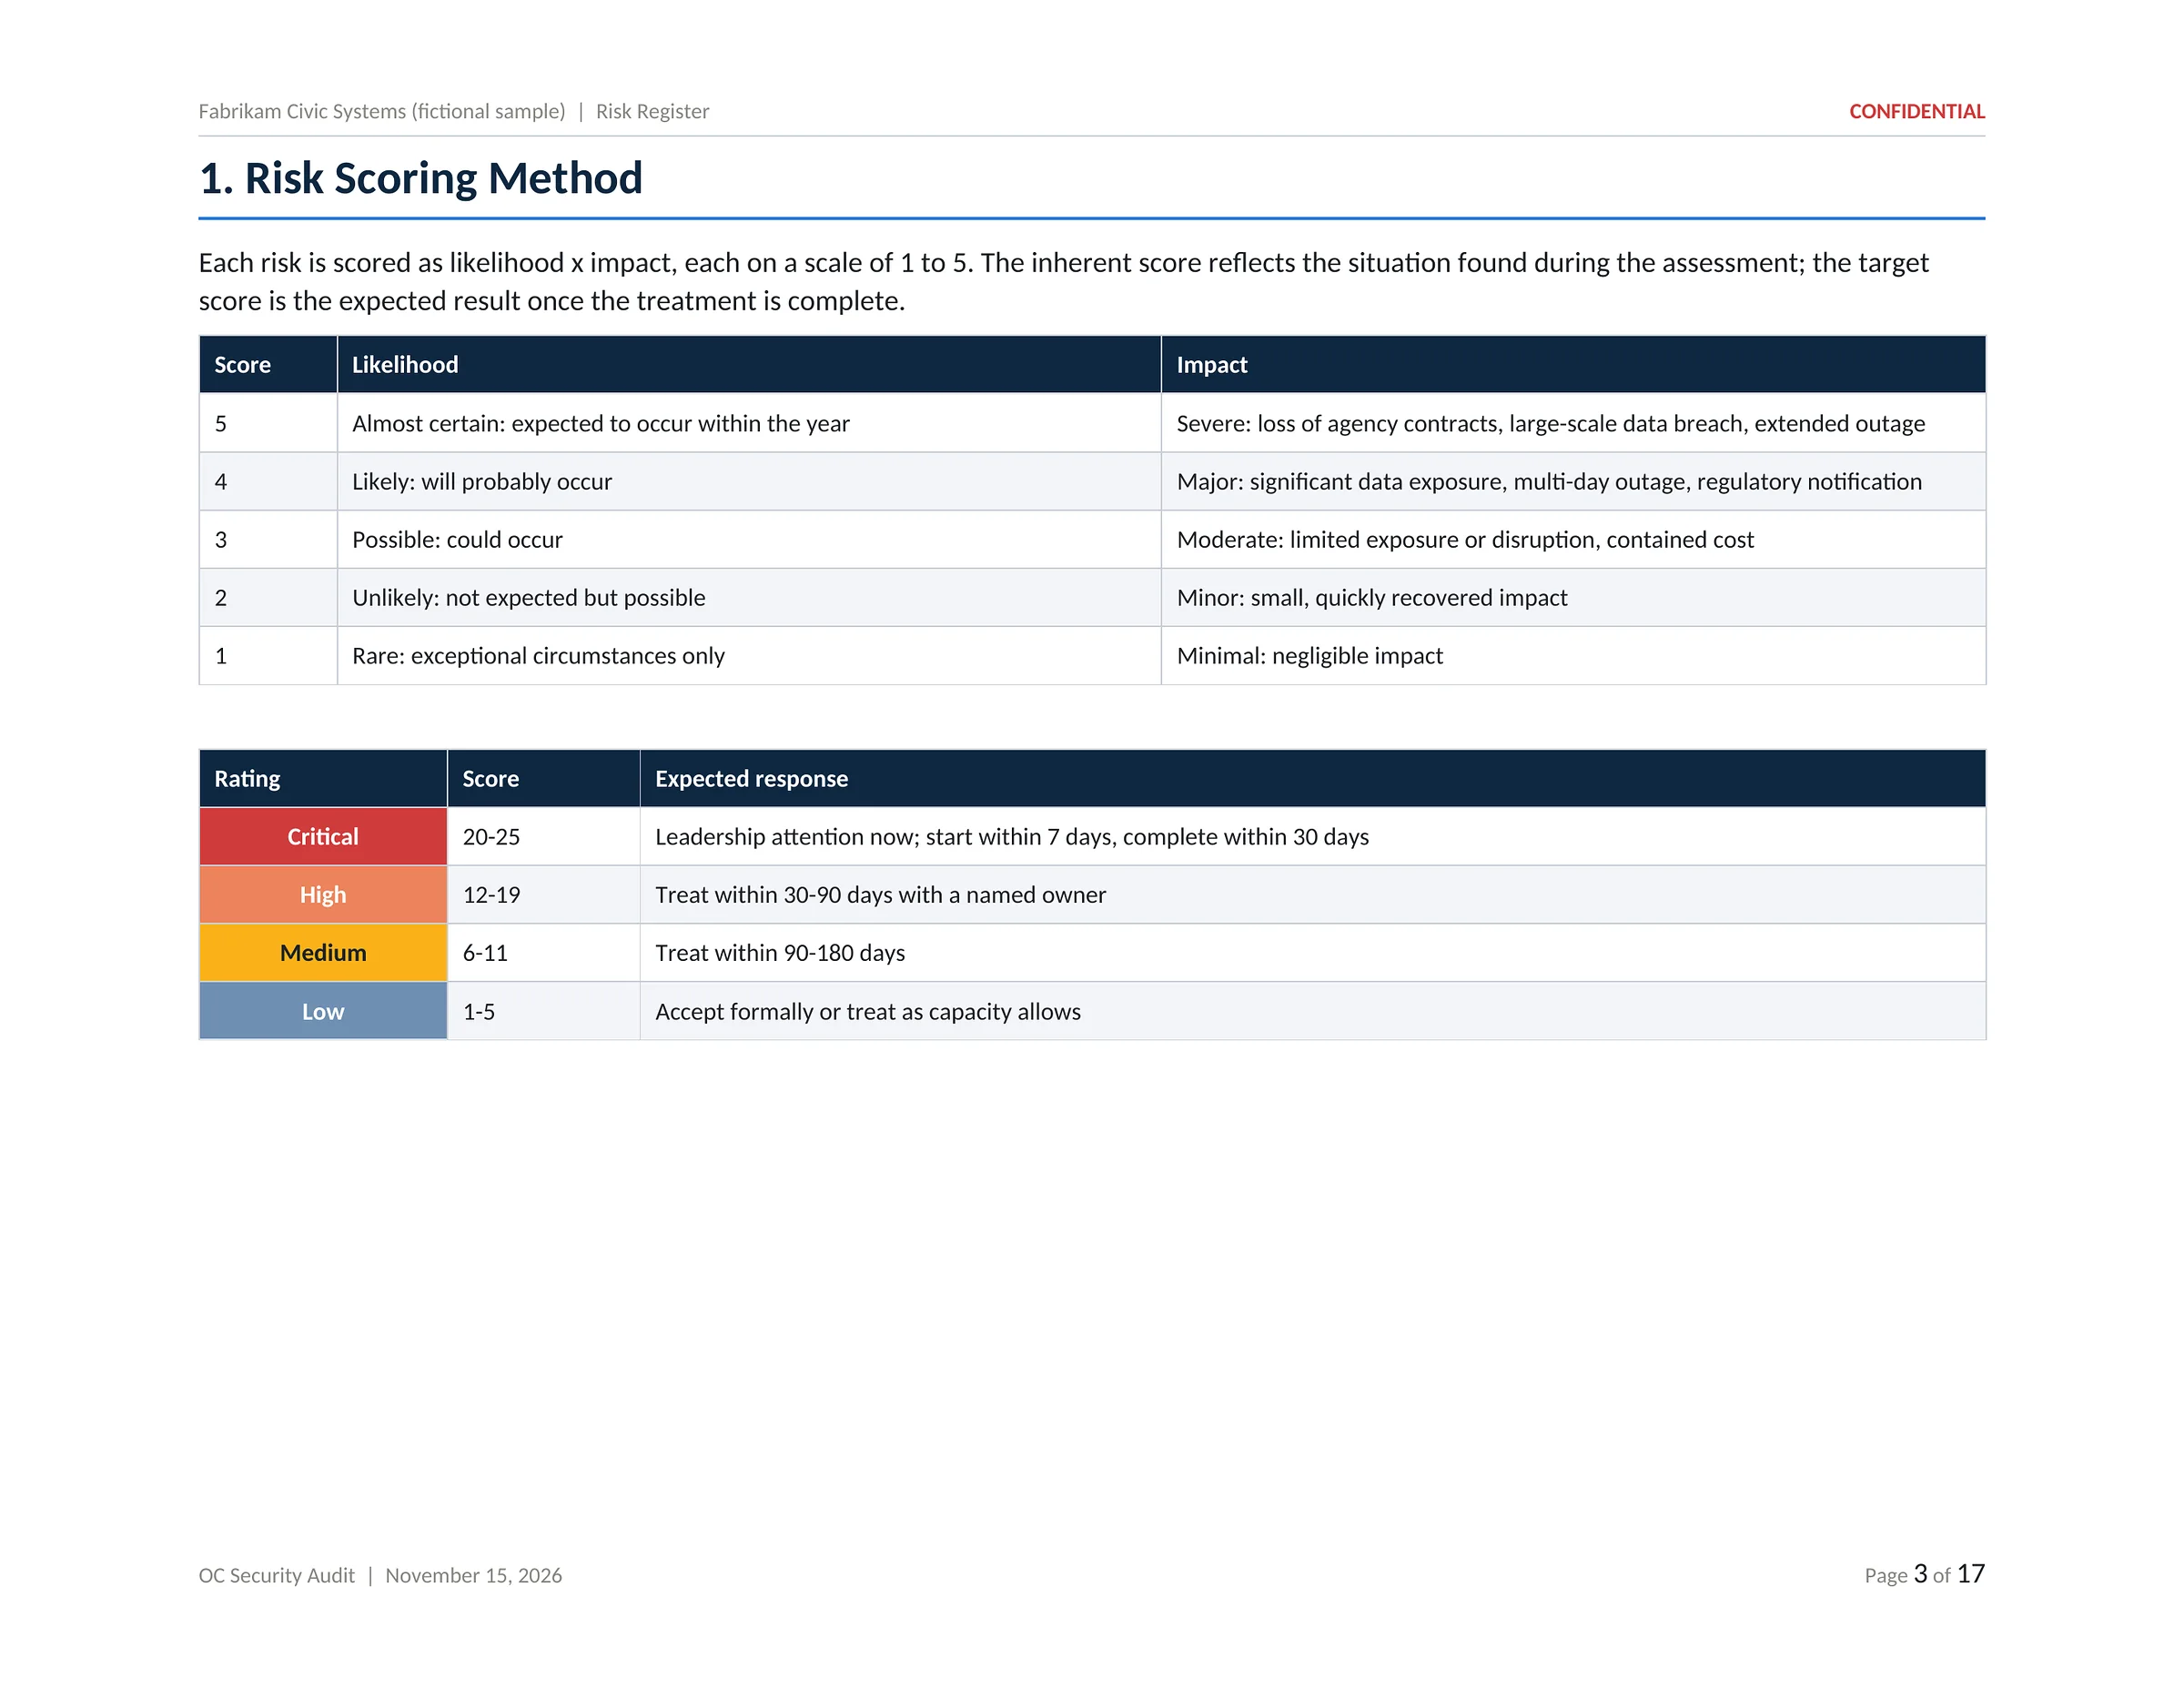
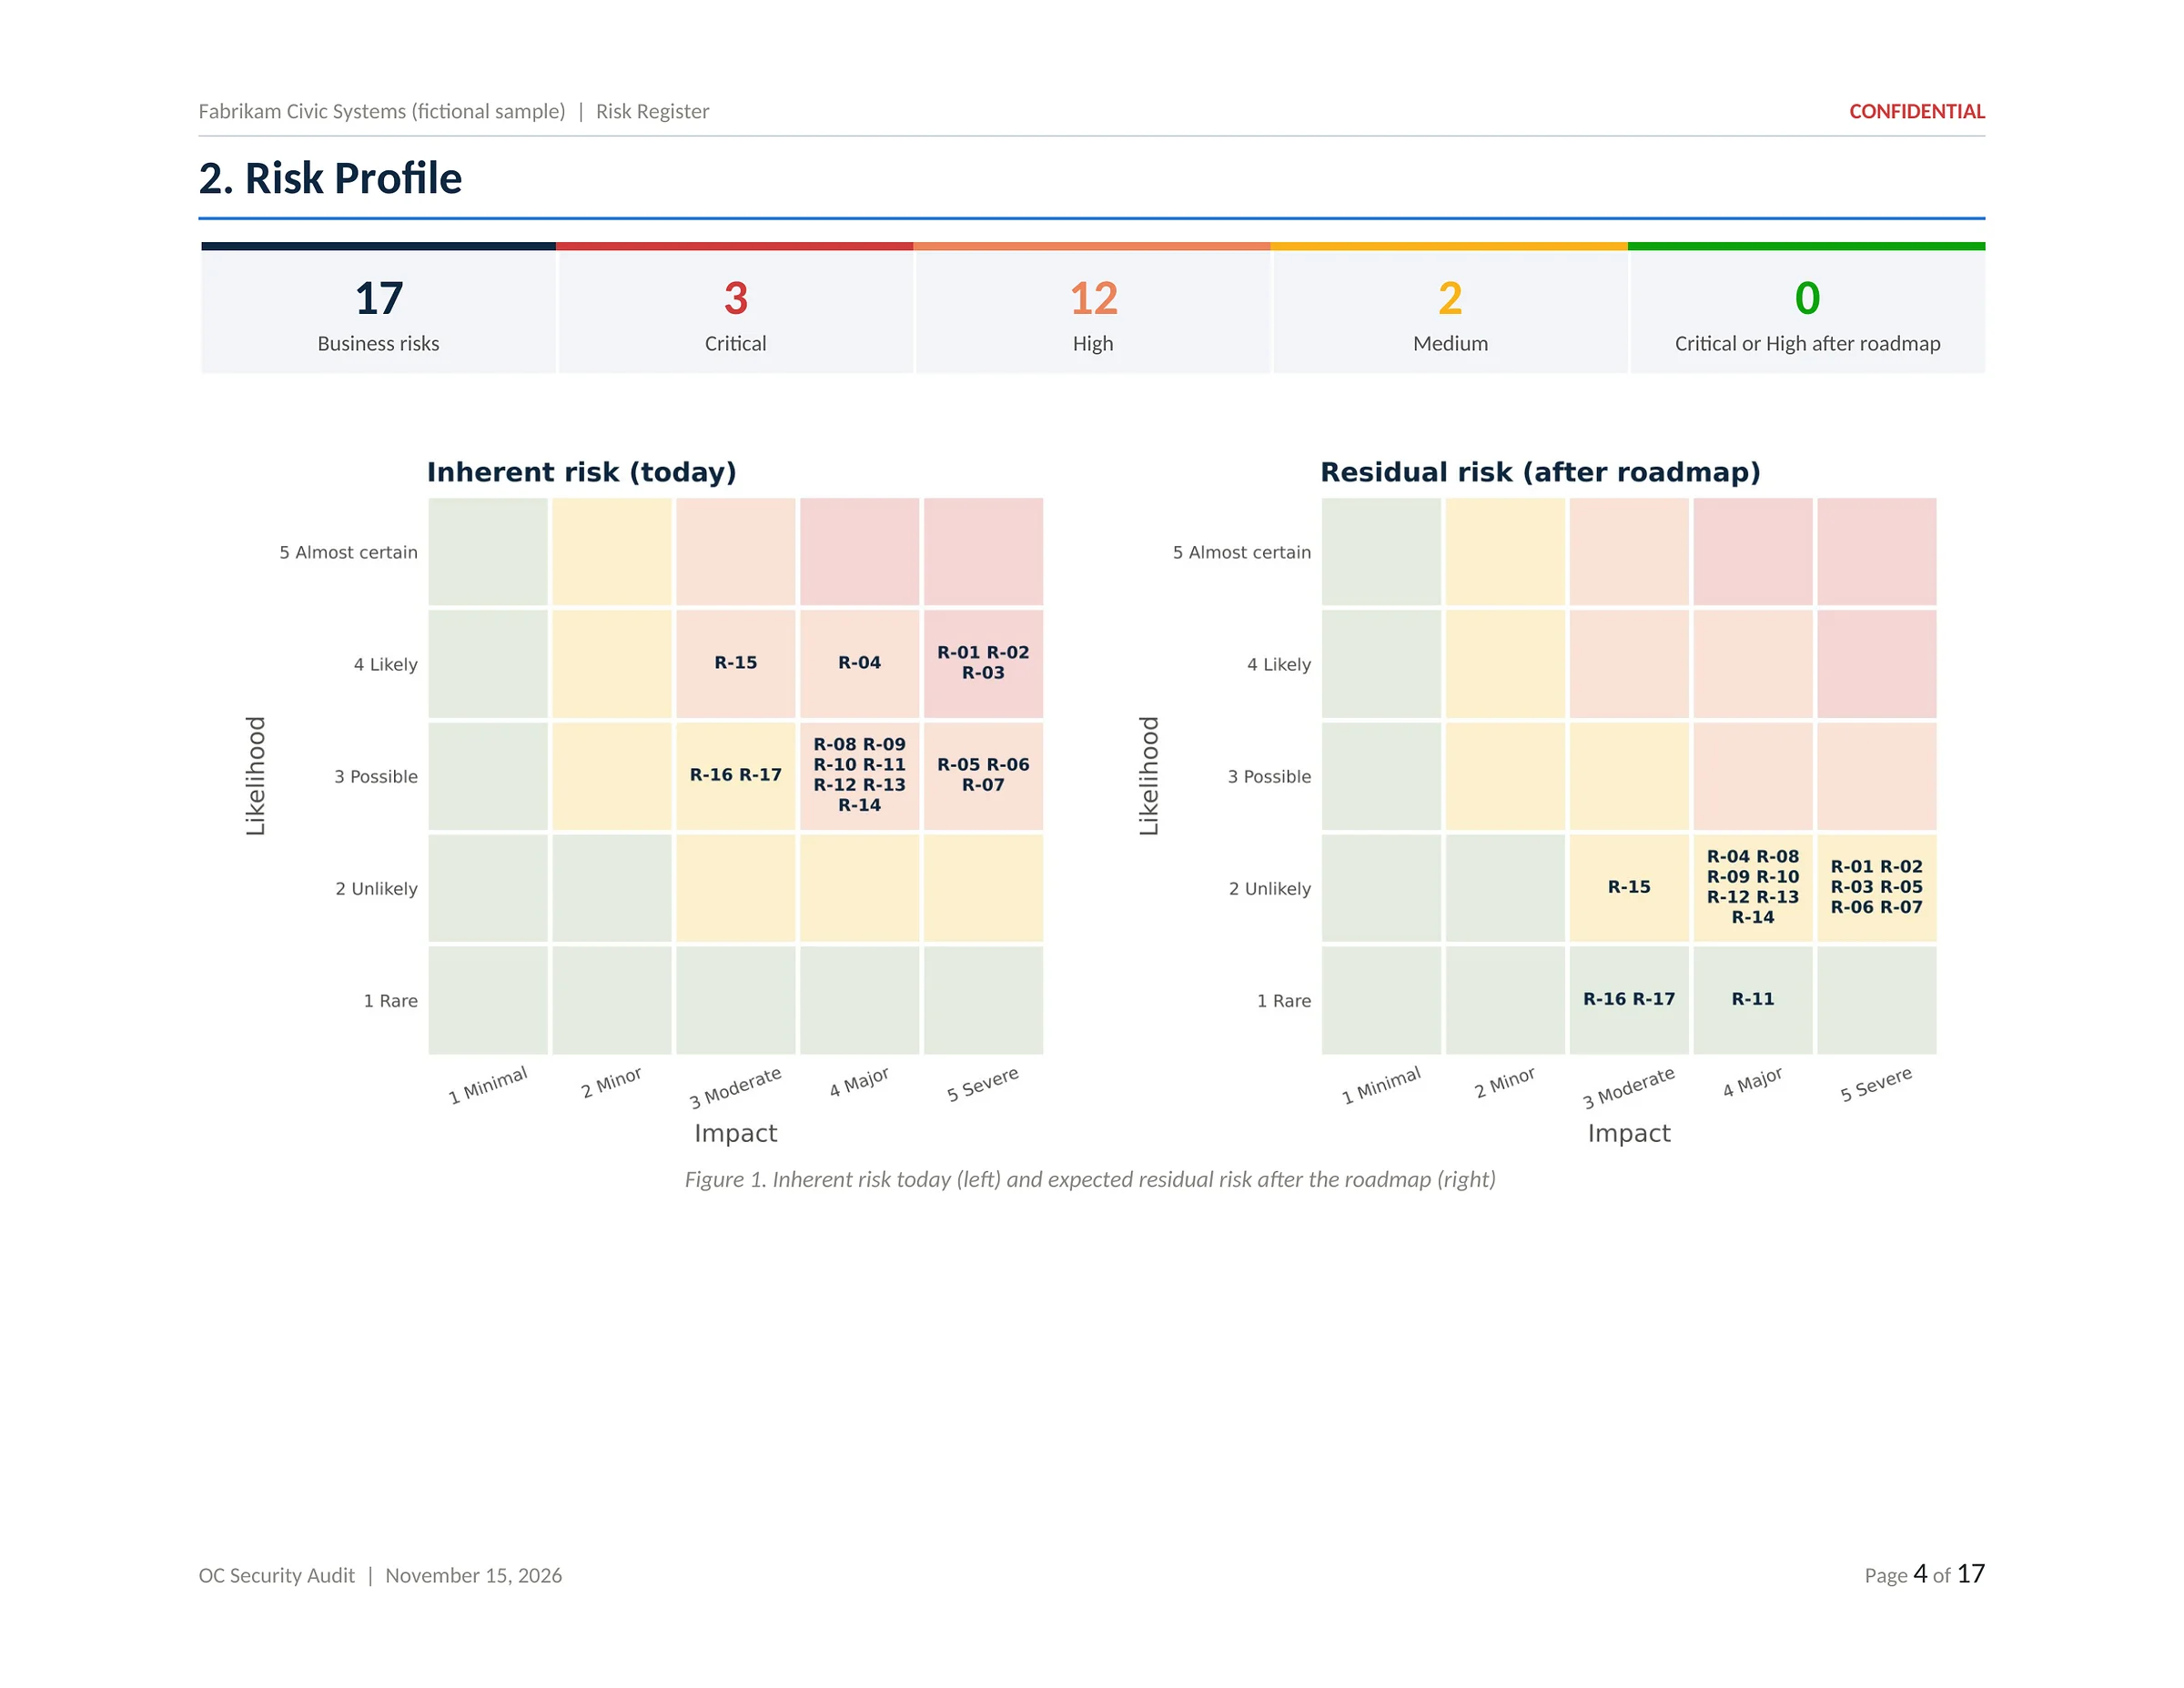
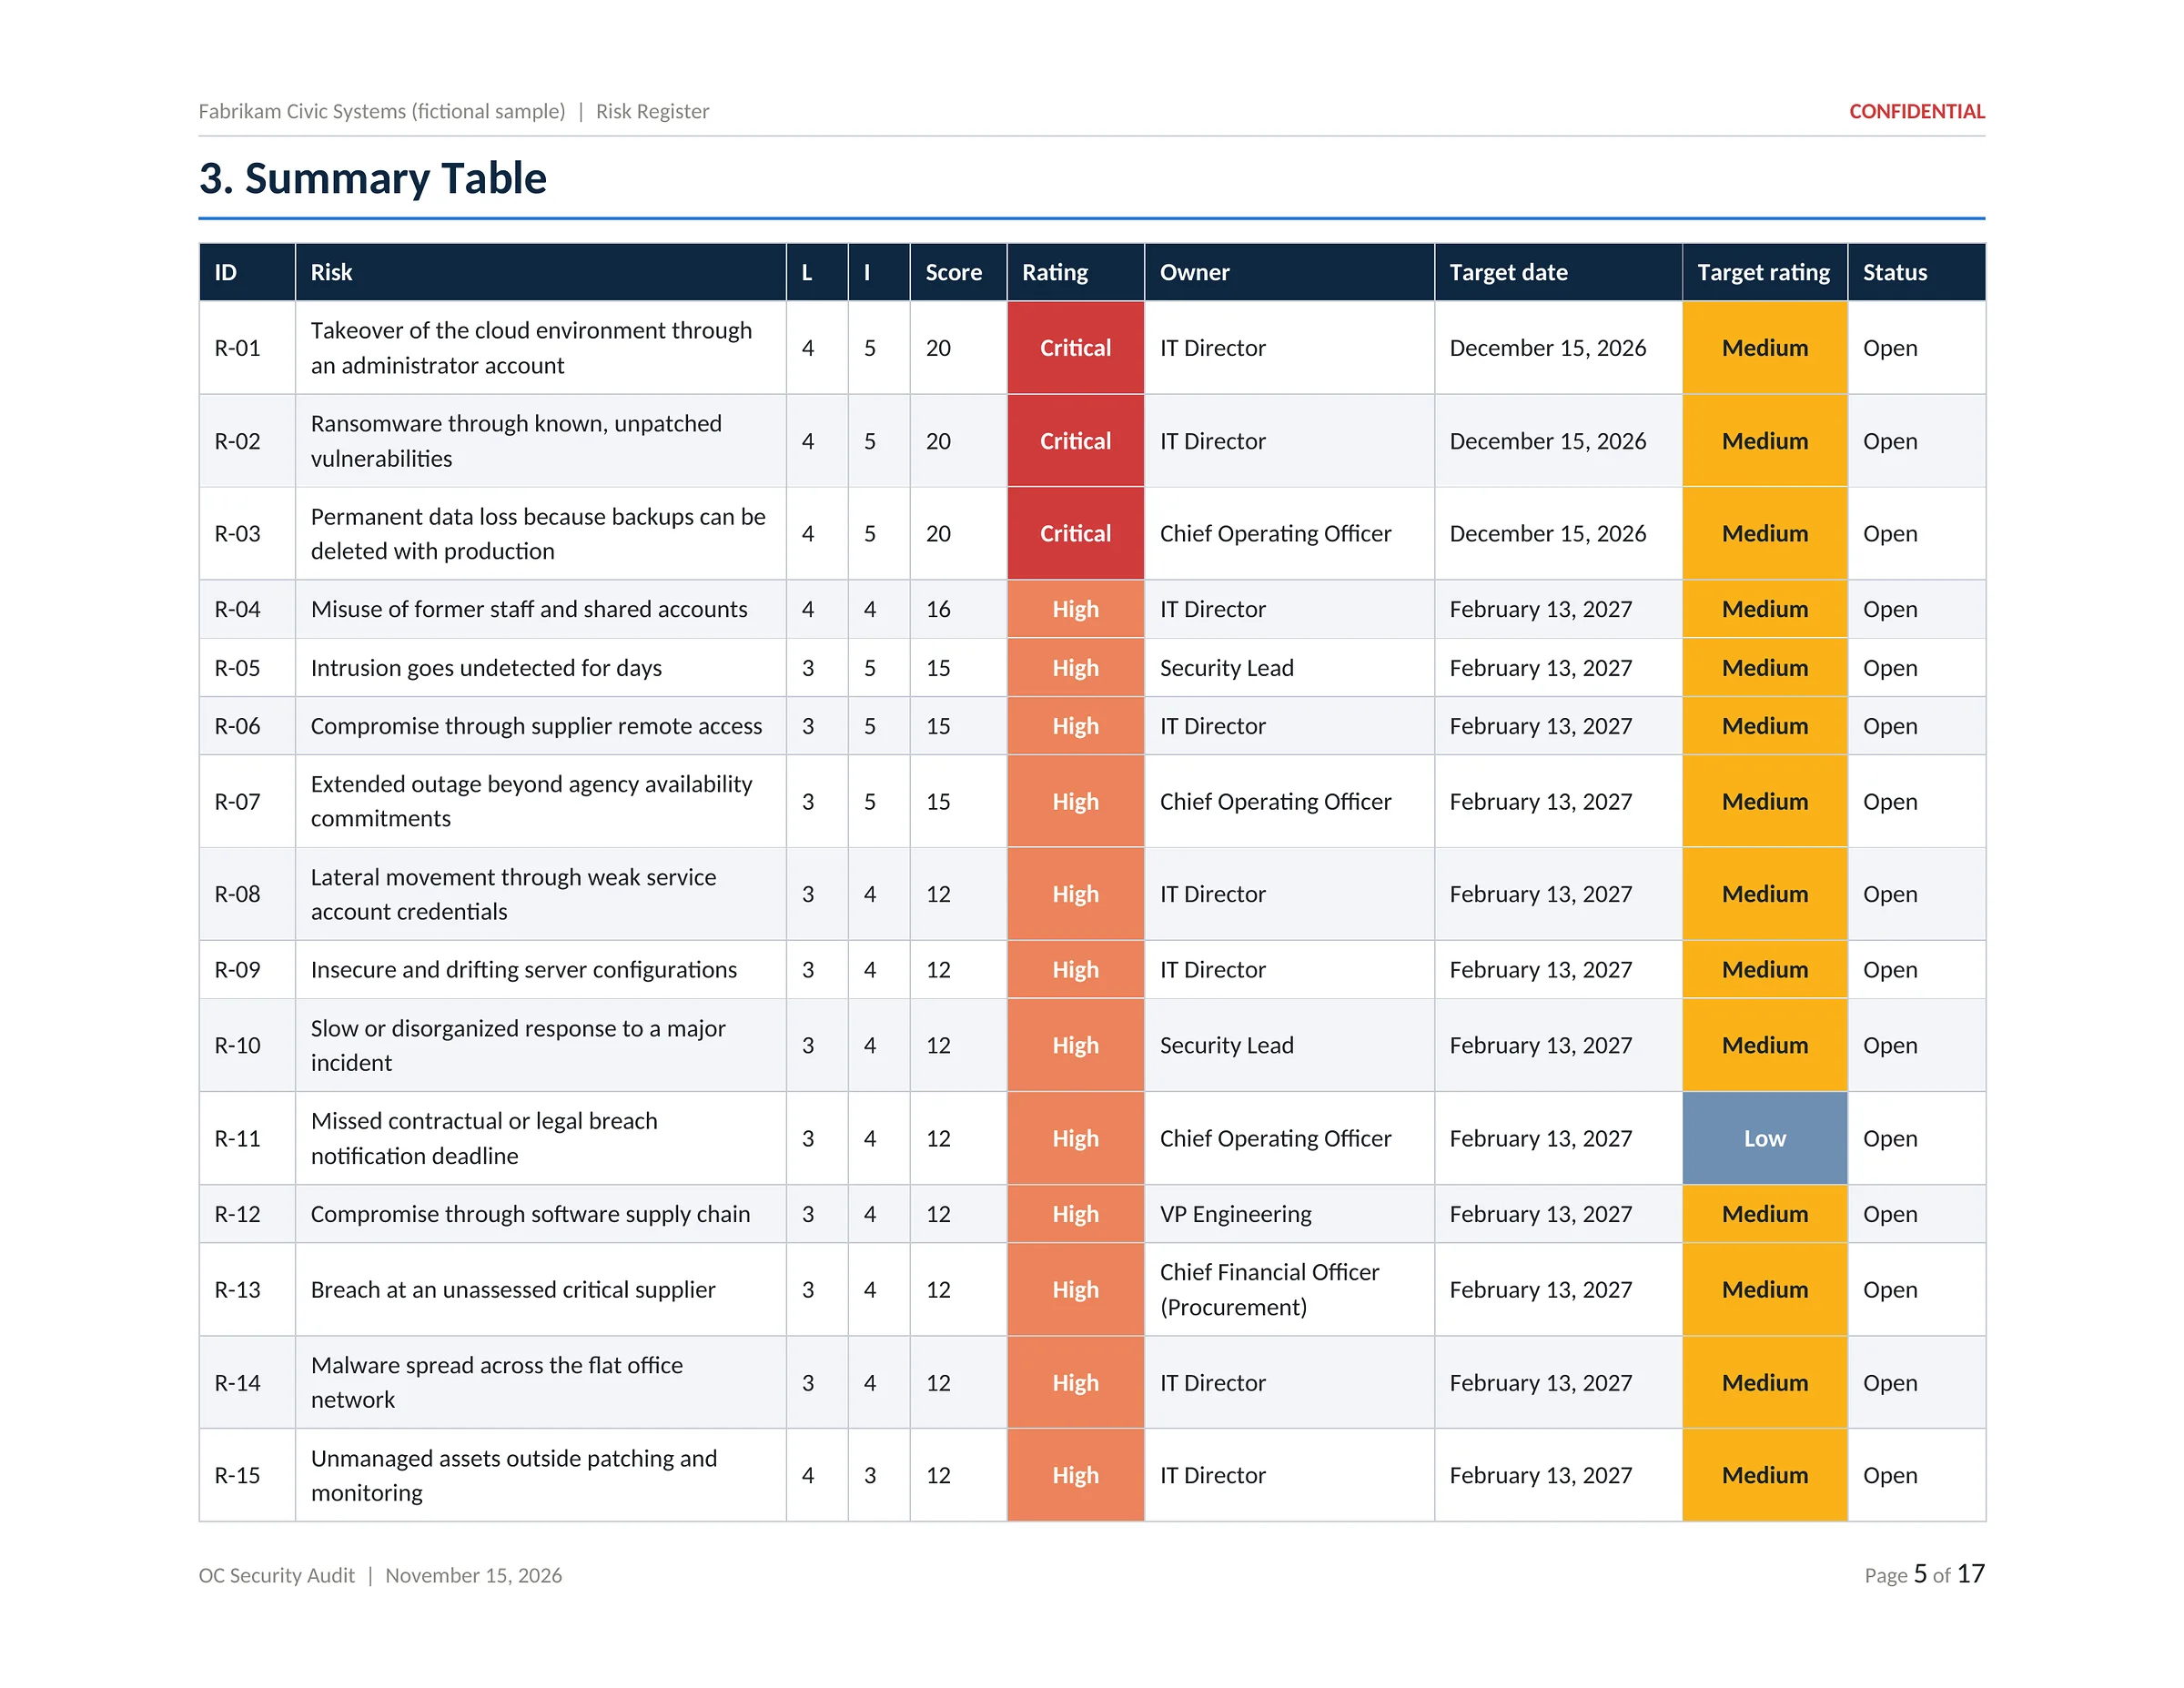
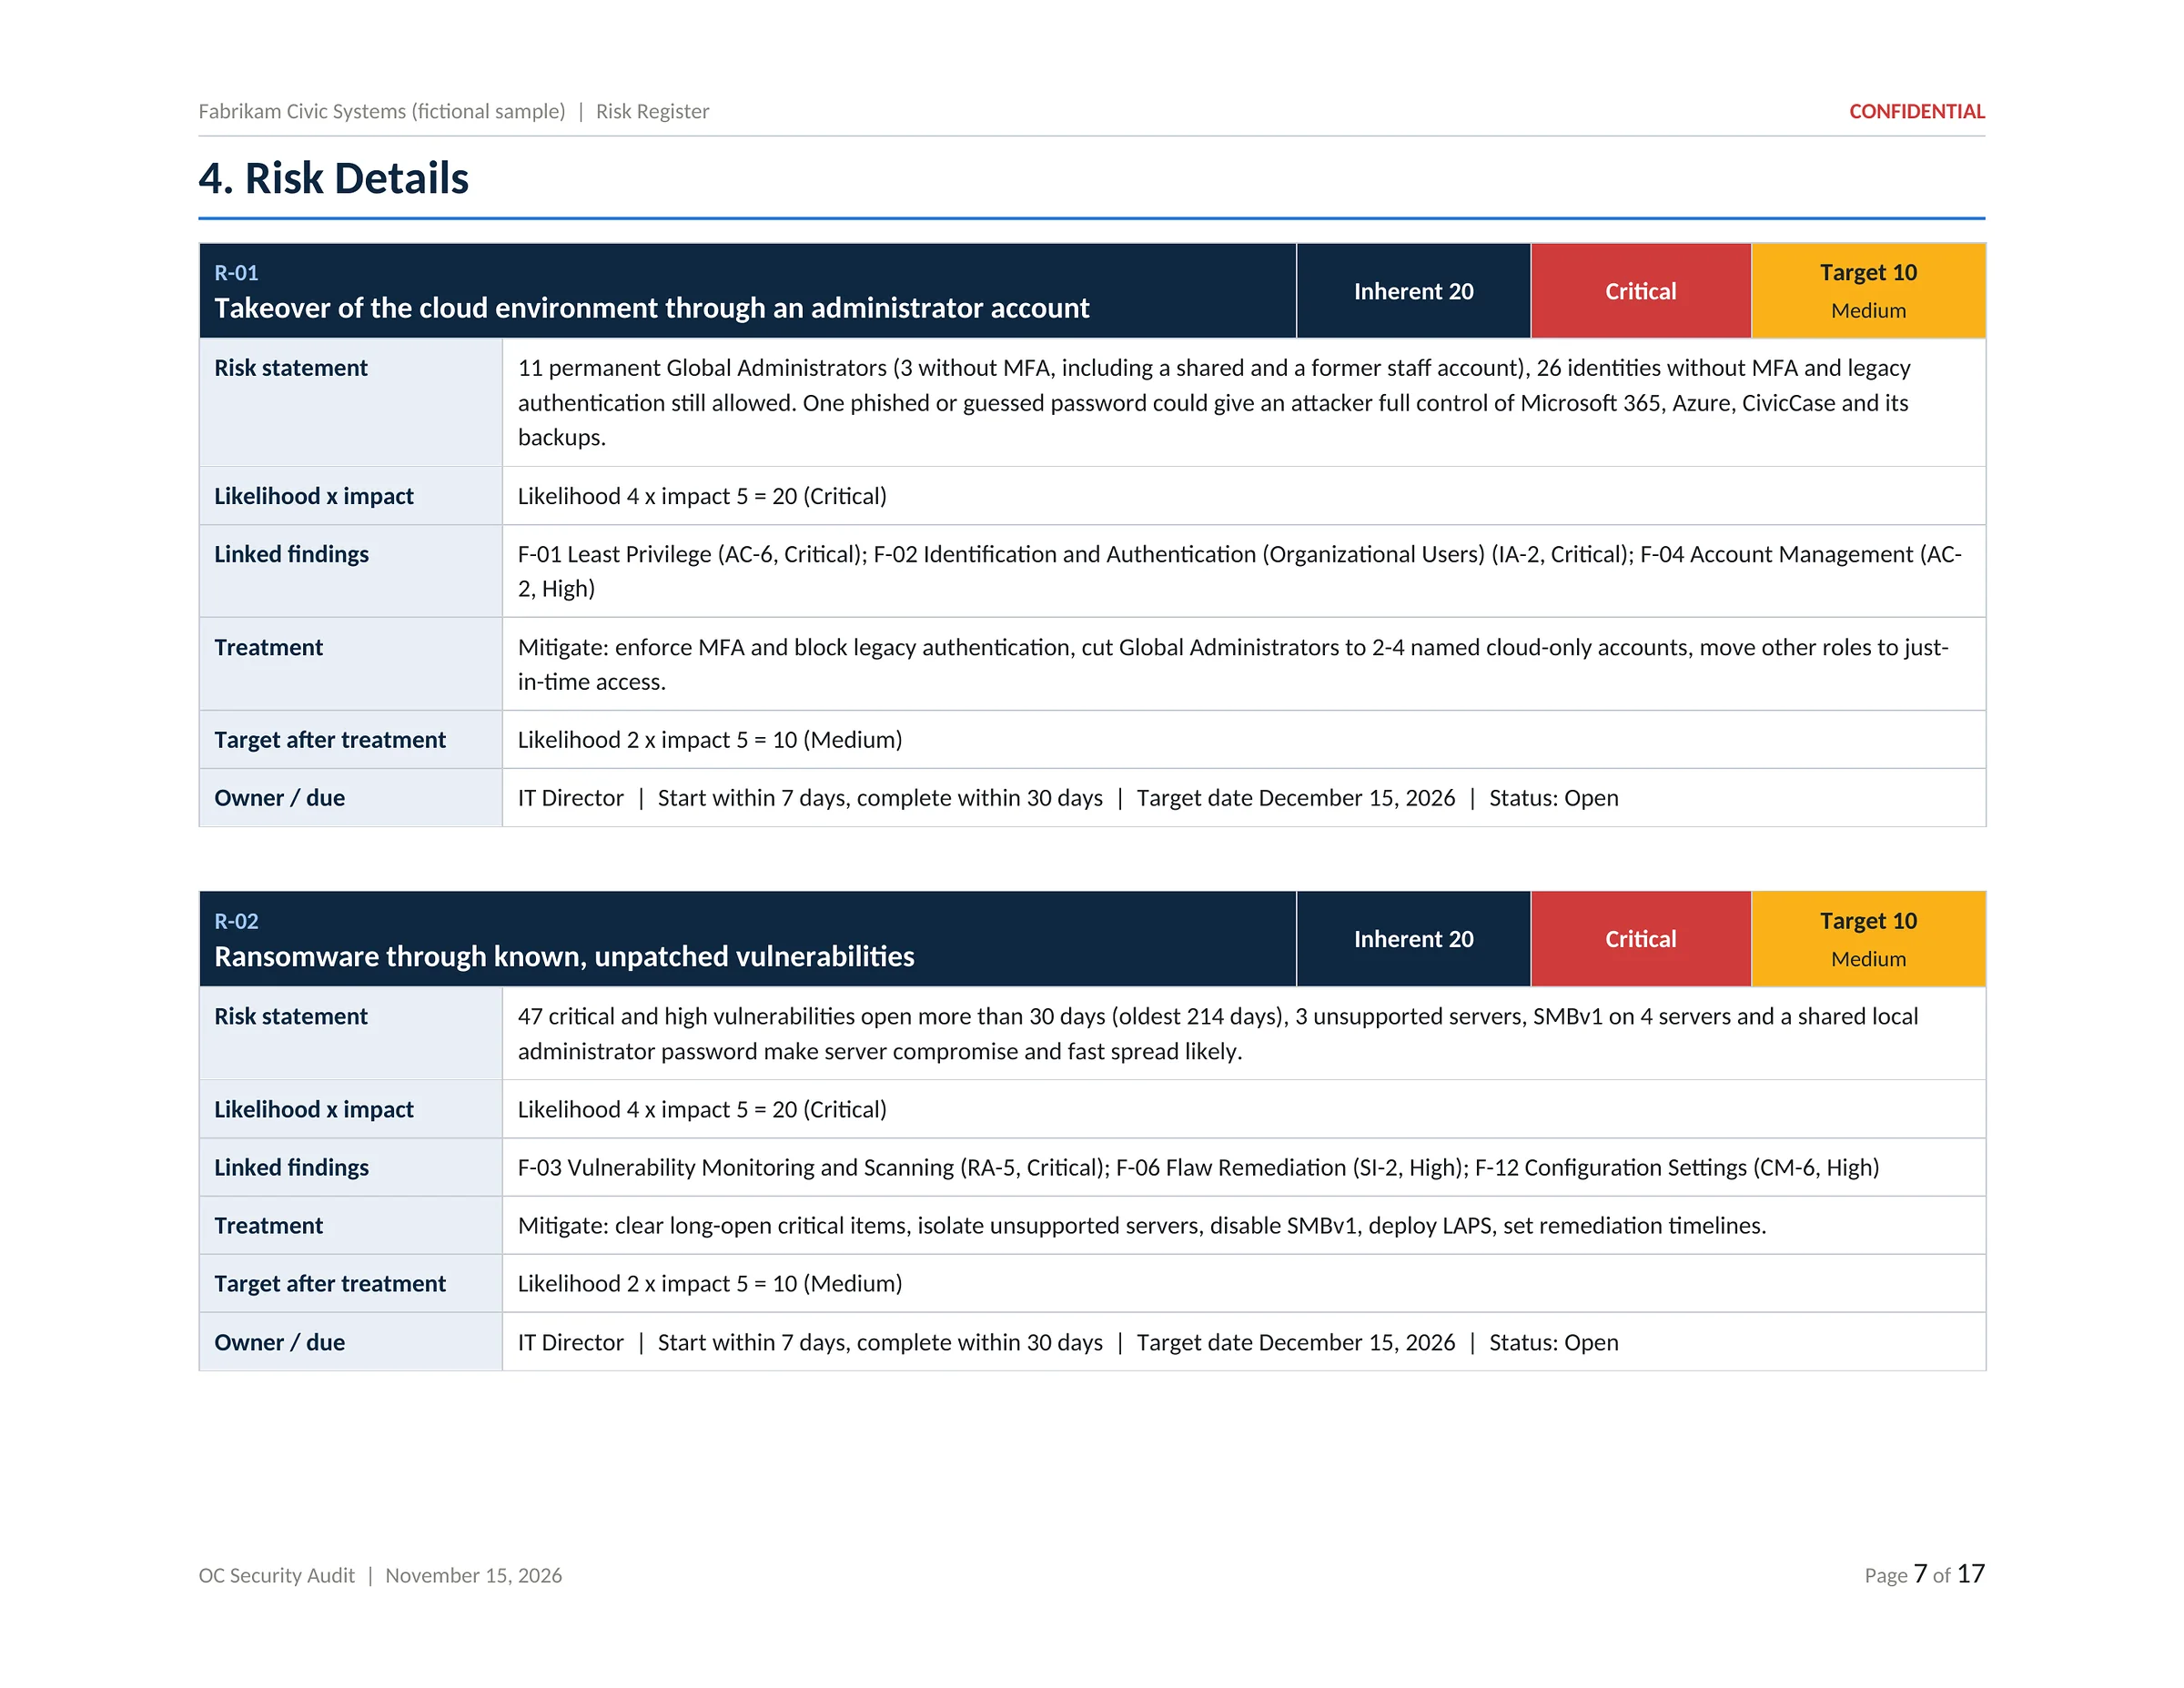
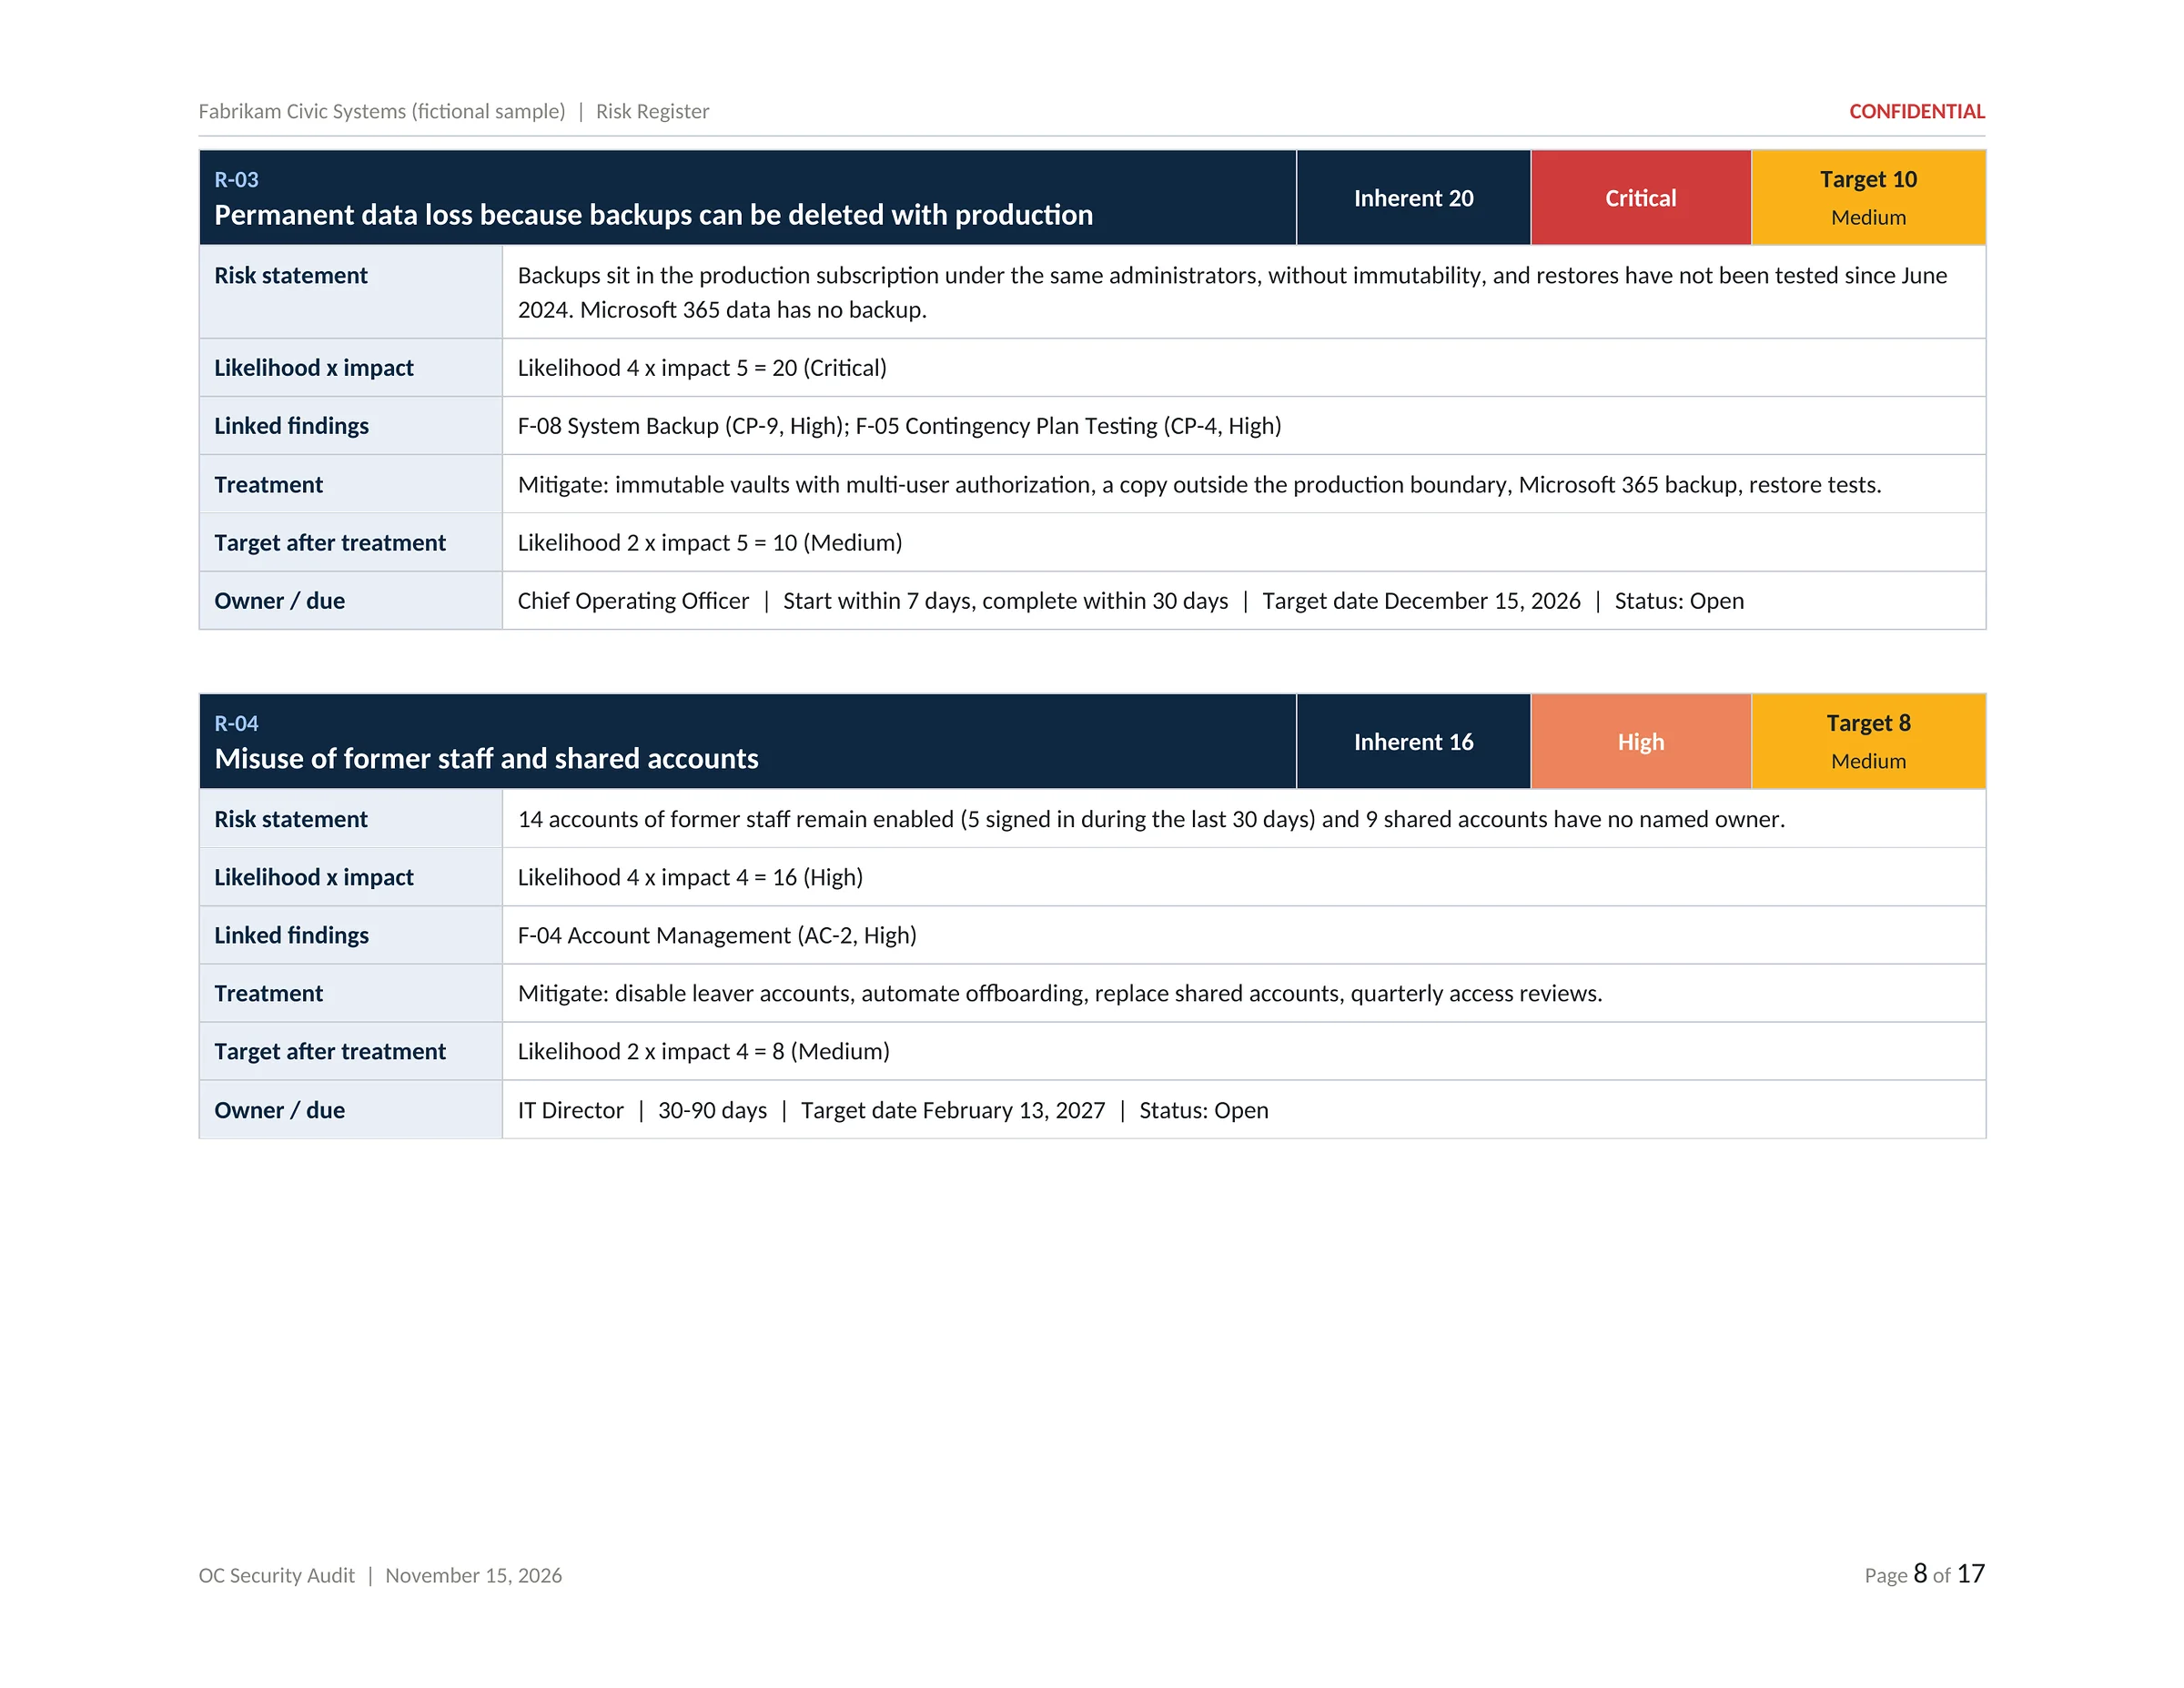
The register that turns 28 findings into 17 business risks. Each risk is scored for likelihood and impact, rated, given an owner, a treatment and a target date, and shown on heat maps today and after the roadmap. A traceability table proves every finding is covered by at least one risk.
Leadership and risk owners for decisions; customers who ask how you manage risk; your plan of action and milestones.
What is included
- Scoring method and rating bands
- Risk profile and counts
- Heat maps today and after remediation
- Summary table with owners and dates
- A detail card for every risk
- Treatment and target after treatment
- Finding-to-risk traceability
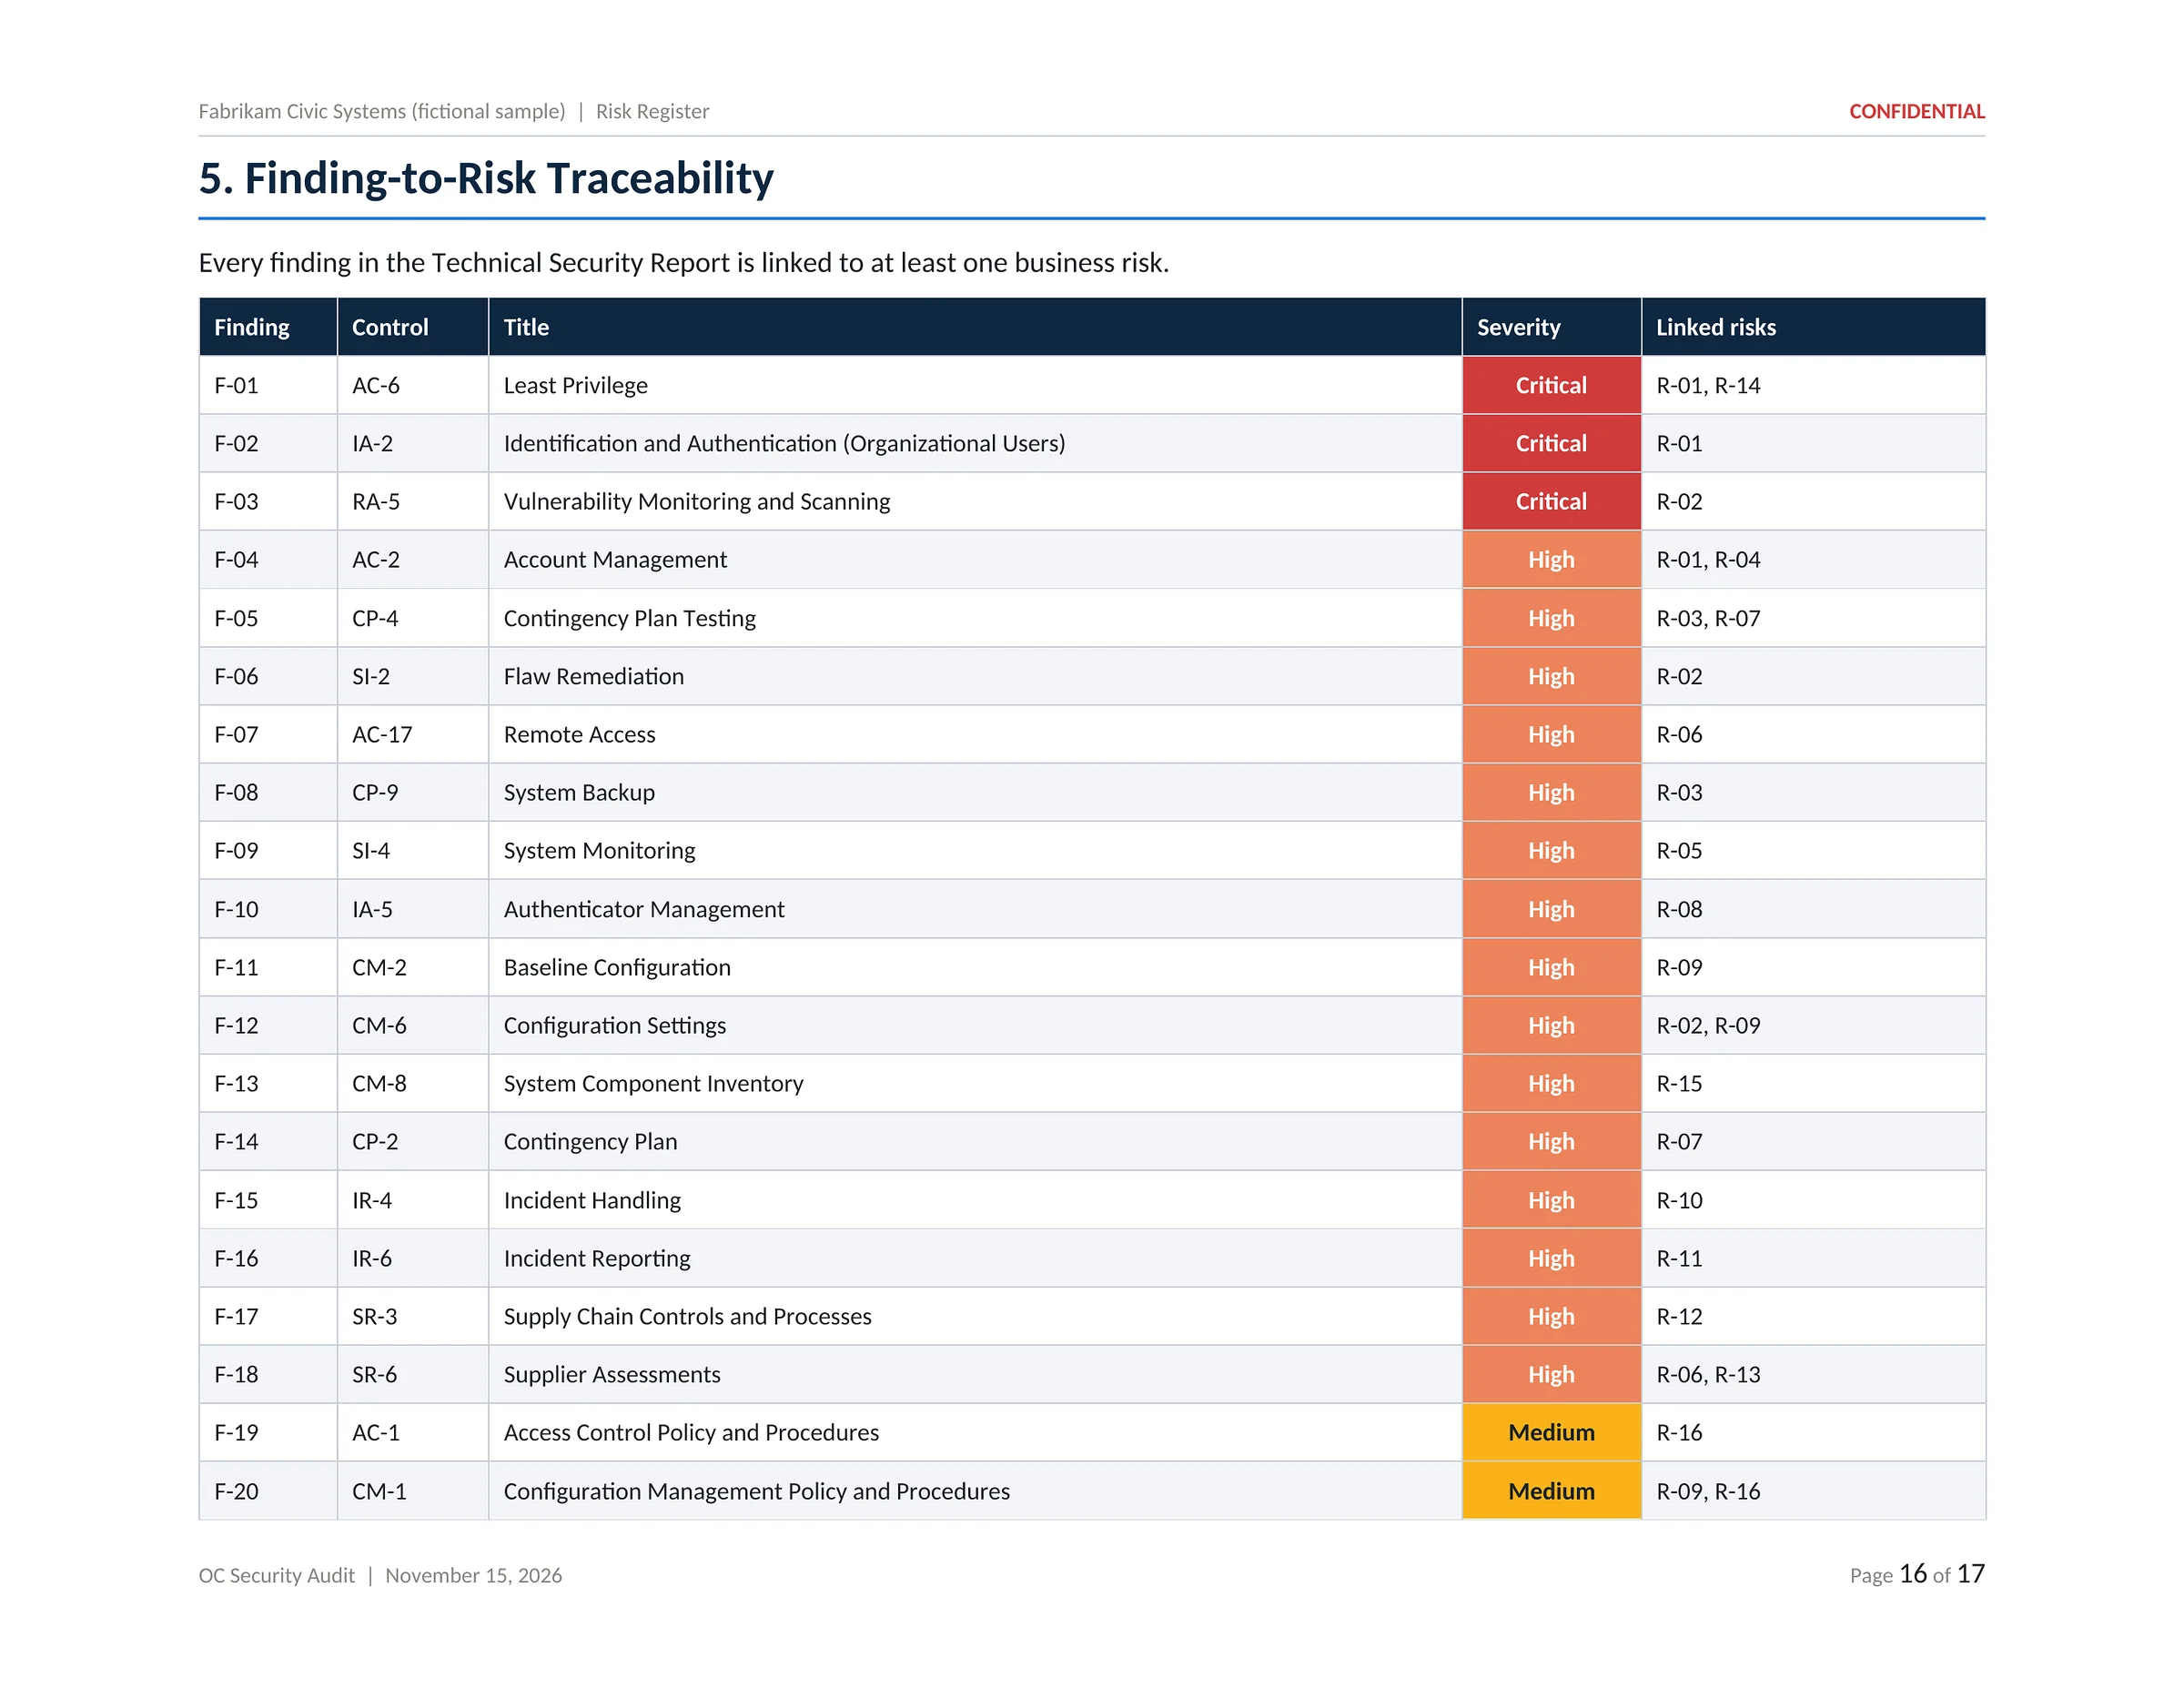
Click the page in the centre to open it full size, then zoom in to read every line.
PDF and Word · 13 pages
Next Steps and Security Roadmap
The 180-day plan. It sets today's measures against 30-day and 180-day targets, lays out 31 actions in four phases on a timeline, groups them into eight security projects with effort and success measures, and shows the expected reduction in risk and the operating rhythm that keeps the plan moving.
IT leadership and project owners who run the work; leadership who approve budget and owners.
What is included
- Where you are and where you should be
- 180-day timeline in four phases
- 31 actions with their risks
- Eight prioritized security projects
- Effort, duration and success measures
- Expected outcome and residual risk
- Future goals for 6 to 18 months
- Governance and operating rhythm
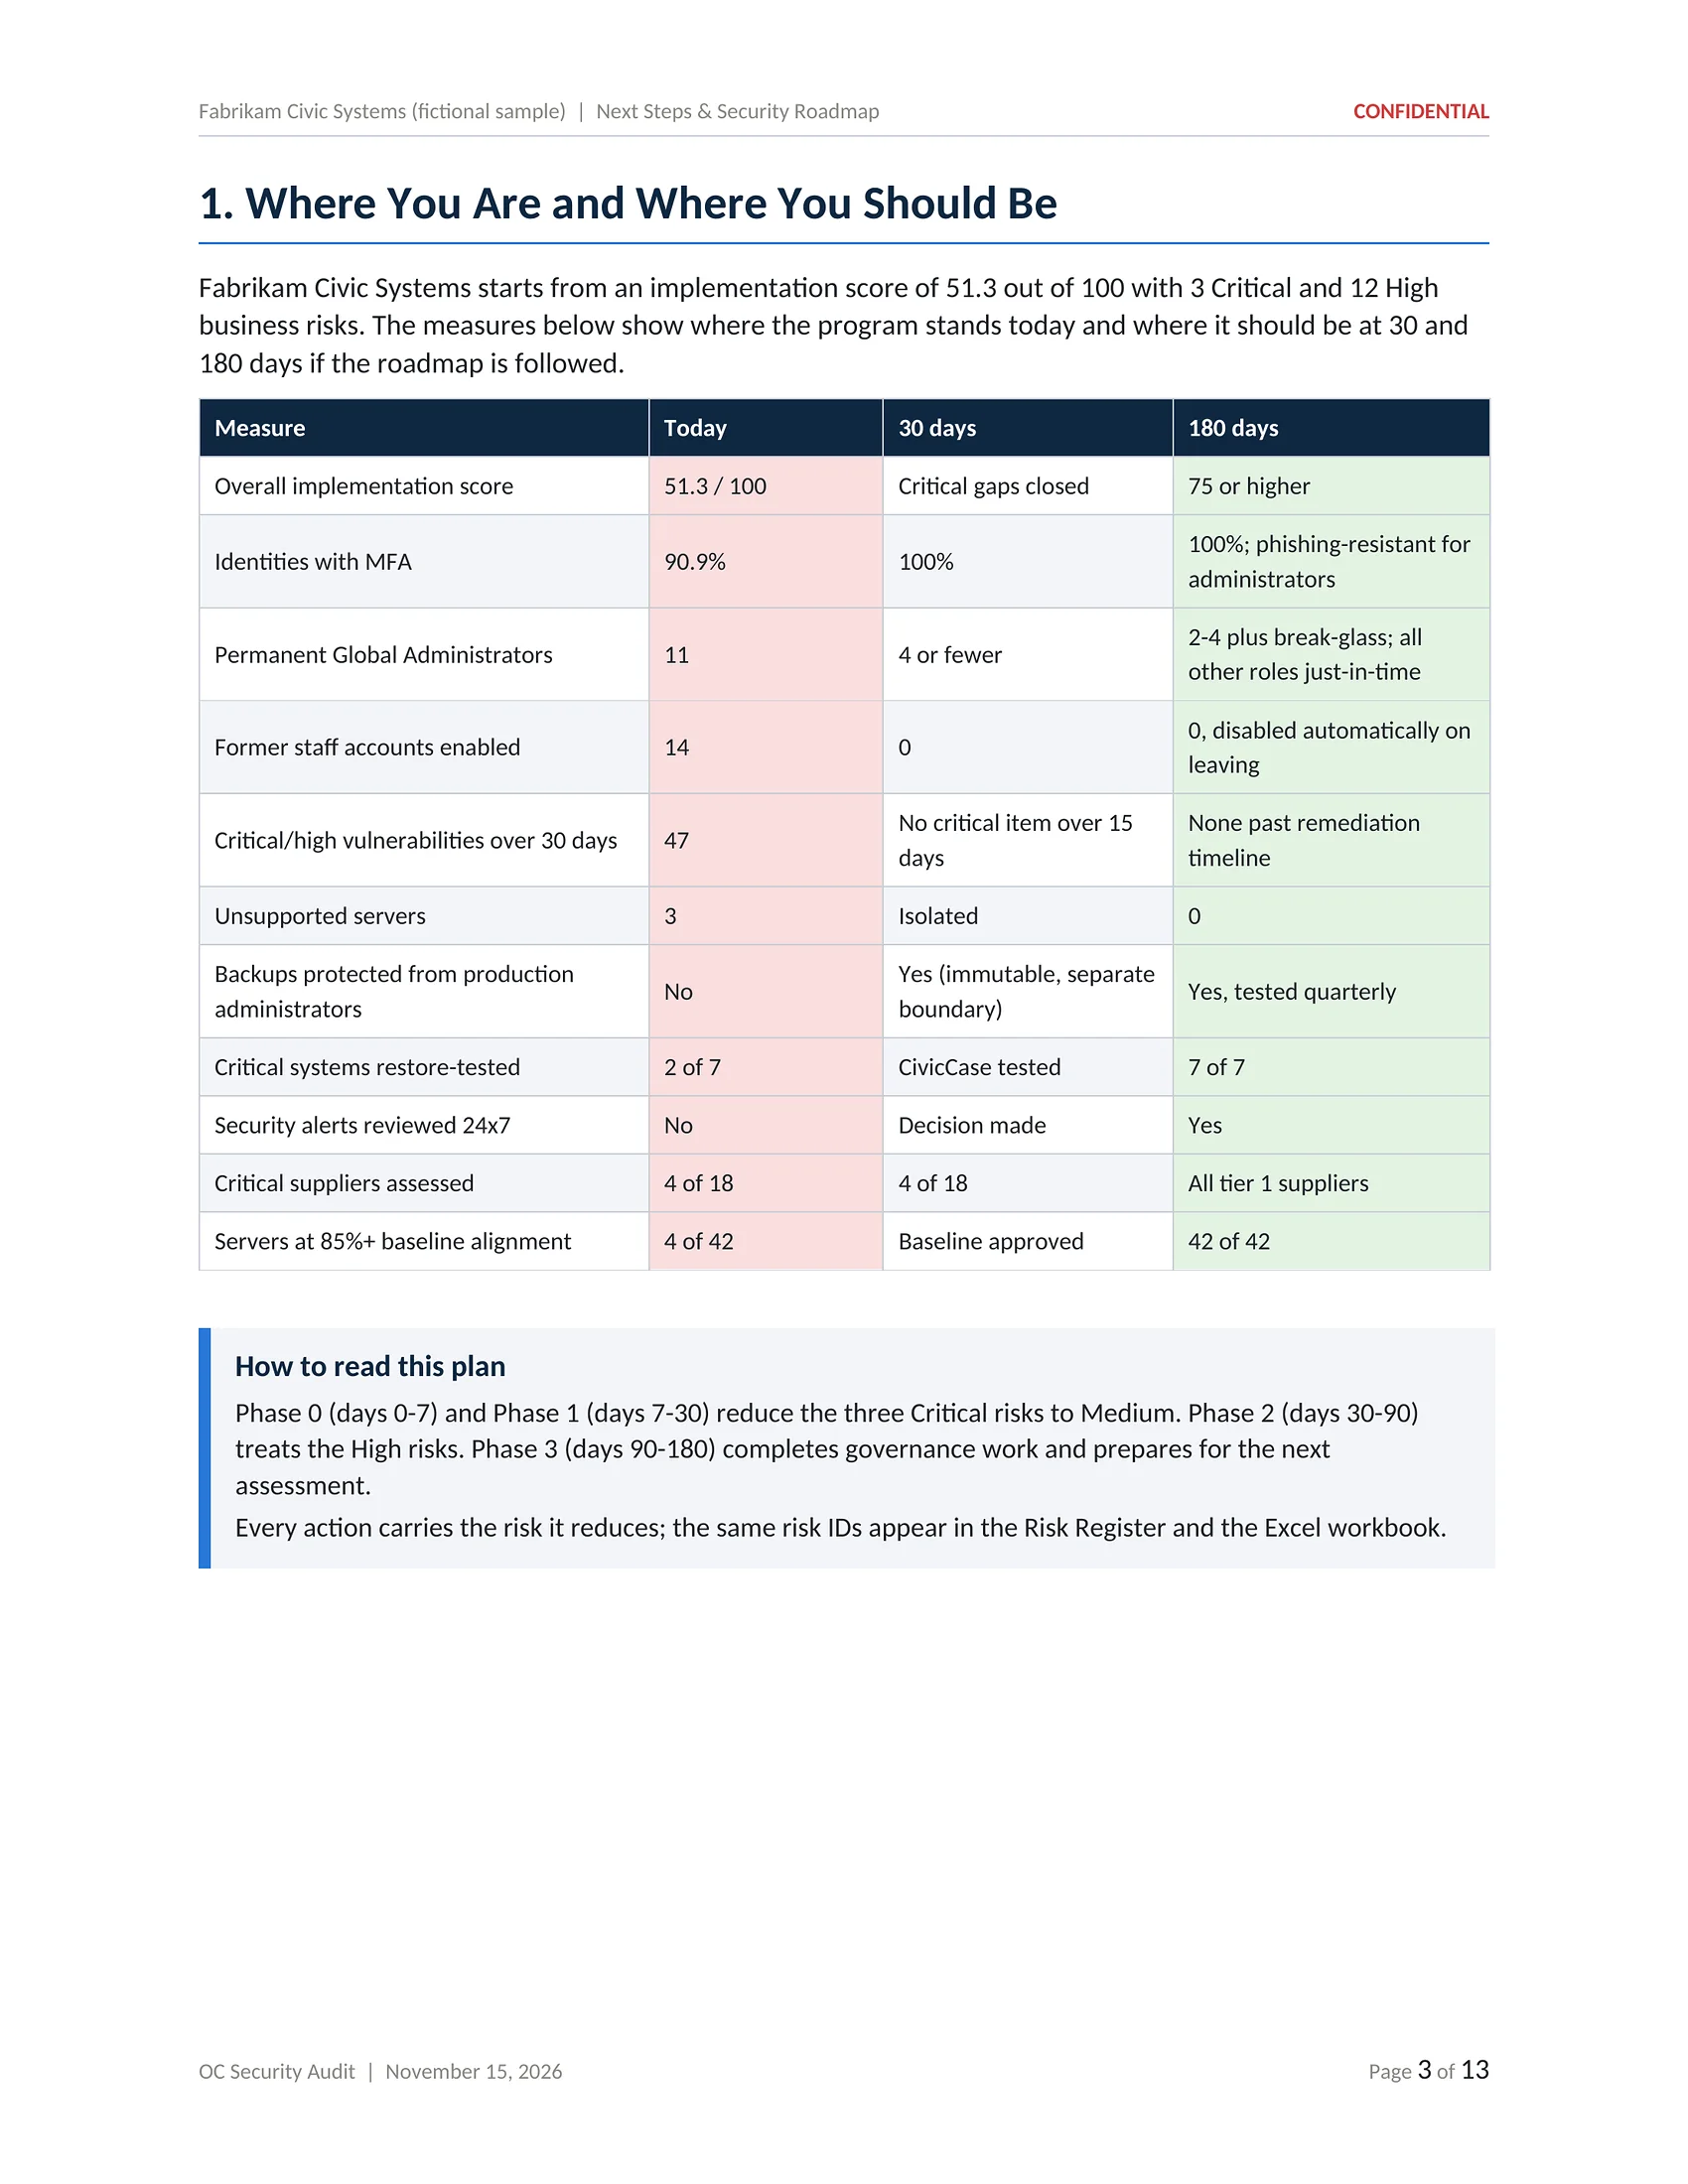
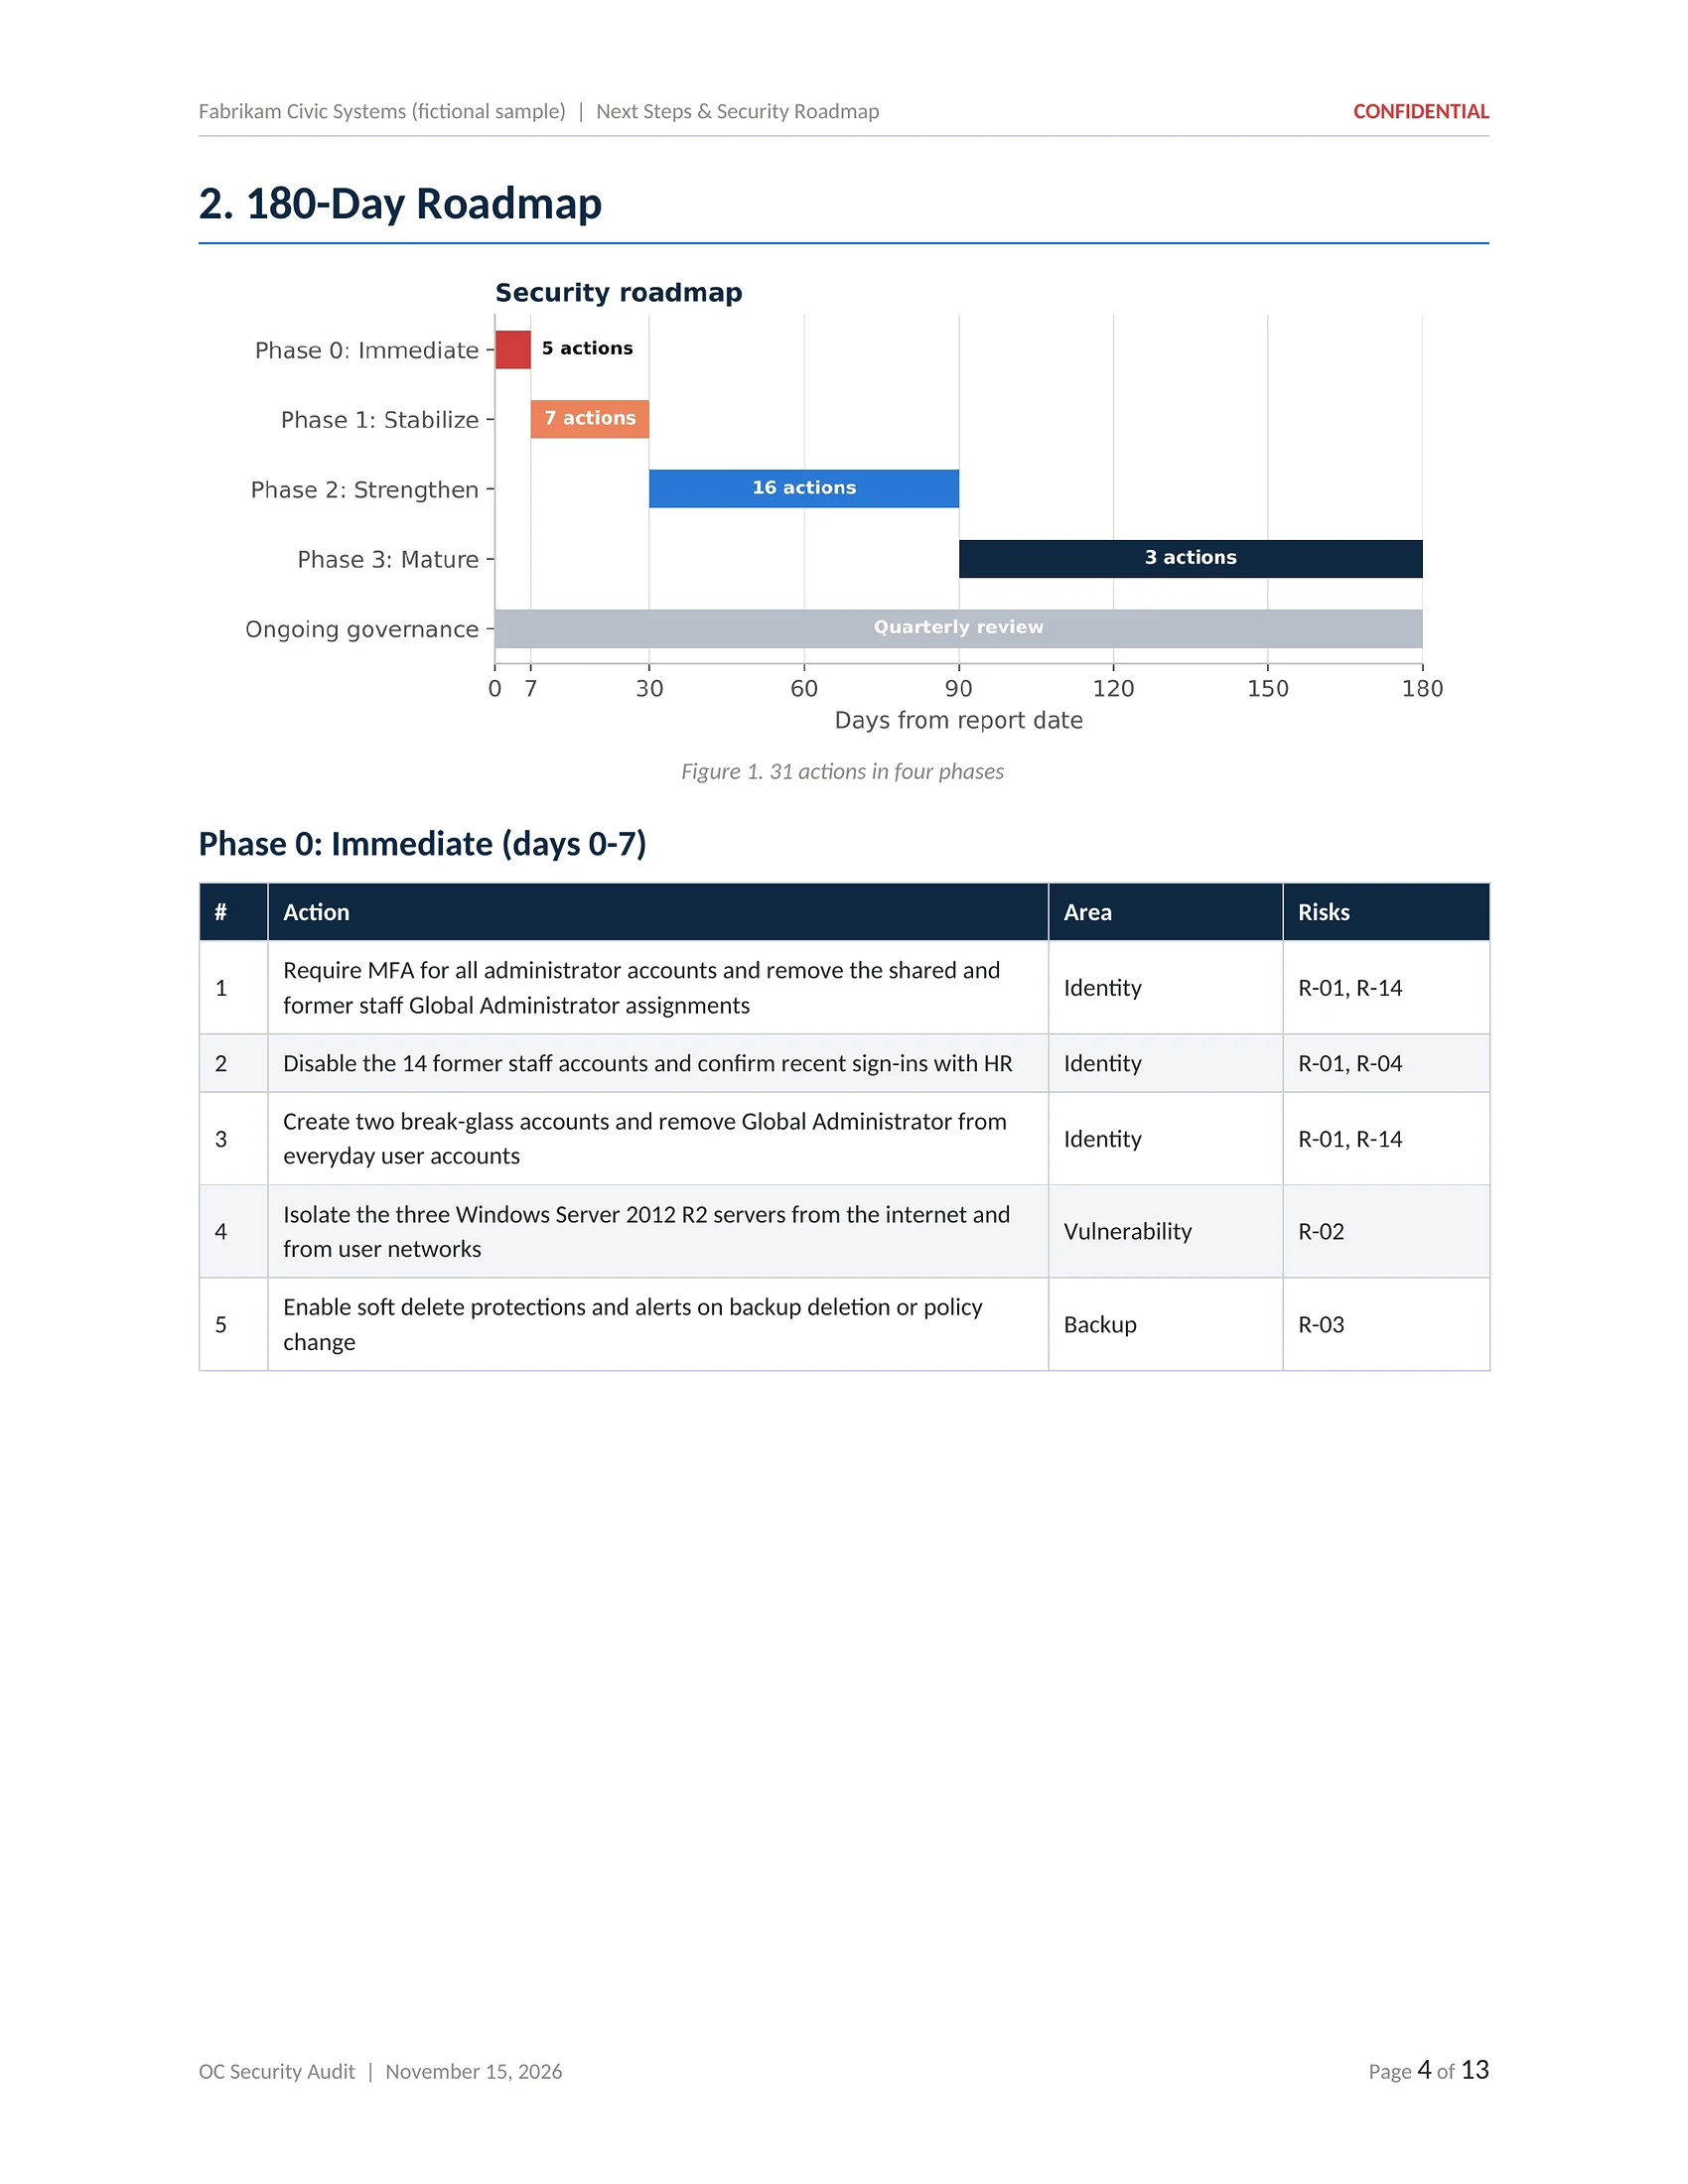
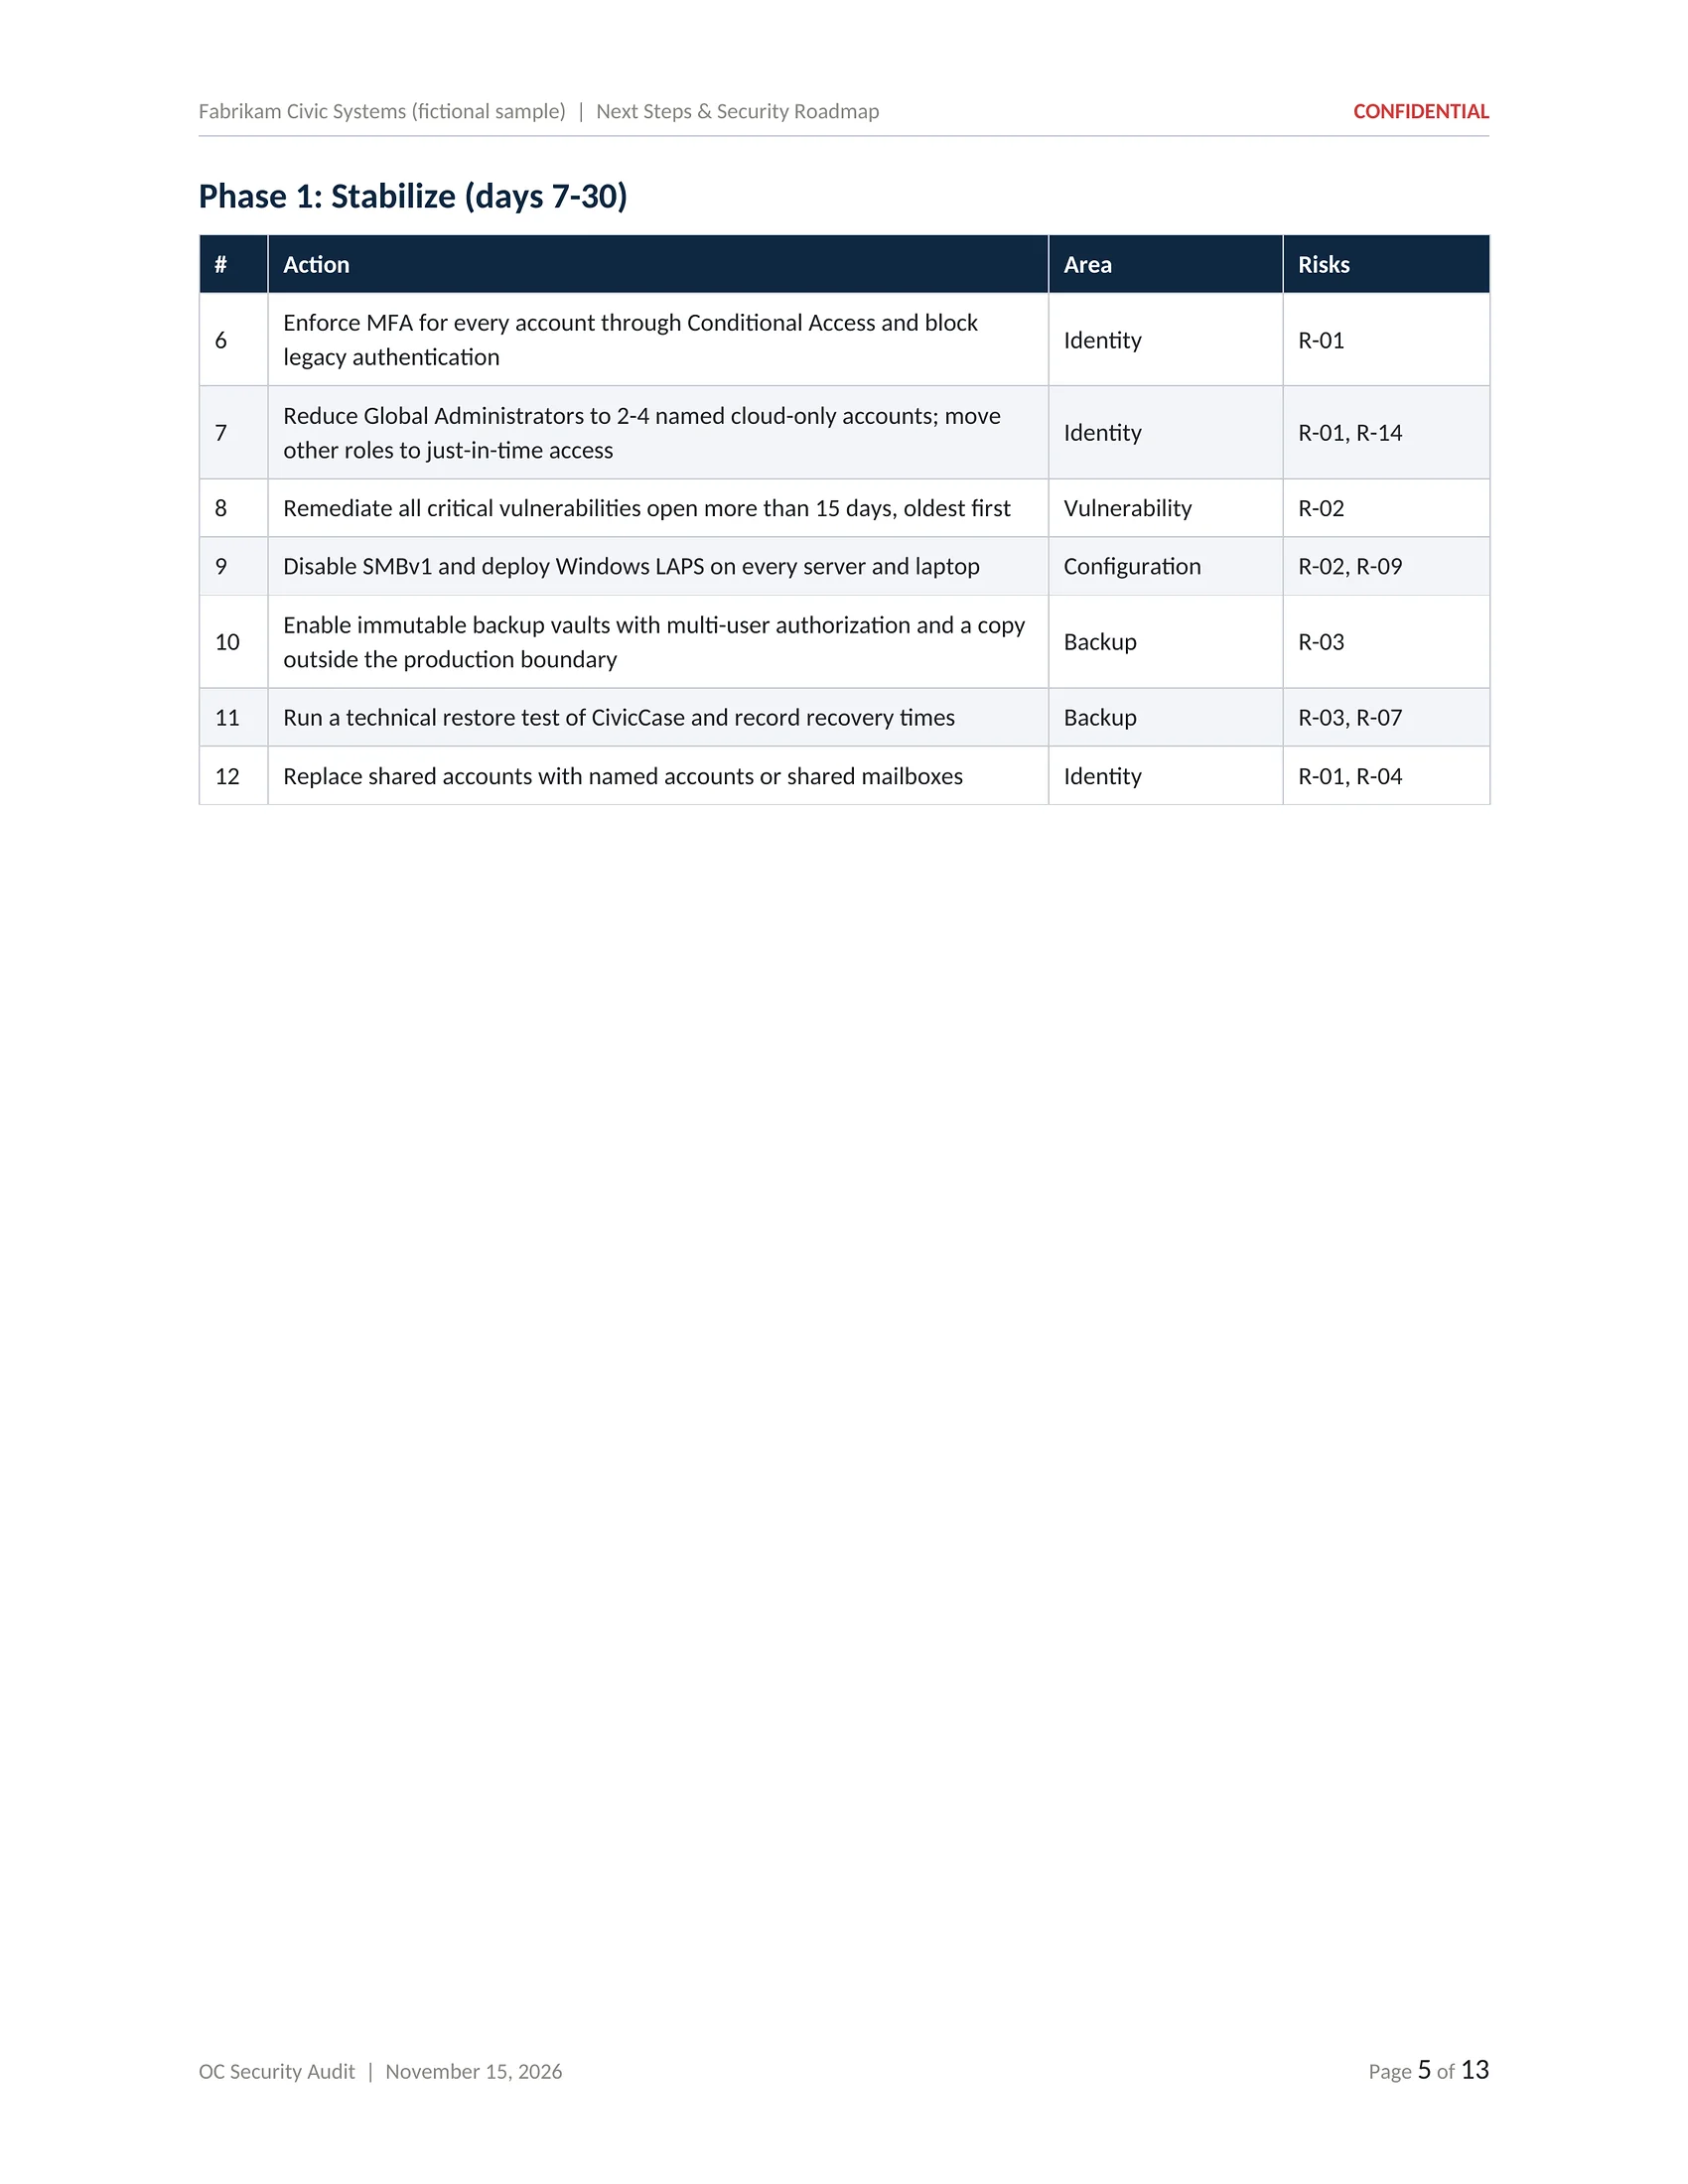
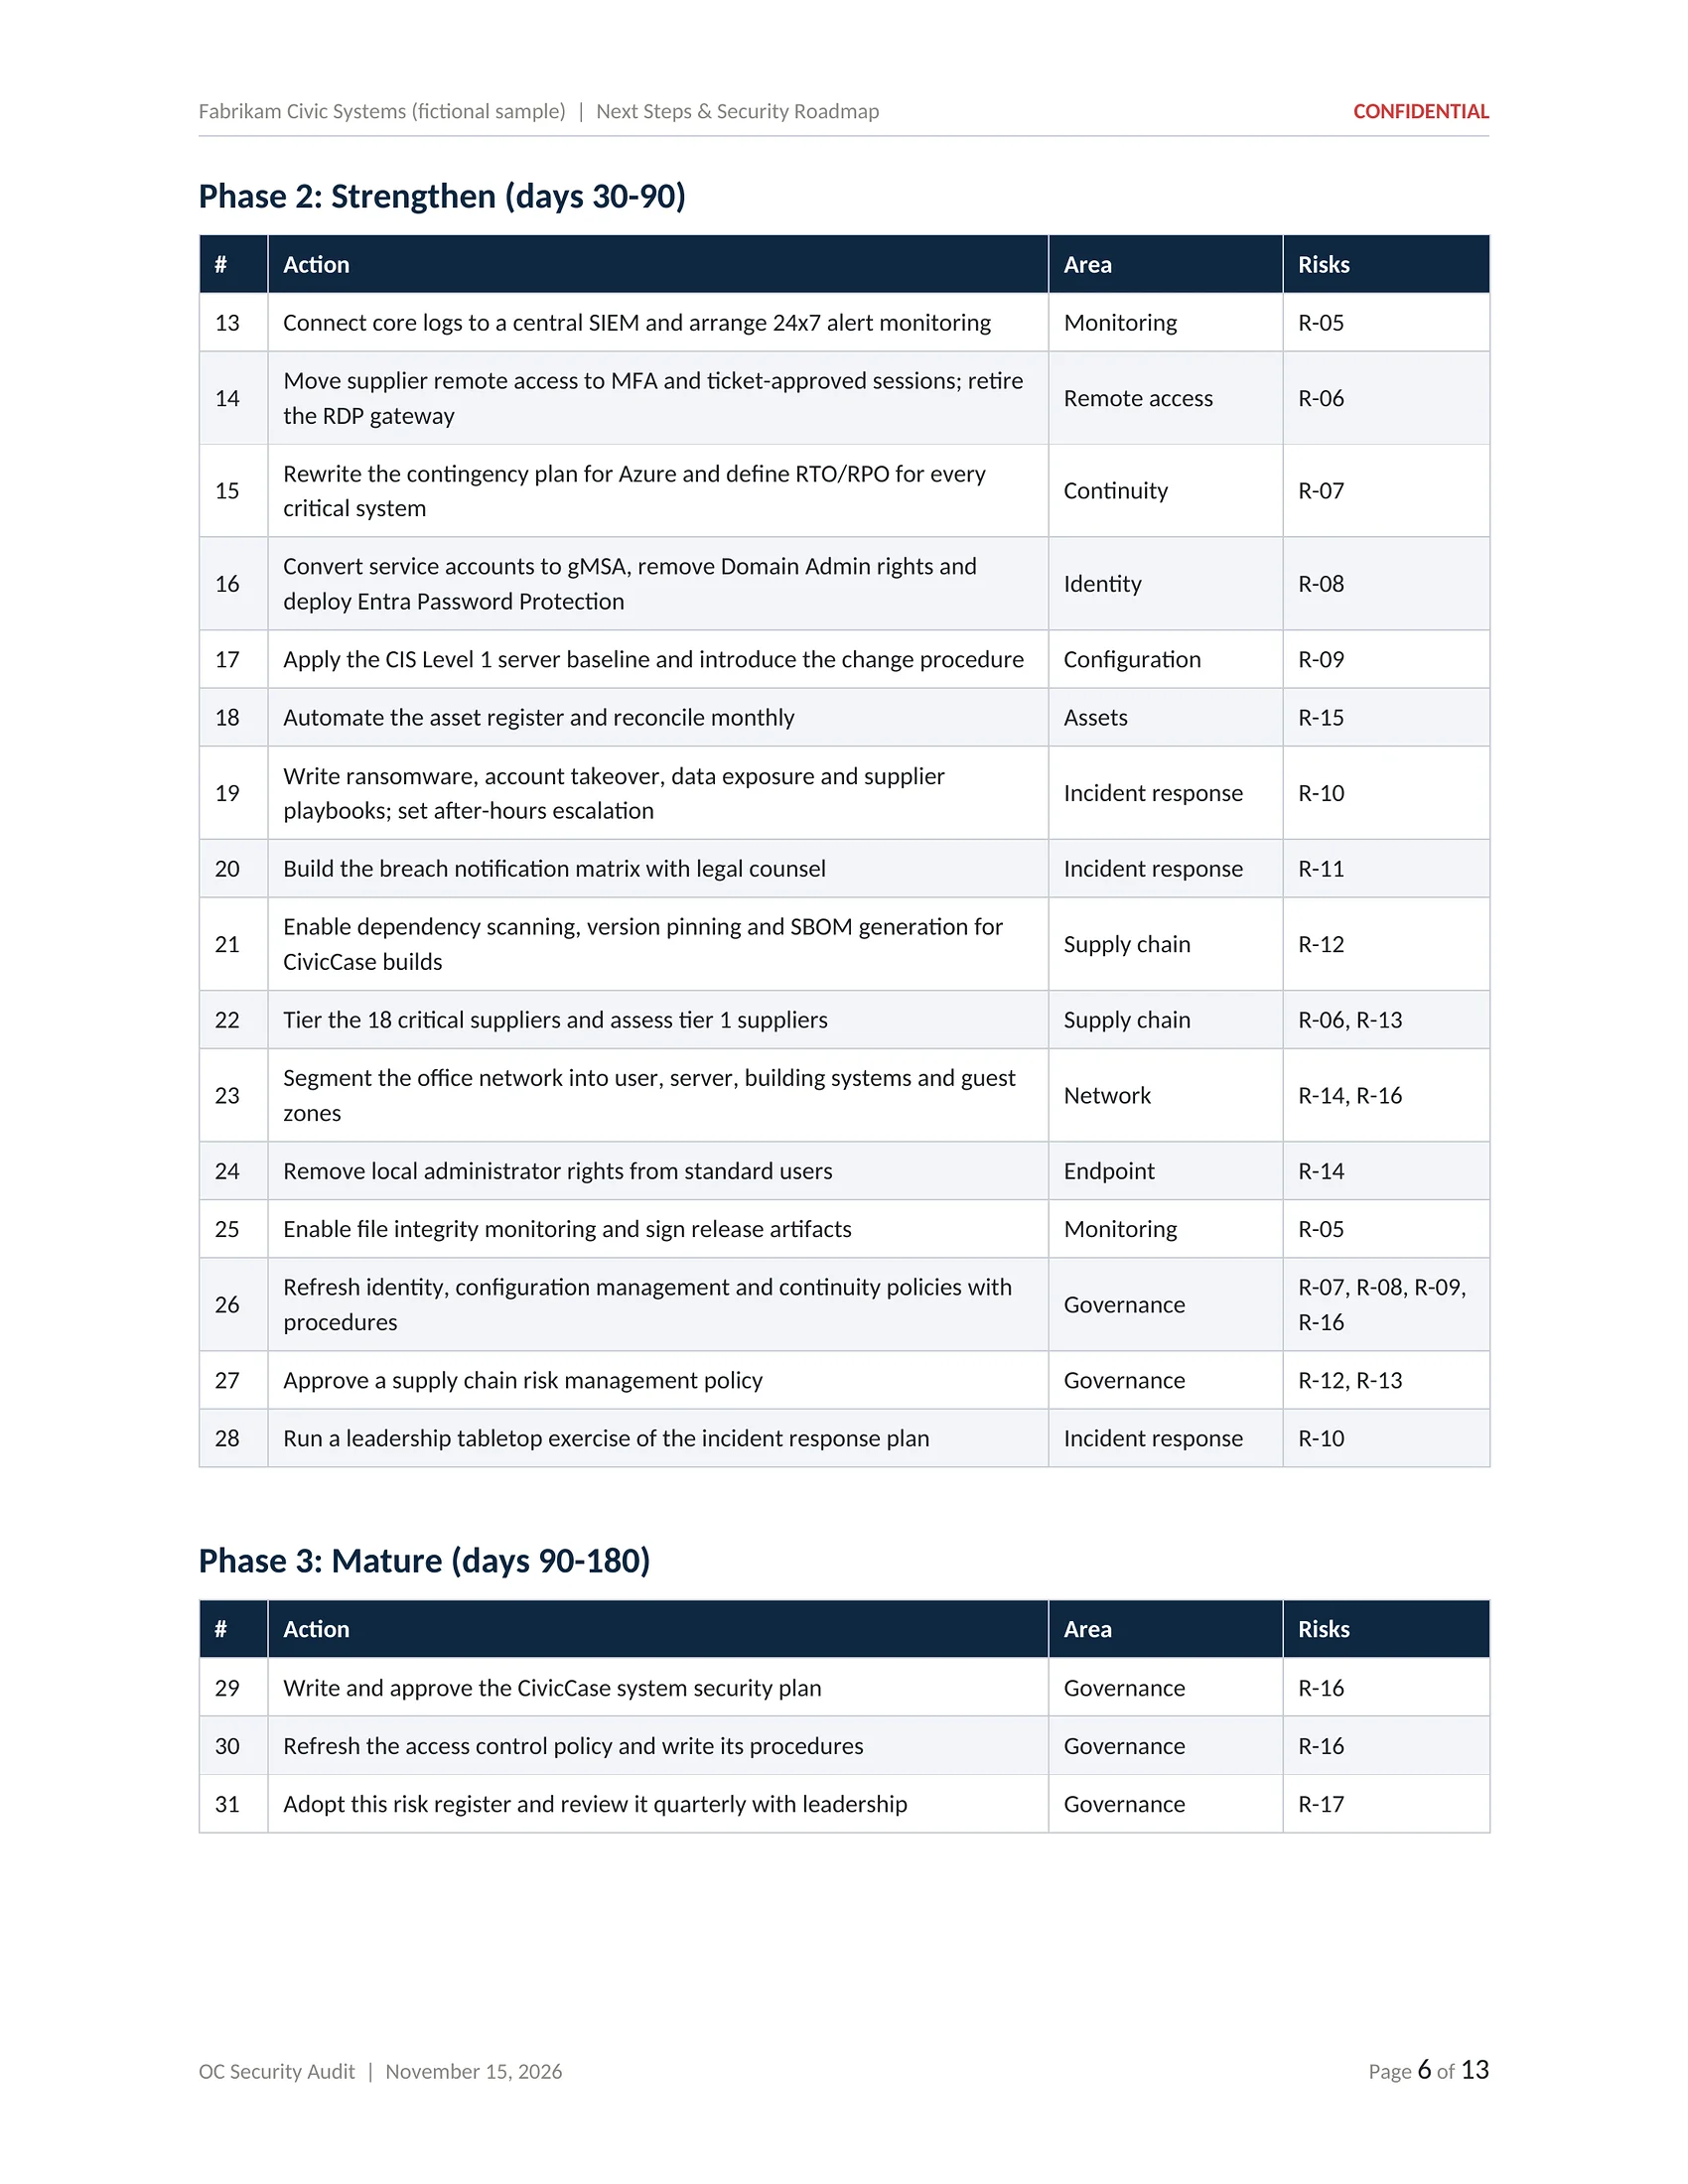
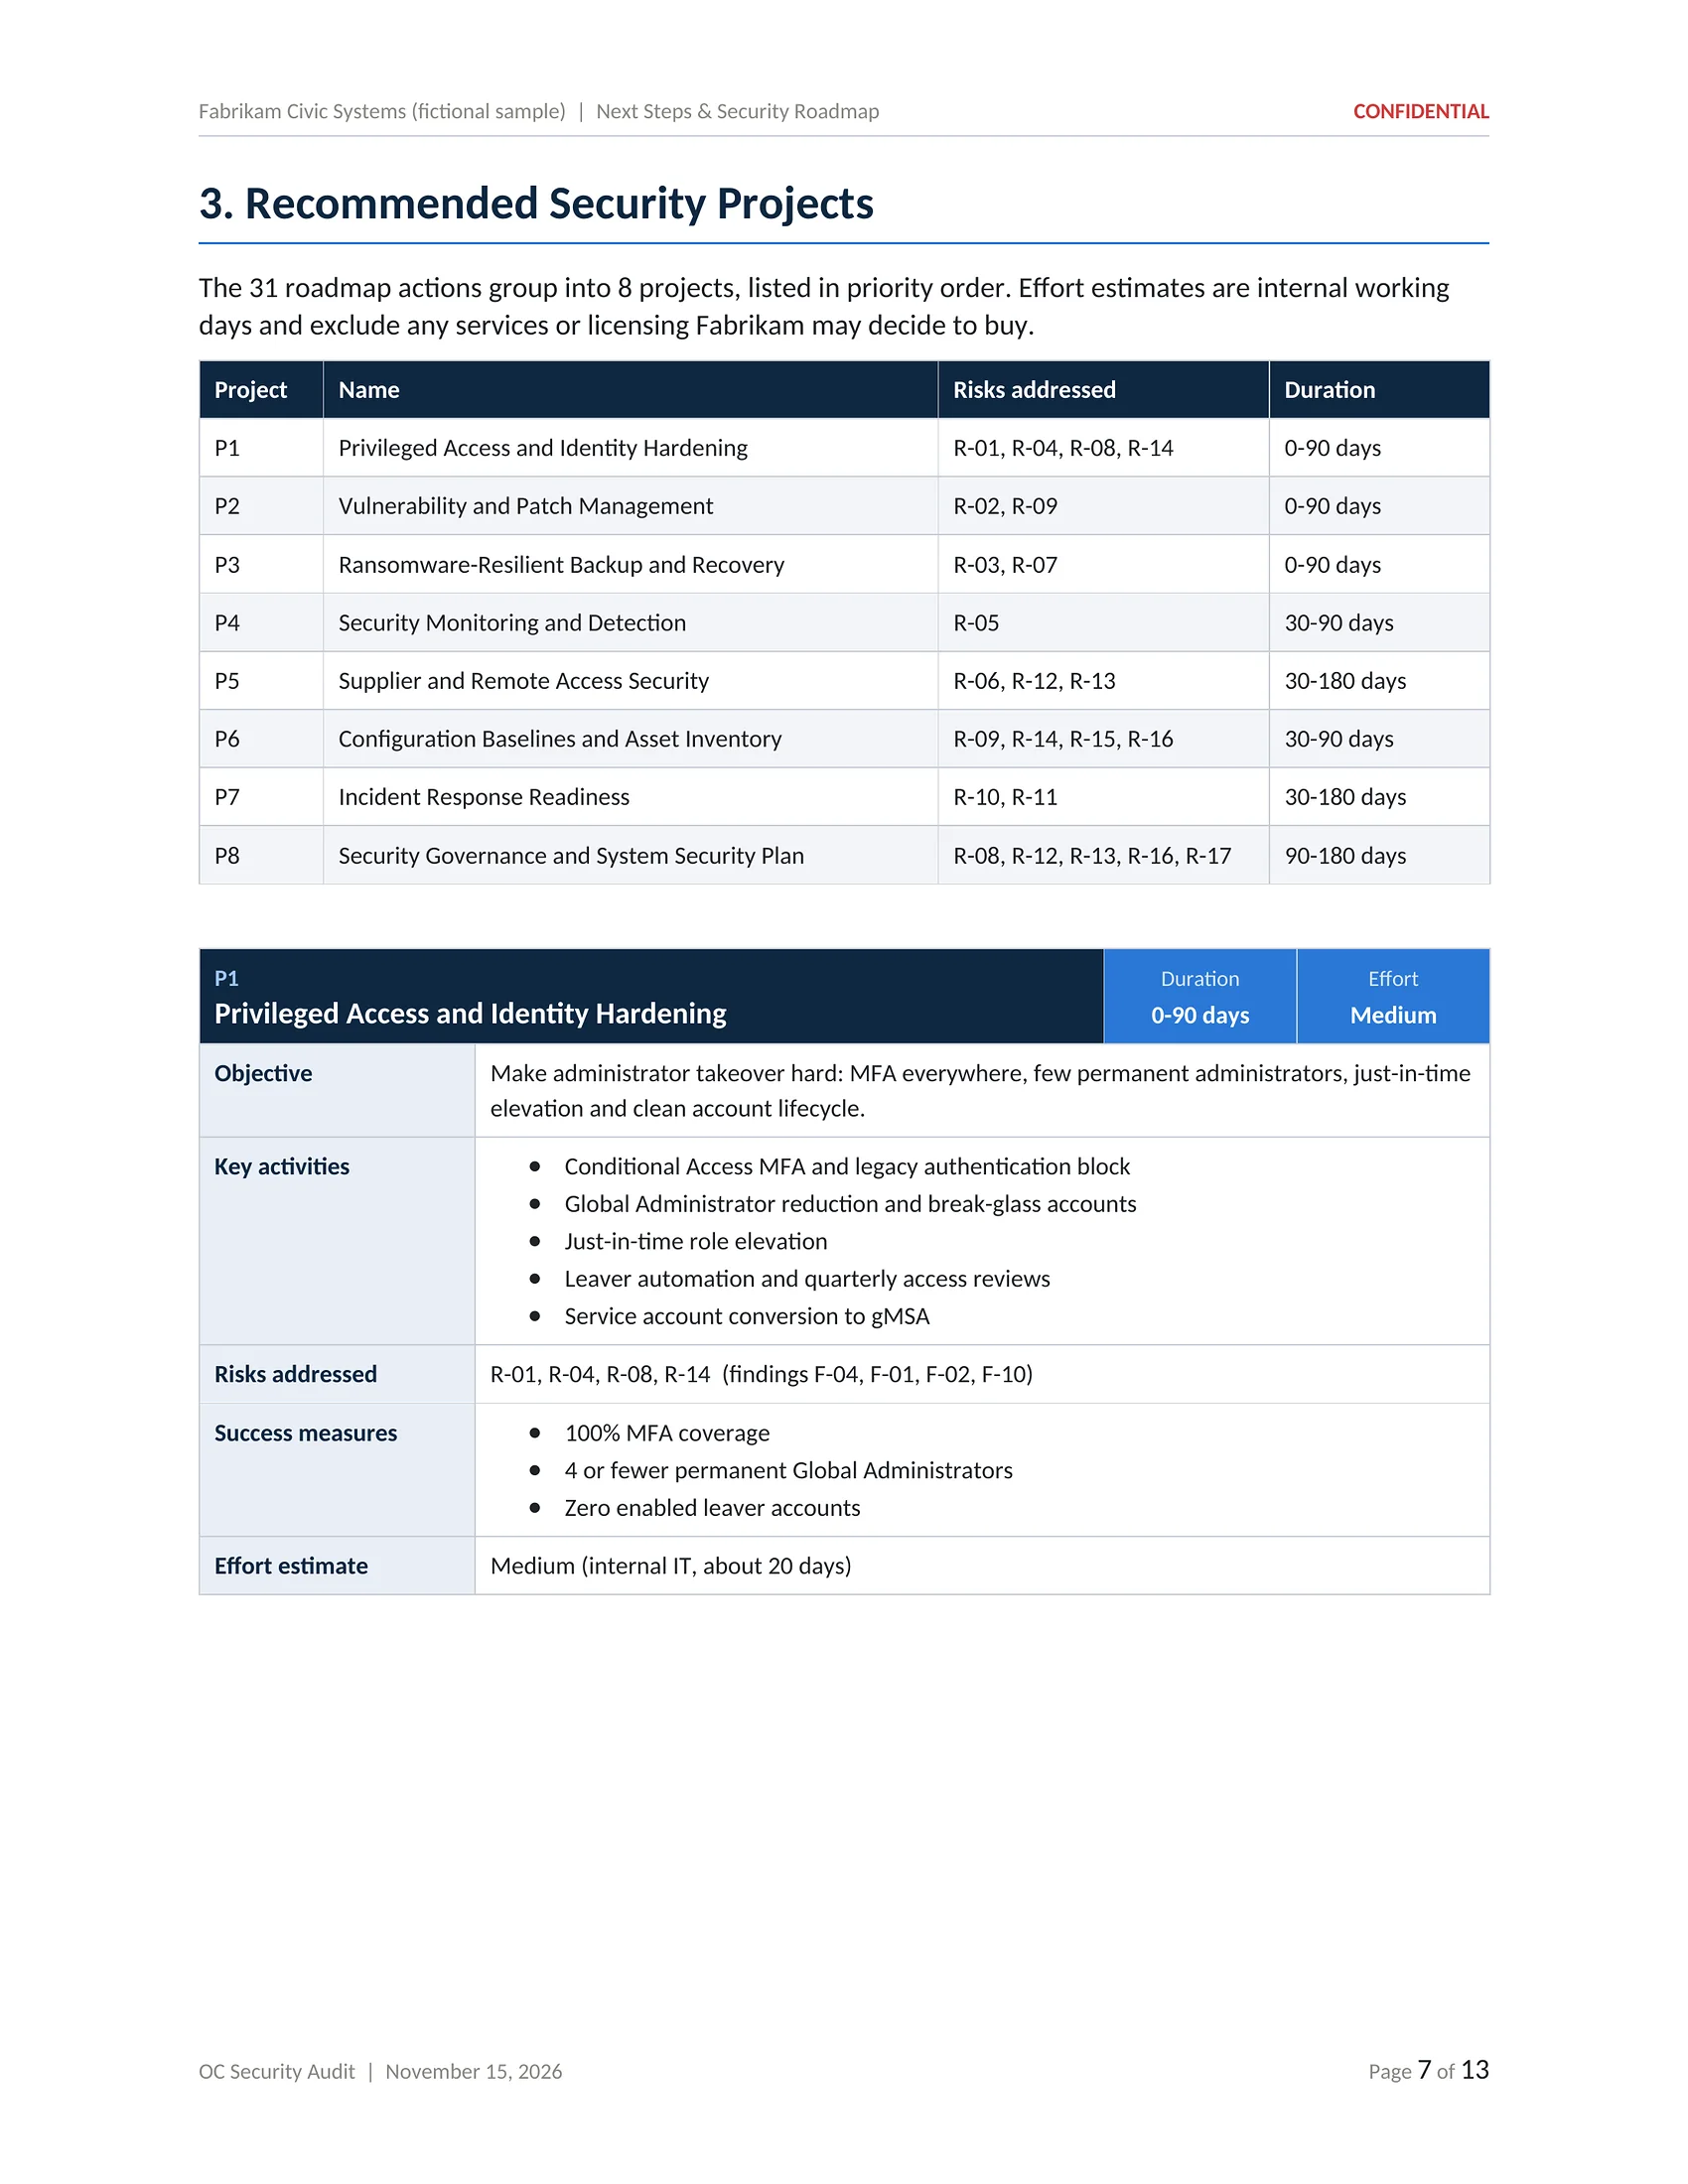
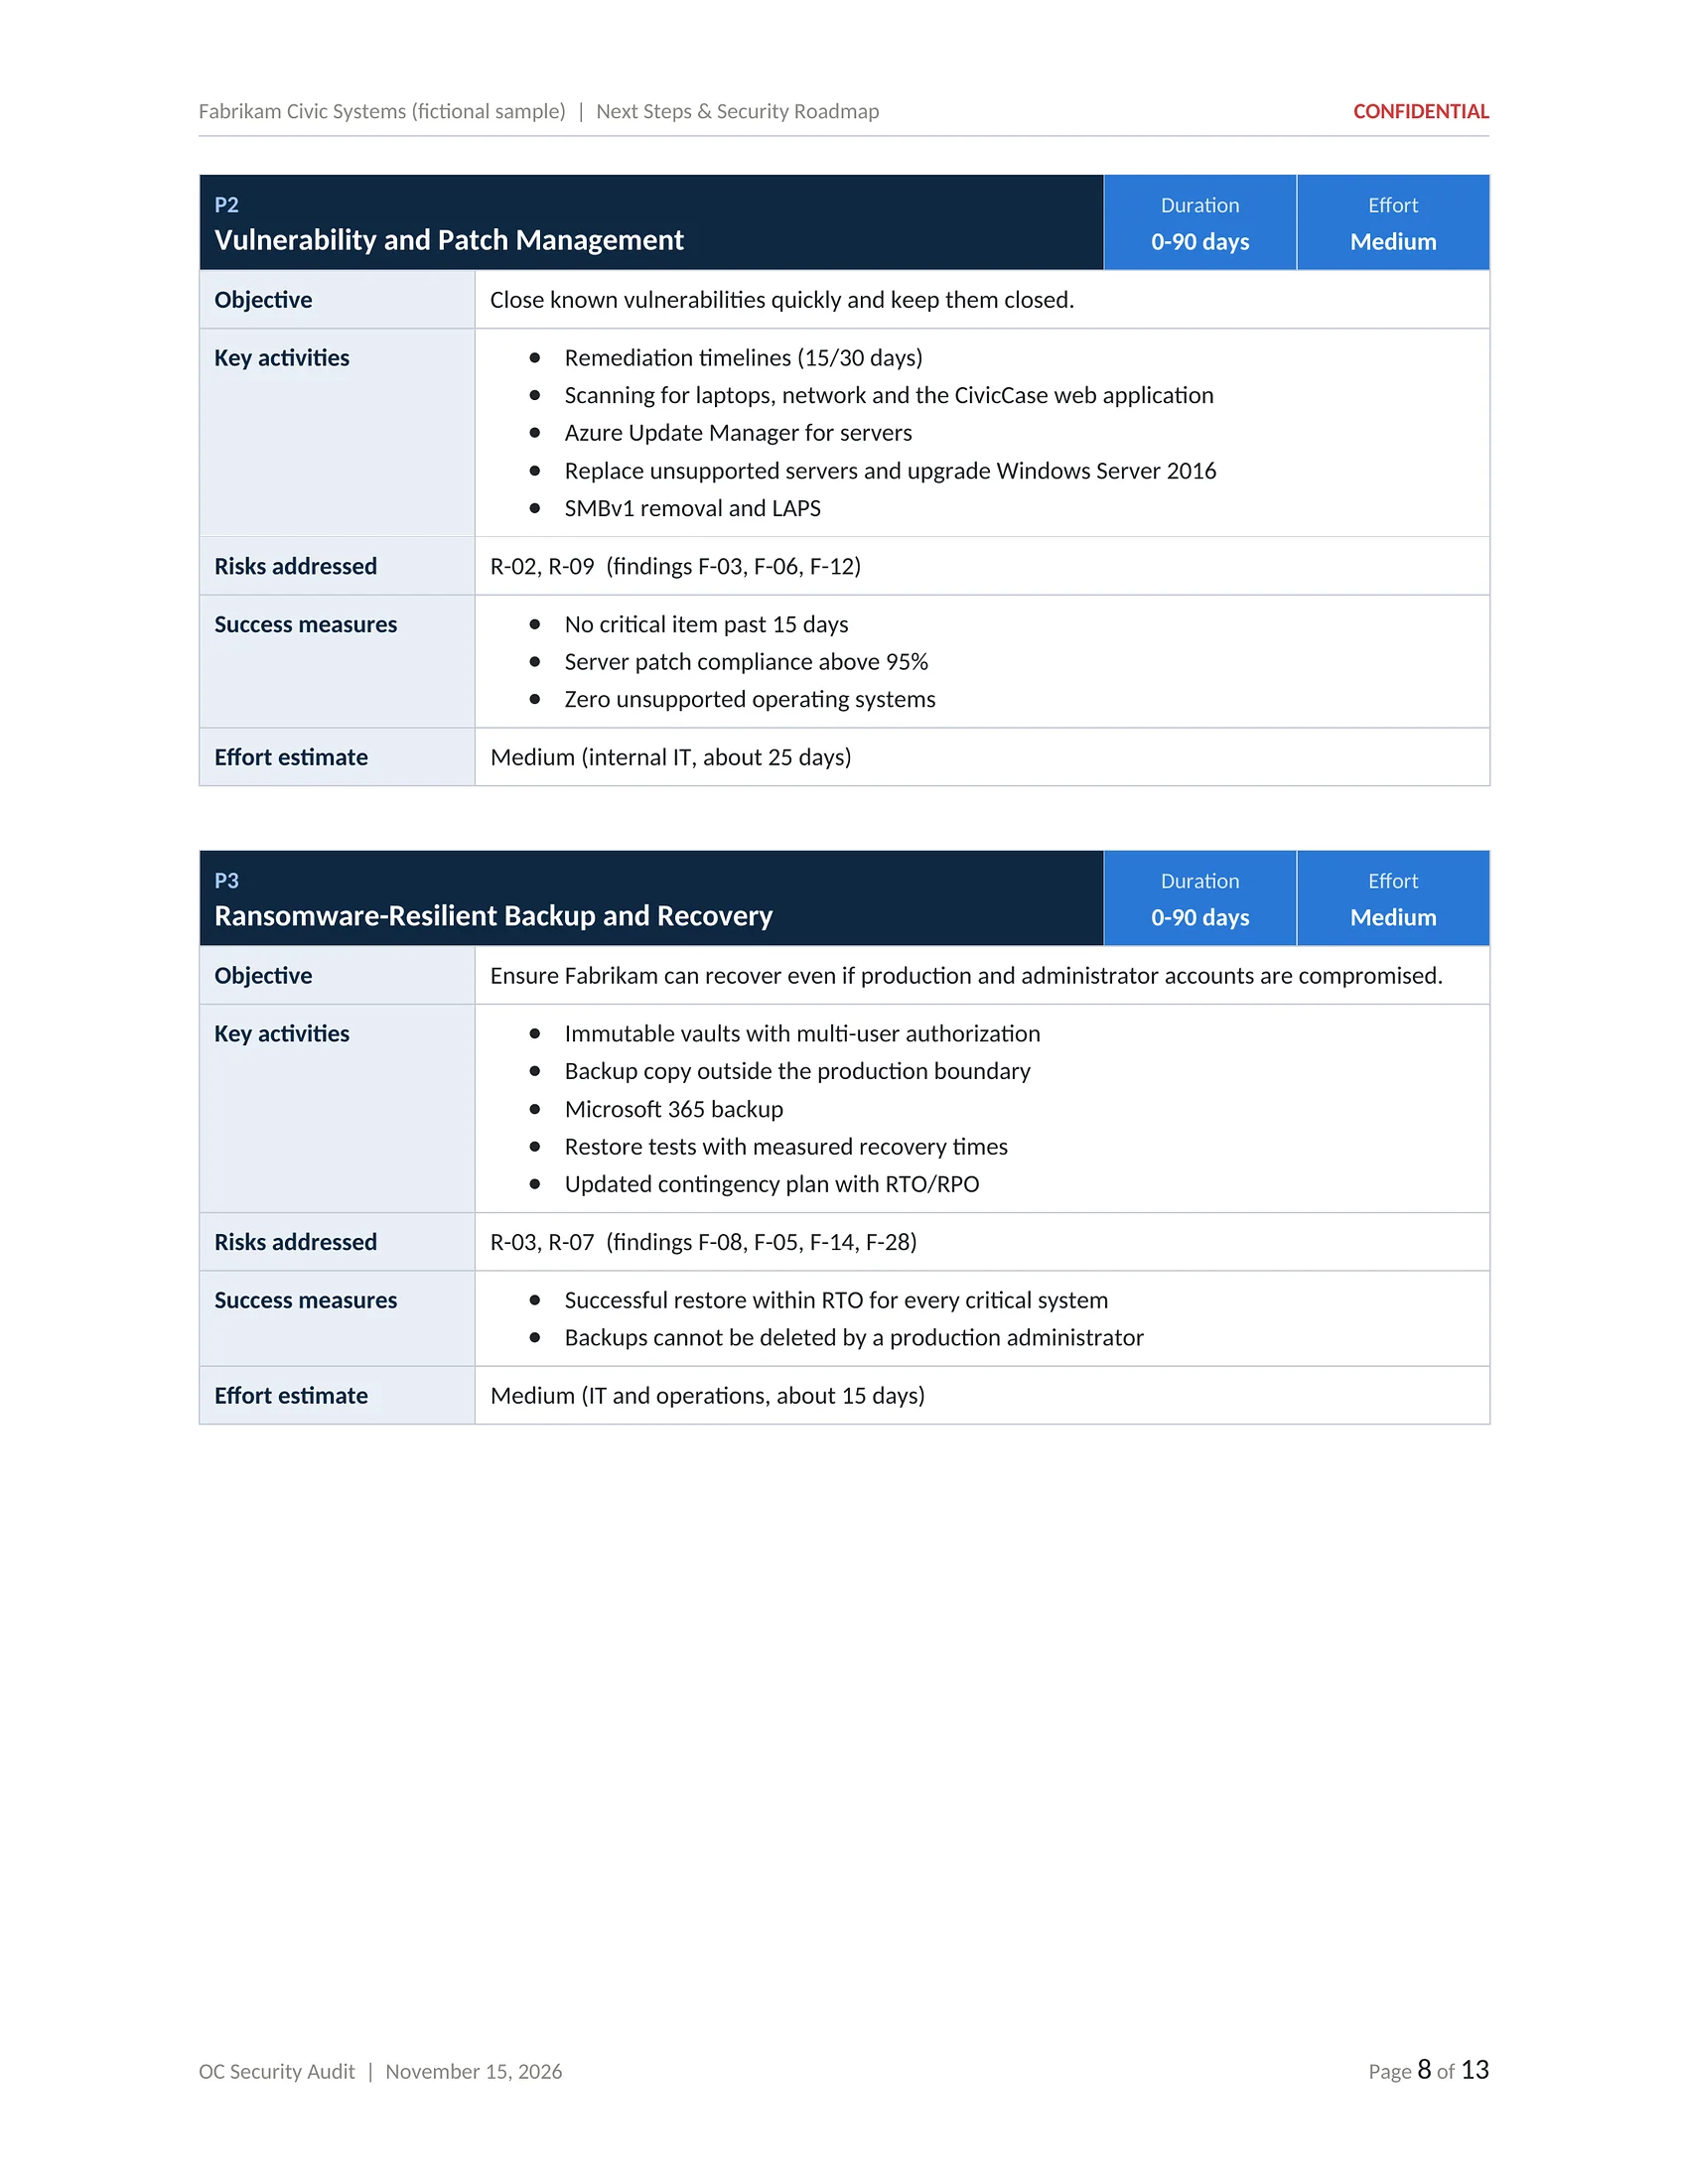
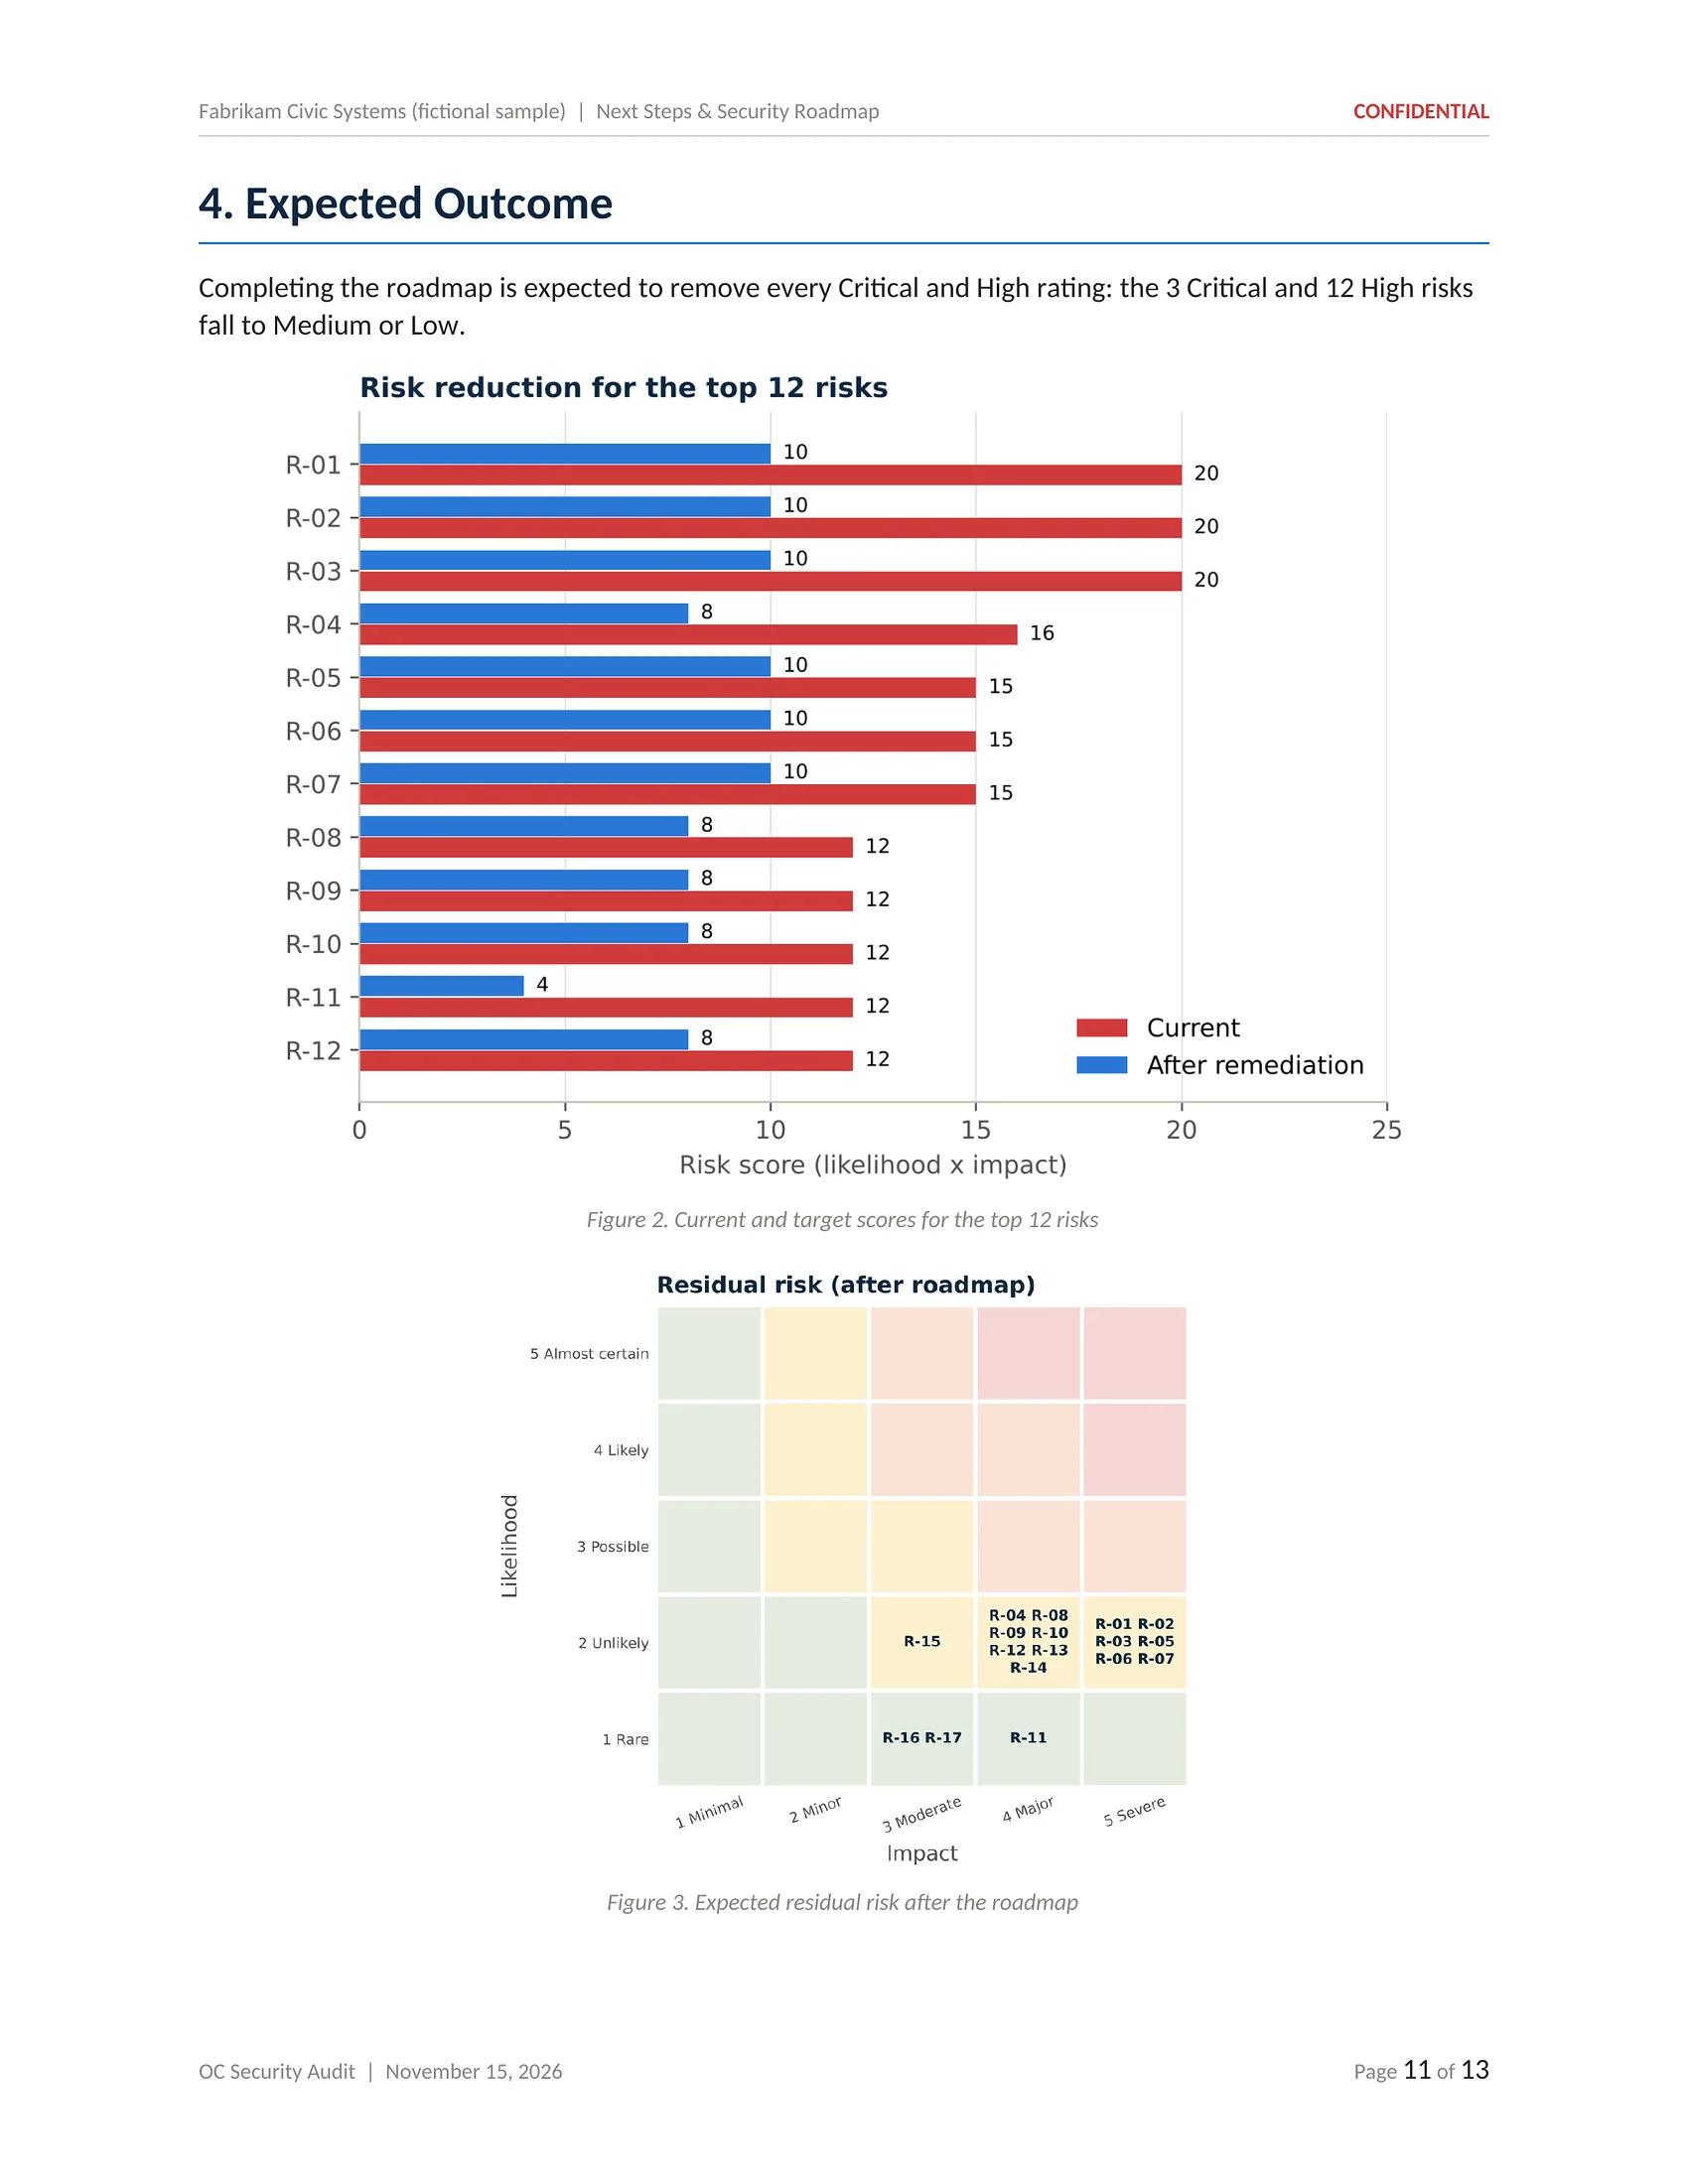
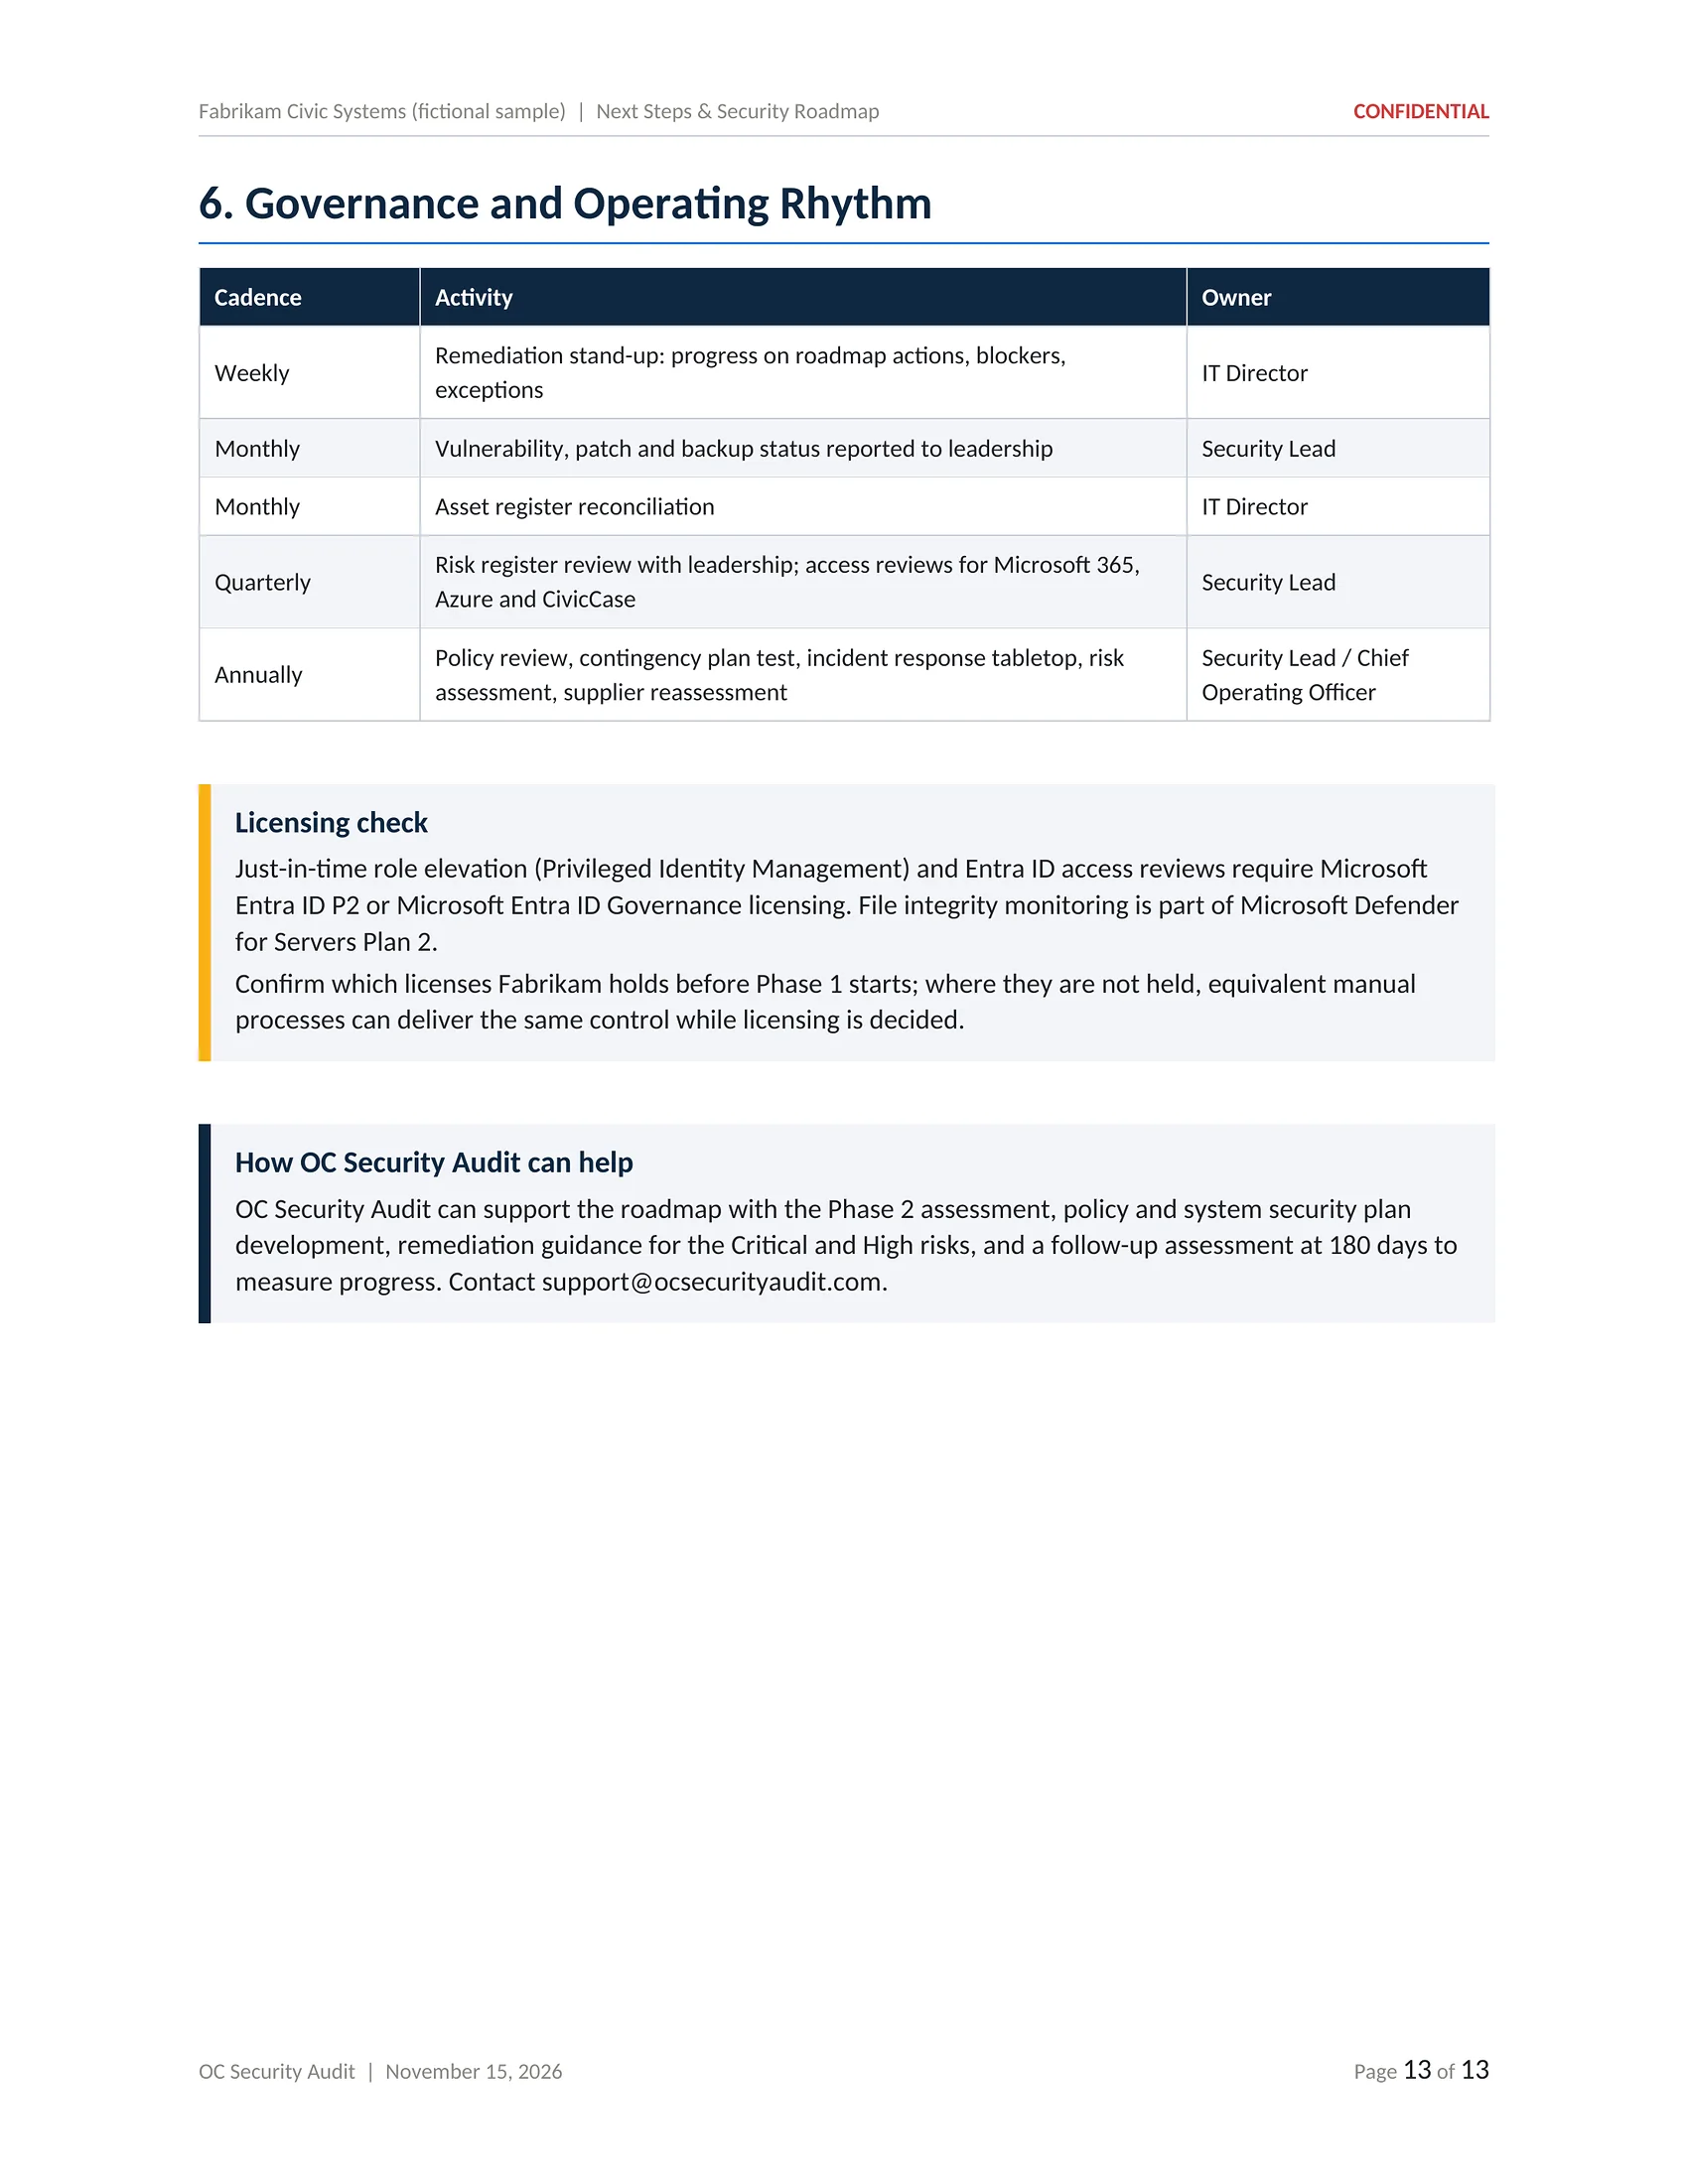
Click the page in the centre to open it full size, then zoom in to read every line.
Excel · 26 sheets
Technical Findings Workbook
Everything in the reports, in a workbook your team keeps working in. It includes the completed OC Security Audit NIST 800-53 template, one sheet per control family, the remediation tracker, all findings, the risk register with live scoring, the remediation plan, the evidence inventories and domain scores. Yellow columns are for your team to maintain.
Whoever tracks remediation; the source for your plan of action and milestones and for customer follow-up questions.
What is included
- Completed NIST 800-53 template
- One sheet per control family
- Remediation tracker
- All findings with status columns
- Risk register with live formulas
- Remediation plan with percent complete
- Accounts, privileged access and vulnerabilities
- Servers, suppliers and critical systems
- Strengths and domain scores
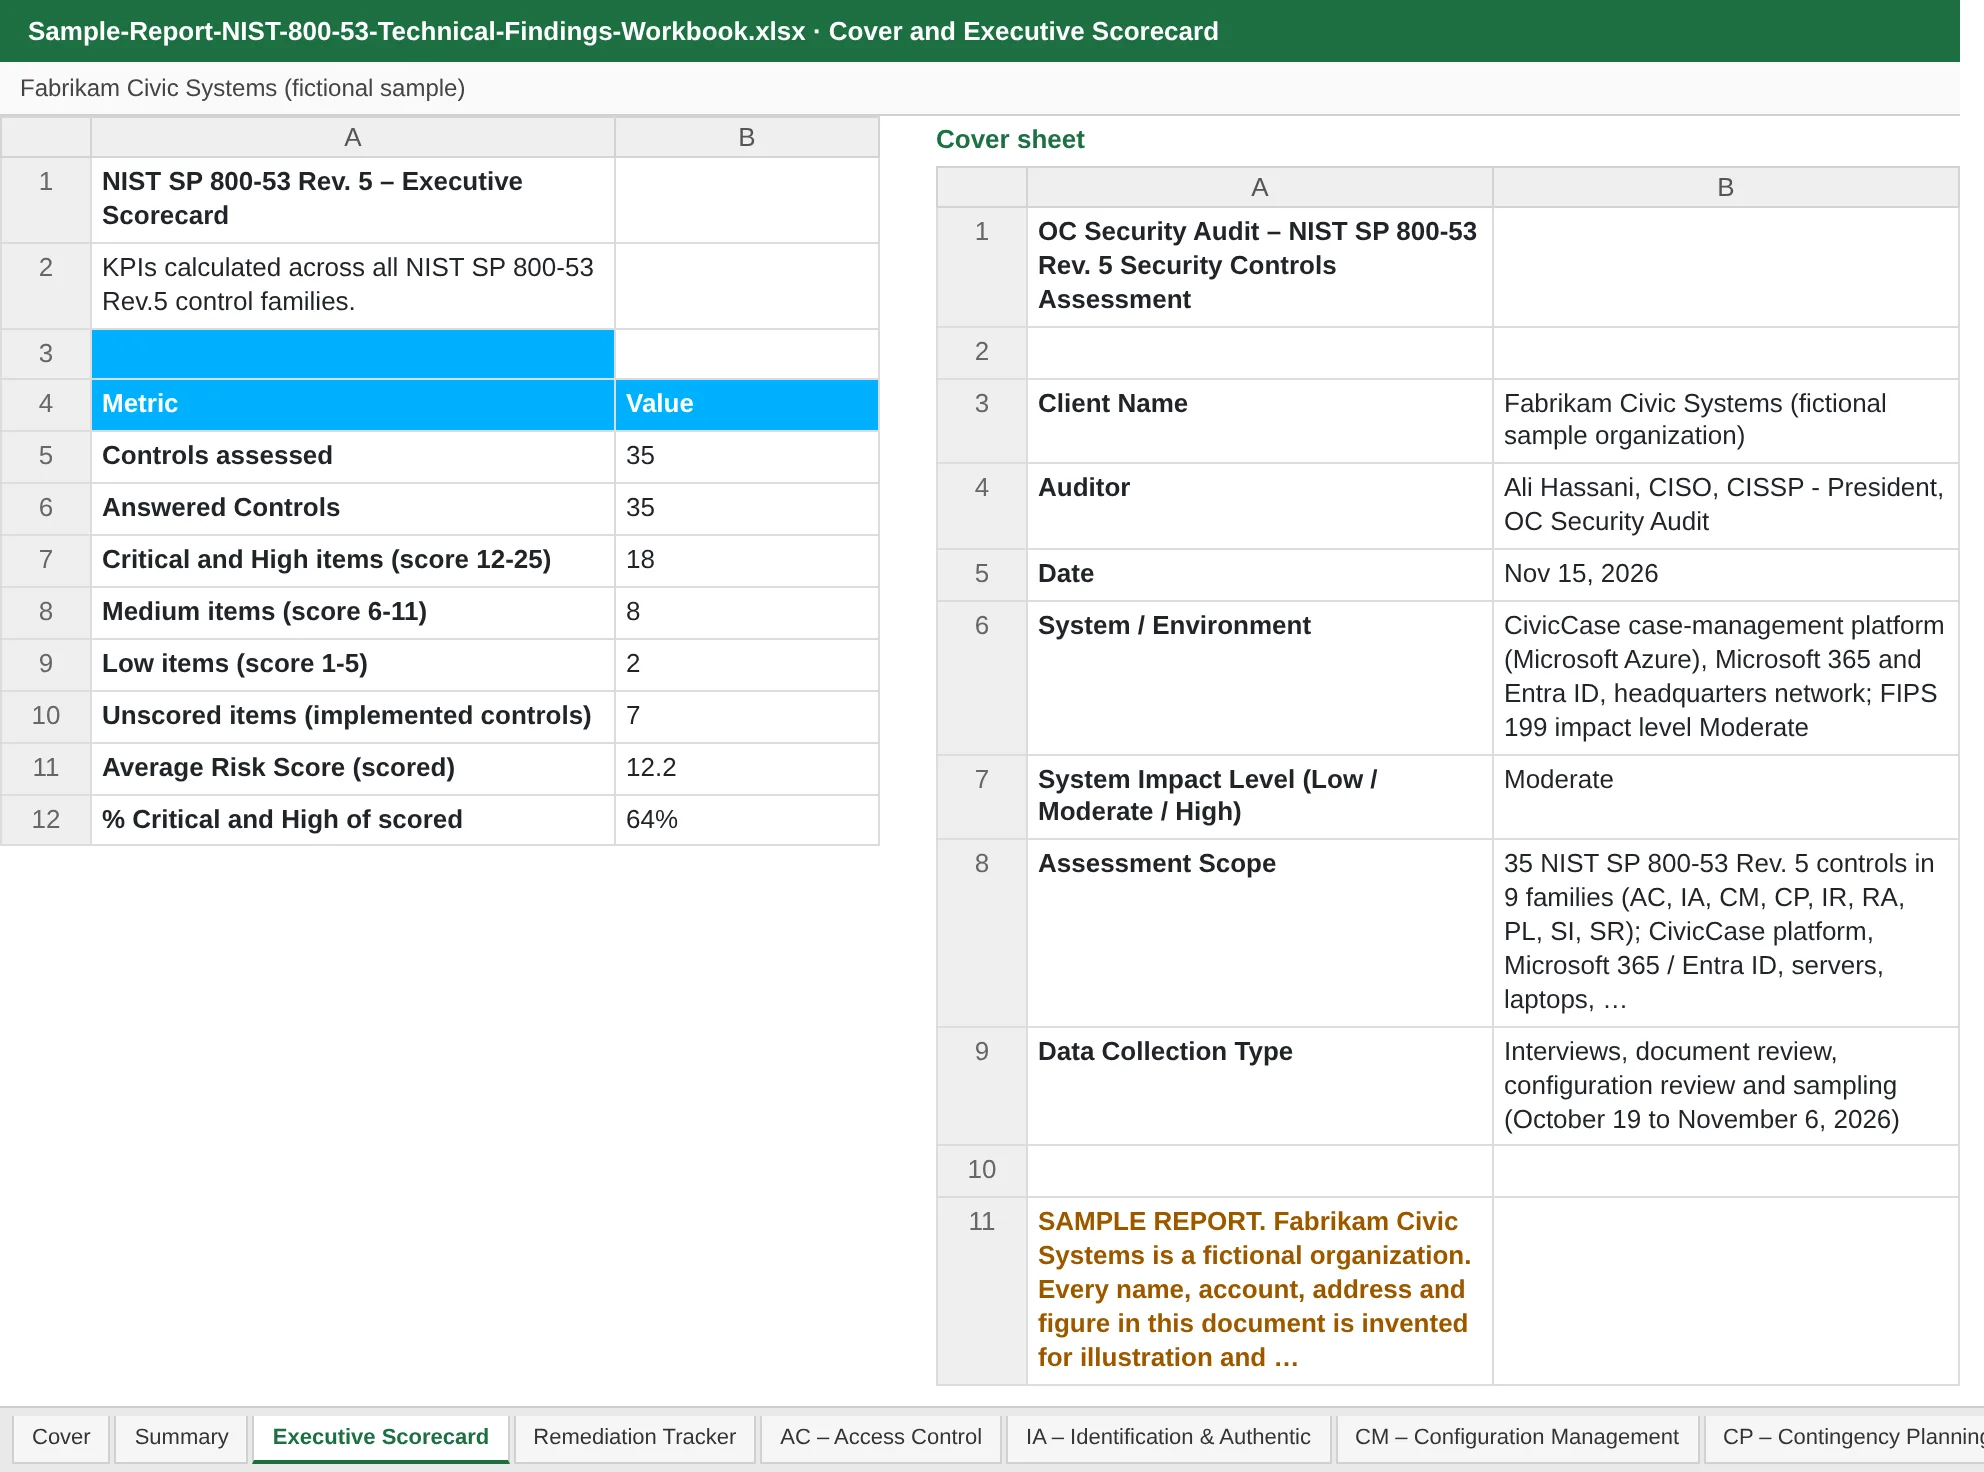
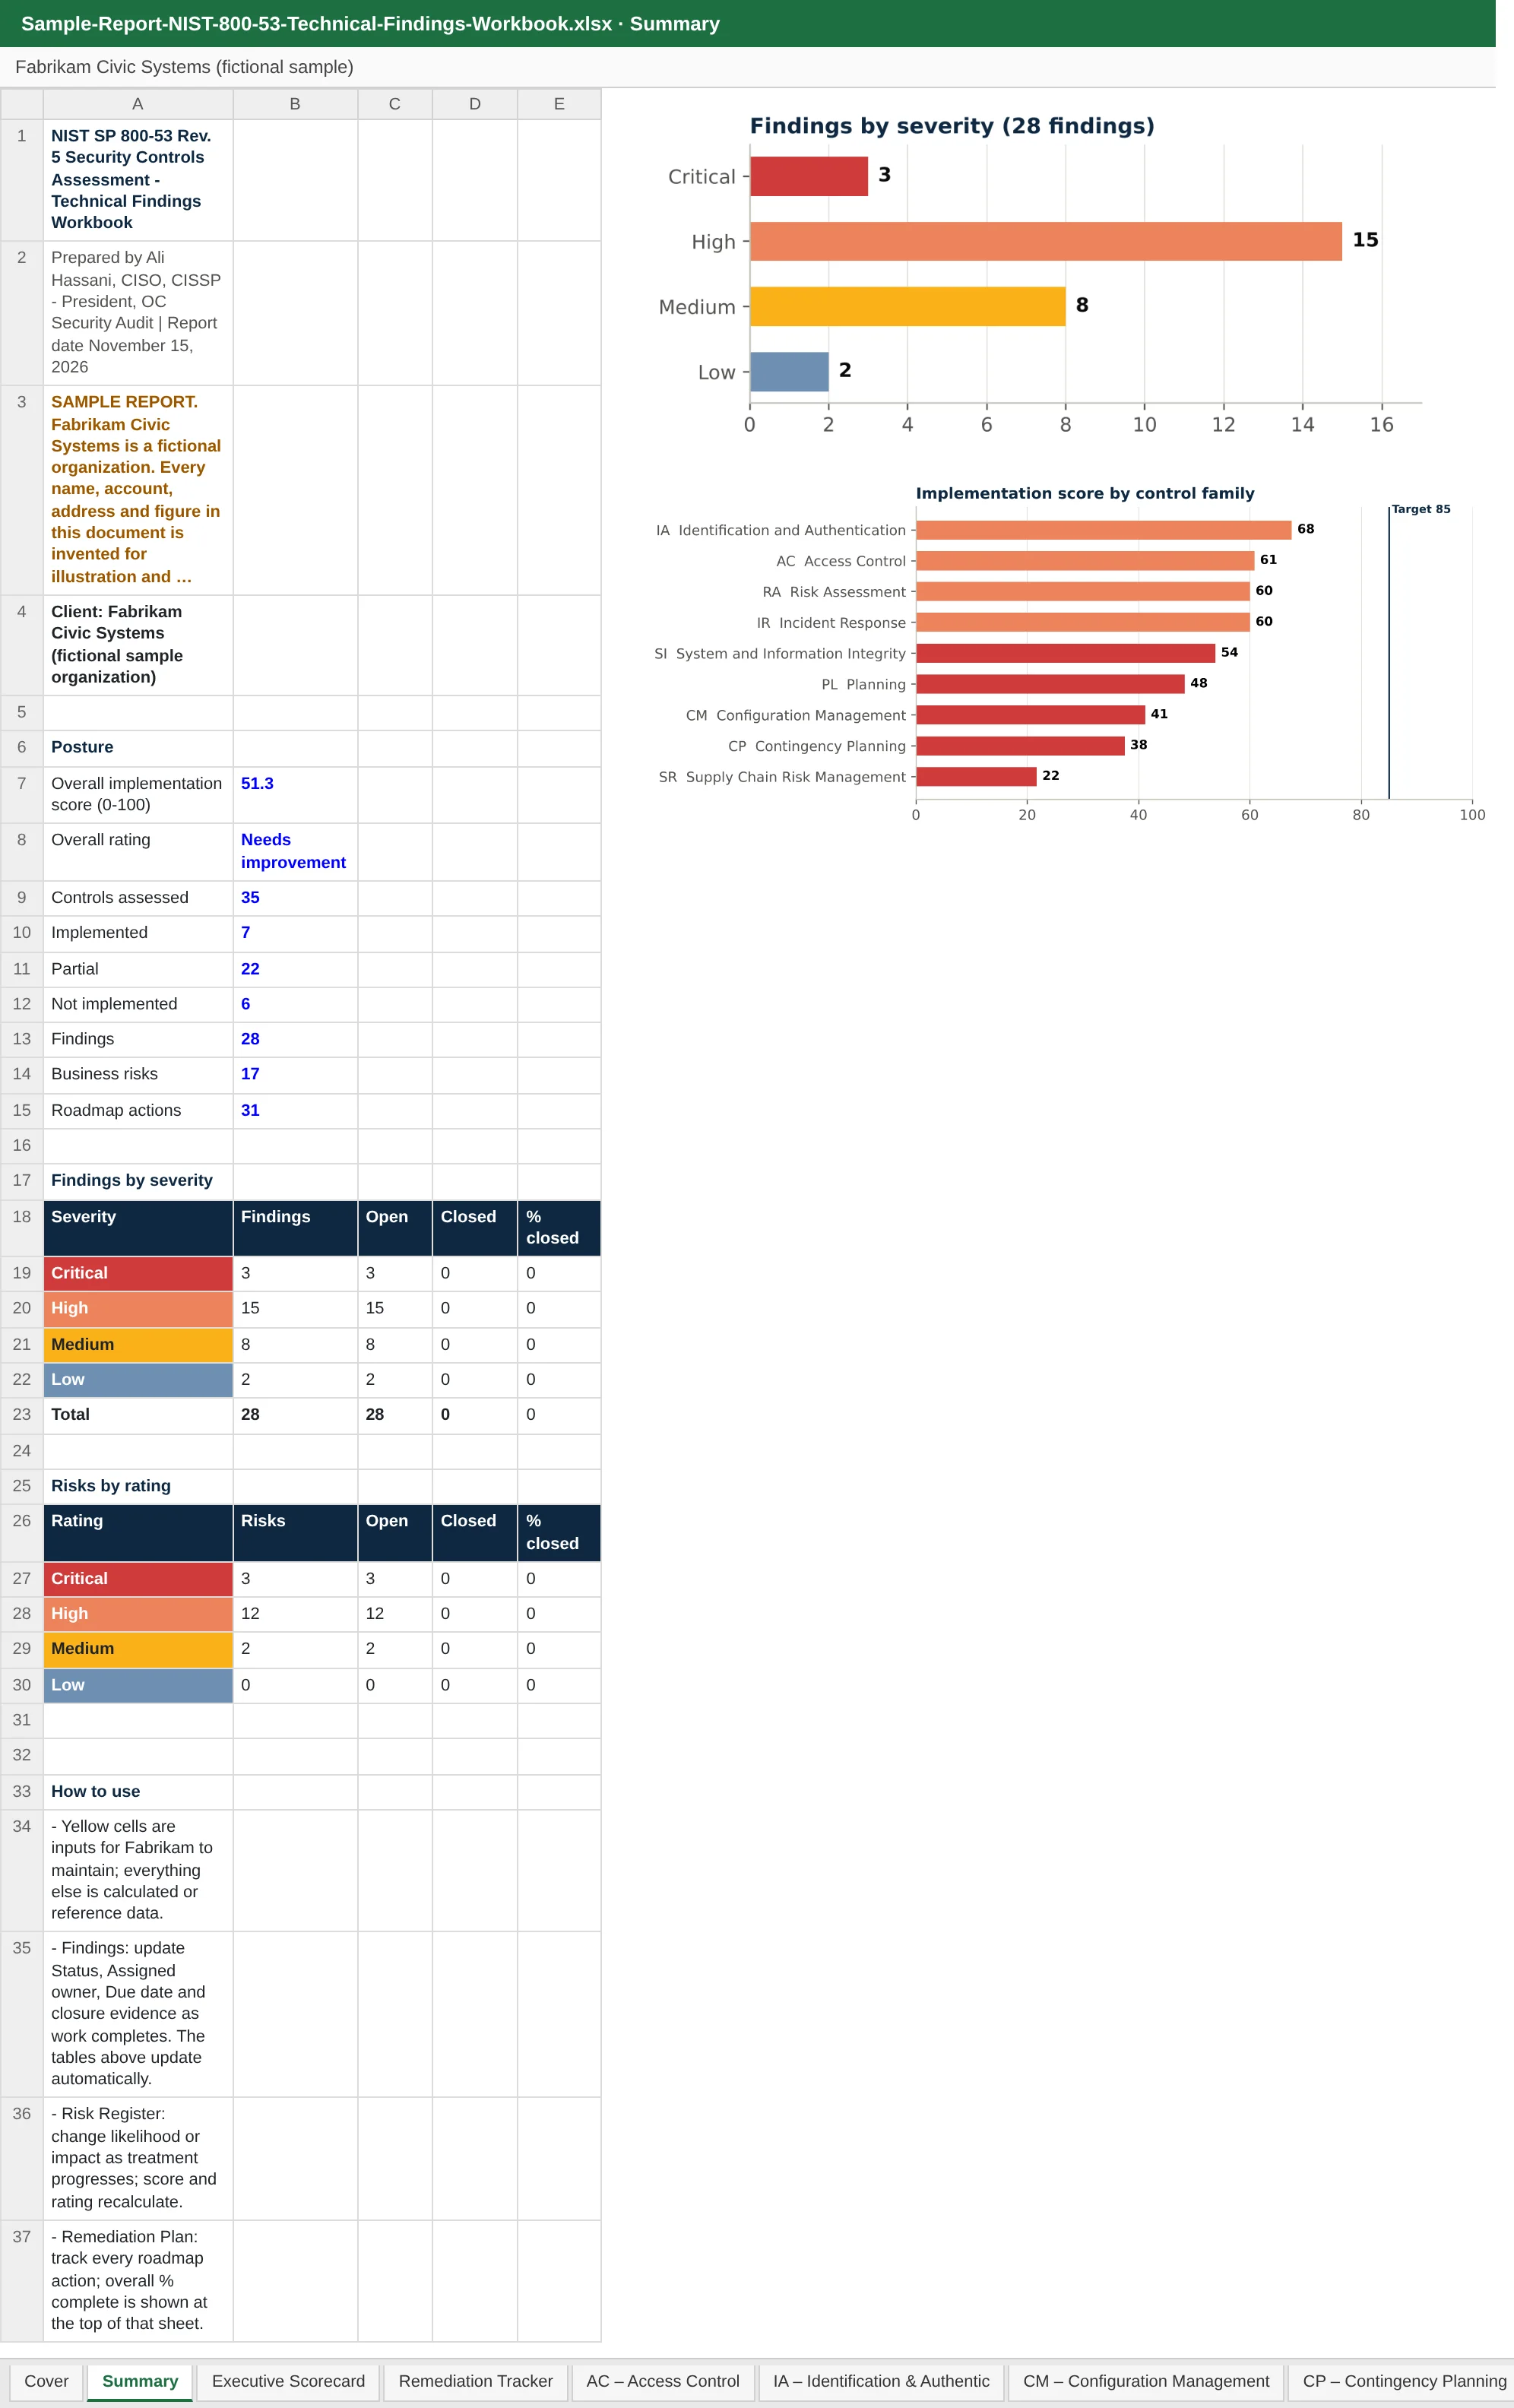
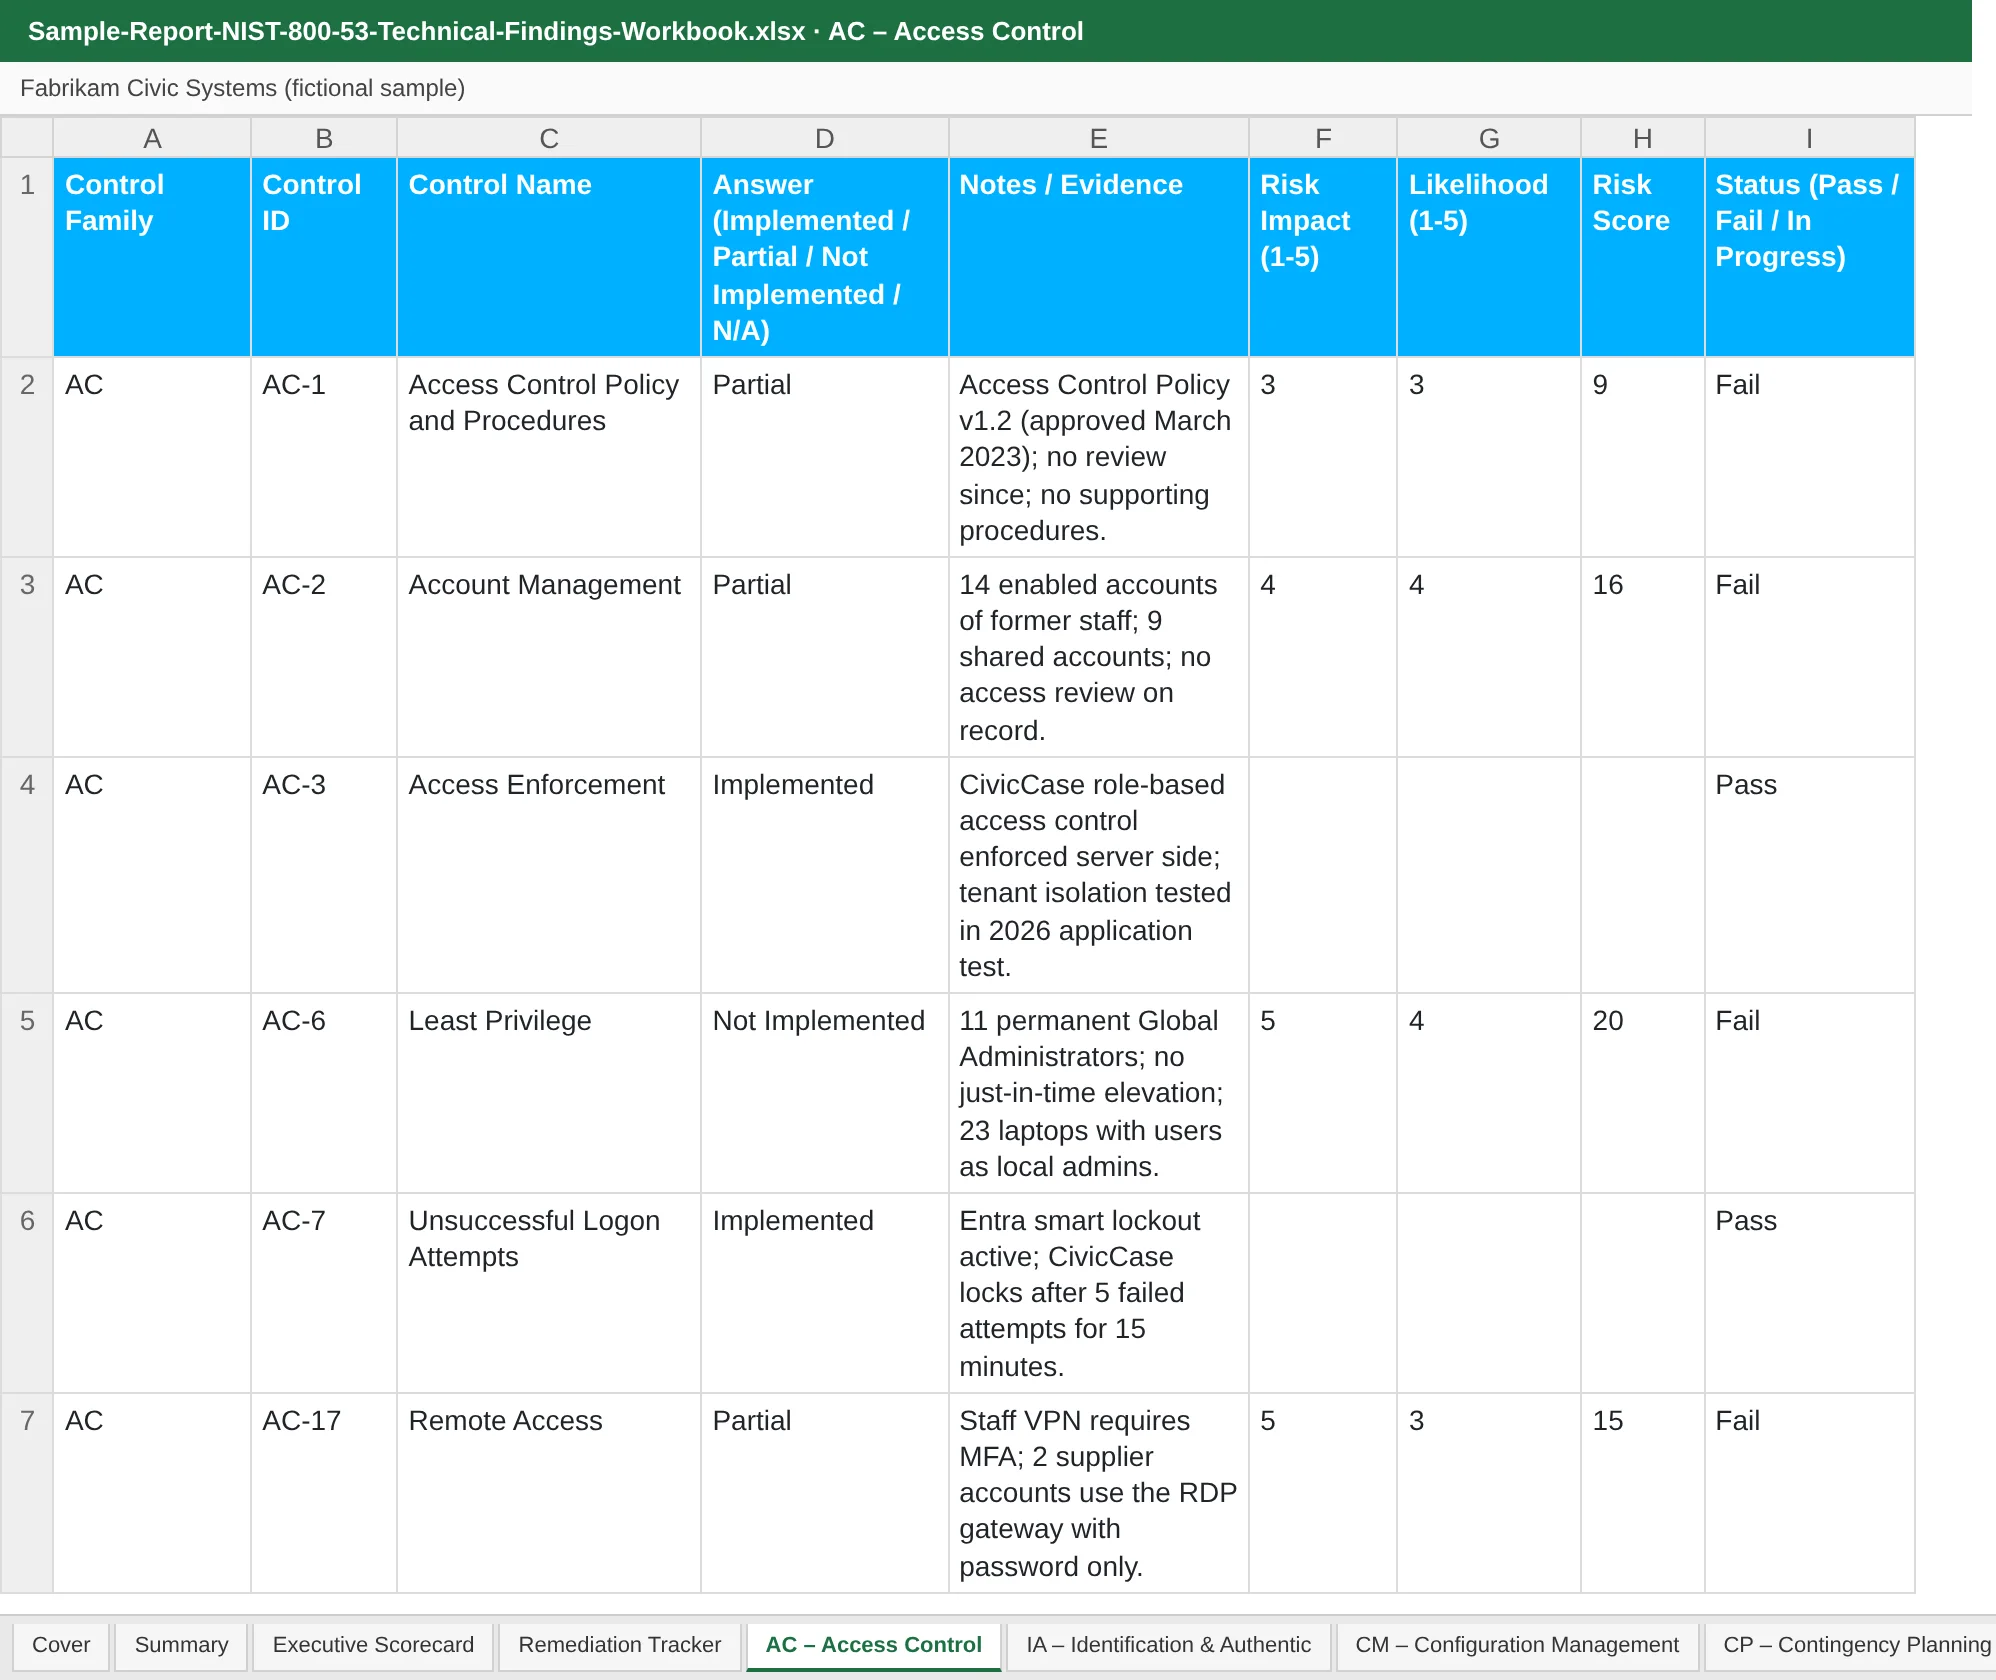
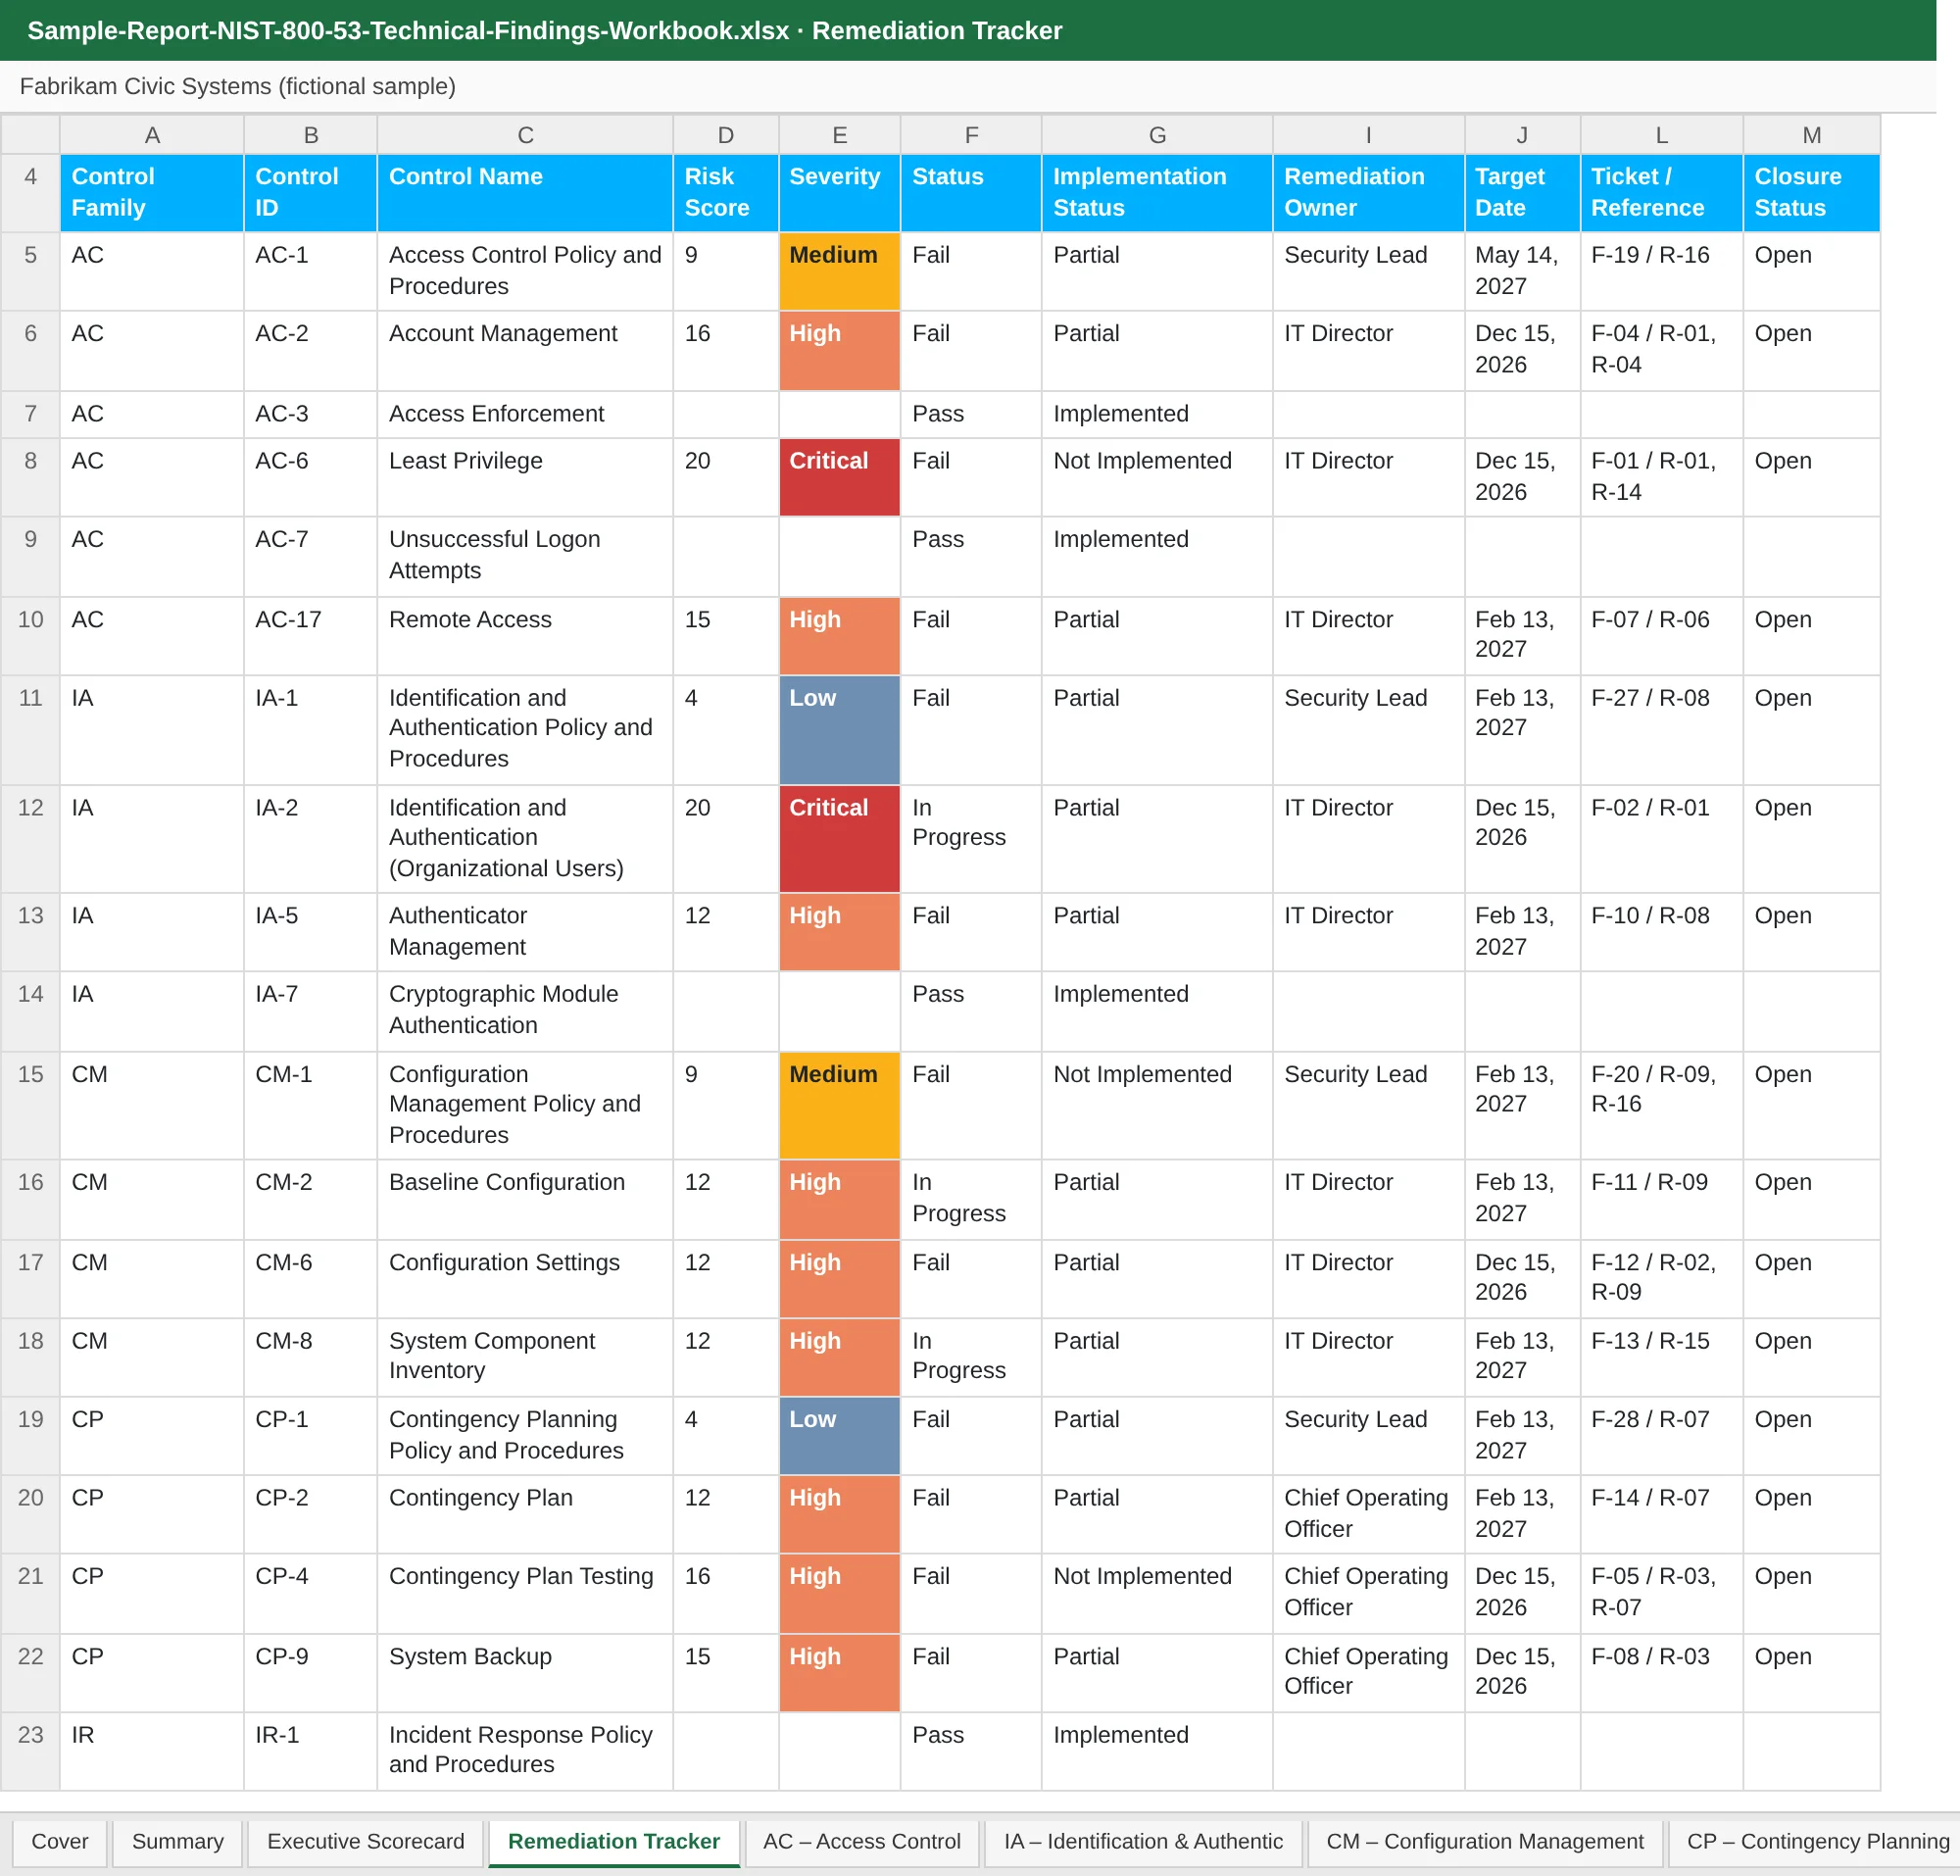
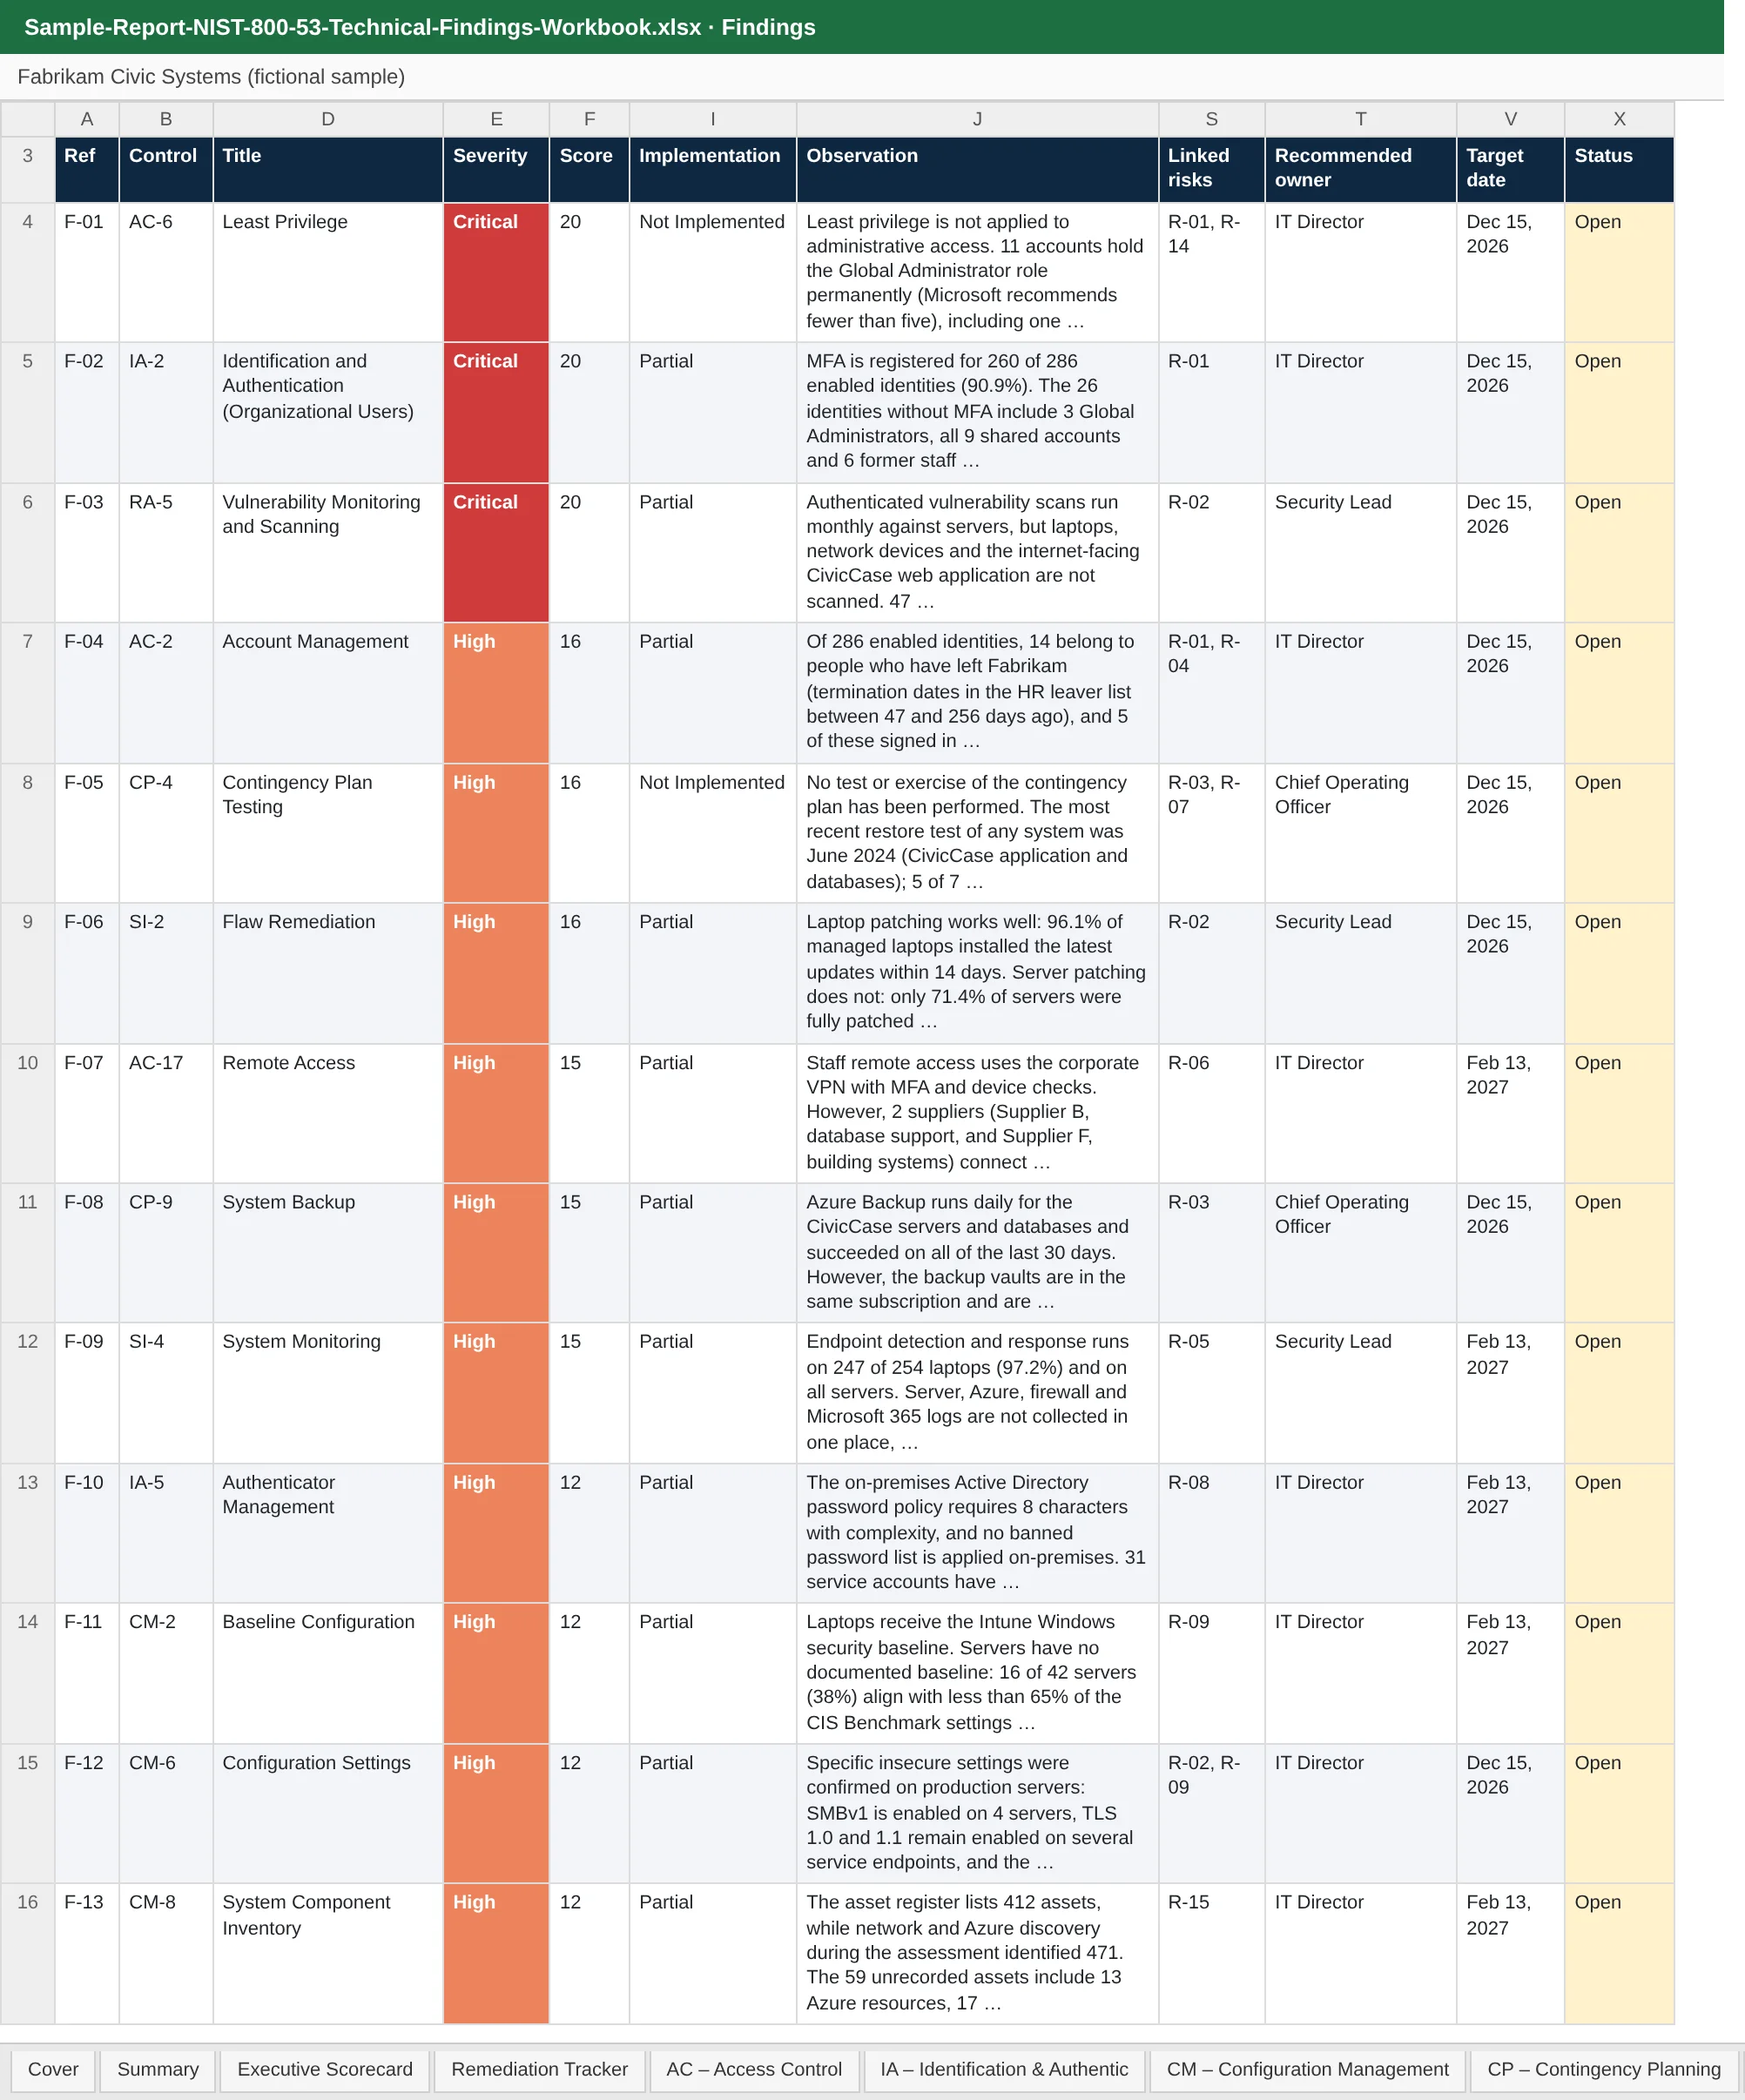
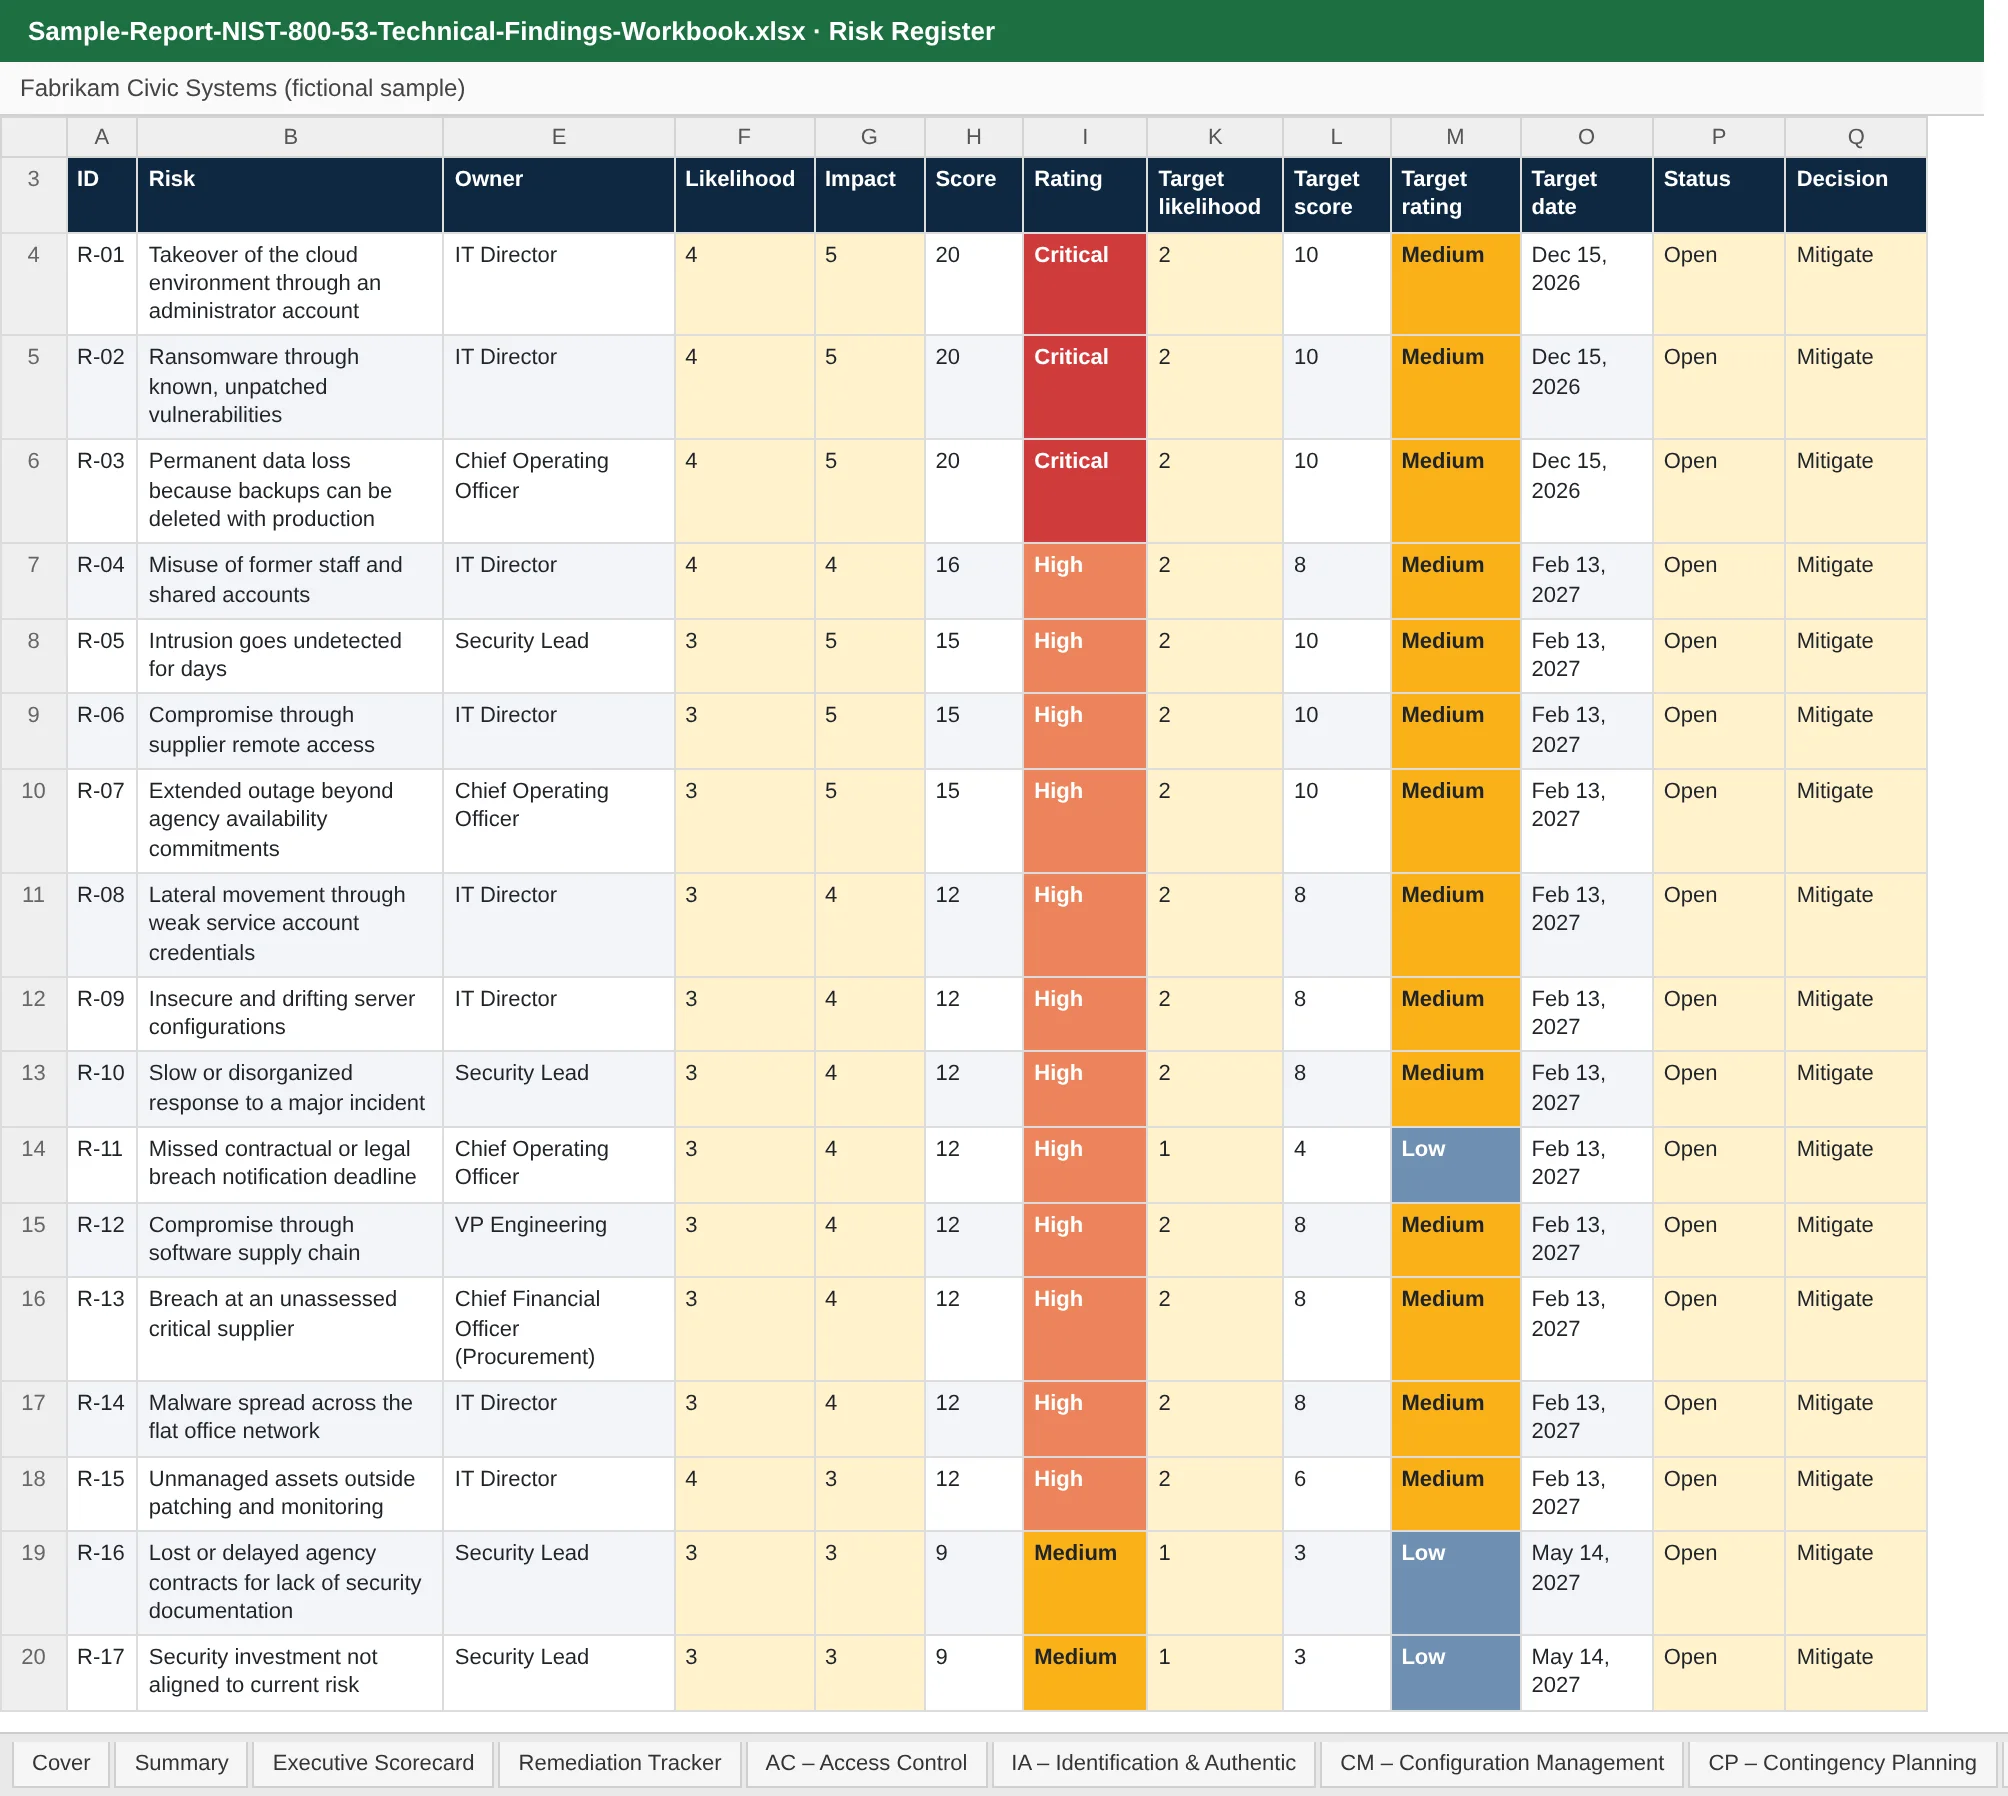
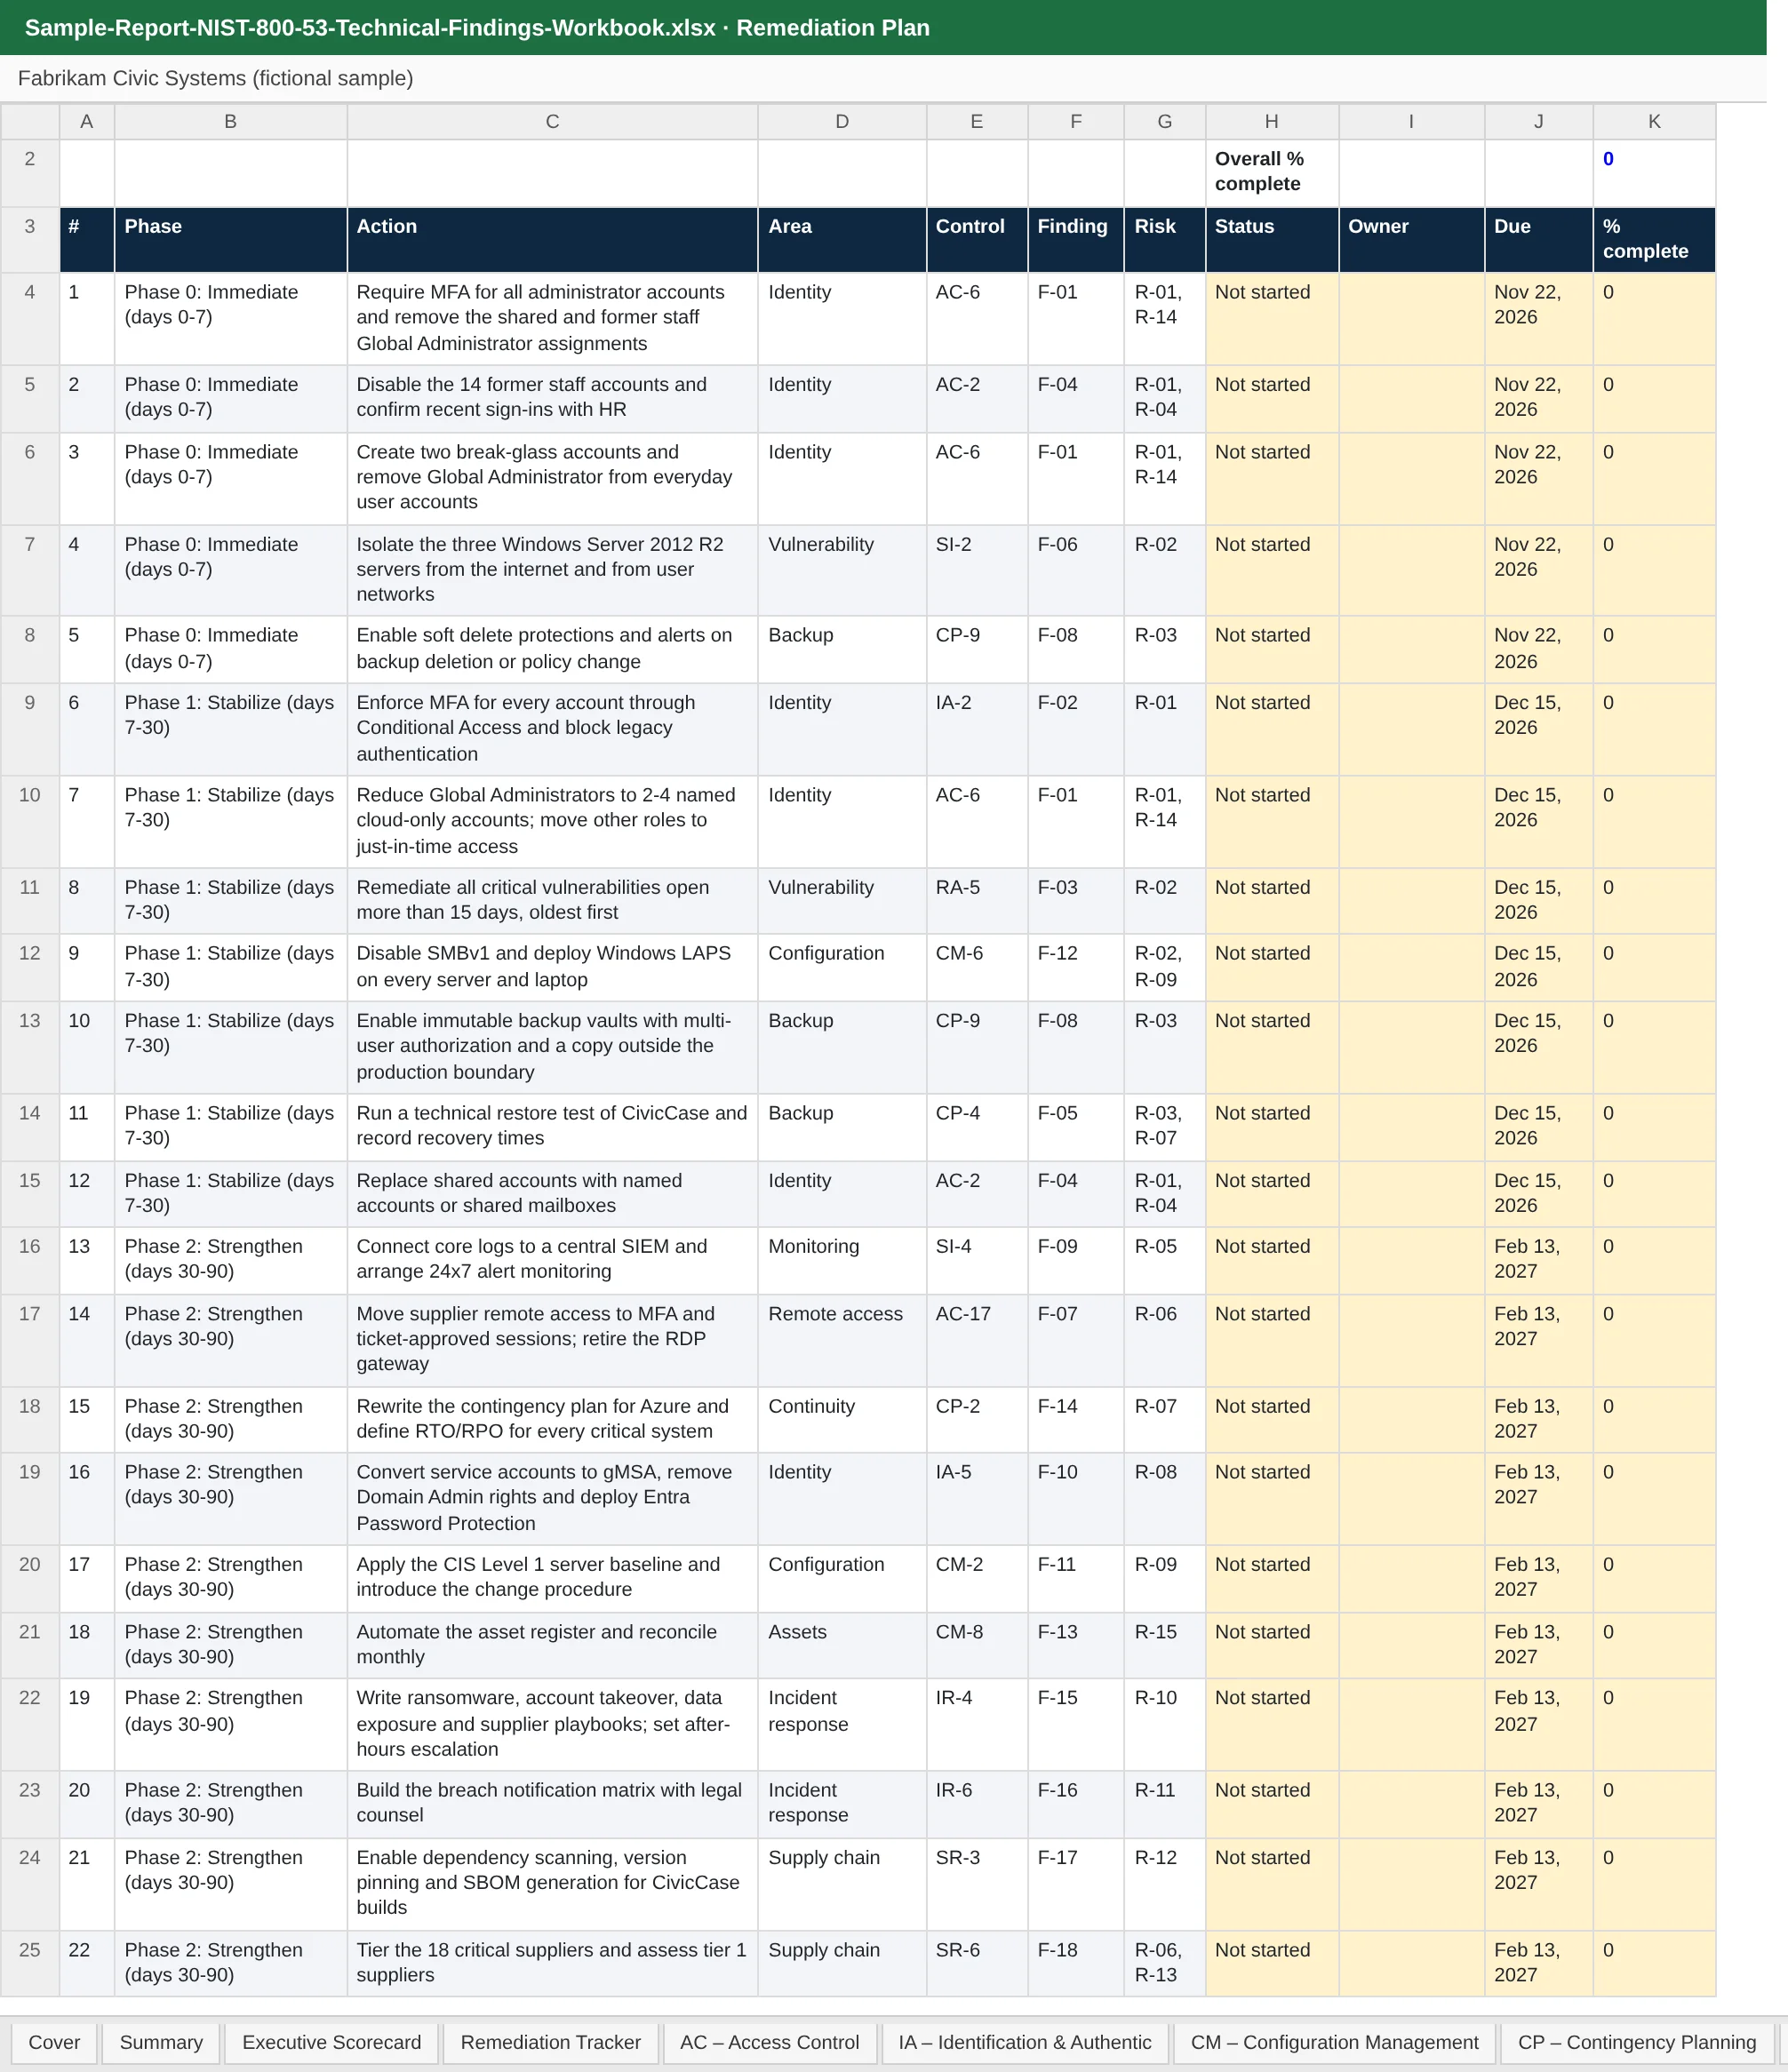
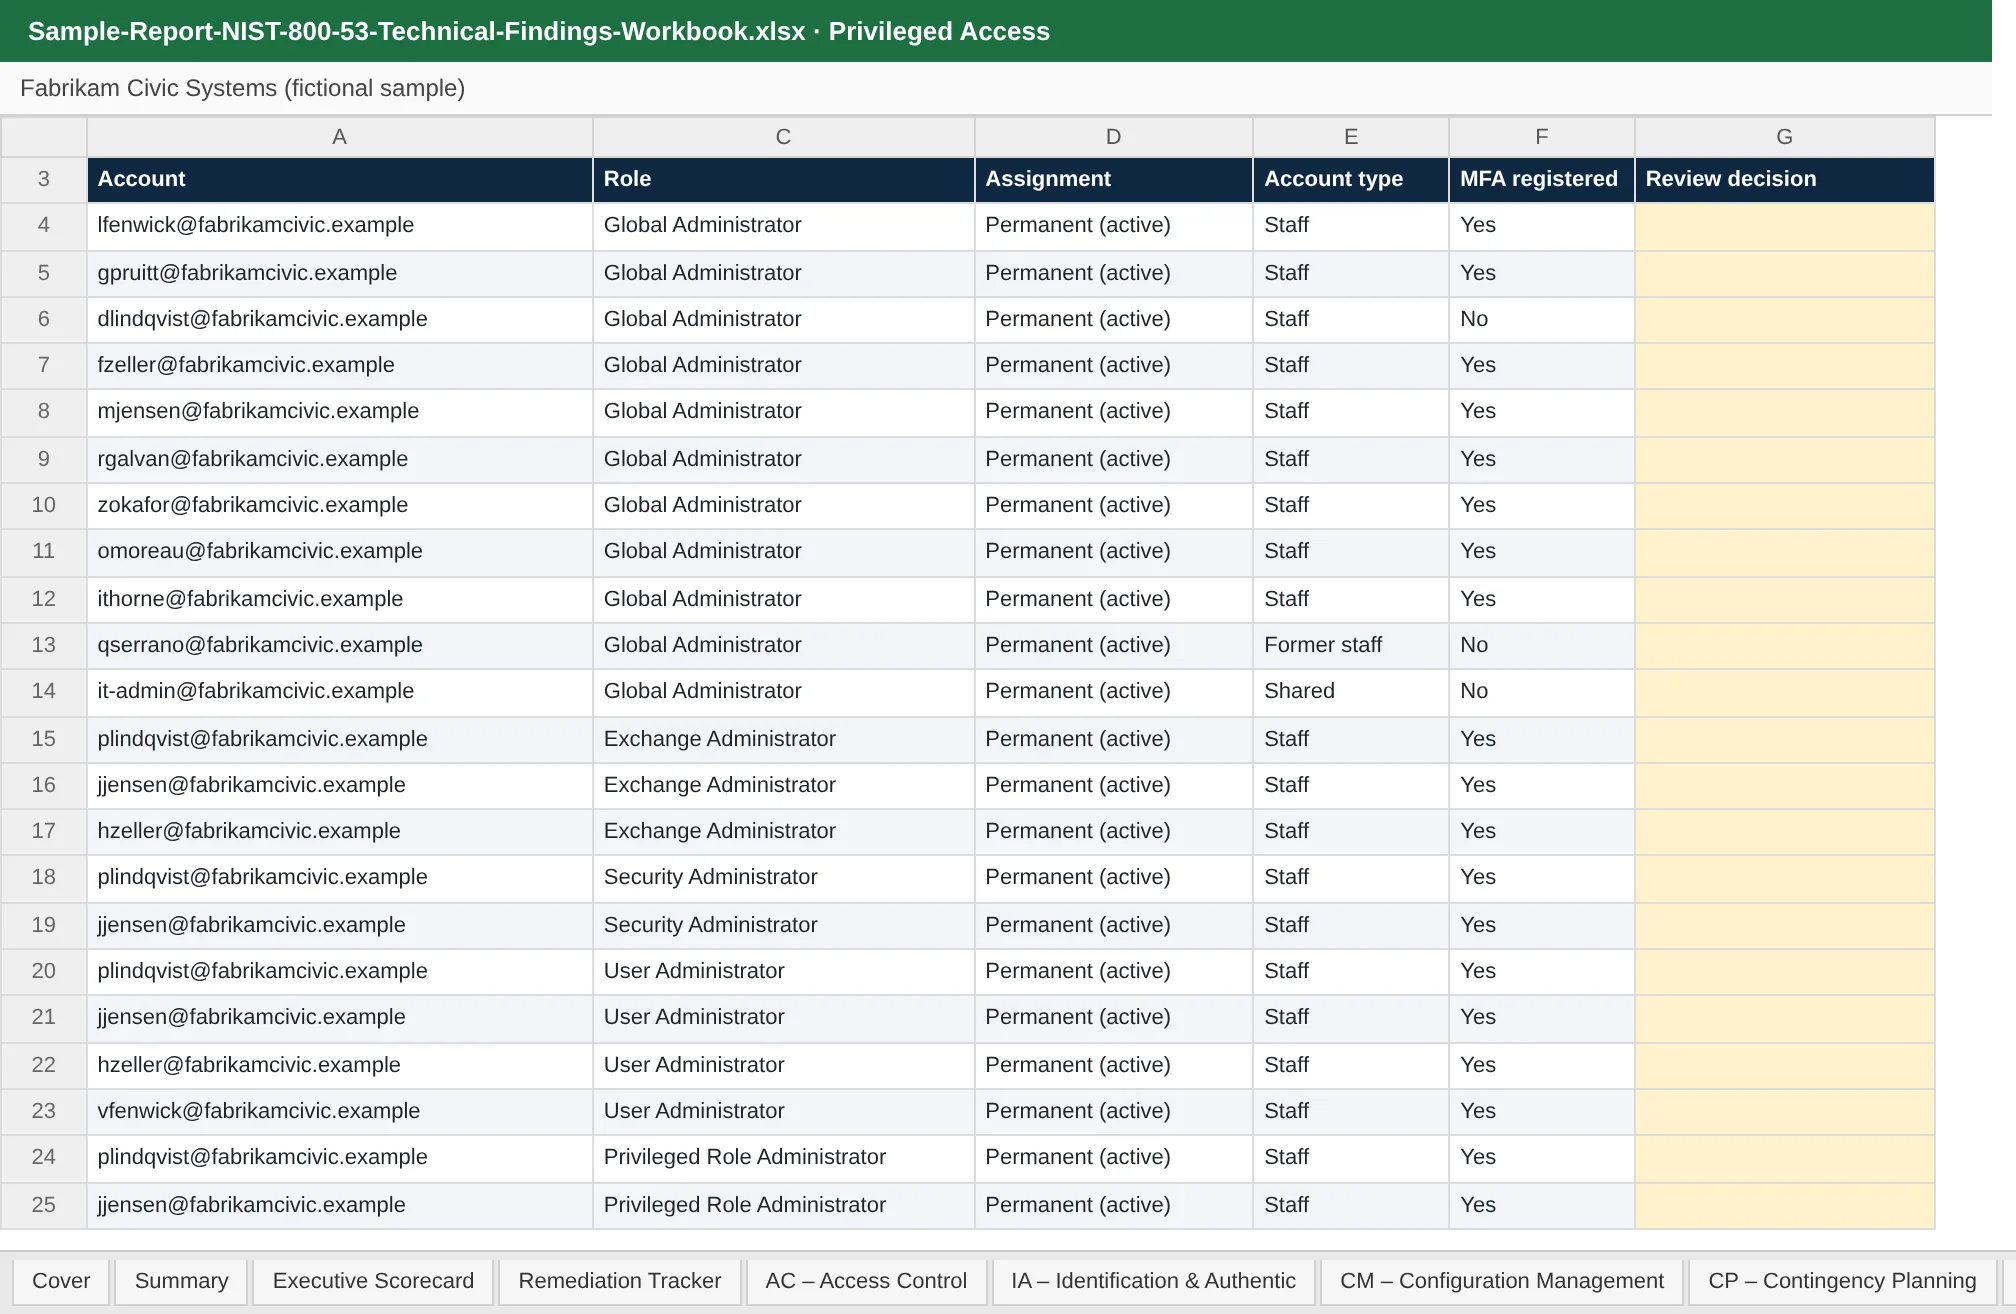
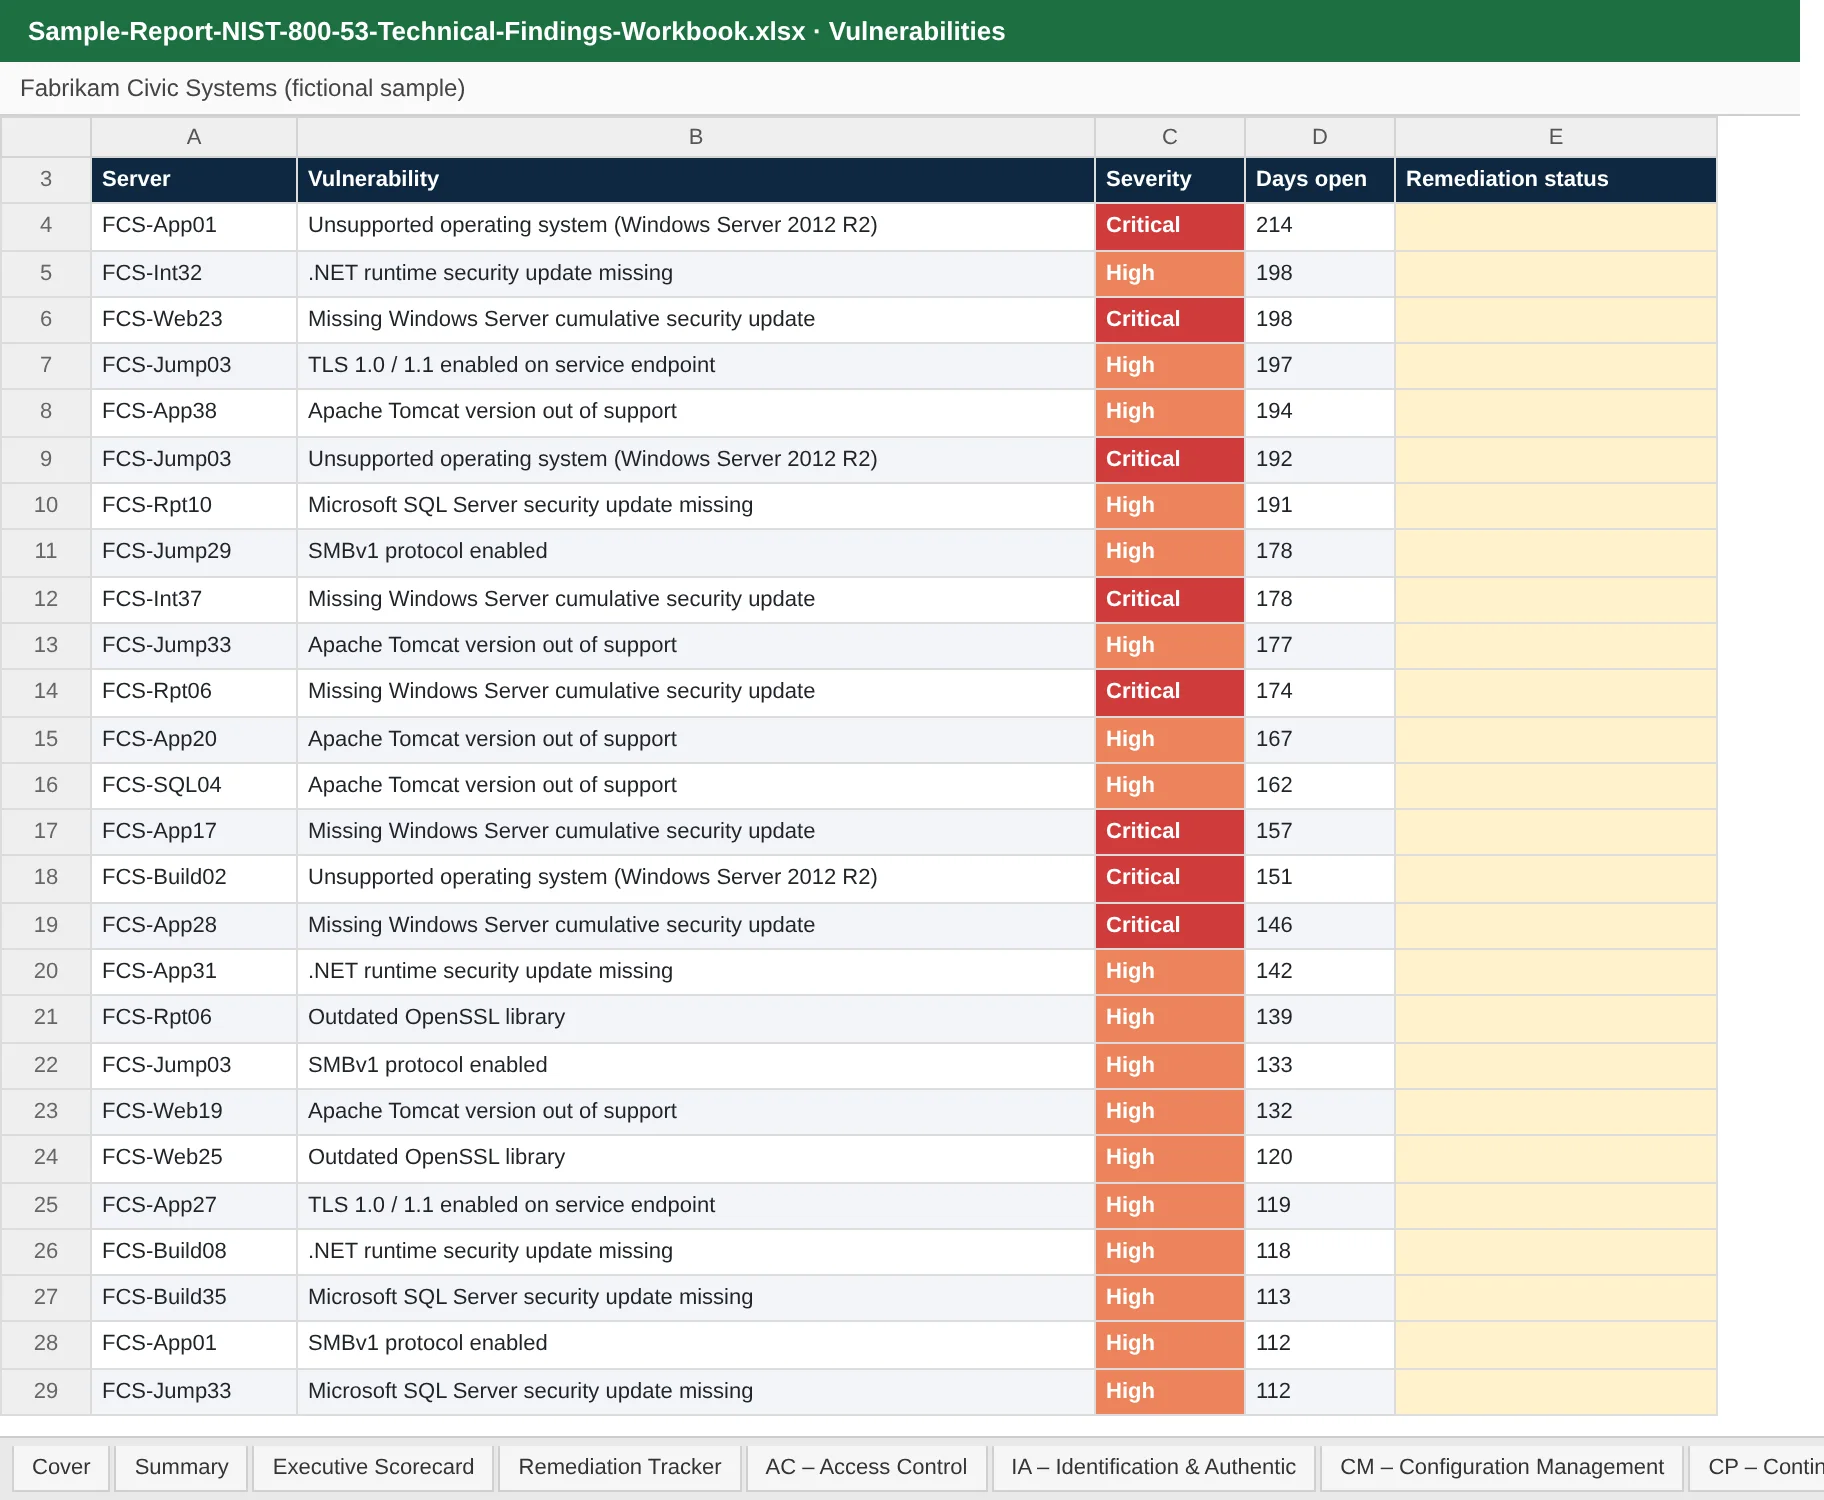
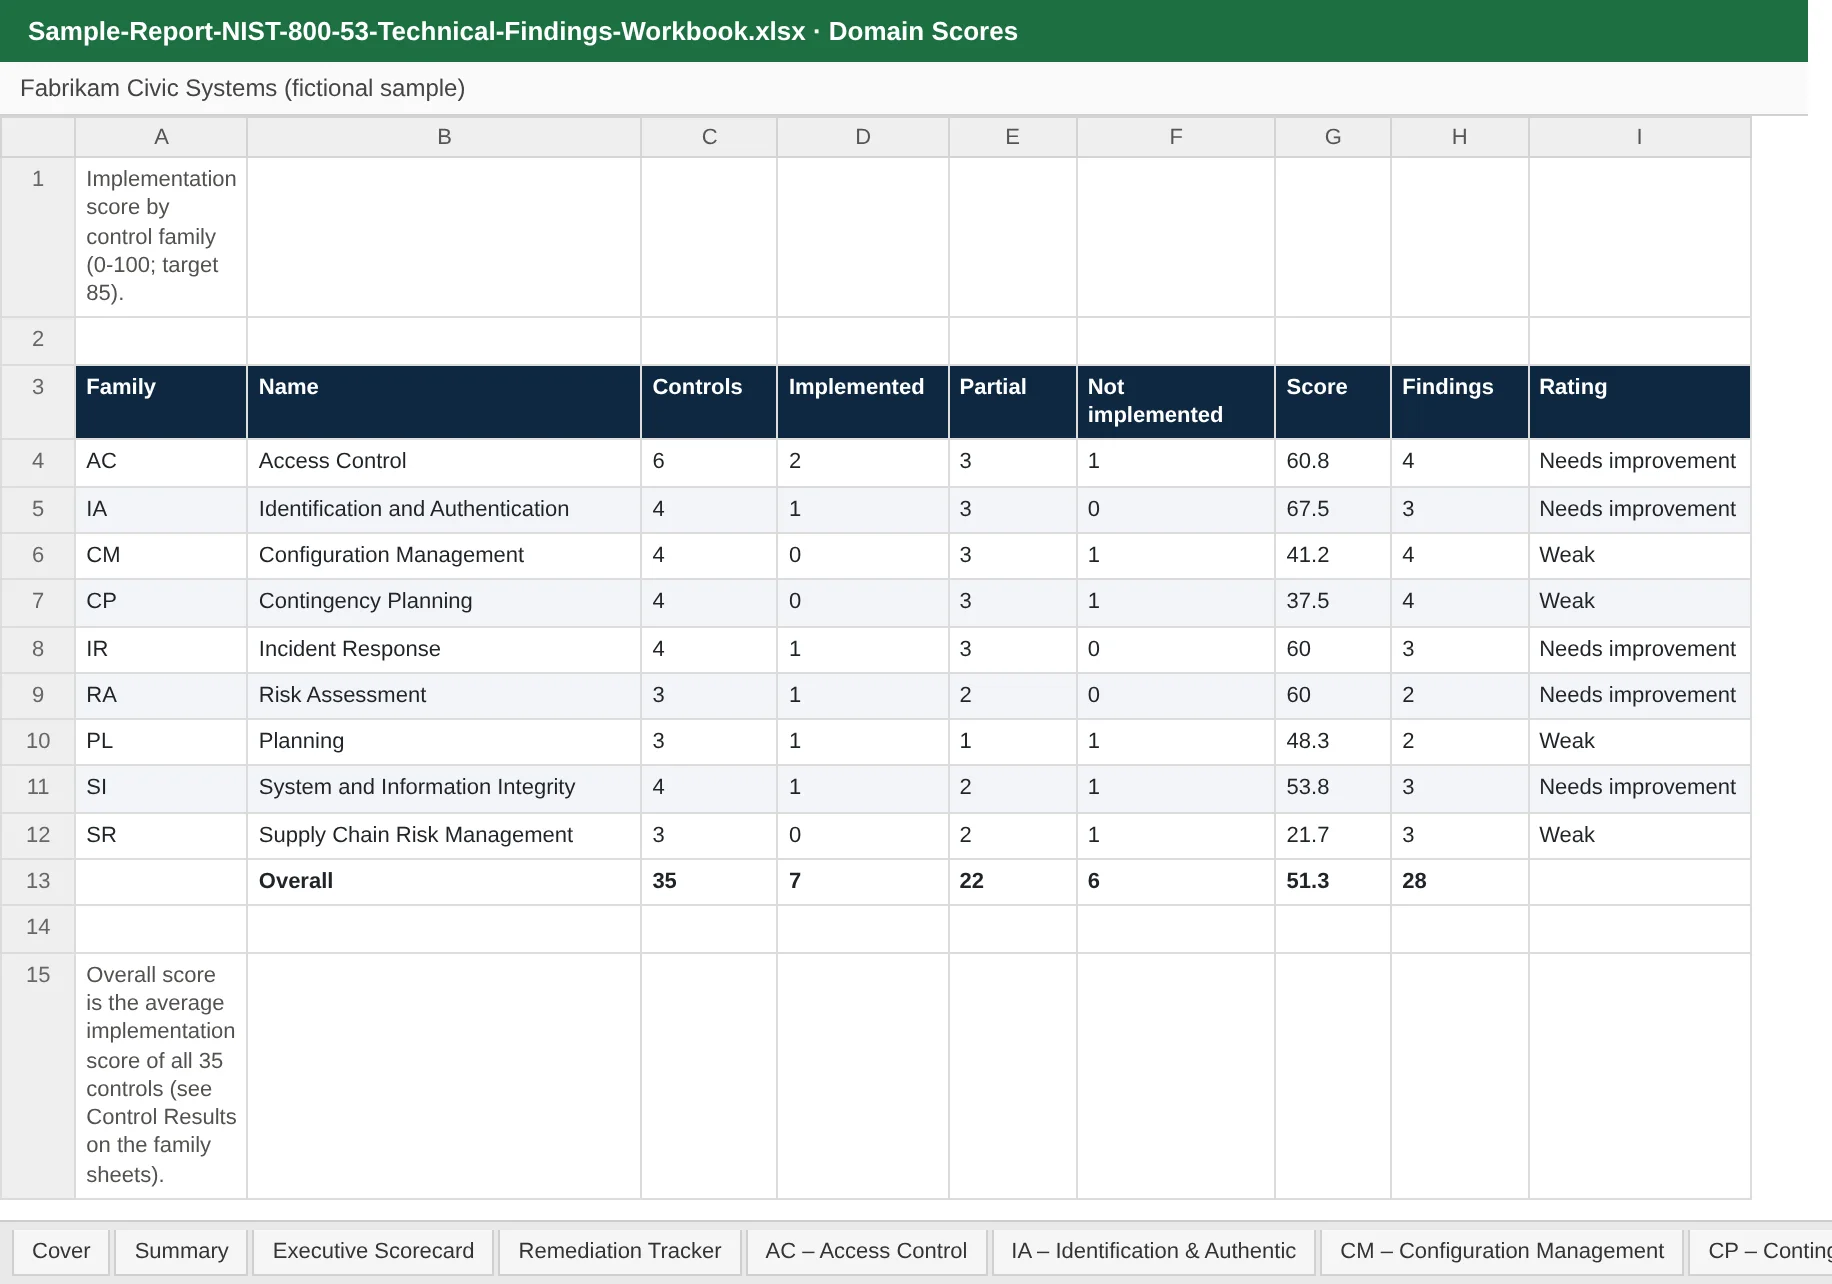
Click the page in the centre to open it full size, then zoom in to read every line.
Want this for your own system?
Book a short scoping call. We will confirm your system, your baseline and a fixed price in writing before any work starts.
One gap, traced
How one finding flows through all five deliverables
Every number is consistent across the reports. Here is one control gap from the sample, followed from the technical finding to the row your team tracks.
Technical finding
Least Privilege, Critical: 11 permanent Global Administrators, including a shared account and a former employee.
Business risk
Takeover of the cloud environment through an administrator account: score 20 today, 10 after treatment.
Roadmap actions
Actions 1 and 3 in the first seven days, action 7 by day 30: fewer administrators and just-in-time access.
Tracked to closure
The Findings and Remediation Plan sheets carry status, owner, due date and closure evidence.
Coverage
Control families covered in the sample
The sample is a focused assessment of 35 Moderate-baseline controls. The remaining families are recommended for a second phase, which the reports say plainly.
| Family | Controls | Implemented / partial / not | Score | Findings |
|---|---|---|---|---|
| AC Access Control | 6 | 2 / 3 / 1 | 61 | 4 |
| IA Identification and Authentication | 4 | 1 / 3 / 0 | 68 | 3 |
| CM Configuration Management | 4 | 0 / 3 / 1 | 41 | 4 |
| CP Contingency Planning | 4 | 0 / 3 / 1 | 38 | 4 |
| IR Incident Response | 4 | 1 / 3 / 0 | 60 | 3 |
| RA Risk Assessment | 3 | 1 / 2 / 0 | 60 | 2 |
| PL Planning | 3 | 1 / 1 / 1 | 48 | 2 |
| SI System and Information Integrity | 4 | 1 / 2 / 1 | 54 | 3 |
| SR Supply Chain Risk Management | 3 | 0 / 2 / 1 | 22 | 3 |
Overall implementation score 51.3 out of 100 (needs improvement). Families recommended for a second phase: AU, SC, AT, PS, PE, MP, MA, CA, SA and PM.
Related pages
Continue with the NIST 800-53 service
Service
NIST 800-53 assessment
Independent gap assessment against the controls that matter for your system and impact level.
See the assessment →
Pricing
What it costs
Assessments start at $3,500. See what sets the final price and what every engagement includes.
See pricing →
All samples
Every sample report
Sample reports for our Microsoft 365, cloud, firewall, compliance and risk assessments.
See all sample reports →
Who leads the assessment
Led by Ali Hassani, CISO
Certified CISO (C|CISO) and CISSP with 25+ years in IT, cybersecurity, compliance and infrastructure, and dozens of Microsoft and Cisco certifications, including MCSE, MCITP, MCSA Security, CCNP and CCNA.
Every NIST 800-53 assessment is planned, performed and signed by Ali. The reports you receive look like this sample: consistent numbers, plain language for leadership, and enough technical detail for your team to fix each gap.
FAQ
Questions about the sample report
Is the sample report based on a real client?
No. Fabrikam Civic Systems is a fictional organization. Every name, account, server, supplier and figure in the sample is invented for illustration and does not describe any real customer.
Will my report look the same?
Yes. You receive the same five deliverables in the same format, with your own system, controls, findings, risks and roadmap. The number of pages depends on the number of controls in scope.
How many controls does the sample cover?
The sample is a focused assessment of 35 Moderate-baseline controls in nine families. A full Moderate-baseline assessment covers 287 controls and enhancements and produces longer technical and workbook deliverables.
Do we get Word and Excel files, or only PDFs?
Both. The four reports come as editable Word documents and PDFs, and the findings workbook is an Excel file your team keeps working in.
Can we share the report with our customers?
Yes. Many clients share the Executive Security Report or Risk Register with government or enterprise customers. The reports are marked confidential, so share them under your normal agreements.
How much does an assessment like this cost?
NIST 800-53 assessments start at $3,500. The final fixed price depends on the number of systems, the baseline and the controls in scope, and is confirmed in writing after a scoping call.
Does the report certify compliance?
No. It is an independent assessment. It does not certify compliance, it is not a FedRAMP third-party assessment and it is not an authorization decision.
NIST SP 800-53 series · Page 8 of 10
Get these five deliverables for your own system
Book a short scoping call and receive a written scope and fixed price before any work starts.
Or call 949-777-5567