
FROM $3,500NIST 800-53 assessment pricing
NIST 800-53 assessment cost: from $3,500
A fixed price confirmed in writing after a short scoping call, with all five deliverables included.
How pricing works
A fixed price, agreed before any work starts
NIST 800-53 assessments start at $3,500. Because SP 800-53 assessments range from a focused review of a few families to a full Moderate or High baseline across several systems, we confirm the final fixed price in writing after a short scoping call, before any work begins.
The price covers the whole engagement: scoping, evidence review, interviews, configuration review and sampling, the five deliverables and a readout with your leadership and IT team. There is no hourly billing and no charge for follow-up questions about the reports.
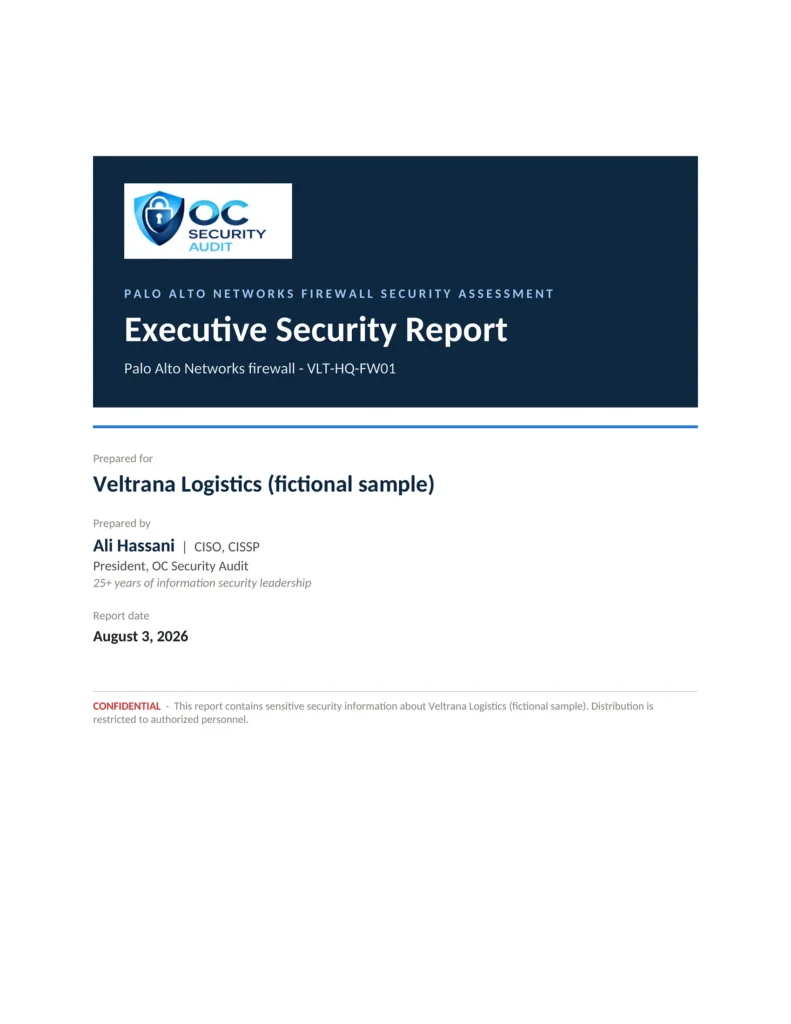
To see exactly what you receive, open the sample report, built for a fictional company. To understand the service itself, read about the NIST 800-53 assessment.
- Starts at $3,500
- Fixed price confirmed in writing
- Five deliverables always included
- Readout with leadership and IT
What sets the price
The factors that decide your fixed price
| Factor | Why it matters | Ask yourself |
|---|---|---|
| Number of systems | Each system has its own boundary, categorization and evidence | Is this one platform, or several separate systems? |
| Baseline | Moderate selects 287 controls and enhancements, High 370, Low 149 | What is the FIPS 199 impact level? |
| Controls in scope | A focused set of families costs less than a full baseline | Do customers ask about specific families first? |
| Evidence readiness | Current plans and exports shorten the work | Do you have a system security plan and recent exports? |
| Locations | Remote work is standard; on-site visits are available | Do you want on-site interviews in Southern California? |
| Add-ons | System security plan writing and POA&M development are separate services | Do you need the plan written, not only assessed? |
Typical scopes
Three common ways to scope the assessment
Every proposal is fixed price. These examples show how scope changes the work, not a price list.
Focused assessment
Selected families where customers ask first, such as Access Control, Identification and Authentication, Contingency Planning and Incident Response. The sample report covers 35 controls in nine families. Starts at $3,500.
Full Moderate baseline
All 287 Moderate-baseline controls and enhancements for one system, with tailoring confirmed. Quoted after scoping.
High baseline or several systems
High-impact systems, several system boundaries or a combined assessment and plan writing. Quoted after scoping.
Included in every engagement
What the price always includes
| Included | Details |
|---|---|
| Scoping call | System boundary, impact level, control set and timeline agreed in writing |
| Assessment work | Document review, interviews, configuration review and sampling for each control in scope |
| Executive Security Report | Score, top risks, posture by family, priority actions and decisions for leadership |
| Technical Security Report | A finding card for every gap with fix and validation steps |
| Risk Register | Business risks scored and mapped to findings, with treatment and target dates |
| Next Steps and Security Roadmap | 180-day plan in four phases with projects and effort |
| Technical Findings Workbook | Excel workbook with live formulas and status columns for your team |
| Readout | A walkthrough with leadership and IT, plus answers to follow-up questions |
This is an independent assessment. It does not certify compliance, it is not a FedRAMP third-party assessment, and it is not an authorization decision; those remain with your authorizing official or customer.
Related pages
Before you book
Service
NIST 800-53 assessment
Independent gap assessment against the controls that matter for your system and impact level.
See the assessment →
Sample
See the sample report
Every page of the five deliverables, built for a fictional company, page by page.
Open the sample →
Next step
Talk to Ali about your scope
A short call to agree on the system, the baseline and a fixed price before any work starts.
Schedule a consultation →
Who leads the assessment
Led by Ali Hassani, CISO
Certified CISO (C|CISO) and CISSP with 25+ years in IT, cybersecurity, compliance and infrastructure, and dozens of Microsoft and Cisco certifications, including MCSE, MCITP, MCSA Security, CCNP and CCNA.
Ali scopes every NIST 800-53 assessment personally and puts the fixed price in writing, so you know the cost and the deliverables before you commit.
FAQ
Questions about this page
How much does a NIST 800-53 assessment cost?
Our NIST 800-53 assessments start at $3,500. The final fixed price depends on the number of systems, the baseline and the controls in scope, and is confirmed in writing after a short scoping call.
Is the price fixed or hourly?
Fixed. Once we agree on the scope, the price does not change unless you ask to add systems or controls.
What is included in the price?
Scoping, the assessment work, five deliverables (executive report, technical report, risk register, roadmap and findings workbook) and a readout with your team.
Is writing the system security plan included?
No. Writing or updating the system security plan and building a plan of action and milestones are separate services. We can quote them together with the assessment.
Do you charge for travel?
Remote assessments are standard. On-site work across Southern California is available; any travel is agreed in the written proposal before work starts.
NIST SP 800-53 series · Page 9 of 10
Sample reports
See exactly what the price includes
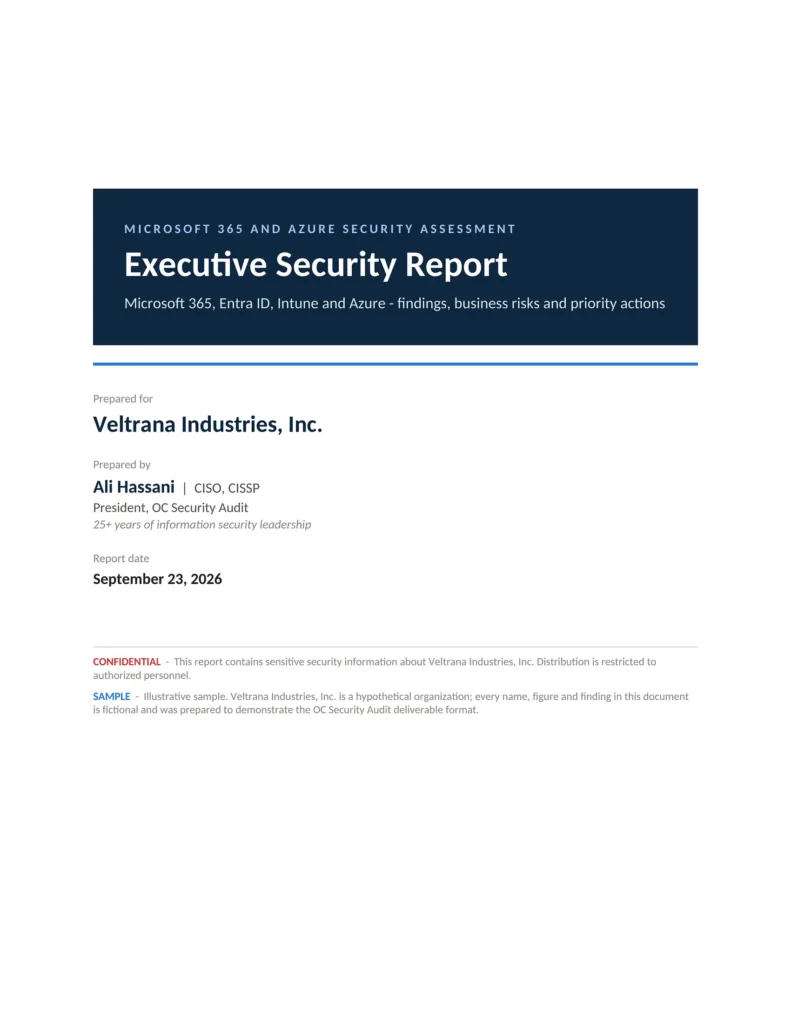
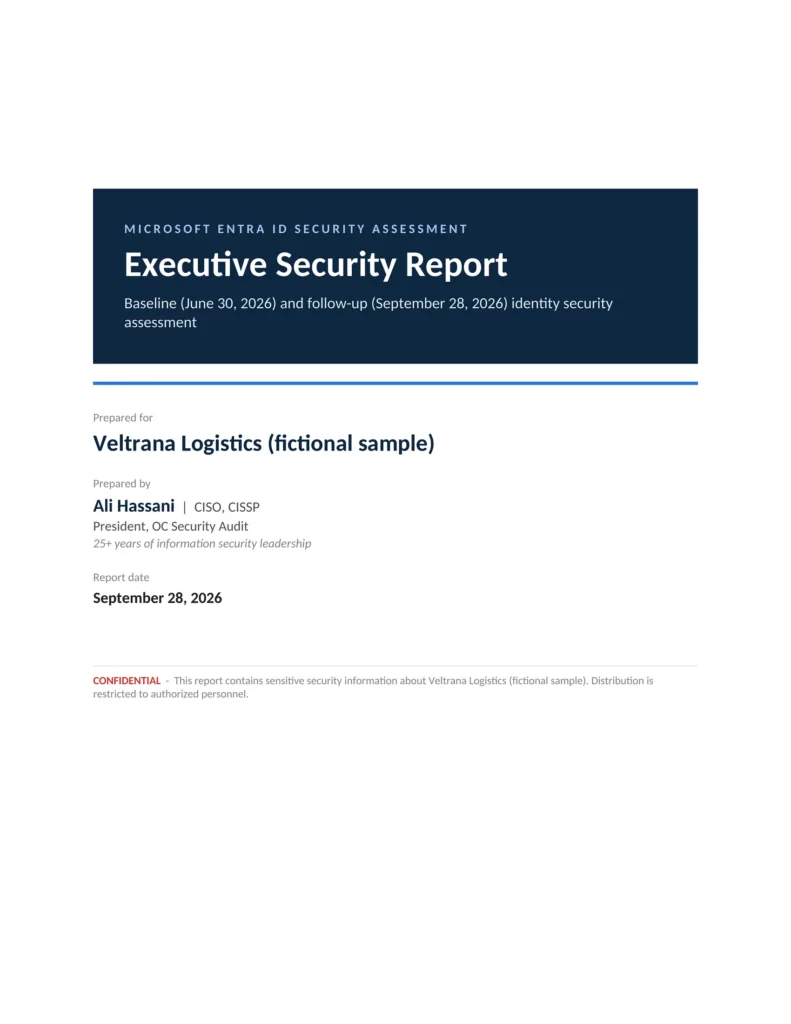
Every audit delivers an executive report, a technical report, a risk register, a security roadmap and a findings workbook. See real sample pages before you decide.
Get a fixed price for your NIST 800-53 assessment
Book a short scoping call. You will have a written scope and fixed price before any work starts.
Or call 949-777-5567