
Cybersecurity Risk Assessment Cost: From $3,500
A CISO-led cybersecurity risk assessment starts at $3,500. You receive a written scope and a fixed fee before any work begins.
No hourly billing, no surprises
Scope, deliverables and fee are agreed in writing. Nothing starts, and nothing is billed, until you approve it.
A scored register and a treatment plan
Every risk scored, owned and given a treatment date, in a report leadership can read.
Cybersecurity risk assessment pricing
Final pricing depends on your size, the number of locations and systems, and the regulations or contracts that apply.
Cybersecurity risk assessment
From $3,500one-time, fixed in writing- Scoping call
- Evidence review, read-only
- Scored risk register
- Executive summary
- Treatment plan with owners and dates
- Leadership walkthrough
Vendor risk review
From $3,500one-time, fixed in writing- Vendor inventory and tiering
- Security questionnaire review
- Evidence and contract terms check
- Vendor risk ratings
- Remediation requests
Ongoing risk management
From $3,500per month- Risk register reviews
- Treatment tracking
- Leadership and board reporting
- Reassessment after major changes
- Questionnaires and insurance renewals
A fixed quote before you commit
The cybersecurity risk assessment cost is set after a short scoping call. We confirm your size, your systems and locations, the regulations that apply and who on your side takes part.
You then receive a written scope and a fixed fee. Nothing starts, and nothing is billed, until you approve it.
Compare with GRC services pricing and vCISO advisory pricing, or see all pricing.
Six things that set the fee
Size
Number of employees, devices and user accounts in scope.
Locations
Offices, clinics or sites, and whether an on-site visit is needed.
Systems
Servers, cloud services, Microsoft 365, firewalls and key applications.
Regulations
HIPAA, PCI DSS, SOC 2, CCPA, IRS WISP or cyber insurance requirements.
Compliance consulting →Vendors
How many key vendors hold your data or reach your network.
Vendor risk →Depth
A leadership-level assessment, or one with technical configuration review.
Compare review types →What you receive for the fee
| Deliverable | What it contains | Who uses it |
|---|---|---|
| Executive summary | Overall risk picture, top five risks and the decisions needed. | Owners, executives, board |
| Risk register | Each risk scored for likelihood and impact, with an owner. | Leadership, IT lead |
| Treatment plan | Mitigate, transfer, accept or avoid, with target dates in 30, 90 and 180-day phases. | IT lead, IT provider |
| Evidence notes | What supports each finding, and what was out of scope. | IT lead, auditors, insurers |
| Walkthrough call | The report presented to leadership and IT, with owners agreed. | Everyone involved |
From first call to final report
Scoping call
We confirm size, systems, regulations and goals.
Written quote
A fixed fee and scope for your approval.
Assessment
Interviews, documents and read-only review.
Report and walkthrough
Scored risks, owners and a treatment plan.
See the work before you decide

Page 17 of 17: Risk assessment pricing
- 1. Cybersecurity risk assessment (hub)
- 2. How to perform a cyber risk assessment
- 3. Small-business risk assessment guide
- 4. Risk assessment vs. vulnerability scan, pen test and audit
- 5. Risk scoring: likelihood and impact
- 6. Cybersecurity risk register guide
- 7. Risk appetite, tolerance and acceptance
- 8. Cyber risk treatment plan
- 9. Risk assessment report guide
- 10. Business impact analysis guide
- 11. CISO-led cyber risk assessment
- 12. Cybersecurity risk management services
- 13. Third-party vendor risk management
- 14. Vendor risk management consulting
- 15. Risk assessment sample report
- 16. Risk assessment checklist
- 17. Risk assessment pricing (this page)

Led by Ali Hassani, CISO
Certified CISO (C|CISO) and CISSP with 25+ years in IT, cybersecurity, compliance and infrastructure, more than 100 business networks designed, implemented and secured, and dozens of Microsoft and Cisco certifications, including MCSE, MCITP, MCSA Security, CCNP and CCNA. Every risk assessment is scoped, priced and delivered by a certified CISO, not handed to a junior analyst.
Questions about risk assessment pricing
How much does a cybersecurity risk assessment cost?
A cybersecurity risk assessment starts at $3,500. The fee depends on your size, the number of locations and systems, and the regulations that apply. It is confirmed in writing before work begins.
What is included in the price?
A scoping call, evidence review, a scored risk register, an executive summary, a treatment plan and a walkthrough with leadership and your IT lead.
Do you need administrator access to our systems?
Where we review configurations we use read-only access. We do not change anything in your systems.
Is a vendor risk review included?
Key vendors are listed and rated in the assessment. A full review of individual vendors is a separate engagement that starts at $3,500.
Do you fix the issues you find?
We stay independent. If you want hands-on help, our partner IT Perfection can implement the fixes, or your own IT team or provider can.
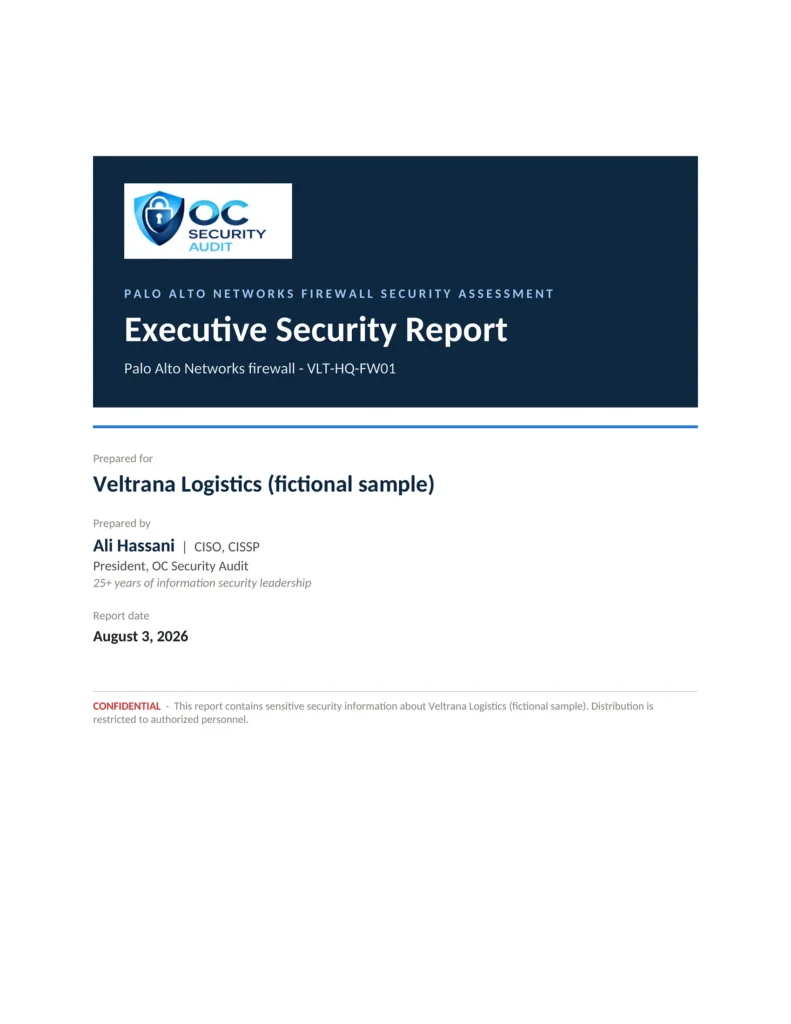
Sample reports
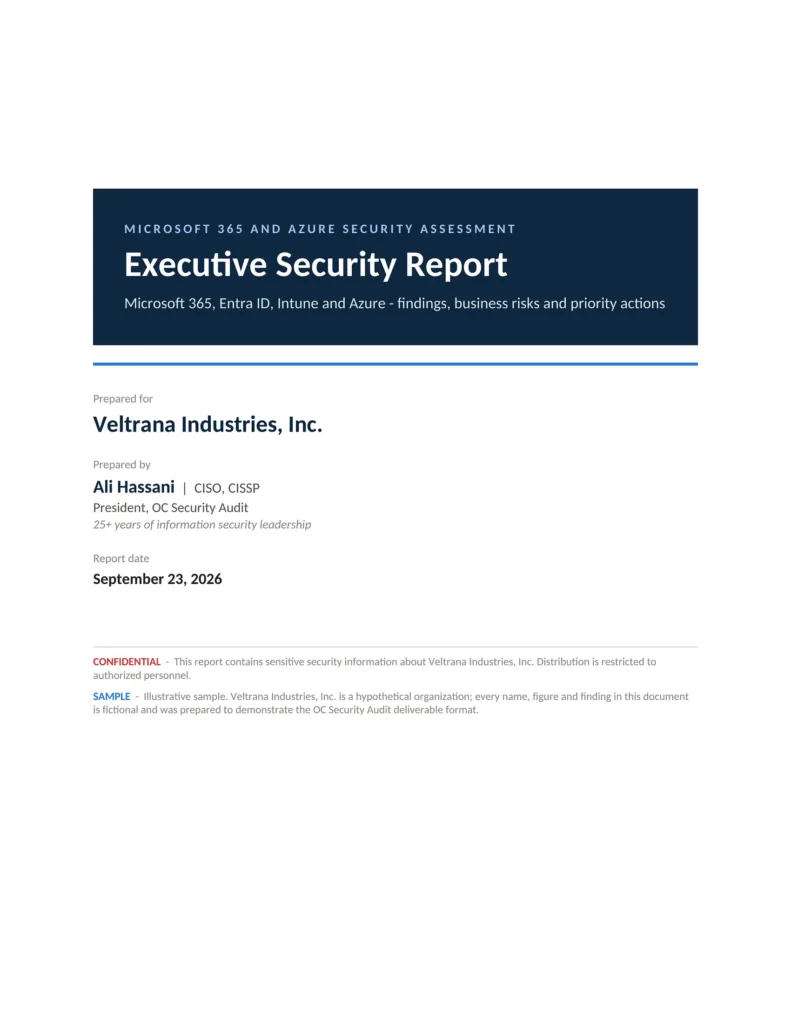
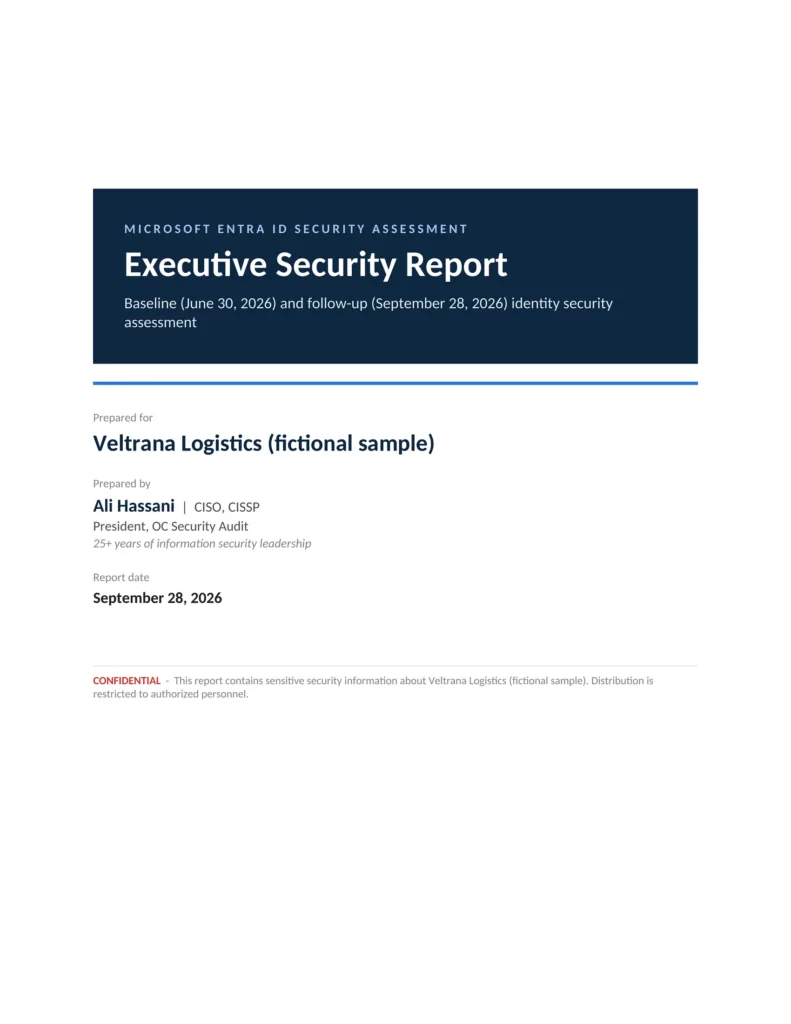
See exactly what the price includes
Every audit delivers an executive report, a technical report, a risk register, a security roadmap and a findings workbook. See real sample pages before you decide.
Get a fixed quote for your risk assessment
Schedule a consultation. A cybersecurity risk assessment starts at $3,500, confirmed in writing before work begins.
We assess and report cybersecurity risk and help you prepare for compliance reviews; we do not certify organizations or give legal advice. Irvine, Orange County and Southern California on-site; remote nationwide.