
Palo Alto Firewall Audit Sample Report
Real pages from all seven deliverables of a Palo Alto firewall audit, shown on a fictional logistics company: six reports and an Excel workbook.
A score your owner can follow
Score by area, top business risks and what to fund first, in plain language.
Evidence your firewall admin can act on
Every finding with the rule, interface or setting behind it, and the exact fix.
Six reports and an Excel workbook
141 controls in 13 areas, each finding mapped to NIST CSF 2.0 and ISO/IEC 27001:2022. The audit is read-only and includes a review of the last 7 days of firewall logs.
| Deliverable | What it contains | Who uses it |
|---|---|---|
| Executive Security Report | Score, top business risks, score by area, what works, priority actions and decisions, in plain language | Owner, CEO, board |
| Technical Security & Configuration Report | Every control with its result and evidence, detailed findings with the exact fix, framework mapping | Firewall administrators, MSP |
| Firewall Rulebase Review | Every security rule in order with zones, applications, profiles, hit counts and the issues found | Firewall administrators |
| Log Review & Threat Activity | Seven days of administrator sign-ins, configuration changes and threat detections | IT manager, security operations |
| Risk Register | Business risks rated by likelihood and impact, with treatment, owner and the findings behind each | Compliance, insurance, auditors |
| Next Steps & Security Roadmap | Four phases from 7-day containment to 180-day governance, grouped into projects | IT manager, vCISO |
| Technical Findings Workbook (Excel) | Findings, risks and actions to track, plus evidence tabs for rules, NAT, administrators, advisories and threats | Firewall administrators, MSP |
A fictional logistics company with one PA-3410
Every number in the pages below comes from a made-up company and illustrates the format only. Your report uses the evidence read from your own firewalls.
- Company
- Veltrana Logistics (fictional company)
- Firewall
- VLT-HQ-FW01: PA-3410 on PAN-OS 11.1.4-h7, single virtual system
- Rule base
- 20 security rules (1 disabled) and 5 NAT rules across 5 zones; untrust is the internet-facing zone
- Review
- August 3, 2026: read-only, from the live configuration, with the last 7 days of system, configuration and threat logs
- Result
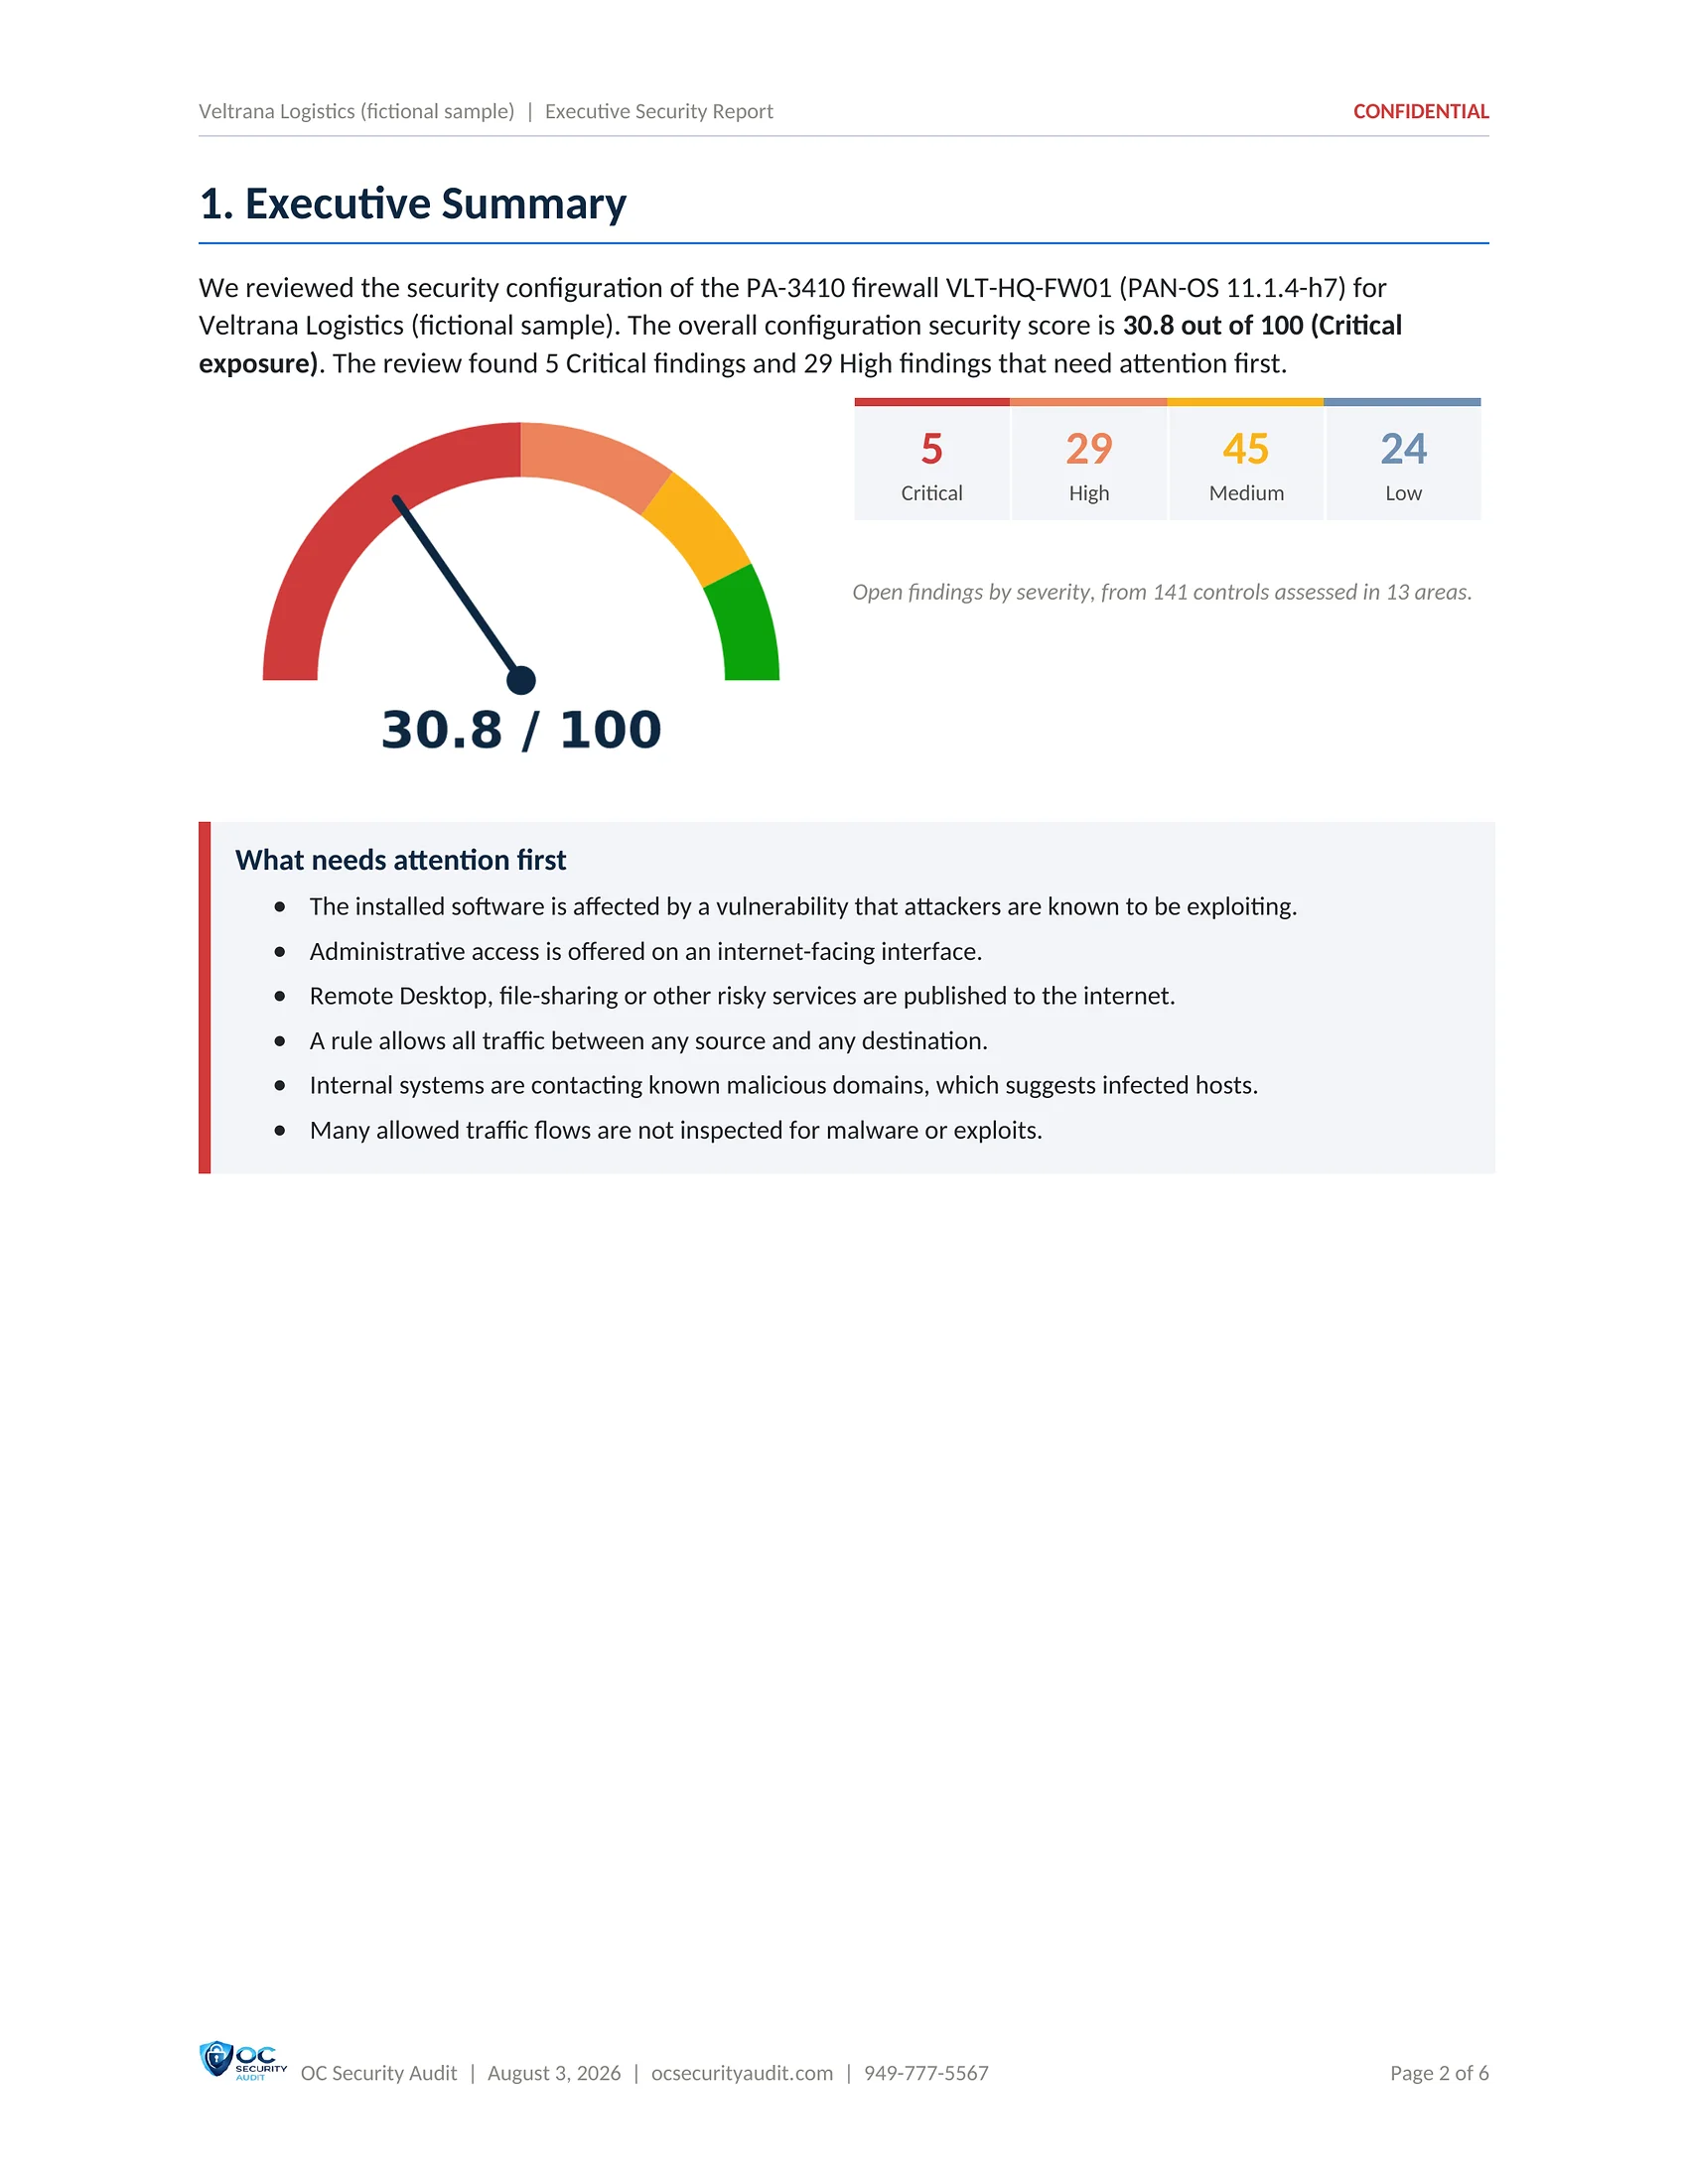
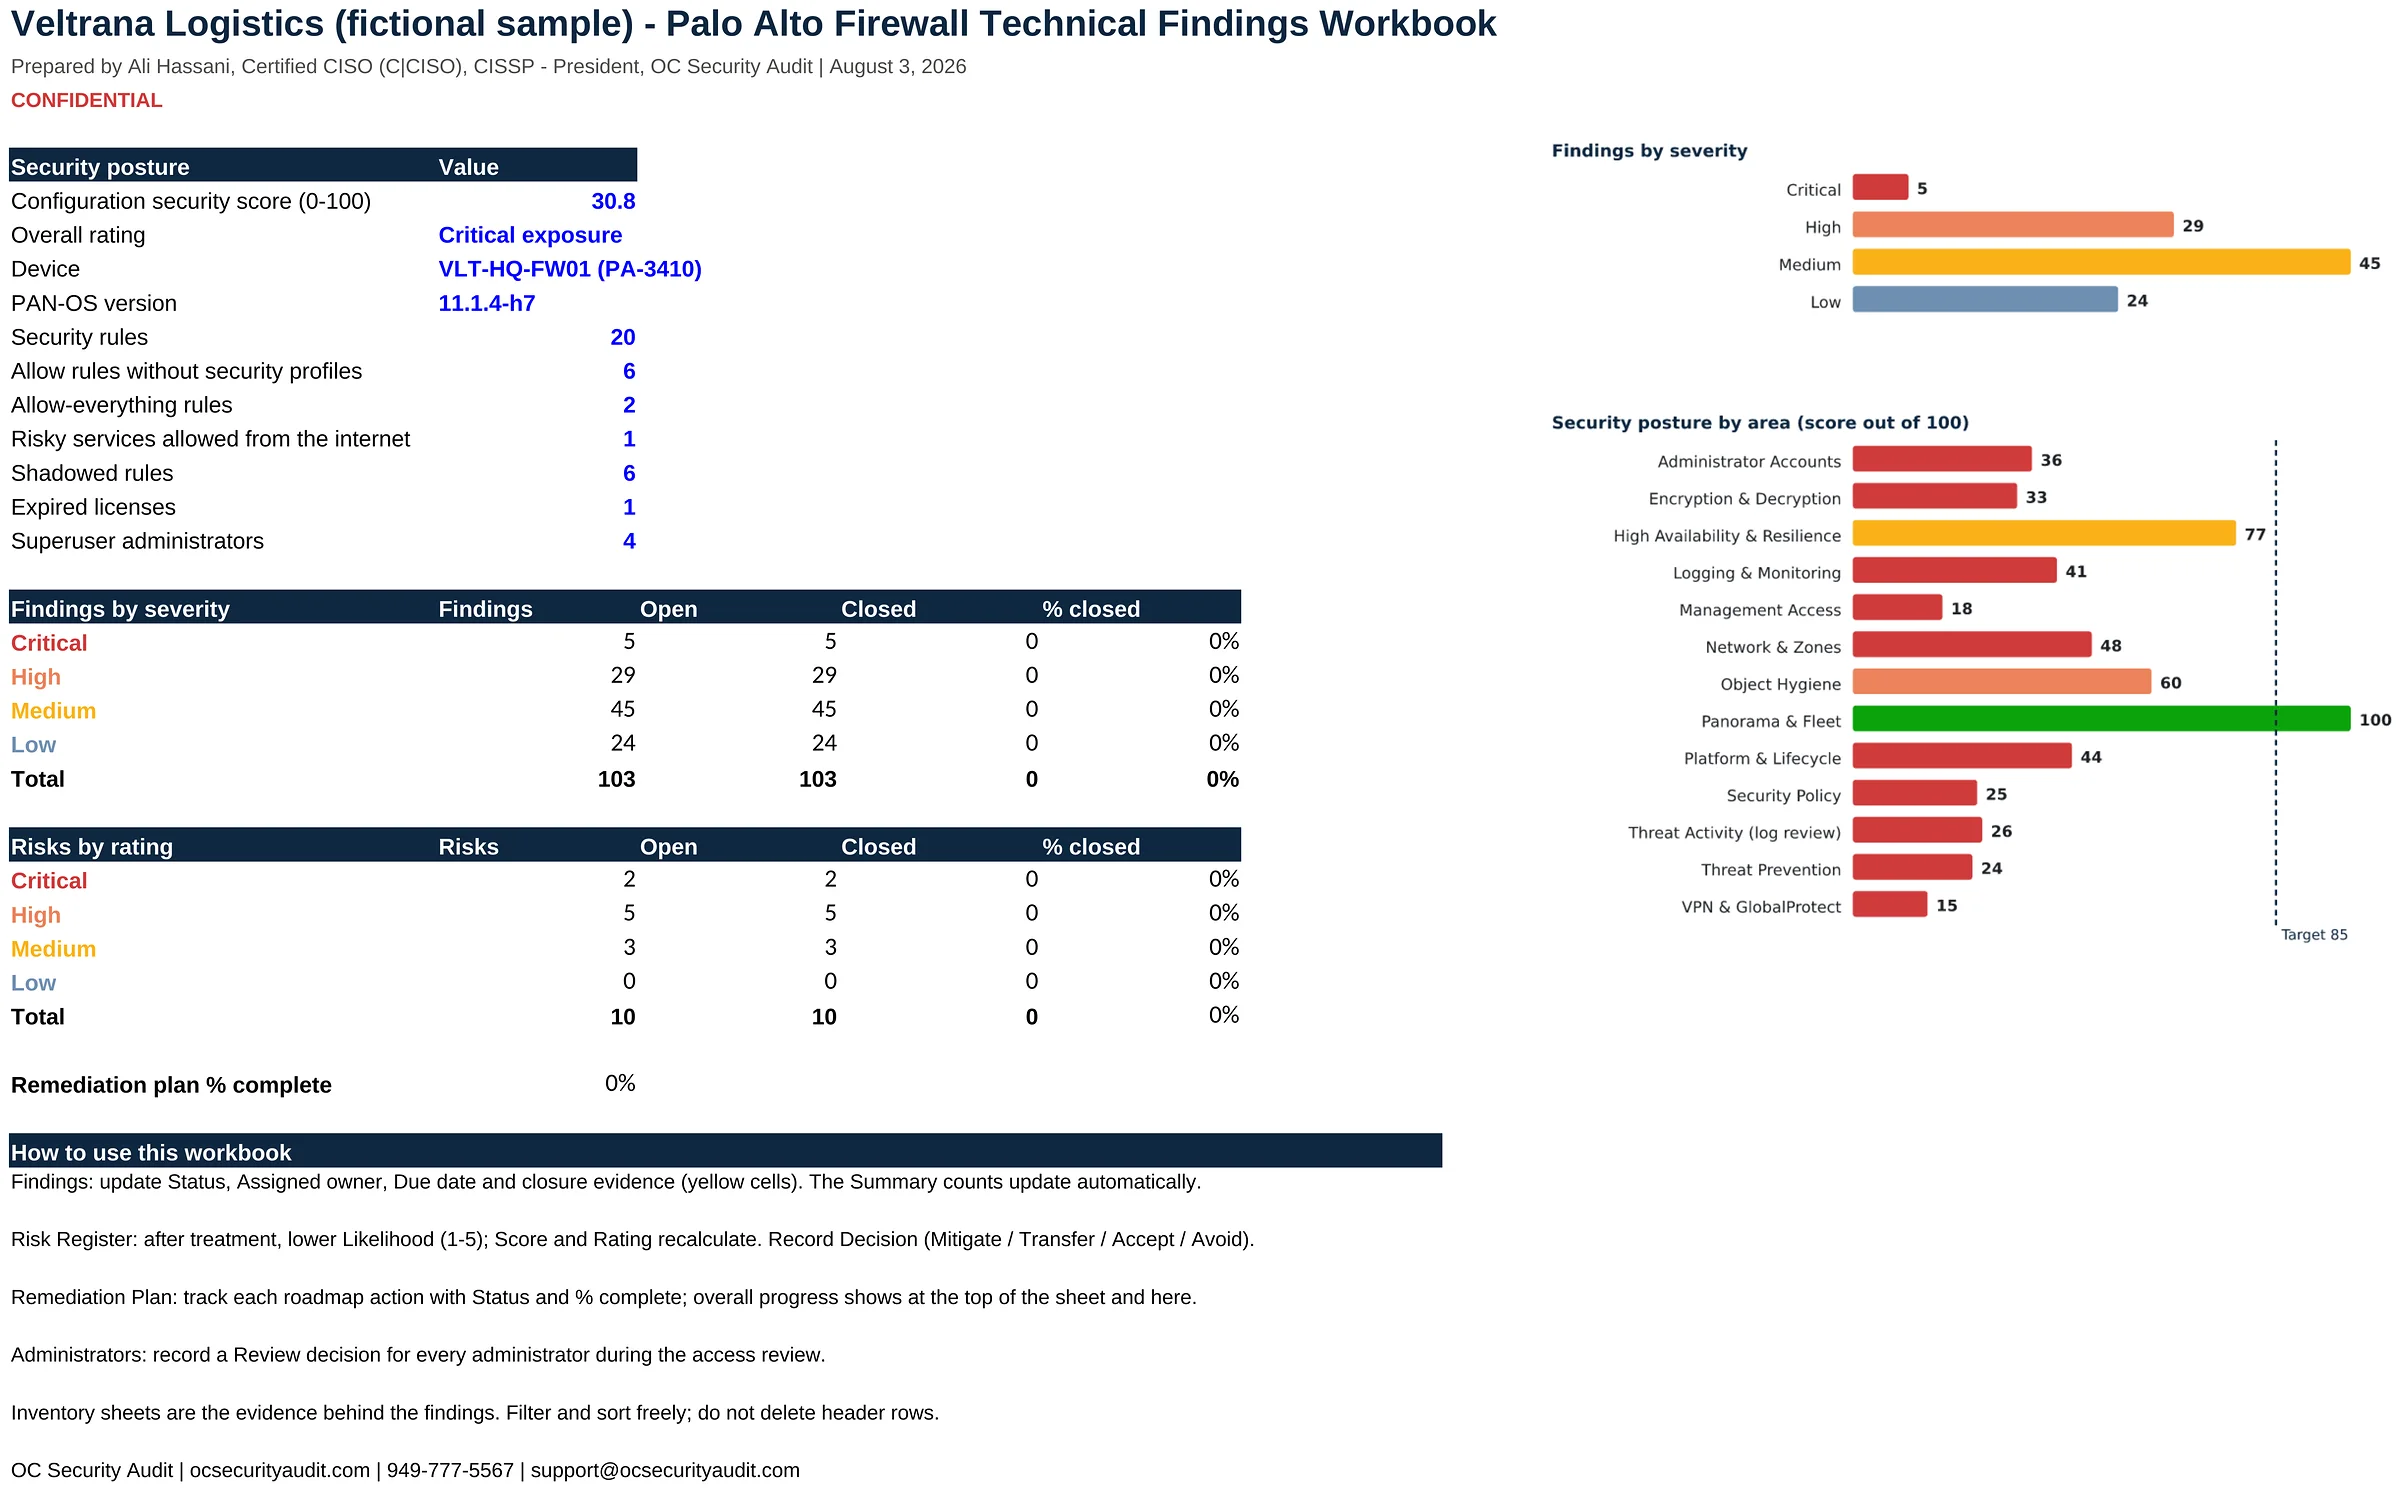
- Score 30.8 out of 100 (Critical exposure): 5 Critical, 29 High, 45 Medium and 24 Low open findings from 141 controls in 13 areas, rolled up into 10 business risks and 103 roadmap actions
Our deliverables
Six reports and an Excel workbook, shown page by page
These are real pages from the deliverables of a Palo Alto firewall audit, run on a fictional company. Each section below shows one deliverable: what it contains, who uses it and 59 sample pages in total that you can step through and open full size.
SAMPLE. Veltrana Logistics is a fictional company and every name, address and number in these pages is illustrative. Your reports use the evidence read, read-only, from your own firewalls.
Deliverable 1 of 7 · PDF · 6 pages
Executive Security Report
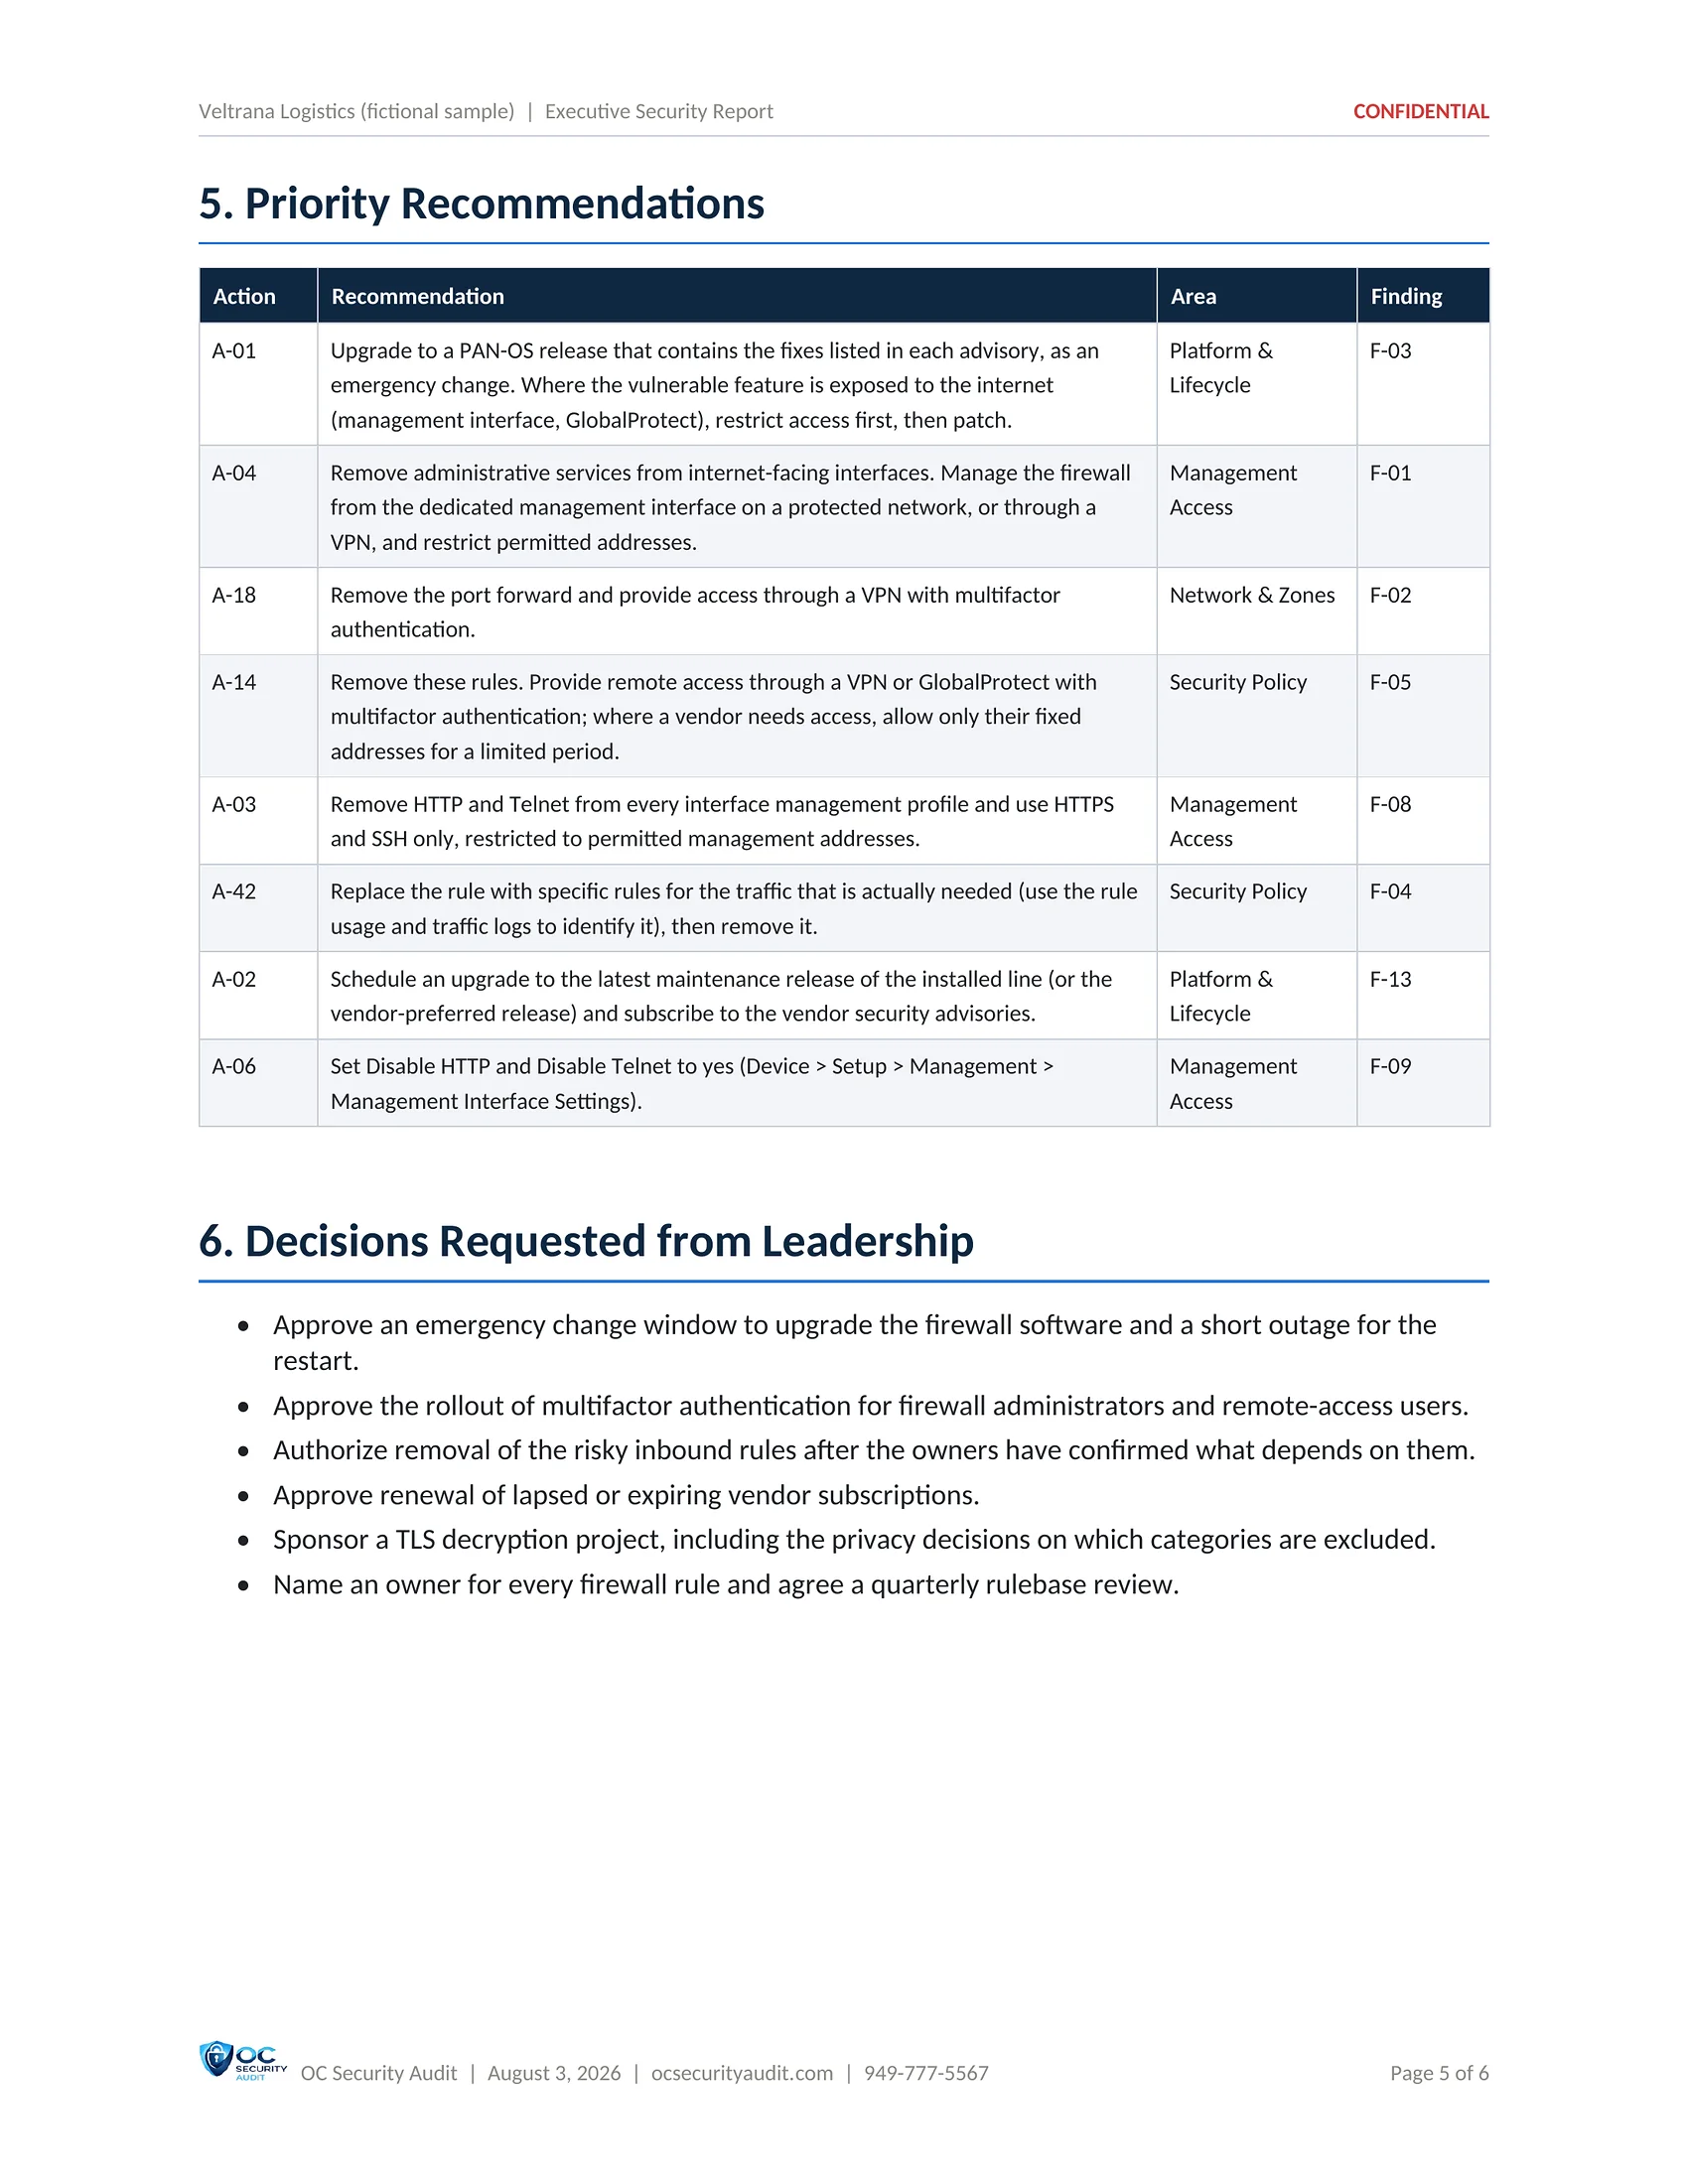
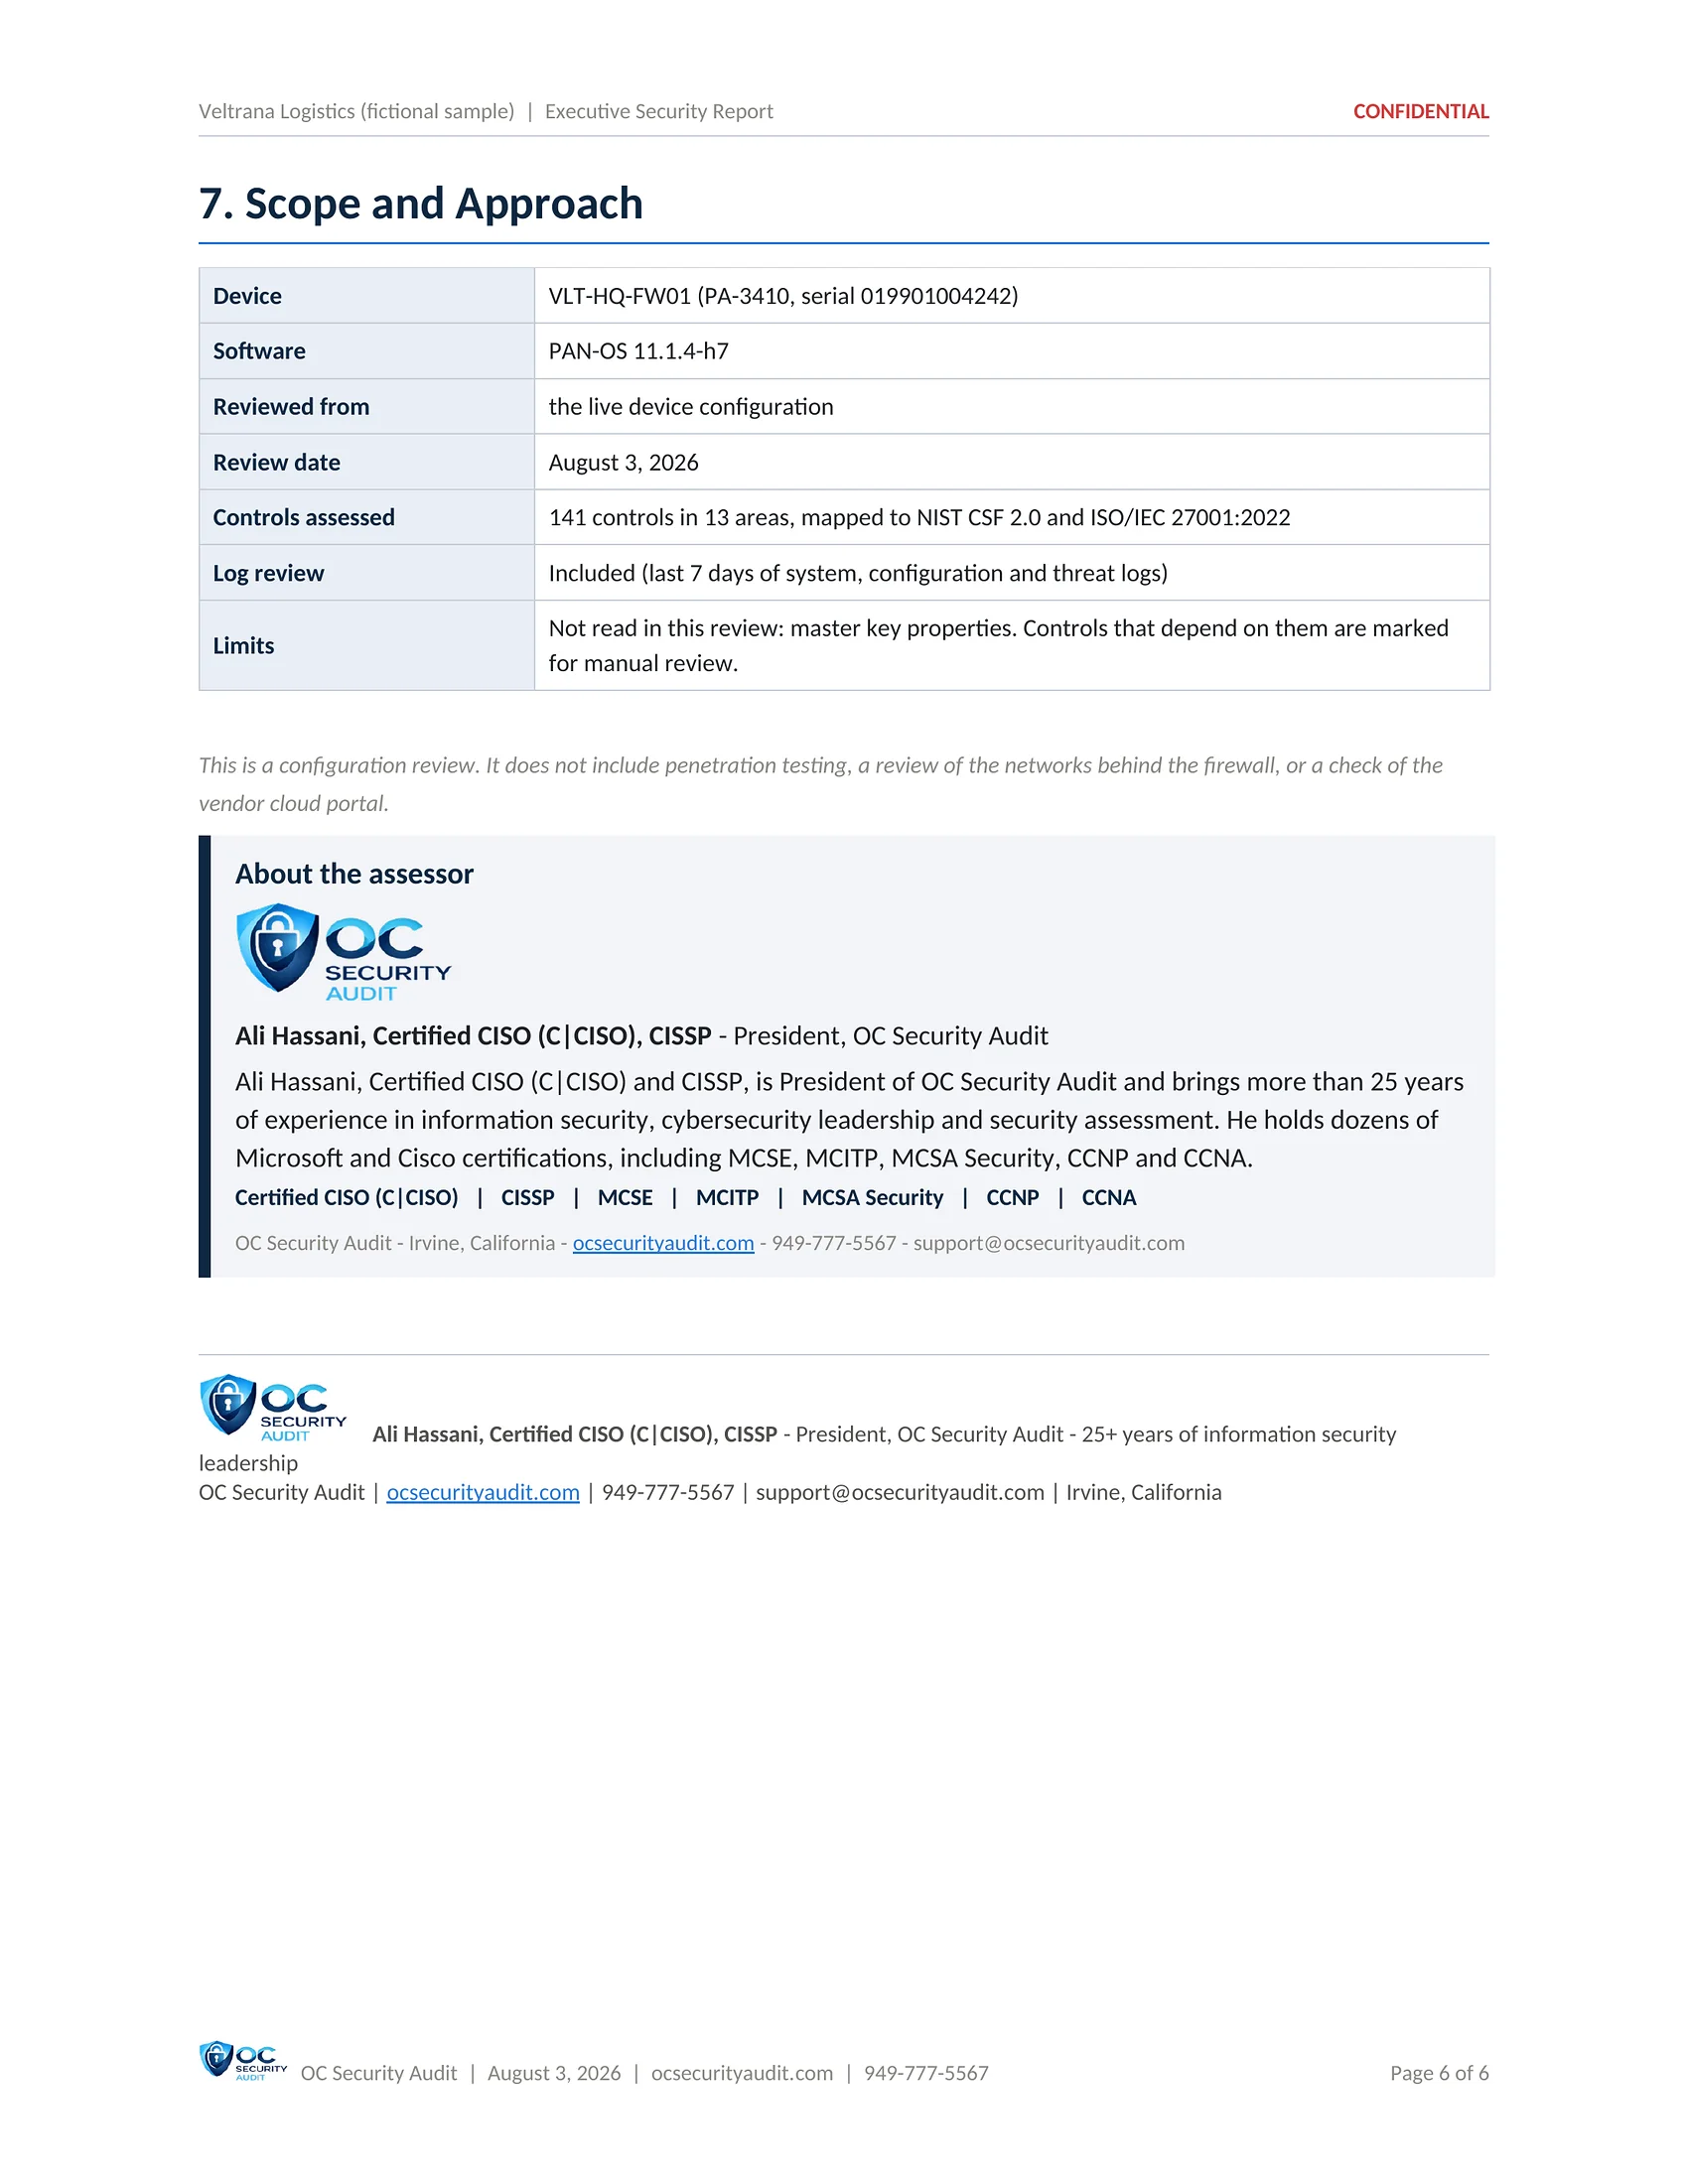
A short, plain-language report for the people who decide and pay. It gives one score for the firewall, the business risks behind it, how each area compares with the target, and the few actions to fund first.
Who uses it
Owner, CEO, board, cyber insurer
What is included
- Overall score and rating out of 100
- Open findings by severity
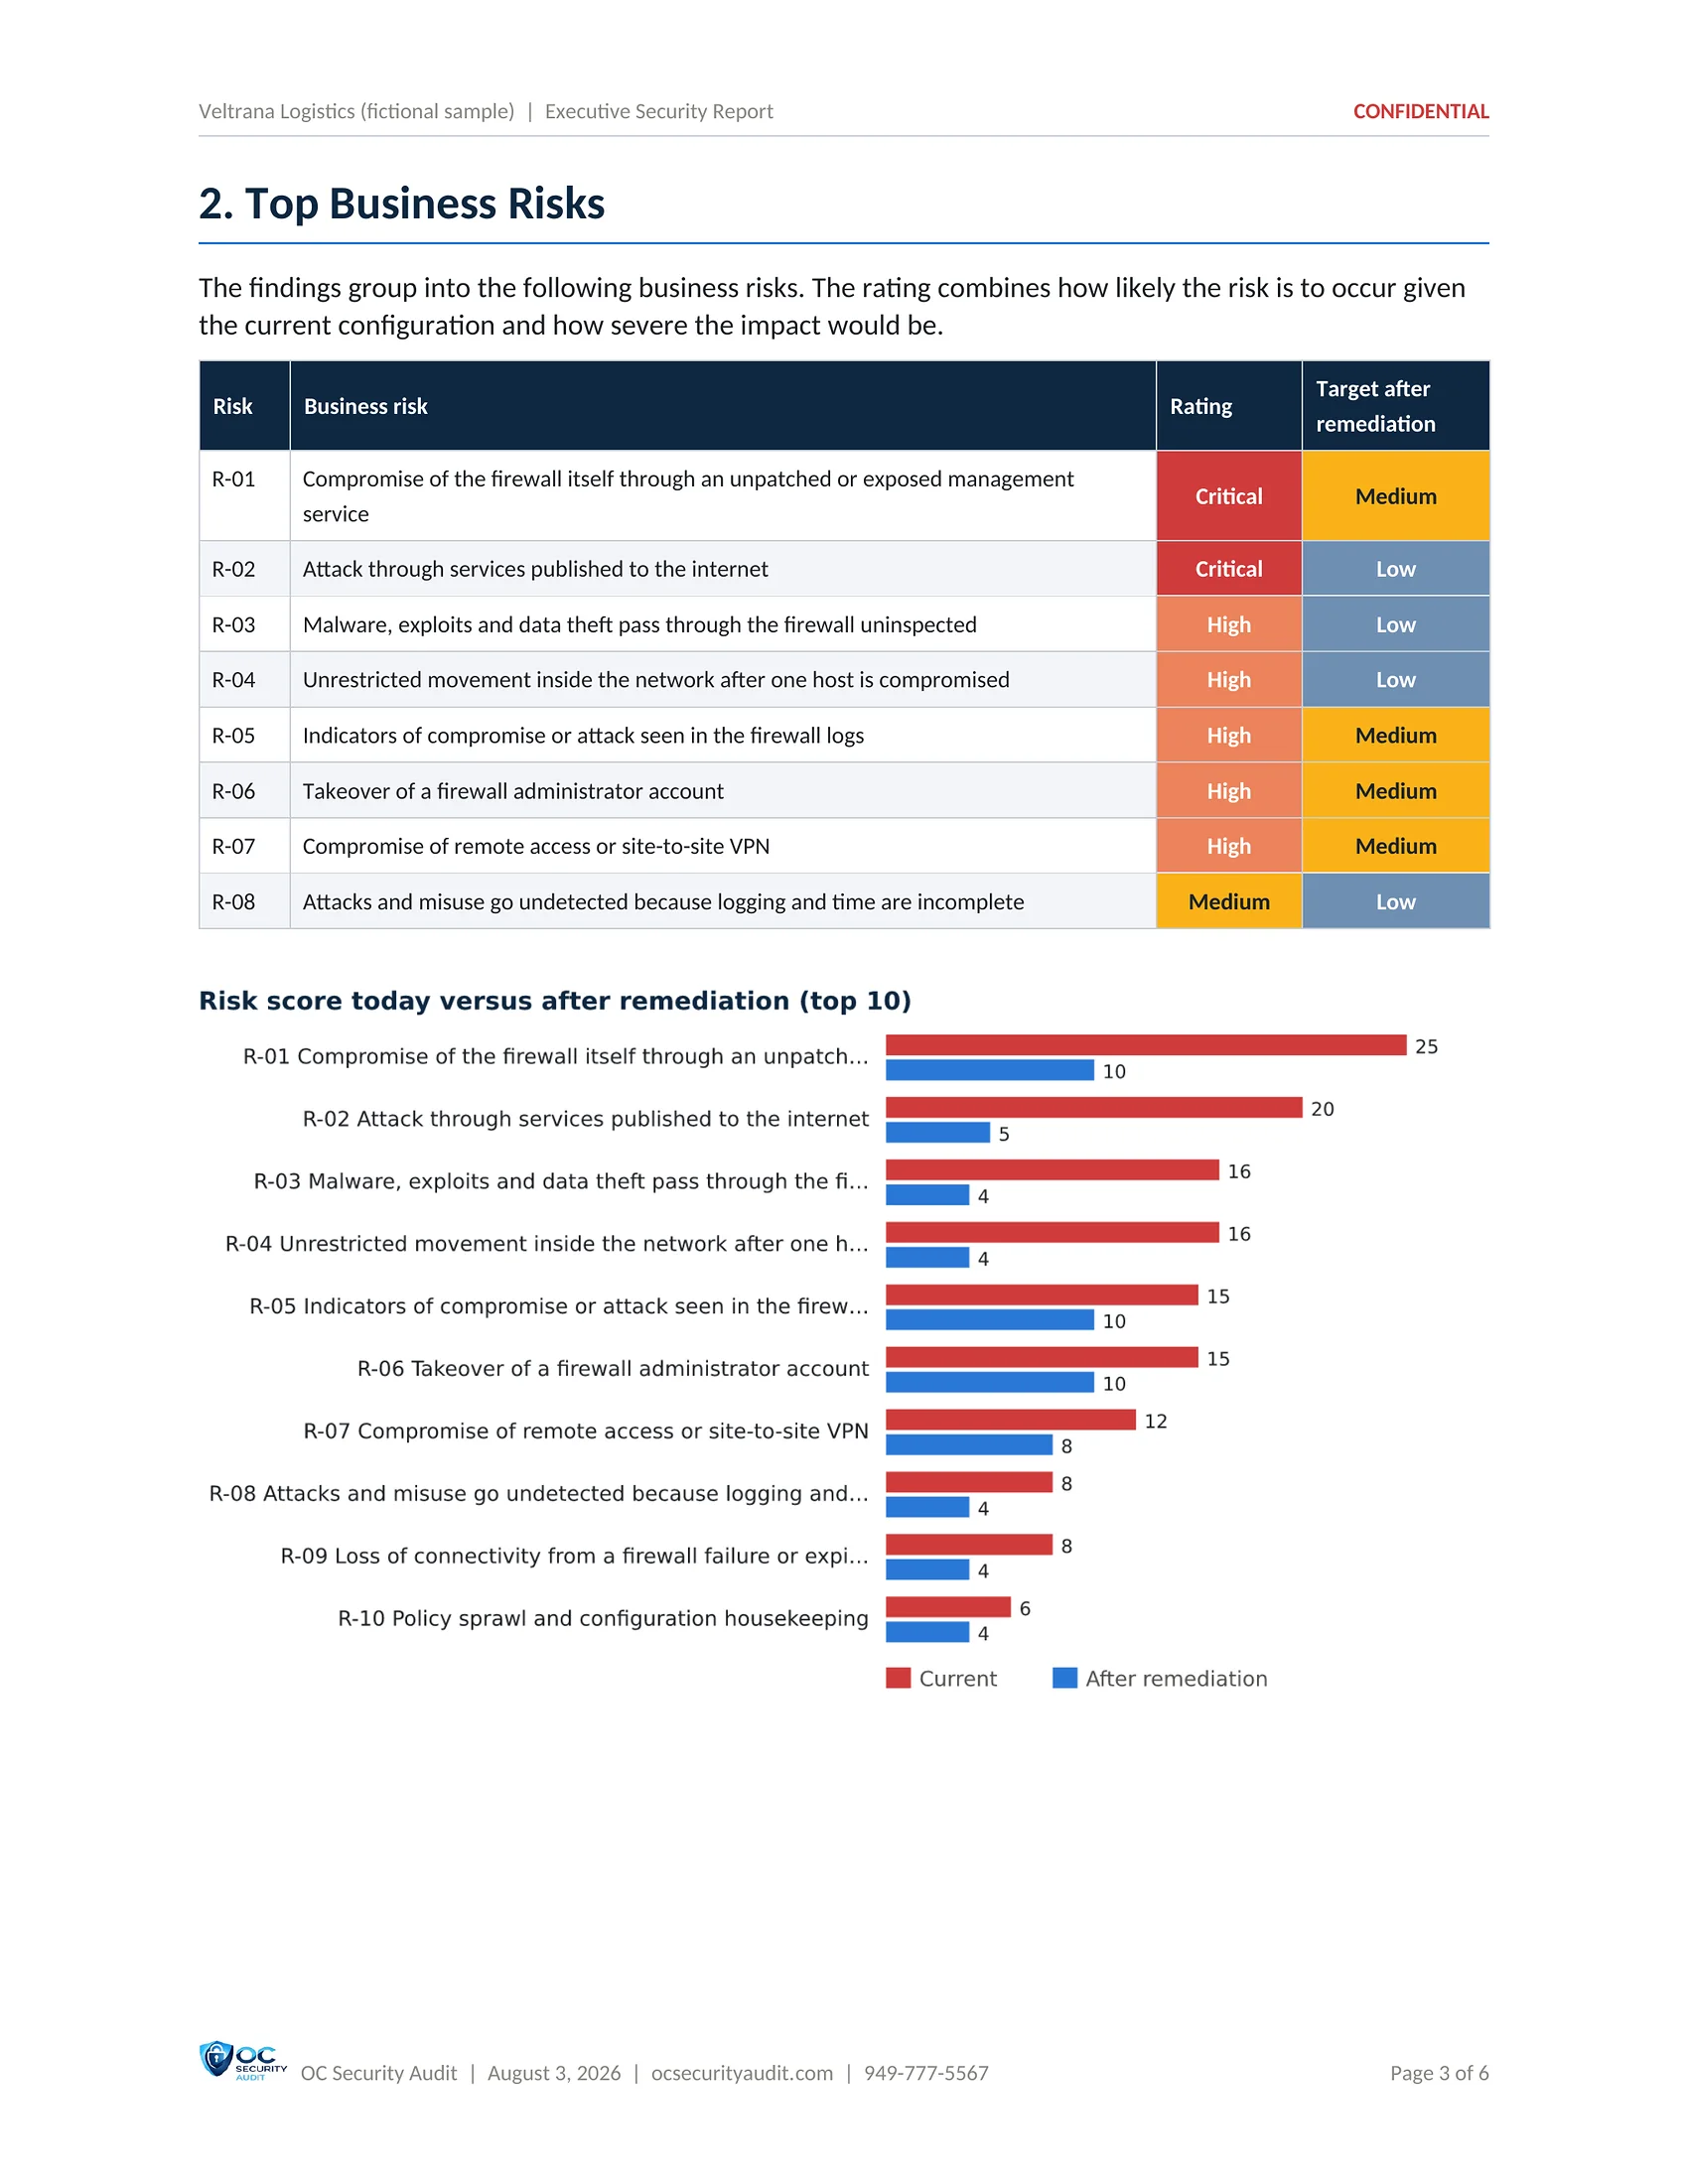
- Top business risks with target ratings
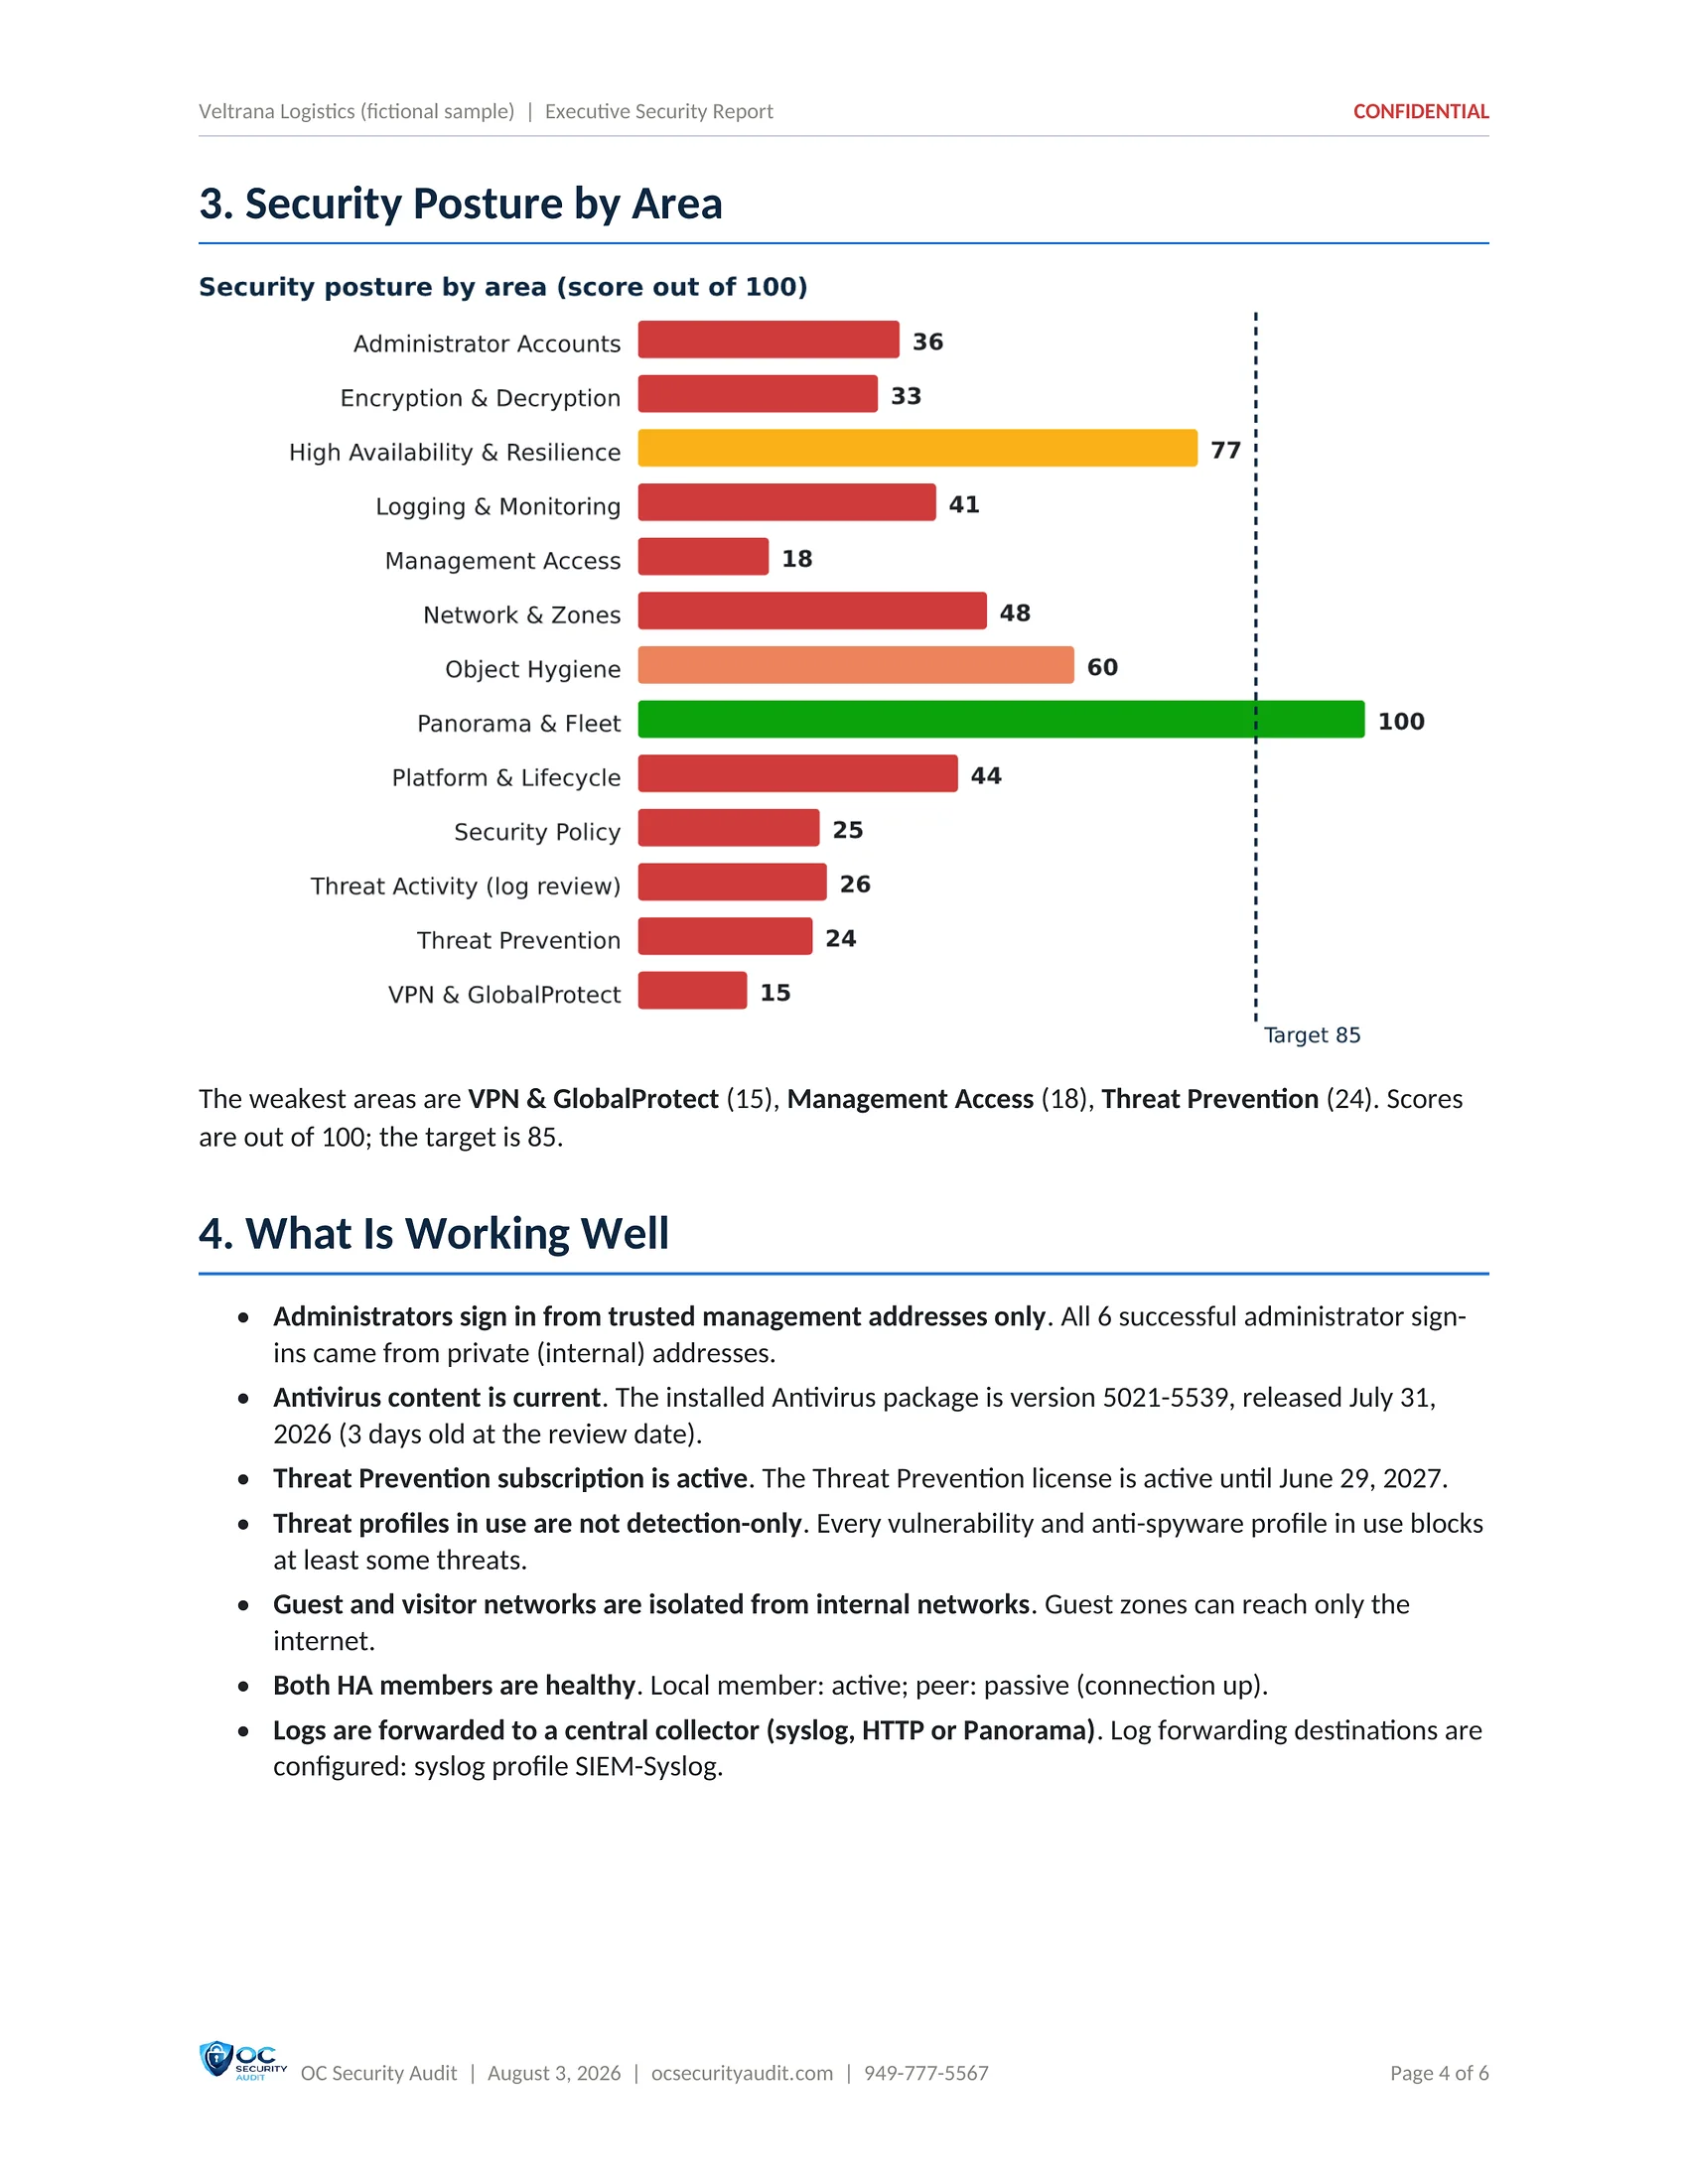
- Score for each of the 13 areas against a target of 85
- What is already working well
- Priority recommendations tied to findings
- Decisions requested from leadership
- Scope, method and limits of the review
Click the centre page to open it full size. Use the arrows, the thumbnails or your arrow keys to move between pages.
Deliverable 2 of 7 · PDF · 69 pages
Technical Security & Configuration Report
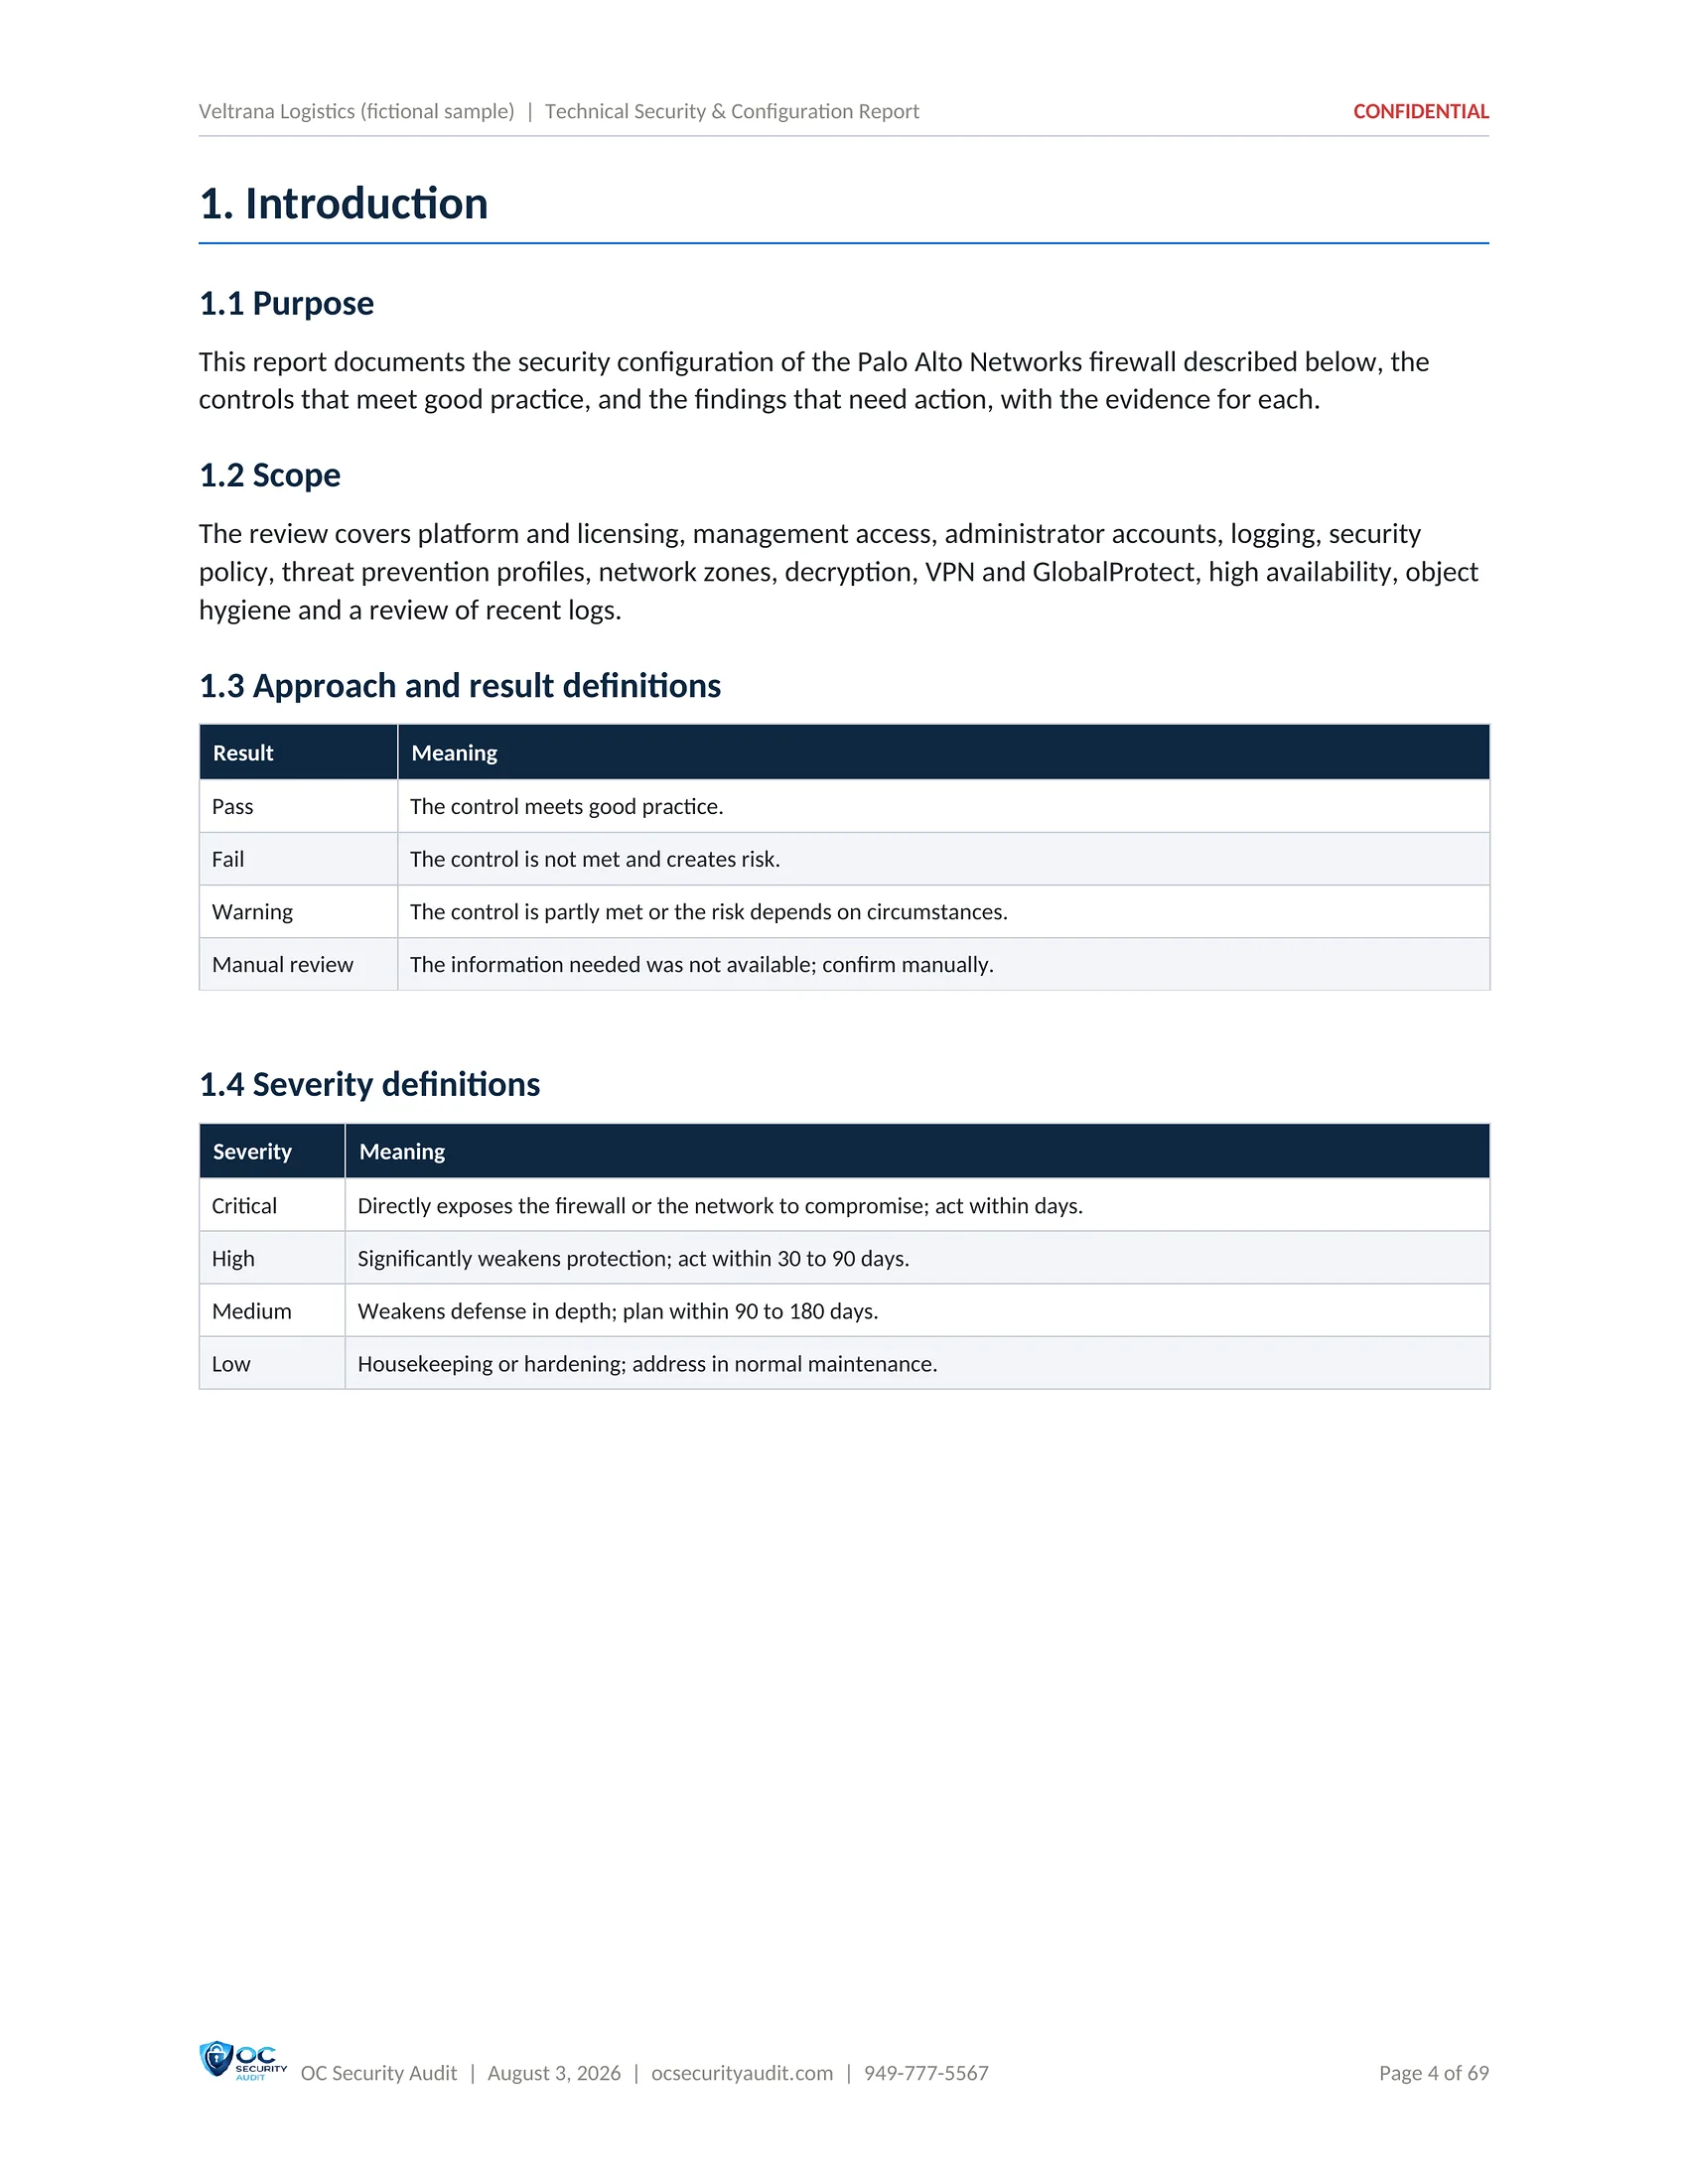
The full evidence for your firewall administrator or MSP. Every control is listed with its result, and every finding comes with what was observed, why it matters, the exact fix, the rules or settings affected and the framework reference.
Each area is explained on its own page: management interface security, PAN-OS end of life and vulnerabilities, security policy and NAT, security profiles, SSL/TLS decryption, GlobalProtect and IPsec VPN, zone protection, logging, HA and Panorama.
Who uses it
Firewall administrators, MSP, IT manager
What is included
- Environment overview read from the firewall
- Results by area with pass, fail and warning counts
- Subscriptions, content versions and vendor advisories
- Interfaces, zones and management profiles
- Key observations for each area
- Detailed finding cards ordered by severity
- Controls that already meet the benchmark
- NIST CSF 2.0 and ISO/IEC 27001:2022 mapping
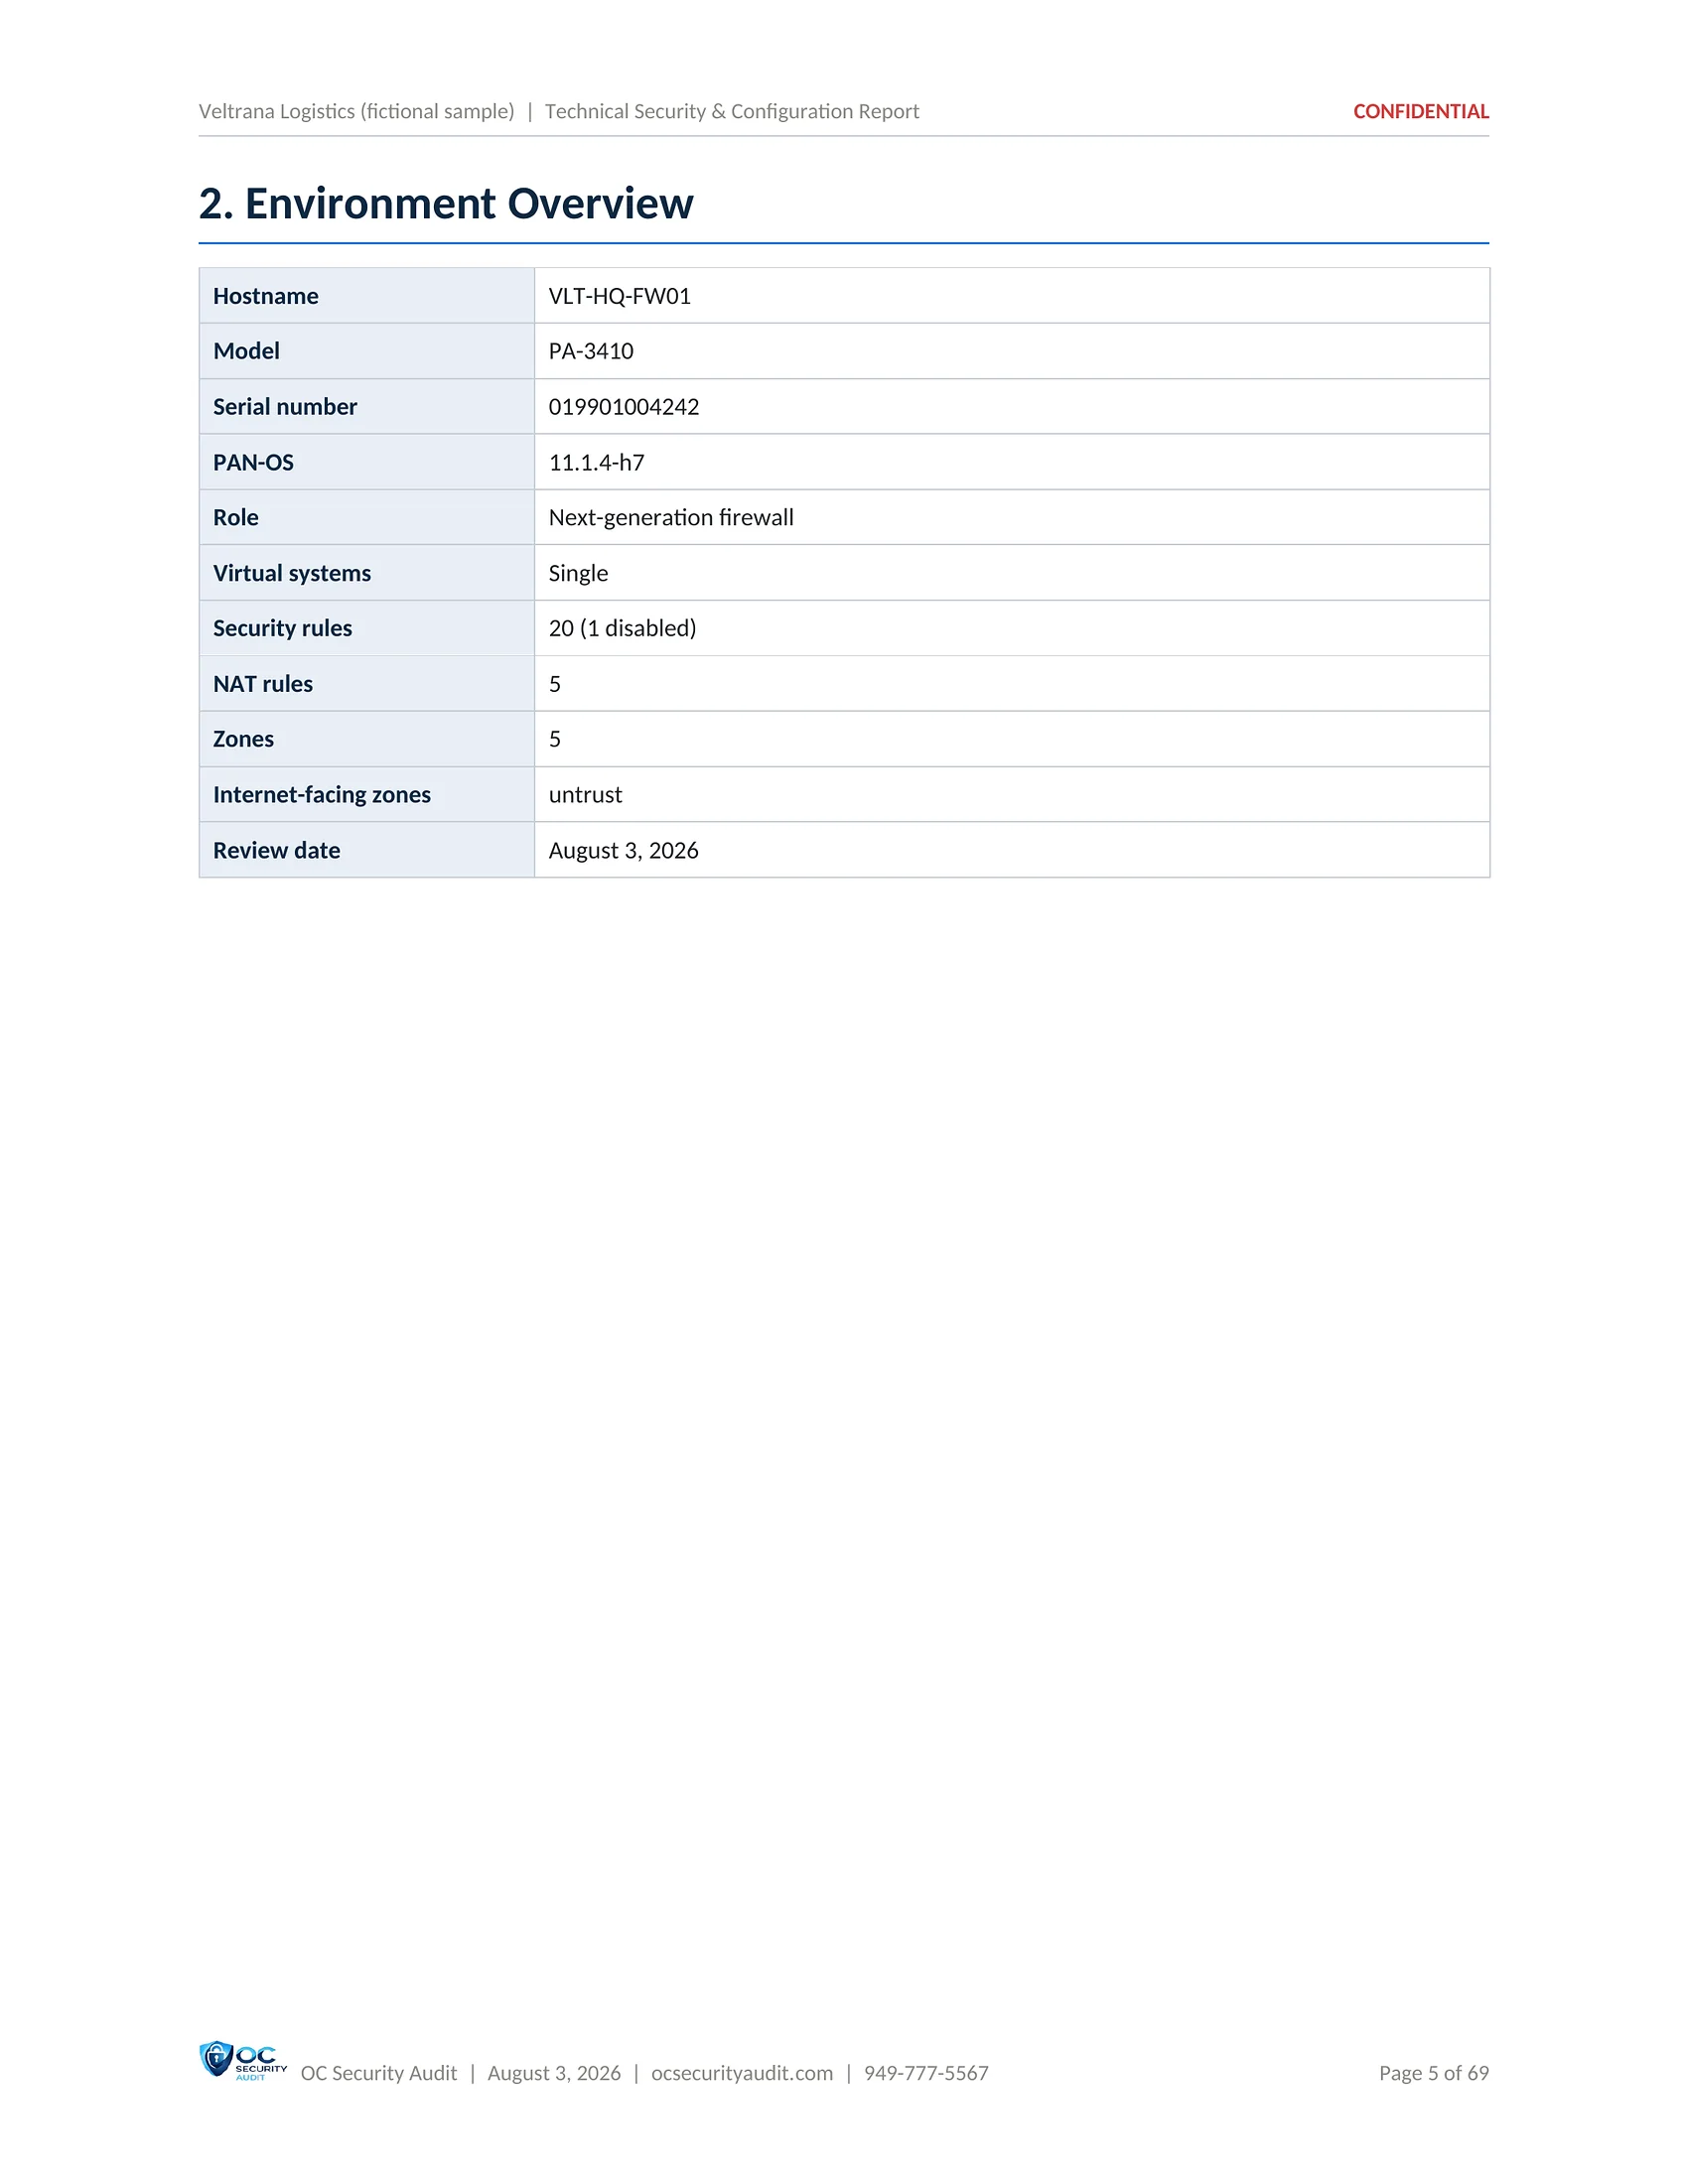
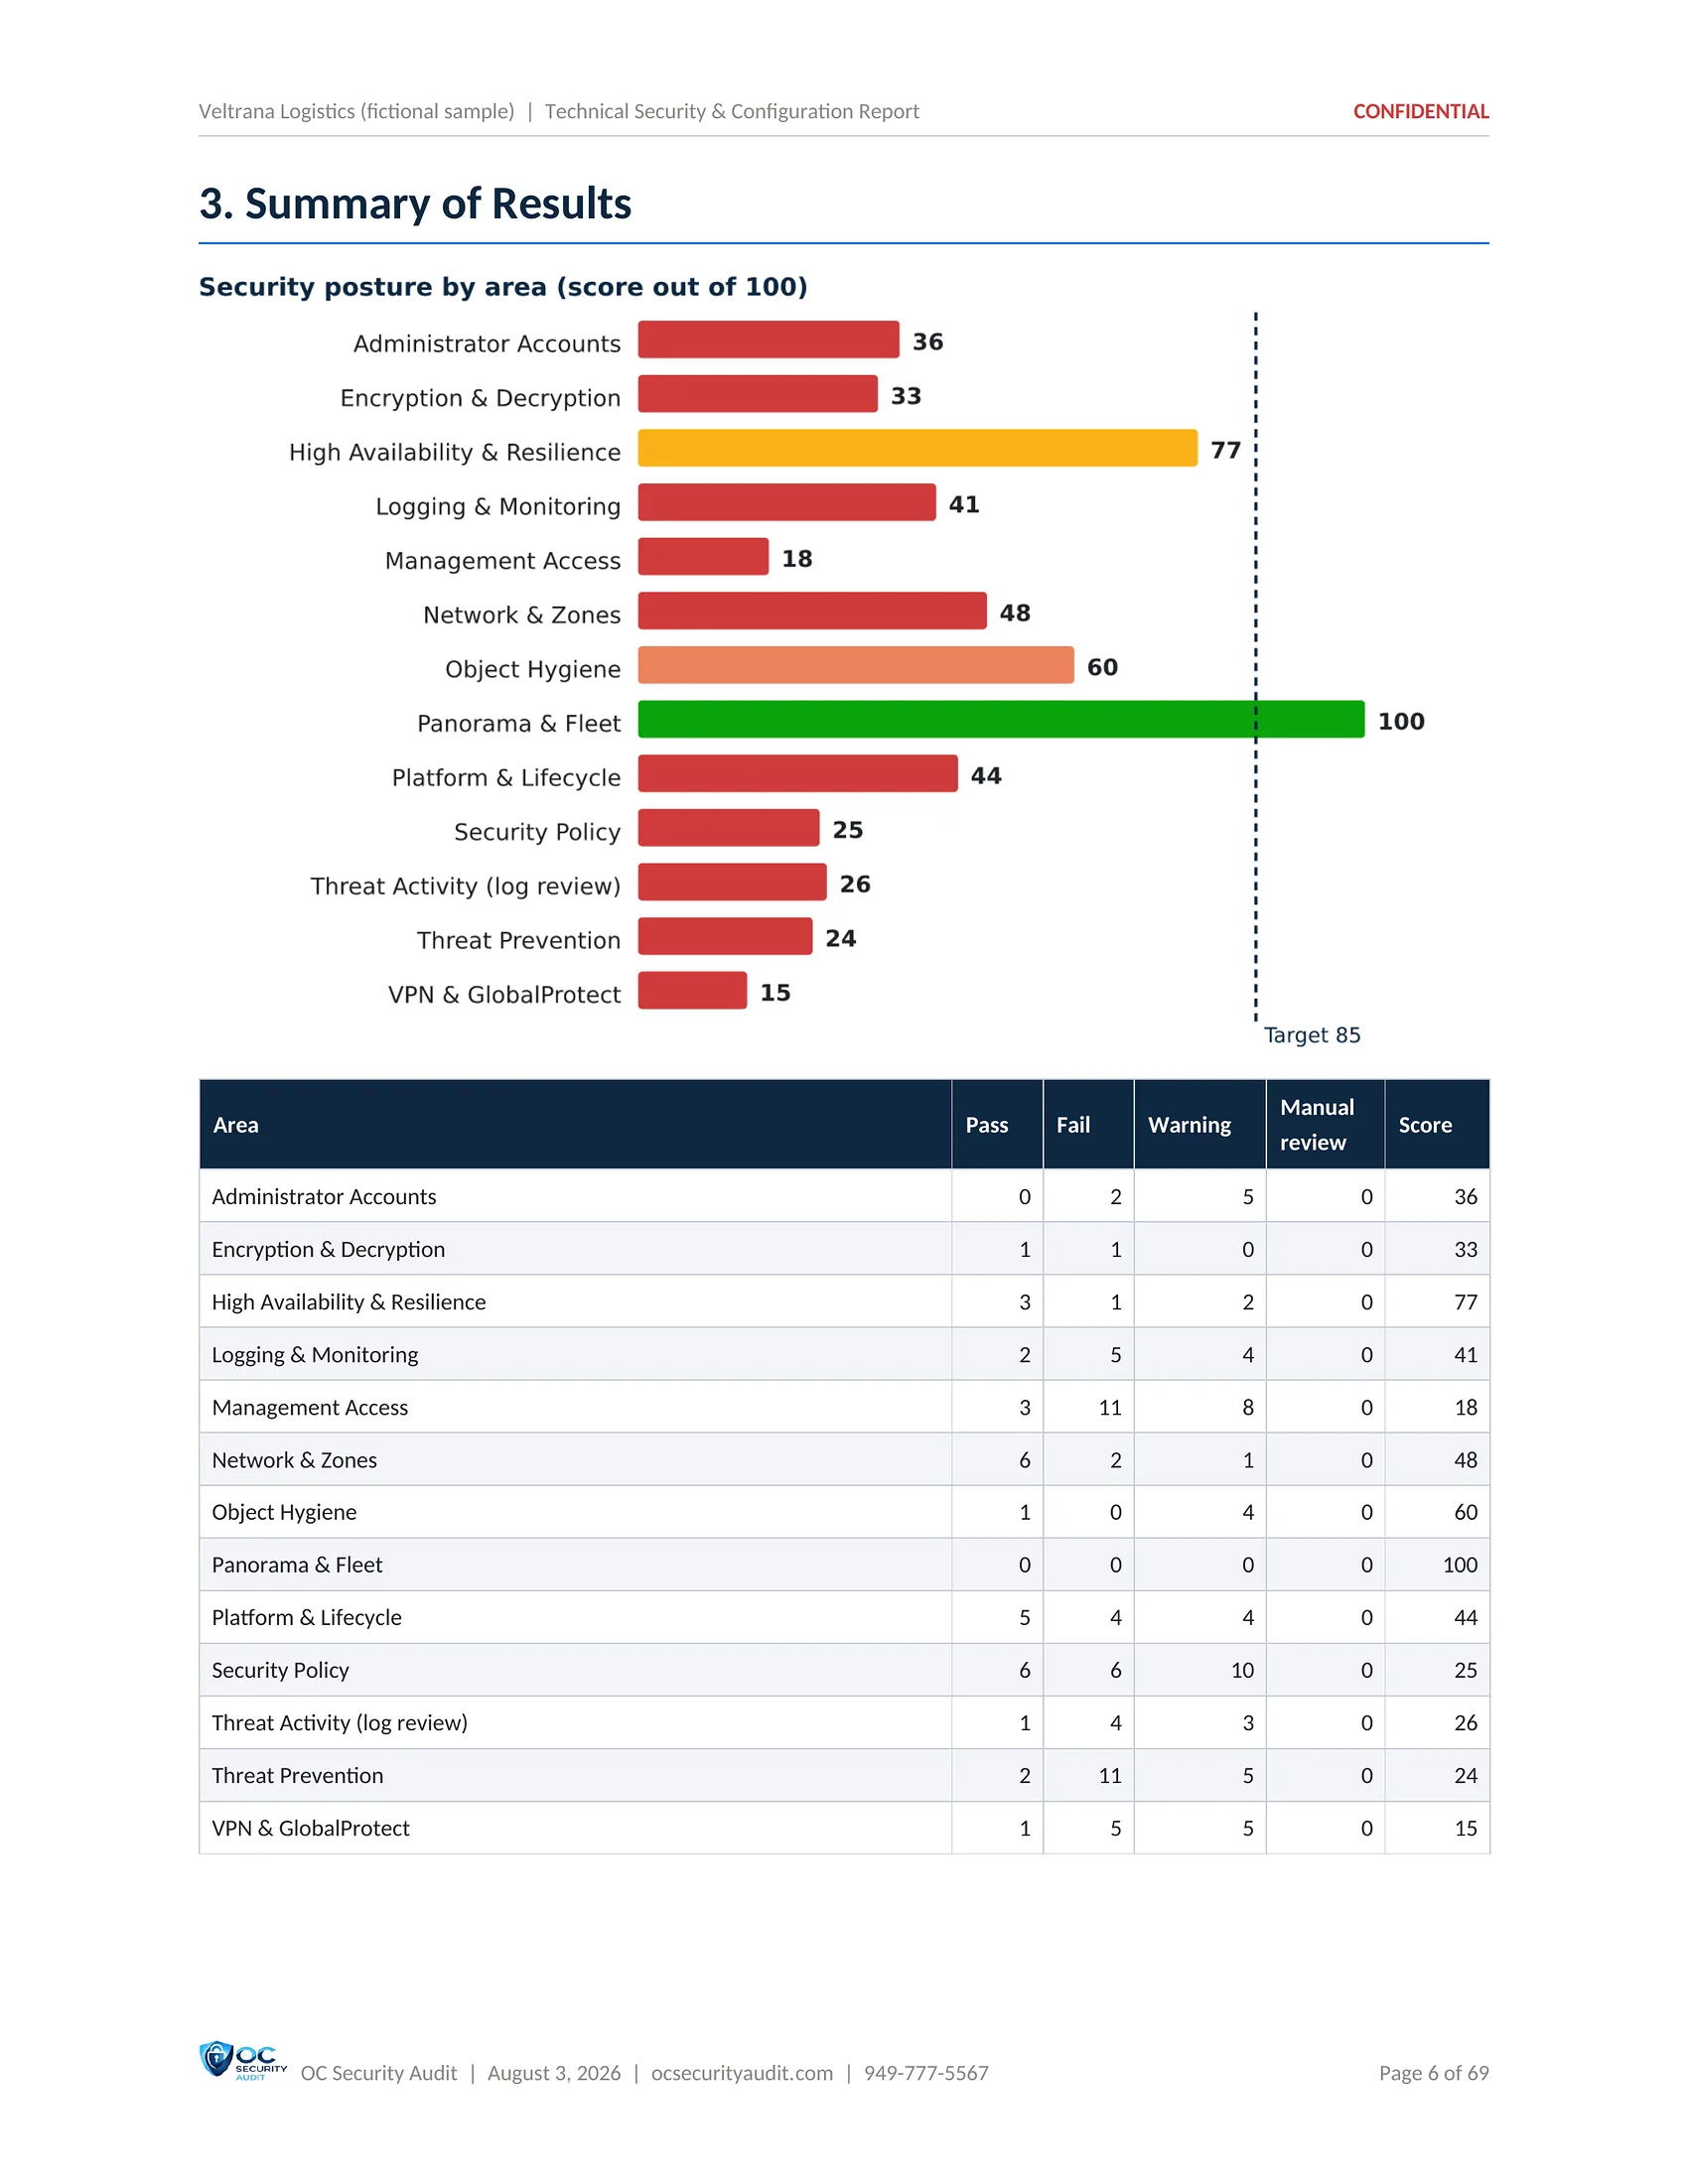
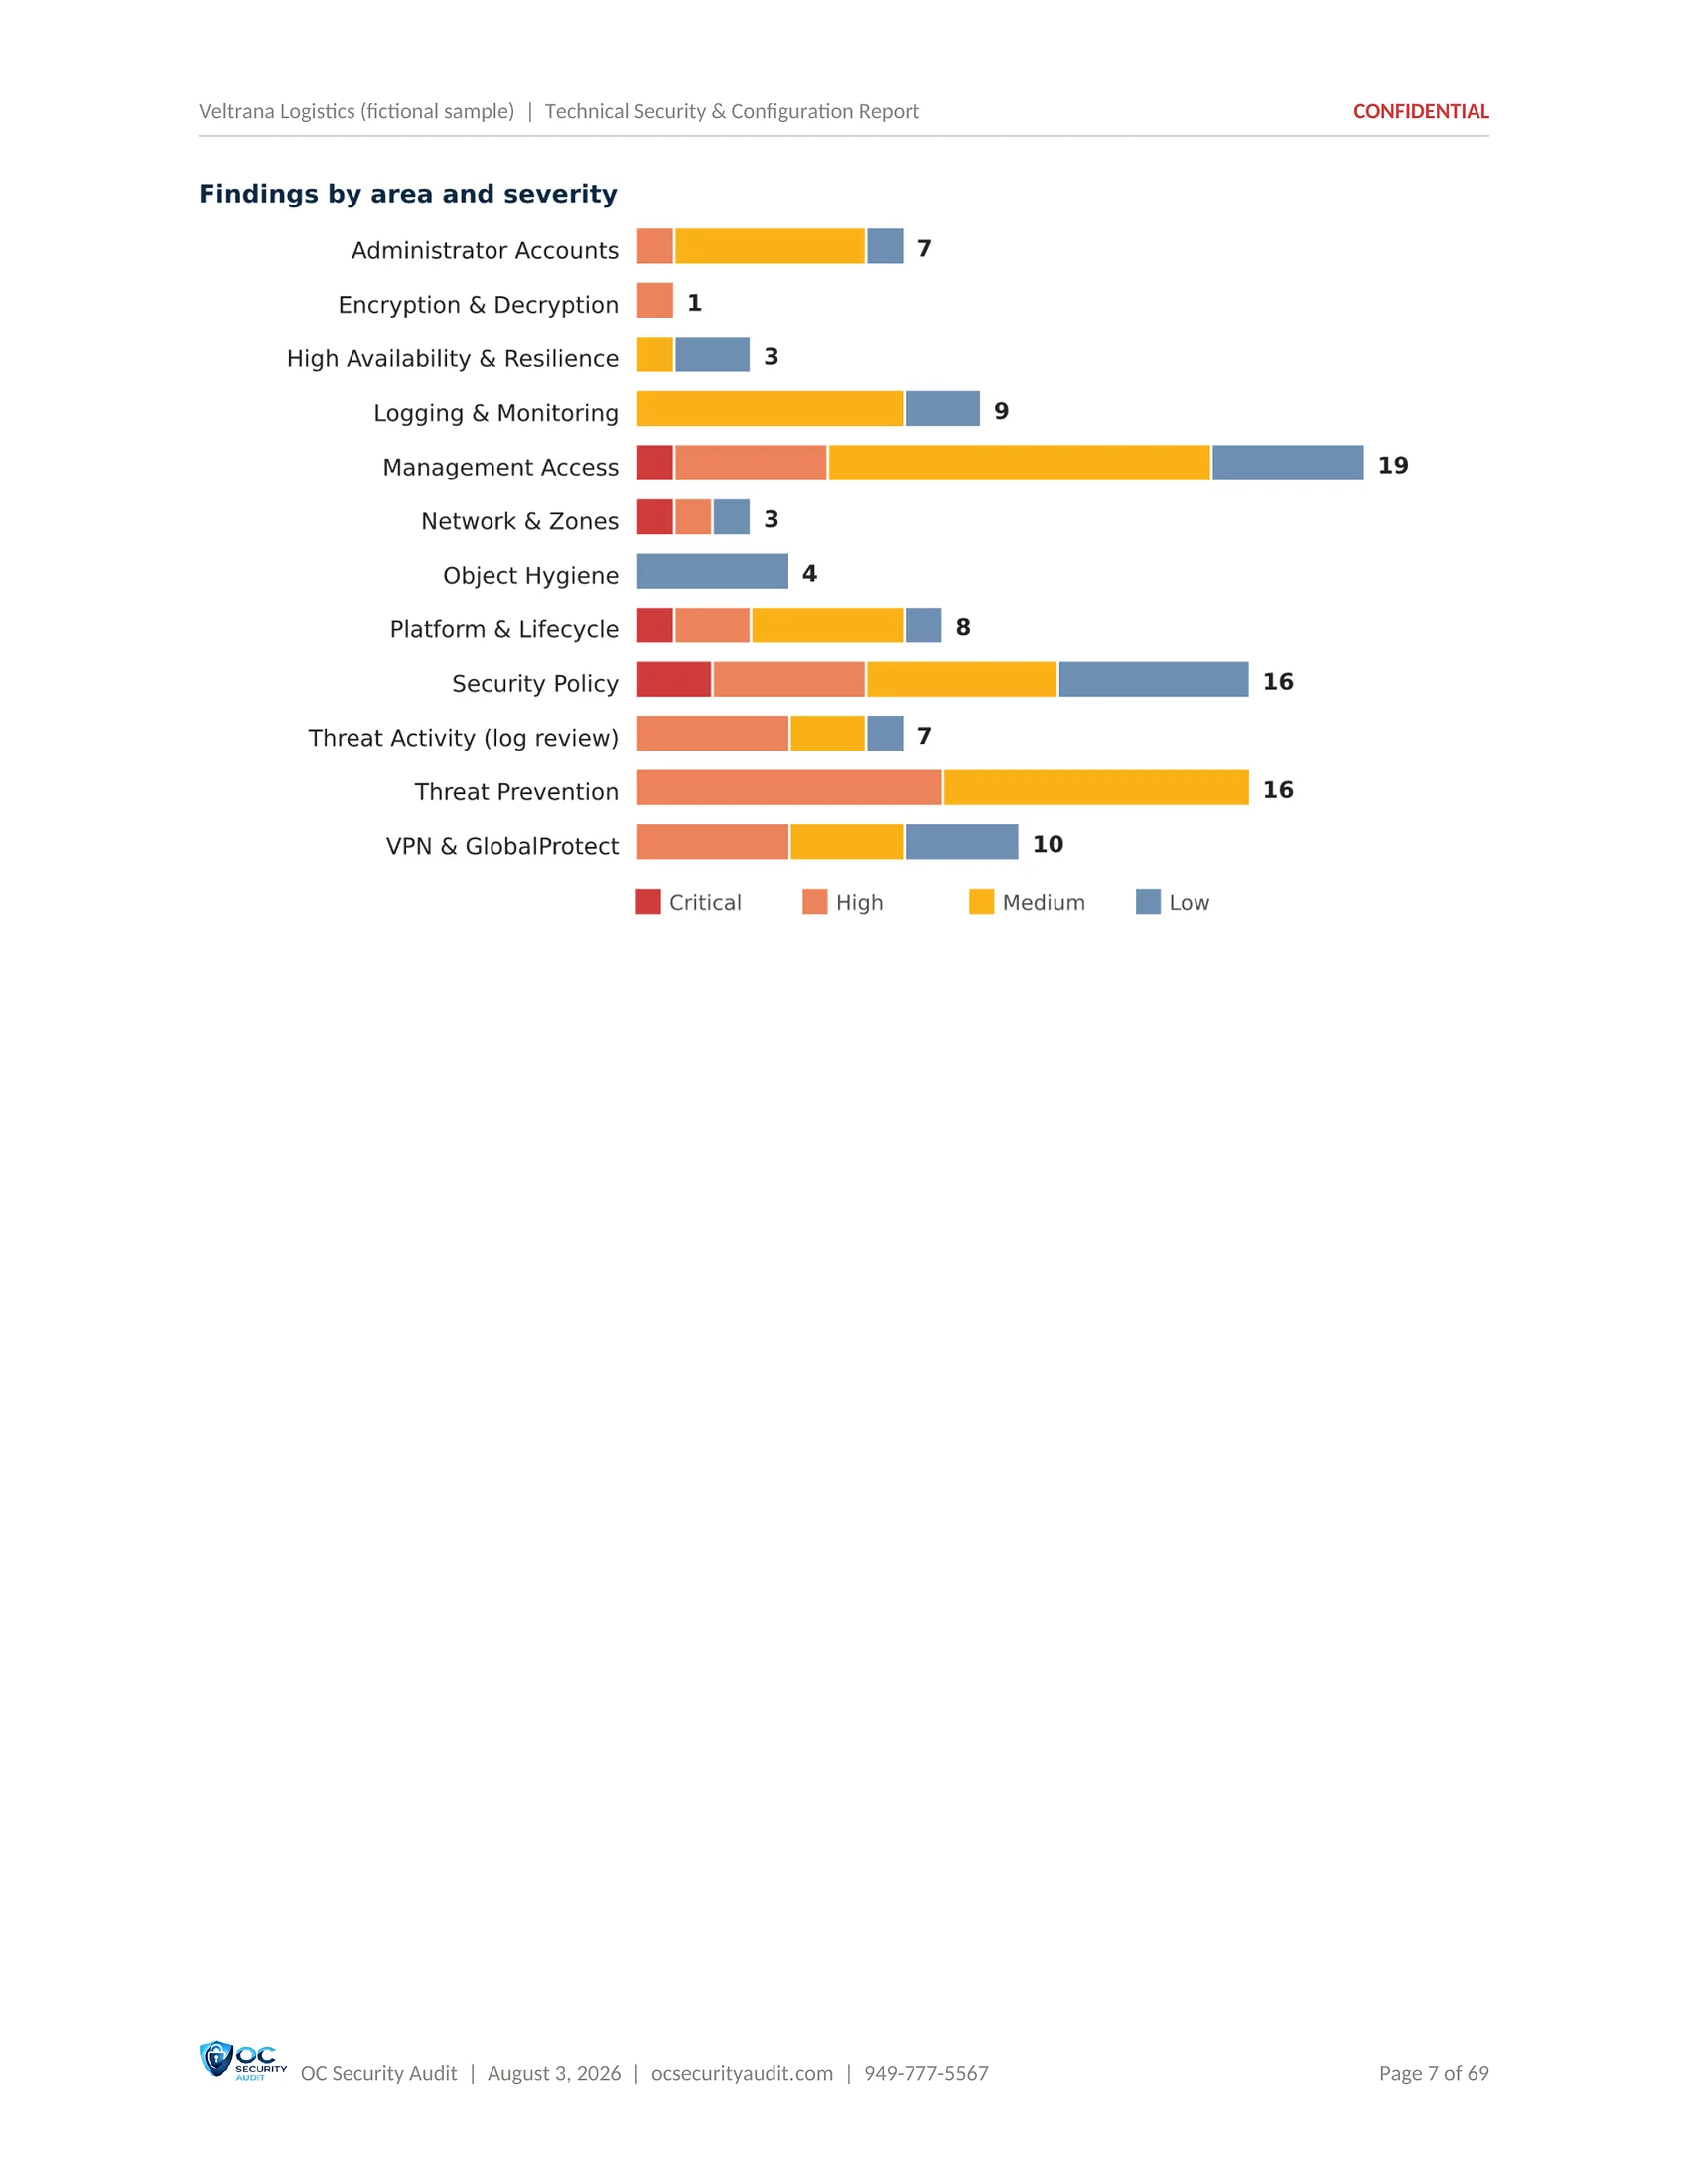
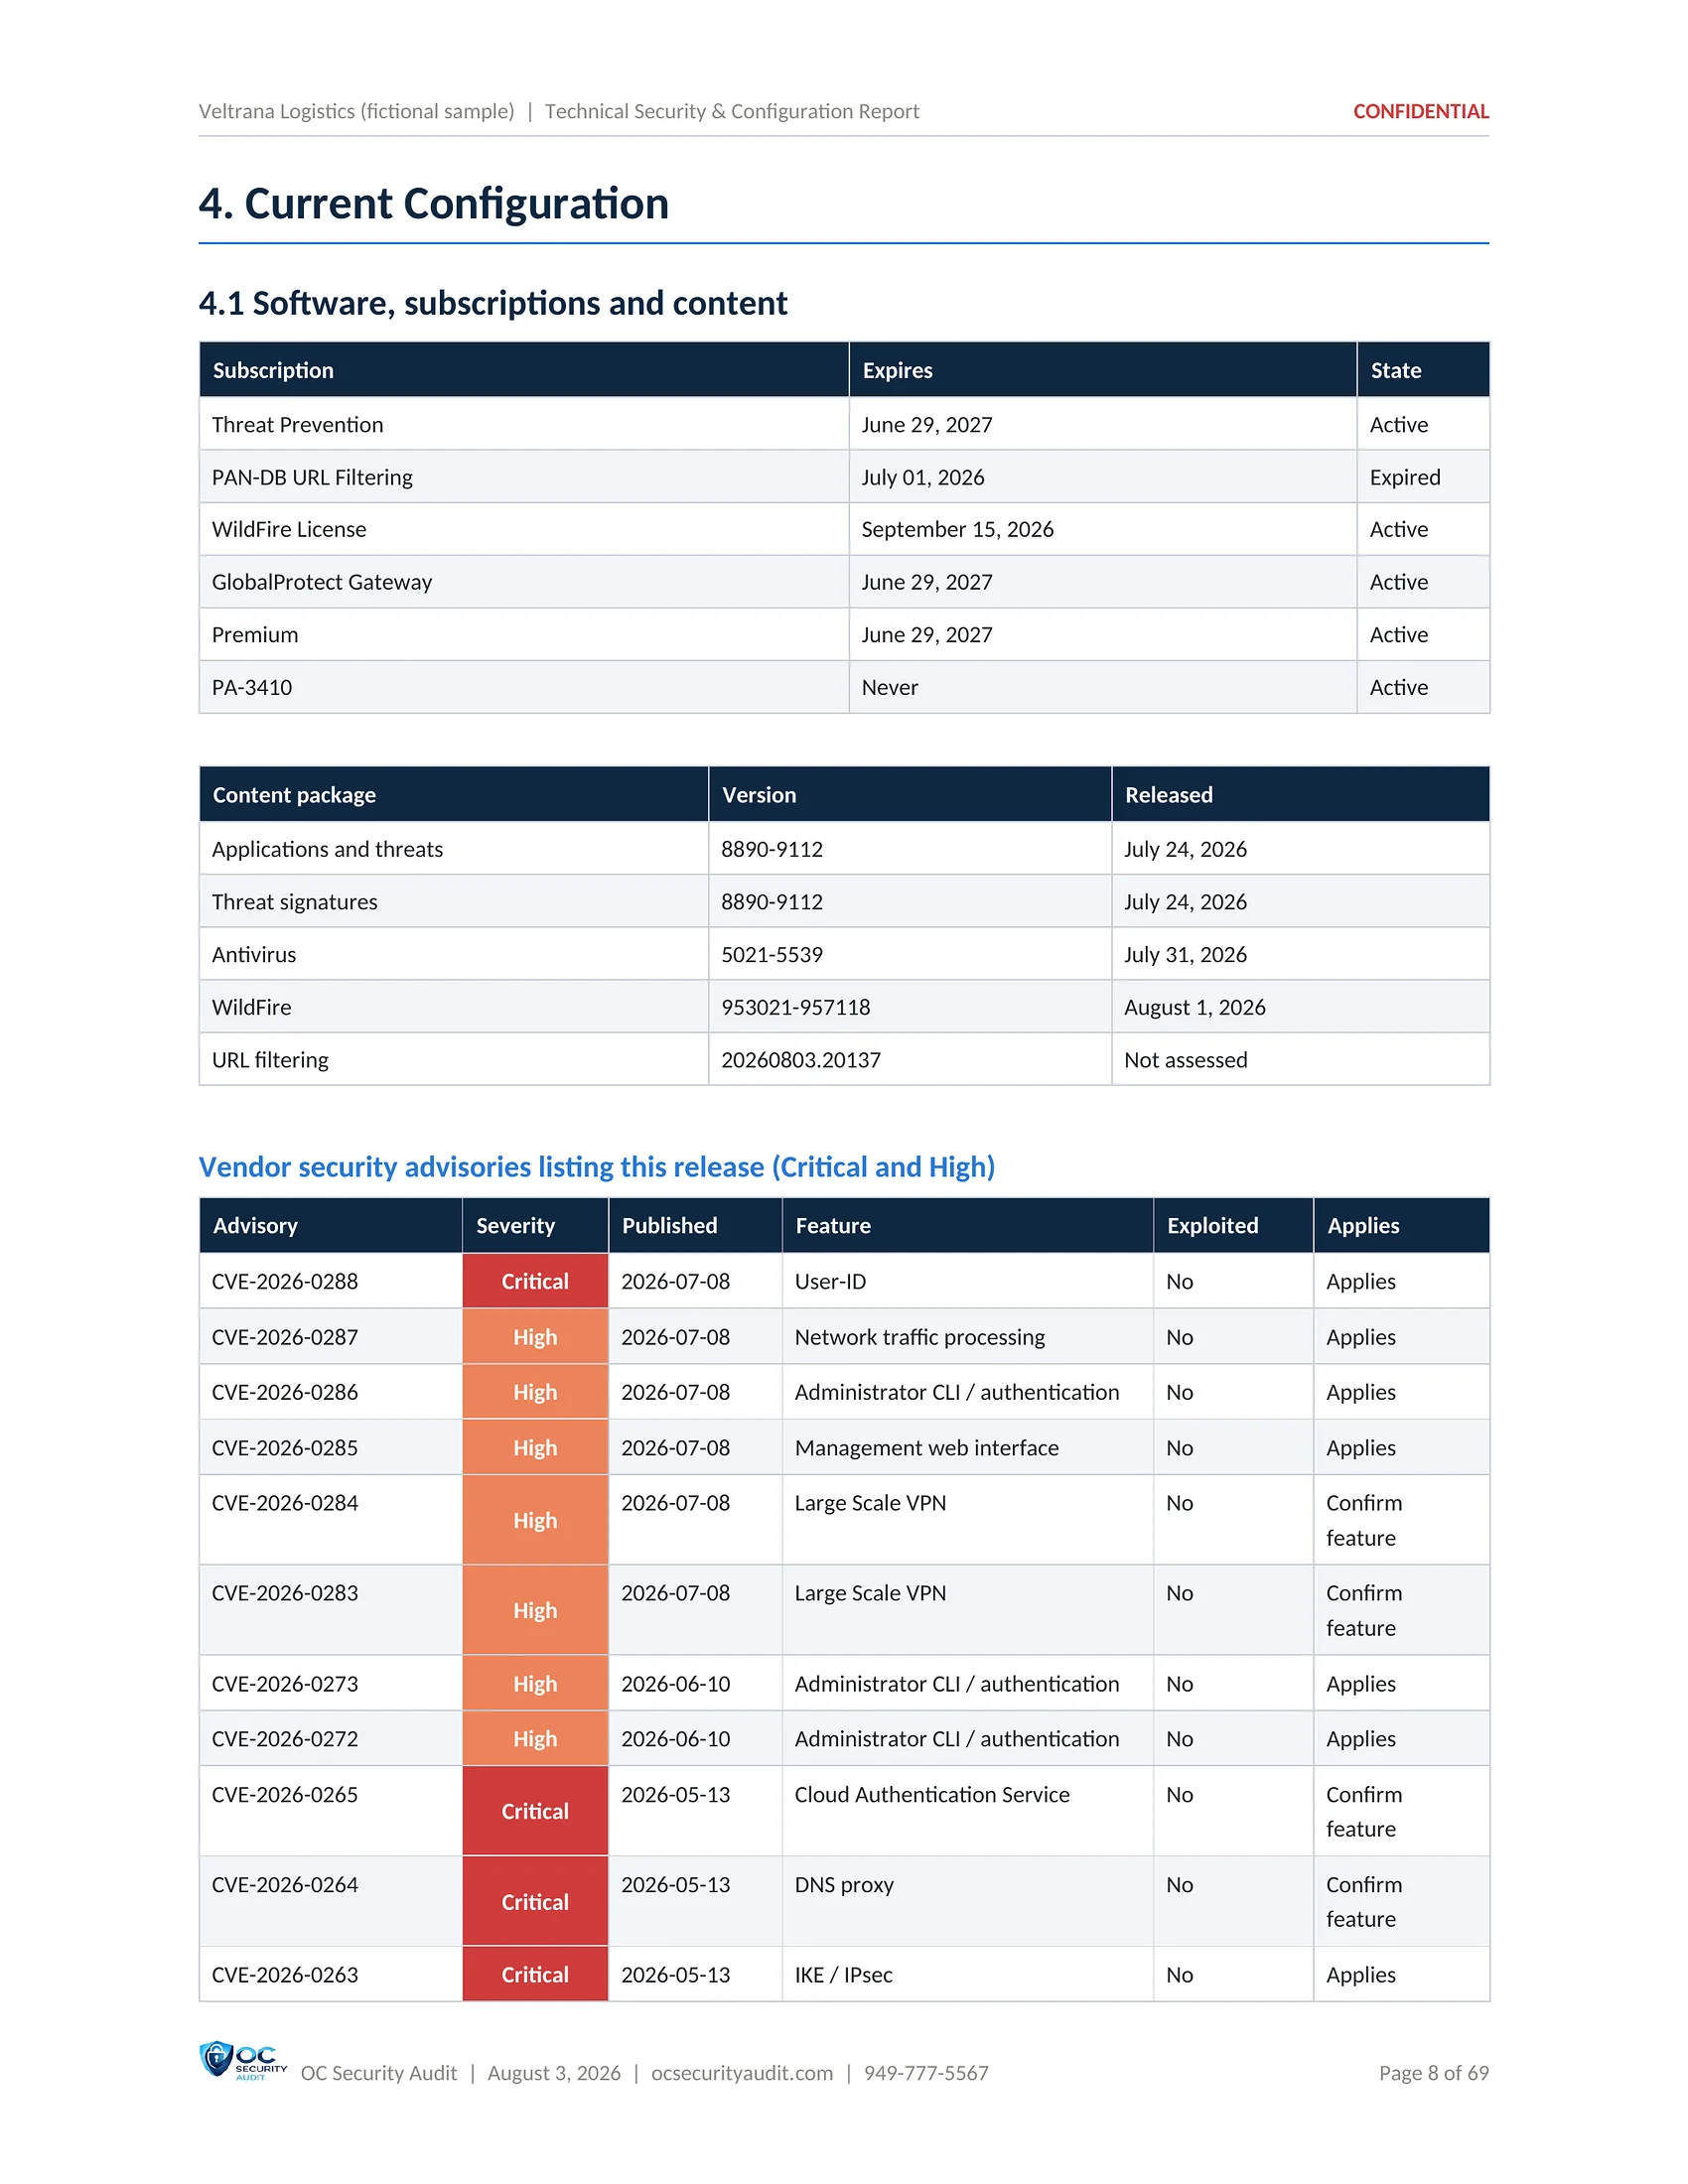
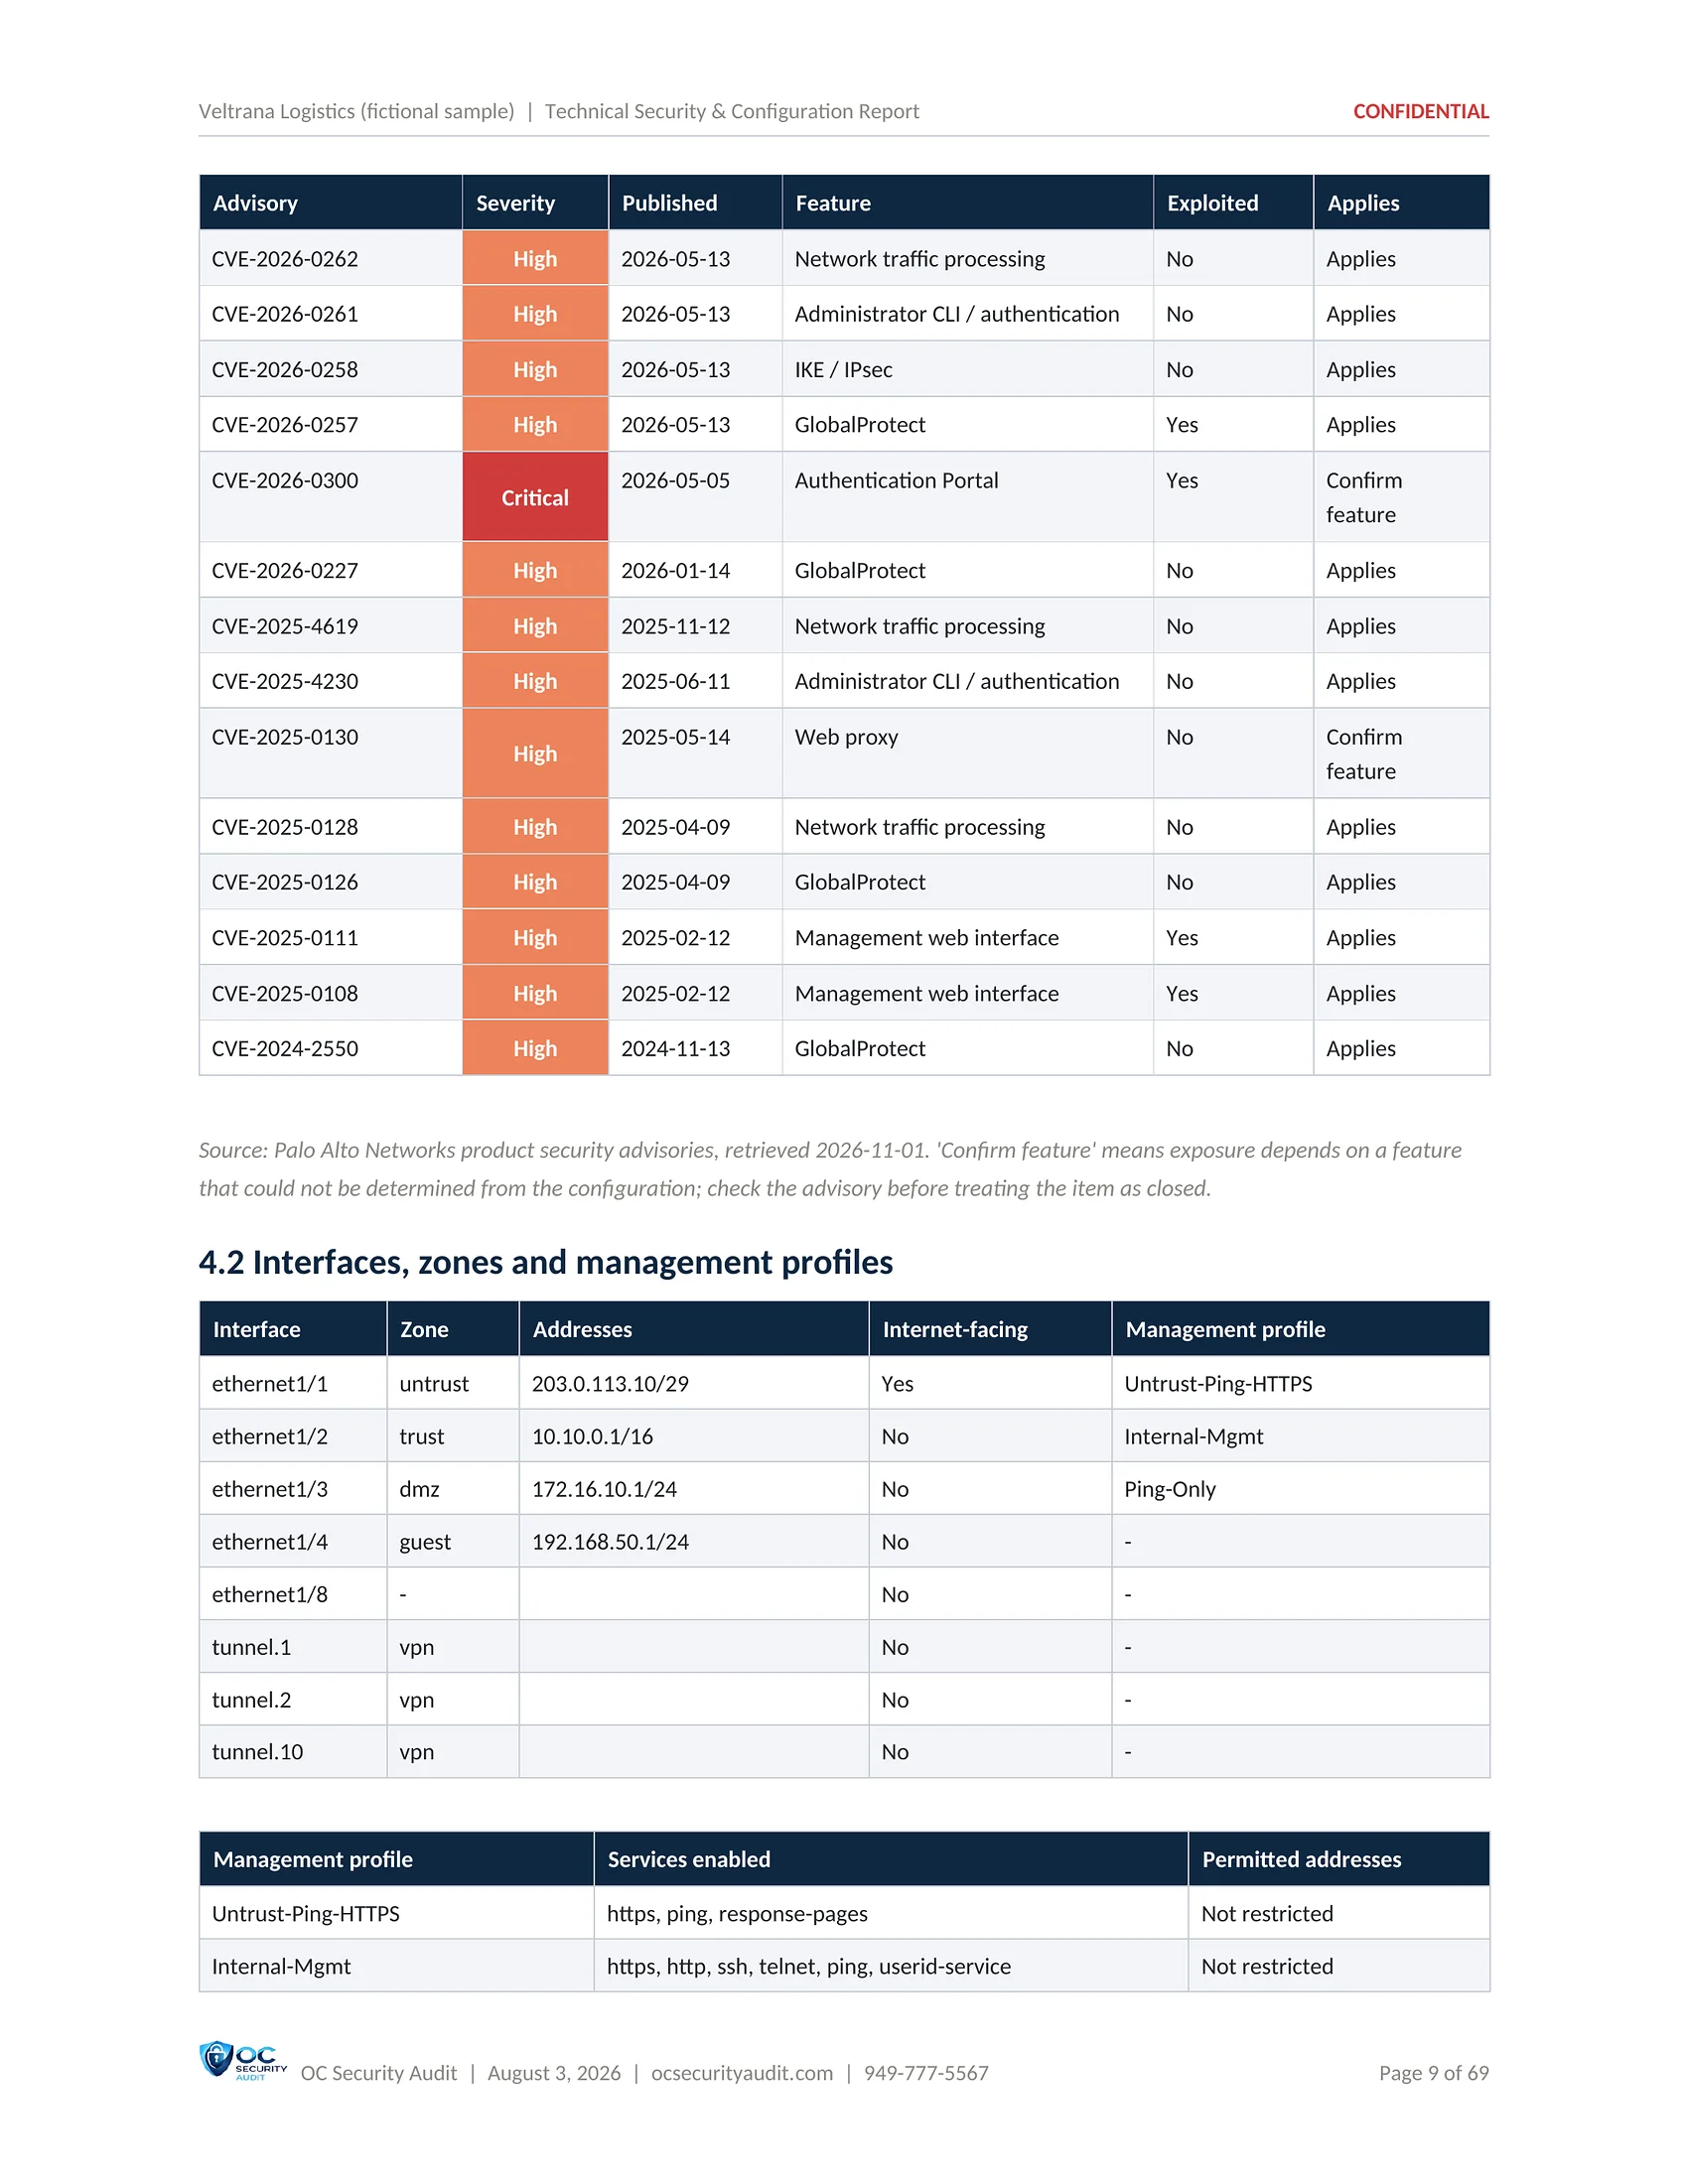
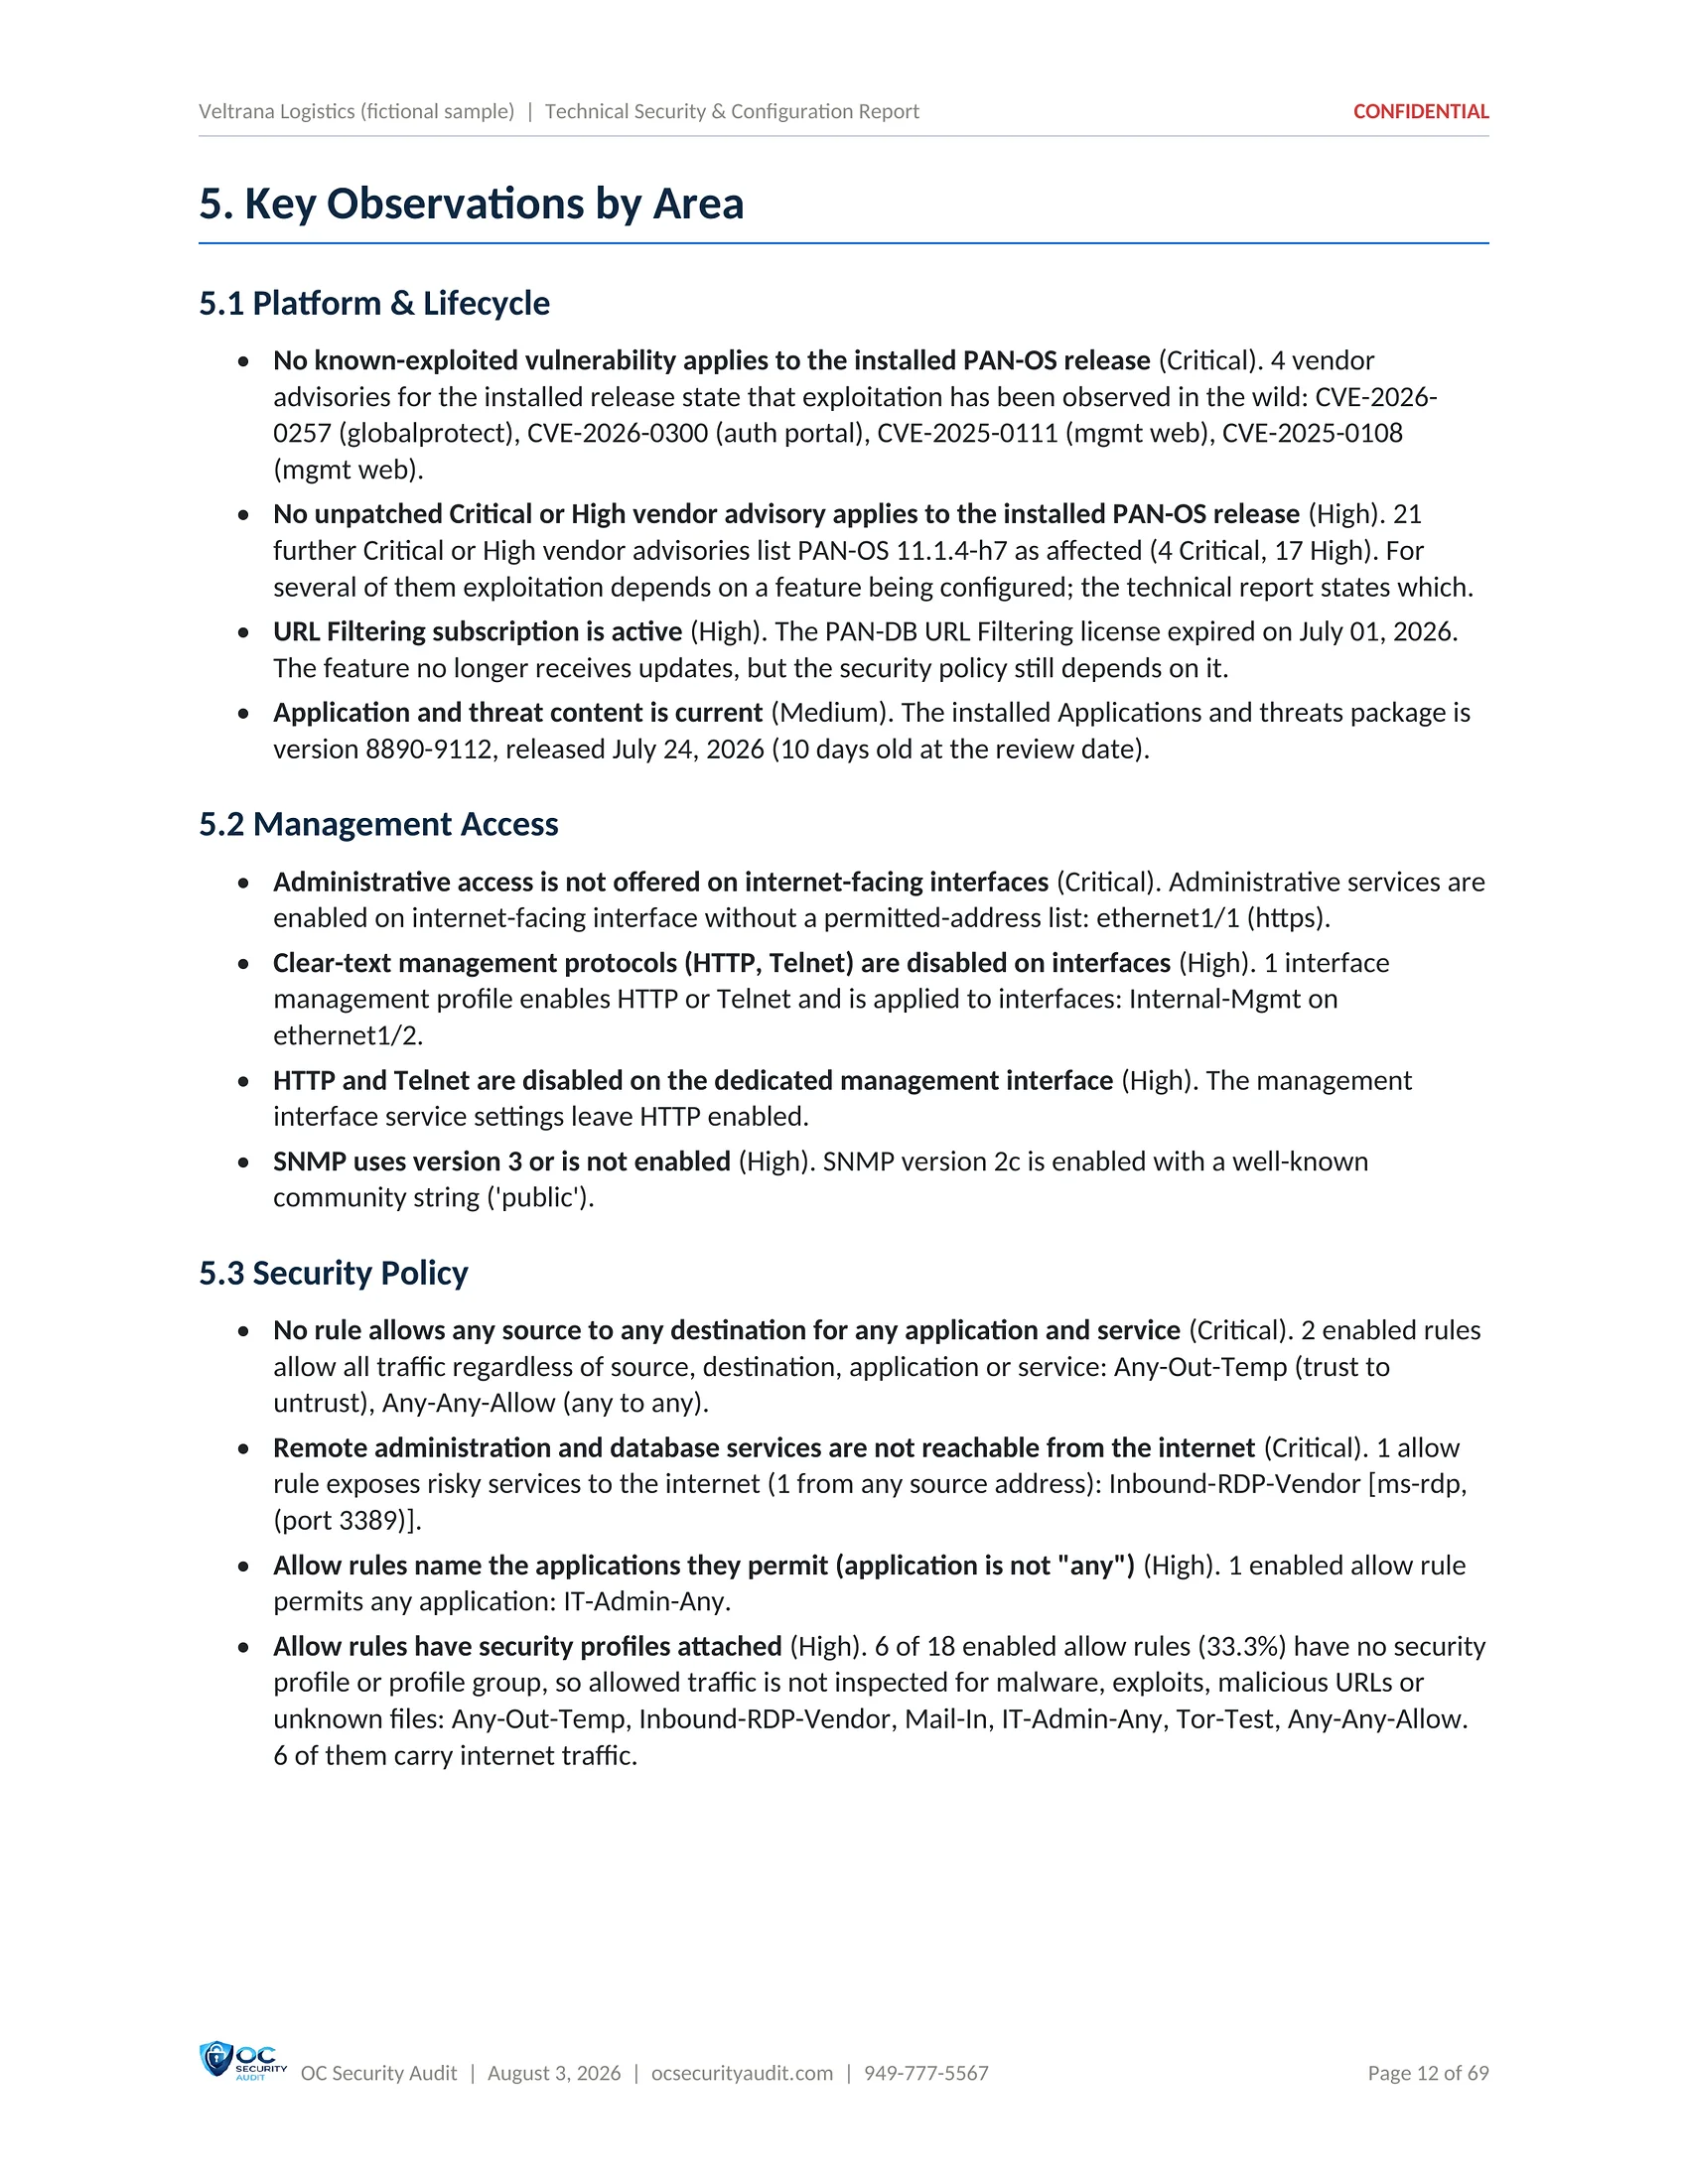
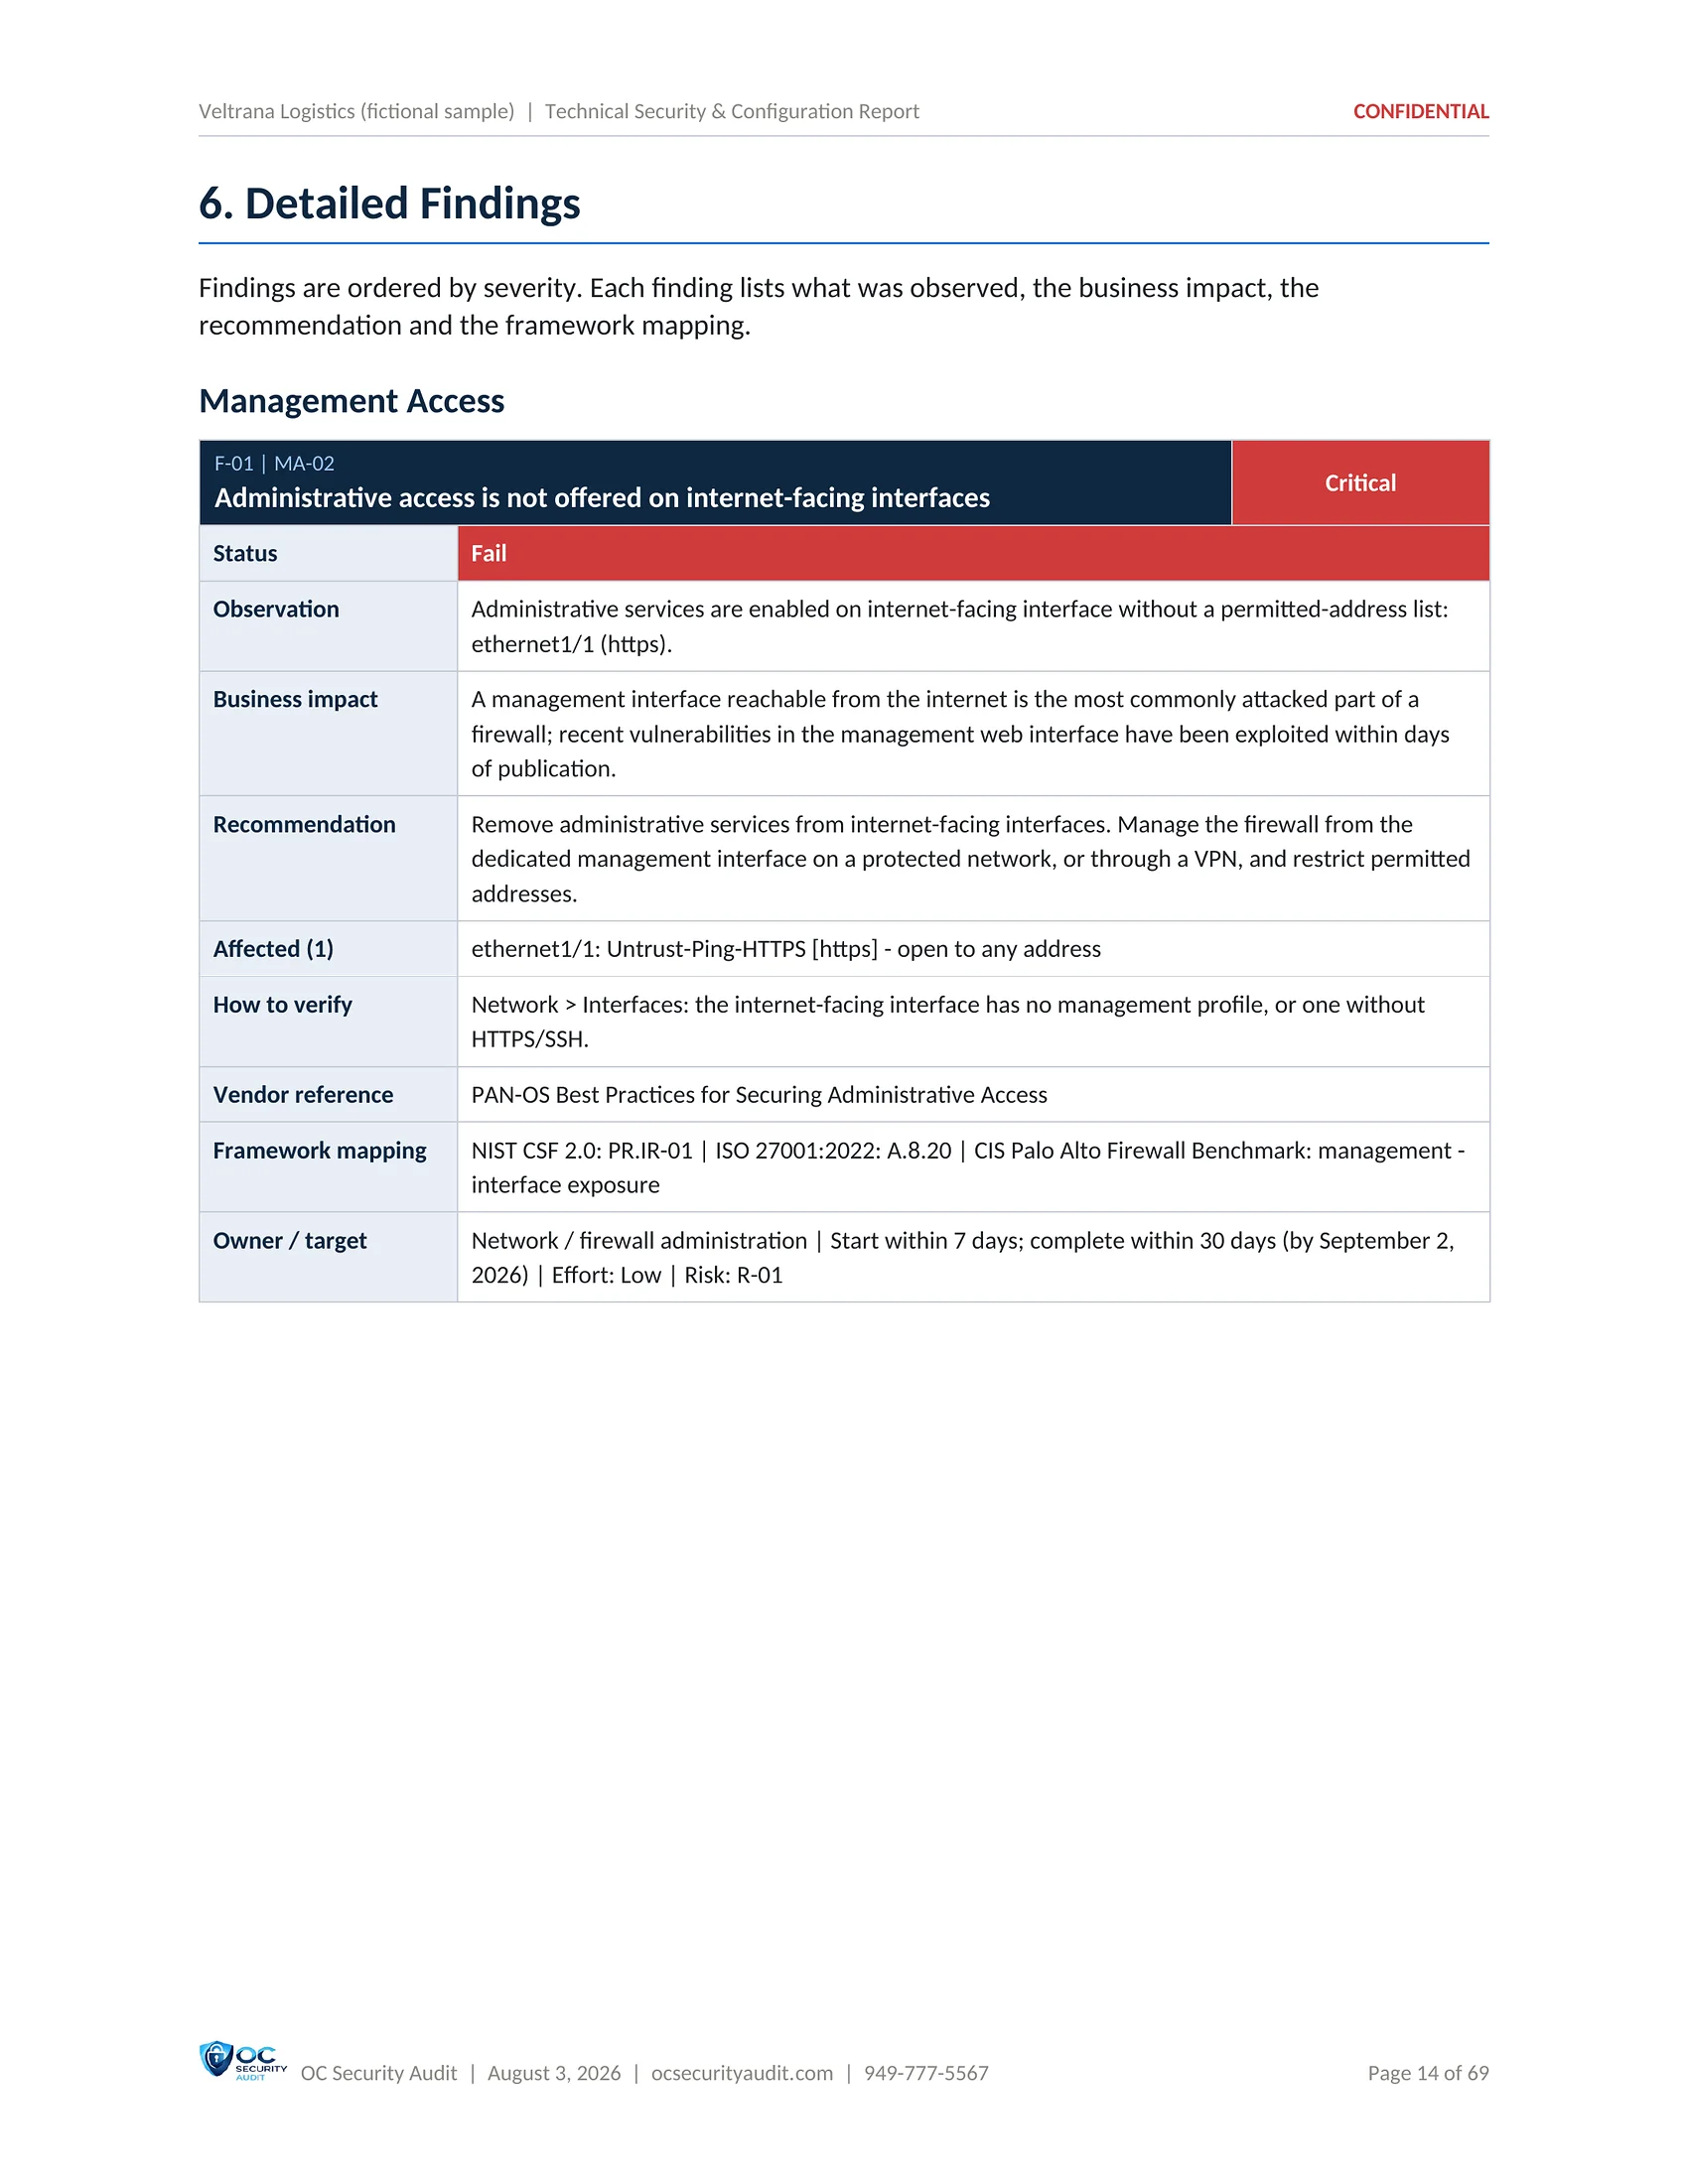
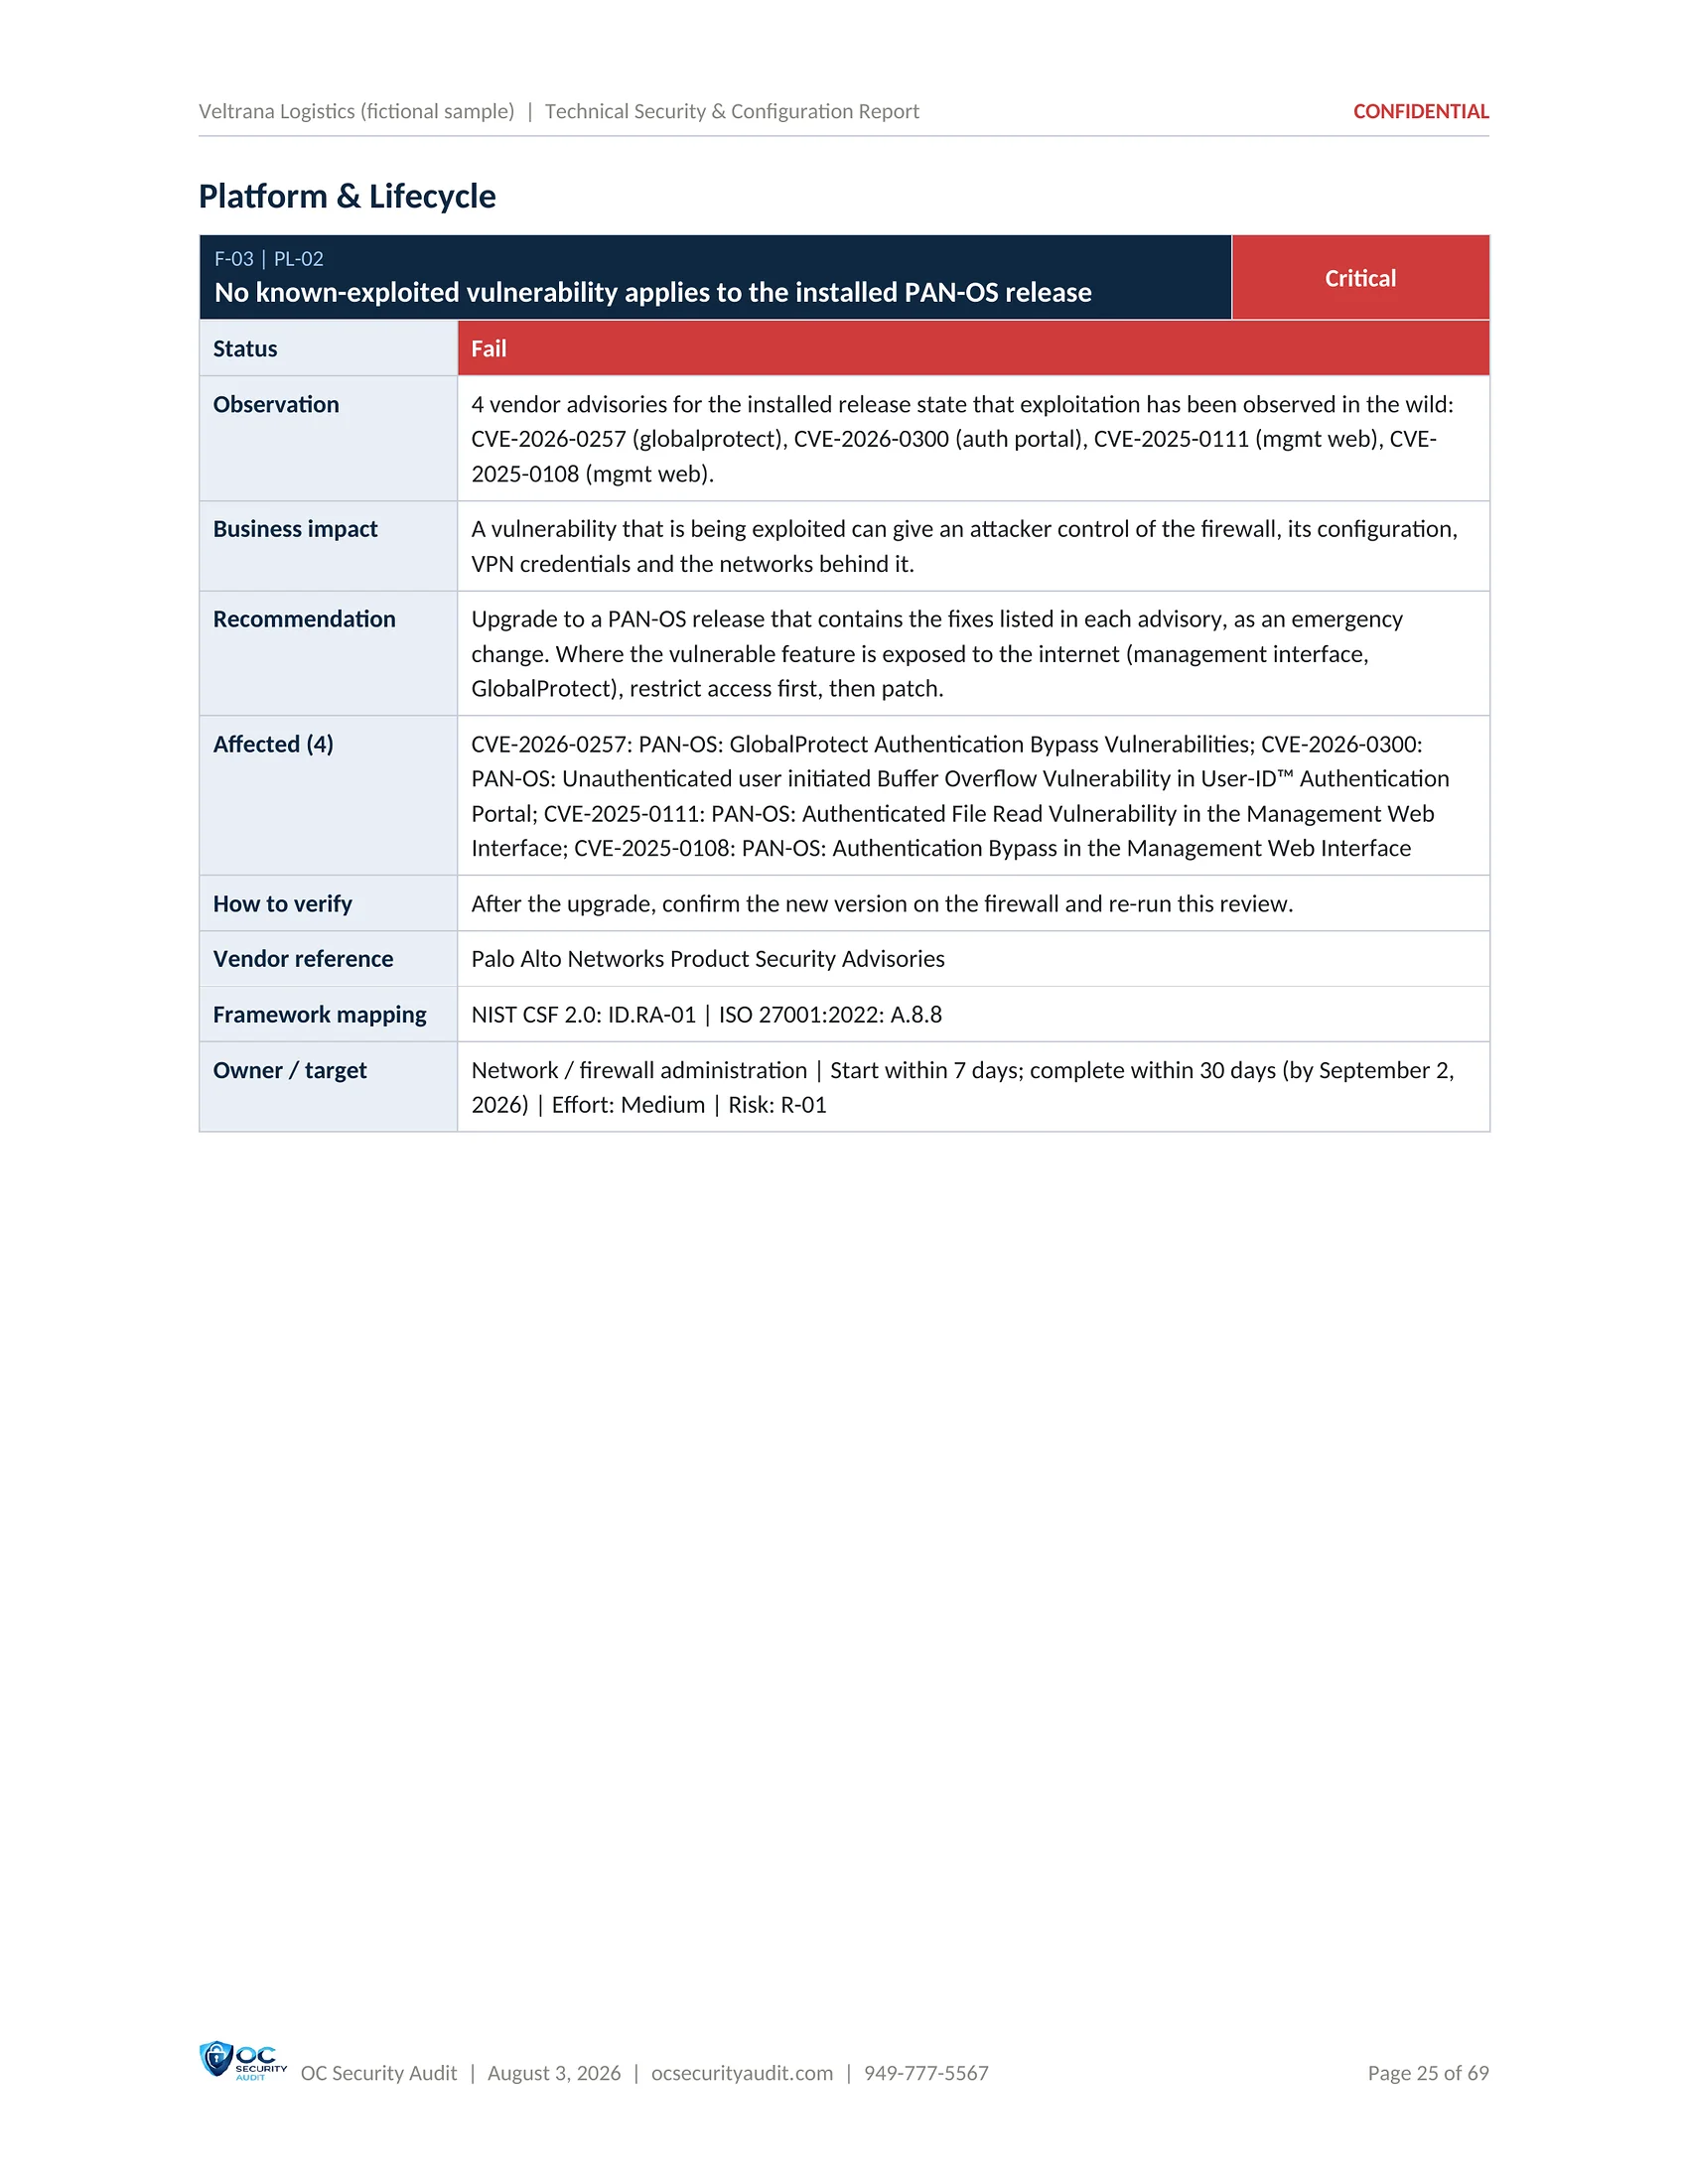
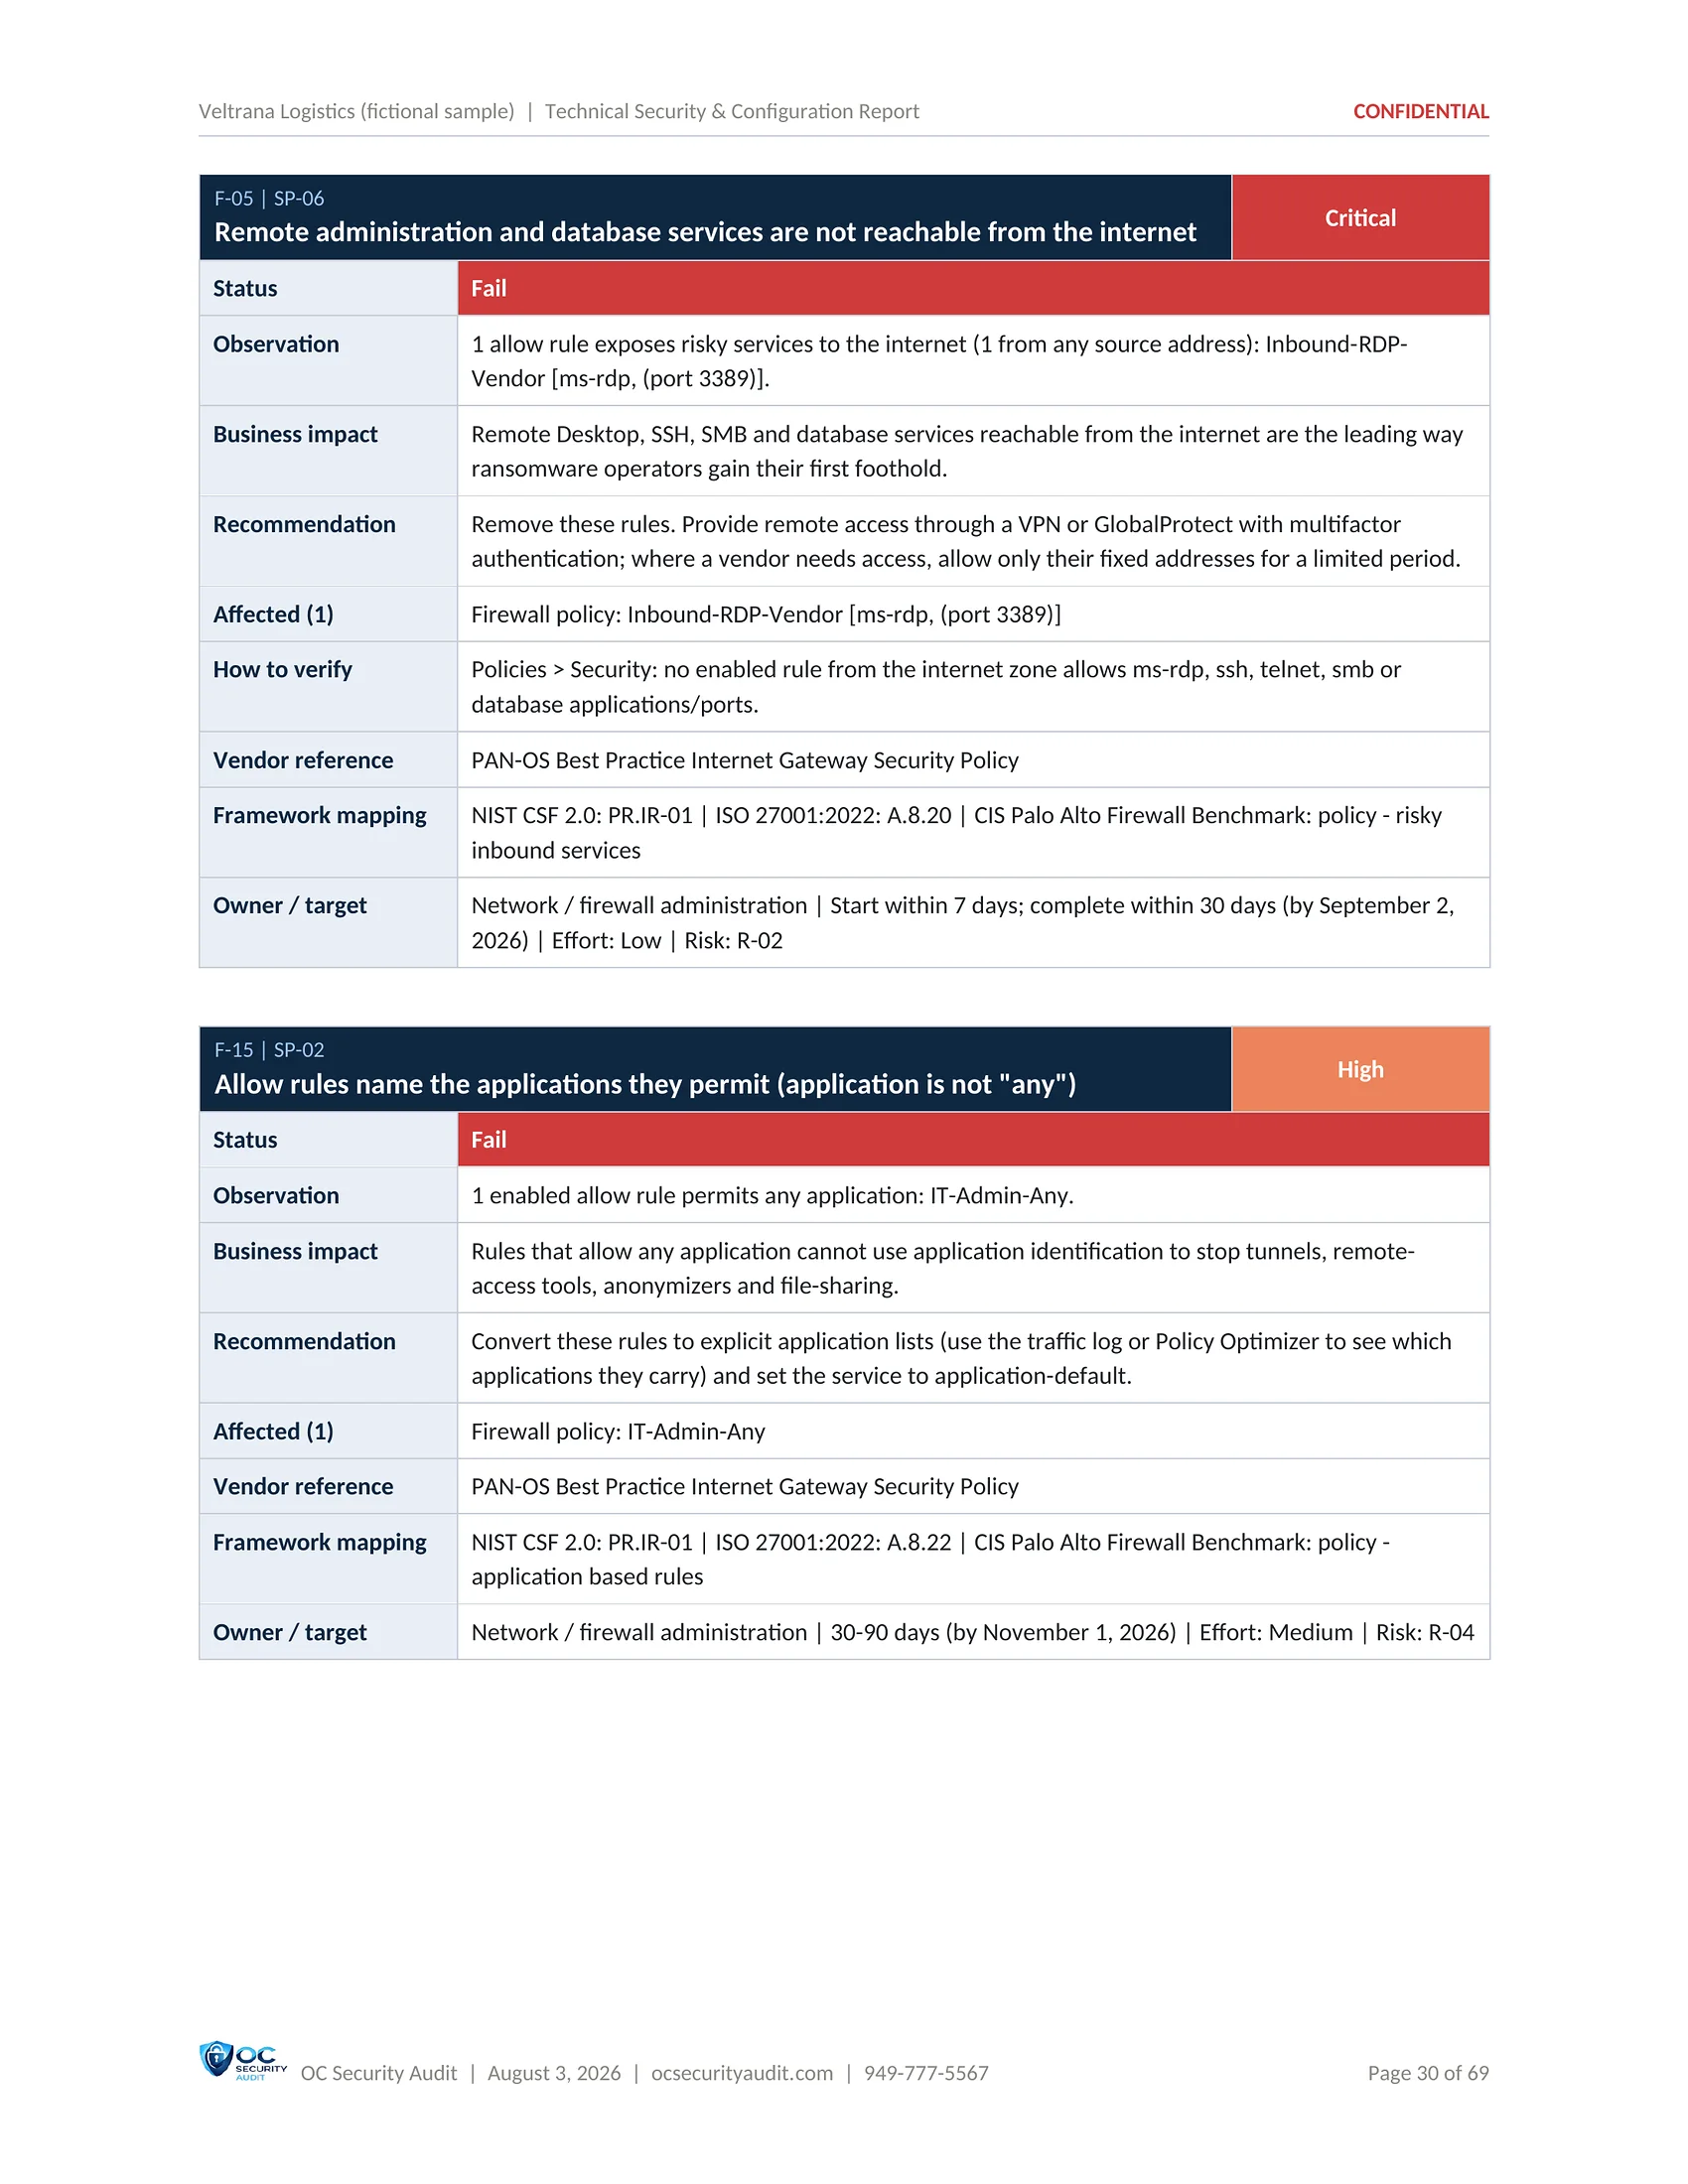
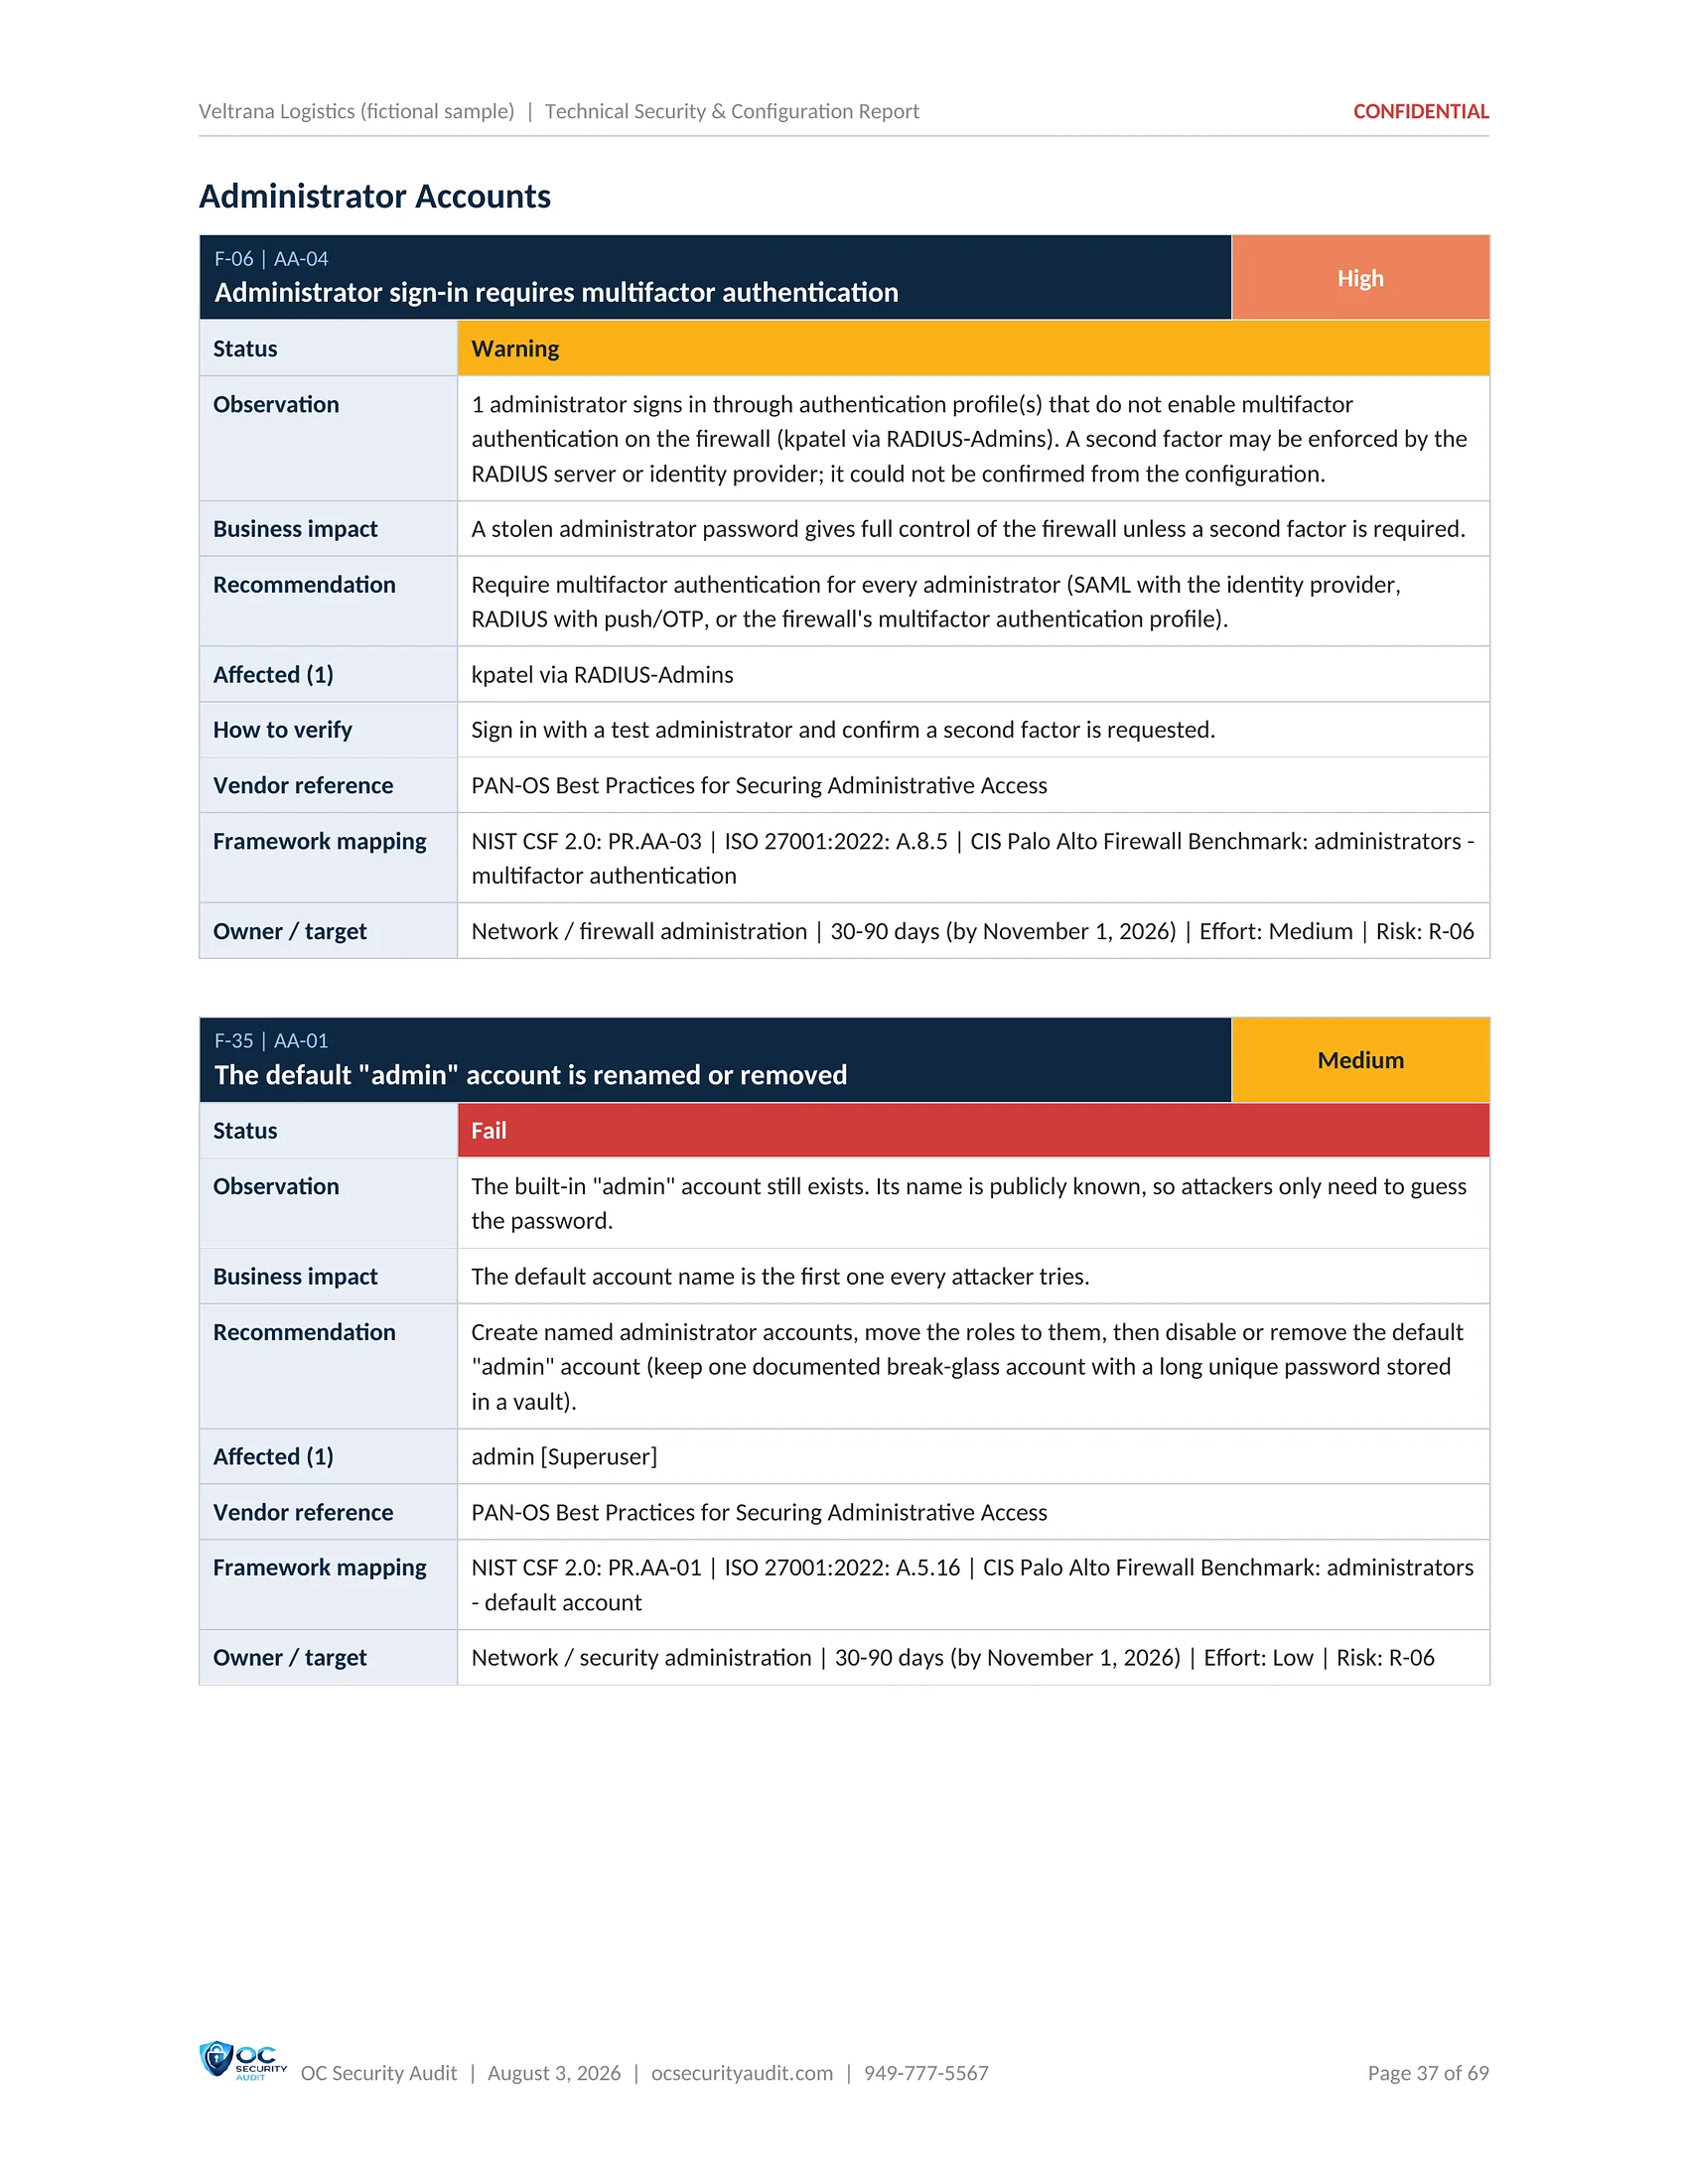
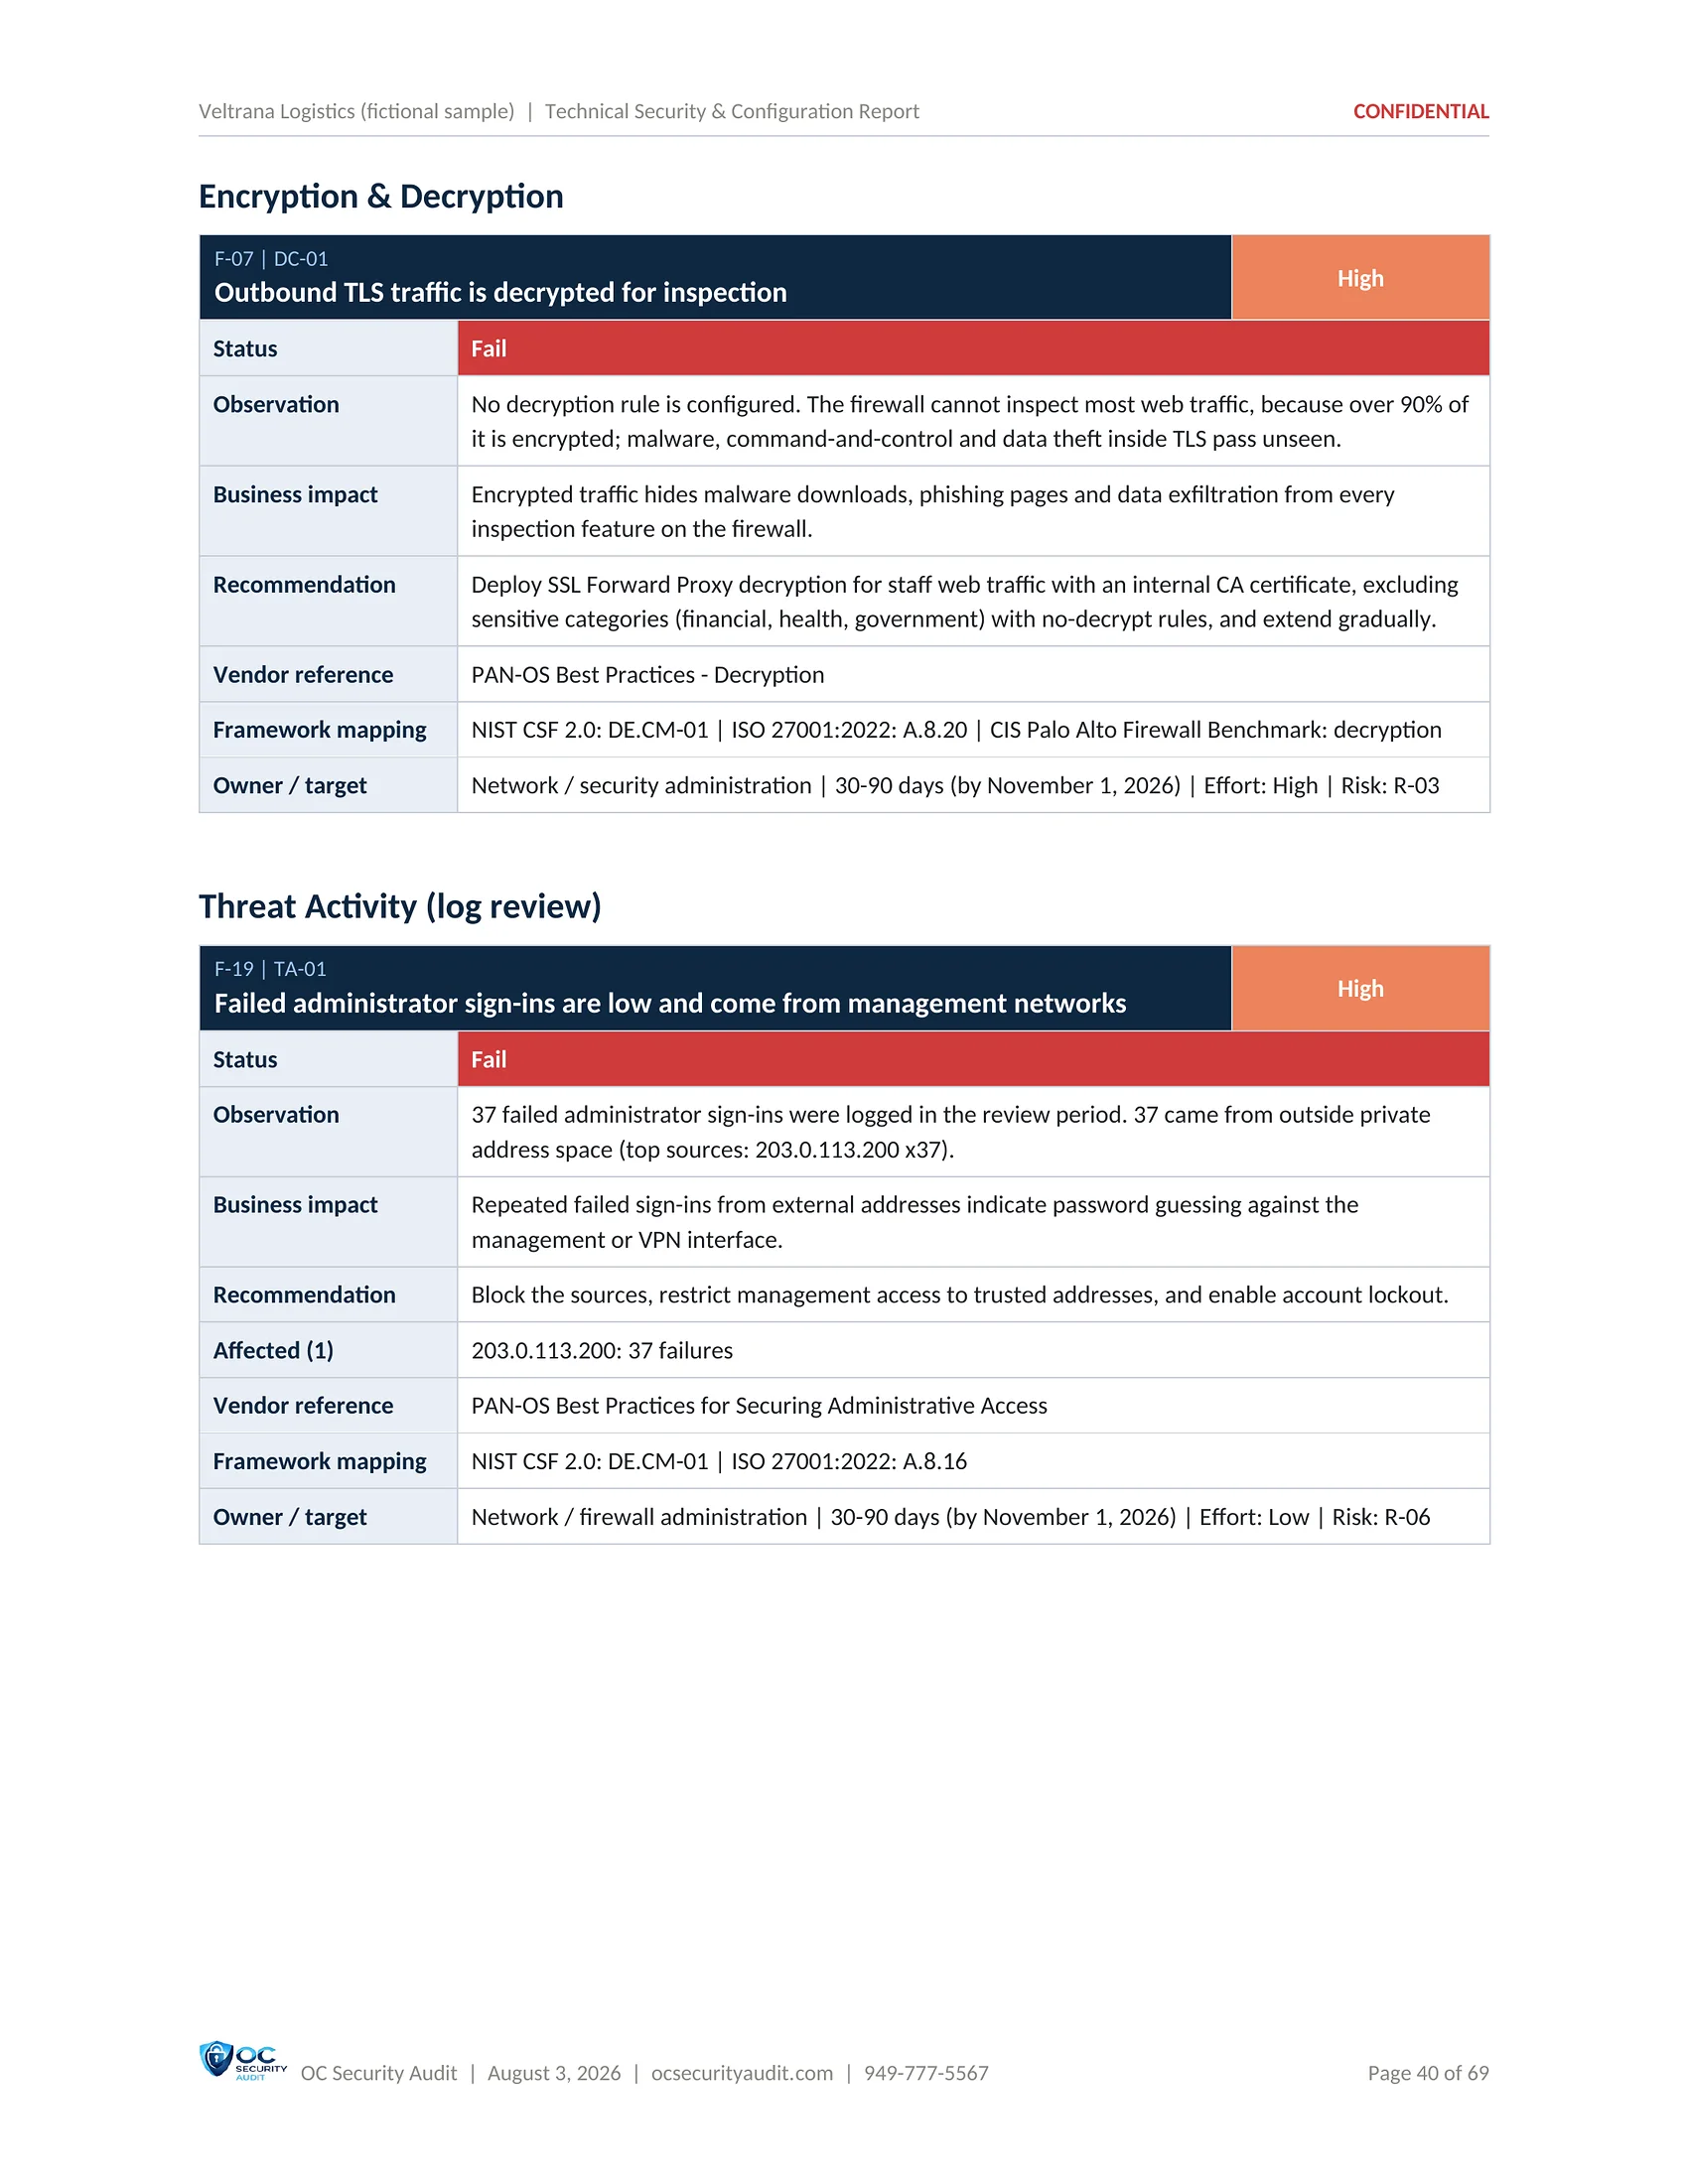
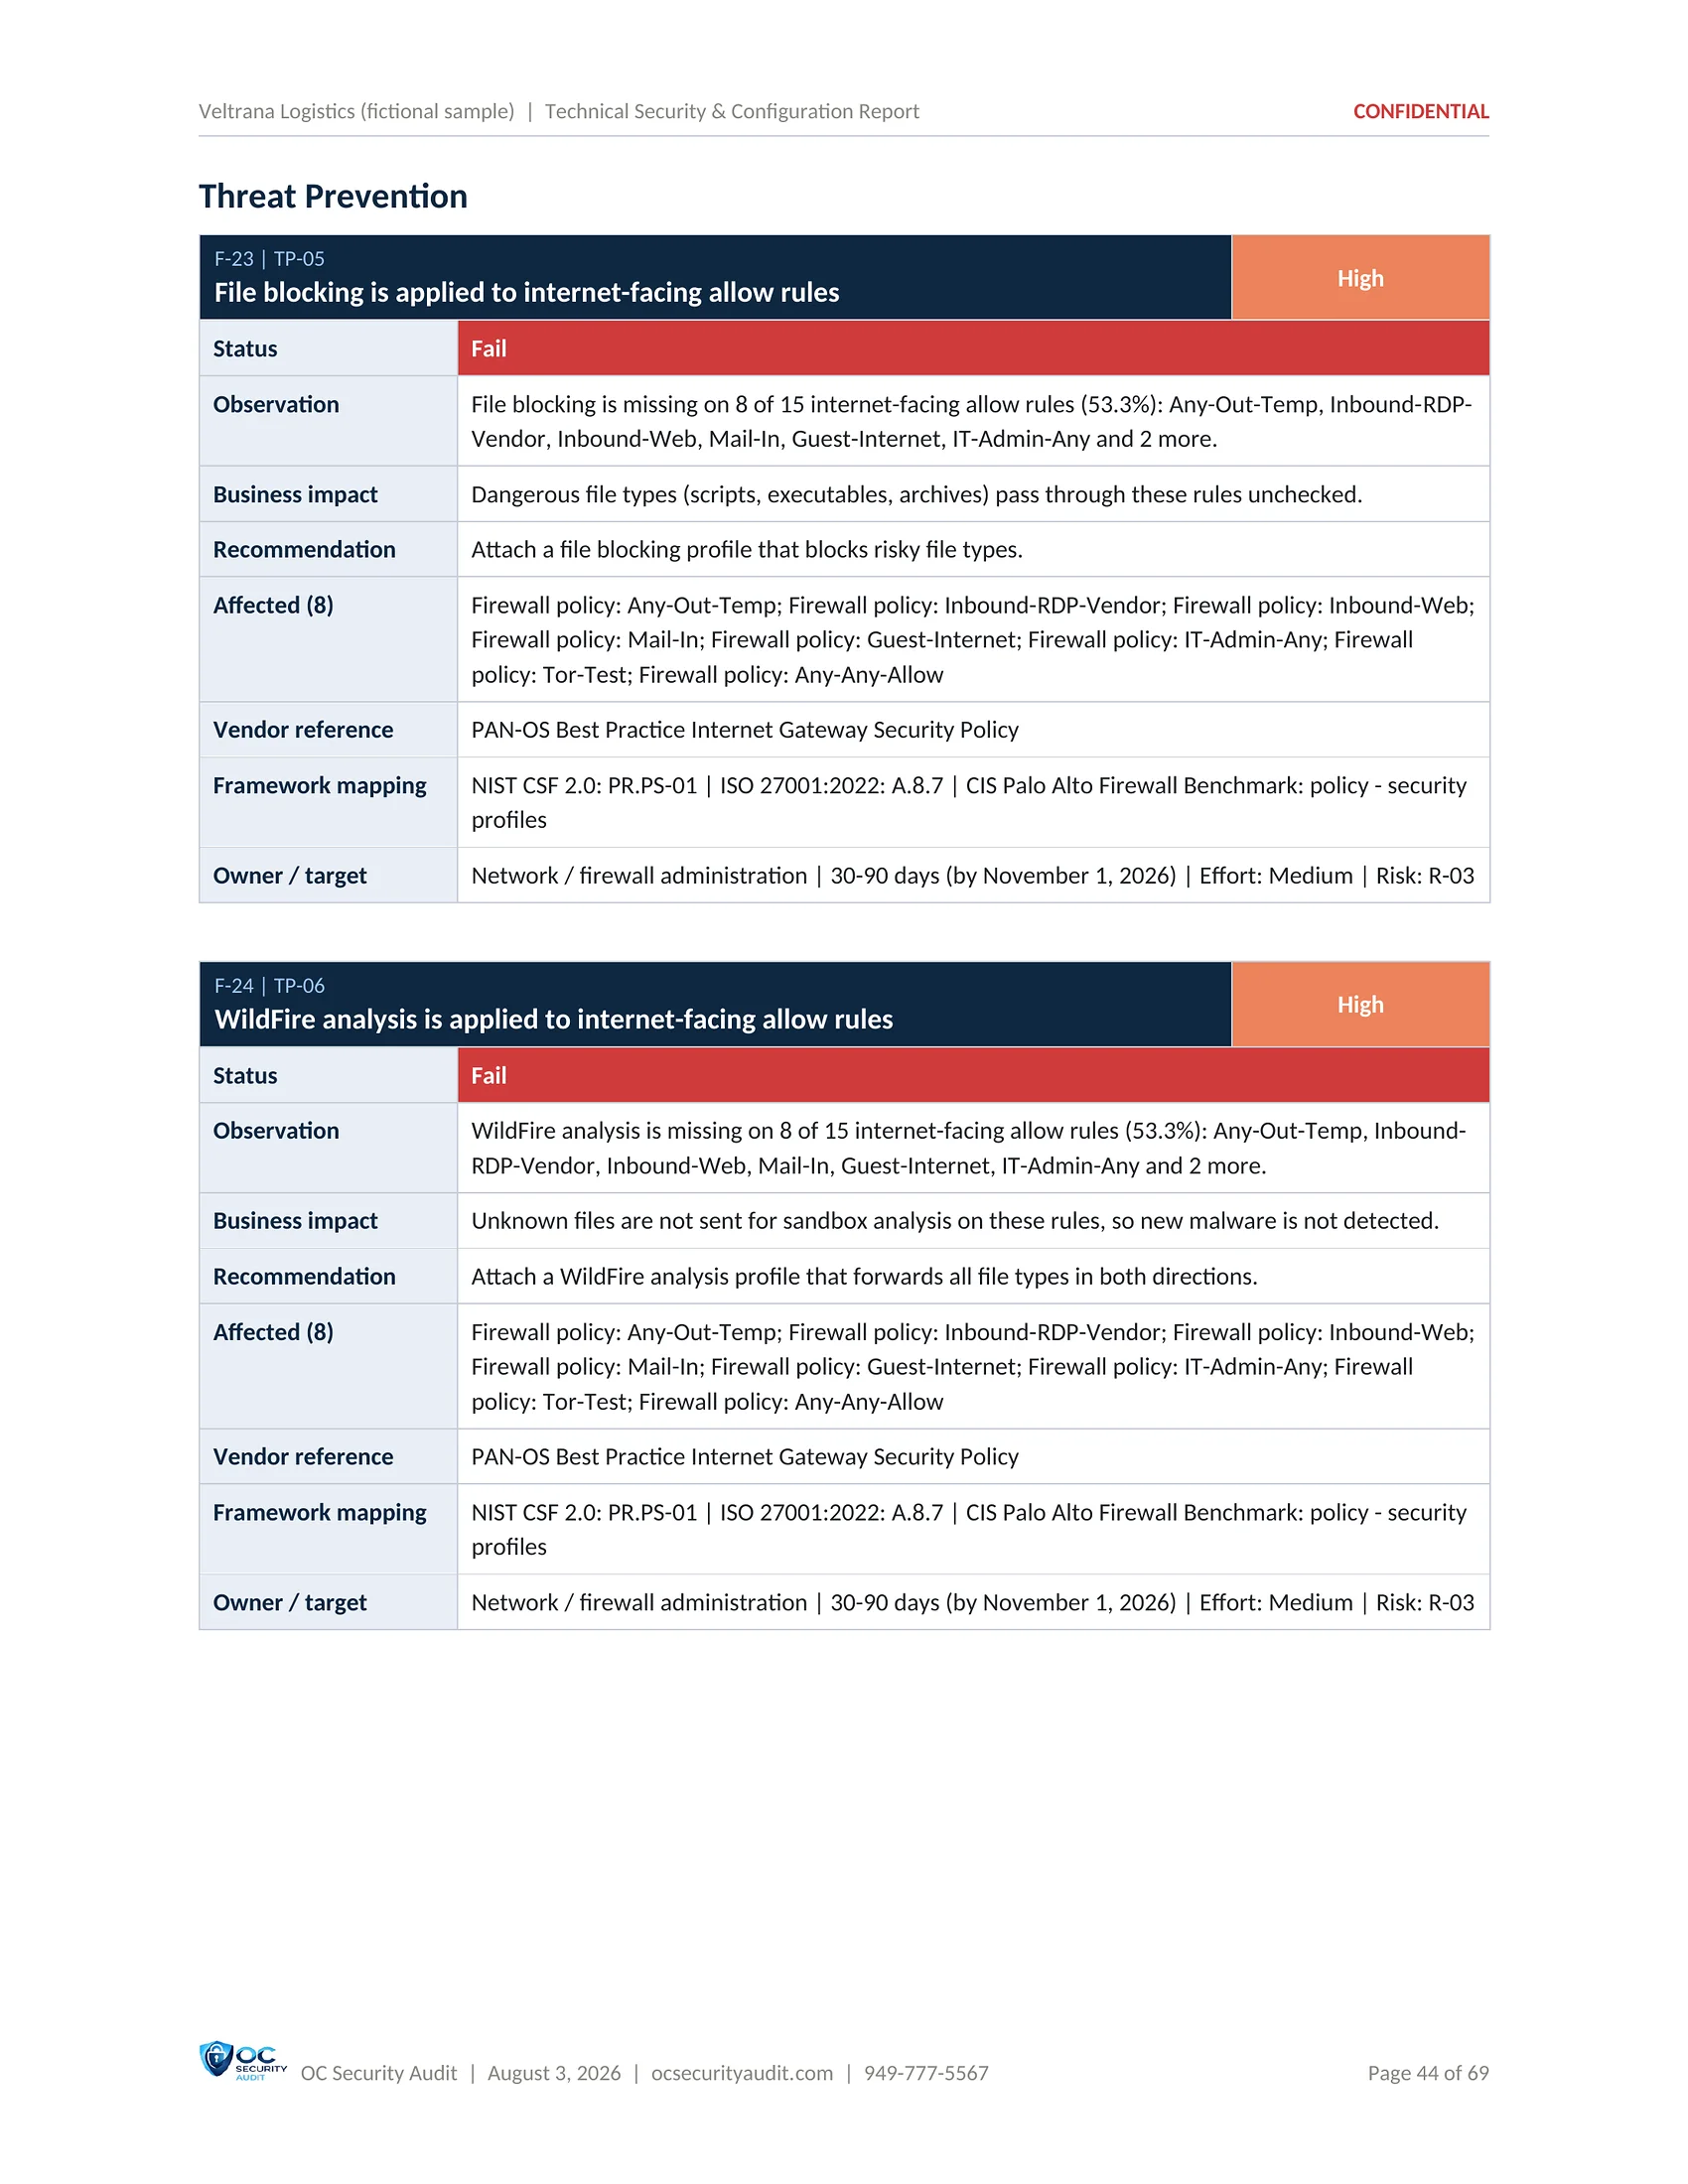
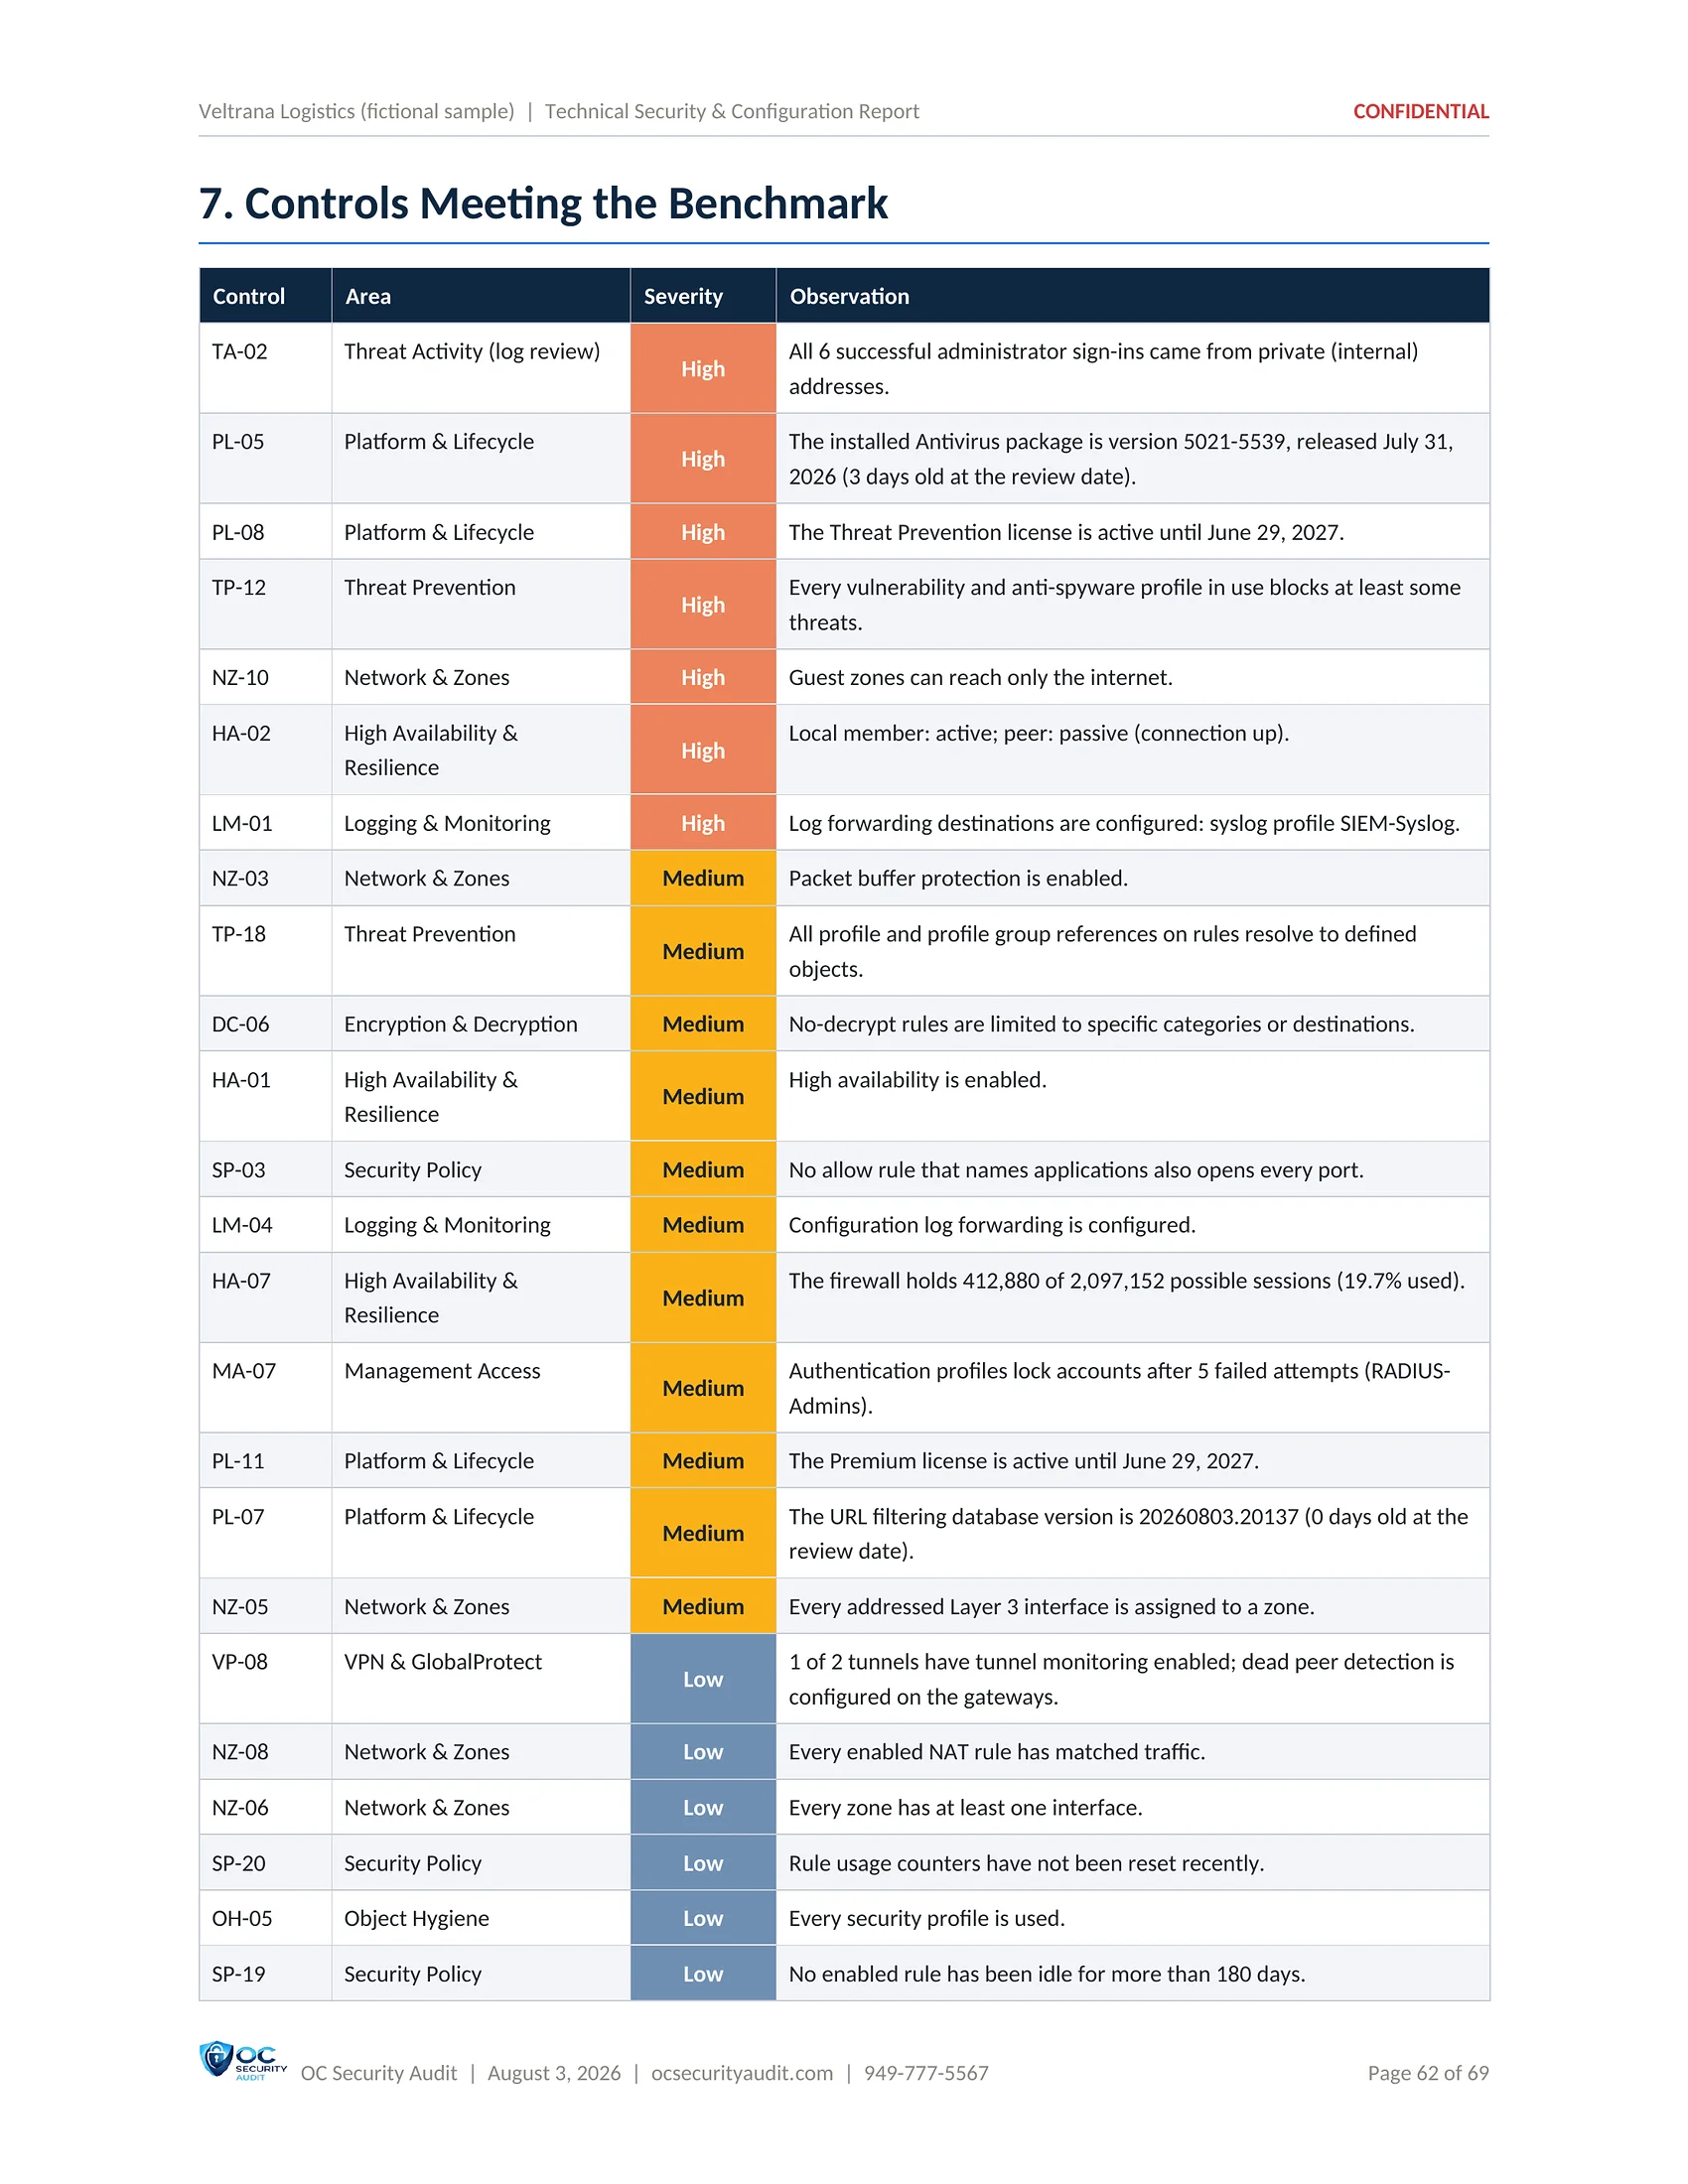
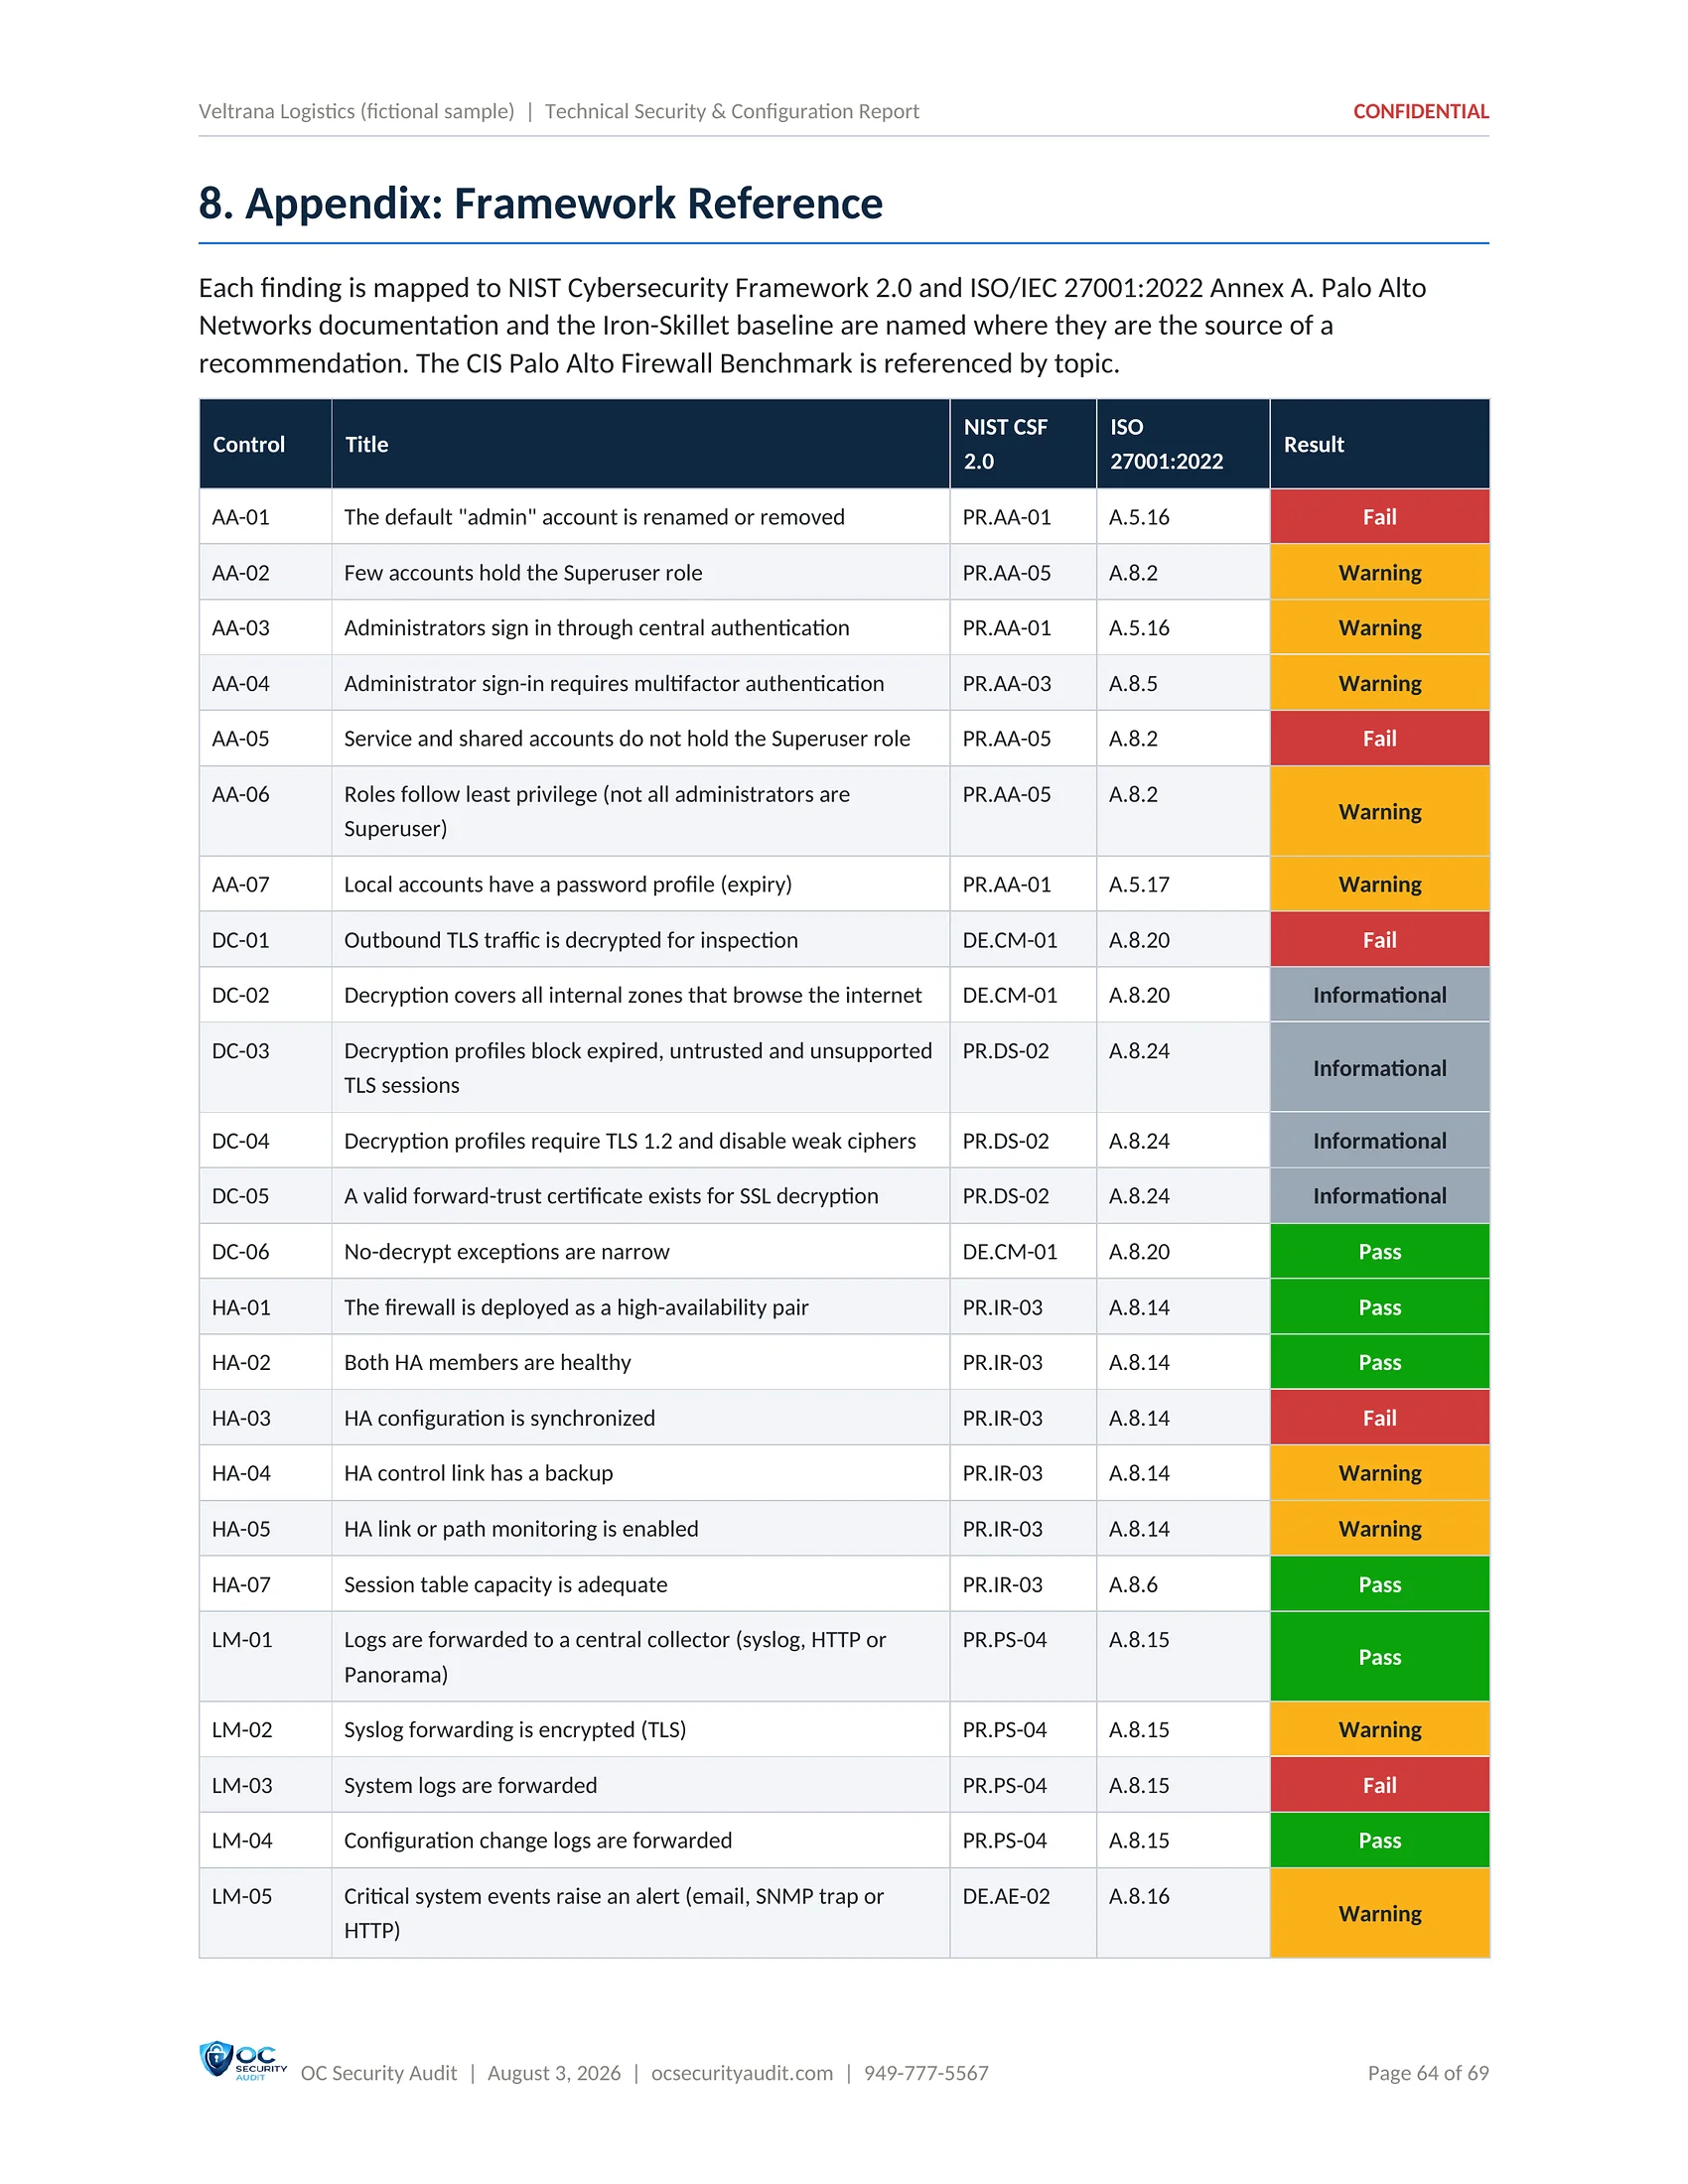
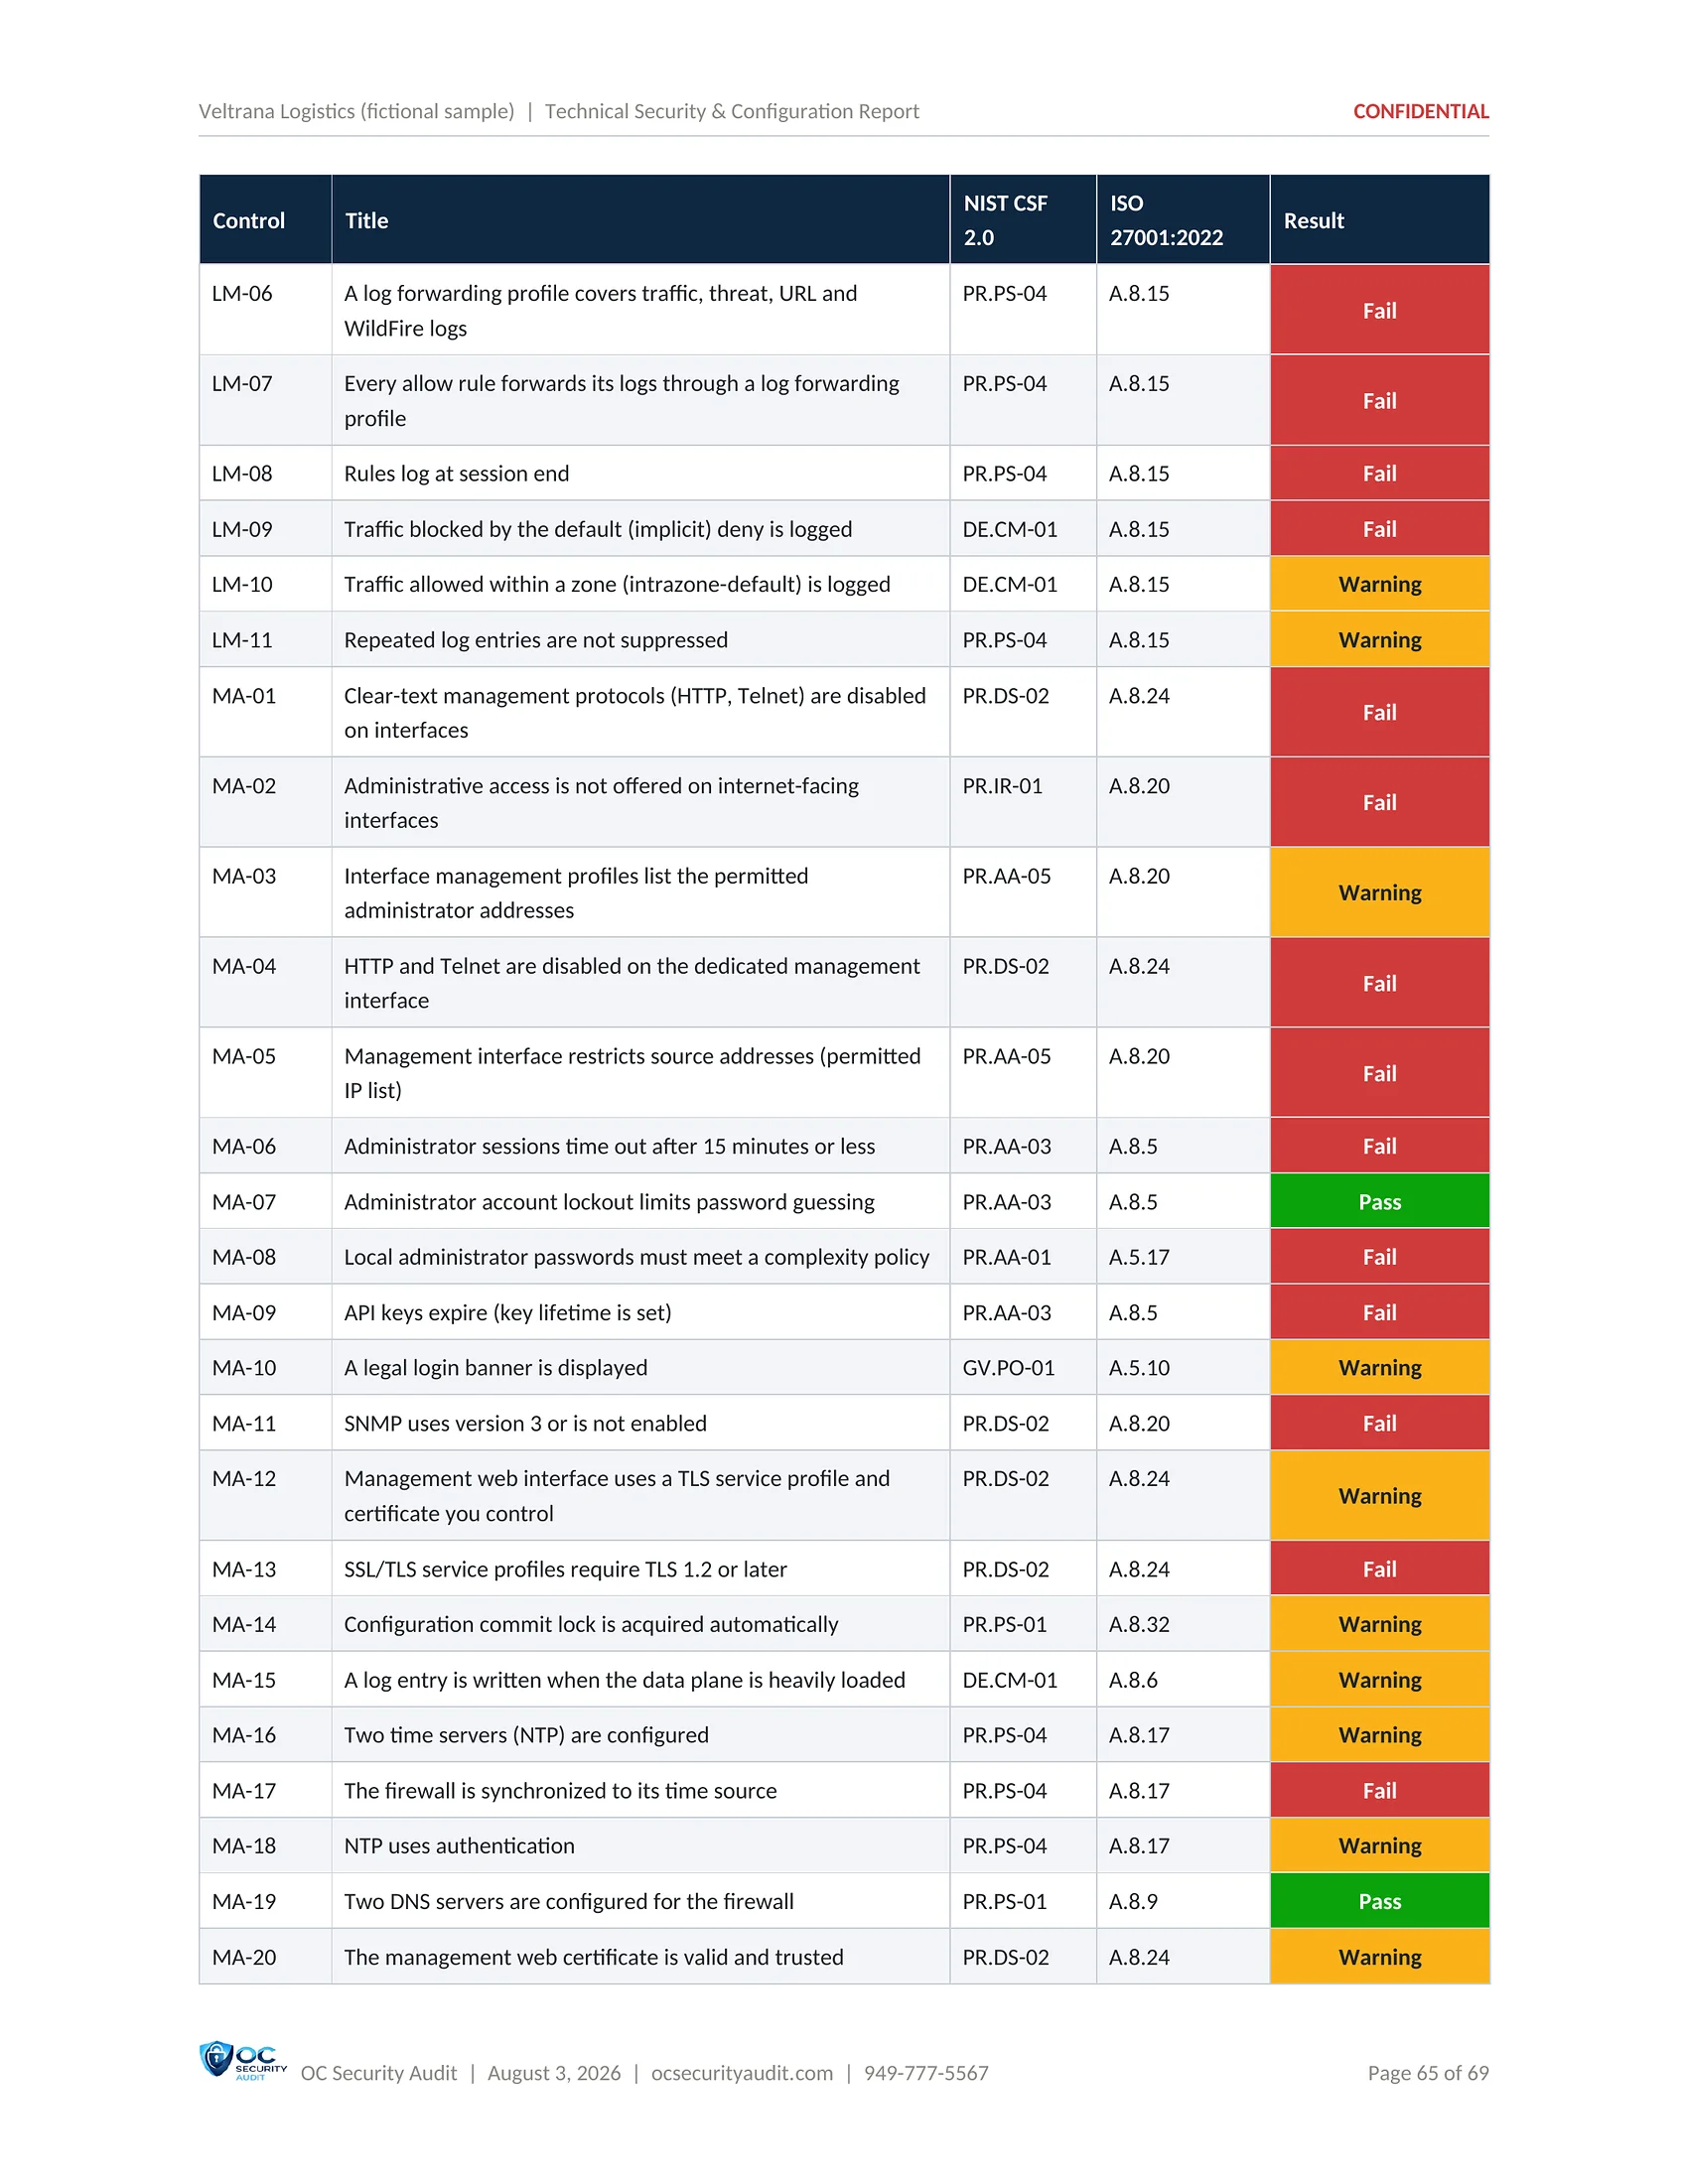
Click the centre page to open it full size. Use the arrows, the thumbnails or your arrow keys to move between pages.
Deliverable 3 of 7 · PDF, landscape · 6 pages
Firewall Rulebase Review
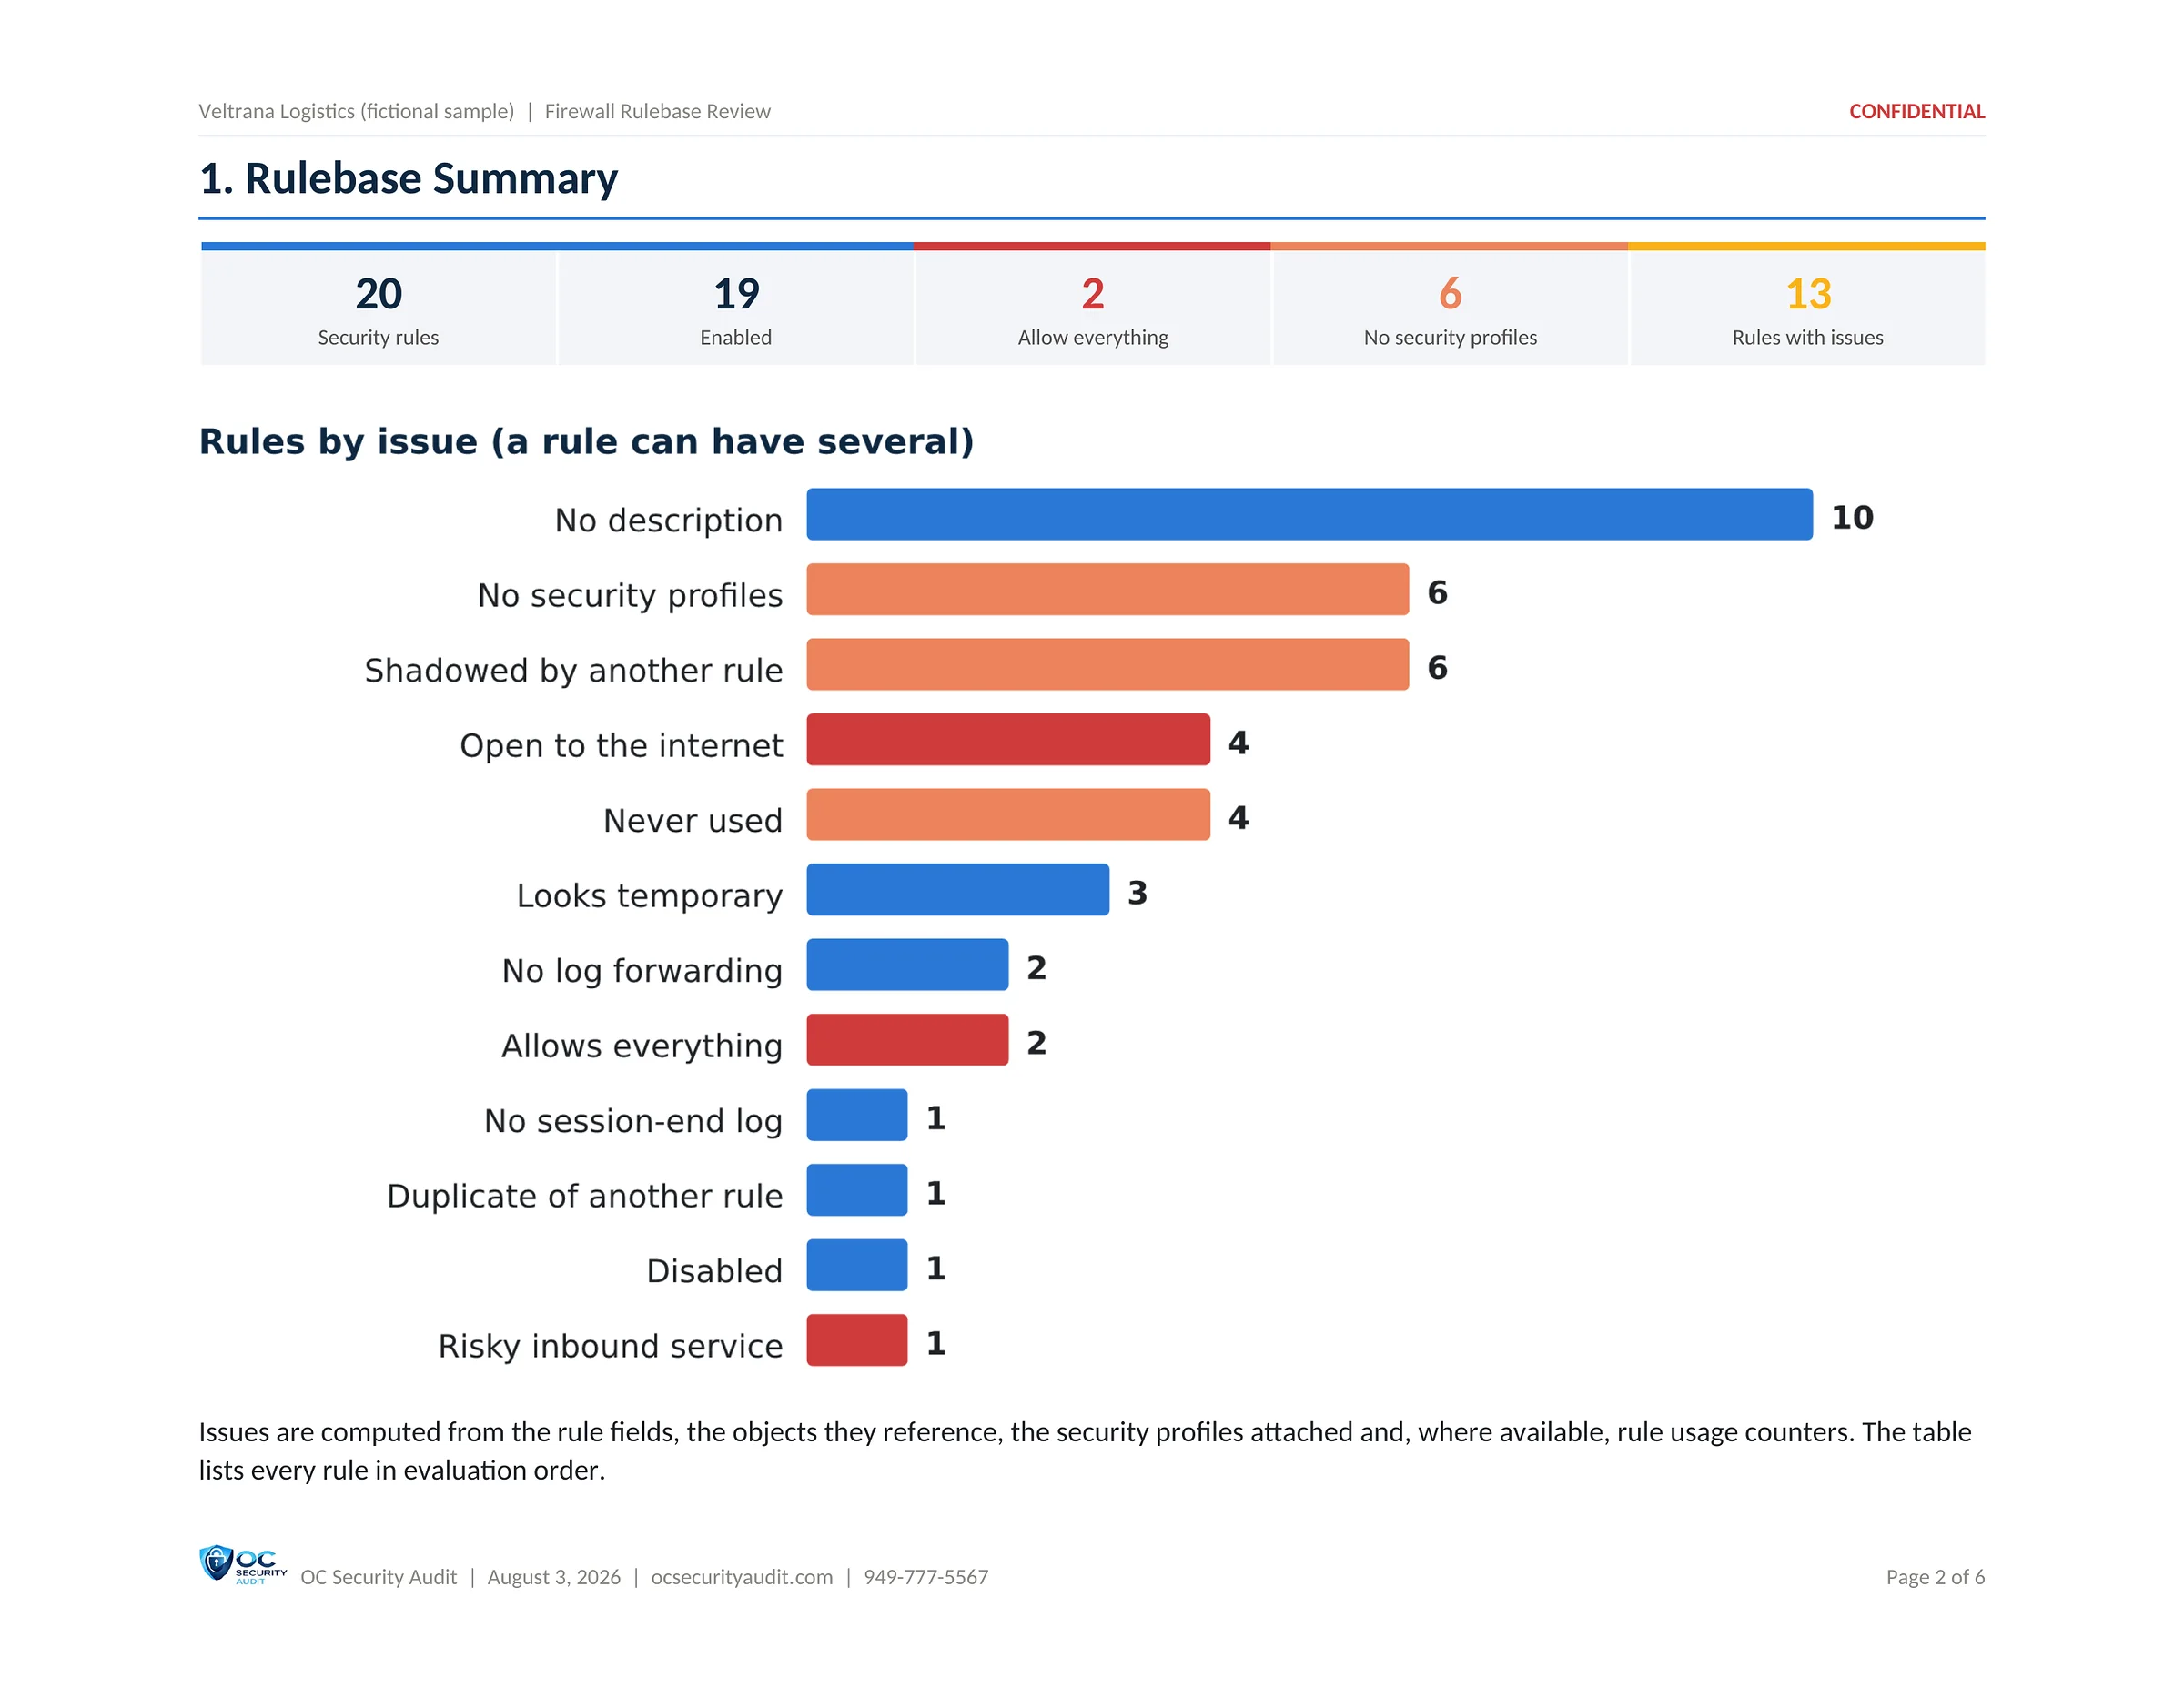
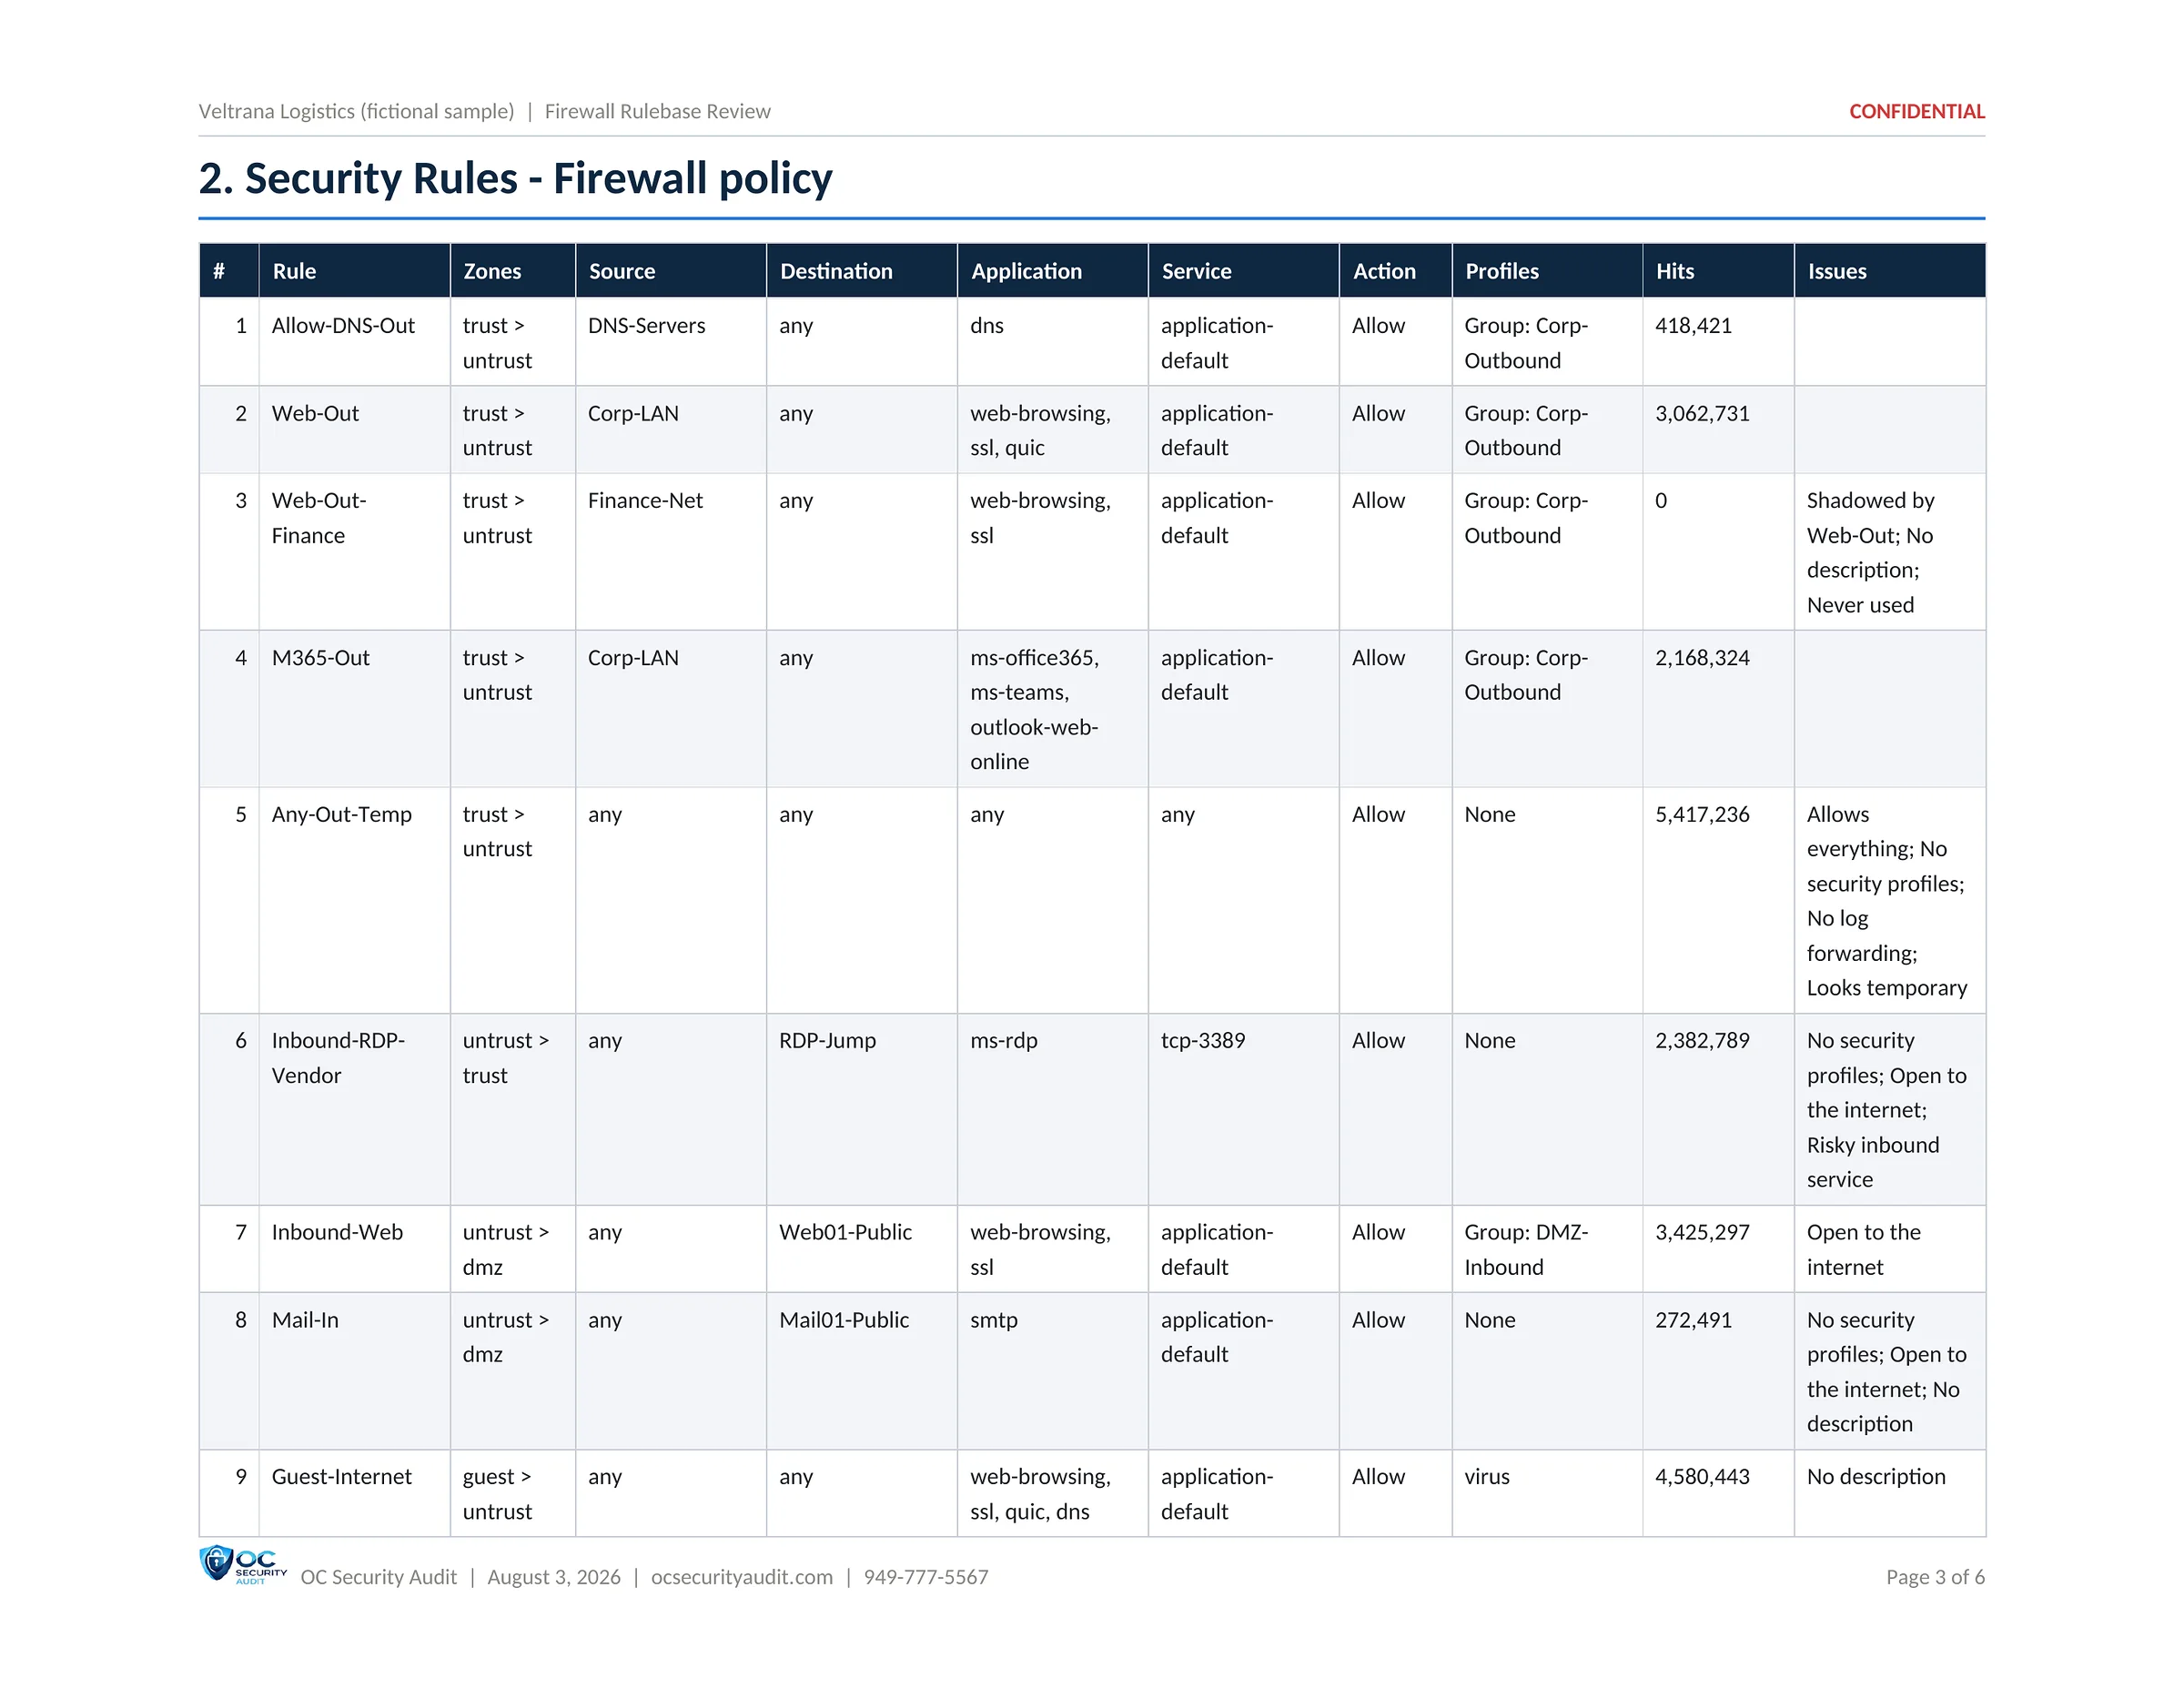
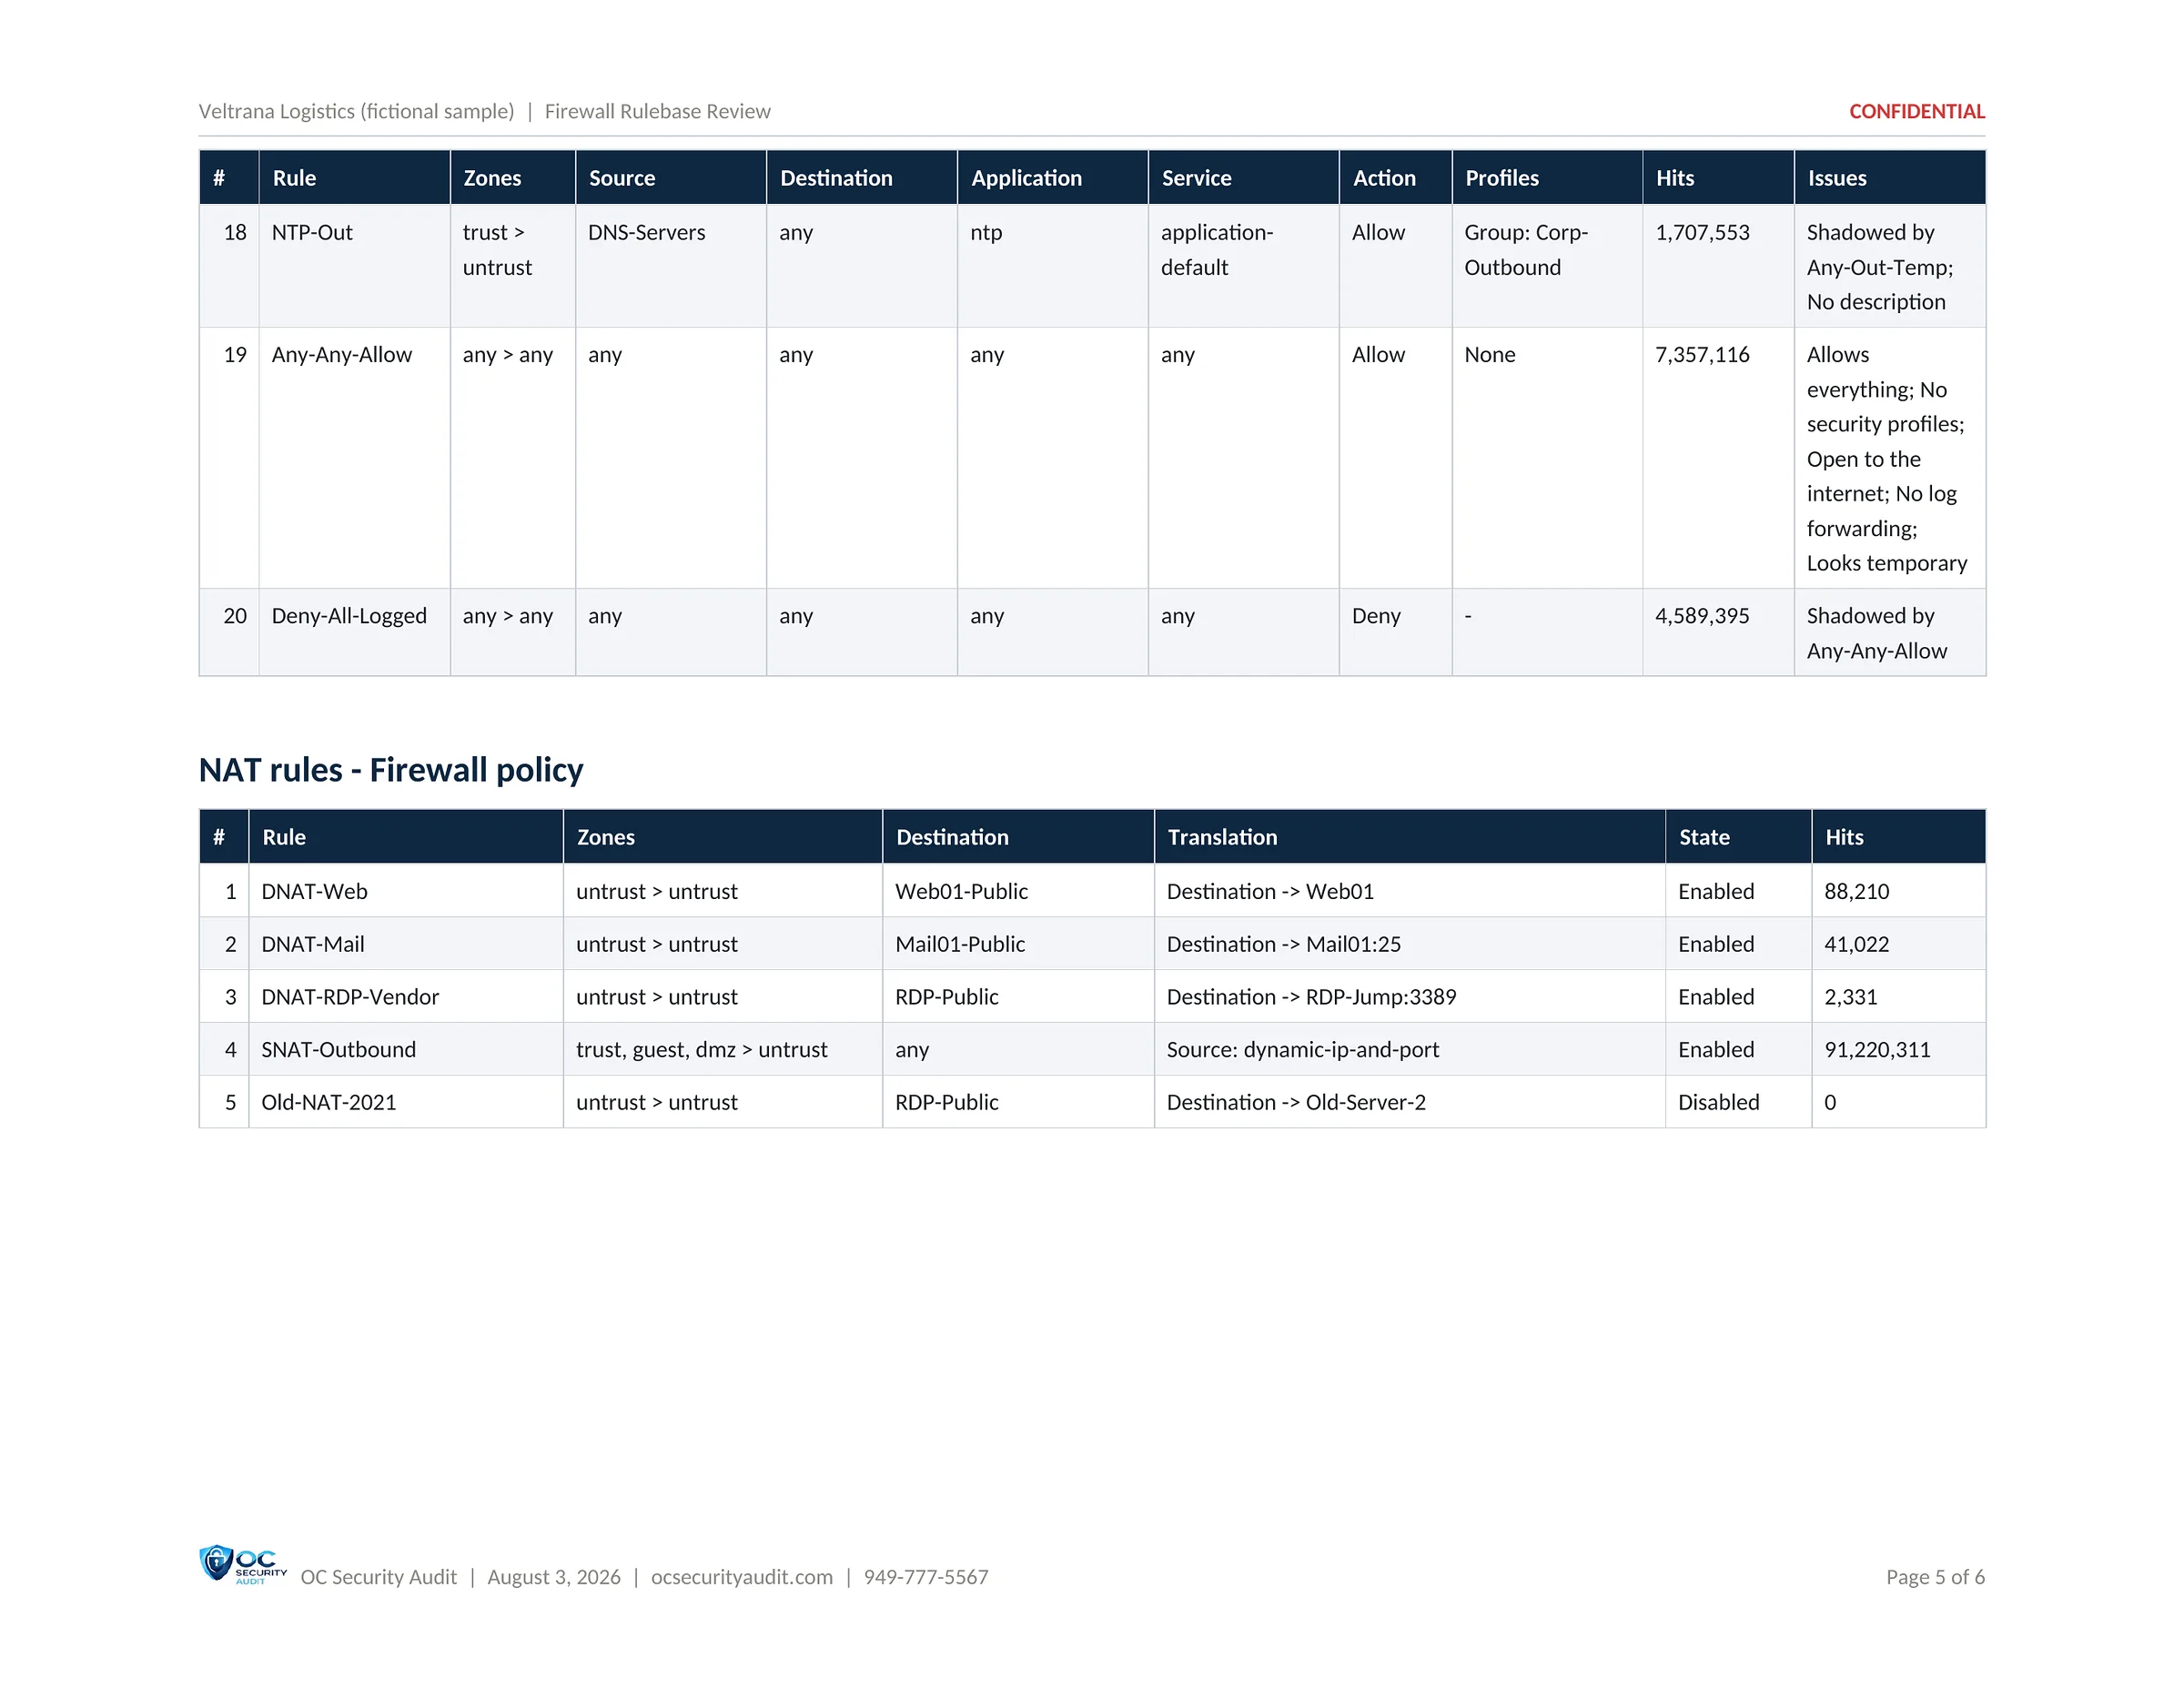
Every security rule in the order the firewall evaluates it, with the issues found on each one. This is the list your administrator works through to remove risky, unused and shadowed rules without guessing.
Who uses it
Firewall administrators, change advisory board
What is included
- Rule counts: total, enabled, allow everything, no profiles, with issues
- Chart of rules by issue type
- Zones, source, destination, application and service per rule
- Action, security profiles and hit counts
- Flags such as shadowed, never used, no description, open to the internet
- NAT rules
- Decryption rules
Click the centre page to open it full size. Use the arrows, the thumbnails or your arrow keys to move between pages.
Deliverable 4 of 7 · PDF · 5 pages
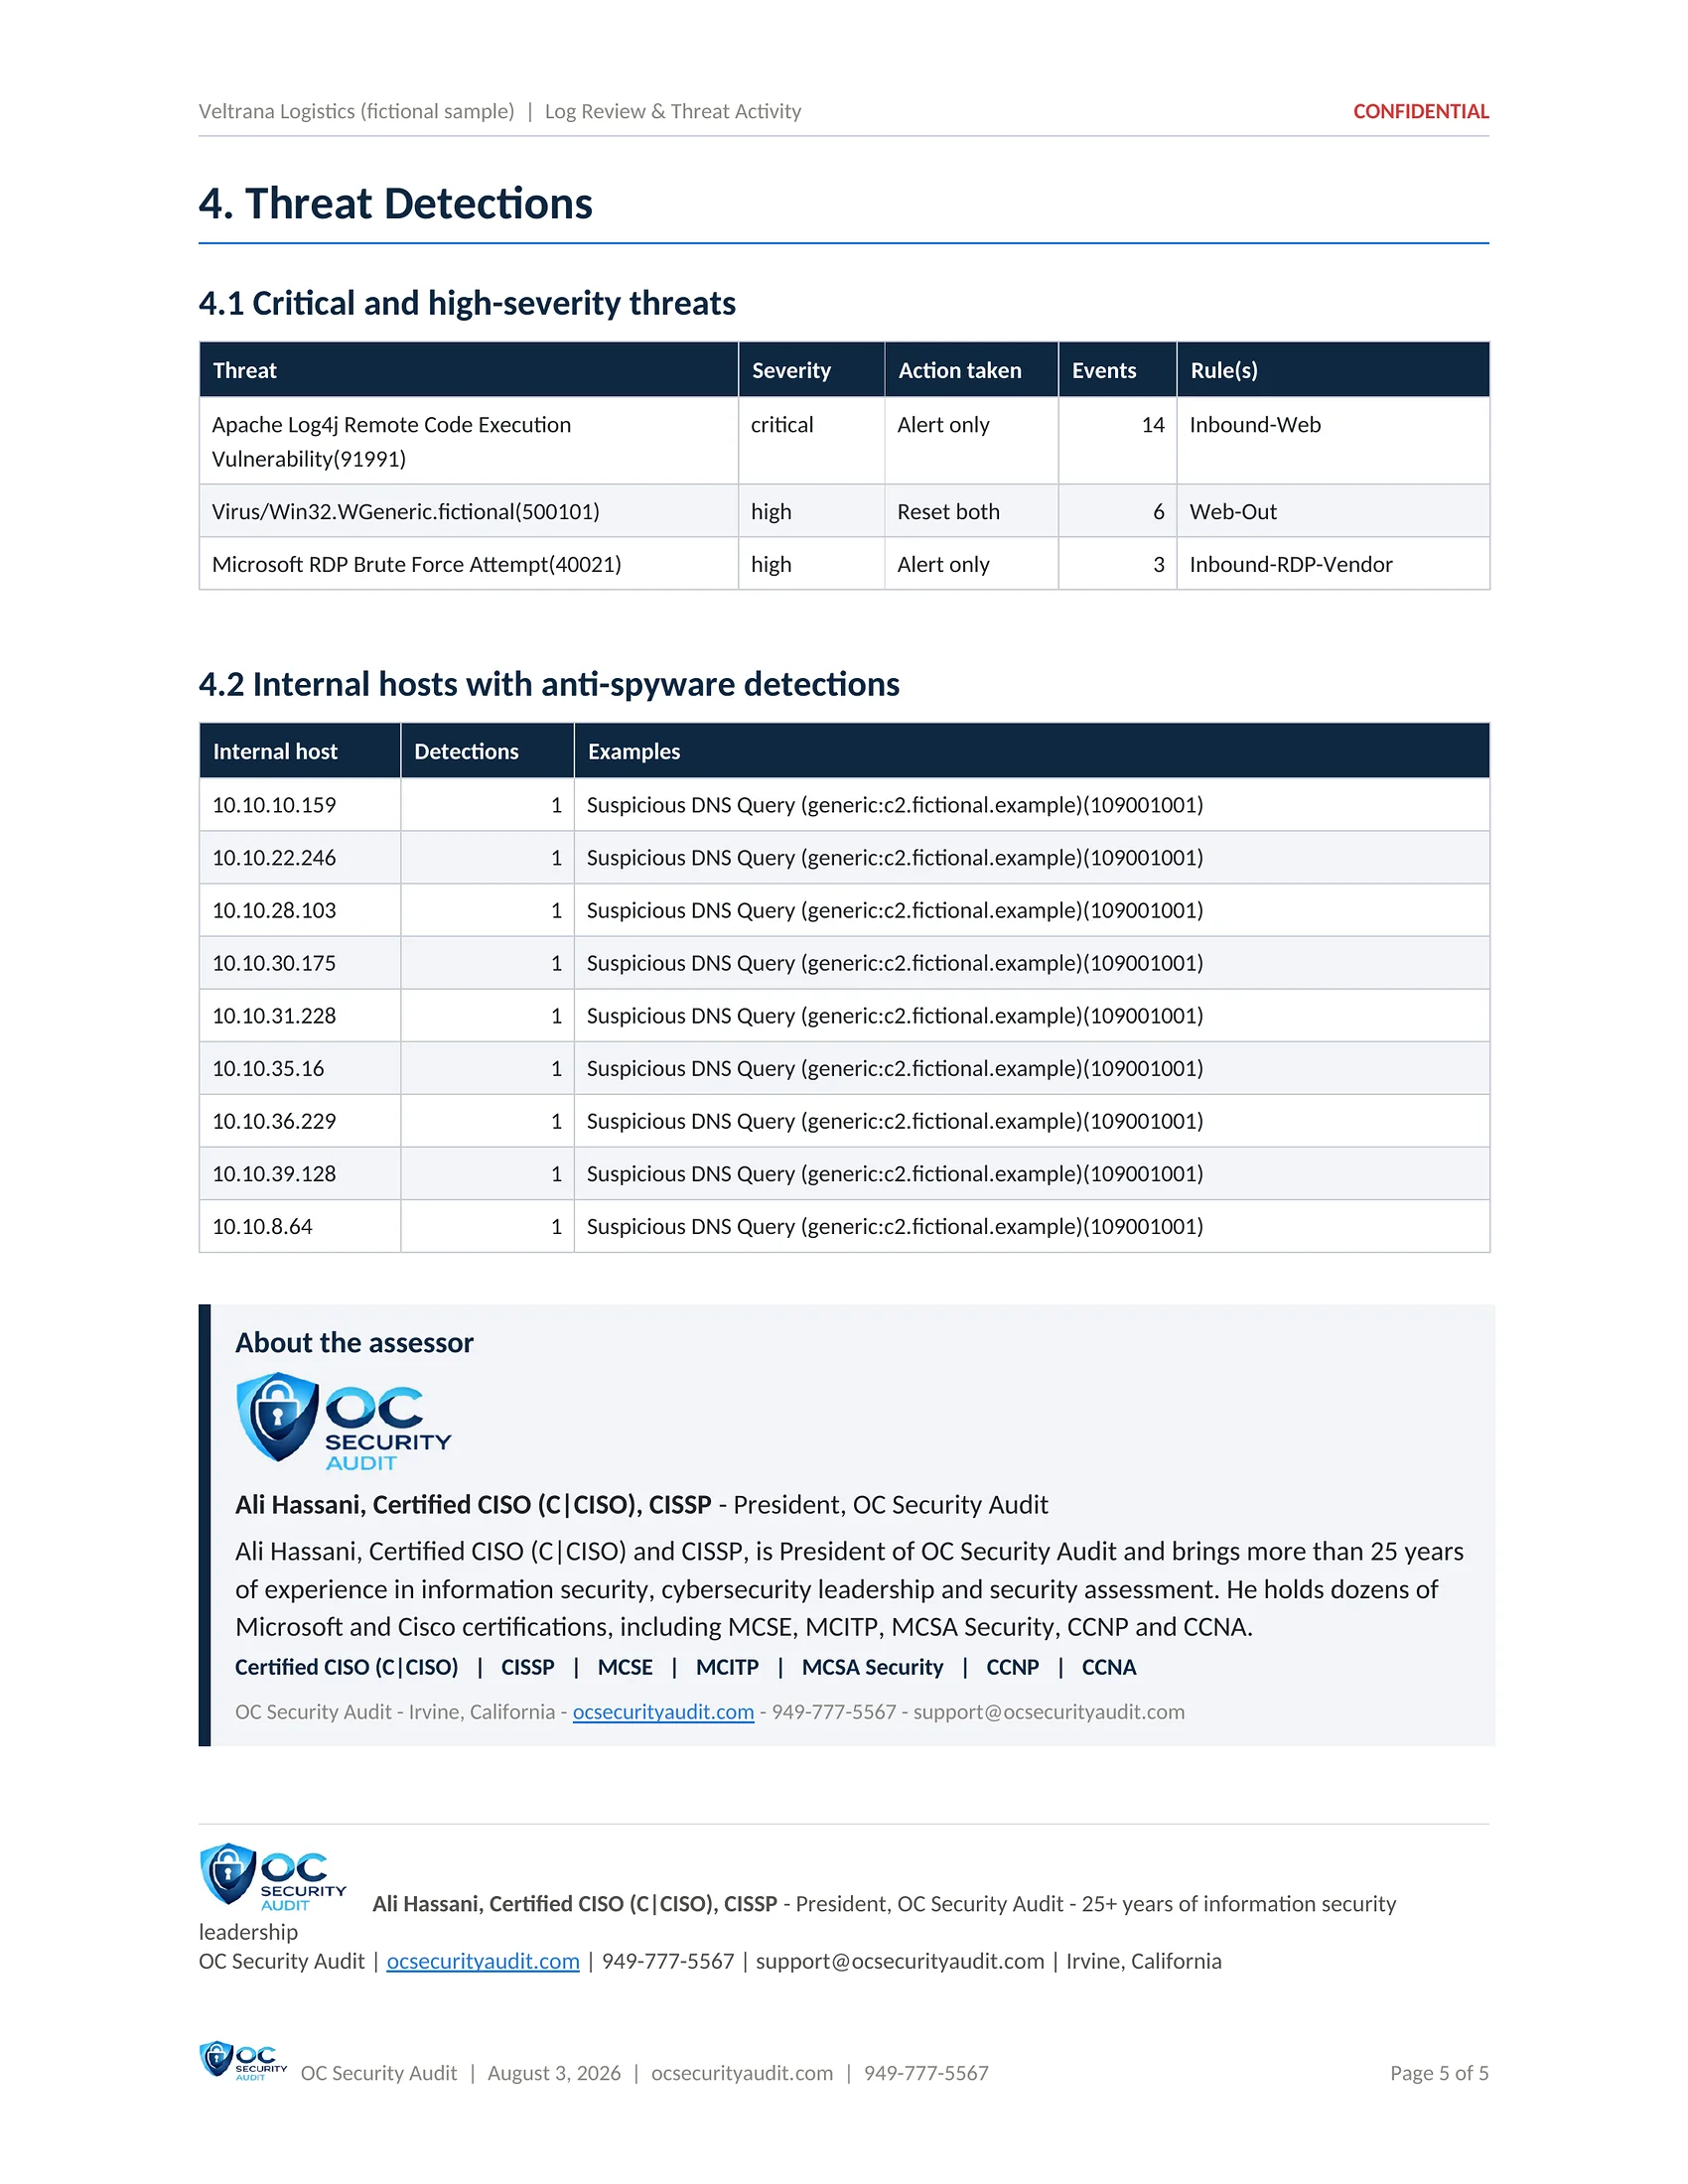
Log Review & Threat Activity
What the firewall itself recorded over the last 7 days: who signed in and from where, what was changed, and which threats were detected and what the firewall did about them.
Who uses it
IT manager, security operations, incident response
What is included
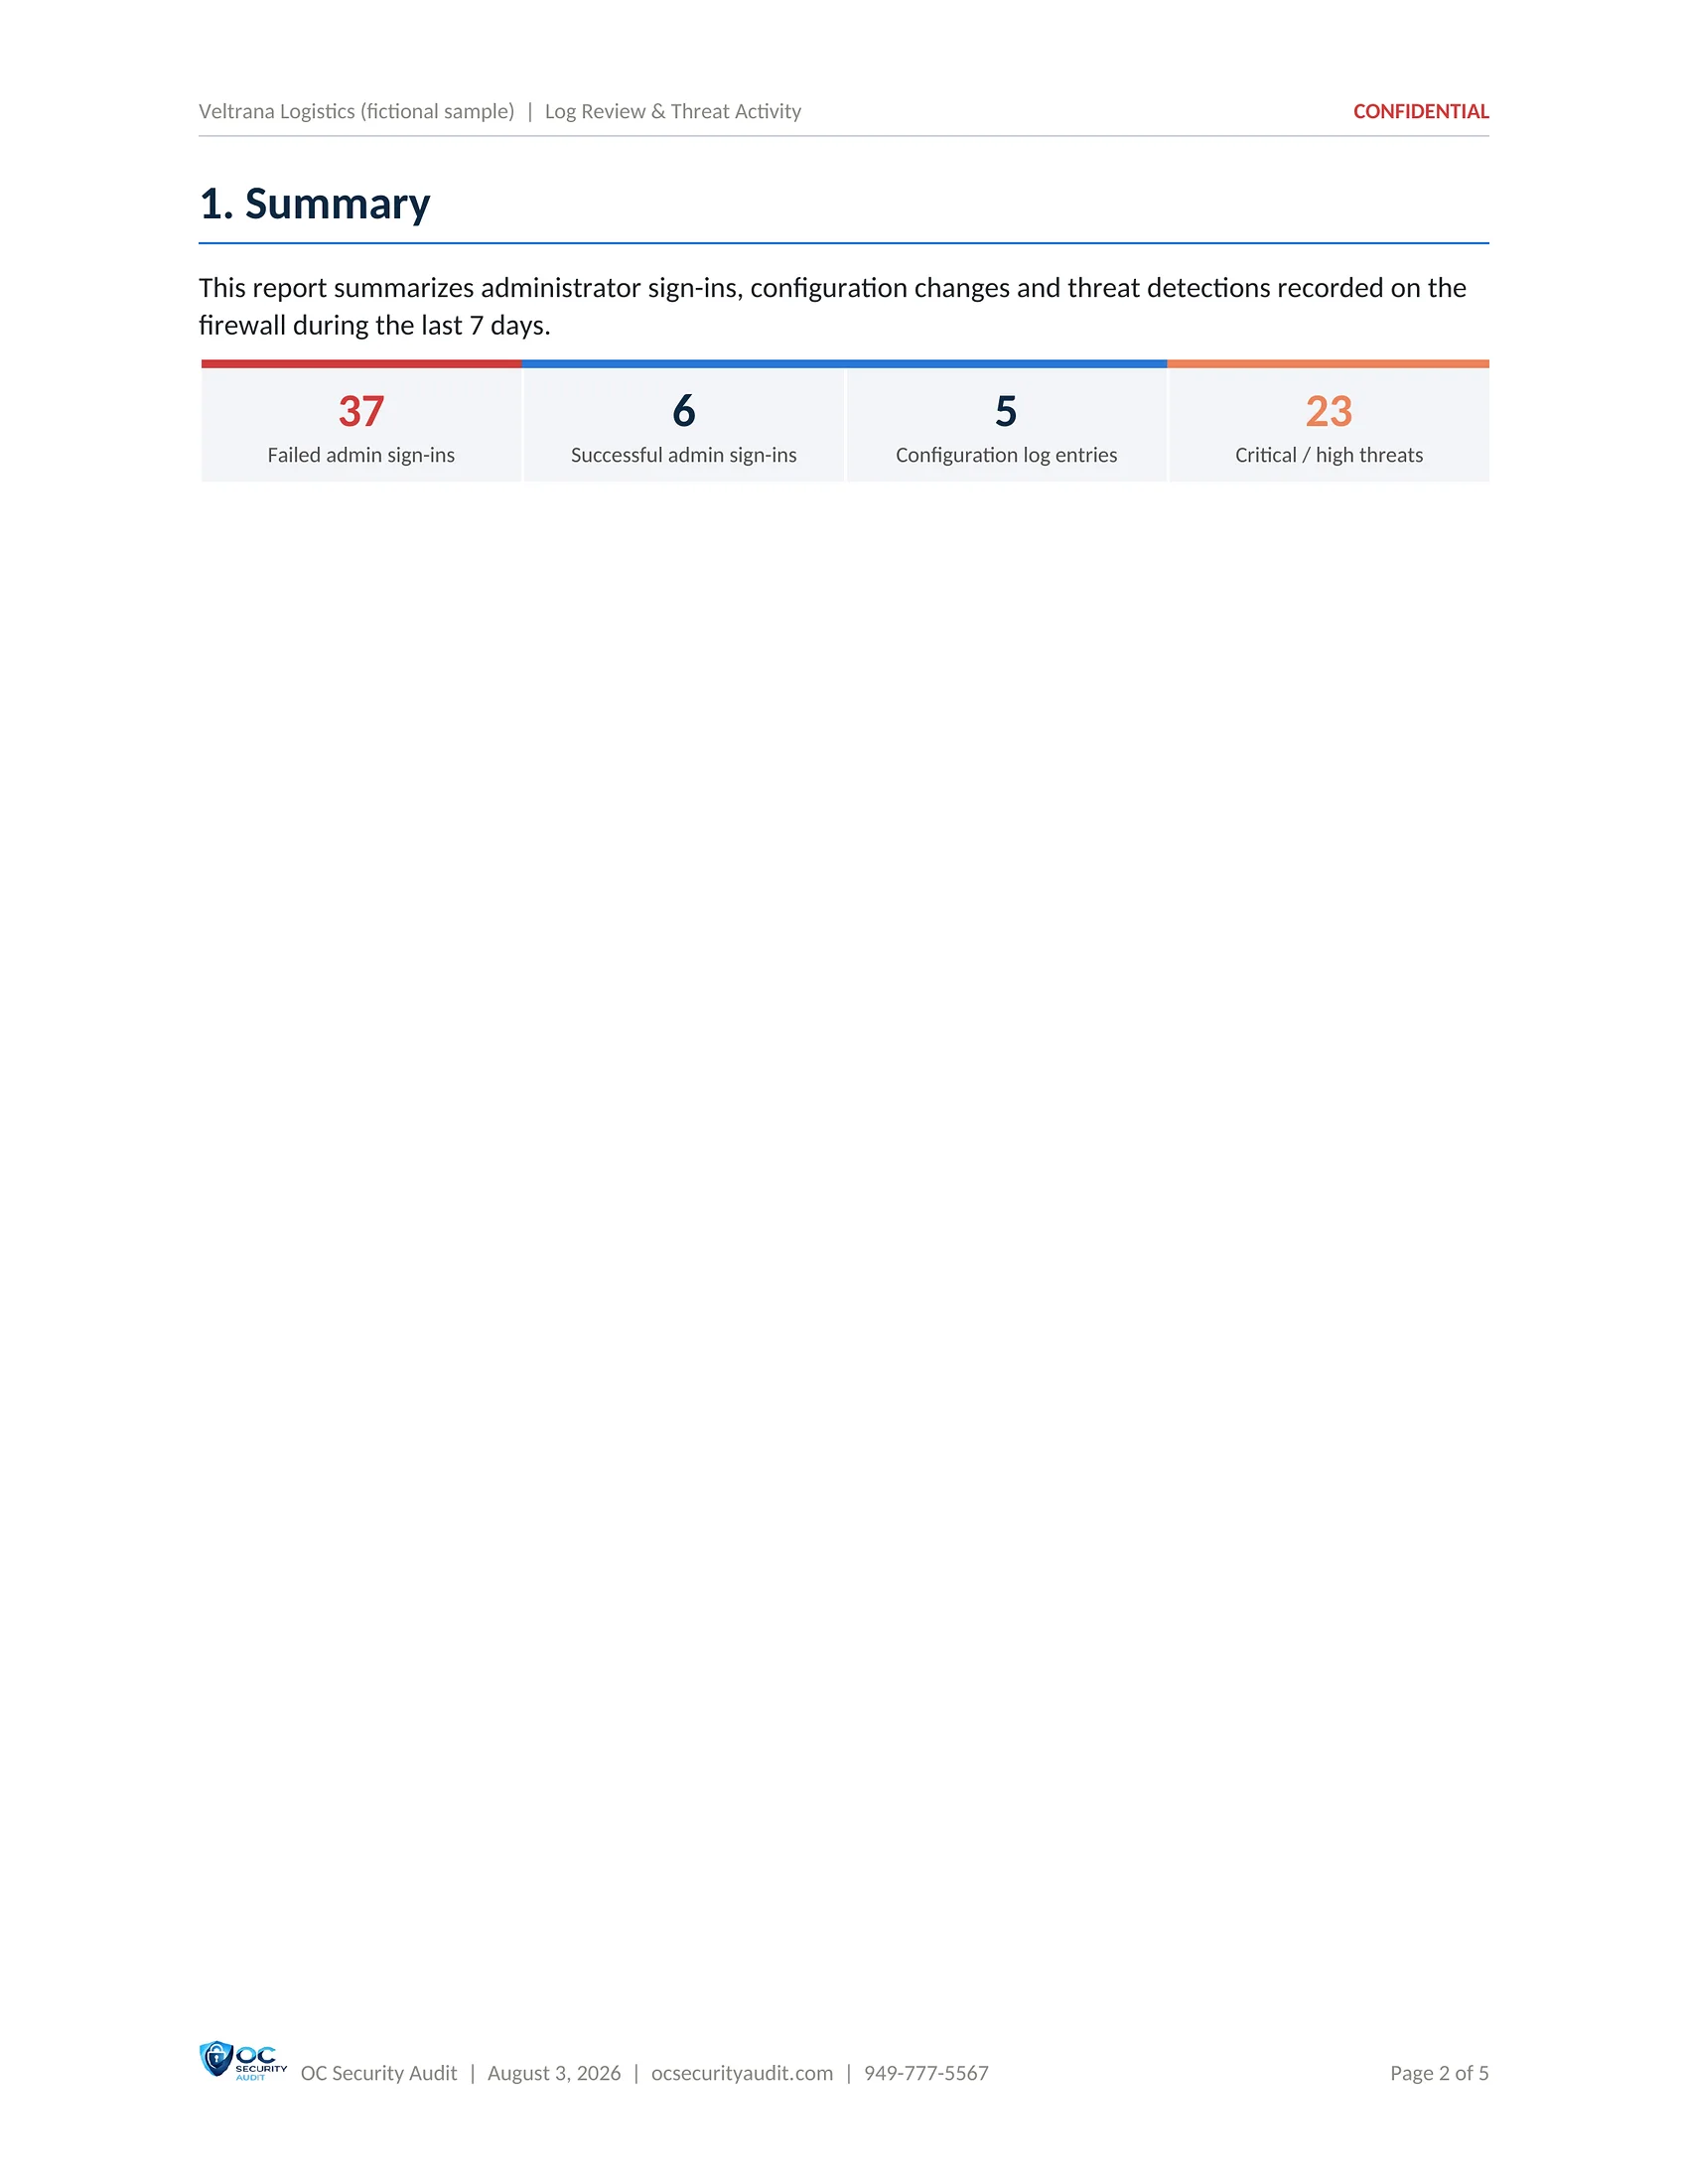
- Seven-day summary of sign-ins, changes and threats
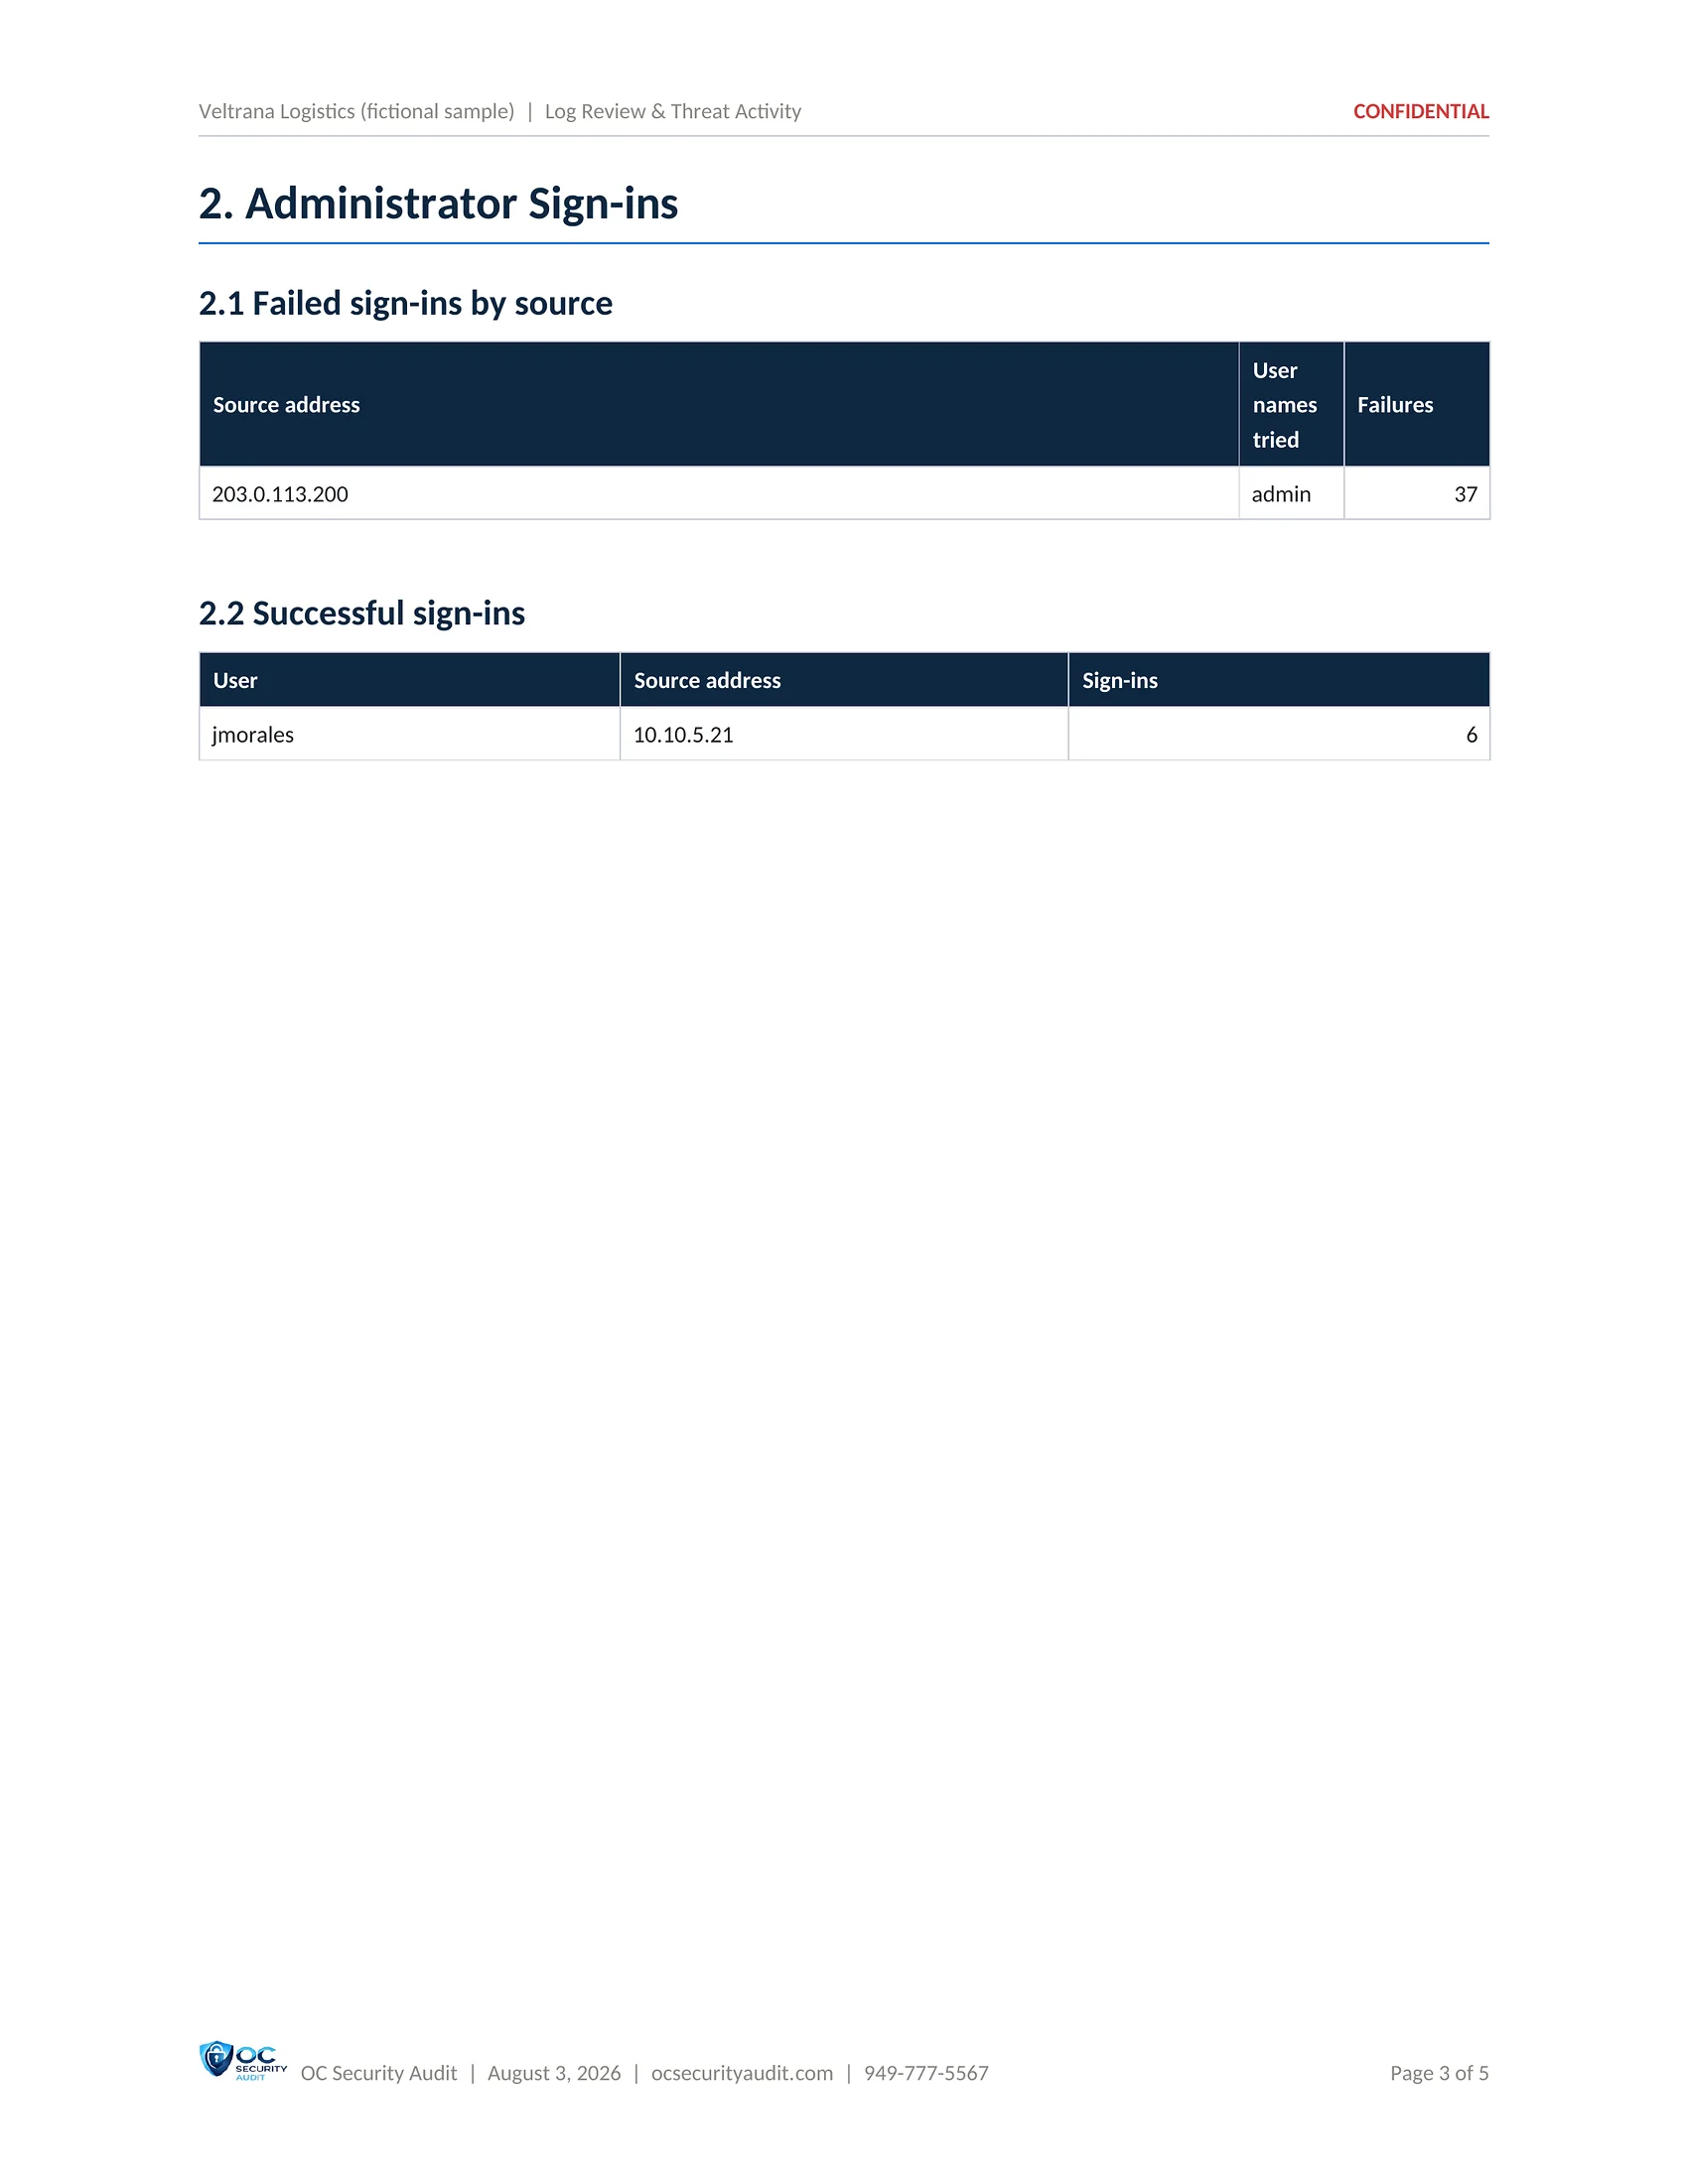
- Failed administrator sign-ins by source address
- Successful sign-ins and their sources
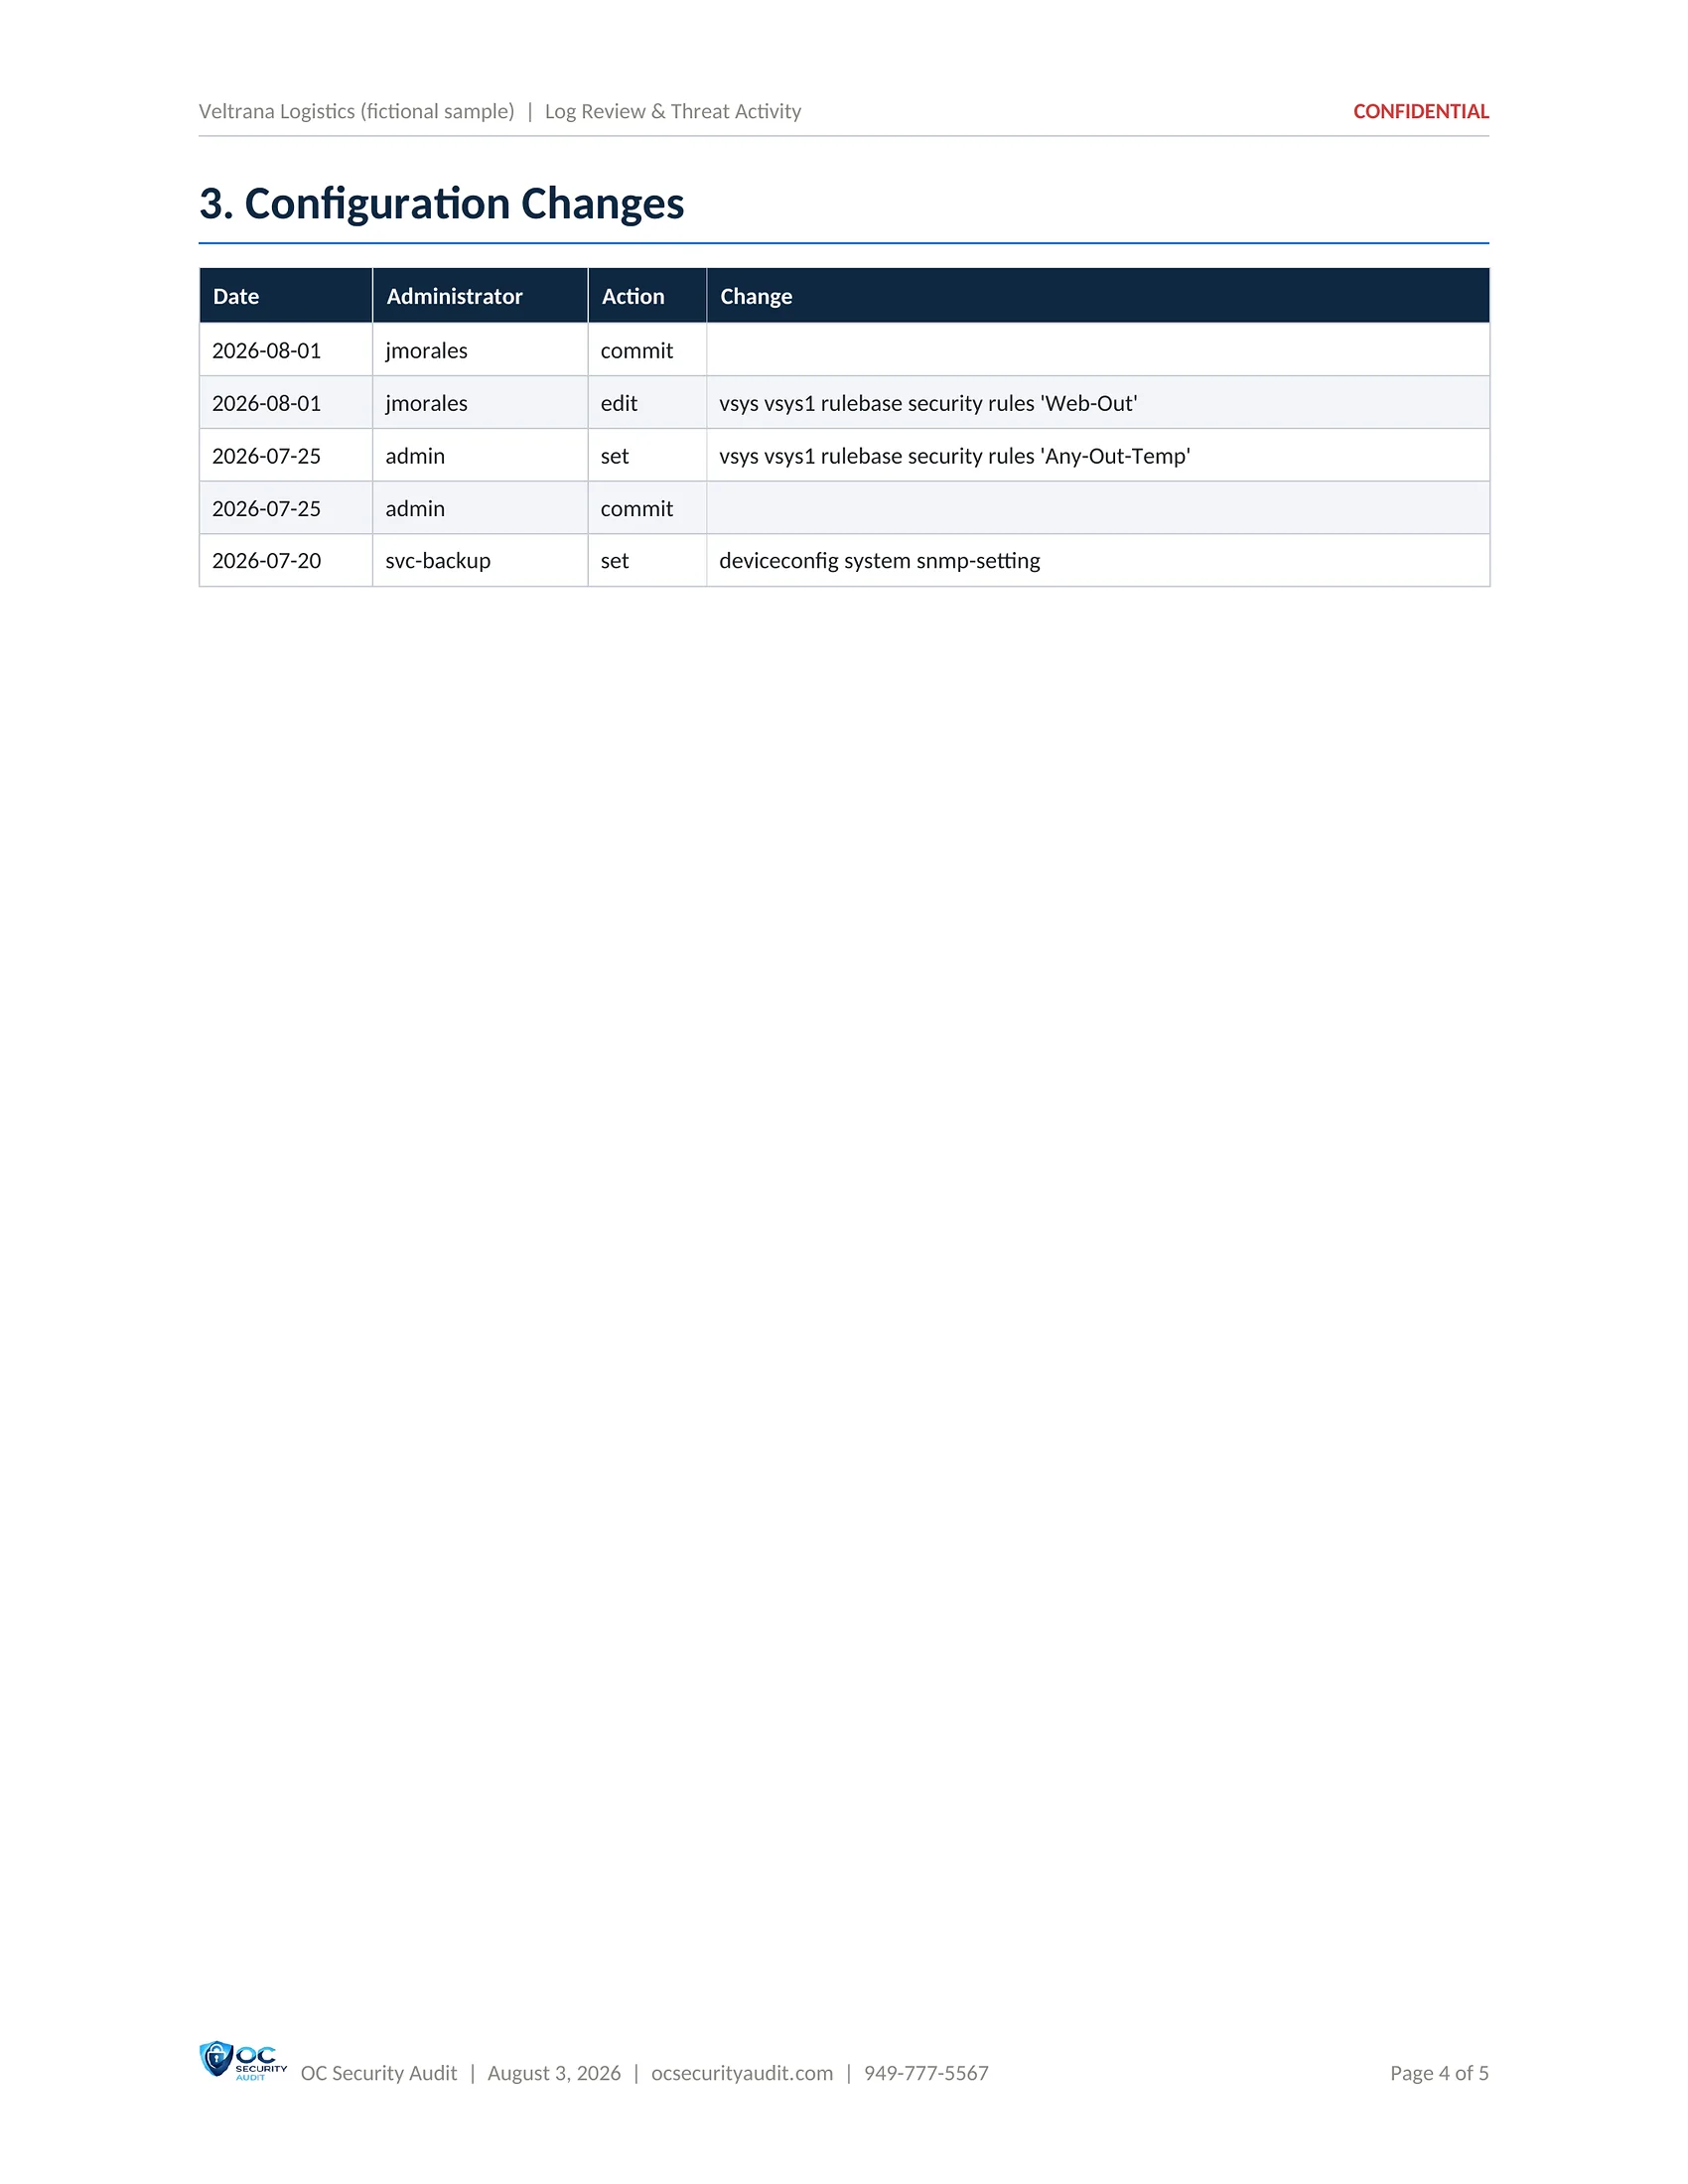
- Configuration changes by date and administrator
- Critical and High threats with the action taken
- Internal hosts with anti-spyware detections
Click the centre page to open it full size. Use the arrows, the thumbnails or your arrow keys to move between pages.
Deliverable 5 of 7 · PDF · 12 pages
Risk Register
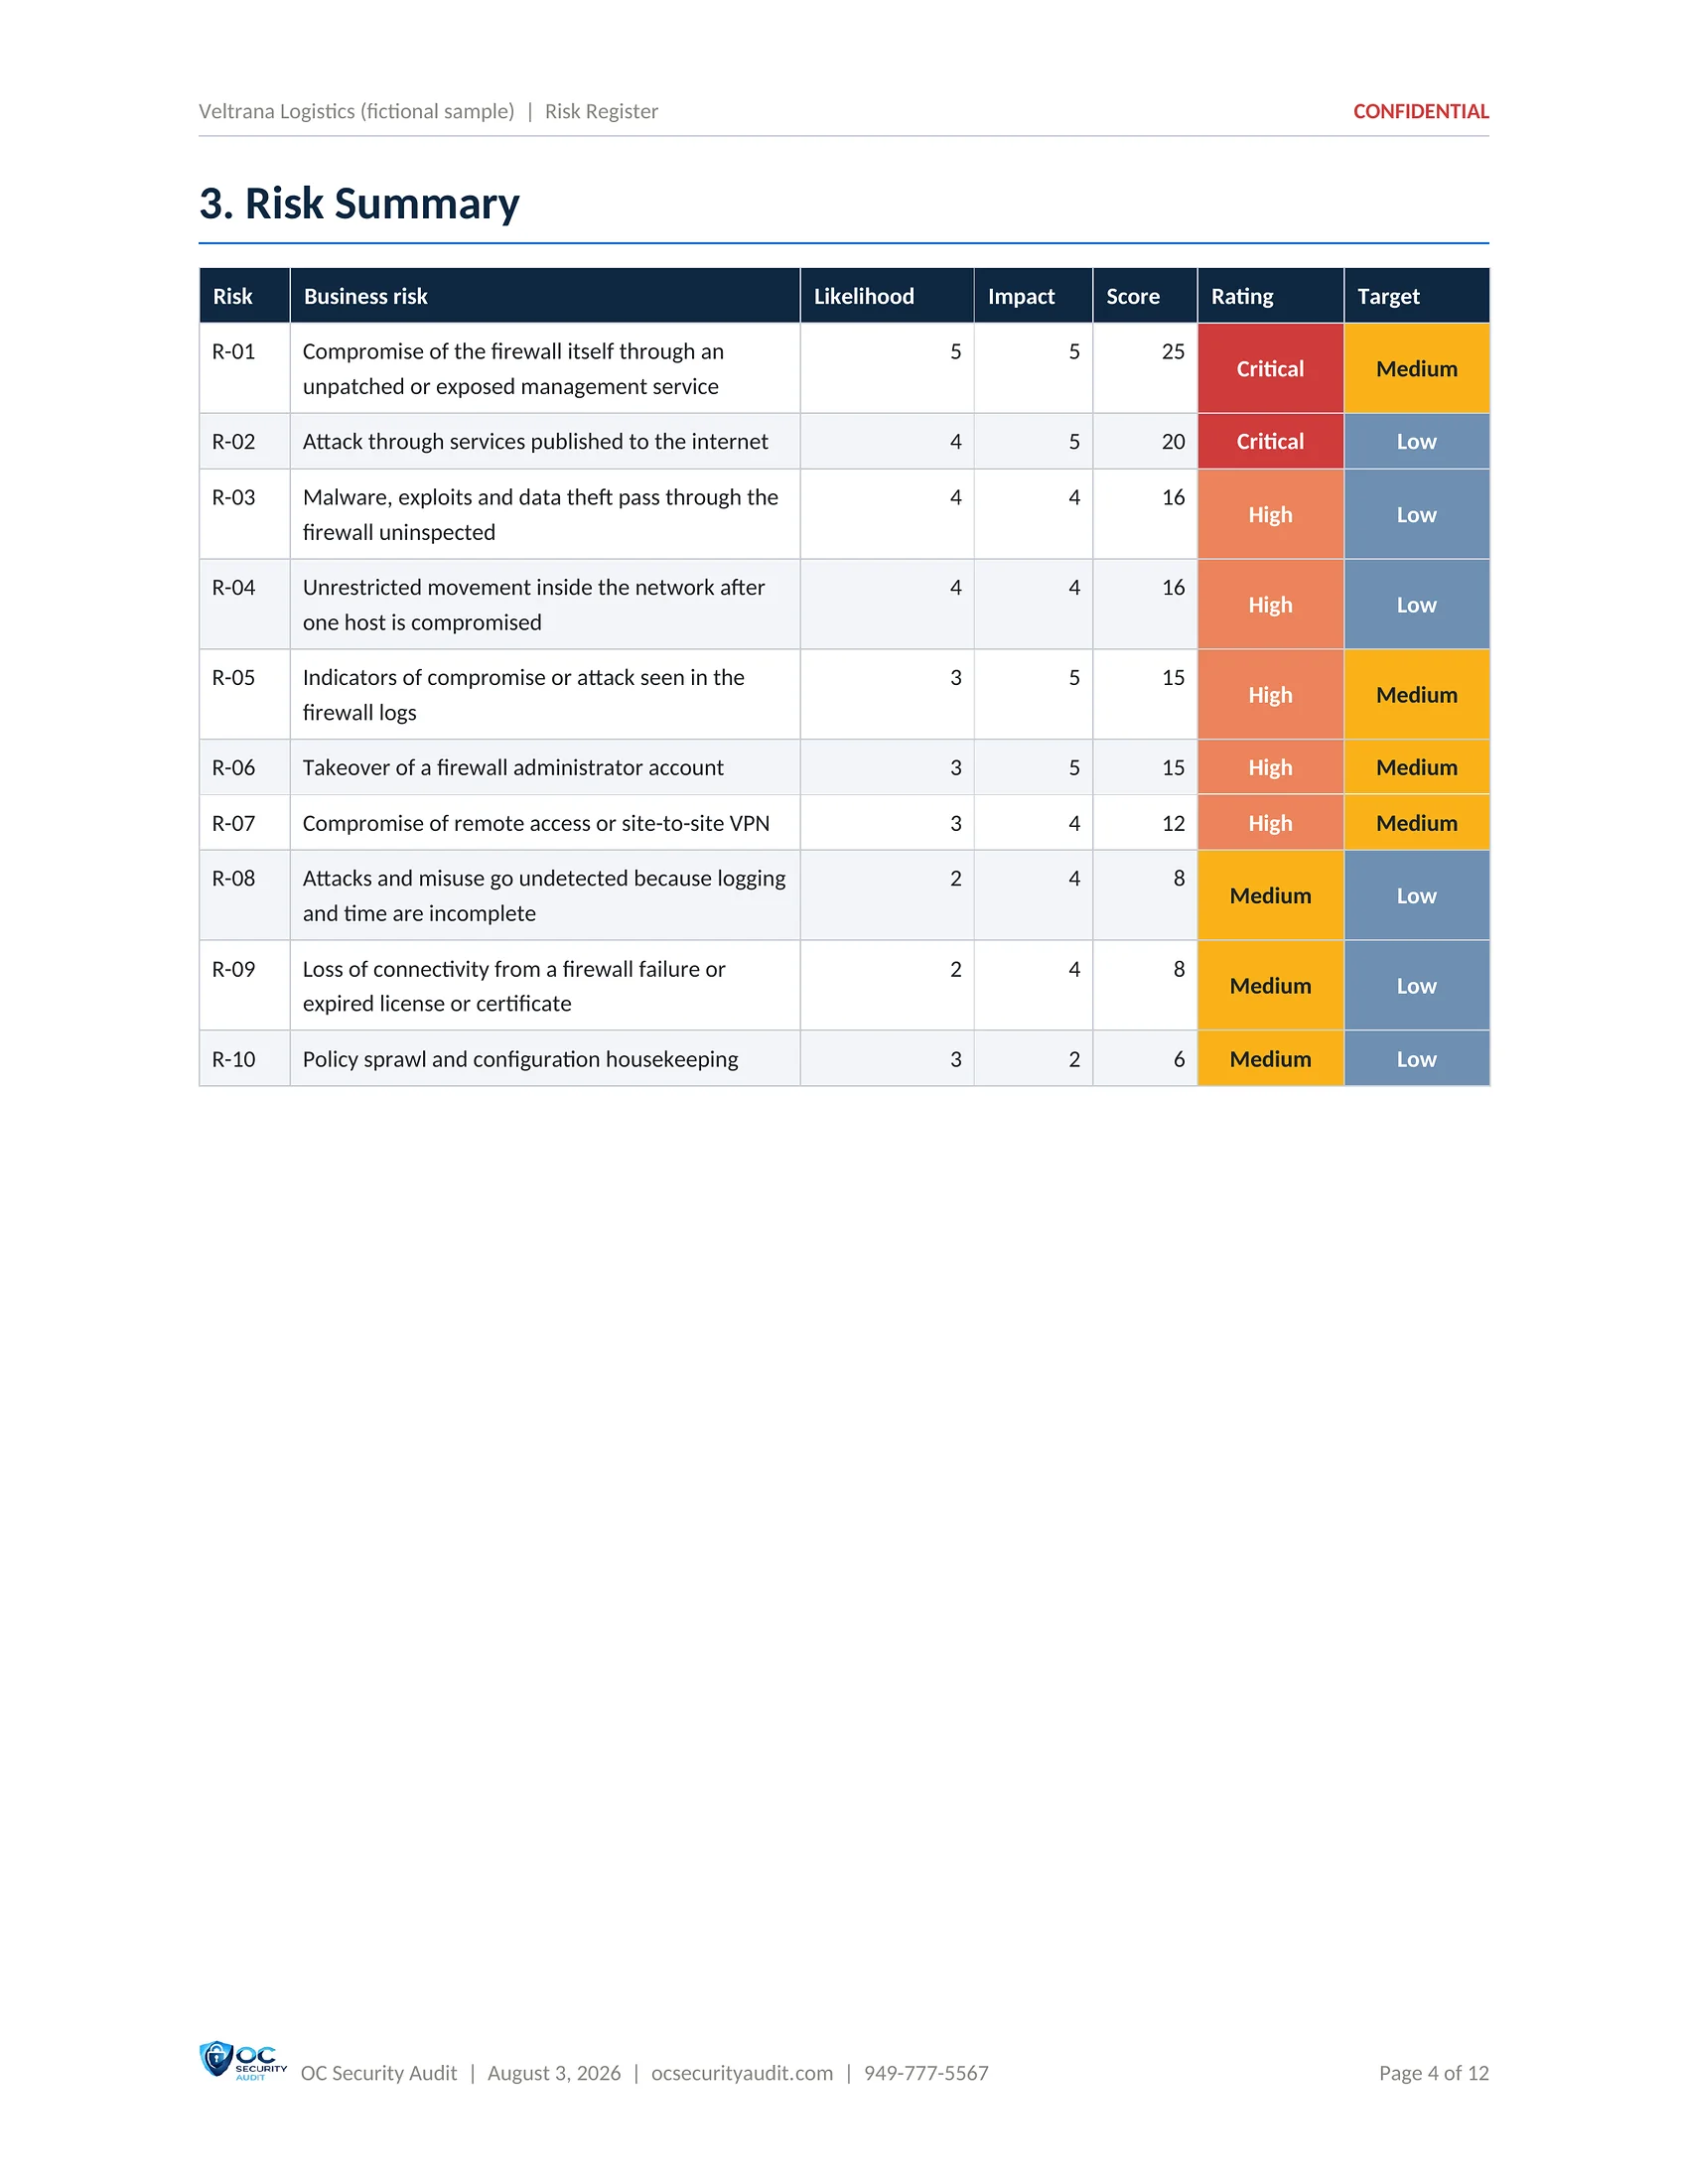
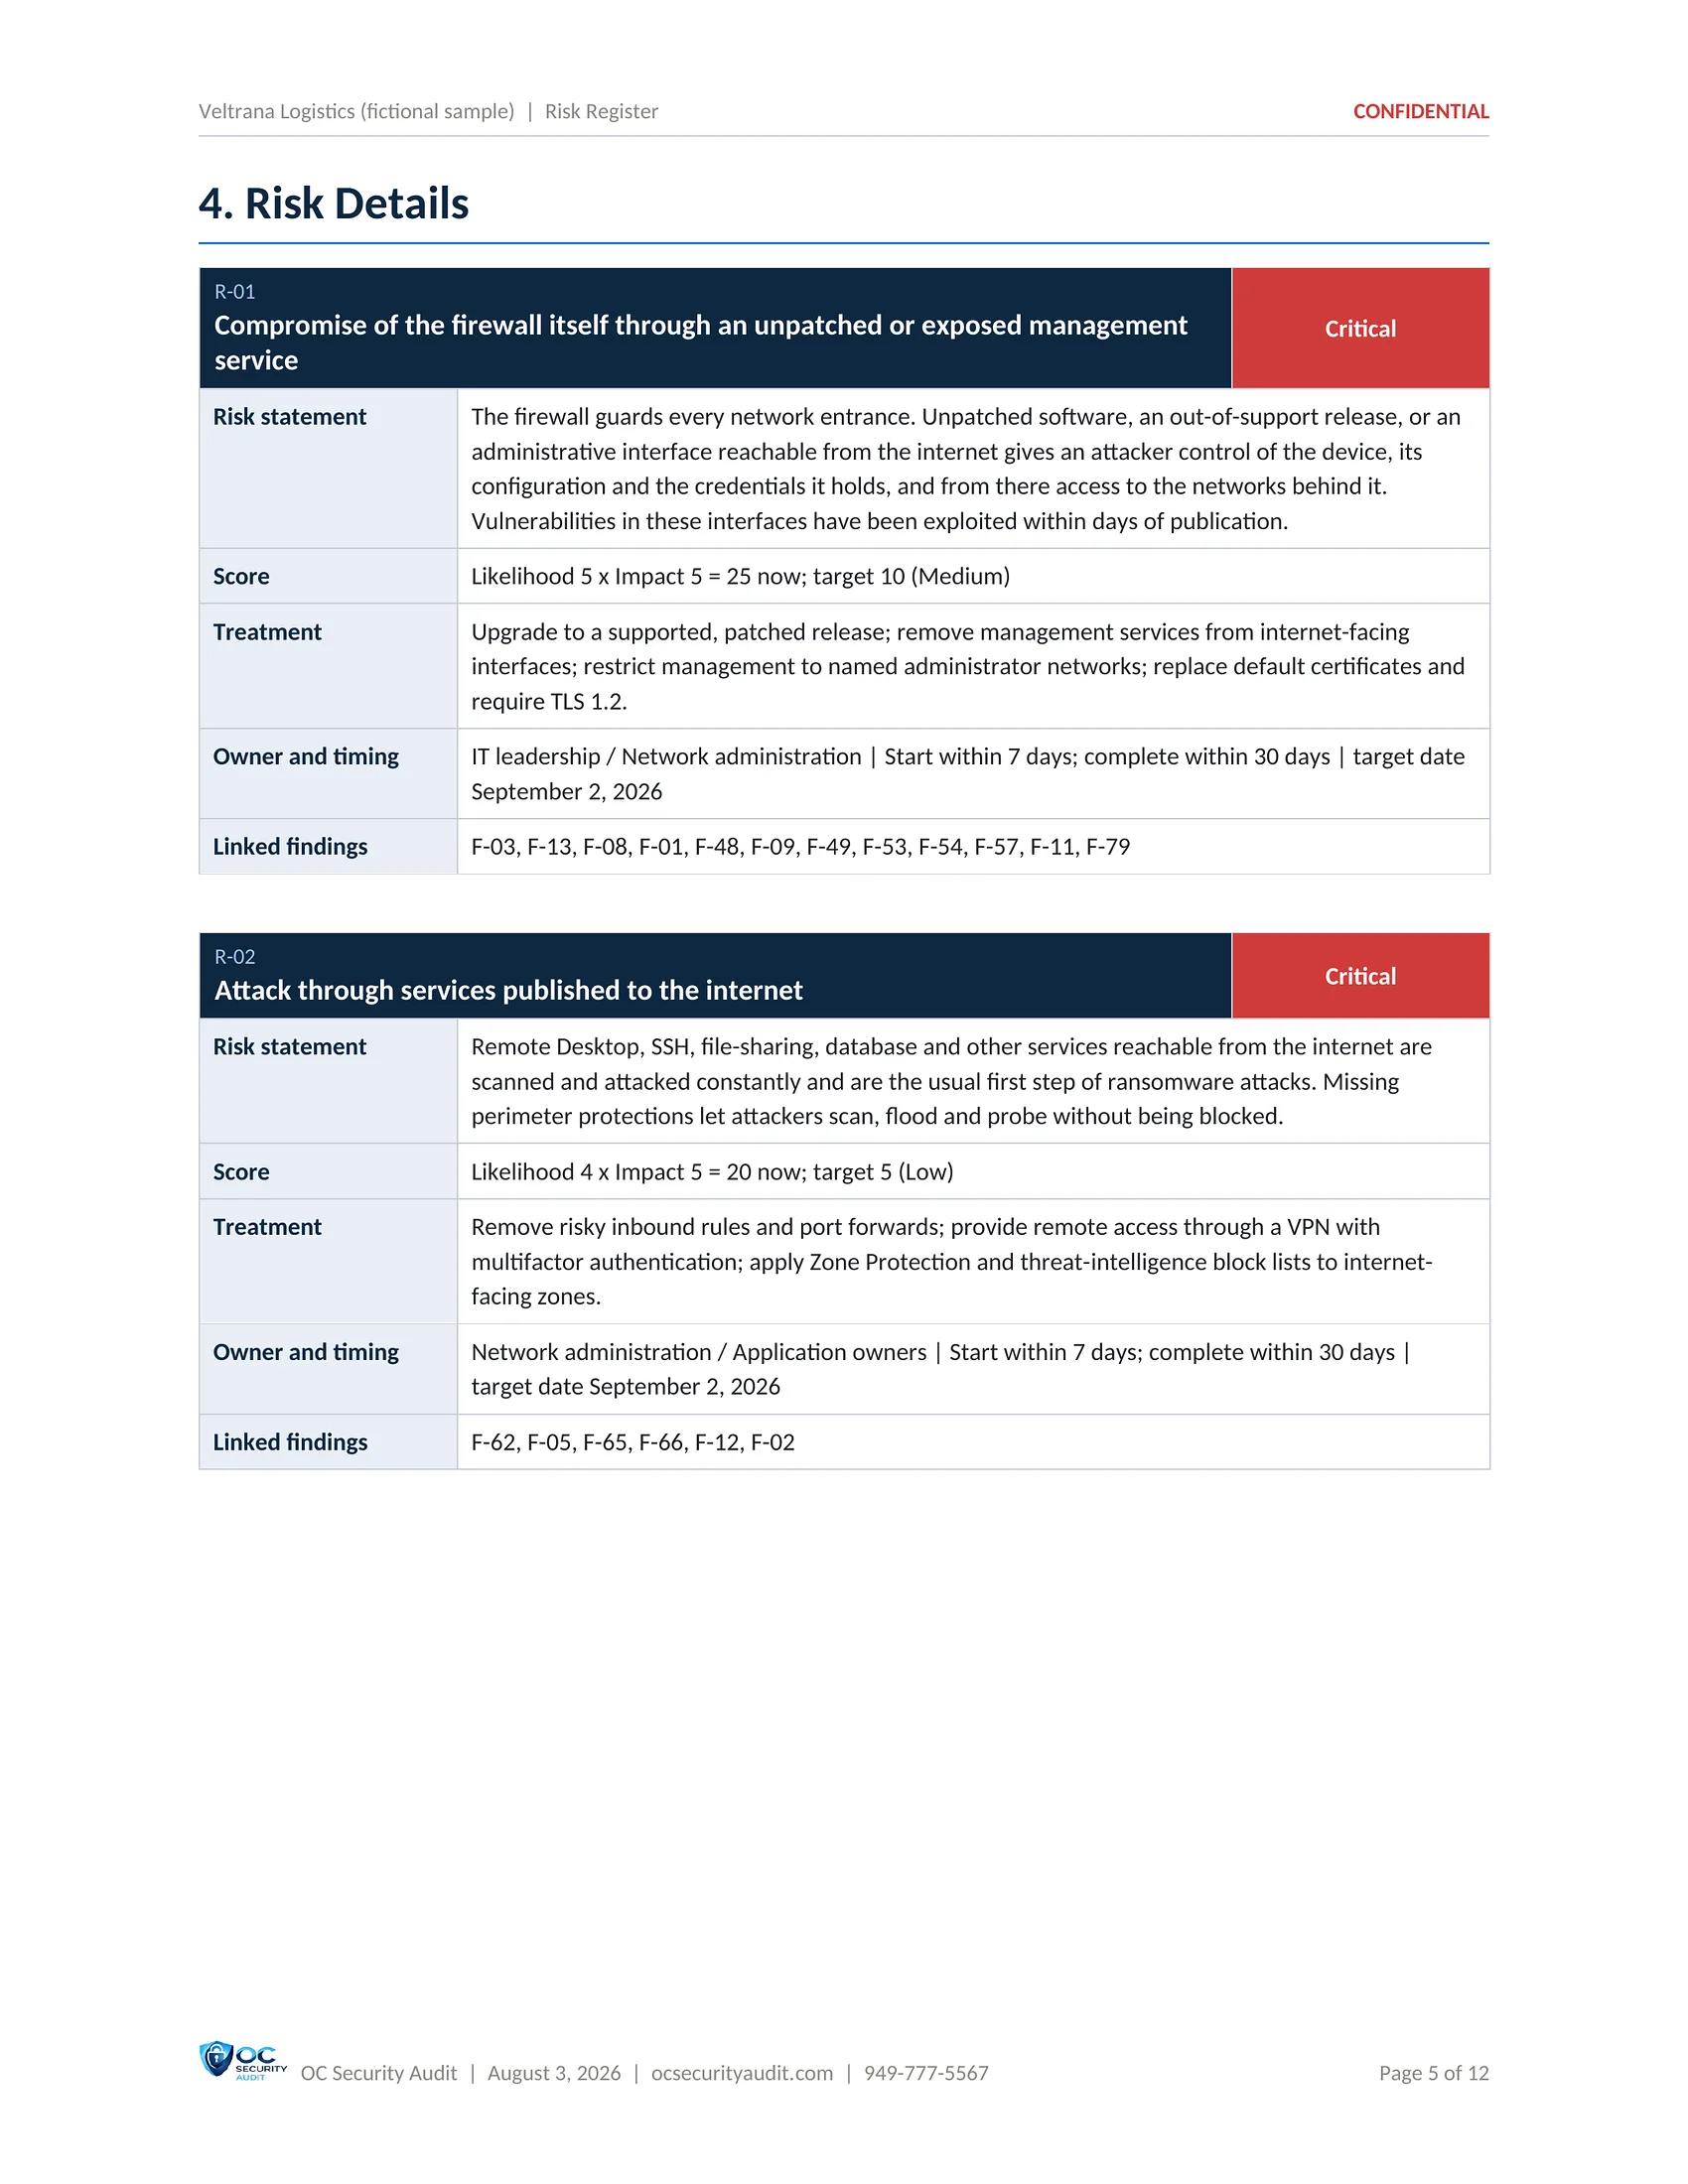
The findings rolled up into business risks that leadership, auditors and insurers understand. Each risk is scored by likelihood and impact, has a treatment and an owner, and is traceable to the findings behind it.
Who uses it
Owner, compliance, auditors, insurer
What is included
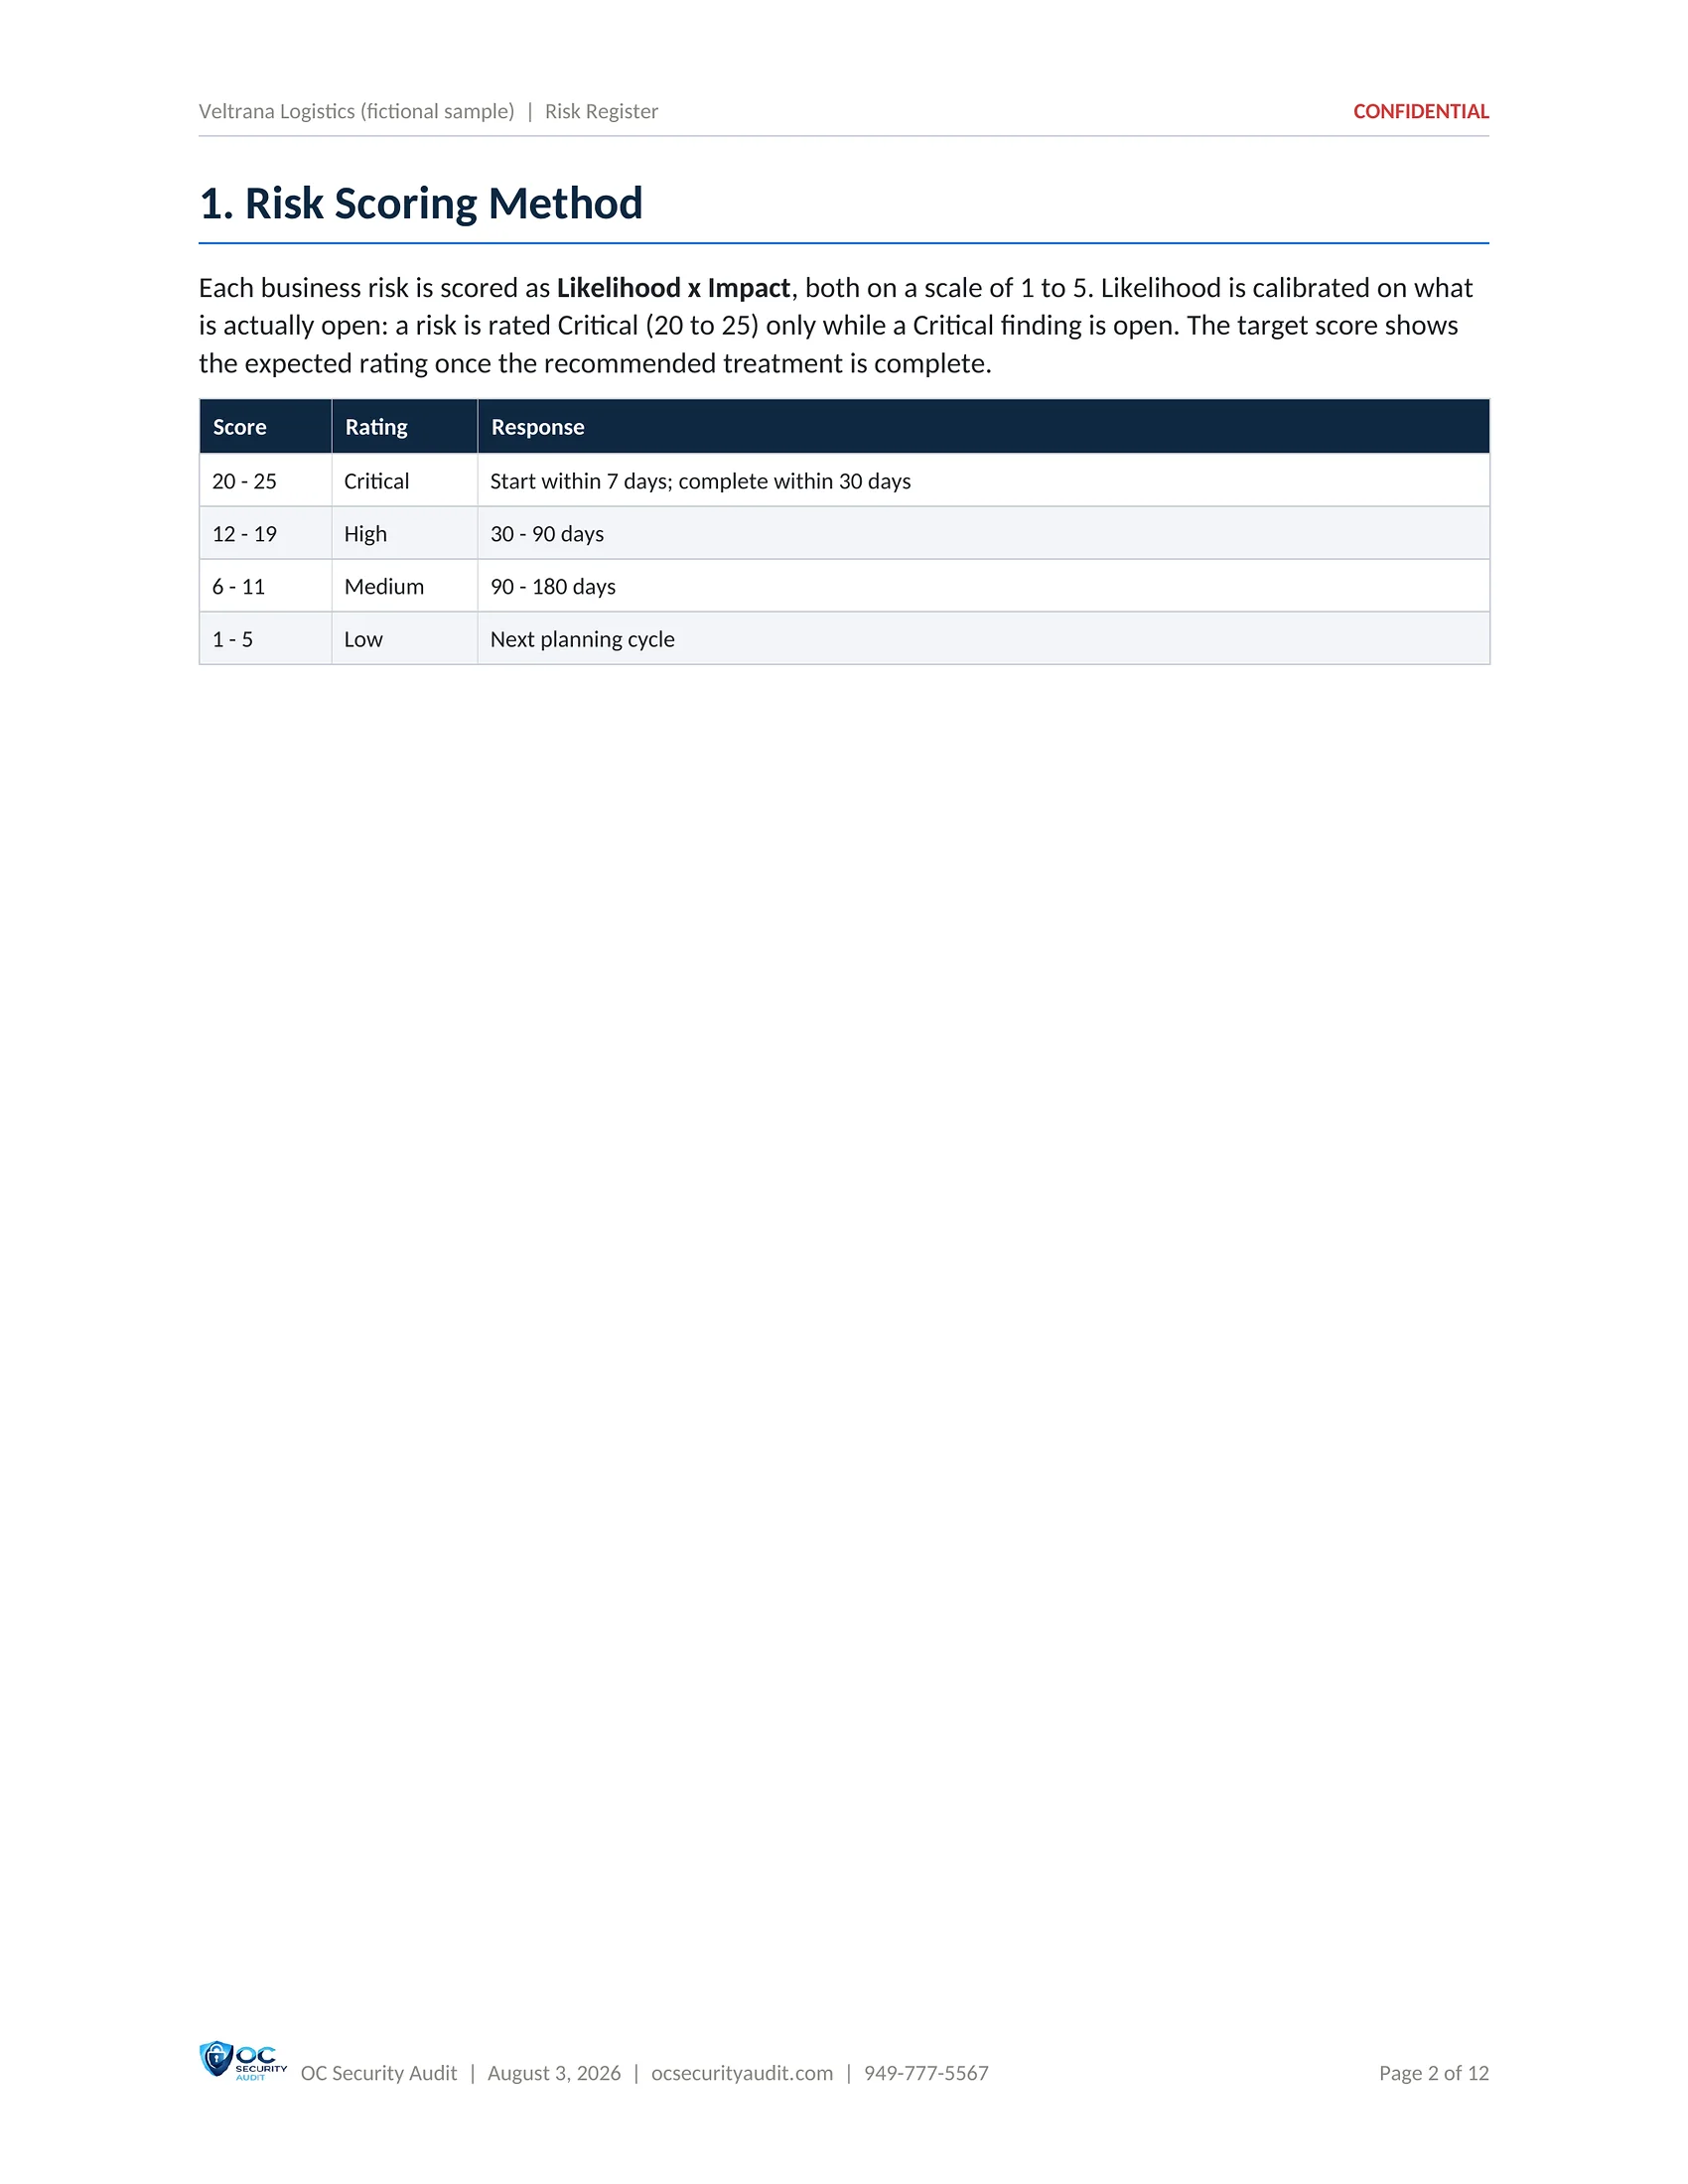
- Scoring method: likelihood times impact, 1 to 5
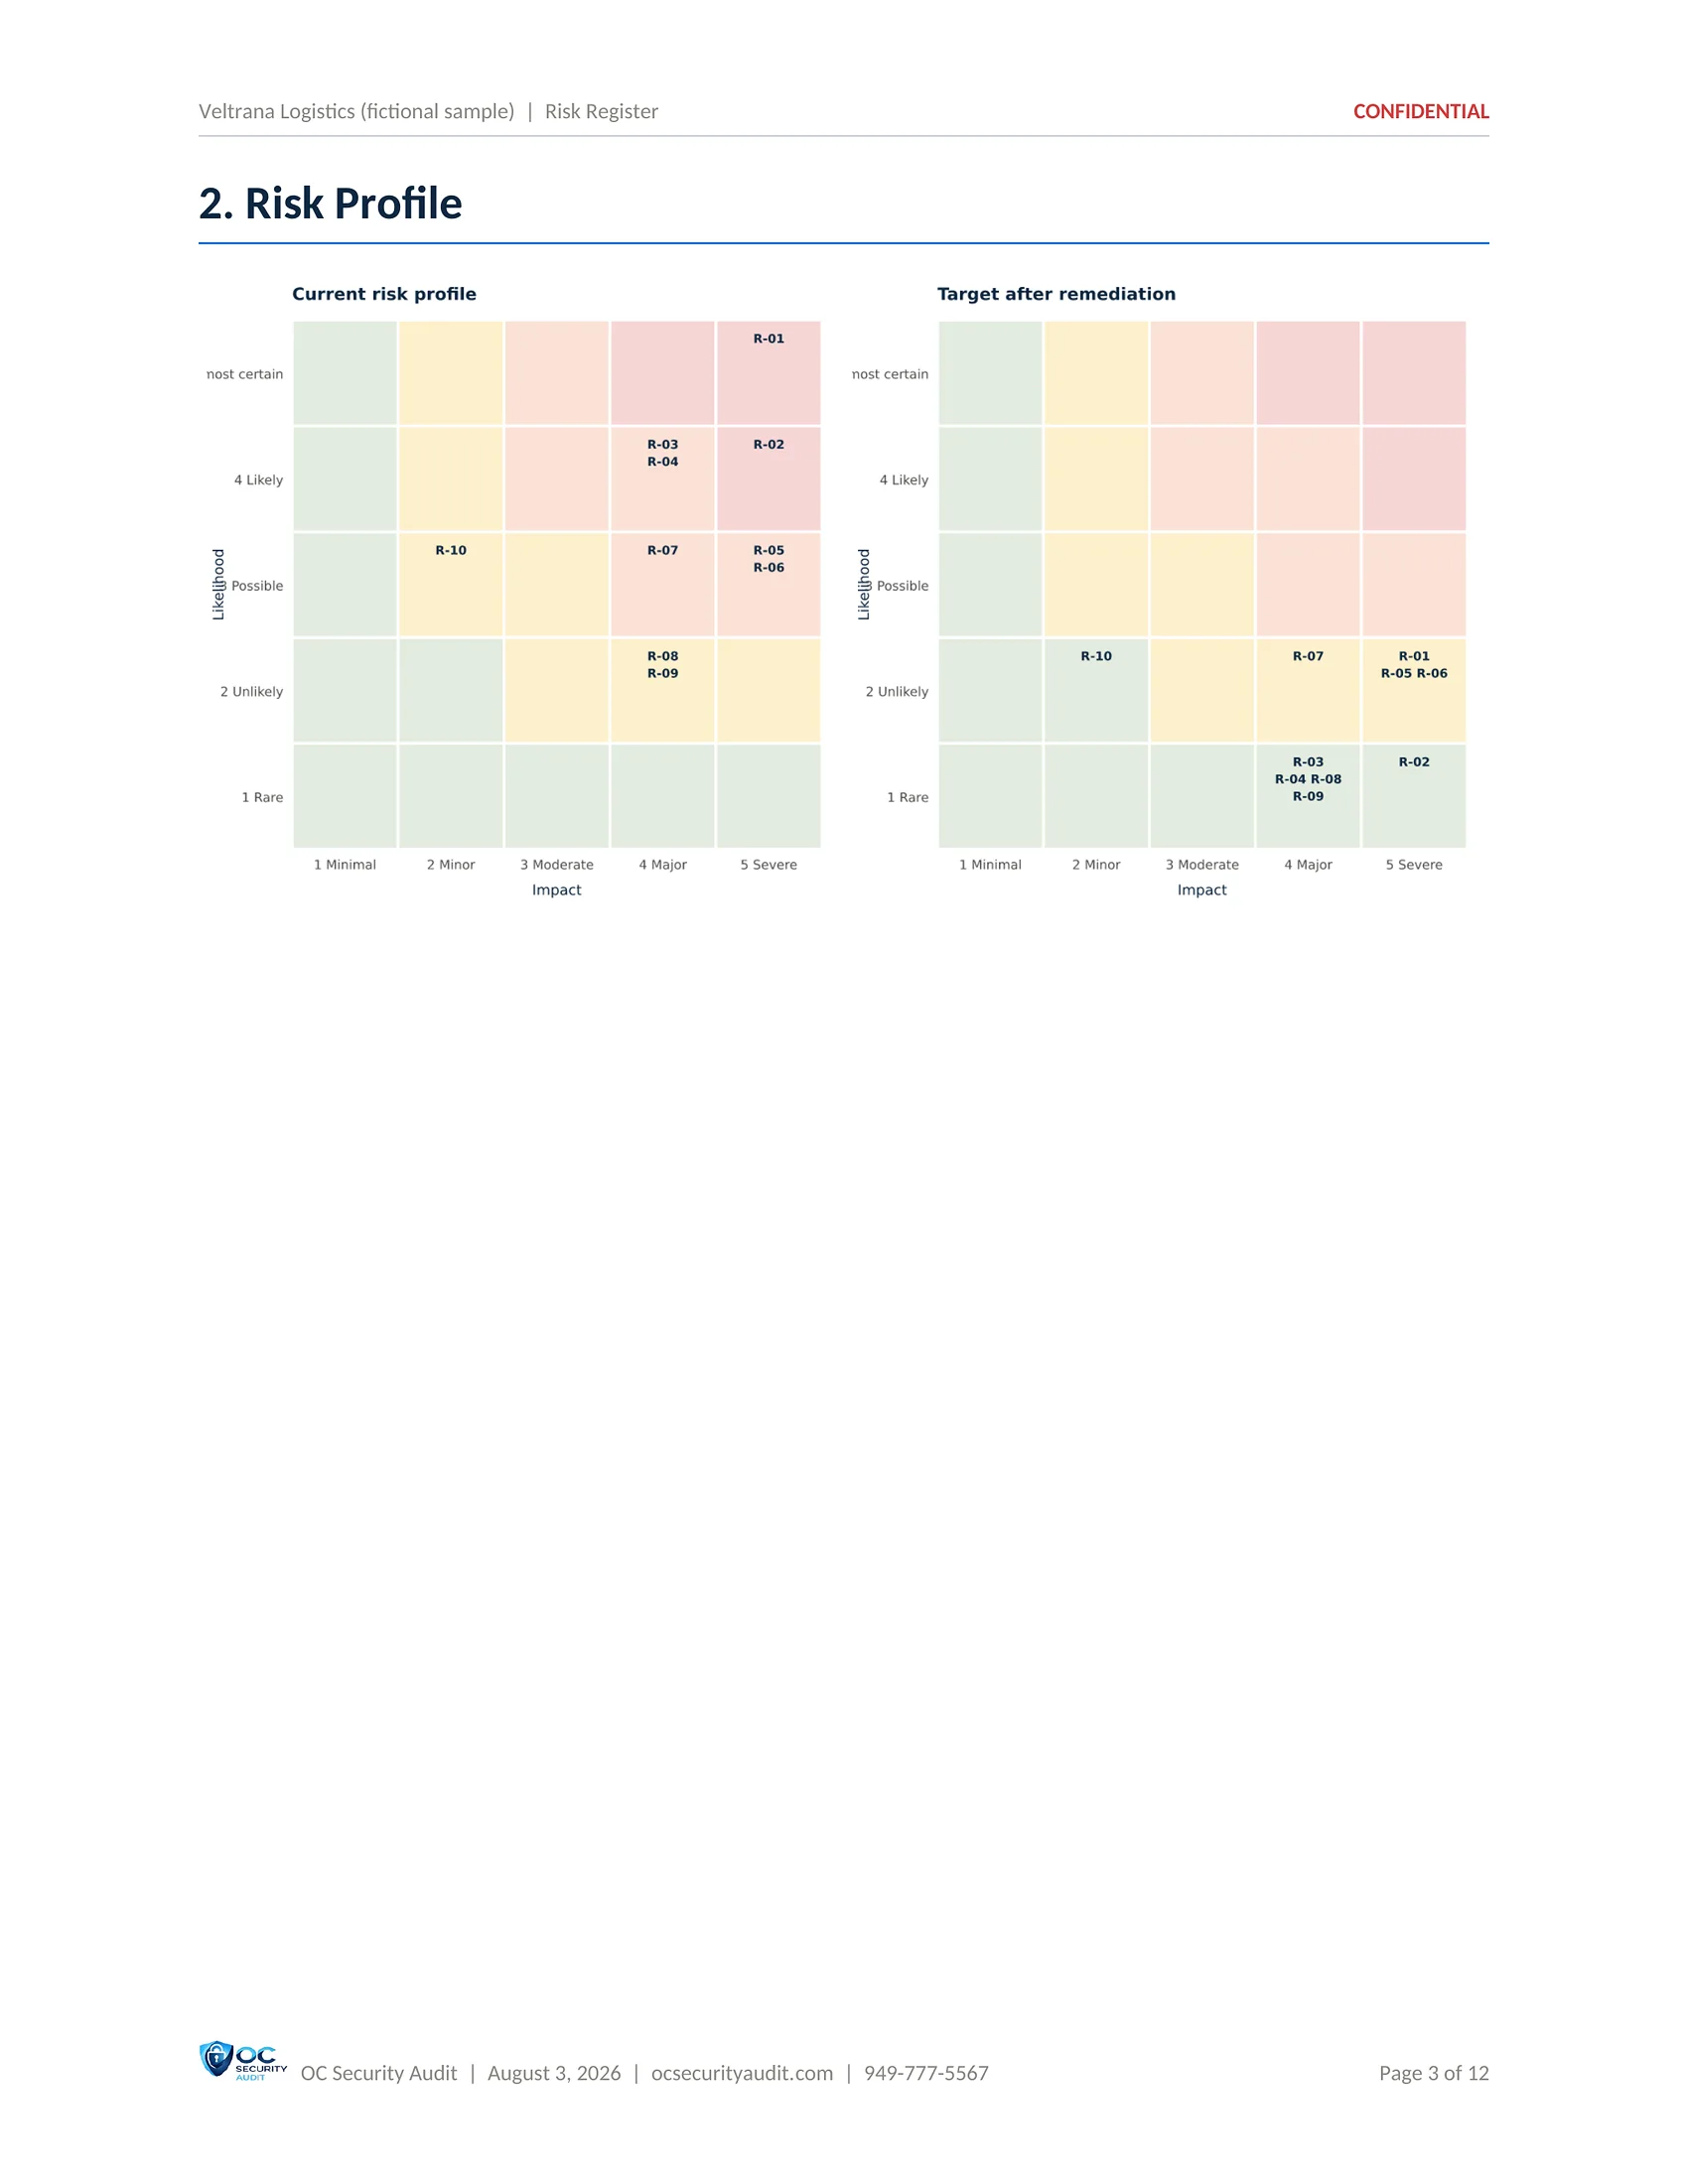
- Heat maps today and after remediation
- Summary of the business risks with target ratings
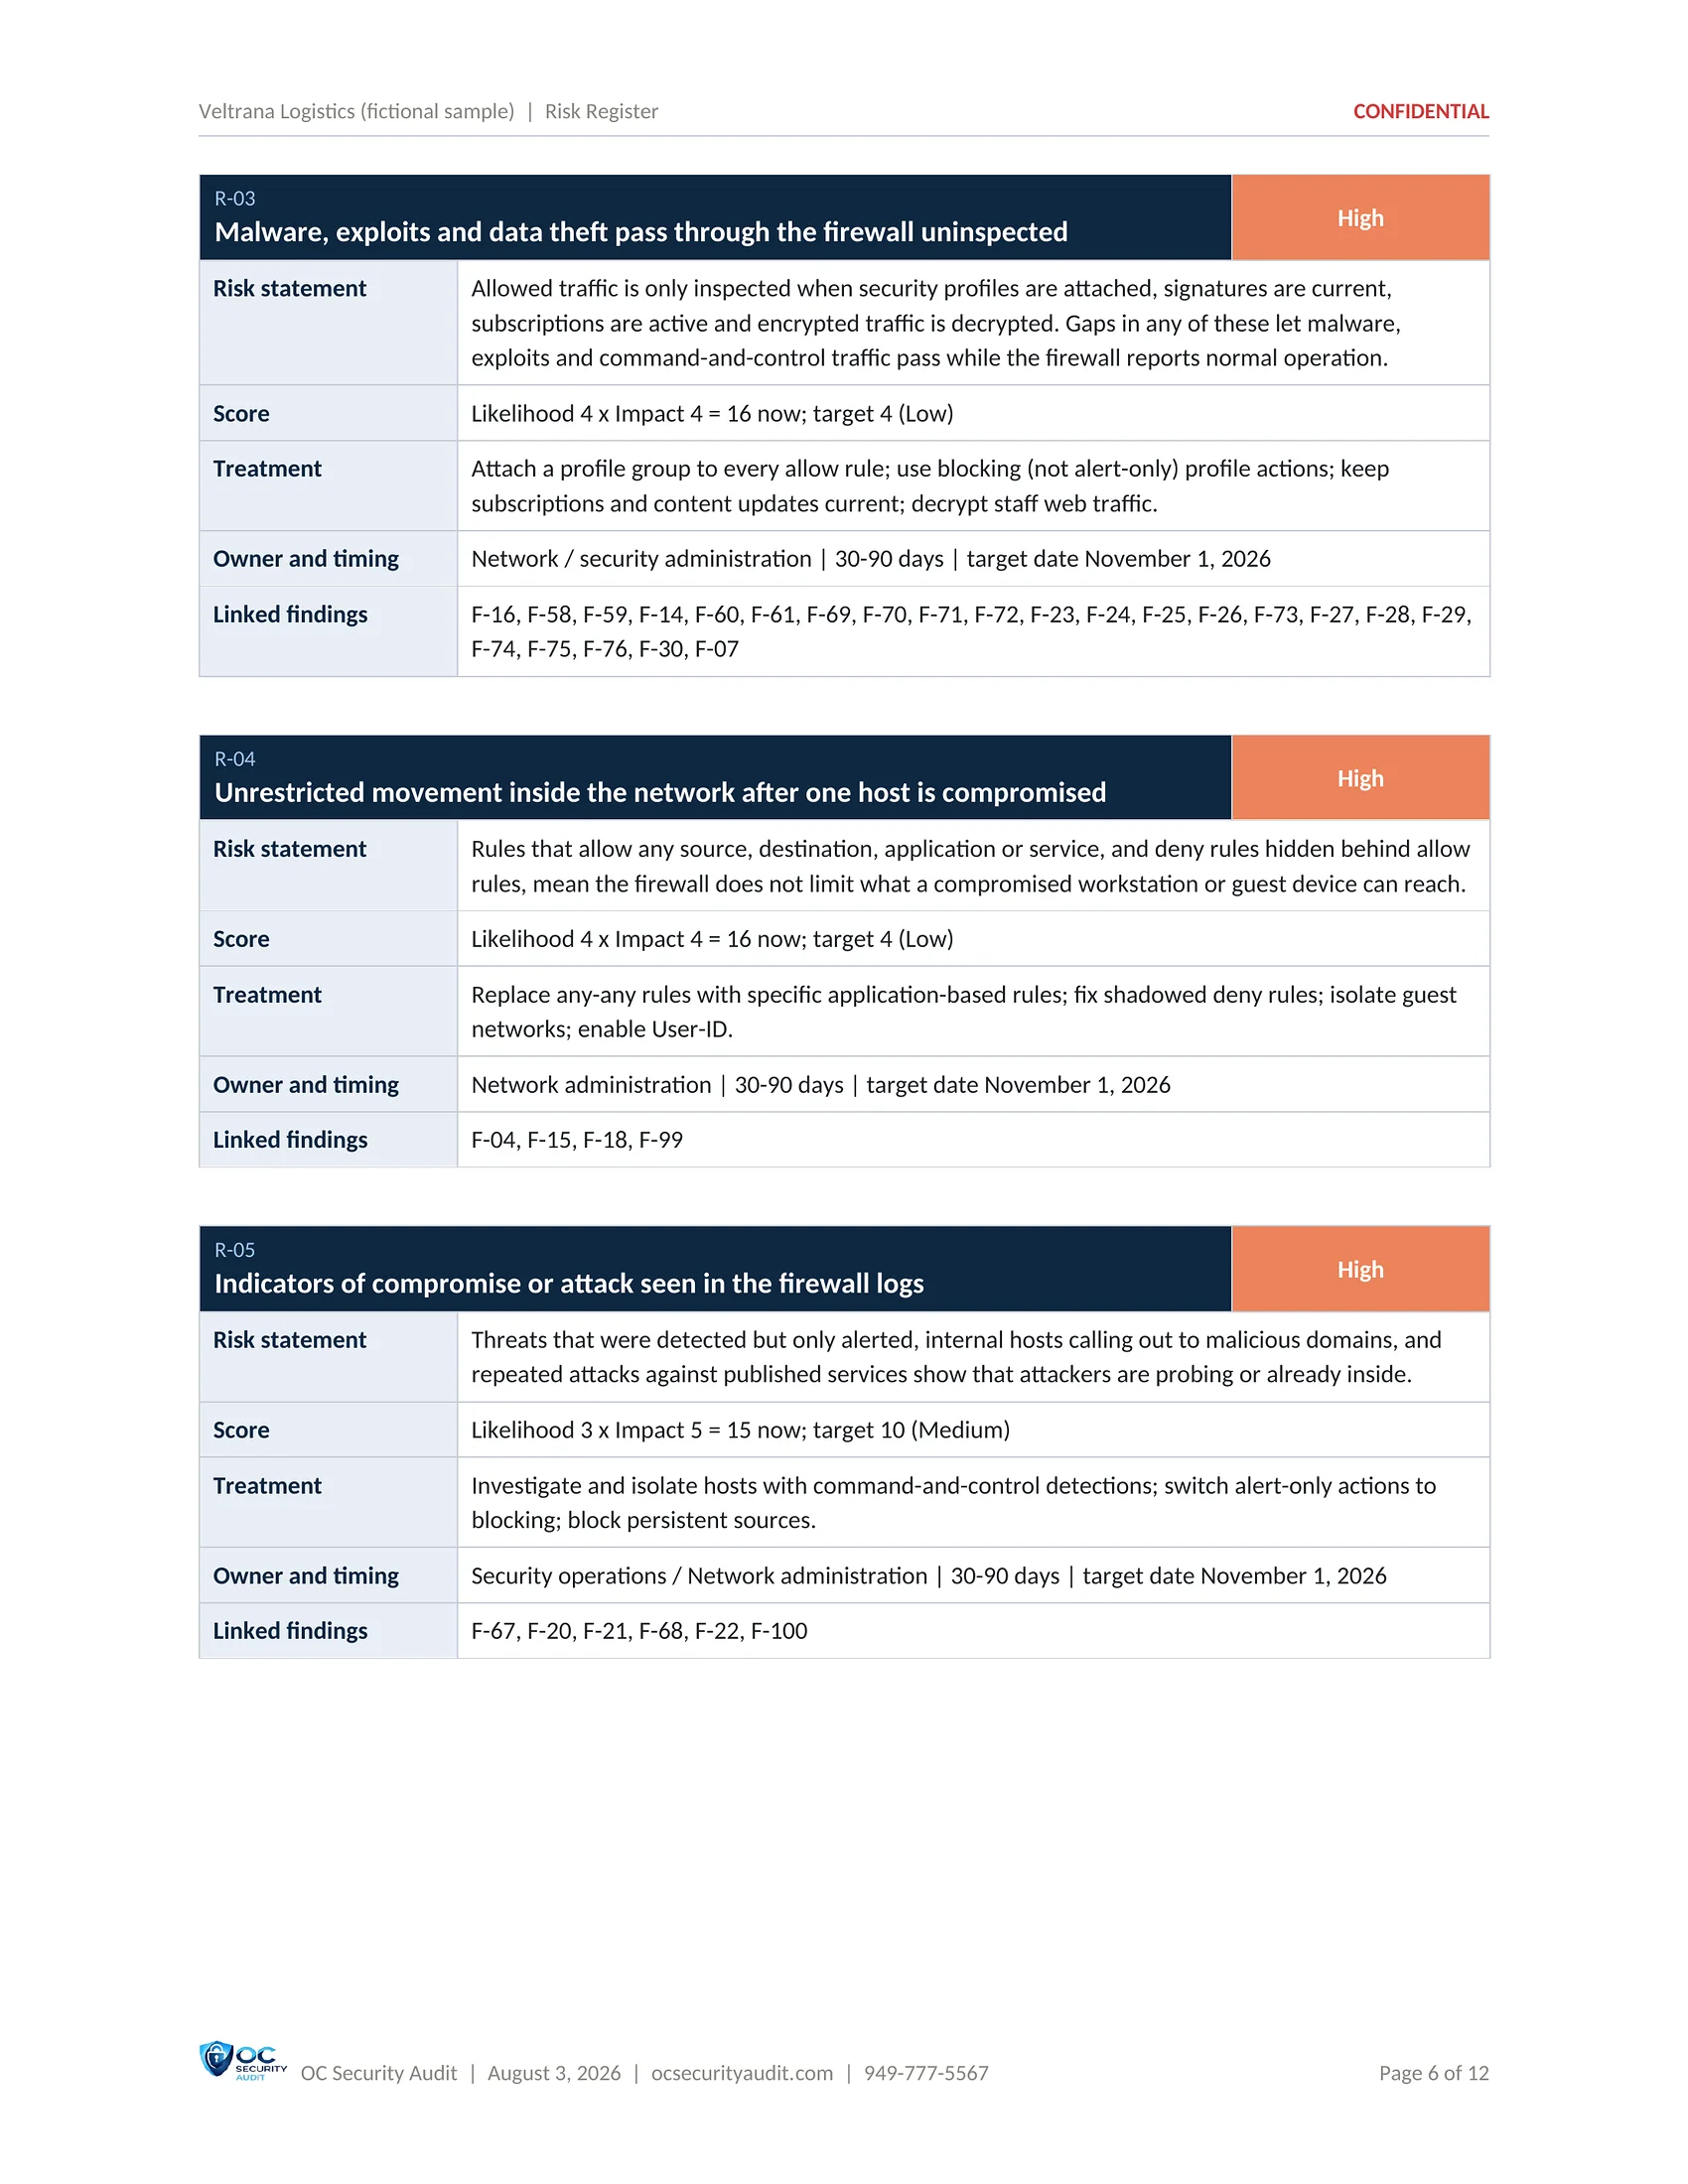
- Risk statement, treatment, owner and timing
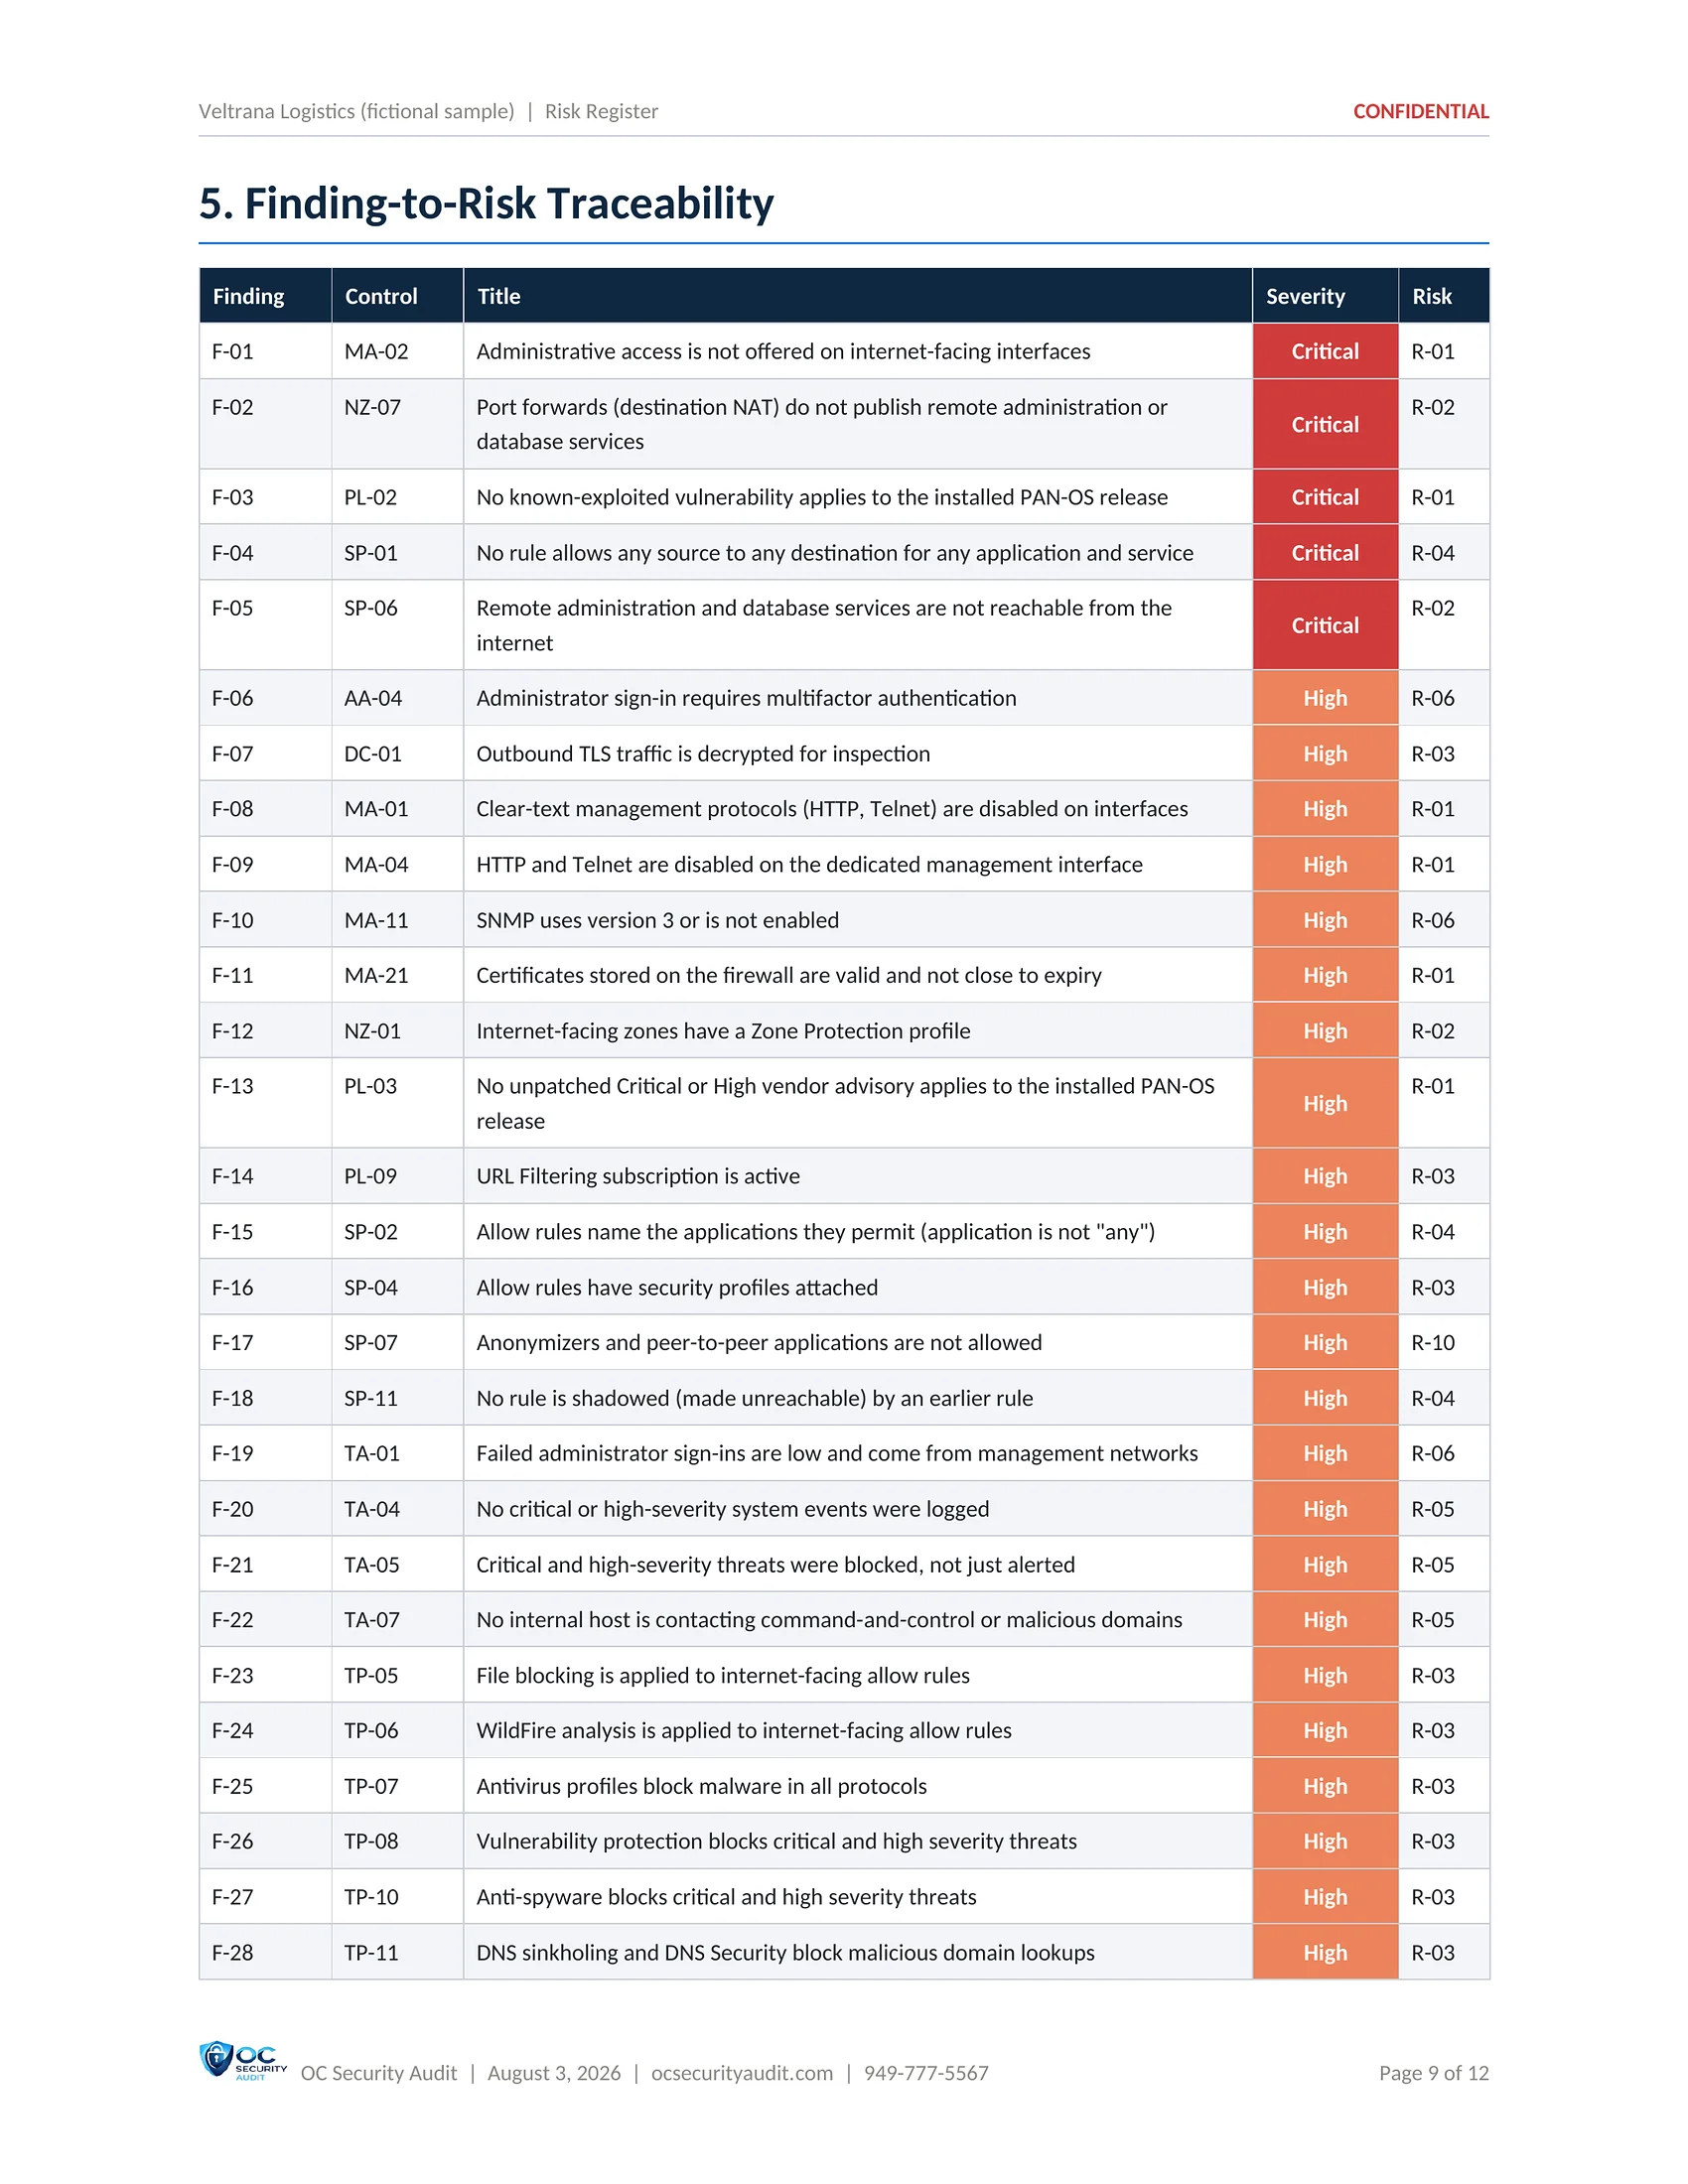
- Findings linked to each risk
- Finding-to-risk traceability table
Click the centre page to open it full size. Use the arrows, the thumbnails or your arrow keys to move between pages.
Deliverable 6 of 7 · PDF · 18 pages
Next Steps & Security Roadmap
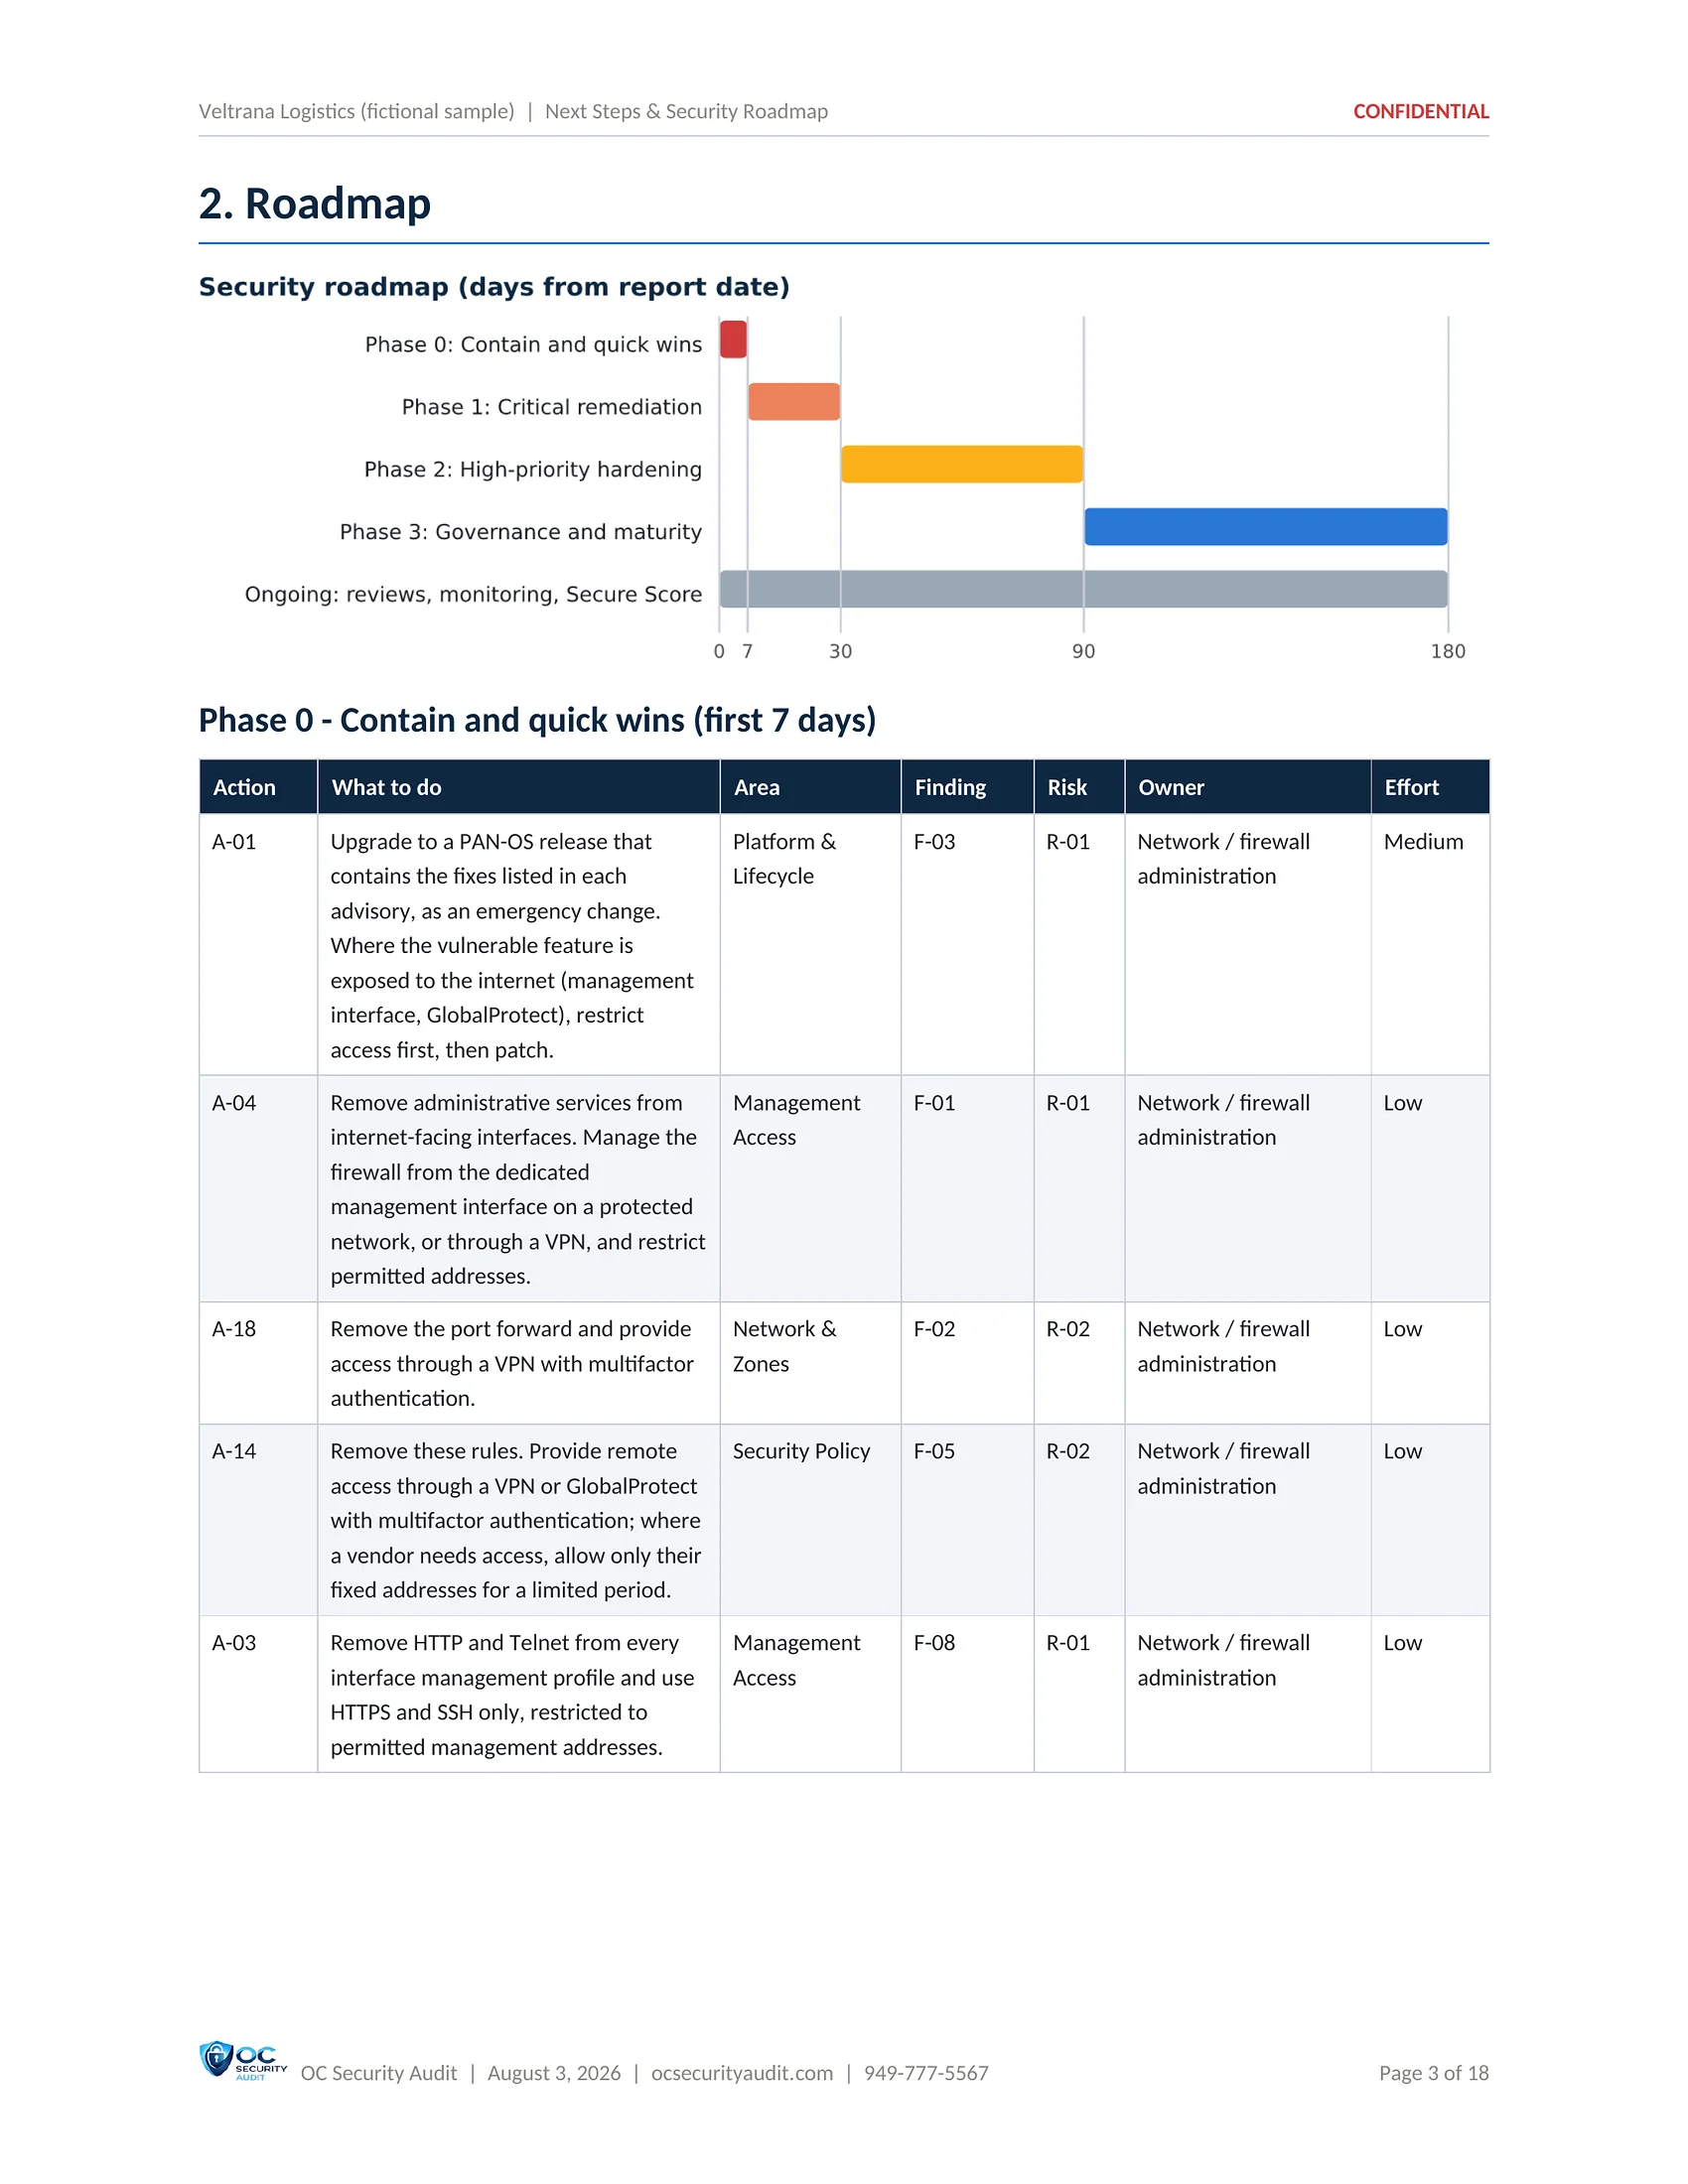
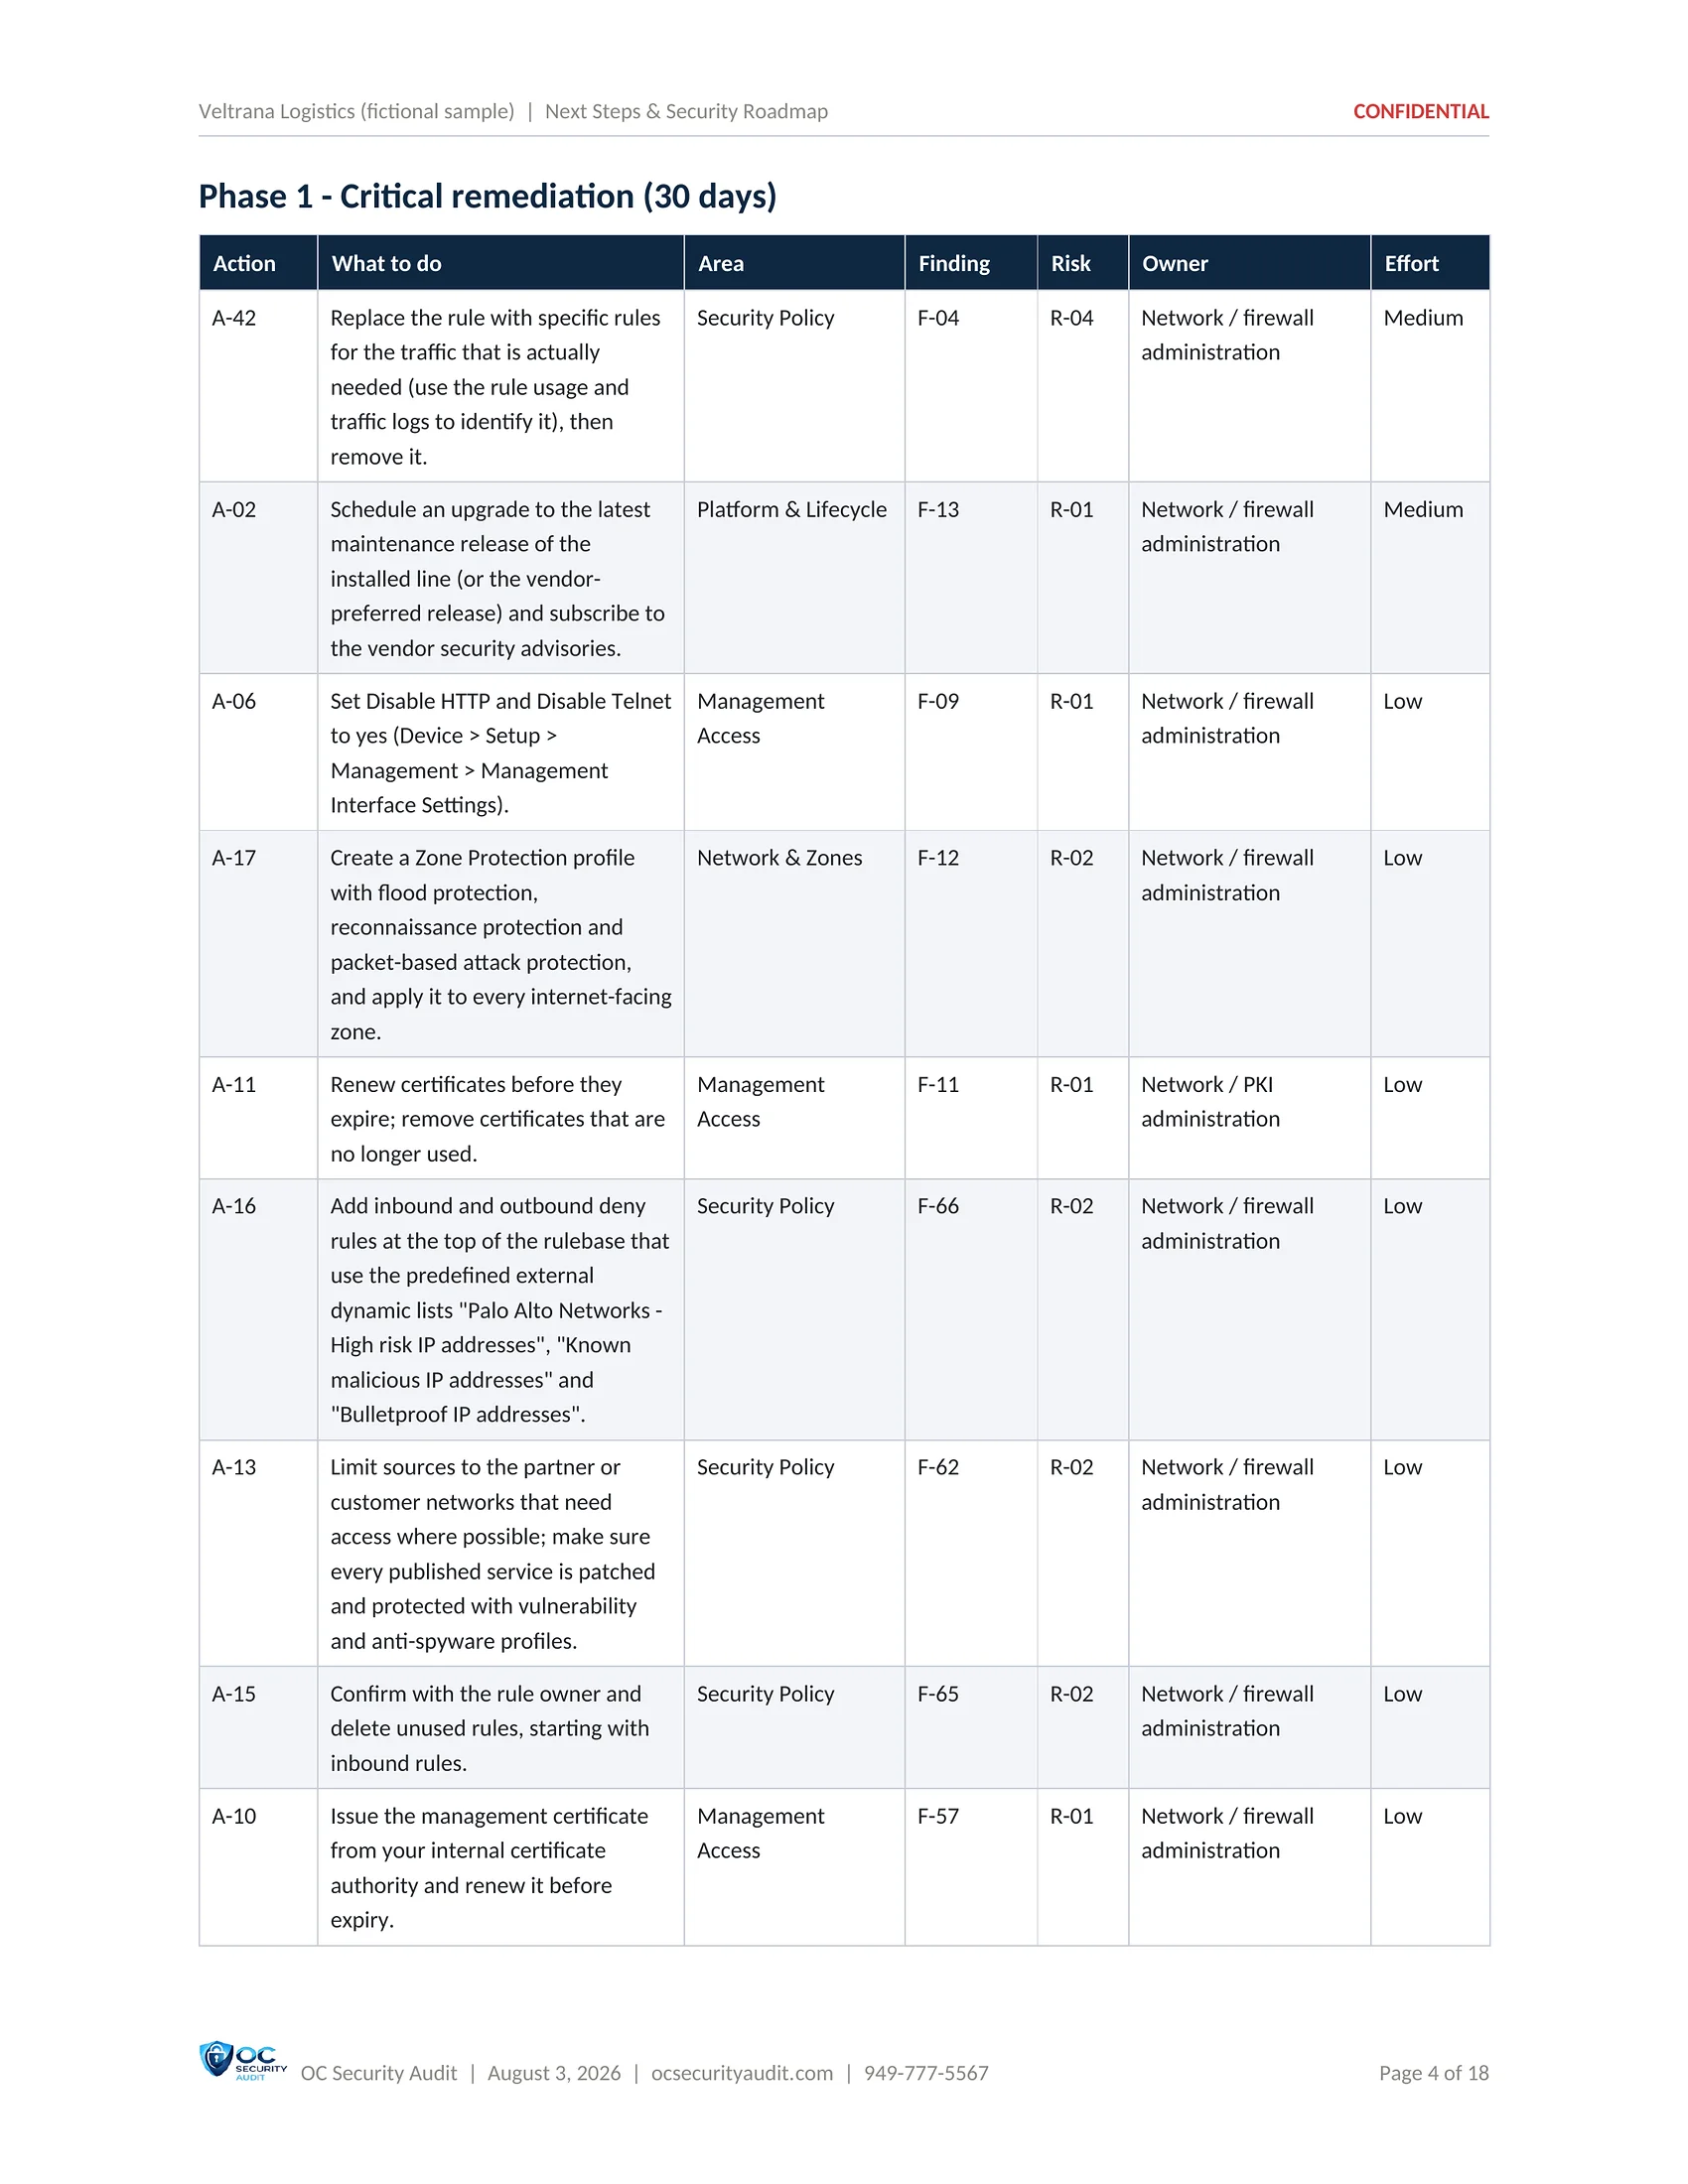
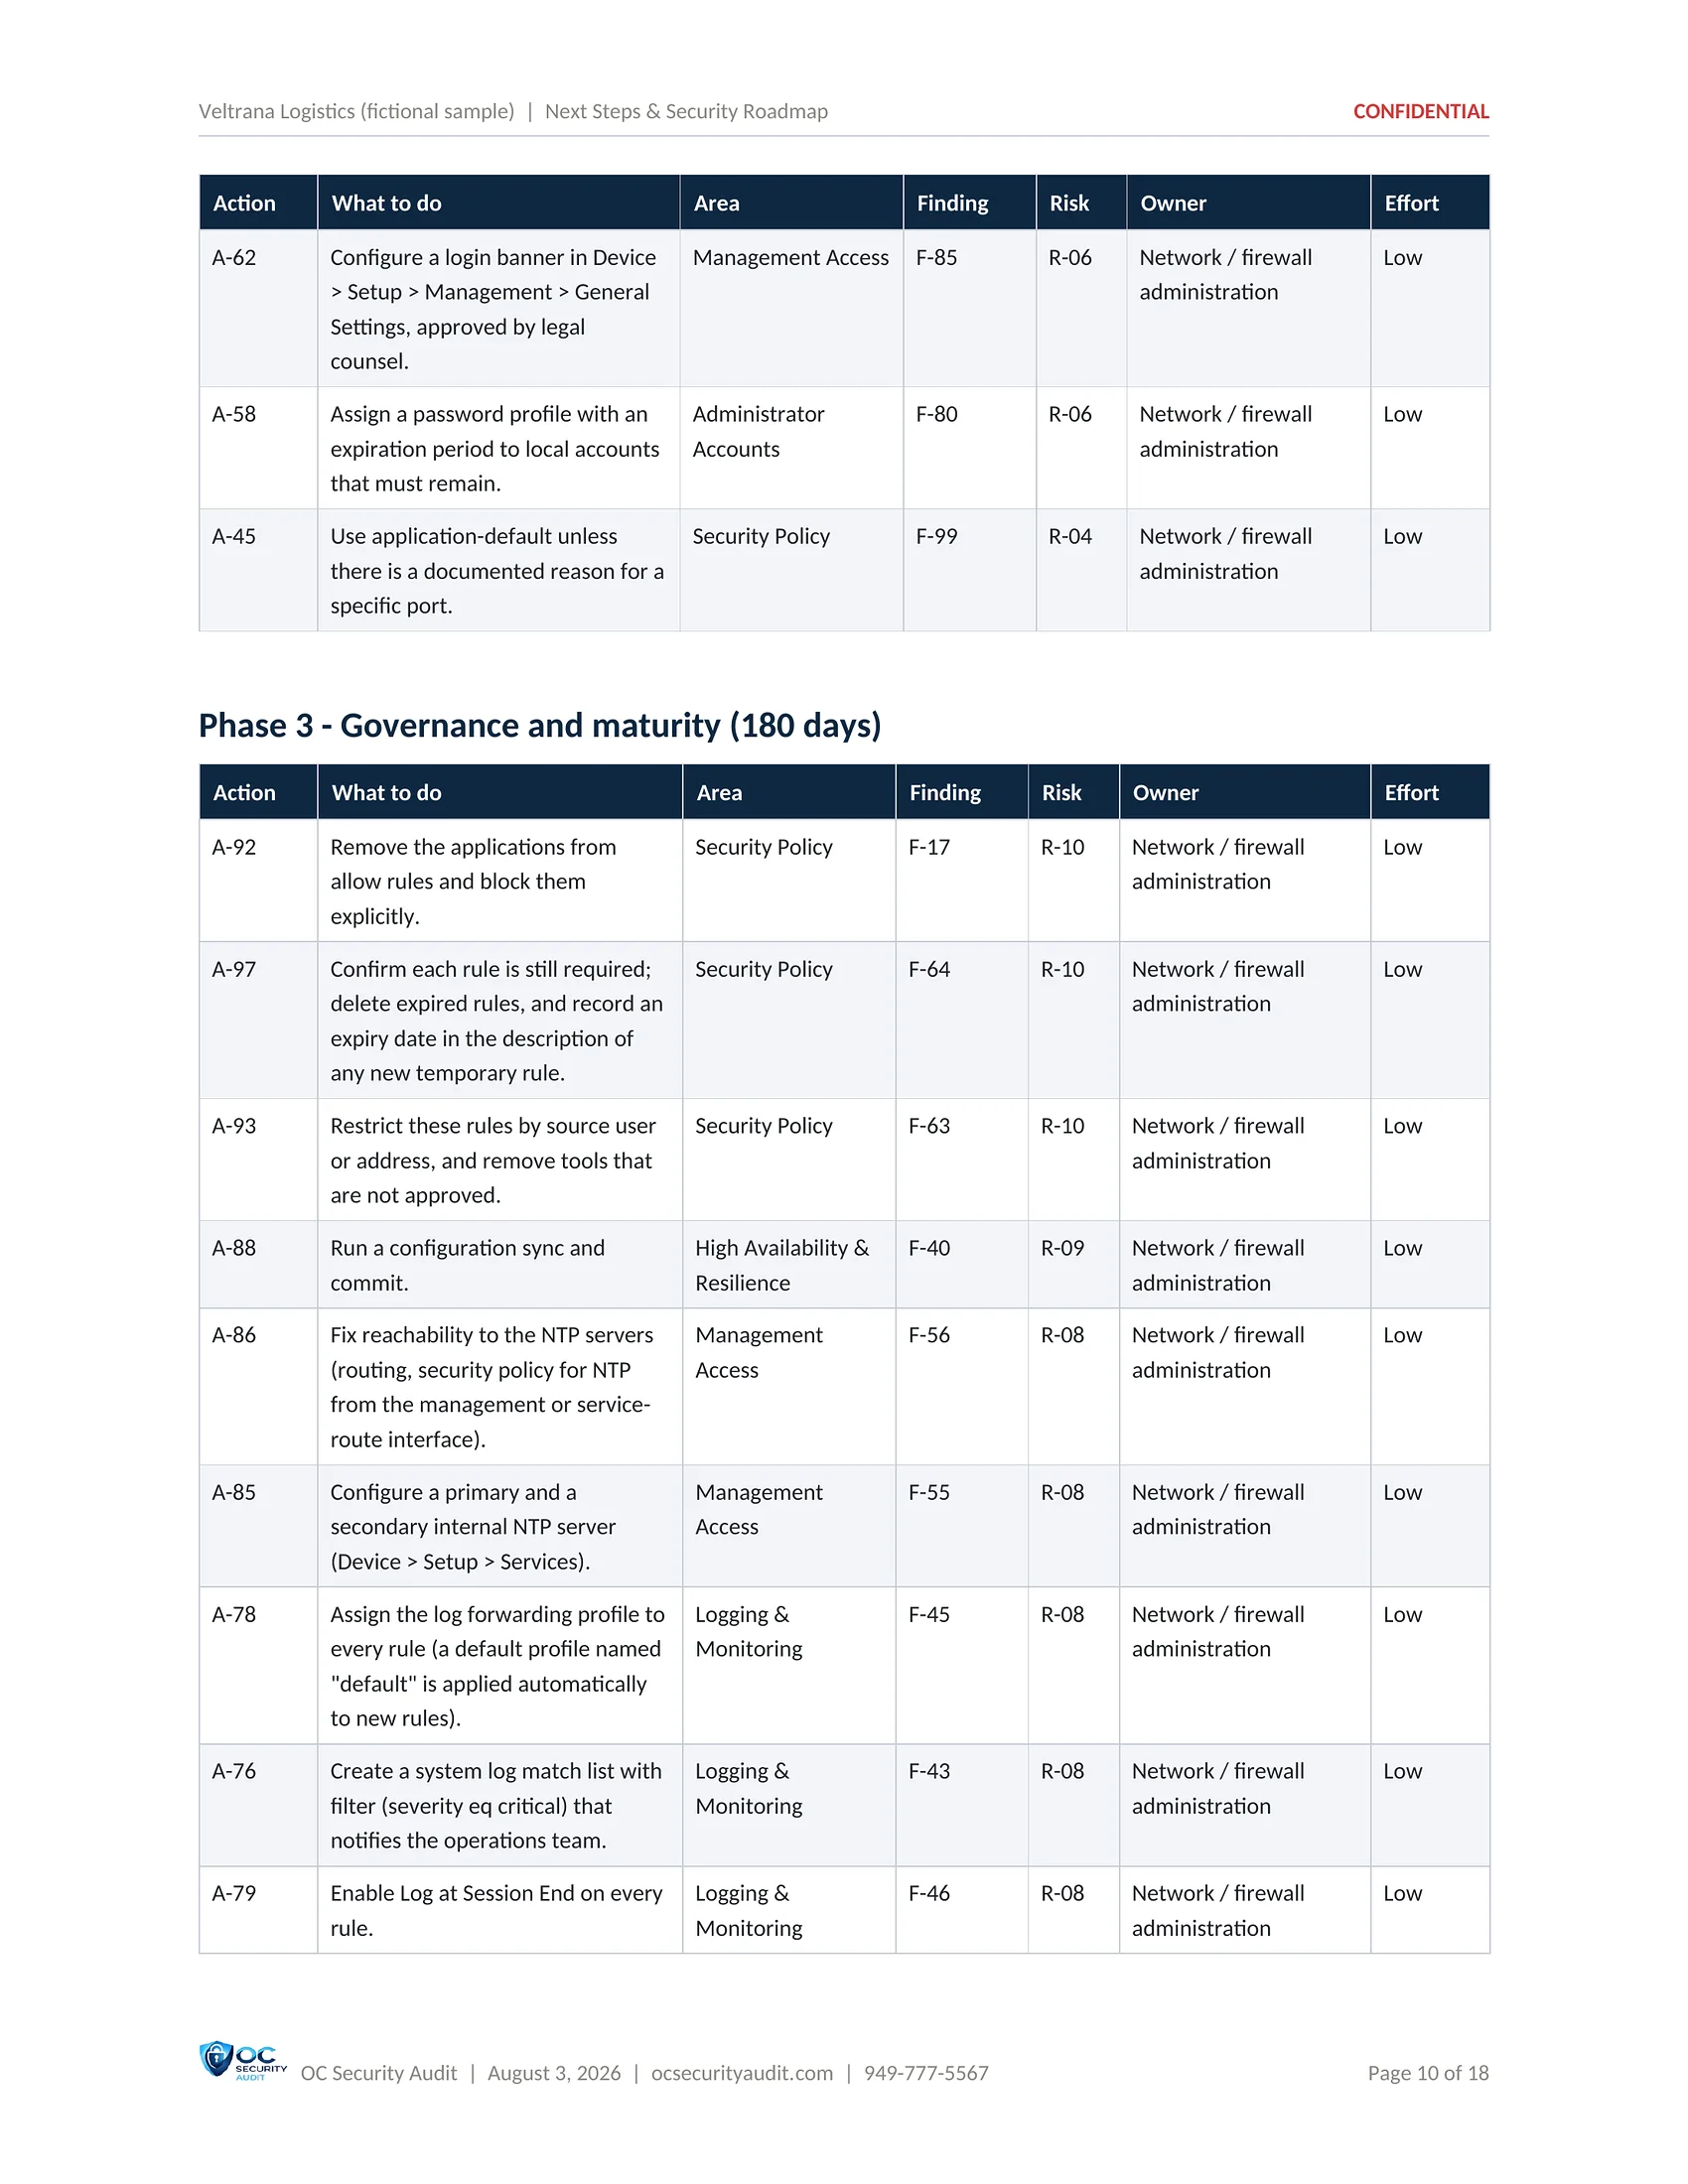
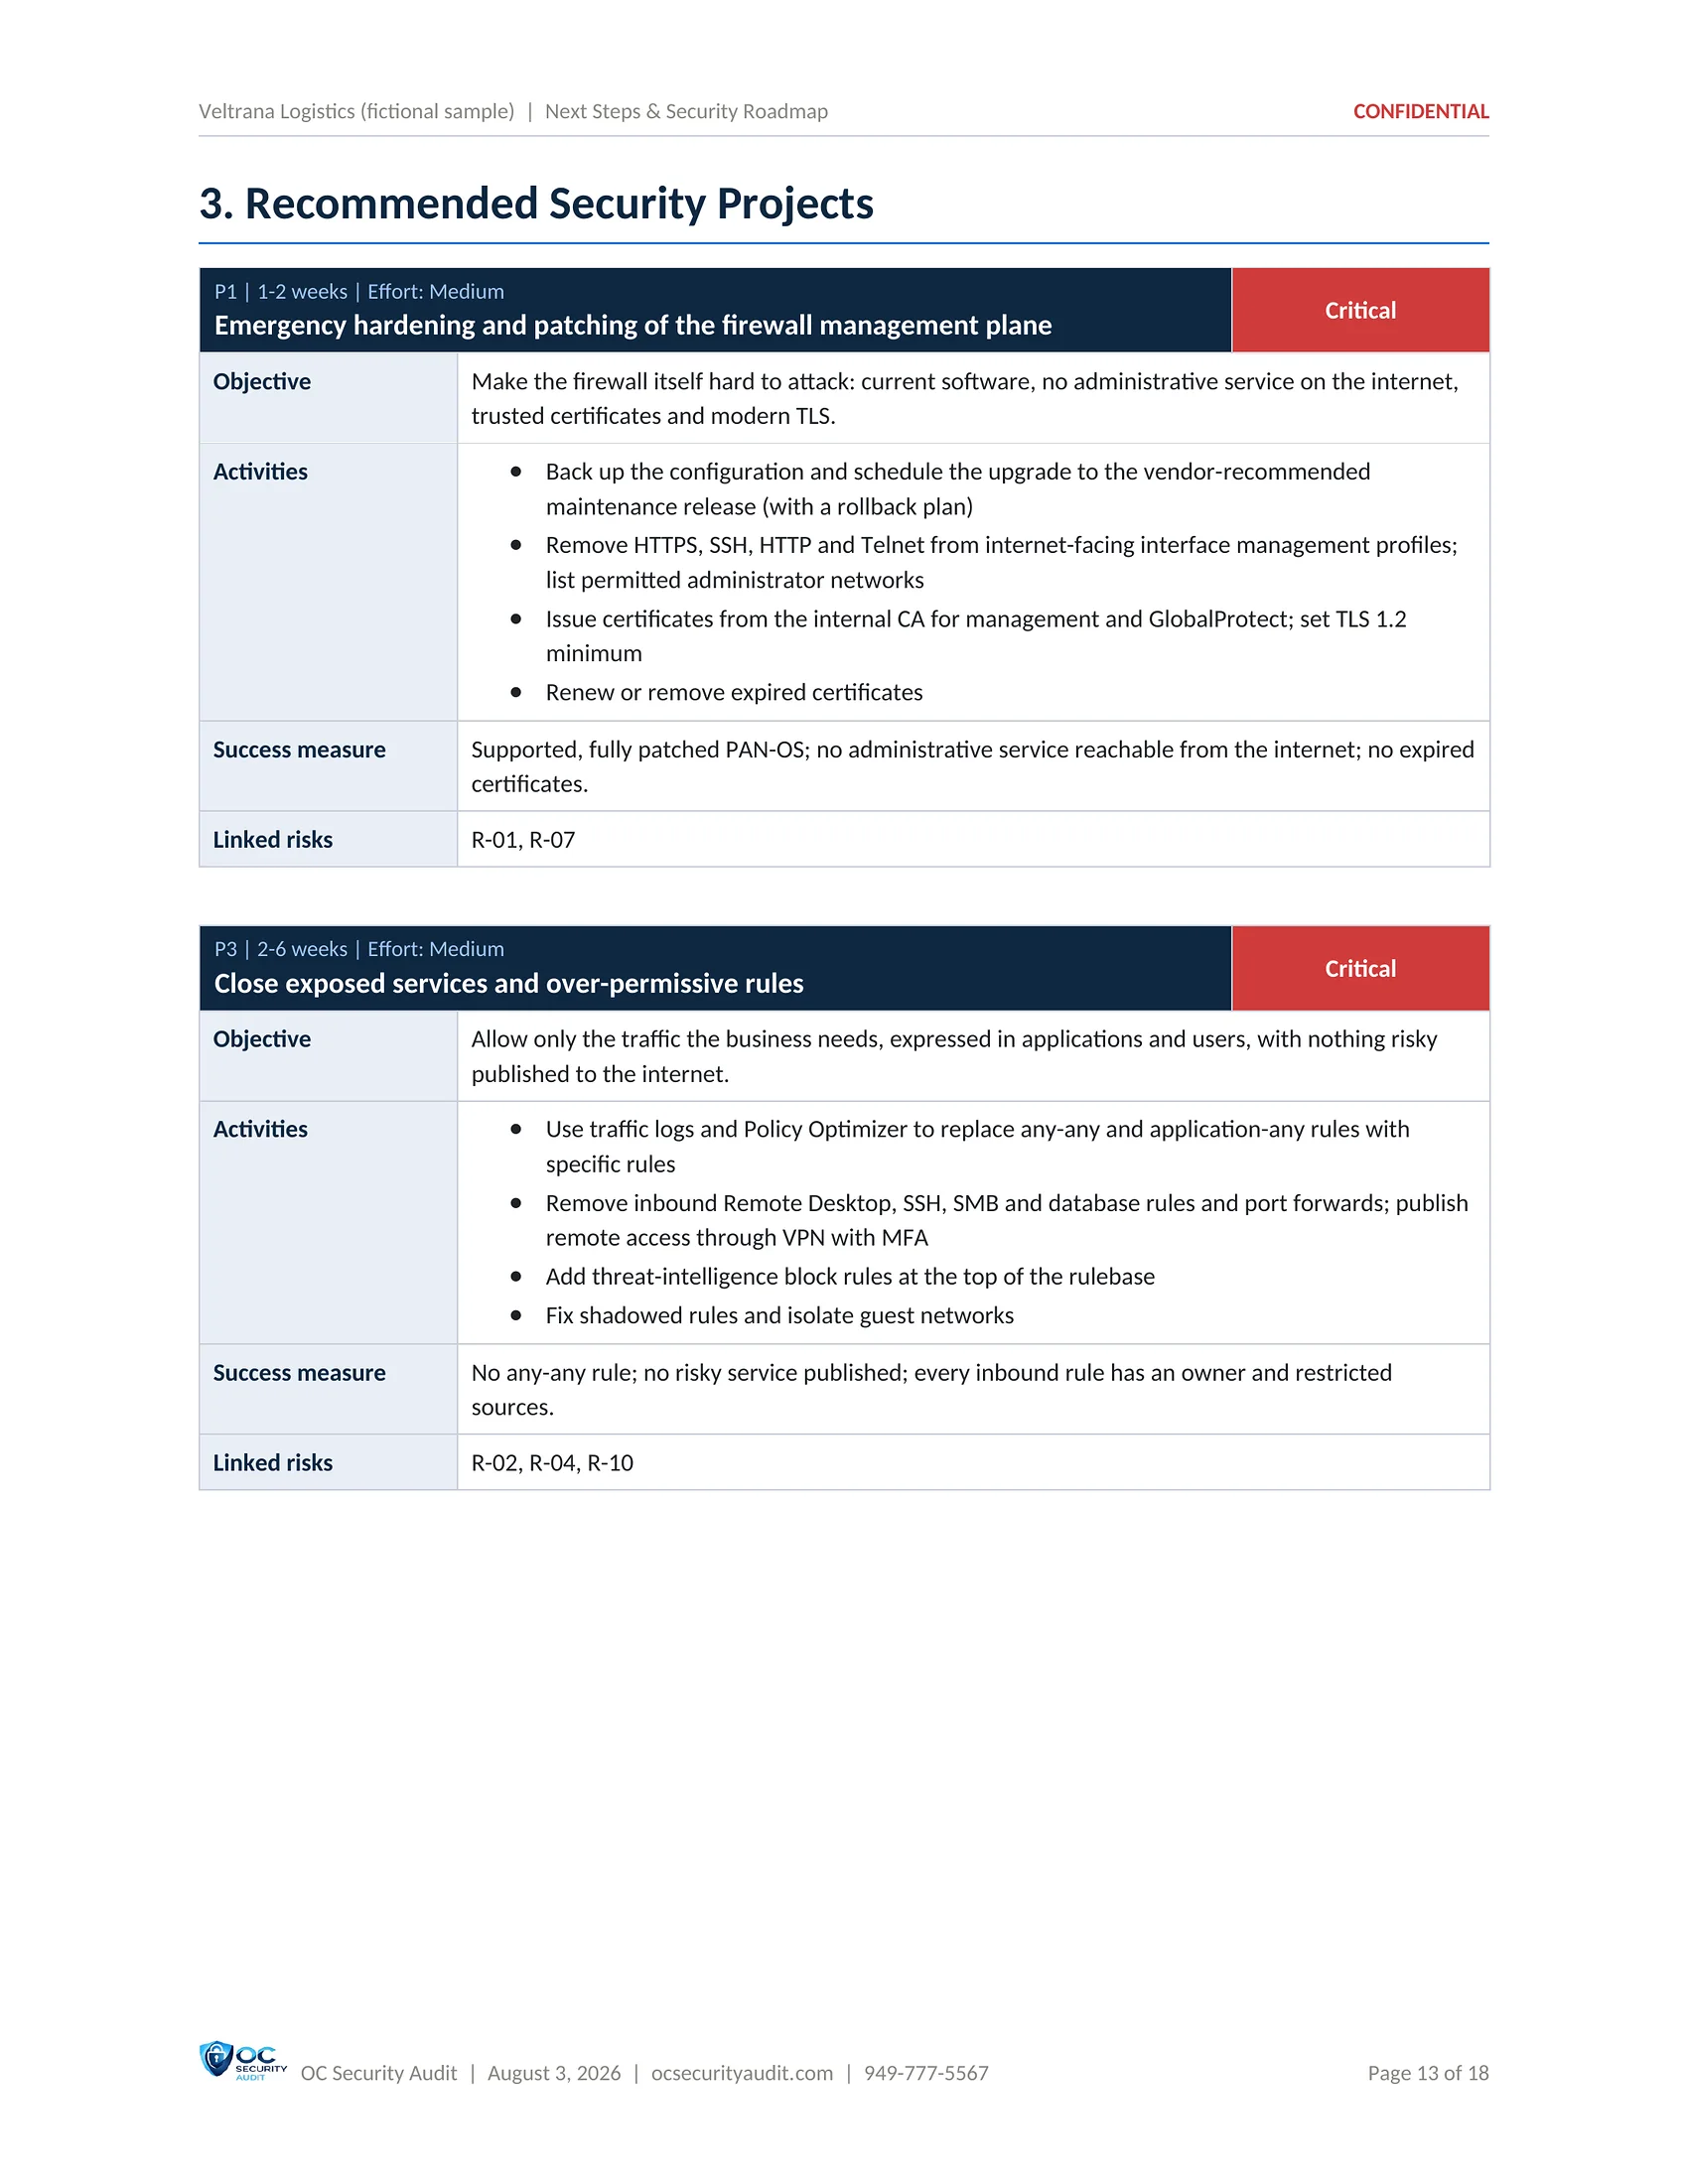
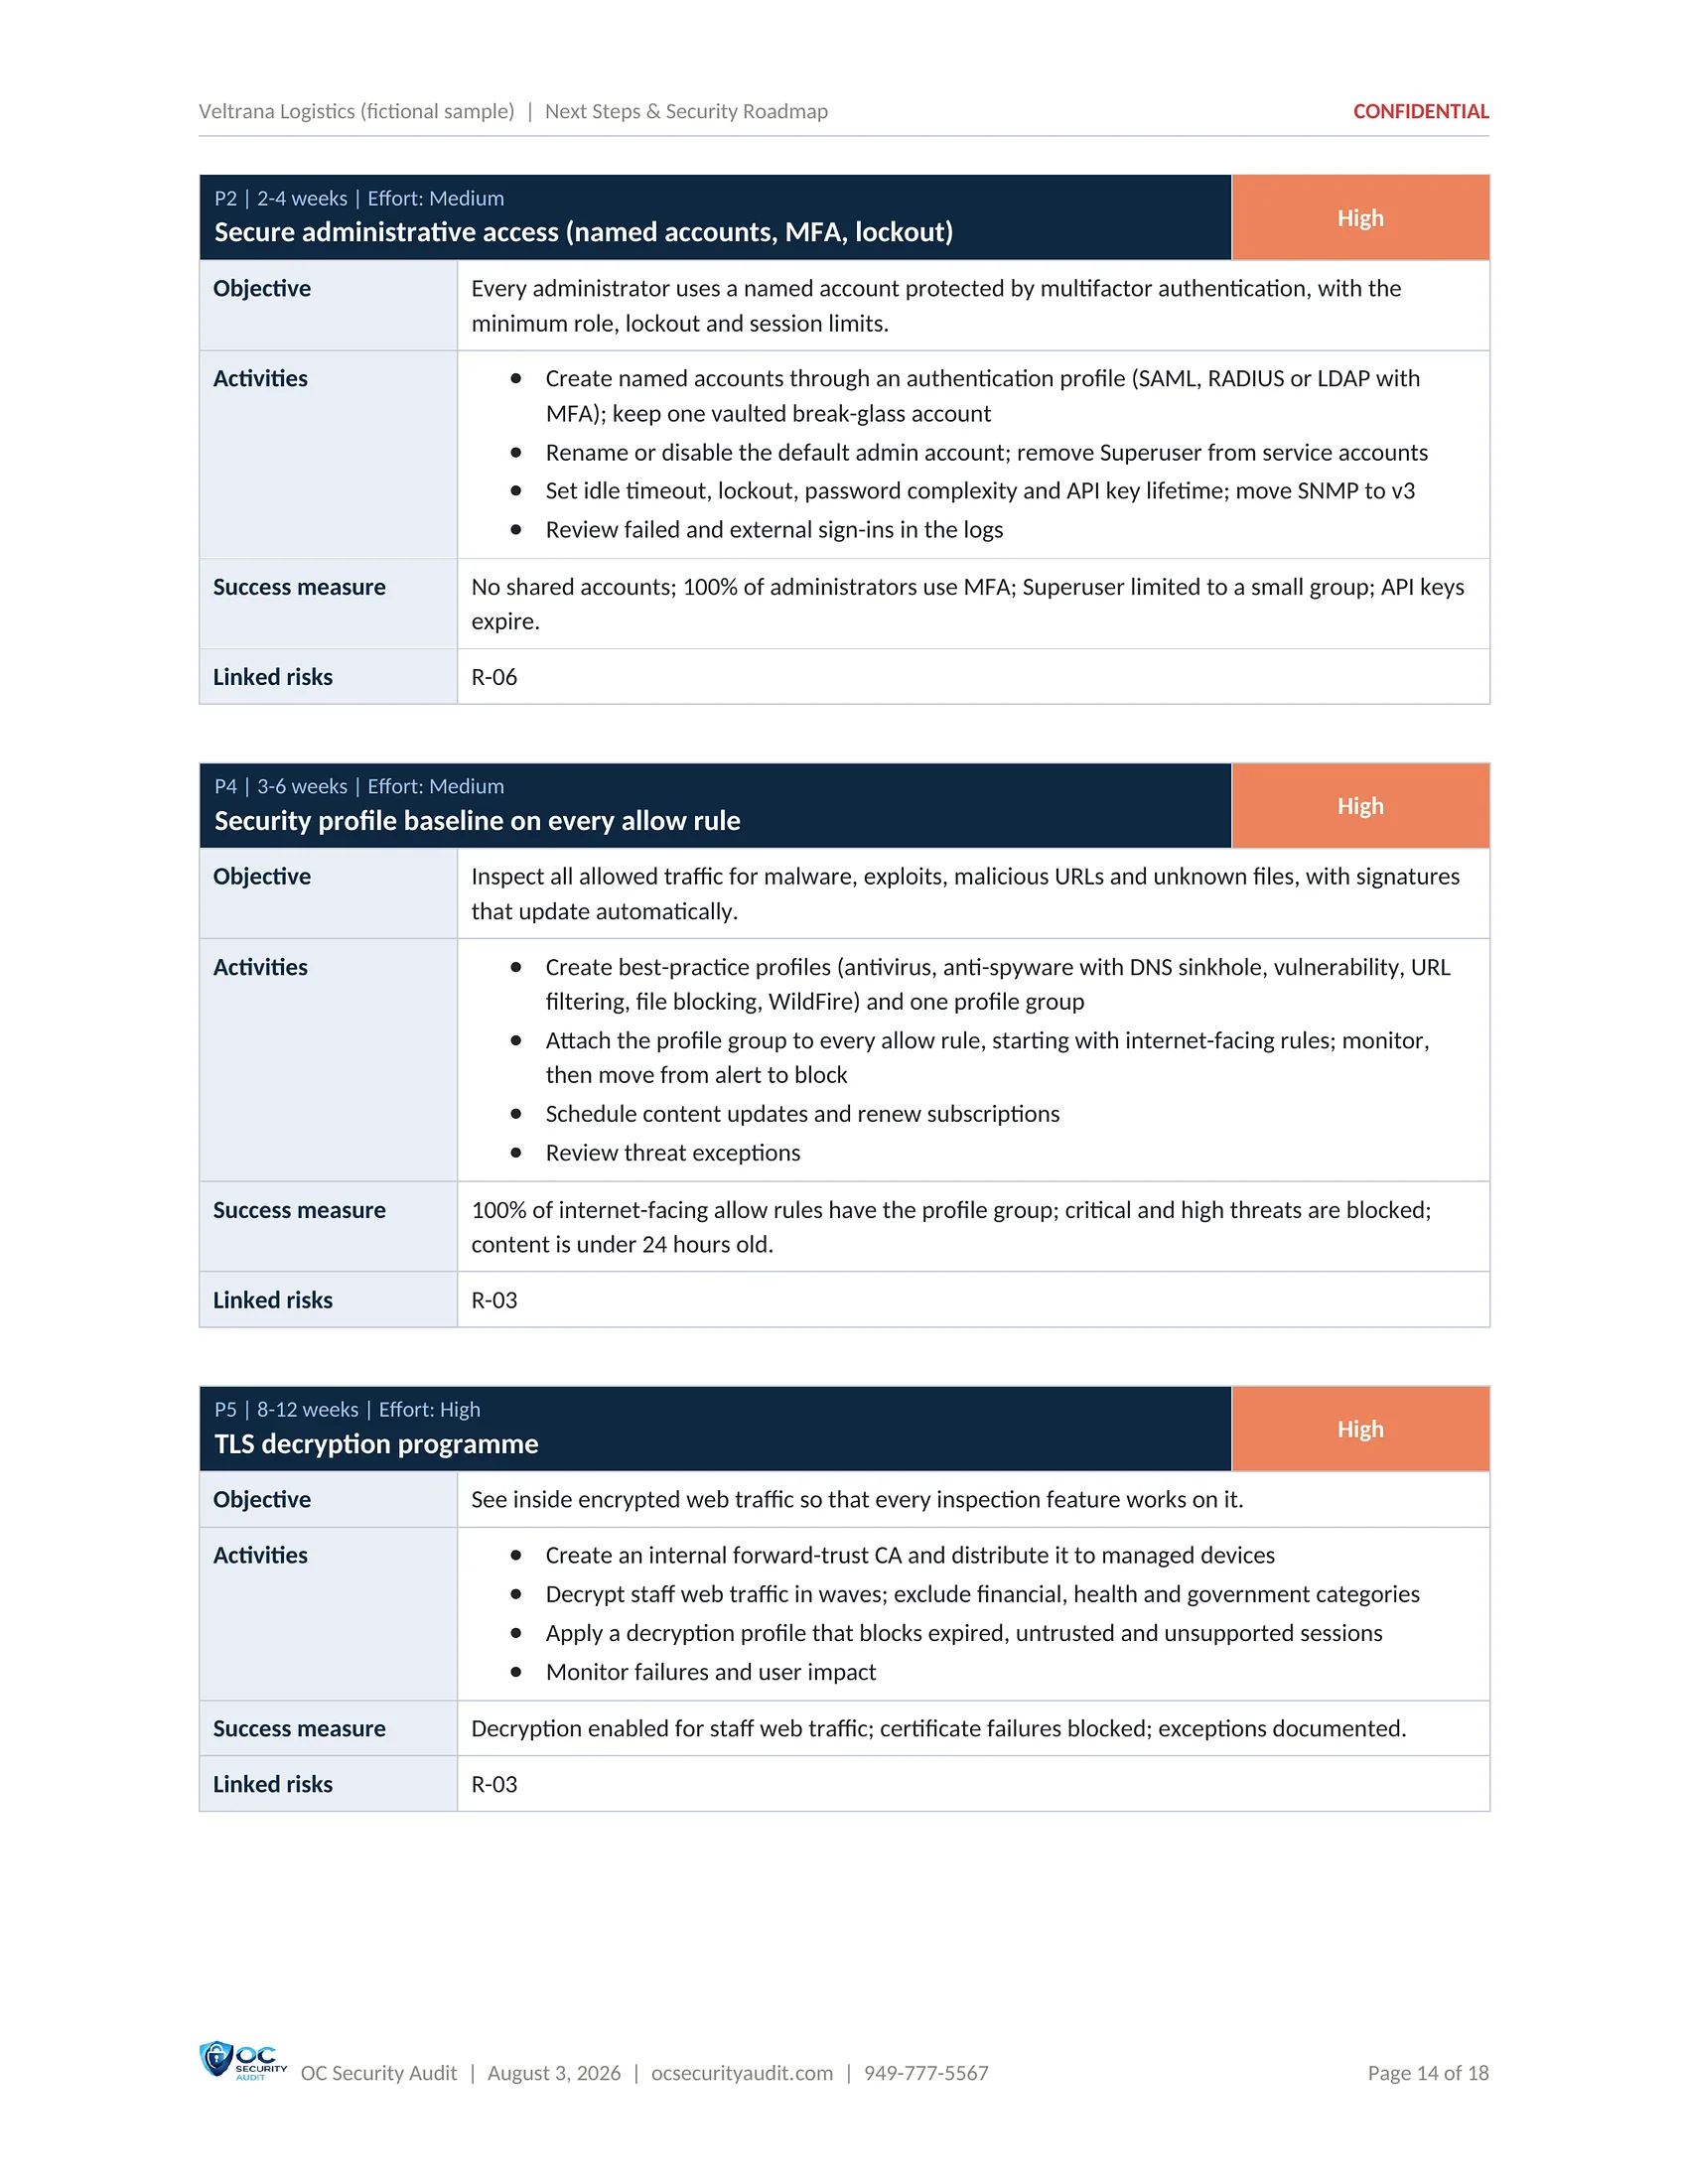
The plan that turns findings into work. Actions are ordered by risk into four phases, from the first 7 days to 180 days, and grouped into projects with an objective, activities and effort.
Who uses it
IT manager, vCISO, MSP, project lead
What is included
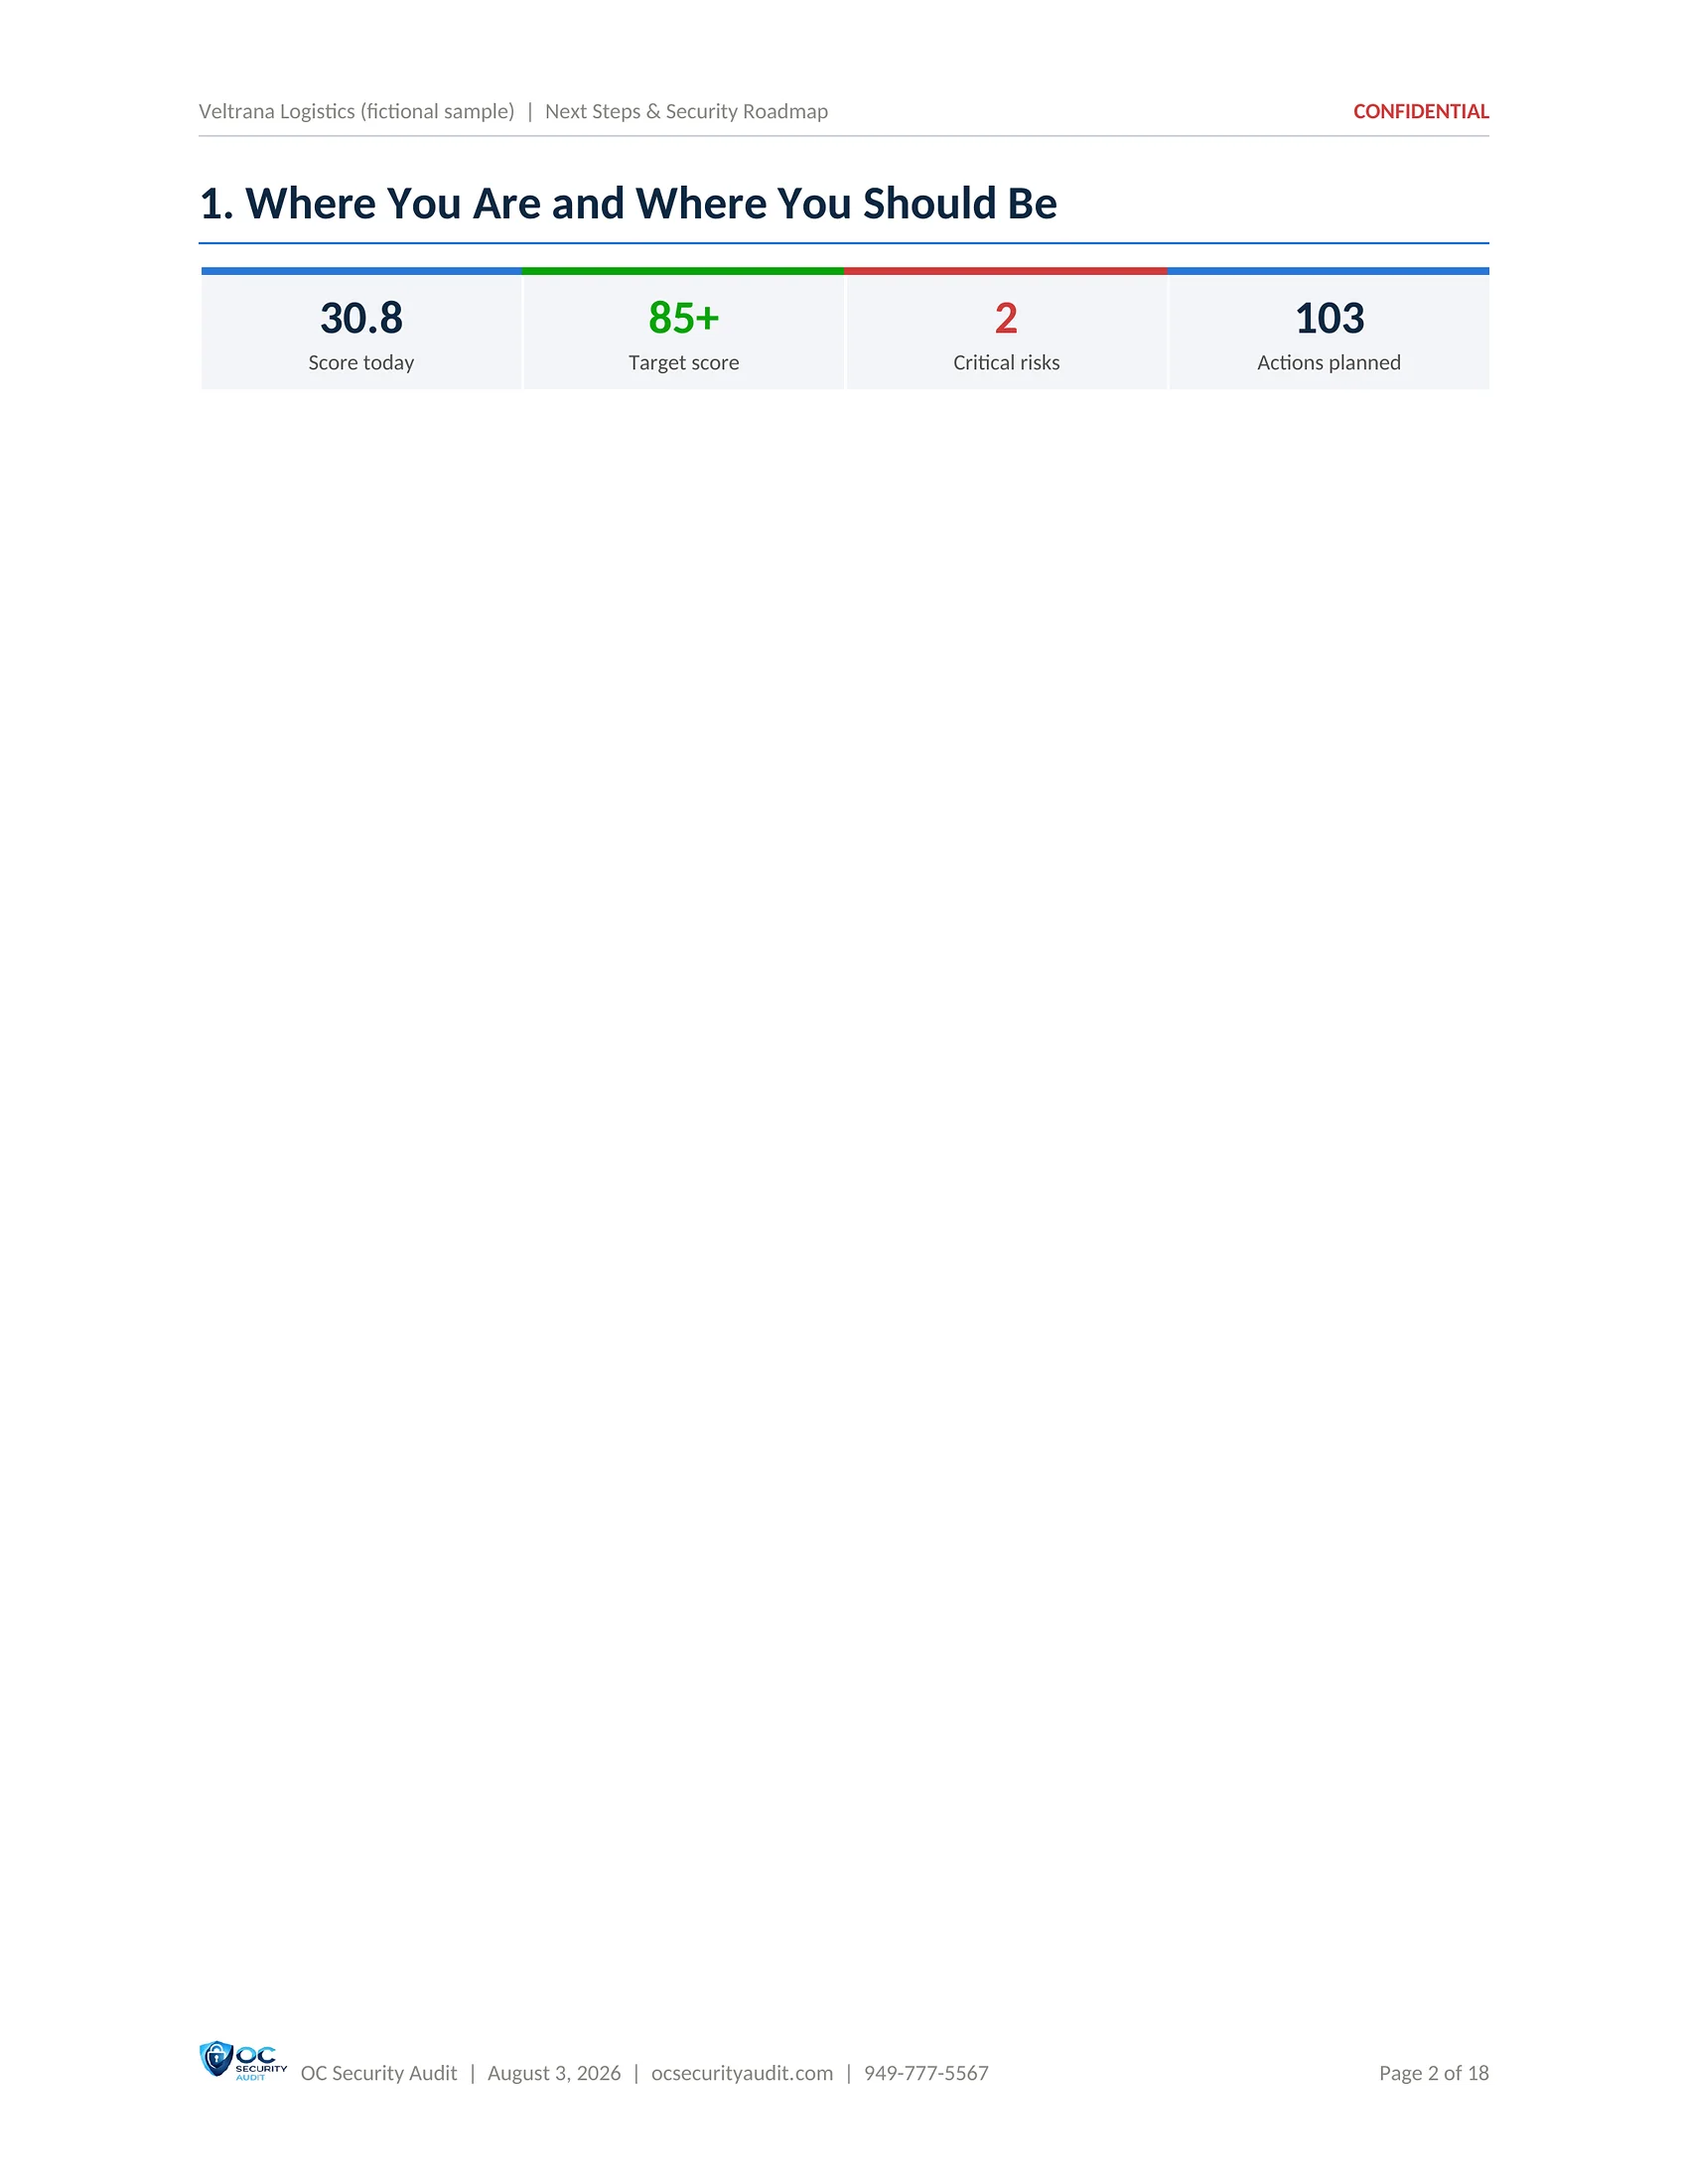
- Score today against the target
- Phase 0: contain and quick wins (7 days)
- Phase 1: critical remediation (30 days)
- Phase 2: high-priority hardening (90 days)
- Phase 3: governance and maturity (180 days)
- Recommended projects with activities and effort
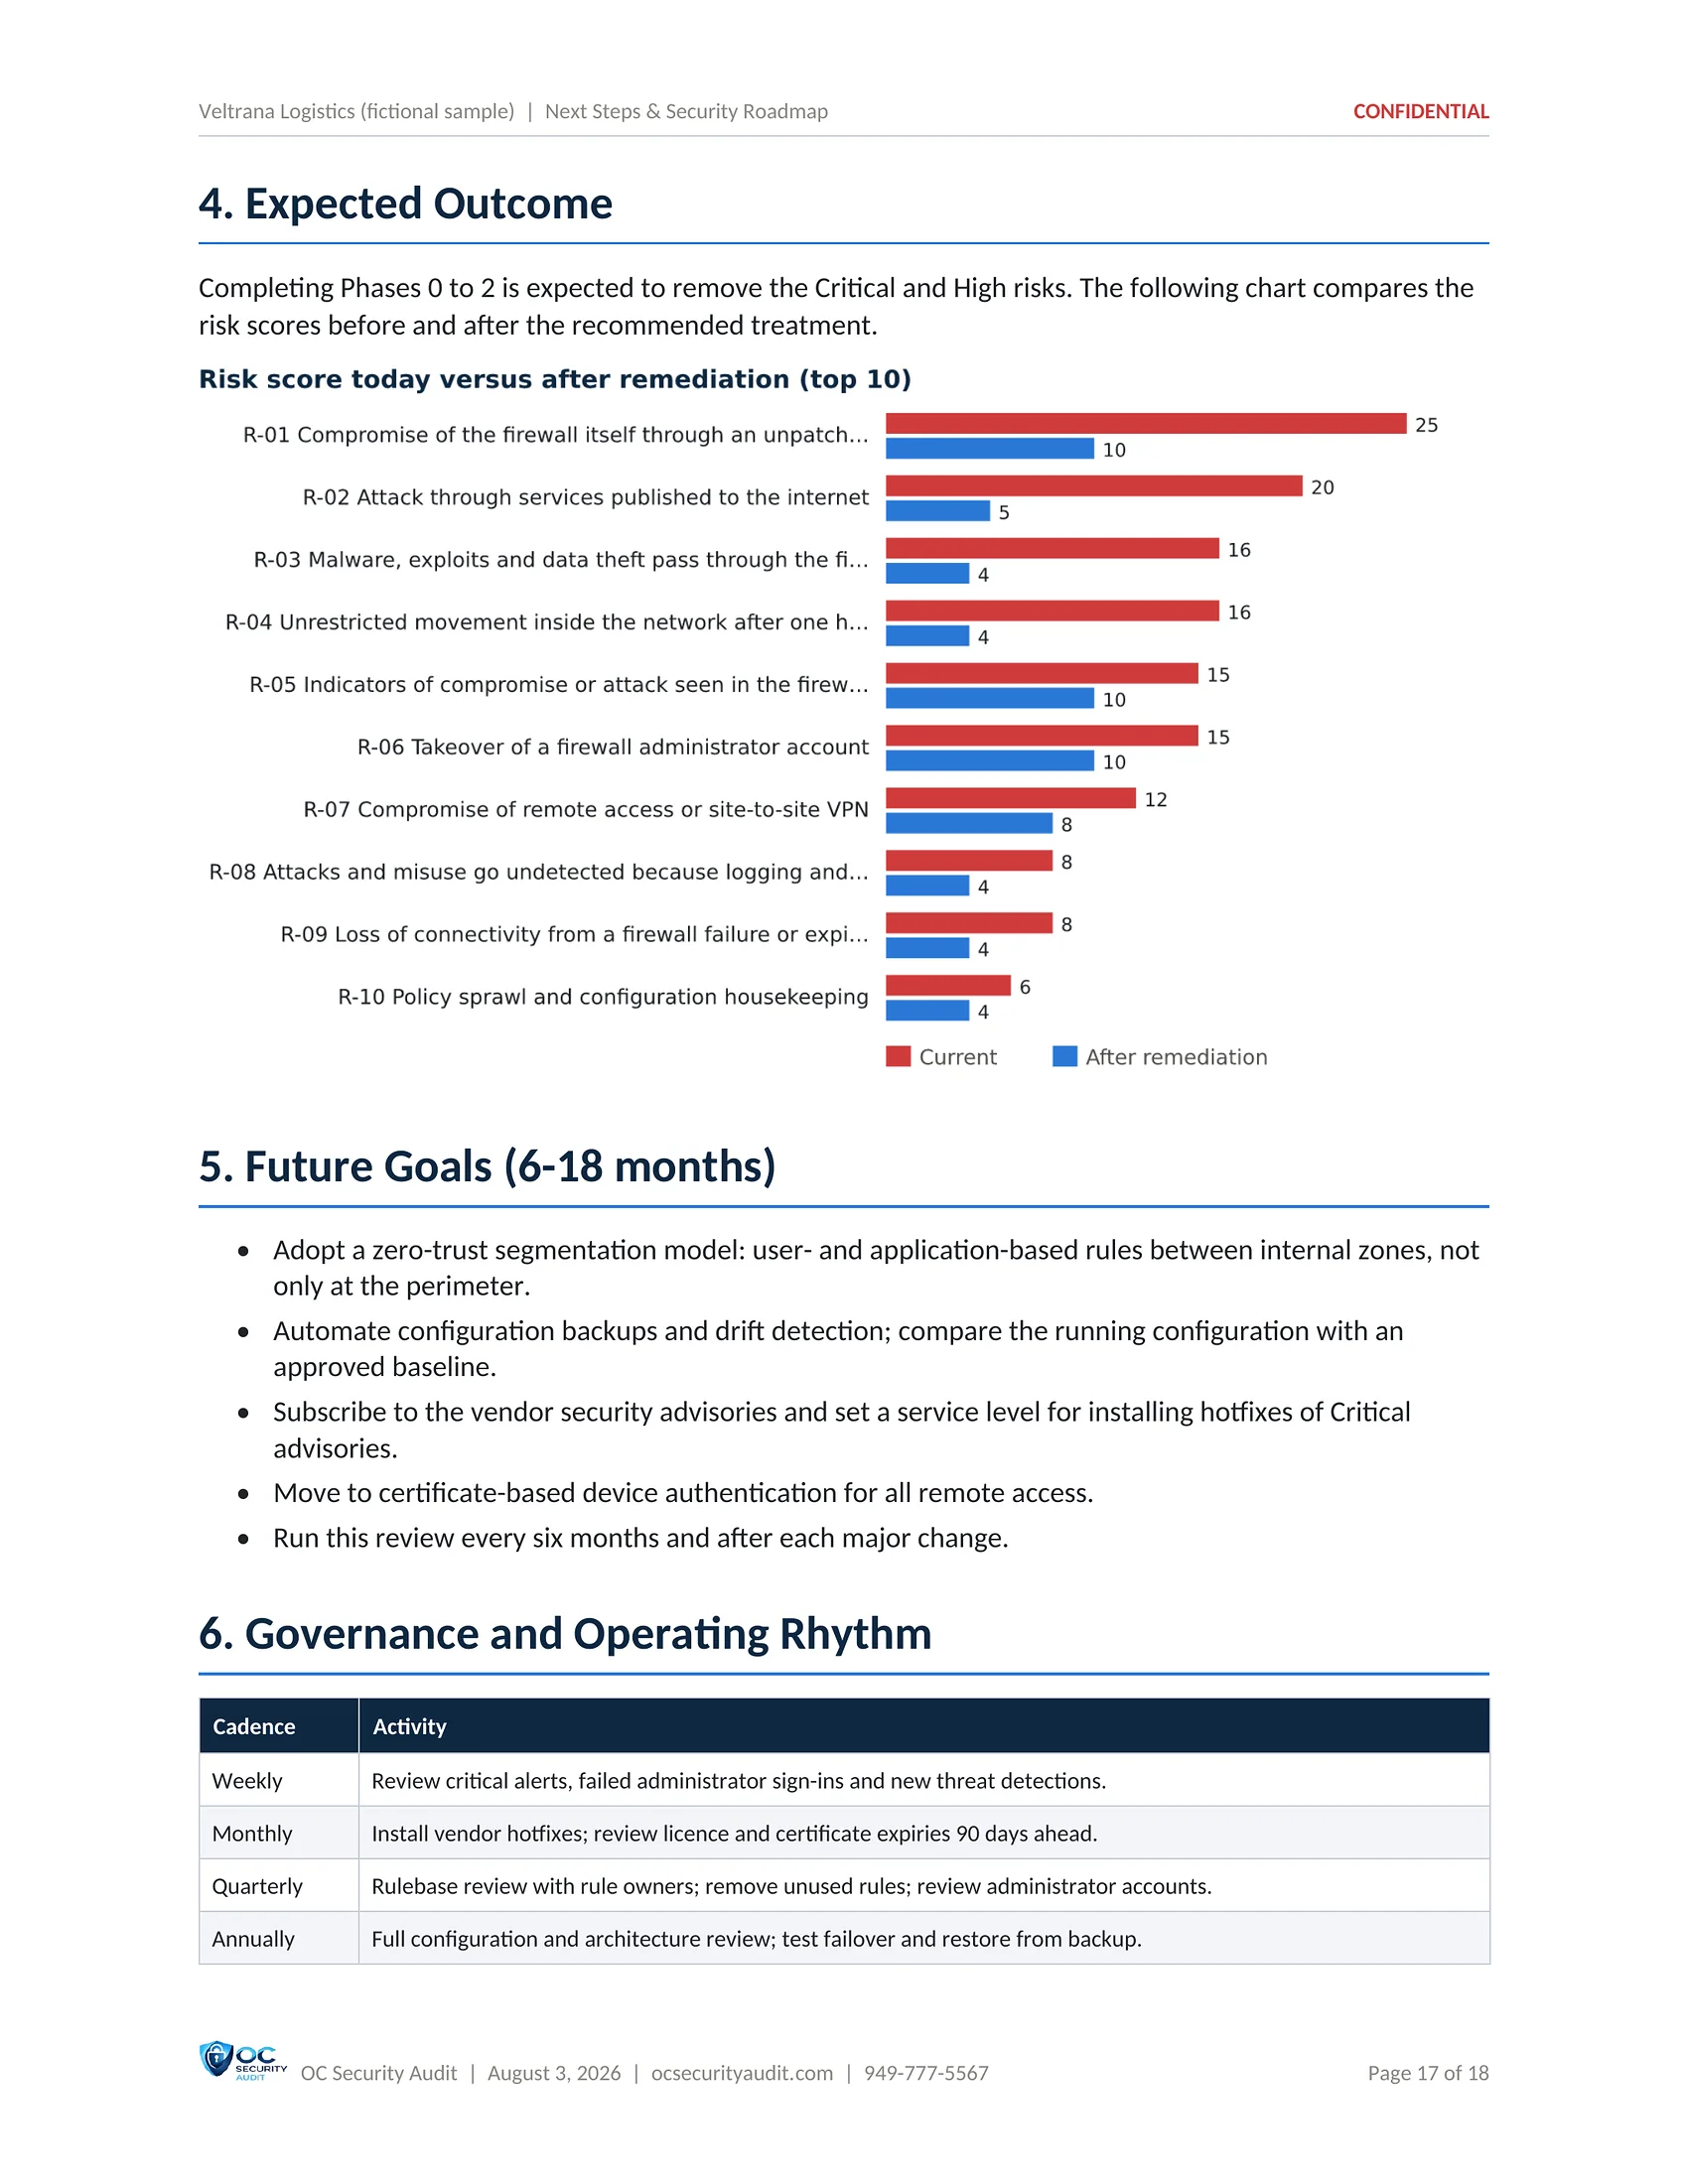
- Expected outcome and future goals
- Governance and operating rhythm
Click the centre page to open it full size. Use the arrows, the thumbnails or your arrow keys to move between pages.
Deliverable 7 of 7 · Excel · 26 tabs
Technical Findings Workbook
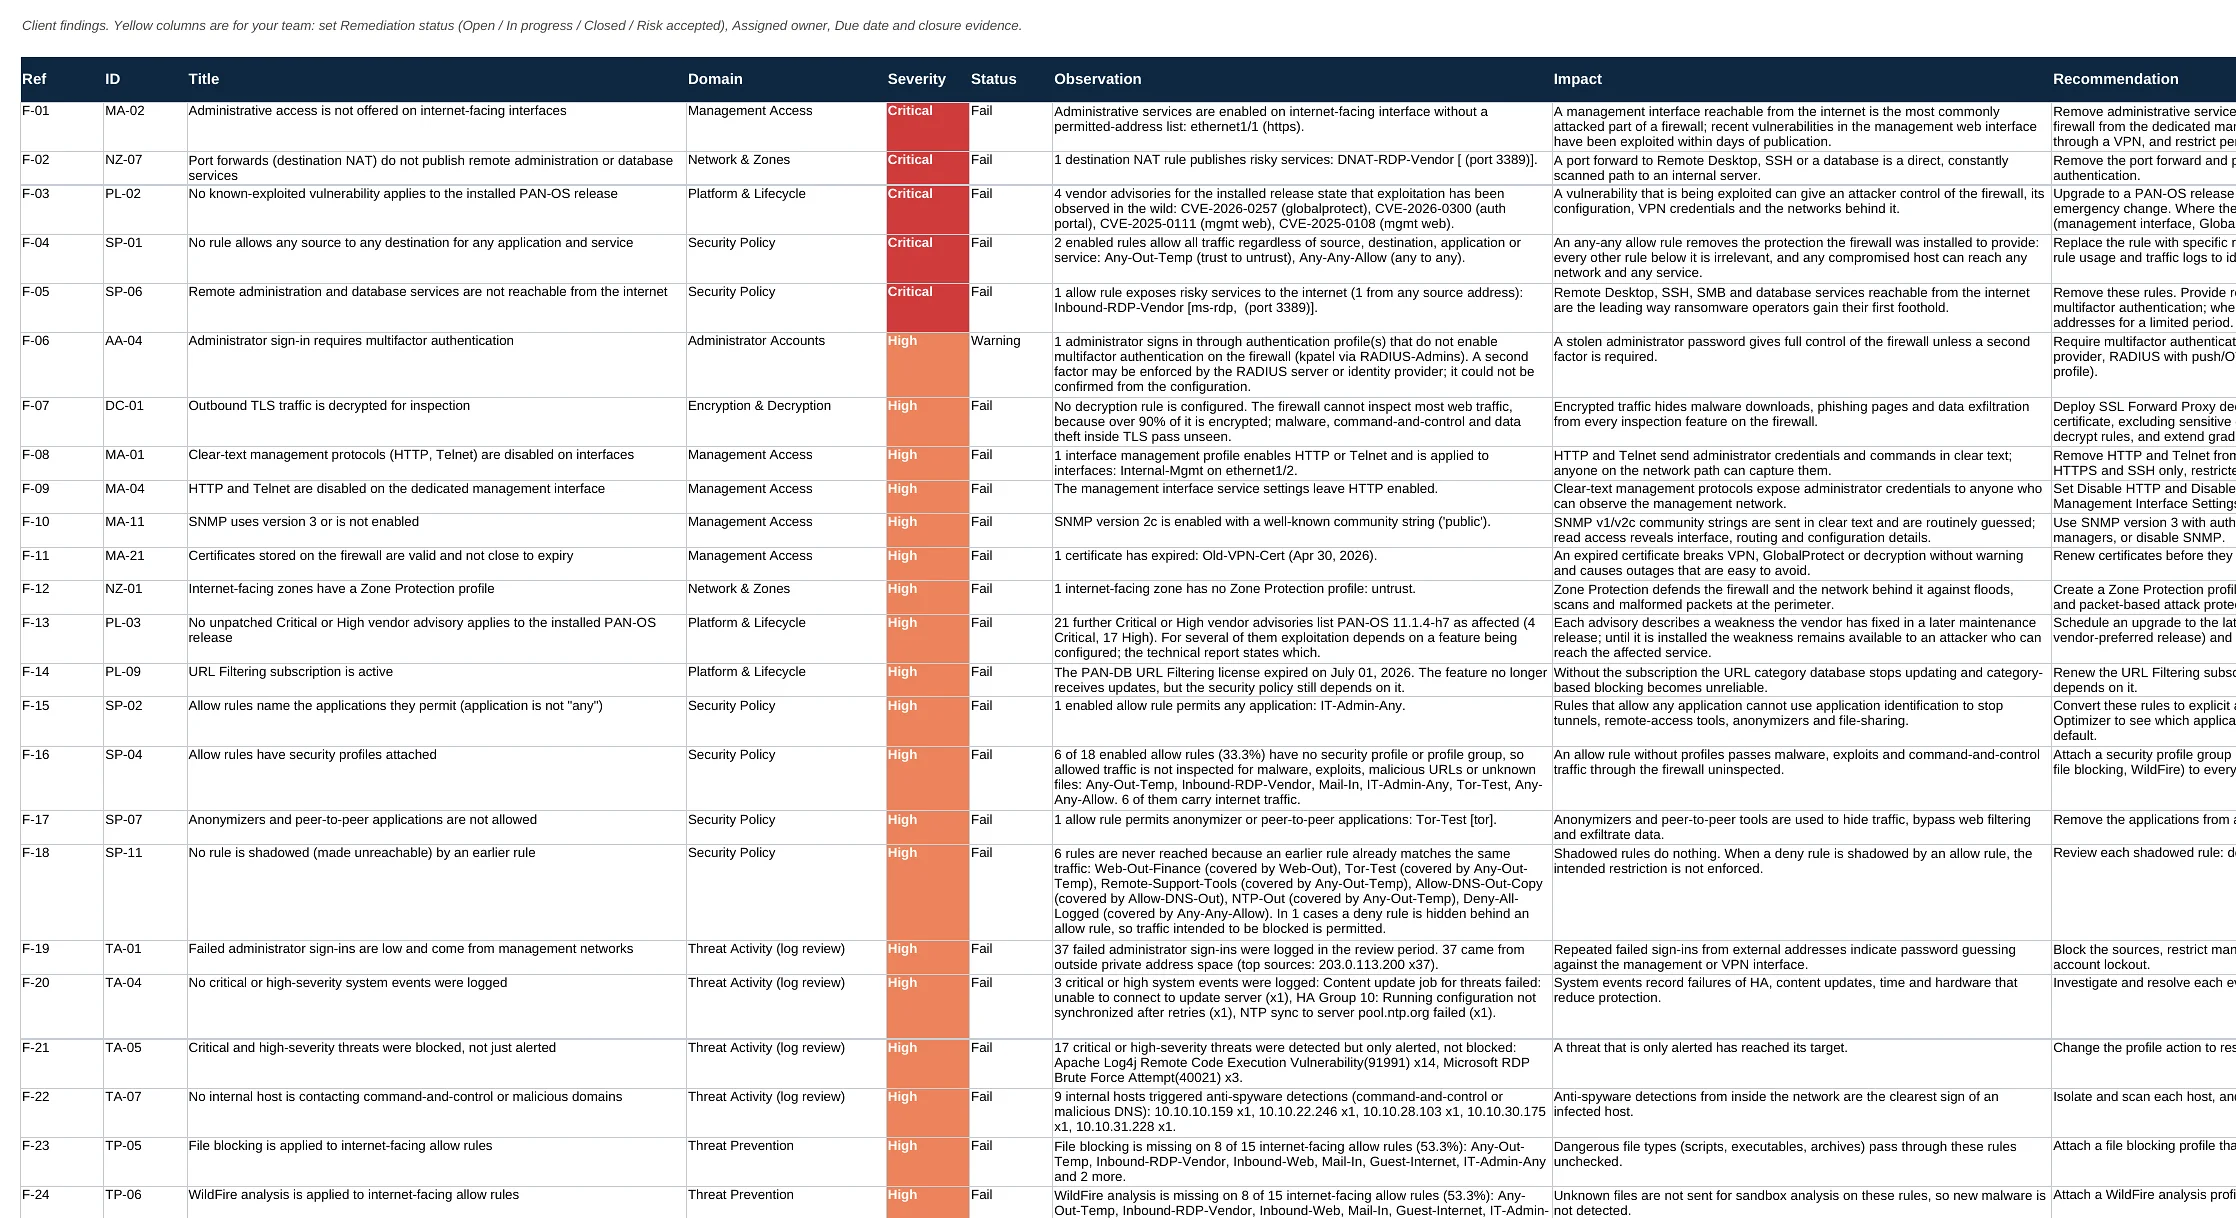
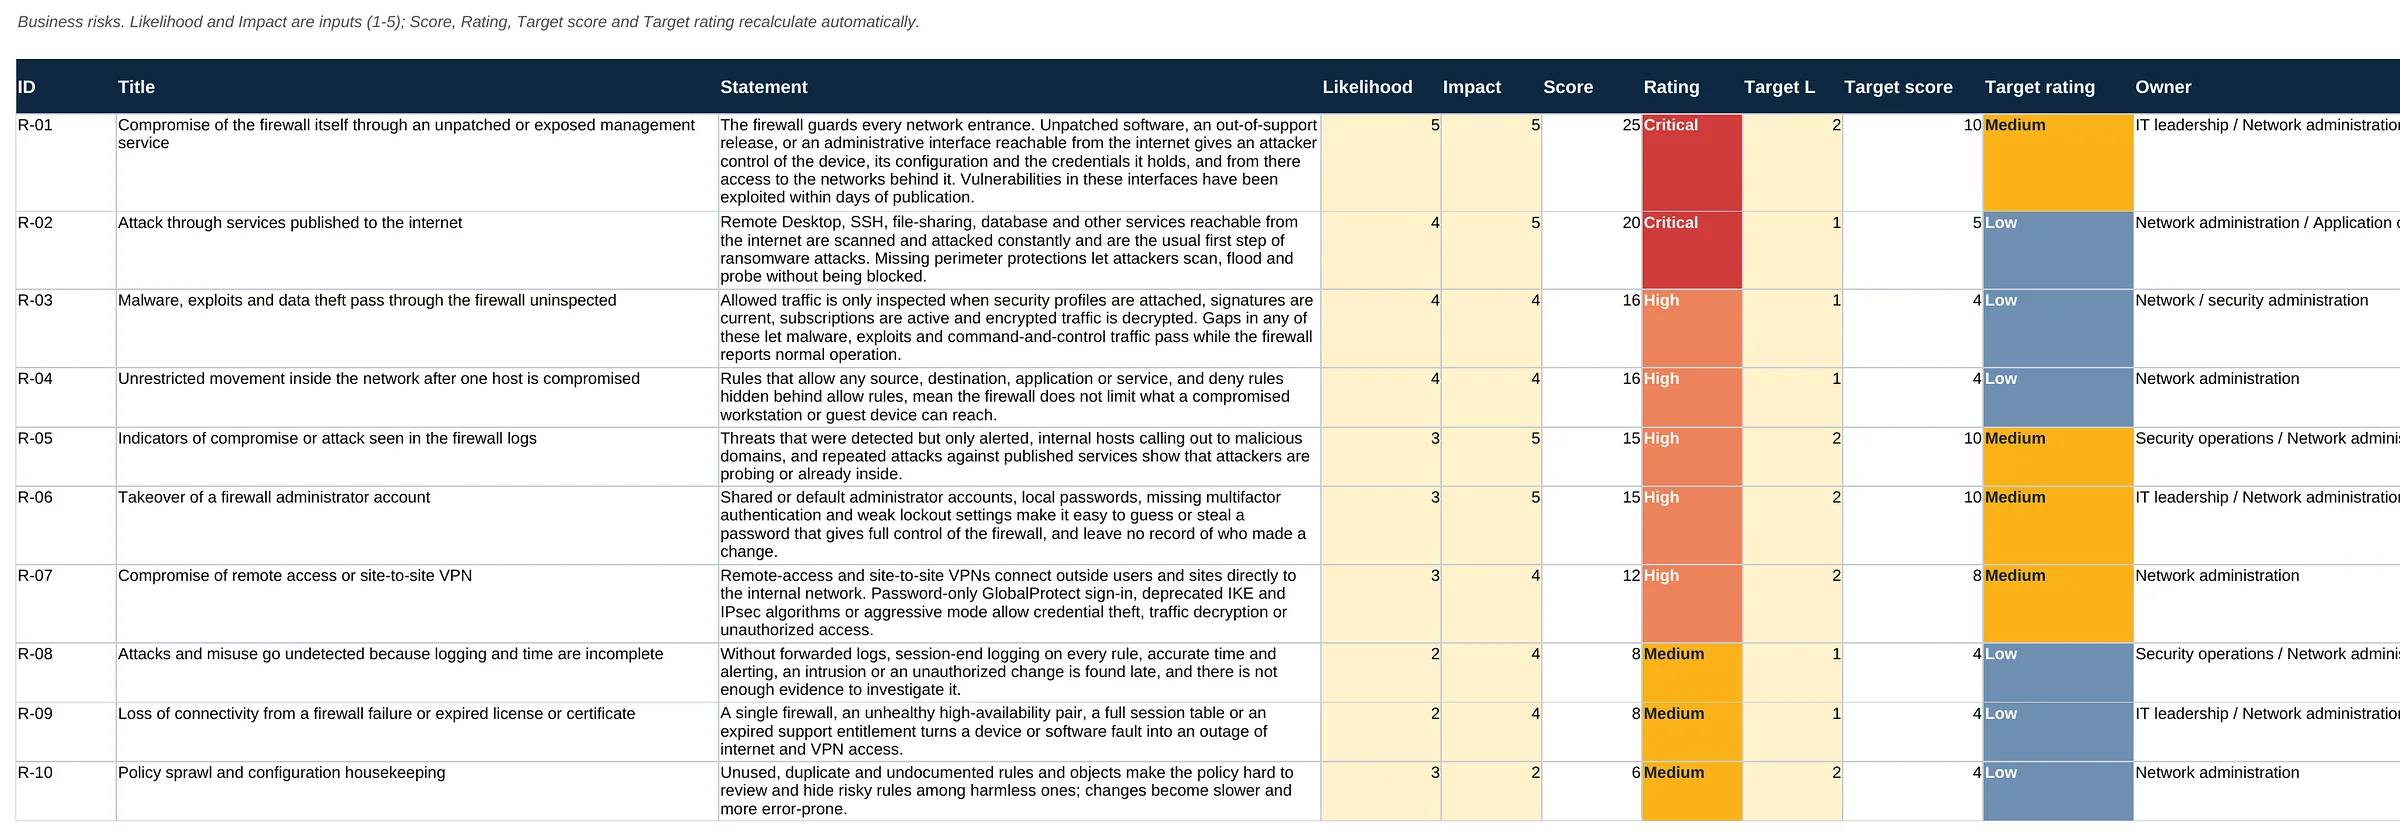
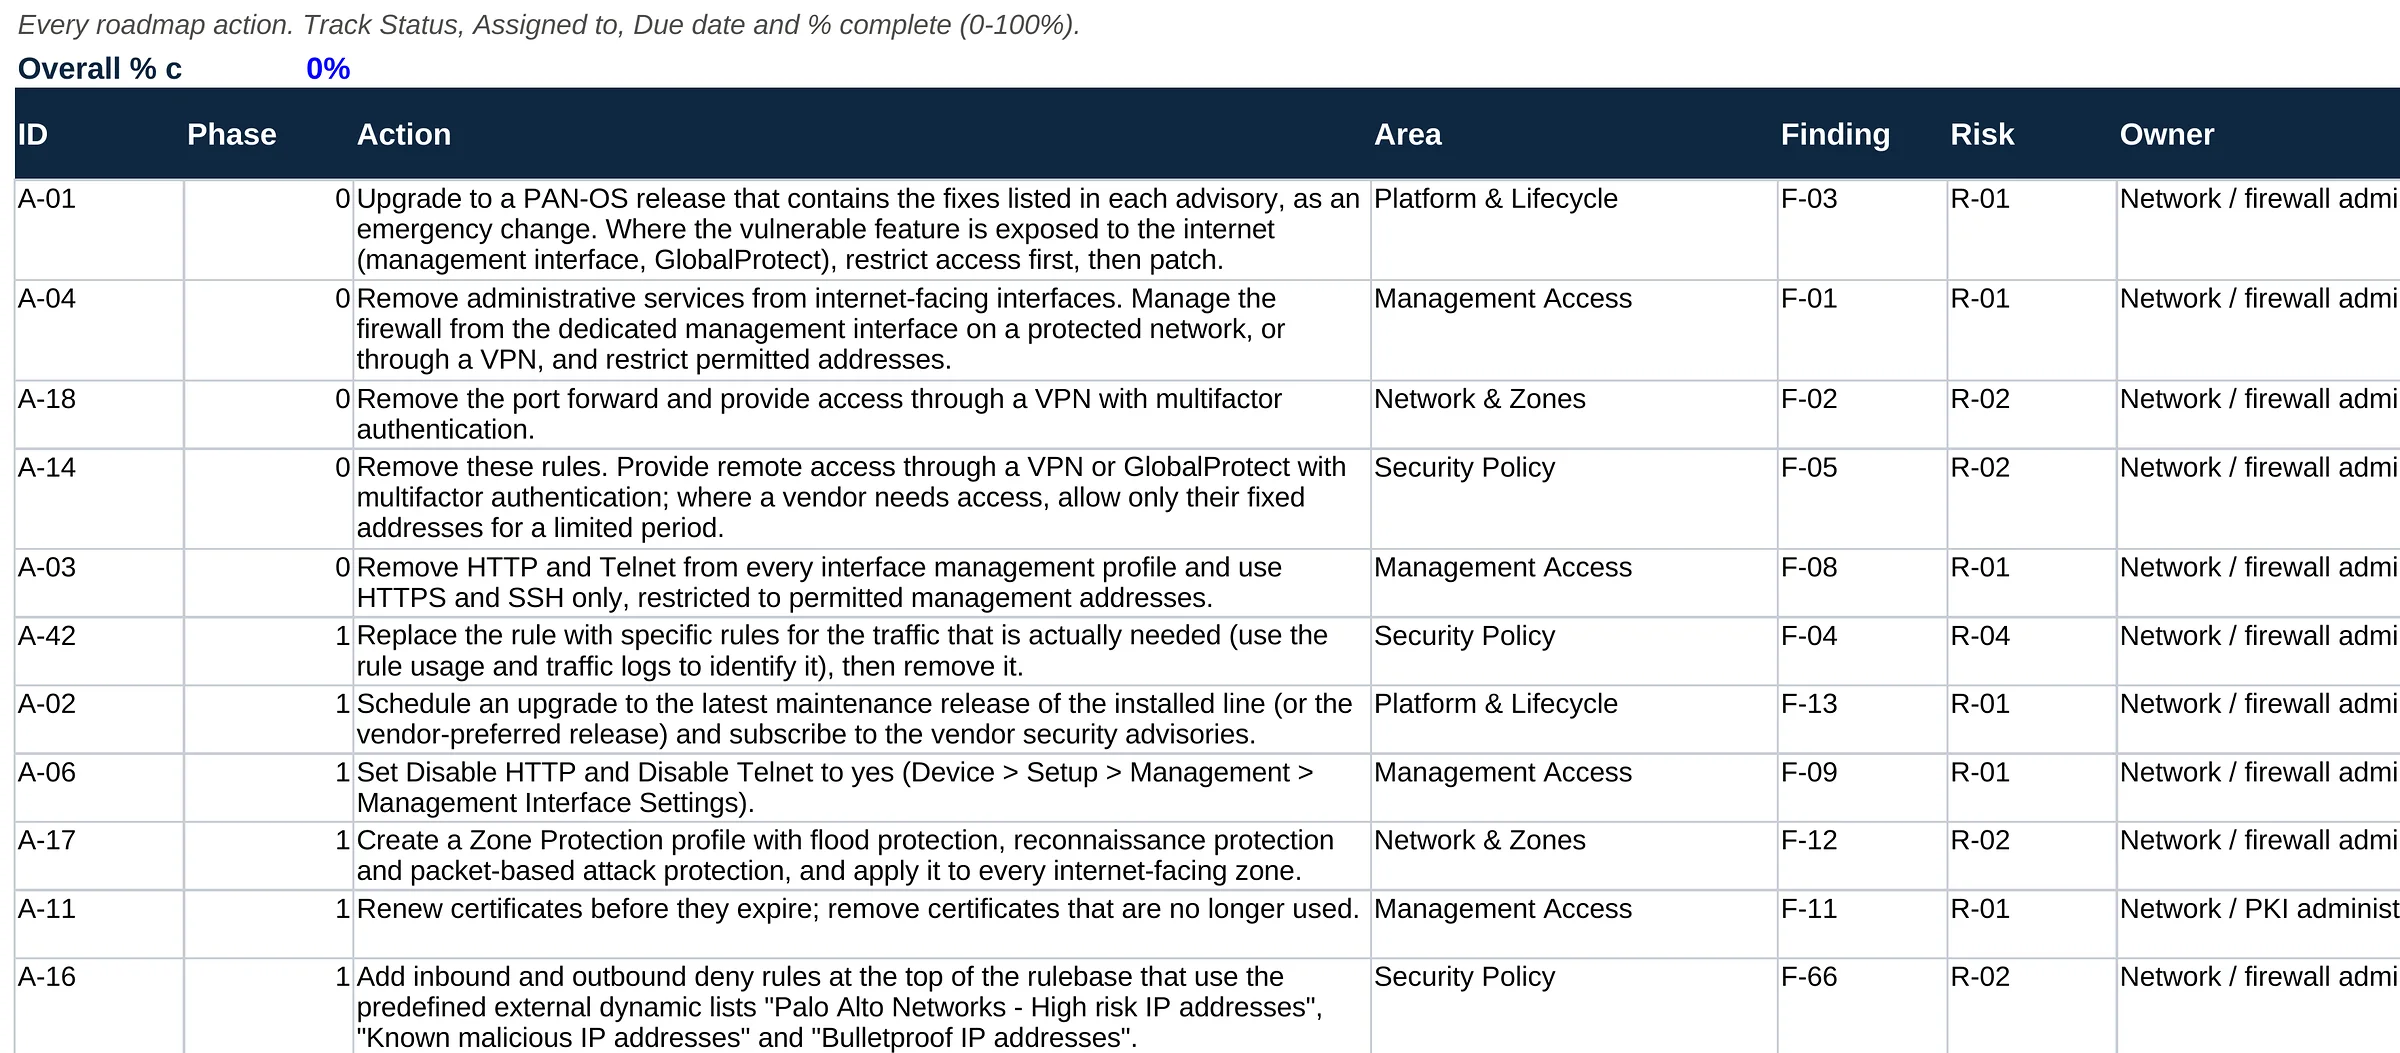
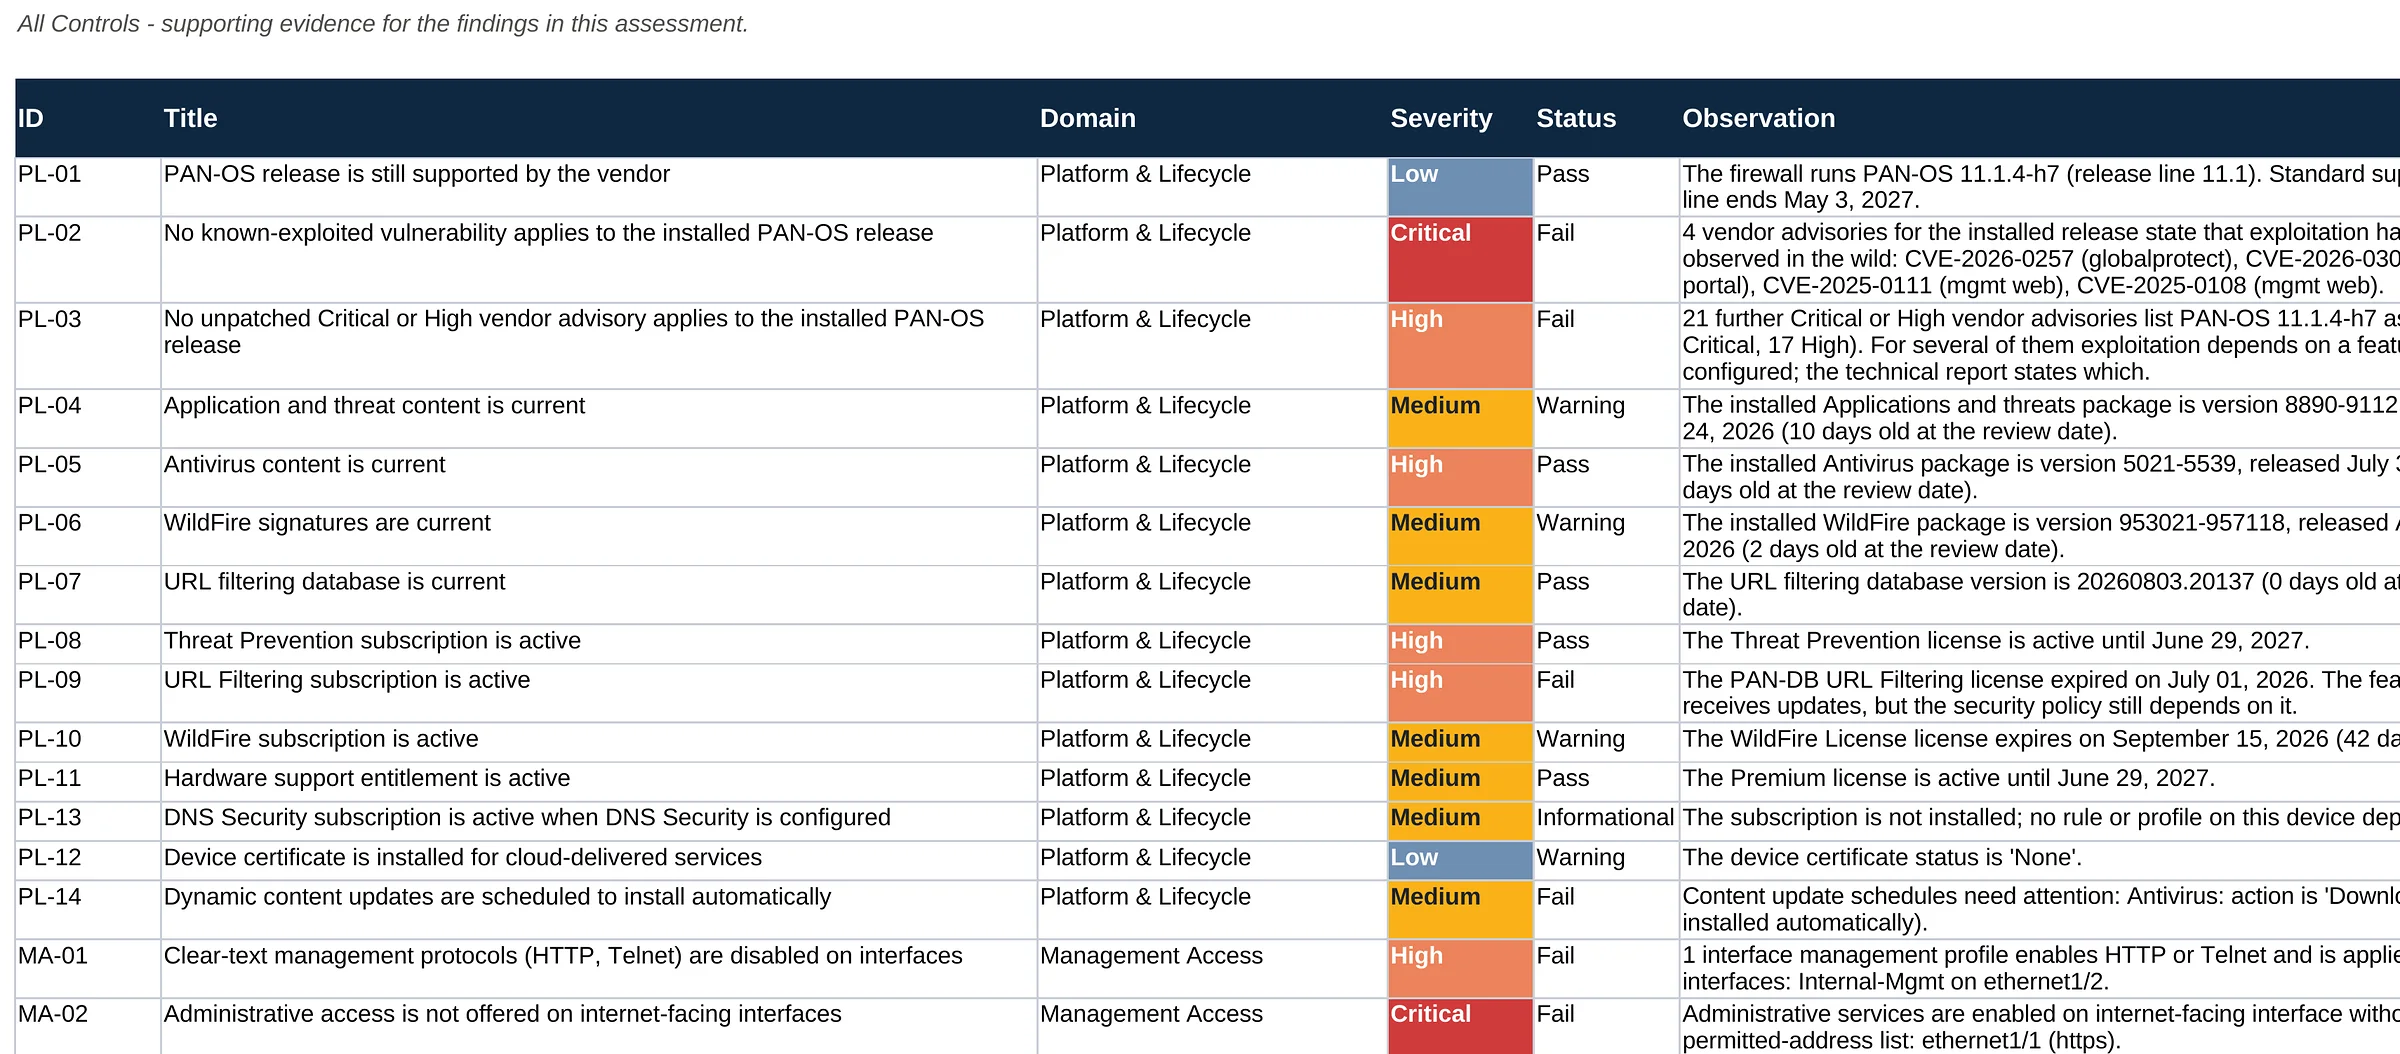
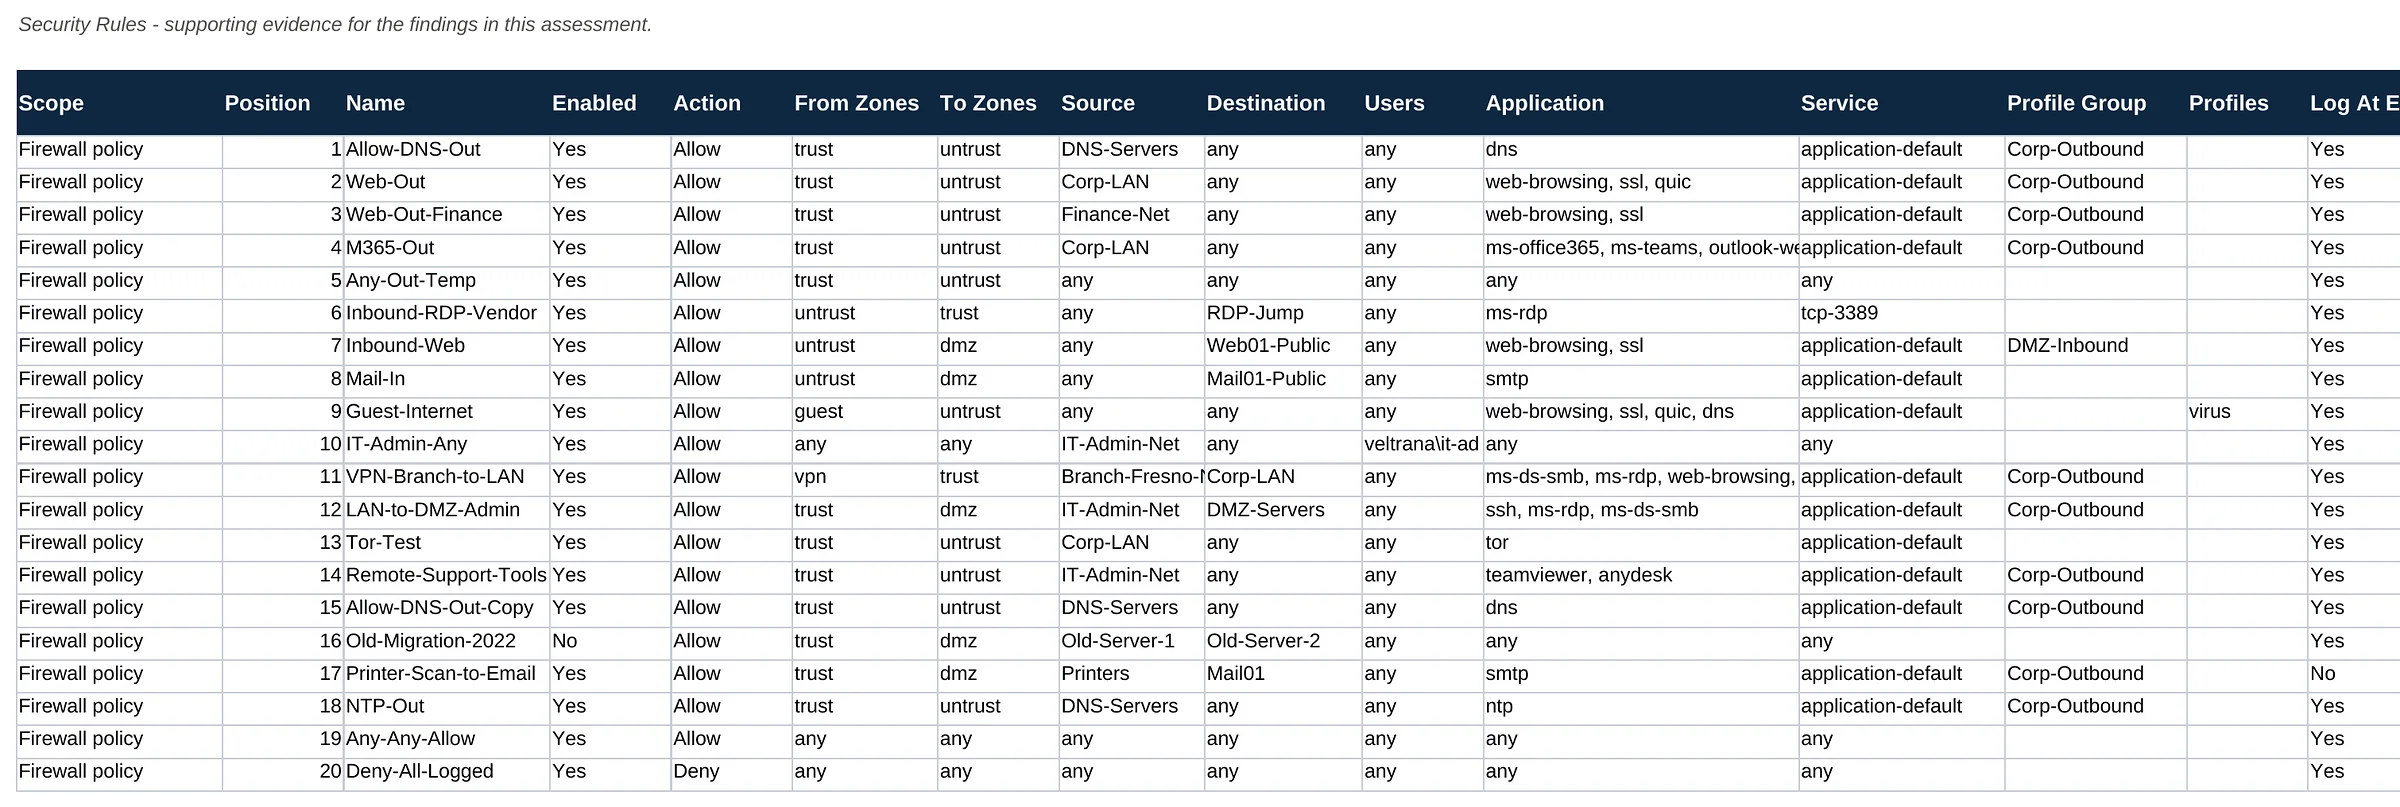
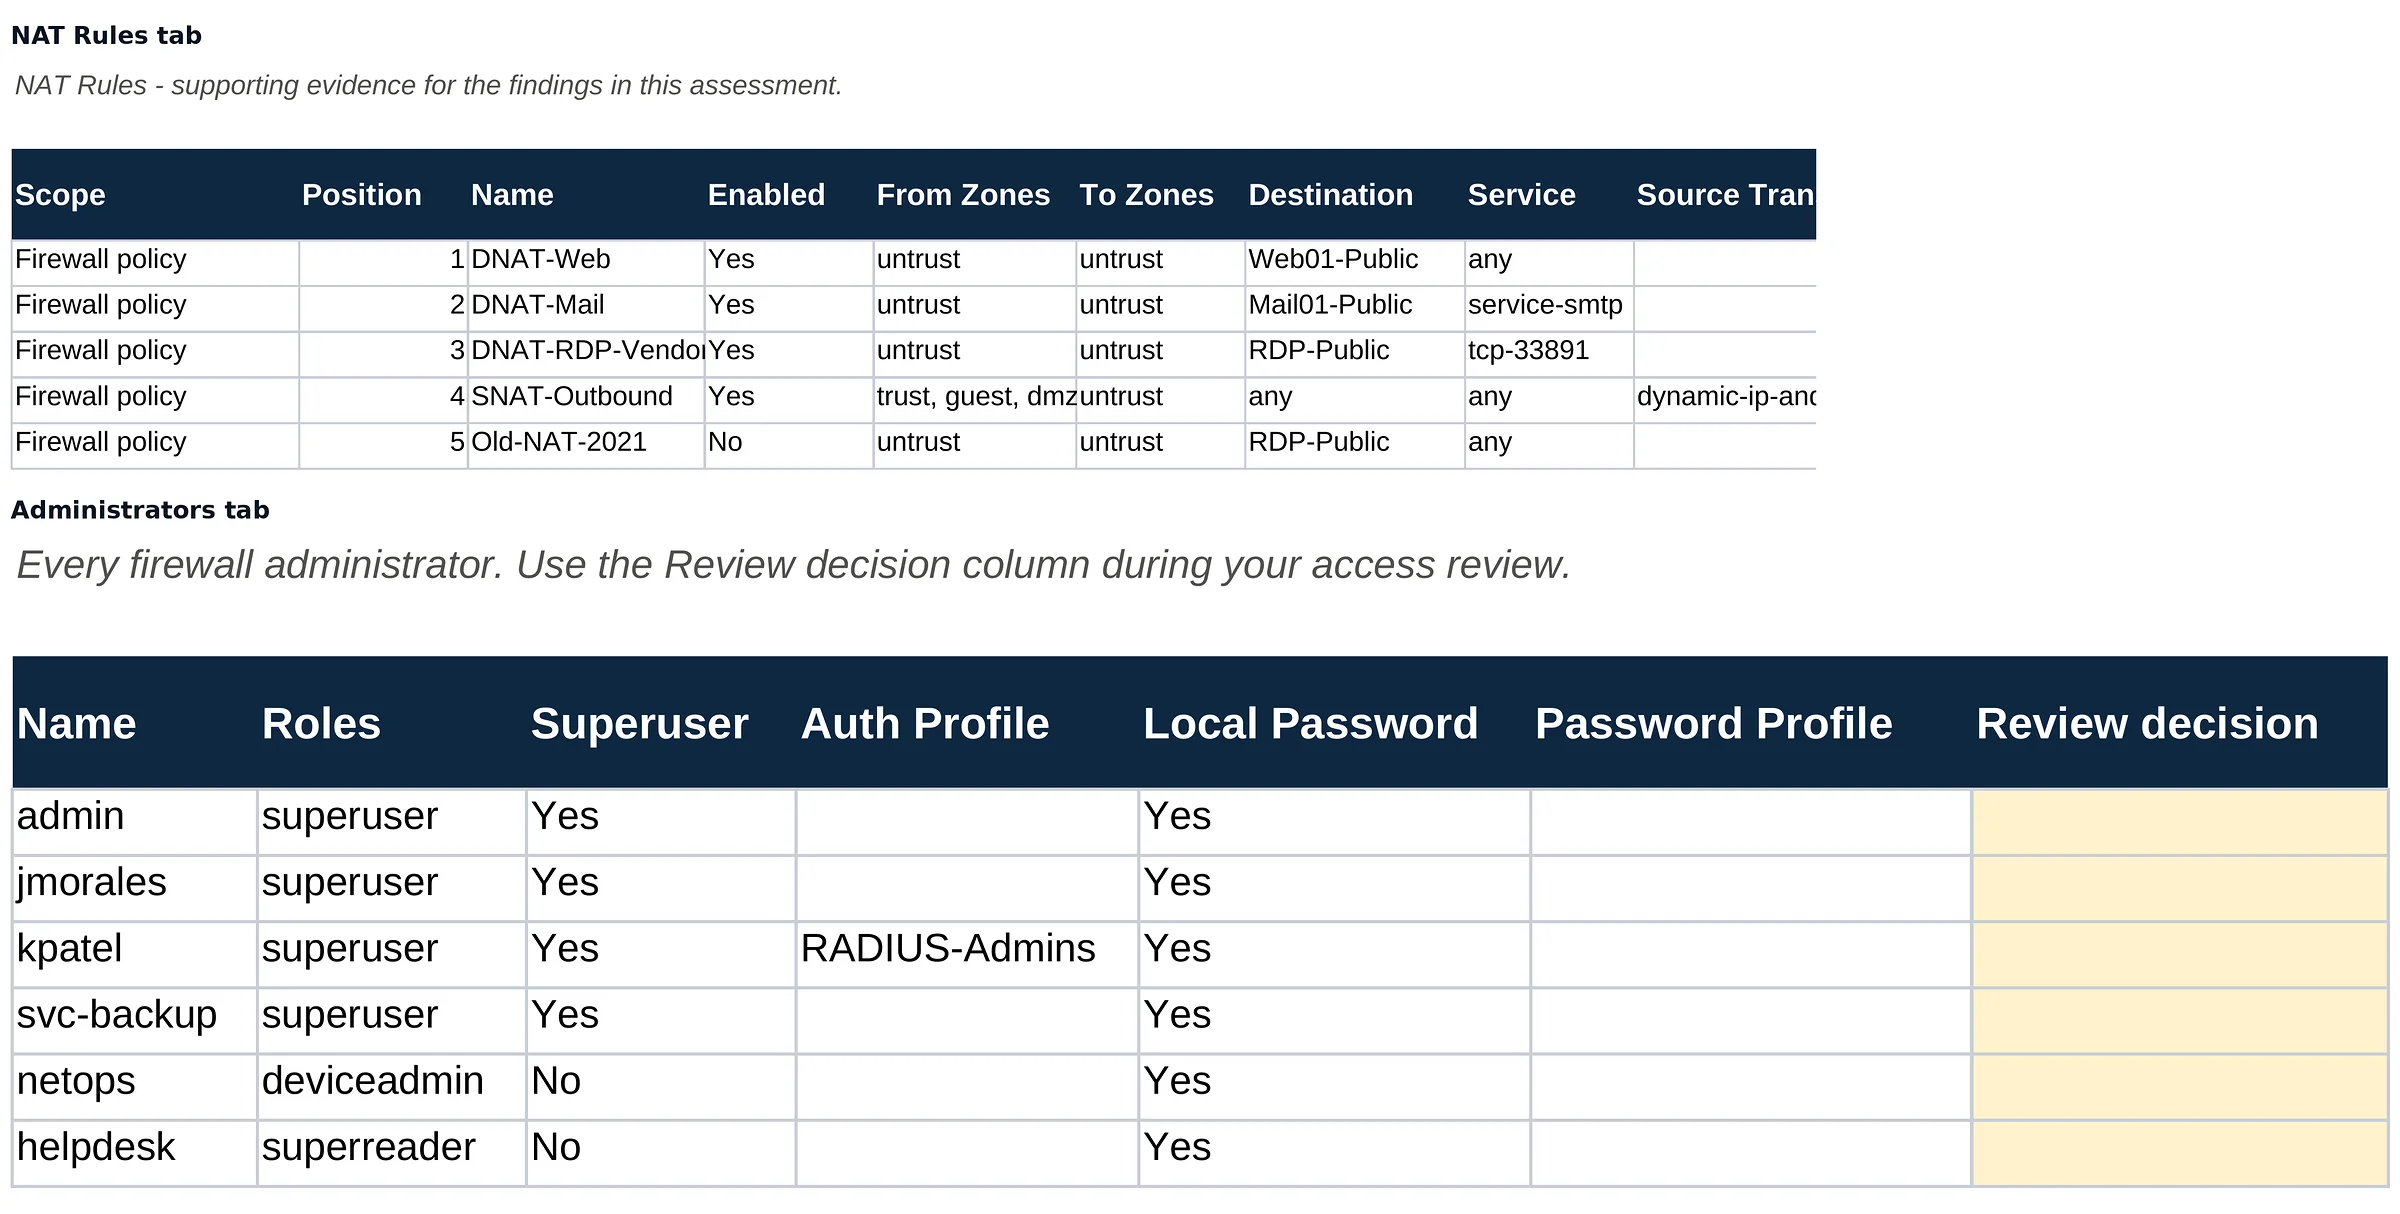
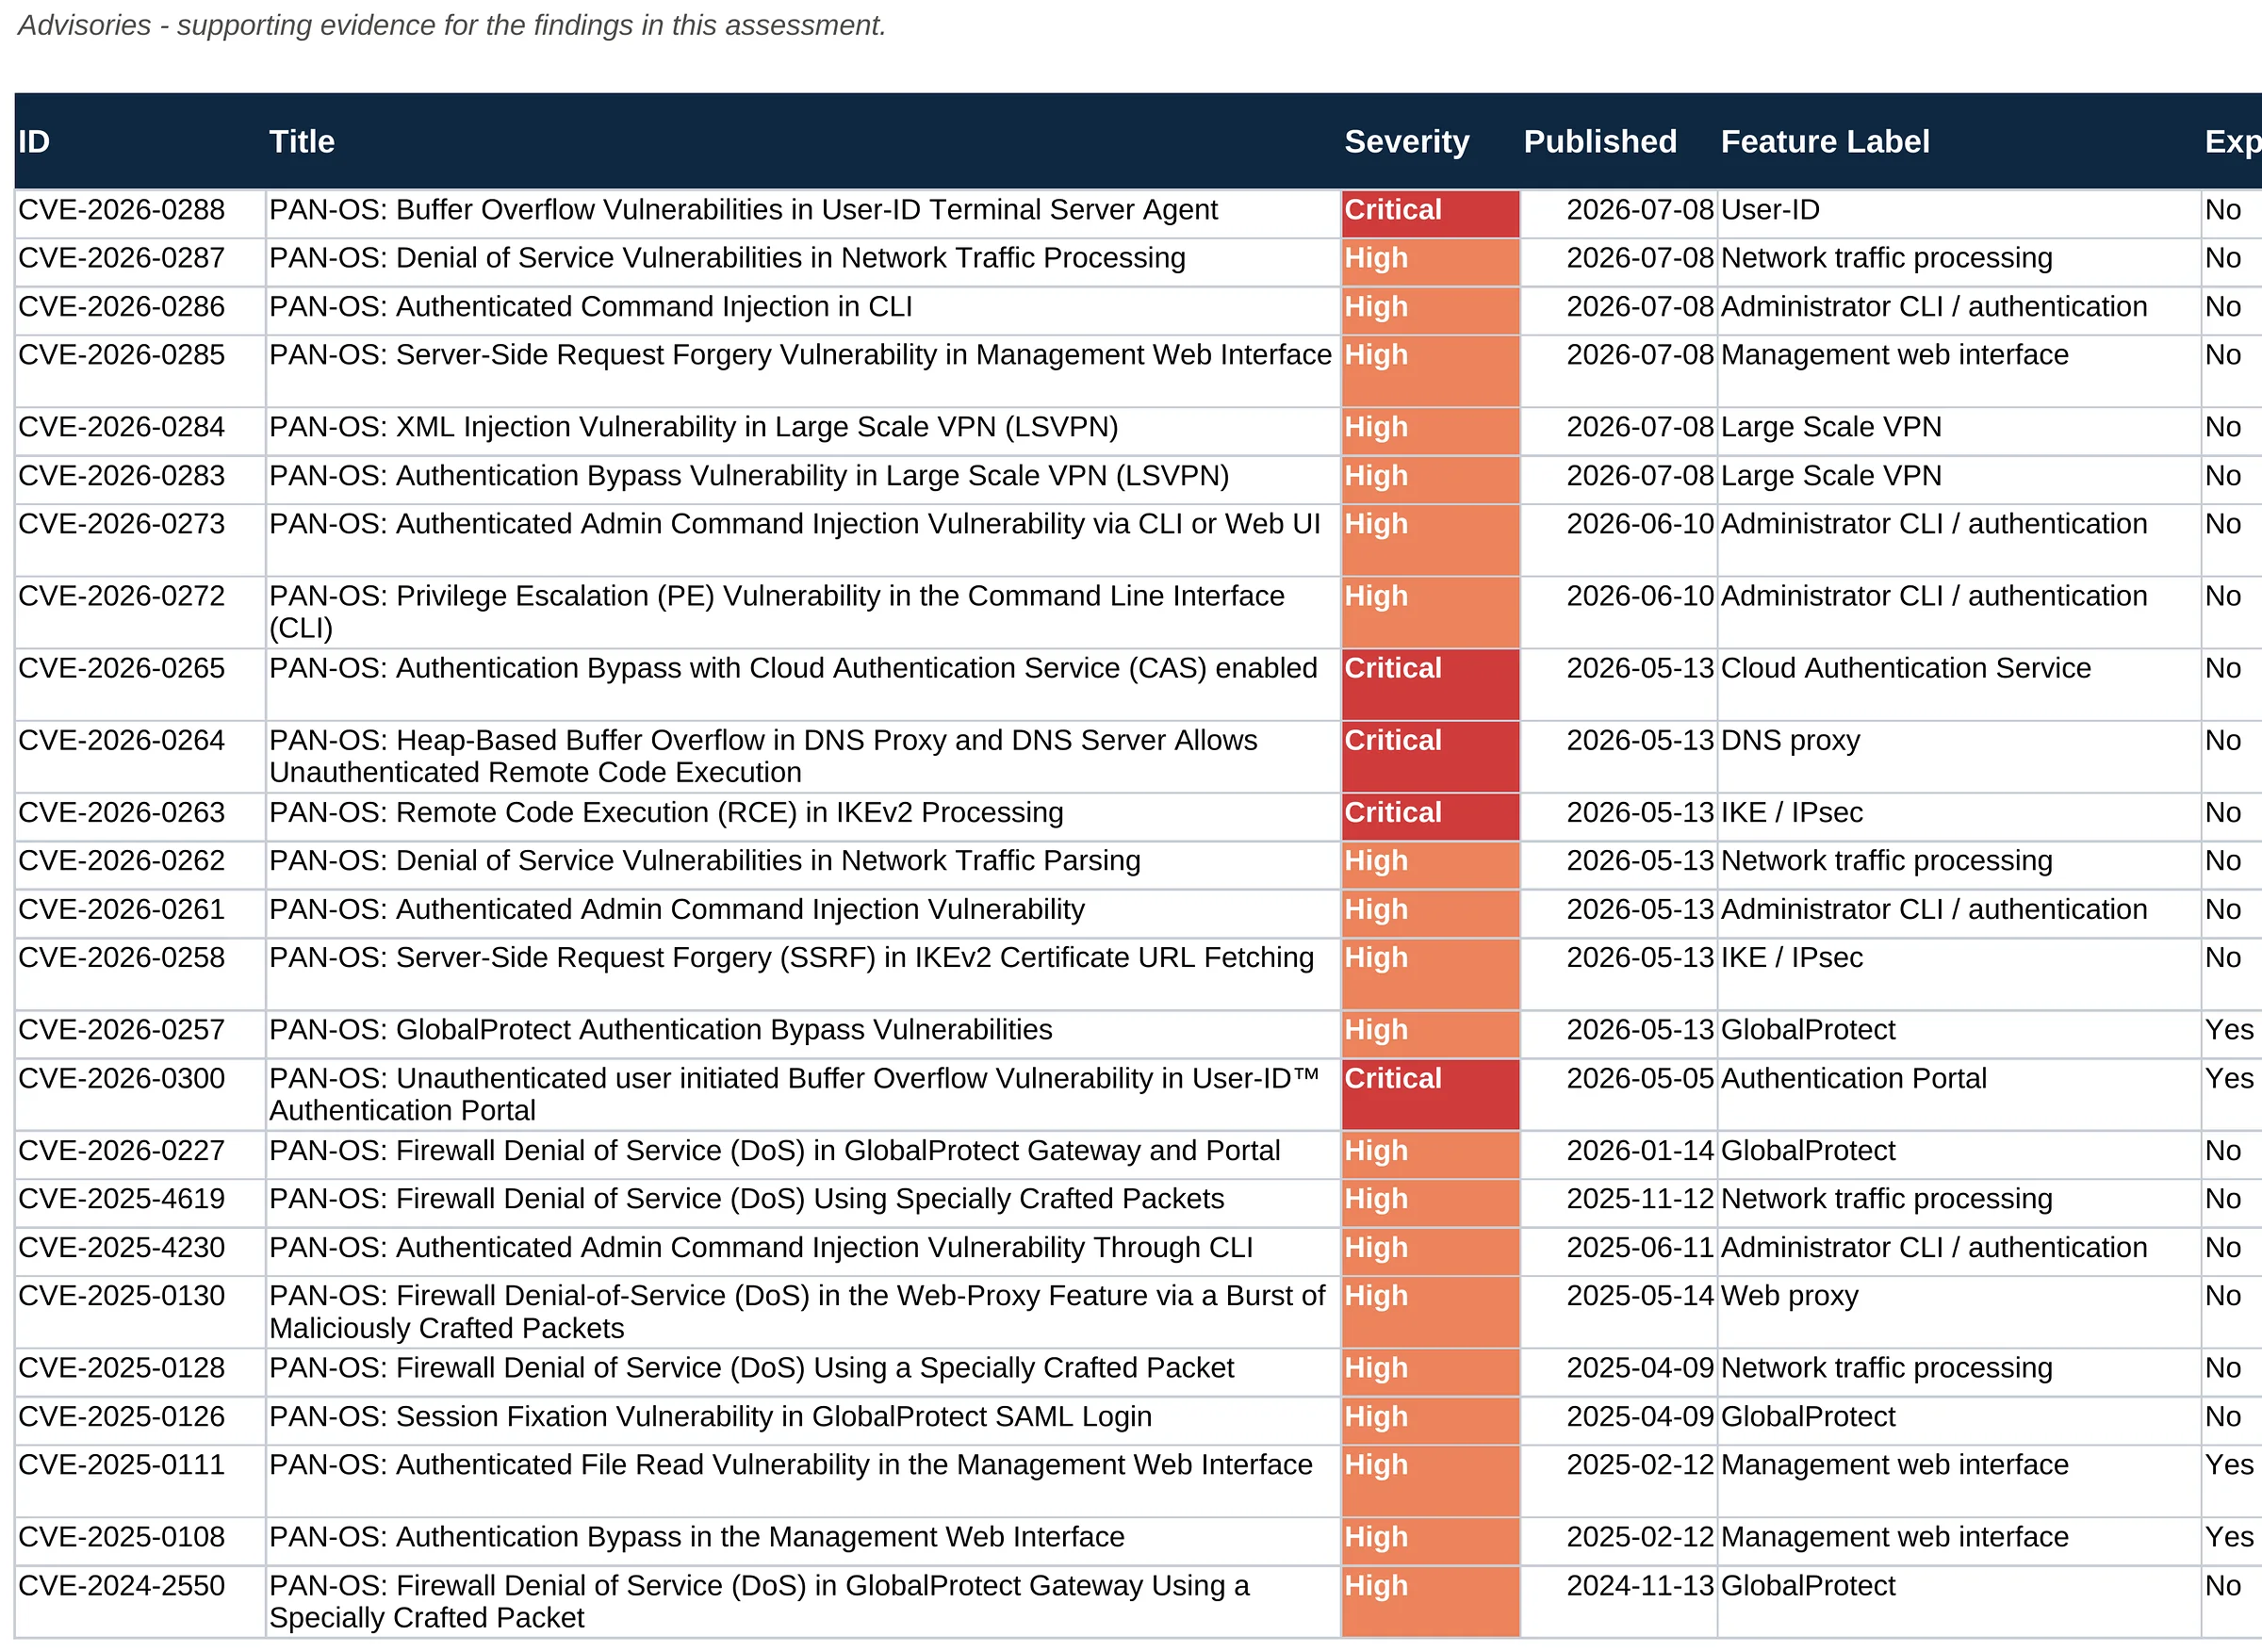
The working file your team tracks the fixes in. It holds every finding, risk and roadmap action with columns for owner, status, due date and evidence, plus the configuration evidence read from the firewall, one tab per topic.
Who uses it
Firewall administrators, MSP, project manager
What is included
- Summary with formulas that update as findings close
- Findings tracker with status, owner, due date and evidence
- Risk register with likelihood and impact inputs
- Remediation plan and projects
- All controls, pass or fail
- Evidence tabs: rules, NAT, interfaces, zones, administrators, certificates, licenses, advisories, VPN, GlobalProtect, threats
- Domain scores and strengths
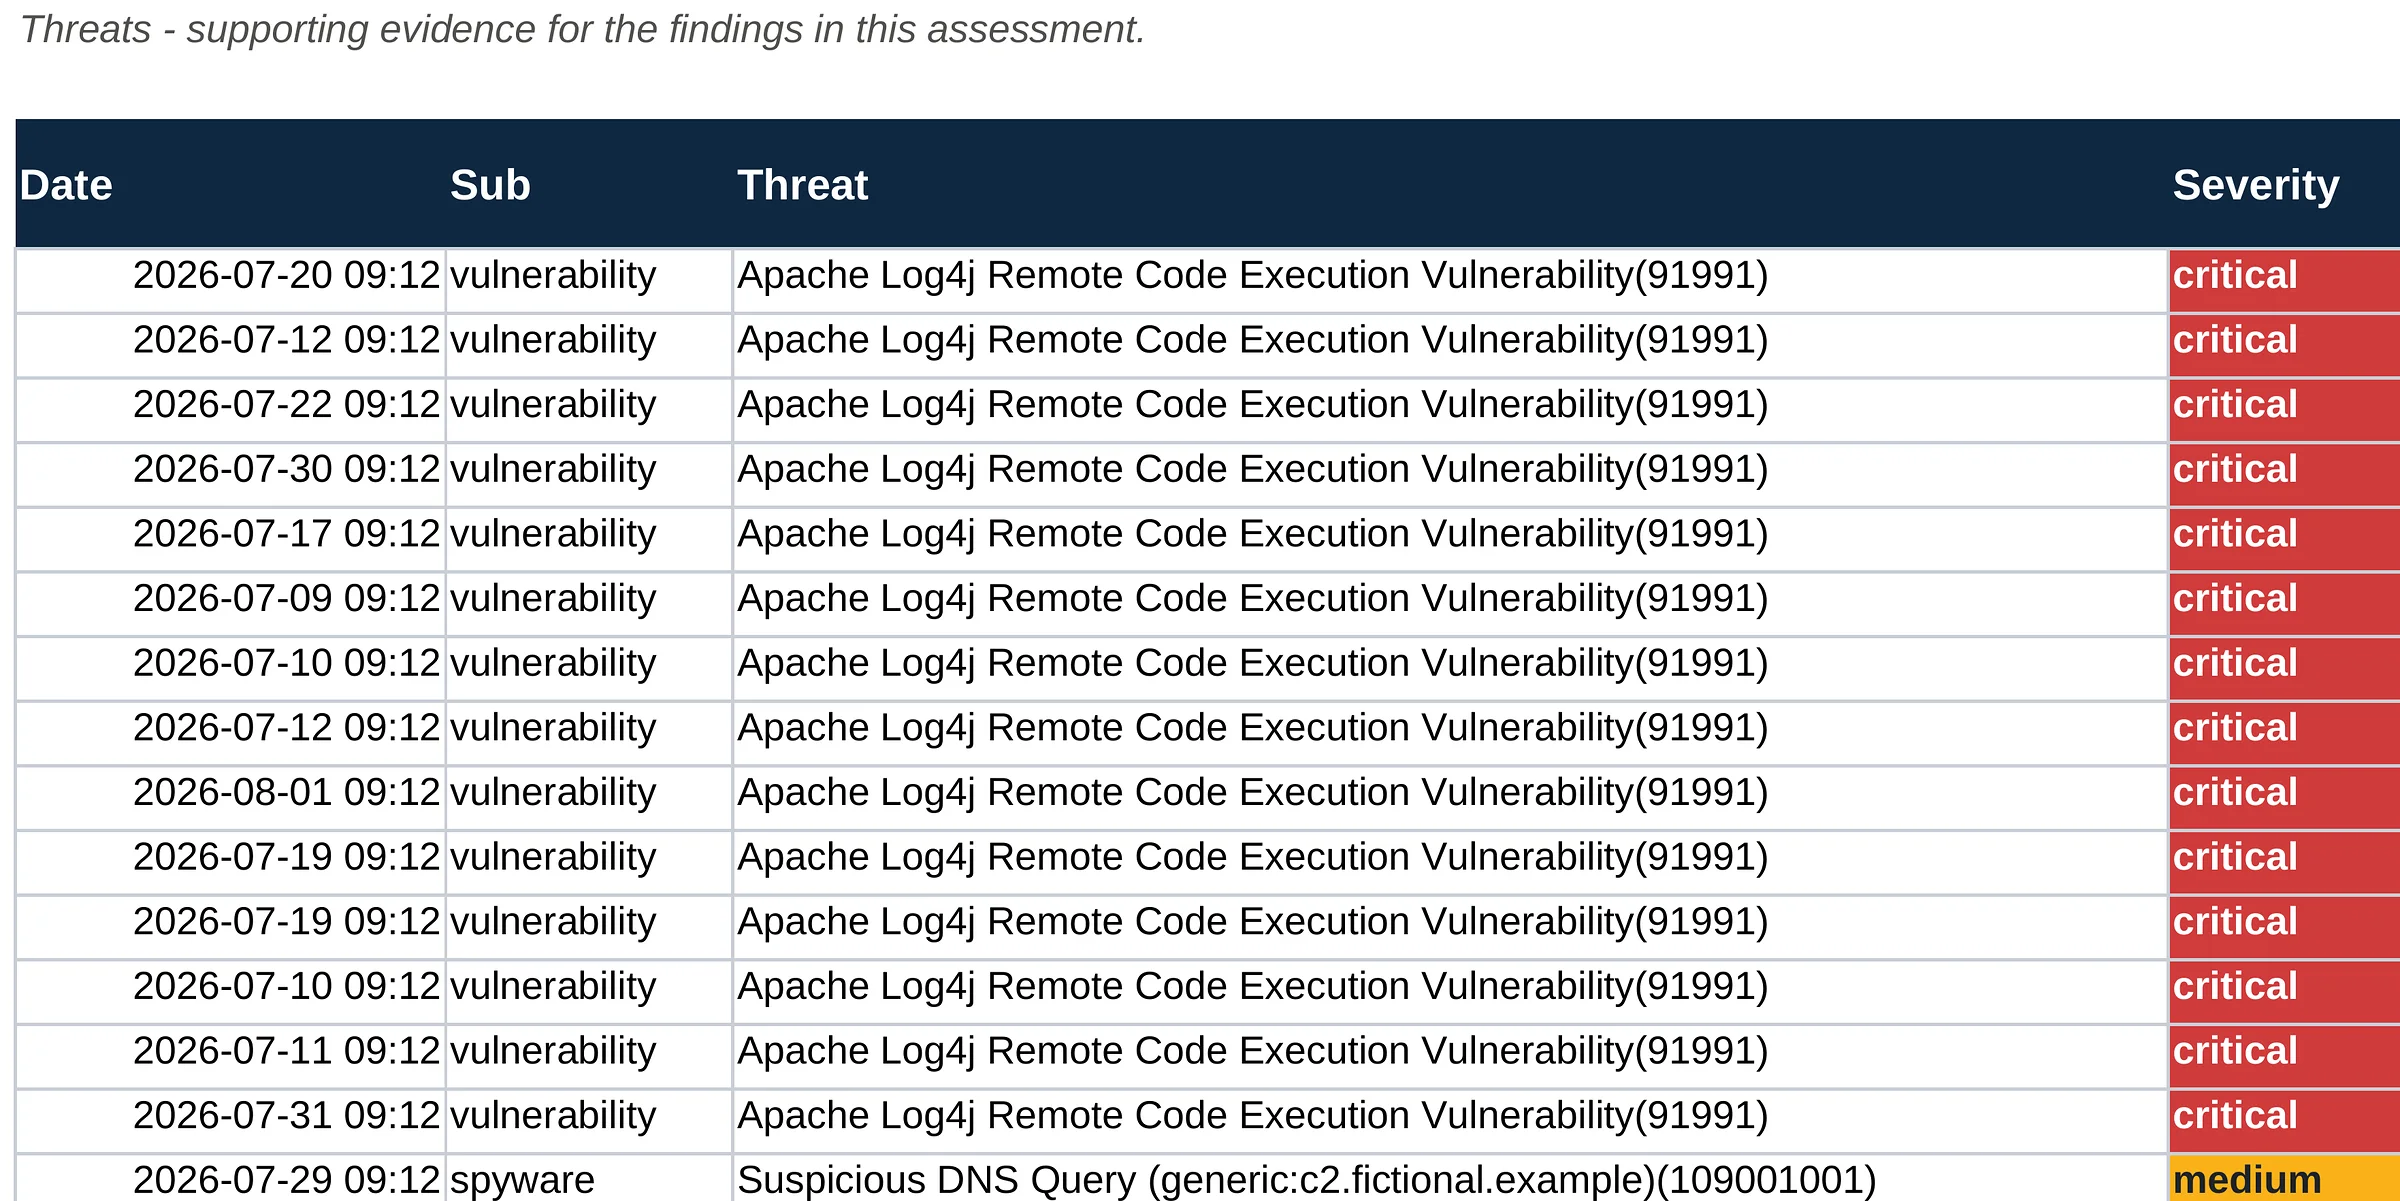
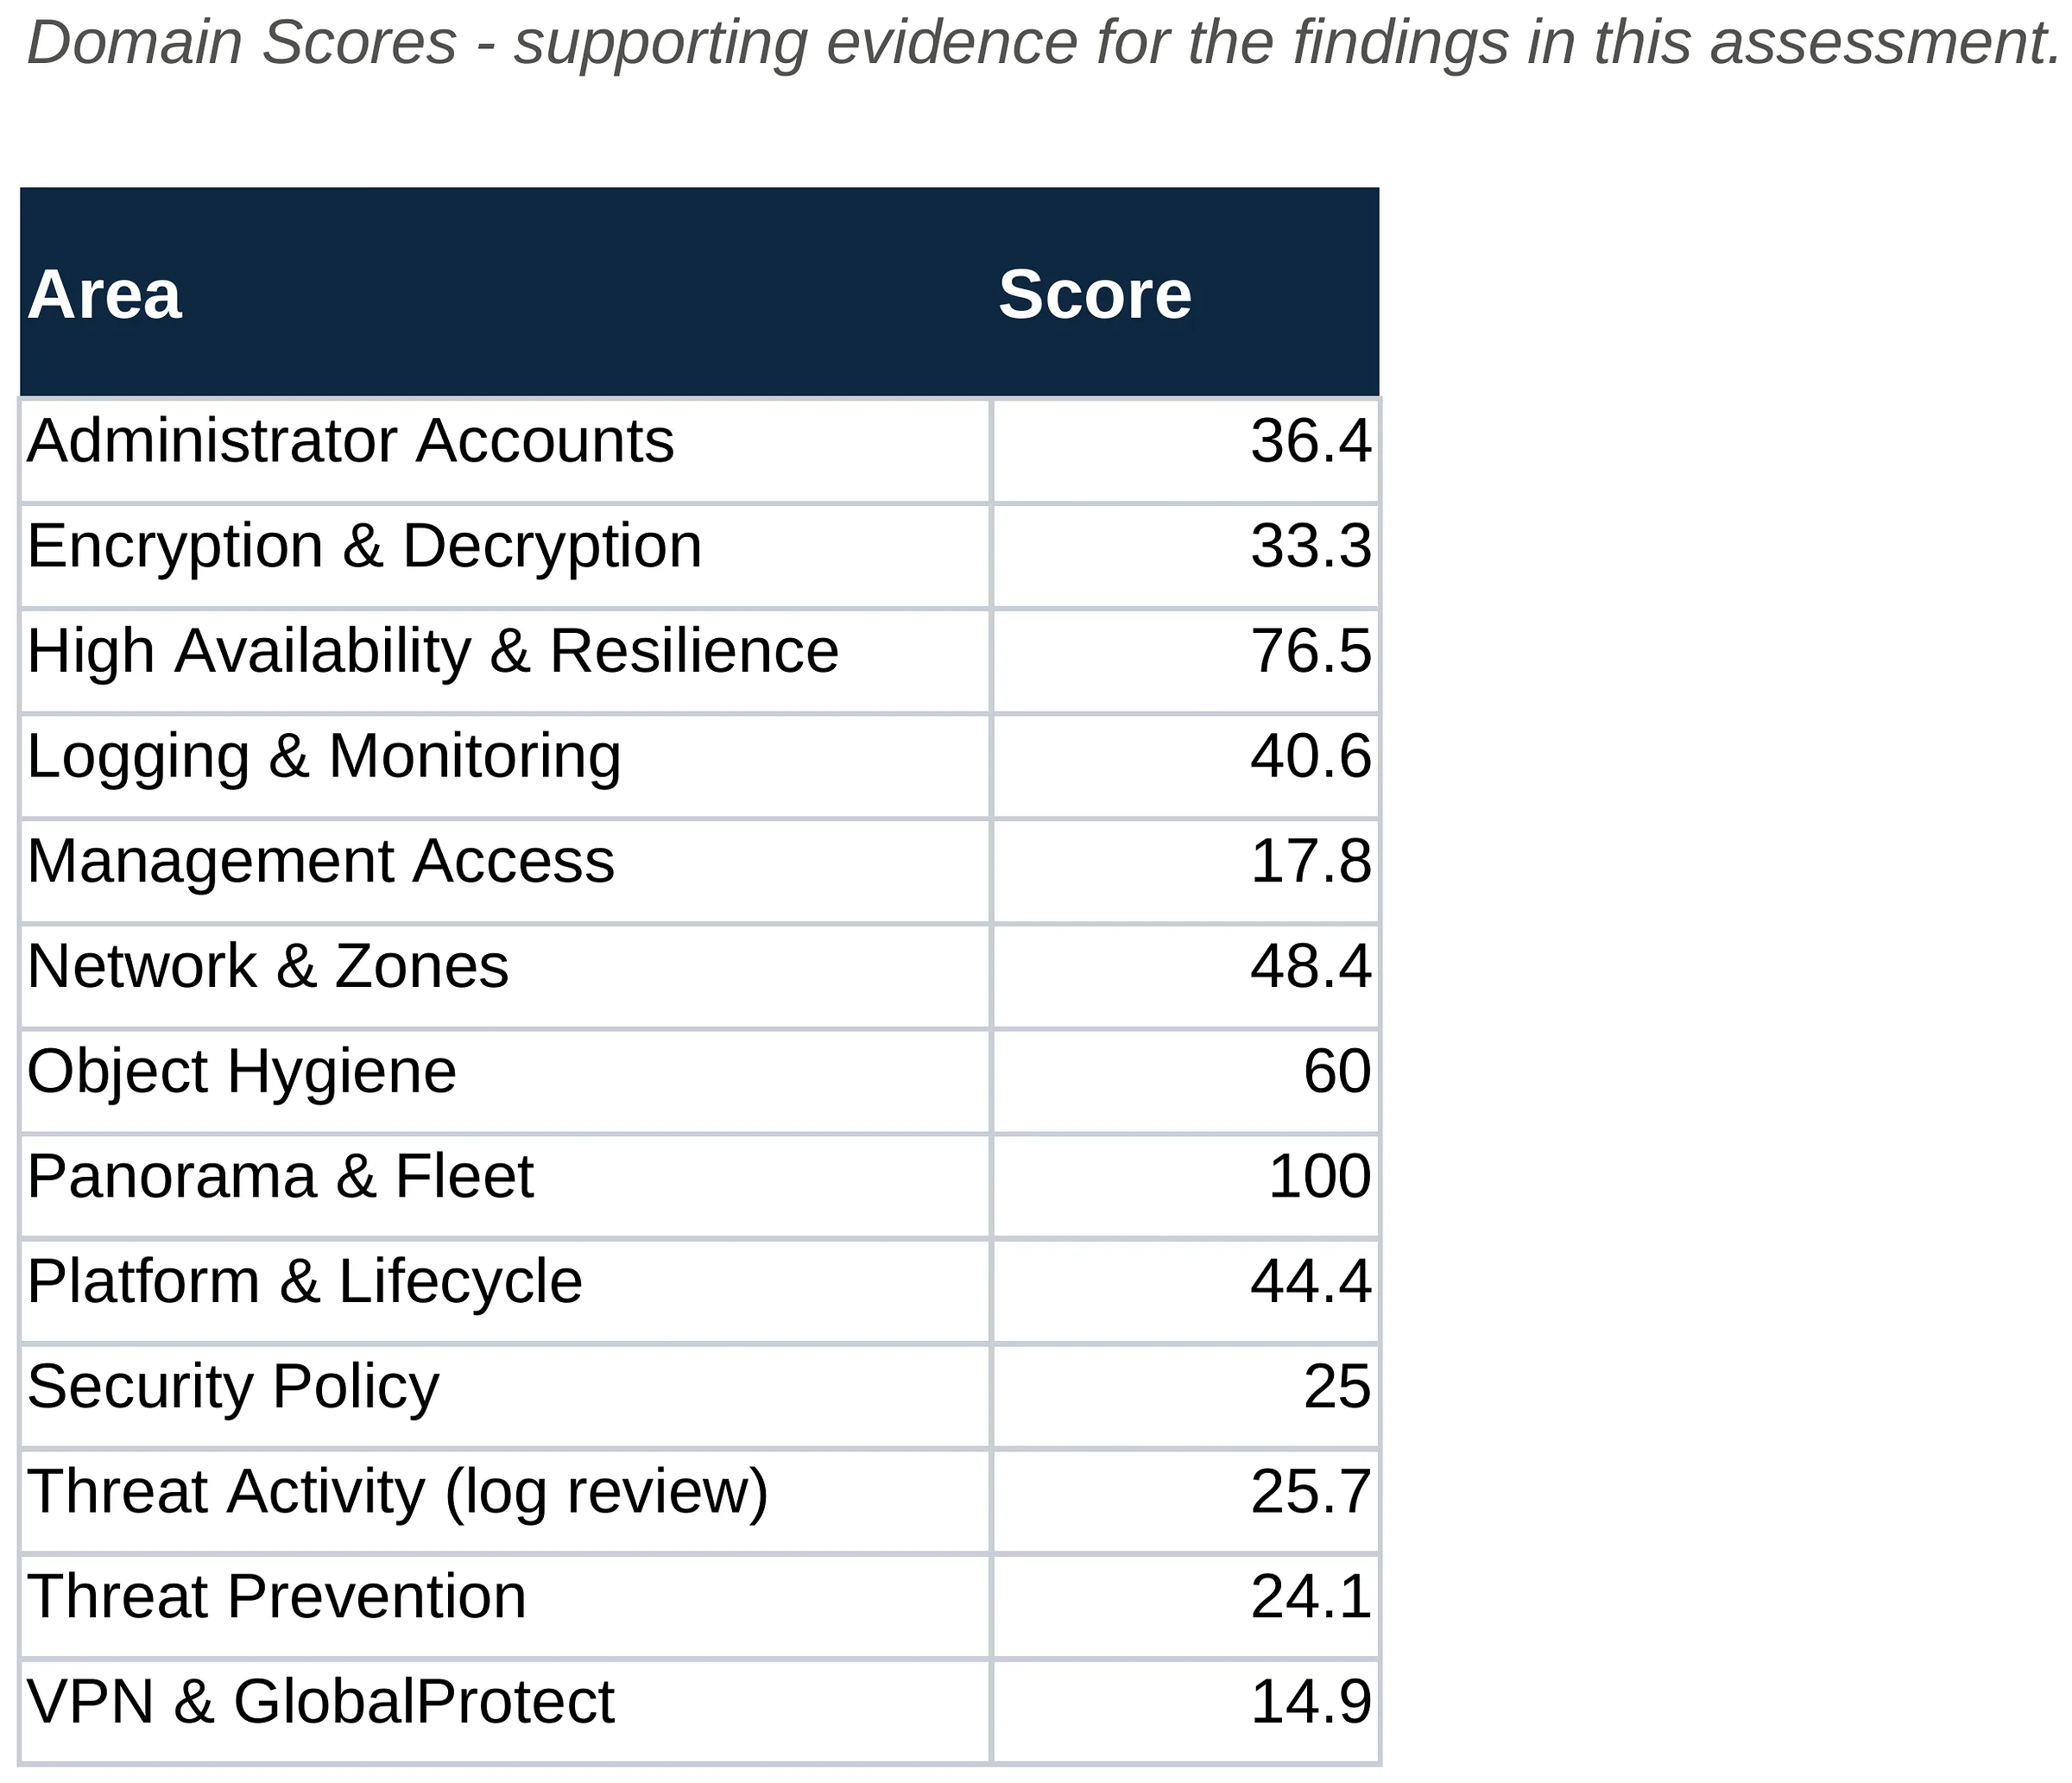
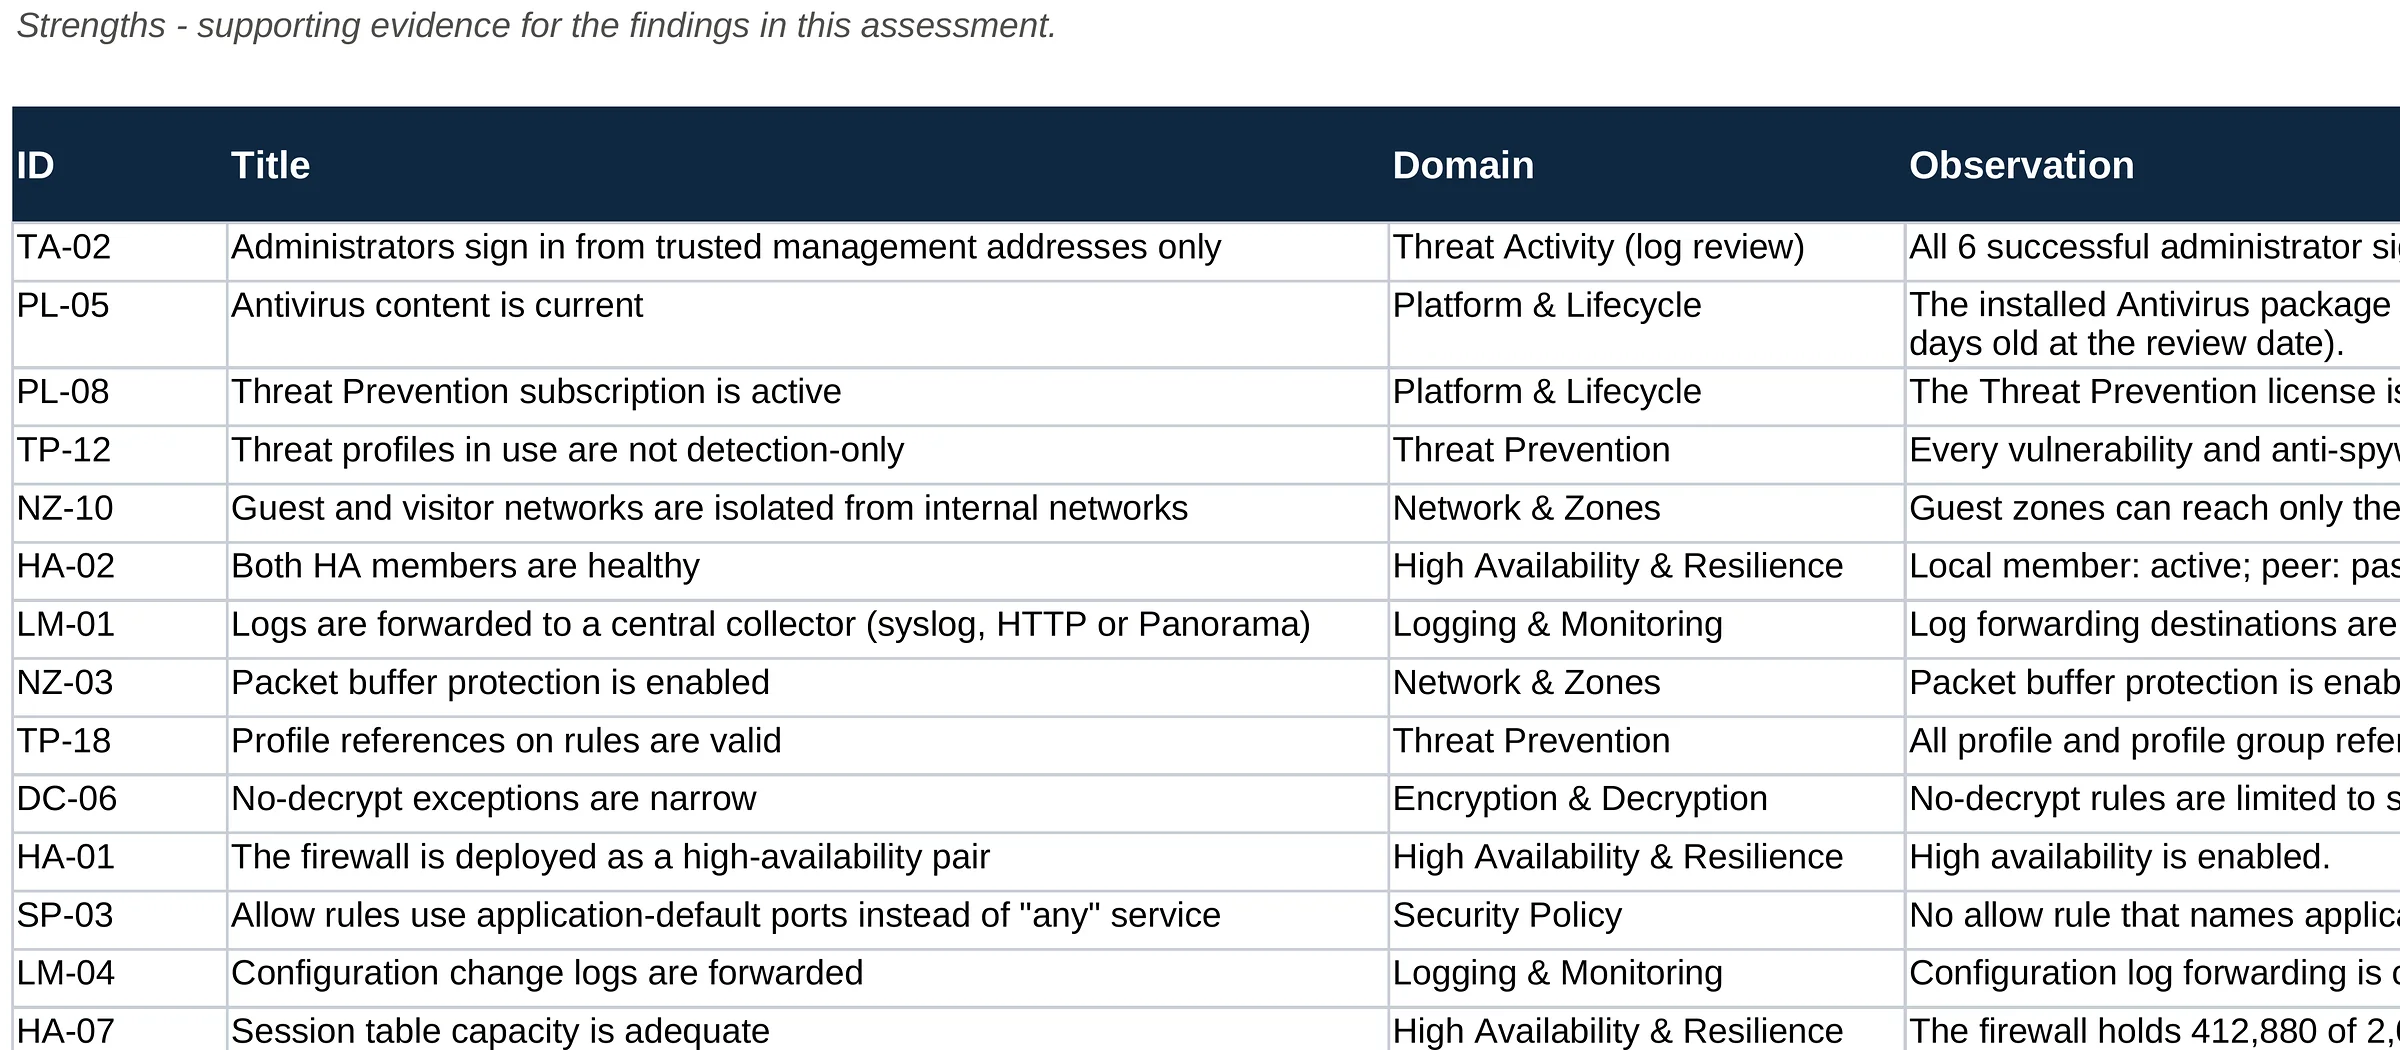
Click the centre page to open it full size. Use the arrows, the thumbnails or your arrow keys to move between pages.
Want these reports for your own firewalls?
We run the same read-only review on your Palo Alto firewalls and Panorama: 141 controls in 13 areas, the 7-day log review, and all seven deliverables, for one fixed price.
Page 10 of 13: Sample report
- 1. Palo Alto Firewall Security Audit (hub)
- 2. PAN-OS management interface security
- 3. PAN-OS end of life & vulnerabilities
- 4. Security policy & NAT rule review
- 5. Security profiles & threat prevention
- 6. SSL/TLS decryption review
- 7. GlobalProtect & IPsec VPN security
- 8. Zone protection & exposed services
- 9. Logging, HA, backup & Panorama
- 10. Sample report (this page)
- 11. Palo Alto firewall security checklist
- 12. Pricing
- 13. How to audit a Palo Alto firewall
Palo Alto Networks, PAN-OS, Panorama, GlobalProtect, Prisma, Strata, WildFire, App-ID and User-ID are trademarks or registered trademarks of Palo Alto Networks, Inc. OC Security Audit is an independent assessment firm and is not affiliated with, sponsored by or endorsed by Palo Alto Networks. All sample companies, firewalls and findings shown on this page are fictional and used for illustration only. The assessment is read-only: no configuration changes, commits or active tests are performed.
Know what your firewall really allows, before an attacker tests it
Schedule a consultation. We scope the Palo Alto firewall audit in 30 minutes and quote one fixed price.
Read-only audit. No changes to your firewalls. Irvine, Orange County and Southern California on-site; remote nationwide.