
CCPA Readiness Assessment: 63 Controls, Five Reports, One Plan
A structured review of your privacy program and public website against the CCPA and CalPrivacy’s regulations, with risk-rated findings, a risk register and a prioritized roadmap. Technical and operational work; legal interpretation stays with your counsel.
We read your website the way a visitor does
A few page requests to your home page and privacy policy, each one logged. No sign-in, no forms submitted, no scripts run on your site.
A practical review of how your business handles California privacy
The assessment combines a structured questionnaire, answered with your privacy, legal, marketing, HR and IT leads, with a read-only review of your public website. Each of the 63 controls is tied to the CCPA (Civil Code) or CalPrivacy’s regulations (11 CCR) and mapped to NIST CSF 2.0 and ISO/IEC 27001:2022.
It answers operational questions: do the notices and links exist, do privacy requests run on time, does the website respond to opt-out signals, are vendor contracts in place, and are the 2026 risk assessment and audit duties planned. It does not decide whether the law applies to you or how to interpret it; your counsel does.
63 controls in 11 areas
| Area | Controls | What we look at |
|---|---|---|
| Governance and accountability | 6 | Documented applicability decision, a named owner, written policies, trained staff, workforce data in scope |
| Notices and privacy policy | 6 | Notice at collection, every required policy disclosure, a policy updated in the last 12 months, the opt-out notice |
| Consumer request handling | 11 | Request methods, 10-day confirmation, 45-day responses, verification, know, delete, correct, agents, records |
| Opt-out of sale or sharing | 6 | A working opt-out, Global Privacy Control, passing choices to third parties, 15-business-day processing, no dark patterns |
| Sensitive personal information and minors | 3 | The right to limit, extra safeguards, opt-in for consumers under 16 |
| Service providers, contractors and third parties | 4 | Vendor inventory, required contract terms, third-party disclosures, due diligence |
| Data inventory, minimization and retention | 4 | Data map, purpose limits, retention periods, de-identified data |
| Reasonable security and incident response | 6 | Security procedures, breach notification plan, access reviews, encryption, testing, logging |
| Risk assessments, cybersecurity audits and ADMT | 4 | Risk assessment triggers and submissions, audit planning, automated decision-making readiness |
| Data broker obligations | 3 | Registration, DROP deletion processing, broker metrics and audit planning |
| Website | 10 | HTTPS, privacy policy link and date, opt-out and limit links, required disclosures, GPC statement, request methods, trackers, consent tool |
Controls that do not apply to your business, for example data broker duties, are marked not applicable with the reason recorded. Controls we cannot confirm are reported for manual review, never as a pass.
Five steps, read-only
Scoping call
We record the facts that decide which controls apply: revenue band, selling or sharing, sensitive data, automated decisions, data broker status. Your counsel confirms applicability.
Questionnaire
Your owners answer each control Yes, Partial, No or Not applicable. Unanswered items become manual review, not assumptions.
Website review
We read your home page and privacy policy, normally with three page requests, and check links, disclosures, the policy date and advertising tags.
Scoring and risk register
Findings are weighted by severity, grouped into business risks and rated by likelihood and impact, with owners and target dates.
Reports and walkthrough
Five reports, walked through with your owner, counsel and IT lead. A follow-up assessment measures progress on the same controls.
What we check on your public website, and what needs a browser
Checked from the page itself
- The site is served over HTTPS
- A privacy policy link on the home page that resolves
- A “Do Not Sell or Share My Personal Information” or “Your Privacy Choices” link
- A “Limit the Use of My Sensitive Personal Information” link where it may be needed
- A privacy policy date within the last 12 months
- 16 California disclosure elements in the policy
- A statement on how Global Privacy Control signals are handled
- Published request methods, including a toll-free number where required
- Advertising and analytics tags present on the home page
- A cookie consent or preference tool
Confirmed in a browser
A page read cannot see tags that load after consent, banners built by scripts, or whether the site actually stops sharing when a Global Privacy Control signal arrives. We confirm those with a browser test, the same steps described in our guide.
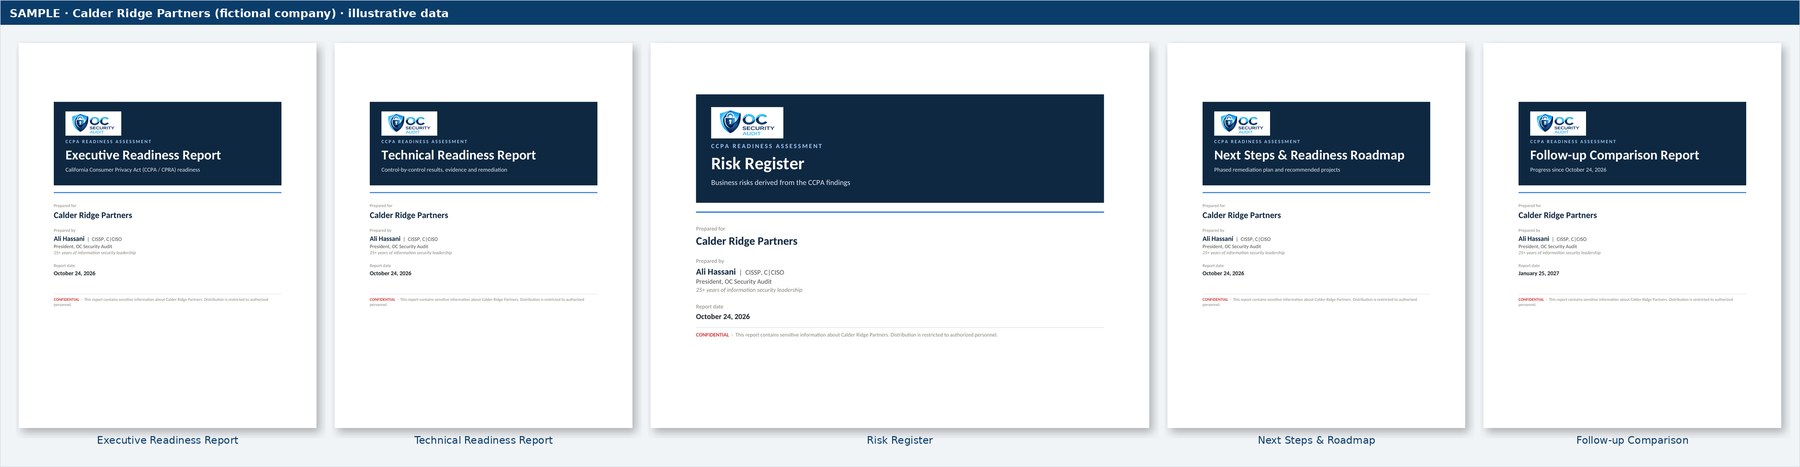
Five reports from one assessment
| Deliverable | What it contains | Who uses it |
|---|---|---|
| Executive Readiness Report | Readiness score, top business risks, readiness by area, priority actions and decisions for leadership (about 10 pages) | Owner, leadership |
| Technical Readiness Report | Control-by-control results with requirement, observation, evidence reviewed, recommendation and framework mapping (about 40 pages) | Privacy lead, IT, counsel |
| Risk Register | Business risks with likelihood, impact, linked findings, treatment, owners, dates and heat maps before and after treatment | Owner, privacy lead |
| Next Steps and Readiness Roadmap | Actions in phases (0 to 7, 7 to 30, 30 to 90 and 90 to 180 days) and grouped projects | Project owner, IT |
| Technical Findings Workbook | Every finding in Excel, with filters and status columns for tracking | IT, privacy lead |
| Follow-up Comparison Report | At the follow-up assessment: findings closed, improved, unchanged or new, and the change in each area | Owner, leadership |
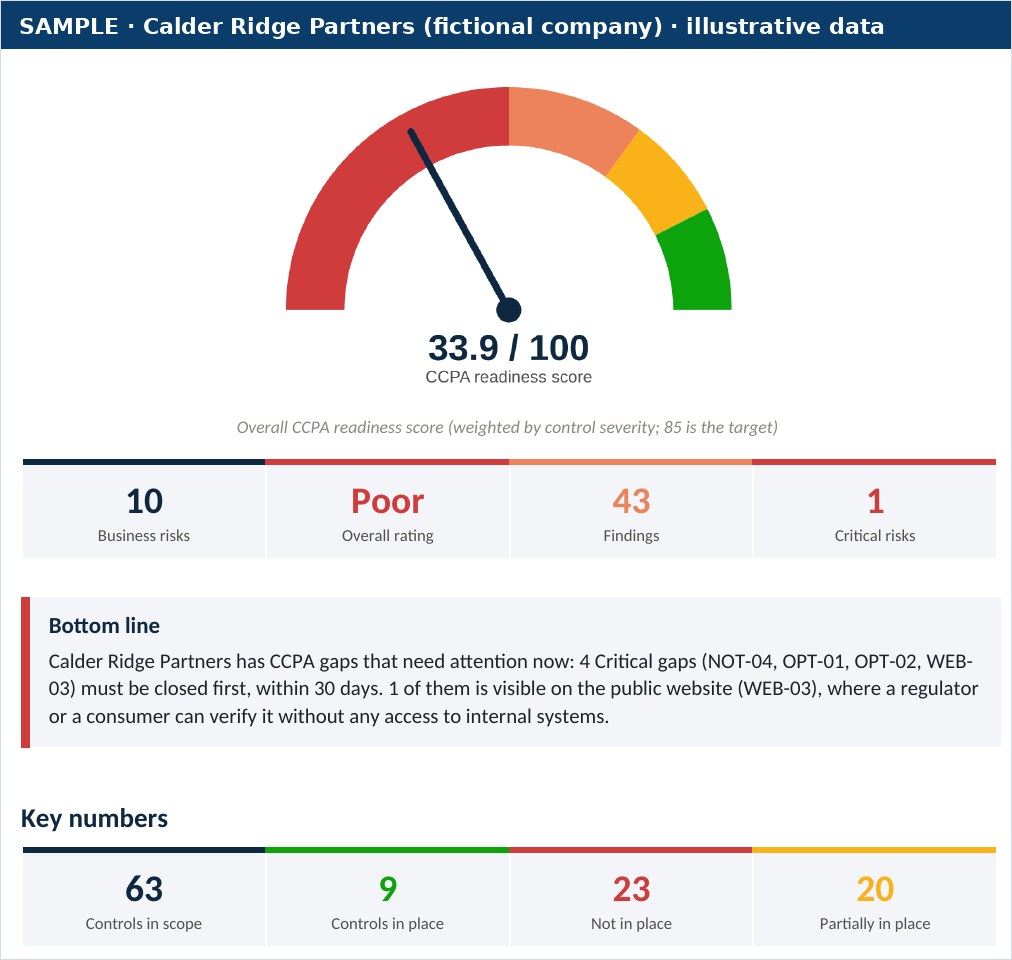
How the readiness score works
Each control carries a severity: Critical, High, Medium or Low. The score is the weighted share of controls in place, with partial controls counting half. Not applicable and manual-review items are left out, so a missing answer never raises or lowers the score.
The score is a readiness measure for planning and tracking progress. It is not a legal determination, a certification or a prediction of how a regulator would view your program.
What this assessment is not
Not legal advice
We assess operations and technology. Applicability, contract language and legal interpretation stay with your privacy counsel.
Not the cybersecurity audit
The annual CCPA cybersecurity audit tests 18 security components and has its own independence rules. The readiness assessment includes six security controls, not the audit itself.
Not a certification
No assessment can certify compliance. The reports show where you stand against each control on the assessment date and what to do next.
A sample finding
- Control
- WEB-03 · Opt-out link on the website
- Finding
- No “Do Not Sell or Share My Personal Information” or “Your Privacy Choices” link on the home page
- Severity
- Critical
- Observation
- Website review (read-only): the link was not found on the home page, and one advertising tag loads there. Whether the tag amounts to selling or sharing depends on its configuration and contract.
- Recommendation
- Add the link to the footer of every page, connect it to the opt-out mechanism and confirm the tag’s status with counsel. Owner: Marketing and Legal.
Page 11 of 13: CCPA readiness assessment
- 1. CCPA and CPRA compliance (hub)
- 2. CCPA vs CPRA explained
- 3. Does the CCPA apply to your business?
- 4. Consumer rights and privacy requests
- 5. Penalties, fines and lawsuits
- 6. Implementation roadmap
- 7. CCPA for IT administrators
- 8. CCPA cybersecurity audit
- 9. Risk assessments and ADMT
- 10. CCPA compliance checklist
- 11. CCPA readiness assessment (this page)
- 12. CCPA assessment sample report
- 13. How to test opt-outs and Global Privacy Control
Guided by Ali Hassani, CISSP, C|CISO
Certified CISO (C|CISO) and CISSP with 25+ years in IT, cybersecurity, compliance and infrastructure, who has earned dozens of Microsoft and Cisco certifications over his career, including MCSE, MCITP, MCSA Security, CCNP and CCNA. OC Security Audit handles the technical side of the CCPA: data inventories, security controls and evidence as your readiness advisor, or the cybersecurity audit as your independent auditor, one role per program. Legal interpretation stays with your privacy counsel.
Questions business owners and IT leaders ask
Do you need access to our systems?
Not for the assessment itself. It uses the questionnaire, documents you choose to share and your public website. Evidence reviews of internal systems are a separate, agreed scope.
Will our website or visitors notice?
Visitors see nothing. Your web server log shows a few page requests from our office, normally three. Firewalls or bot protection may log them like any other visitor.
Is the readiness score a compliance certificate?
No. It is a planning measure based on the controls assessed on that date. Only your counsel can advise on legal compliance.
Can you re-check after we fix things?
Yes. A follow-up assessment uses the same controls and scoring, and a comparison report shows what closed, what improved and what is unchanged.
Does this cover the CCPA cybersecurity audit?
No. The cybersecurity audit is a separate, annual audit of 18 security components for businesses in scope. We can be your readiness advisor or your independent auditor, never both for the same program.
General information, not legal advice
This page summarizes California privacy law and regulations as of October 2026 to help businesses plan their cybersecurity and IT work. It is general information, not legal advice. It does not create an attorney-client relationship and does not guarantee compliance or any outcome. OC Security Audit is a cybersecurity firm, not a law firm. Confirm how the CCPA applies to your business with qualified California privacy counsel. Enforcement examples summarize the regulators’ public announcements; settlements can resolve allegations without an admission of wrongdoing. Laws, regulations and inflation-adjusted amounts change, so check the primary sources below.
Primary sources · Last reviewed October 2026
- California Civil Code, Title 1.81.5: California Consumer Privacy Act
- CalPrivacy: text of the CCPA regulations on cybersecurity audits, risk assessments and ADMT (effective January 1, 2026)
- CalPrivacy: CCPA updates, cybersecurity audit, risk assessment and ADMT rulemaking
- Global Privacy Control specification and browser support
See where your privacy program stands, control by control
Schedule a consultation. We scope the readiness assessment, explain what we need from your team and show you the sample reports.
Read-only reviews. Irvine, Orange County and Southern California on-site; remote nationwide.