
CCPA Consumer Rights and How to Handle Privacy Requests
Know, delete, correct, opt out, limit and no retaliation. What each right means, the deadlines and the systems your team must search.
10 business days to confirm, 45 days to answer
Opt-outs of sale and sharing must be honored as soon as feasibly possible and no later than 15 business days.
Every consumer right is a process your team must run
Someone receives the request, verifies it when the law allows, finds the data across systems and vendors, acts on it, answers on time and keeps a record.
CalPrivacy’s complaint data shows where it goes wrong: the right to delete is among the most common complaint categories. Published enforcement cases keep returning to the same failures: opt-outs that do not work and verification that asks for too much.
What California residents can ask for
| Right | What the consumer can ask | Deadline | Verification |
|---|---|---|---|
| Know (access) | The categories and specific pieces of personal information collected, the sources, the purposes and the categories of third parties that received it, in a portable format. Covers 12 months, or back to January 1, 2022 on request unless impossible or disproportionate | Confirm within 10 business days; answer within 45 calendar days, extendable once by 45 days with notice | Yes, with a higher standard for specific pieces of information |
| Delete | Deletion of personal information collected from the consumer; from January 1, 2027, also data collected about them from other sources (SB 923) | Same as above | Yes |
| Correct | Correction of inaccurate personal information | Same as above | Yes |
| Opt out of sale and sharing | Stop selling or sharing their personal information, including through opt-out preference signals such as Global Privacy Control | As soon as feasibly possible, no later than 15 business days | You may not require identity verification |
| Limit sensitive personal information | Limit its use and disclosure to the purposes the regulations allow | No later than 15 business days | You may not require identity verification |
| No retaliation | Equal service and price for exercising rights; financial incentives only with a notice and consent | Always | Not applicable |
| Automated decision-making | Opt out of automated decisions on significant matters, unless an exception such as a human appeal applies, and get information about them, where the business uses them | From January 1, 2027 | Yes, for access |
Minors: a business may not sell or share the personal information of consumers it knows are under 16 without opt-in consent, from the consumer if 13 to 15 and from a parent or guardian if under 13. Willfully disregarding a consumer’s age counts as knowing it.
A six-step workflow that meets the deadlines
Intake
Offer two or more ways to submit requests, including a toll-free number, and a method on your website if you have one. A business that operates only online with a direct relationship may use an email address today; from January 1, 2027, SB 923 requires an online method such as a webform as well.
Confirm within 10 business days
Acknowledge the request, explain how you will verify it and when to expect an answer.
Verify, proportionately
Match information you already hold. Never make a consumer create an account, although an existing account holder can be asked to use it. Do not require identity verification for opt-outs or requests to limit.
Search and act
Search every system and vendor that holds the data. Data in archived or backup systems may be handled when it is restored to an active system or next accessed or used for a sale, disclosure or commercial purpose.
Respond within 45 days
Answer within 45 calendar days, or extend once by 45 days with notice and a reason. Explain any denial in detail.
Record
Keep a record of every request and response for at least 24 months: date, type, how it was made, the response and any reason for denial.
Six rules for opt-outs that work
The links
A “Do Not Sell or Share My Personal Information” link, and a “Limit the Use of My Sensitive Personal Information” link when required, or the combined alternative opt-out link.
Opt-out preference signals
Treat a valid signal such as Global Privacy Control as an opt-out for that browser or device and, if known, the consumer’s account.
Show the result
Since January 1, 2026, display whether the signal or request was processed, for example “Opt-Out Request Honored”.
Symmetry, no dark patterns
Opting out takes no more steps than opting in. Closing a banner is not consent. A cookie banner alone is not an opt-out method.
Pass it on
Notify third parties that received the data after the request, and direct them to comply and forward it.
Test it
Retest after every website release. In one CalPrivacy case, a retailer’s consent tool was broken for 40 days, according to the agency.
Where personal information hides, and how to find it
| System | Where personal information hides | How IT finds and acts on it |
|---|---|---|
| Microsoft 365 | Mailboxes, OneDrive, SharePoint, Teams chats | Microsoft Purview content search or eDiscovery; retention policies for deletion |
| CRM and marketing platforms | Contacts, leads, campaign lists, web form submissions | Admin search and export; suppression list so deleted contacts are not re-imported |
| ERP, billing and e-commerce | Orders, invoices, addresses, payment tokens | Built-in reports; legal retention rules can override deletion |
| HR and payroll | Employee and applicant records | HR system exports; many employment records must be kept by law |
| File servers and NAS | Spreadsheets, scans, exports | File indexing or DLP discovery scans |
| Backups and archives | Copies of everything | Document the process: delete when restored to an active system or next accessed or used for a sale, disclosure or commercial purpose |
| Vendors | Help desk, email platform, analytics, payroll provider | Contract terms requiring them to help with requests; notify them of deletions |
| Logs and security tools | IP addresses, device identifiers, user names | Retention settings; security exceptions usually apply |
Enforcement actions and announced amounts
| Case | What the regulator cited | Result |
|---|---|---|
| American Honda Motor Co. (CalPrivacy, March 2025) | Asked for too much information to process opt-outs, required consumers to confirm agents directly, offered a one-step “Allow All” against a two-step opt-out | $632,500 |
| Todd Snyder, Inc. (CalPrivacy, May 2025) | Cookie tool broken for 40 days so opt-outs failed; demanded a photo ID for every request | $345,178 |
| The Walt Disney Company (Attorney General, February 2026) | Opt-outs applied to one service or device, not the whole account; many connected-TV apps had no in-app opt-out | $2.75 million |
| Ford Motor Company (CalPrivacy, March 2026) | Required an email verification step before processing opt-outs | $375,703 |
Summaries of the regulators’ announcements. Settlements can resolve allegations without an admission of wrongdoing.
A finding from a sample report
- Area
- Requests to delete
- Finding
- Deletion requests do not reach the email marketing platform or the backups
- Severity
- High
- Evidence
- Three of five sampled deletion requests were closed in the ticket system while the contact still existed in the email marketing platform. No suppression list. Backup handling not documented.
- Fix
- Add the marketing platform and CRM to the deletion runbook, keep a suppression list, document backup handling and test monthly with a sample request.
Timelines your team must meet
to confirm a request to know, delete or correct
Source: 11 CCR §7021(a)to respond, plus one 45-day extension with notice
Source: 11 CCR §7021(b)at most to stop selling or sharing after an opt-out
Source: 11 CCR §7026to keep records of requests and responses
Source: 11 CCR §7101Page 4 of 10: Consumer rights and privacy requests
- 1. CCPA and CPRA compliance (hub)
- 2. CCPA vs CPRA explained
- 3. Does the CCPA apply to your business?
- 4. Consumer rights and privacy requests (this page)
- 5. Penalties, fines and lawsuits
- 6. Implementation roadmap
- 7. CCPA for IT administrators
- 8. CCPA cybersecurity audit
- 9. Risk assessments and ADMT
- 10. CCPA compliance checklist
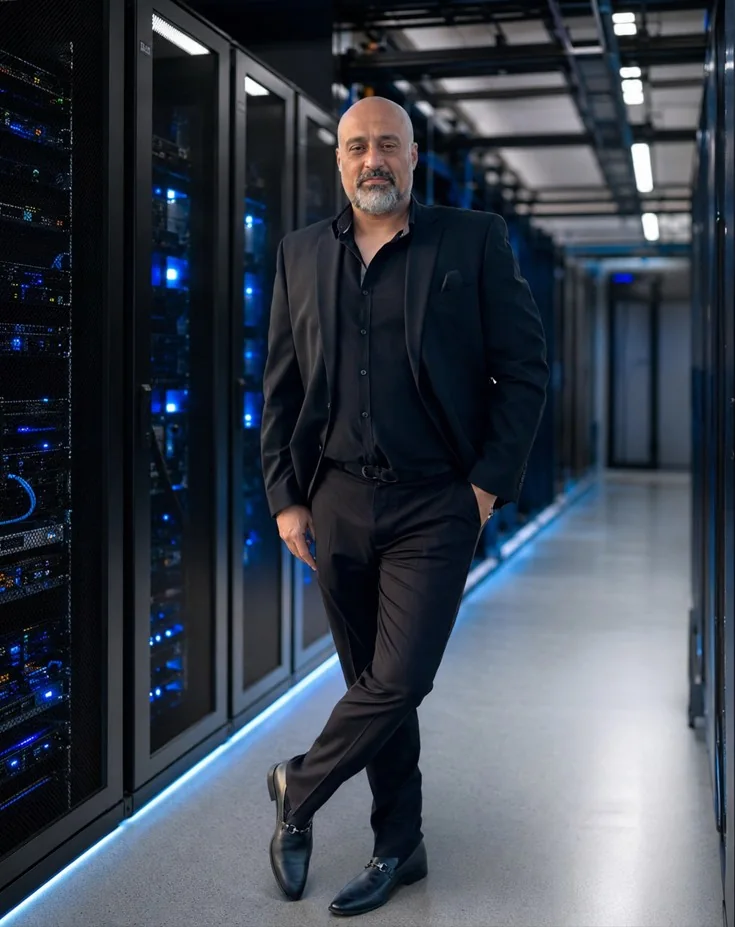
Guided by Ali Hassani, CISSP, C|CISO
Certified CISO (C|CISO) and CISSP with 25+ years in IT, cybersecurity, compliance and infrastructure, who has earned dozens of Microsoft and Cisco certifications over his career, including MCSE, MCITP, MCSA Security, CCNP and CCNA. OC Security Audit handles the technical side of the CCPA: data inventories, security controls and evidence as your readiness advisor, or the cybersecurity audit as your independent auditor, one role per program. Legal interpretation stays with your privacy counsel.
Questions business owners and IT leaders ask
Can we require a photo ID?
Not for opt-outs or requests to limit. For know, delete and correct, verification must be proportionate to the data. CalPrivacy’s action against Todd Snyder cited a photo ID requirement for every request.
Do we have to delete data we need for legal or tax reasons?
Not if one of the law’s exceptions applies, such as completing a transaction, security, legal obligations and internal uses compatible with the context. Confirm with counsel, and explain the reason when you deny a request.
What about data in backups?
You may delay deletion in archived or backup systems until that data is restored to an active system or next accessed or used for a sale, disclosure or commercial purpose. Document the process.
How do authorized agents work?
Consumers may use an authorized agent. For know, delete and correct requests, you may ask for the consumer’s signed permission and also have the consumer verify their identity or confirm the agent directly. For opt-outs and requests to limit, you may ask only for the signed permission, and none for an opt-out preference signal. CalPrivacy’s action against Honda cited, in part, making consumers confirm their agents directly on opt-outs.
How long do we keep request records?
At least 24 months, including the date, the type of request, how it was made, your response and any reason for denial.
General information, not legal advice
This page summarizes California privacy law and regulations as of October 2026 to help businesses plan their cybersecurity and IT work. It is general information, not legal advice. It does not create an attorney-client relationship and does not guarantee compliance or any outcome. OC Security Audit is a cybersecurity firm, not a law firm. Confirm how the CCPA applies to your business with qualified California privacy counsel. Enforcement examples summarize the regulators’ public announcements; settlements can resolve allegations without an admission of wrongdoing. Laws, regulations and inflation-adjusted amounts change, so check the primary sources below.
Primary sources · Last reviewed October 2026
- California Civil Code, Title 1.81.5: California Consumer Privacy Act
- CalPrivacy: text of the CCPA regulations on cybersecurity audits, risk assessments and ADMT (effective January 1, 2026)
- Cal. Code Regs. tit. 11, §7101, record-keeping (Cornell Legal Information Institute)
- CalPrivacy: SB 923 strengthens deletion rights (signed September 27, 2026)
- CalPrivacy: American Honda Motor Co. settlement, March 12, 2025
- CalPrivacy: Todd Snyder, Inc. decision, May 6, 2025
- California Attorney General: Disney settlement, February 11, 2026
- CalPrivacy: Ford Motor Company decision, March 5, 2026
- CalPrivacy: annual enforcement update, board meeting of May 1, 2026
- Global Privacy Control specification and browser support
Find out whether your requests and opt-outs actually work
Schedule a consultation. We test your request intake, deletion runbooks and opt-out signals against the technical and timing requirements in the regulations.
Read-only reviews. Irvine, Orange County and Southern California on-site; remote nationwide.