
CCPA Penalties, Fines and Lawsuits: What Non-Compliance Costs
Up to $2,663 per violation and $7,988 per intentional violation, breach lawsuits of $107 to $799 per consumer, and enforcement that has already reached $12.75 million in one case.
Two regulators, plus consumers after a breach
The Attorney General and CalPrivacy both enforce the CCPA. After certain breaches, consumers can sue for statutory damages.
How CCPA fines and penalties are calculated
CalPrivacy can impose administrative fines, and the Attorney General can seek civil penalties and injunctions in court. Both are set per violation and adjusted for inflation every odd-numbered year. The current amounts took effect January 1, 2025.
The CPRA removed the automatic 30-day period that let businesses fix violations after a notice. CalPrivacy may still allow time to cure at its discretion, but businesses can no longer count on it.
Separately, consumers can sue after a breach of their nonencrypted and nonredacted personal information caused by a failure to maintain reasonable security.
Four ways non-compliance turns into cost
| Path | Who | Amount | Notes |
|---|---|---|---|
| Administrative fine | CalPrivacy | Up to $2,663 per violation, or $7,988 per intentional violation or violation involving consumers the business knows are under 16 | Civil Code §1798.155, as adjusted January 1, 2025 |
| Civil penalty | Attorney General | The same amounts per violation, in a civil action, plus injunctions | Civil Code §1798.199.90 |
| Data breach lawsuit | Consumers, often as class actions | $107 to $799 per consumer per incident, or actual damages if greater | Civil Code §1798.150: nonencrypted and nonredacted personal information, or an email address with a password or security answer, subject to unauthorized access and exfiltration, theft or disclosure because of a failure to maintain reasonable security. A 30-day notice and cure applies to statutory damages; adding security after the breach is not a cure. |
| Data broker penalties | CalPrivacy | $200 per day for failing to register; $200 per day for each deletion request not processed | Delete Act, plus investigation costs |
What the numbers can add up to
If each affected consumer counted as one violation
At $7,988 per violation
Statutory damages at $107 to $799 per consumer per incident
Real CCPA enforcement actions and what regulators cited
| Date | Company | Regulator | Amount | What the regulator cited |
|---|---|---|---|---|
| May 8, 2026 | General Motors | Attorney General with four district attorneys, supported by CalPrivacy | $12.75 million | Alleged sale of drivers’ names, contact details, location and driving data to data brokers. The settlement, subject to court approval, bars GM from selling driving data to consumer reporting agencies for five years; GM resolved the matter without admitting liability. |
| March 5, 2026 | Ford Motor Company | CalPrivacy | $375,703 | Required email verification before processing opt-outs; must audit its website tracking technologies. |
| March 3, 2026 | PlayOn Sports (GoFan) | CalPrivacy | $1.10 million | Made users accept tracking to use tickets, offered no working opt-out and ignored opt-out preference signals. |
| February 11, 2026 | The Walt Disney Company | Attorney General | $2.75 million | Opt-outs did not apply across services and devices; no in-app opt-out in many connected-TV apps. |
| September 30, 2025 | Tractor Supply Company | CalPrivacy | $1.35 million | No working opt-out, ignored Global Privacy Control, did not inform job applicants of their rights, shared data without required contracts. |
| July 1, 2025 | Healthline Media | Attorney General | $1.55 million | Kept sharing data with advertisers after opt-outs; shared article titles suggesting medical diagnoses to target ads. |
| May 6, 2025 | Todd Snyder, Inc. | CalPrivacy | $345,178 | Cookie tool broken for 40 days; demanded a photo ID for every request. |
| March 12, 2025 | American Honda Motor Co. | CalPrivacy | $632,500 | Over-verification of opt-outs, asymmetrical cookie choices, missing advertising technology contracts. |
Amounts and descriptions as announced by the regulators; settlements can resolve allegations without an admission of wrongdoing. CalPrivacy has also brought multiple actions against data brokers that failed to register.
The costs that do not show up in the headline
Mandated changes
Settlements can require program changes, audits and reporting. Ford must audit its website tracking technologies, and the General Motors settlement bars GM from selling driving data to consumer reporting agencies for five years.
Breach costs
The global average cost of a data breach reached $4.99 million in 2026, and $11.5 million in the United States, according to IBM’s Cost of a Data Breach Report 2026.
Class actions
Statutory damages of $107 to $799 per consumer per incident add up quickly when a breach becomes a class action, and defense costs start long before any judgment.
Executive certification
Businesses in scope for cybersecurity audits must certify completion to CalPrivacy under penalty of perjury, signed by a member of executive management.
Lost time
Investigations demand records, policies and evidence under deadlines, pulling legal, IT and leadership away from the business.
Trust
Enforcement announcements name the company and describe what went wrong, in public.
Seven controls that reduce your exposure
Encrypt personal information at rest and in transit
Statutory damages in CCPA breach lawsuits apply to nonencrypted and nonredacted data, which makes encryption one of the most valuable controls to get right.
Make opt-outs work, and keep testing them
Honor Global Privacy Control, block advertising tags for opted-out visitors, show the opt-out status and retest after every release.
Verify only what you must
No identity checks for opt-outs. Proportionate checks for know, delete and correct.
Sign the required contracts
Service providers, contractors and third parties you sell or share personal information to need CCPA contract terms.
Collect less, keep less
Data minimization is now enforced. Data you do not keep cannot be breached or sold.
Document reasonable security
Map your controls to the 18 components in the cybersecurity audit regulation and keep the evidence.
Rehearse breach response
Notices to residents within 30 days of discovering a breach and to the Attorney General within 15 days of notifying residents when more than 500 are affected.
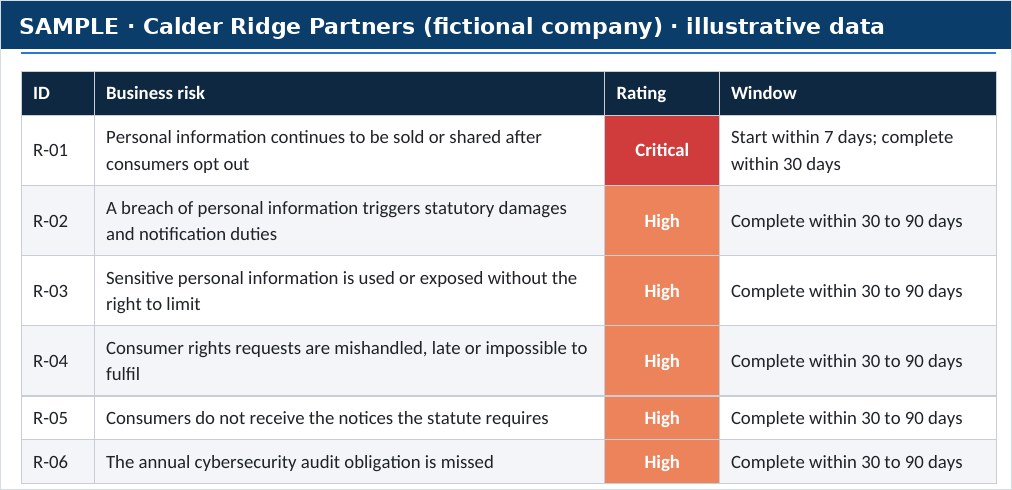
A finding with an exposure estimate
- Area
- Access control and encryption
- Finding
- Unencrypted file share with 18,400 client records is open to all staff
- Severity
- Critical
- Evidence
- Share permissions grant every domain user modify rights. Files include names with Social Security numbers. No encryption at rest on the storage device.
- Exposure
- If stolen: 18,400 × $107 to $799 = $1,968,800 to $14,701,600 in statutory damages, before defense costs.
- Fix
- Restrict the share to the tax team, enable encryption at rest, move Social Security numbers into the practice-management system and log access.
What non-compliance has cost so far
largest announced CCPA settlement as of October 2026 (General Motors)
Source: California Attorney General, May 8, 2026per intentional violation or violation involving consumers the business knows are under 16
Source: CalPrivacy monetary adjustment, January 1, 2025maximum statutory damages per consumer per incident in breach lawsuits
Source: Civil Code §1798.150, as adjustedglobal average cost of a data breach in 2026
Source: IBM Cost of a Data Breach Report 2026Page 5 of 13: Penalties, fines and lawsuits
- 1. CCPA and CPRA compliance (hub)
- 2. CCPA vs CPRA explained
- 3. Does the CCPA apply to your business?
- 4. Consumer rights and privacy requests
- 5. Penalties, fines and lawsuits (this page)
- 6. Implementation roadmap
- 7. CCPA for IT administrators
- 8. CCPA cybersecurity audit
- 9. Risk assessments and ADMT
- 10. CCPA compliance checklist
- 11. CCPA readiness assessment
- 12. CCPA assessment sample report
- 13. How to test opt-outs and Global Privacy Control
Guided by Ali Hassani, CISSP, C|CISO
Certified CISO (C|CISO) and CISSP with 25+ years in IT, cybersecurity, compliance and infrastructure, who has earned dozens of Microsoft and Cisco certifications over his career, including MCSE, MCITP, MCSA Security, CCNP and CCNA. OC Security Audit handles the technical side of the CCPA: data inventories, security controls and evidence as your readiness advisor, or the cybersecurity audit as your independent auditor, one role per program. Legal interpretation stays with your privacy counsel.
Questions business owners and IT leaders ask
Is there still a 30-day cure period?
Not an automatic one for regulator enforcement; the CPRA removed it, although CalPrivacy may choose to allow time to cure. A 30-day notice-and-cure step still applies before consumers sue for statutory damages after a breach.
Can consumers sue for any CCPA violation?
No. The private right of action covers breaches of certain nonencrypted and nonredacted personal information caused by a failure to maintain reasonable security. Other violations are enforced by the Attorney General and CalPrivacy.
Are fines counted per consumer?
The law sets amounts per violation. How violations are counted depends on the facts of each case.
Does cyber insurance cover CCPA fines?
Policies differ. Ask your broker whether regulatory fines and privacy class actions are covered and which security controls the policy requires.
What reduces breach lawsuit exposure the most?
Encryption and redaction of personal information, because statutory damages apply to nonencrypted and nonredacted data, together with documented reasonable security.
General information, not legal advice
This page summarizes California privacy law and regulations as of October 2026 to help businesses plan their cybersecurity and IT work. It is general information, not legal advice. It does not create an attorney-client relationship and does not guarantee compliance or any outcome. OC Security Audit is a cybersecurity firm, not a law firm. Confirm how the CCPA applies to your business with qualified California privacy counsel. Enforcement examples summarize the regulators’ public announcements; settlements can resolve allegations without an admission of wrongdoing. Laws, regulations and inflation-adjusted amounts change, so check the primary sources below.
Primary sources · Last reviewed October 2026
- CalPrivacy: updated monetary thresholds in the CCPA (effective January 1, 2025)
- California Civil Code, Title 1.81.5: California Consumer Privacy Act
- California Attorney General: General Motors settlement, May 8, 2026
- California Attorney General: Disney settlement, February 11, 2026
- California Attorney General: Healthline settlement, July 1, 2025
- CalPrivacy: Tractor Supply Company decision, September 30, 2025
- CalPrivacy: American Honda Motor Co. settlement, March 12, 2025
- CalPrivacy: Todd Snyder, Inc. decision, May 6, 2025
- CalPrivacy: PlayOn Sports decision, March 3, 2026
- CalPrivacy: Ford Motor Company decision, March 5, 2026
- CalPrivacy: data brokers and the DROP deletion platform
- California Legislature: SB 446, data breach notification deadlines
- IBM: Cost of a Data Breach Report 2026
Lower your exposure before it is counted
Schedule a consultation. We look for the unencrypted data, broken opt-outs and missing controls that regulators and plaintiffs most often cite.
Read-only reviews. Irvine, Orange County and Southern California on-site; remote nationwide.