
CCPA Risk Assessments and ADMT Rules: When You Need One
Selling or sharing data, processing sensitive personal information, using automated decision-making for significant decisions: each now requires a documented risk assessment before you start.
Automated decision-making rules apply from January 1, 2027
If software makes, or substantially makes, decisions about financial or lending services, housing, education, employment or healthcare, consumers get notice, access and, in most cases, opt-out rights.
What a CCPA risk assessment is
A risk assessment weighs the privacy risks of a processing activity against its benefits to the consumer, the business, other stakeholders and the public. If the risks outweigh the benefits, the regulation’s goal is to restrict or stop the processing.
It must be done before the activity starts, reviewed at least every three years and updated within 45 days of a material change.
Six activities that require a risk assessment
| Activity (11 CCR §7150(b)) | Everyday example |
|---|---|
| Selling or sharing personal information | Advertising pixels that share browsing data for cross-context behavioral advertising |
| Processing sensitive personal information | Precise geolocation, health information, government ID numbers, account log-ins with passwords |
| Using automated decision-making technology (ADMT) for a significant decision | Automatic screening of loan or job applications |
| Automated inferences from systematic observation of applicants, students, employees or contractors | Monitoring software that scores employee productivity |
| Automated inferences based on presence in a sensitive location | Inferring health conditions from visits to clinics |
| Processing personal information you intend to use to train ADMT for significant decisions, or facial-recognition, emotion-recognition, identity-verification or biometric profiling technology | Using customer photos to train face matching, or letting a vendor train on them |
Exception: processing employees’ or contractors’ sensitive personal information solely to administer pay, employment authorization, benefits, reasonable accommodation or required wage reporting does not need a risk assessment.
What every risk assessment must cover
Purpose and data
- A specific purpose, never “to improve our services”
- The categories of personal information, including sensitive data
- The minimum personal information needed for the purpose
How the processing works
- Collection methods and sources
- Retention per category
- How you interact with consumers
- The approximate number of consumers
- Disclosures made to consumers
- Who receives the data, and why
- For ADMT: its logic, assumptions and limitations, its output and how the output is used
Benefits, harms and safeguards
- Specific benefits
- Negative impacts and their causes, such as unauthorized access, discrimination, loss of control, coercion, and economic, physical, reputational or psychological harm
- Safeguards such as encryption, segmentation, access controls and monitoring
Decision and sign-off
- Whether you will go ahead
- Who provided the information
- Who reviewed and approved it, and when
- Approval by someone with authority over the decision
The written report documents the assessment, including the purpose, the data, how the processing works, the safeguards, the decision and the sign-off. Confirm the full required content with counsel.
The risk assessment calendar
Before starting any new covered processing.Conduct and document the assessment first.
Assessments for processing that began before 2026 and continues.
Submit information about 2026 and 2027 assessments to CalPrivacy.The number of assessments, the categories of personal information involved and an attestation by an executive, under penalty of perjury.
Submit information about the previous year’s assessments.
Hand over the full reports to CalPrivacy or the Attorney General.
For as long as the processing continues or five years after the assessment is completed, whichever is later.
The ADMT rules in plain language
What counts as ADMT
Technology that processes personal information and uses computation to replace, or substantially replace, human decision-making. A human reviewer who can interpret the output, analyzes it and has authority to change the decision keeps it out of scope.
Significant decisions
Decisions that result in the provision or denial of financial or lending services, housing, education enrollment or opportunities, employment or contracting opportunities or pay, or healthcare services.
What you owe consumers
A pre-use notice with the specific purpose, a right to opt out unless an exception applies (a human appeal, or certain hiring, admission, work-allocation and pay uses), and a right to access information about the decision. Existing uses must comply by January 1, 2027; risk assessments follow their own deadlines.
AI tools in hiring and lending deserve a close look. Employment law adds its own rules: California’s regulations on automated decision systems in employment have applied since October 1, 2025, and SB 947, signed September 30, 2026, bars discipline or firing based solely on an automated system from July 1, 2027. See our AI governance and compliance guide
What IT contributes to every assessment
System facts
Which systems process the data, where it is stored, who can access it and how long it is kept.
Data flows
Which vendors and third parties receive the data and through which integrations.
Safeguards
Encryption, segmentation, access controls, monitoring and change management, the safeguards the regulation names.
Tool inventory
An inventory of AI and automated tools in use, including the ones nobody approved.
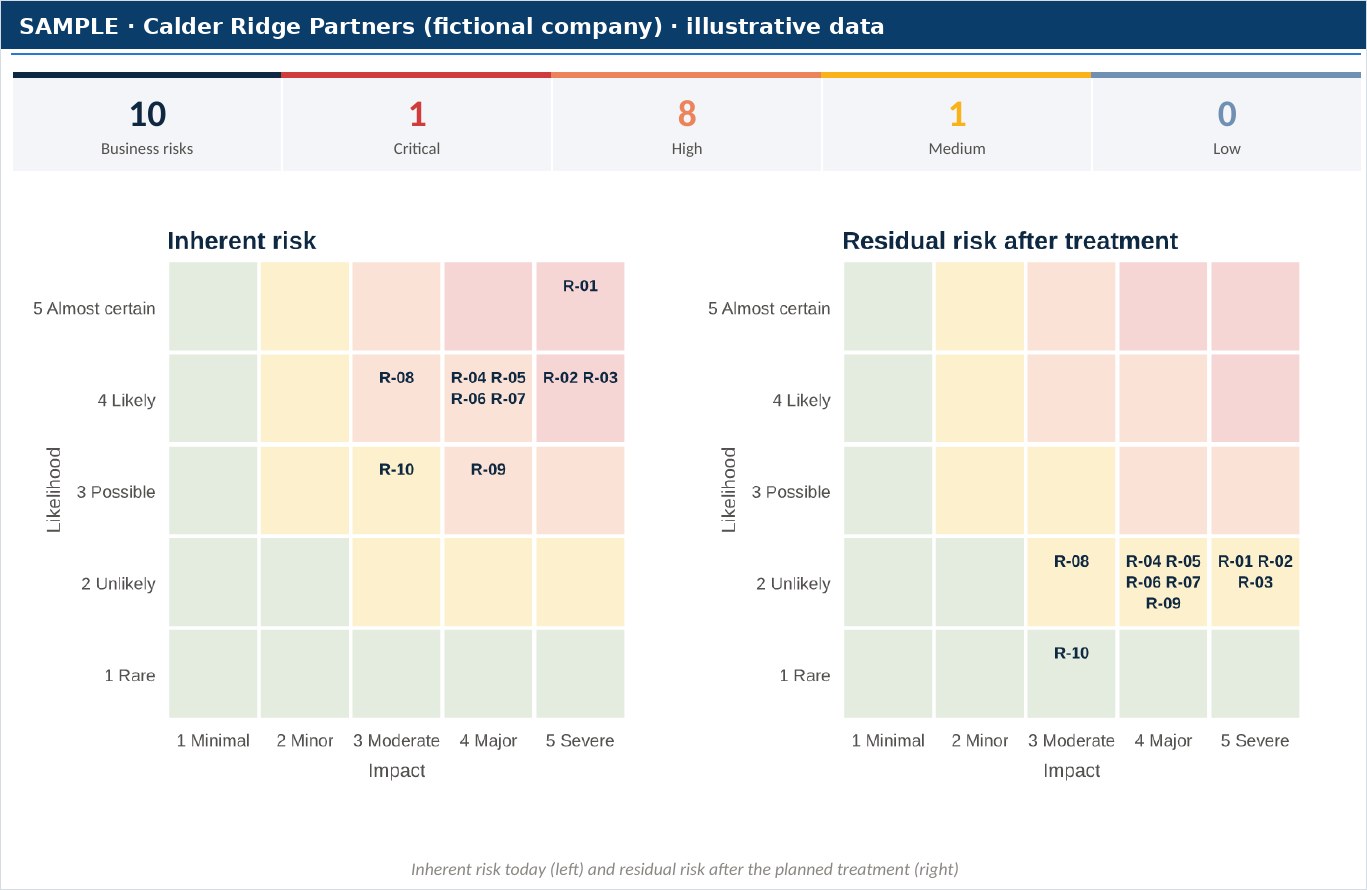
A finding from a sample report
- Area
- Automated decision-making
- Finding
- Résumé-screening feature rejects applicants automatically, with no risk assessment and no pre-use notice
- Severity
- High
- Evidence
- The hiring platform’s auto-reject feature declines applicants below a score. Recruiters do not review rejected applications. The job application contains no notice about automated decisions.
- Fix
- Add meaningful human review, or prepare the pre-use notice, the opt-out or appeal process and a risk assessment before January 1, 2027.
Risk assessment deadlines and cadences
deadline for assessments of processing that began before 2026
Source: 11 CCR §7155(b)first submission of assessment information to CalPrivacy
Source: 11 CCR §7157(a)(1)to update an assessment after a material change
Source: 11 CCR §7155(a)(3)to hand over full reports when CalPrivacy or the Attorney General asks
Source: 11 CCR §7157(e)Page 9 of 13: Risk assessments and ADMT
- 1. CCPA and CPRA compliance (hub)
- 2. CCPA vs CPRA explained
- 3. Does the CCPA apply to your business?
- 4. Consumer rights and privacy requests
- 5. Penalties, fines and lawsuits
- 6. Implementation roadmap
- 7. CCPA for IT administrators
- 8. CCPA cybersecurity audit
- 9. Risk assessments and ADMT (this page)
- 10. CCPA compliance checklist
- 11. CCPA readiness assessment
- 12. CCPA assessment sample report
- 13. How to test opt-outs and Global Privacy Control
Guided by Ali Hassani, CISSP, C|CISO
Certified CISO (C|CISO) and CISSP with 25+ years in IT, cybersecurity, compliance and infrastructure, who has earned dozens of Microsoft and Cisco certifications over his career, including MCSE, MCITP, MCSA Security, CCNP and CCNA. OC Security Audit handles the technical side of the CCPA: data inventories, security controls and evidence as your readiness advisor, or the cybersecurity audit as your independent auditor, one role per program. Legal interpretation stays with your privacy counsel.
Questions business owners and IT leaders ask
Does every business need risk assessments?
Only businesses whose processing presents significant risk as defined. But selling or sharing personal information, including through advertising pixels, and processing sensitive personal information are common triggers.
Can one assessment cover similar activities?
Yes. A single assessment can cover a comparable set of processing activities that present similar risks.
Can we reuse an assessment done for another state’s law?
Yes, if it contains everything §7152 requires, or you add what is missing.
Is using ChatGPT or Copilot automated decision-making?
The ADMT rules apply only when the output is used to make a significant decision without meaningful human involvement. Using AI to draft an email is not. Using it to reject job applicants automatically could be. Separately, some uses need a risk assessment even without a significant decision, such as automated inferences about workers or applicants, or training technology on personal information.
Who must approve the assessment?
Someone with authority to decide whether the processing goes ahead. The yearly submission must come from a member of executive management.
General information, not legal advice
This page summarizes California privacy law and regulations as of October 2026 to help businesses plan their cybersecurity and IT work. It is general information, not legal advice. It does not create an attorney-client relationship and does not guarantee compliance or any outcome. OC Security Audit is a cybersecurity firm, not a law firm. Confirm how the CCPA applies to your business with qualified California privacy counsel. Enforcement examples summarize the regulators’ public announcements; settlements can resolve allegations without an admission of wrongdoing. Laws, regulations and inflation-adjusted amounts change, so check the primary sources below.
Primary sources · Last reviewed October 2026
- CalPrivacy: text of the CCPA regulations on cybersecurity audits, risk assessments and ADMT (effective January 1, 2026)
- CalPrivacy: CCPA updates, cybersecurity audit, risk assessment and ADMT rulemaking
- California Civil Code, Title 1.81.5: California Consumer Privacy Act
- California Legislature: SB 947, automated decision systems in employment (signed September 30, 2026)
- Jackson Lewis: California’s employment regulations on automated decision systems, effective October 1, 2025
Know which activities need an assessment, and get them done
Schedule a consultation. We help you list likely triggers for your counsel and document the system facts, data flows and safeguards for each assessment; your counsel confirms the content the regulation requires.
Read-only reviews. Irvine, Orange County and Southern California on-site; remote nationwide.