
HIPAA compliance consulting
How the assessment runs, the packages, what to prepare and the safeguards we review.
See the service →HIPAA compliance assessment sample
Every page of a real-format HIPAA Security Rule assessment for a fictional two-location clinic: executive report, technical findings, risk register, roadmap and workbook.
Written for practice leaders
Scores, business risks and leadership decisions in plain language, so owners can approve a funded 180-day plan instead of a binder.
Evidence your IT provider can use
Each finding names the 45 CFR reference, the evidence, the business impact, the exact steps and how to confirm the fix worked.
Our deliverables
A HIPAA compliance assessment is only useful if leadership can decide from it and the IT team can work from it. This sample shows every deliverable we hand over at the end of a HIPAA Security Rule assessment, page by page, so you can judge the depth before you book. It covers the administrative, physical and technical safeguards in 45 CFR Part 164, Subpart C, across Microsoft 365, Entra ID, Intune, Active Directory and Windows servers, two firewalls with remote access VPN, the Cisco switching and wireless network, backups and external exposure.
OC Security Audit runs these assessments for medical practices, dental offices, clinics and business associates from Irvine, on-site across Orange County, Los Angeles and Southern California, and remotely nationwide. The work is read-only: we review settings, evidence and documents, and nothing in your environment is changed.
Sample notice. Contoso Family Health Clinic is a fictional organization. Every name, account, address and figure in these pages is invented for illustration and describes no real customer. The structure, depth and format are the same as the reports our clients receive.
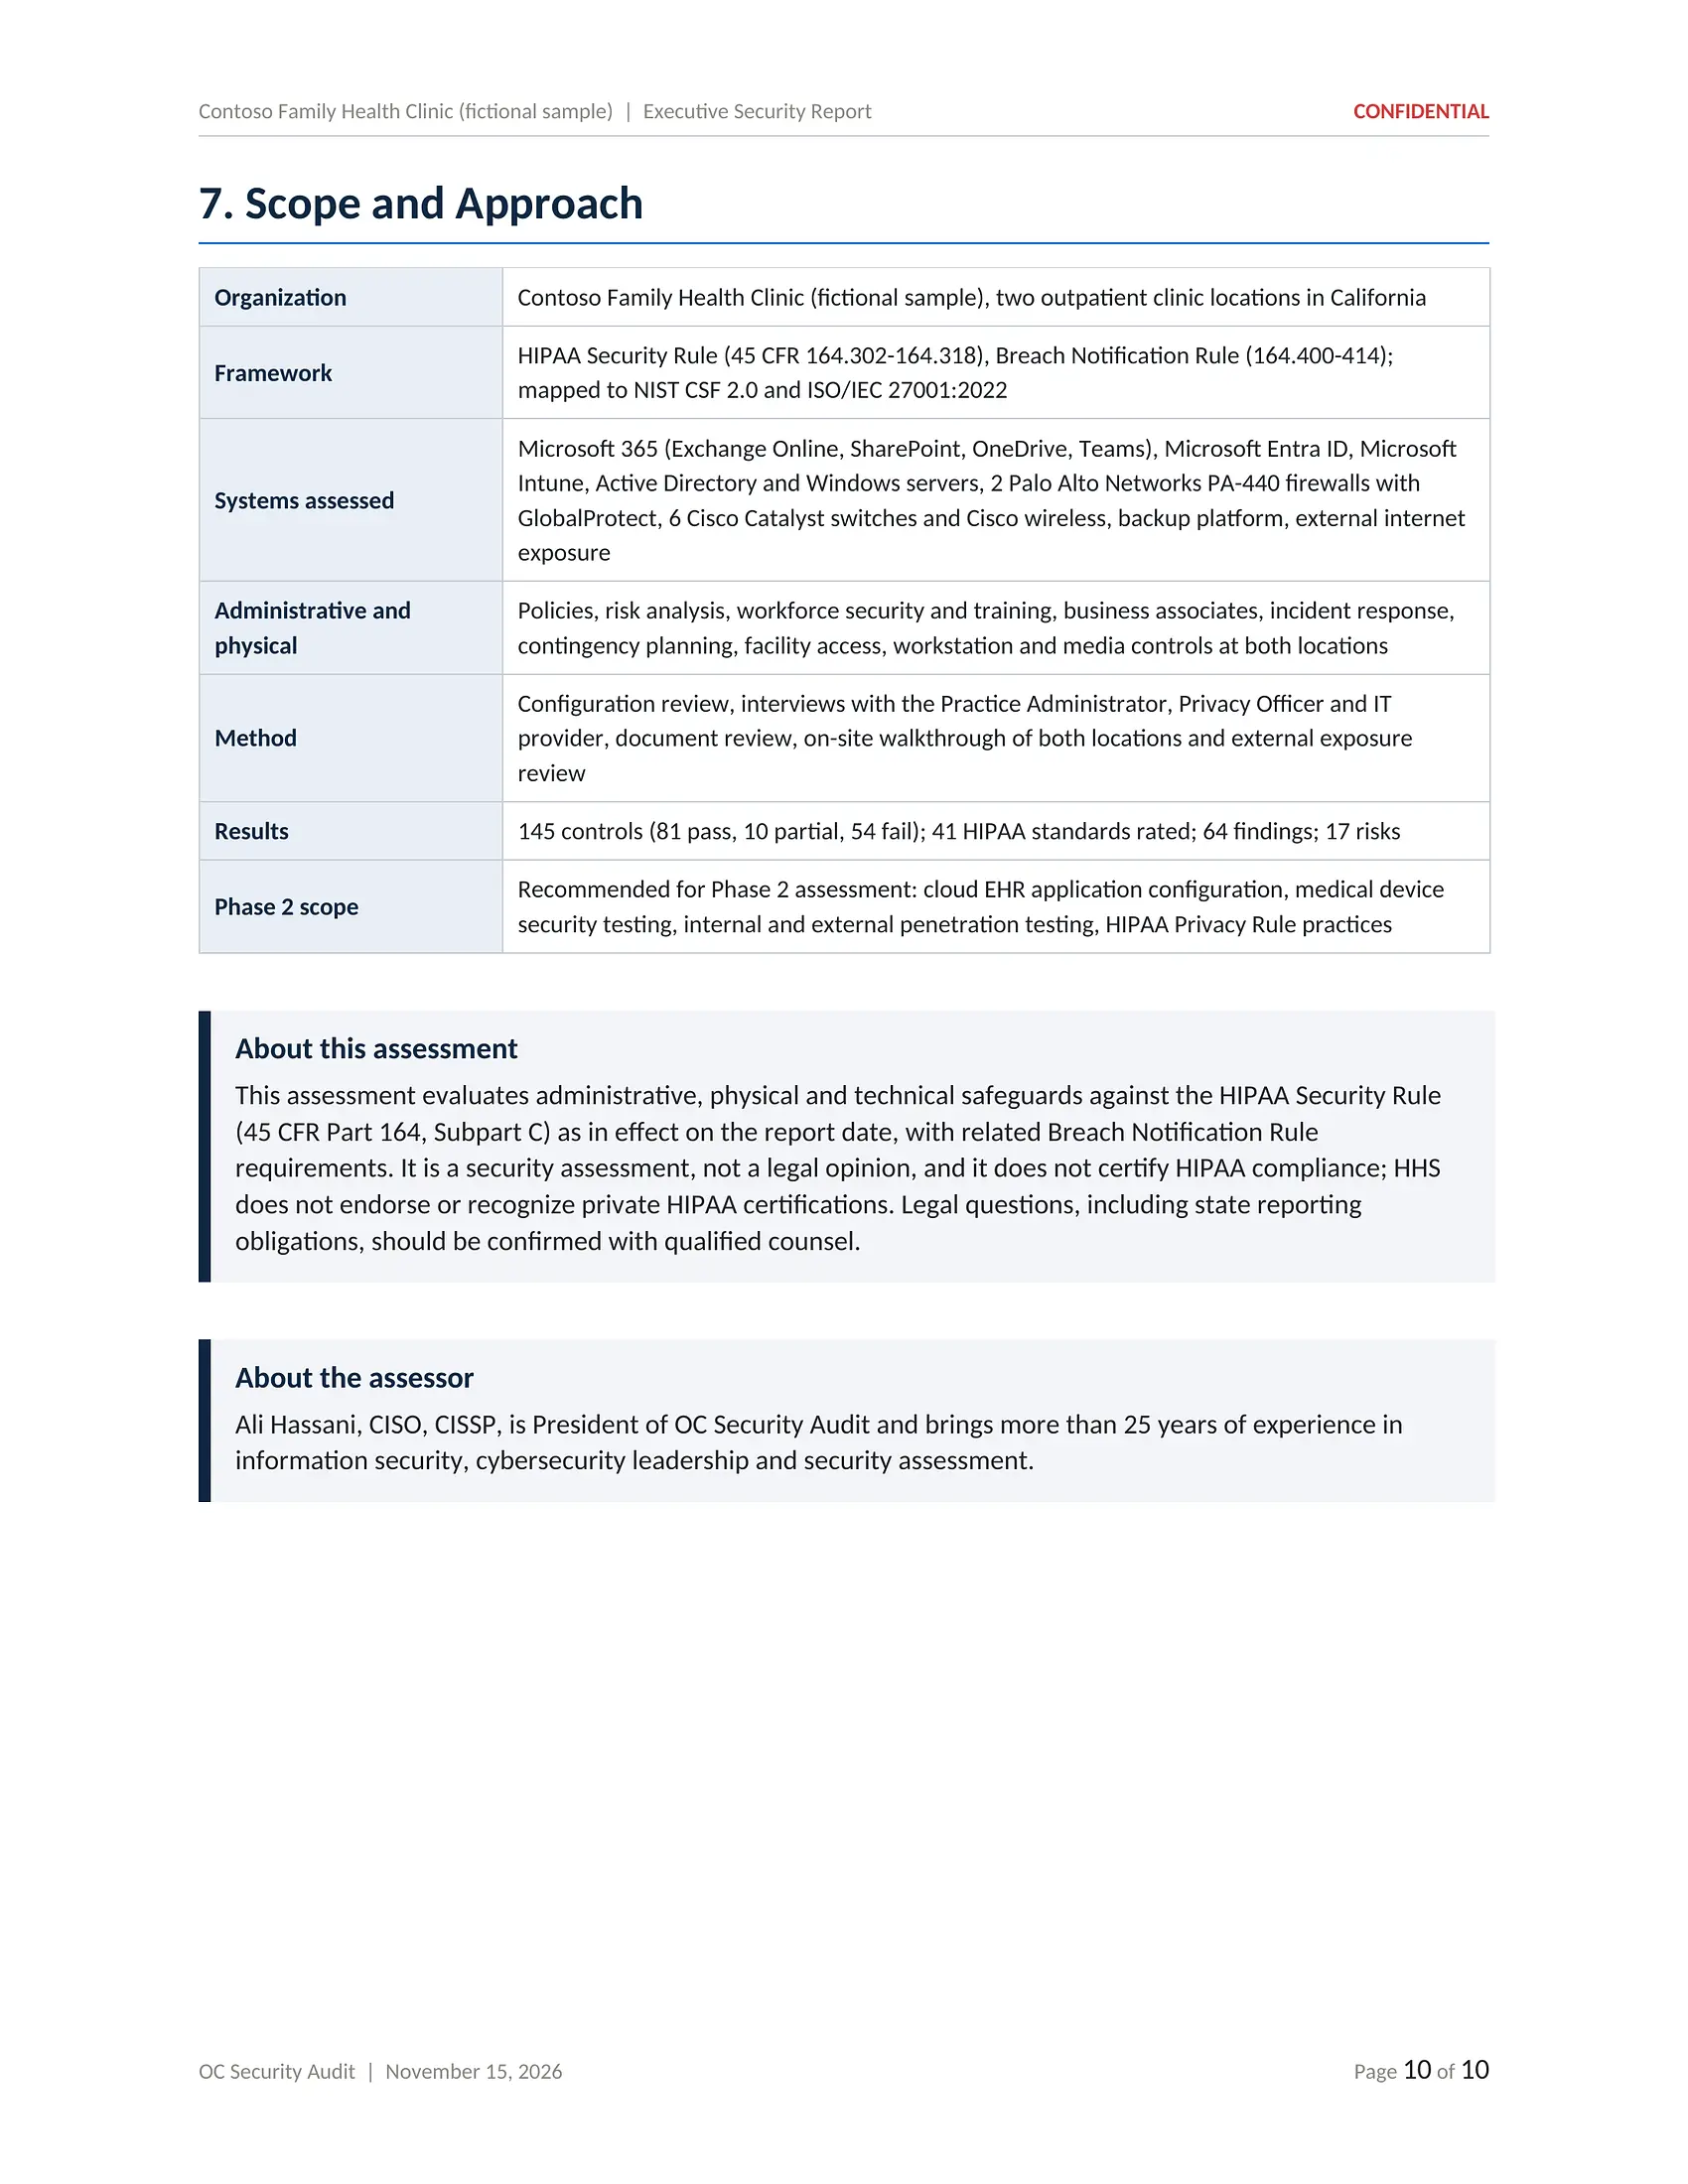
Deliverable 1 of 5 · PDF and Word · 10 pages
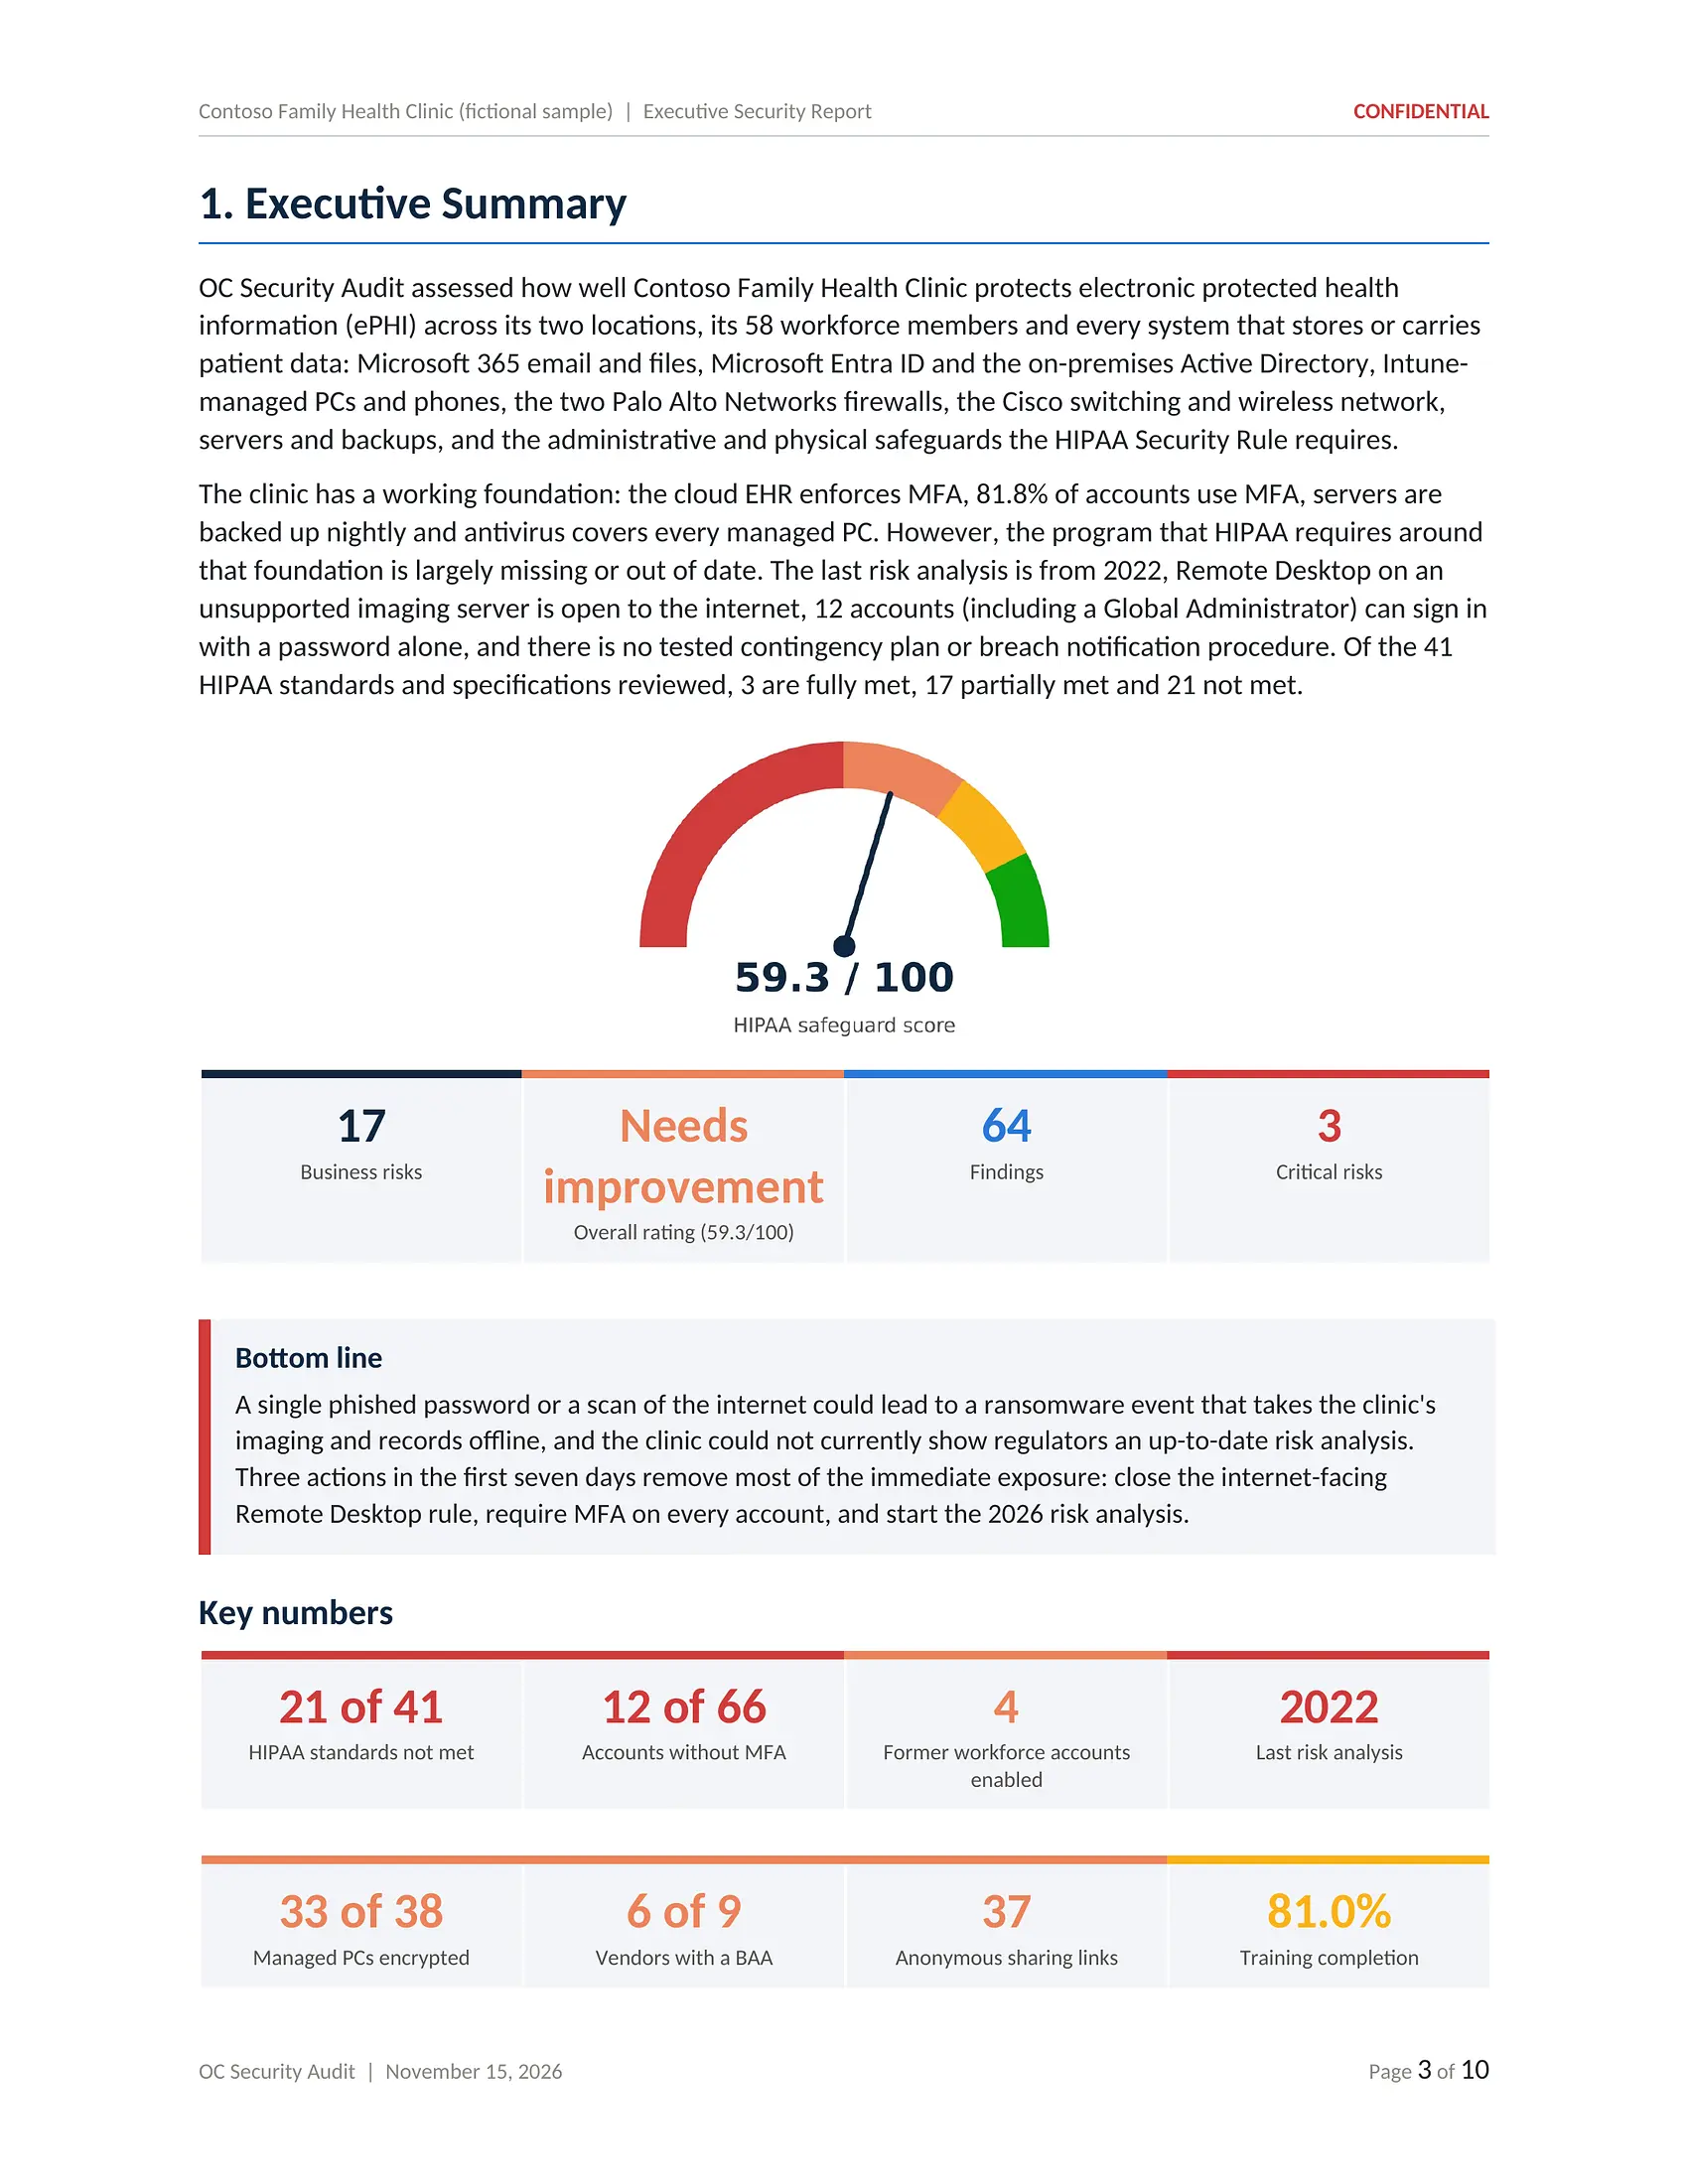
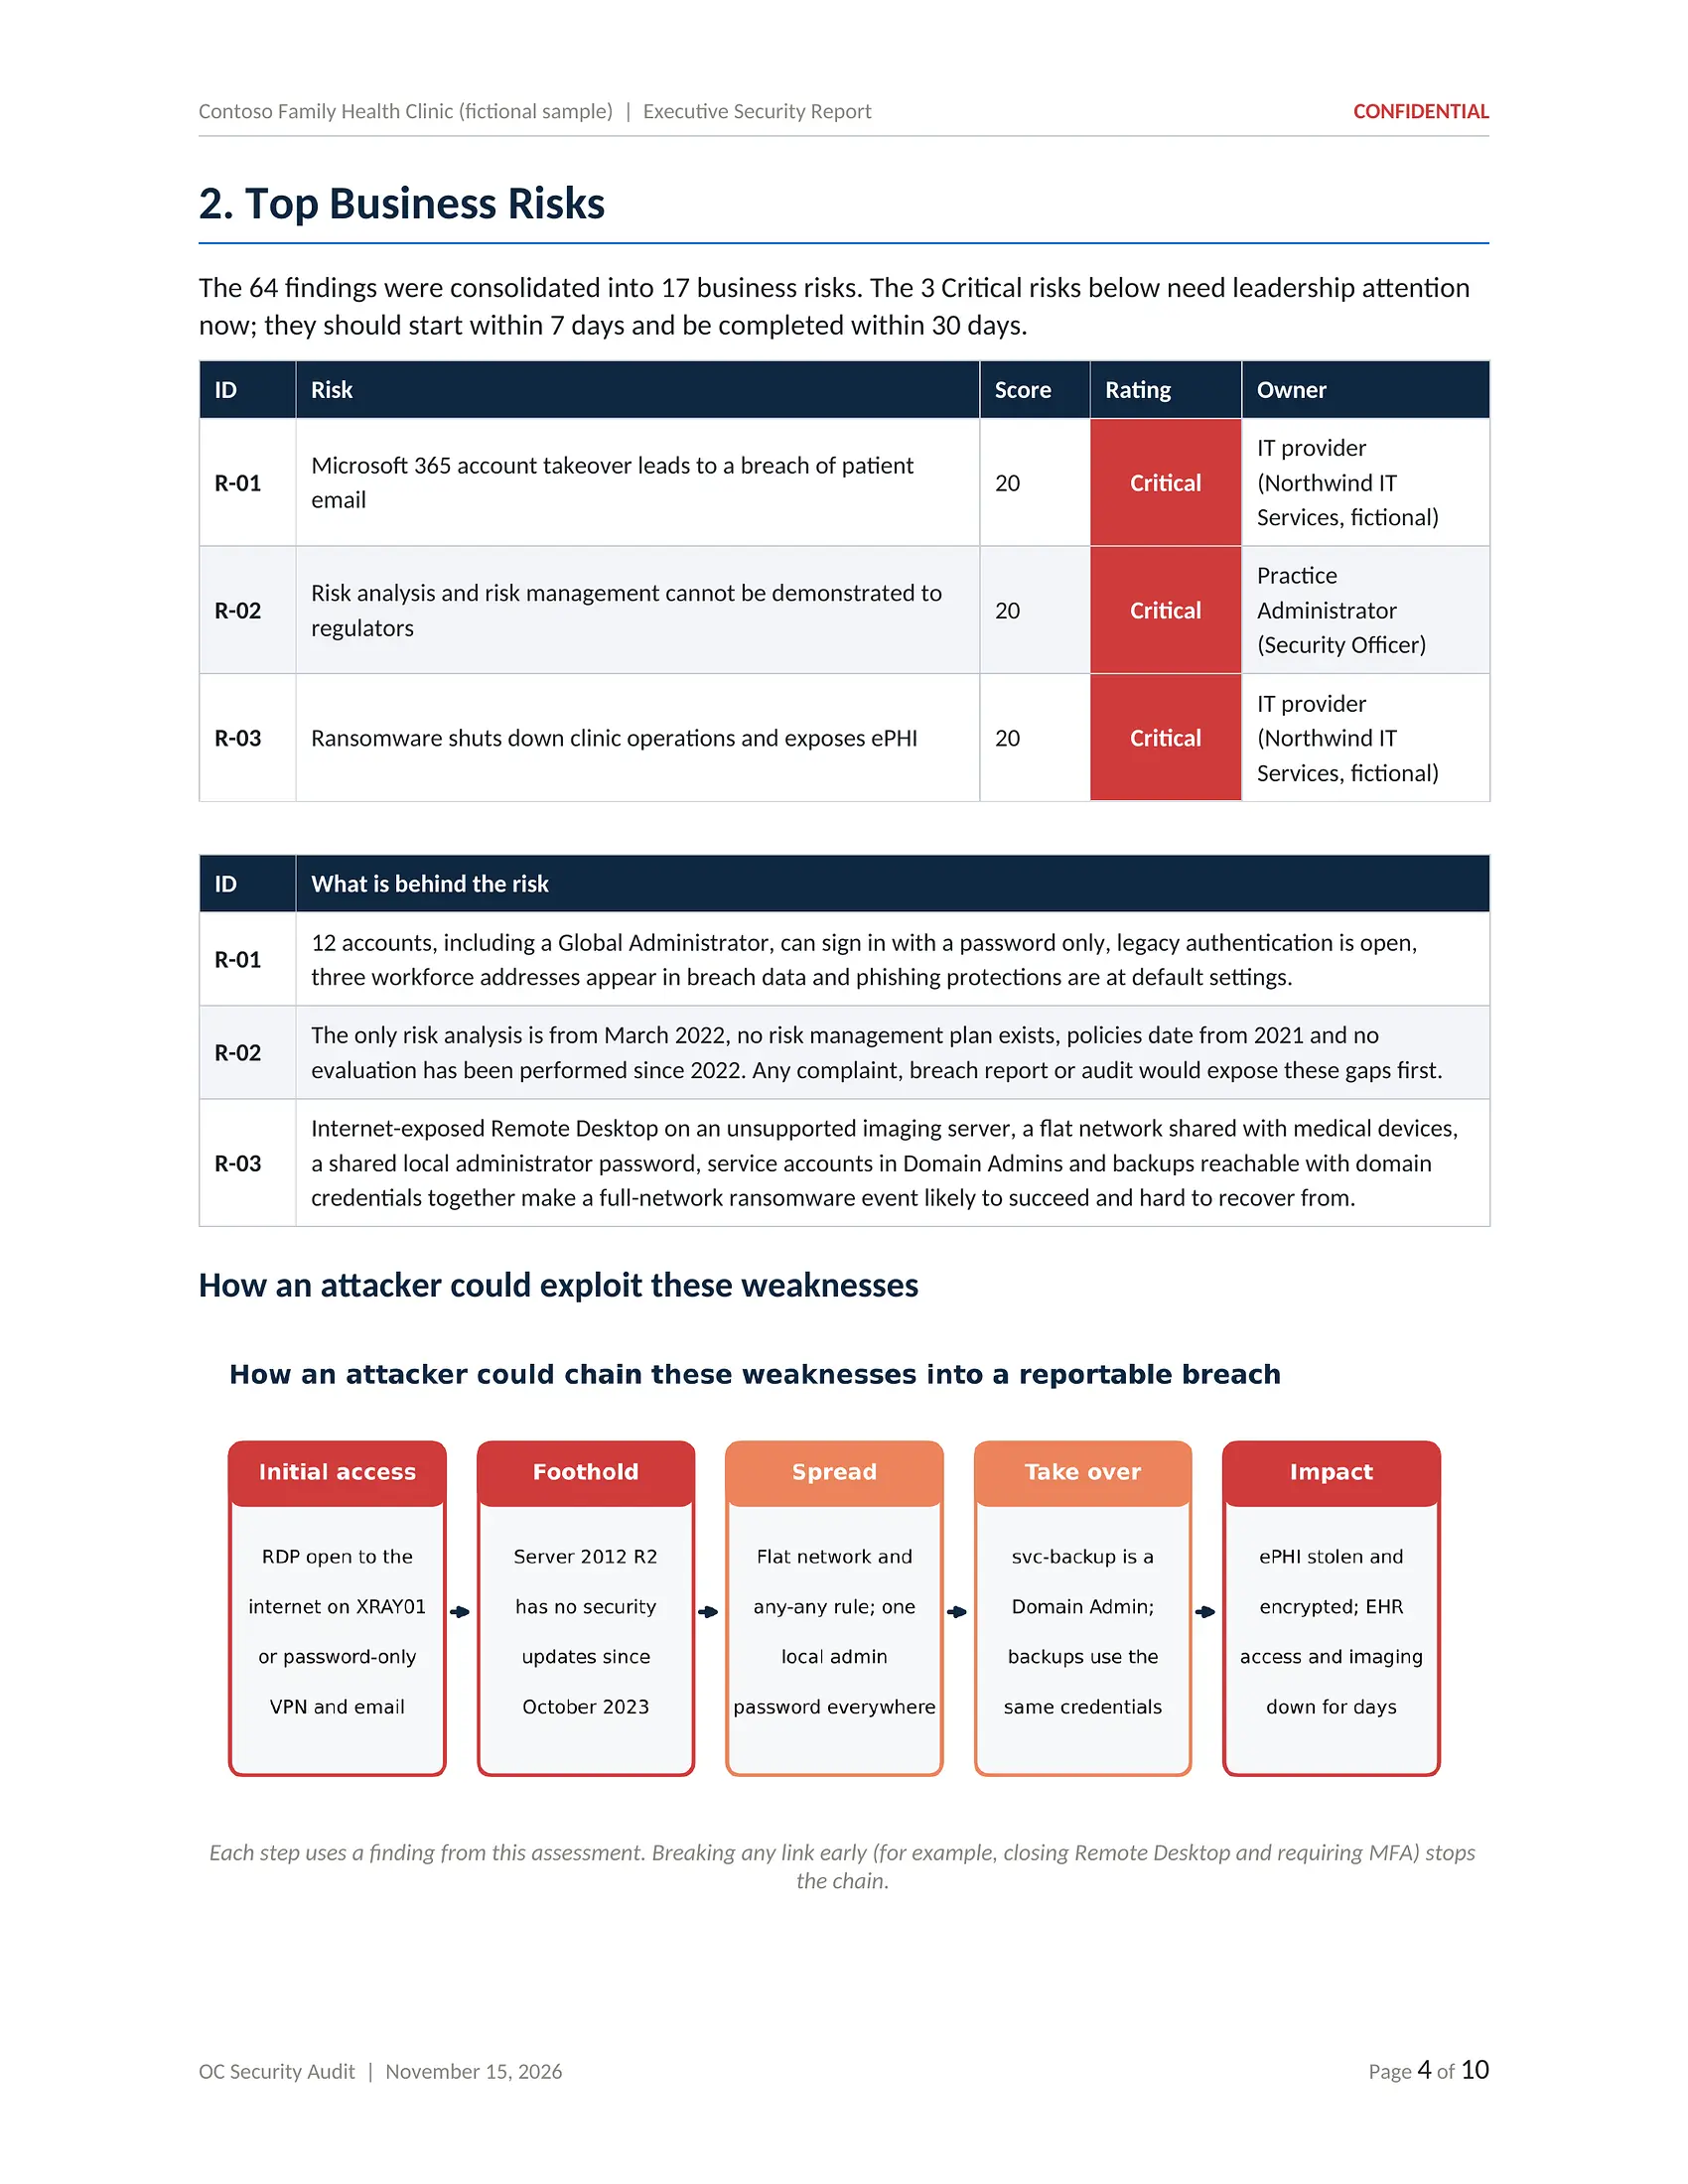
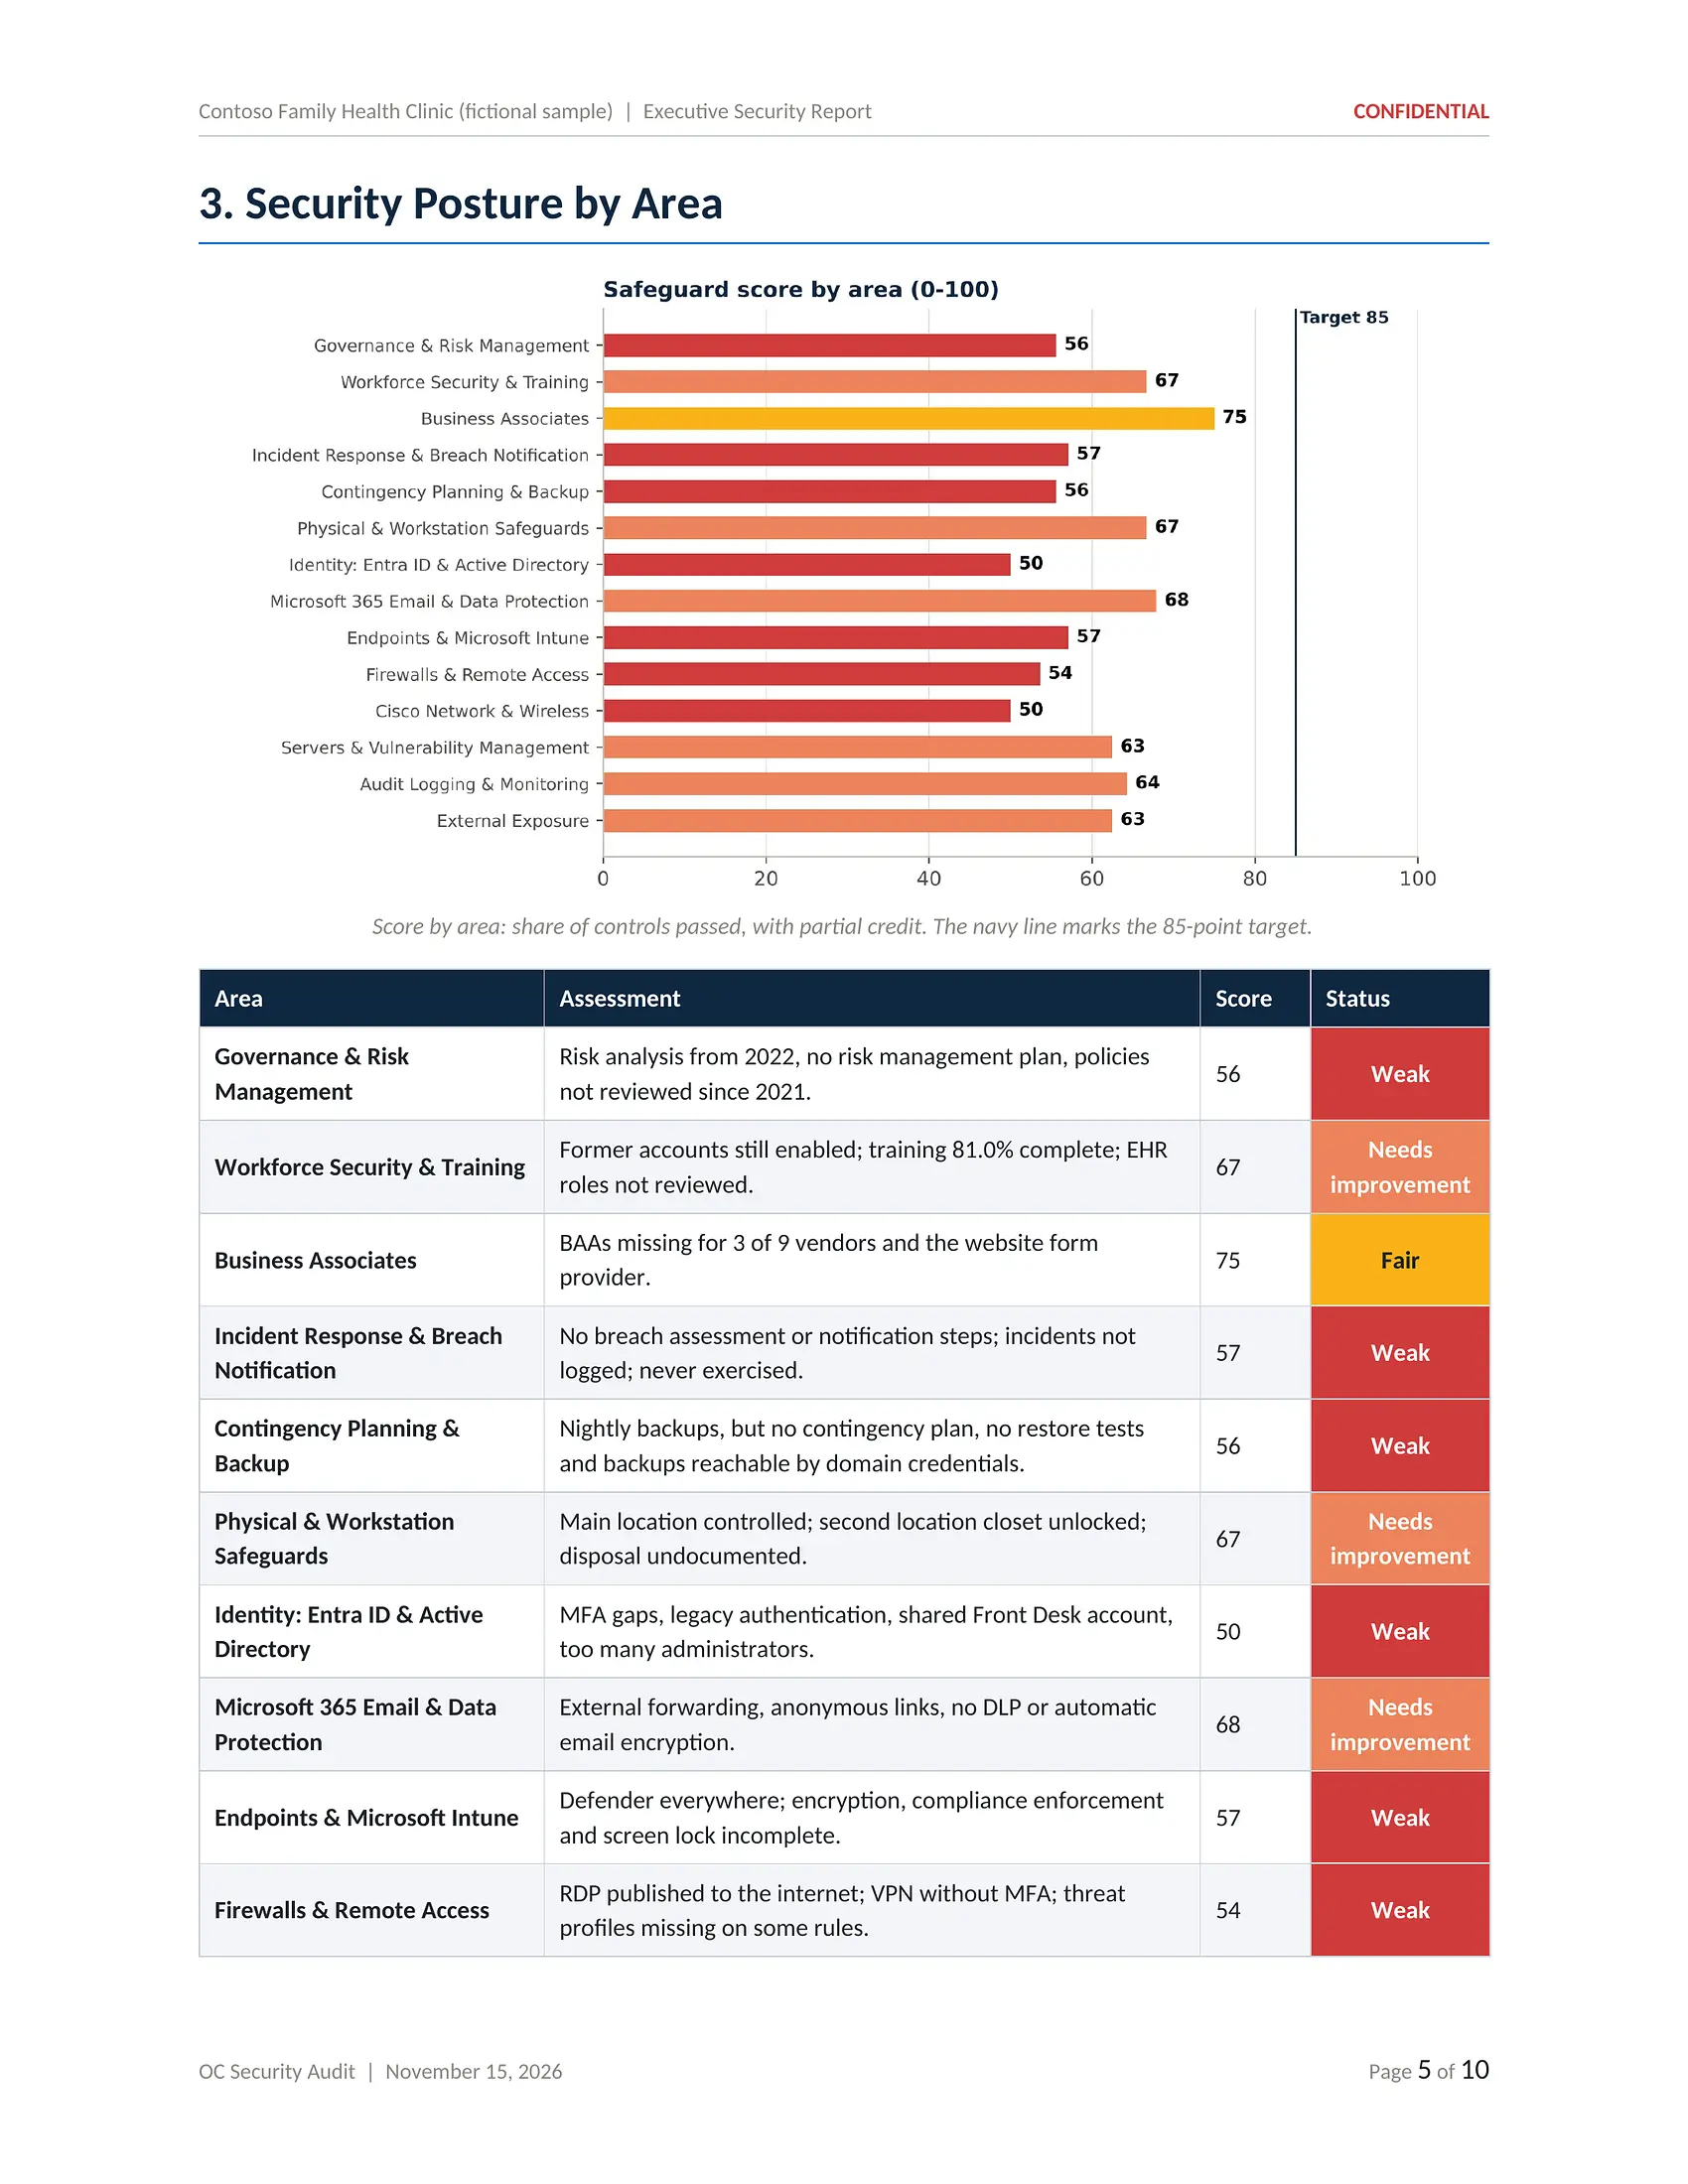
The report leadership reads first. It turns 145 control results into a score, the business risks that matter, the decisions the owners need to make and a 180-day plan, written so a practice owner can act on it without a technical background.
Who uses it
Practice owner, physicians and partners, practice administrator, HIPAA Security Officer and Privacy Officer.
What is included
SAMPLE · Contoso Family Health Clinic (fictional)
1 / 9
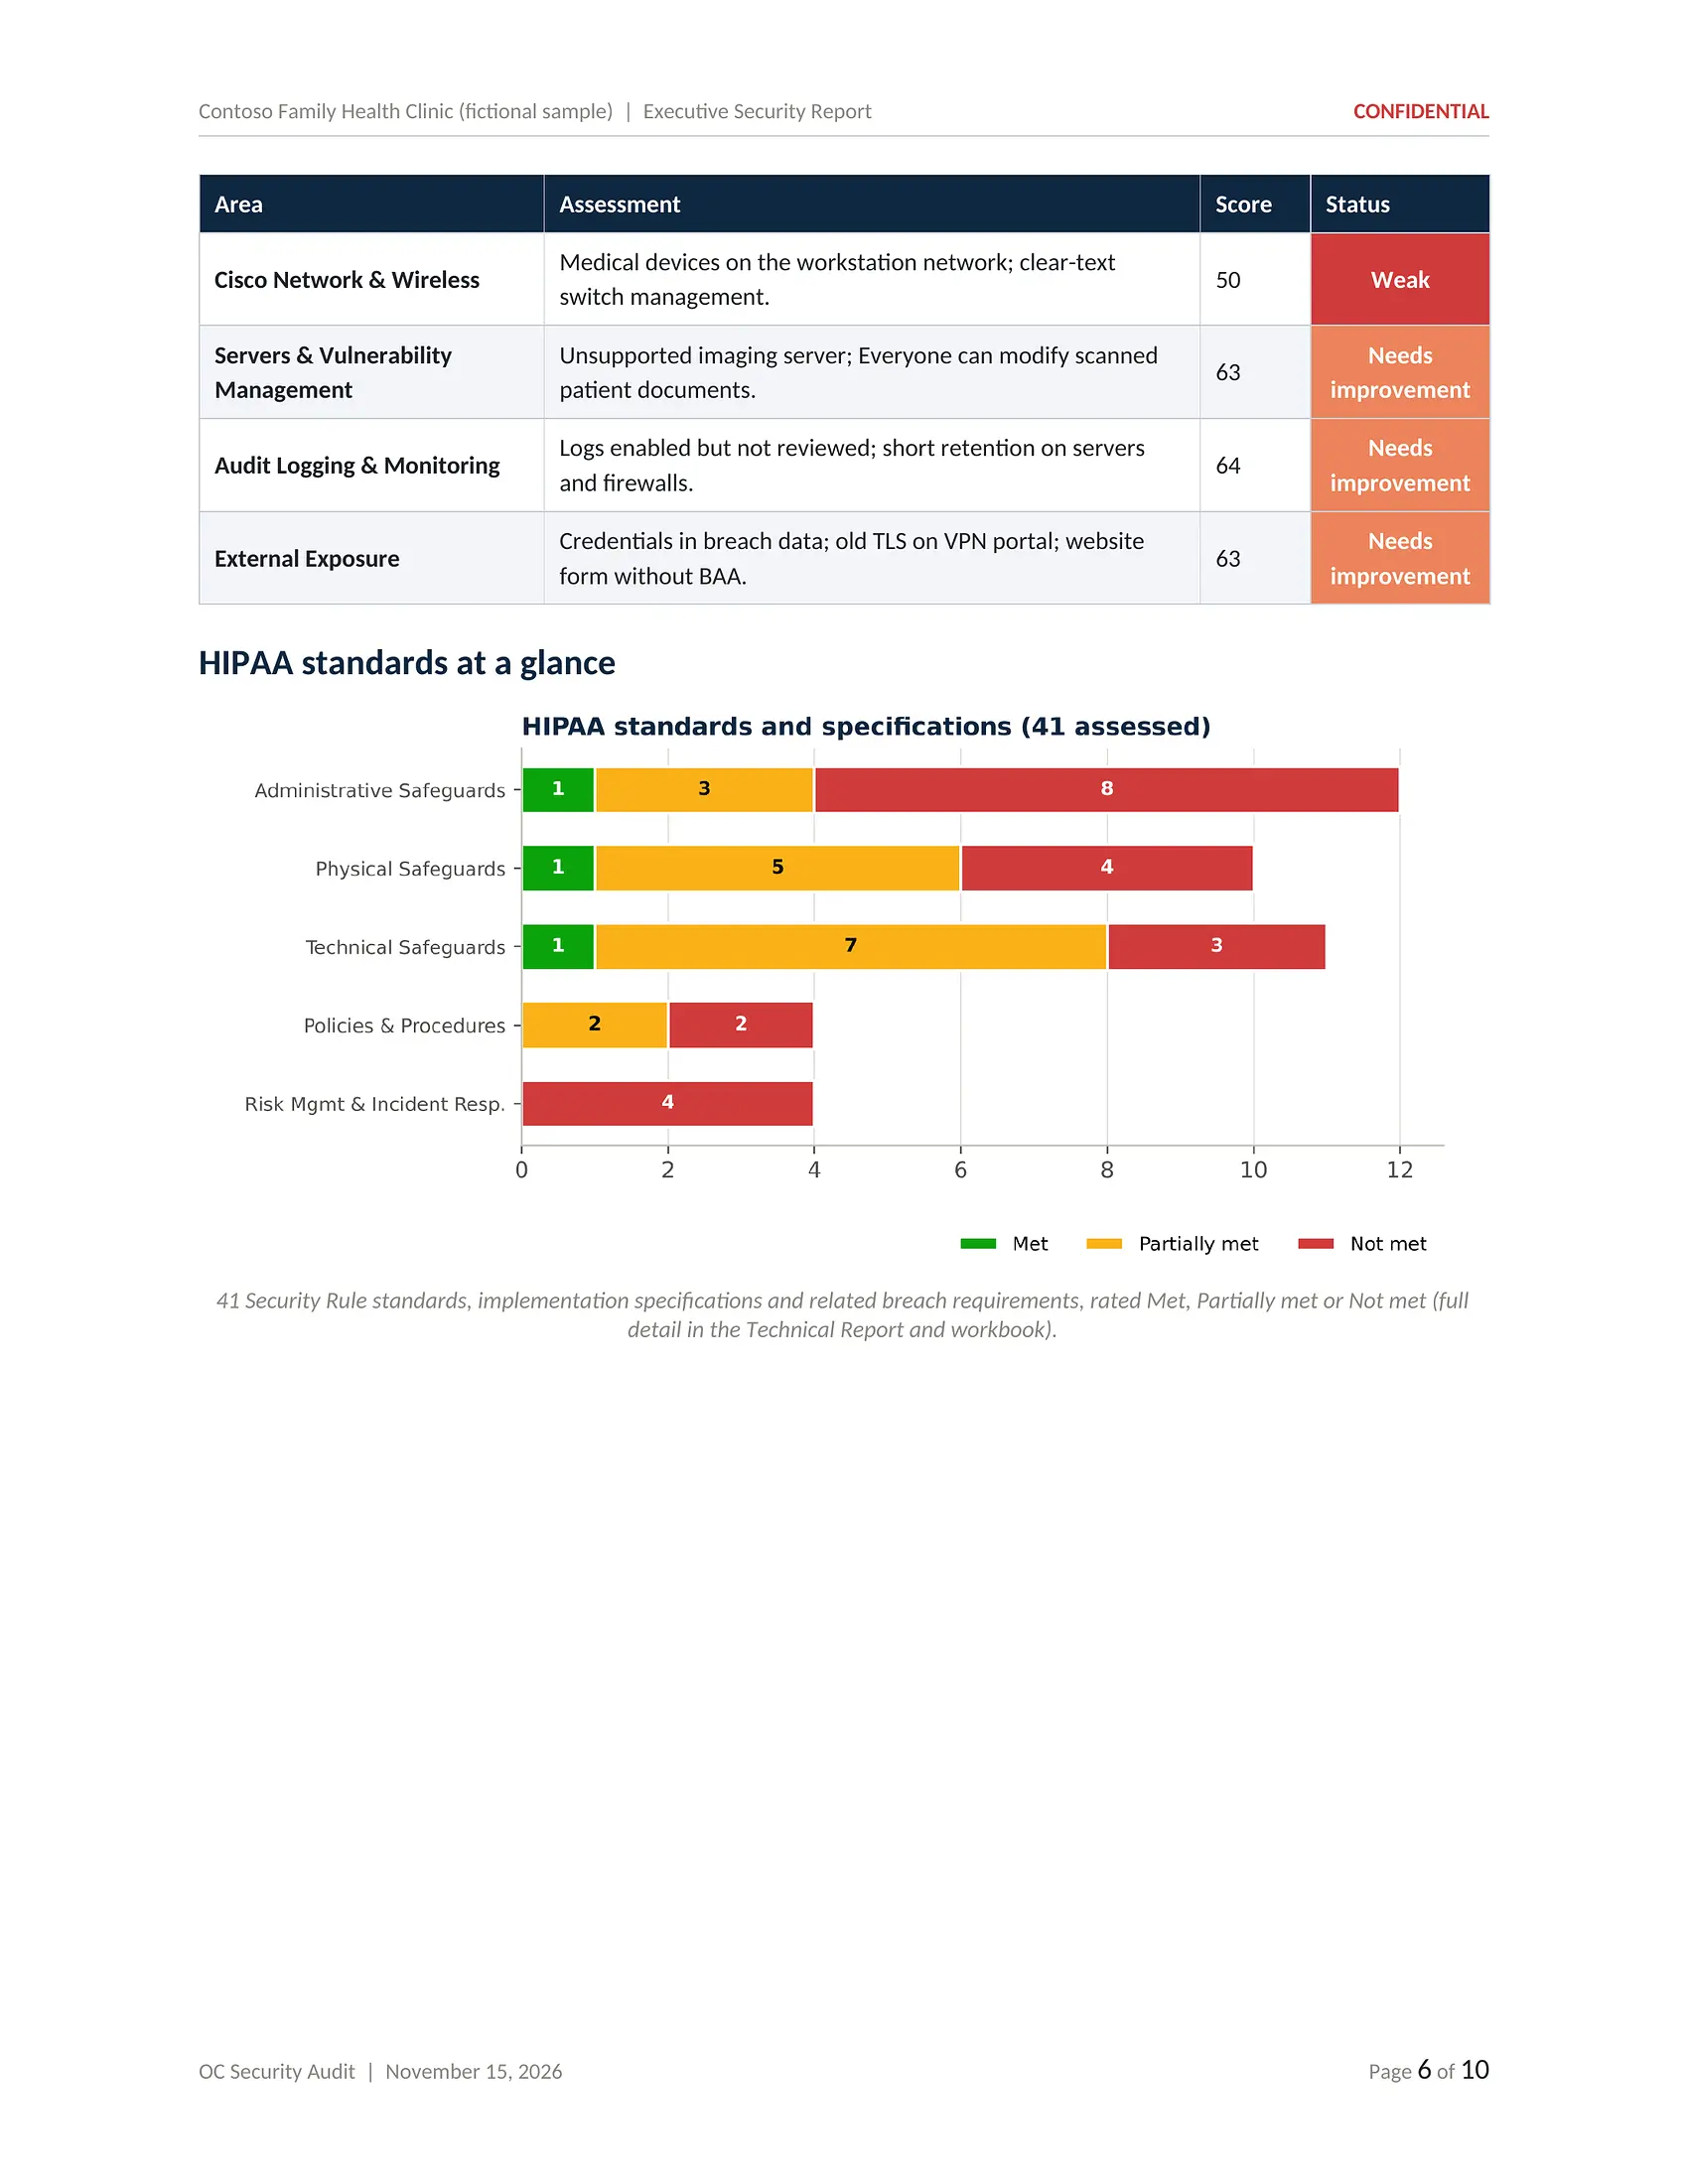
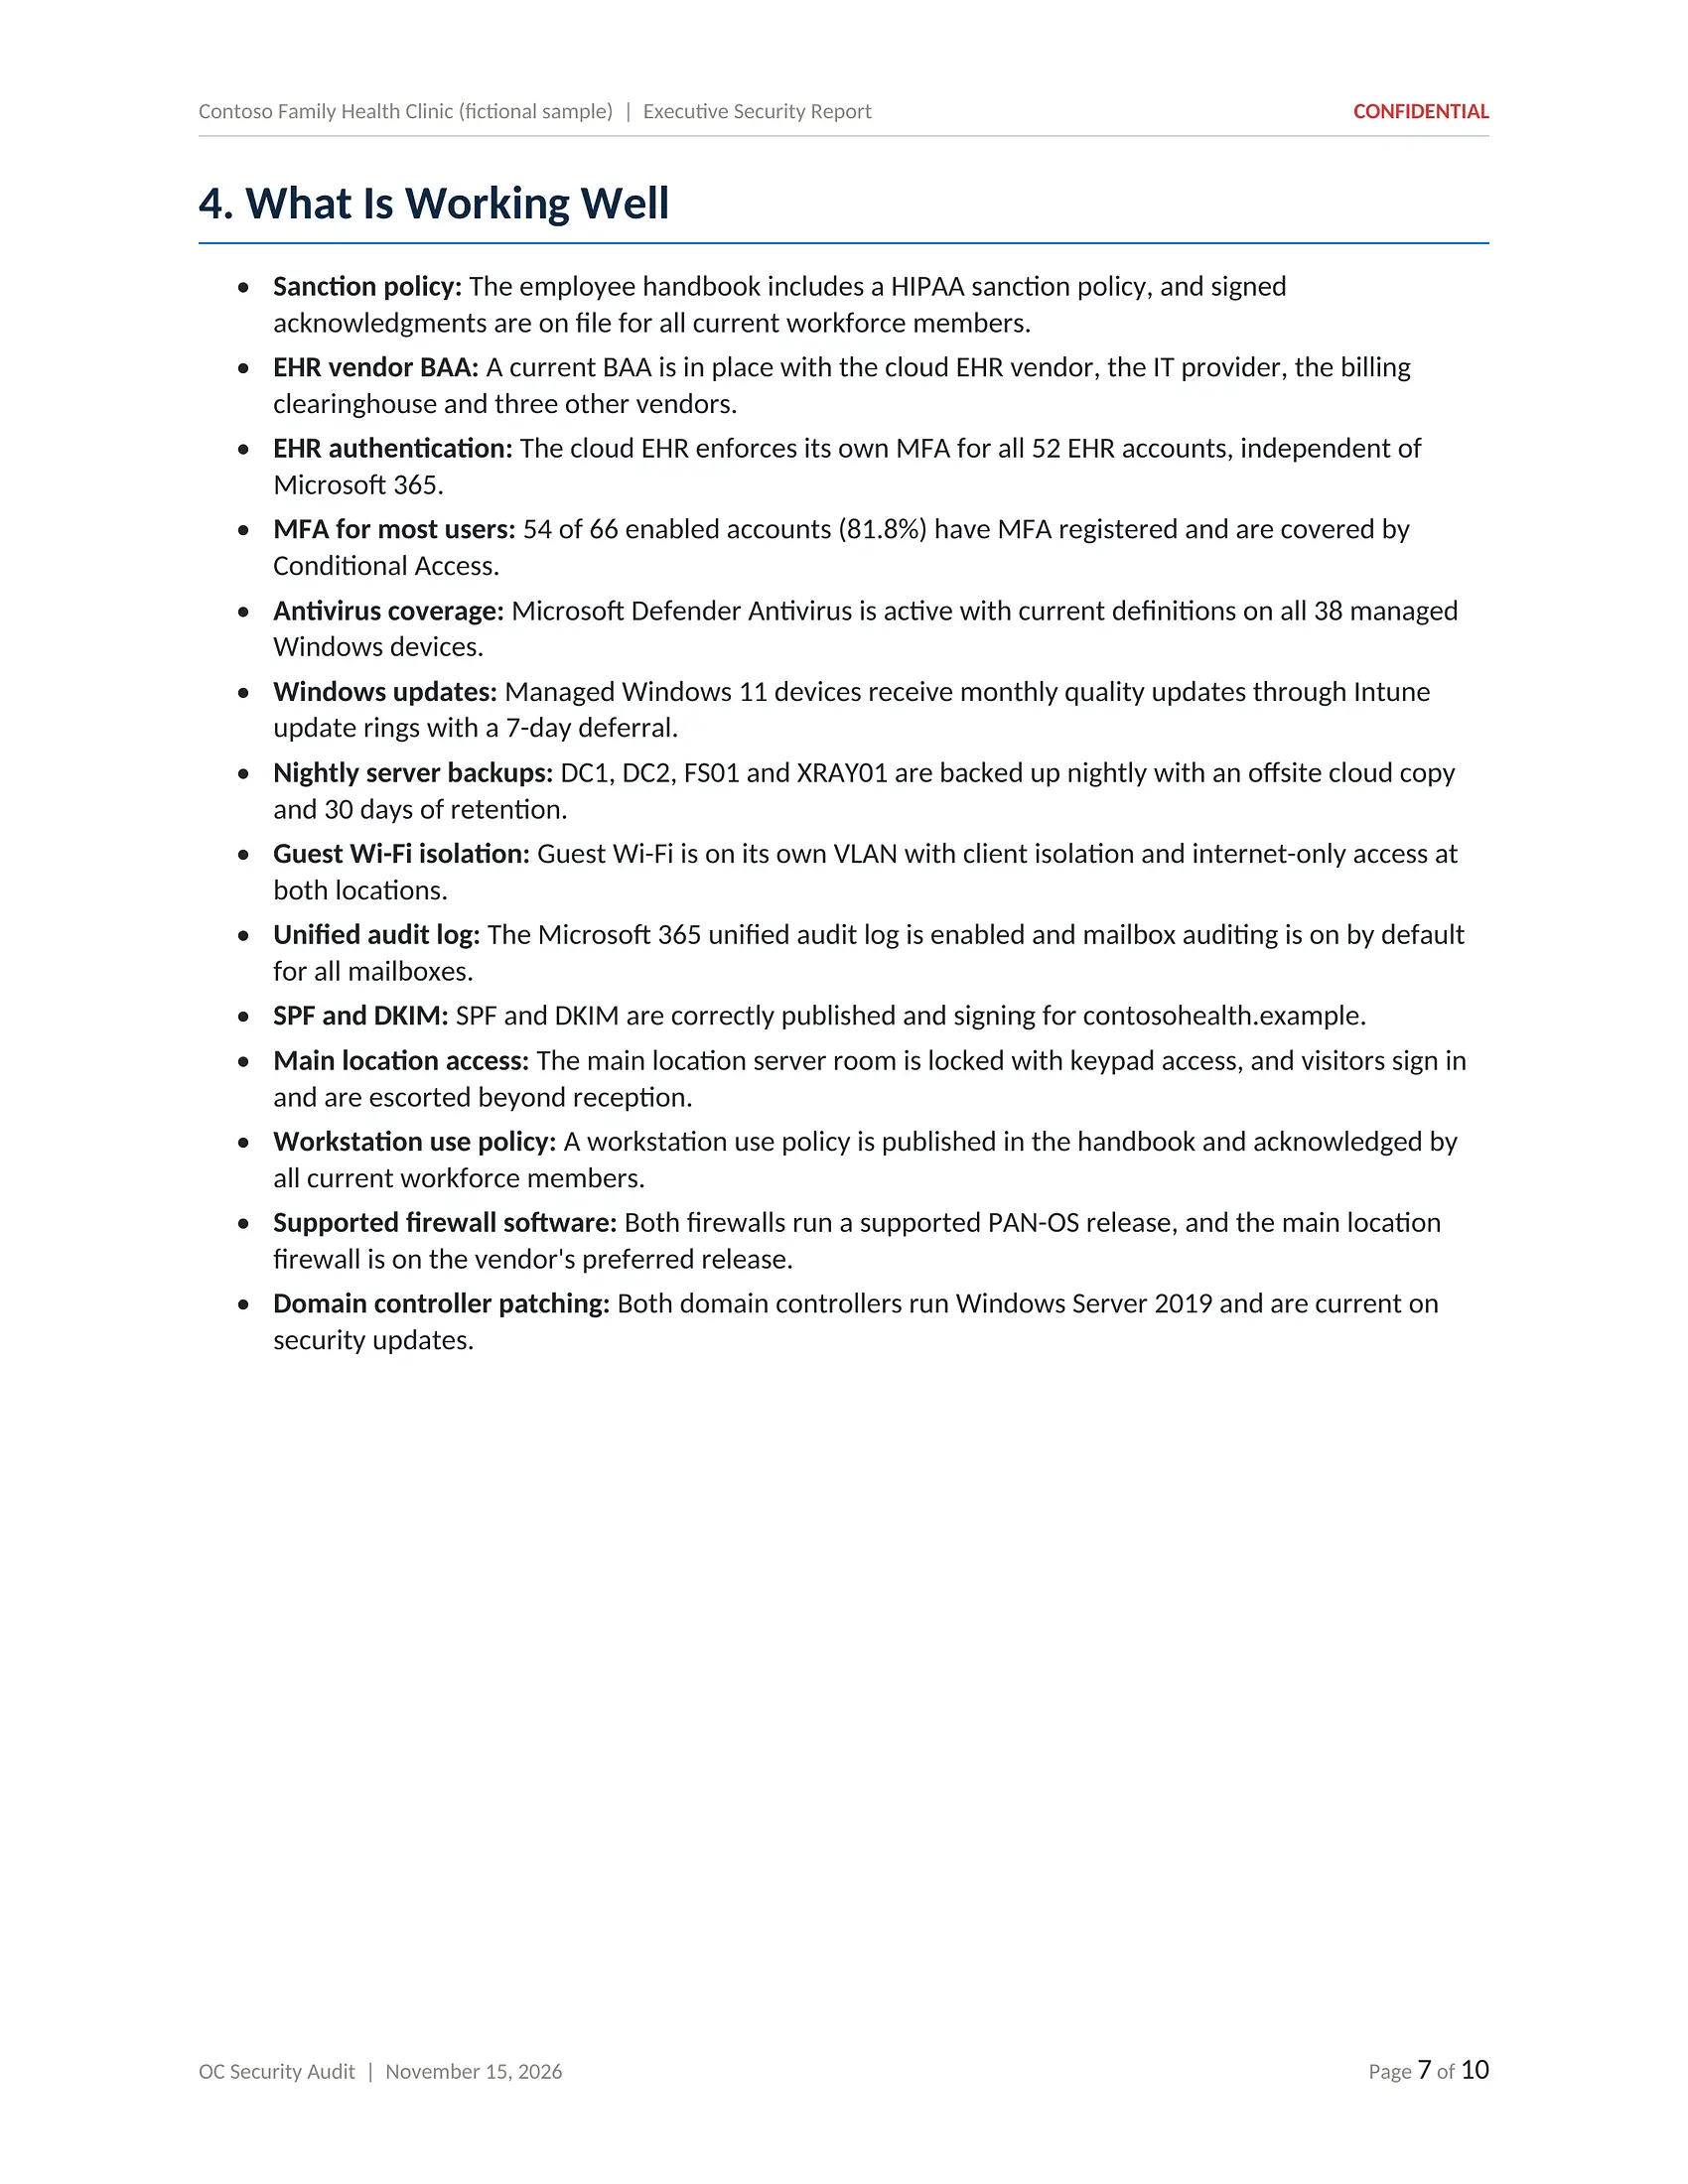
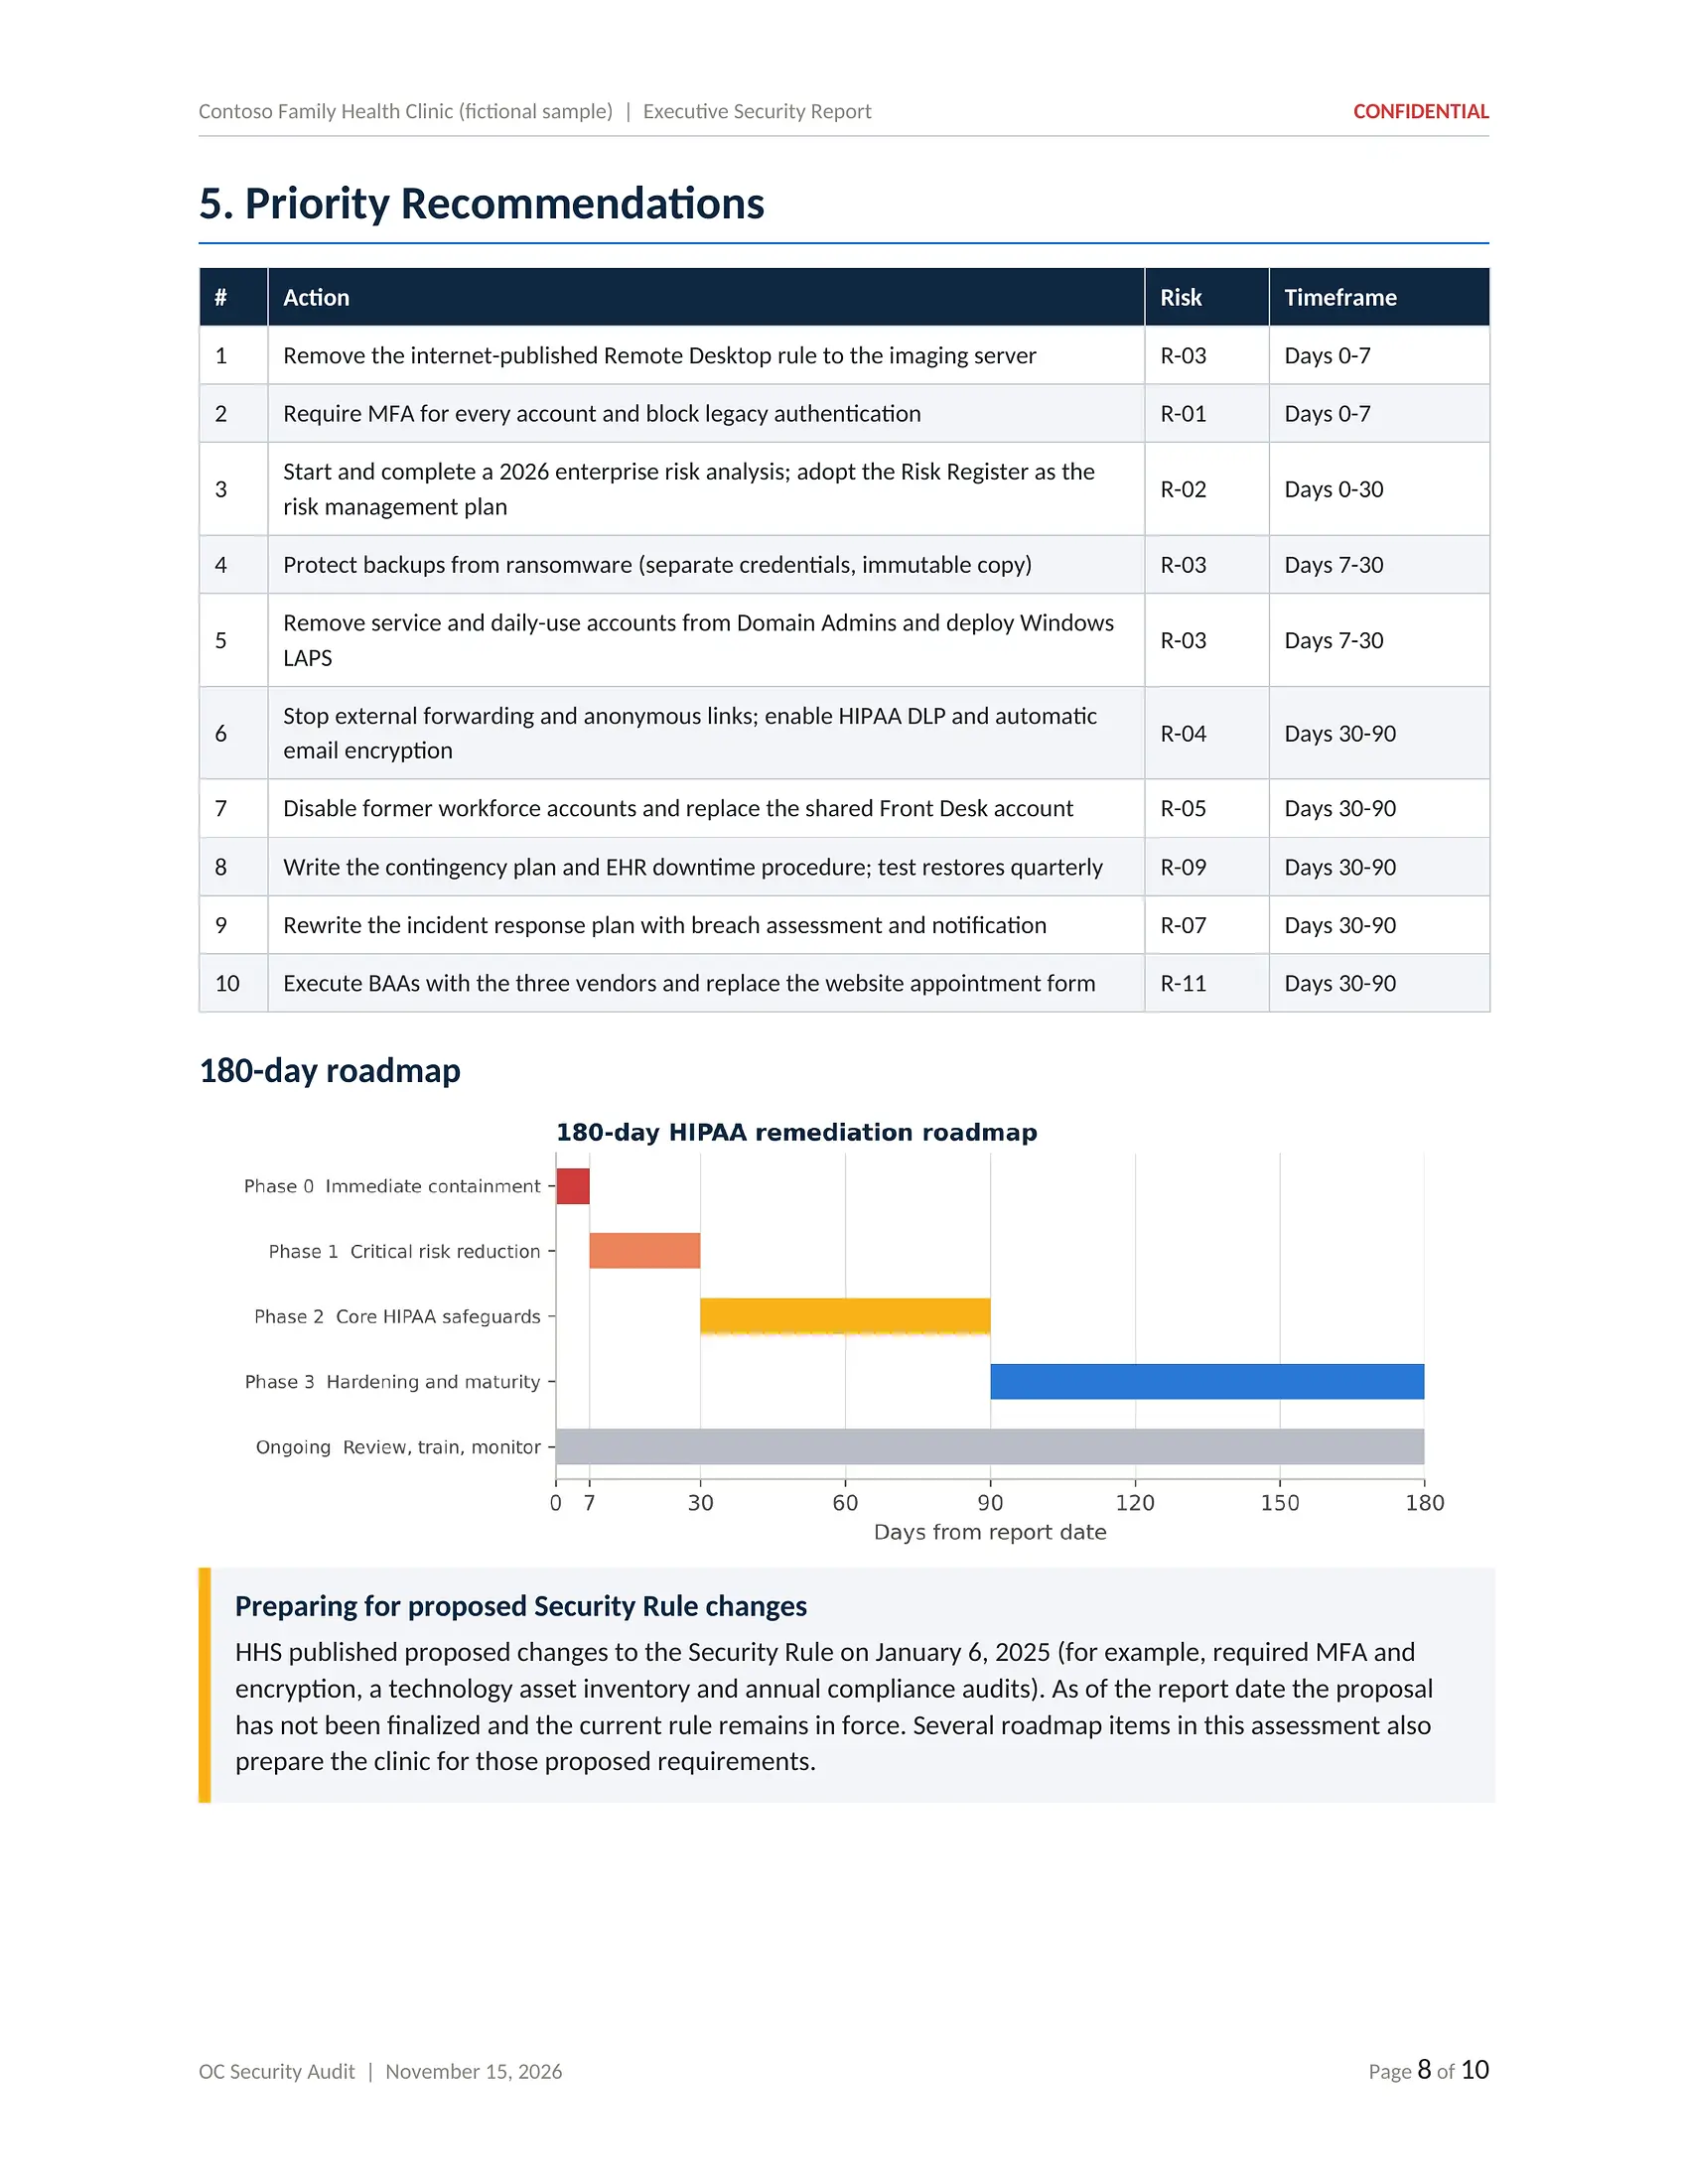
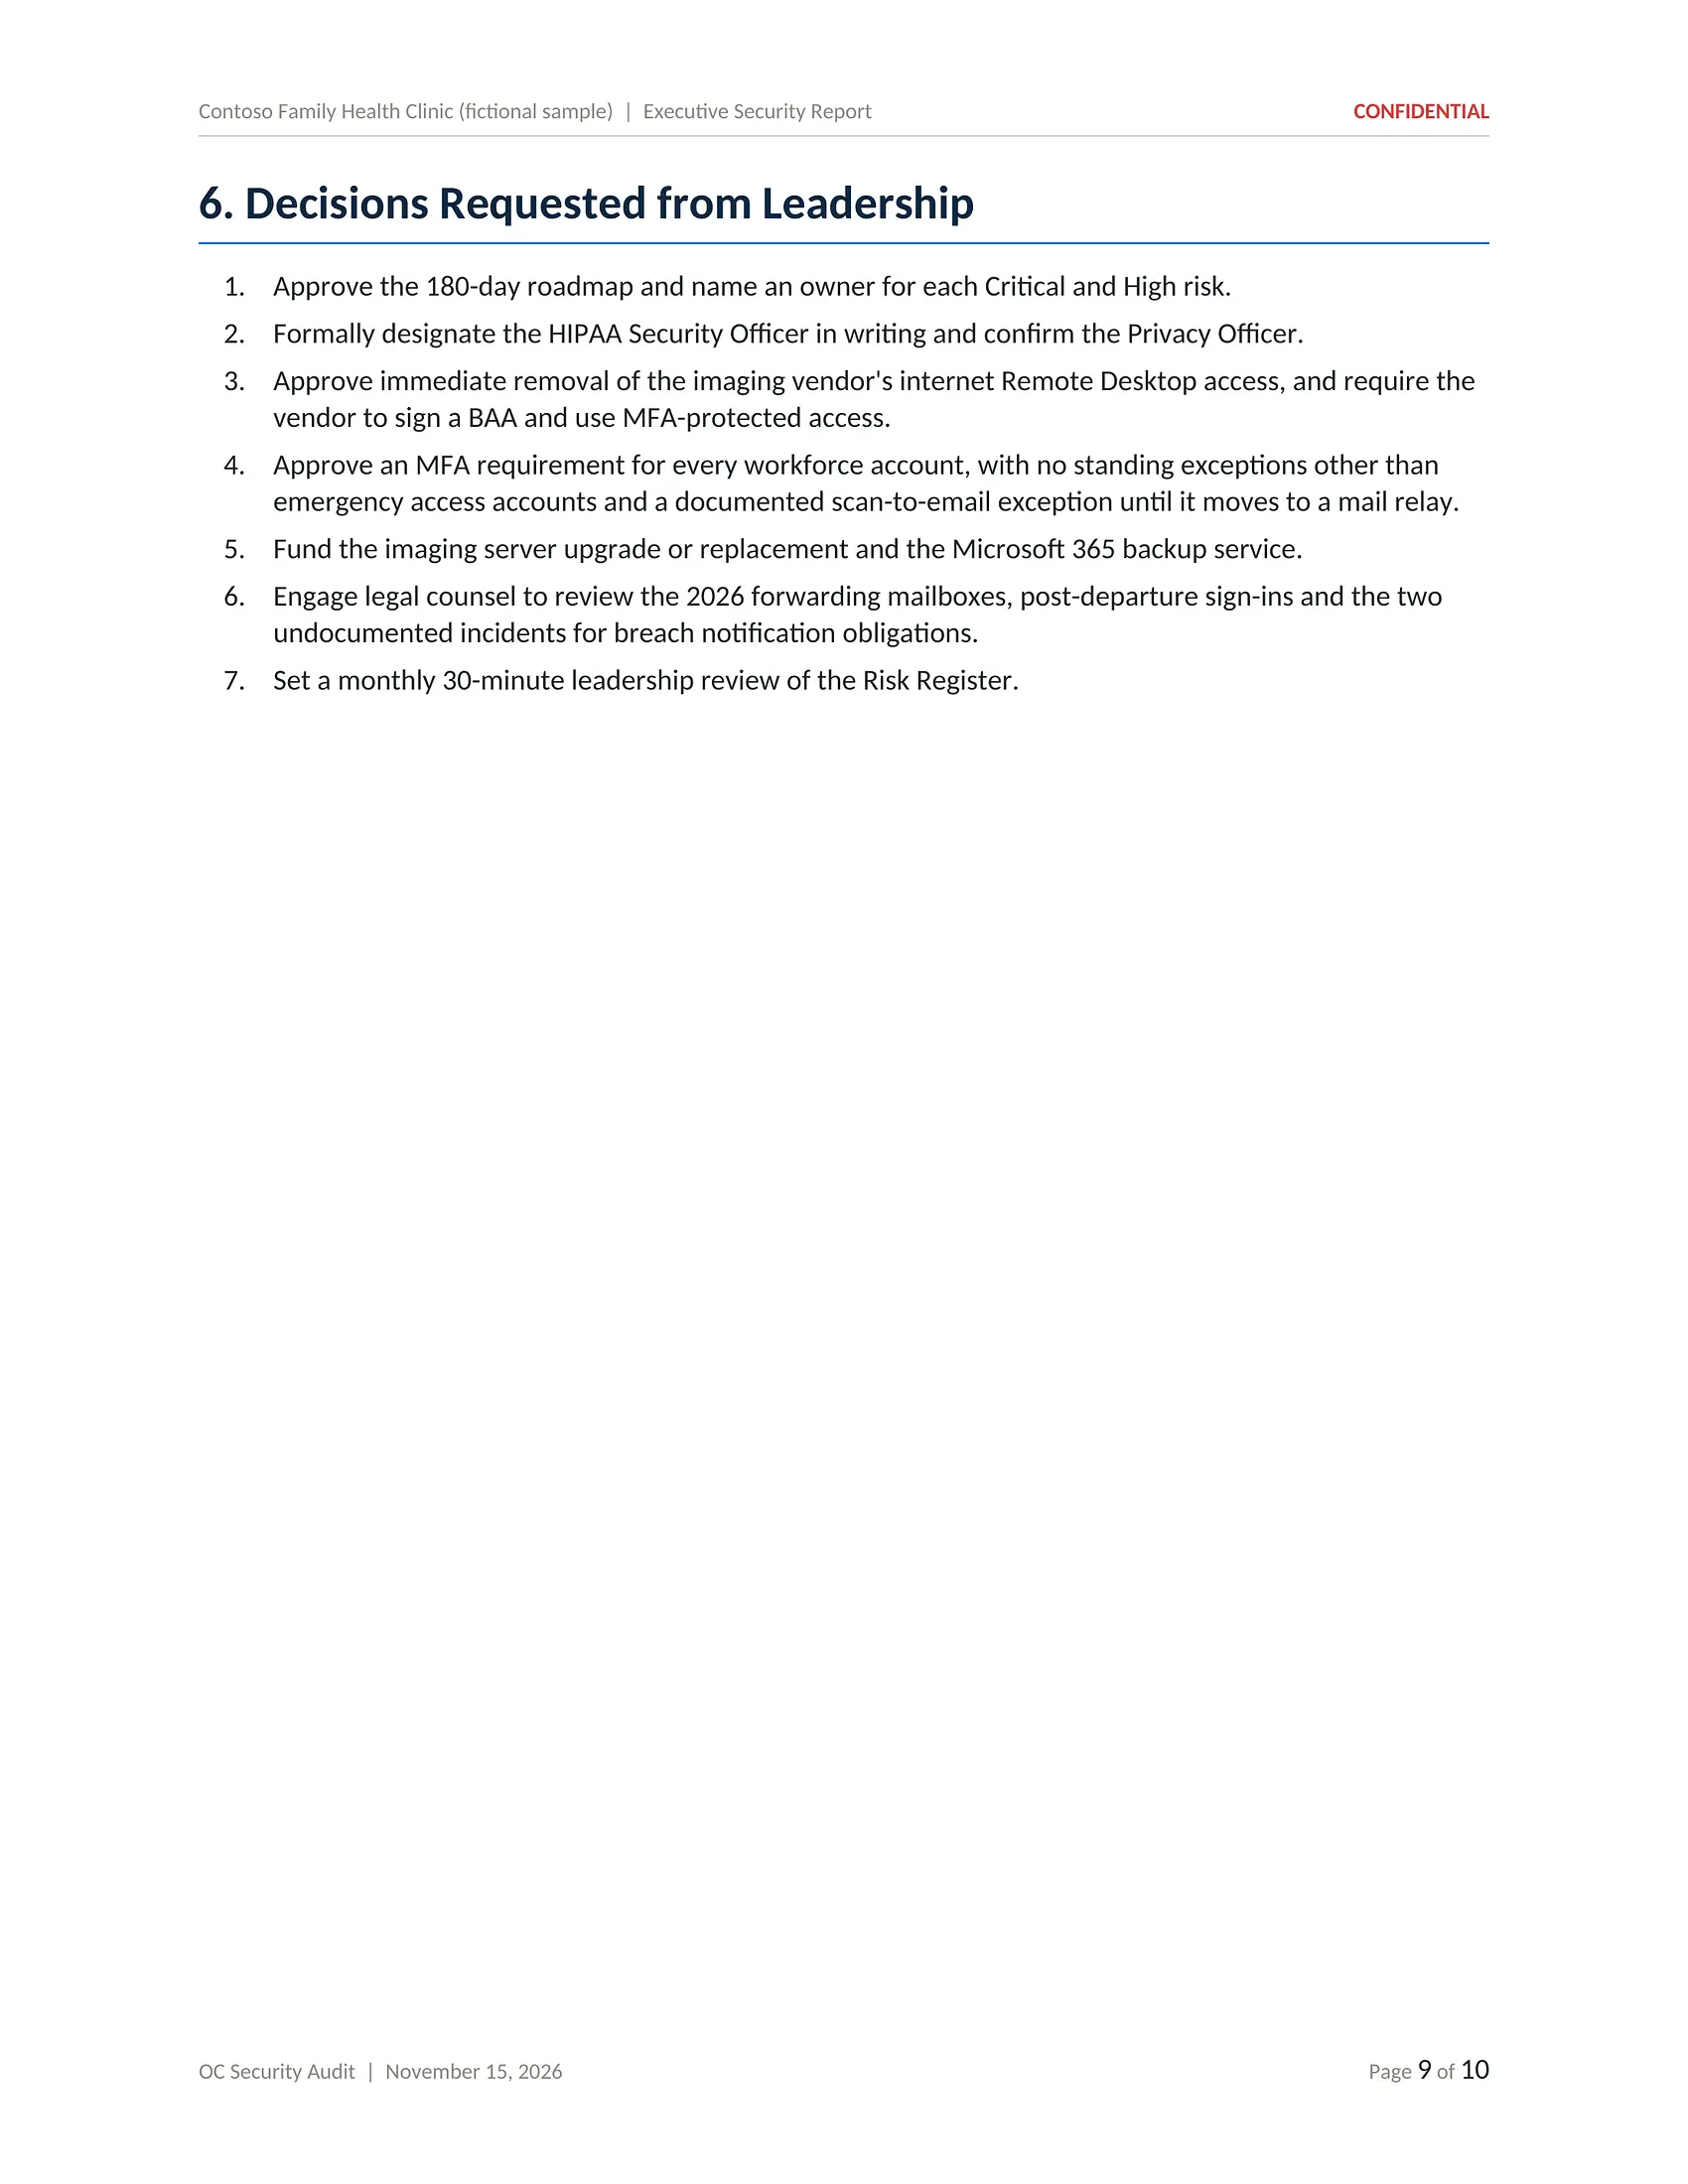
Click the page in the centre to open it full size and zoom in.
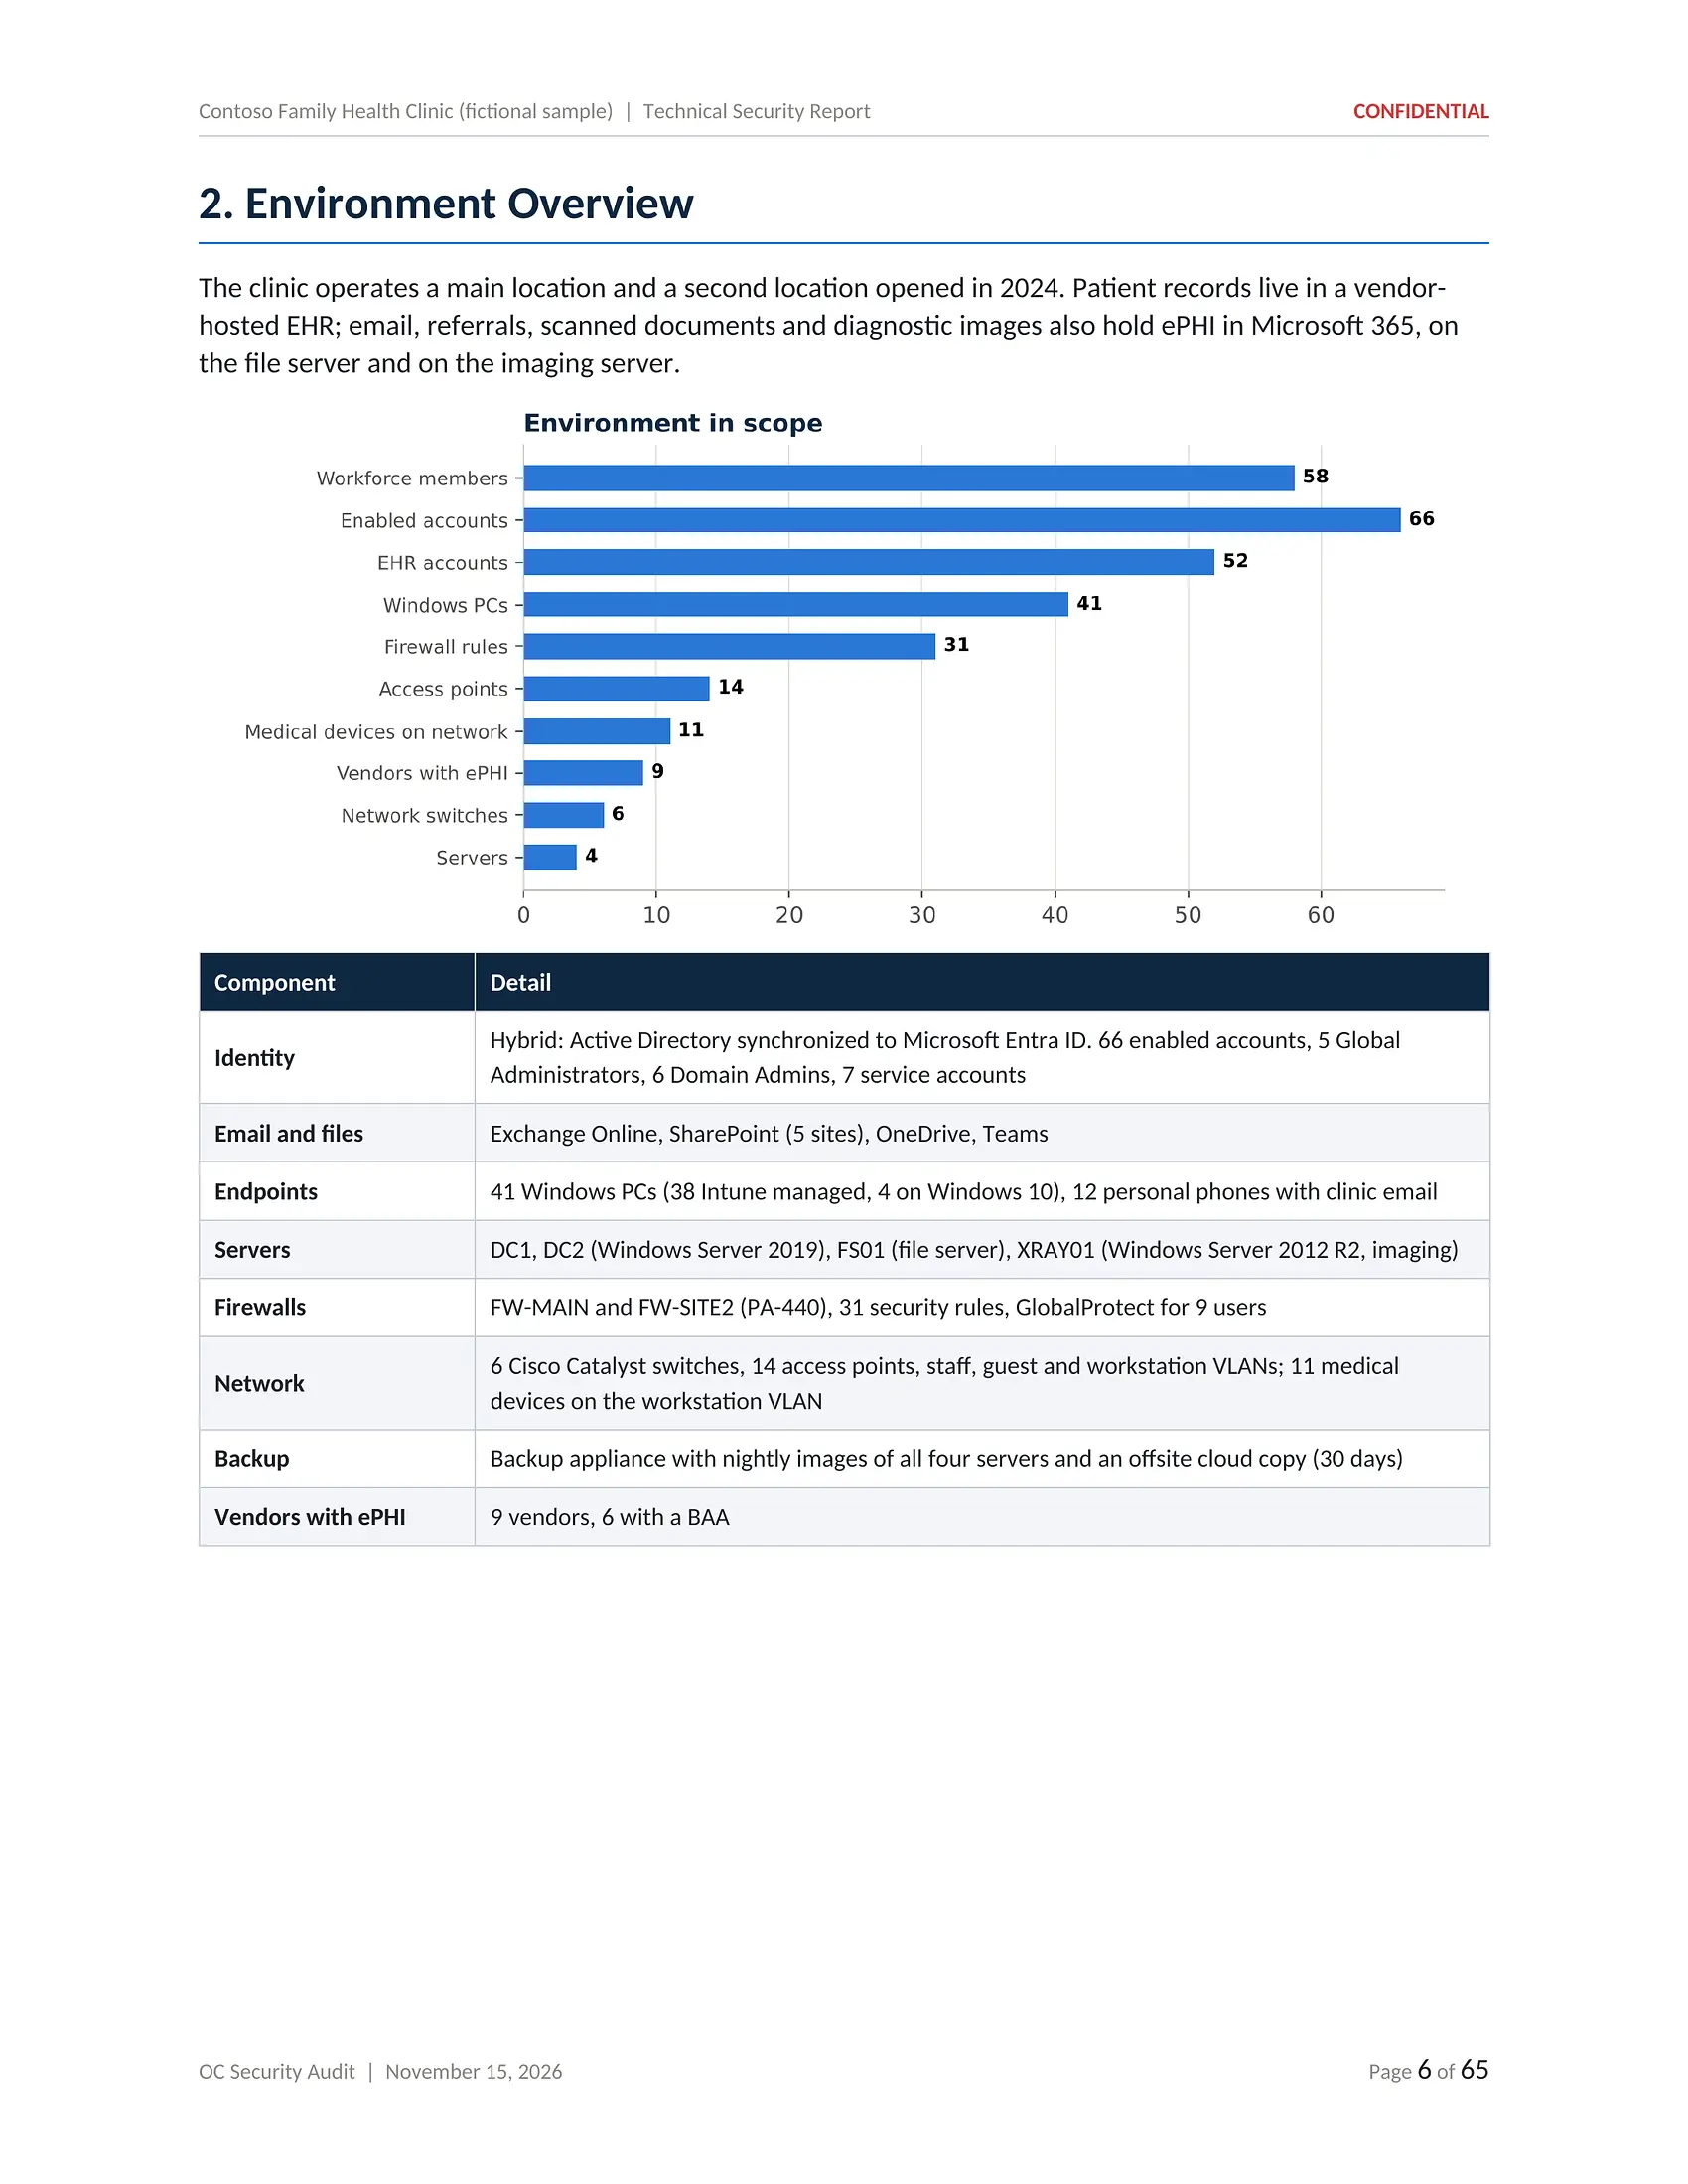
Deliverable 2 of 5 · PDF and Word · 65 pages
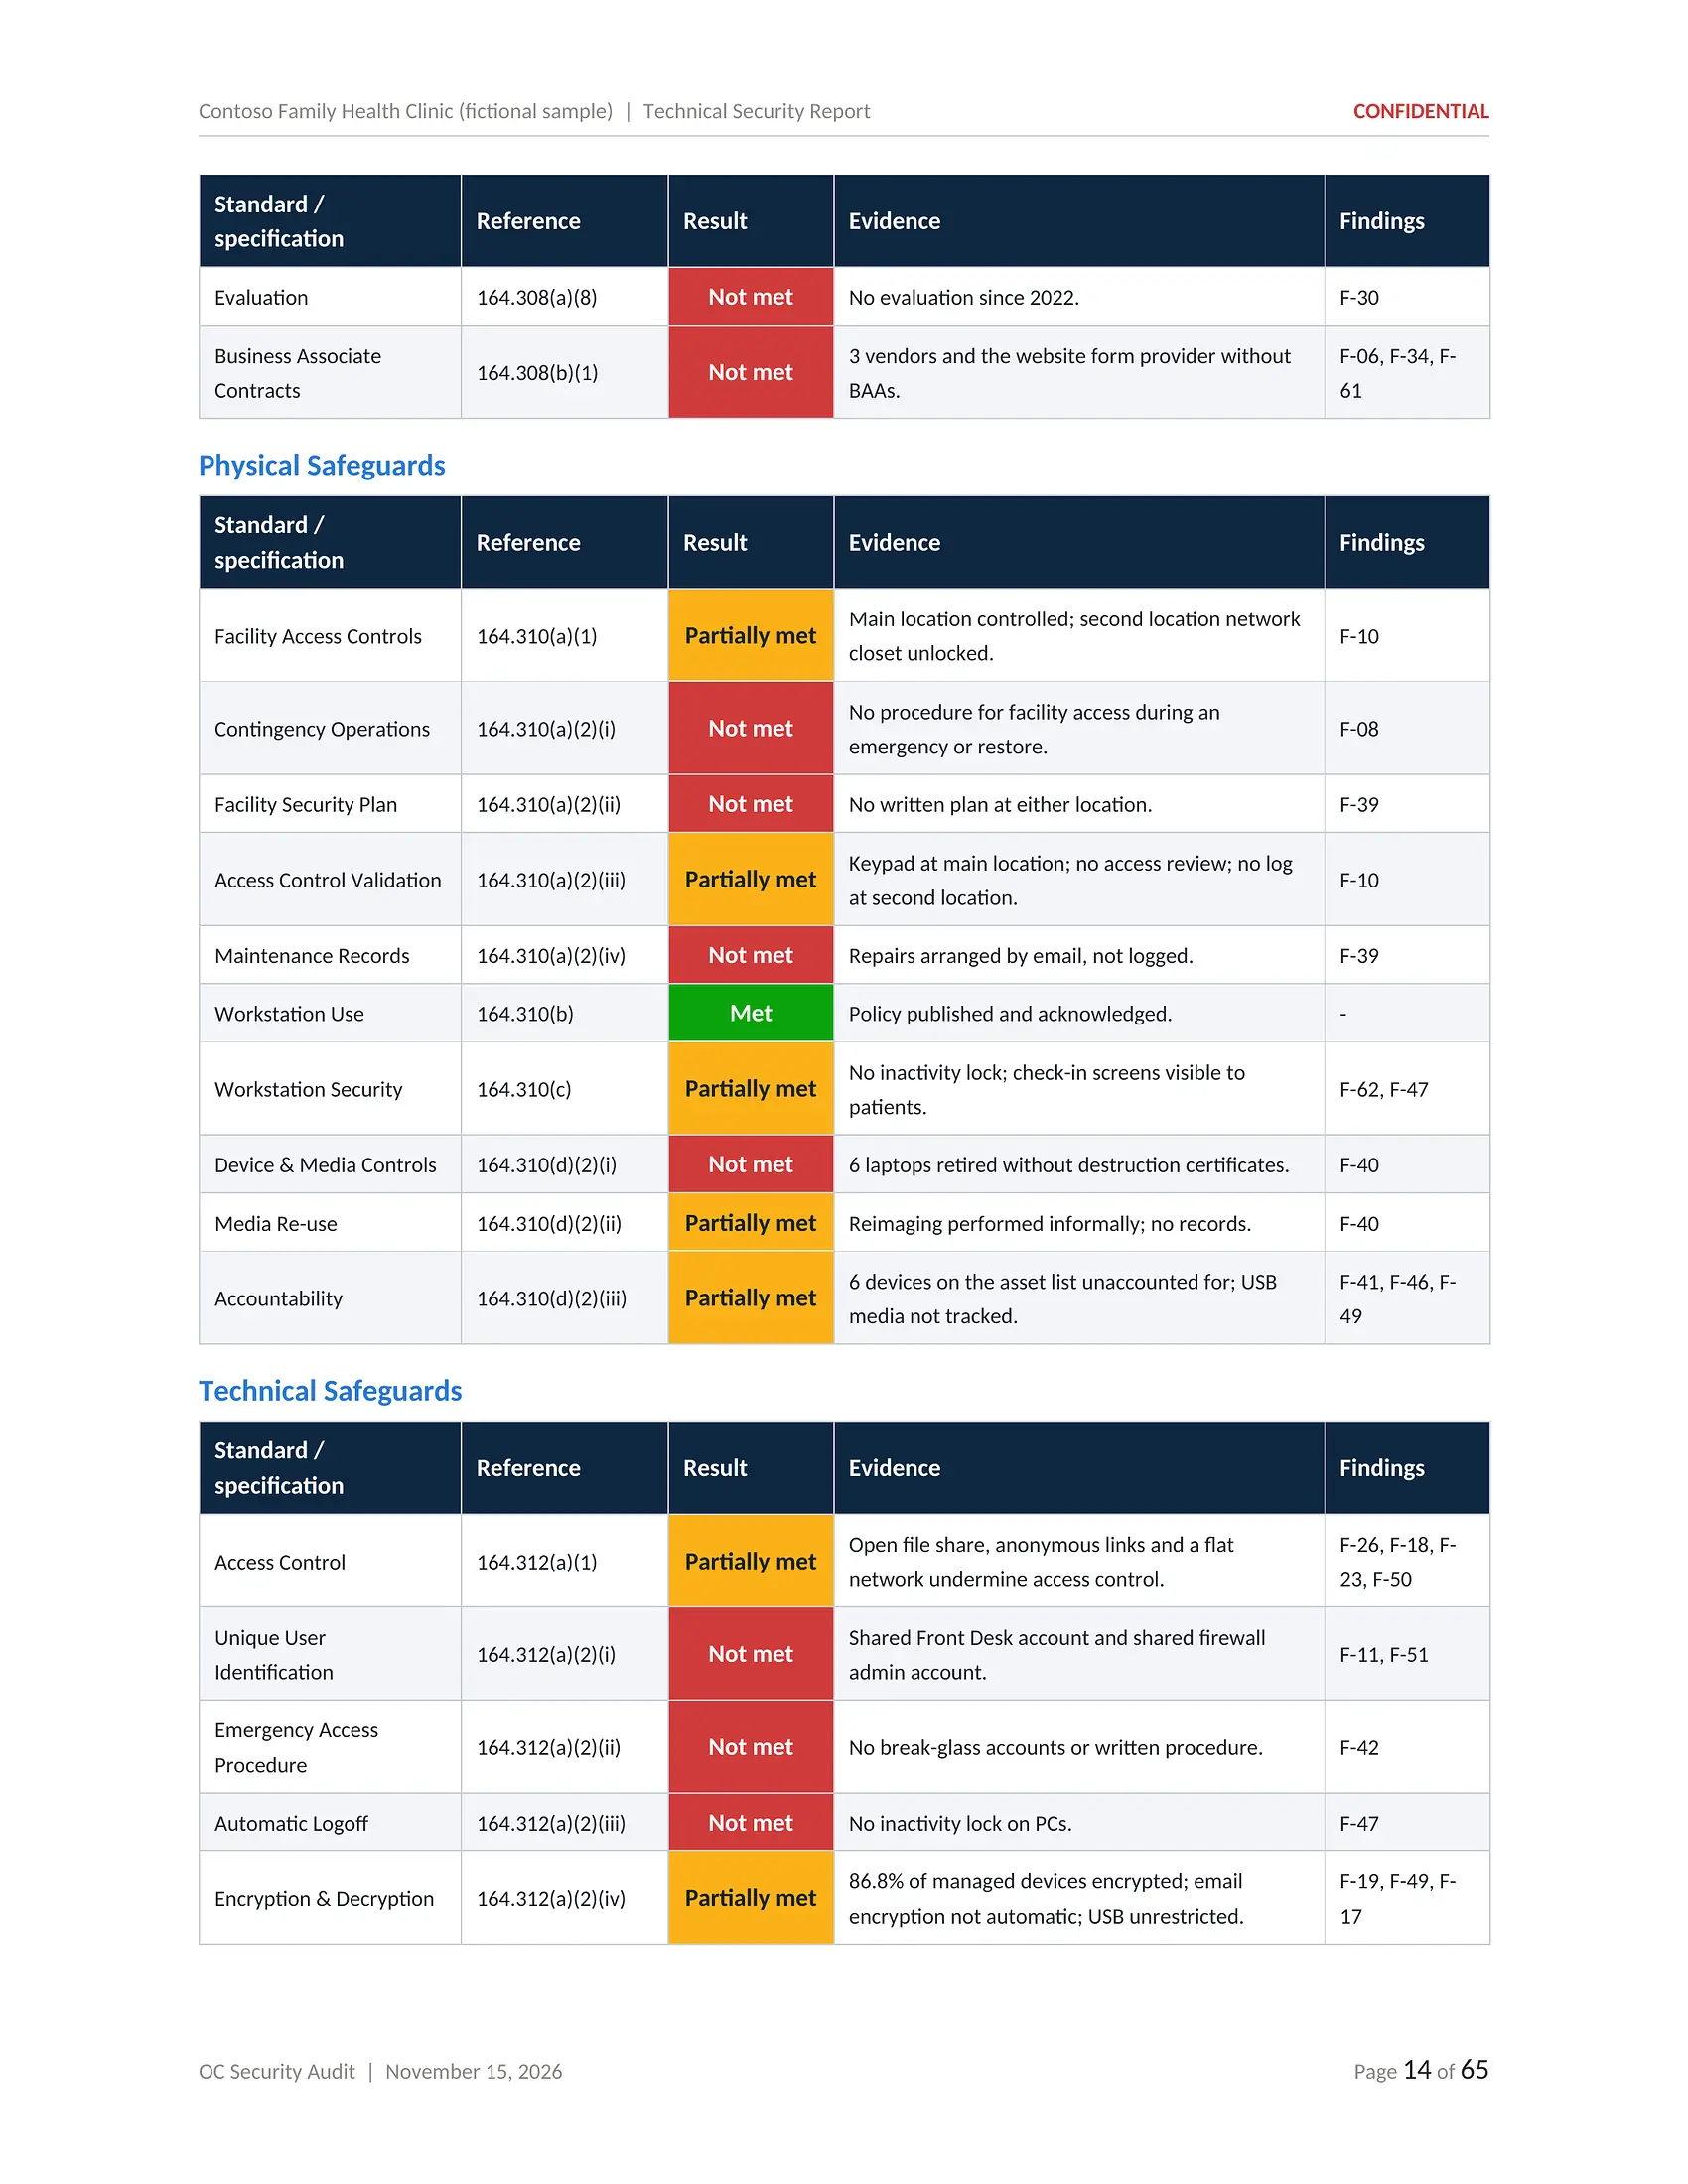
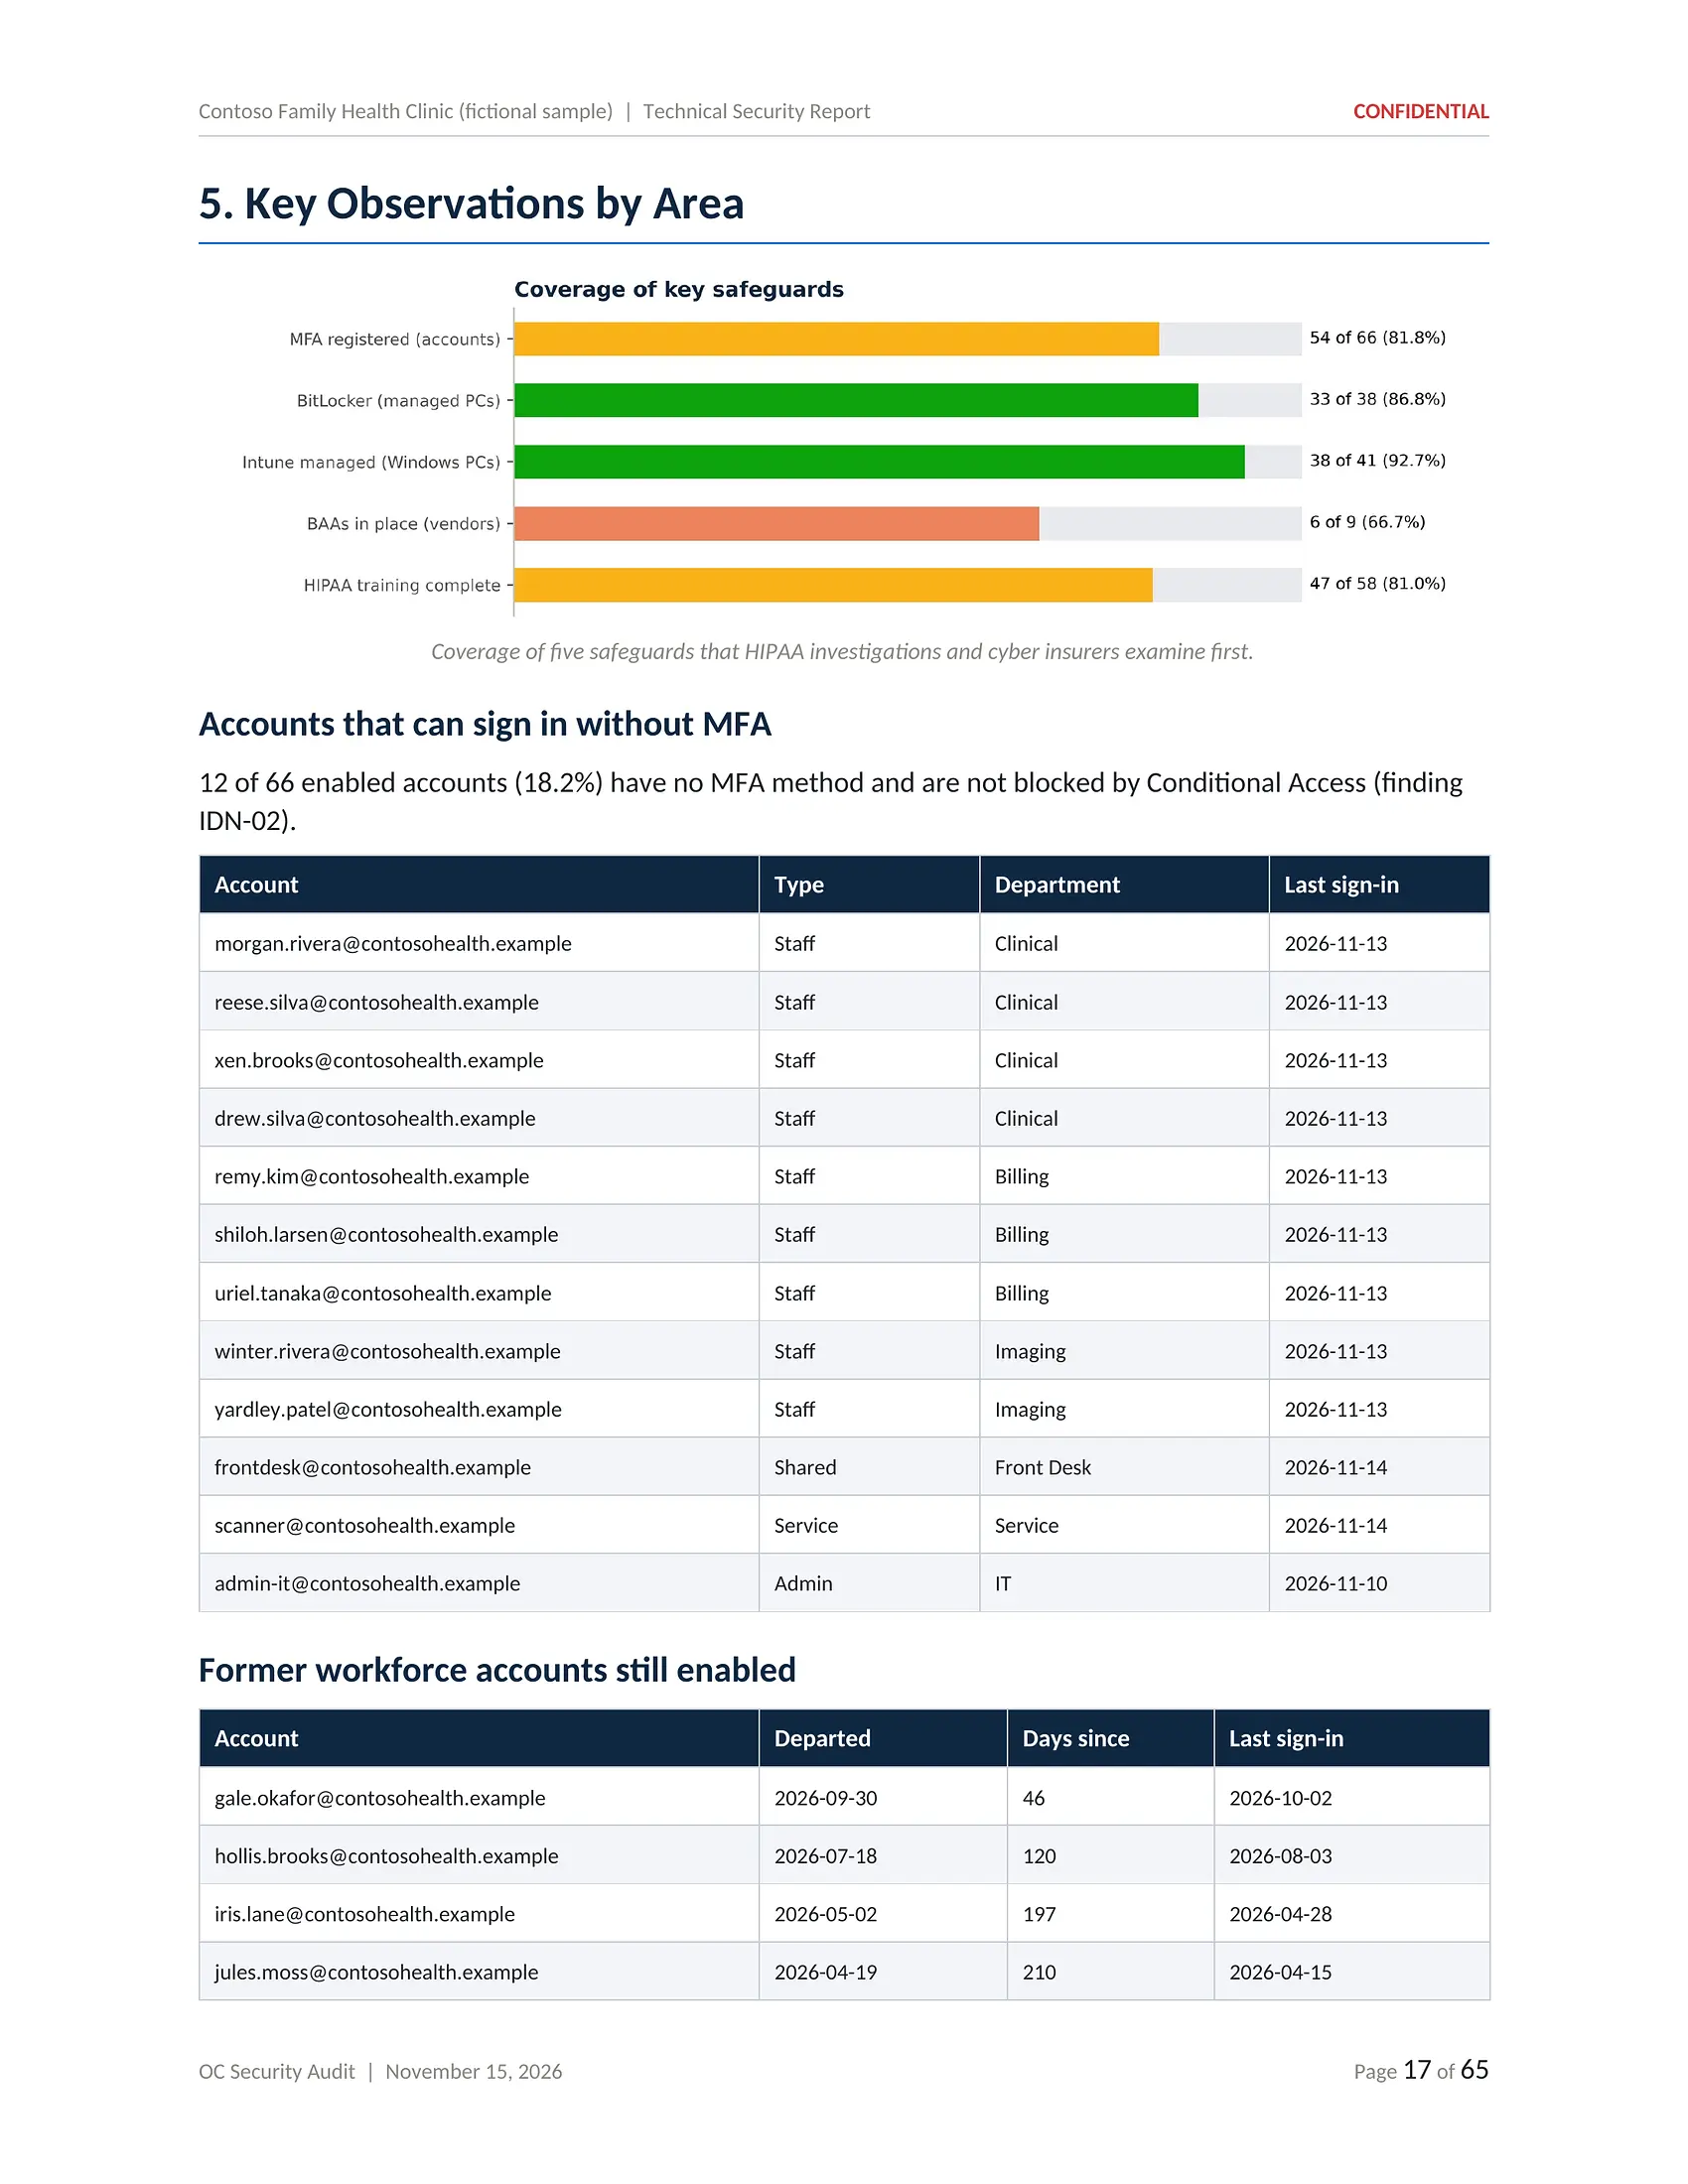
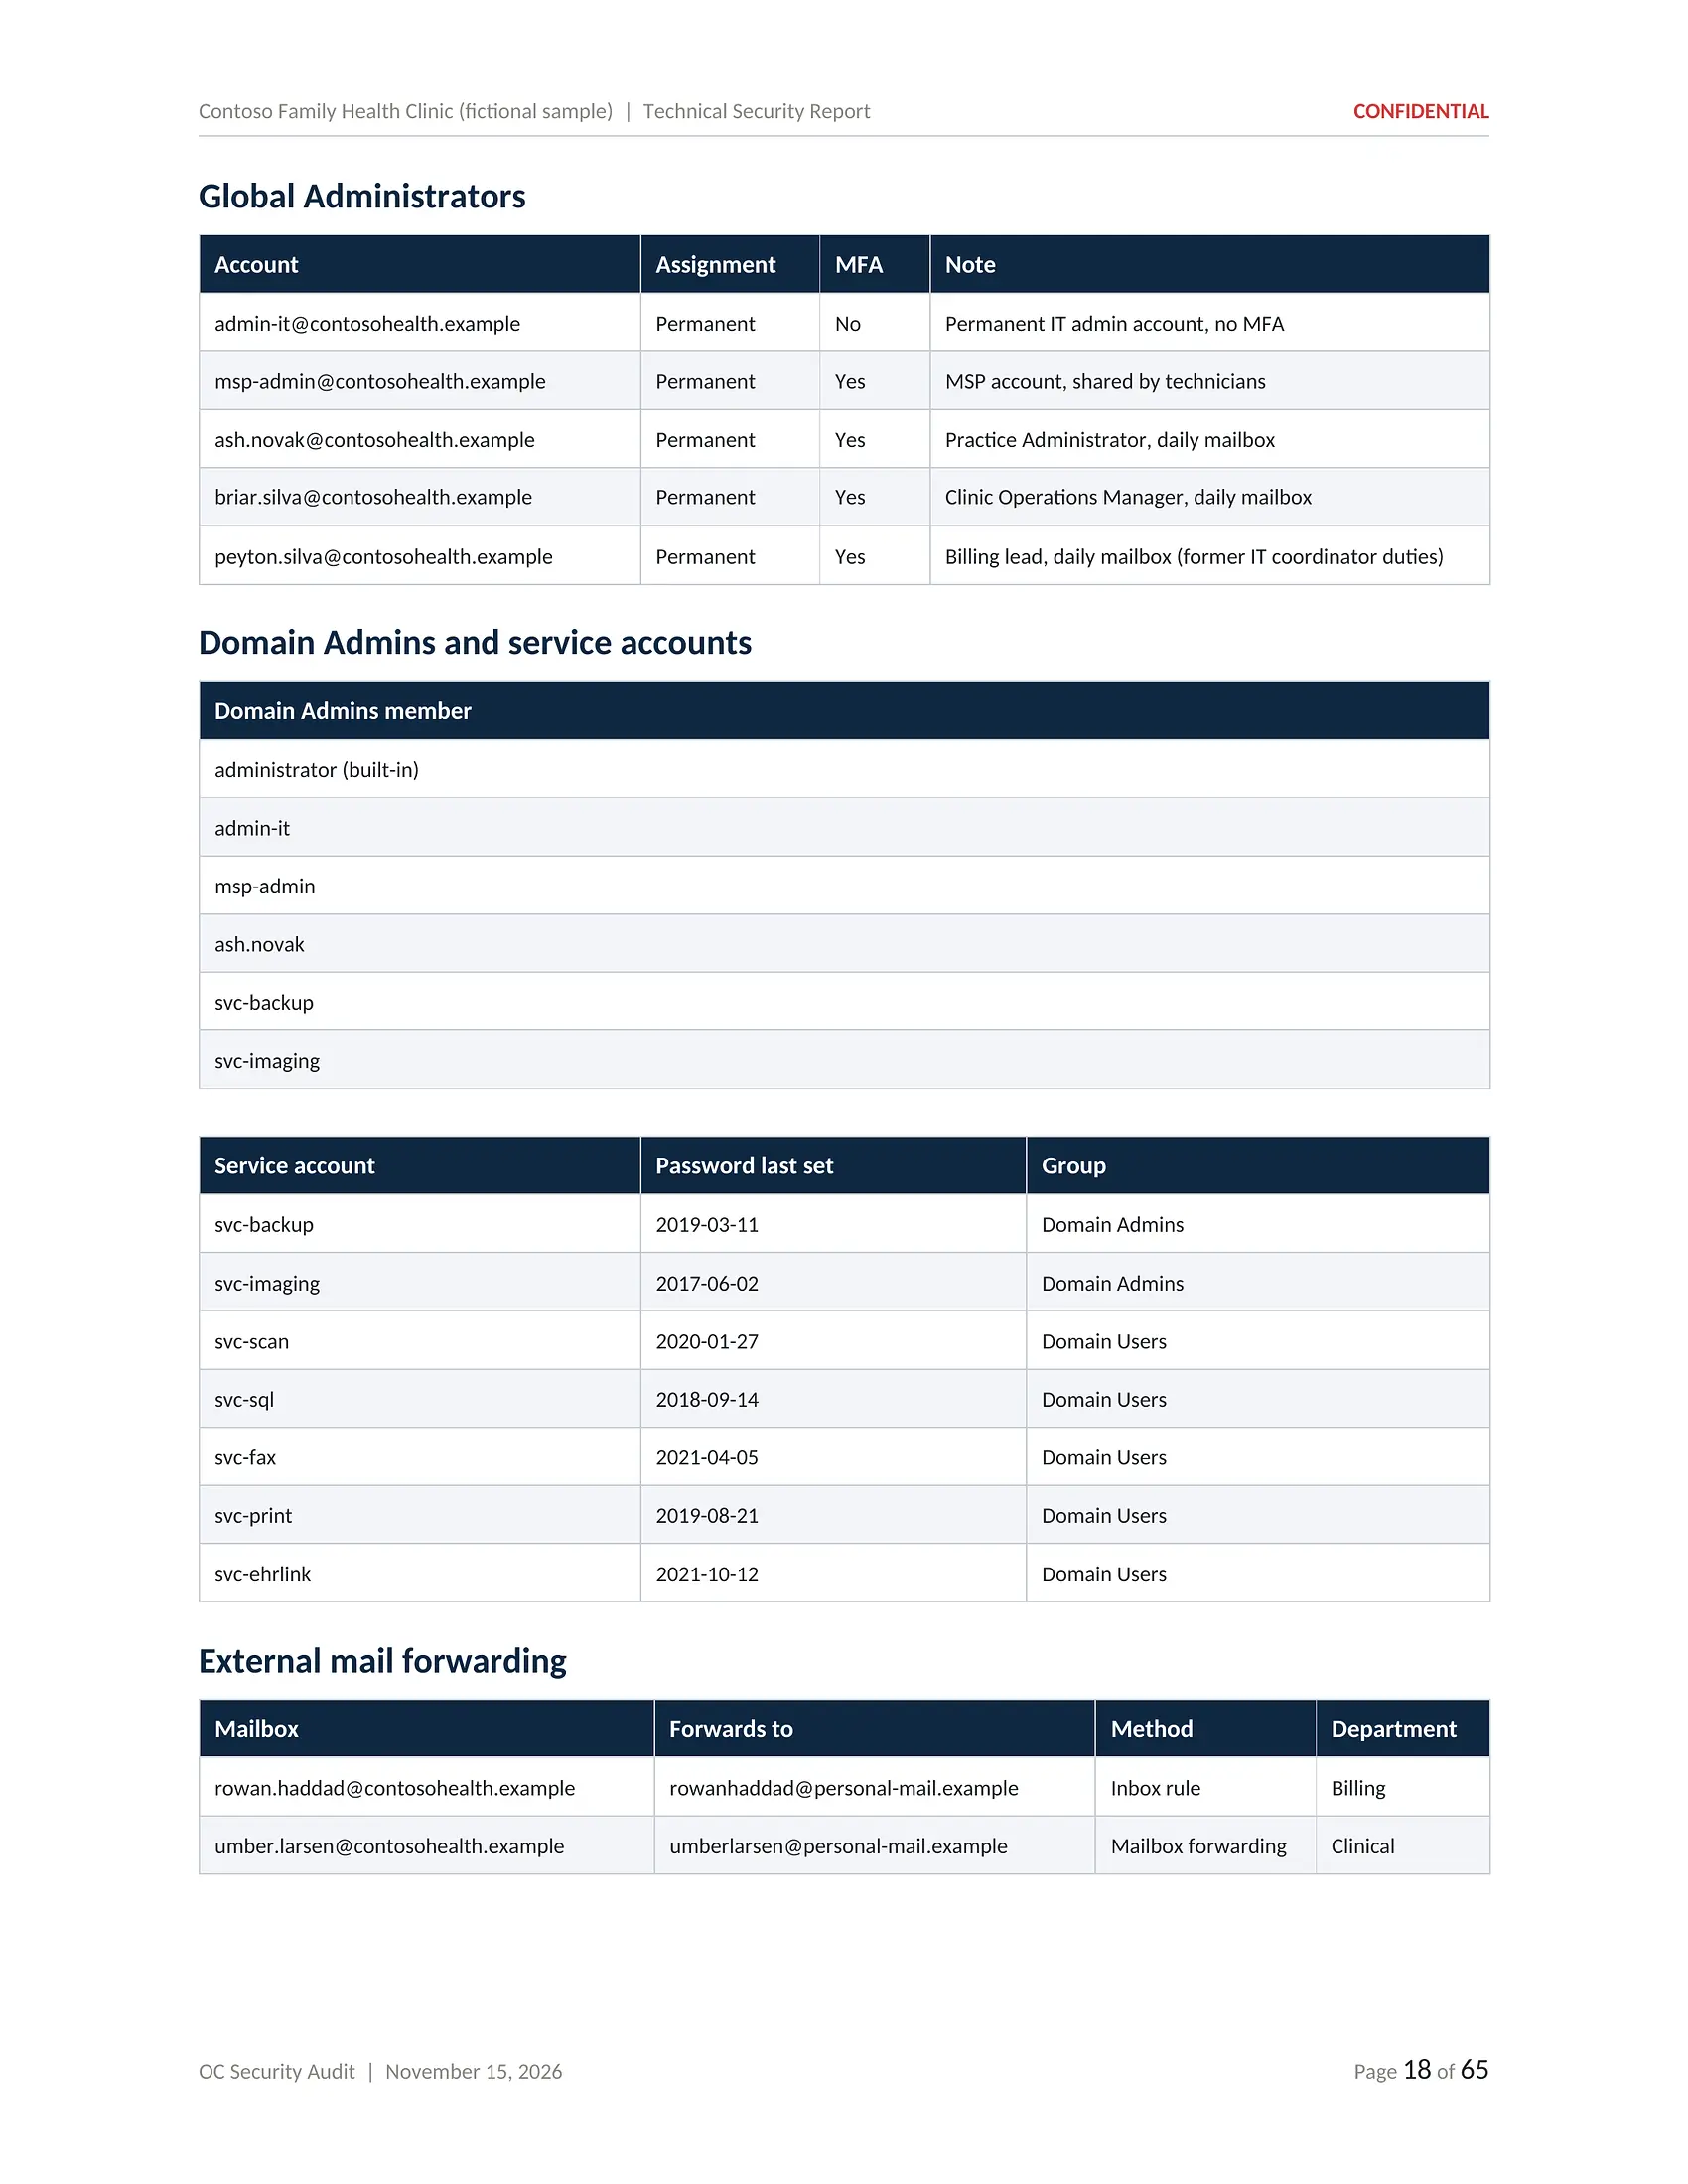
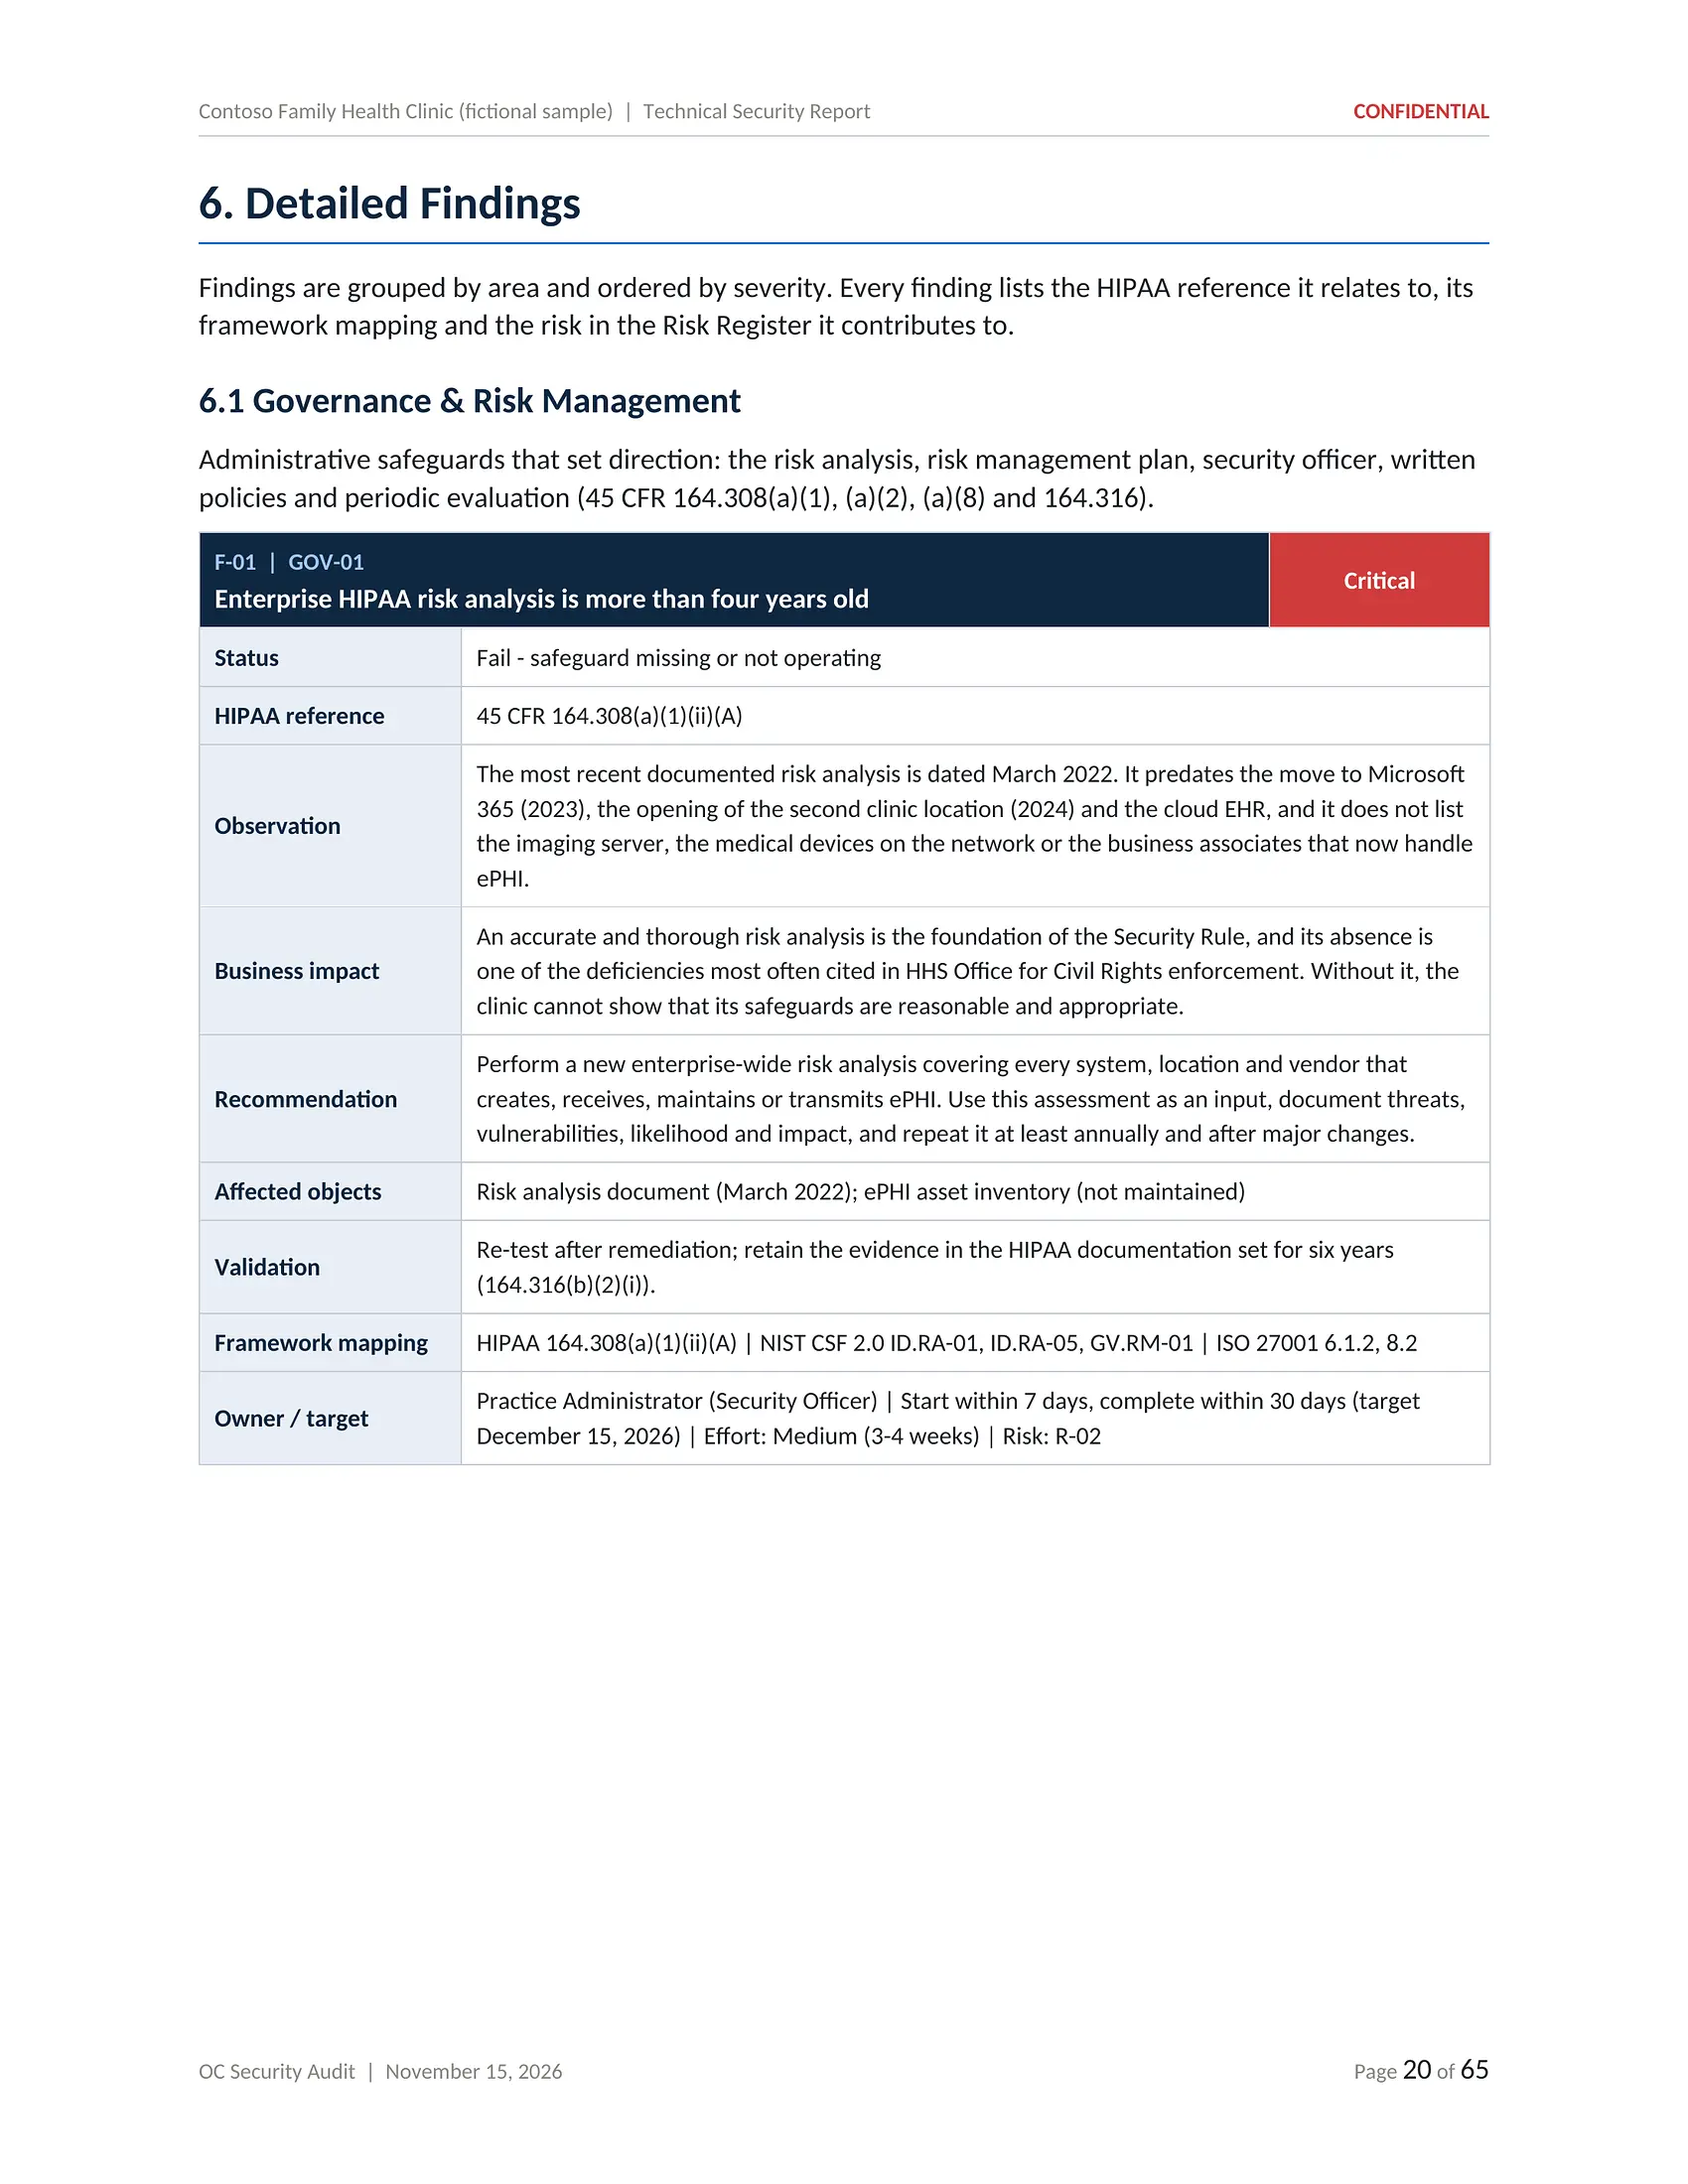
The working document for your IT provider. Every finding shows the HIPAA reference, what was observed, the business impact, the exact fix, the objects affected and how to confirm the fix worked, grouped by area and ordered by severity.
Who uses it
IT provider or MSP, internal IT staff, the HIPAA Security Officer and any auditor or investigator who asks for the evidence.
What is included
SAMPLE · Contoso Family Health Clinic (fictional)
1 / 16
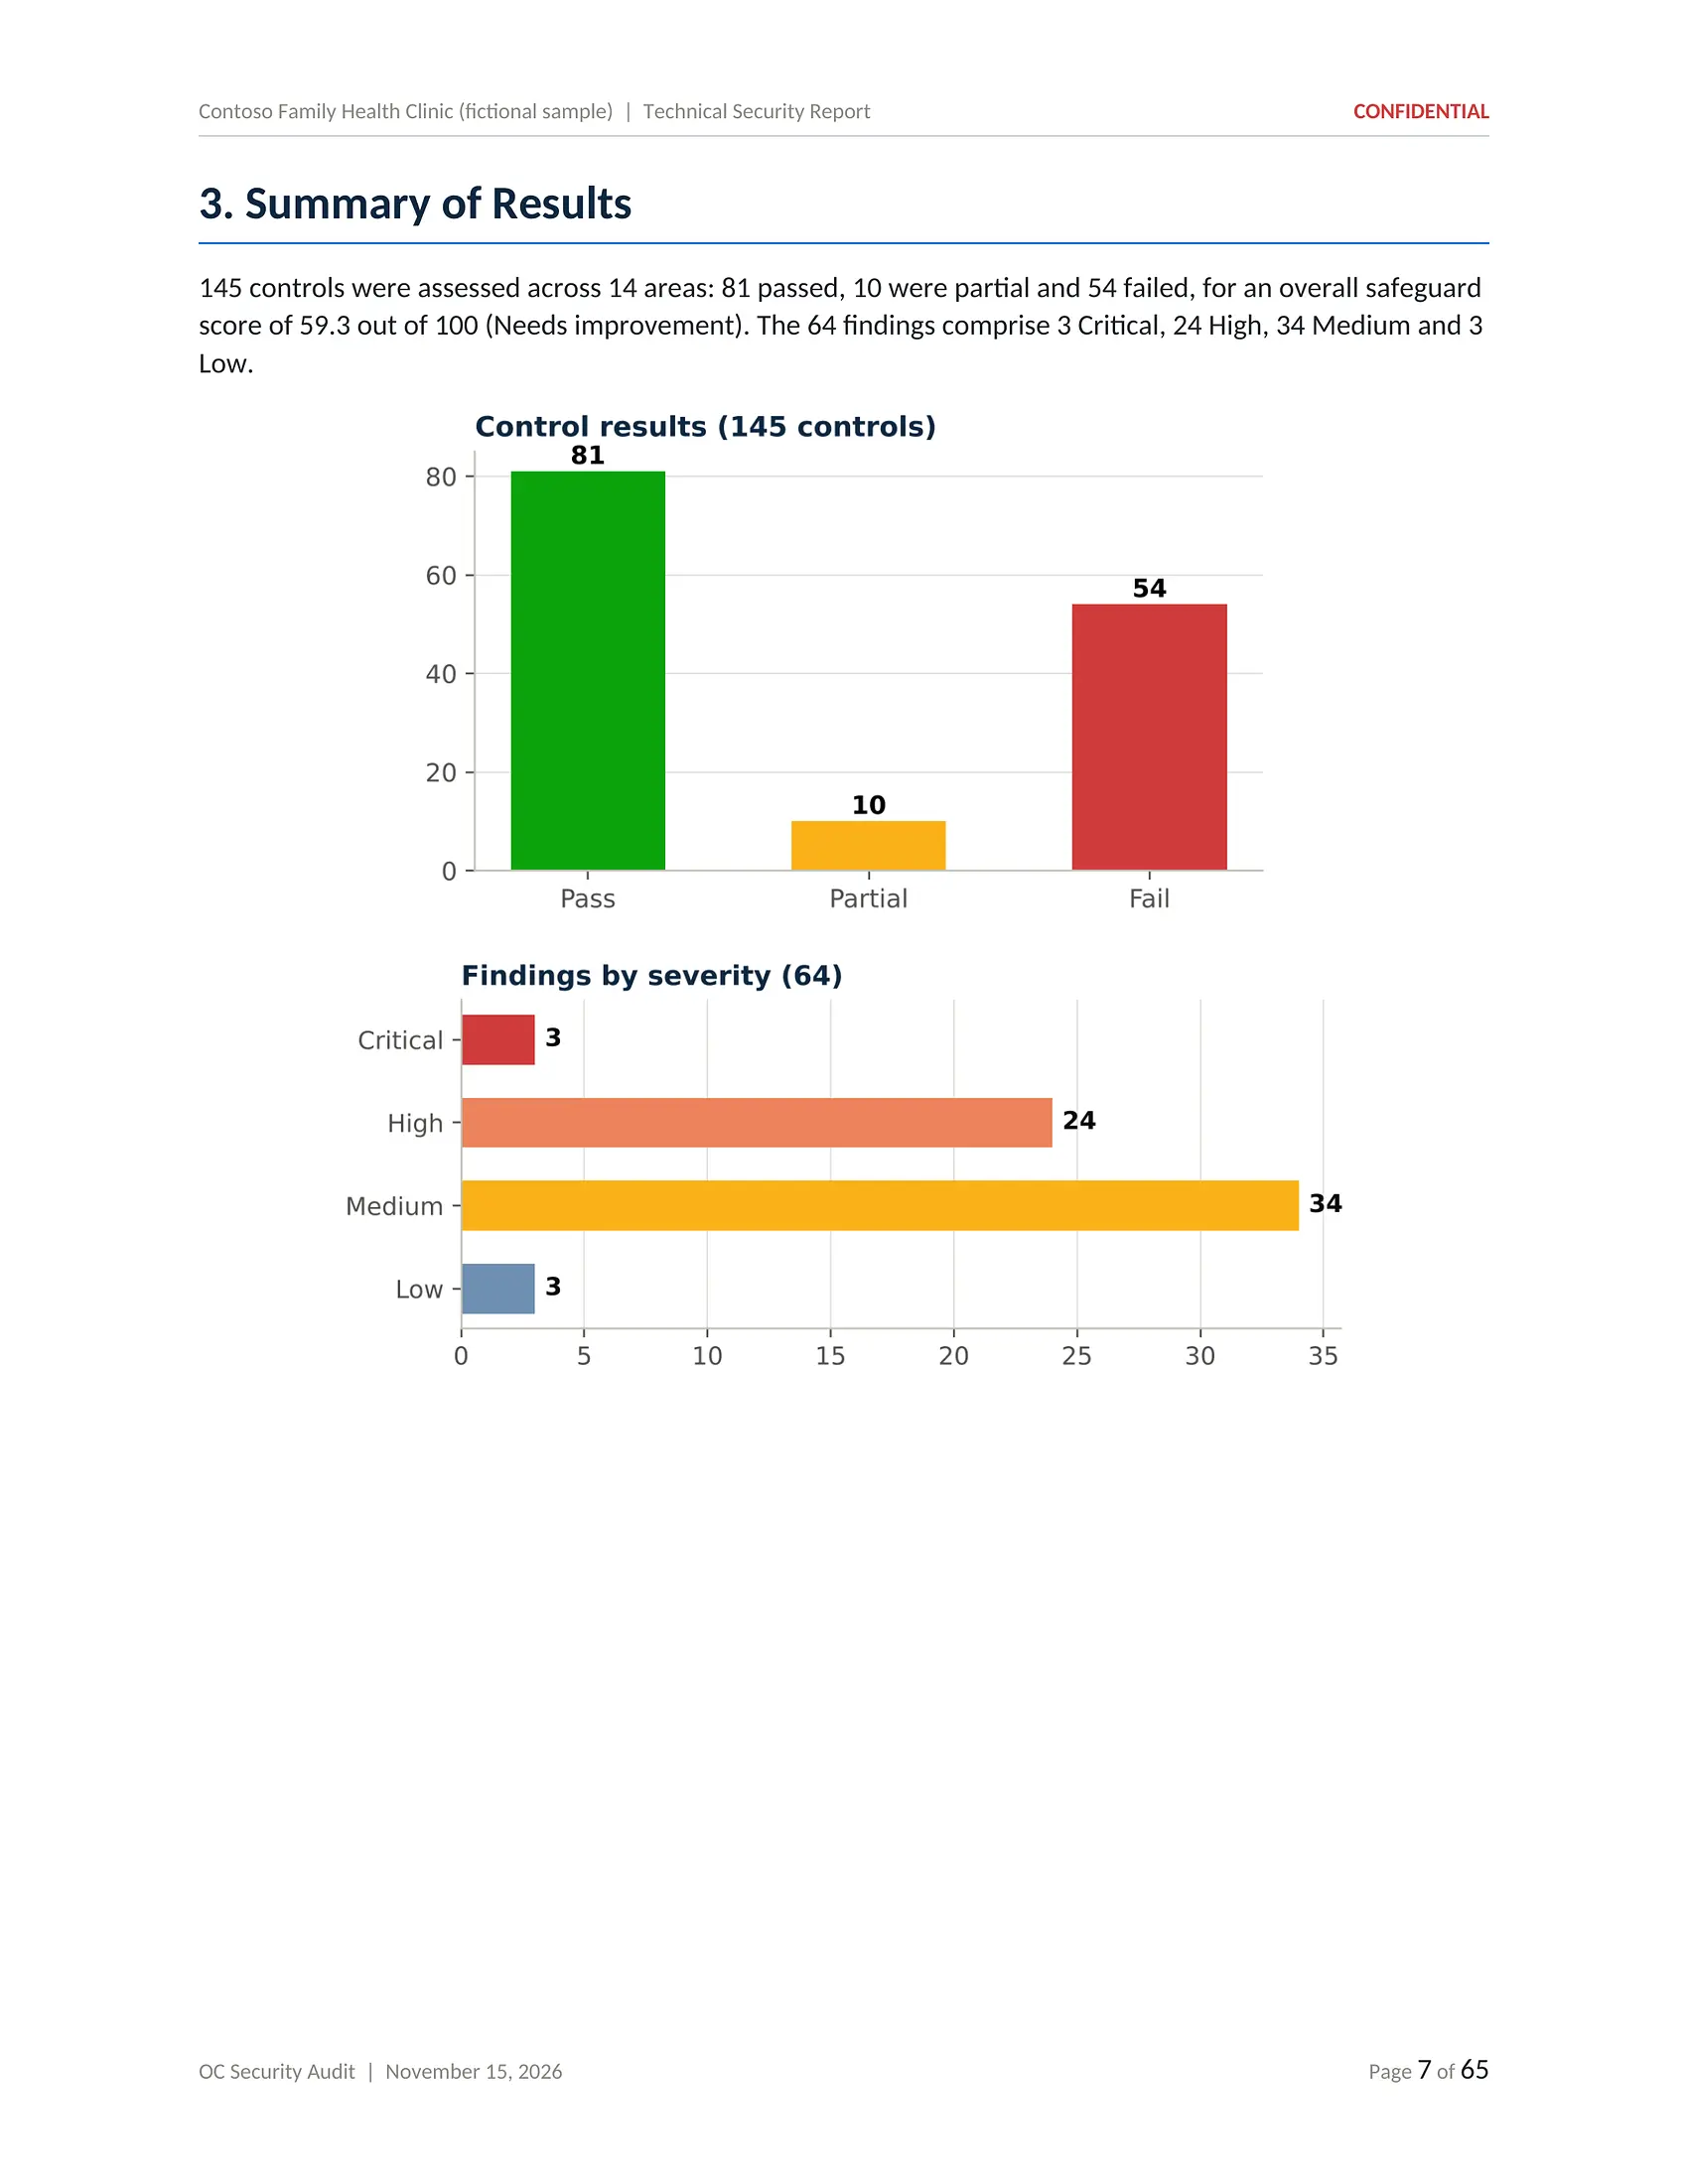
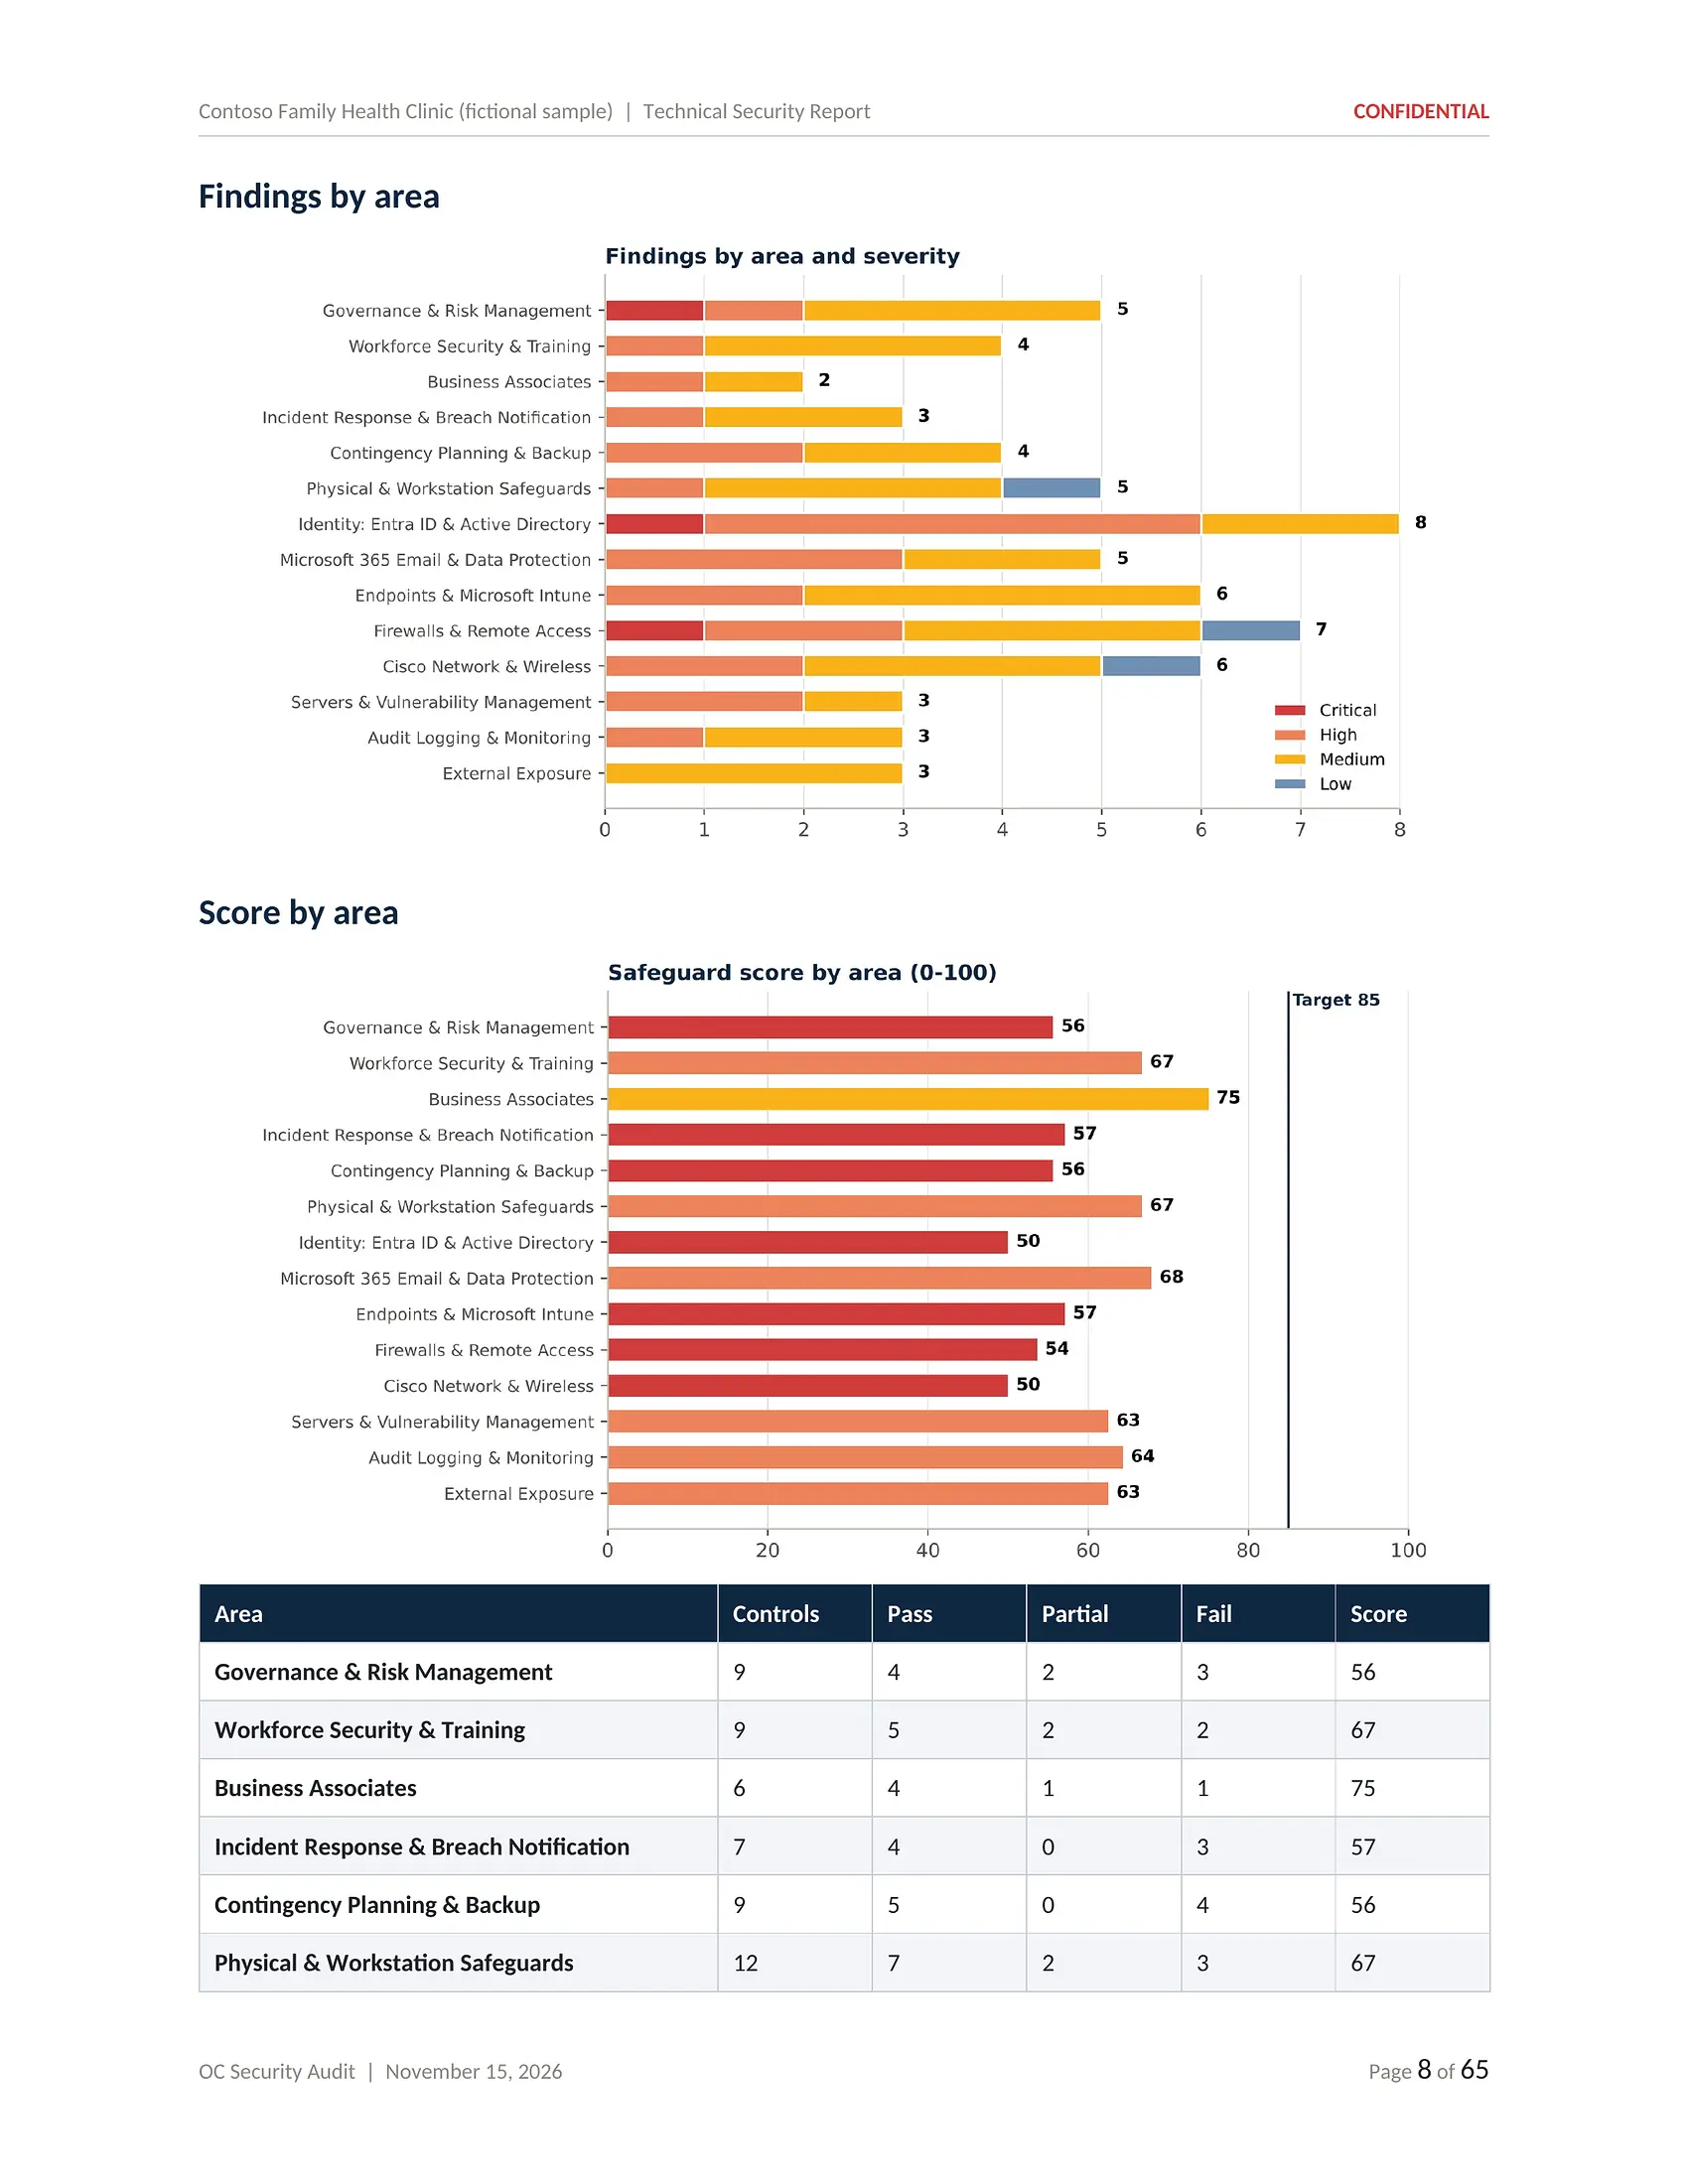
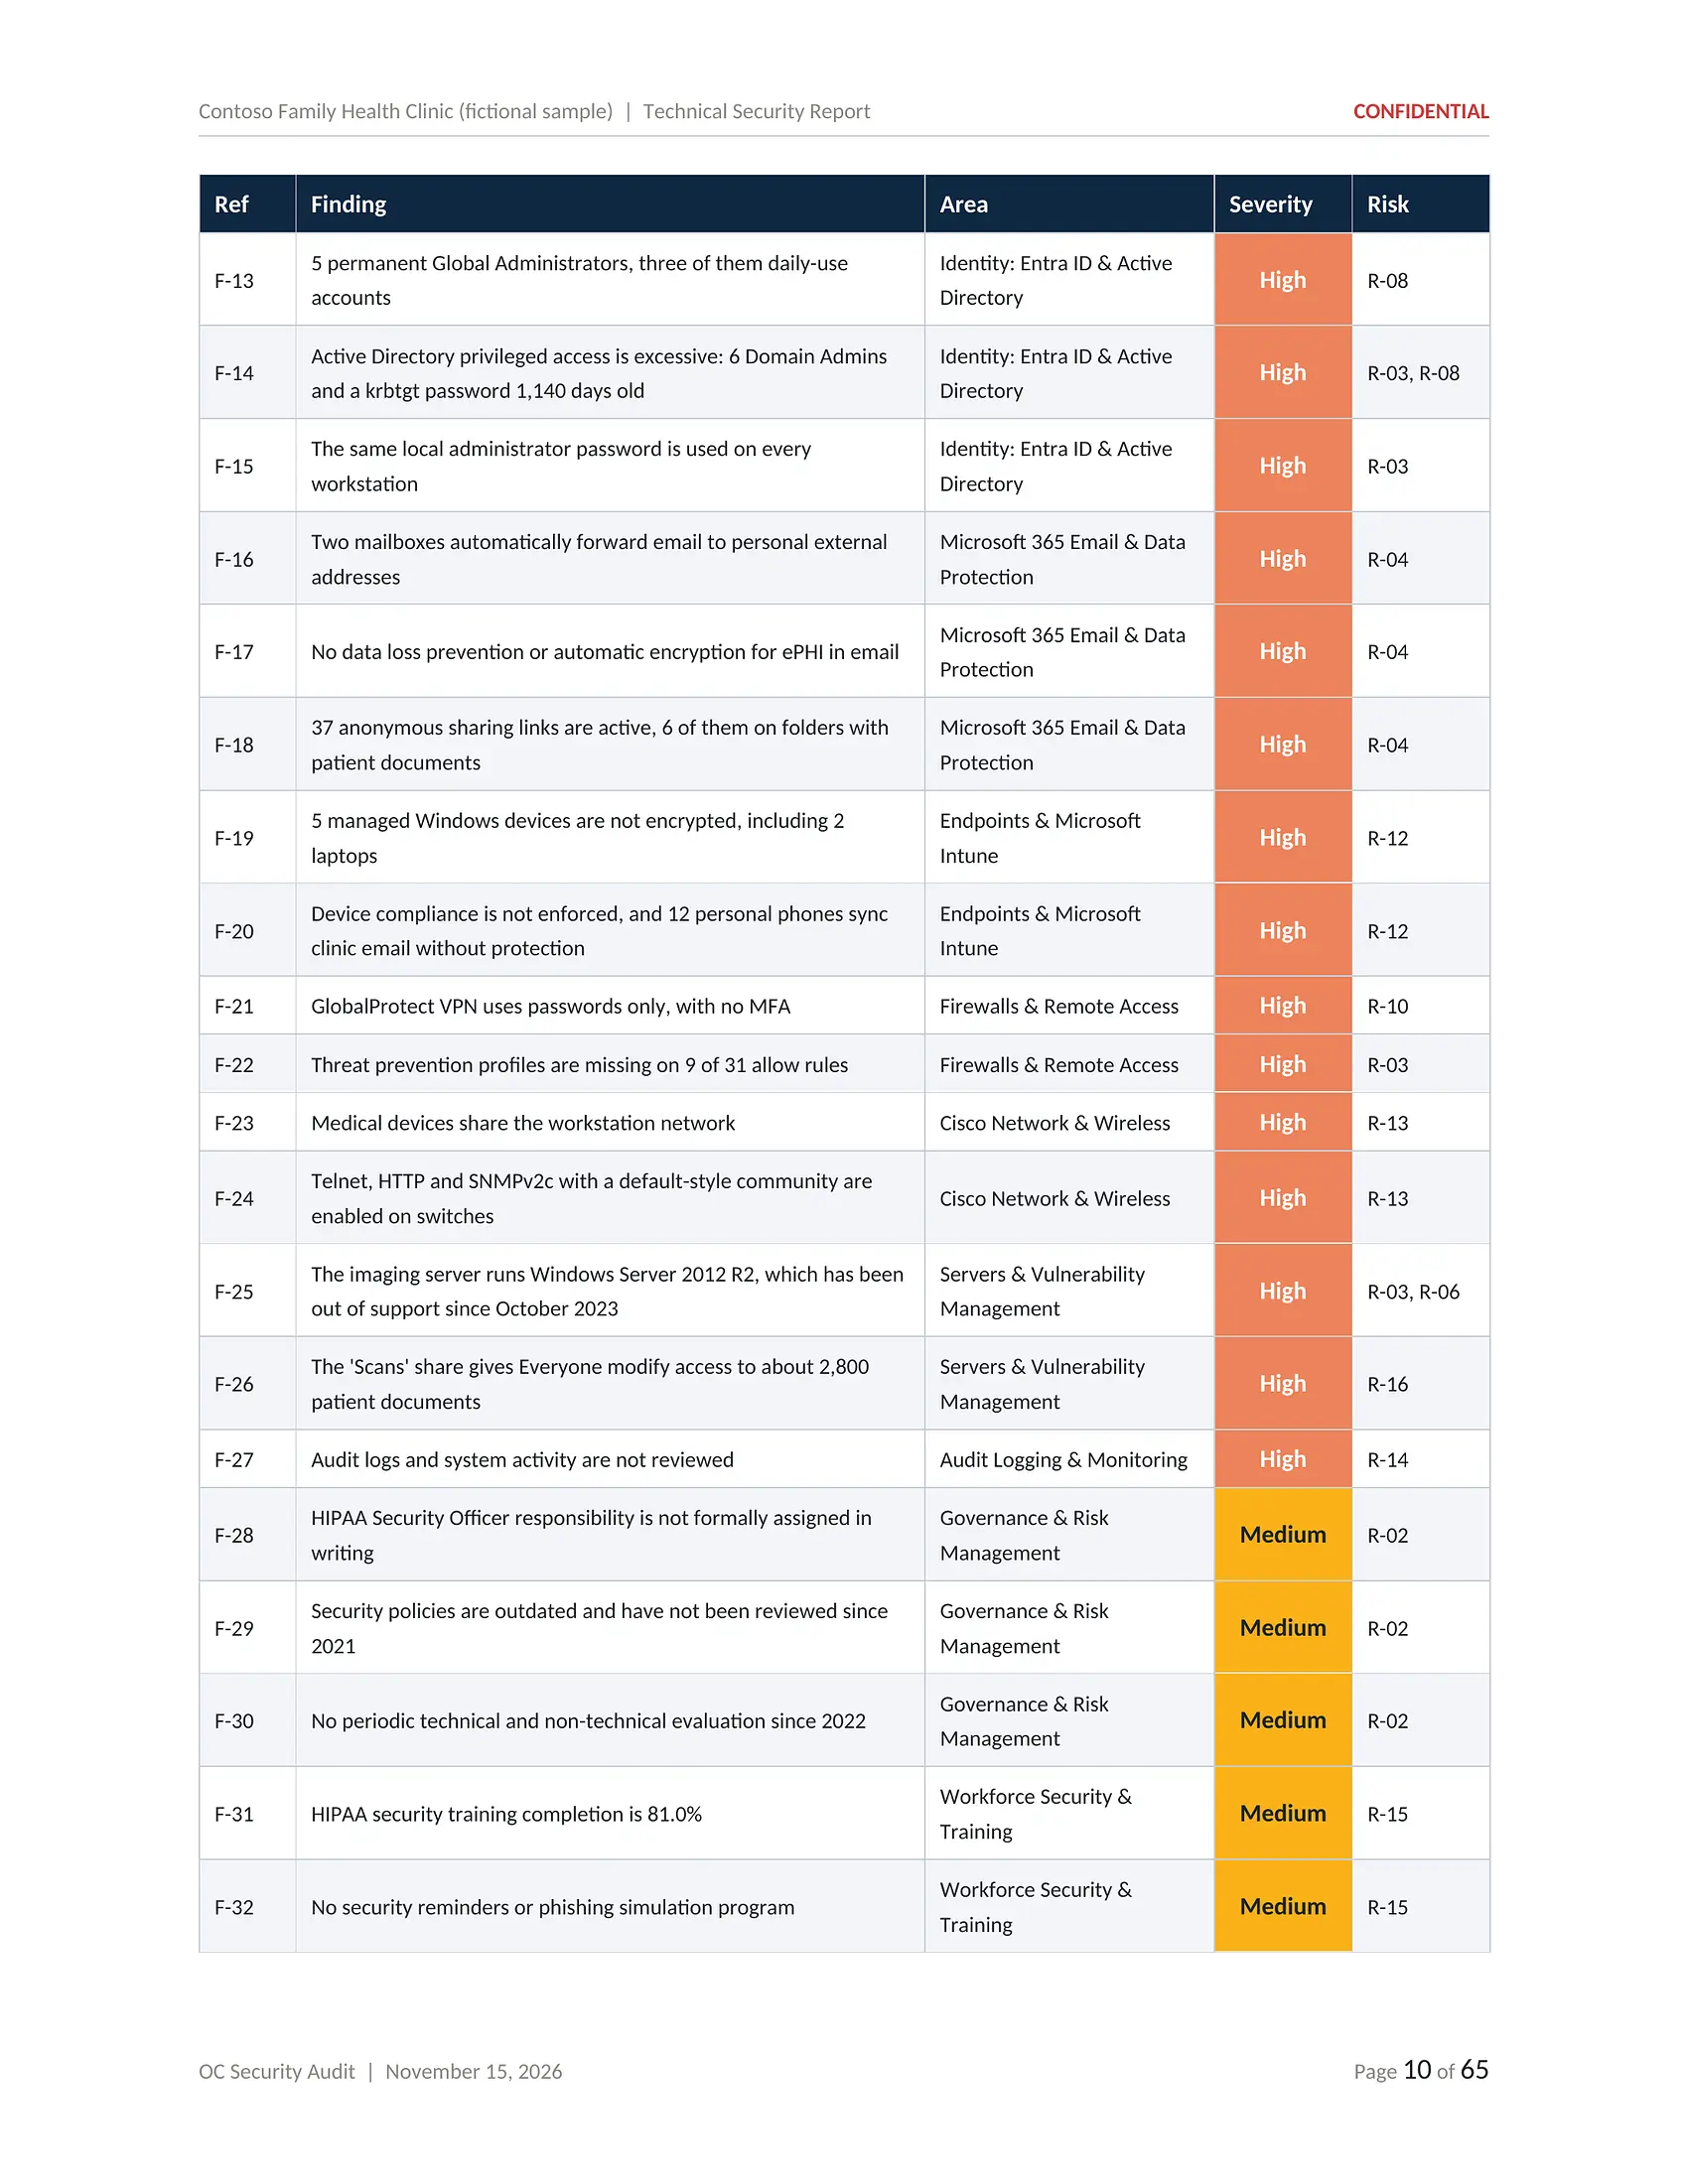
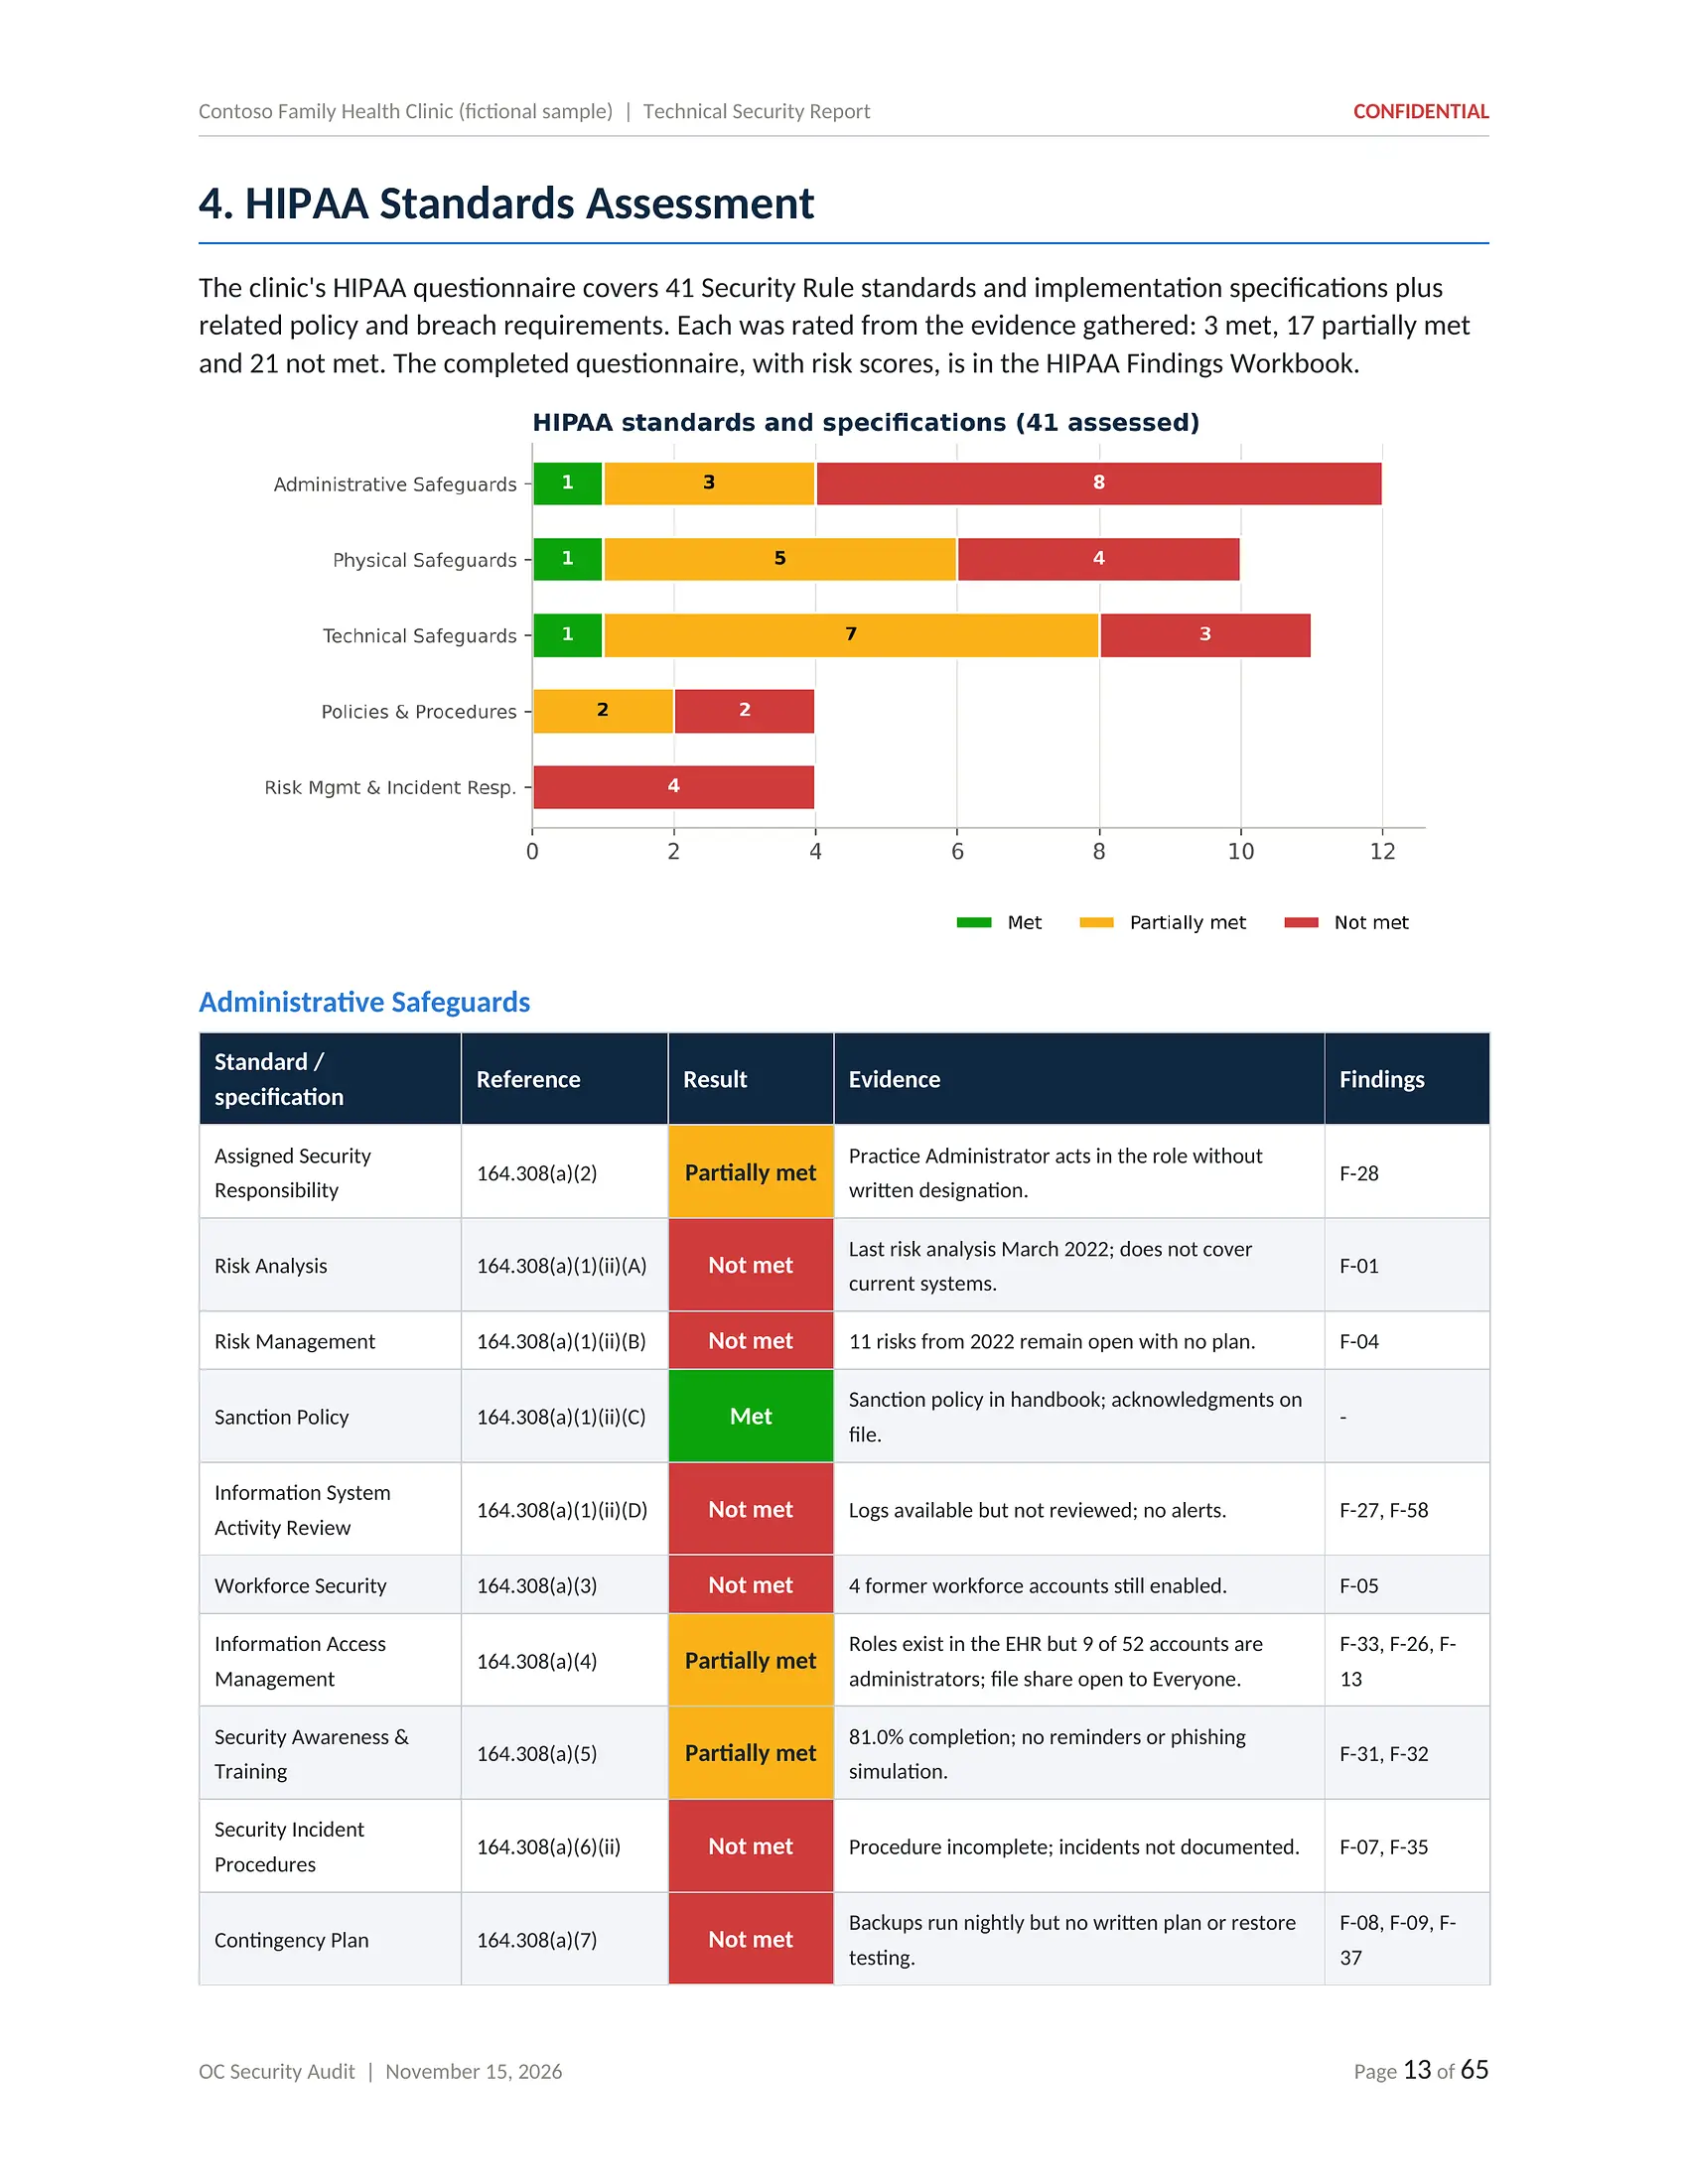
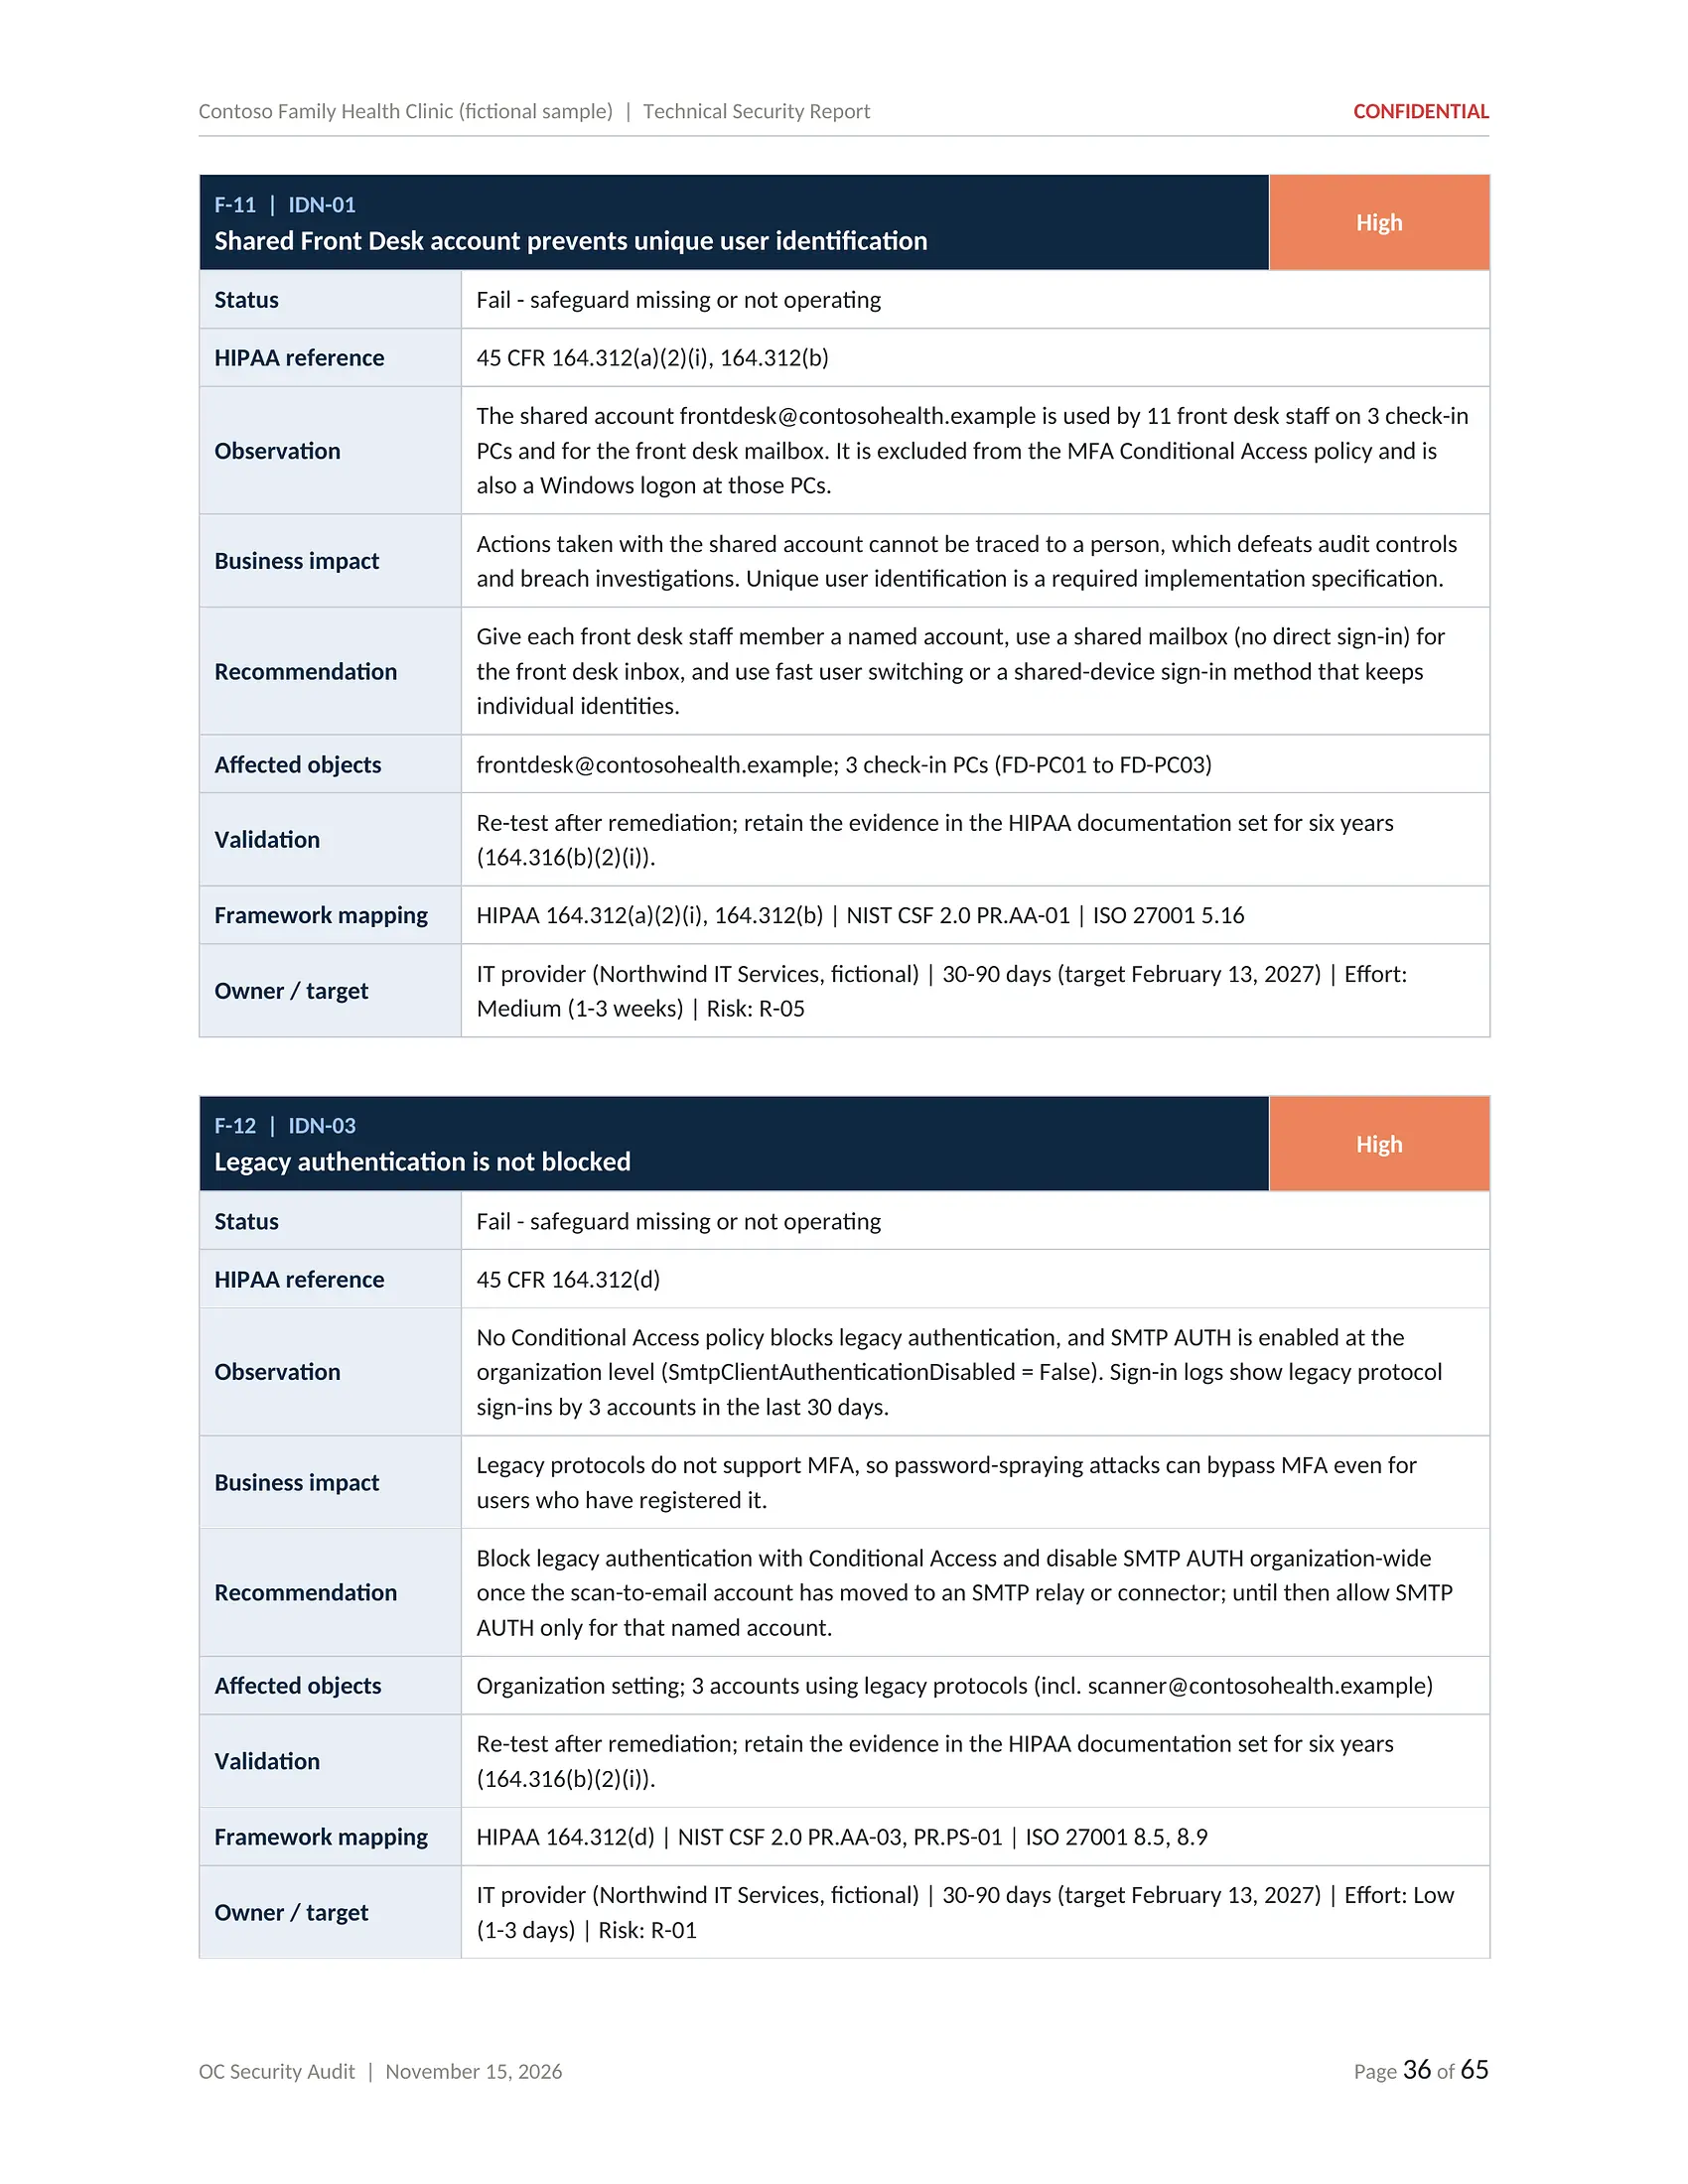
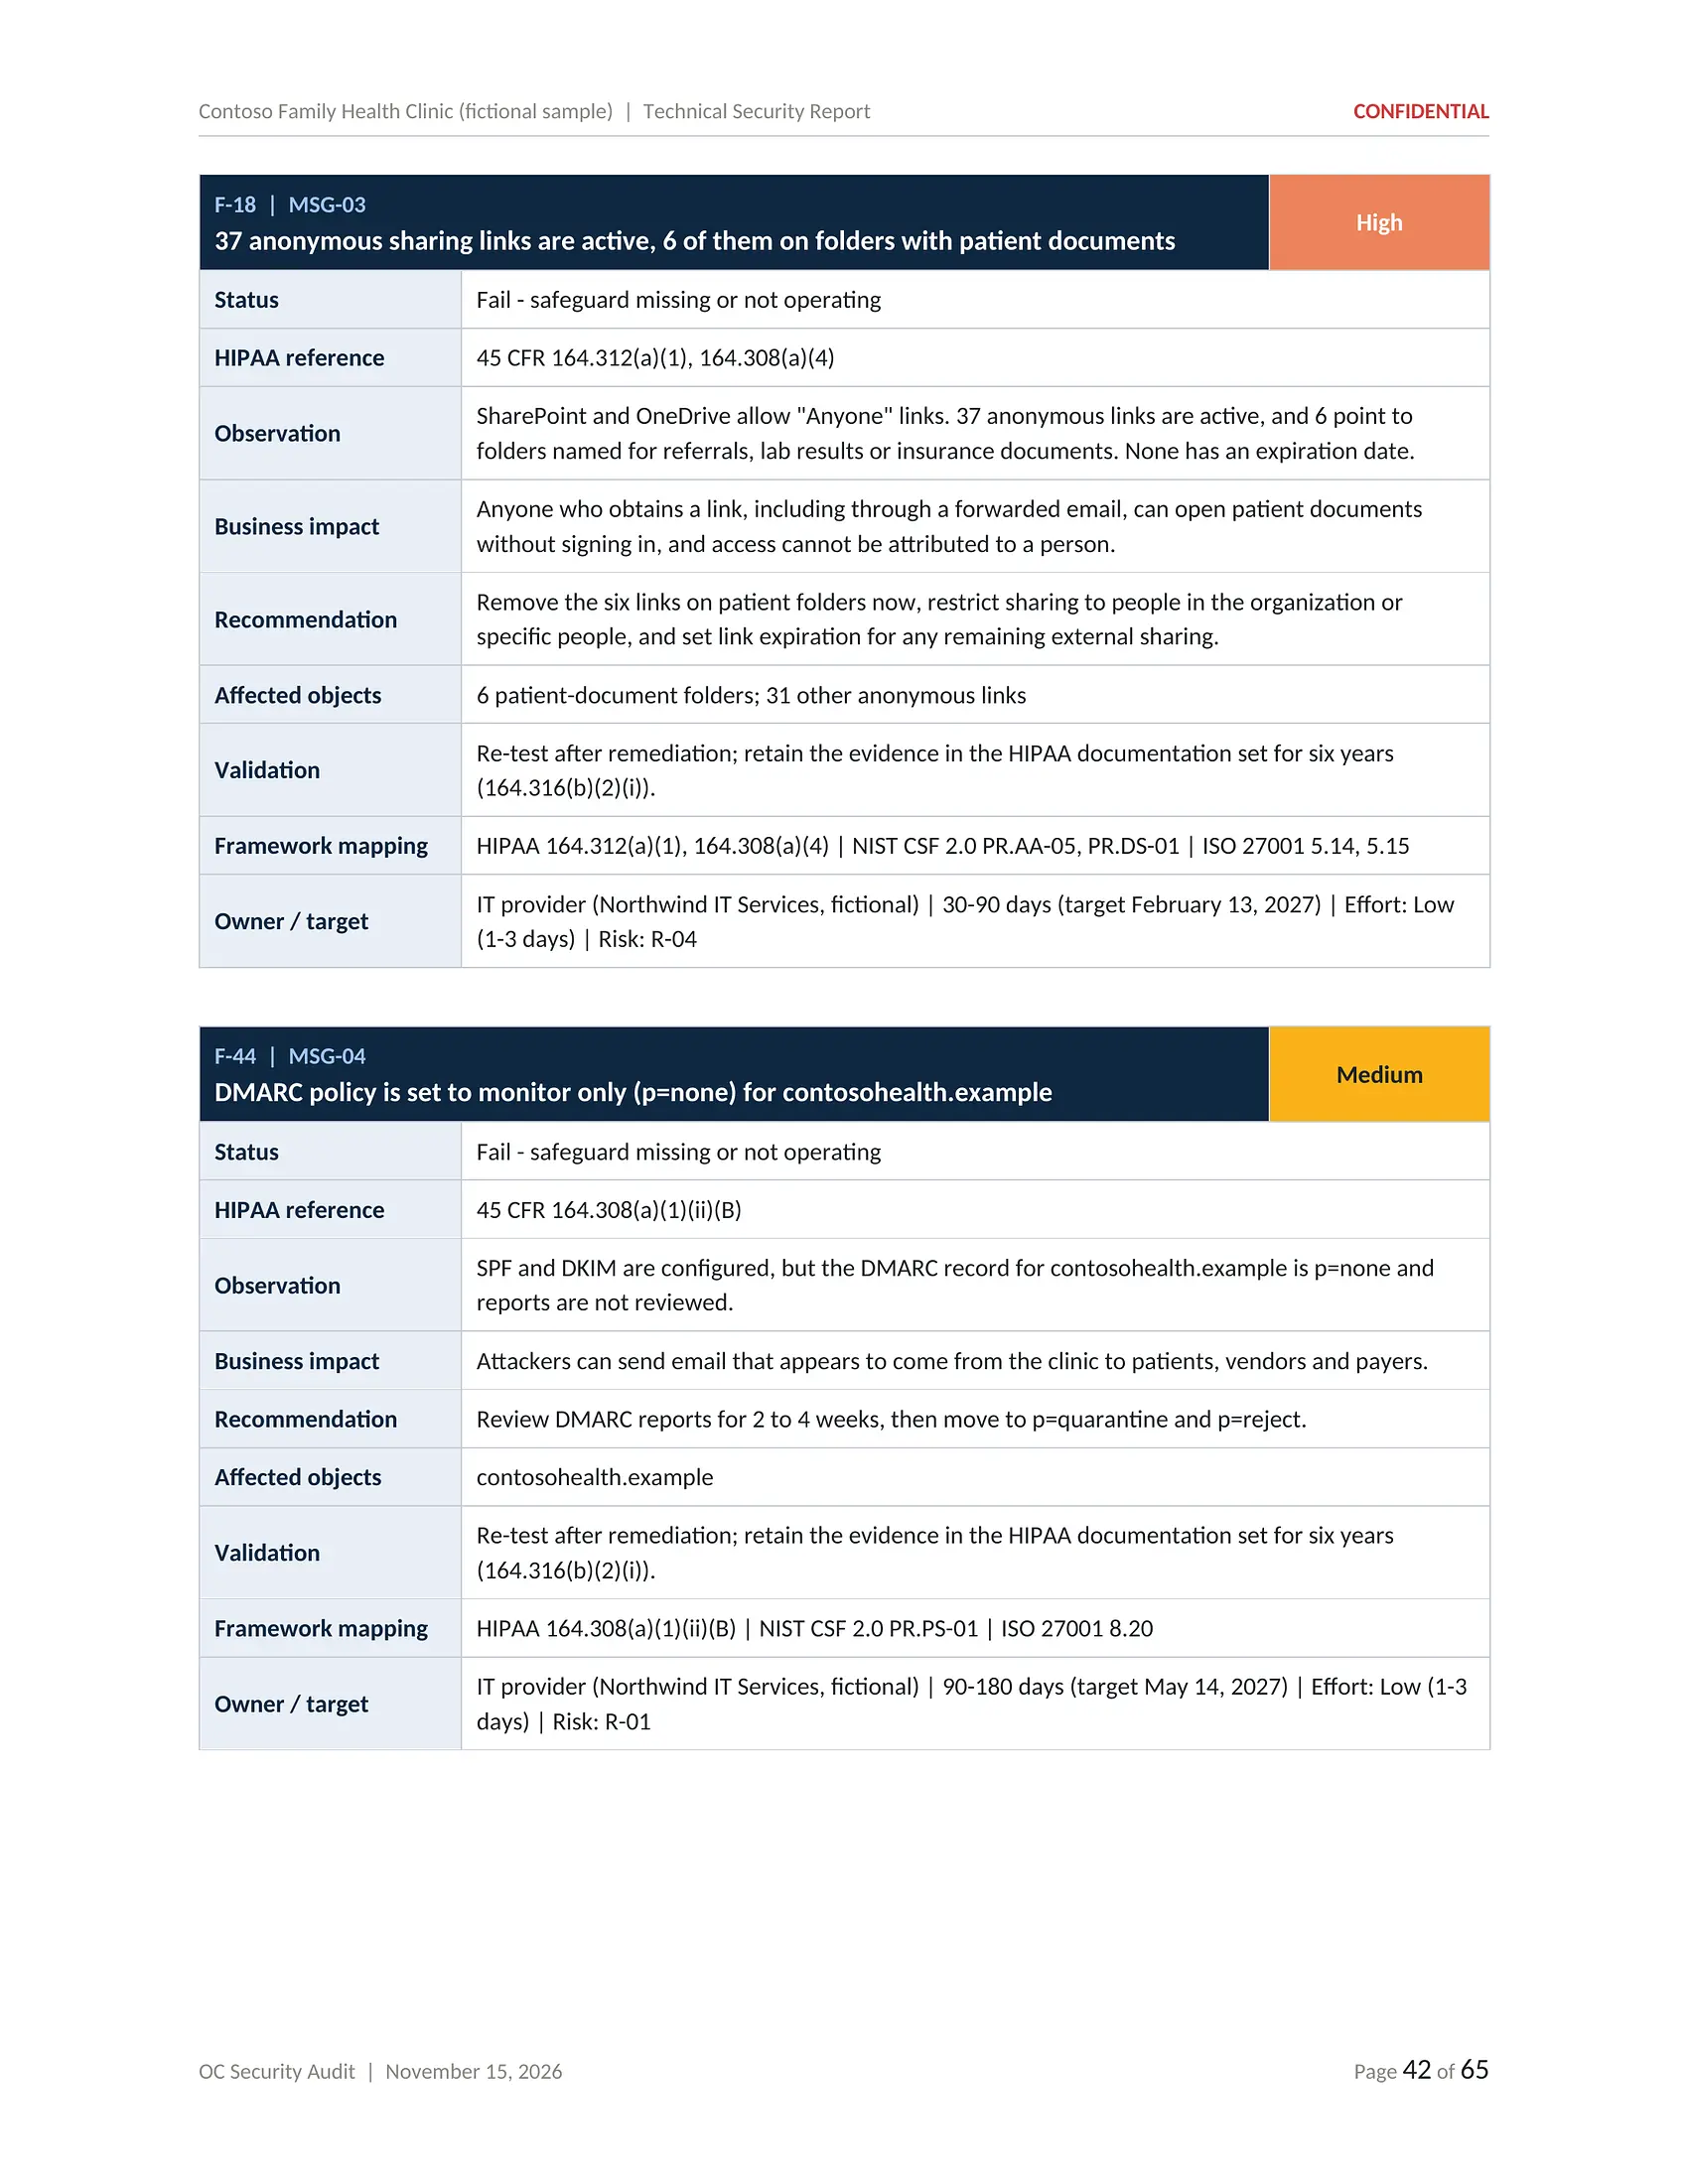
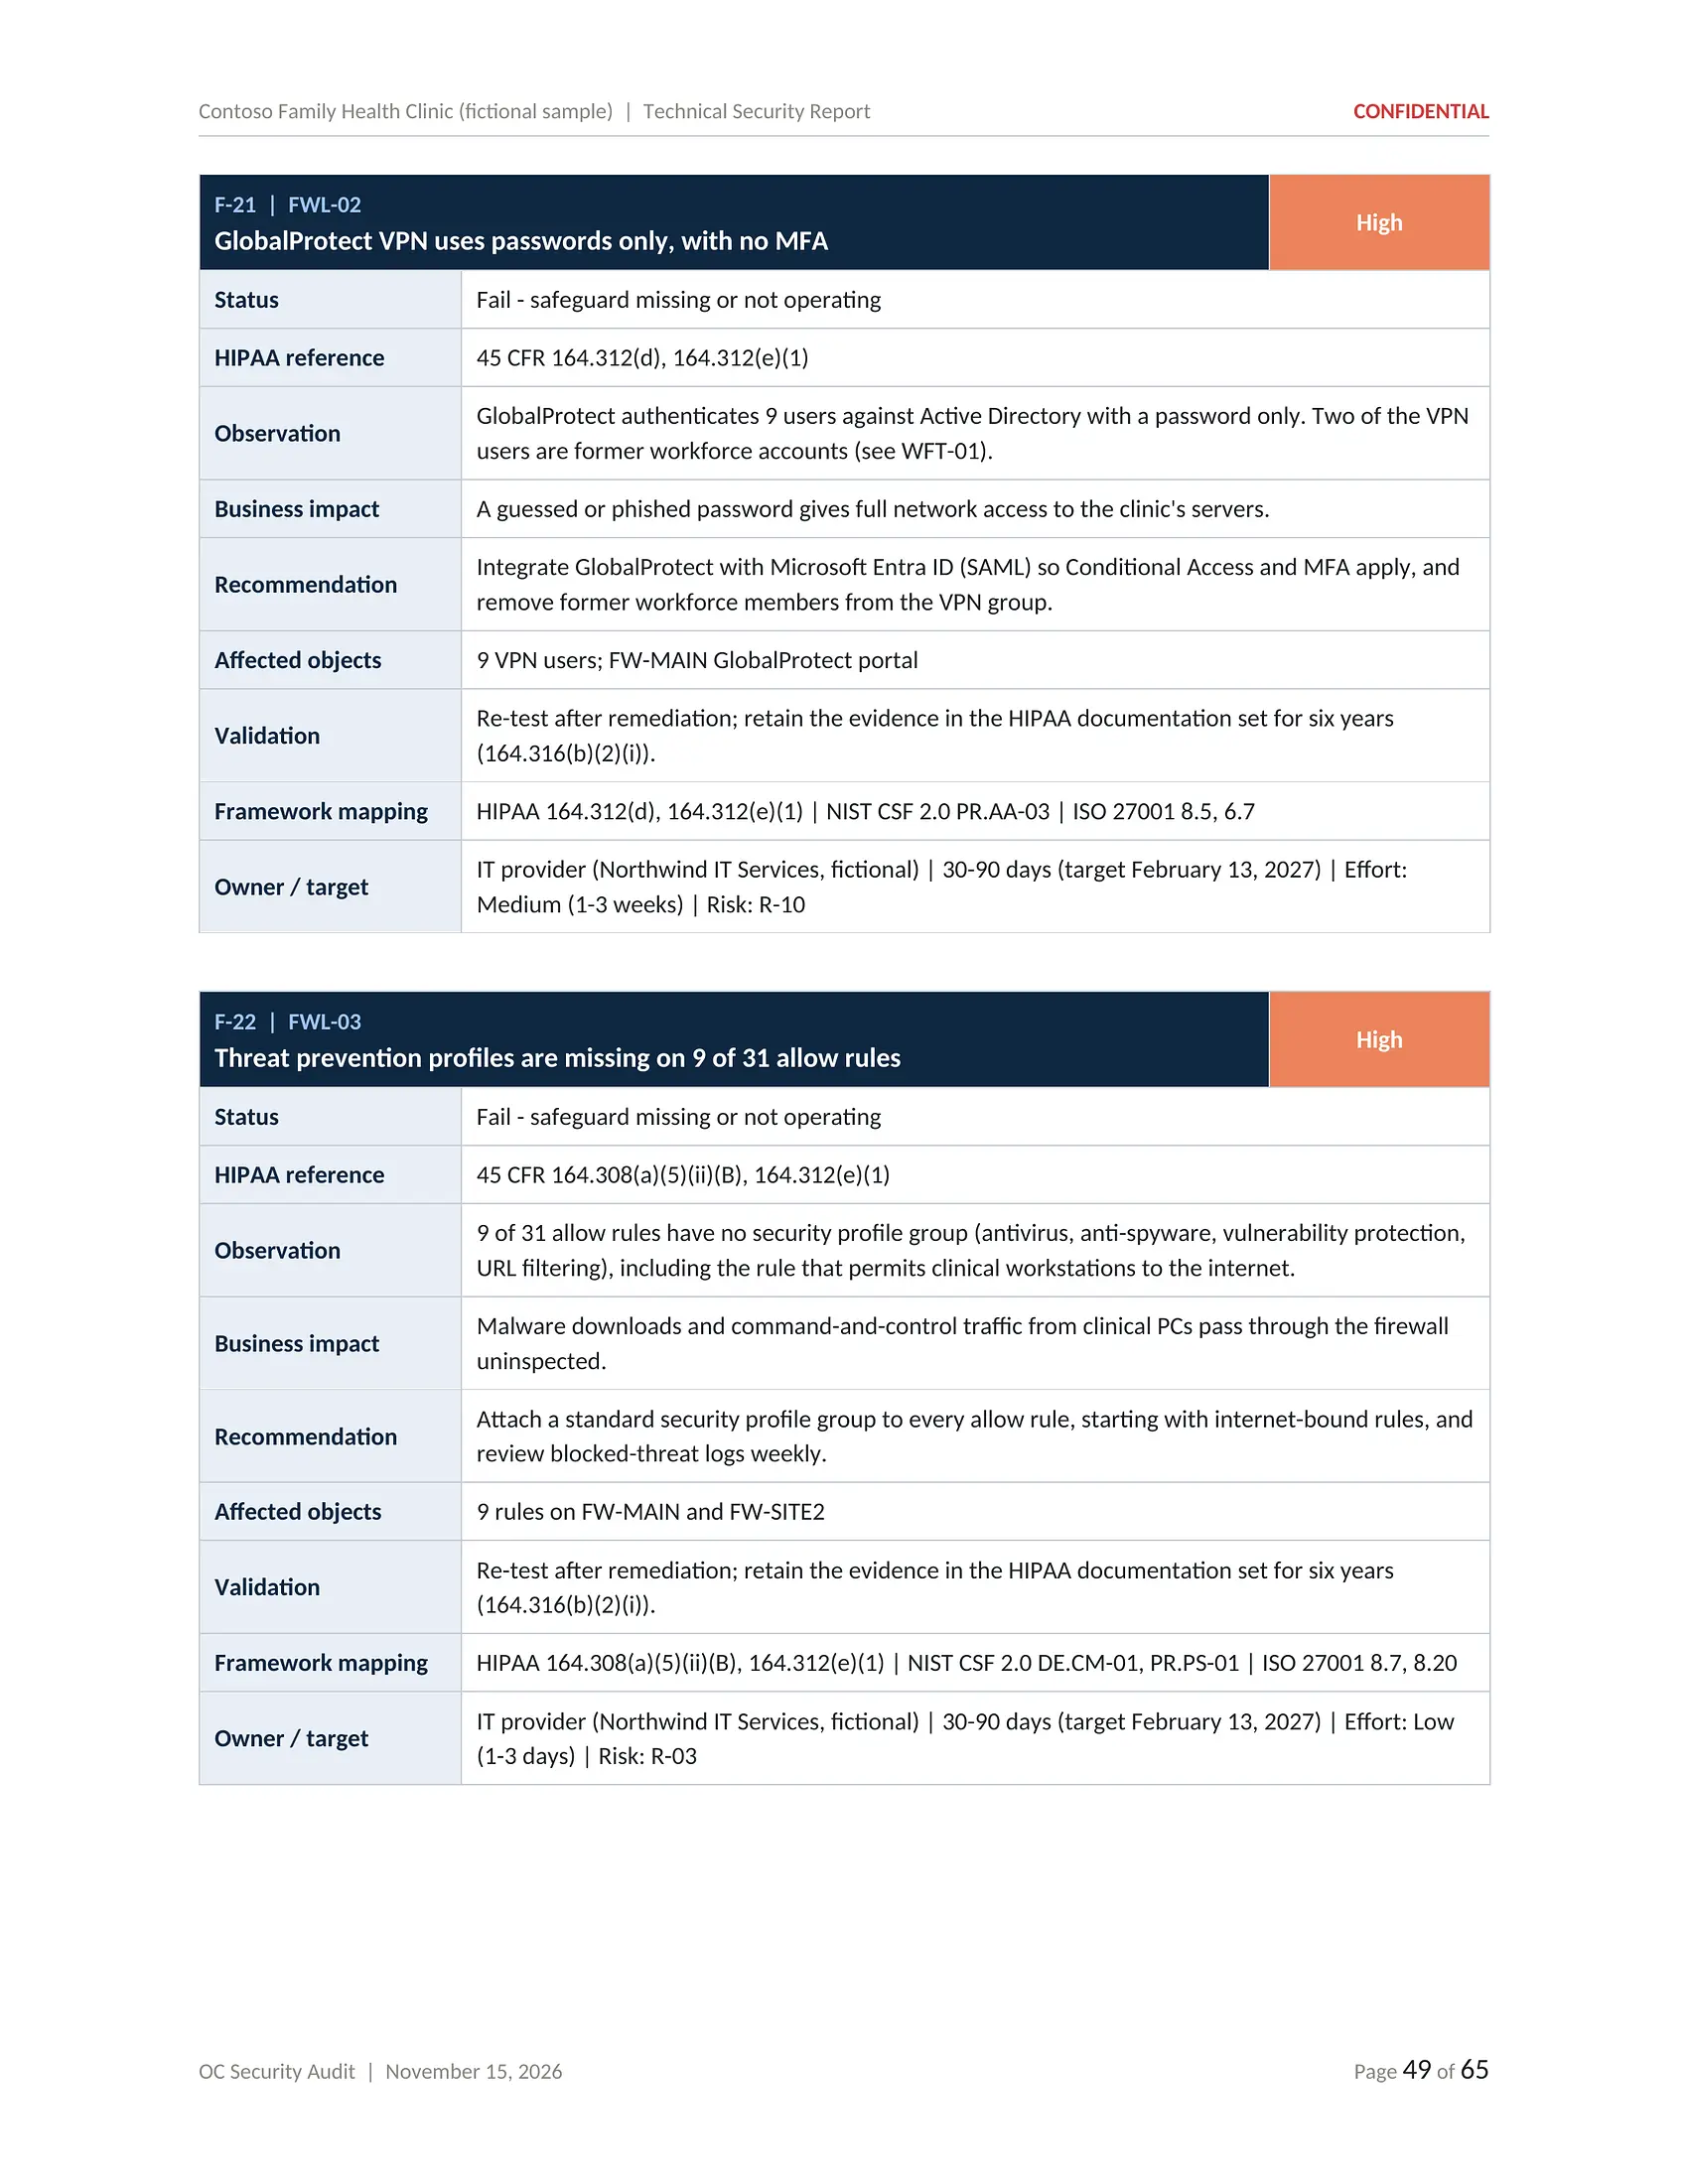
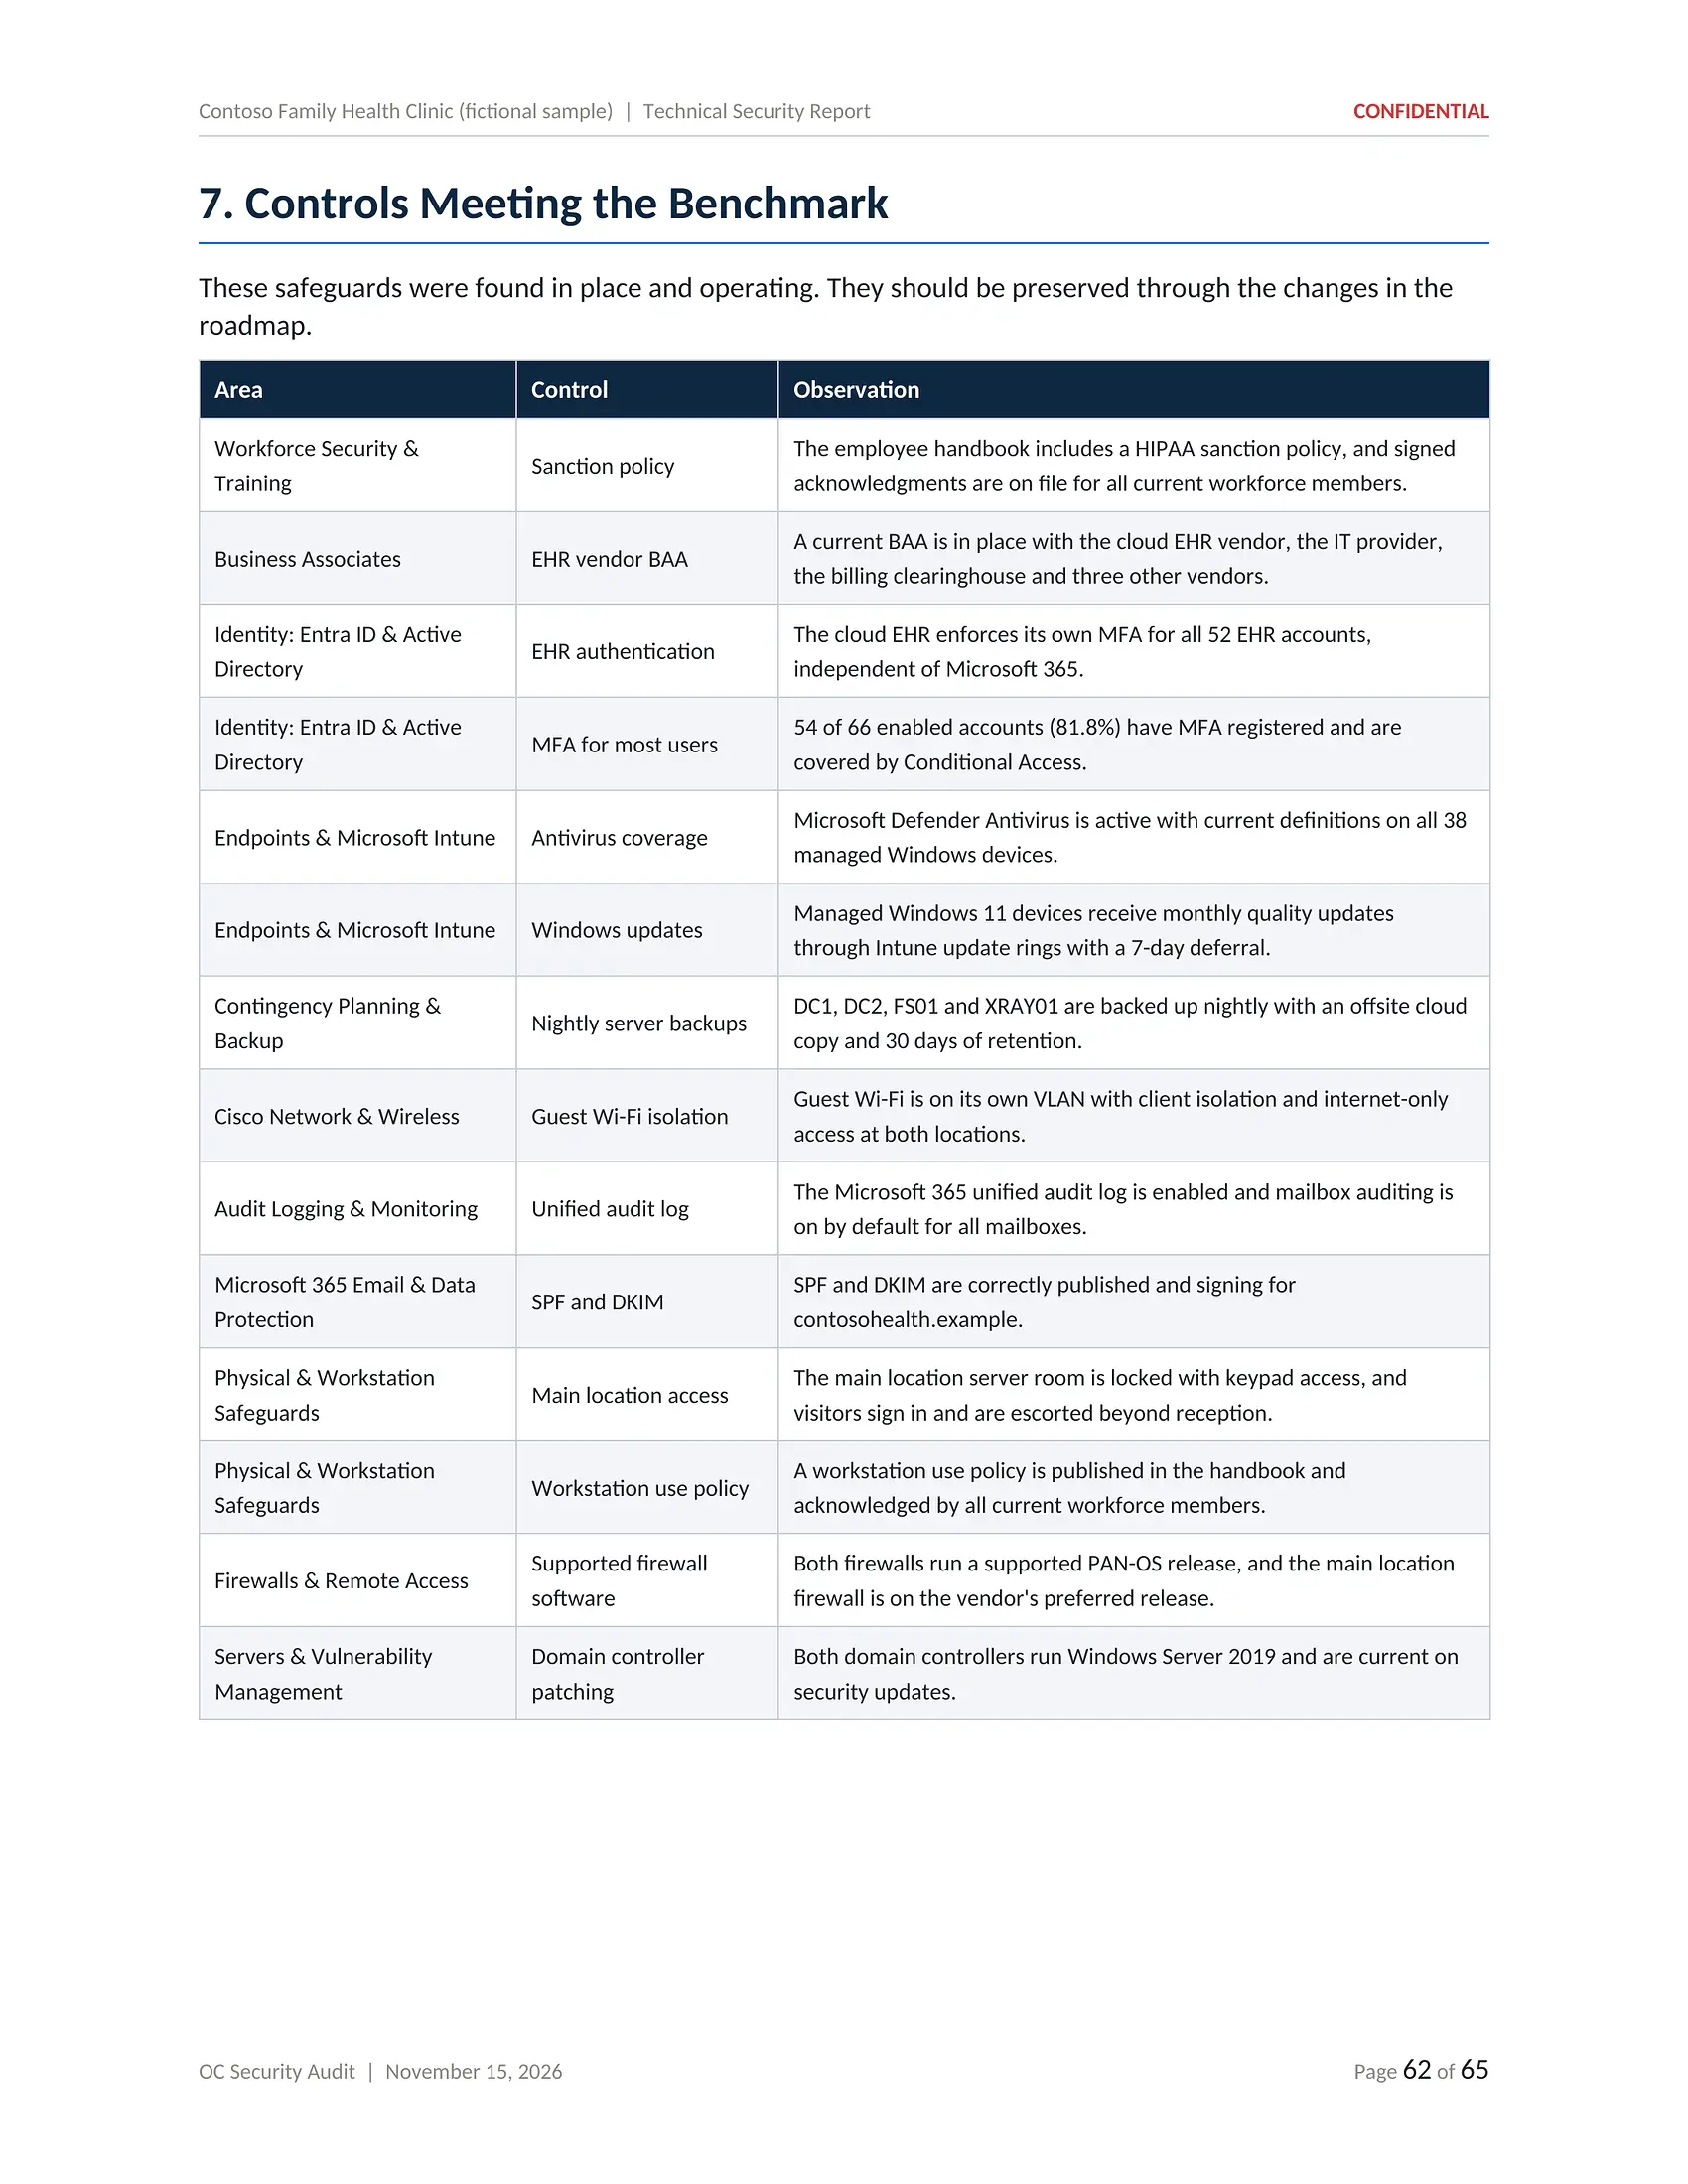
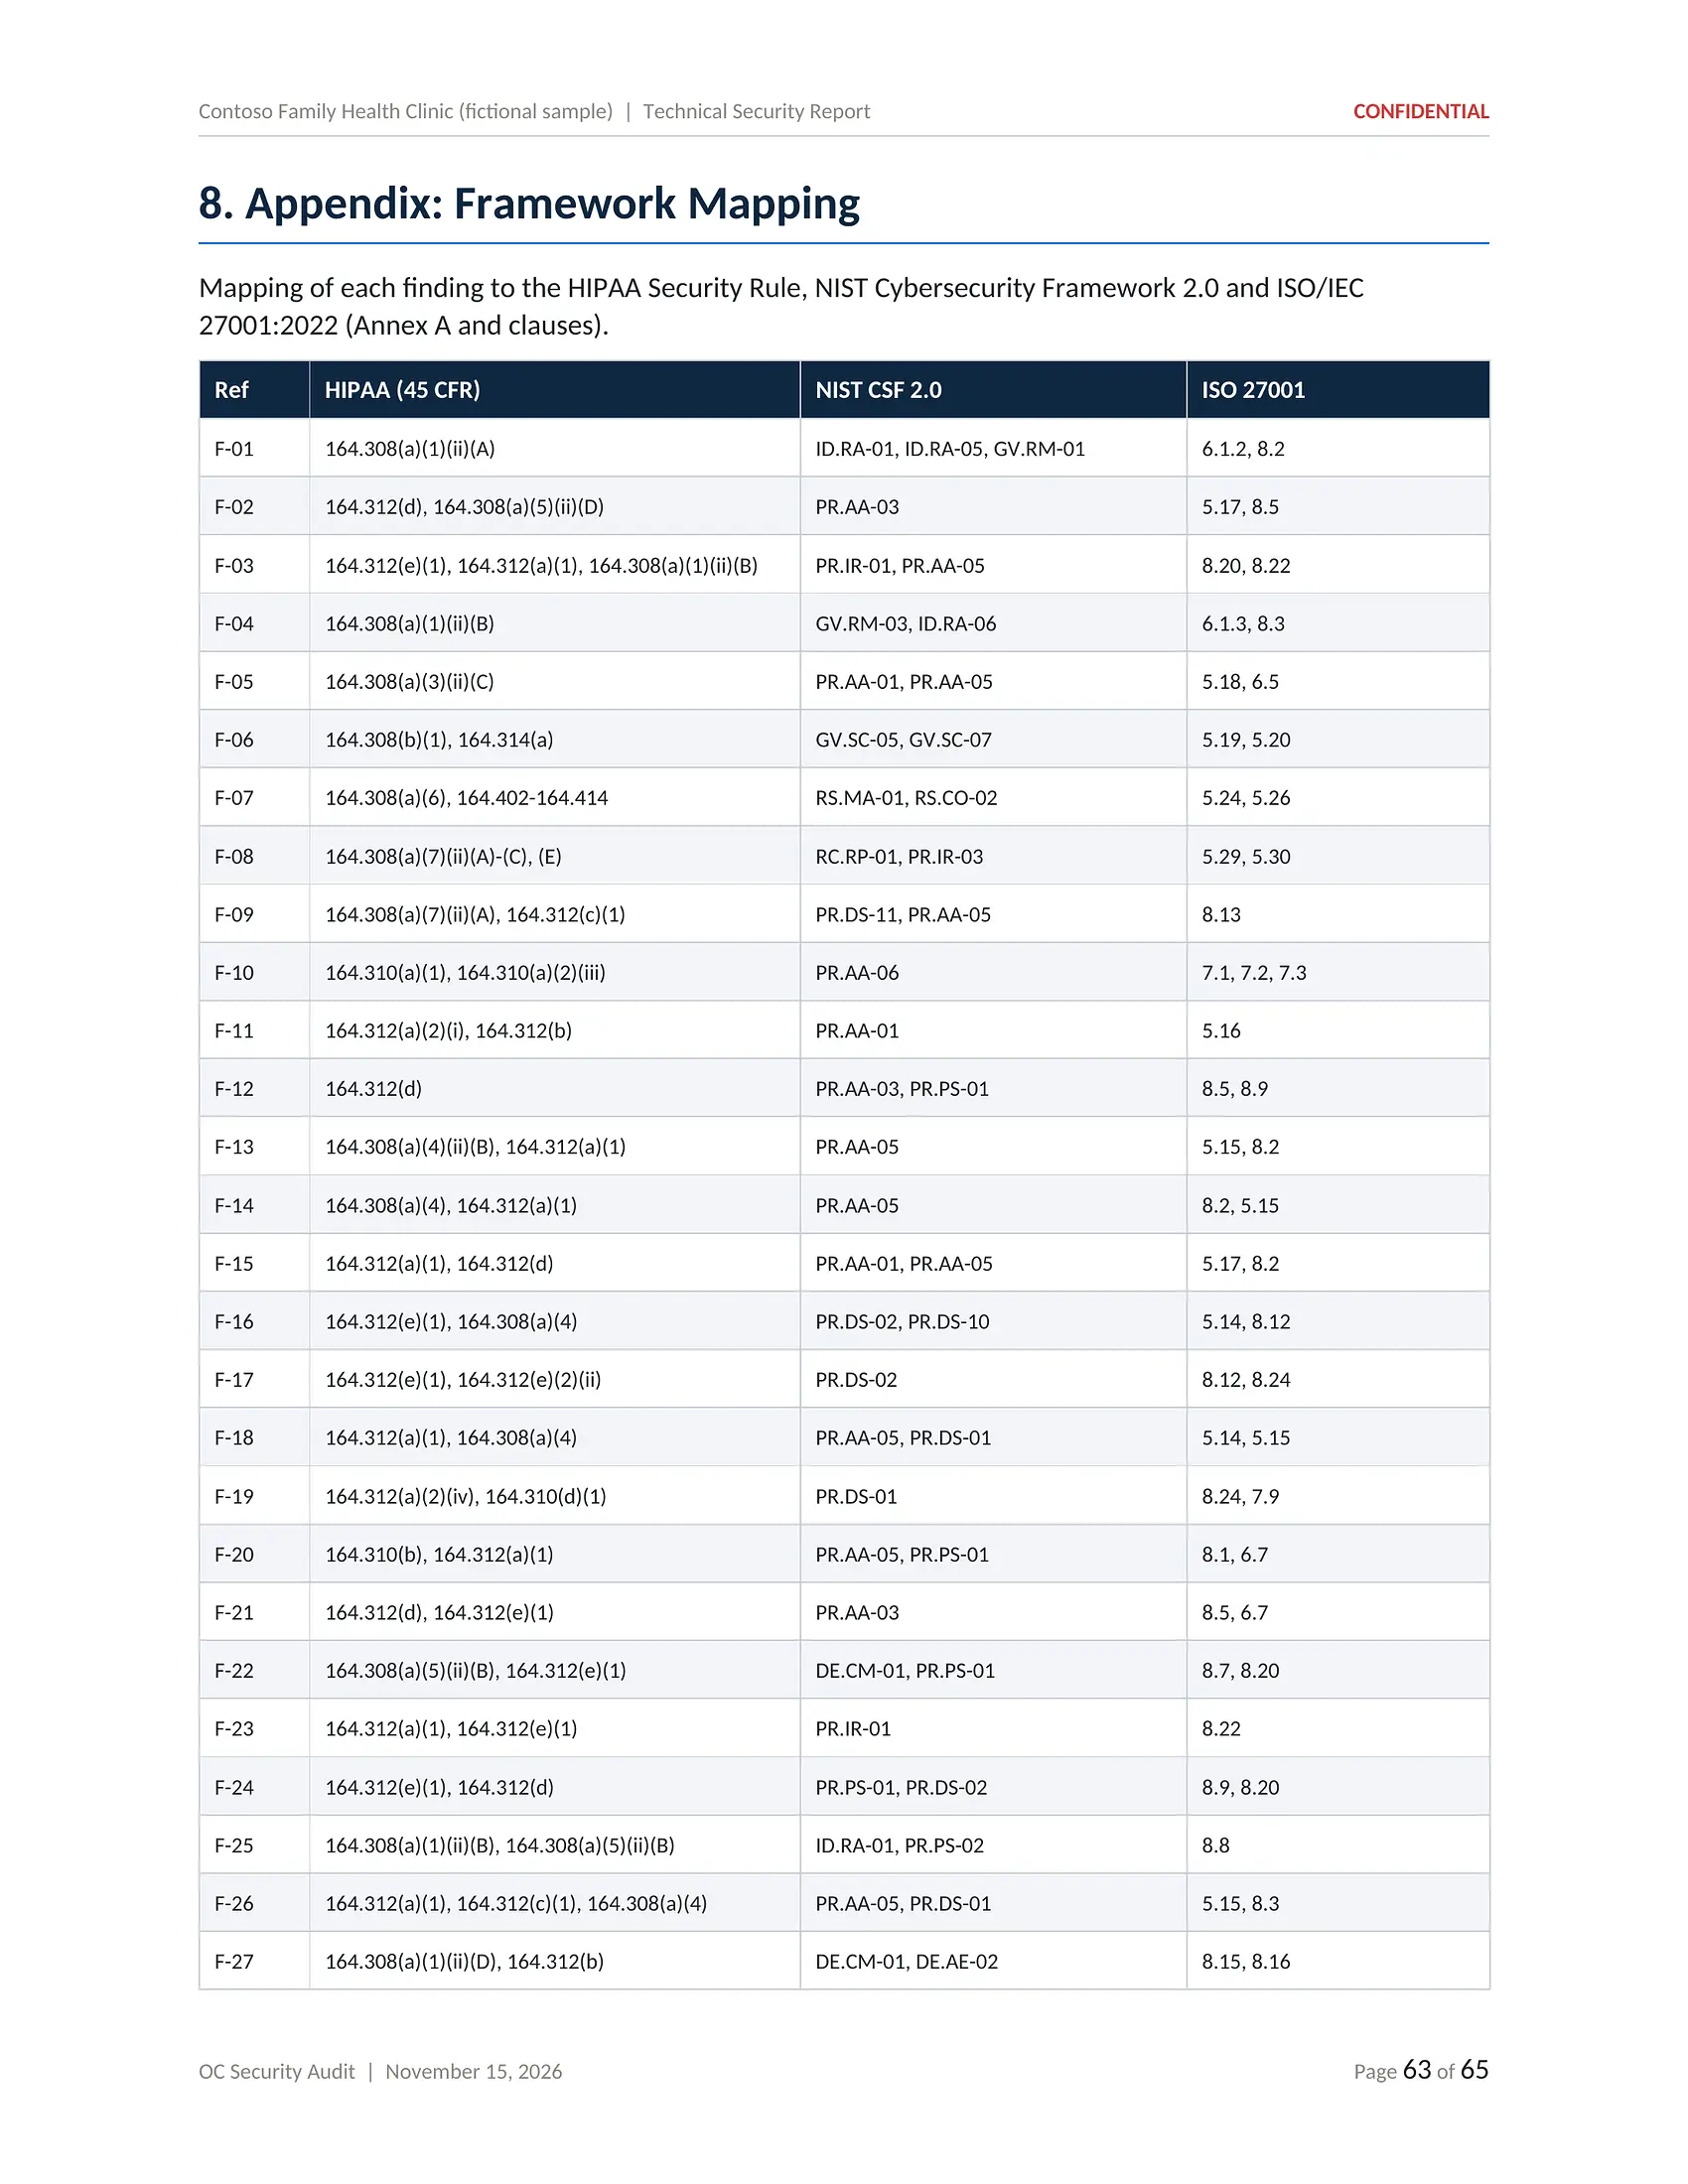
Click the page in the centre to open it full size and zoom in.
Deliverable 3 of 5 · PDF and Word · 18 pages · landscape
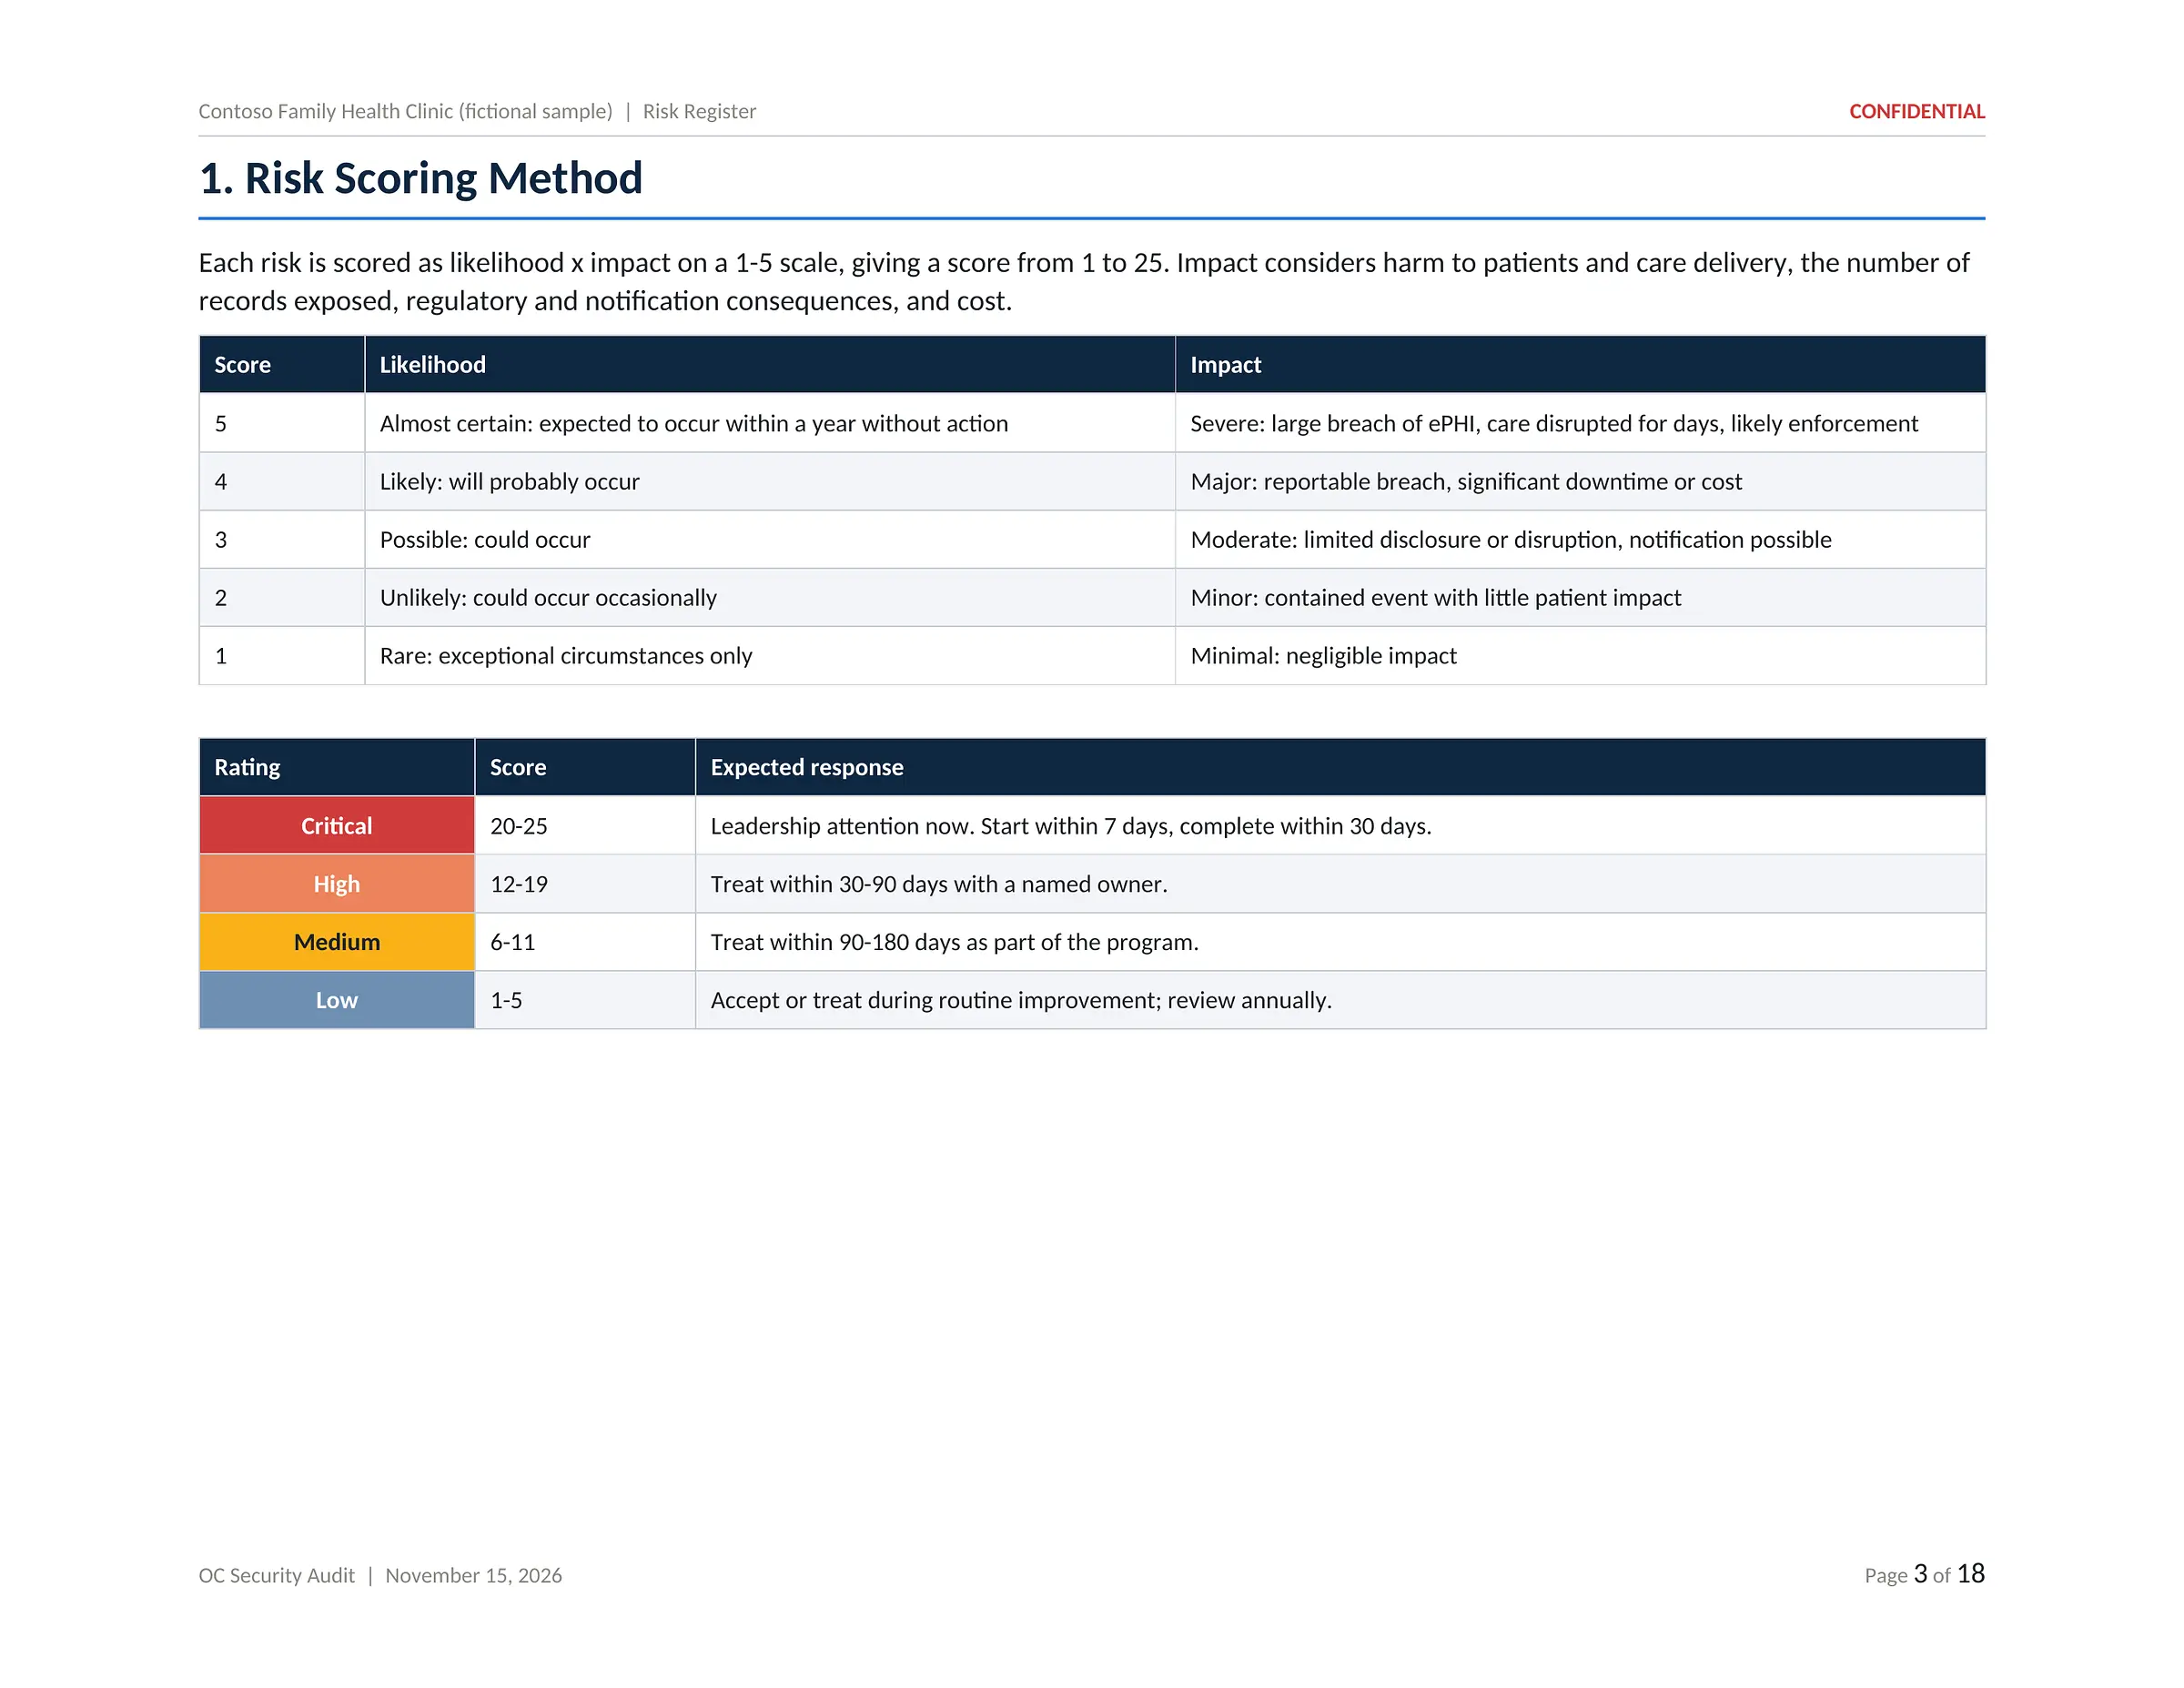
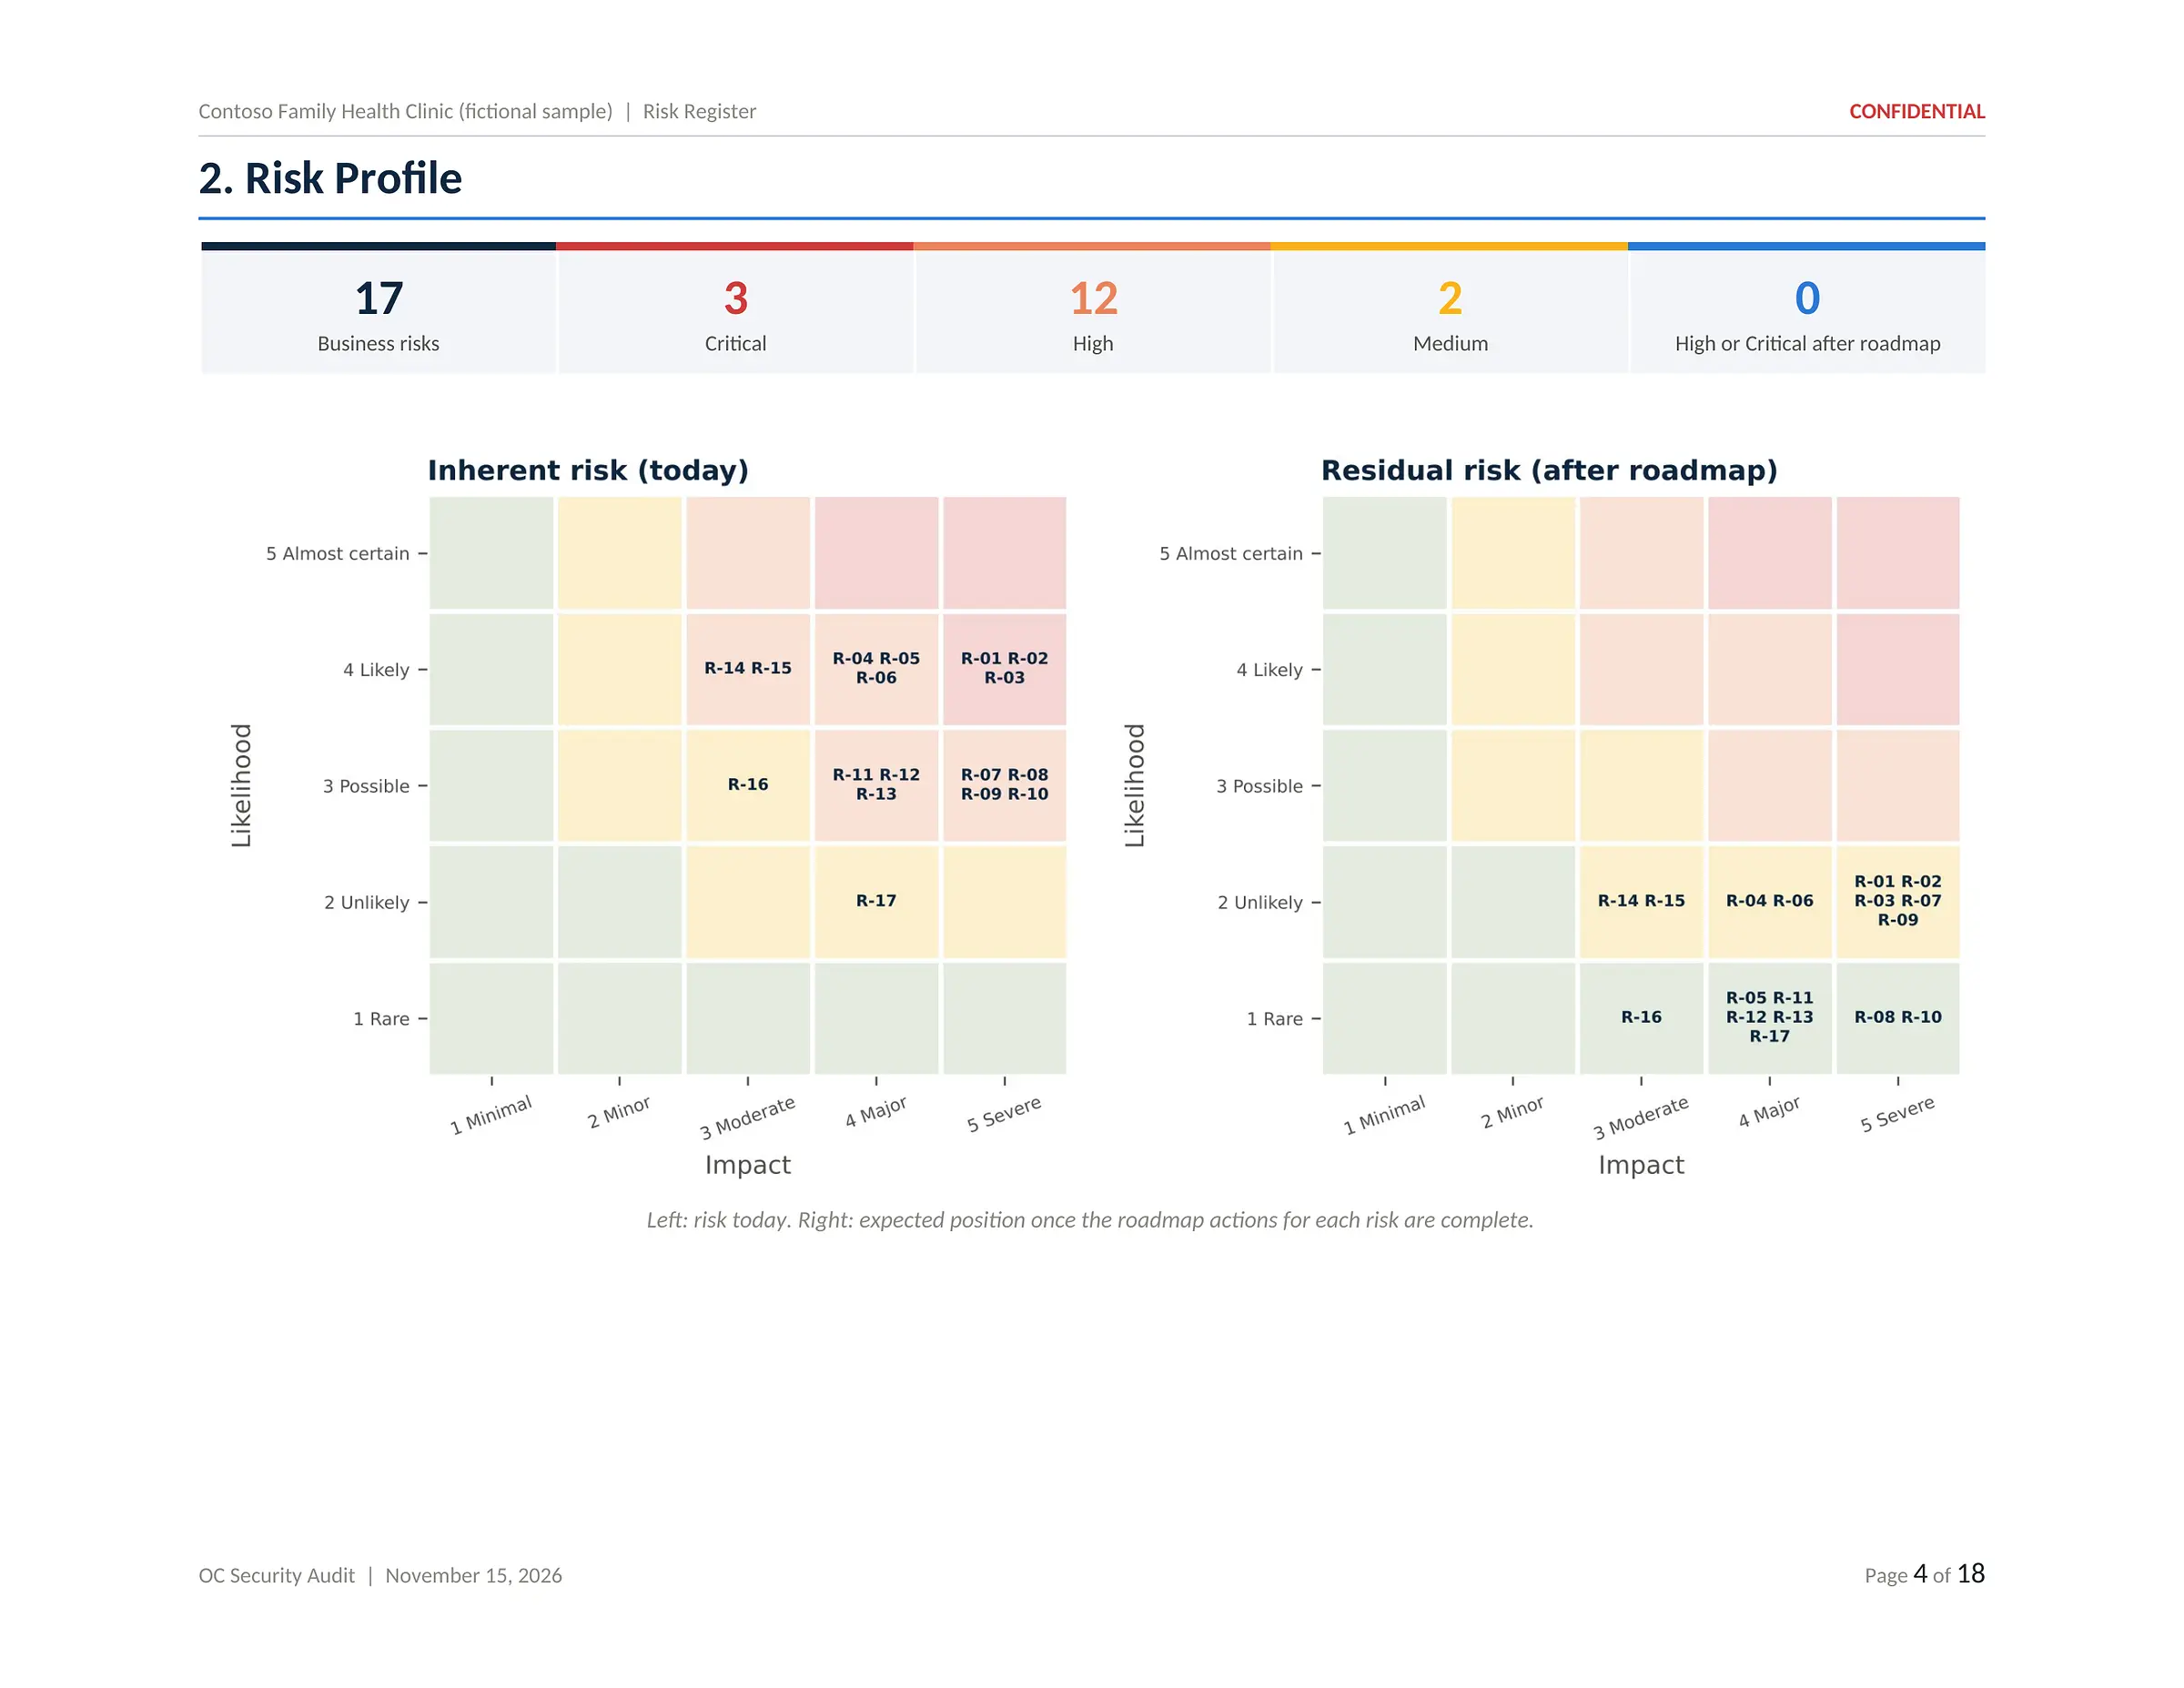
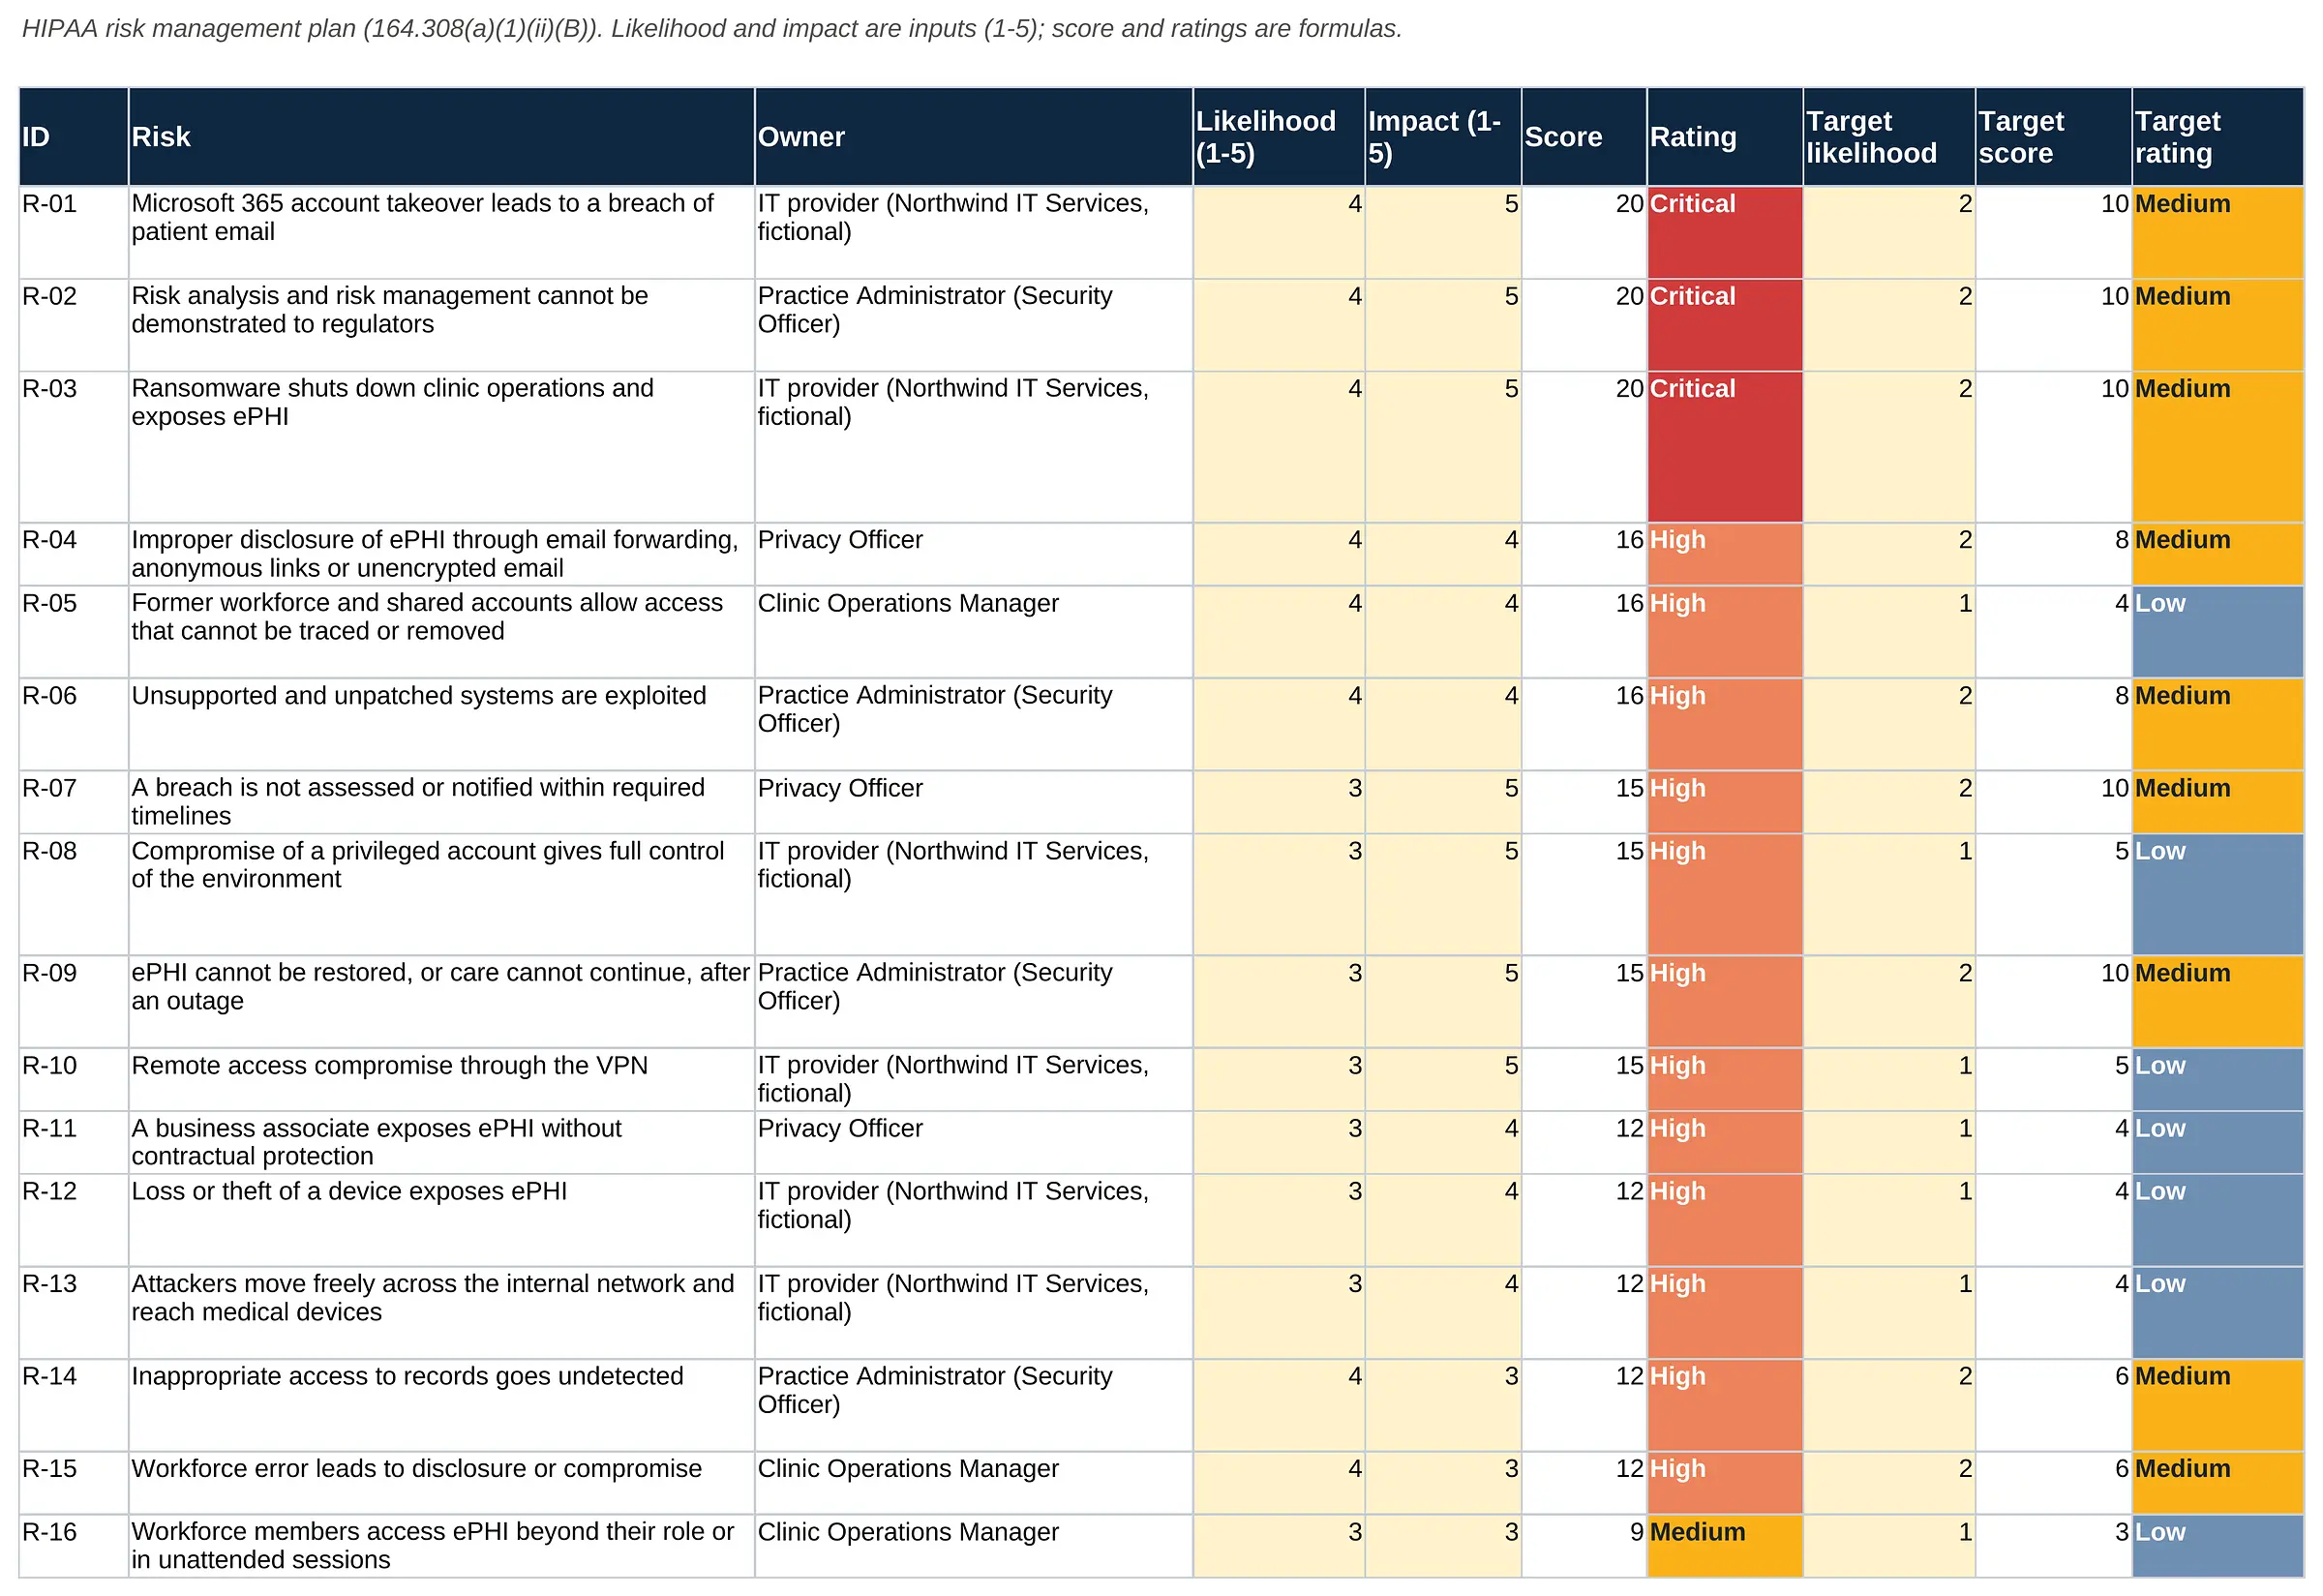
The 64 findings rolled up into 17 business risks, each scored for likelihood and impact on patients, care delivery and the practice, with an owner, a treatment decision, a target rating and a due date. It is the backbone of an ongoing risk management plan.
Who uses it
HIPAA Security Officer, practice leadership at the monthly risk review, your cyber insurance broker and anyone who asks how risk is being managed.
What is included
SAMPLE · Contoso Family Health Clinic (fictional)
1 / 9
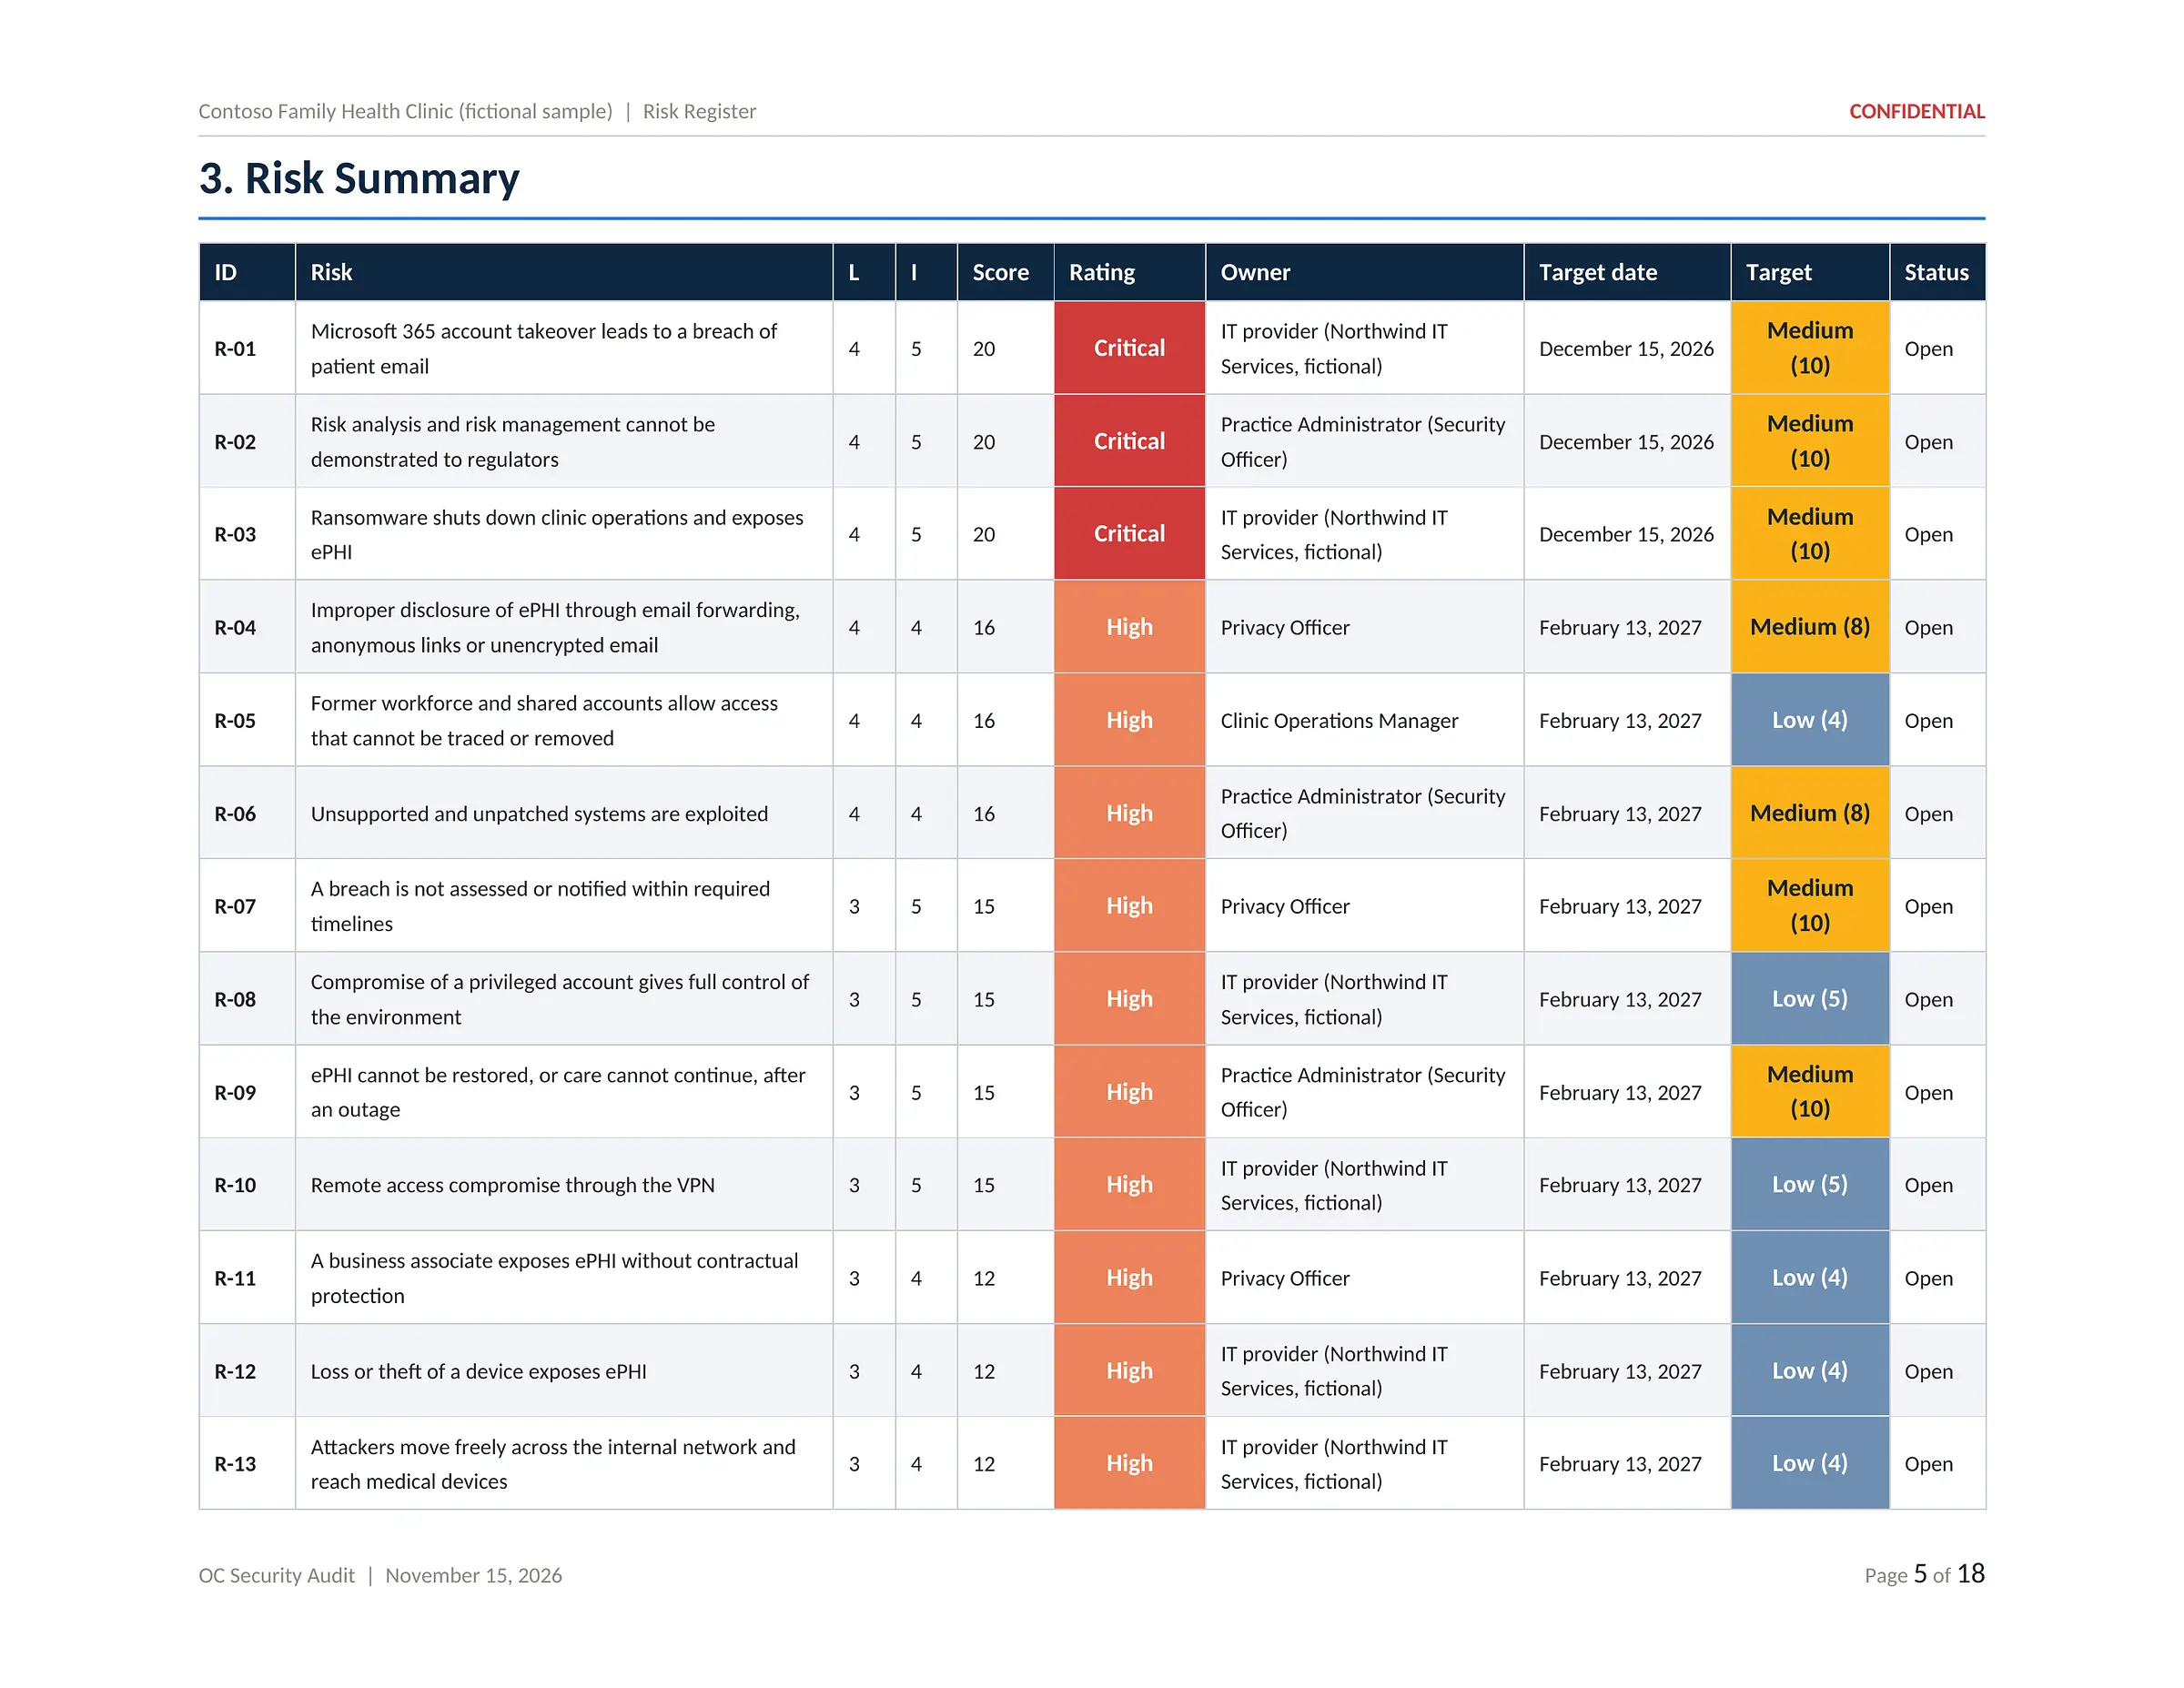
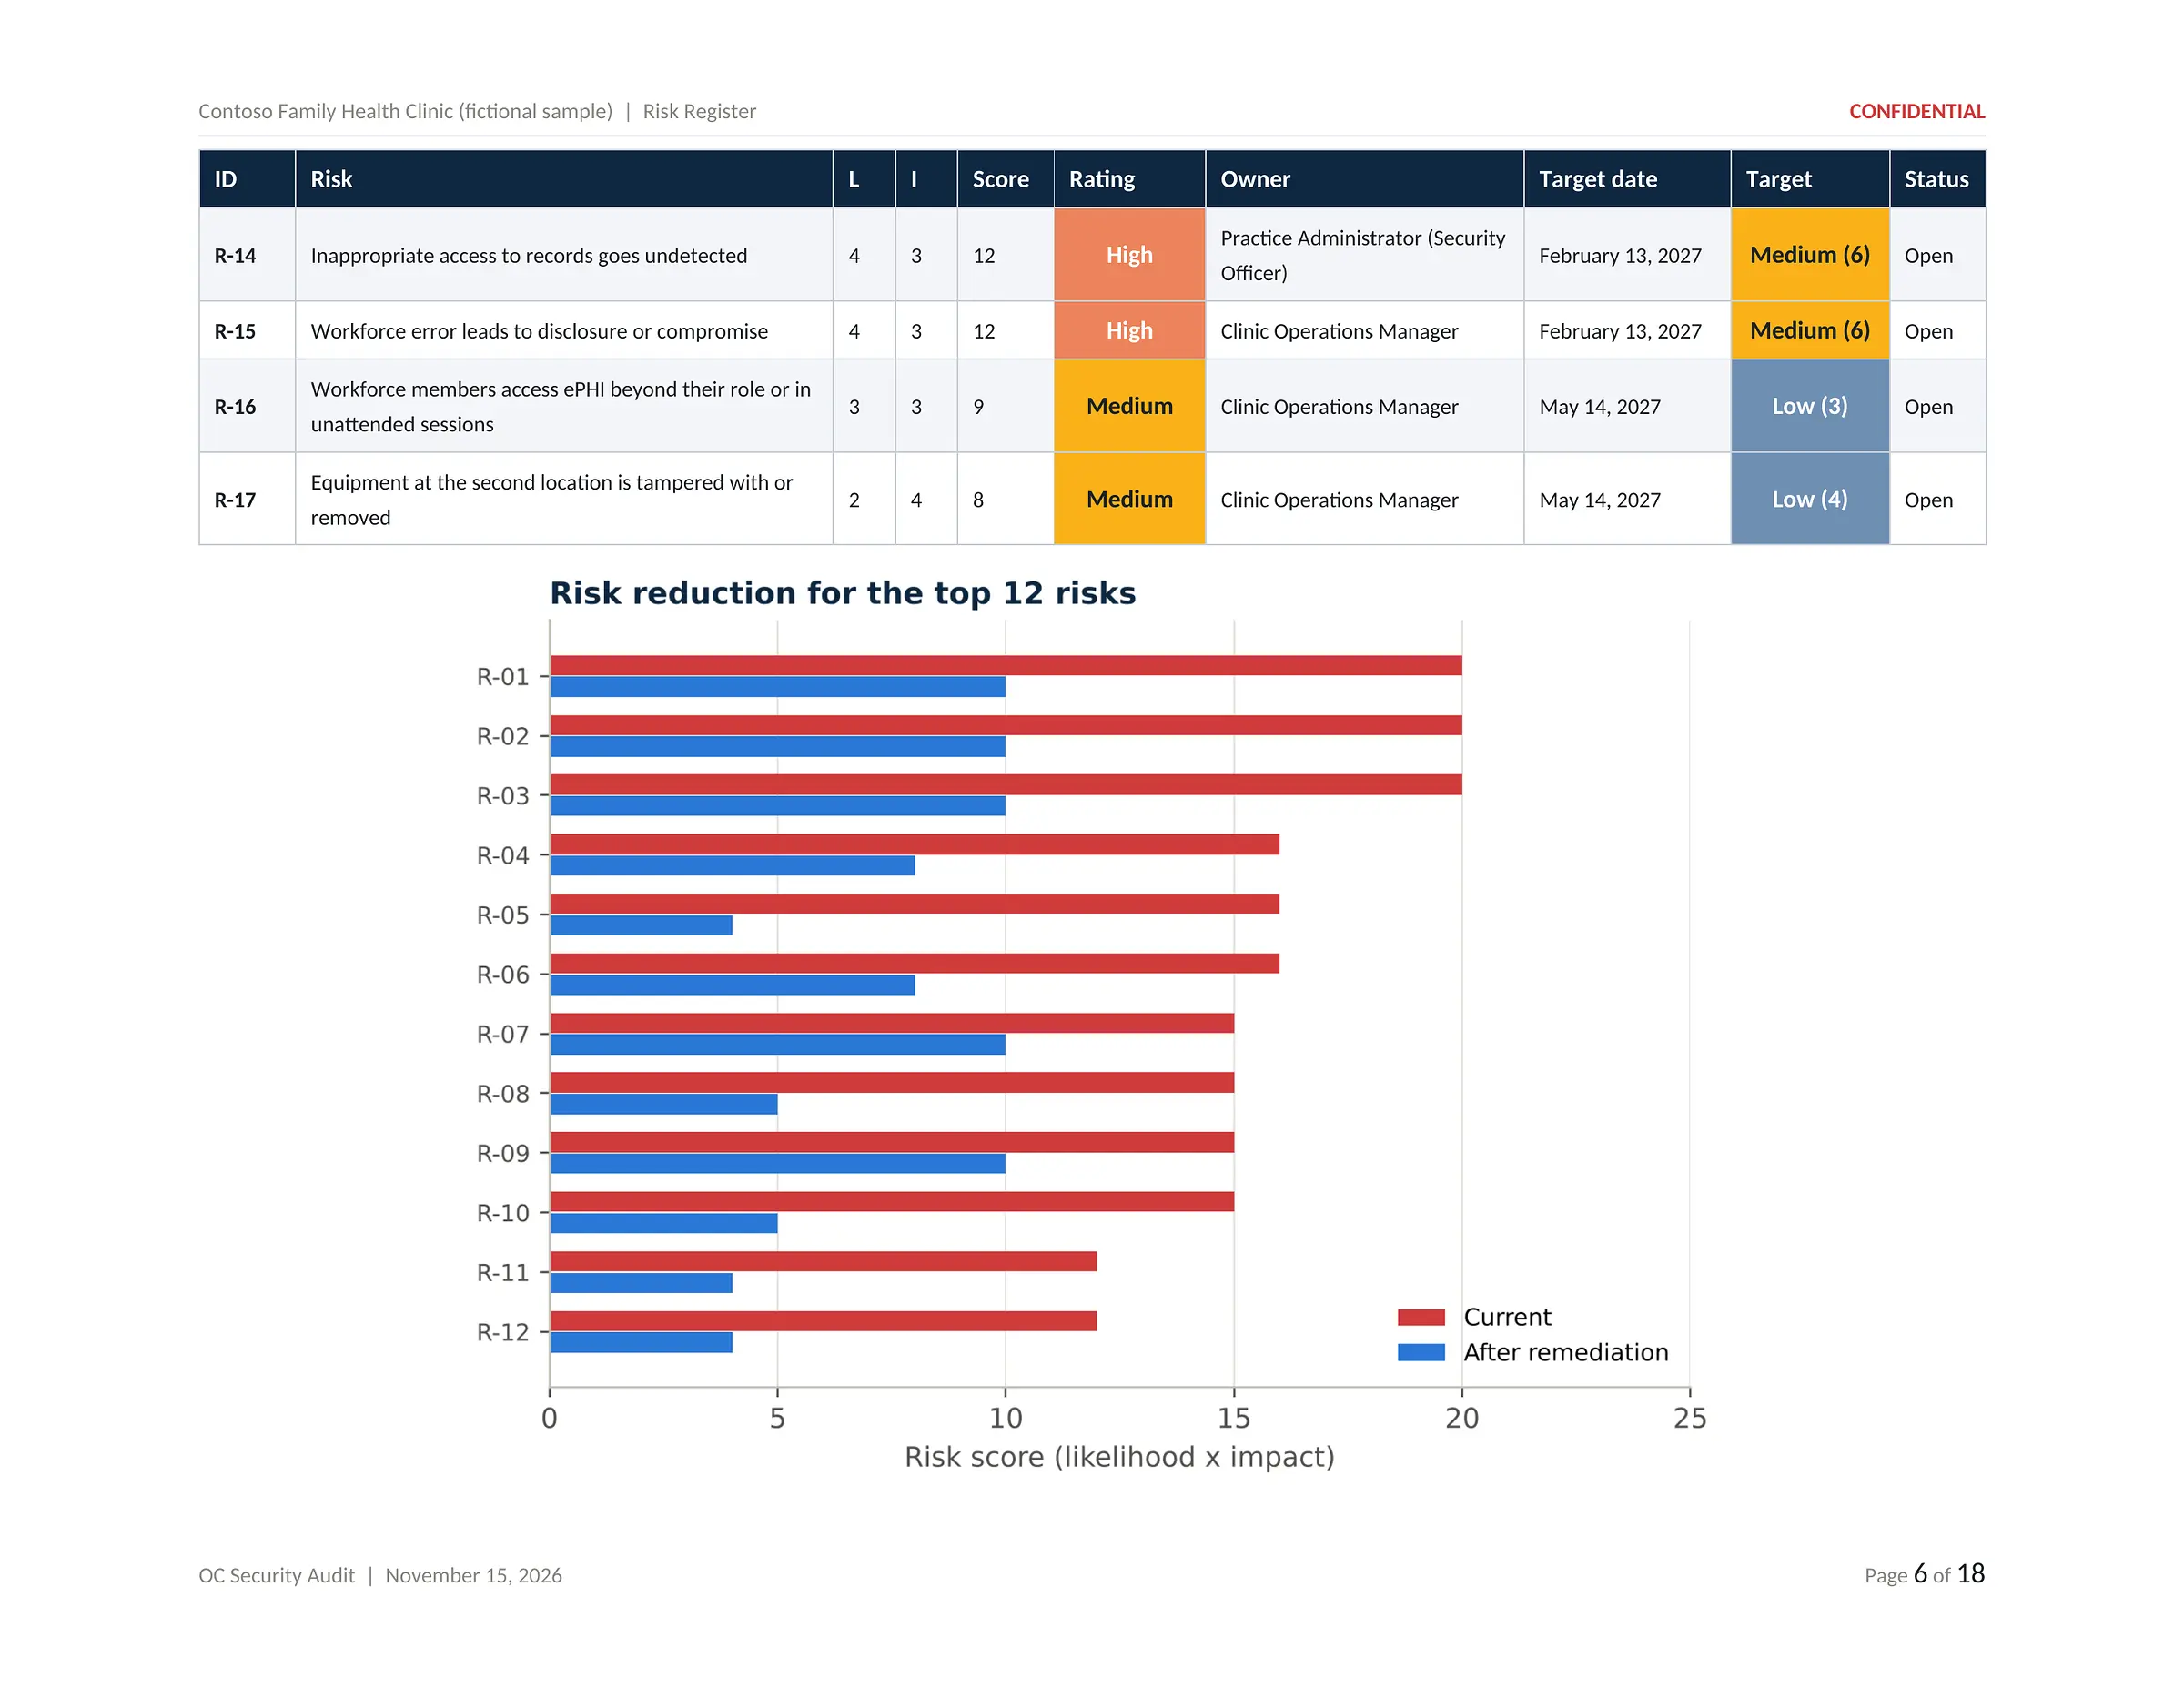
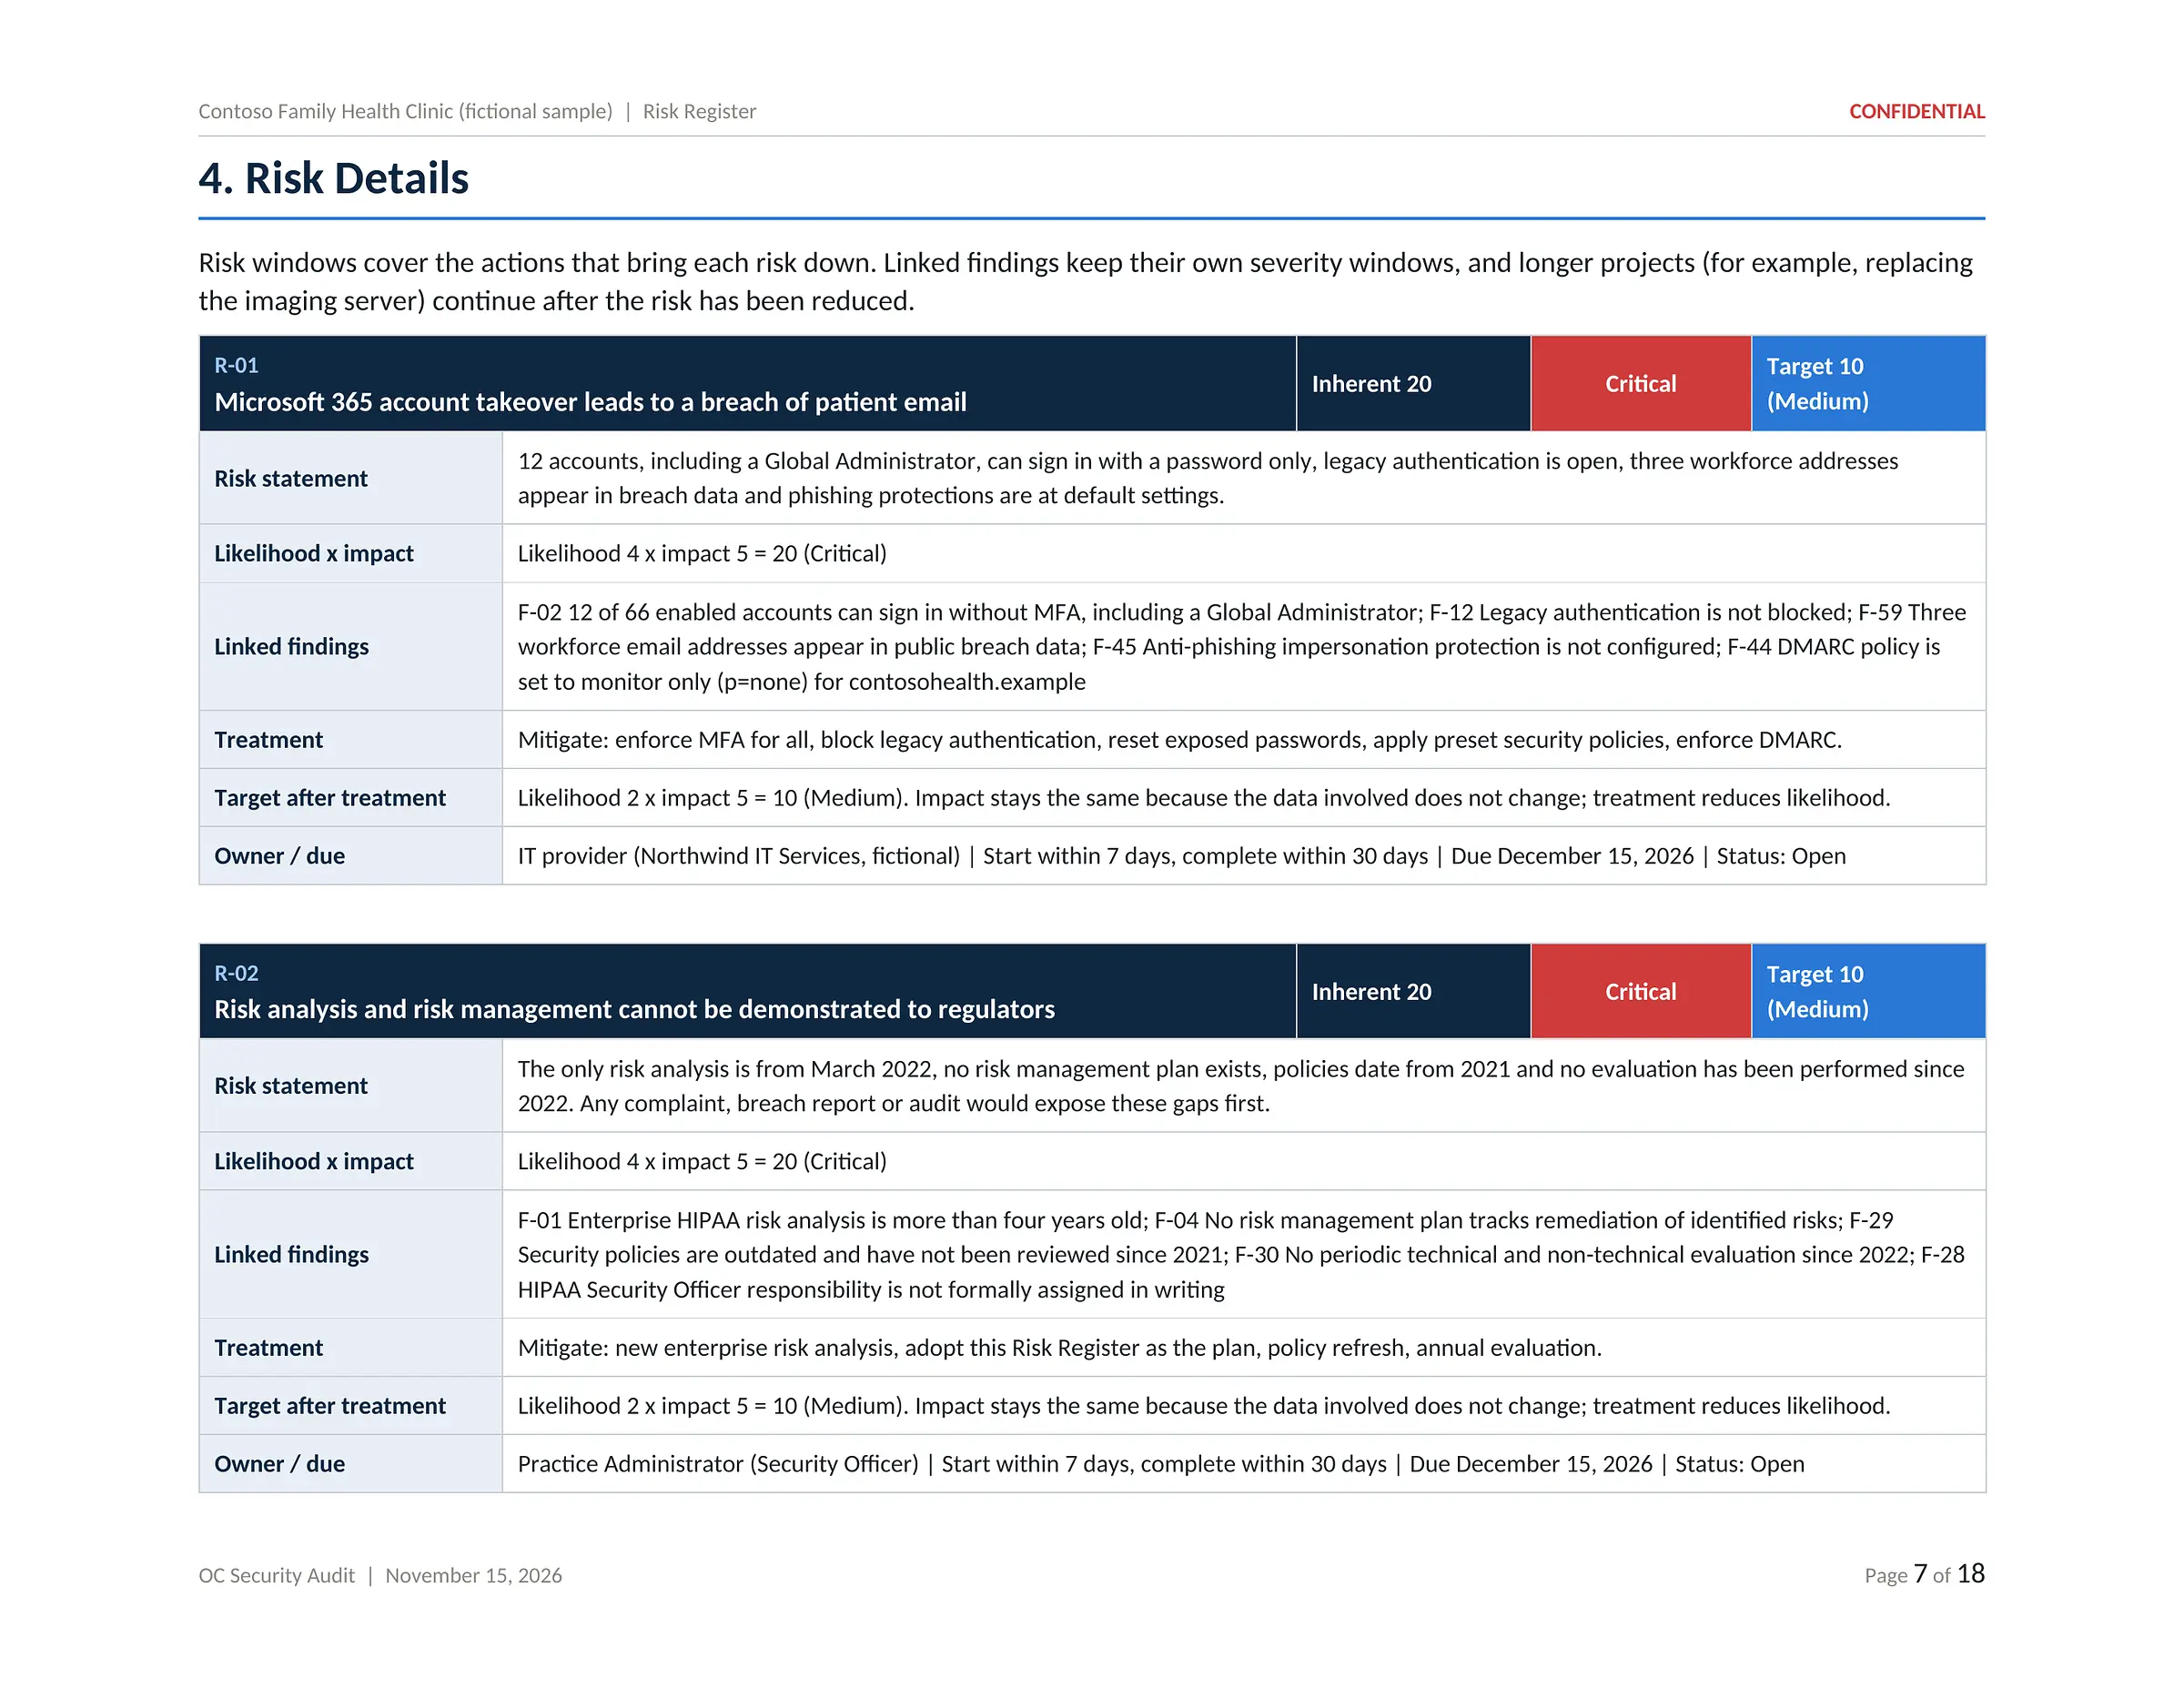
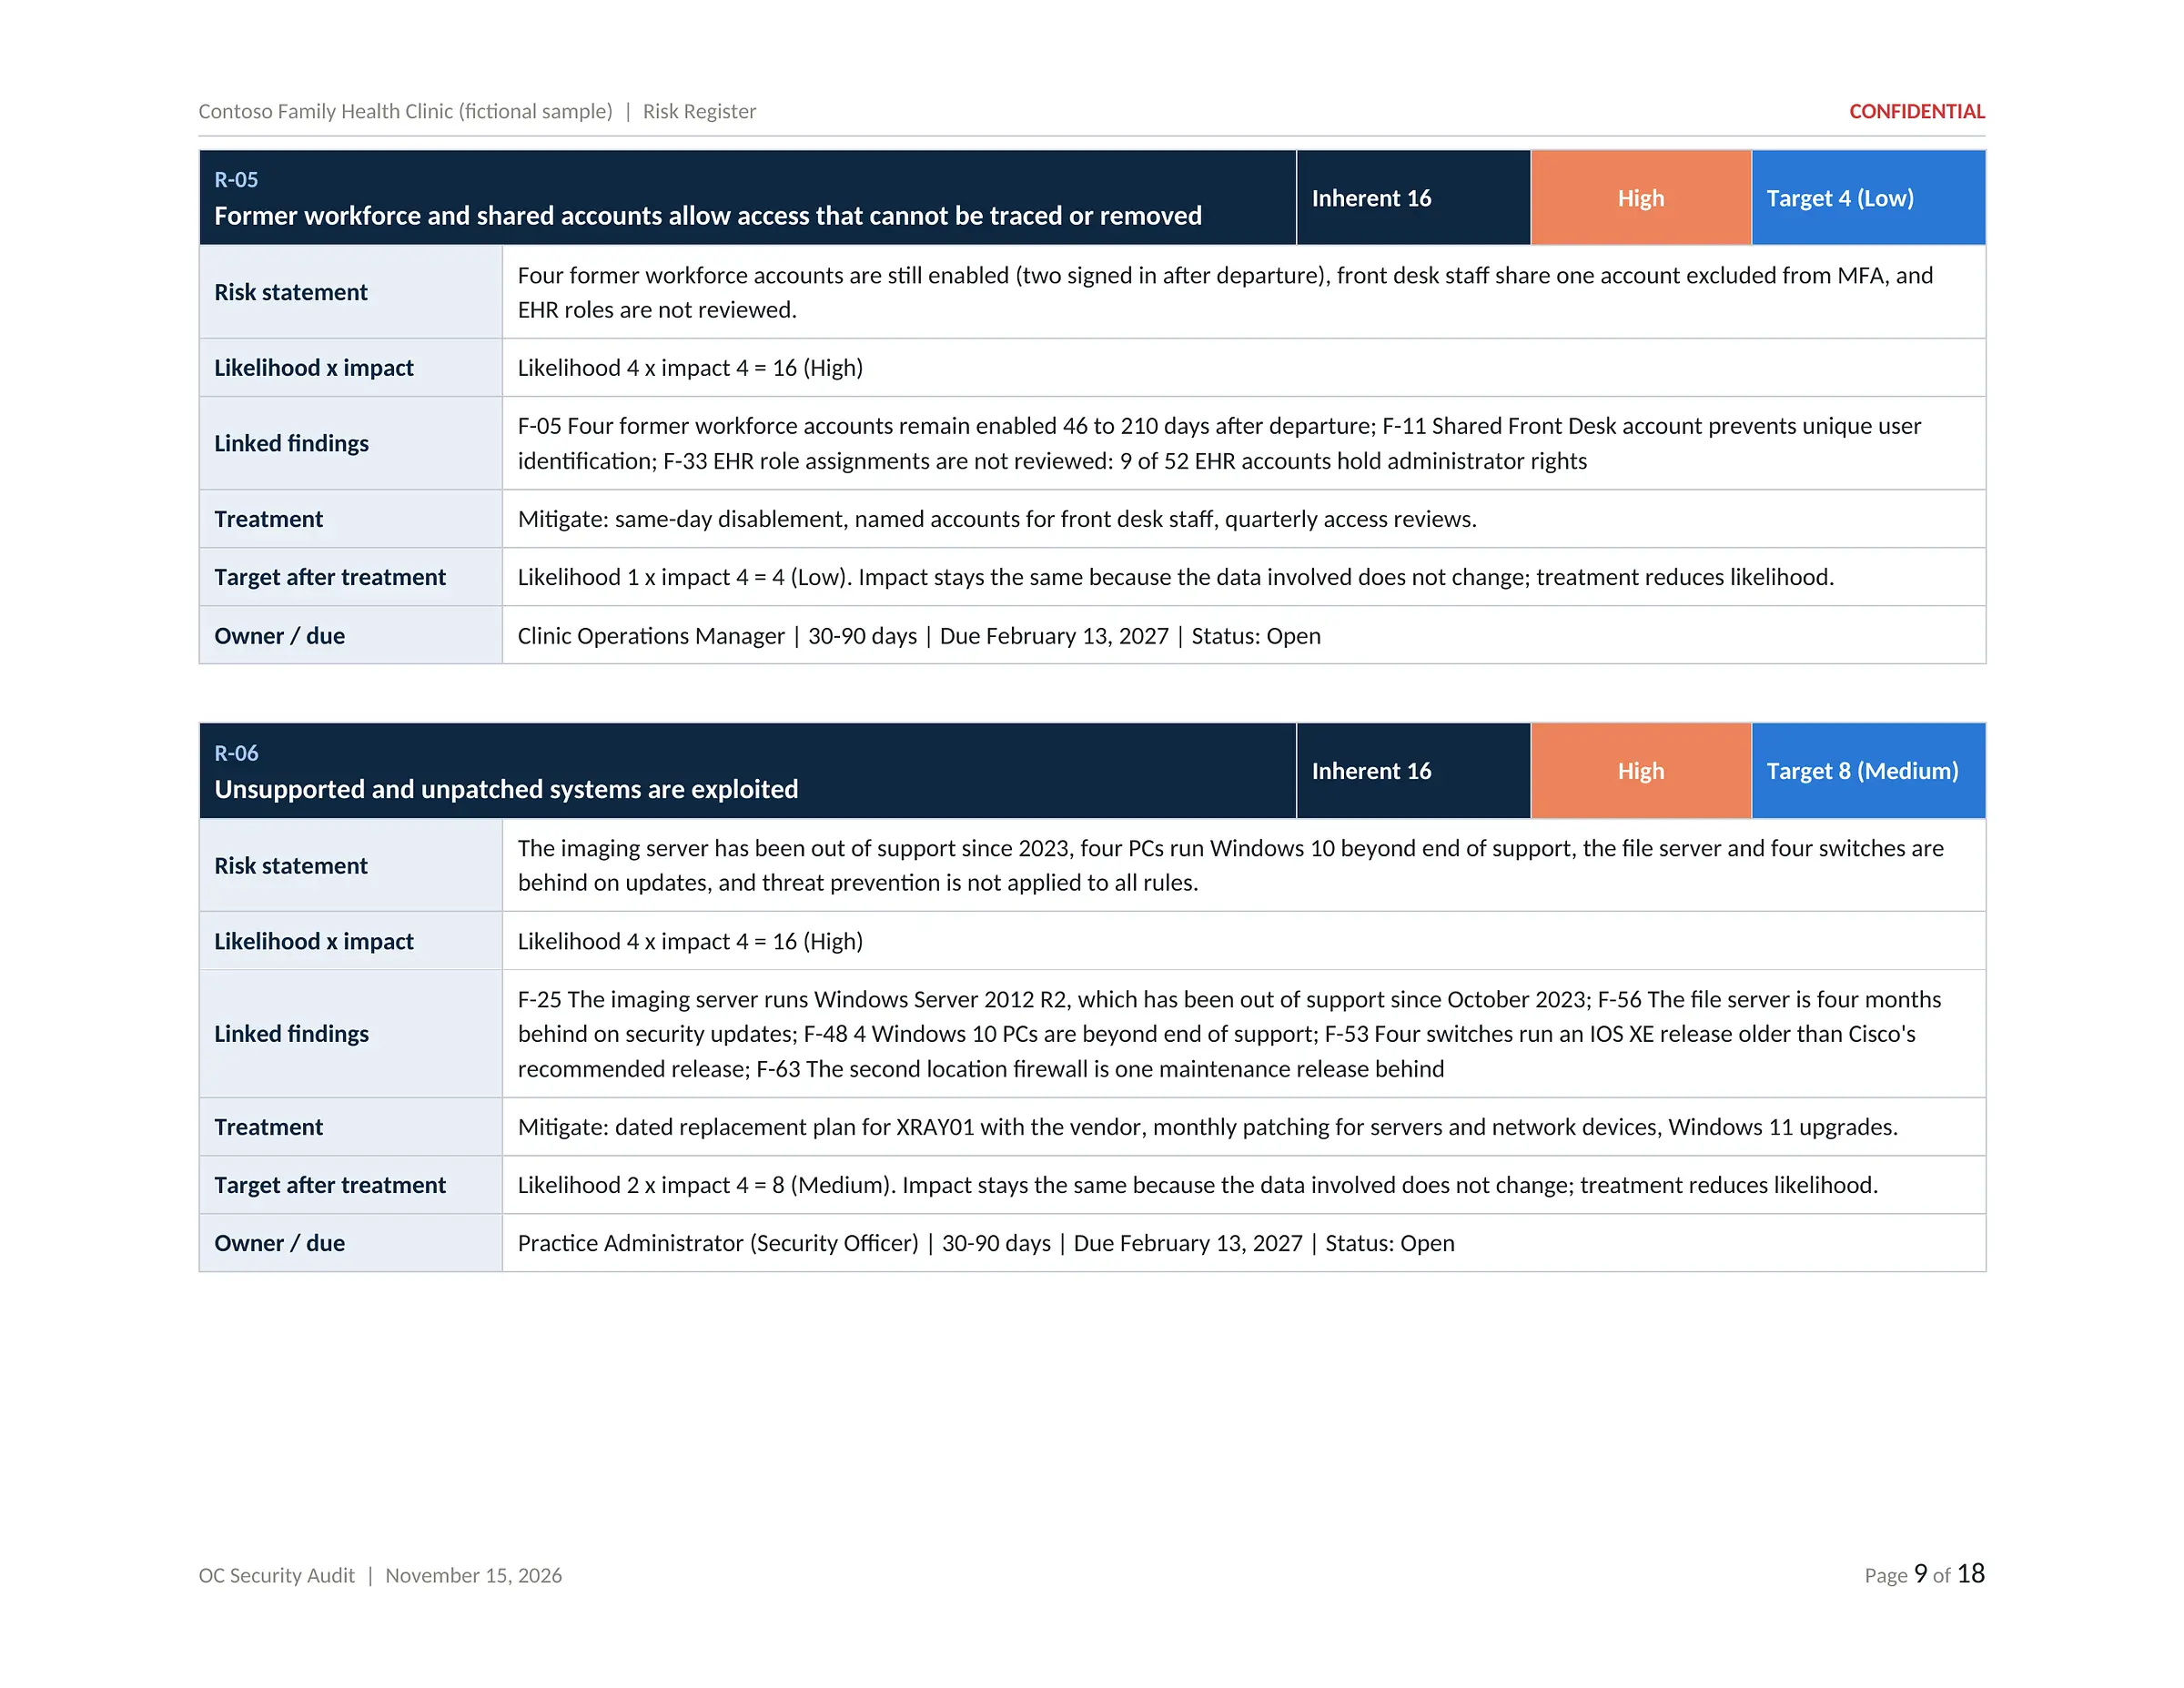
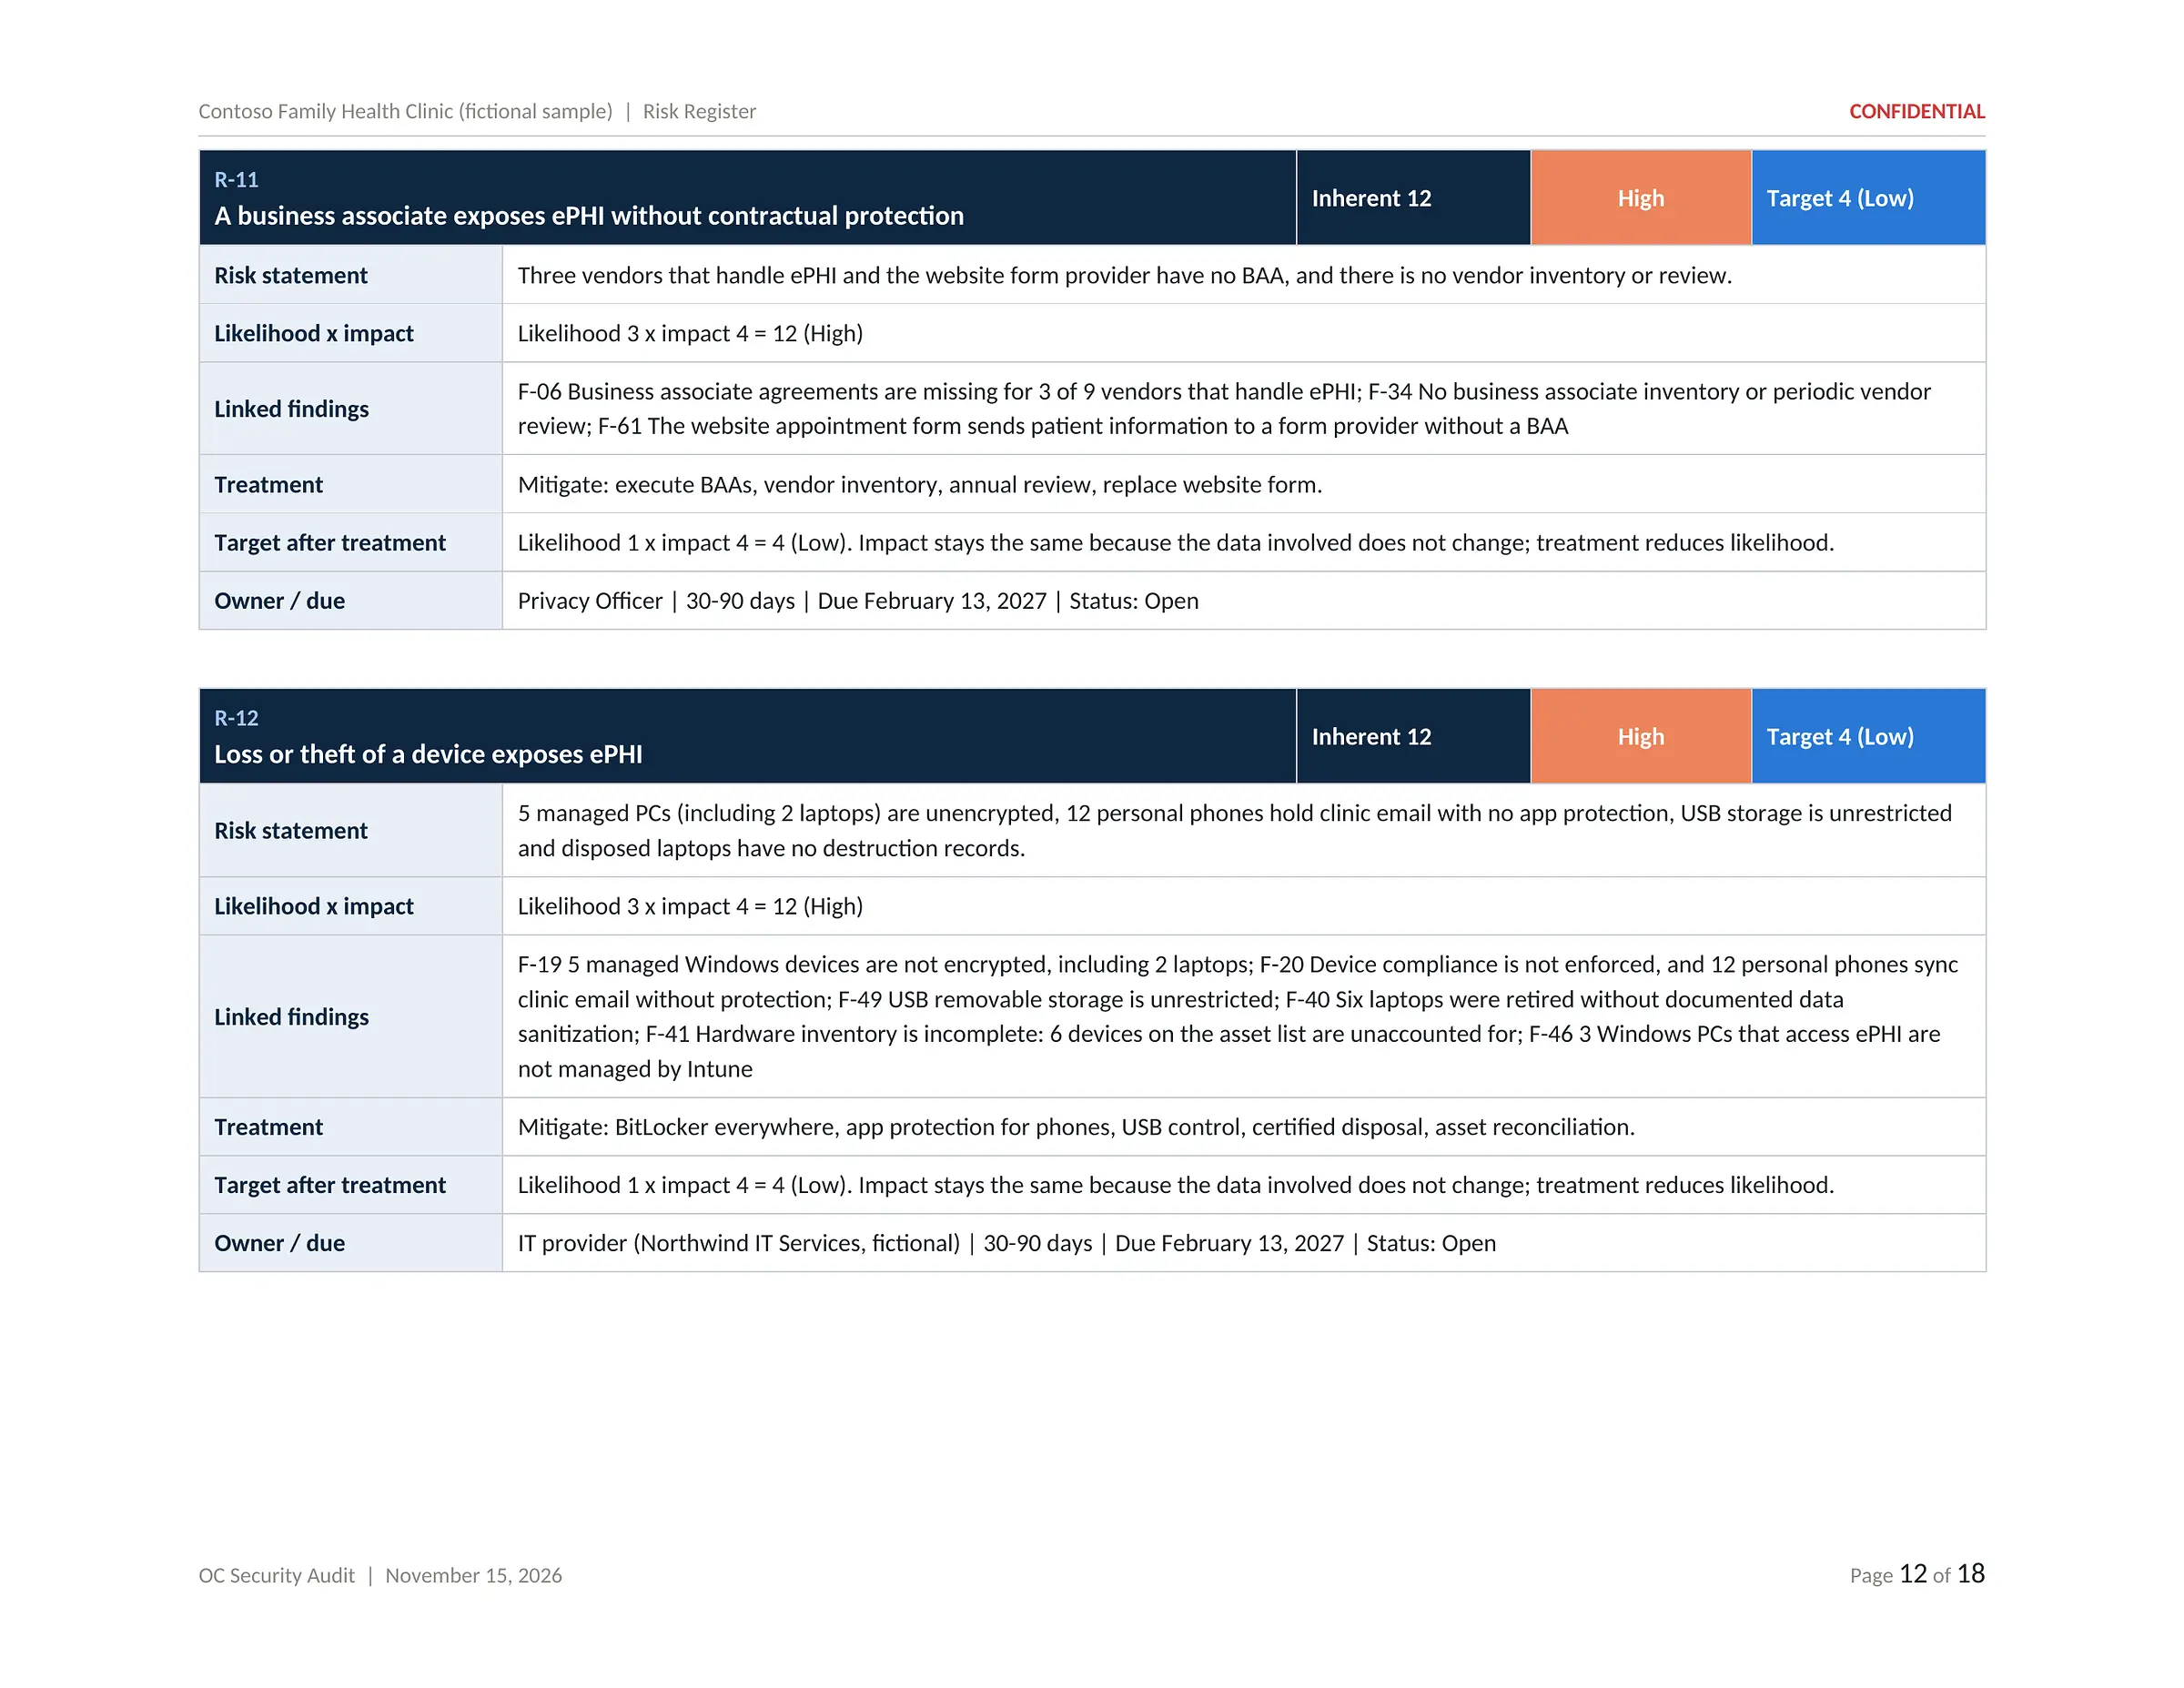
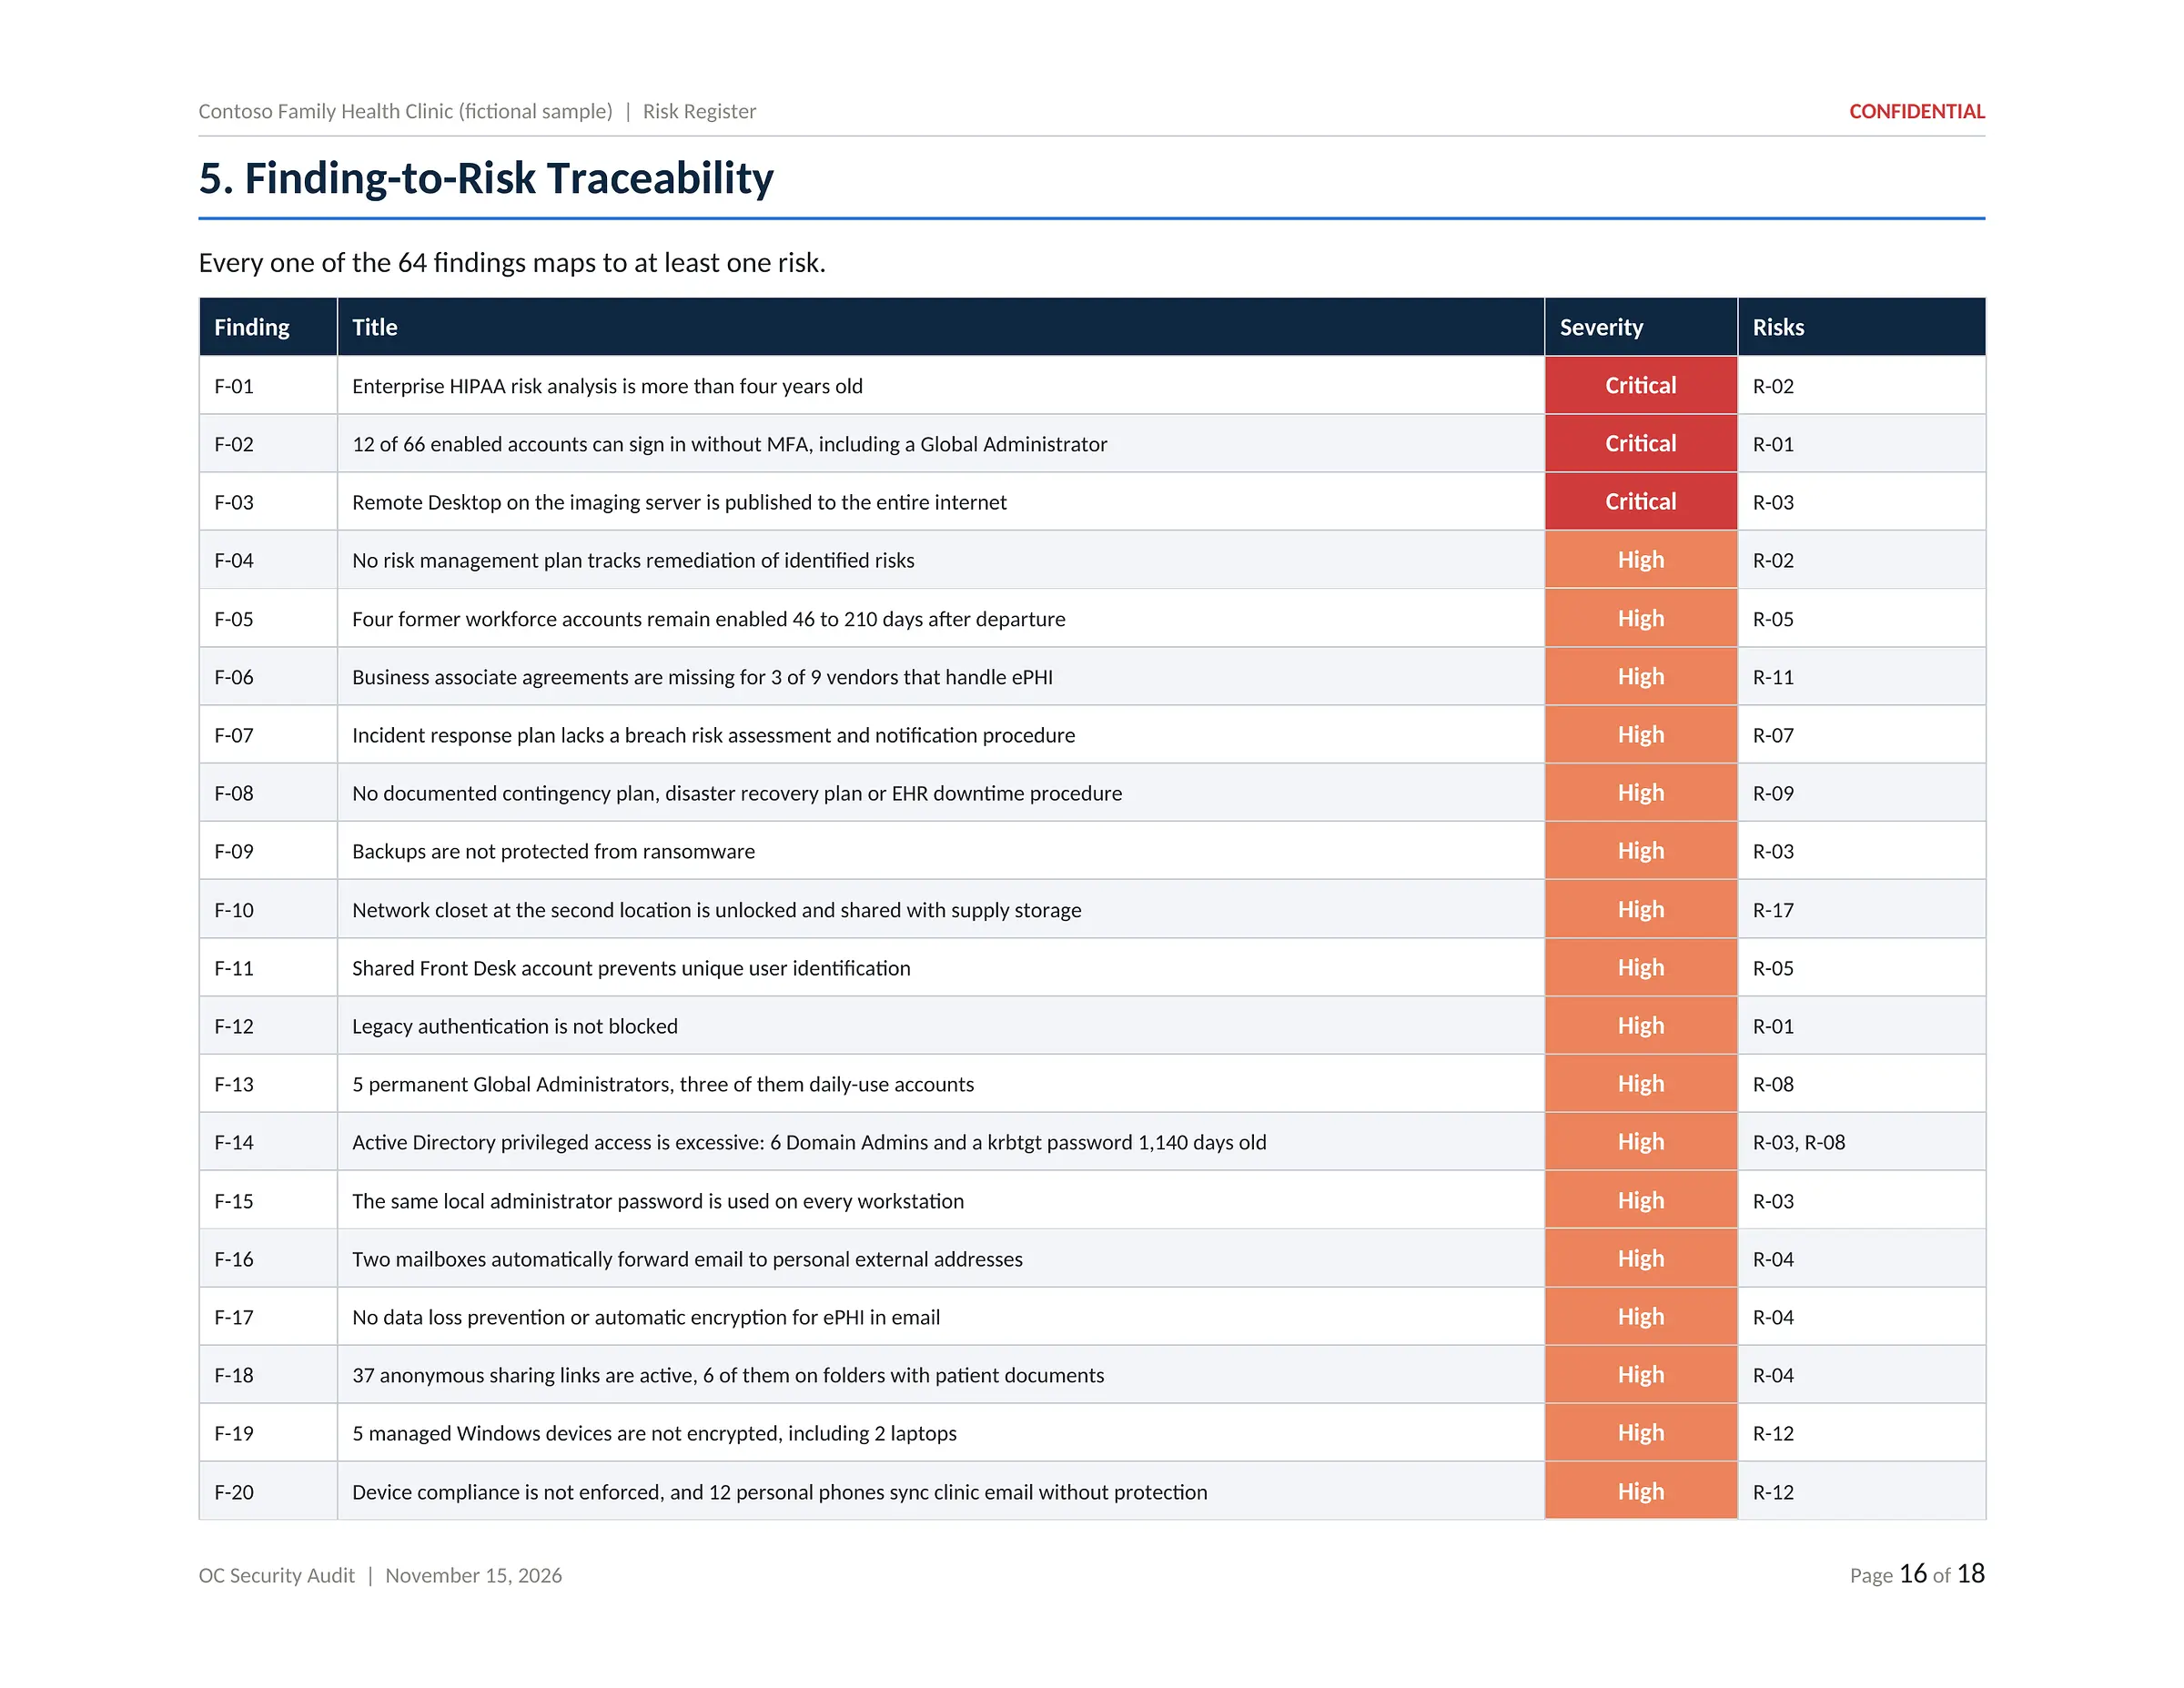
Click the page in the centre to open it full size and zoom in.
Deliverable 4 of 5 · PDF and Word · 15 pages
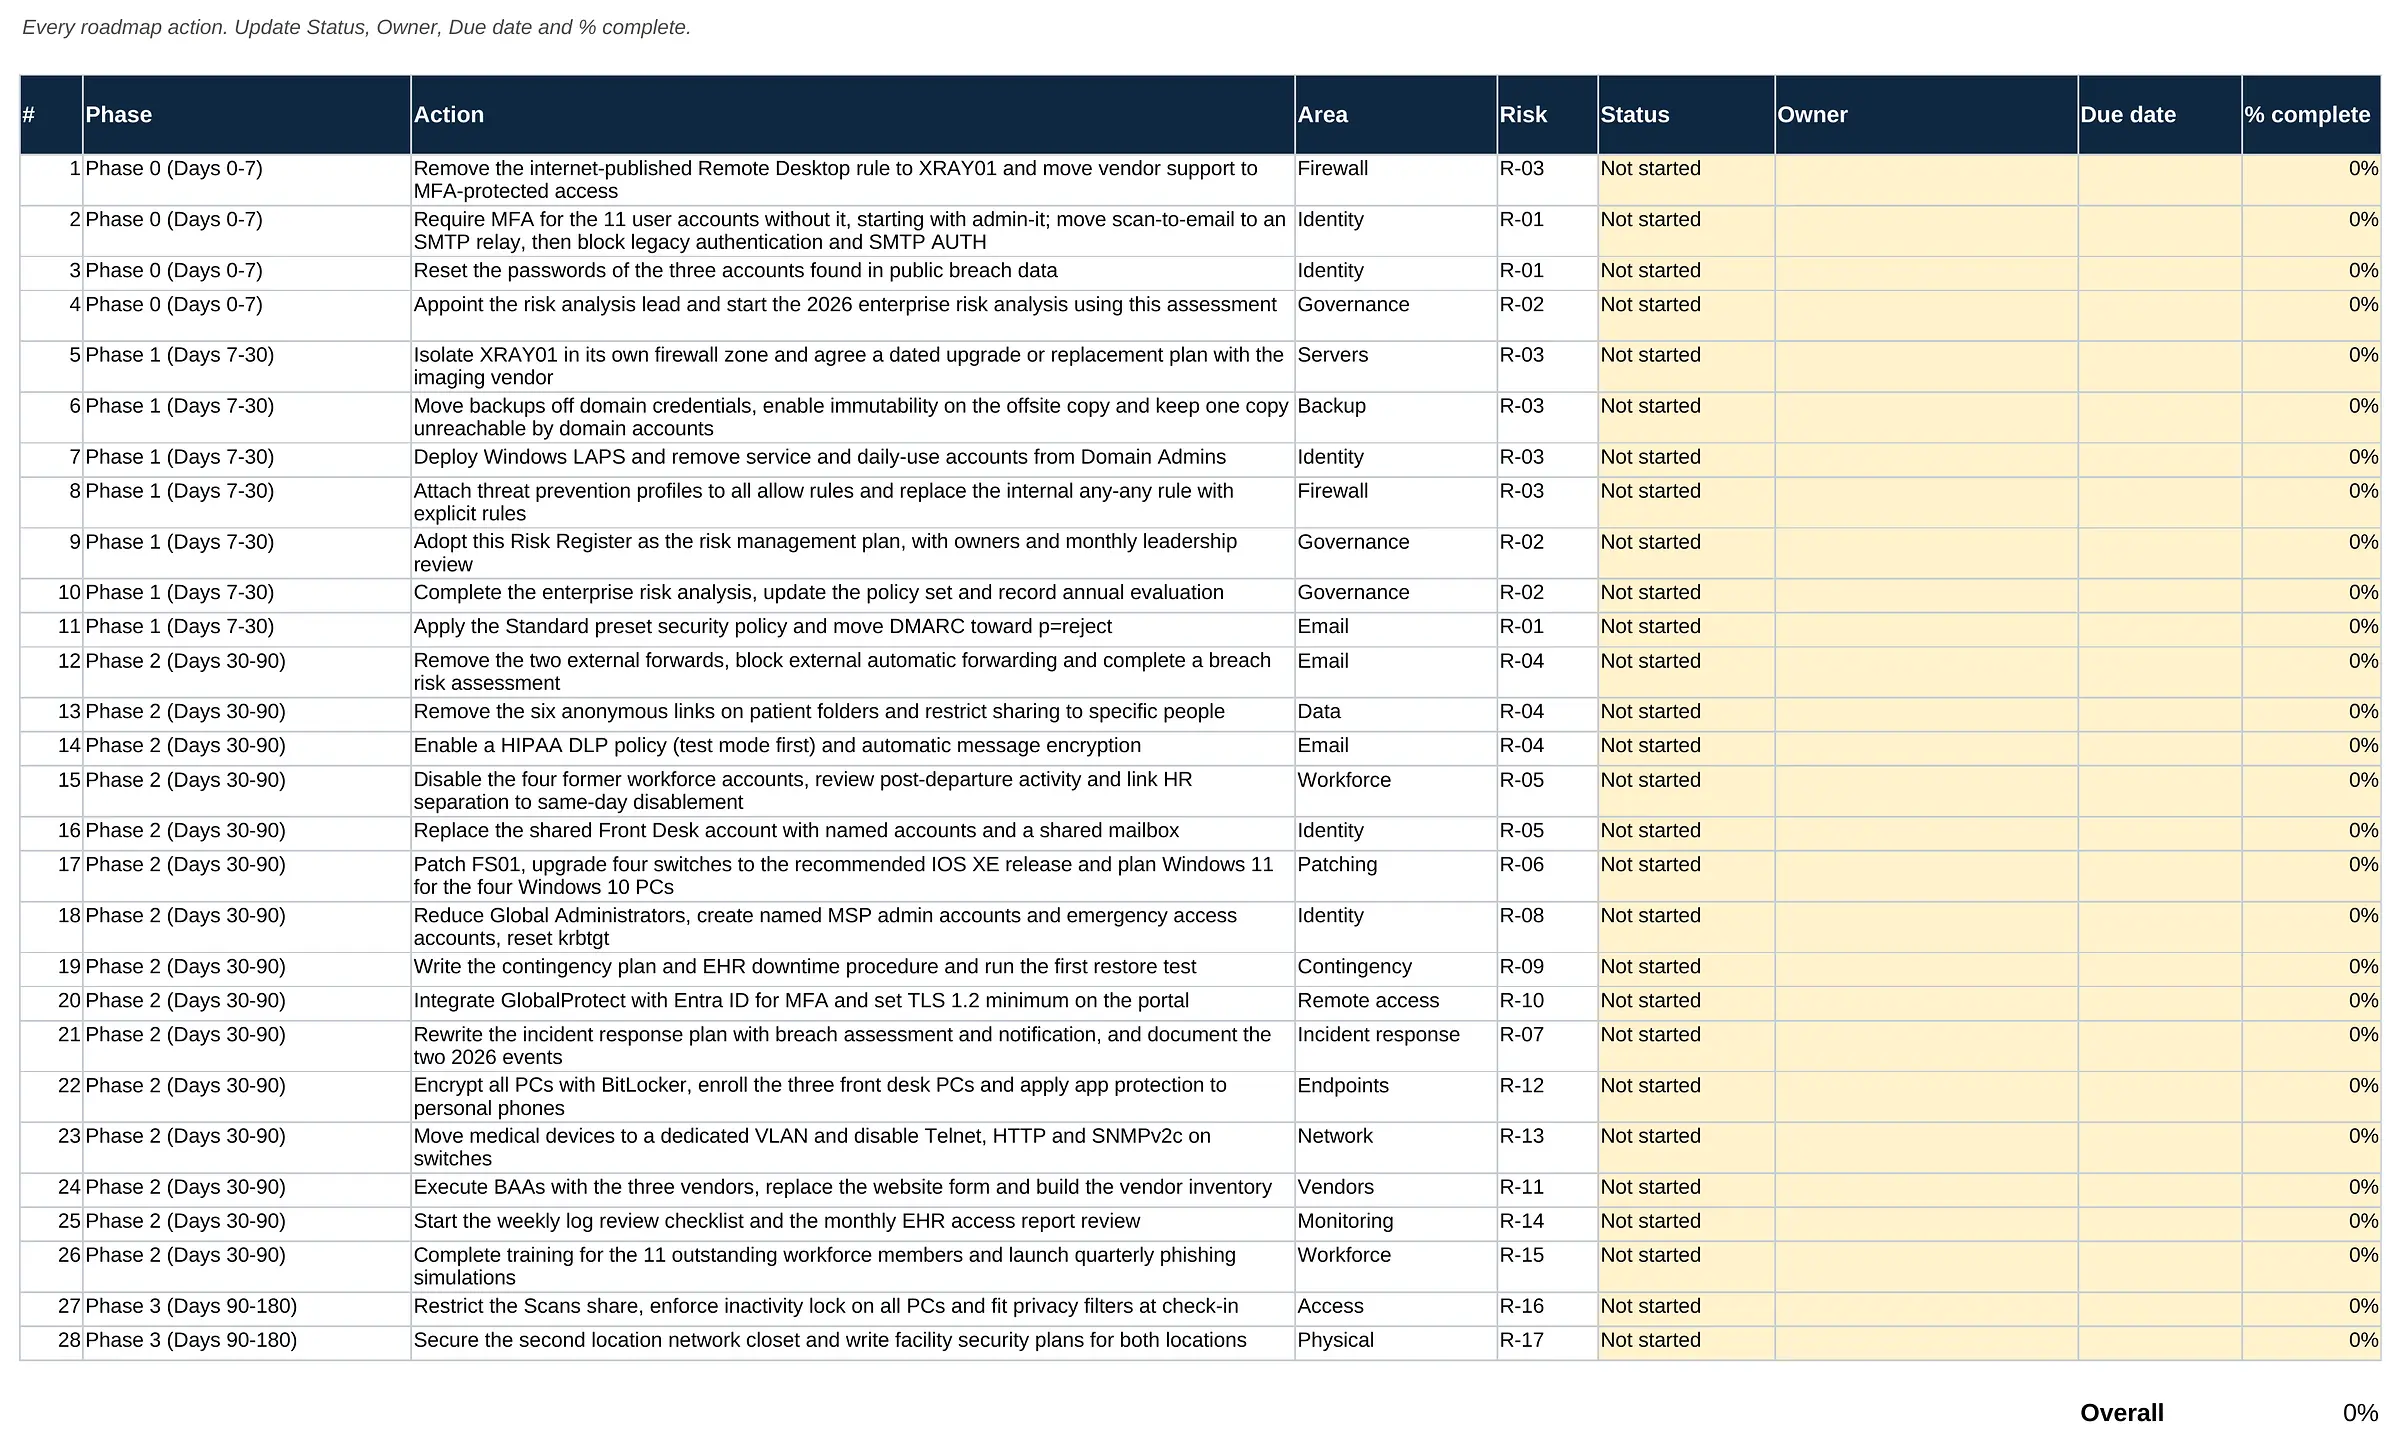
The order of work. 28 actions in four phases over 180 days, grouped into ten projects your IT provider can schedule and price, with today’s measures against 30-day and 180-day targets and the governance rhythm that keeps the program current.
Who uses it
Practice administrator and owners for budgeting, the IT provider for scheduling, and the Security Officer for tracking progress.
What is included
SAMPLE · Contoso Family Health Clinic (fictional)
1 / 9
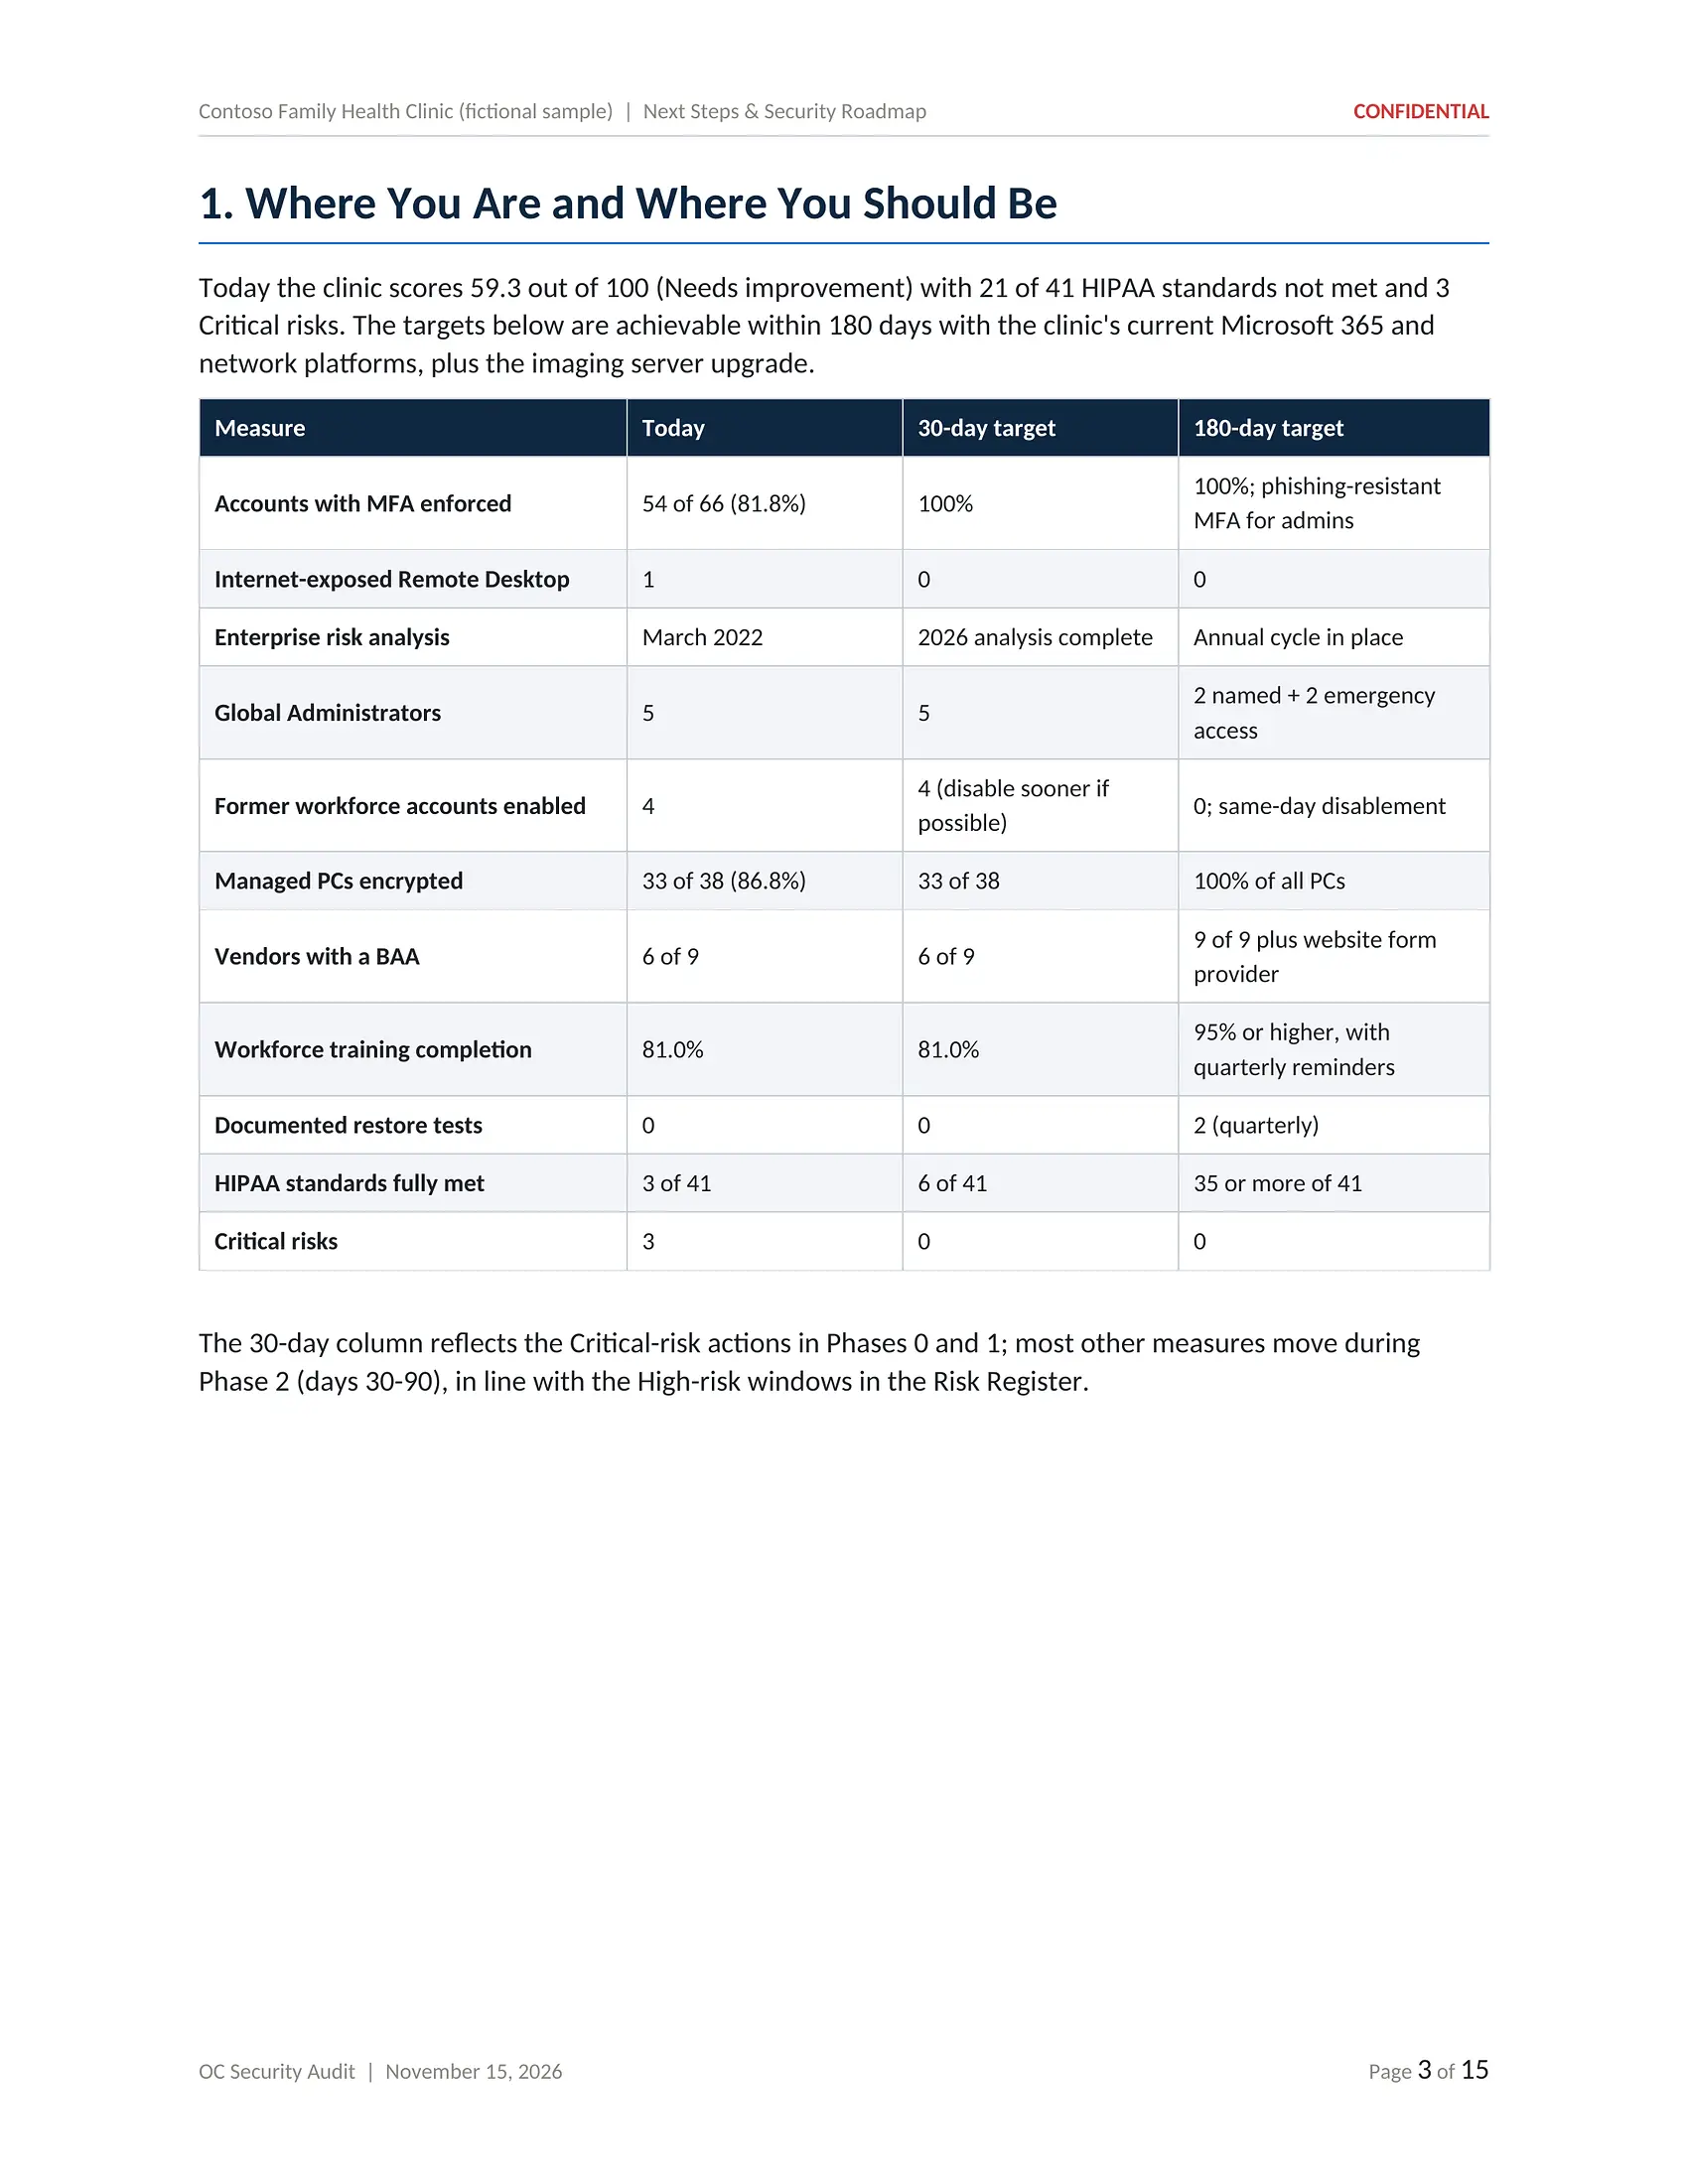
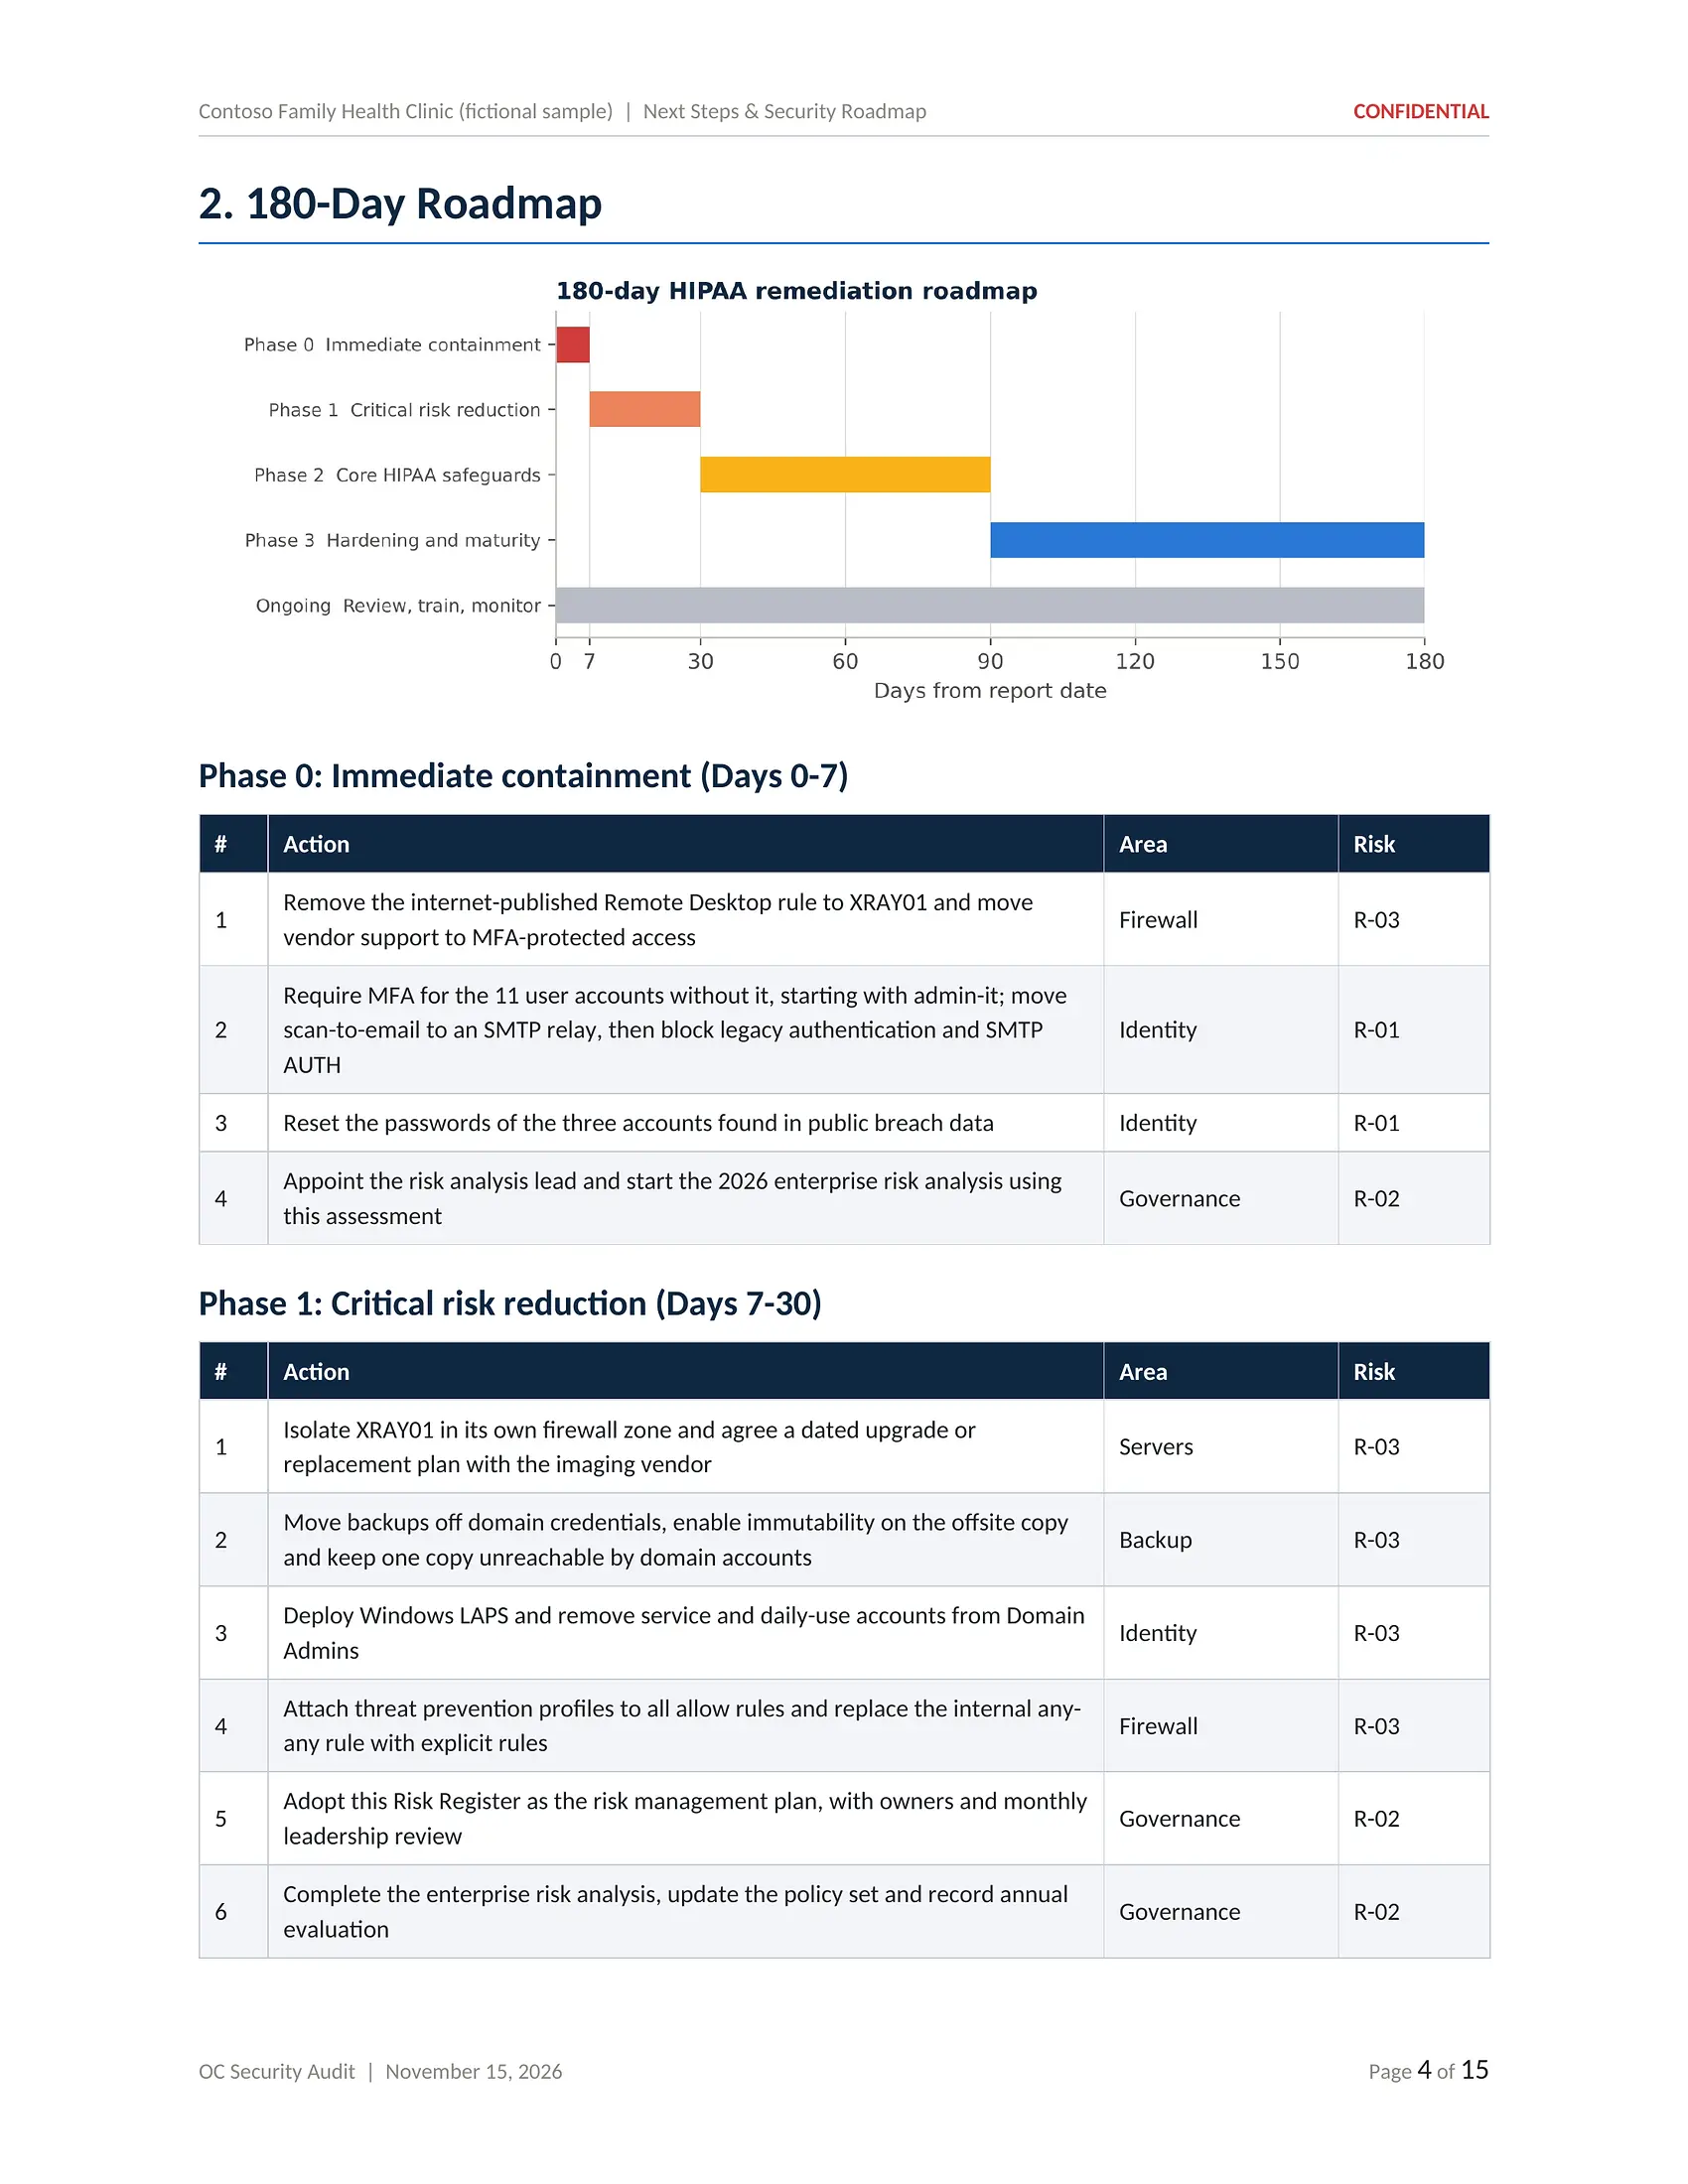
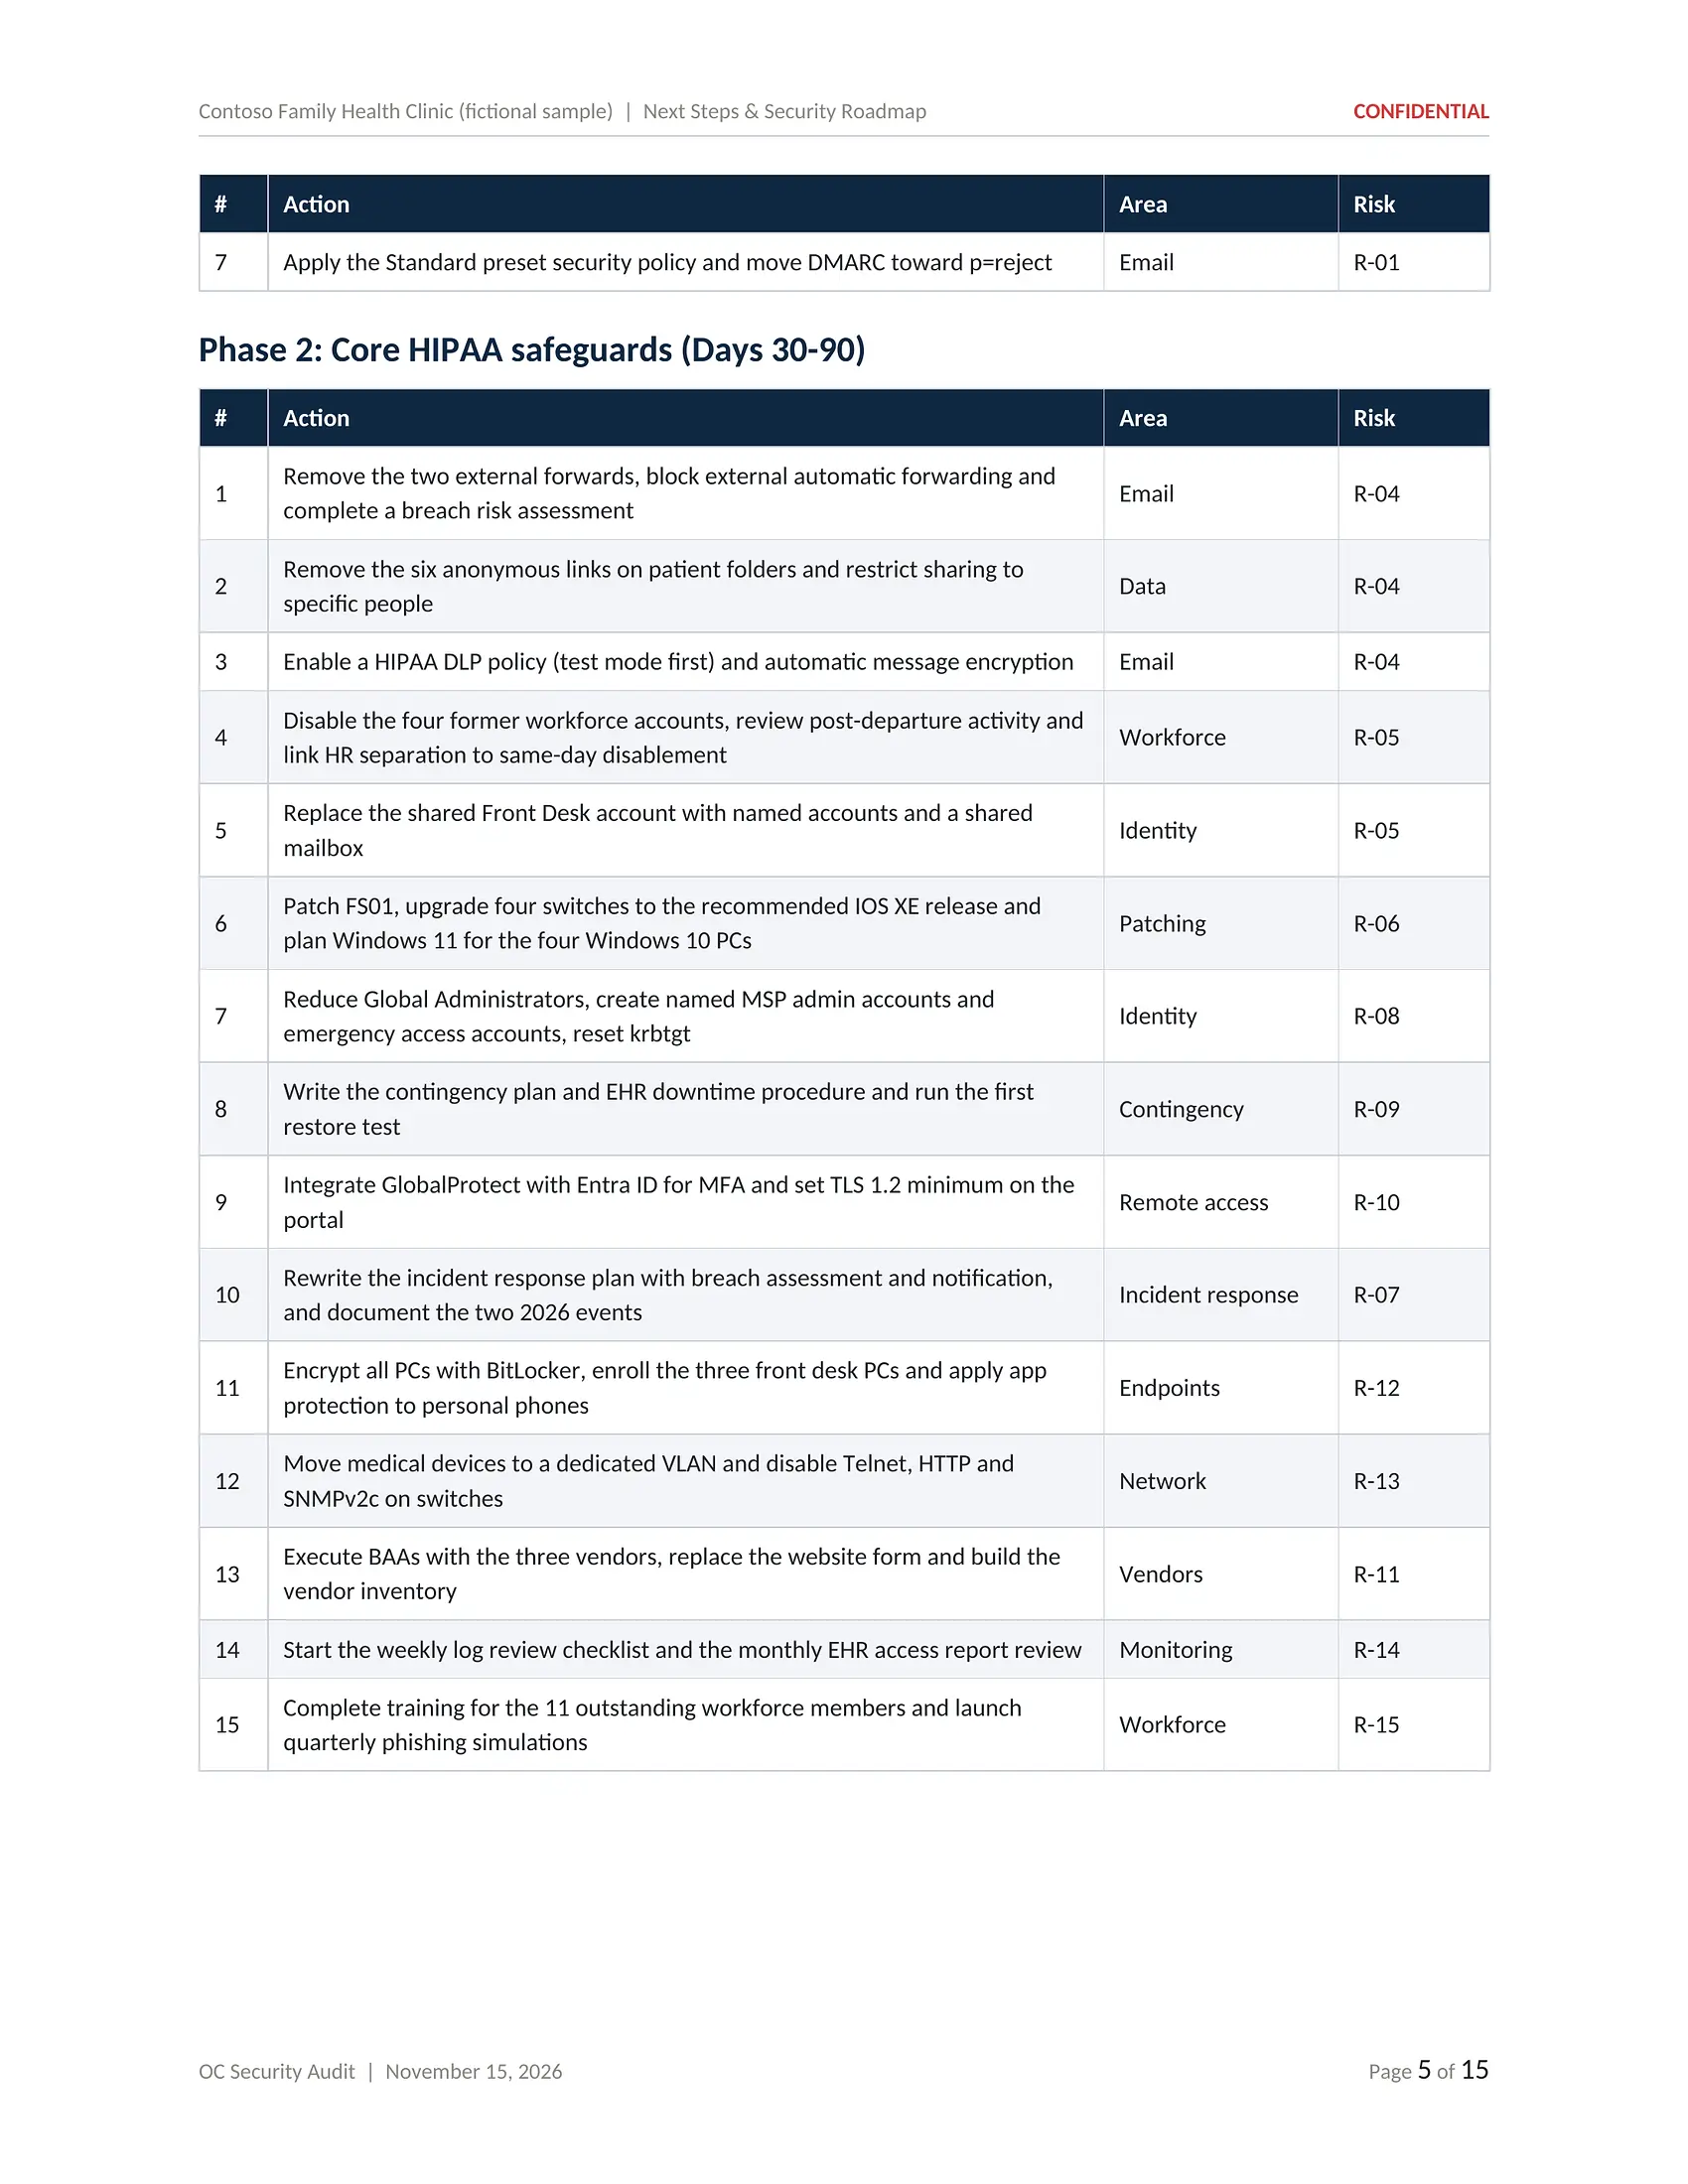
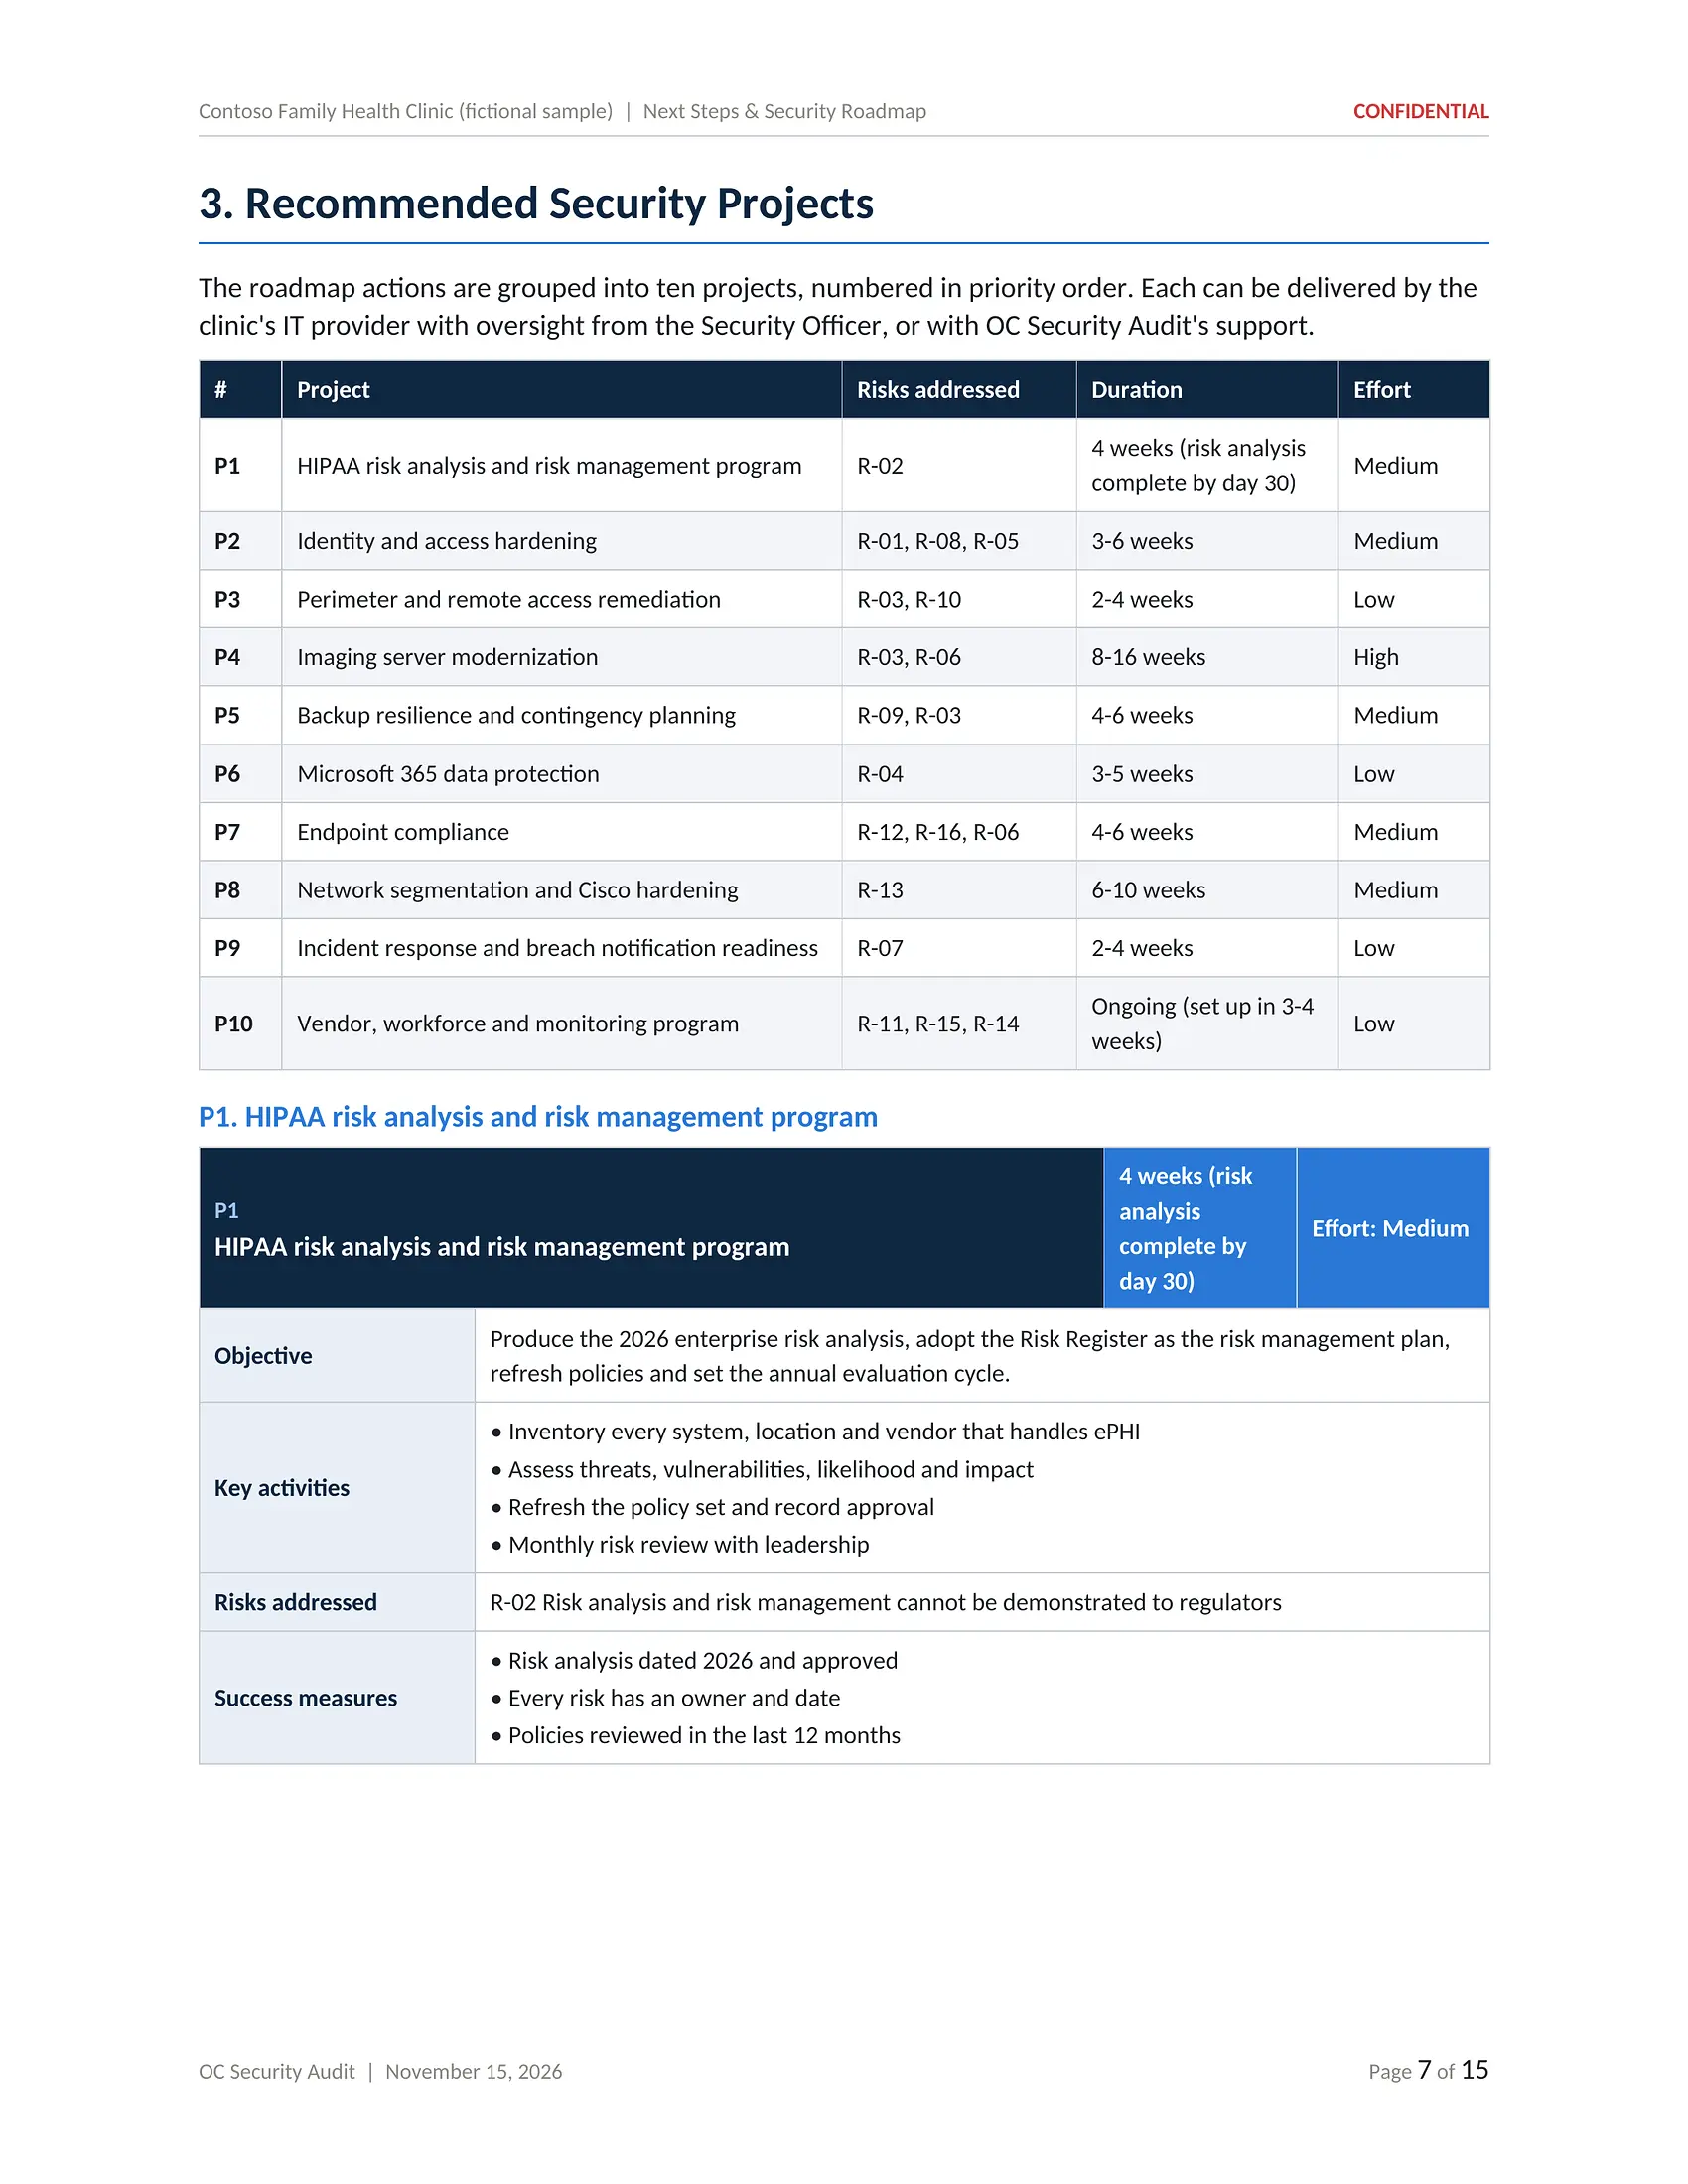
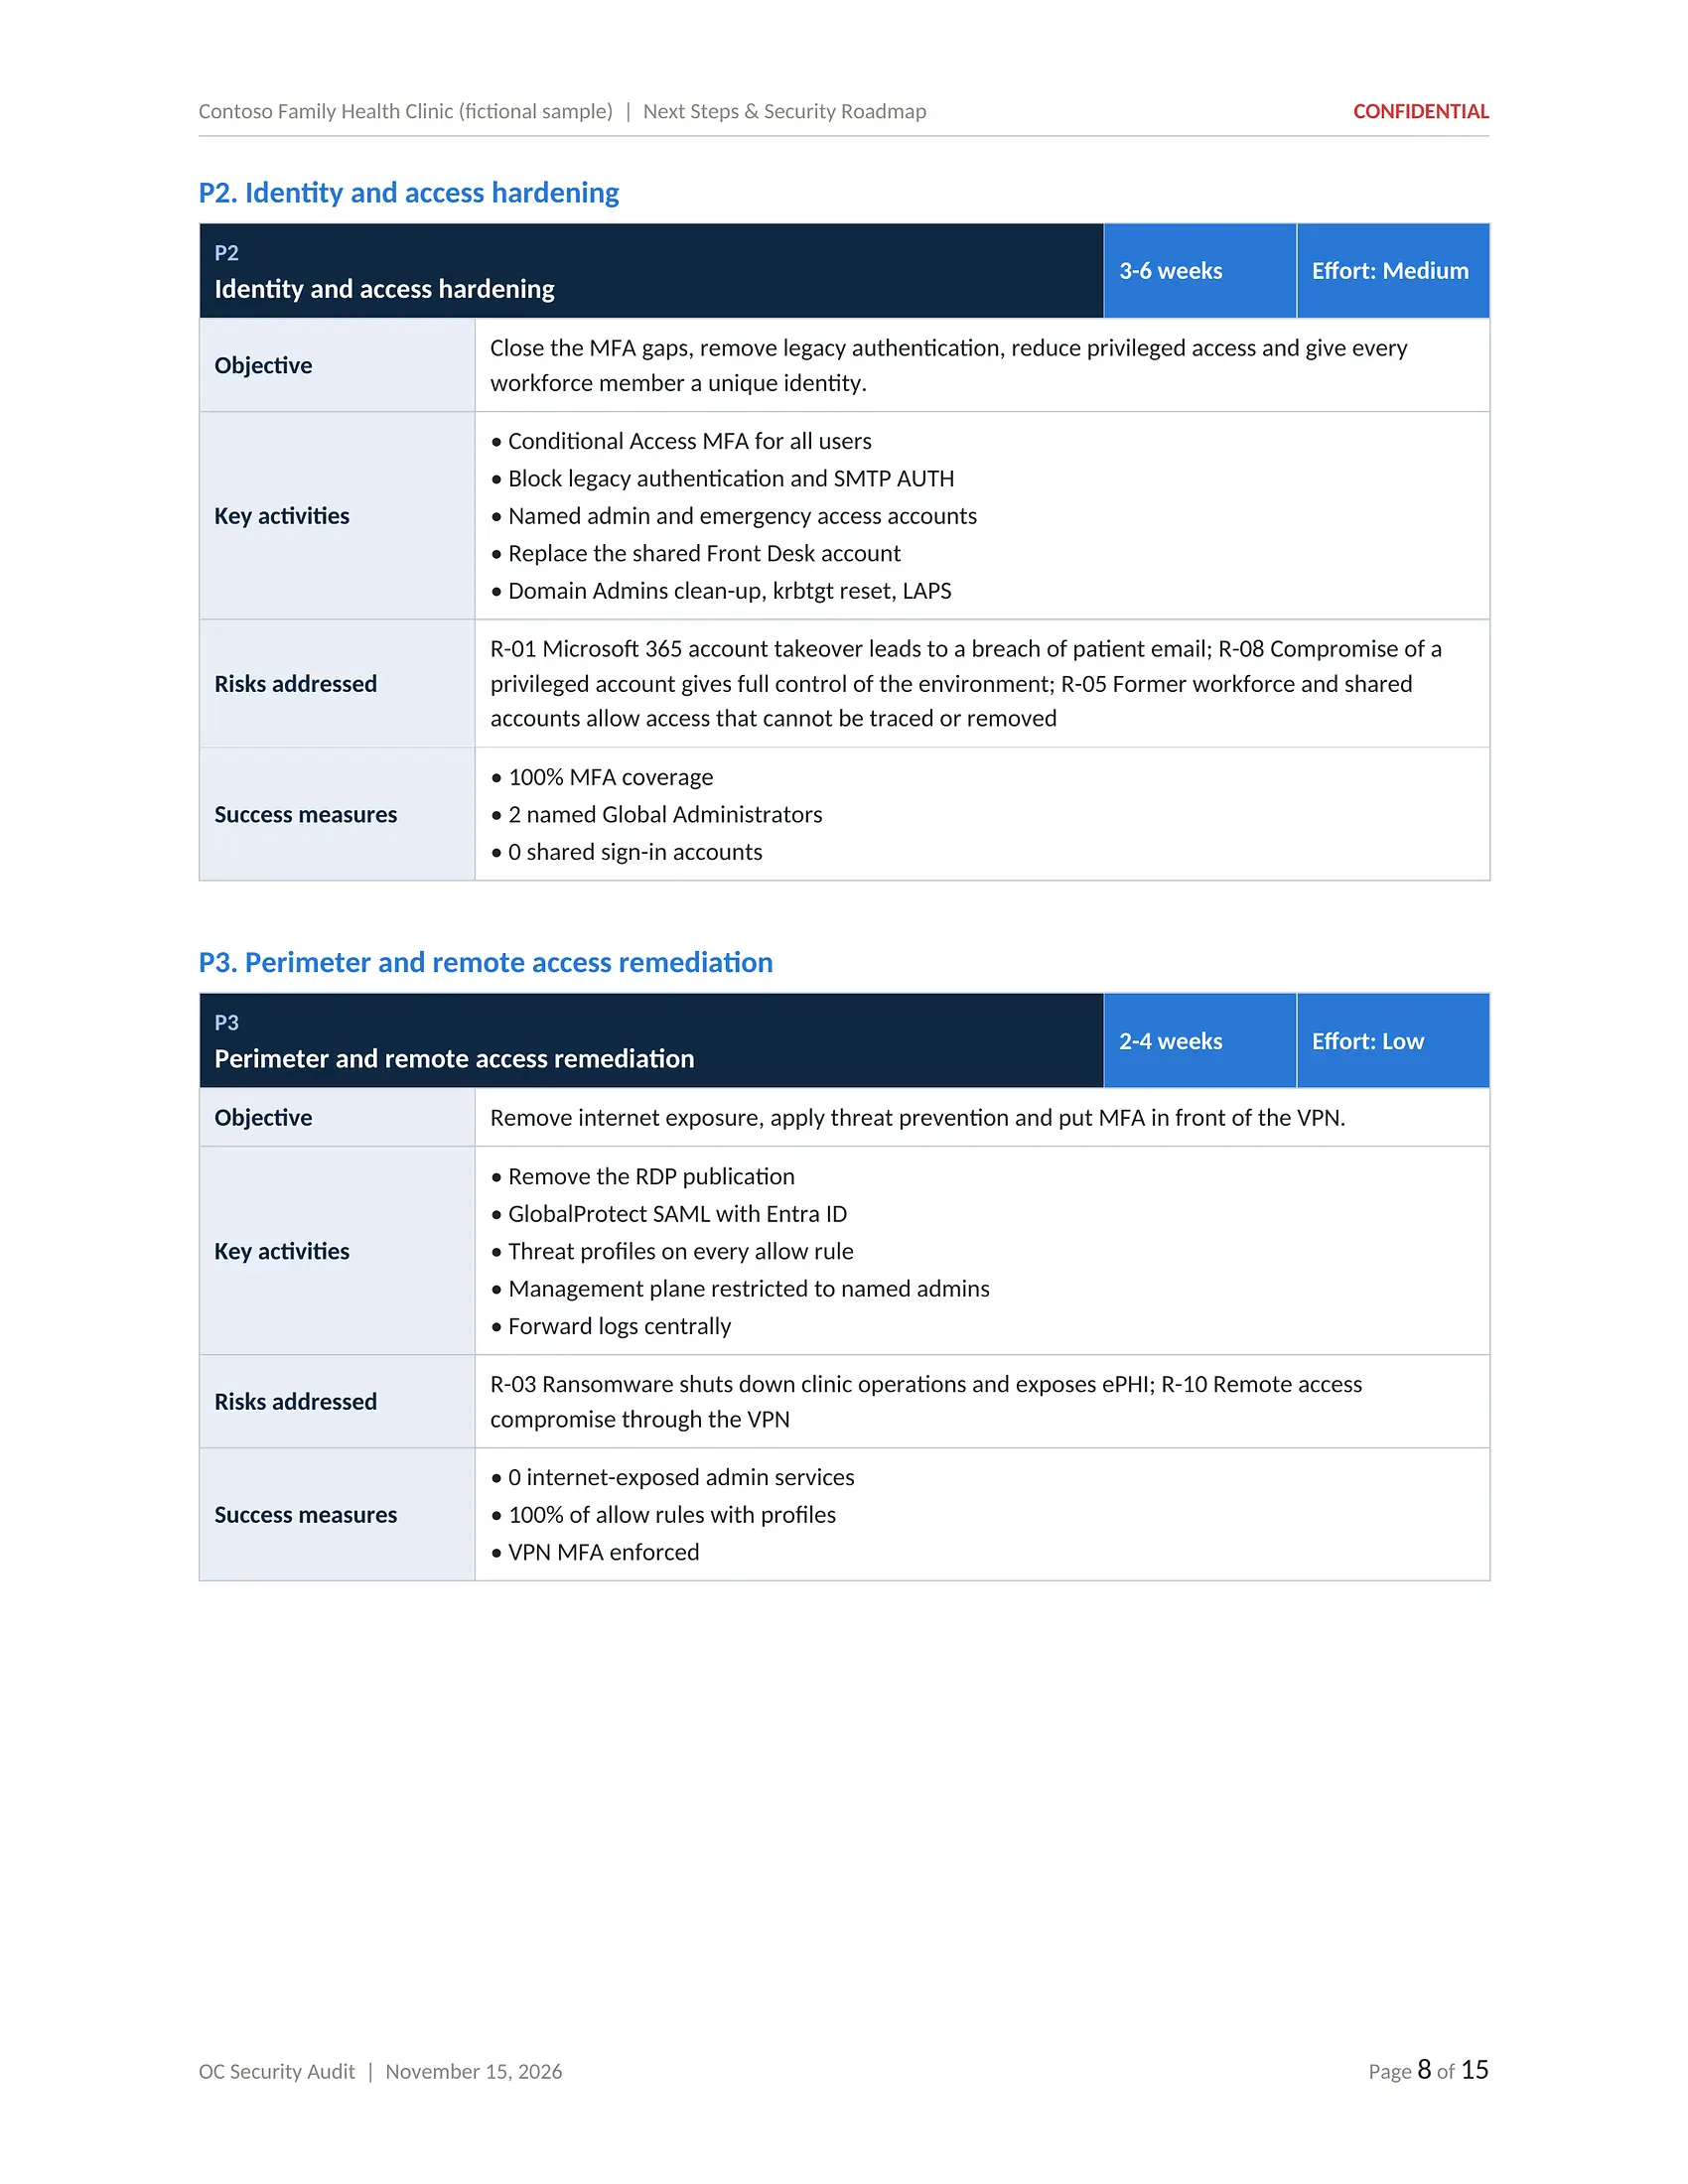
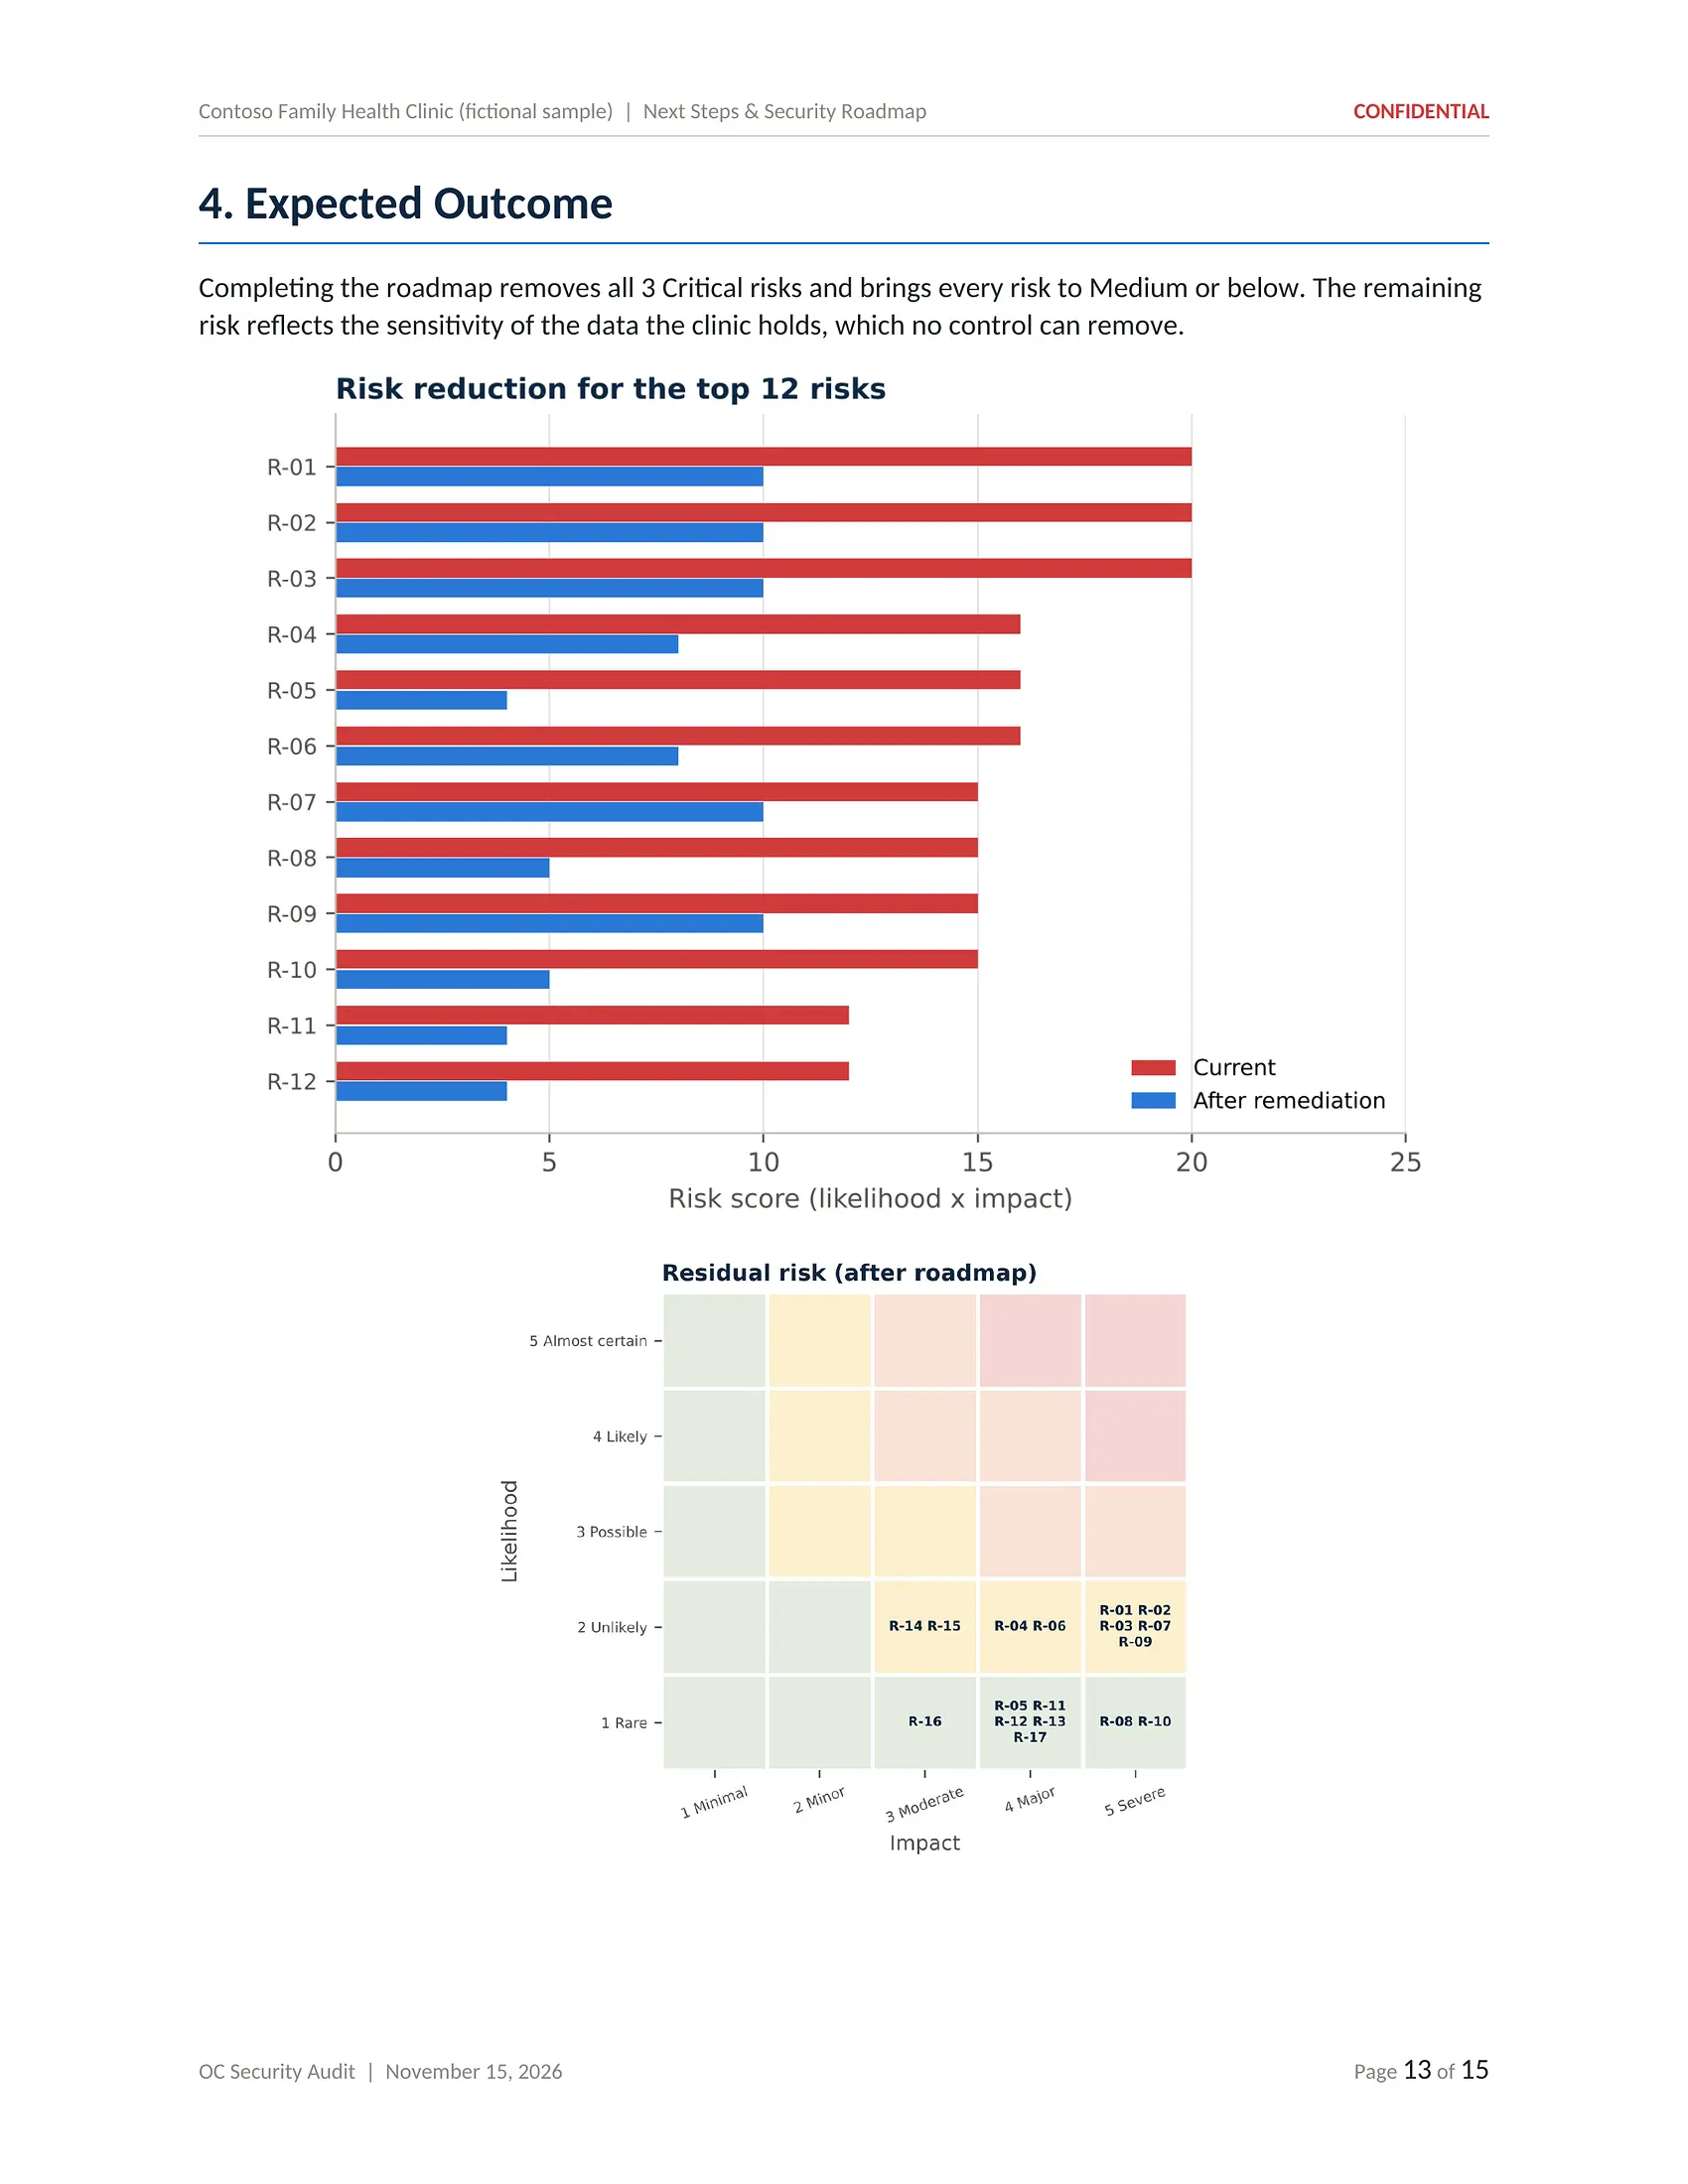
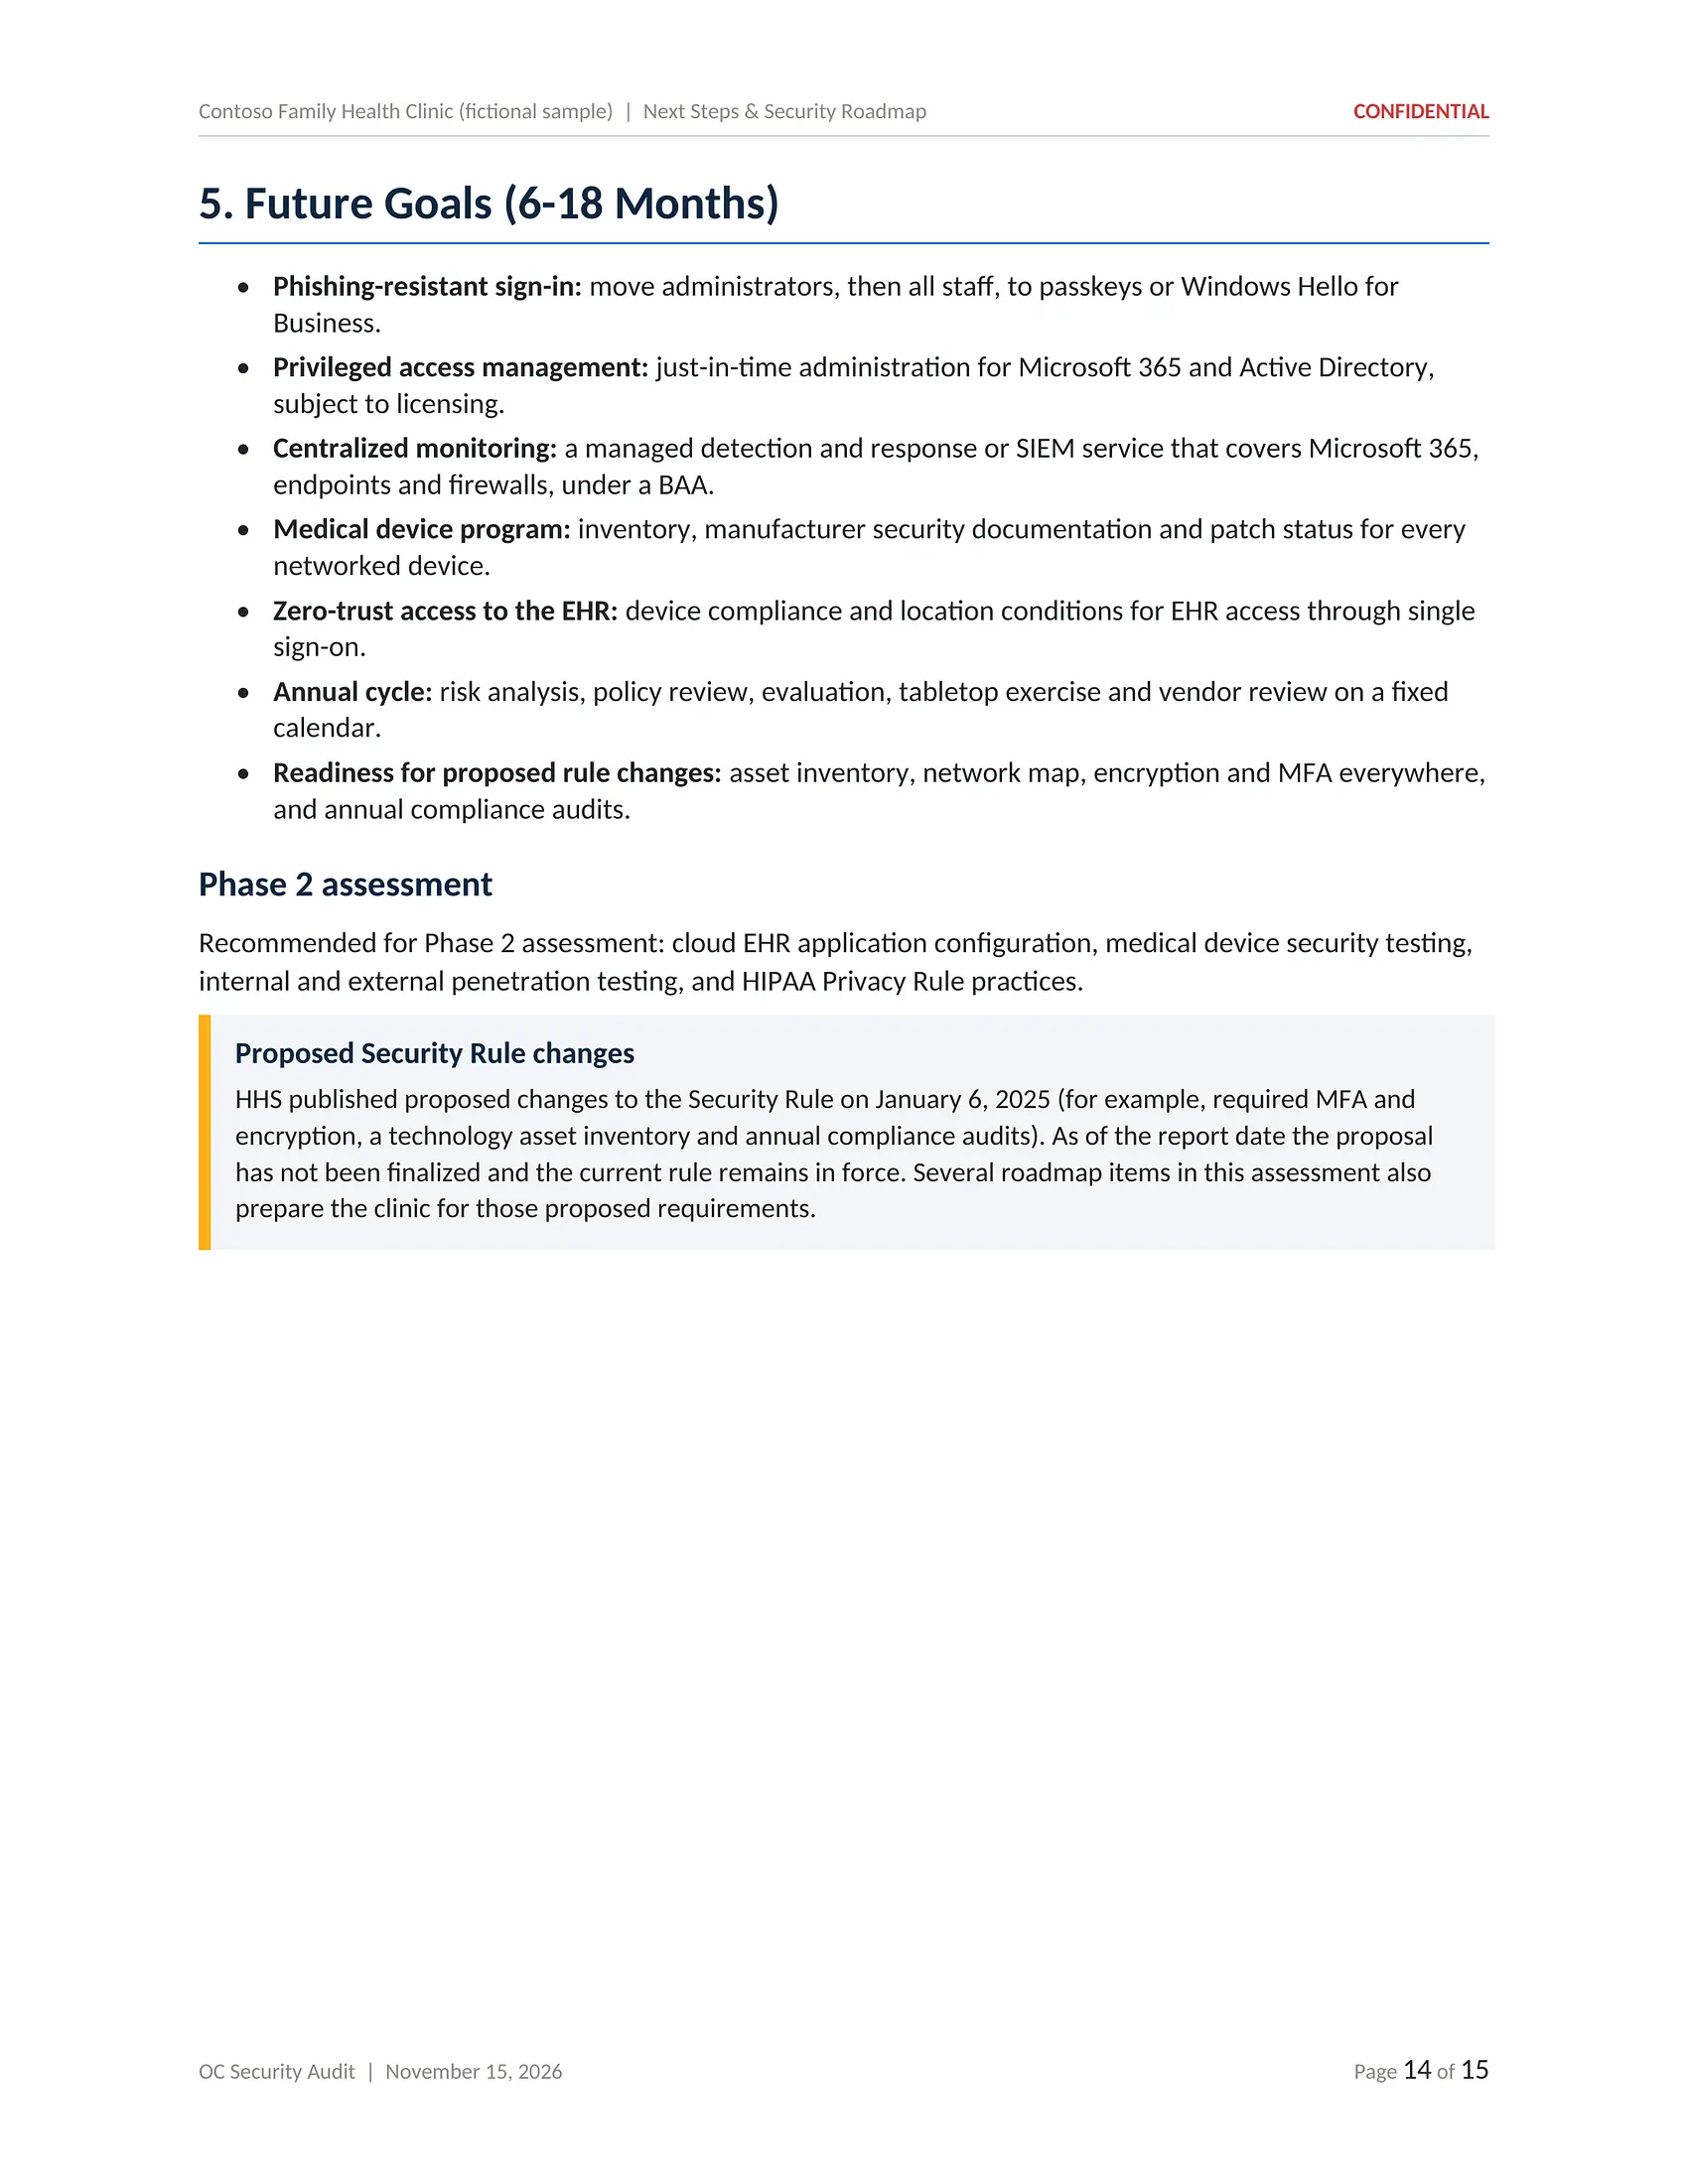
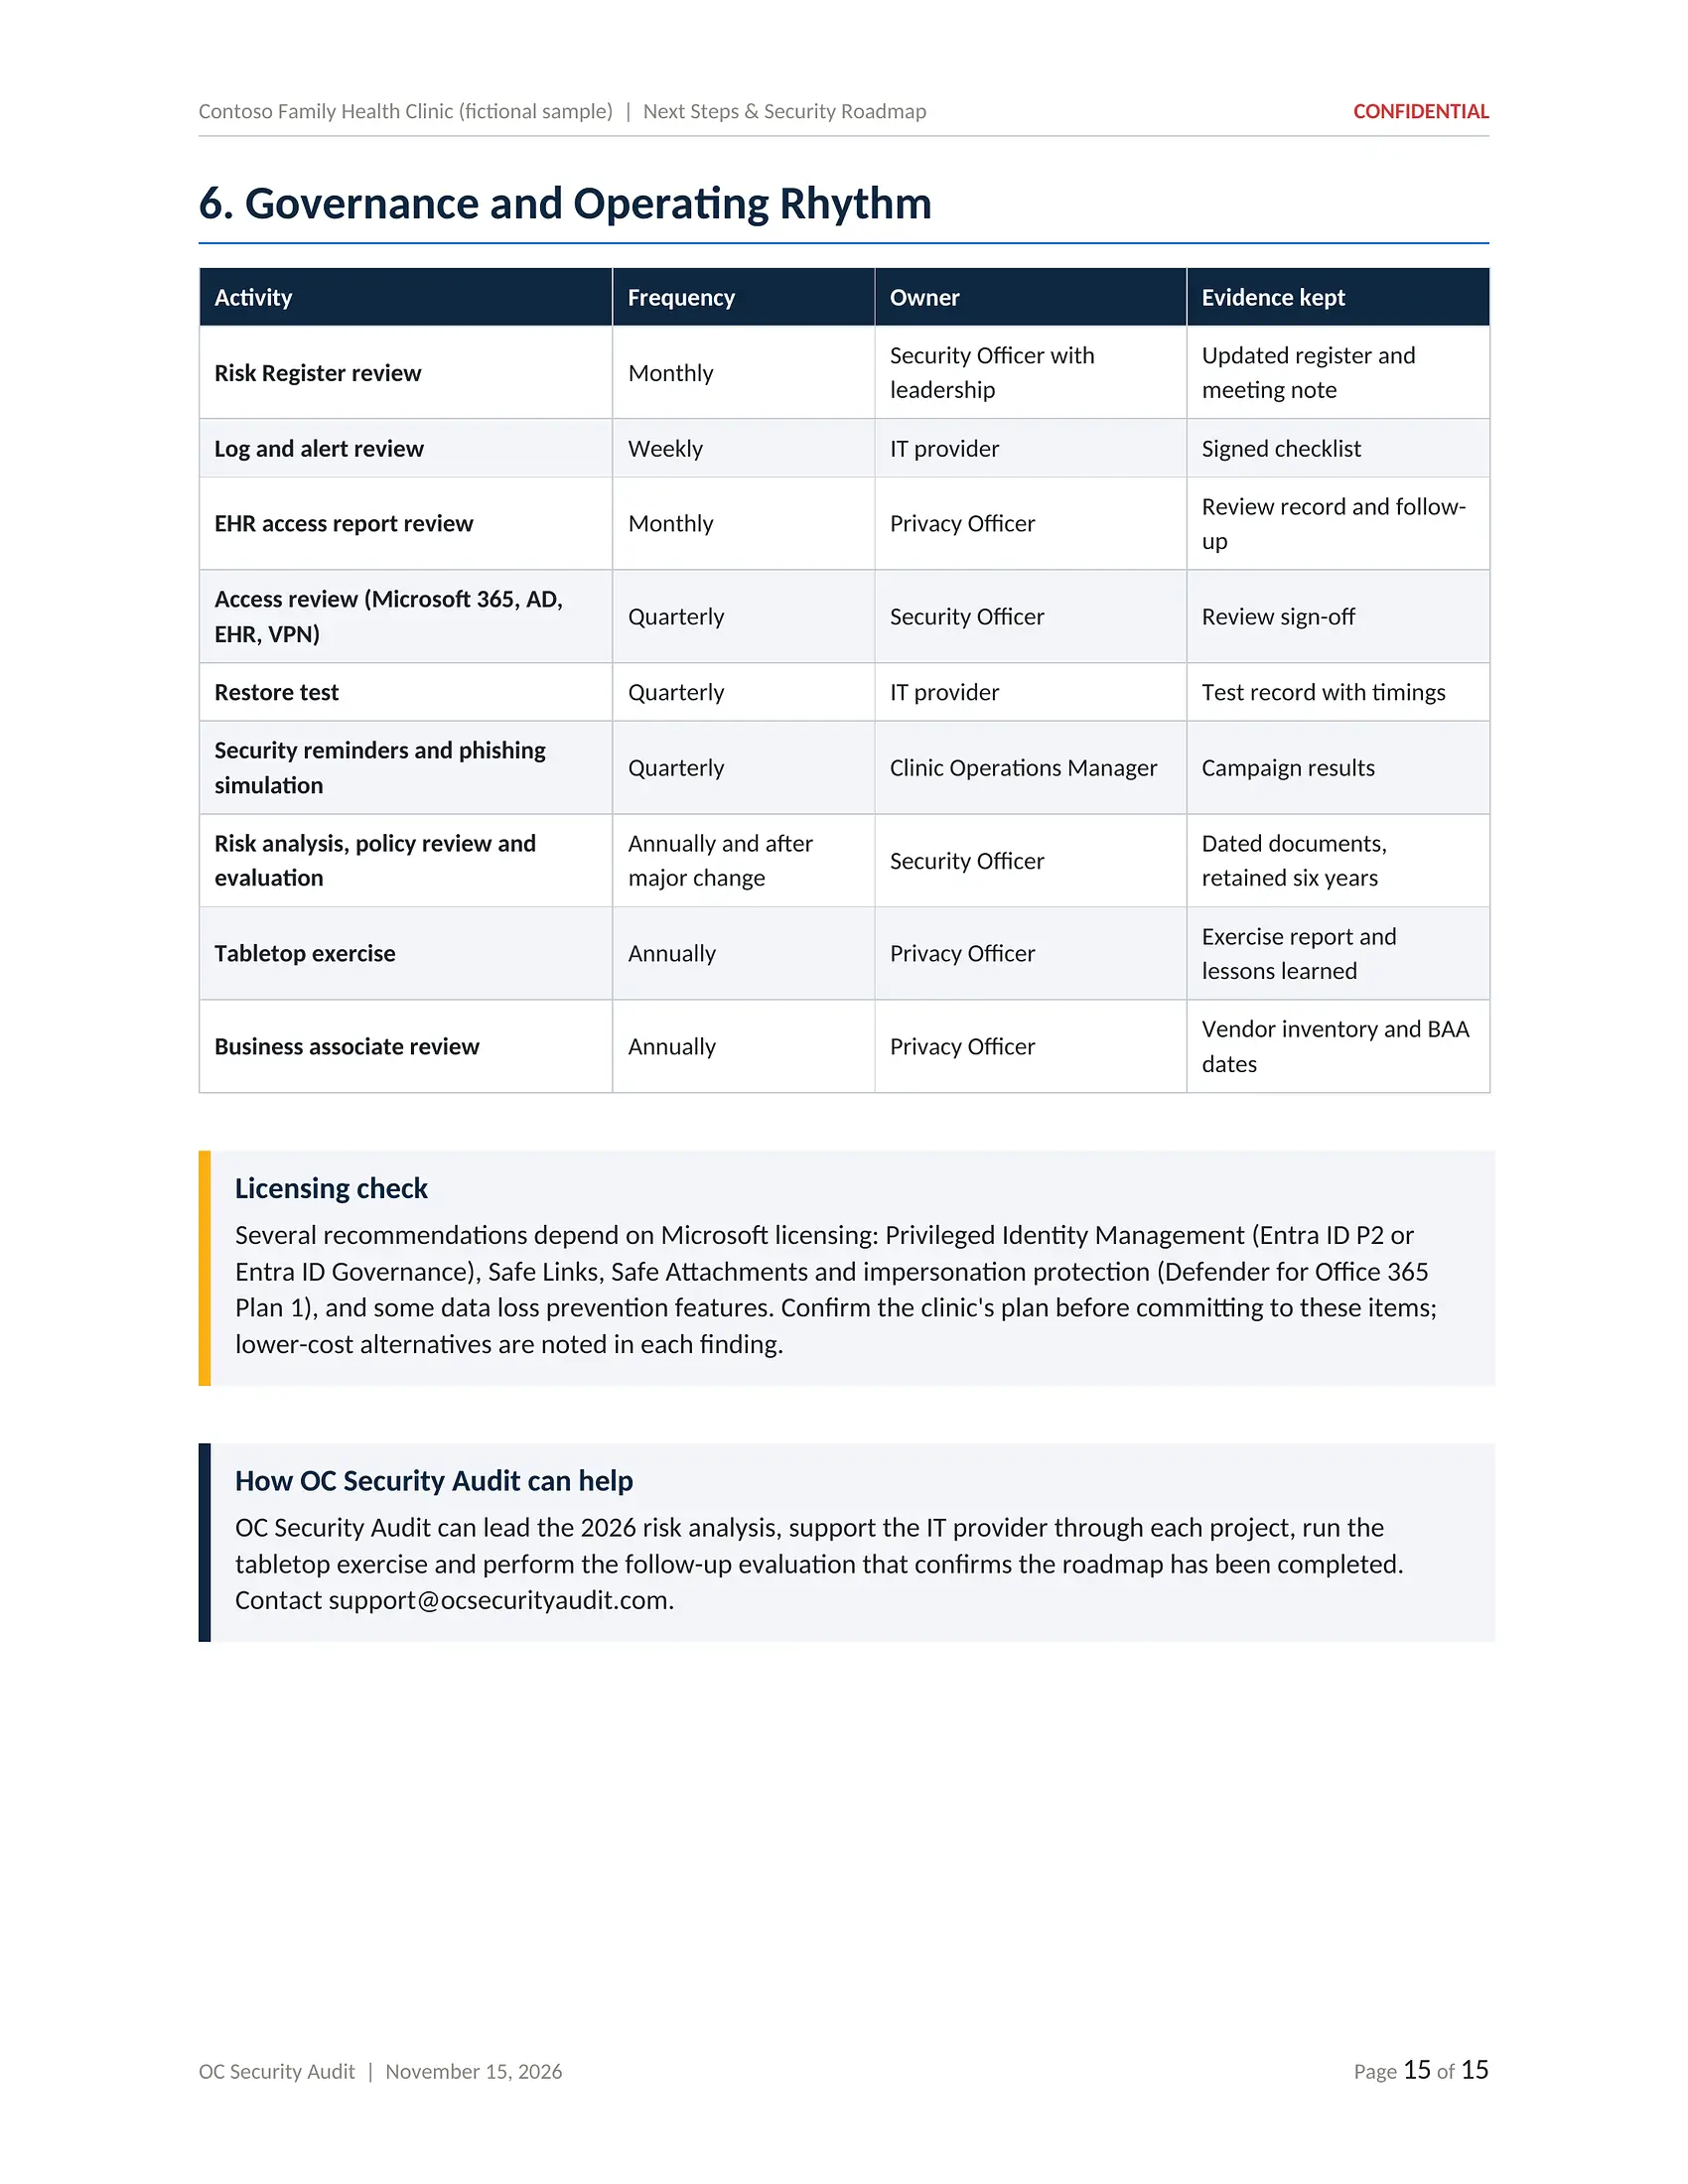
Click the page in the centre to open it full size and zoom in.
Deliverable 5 of 5 · Excel · 20 sheets
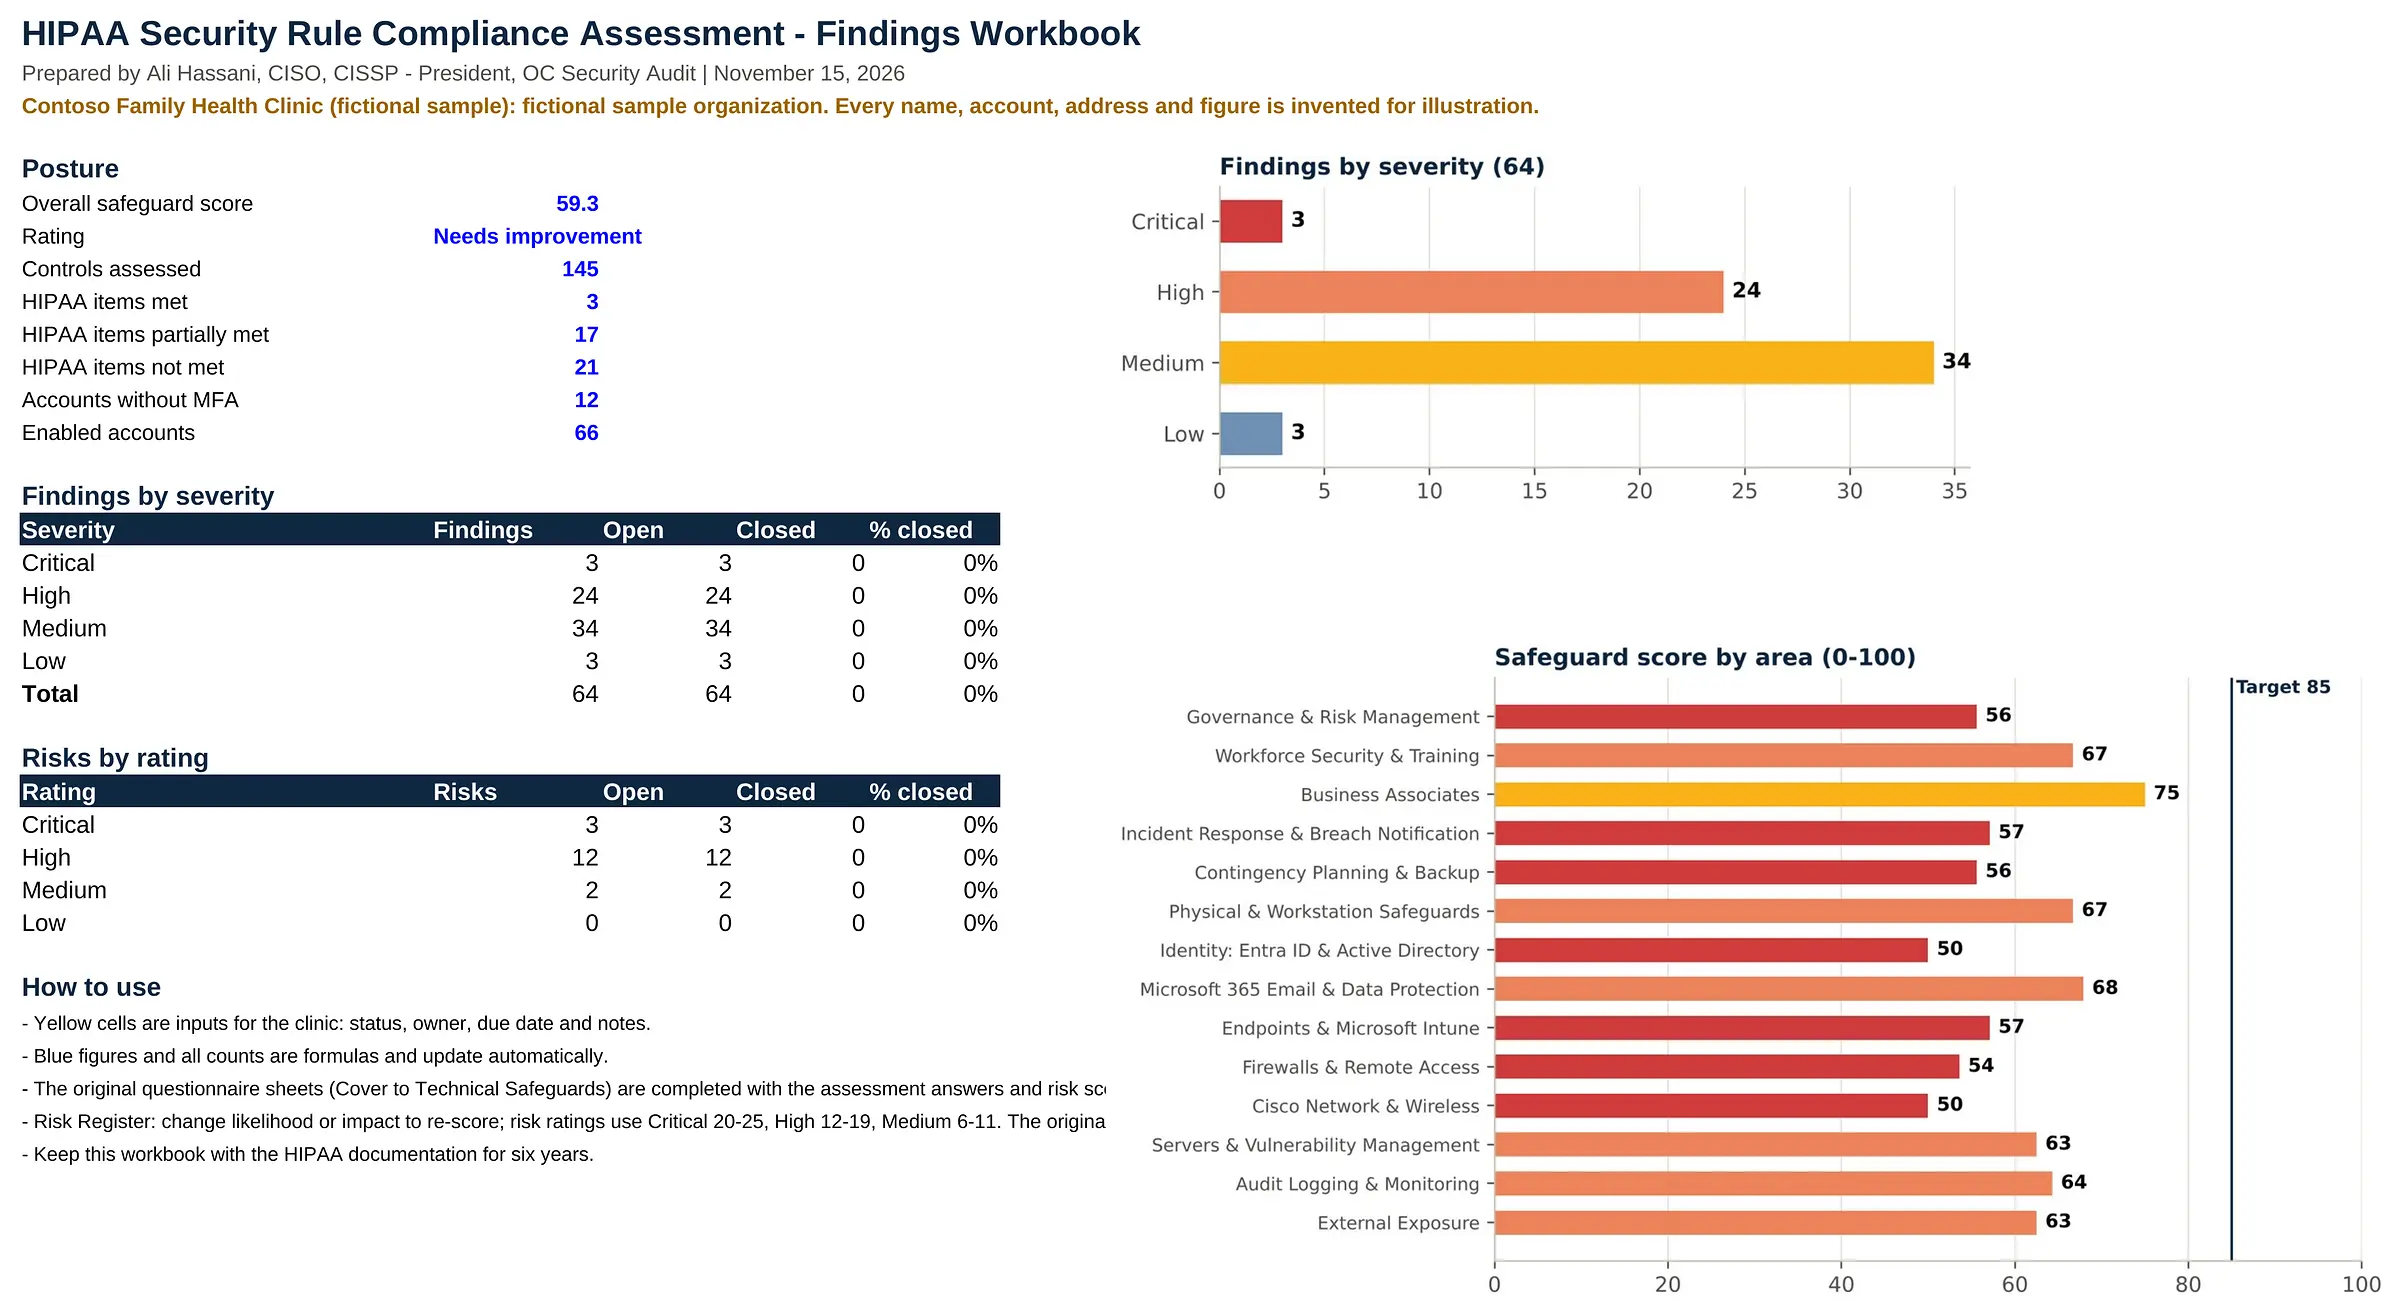
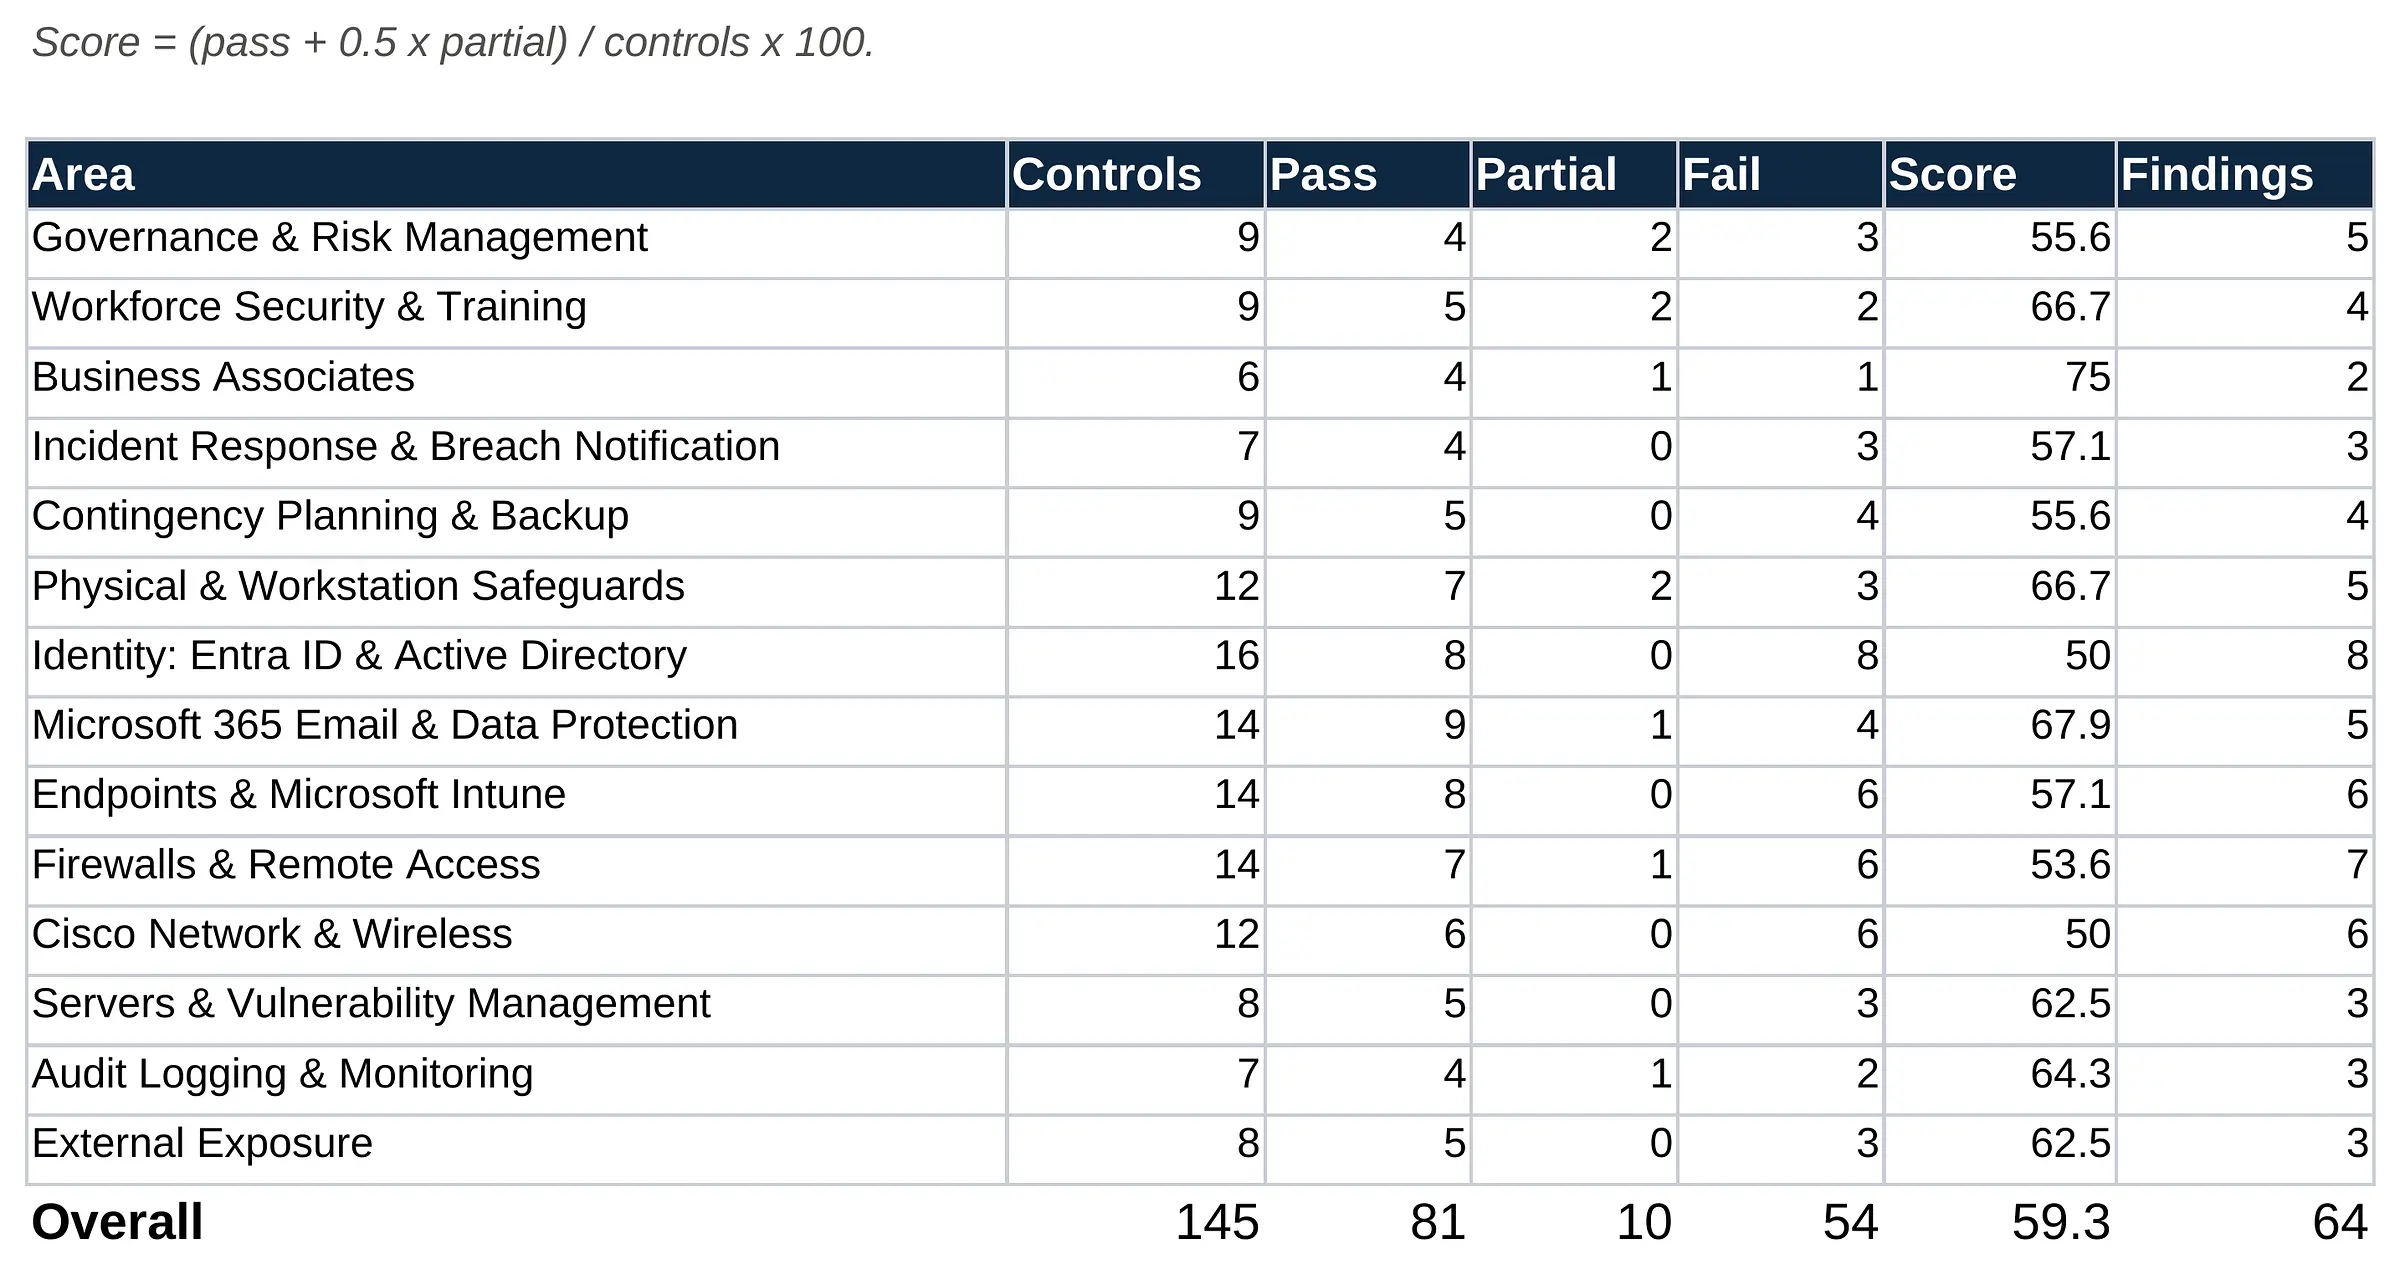
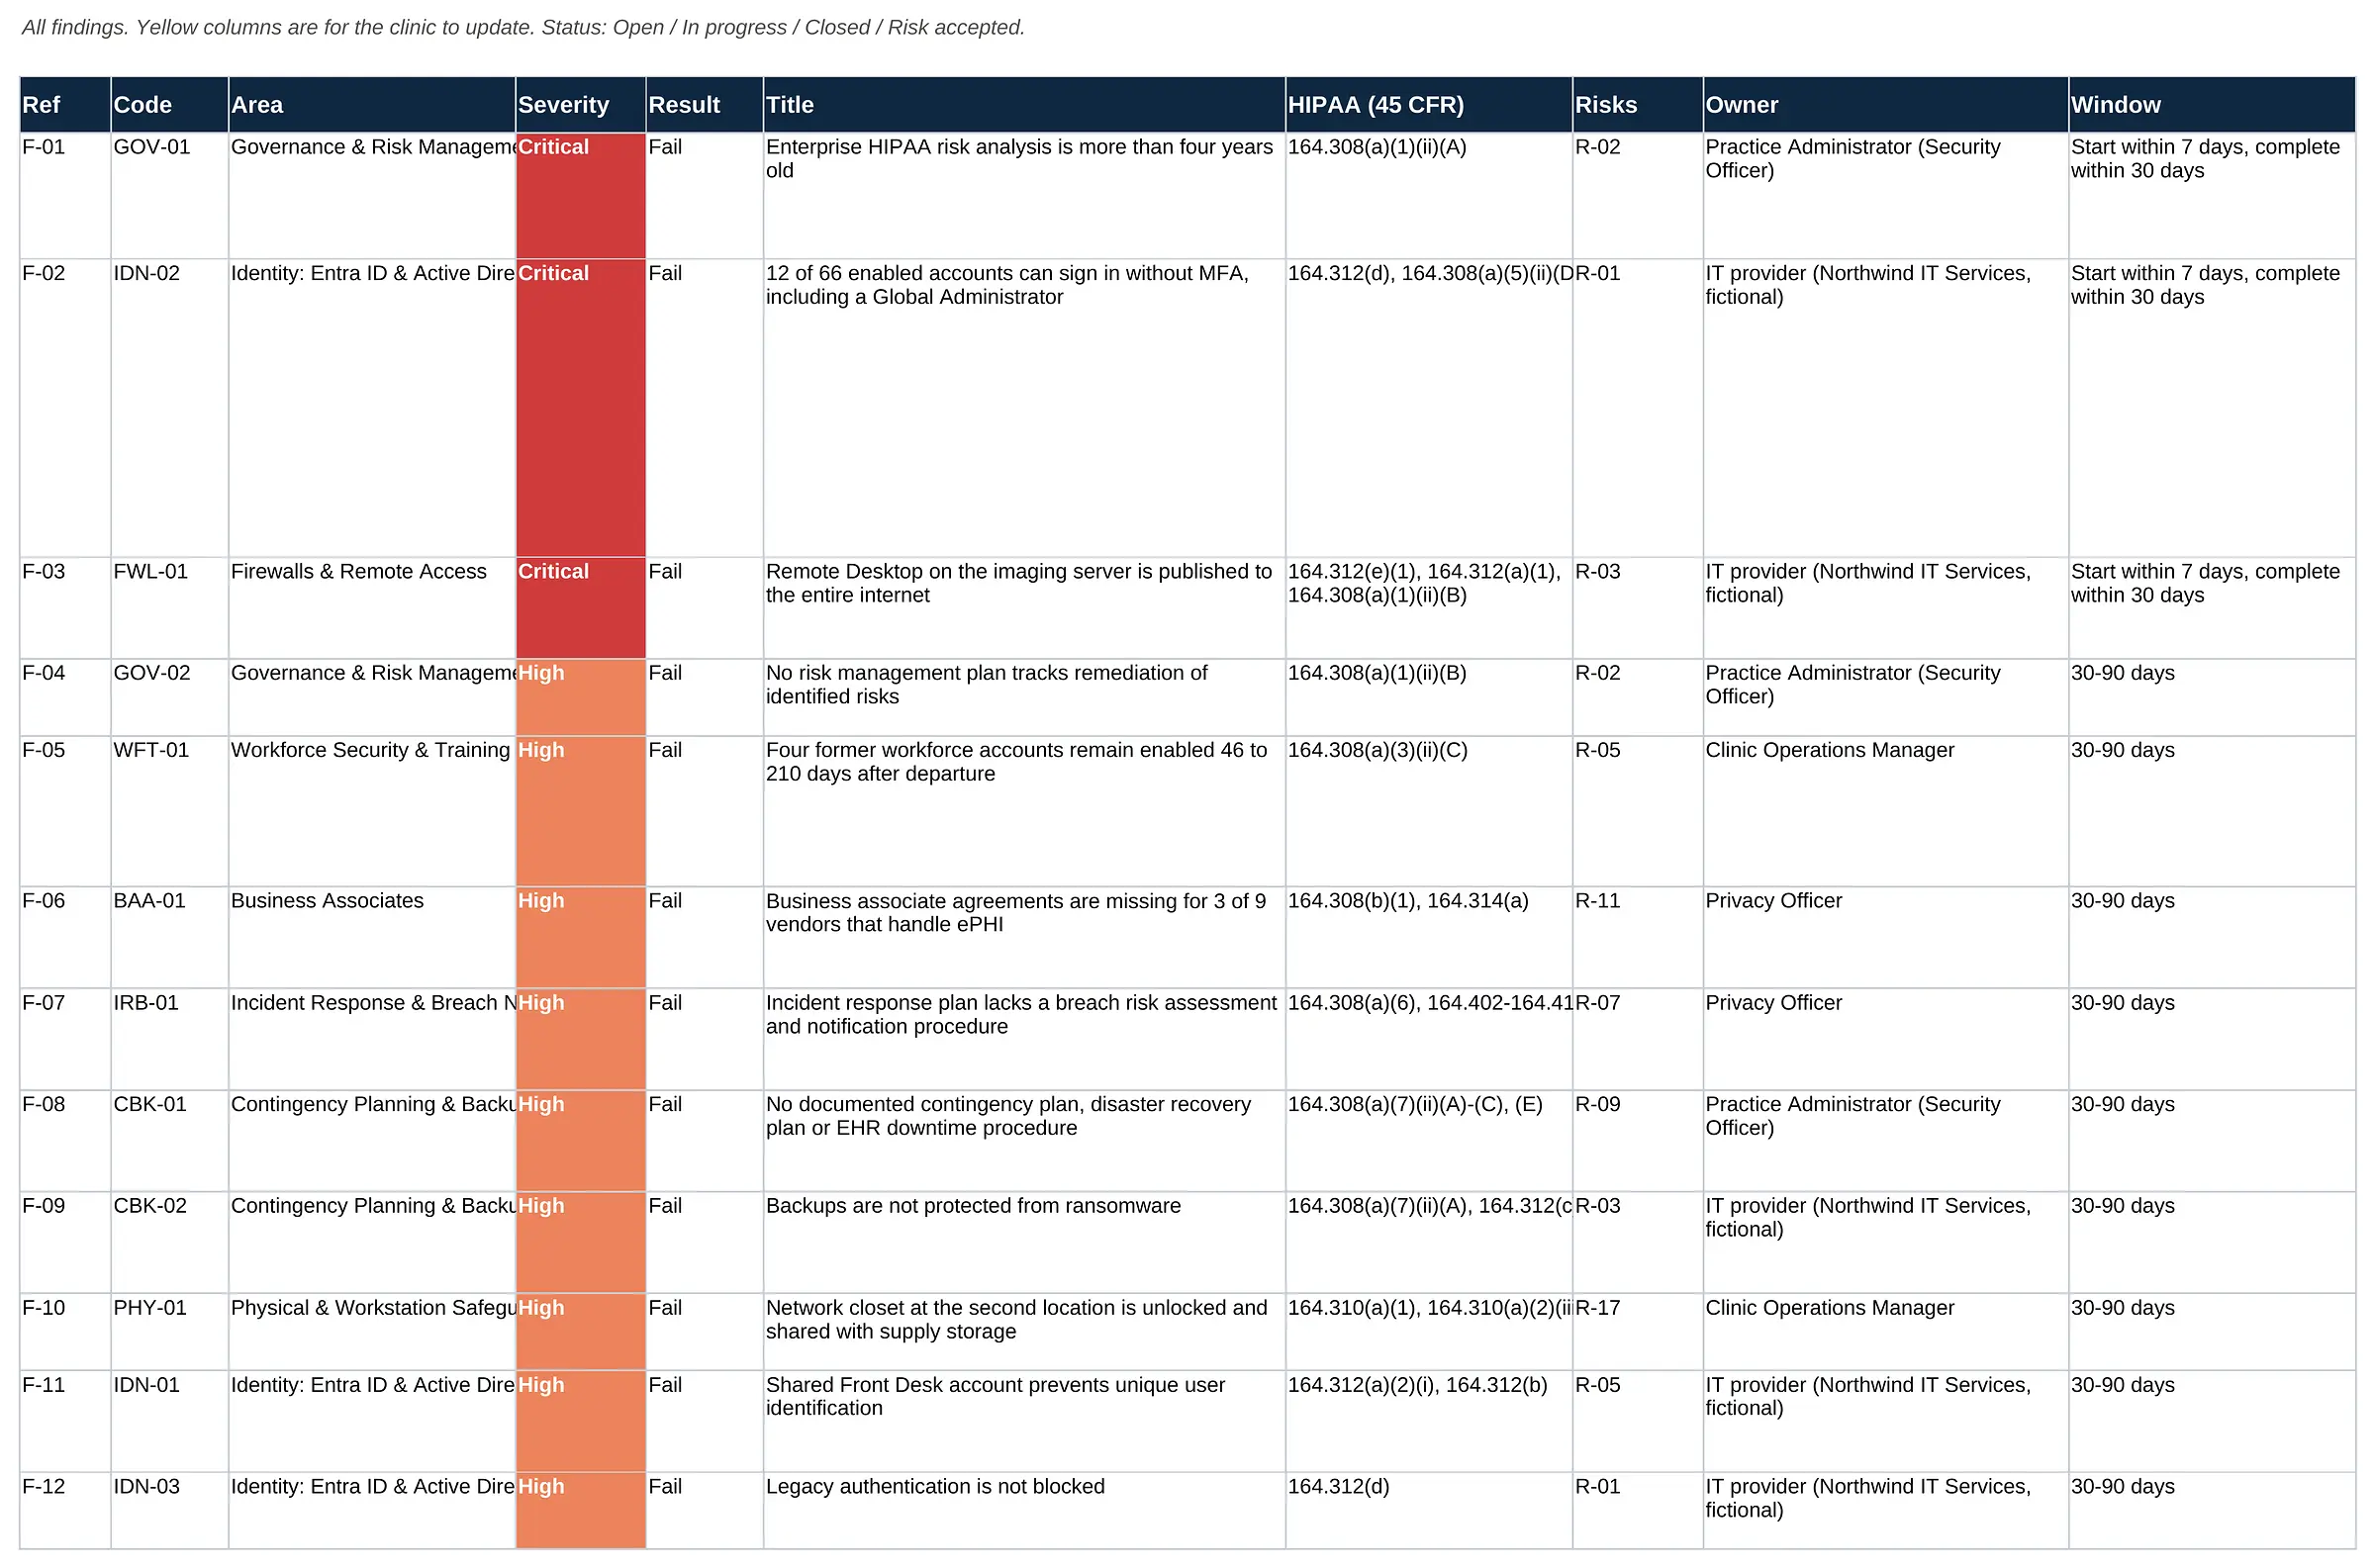
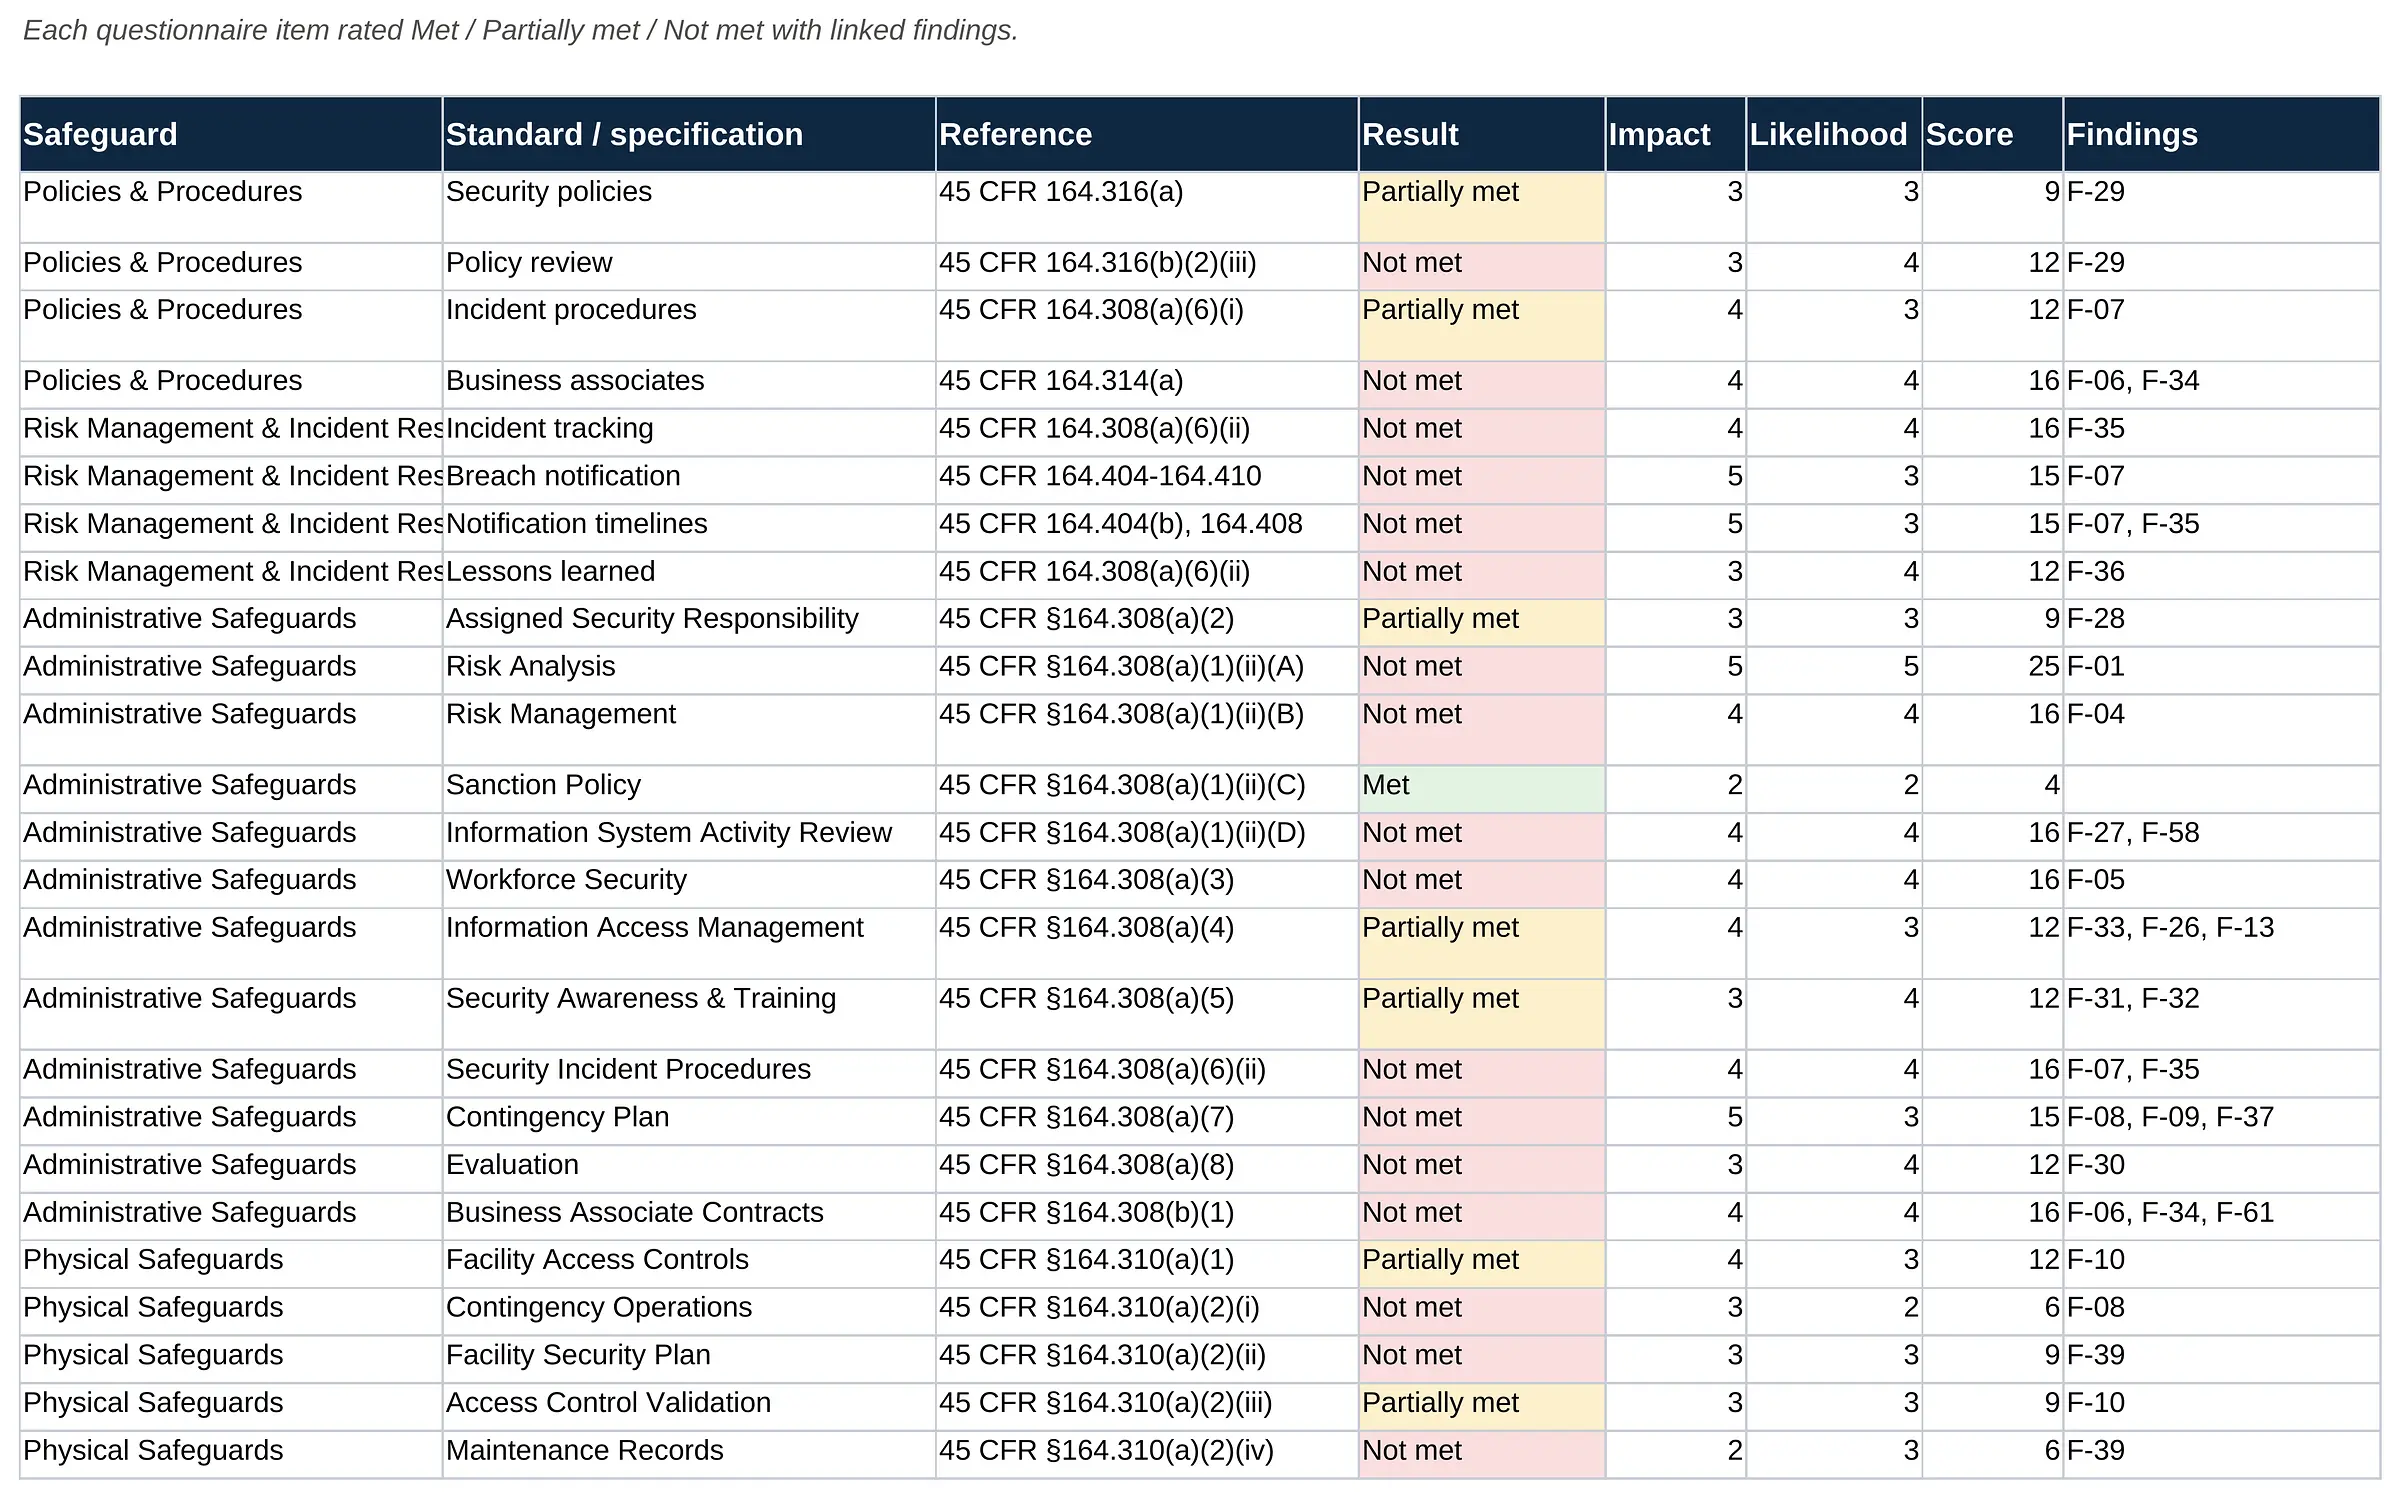
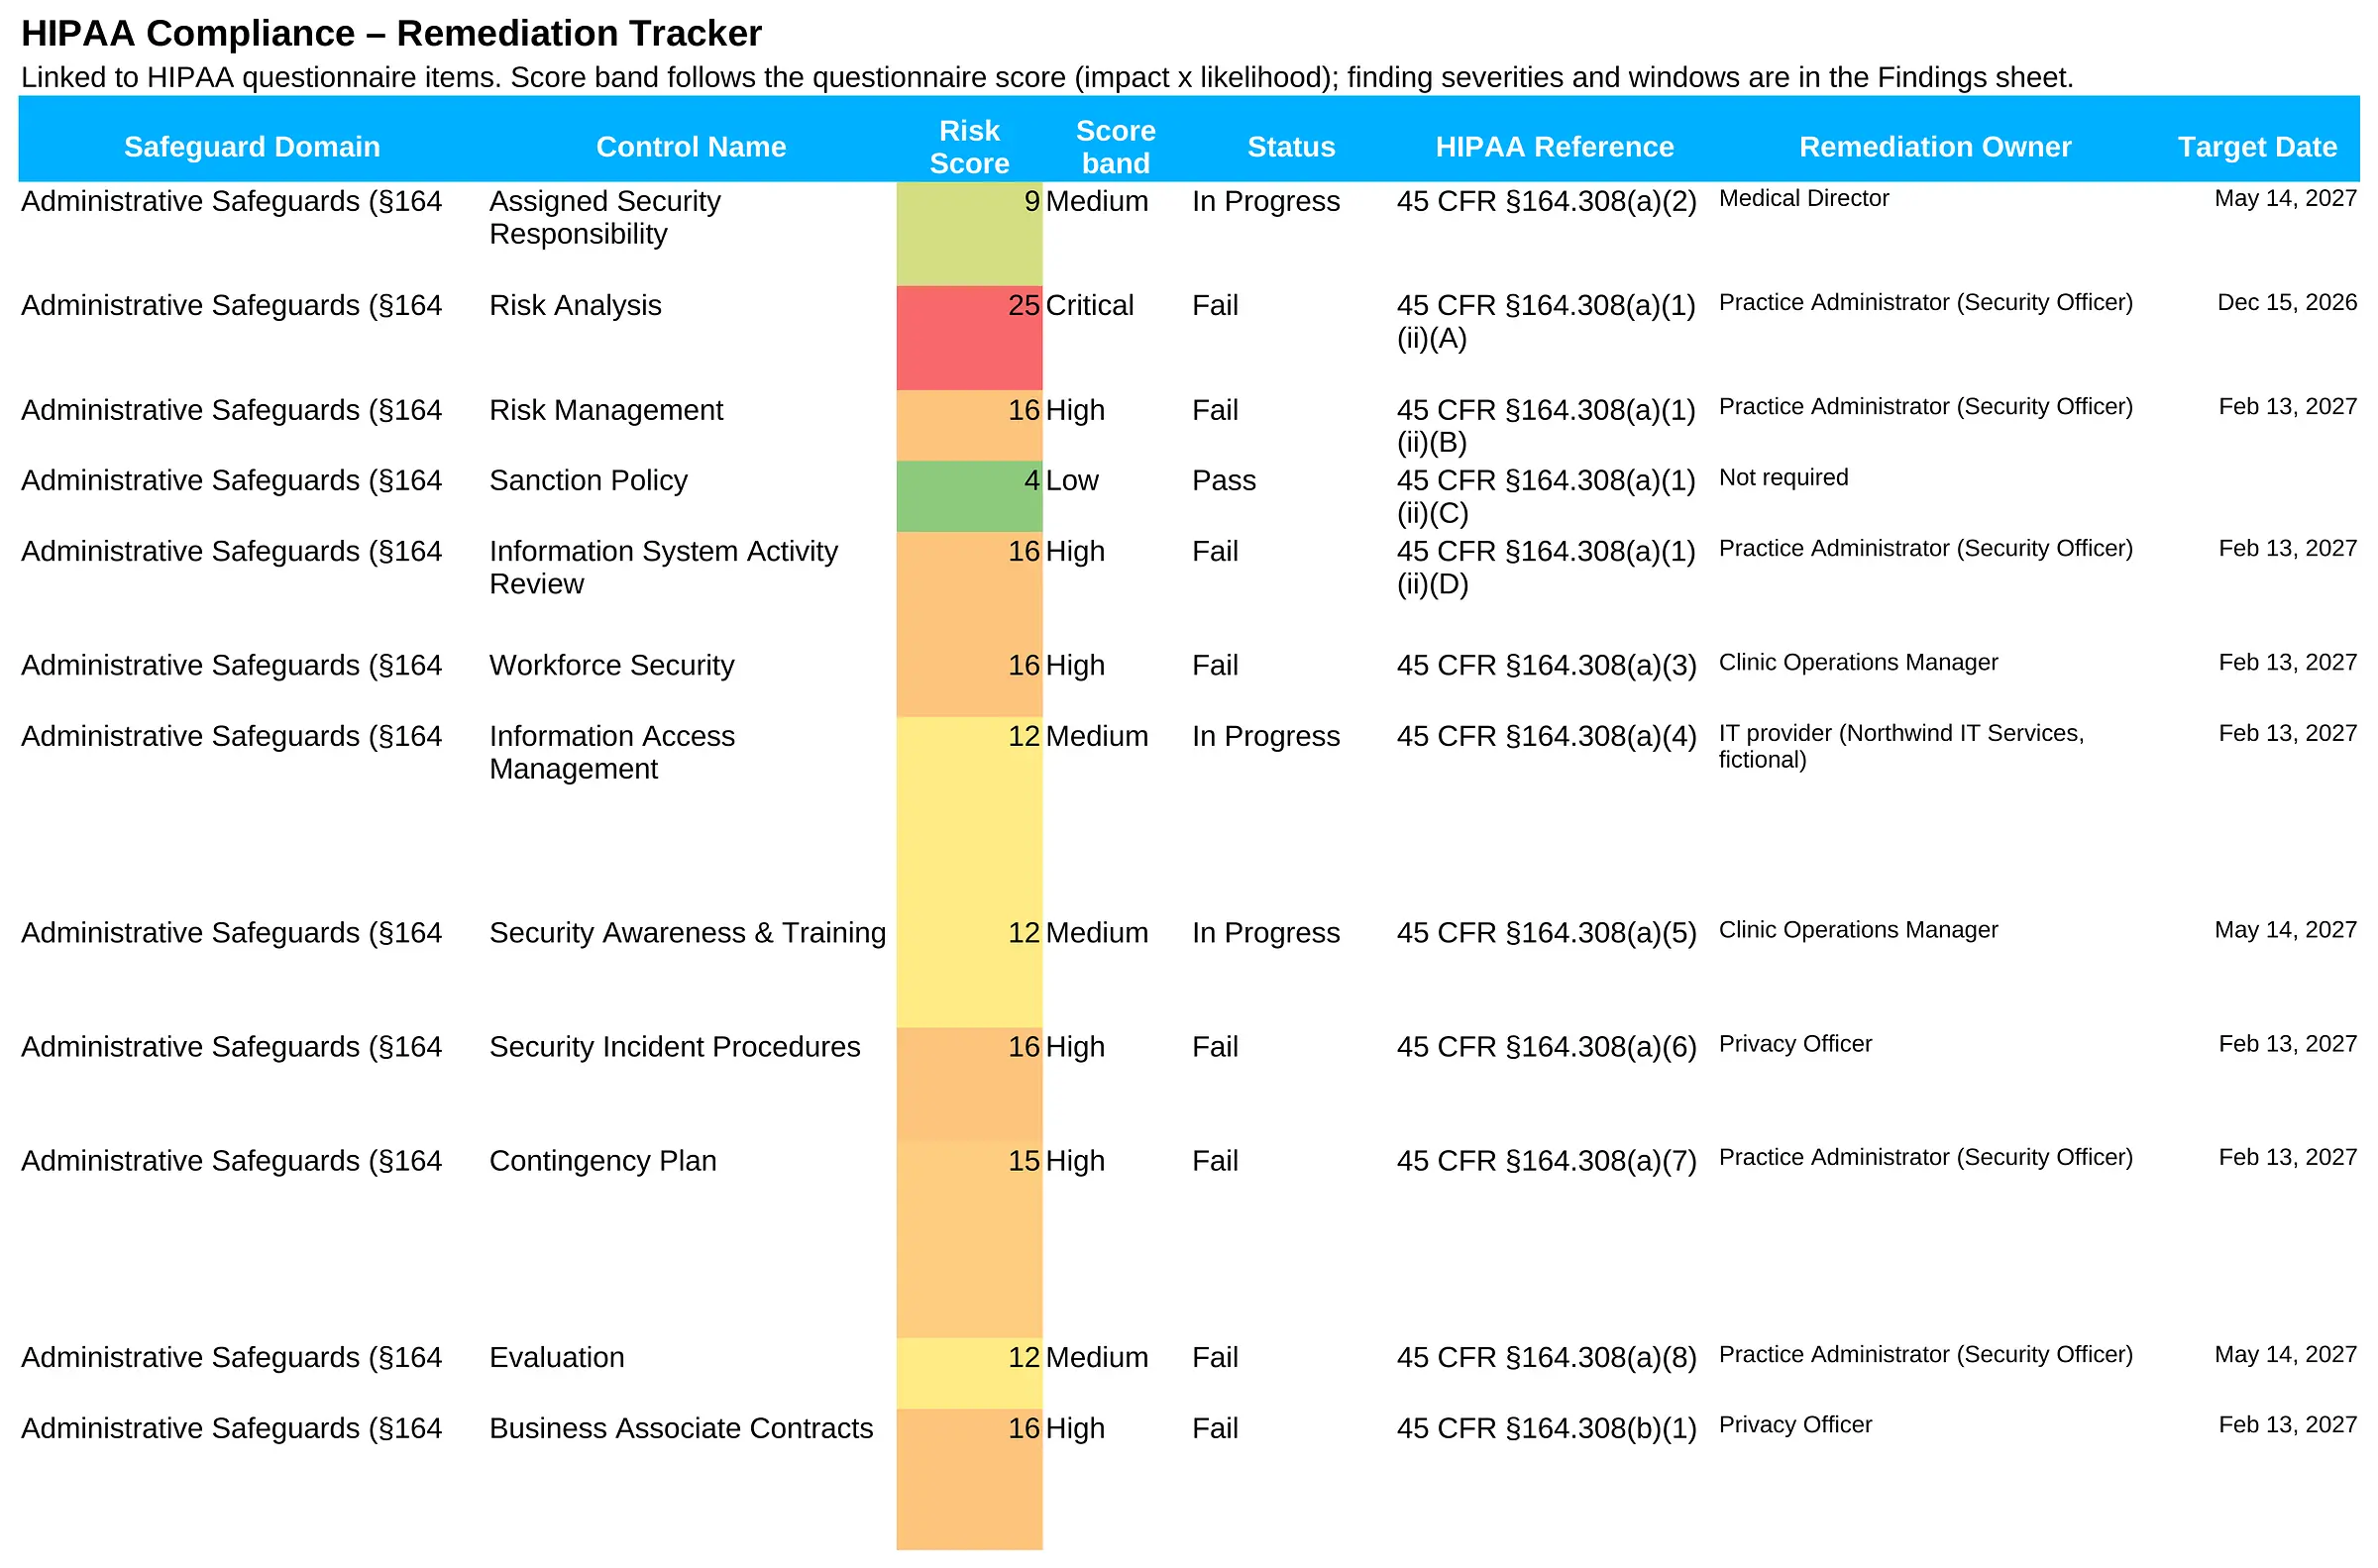
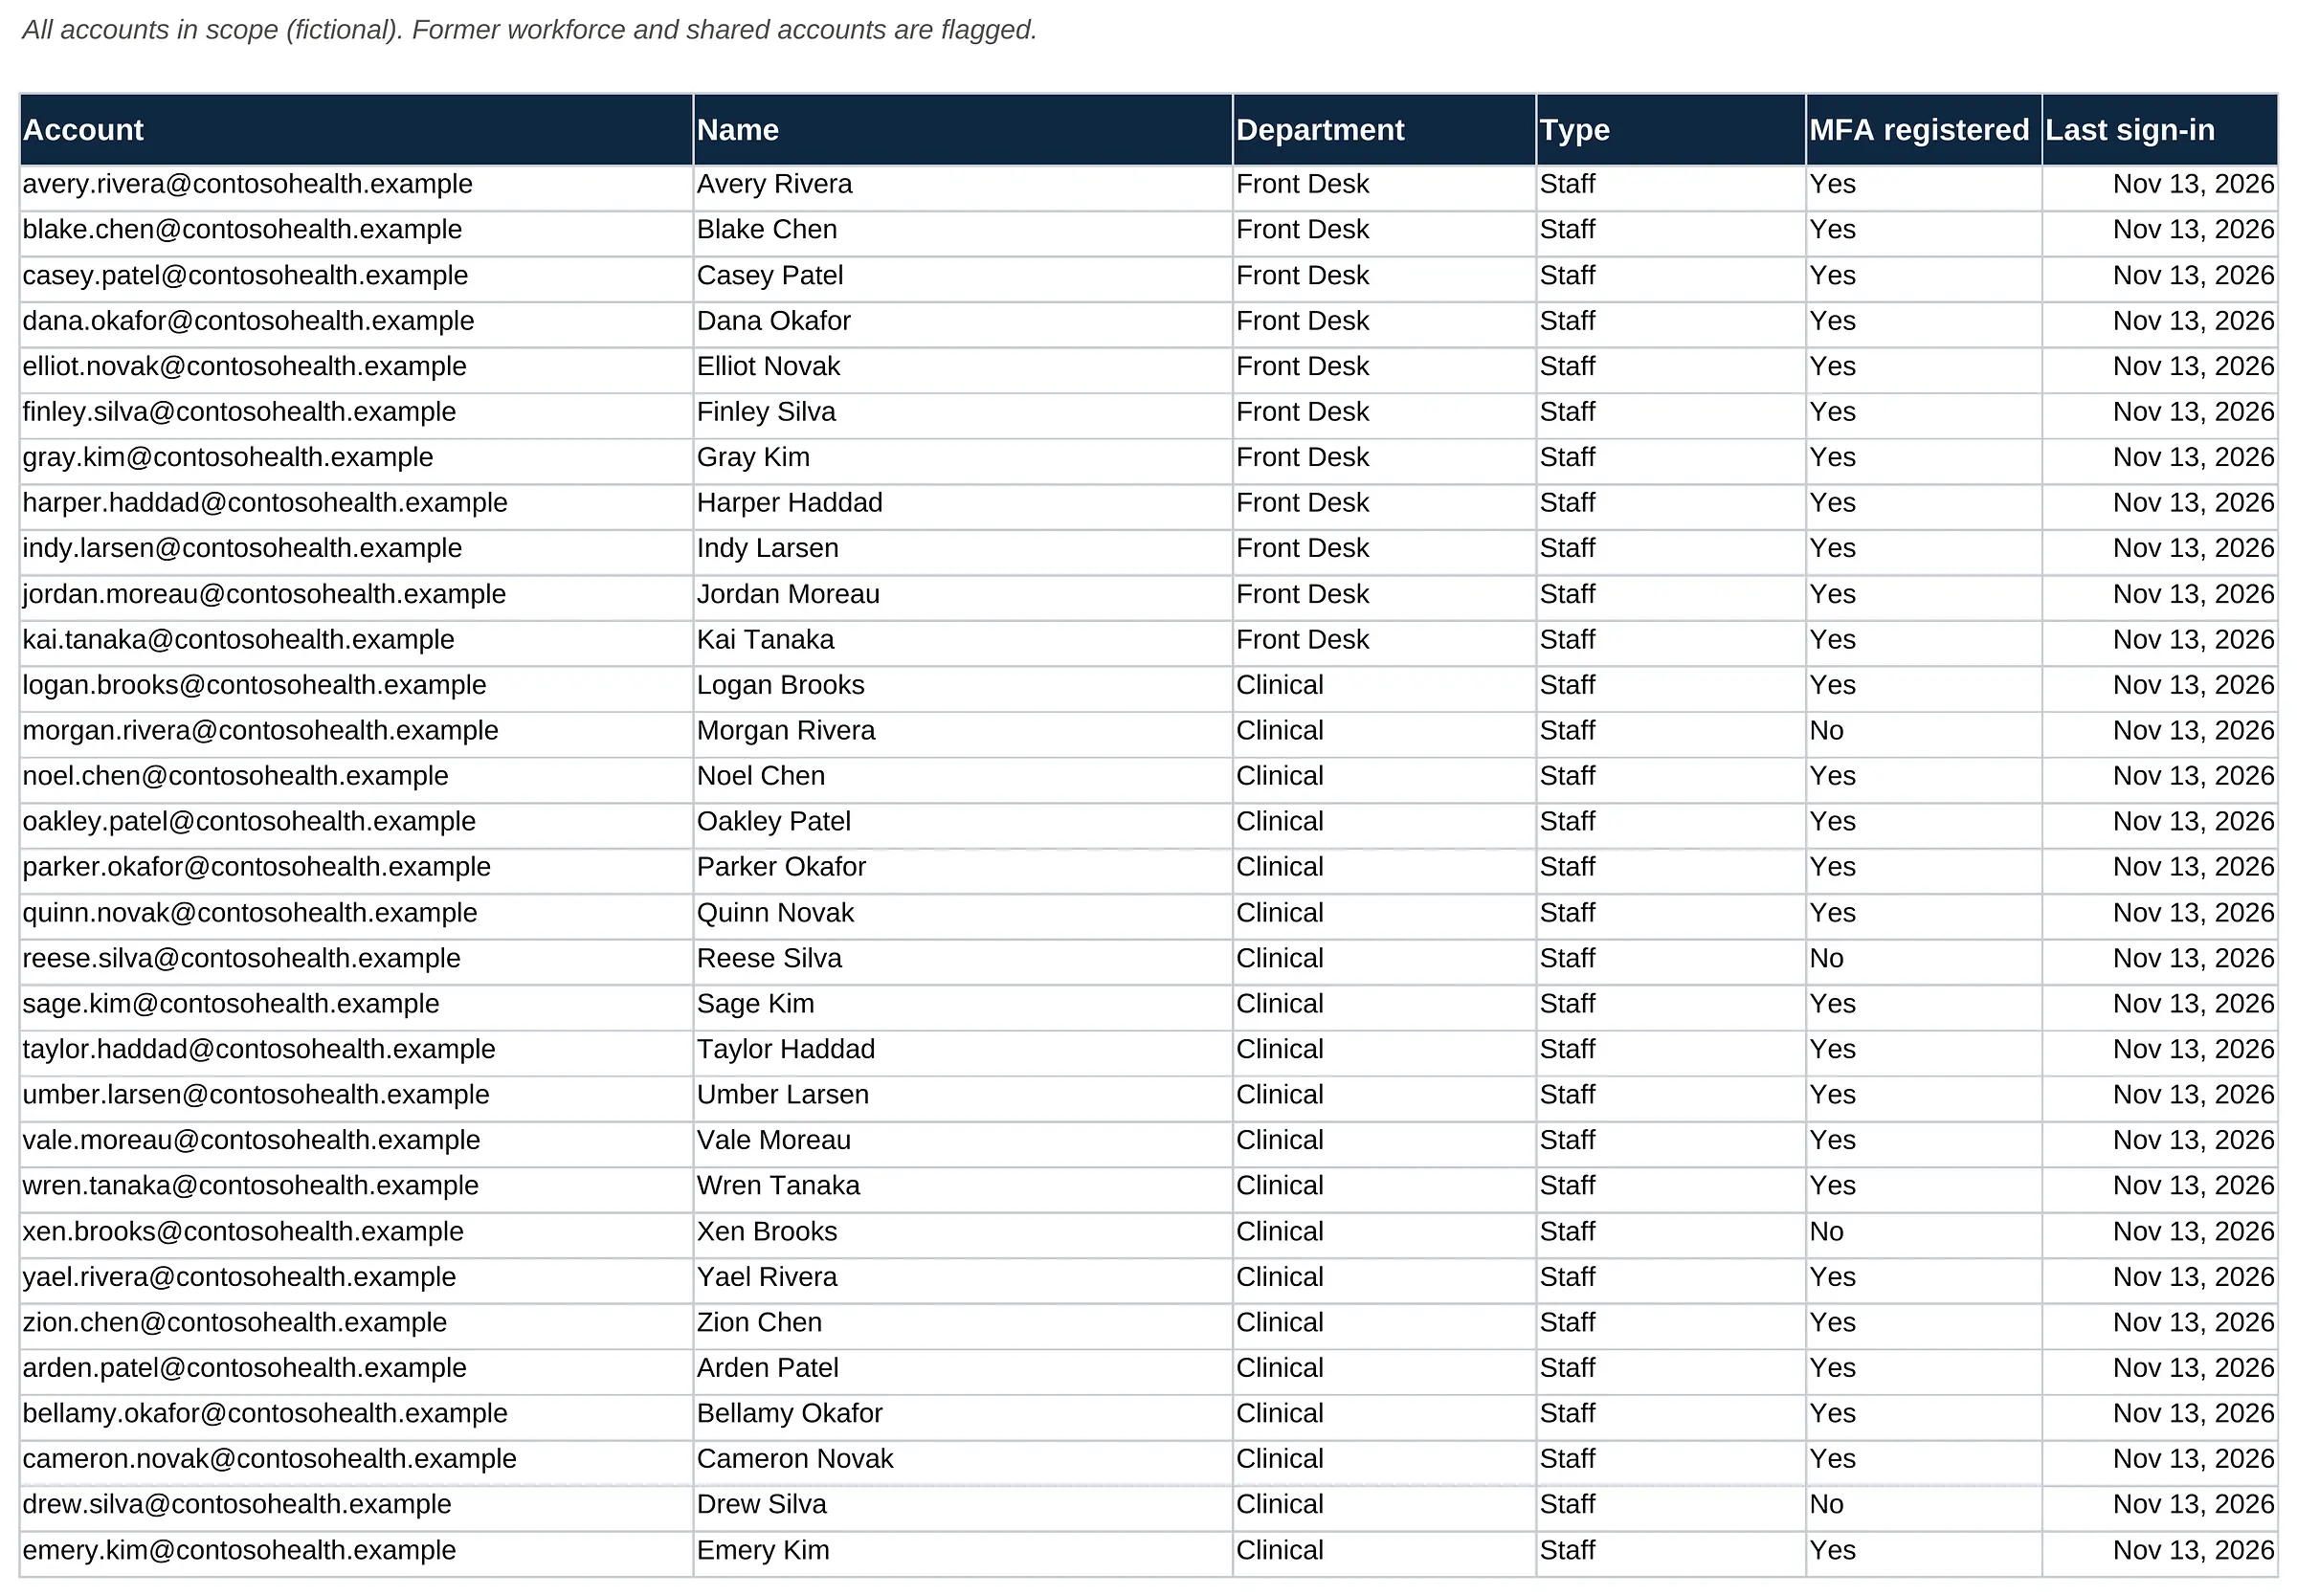
Everything in the reports as filterable data. The completed HIPAA questionnaire, every finding, the risk register, the remediation plan and the account lists, with owner, status and due-date columns your team fills in as items close.
Who uses it
IT provider and internal IT for daily tracking, the Security Officer for evidence, and the next assessor for a fast follow-up comparison.
What is included
SAMPLE · Contoso Family Health Clinic (fictional)
1 / 12
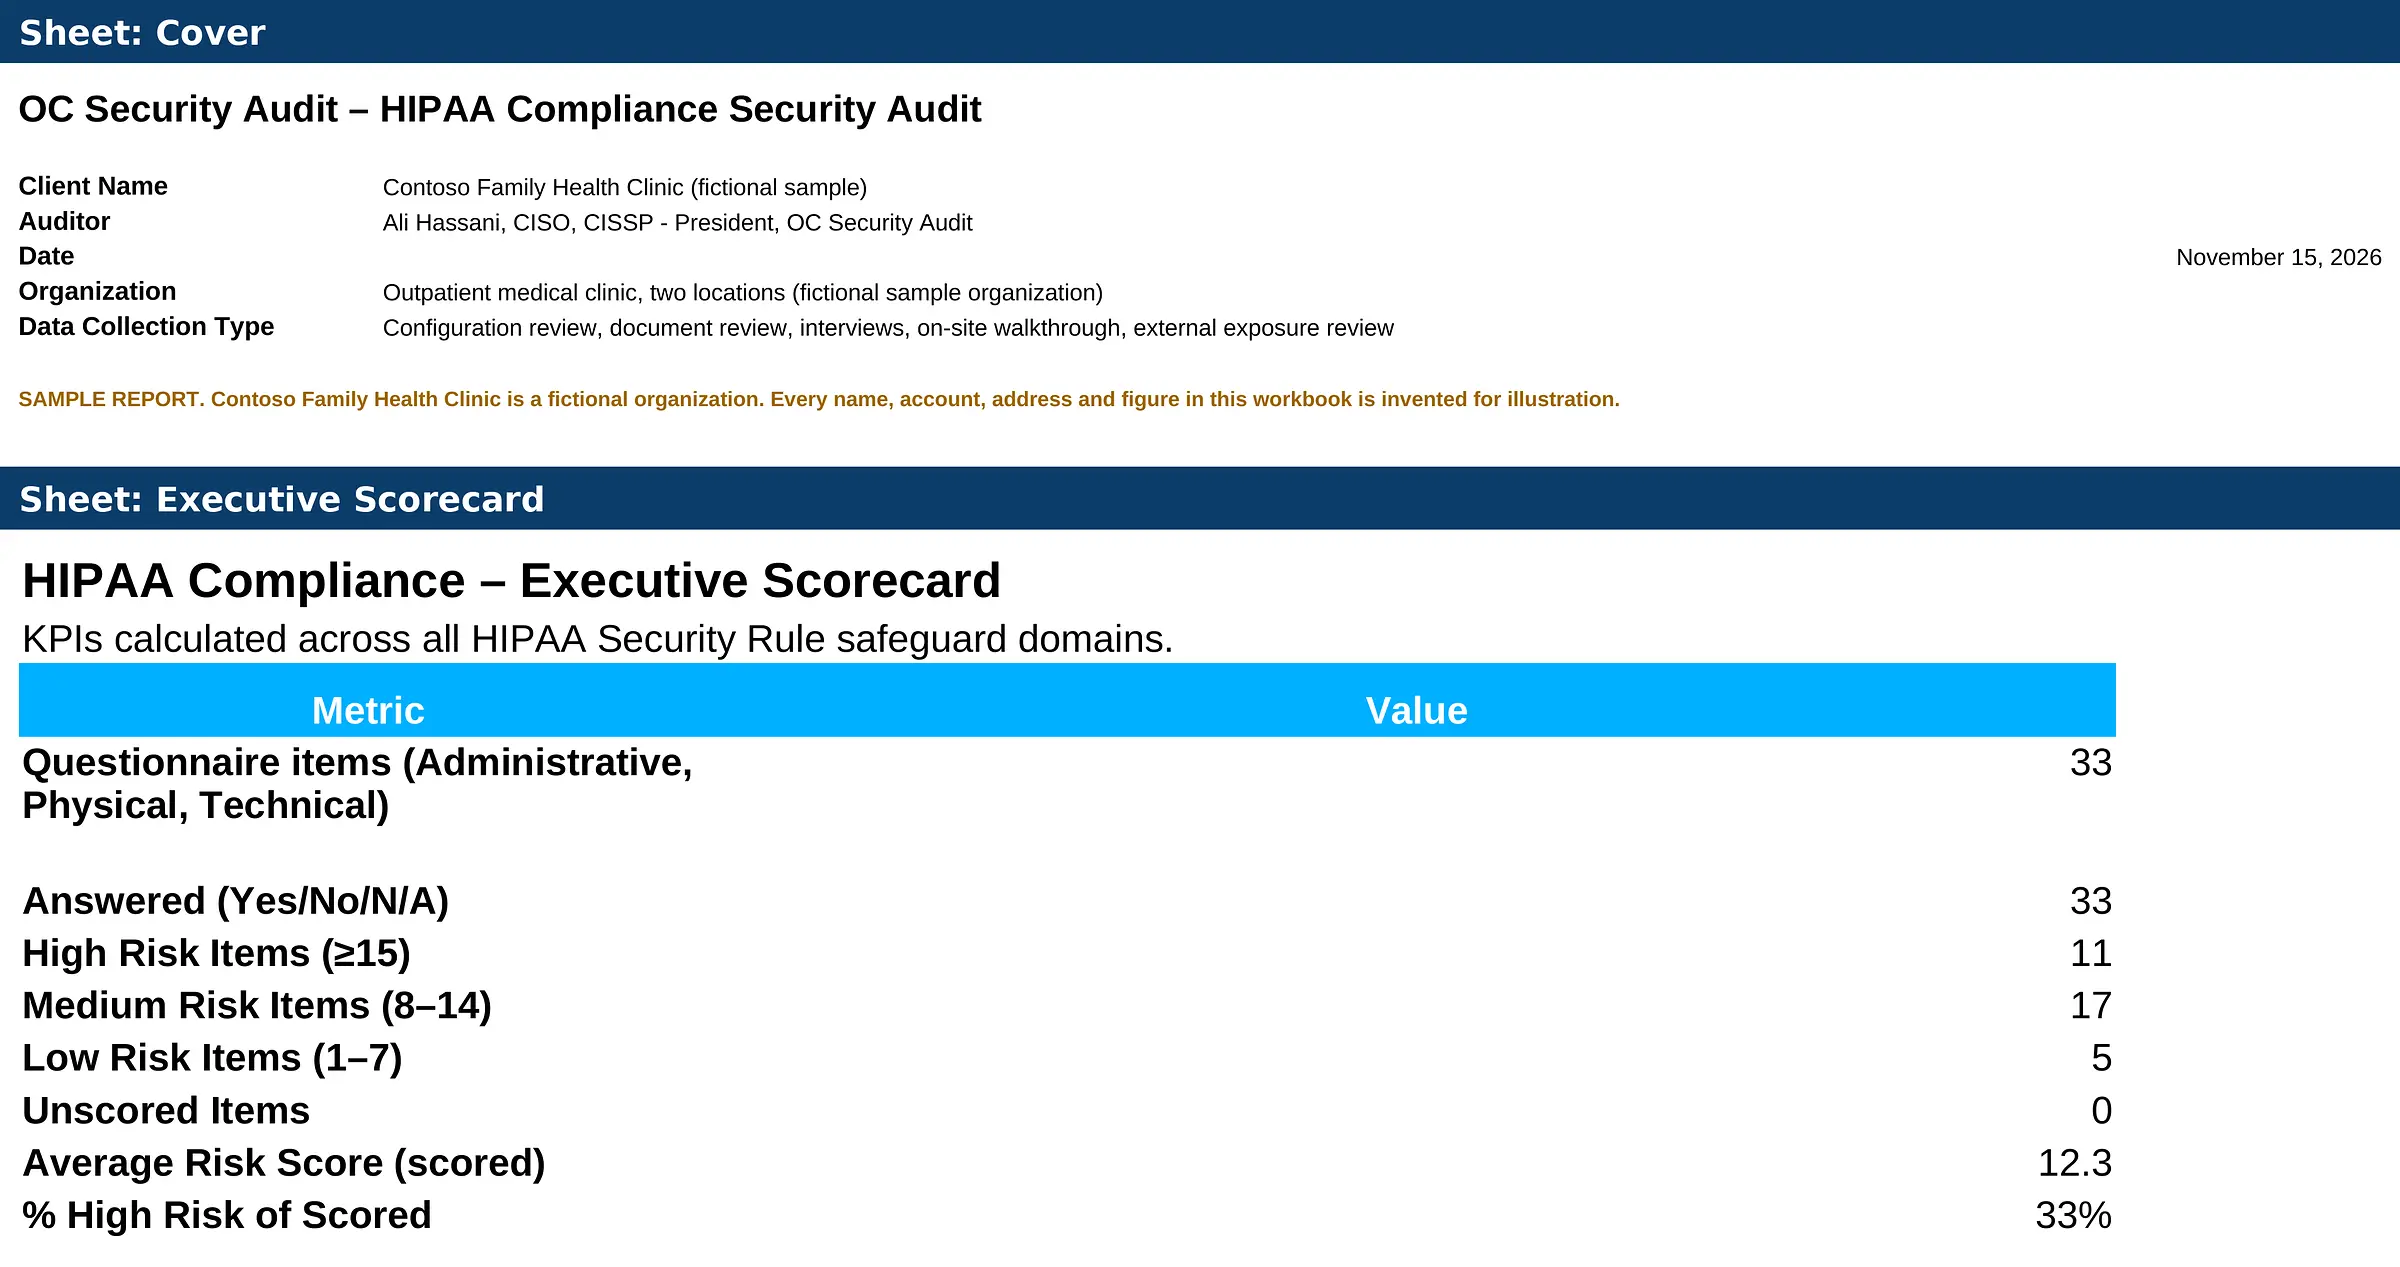
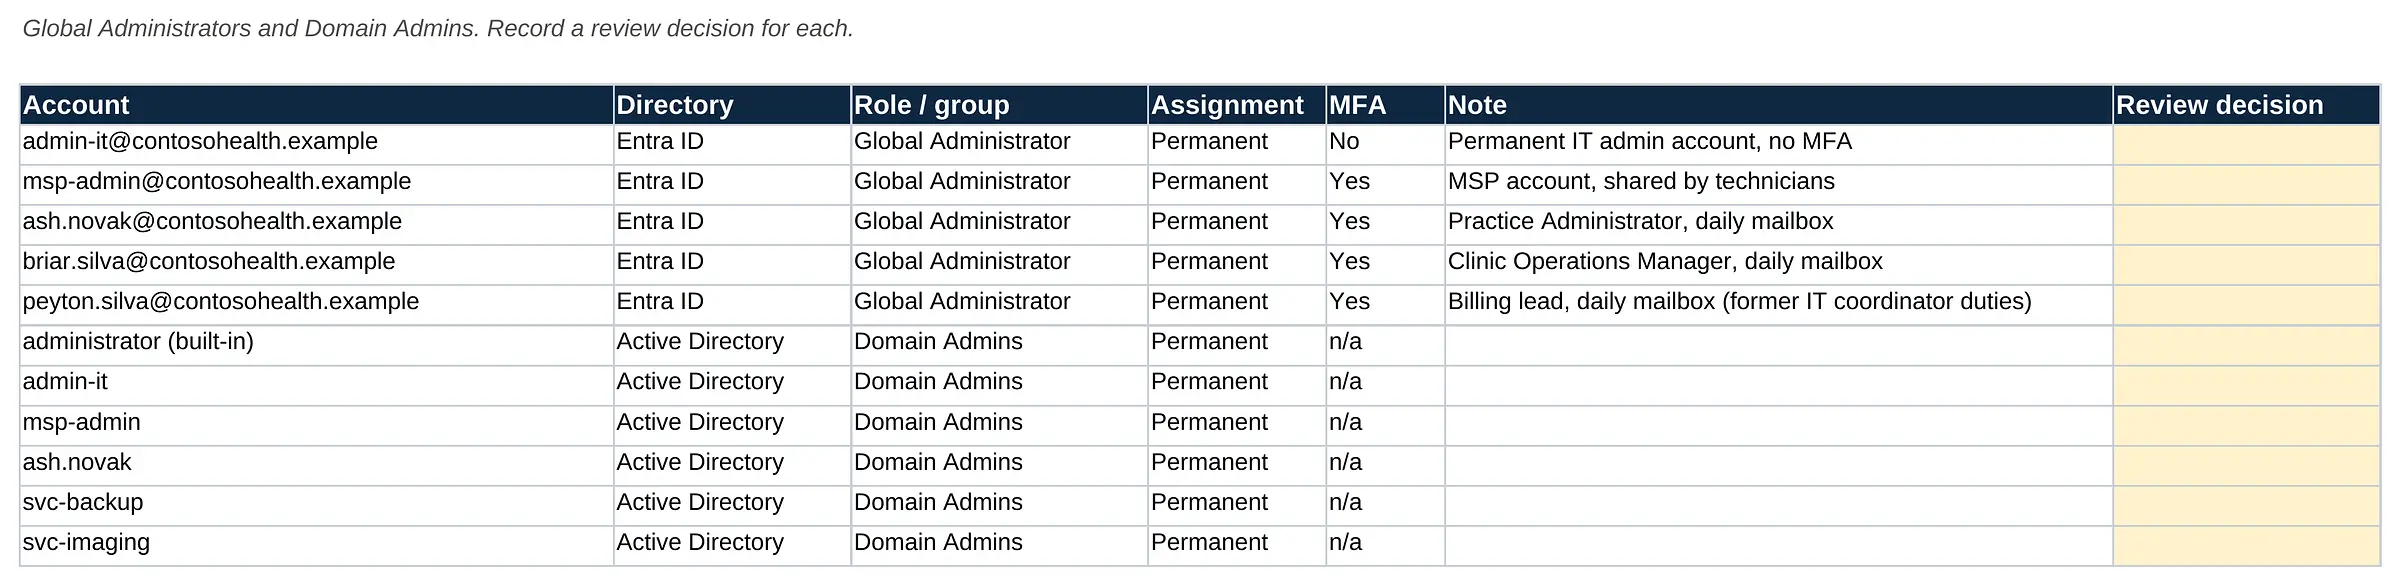
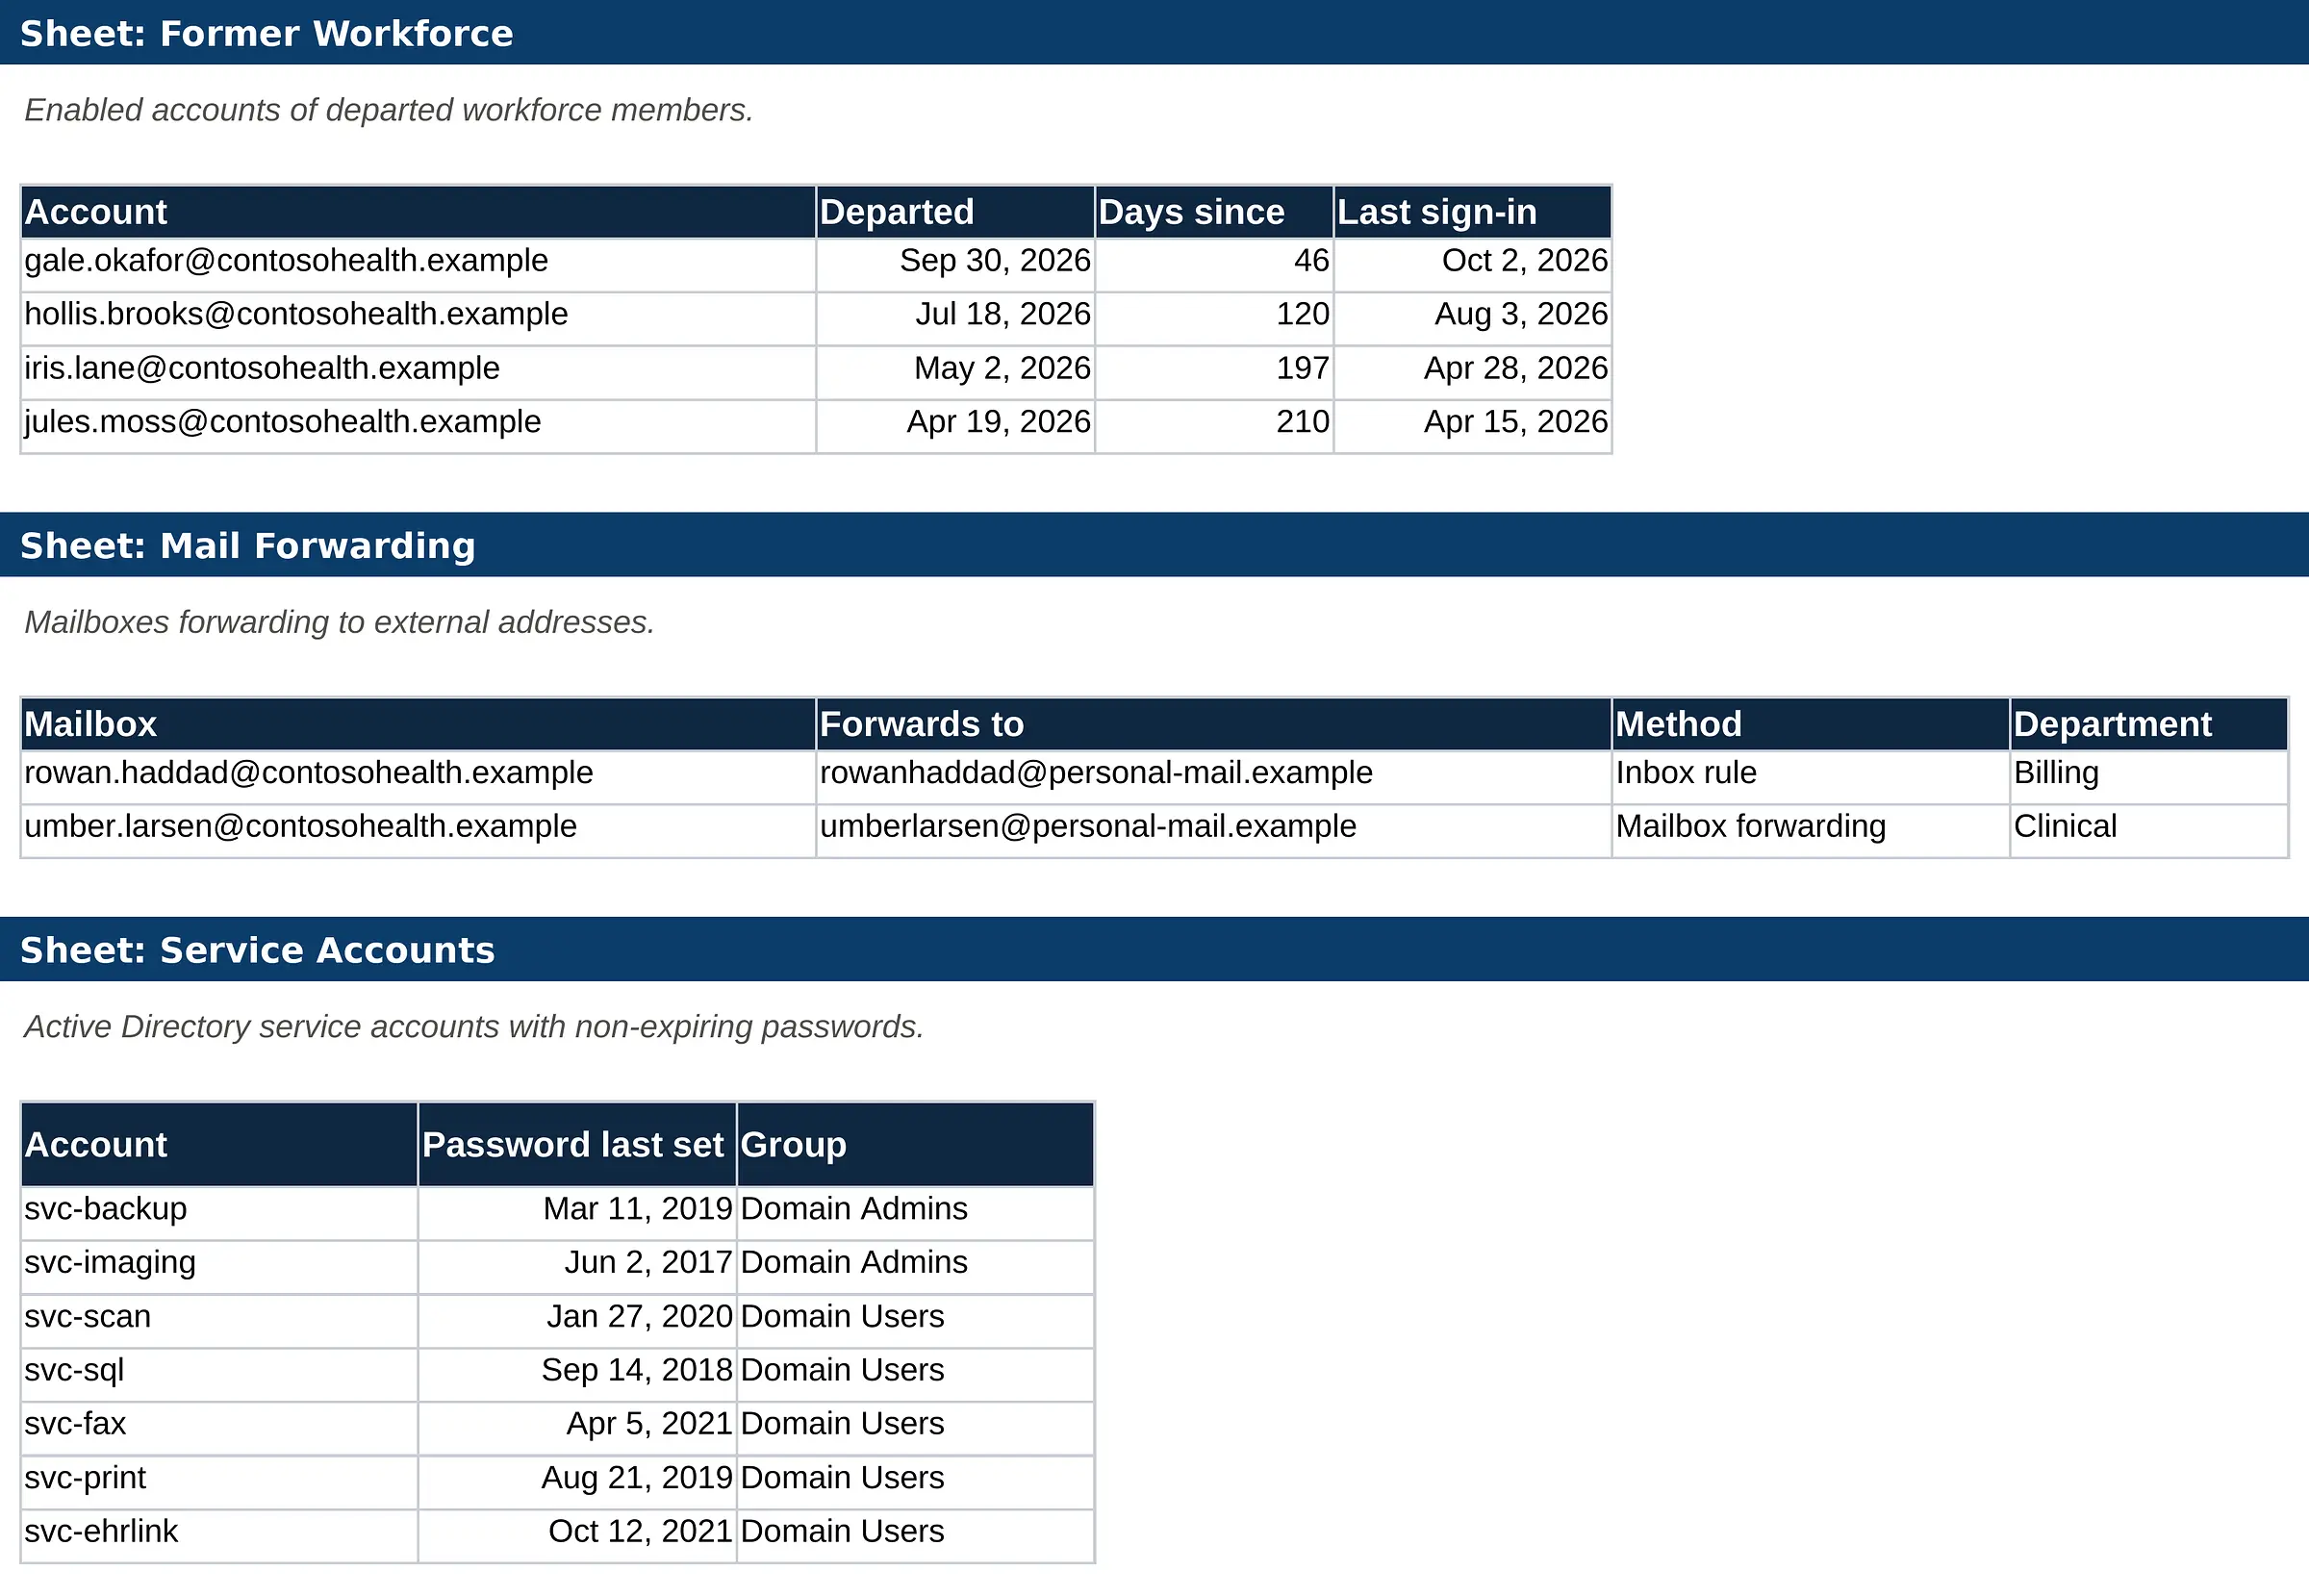
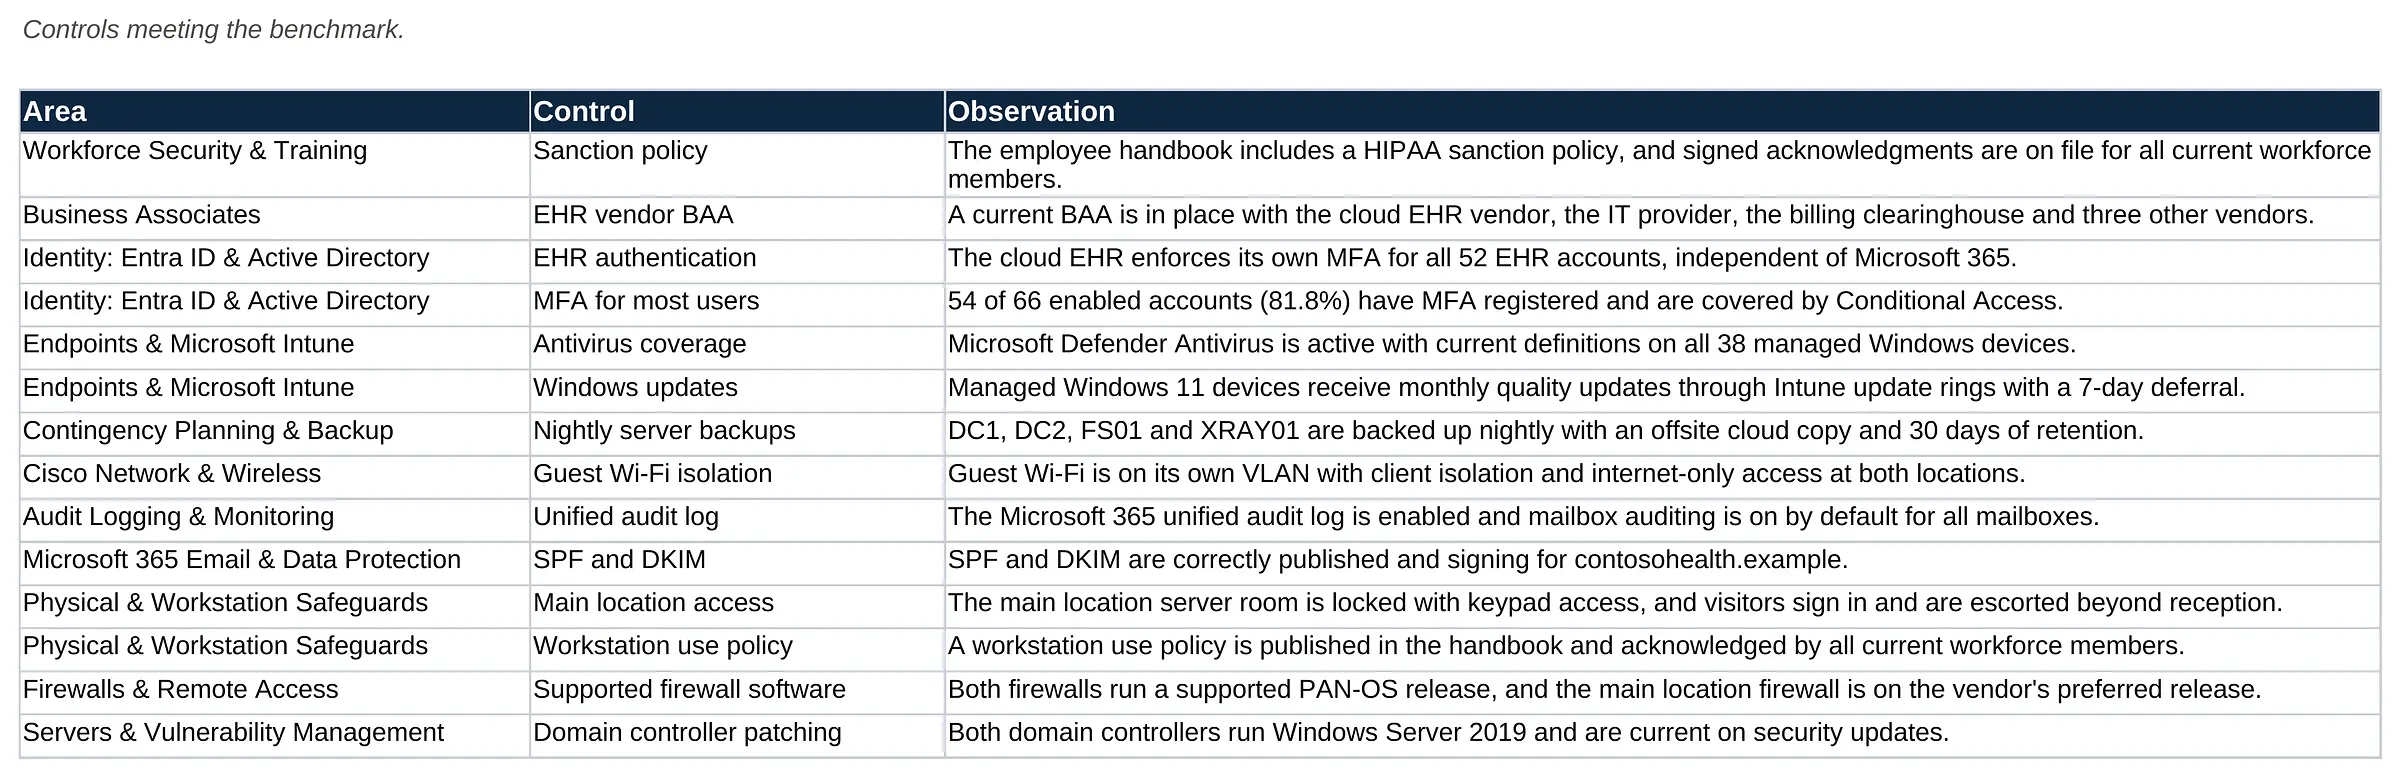
Click the page in the centre to open it full size and zoom in.
How the deliverables connect
Every item carries the same ID through all five deliverables, so nobody has to re-read a 65-page report to know what to do next. Here is one example from the sample.
Finding
F-02 in the Technical Security Report: 12 of 66 enabled accounts can sign in without MFA, including a Global Administrator. HIPAA reference 45 CFR 164.312(d).
Risk
R-01 in the Risk Register: Microsoft 365 account takeover leads to a breach of patient email. Likelihood 4 × impact 5 = 20, Critical, owned by the IT provider.
Action
Phase 0, action 2 in the roadmap: require MFA for the accounts without it, move scan-to-email to a relay, then block legacy authentication, within 7 days.
Tracking
The Findings, Risk Register and Remediation Plan sheets in the workbook carry the same IDs, with owner, status and due date for each item until it closes.
What the assessment covers
The assessment follows the structure of the Security Rule. The table shows what we review in each group and examples of what the sample found at the fictional clinic.
| Safeguard group | What we review | Examples from the sample |
|---|---|---|
| Administrative safeguards, 164.308 | Risk analysis and risk management, Security Officer, workforce security and training, information access, incident procedures, contingency plan, evaluation, business associates | Risk analysis dated 2022, no risk management plan, BAAs missing for 3 of 9 vendors, training 81.0% complete |
| Physical safeguards, 164.310 | Facility access, workstation use and security, device and media controls at both locations | Second-location network closet, automatic lock on exam room PCs, unrestricted USB storage, incomplete hardware inventory |
| Technical safeguards, 164.312 | Access control, audit controls, integrity, authentication and transmission security in Microsoft 365, Entra ID, Intune, Active Directory, firewalls and the network | Shared front desk account, accounts without MFA, anonymous sharing links, VPN without MFA, logs not reviewed |
| Organizational and documentation, 164.314 and 164.316 | Business associate contracts, written policies and procedures, review dates and retention | Website appointment form sends patient data to a provider without a BAA, policies not reviewed since 2021 |
| Breach Notification Rule, 164.400 to 164.414 | How incidents are recorded, assessed and, where required, notified | No incident log and no documented breach risk assessment steps |
An assessment supports your risk analysis and readiness. It is not legal advice and is not a certification of HIPAA compliance; there is no official HIPAA certification. The sample also notes the changes to the Security Rule that HHS proposed on January 6, 2025, as proposed and not final, so the roadmap can prepare for them.
Related
How the assessment runs, the packages, what to prepare and the safeguards we review.
See the service →
Fixed starting prices and a scope estimator for locations, workforce, systems and vendors.
See pricing →
Compare this HIPAA sample with our Microsoft 365, network, firewall and Active Directory samples.
Browse sample reports →
Who prepares the report
Certified CISO (C|CISO) and CISSP with 25+ years in IT, cybersecurity, compliance and infrastructure, and dozens of Microsoft and Cisco certifications, including MCSE, MCITP, MCSA Security, CCNP and CCNA. Every HIPAA assessment is evidence-based and written so the practice owner and the IT team can both act on it.
We stay independent: we assess and advise, and your IT provider or internal team carries out the fixes, with our help if you want it.
FAQ
No. Contoso Family Health Clinic is a fictional organization, and every name, account, address and figure in the sample is invented. We never publish client data. The structure, depth and format are the same as the reports our clients receive.
The full set shown here is an Executive Security Report, a Technical Security Report, a Risk Register, a Next Steps and Security Roadmap, and a Findings Workbook in Excel. The exact set depends on the package you choose; the HIPAA readiness pricing page lists what each package includes.
No. There is no official HIPAA certification, and an assessment is not legal advice. The report shows which Security Rule safeguards are in place, which are missing, the evidence for each and a prioritized plan, which supports your own risk analysis and compliance decisions.
Yes. The Risk Register scores each risk for likelihood and impact on ePHI, names an owner and records the treatment, which is the core of the risk analysis and risk management work in 45 CFR 164.308(a)(1). Whether it meets all of your obligations is a decision for your organization and, where needed, your legal counsel.
We use read-only access to the systems in scope, review documents and interview your staff. Nothing in your environment is changed during the assessment. Your IT provider or internal team carries out the fixes in the roadmap.
HHS published proposed changes to the Security Rule on January 6, 2025. The sample describes them as proposed and not final, and the roadmap points out which planned actions would also prepare the clinic for them.
Yes. OC Security Audit is based in Irvine and works on-site across Orange County, Los Angeles and Southern California, and remotely with practices and business associates nationwide.
Tell us about your locations, systems and vendors. We will confirm the scope, the deliverables and a written fee before any work starts.
Or call 949-777-5567
This website uses essential cookies for security and operation. Optional analytics and advertising cookies help measure site use and outreach. Choose Allow or Deny. You can change your choice at any time.