Network administrator working on a laptop beside a server rack
Orange County Technical security implementation

Server Security Hardening Assessment

Use this server security hardening to identify gaps across secure configuration, privileged access, and logging and monitoring. Treat the result as initial guidance and validate material findings through a professional review.

CISO-led guidance from Ali Hassani, backed by 25+ years of IT, cybersecurity, compliance, and infrastructure experience.

25+ yearsIT & cybersecurity experience
Certified expertsCISSP · C|CISO · Microsoft · Cisco
Southern CaliforniaLocal and on-site, based in Irvine
NationwideRemote audits & advisory

FROM FIRST CHECK TO NEXT STEP

Which Server Hardening Gaps Need Validation?

Answer against the systems and workloads your organization actually operates. Use the assessment to identify unverified settings and plan safe, scoped follow-up.

  • Review administration, patching, and service exposure.
  • Check monitoring and recovery readiness.
Discuss My Server Hardening Results

Initial guidance only, not a professional audit or compliance certification. Do not enter confidential information.

Ali Hassani, CISO, in a datacenter
OC Security Audit

Practical server-hardening guidance for business networks

OC Security Audit provides cybersecurity audit, security assessment, compliance-readiness, risk-assessment, Microsoft 365, Azure, firewall, vulnerability-assessment, and vCISO advisory services for organizations in Orange County, Irvine, Los Angeles County, and Southern California.

Ali Hassani, CISO, is a cybersecurity consultant with 25+ years of hands-on experience supporting business networks through security audits, security implementation, infrastructure improvement, risk reduction, and operational planning.

CISSPCCISOMCSEMCSA SecurityMCITPCCNACCNP
5–10 minutesTypical completion time
50 questionsSimple controlled selections
7 categoriesSecurity domains reviewed
Instant reportOn-page charts and priorities
Secure configurationBaseline standards, approved builds, drift detection, and controlled exceptions.
Patch and exposure reviewRisk-based updates, vulnerability scans, internet-facing systems, and KEV prioritization.
Access and monitoringAdministrative controls, least privilege, centralized logging, alerting, and EDR coverage.
Resilience and recoveryProtected backups, restore testing, physical safeguards, and business-continuity alignment.
Important disclaimer. This free Server Security Hardening Assessment is an introductory informational tool provided by OC Security Audit. It is not a formal audit, penetration test, vulnerability scan, configuration review, legal opinion, compliance determination, certification, attestation, guarantee, or substitute for professional advice. Results depend entirely on the selections made. Do not change server, firewall, identity, backup, cloud, logging, or application settings solely because of this tool. Always consult a qualified cybersecurity consultant, appropriate vendors, and legal or compliance advisors before taking action.

Start the server-hardening self-assessment

Answer the questions using controlled selections. Use the information dropdown below each question for checking guidance, risk level, and potential impact.

0 of 50 questions answered
OC Security Audit free assessment tools

Server Security Hardening Assessment Report

This introductory report is generated locally in your browser from controlled selections. No information is submitted to OC Security Audit.

0%
Preliminary risk level

Executive summary

Optional context selected

No optional context was selected.

Assessment analytics

0Critical priorities
0High priorities
0Medium priorities
0Questions answered

Risk level by assessment category

Highest-priority areas to validate

Recommended next steps

1. Validate the highest-priority findings with evidence review and technical testing.

2. Prioritize unsupported systems, internet-facing services, KEV-listed vulnerabilities, exposed administrative protocols, privileged access, missing logging, and untested backups.

3. Review remediation sequencing, maintenance windows, rollback planning, and operational impact with qualified consultants and vendors.

4. Reassess after remediation to confirm that controls remain effective.

Ali Hassani, CISO

Discuss the report with OC Security Audit

Ali Hassani, CISO, brings 25+ years of hands-on IT and cybersecurity experience. For a professional server-hardening, vulnerability-assessment, or infrastructure-security consultation, call 949-777-5567 or contact OC Security Audit.

Final disclaimer and limitation of liability. This report is a free, preliminary server-security-hardening summary provided by OC Security Audit. It is not a formal audit, penetration test, vulnerability scan, configuration review, forensic investigation, legal opinion, compliance determination, insurance representation, certification, attestation, guarantee, or professional-services engagement. It may be incomplete or inaccurate because it is based only on self-reported selections and does not inspect servers, operating systems, cloud resources, hypervisors, network paths, firewall rules, identity platforms, logs, backup systems, evidence, vendor contracts, legal obligations, or actual incident-response performance. Do not implement changes solely because of this report. Always consult qualified cybersecurity, technology, legal, compliance, insurance, and vendor advisors. To the maximum extent permitted by applicable law, OC Security Audit, its representatives, and related parties disclaim liability for any action, inaction, decision, outage, loss, cost, damage, or outcome arising from or related to this tool or report.

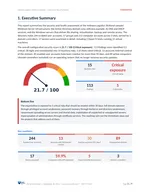
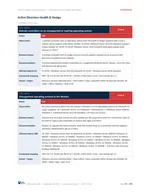
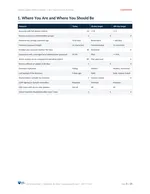
Microsoft 365 audit sample executive report cover (fictional company, illustrative data)Entra ID audit sample executive report cover (fictional company, illustrative data)Palo Alto firewall audit sample executive report cover (fictional company, illustrative data)

Sample reports

This tool is a quick check. A full audit goes further.

See what a full security audit delivers: real pages from our executive and technical reports, risk registers, roadmaps and workbooks, for fictional companies.

Browse sample reports