
iPhone Security for Healthcare and Regulated Businesses
Build an iPhone security program for healthcare and regulated work covering ePHI, MDM, apps, messaging, lost devices, risk analysis, evidence, and vendors.
Read articleFind exposure, strengthen essential controls, and build practical resilience around the systems your organization depends on.
Explore cybersecurity services →Evaluate controls independently, document defensible findings, and focus remediation on the risks with the greatest operational impact.
Explore security audits →Translate security obligations into clear evidence, accountable remediation, and a practical path toward audit or customer readiness.
Explore compliance services →Bring security governance, risk decisions, leadership communication, and improvement planning into one accountable executive program.
Explore vCISO services → Build an iPhone security program for healthcare and regulated work covering ePHI, MDM, apps, messaging, lost devices, risk analysis, evidence, and vendors.
Read article
Compliance and Regulatory Updates PCI DSS Payment-Page Scripts and E-Skimming: Evidence for Requirements 6.4.3 and 11.6.1 Prepare defensible PCI DSS evidence for payment-page script authorization, integrity monitoring, inventory, change detection, and e-skimming response under Requirements 6.4.3 and 11.6.1. Call 949-777-5567 Schedule a Compliance Review CISO-led analysis by Ali Hassani, backed by 25+ years of IT,…
Read article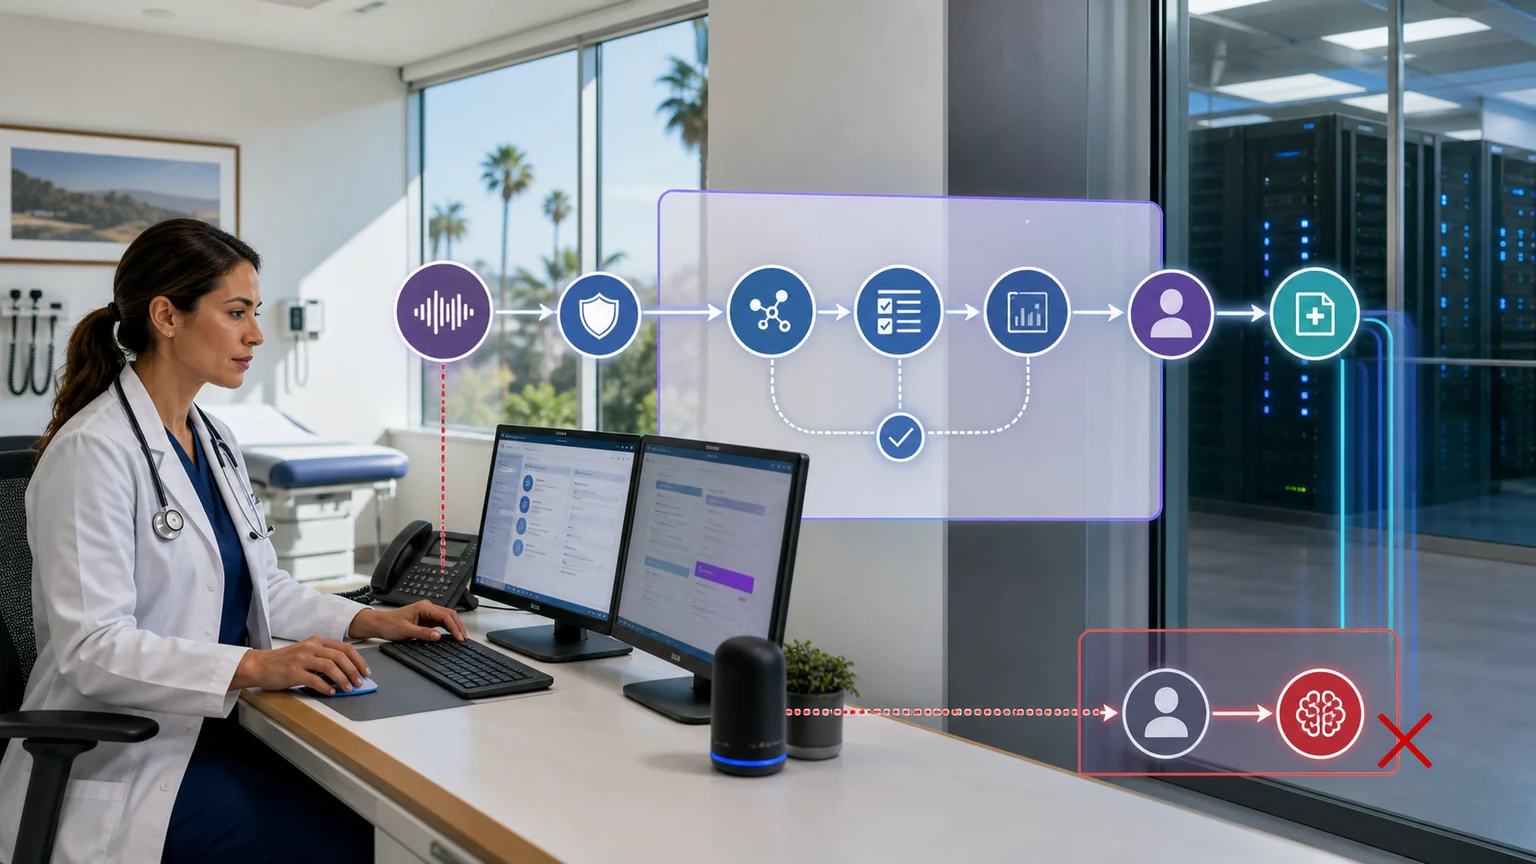
Compliance and Regulatory Updates HIPAA and AI Tools: Mapping ePHI, Vendors, BAAs, Risk Analysis, and Human Review Evaluate AI tools that may handle ePHI by mapping data flows, confirming vendor responsibilities and BAAs, documenting risk analysis, and keeping qualified human review in the process. Call 949-777-5567 Schedule a Compliance Review CISO-led analysis by Ali Hassani,…
Read article
PCI DSS v4.x provides flexibility, but not all flexibility works the same way. A compensating control is not a convenient substitute for a difficult requirement, and the customized approach is not a way to avoid defined testing. Each has a different purpose, design burden, documentation model, and assessment path.
Read article
Separate current HIPAA Security Rule duties from proposed changes, then prioritize risk analysis, hardening, identity, logging, backup, and evidence.
Read article
Understand California’s final cybersecurity audit and risk-assessment regulations, scope, timing, evidence, independence, and readiness steps.
Read articleThis website uses essential cookies for security and operation. Optional analytics and advertising cookies help measure site use and outreach. Choose Allow or Deny. You can change your choice at any time.