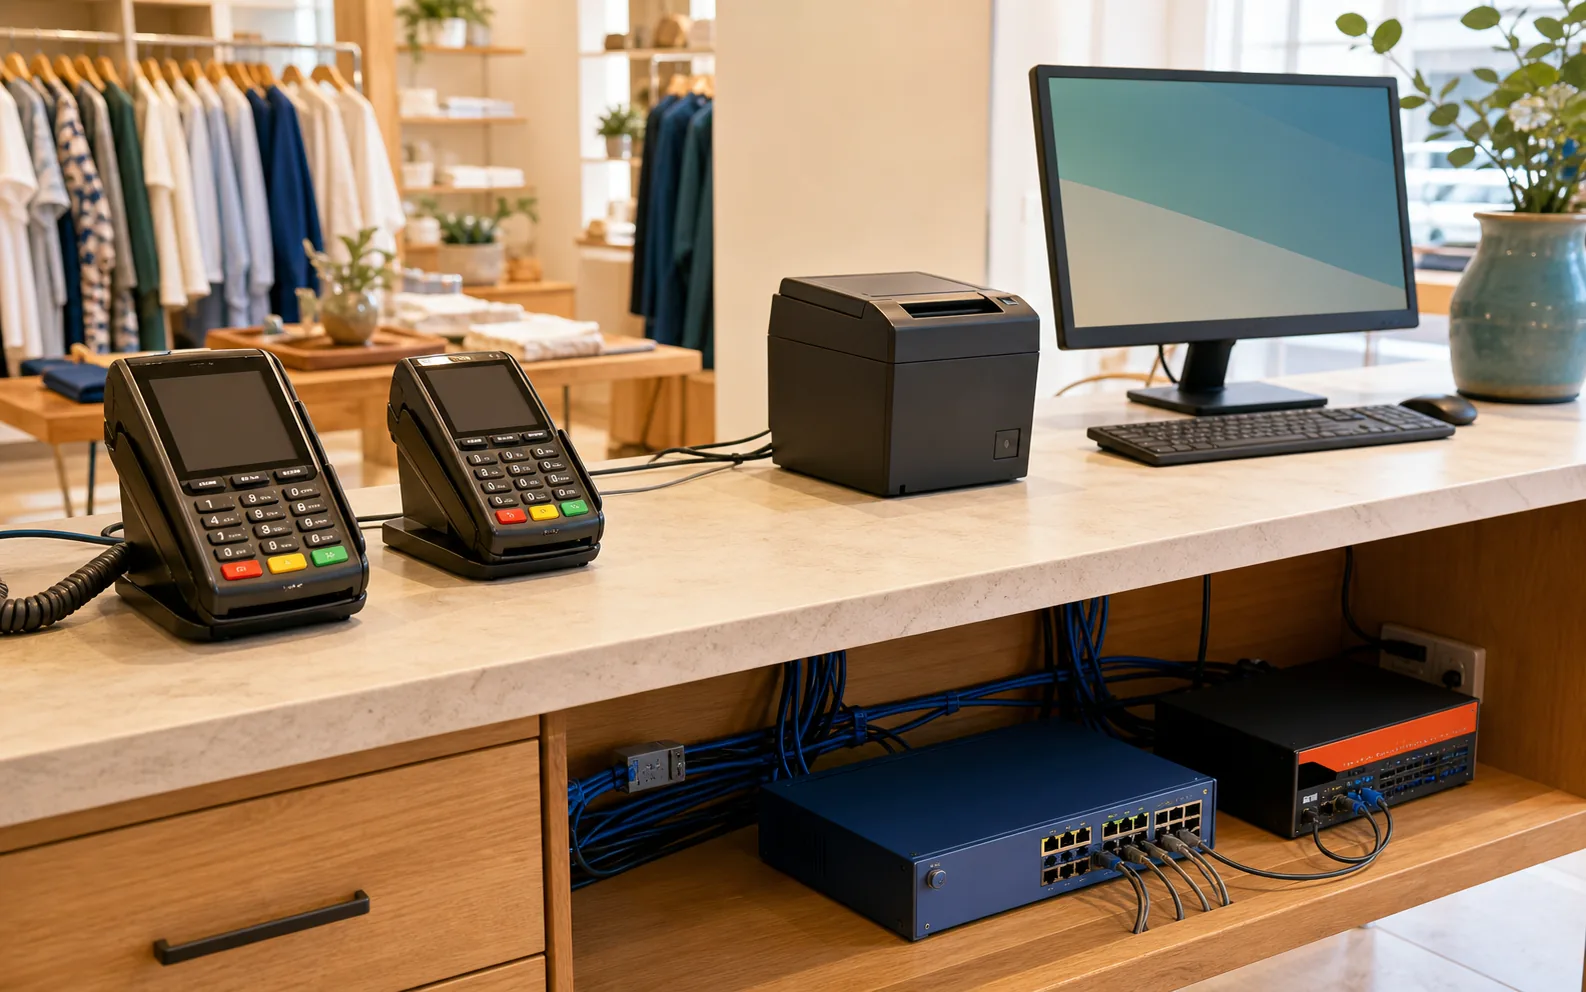
Payment scope and data flow
Map terminals, e-commerce, call-center, mobile, processor, gateway, tokenization, storage, transmission, and administrative access paths.
Find exposure, strengthen essential controls, and build practical resilience around the systems your organization depends on.
Explore cybersecurity services →Evaluate controls independently, document defensible findings, and focus remediation on the risks with the greatest operational impact.
Explore security audits →Translate security obligations into clear evidence, accountable remediation, and a practical path toward audit or customer readiness.
Explore compliance services →Bring security governance, risk decisions, leadership communication, and improvement planning into one accountable executive program.
Explore vCISO services →PCI DSS assessment and readiness cost estimate
Estimate the cost to clarify cardholder-data scope, payment channels, network segmentation, service-provider dependencies, vulnerability evidence, policies, and remediation priorities.
Focused OC Security Audit starting price
The crossed-out figure is an illustrative planning comparison, not a third-party market survey. Final scope and fees are confirmed in writing.
Ali Hassani, CISO, brings 25+ years of IT, cybersecurity, compliance, network, Microsoft, and infrastructure experience to each engagement.
Instant service pricing estimate
Choose the closest answer for ten simple scope questions. The estimate updates in your browser and does not collect or transmit your selections.
Professional audit deliverables
The engagement turns technical and documentation review into clear priorities for leadership, IT, vendors, and follow-up validation.
What the service reviews
Map terminals, e-commerce, call-center, mobile, processor, gateway, tokenization, storage, transmission, and administrative access paths.
Review network boundaries, access control, MFA, logging, vulnerability management, secure configuration, endpoint protections, and service-provider responsibility.
Organize policies, inventories, diagrams, scan results, change records, test evidence, provider attestations, and remediation tracking for the applicable path.
For scope context, review OC Security Audit’s PCI DSS Readiness service and the authoritative PCI Security Standards Council PCI DSS resources. A related free readiness tool can help identify questions before a professional engagement.
Experienced, independent guidance
Ali helps businesses reduce uncertainty about PCI scope, technical boundaries, evidence, and remediation without confusing readiness consulting with formal assessor validation.
Ali Hassani is a CISO, cybersecurity and IT consultant, and infrastructure leader with 25+ years of experience. Certifications include CISSP, CCISO, CCNP, CCNA, MCSE, MCSA Security, MCITP, MCP, and MCTS. Learn more about Ali Hassani.
Pricing questions
Locations, payment channels, terminals, e-commerce integrations, in-scope systems, service providers, segmentation, validation path, testing evidence, and documentation condition determine effort.
This page describes readiness and security consulting, not a QSA attestation. Organizations that require formal assessor validation should confirm the applicable PCI SSC program and qualified assessor requirements.
The review can identify scope drivers and possible segmentation or architecture improvements. Any scope-reduction decision must be supported by the actual data flow, controls, testing, and applicable validation requirements.
Call for a confidential conversation or send the basic environment details you already have. OC Security Audit will confirm objectives, exclusions, access, timing, deliverables, and a written fee.
This estimator is for initial guidance only and does not replace a professional cybersecurity audit, compliance assessment, penetration test, legal/compliance review, or written proposal. Do not enter confidential information.
This website uses essential cookies for security and operation. Optional analytics and advertising cookies help measure site use and outreach. Choose Allow or Deny. You can change your choice at any time.